❌

Visualização normal

Antes de ontemCybersecurity News
  • ✇Firewall Daily – The Cyber Express
  • GMO Internet Compensates Users as Cyberattacks Hit Japanese Companies Ashish Khaitan
    Japanese companies are starting to compensate customers after a run of cyberattacks disrupted internet services and stirred concerns about economic stability. GMO Internet is the latest to do so, pledging payouts after hackers breached its foreign exchange trading service.  In a blog post on Oct 25, chief executive Masatoshi Kumagai said customers would be compensated for losses caused by unauthorized access, and each would receive 5,000 yen (S$41) as “an initial gesture of good faith.”  K
     

GMO Internet Compensates Users as Cyberattacks Hit Japanese Companies

26 de Outubro de 2026, 07:36

GMO Internet

Japanese companies are starting to compensate customers after a run of cyberattacks disrupted internet services and stirred concerns about economic stability. GMO Internet is the latest to do so, pledging payouts after hackers breached its foreign exchange trading service.  In a blog post on Oct 25, chief executive Masatoshi Kumagai said customers would be compensated for losses caused by unauthorized access, and each would receive 5,000 yen (S$41) as “an initial gesture of good faith.”  Kumagai, whose group spans internet infrastructure and cryptocurrency trading, warned that “the internet itself is now starting to break down.” He added: “The internet is increasingly being transformed into a tool that malicious actors use to threaten and rob people.”  GMO Internet shares, worth US$2.6 billion (S$3.3 billion) in market value at the Oct 23 close, fell 11% in Tokyo morning trade while the benchmark index was flat.  The company said a party believed to be behind the attack had demanded money and threatened to disclose company and customer information. GMO Internet refused and said it would handle the incident with police and other authorities. It will give customers a free alternative service for six months, though it cannot yet calculate how the goodwill payments and compensation will affect earnings.  Kumagai said the company’s white-hat hackers had identified security issues, but the depth and speed of the response were insufficient. 

AI and PHP Flaws Put Japanese Companies at Risk

Experts say AI is helping attackers automate tasks from scanning for software vulnerabilities to crafting phishing campaigns, making cybercrime faster, cheaper and harder to detect.  On Oct 23, Japan said it would set up a team to simulate cyberattacks using AI to find weaknesses in technology systems. Organisations were rushing to limit risks from flaws in PHP, the programming language underpinning much of the internet. Last week, government and company websites in Japan, Europe and elsewhere went offline after critical PHP vulnerabilities were disclosed, prompting millions of hacking attempts. 

GMO Internet Chief Seeks Stronger Cyberdefence

Kumagai has asked the Japanese government to apply cyberdefence measures in response to the attack, following the introduction of a cyberdefence system in October. That system could involve steps such as attacking hostile servers to neutralise threats.  “Now is the time for the public and private sectors to work together to protect Japan,” he wrote. 

Rising Security Costs for Japanese Companies

The recent attacks have exposed weaknesses in how Japanese companies protect their large stores of customer data, raising the prospect of steep costs to shore up defences.  “Companies already have standard security measures in place, so if they want to strengthen them further, there is a possibility that the additional cost burden could be quite substantial,” said Shoichi Arisawa, an analyst at IwaiCosmo Securities.  TrendAI data shows 723 cybersecurity incidents in the year to Oct 20, more than the annual totals for 2025 and 2024. Satoshi Nagano, president of ESET Japan, said: “Reports may reflect both the threats organisations face and greater visibility into incidents that would previously have gone undetected, been underinvestigated, or remained undisclosed.”  GMO Internet is not alone in paying customers. Park24, which runs the Times car-sharing service, said on Oct 23 it would pay customers 3,000 yen each after a personal data breach. It will stop keeping identity document images once registration checks are done and expects an extraordinary loss of 5.5 billion yen from its response to the attack and compensation payments. 
  • ✇Firewall Daily – The Cyber Express
  • Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services Ashish Khaitan
    Japan is preparing to set up a dedicated team to run AI-driven cyberattack simulations to expose weaknesses in technology systems. Japan’s plan for AI cyberattack simulations comes as organizations worldwide scramble to address critical PHP flaws that have disrupted parts of the internet.  Speaking on Friday, Industry Minister Ryosei Akazawa said those defending against cyber threats need to think like attackers, using AI proactively to uncover potential weak points before they can be exploited.
     

Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

23 de Outubro de 2026, 04:19

AI cyberattack simulations

Japan is preparing to set up a dedicated team to run AI-driven cyberattack simulations to expose weaknesses in technology systems. Japan’s plan for AI cyberattack simulations comes as organizations worldwide scramble to address critical PHP flaws that have disrupted parts of the internet. 

Speaking on Friday, Industry Minister Ryosei Akazawa said those defending against cyber threats need to think like attackers, using AI proactively to uncover potential weak points before they can be exploited. 

His comments follow widespread disruption caused by the disclosure of the PHP flaws, which led to millions of reported hacking attempts. Businesses and governments were forced to patch their systems or temporarily take websites offline.  

Because PHP is widely used to build and run websites and web applications, any weakness in the language poses a risk to organizations across many sectors. 

How PHP Flaws Hit Banks, Airlines and Government 

The vulnerabilities triggered precautionary shutdowns across banking, transport, airline and government services in several countries. 

In Japan, Nomura, Mitsubishi UFJ Financial Group, ANA and East Japan Railway temporarily halted some online services. The Ministry of Finance, the National Tax Agency and the Meteorological Agency also suspended certain digital services as part of their security response. 

On Friday, JR East said some of its services were back online, while others would resume only after safety checks. Nippon Paint said it had applied a security patch and restored its website. 

The disruption shows how difficult it is to secure interconnected digital infrastructure when a widely used software component turns out to have serious weaknesses. 

SoftBank Pauses Emergency Alerts Over PHP Flaws 

The fallout also reached services people rely on in a crisis. Telecommunications company SoftBank said it was temporarily suspending its mobile emergency alert system while it carried out maintenance to fix a PHP vulnerability. 

While the system is down, customers will not receive early warnings through it for earthquakes, tsunami threats, disasters, or evacuation information. The case shows that cybersecurity incidents can extend well beyond ordinary websites and interrupt access to vital public safety information. 

Why Japan AI Cyberattack Simulations Point to Proactive Defense 

The episode has put a fresh focus on finding vulnerabilities before attackers do. The Japan AI cyberattack simulations are designed to help defenders understand how weaknesses might be targeted and to sharpen their response capabilities, in line with the approach Ryosei Akazawa outlined. 

Simulation alone is not enough, however. Installing patches remains essential, and organizations need to test updated systems carefully before bringing services back, especially where transport, finance, and government operations are affected. 

As AI tools grow more capable for both attackers and defenders, businesses and governments face the task of pairing fast vulnerability detection with effective security updates, continuous monitoring, and resilient digital infrastructure. 

Cloudflare
Verify you are human

loading

Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content.
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare

site-verification-ok

Cloudflare
Verify you are human
loading
Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content.
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare

site-verification-ok

  • ✇Cybersecurity News
  • Zeabur Shutdown Follows Repeated Data Breaches Do Son
    The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts. Related Posts: Railway Security Incident Exposes Customer Environment Variables and Pauses All Deployments Sourcenext Data Breach Exposes 22.5M User Records OpenCode Security Breach Exposes 1.4% of Console Users The post Zeabur Shutdown Follows Repeated Data Breaches appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • AWS Patches Critical Amazon Neptune Vulnerability in Apache TinkerPop Gremlin Do Son
    Upgrade your DB cluster to fix CVE-2026-110812, a critical 9.9 CVSS Amazon Neptune vulnerability in Apache TinkerPop Gremlin. Related Posts: Rank Math SEO PRO Supply-Chain Compromise Exploited in the Wild via Version 3.0.123 Critical BeyondTrust Remote Support Vulnerability Exploited in the Wild by ARMORY CASTLE Chrome 155 Update Fixes 10 Security Flaws, Including Critical Prerender Bug The post AWS Patches Critical Amazon Neptune Vulnerability in Apache TinkerPop Gremlin appeared first on Da
     

Amazon Fire TV Cube Security Flaws Allow Bootloader Unlocking and Permanent Root Access

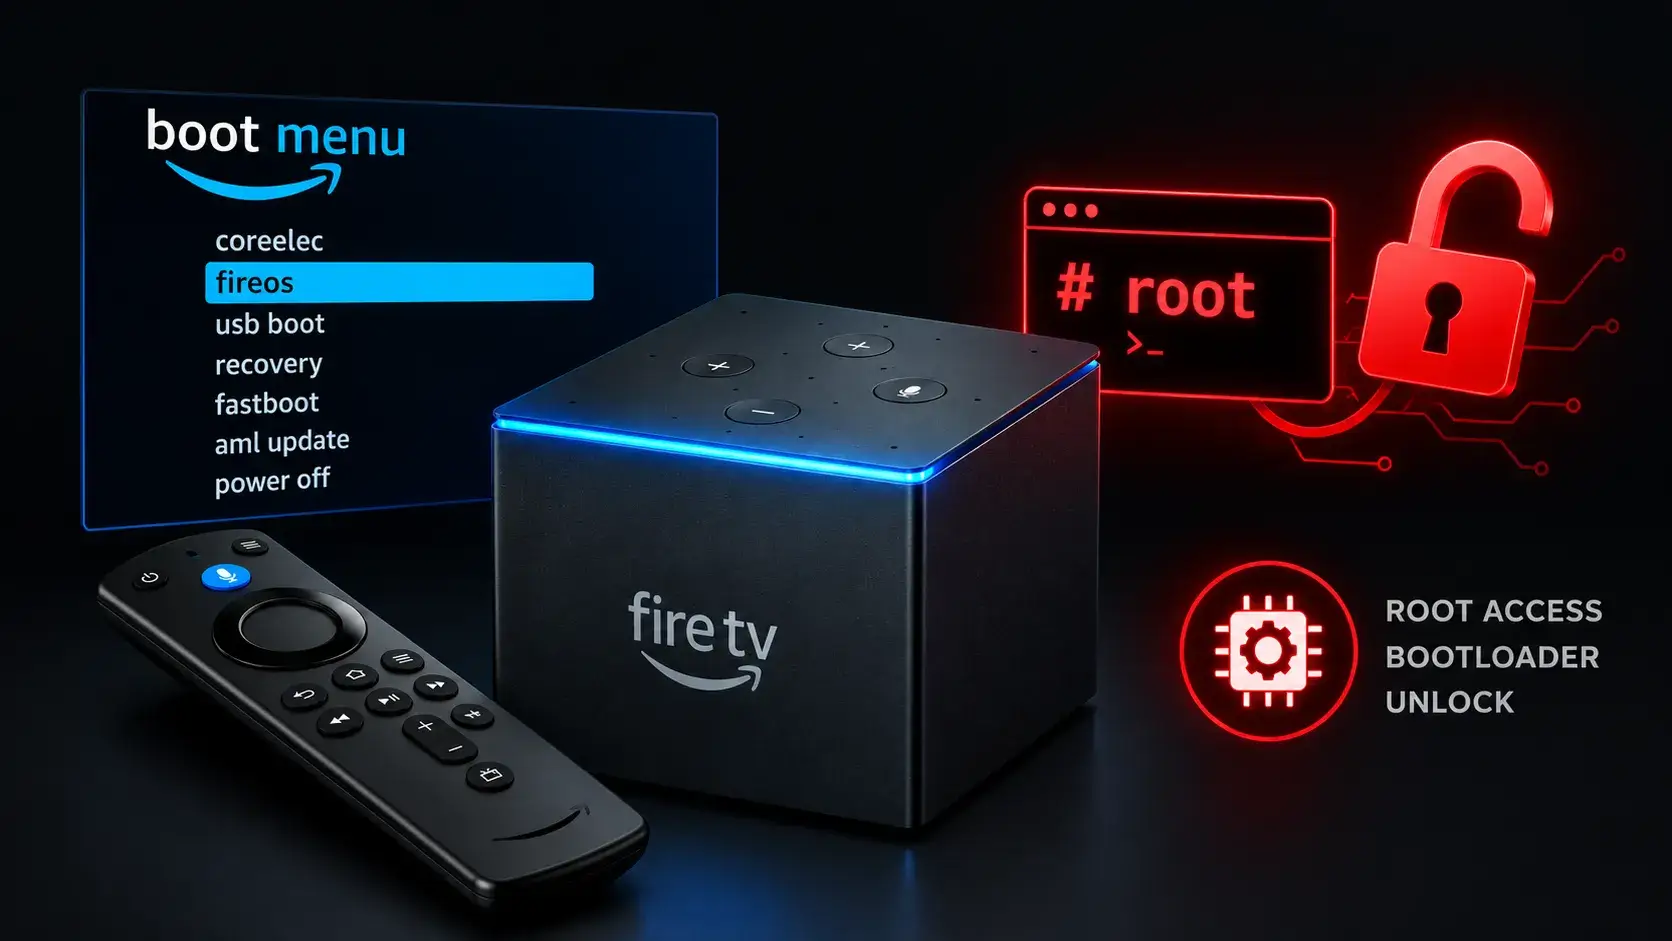
A recently released exploit package lets the third-generation Amazon Fire TV Cube gain an unlocked bootloader and persistent root access on firmware version PS7717 or earlier. Developed by XDA developer Pro-me3us, the project targets devices codenamed “gazelle”. It combines temporary privilege escalation with a separate bootloader vulnerability to enable lasting system modifications. This release includes […]

The post Amazon Fire TV Cube Security Flaws Allow Bootloader Unlocking and Permanent Root Access appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AWS Fixes AI Agent Flaws Enabling Authentication Bypass and Credential Theft

AWS released security updates for three vulnerabilities in its open-source Loom platform, used for AI agent orchestration. These vulnerabilities could allow unauthenticated administrative takeover, disclosure of OAuth2 credentials, and access to internal services. The company strongly urges users to upgrade all Loom deployments and forks to version 1.7.0. AWS announced these issues in Security Bulletin […]

The post AWS Fixes AI Agent Flaws Enabling Authentication Bypass and Credential Theft appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

  • ✇Cybersecurity News
  • AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Studio Code Execution Flaws Do Son
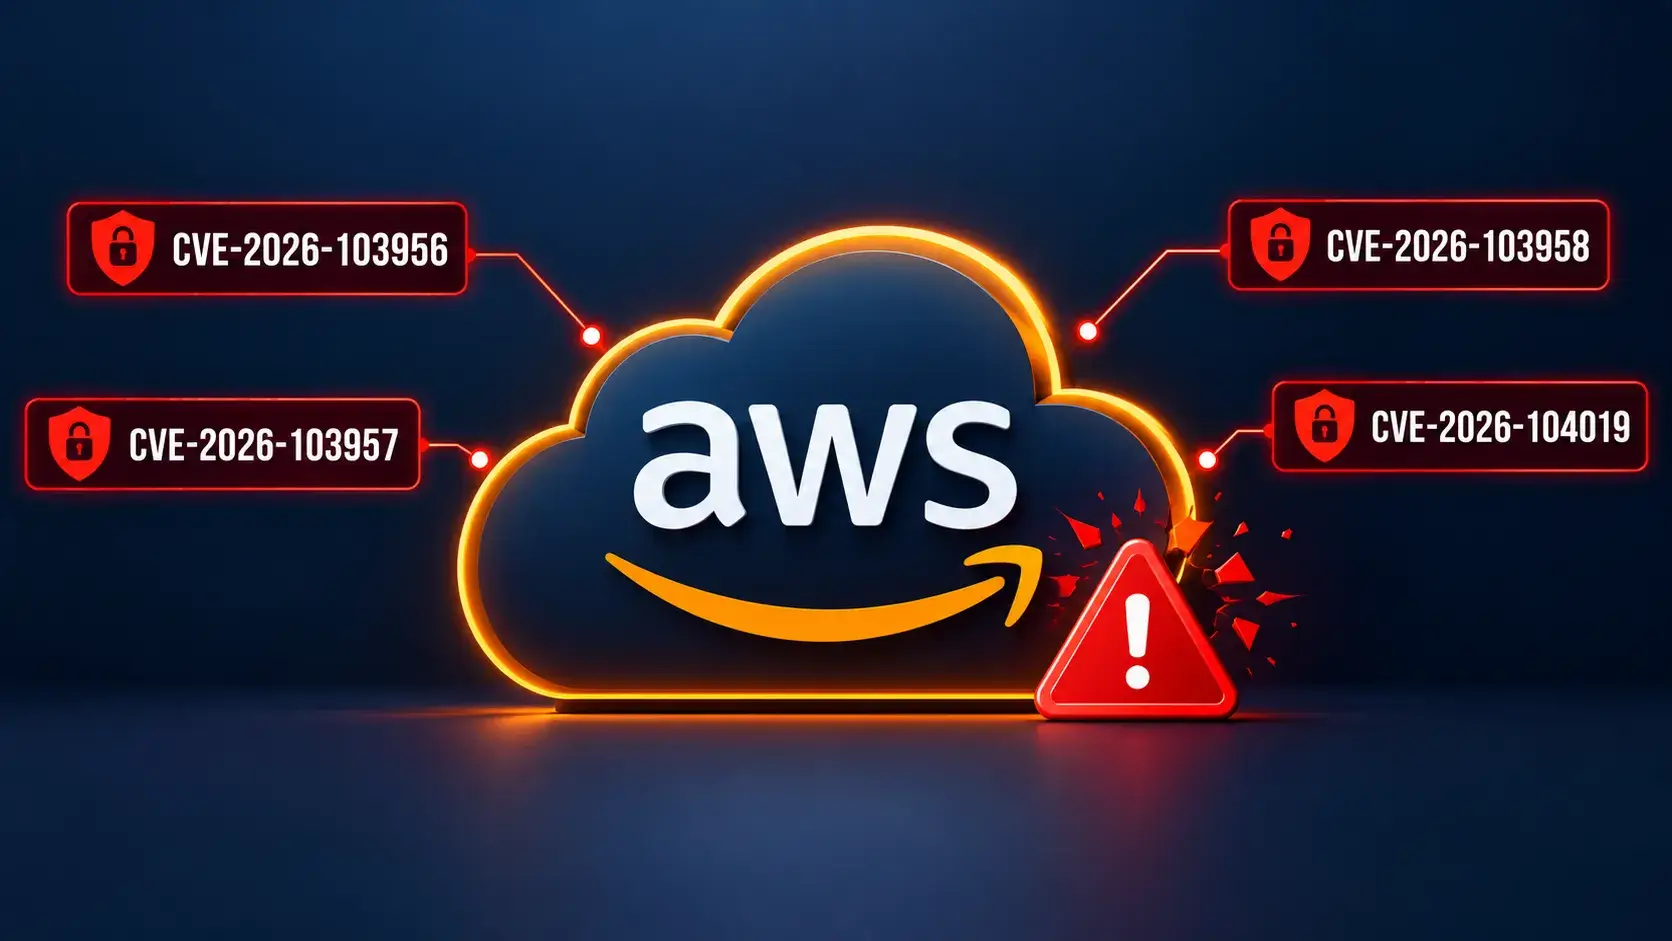
    AWS fixes Loom for AWS admin takeover CVE-2026-103956 and a SageMaker Unified Studio code execution bug, CVE-2026-104019. Patch now. Related Posts: Citrix NetScaler CVE-2026-88779 Exploited in the Wild to Knock SAML Gateways Offline Unpatched Apache OpenOffice Vulnerability Leads New Apache Advisories for LDAP API and Traffic Server Microsoft Reissues September 2026 Exchange Server Security Updates to Add CVE-2026-96940 The post AWS Fixes Loom for AWS Admin Takeover and SageMaker Unified Stud
     

TIKTOUK WordPress Toolkit Could Enable AWS, SMTP and API Credential Theft Attacks

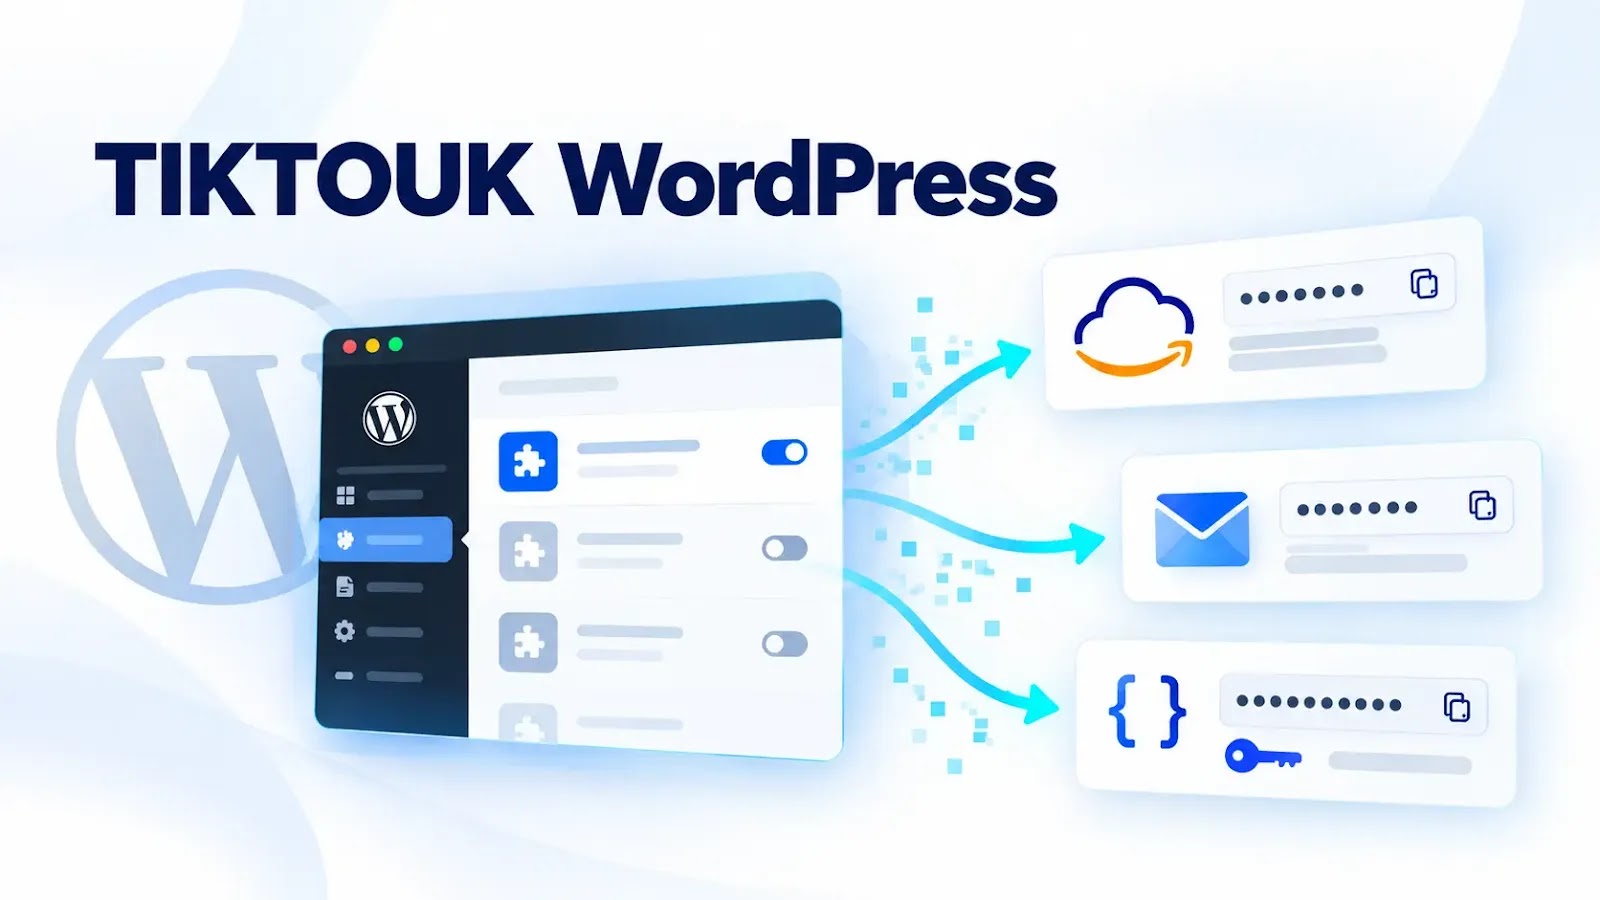
A credential-collection toolkit dubbed TIKTOUK that combines WordPress reconnaissance, exposed-file harvesting, plugin credential decryption, and JavaScript secret scanning. The toolkit consists of two Python scripts, wp2s_poll.py and wp2s_crack.py, alongside a stripped Go-based Linux crawler named jscrawl-amd64. All three components retrieve targets from a central HTTP hub, execute assigned collection tasks, and submit status reports and […]

The post TIKTOUK WordPress Toolkit Could Enable AWS, SMTP and API Credential Theft Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Marimo RCE Flaw Lets Hackers Steal AWS Credentials and Pivot to Bastion Host in 8 Seconds

A threat actor exploited a critical pre-authentication remote code execution vulnerability in marimo to harvest AWS credentials, retrieve an SSH private key from AWS Secrets Manager, and authenticate to a bastion host in just eight seconds, according to the Sysdig Threat Research Team. This vulnerability, tracked as CVE-2026-39987, affects marimo versions up to 0.20.4 and […]

The post Marimo RCE Flaw Lets Hackers Steal AWS Credentials and Pivot to Bastion Host in 8 Seconds appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

  • ✇Security Boulevard
  • New York’s 3D Printing Crackdown: Security or Surveillance? Tom Eston
    New York’s latest budget proposal could fundamentally change how 3D printers work—requiring built-in software that scans and blocks certain designs. Supporters say it’s about stopping ghost guns. Critics say it opens the door to surveillance and limits innovation. In this episode, we break down what’s actually in the proposal, why it’s raising alarms across the […] The post New York’s 3D Printing Crackdown: Security or Surveillance? appeared first on Shared Security Podcast. The post New York’s
     

New York’s 3D Printing Crackdown: Security or Surveillance?

27 de Abril de 2026, 01:00

New York’s latest budget proposal could fundamentally change how 3D printers work—requiring built-in software that scans and blocks certain designs. Supporters say it’s about stopping ghost guns. Critics say it opens the door to surveillance and limits innovation. In this episode, we break down what’s actually in the proposal, why it’s raising alarms across the […]

The post New York’s 3D Printing Crackdown: Security or Surveillance? appeared first on Shared Security Podcast.

The post New York’s 3D Printing Crackdown: Security or Surveillance? appeared first on Security Boulevard.

💾

  • ✇Security Boulevard
  • Why the US–EU Privacy Divide Still Matters in the Age of AI  Jonathan Mortensen
    Explore the evolving landscape of privacy and security in the age of AI. This article examines the cultural and regulatory differences between the U.S. and Europe, the limitations of current policies, and the imperative for architectural solutions to ensure that autonomous systems can uphold privacy standards. The post Why the US–EU Privacy Divide Still Matters in the Age of AI  appeared first on Security Boulevard.
     

Why the US–EU Privacy Divide Still Matters in the Age of AI 

19 de Fevereiro de 2026, 05:00
Data Privacy Automation User Privacy Threatens Security Defenses

Explore the evolving landscape of privacy and security in the age of AI. This article examines the cultural and regulatory differences between the U.S. and Europe, the limitations of current policies, and the imperative for architectural solutions to ensure that autonomous systems can uphold privacy standards.

The post Why the US–EU Privacy Divide Still Matters in the Age of AI  appeared first on Security Boulevard.

❌
❌