❌

Visualização normal

Antes de ontemCybersecurity News
  • ✇Cybersecurity News
  • cPGuard Supply Chain Attack Pushes Backdoor Through Update Channel Do Son
    cPGuard supply chain attack: an update channel compromise pushed a backdoor in versions 5.88.12-5.88.19. Update to 5.88.25 and rotate credentials. Related Posts: Ubuntu Kernel Fixes for CVE-2026-98432 (CVSS 9.8) Land in Proposed Pocket TeamViewer Client Vulnerability Enables Remote Code Execution 7 Unpatched phpMyAdmin Vulnerabilities Exposed The post cPGuard Supply Chain Attack Pushes Backdoor Through Update Channel appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • UAT-11985 Uses AI-Written Lures and an AitM Phishing Kit Against Taiwan Researchers Do Son
    UAT-11985 used AI-written lures and an AitM phishing kit in a Taiwan spear-phishing campaign that steals Google logins and bypasses MFA. Related Posts: Suspected TraderTraitor Hackers Use Trojanized Terraform Provider to Deliver FLATROOF and ROOFDECK The Devastating Ledger Security Breach The Reality of Ransomware Recovery Services The post UAT-11985 Uses AI-Written Lures and an AitM Phishing Kit Against Taiwan Researchers appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • SVG Phishing Attacks Return in August as Symantec Logs 222,000 Detections Do Son
    SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it. Related Posts: Russia's Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor Nigeria-Based Fraudsters Hijack .edu Accounts to Run University Job Scams Microsoft Links JADEPUFFER Azure Attack to Agentic Ransomware Actor Storm-3168 The post SVG Phishing Attacks Return in August as Symantec Logs 222,000 Detections appeared
     

The Password Notebook Is Back — but Is It Actually Safer?

25 de Agosto de 2026, 15:18

Password notebooks are making an unexpected comeback as infostealers and browser attacks revive debate over the safest way to store credentials.

The post The Password Notebook Is Back — but Is It Actually Safer? appeared first on TechRepublic.

77 Counterfeit Open VSX Extensions Collected Developer and CI/CD Data

10 de Agosto de 2026, 11:52

Security researchers found 150 lookalike Open VSX extensions published under trusted names, highlighting how extension marketplaces can expose developer credentials, source code, and CI/CD systems to supply-chain risk.

The post 77 Counterfeit Open VSX Extensions Collected Developer and CI/CD Data appeared first on TechRepublic.

Fake The Odyssey Downloads Are Hiding Password-Stealing Malware

10 de Agosto de 2026, 11:21

Fake downloads of The Odyssey are spreading Lumma Stealer malware capable of stealing passwords, cookies, payment data, and cryptocurrency information.

The post Fake The Odyssey Downloads Are Hiding Password-Stealing Malware appeared first on TechRepublic.

AssuranceAmerica Data Breach: 6.9M Driver’s License Numbers Exposed

9 de Julho de 2026, 11:16

AssuranceAmerica says hackers accessed the driver's license data of 6.9 million customers, exposing personal information and raising concerns about identity theft.

The post AssuranceAmerica Data Breach: 6.9M Driver’s License Numbers Exposed appeared first on TechRepublic.

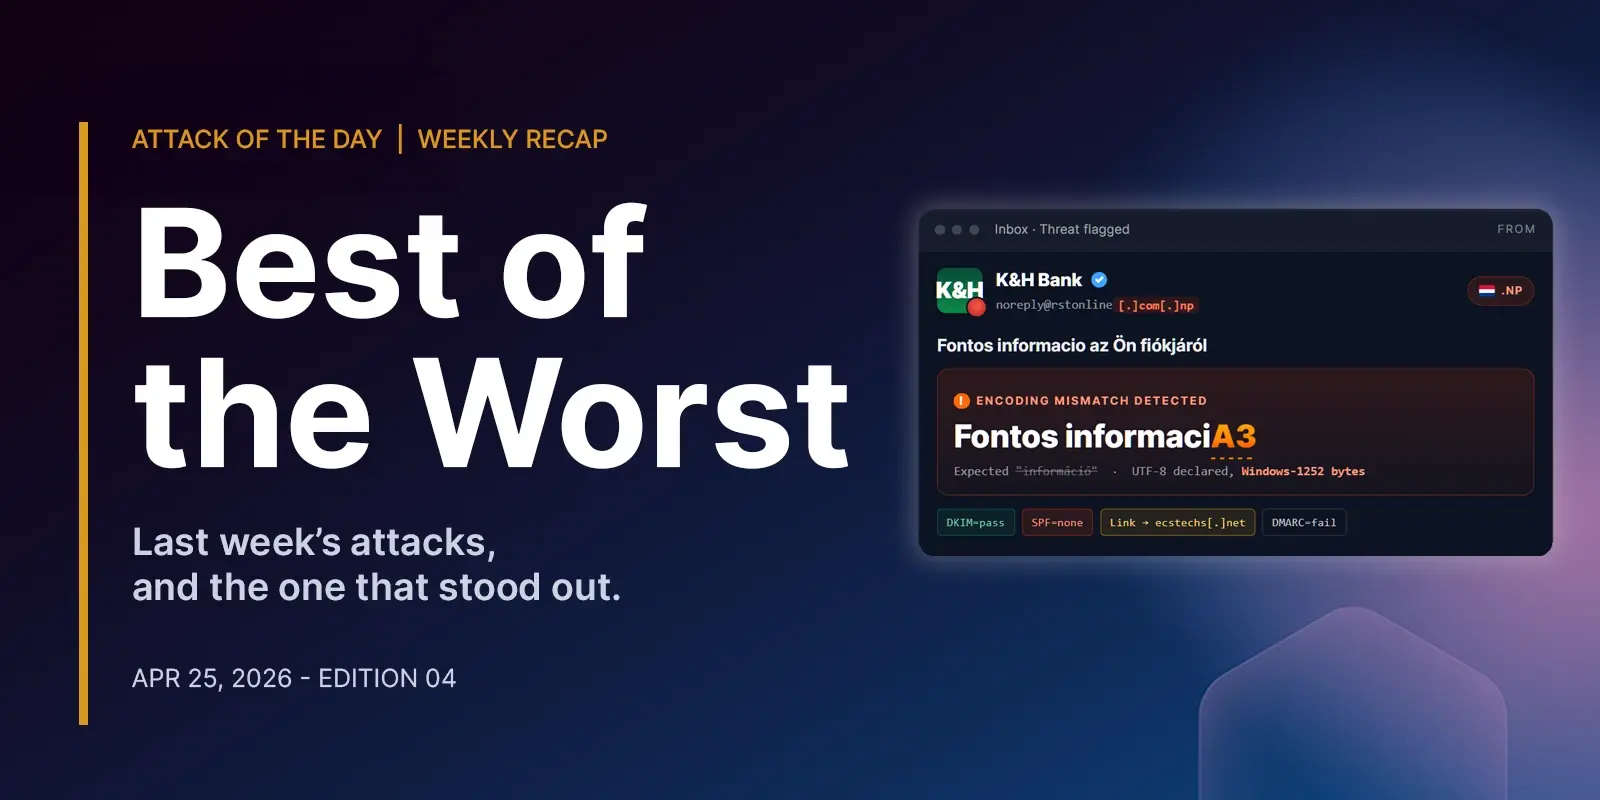
Best of the Worst: Five Attacks That Looked Broken (and Worked)

25 de Abril de 2026, 08:38

I skipped last week's roundup. Holiday weekend, family stuff, the usual. So this is a two-week-ish view of what we've published in the Threat Intelligence series since Edition 03 dropped on April 13.

The post Best of the Worst: Five Attacks That Looked Broken (and Worked) appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Claude Mythos and the Cybersecurity Risk That Was Already Here Jacob Krell
    On March 26, Anthropic confirmed the existence of Claude Mythos, an unreleased AI model described internally as "a step change" in capabilities, after a data leak exposed approximately 3,000 unpublished assets in a publicly searchable, unencrypted data store (Fortune, March 26, 2026). The leak was not a sophisticated intrusion. A toggle switch in Anthropic's content management system was left in the wrong position, setting digital assets to public by default (Fortune, March 26, 2026). Amon
     

Claude Mythos and the Cybersecurity Risk That Was Already Here

27 de Março de 2026, 16:15

On March 26, Anthropic confirmed the existence of Claude Mythos, an unreleased AI model described internally as "a step change" in capabilities, after a data leak exposed approximately 3,000 unpublished assets in a publicly searchable, unencrypted data store (Fortune, March 26, 2026). The leak was not a sophisticated intrusion. A toggle switch in Anthropic's content management system was left in the wrong position, setting digital assets to public by default (Fortune, March 26, 2026). Among the exposed materials were internal assessments describing Mythos as posing "unprecedented cybersecurity risks" and being "far ahead of any other AI model in cyber capabilities" (World Today News, March 2026).

The post Claude Mythos and the Cybersecurity Risk That Was Already Here appeared first on Security Boulevard.

❌
❌