 Entrar

Japan Plans Major Cyber Hunt to Detect Hidden Attacks on Critical Infrastructure
5 de Outubro de 2026, 03:02


Cisco patched 18 Secure Firewall vulnerabilities in FMC, ASA, and FTD, including critical unauthenticated root remote code execution flaws. Update now.
Related Posts:
The post Cisco Patches 18 Secure Firewall Flaws, Several Root RCE appeared first on Daily CyberSecurity.
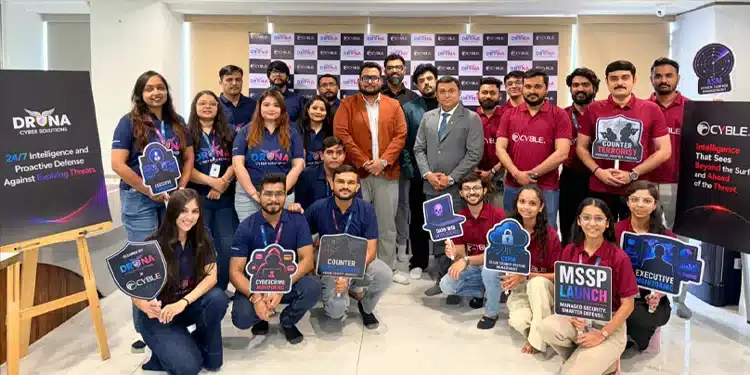
The AI-Powered Intelligence for Cyber Defense initiative was formally launched Tuesday at DRONA Cyber Solutions' Command and Control Centre, where the companies presented a live technical demonstration showing how an intrusion attempt can be detected, investigated and contained.
The launch comes as India faces a growing cybercrime burden. India recorded 28.15 lakh cybercrime cases in 2025, a 24 percent increase over the previous year, with reported losses reaching ₹22,495 crore. The government's 1930 cybercrime helpline received 32.4 million calls during the year. Of the complaints filed, 55,484 were converted into FIRs.
While large enterprises and banks increasingly have dedicated security teams, budgets and incident response capabilities, many manufacturers, hospital chains, schools and mid-sized businesses, particularly across Tier-2 and Tier-3 cities, continue to operate without comparable security resources.
The final containment action was authorised by a human analyst rather than executed automatically. The demonstration brought together multiple capabilities. Cyble Vision provided the initial detection through continuous monitoring of criminal marketplaces and leak sites.
Cyble Hawk supported the investigative process and attribution, while Cyble Titan handled endpoint enforcement, using hardware-level integrity checks to support its assessment. DRONA analysts remained at the centre of the process, making decisions that the system was deliberately not permitted to make independently.
Mandar Patil, Executive Vice President at Cyble, said the initiative was designed to address a longstanding gap between threat detection and action for mid-sized businesses.
"India is not short of alerts. It is short of what happens next," Patil said. "We have spent a long time in this industry watching mid-sized businesses get told about a threat and then having nowhere to take that information. What we are launching today is not another alert. It is a complete chain — intelligence before the attack, investigation that would stand up to scrutiny, enforcement on the device, and a person accountable for the decision at the end of it."Dhruv Pandit, Co-Founder and CEO of DRONA Cyber Solutions, said the initiative reflects the operational needs of organisations that require immediate action rather than another security dashboard.
"A factory owner calling us at two in the morning does not want to be shown a dashboard," Pandit said. "He wants to know what happened, he wants it contained, and he wants someone to take responsibility for what happens next."
The session brought together speakers from Cyble and DRONA Cyber Solutions to examine areas including dark web threat intelligence, government and PSU cybersecurity projects, digital forensics and incident response (DFIR), and the transition of threat intelligence from information to action.
Mandar Patil and Augustin Kurian of Cyble discussed the dark web threat intelligence landscape. Prathmesh Pawar spoke about government and PSU cybersecurity projects, while Brijesh Kapadiya addressed DFIR and Vijay Mali discussed moving threat intelligence from information to action. The keynote was delivered by Prof. Dr. Kapil Kumar, Coordinator, Department of Biochemistry and Forensic Science.
The session highlighted several practical aspects of cybersecurity work. The dark web was discussed not simply as a hidden part of the internet, but as a structured ecosystem requiring dedicated intelligence-gathering and threat-discovery methods. DFIR was presented as an area where speed and process are as important as technical expertise.
Another key takeaway was the importance of turning threat intelligence into action. Rather than treating intelligence as information alone, the session focused on how it can inform practical security decisions.
Patil told students that the cybersecurity industry faces a shortage of professionals with practical skills in analysing and validating threat intelligence."The gap this industry has is not a gap of ideas. It is a gap of people who know how to do the work," Patil said. "What separates a useful analyst from an alert-reader is the ability to ask whether a piece of intelligence is actually true before you act on it."Augustin Kurian, Editor-in-Chief of The Cyber Express, told students that threat intelligence and journalism share an emphasis on verification.
Every story we publish about a breach, a ransomware group or a leaked database starts exactly where today's demonstration started — with intelligence somebody had to go and find, verify, and decide was worth acting on," Kurian said. The instinct we have tried to build at The Cyber Express is the same instinct a good analyst needs: do not report, and do not act on, what you have not verified.The programme also involved technical and production teams supporting the session. Screen, sound and lighting were handled by the technical team under the guidance and supervision of Aditya More, while Misha Alagiya, Kavya Maharaja, Pathak Ami, Omi and Nandini supported stage management and photography.
"India's exposure is too large for any single partnership to take credit for solving," Patil said. "What matters is whether more of these collaborations exist a year from now, and whether the businesses we are talking about today — the ones without a security team — actually have somewhere to turn."
The AI-Powered Intelligence for Cyber Defense initiative will be delivered through DRONA's Ahmedabad command centre, with the companies indicating an intent to extend the service model to customers elsewhere in India over time.
The initiative also folds into DRONA's existing Cyber Yodha Campaign, a national programme aimed at building 50 integrated cybersecurity command centre labs and training more than 100,000 defenders.
By leveraging Myrmidon Defense Technology (MDT), Sevii enables cybersecurity teams to orchestrate autonomous AI agent swarms to hunt, isolate, and remediate threats at machine speed. This "AI fire with AI fire" approach addresses the critical shortage of security professionals while offering a fixed-cost model that eliminates the unpredictability of AI token consumption.
The post Sevii Adds Ability to Dynamically Deploy AI Agents to Combat Cyberattacks appeared first on Security Boulevard.

Phishing still hooks users around the world and coaxes them to hand over credentials. But on occasion the good guys take them down, like the FBI in collaboration with Indonesian law enforcement did with W3LLStore marketplace.
The post FBI, Indonesian Authorities Team to Take Down Site Ripping Off Users for Millions appeared first on Security Boulevard.
When More Tools Create More Problems For years, organizations have approached cybersecurity with a simple mindset-add more tools to strengthen defenses. Firewalls, endpoint solutions, intrusion detection systems, and monitoring platforms have all been layered together to create what appears to be a comprehensive security posture. Yet, despite this growing investment, security outcomes have not improved
The post Why Traditional Security Tools Fail-and How Unified AI Platforms Solve the Problem appeared first on Seceon Inc.
The post Why Traditional Security Tools Fail-and How Unified AI Platforms Solve the Problem appeared first on Security Boulevard.
Software supply chain attacks are evolving. Beyond compromised packages, discover the 2026 "Agentic" threat surface—where prompt injection, toolchain poisoning, and hallucinated dependencies bypass traditional DevSecOps. Learn how the 3 Pillars and AI-driven sandboxing provide a new defensive architecture.
The post Coding Agents Widen Your Supply Chain Attack Surface appeared first on Security Boulevard.

MCP Gateways are the wrong abstraction for AI security. Discover why runtime hooks and MCP registries offer a superior, context-aware defense against data leaks and unauthorized tool calls in modern agentic architectures.
The post Why MCP Gateways are a Bad Idea (and What to Do Instead) appeared first on Security Boulevard.

Europe’s plan to build sovereign search infrastructure highlights a growing security concern: dependence on foreign platforms for access to information and AI knowledge may represent a systemic vulnerability.
The post Europe’s Sovereign Search Plan is Really a Security Strategy appeared first on Security Boulevard.
Discover how the integration of large language models is transforming software security, lowering barriers for attackers, and necessitating autonomous defense platforms to keep pace with emerging threats.
The post The New Security Reality: When AI Accelerates Both Attack and Defense appeared first on Security Boulevard.
Baseline coding agents didn’t fare too well against purpose-built AI security agents in detecting flaws in DeFi contracts underscoring that organizations must not rely on audits and must press AI into use for detecting vulnerabilities.
The post Purpose-built AI Security Agent Detected 92% of DeFi Contracts Vulnerabilities appeared first on Security Boulevard.
Learn how to detect anomalous context injections in MCP deployments using post-quantum cryptography and ai-driven behavioral analysis to prevent puppet attacks.
The post Anomalous Context Injection Detection in Post-Quantum Environments appeared first on Security Boulevard.

The latest shutdown may be temporary, but the damage at CISA is not. Staffing cuts, stalled leadership and political crossfire have hollowed out what was once a bright spot in federal cybersecurity. When institutions built on trust and coordination lose people and mission clarity, the risks extend far beyond Washington.
The post CISA on Life Support appeared first on Security Boulevard.

Agentic AI is transforming cybersecurity by enabling autonomous threat detection, real-time response, and proactive defense across modern infrastructure.
The post Agentic AI in Cybersecurity is a Smarter, Faster Path to Resilience appeared first on Security Boulevard.
