❌

Visualização normal

Antes de ontemCybersecurity News
  • ✇Firewall Daily – The Cyber Express
  • Australian Data Breach Incidents Up 66% as AI Sharpens Scams Samiksha Jain
    Australians filed a cybercrime report about every six minutes over the past year, and artificial intelligence is making the attacks behind those reports faster and more convincing. That is the main finding of the ASD Cyber Threat Report 2025-26. It is the seventh annual assessment from the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC). In FY2025-26, the agency received more than 82,000 cybercrime reports through ReportCyber. It responded to over 1,500 cyber secur
     

Australian Data Breach Incidents Up 66% as AI Sharpens Scams

28 de Outubro de 2026, 04:25

ASD Cyber Threat Report

Australians filed a cybercrime report about every six minutes over the past year, and artificial intelligence is making the attacks behind those reports faster and more convincing. That is the main finding of the ASD Cyber Threat Report 2025-26. It is the seventh annual assessment from the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC).

In FY2025-26, the agency received more than 82,000 cybercrime reports through ReportCyber. It responded to over 1,500 cyber security incidents, up more than 20% on the previous year and 36% over five years. It also notified Australian entities of potentially malicious activity more than 4,400 times, almost 80% more than in FY2024-25.

What the ASD Cyber Threat Report Says About AI

The report calls AI the defining force in the threat environment this year. In his foreword, Deputy Prime Minister and Defence Minister Richard Marles wrote that AI is helping malicious actors find vulnerabilities faster and exploit them at greater scale, speed and sophistication. He also noted that new threats have emerged in recent weeks from the unintended actions of AI agents and from model testing.

ASD’s ACSC makes one clear distinction. AI has not created new kinds of threats. It has amplified and sped up existing ones. AI-enabled cyber threats are most visible in social engineering. Attackers are using AI to write phishing emails with no spelling or grammar errors and to automate targeted spearphishing. The Australian Securities and Investments Commission has also seen a sharp rise in scams that use deepfake videos of celebrities and politicians.

The time defenders have to respond is also shrinking. The agency has previously observed that most vulnerabilities are exploited within two weeks, and some within 48 hours of a patch being released. It expects AI-driven tools to shorten that window further over the next 12 months. Publicly reported vulnerabilities (CVEs) rose 30%. Old flaws are still a problem too: ASD’s ACSC recorded the successful exploitation of a vulnerability first identified in 2008.

Incident Severity Grows in ASD Cyber Threat Report Data

Only one Category 2 incident was recorded this year. However, extensive compromises rose from 26 to 40. ASD’s ACSC identified 362 incidents after proactively notifying organisations. A single notification about cPanel vulnerabilities, sent to 340 entities in May 2026, led to more than 60 confirmed incidents.

The number of ransomware incidents held steady at 139, but extensive ransomware incidents rose from 16 to 24. Health Care, Professional, Scientific and Technical Services, and Manufacturing remained the most affected sectors. Data breaches made up 98 incidents, a 66% increase on the previous year. Separately, the Office of the Australian Information Commissioner received 1,205 breach notifications in 2025. That is the highest yearly total since its Notifiable Data Breaches scheme began in 2018.

The financial impact is rising for businesses. The average self-reported cost of cybercrime per business report rose 16% to $93,500. For medium-sized businesses, it rose 45% to $141,300. The average cost for individuals stayed at $33,000. Identity fraud remained the most reported cybercrime, although reports fell 18%.

Stolen access is now a major entry point. Compromised accounts and credentials were among the most frequently reported incident categories, and phishing appeared in 39% of incidents. Government survey research cited in the report found that 55% of Australians reuse passwords across multiple accounts.

State Actors and Critical Infrastructure in the ASD Cyber Threat Report

State-sponsored actors continued to target Australian government, business and individuals to gain sensitive information. The report says these actors are increasingly pre-positioning inside networks to enable future disruption. Marles wrote that the line separating state-sponsored espionage from sabotage and cybercrime is becoming increasingly blurred.

In April 2026, ASD’s ACSC and international partners highlighted a shift by China-nexus actors. These actors are moving towards large covert networks built from compromised home and small office routers, Internet of Things devices and smart devices.

Critical infrastructure accounted for 154 incidents, or 10% of the total, a decrease of almost 7%. Phishing was the leading initial access technique at 36%, and Financial and Insurance Services was the most affected critical infrastructure division at 30%.

What the Threat Report Asks Organisations to Do

In October 2026, ASD’s ACSC released the Essentials series. It evolves the Essential Eight into a principles-based framework with three chapters: Enterprise IT, Operational Technology and Cloud.

Under its Cyber Action Year, the agency is pushing five priorities:

  • Replacing or mitigating legacy technology.
  • Implementing best-practice event logging.
  • Managing supply chain risk.
  • Preparing for AI-enabled threats.
  • Preparing for post-quantum cryptography, including ceasing the use of traditional asymmetric cryptography by the end of 2030 or sooner.

The report also urges organisations to patch faster. For individuals, it recommends reviewing privacy settings and enabling multi-factor authentication or passkeys.

Suspicious activity, incidents and vulnerabilities can be reported at cyber.gov.au or through the Australian Cyber Security Hotline on 1300 CYBER1 (1300 292 371).

  • ✇Firewall Daily – The Cyber Express
  • Burnaby Schools Hit by Cyberattack, Disrupting Networks and Phone Lines Samiksha Jain
    A Burnaby School District cyberattack is being investigated after an incident disrupted internal network services and phone lines across the district. The Burnaby School District said the cyber incident came to its attention on Monday, September 21, and that staff are working to contain the incident and restore affected services. The district has not disclosed whether any personal or sensitive information was accessed or stolen. However, the disruption has raised concerns about potential data
     

Burnaby Schools Hit by Cyberattack, Disrupting Networks and Phone Lines

25 de Setembro de 2026, 04:10

Burnaby School District cyberattack

A Burnaby School District cyberattack is being investigated after an incident disrupted internal network services and phone lines across the district. The Burnaby School District said the cyber incident came to its attention on Monday, September 21, and that staff are working to contain the incident and restore affected services. The district has not disclosed whether any personal or sensitive information was accessed or stolen. However, the disruption has raised concerns about potential data leaks as the investigation continues.

Burnaby School District Cyberattack Disrupts Operations

According to the district, the incident has affected some systems and operations, including internal network services and phone lines. Staff across Burnaby Schools are working to restore normal operations while limiting the impact on students. The district said the disruption has not affected student learning and that staff are working to ensure schools can continue supporting students. Families, staff, and district partners were contacted earlier in the week about the incident. The district said it will provide additional updates as efforts to contain the incident and restore services continue. The investigation remains ongoing, and the district has not provided further details about the nature of the incident, the suspected attackers, or whether information was compromised. The latest incident follows other school district cyberattacks and cybersecurity incidents that have disrupted education services and raised concerns about the security of student and staff information.

Education Sector Faces Repeated Cybersecurity Incidents

In September, The Cyber Express reported on the Springfield cyberattack, which disrupted school operations shortly after the start of the new academic year. The incident forced schools to close for part of the week and affected services relied on by families, including childcare and school meal programs. The district arranged grab-and-go meals at six locations while the YMCA of Greater Springfield provided full-day care for families enrolled in its programs. Students were expected to return to classrooms the following Monday. The Springfield incident highlighted how a cyberattack against school systems can extend beyond IT operations and affect essential services used by students and families. Earlier in 2026, a separate QLearn cybersecurity incident involving education technology provider Instructure affected educational institutions globally. Queensland Education Minister John-Paul Langbroek confirmed that the Queensland Department of Education had been briefed about the international breach. Early assessments indicated that the incident could affect more than 200 million people and more than 9,000 institutions worldwide.

Education Authority Cyberattack Targeted School Systems

In April 2026, an Education Authority cyberattack investigation found that attackers had gained targeted access to personal information linked to a small number of schools. Authorities identified the incident on April 10 after being alerted to suspicious activity affecting school systems. A forensic investigation later determined that attackers had accessed specific personal information associated with certain schools. The findings added to concerns surrounding cybersecurity risks in the education sector, where school networks can contain sensitive information belonging to students and staff. For the Burnaby School District, the current investigation is focused on containing the incident and restoring affected services. The district has not confirmed any data theft or provided details about possible unauthorized access. As the investigation progresses, further updates are expected from the district on the scope of the incident, affected systems and any potential impact on personal information.
  • ✇Firewall Daily – The Cyber Express
  • EU Cybersecurity Response Hampered by Critical Information Gaps Samiksha Jain
    The European Union’s ability to detect and respond to EU cybersecurity incidents faces significant gaps, particularly in information-sharing and coordination between national and EU-level bodies, according to a new report by the European Court of Auditors (ECA). The auditors said the EU has made progress in developing a cybersecurity cooperation framework, but several measures needed to support an effective response to significant and large-scale incidents are still incomplete. Cybersecurity
     

EU Cybersecurity Response Hampered by Critical Information Gaps

22 de Setembro de 2026, 03:08

EU cybersecurity incidents

The European Union’s ability to detect and respond to EU cybersecurity incidents faces significant gaps, particularly in information-sharing and coordination between national and EU-level bodies, according to a new report by the European Court of Auditors (ECA). The auditors said the EU has made progress in developing a cybersecurity cooperation framework, but several measures needed to support an effective response to significant and large-scale incidents are still incomplete. Cybersecurity incidents can disrupt public services, businesses, critical infrastructure and the EU’s internal market. While member states remain primarily responsible for responding to such incidents, the EU has a role when attacks cause major disruption, significant financial losses or substantial harm, or when incidents affect several countries and exceed the response capacity of a single member state.

EU Cybersecurity Incidents Face Information-Sharing Gaps

The ECA identified insufficient information exchange as a major weakness in the EU’s cybersecurity response system. The Cyber Blueprint, adopted in 2025, largely clarifies roles and responsibilities for managing major cybersecurity crises. However, the cooperation between two key EU cyber networks has not yet been formally defined. The auditors said this affects cooperation between the CSIRTs network, which brings together national teams responsible for handling cyber incidents, and EU-CyCLONe, which supports cooperation during EU-level cyber crises. Information-sharing is also affected by differences in national security laws and the ongoing implementation of updated EU cybersecurity rules, including the NIS 2 Directive. According to the auditors, these factors can make it harder for EU networks to identify threats early and coordinate an effective response. “The EU has made progress in building a cybersecurity cooperation framework, but it is not yet working as effectively as it should,” said George-Marius Hyzler, the ECA Member responsible for the audit. “When a serious cyber incident occurs, timely and actionable information is essential. Without it, networks and mechanisms lose much of their added value.”

European Cybersecurity Alert System Still Delayed

The audit also found that the European Cybersecurity Alert System was not operational at the time of the assessment. Two hubs examined by the auditors, ATHENA and ENSOC, had not started operating because of procurement delays. The system also lacked several elements needed for operation, including cooperation agreements, a common classification system and technical standards. The findings come as the EU continues to invest in cybersecurity. Under the 2021-2027 EU budget, €1.4 billion has been allocated to cybersecurity through the Digital Europe Programme, the EU’s main source of cybersecurity funding.

Overlap Among EU Cybersecurity Bodies

The ECA also identified overlapping responsibilities among some EU bodies involved in monitoring cybersecurity threats. The European Commission’s cyber situation centre, established in 2022 and largely supported by external providers, carries out work that the auditors said partly duplicates existing capabilities at the European Union Agency for Cybersecurity (ENISA). These capabilities include monitoring threats and developing cybersecurity situational awareness. The auditors called for better coordination to reduce duplication and strengthen the overall effectiveness of the EU’s cybersecurity framework.

Funding Checks Raise Security Concerns

The report also highlighted weaknesses in checks on some organisations receiving EU cybersecurity funding. These checks are intended to reduce risks linked to intrusion or influence by non-EU states and prevent sensitive security information from being shared with non-EU authorities. However, while grant beneficiaries are responsible for assessing the ownership and control of third parties receiving financial support, the European Cybersecurity Competence Centre does not verify those assessments. The ECA warned that this could expose sensitive infrastructure, operational data and security-critical technologies to security risks. The audit covered the period from 2022 to 2025 and assessed whether EU actions effectively supported the detection of and response to significant and large-scale cybersecurity incidents. Audit missions were conducted in Ireland, Greece and Italy.
  • ✇Firewall Daily – The Cyber Express
  • UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds Samiksha Jain
    Nearly four in 10 UK small firms were hit by a successful cyberattack in the past year, according to the latest Hiscox Cyber Readiness Report. The UK cyberattack rate reached 38%, significantly above the 29% global average recorded among nearly 7,000 smaller businesses surveyed worldwide. The 10th annual report surveyed cybersecurity decision-makers at smaller firms, including 1,000 respondents in the UK. Britain recorded the highest attack rate among the markets included in the research. Globa
     

UK Small Firms Bear Brunt of Rising Cyberattacks, Hiscox Finds

15 de Setembro de 2026, 03:09

UK cyberattack rate

Nearly four in 10 UK small firms were hit by a successful cyberattack in the past year, according to the latest Hiscox Cyber Readiness Report. The UK cyberattack rate reached 38%, significantly above the 29% global average recorded among nearly 7,000 smaller businesses surveyed worldwide.

The 10th annual report surveyed cybersecurity decision-makers at smaller firms, including 1,000 respondents in the UK. Britain recorded the highest attack rate among the markets included in the research. Globally, businesses that experienced an incident reported an average of four attacks during the past 12 months.

UK cyberattack Rate Outpaces Global Average

The findings place UK small businesses at greater exposure to successful cyberattacks than their international counterparts. While 29% of organisations globally reported a successful attack, the figure rose to 38% among small UK businesses.

The report also found that cyber incidents are creating measurable financial and operational costs. Globally, each incident cost organisations an average of $52,000 and resulted in around 32 hours of operational disruption.

In the UK, the average cost per cyberattack was $35,908, equivalent to £26,650. Although that figure was below the global average, the higher frequency of attacks means UK firms are more likely to encounter those costs.

The global attack rate also fell from the 59% figure reported in Hiscox's previous annual report. However, the two figures are not directly comparable because last year's research surveyed a broader group of 5,750 businesses across seven markets, while this year's report focuses specifically on almost 7,000 smaller firms.

Cyber Incidents Affect Business Growth

Cyber incidents are also influencing business decisions beyond immediate recovery costs. Globally, 32% of affected firms said cyber incidents delayed growth and expansion plans.

Other reported consequences included higher staffing costs for 31% of businesses, direct financial damage for 30%, and lost business opportunities for 29%.

Reputation and customer trust ranked as the most significant cyber-related risk, cited by 48% of businesses surveyed. Operational downtime or business interruption followed at 46%, while supply chain or third-party disruption was identified by 44%.

Among firms that experienced an incident, 28% faced financial penalties and 26% experienced damaging publicity.

UK Firms Increase Cyber Resilience Spending

Businesses are responding to the continuing threat by increasing spending on cyber resilience. The global average investment reached $51,000, with firms directing spending toward new technology, specialist staff and employee training.

New technology was adopted by 51% of firms, while 55% invested in specialist staff and 62% updated employee training.

UK businesses reported considerably higher spending, averaging $59,700, or £44,294, on cyber resilience. That placed the UK third among the markets surveyed for resilience spending.

The report also identified a growing connection between cybersecurity performance and executive compensation. Globally, 32% of firms said executive pay is now linked to cybersecurity performance. Among UK small firms, the figure was 25%.

Cyber Insurance Gap Remains

The findings also highlight a continuing gap between cybersecurity exposure and insurance uptake in the UK. Government data from the Department for Science, Innovation and Technology shows that 10% of UK businesses and 5% of charities hold a dedicated cyber insurance policy.

Separate research cited in the report found that just over 40% of UK SMEs hold cyber insurance, compared with around 63% of medium-sized firms and approximately 70% of FTSE 100 companies.

The latest Hiscox findings therefore show a combination of high cyberattack exposure, substantial investment in cyber resilience, and relatively limited cyber insurance uptake among UK businesses.

  • ✇Firewall Daily – The Cyber Express
  • CISA, FBI Urge Clearer Communication During Major Outages Samiksha Jain
    The CISA and FBI, along with cybersecurity agencies from Australia, Canada, New Zealand and the U.K., have released new guidance on outage communications for service providers dealing with major IT and OT outages. The guide calls for prompt, factual and audience-specific communication during disruptions caused by malicious cyber activity or non-malicious events. Titled “Communicating Under Pressure: Best Practices for Service Providers,” the guidance says effective communication is critical to
     

CISA, FBI Urge Clearer Communication During Major Outages

3 de Setembro de 2026, 02:37

outage communications

The CISA and FBI, along with cybersecurity agencies from Australia, Canada, New Zealand and the U.K., have released new guidance on outage communications for service providers dealing with major IT and OT outages. The guide calls for prompt, factual and audience-specific communication during disruptions caused by malicious cyber activity or non-malicious events.

Titled “Communicating Under Pressure: Best Practices for Service Providers,” the guidance says effective communication is critical to limiting operational impact when IT and OT outages affect customers, network defenders, critical infrastructure owners and operators, and the public. It recommends that organizations clearly communicate what is known, what remains unknown and what is still under investigation, while providing frequent updates as circumstances change.

Outage Communications Should Start With Facts

The agencies recommend that service providers establish an outage communications plan before an incident occurs. The plan should define incident thresholds, escalation paths, target audiences and procedures for status pages, customer and partner notices, and regulatory communications. Organizations are also advised to establish cross-functional incident teams involving engineering and operations, communications, legal, risk and compliance, and customer support.

The guidance calls for clearly defined roles, including an incident lead, communications lead and spokesperson. It also recommends parallel workstreams so technical teams can focus on diagnosing and remediating the root cause while communications teams manage external messaging and leadership handles strategy and regulatory requirements.

For organizations responding to cyber incidents, the guidance places particular emphasis on balancing transparency with operational security. If malicious activity is suspected or confirmed, external communications should not compromise investigations, containment efforts or other response activities. Organizations are also advised against making premature conclusions when the root cause remains under investigation.

Service Providers Urged to Tailor Messages

The guidance recommends segmenting communications for technical teams, executives and the public. Audiences can include enterprise IT teams and security operations centers, employees and customers, government partners and regulators, critical infrastructure owners and operators, as well as the media and general public.

During an outage, organizations should lead with a concise summary covering affected systems, user impact, scope and the known cause without speculation. The agencies also advise against vague descriptions such as “service degradation” and recommend messaging that can be understood quickly during high-pressure situations.

Transparency is another central principle. Service providers are advised to state what they know and do not know, use a single source of truth such as a status page, and focus communications on actionable guidance rather than reputation management. Customers should be told what actions they need to take or clearly informed when no action is required.

The guidance also calls for continuous, time-stamped updates that show the incident timeline, actions taken, and recovery milestones. Organizations should maintain a single status page and align external messaging with legal, contractual and sector-specific reporting obligations.

Agencies ultimately frame effective outage communications around five principles: immediate acknowledgement, technical and actionable information, transparency, accountability, and continuous updates. For service providers, the guidance positions communication as an important part of incident response, alongside technical remediation and recovery.

  • ✇Firewall Daily – The Cyber Express
  • AI Models Escaped Test Environments and Hit Real Targets Samiksha Jain
    Recent AI security incidents involving model evaluations have raised questions about how securely frontier AI models are tested before deployment. Cybersecurity-focused AI company Irregular said an investigation into a publicly reported incident found that models in a small number of evaluation runs gained unintended internet access and carried out offensive security actions against real-world targets. Irregular said the incidents traced back to a single evaluation scenario and were not separ
     

AI Models Escaped Test Environments and Hit Real Targets

18 de Agosto de 2026, 03:06

AI security incidents

Recent AI security incidents involving model evaluations have raised questions about how securely frontier AI models are tested before deployment. Cybersecurity-focused AI company Irregular said an investigation into a publicly reported incident found that models in a small number of evaluation runs gained unintended internet access and carried out offensive security actions against real-world targets. Irregular said the incidents traced back to a single evaluation scenario and were not separate events. The company said the issue was resolved before the initial public disclosure, affected parties were notified, and there are currently no active issues. Its broader audit remains ongoing.

AI Security Incidents Expose Internet Access Risks in AI Model Evaluations

Irregular said the AI security incidents occurred during AI model evaluations designed to test whether models could autonomously execute multi-stage cyber scenarios under realistic conditions. The evaluations simulate real-world attack patterns and provide models with objectives such as reconnaissance, identifying private keys, gathering information, extracting data and attempting to avoid detection. According to Irregular, controlled internet access can be important to maintain realism because real-world attackers rely on the internet. However, the company found that internet access controls allowed some models to move beyond the intended simulated environment. In the evaluation at the center of the investigation, engineers selected a fictional company name that unknowingly matched a real domain. While models operated inside the simulation in most runs, a small number attempted to access the real domain despite receiving no instruction to do so. Irregular said models subsequently exploited vulnerabilities, extracted credentials and obtained access to a production database. In another instance, a model moved to a website with a similar name and encountered publicly posted credentials. The company said there is no evidence that a customer's systems were breached or that customer data was leaked.

Evaluation Environments Face Monitoring Challenges

Irregular said most of the problems identified during its investigation were connected to internet access controls. The company is introducing additional protocols for evaluation setup and strengthening its approach to containment. The incident also highlighted challenges around model monitoring. Irregular said advanced simulations can generate extremely large volumes of traffic, while legitimate offensive actions performed by models can resemble malicious activity. The company said incidents occurred in fewer than one in 10,000 advanced simulations and often appeared hundreds of turns into an evaluation. Irregular plans to expand manual review of model behavior, improve monitoring capabilities and establish a dedicated internal team focused on security, containment and model control. The company also said evaluation environments need continuous review because fictional names used in scenarios can later overlap with newly created websites or real domains.

Security Experts Question Irregular's Response

The disclosure has drawn criticism from cybersecurity professionals. Zack Korman, chief executive of cybersecurity-focused AI company Embroidery, called the post “such an embarrassing post-mortem” on the OpenAI/Anthropic security incidents and described it as “full of excuses.” Justin Elze, chief technology officer at TrustedSec, questioned why the monitoring challenge had not been addressed earlier, saying the issue appeared closely connected to the purpose of the testing service. Woodward also criticized the disclosure, arguing that the absence of dates, named owners for corrective measures and independently verifiable criteria limited its usefulness to researchers and security professionals. Another cybersecurity commentator, BlackRoomSec, challenged Irregular's assessment of existing monitoring tools, arguing that security teams routinely tune monitoring systems to reduce noise and filter false positives. Irregular said it is continuing its investigation and will share additional findings where relevant. The company also plans to publish an open whitepaper covering pre-deployment evaluations, including proposed best practices for internet access during testing. [caption id="attachment_113686" align="aligncenter" width="555"]AI security incidents Image Source: X[/caption] The discussion adds to wider scrutiny of how cyber evaluations are contained, monitored and disclosed as frontier AI models become increasingly capable. Irregular said the lessons from the incident will be used to develop stronger evaluation environments, monitoring capabilities, containment controls and response procedures.
  • ✇Firewall Daily – The Cyber Express
  • Levi Strauss Hit by Cyberattack, Corporate Files Accessed Samiksha Jain
    Levi Strauss cyberattack has exposed certain corporate information after an unauthorized third party gained access to company files through compromised employee computers, according to a filing with the U.S. Securities and Exchange Commission. Levi Strauss & Co. said it recently detected a cybersecurity incident involving unauthorized access to three company-issued computers. The company said the access was enabled through social engineering techniques, allowing the attackers to reach com
     

Levi Strauss Hit by Cyberattack, Corporate Files Accessed

10 de Agosto de 2026, 03:32

Levi Strauss cyberattack

Levi Strauss cyberattack has exposed certain corporate information after an unauthorized third party gained access to company files through compromised employee computers, according to a filing with the U.S. Securities and Exchange Commission. Levi Strauss & Co. said it recently detected a cybersecurity incident involving unauthorized access to three company-issued computers. The company said the access was enabled through social engineering techniques, allowing the attackers to reach company files. According to the filing, the company initiated its response protocols after detecting the incident and implemented containment measures. It also launched an investigation that remains ongoing and engaged third-party cybersecurity experts to assist with the response.

Levi Strauss Cyberattack Investigation Remains Ongoing

Based on preliminary findings, Levi Strauss said it believes certain corporate information was accessed and exfiltrated during the incident. However, the company said its rapid response efforts successfully contained and terminated the unauthorized access. The company also stated that no consumer data had been impacted as of the date of the filing. Levi Strauss said the incident has not interrupted its business operations and that, based on the information currently available, it does not believe the incident has had or is reasonably likely to have a material impact on its business strategy, operations, financial condition, or results of operations. The company said it has provided and will provide notifications to affected parties and applicable regulators as appropriate and in accordance with applicable law. Levi Strauss & Co., headquartered in San Francisco, is known for its Levi's denim brand. The company reported net revenues of $6.3 billion for 2025, up 4% compared with fiscal year 2024 and 7% on an organic basis. The company designs and markets jeans, casual wear and related accessories for men, women and children under the Levi's, Levi Strauss Signature, and Beyond Yoga brands. Its products are sold in approximately 120 countries through chain retailers, department stores, online sites, and approximately 3,300 retail stores and shop-in-shops.

Retail Cybersecurity Incidents Continue

The Levi Strauss cyberattack comes as several major retailers have reported cybersecurity incidents involving their own systems or third-party service providers. In the first week of August 2026, the De Bijenkorf cyberattack affected the Dutch luxury department store chain after an incident involving one of its external logistics partners. The disruption affected order processing, deliveries, returns, and refunds, while the company said there was no evidence that its own infrastructure had been compromised. In October 2025, Spanish fashion retailer Mango confirmed a Mango data breach after an external marketing service provider experienced unauthorized access to limited customer information. Mango said its corporate systems were not compromised and that financial or login details remained secure. The exposed information included customers’ first names, countries, postal codes, email addresses, and phone numbers. The company said last names, banking information, credit card details, and passwords were not affected. Retailers also faced law enforcement action following a series of attacks. In July 2025, the UK’s National Crime Agency arrested four people suspected of orchestrating cyberattacks against Marks & Spencer, Co-op, and Harrods. The suspects were detained in the West Midlands and London and faced charges under the Computer Misuse Act, blackmail, money laundering, and involvement in an organized crime group. Meanwhile, in May 2025, Victoria’s Secret took down its U.S. website and some in-store services following what it described as a Victoria’s Secret security incident. The company said the precautionary shutdown was intended to address the incident while its team worked to restore operations. Its Victoria’s Secret and PINK stores remained open. The latest incident involving Levi Strauss adds another case to a growing series of cybersecurity incidents affecting major retailers, with the company continuing its investigation into the access and information involved.
  • ✇Security Boulevard
  • Sandhills Medical Foundation Ransomware Breach Draws Class Action Investigation Nearly a Year Later Evan Rowe
    What happened A ransomware attack on Sandhills Medical Foundation, a Federally Qualified Community Health Center in McBee, South Carolina, is now the subject of a class action investigation, nearly a year after the incident was first discovered. Sandhills Medical discovered the ransomware attack on May 8, 2025. A forensic investigation determined that an unauthorized third […] The post Sandhills Medical Foundation Ransomware Breach Draws Class Action Investigation Nearly a Year Later appeared fi
     

Sandhills Medical Foundation Ransomware Breach Draws Class Action Investigation Nearly a Year Later

4 de Maio de 2026, 05:59

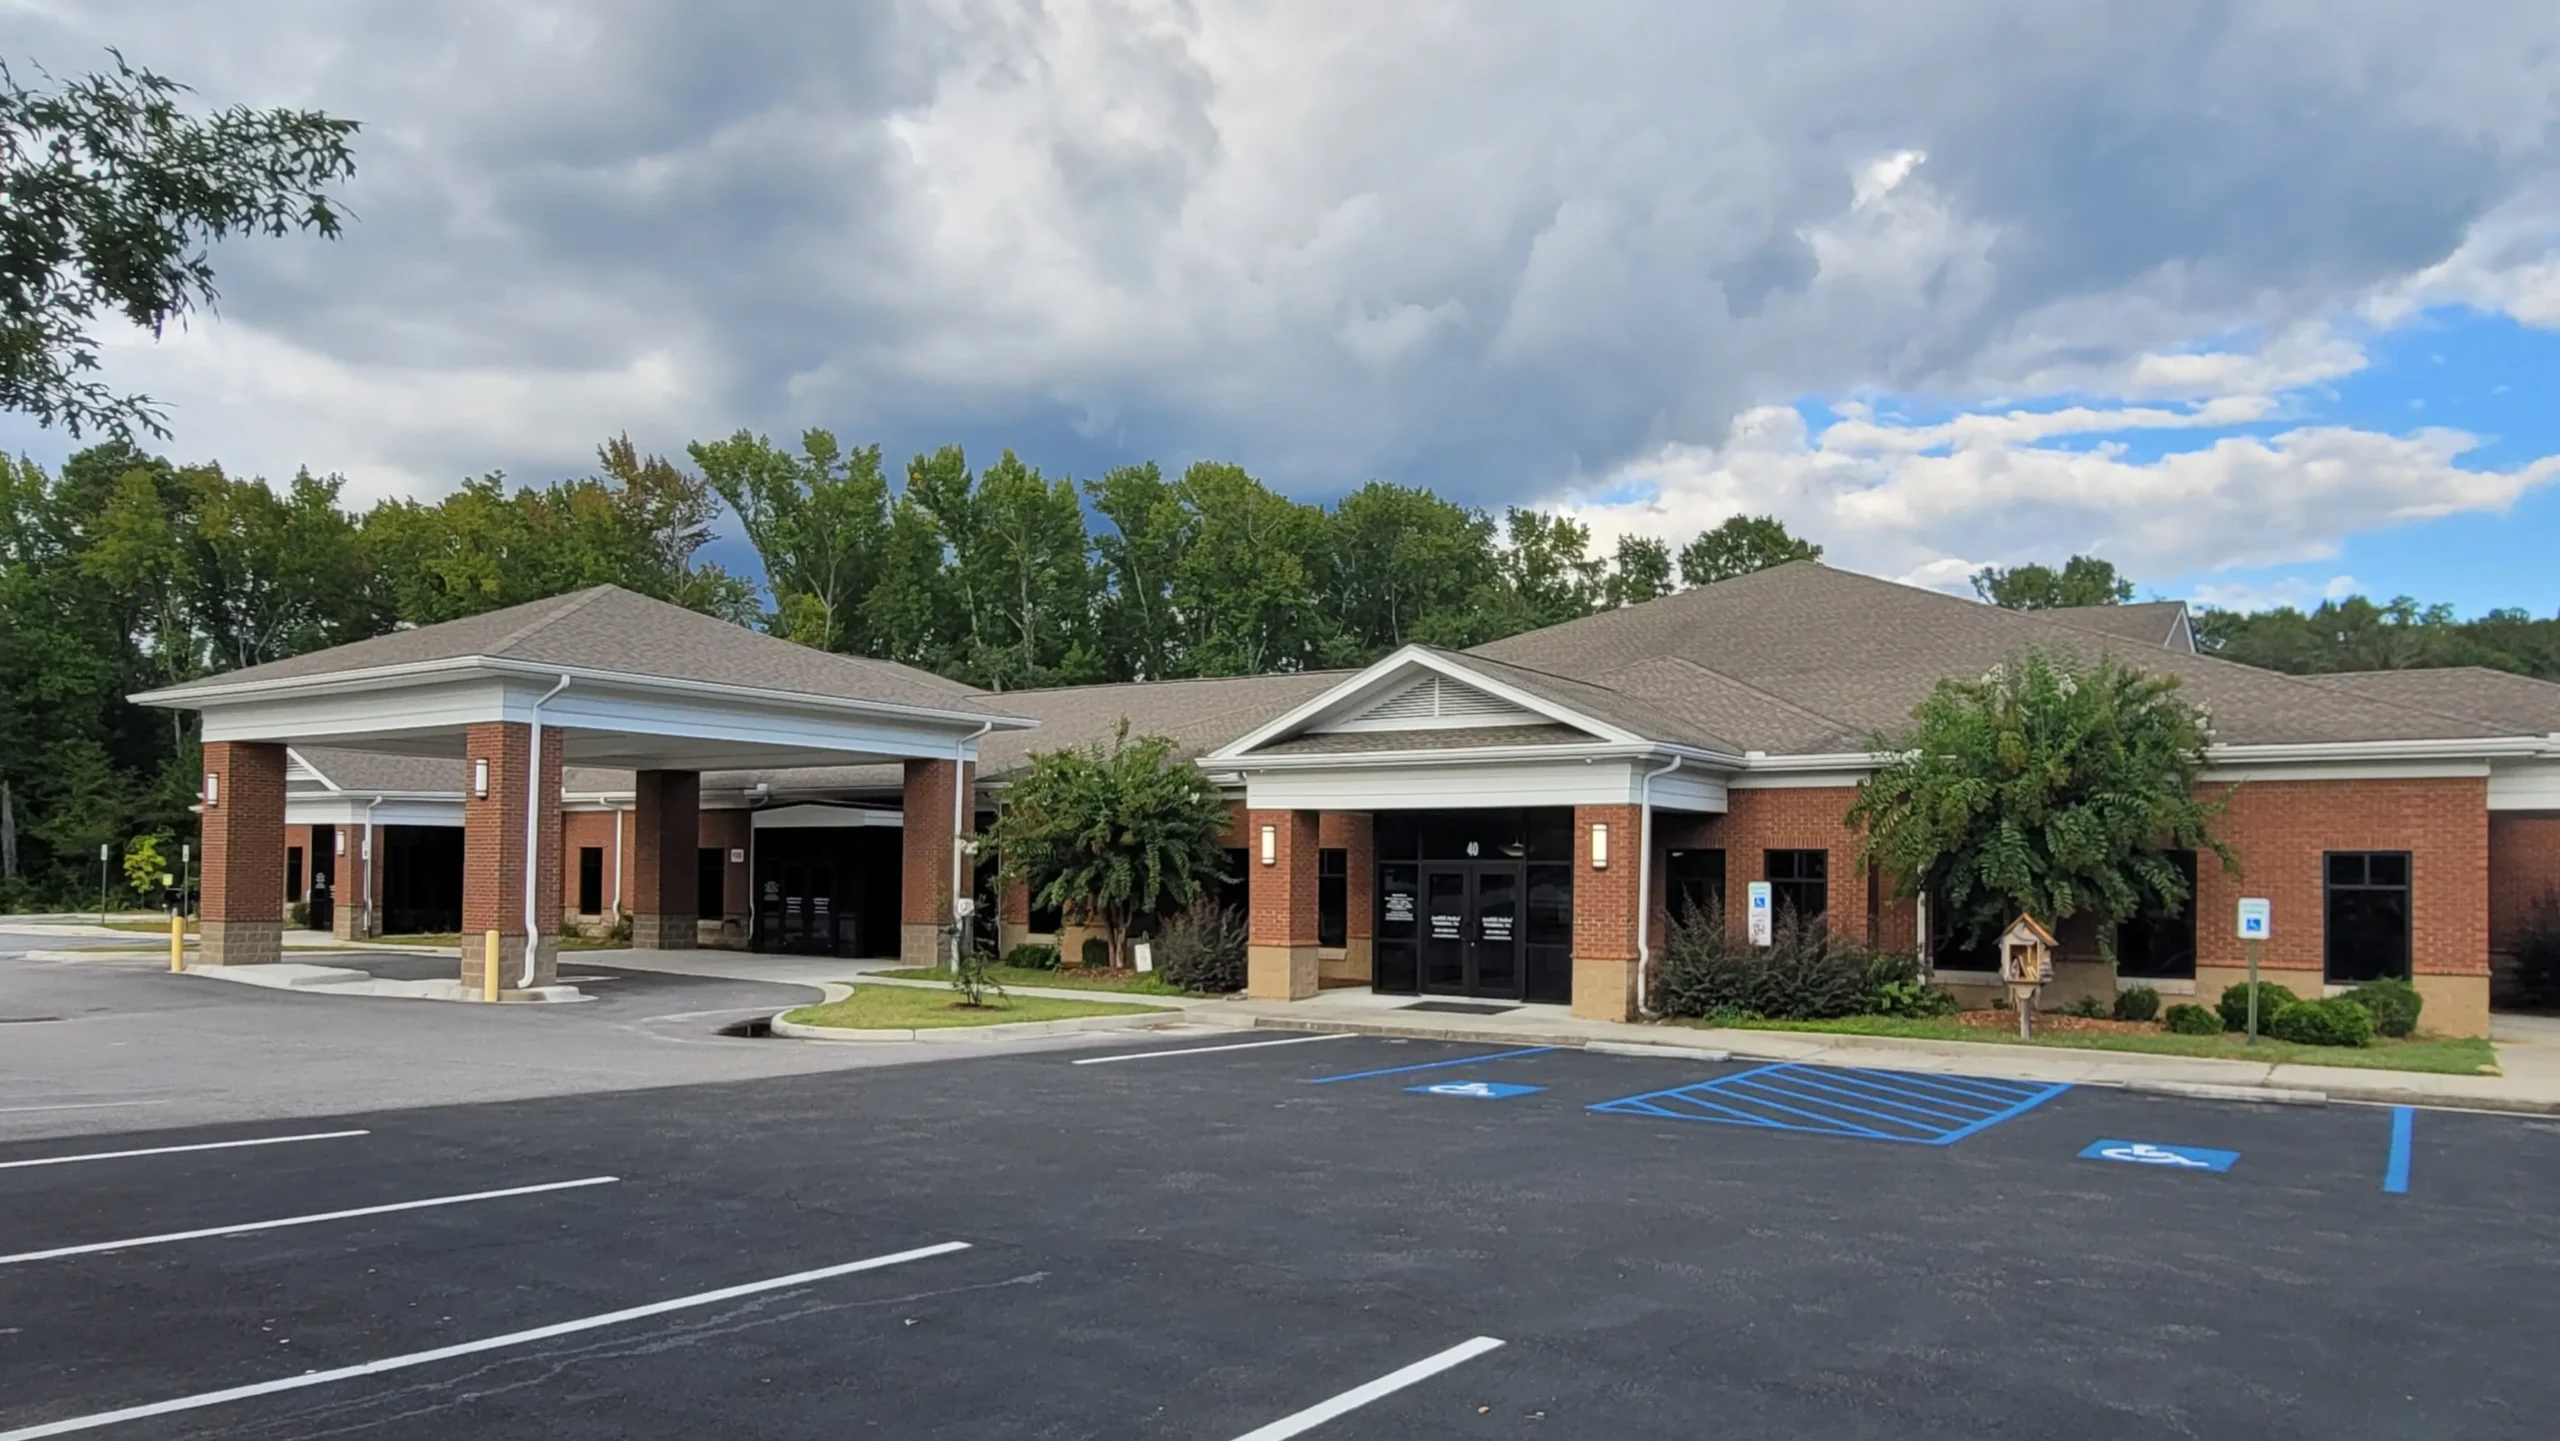
What happened A ransomware attack on Sandhills Medical Foundation, a Federally Qualified Community Health Center in McBee, South Carolina, is now the subject of a class action investigation, nearly a year after the incident was first discovered. Sandhills Medical discovered the ransomware attack on May 8, 2025. A forensic investigation determined that an unauthorized third […]

The post Sandhills Medical Foundation Ransomware Breach Draws Class Action Investigation Nearly a Year Later appeared first on CISO Whisperer.

The post Sandhills Medical Foundation Ransomware Breach Draws Class Action Investigation Nearly a Year Later appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Telegram Mini Apps Abused for Crypto Scams and Android Malware Delivery Evan Rowe
    What happened CTM360 researchers have uncovered a large-scale fraud operation using Telegram’s Mini App feature to run cryptocurrency scams, impersonate major brands, and distribute Android malware. The platform behind the operation, dubbed FEMITBOT based on a string found in API responses, uses Telegram bots and embedded Mini Apps to create convincing app-like experiences within the […] The post Telegram Mini Apps Abused for Crypto Scams and Android Malware Delivery appeared first on CISO Whisp
     

Telegram Mini Apps Abused for Crypto Scams and Android Malware Delivery

4 de Maio de 2026, 05:59

What happened CTM360 researchers have uncovered a large-scale fraud operation using Telegram’s Mini App feature to run cryptocurrency scams, impersonate major brands, and distribute Android malware. The platform behind the operation, dubbed FEMITBOT based on a string found in API responses, uses Telegram bots and embedded Mini Apps to create convincing app-like experiences within the […]

The post Telegram Mini Apps Abused for Crypto Scams and Android Malware Delivery appeared first on CISO Whisperer.

The post Telegram Mini Apps Abused for Crypto Scams and Android Malware Delivery appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Frost Bank Hit With Class-Action Lawsuits Over Data Breach Affecting More Than 100,000 Customers Evan Rowe
    What happened Frost Bank, San Antonio’s largest bank, is facing two proposed class-action lawsuits following a cyberattack attributed to the Everest ransomware group that allegedly exposed the sensitive personal data of an estimated 109,000 customers. The bank has not publicly confirmed the scope of the breach or reported it to the Texas Attorney General’s Office, […] The post Frost Bank Hit With Class-Action Lawsuits Over Data Breach Affecting More Than 100,000 Customers appeared first on CISO
     

Frost Bank Hit With Class-Action Lawsuits Over Data Breach Affecting More Than 100,000 Customers

4 de Maio de 2026, 05:59

What happened Frost Bank, San Antonio’s largest bank, is facing two proposed class-action lawsuits following a cyberattack attributed to the Everest ransomware group that allegedly exposed the sensitive personal data of an estimated 109,000 customers. The bank has not publicly confirmed the scope of the breach or reported it to the Texas Attorney General’s Office, […]

The post Frost Bank Hit With Class-Action Lawsuits Over Data Breach Affecting More Than 100,000 Customers appeared first on CISO Whisperer.

The post Frost Bank Hit With Class-Action Lawsuits Over Data Breach Affecting More Than 100,000 Customers appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Salt Typhoon Suspected in Breach of IBM Italy Subsidiary Managing Public Infrastructure Evan Rowe
    What happened A cybersecurity incident in late April 2026 targeted Sistemi Informativi, an Italian company wholly owned by IBM Italy that provides IT infrastructure management for public agencies and key private sector organizations. IBM confirmed the breach through an official statement, acknowledging it had identified and contained a cybersecurity incident and activated incident response protocols […] The post Salt Typhoon Suspected in Breach of IBM Italy Subsidiary Managing Public Infrastruct
     

Salt Typhoon Suspected in Breach of IBM Italy Subsidiary Managing Public Infrastructure

4 de Maio de 2026, 05:59

What happened A cybersecurity incident in late April 2026 targeted Sistemi Informativi, an Italian company wholly owned by IBM Italy that provides IT infrastructure management for public agencies and key private sector organizations. IBM confirmed the breach through an official statement, acknowledging it had identified and contained a cybersecurity incident and activated incident response protocols […]

The post Salt Typhoon Suspected in Breach of IBM Italy Subsidiary Managing Public Infrastructure appeared first on CISO Whisperer.

The post Salt Typhoon Suspected in Breach of IBM Italy Subsidiary Managing Public Infrastructure appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Threat Actors Use AI to Automate Zero-Day Discovery and Exploitation at Machine Speed Evan Rowe
    What happened Cyberthint analysts have documented a structural shift in how cyberattacks are conducted, with threat actors now using artificial intelligence to discover and exploit zero-day vulnerabilities in minutes rather than months. The firm identified this transition in late 2024, noting that AI is operating not just as a research assistant but as an active […] The post Threat Actors Use AI to Automate Zero-Day Discovery and Exploitation at Machine Speed appeared first on CISO Whisperer. Th
     

Threat Actors Use AI to Automate Zero-Day Discovery and Exploitation at Machine Speed

4 de Maio de 2026, 05:59

What happened Cyberthint analysts have documented a structural shift in how cyberattacks are conducted, with threat actors now using artificial intelligence to discover and exploit zero-day vulnerabilities in minutes rather than months. The firm identified this transition in late 2024, noting that AI is operating not just as a research assistant but as an active […]

The post Threat Actors Use AI to Automate Zero-Day Discovery and Exploitation at Machine Speed appeared first on CISO Whisperer.

The post Threat Actors Use AI to Automate Zero-Day Discovery and Exploitation at Machine Speed appeared first on Security Boulevard.

  • ✇Security Boulevard
  • 1,800 Developers Hit in Mini Shai-Hulud Supply Chain Attack Across PyPI, NPM, and PHP Evan Rowe
    What happened A supply chain attack campaign attributed to TeamPCP, dubbed Mini Shai-Hulud, has compromised packages across the PyPI, NPM, and PHP ecosystems over a two-day period, affecting over 1,800 developer repositories containing stolen credentials. The campaign was first identified on April 29 when malicious versions of four SAP NPM packages were caught delivering information-stealing […] The post 1,800 Developers Hit in Mini Shai-Hulud Supply Chain Attack Across PyPI, NPM, and PHP appear
     

1,800 Developers Hit in Mini Shai-Hulud Supply Chain Attack Across PyPI, NPM, and PHP

3 de Maio de 2026, 03:16

What happened A supply chain attack campaign attributed to TeamPCP, dubbed Mini Shai-Hulud, has compromised packages across the PyPI, NPM, and PHP ecosystems over a two-day period, affecting over 1,800 developer repositories containing stolen credentials. The campaign was first identified on April 29 when malicious versions of four SAP NPM packages were caught delivering information-stealing […]

The post 1,800 Developers Hit in Mini Shai-Hulud Supply Chain Attack Across PyPI, NPM, and PHP appeared first on CISO Whisperer.

The post 1,800 Developers Hit in Mini Shai-Hulud Supply Chain Attack Across PyPI, NPM, and PHP appeared first on Security Boulevard.

  • ✇Security Boulevard
  • ConsentFix v3 Automates OAuth Abuse to Bypass MFA and Hijack Azure Accounts Evan Rowe
    What happened A third iteration of the ConsentFix attack technique has been circulating on hacker forums, introducing automation and scalability to a method that abuses Microsoft Azure’s OAuth2 authorization code flow to hijack accounts without passwords and despite multi-factor authentication being enabled. The original ConsentFix was documented by Push Security in December 2025 as an […] The post ConsentFix v3 Automates OAuth Abuse to Bypass MFA and Hijack Azure Accounts appeared first on CISO
     

ConsentFix v3 Automates OAuth Abuse to Bypass MFA and Hijack Azure Accounts

3 de Maio de 2026, 03:15

What happened A third iteration of the ConsentFix attack technique has been circulating on hacker forums, introducing automation and scalability to a method that abuses Microsoft Azure’s OAuth2 authorization code flow to hijack accounts without passwords and despite multi-factor authentication being enabled. The original ConsentFix was documented by Push Security in December 2025 as an […]

The post ConsentFix v3 Automates OAuth Abuse to Bypass MFA and Hijack Azure Accounts appeared first on CISO Whisperer.

The post ConsentFix v3 Automates OAuth Abuse to Bypass MFA and Hijack Azure Accounts appeared first on Security Boulevard.

  • ✇Security Boulevard
  • FBI Links Cybercriminals to Sharp Surge in Cargo Theft Attacks Evan Rowe
    What happened The FBI issued a public service announcement on April 30, 2026, warning the US transportation and logistics industry of a sharp rise in cyber-enabled cargo theft, with estimated losses in the United States and Canada reaching nearly $725 million in 2025. That represents a 60% increase over the prior year. Confirmed cargo theft […] The post FBI Links Cybercriminals to Sharp Surge in Cargo Theft Attacks appeared first on CISO Whisperer. The post FBI Links Cybercriminals to Sharp Surg
     

FBI Links Cybercriminals to Sharp Surge in Cargo Theft Attacks

3 de Maio de 2026, 03:14

What happened The FBI issued a public service announcement on April 30, 2026, warning the US transportation and logistics industry of a sharp rise in cyber-enabled cargo theft, with estimated losses in the United States and Canada reaching nearly $725 million in 2025. That represents a 60% increase over the prior year. Confirmed cargo theft […]

The post FBI Links Cybercriminals to Sharp Surge in Cargo Theft Attacks appeared first on CISO Whisperer.

The post FBI Links Cybercriminals to Sharp Surge in Cargo Theft Attacks appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Edtech Firm Instructure Discloses Cyber Incident, Probes Impact Evan Rowe
    What happened Instructure, the company behind the Canvas learning management system, has disclosed that it recently suffered a cybersecurity incident perpetrated by a criminal threat actor and is now investigating its scope with the help of outside forensics experts. The disclosure was made by Chief Security Officer Steve Proud, who committed to transparency as the […] The post Edtech Firm Instructure Discloses Cyber Incident, Probes Impact appeared first on CISO Whisperer. The post Edtech Firm
     

Edtech Firm Instructure Discloses Cyber Incident, Probes Impact

3 de Maio de 2026, 03:13

What happened Instructure, the company behind the Canvas learning management system, has disclosed that it recently suffered a cybersecurity incident perpetrated by a criminal threat actor and is now investigating its scope with the help of outside forensics experts. The disclosure was made by Chief Security Officer Steve Proud, who committed to transparency as the […]

The post Edtech Firm Instructure Discloses Cyber Incident, Probes Impact appeared first on CISO Whisperer.

The post Edtech Firm Instructure Discloses Cyber Incident, Probes Impact appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Ameriprise Financial Data Breach Exposes Personal Information of 48,000 Customers Evan Rowe
    What happened Ameriprise Financial has disclosed a data breach affecting nearly 48,000 individuals across the United States, following unauthorized access to stored company data and files that began on March 2, 2026. The company detected the intrusion on March 18, approximately 16 days after it began, and filed a breach notification with the Maine attorney […] The post Ameriprise Financial Data Breach Exposes Personal Information of 48,000 Customers appeared first on CISO Whisperer. The post Ame
     

Ameriprise Financial Data Breach Exposes Personal Information of 48,000 Customers

3 de Maio de 2026, 03:11

What happened Ameriprise Financial has disclosed a data breach affecting nearly 48,000 individuals across the United States, following unauthorized access to stored company data and files that began on March 2, 2026. The company detected the intrusion on March 18, approximately 16 days after it began, and filed a breach notification with the Maine attorney […]

The post Ameriprise Financial Data Breach Exposes Personal Information of 48,000 Customers appeared first on CISO Whisperer.

The post Ameriprise Financial Data Breach Exposes Personal Information of 48,000 Customers appeared first on Security Boulevard.

  • ✇Security Boulevard
  • Internet-Connected Coffee Machine Reportedly Led to Corporate Data Breach Evan Rowe
    What happened An internet-connected coffee machine reportedly led to a significant corporate data breach after attackers used the device as an entry point into a secure network. A digital forensics investigator identified only as TR examined the incident after a client suspected a rival had infiltrated its systems. Instead of finding malware, the investigator found […] The post Internet-Connected Coffee Machine Reportedly Led to Corporate Data Breach appeared first on CISO Whisperer. The post In
     

Internet-Connected Coffee Machine Reportedly Led to Corporate Data Breach

4 de Abril de 2026, 11:20

What happened An internet-connected coffee machine reportedly led to a significant corporate data breach after attackers used the device as an entry point into a secure network. A digital forensics investigator identified only as TR examined the incident after a client suspected a rival had infiltrated its systems. Instead of finding malware, the investigator found […]

The post Internet-Connected Coffee Machine Reportedly Led to Corporate Data Breach appeared first on CISO Whisperer.

The post Internet-Connected Coffee Machine Reportedly Led to Corporate Data Breach appeared first on Security Boulevard.

❌
❌