❌

Visualização normal

Antes de ontemCybersecurity News
  • ✇Firewall Daily – The Cyber Express
  • OLVX Marketplace Dismantled After Joint FBI-North Macedonia Probe Samiksha Jain
    The OLVX marketplace, an illicit online platform used to sell stolen personal data, login credentials and cybercrime tools, has been dismantled following a coordinated investigation by North Macedonia’s Ministry of Interior and the US Federal Bureau of Investigation (FBI). Authorities have filed criminal charges against a 20-year-old suspect from the Tetovo area, alleging involvement in computer fraud, misuse of personal data and the production and distribution of child sexual abuse material.
     

OLVX Marketplace Dismantled After Joint FBI-North Macedonia Probe

15 de Outubro de 2026, 02:31

OLVX marketplace

The OLVX marketplace, an illicit online platform used to sell stolen personal data, login credentials and cybercrime tools, has been dismantled following a coordinated investigation by North Macedonia’s Ministry of Interior and the US Federal Bureau of Investigation (FBI). Authorities have filed criminal charges against a 20-year-old suspect from the Tetovo area, alleging involvement in computer fraud, misuse of personal data and the production and distribution of child sexual abuse material. According to North Macedonia’s Ministry of Interior, the Cybercrime and Digital Forensics Sector submitted the charges against E.A., from the village of Golema Rečica, to the Basic Public Prosecutor’s Office in Tetovo. The investigation focused on the suspect’s alleged administration of the OLVX marketplace, which operated between 2023 and 2025. The operation began after the FBI provided intelligence that prompted a joint investigation into the platform and its associated criminal activities.

OLVX Marketplace Offered More Than 1,500 Stolen Login Credentials

Evidence gathered during the investigation indicated that the suspect administered domains and websites associated with OLVX between 2023 and 2025. The platform functioned as a cybercrime marketplace, where users could buy and sell stolen digital information, software tools and services intended to facilitate criminal activity. The marketplace primarily served cybercriminals seeking personal information and stolen login credentials that could provide access to victims’ online accounts and computer networks. During its operation, more than 1,500 sets of stolen login credentials were offered for sale, according to the authorities. The platform also used a cryptocurrency-based payment arrangement. Rather than operating an escrow service, as many underground marketplaces do, OLVX allowed users to load funds onto the site and use those funds to pay one another. The arrangement provided an alternative payment mechanism for transactions conducted through the platform.

Telegram Group Allegedly Offered Cybercrime Tools

The investigation also examined the suspect’s alleged activities on Telegram. Authorities said that between 2025 and 2026, the suspect administered an illicit online group called ONEMILI, which offered software tools and services designed to facilitate cybercrime. These included fraudulent refund schemes, according to the Ministry of Interior. Investigators also obtained evidence indicating that the suspect had acquired and possessed child sexual abuse material (CSAM) for personal use through Telegram. The allegations form part of the criminal charges filed with the prosecutor’s office. The available information does not specify whether the suspect has been arrested or whether court proceedings have begun.

FBI Investigation Highlights Cross-Border Cybercrime Enforcement

The operation marks the first jointly coordinated cybercrime operation between North Macedonia’s Ministry of Interior and the FBI, according to the ministry. The case demonstrates how intelligence sharing between law enforcement agencies can support investigations into online platforms operating across jurisdictions. Authorities have increasingly targeted illicit online marketplaces that facilitate the exchange of stolen information, cybercrime tools and tactics. Over the past five years, law enforcement agencies have taken down dozens of such marketplaces, which have become focal points for cybercriminals trading data and services. In a separate development, Microsoft announced the takedown of three popular Chinese phishing sites used by cybercriminals to send hundreds of millions of malicious messages impersonating more than 75,000 organizations worldwide. Although the cases involve different platforms and activities, both illustrate law enforcement and technology companies’ efforts to disrupt online infrastructure used for cybercrime. The North Macedonia investigation highlights the role of international cooperation in identifying platform administrators and disrupting services linked to the trade in stolen data. The Ministry of Interior said its Cybercrime and Digital Forensics Sector would continue working to combat cybercrime, protect personal data and improve digital safety.
  • ✇Security Affairs
  • Hunt.io Finds New Infrastructure Of BraZetsu Access Broker Months Before Disclosure Pierluigi Paganini
    Hunt.io traced BraZetsu ‘s infrastructure and found that hosting patterns and certificate data remained useful after published IOCs became outdated. Group-IB researchers published a detailed writeup on BraZetsu back on August 31, naming it a Python framework compiled with Nuitka and tying it to a Brazilian actor called Exilware with high confidence. Hunt.io checked whether the published indicators still held up against its own certificate data. What they found is that the infrastructure had
     

Hunt.io Finds New Infrastructure Of BraZetsu Access Broker Months Before Disclosure

8 de Outubro de 2026, 14:47

Hunt.io traced BraZetsu ‘s infrastructure and found that hosting patterns and certificate data remained useful after published IOCs became outdated.

Group-IB researchers published a detailed writeup on BraZetsu back on August 31, naming it a Python framework compiled with Nuitka and tying it to a Brazilian actor called Exilware with high confidence. Hunt.io checked whether the published indicators still held up against its own certificate data. What they found is that the infrastructure had already moved on, quietly, months before anyone wrote about it.

BraZetsu is an initial access broker tool that breaks into Windows machines, checks them for ERP software, SCADA traces, EDR products, and certificate files, then packages the information for sale.

The group behind it, called Infected Marketplace, charges a deposit of about 5.80 Brazilian reais to let buyers browse the listings. The buyer who later deploys ransomware or steals money from a bank account doesn’t need to know how BraZetsu works. They simply buy a machine that has already been compromised.

Hunt.io’s approach was narrow on purpose. Instead of reversing the binary again, they took the hostnames and IP address Group-IB had already published and ran them against their own TLS certificate inventory.

“We didn’t reverse the binary again. We took the published indicators and checked what our certificate inventory still shows.” Hunt.io states. “The premise is narrow. An operator who keeps a panel and a command channel under the same apex, with Let’s Encrypt off port 443, leaves a more stable trail in the certificate inventory than the address of the month.”

Binaries can change all the time. A hostname linked to a valid TLS certificate is much harder to replace.

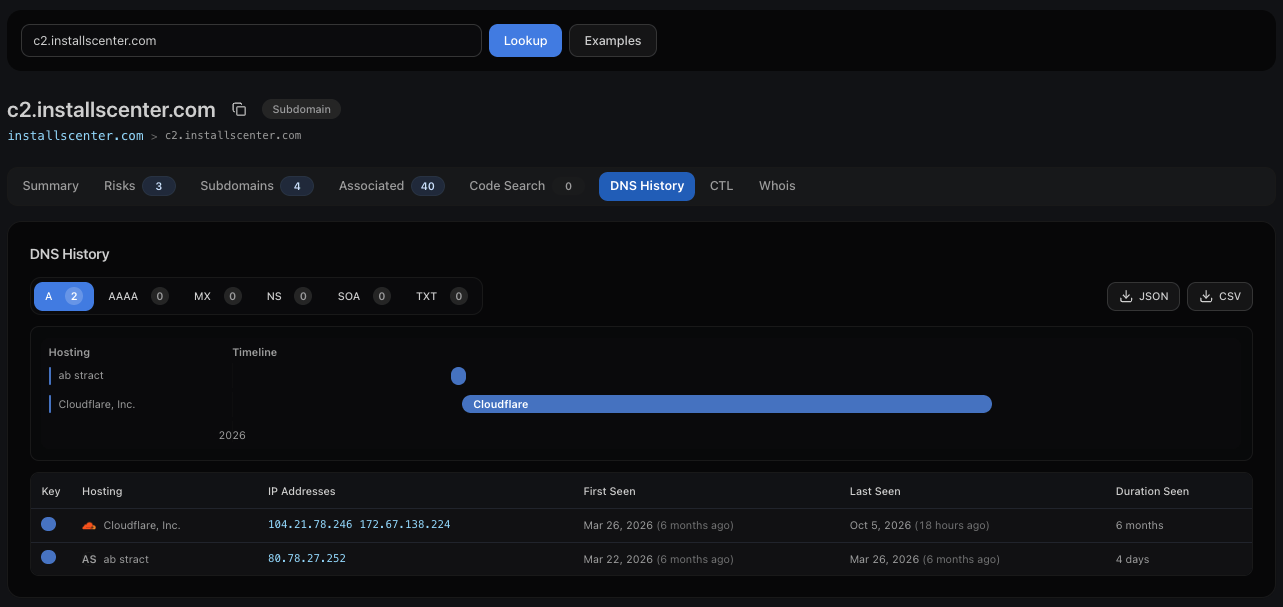
That approach worked quickly. The command server hostname mentioned in the August report, c2.installscenter.com, had already been using TLS on a second server since April 4, almost five months before the report was published. Researchers found it on the same IP address as the control panel hostname, painel.installscenter.com. Both were hosted by the same Swedish provider, Njalla.

The original seed IP, a Contabo server, tells its own story. From January through early February it served Contabo’s default factory hostname, boring and unremarkable. Then on February 11, right around when Group-IB dates the first BraZetsu version, the certificate switched to painel.seu-dominio.com, a Portuguese placeholder name literally meaning “your domain” lifted straight from hosting tutorials. That name showed up 17 separate times over five weeks, every two to four days, which is a strong signal of a panel someone actually kept running, not a page thrown up for one night.

When the operators eventually moved providers, they kept the exact same habits. The new host came alive on March 21, the very day the installscenter.com domain was registered, running the identical Hestia Control Panel setup with the same painel prefix. Different hosting company, same fingerprint.

“Passive DNS helps explain it. Our records show c2.installscenter[.]com resolving to 80.78.27[.]252 between 22 and 26 March, and to Cloudflare (104.21.78.246, 172.67.138.224) from 26 March on.” states the report. “The only A record we have for painel.installscenter[.]com is Cloudflare, from 21 March.”
The real lesson here isn’t about BraZetsu specifically, it’s about what actually survives a public takedown report. Hashes rotated across five different versions in just four months, useless as a long-term detection signal. What held steady from February through June was the naming convention and hosting pattern itself, a panel prefix on a nonstandard port, running on a VPS configured with Hestia Control Panel.

Hunt.io’s conclusion lands on a point worth remembering for anyone building detection rules off a threat intel report: don’t chase the IP of the month, chase the pattern. Before publishing, the researchers notified the relevant national CERTs and confirmed no victim data was recovered during the investigation, which is the responsible way to handle infrastructure still potentially active.

“The public reporting gave us three things to work from: the C2 hostname, the IP tied to it early in the year, and the shop both of them served. Our certificate inventory showed what happened to that hostname after the first VPS went quiet. It showed up on a new host in a different provider, with a control panel on the same apex.” concludes the report. “The TLS services on 80.78.27[.]252 went quiet after 20 June. The pattern is more stable: a painel. or c2. prefix on a port that isn’t 443, on a VPS running Hestia Control Panel. It held from February to June across two providers, and that’s what we’d build detection on, not the IP.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, BraZetsu)

❌
❌