Bank of America has a message for its customers: please, for the love of God, stop handing your banking passwords to your AI assistant. And if your robot does something daft with your money? That's your problem, not theirs.
Meanwhile, a company that promised to rescue ransomware victims without paying the criminals stands accused of... paying the criminals. ProPublica's Renee Dudley was on the case years before the indictment.
Plus, Dropzone AI's Edward Wu asks what happens when AI models
Bank of America has a message for its customers: please, for the love of God, stop handing your banking passwords to your AI assistant. And if your robot does something daft with your money? That's your problem, not theirs.
Meanwhile, a company that promised to rescue ransomware victims without paying the criminals stands accused of... paying the criminals. ProPublica's Renee Dudley was on the case years before the indictment.
Plus, Dropzone AI's Edward Wu asks what happens when AI models break out of their test environment and go hacking, and whether AI agents can help overstretched security teams keep up.
All this and more in episode 491 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Renee Dudley.
Dutch spies, Russian hackers and Jared Kushner’s iPhone. It sounds like the ingredients for a thriller, but according to claims in a new book the US President's son-in-law may have been hacked twice. Is any of it true, and what does it tell us about the phones in our pockets?
Meanwhile, James Ball explains that of the internet’s most trusted security keys were protected by numbers so small that one of them was... four. Yes, "4". And then, of course, to make the week worse we suffered a PHPoca
Dutch spies, Russian hackers and Jared Kushner’s iPhone. It sounds like the ingredients for a thriller, but according to claims in a new book the US President's son-in-law may have been hacked twice. Is any of it true, and what does it tell us about the phones in our pockets?
Meanwhile, James Ball explains that of the internet’s most trusted security keys were protected by numbers so small that one of them was... four. Yes, "4". And then, of course, to make the week worse we suffered a PHPocalpyse...
Plus, Chuck Randolph of 360 Privacy explains how the internet has made it scarily easy to put company executives and public officials in danger.
All this and more in episode 490 of the “Smashing Security” podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest James Ball.
Imagine buying a brand new hardware wallet for your cryptocurrency with the shrink-wrap still on... what could possibly be hiding inside? We break out a Geiger counter and a cat to find out.
Meanwhile, malicious ads are targeting journalists with zero-click attacks.
Plus, Origin’s Spencer Thompson reveals what AI agents are really getting up to on your employees’ laptops when nobody’s looking.
All this and more in episode 489 of the “Smashing Security” podcast with cybersecurity expert
Imagine buying a brand new hardware wallet for your cryptocurrency with the shrink-wrap still on... what could possibly be hiding inside? We break out a Geiger counter and a cat to find out.
Meanwhile, malicious ads are targeting journalists with zero-click attacks.
Plus, Origin’s Spencer Thompson reveals what AI agents are really getting up to on your employees’ laptops when nobody’s looking.
All this and more in episode 489 of the “Smashing Security” podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Lianne Potter.
A ransomware negotiator attended a cybersecurity conference, only to be arrested by the FBI in connection with its investigation into the ShinyHunters gang.
Meanwhile, hackers get the keys to ASOS's app and the chance to message every single customer. What did they say? And how did the company respond? We have thoughts.
All this and more is discussed in episode 488 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Paul Ducklin
A ransomware negotiator attended a cybersecurity conference, only to be arrested by the FBI in connection with its investigation into the ShinyHunters gang.
Meanwhile, hackers get the keys to ASOS's app and the chance to message every single customer. What did they say? And how did the company respond? We have thoughts.
All this and more is discussed in episode 488 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Paul Ducklin.
Microsoft's Twitter account, with its 13 million followers, was hijacked by a paperclip. There was no ransomware or data theft, just Clippy, a dodgy crypto coin, and a corporate apology that wasn't from Microsoft either.
Meanwhile, UK losses from hacked email and social media accounts have rocketed by 417%, as scammers pose as your friends to flog you tickets to gigs that don't exist.
Plus, Hack The Box's Christine Bartlett joins us for a featured interview to ask what happens when AI agen
Microsoft's Twitter account, with its 13 million followers, was hijacked by a paperclip. There was no ransomware or data theft, just Clippy, a dodgy crypto coin, and a corporate apology that wasn't from Microsoft either.
Meanwhile, UK losses from hacked email and social media accounts have rocketed by 417%, as scammers pose as your friends to flog you tickets to gigs that don't exist.
Plus, Hack The Box's Christine Bartlett joins us for a featured interview to ask what happens when AI agents join your security team, and whether anyone has thought to give them a performance review.
A store in Auckland vibe-coded itself a new website. Within hours, its inventory had somehow expanded to include a pair of crusty socks, an $850 banana, and all of New Zealand's national parks. What could possibly have gone wrong?
Meanwhile, a hacker collective backed a truck into one of the license-plate-reading Flock safety cameras popping up on American street corners, and took a very close look inside.
All this and more in episode 486 of the "Smashing Security" podcast with cybersecuri
A store in Auckland vibe-coded itself a new website. Within hours, its inventory had somehow expanded to include a pair of crusty socks, an $850 banana, and all of New Zealand's national parks. What could possibly have gone wrong?
Meanwhile, a hacker collective backed a truck into one of the license-plate-reading Flock safety cameras popping up on American street corners, and took a very close look inside.
All this and more in episode 486 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Dave Bittner.
Researchers wanted to test if LG's smart TVs come with any security risks - but their lawyers noticed a snag: the terms and conditions would forbid it. So they came up with a solution. They got plastered before setting up the TV, on the reasoning that you can't be legally bound to a contract you agreed to while drunk. What they discovered will make you look at your TV rather differently...
Meanwhile, awful Android malware with the audacious name "Awesome" (in Indonesian) is doing the rounds,
Researchers wanted to test if LG's smart TVs come with any security risks - but their lawyers noticed a snag: the terms and conditions would forbid it. So they came up with a solution. They got plastered before setting up the TV, on the reasoning that you can't be legally bound to a contract you agreed to while drunk. What they discovered will make you look at your TV rather differently...
Meanwhile, awful Android malware with the audacious name "Awesome" (in Indonesian) is doing the rounds, stealing your data, demanding a ransom, and then giving you a "jump scare"...
Plus, in our featured interview, Andy Hornegold of Intruder explains why the mid-market is where cybercriminals are having the most fun right now - and how AI is helping attackers get from "first foot in the door" to "full ransomware disaster" in less than a working day.
All this and more in episode 485 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Lianne Potter.
When a chap called Matt noticed his Bluetooth headphones wouldn't switch to his phone, he was surprised to realise the reason was a single AliExpress webpage sitting open in his browser - playing nothing at all, at zero volume. And yet somehow his hardware could hear it. Audio fingerprinting is one of the sneakiest tracking tricks on the web.
Meanwhile, the intelligence agencies of the "Five Eyes" (not Five Guys) have got together and published advice on how companies should communicate after
When a chap called Matt noticed his Bluetooth headphones wouldn't switch to his phone, he was surprised to realise the reason was a single AliExpress webpage sitting open in his browser - playing nothing at all, at zero volume. And yet somehow his hardware could hear it. Audio fingerprinting is one of the sneakiest tracking tricks on the web.
Meanwhile, the intelligence agencies of the "Five Eyes" (not Five Guys) have got together and published advice on how companies should communicate after a cyber attack. The summary? For the love of God, stop calling every breach "sophisticated."
All this and more in episode 484 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Danny Palmer.
You've had your iPhone stolen. A day later, you get a text from Apple saying they've found it, and a very helpful woman called Alice from Apple Support calls to walk you through recovering it. She's polite. She's professional. But she is not from Apple. She's not even human. And she's about to break into your iPhone.
Meanwhile, OpenAI, Anthropic, and Meta have all announced - with varying degrees of drama - that their AI agents have "broken out of the sandbox" and gone hacking. James takes a
You've had your iPhone stolen. A day later, you get a text from Apple saying they've found it, and a very helpful woman called Alice from Apple Support calls to walk you through recovering it. She's polite. She's professional. But she is not from Apple. She's not even human. And she's about to break into your iPhone.
Meanwhile, OpenAI, Anthropic, and Meta have all announced - with varying degrees of drama - that their AI agents have "broken out of the sandbox" and gone hacking. James takes a step back and asks the awkward question: is this really an emergent AI apocalypse, or did they just leave the door open?
All this and more in episode 483 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest James Ball.
This weekly roundup highlights a broad range of cybersecurity and technology developments affecting cloud identity infrastructure, social media platforms, businesses, digital assets, and international law enforcement.
From a critical Microsoft Entra ID vulnerability exploited before remediation to a global crackdown on West African cybercrime networks, recent developments demonstrate how attackers continue to target both technical systems and human trust.
The latest developments also sh
This weekly roundup highlights a broad range of cybersecurity and technology developments affecting cloud identity infrastructure, social media platforms, businesses, digital assets, and international law enforcement. From a critical Microsoft Entra ID vulnerability exploited before remediation to a global crackdown on West African cybercrime networks, recent developments demonstrate how attackers continue to target both technical systems and human trust.The latest developments also show that cybersecurity risks are expanding alongside the rapid adoption of cloud services and artificial intelligence. Organizations are facing threats involving identity infrastructure, autonomous AI agents, software vulnerabilities, digital transactions, online fraud, and the misuse of emerging technologies.
The Cyber Express Weekly Roundup
Microsoft Confirms Exploited Entra ID Flaw
Microsoft confirmed that a critical vulnerability in Entra ID, CVE-2026-69836, was exploited before the flaw was fixed server-side. The vulnerability carries a CVSS score of 10.0 and could allow unauthenticated attackers to achieve remote code execution, potentially affecting Microsoft’s cloud-based identity infrastructure. Read more...
New Zealand Proposes Social Media Ban for Under-16s
New Zealand has introduced legislation that would require high-risk social media platforms to prevent users under the age of 16 from accessing their services. Proposed age-verification methods could include digital identification, facial age estimation, or official identification documents. Read more...
Cyble and DRONA Launch AI Cyber Defense Initiative in India
Cyble and DRONA Cyber Solutions have launched an AI-powered cybersecurity initiative in Ahmedabad aimed at helping mid-sized businesses detect, investigate, and contain cyber threats. The initiative combines threat intelligence, AI-driven investigations, and endpoint enforcement to provide organizations with faster and more coordinated responses to security incidents. Read more...
AI Agents Could Create New Cybersecurity Risks
Adarsh Kant Sinha, CEO of ANVE.AI, warned that autonomous AI agents could introduce significant new cybersecurity risks as organizations increasingly allow them to interact with business-critical systems. AI agents may gain access to email, customer relationship management platforms, cloud infrastructure, and financial systems, potentially creating new avenues for misuse or compromise. Read more...
Ledger said it fixed a clear-signing vulnerability in its Ethereum application approximately two weeks before security firm TestMachine publicly disclosed the issue. The vulnerability could potentially allow a malicious application to display one transaction to a user while preparing a different transaction for signing. Read more...
Global Crackdown Nets 58 Arrests in West African Crime Networks
An eight-month international law enforcement operation led by INTERPOL has resulted in 58 arrests and the identification of 263 suspects across 22 countries. Operation Jackal IV targeted West African criminal networks involved in cyber-enabled fraud, money laundering, romance scams, and investment scams. Read more...
Weekly Cybersecurity Takeaway
This week’s developments demonstrate that cybersecurity threats are crossing organizational, technological, and geographical boundaries, affecting cloud identity systems, artificial intelligence, digital platforms, cryptocurrency applications, and international financial crime.Organizations should prioritize strong identity and access controls, rapid vulnerability remediation, careful management of AI-agent permissions, secure integrations, human oversight, and continuous threat monitoring. As autonomous technologies become more deeply integrated into business operations and cybercriminal networks continue to operate across borders, security teams must adapt to a threat landscape that is becoming broader, more interconnected, and increasingly difficult to contain.
A hacker calling themselves "CYBERLEEK" has been leaking gameplay footage from GTA 6 ahead of its official reveal this week - but they're not asking Rockstar Games for a ransom. Instead, they've launched their own cryptocurrency, promising to release ever more juicy clips from a virtual strip club...
Meanwhile, your smart TV might be doing more than binge-watching Netflix while you sleep. We explore the shadowy world of "residential proxies" - how they end up inside home routers, smart TVs, a
A hacker calling themselves "CYBERLEEK" has been leaking gameplay footage from GTA 6 ahead of its official reveal this week - but they're not asking Rockstar Games for a ransom. Instead, they've launched their own cryptocurrency, promising to release ever more juicy clips from a virtual strip club...
Meanwhile, your smart TV might be doing more than binge-watching Netflix while you sleep. We explore the shadowy world of "residential proxies" - how they end up inside home routers, smart TVs, and IoT devices, and why an entire criminal economy is quietly running through your internet connection.
All this and more in episode 482 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Paul Ducklin.
At Black Hat this month, a group of security researchers took a $9,000 robot dog, plugged Google's AI into its brain, and jailbroke it by telling it - with a completely straight face - that it was a Pokemon. What followed involved a wall, a blue ice chest, and anyone in the room wearing white shoes. Oh, and did we mention you can buy a flamethrower attachment?
Meanwhile, in Salzburg, 280 gold statuettes of Mozart have vanished from the streets. This has happened to the same artist before. Org
At Black Hat this month, a group of security researchers took a $9,000 robot dog, plugged Google's AI into its brain, and jailbroke it by telling it - with a completely straight face - that it was a Pokemon. What followed involved a wall, a blue ice chest, and anyone in the room wearing white shoes. Oh, and did we mention you can buy a flamethrower attachment?
Meanwhile, in Salzburg, 280 gold statuettes of Mozart have vanished from the streets. This has happened to the same artist before. Organised crime, or a publicity stunt? Jenny has thoughts - and some parallels for the world of cybersecurity.
All this and more in episode 481 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Jenny Radcliffe.
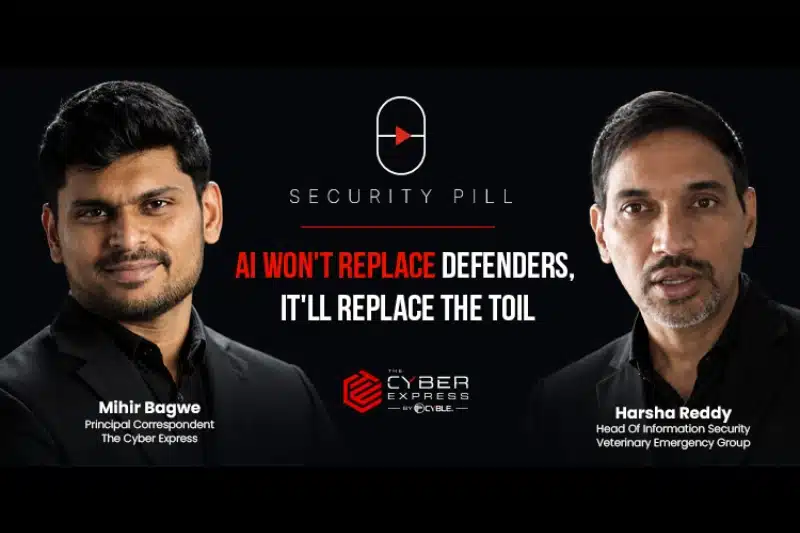
As enterprises race to bolt AI onto every business process, security leaders are being forced to answer a harder question than "should we adopt it" — it's "who's accountable when it goes wrong." To unpack this, The Cyber Express sat down with Harsha Reddy, Head of Information Security at Veterinary Emergency Group (VEG).
With nearly two decades in security leadership — including senior roles at Lixil and American Standard before joining VEG — Harsha brings a practitioner's view of where AI is g
As enterprises race to bolt AI onto every business process, security leaders are being forced to answer a harder question than "should we adopt it" — it's "who's accountable when it goes wrong." To unpack this, The Cyber Express sat down with Harsha Reddy, Head of Information Security at Veterinary Emergency Group (VEG).
With nearly two decades in security leadership — including senior roles at Lixil and American Standard before joining VEG — Harsha brings a practitioner's view of where AI is genuinely changing the CISO's job, and where it's mostly just hype and shadow adoption.
Watch the Full Interview:
Harsha Reddy Explains Why AI Will Replace Tasks, Not Defenders
Harsha pushes back on the narrative that AI will hollow out security teams, pointing to Gartner research showing that while most fields are projected to lose jobs to AI, cybersecurity is expected to gain them. In his view, the technology is mainly absorbing the "toil" — log review, alert triage, evidence gathering — that keeps analysts from actually defending.
“It's the analyst who refuses to use AI that will get replaced by an analyst who uses it,” he says.
On adoption, Reddy points to a 2024 Microsoft-LinkedIn survey in which most executives called AI critical to their business, yet a majority had no formal plan and most had employees already bringing in their own tools. That gap, he argues, is why so many organizations are now dealing with AI-related data leaks. "Many organizations started onboarding AI like software when they should be onboarding it like staff." His fix isn't more restrictions — blocking AI just pushes it into the shadows — but guardrails, an internal AI enablement committee, and measuring actual business value instead of token consumption.
The conversation also digs into deepfake-driven fraud, why training employees to spot deepfakes is “a losing bet” at machine speed, and how he decides when to greenlight a new AI tool versus telling a business unit “not yet.”
The conversation closes with our newly introduced rapid-fire round "Express Shots" — Claude vs. ChatGPT, passkeys vs. passwords, and Reddy's prediction for the biggest cybersecurity threat of 2030.
Read the latest updates Firewall Daily news and insights on The Cyber Expres, your trusted source for cybersecurity and information technology updates."
Would you like access to Anthropic's Claude at 90% off the normal price? All you have to do is redirect your traffic to a mysterious service called "Poison Claude". Only problem is that it's run by fraudsters...
Meanwhile, a phishing-as-a-service platform called "Greatness" has come up with something rather nasty: a phishing attack that doesn't need a fake website, a suspicious URL, or your password. Just a real Microsoft login page and a moment of misplaced trust - and the attackers walk off
Would you like access to Anthropic's Claude at 90% off the normal price? All you have to do is redirect your traffic to a mysterious service called "Poison Claude". Only problem is that it's run by fraudsters...
Meanwhile, a phishing-as-a-service platform called "Greatness" has come up with something rather nasty: a phishing attack that doesn't need a fake website, a suspicious URL, or your password. Just a real Microsoft login page and a moment of misplaced trust - and the attackers walk off with full access to your emails, your files, and your entire organisation.
All this and more in episode 480 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Lianne Potter.
Graham gets a phone call from the police. Well, someone who sounds convincingly like the police. There's just one small problem: what they really want is the 24-word seed key to Graham's cryptocurrency wallet.
Meanwhile, if you've stayed in a hotel recently, the free Wi-Fi you connected to might have come with an unexpected extra: an all-you-can-eat buffet of "Captive Crunch" for a Russian intelligence-linked hacking group.
And a group calling itself the "ExFilSquad" has walked off with 6
Graham gets a phone call from the police. Well, someone who sounds convincingly like the police. There's just one small problem: what they really want is the 24-word seed key to Graham's cryptocurrency wallet.
Meanwhile, if you've stayed in a hotel recently, the free Wi-Fi you connected to might have come with an unexpected extra: an all-you-can-eat buffet of "Captive Crunch" for a Russian intelligence-linked hacking group.
And a group calling itself the "ExFilSquad" has walked off with 600,000 records of the UK's teachers and head teachers from the Department for Education — sending an unusually polite ransom demand.
All this and more in episode 479 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Danny Palmer.
You've been headhunted for a great job in cryptocurrency. All you have to do is complete a short online assessment - with your webcam on, of course, so they can verify who you really are. Which is ironic, because the person recruiting you doesn't exist. And North Korean hackers using this trick have already made off with $643 million in crypto this year alone.
Meanwhile, researchers at UC San Diego have discovered that 2.2 million cars across the United States can be unlocked or immobilised b
You've been headhunted for a great job in cryptocurrency. All you have to do is complete a short online assessment - with your webcam on, of course, so they can verify who you really are. Which is ironic, because the person recruiting you doesn't exist. And North Korean hackers using this trick have already made off with $643 million in crypto this year alone.
Meanwhile, researchers at UC San Diego have discovered that 2.2 million cars across the United States can be unlocked or immobilised by anyone with a bit of Bluetooth kit - thanks to one aftermarket car alarm that made a truly spectacular cryptographic blunder. The bug has been sitting there since 2017. Nobody noticed.
All this and more in episode 478 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Paul Ducklin.
A Russian intelligence-linked hacker is arrested in Thailand while enjoying a beach holiday - and the trail of evidence that nailed him to the Russian government includes 14 separate orders of chicken McNuggets.
Meanwhile, AI music generator Suno has been hacked - and the stolen data appears to show exactly how much copyrighted music they hoovered up to train their models.
All this and more in episode 477 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Grah
A Russian intelligence-linked hacker is arrested in Thailand while enjoying a beach holiday - and the trail of evidence that nailed him to the Russian government includes 14 separate orders of chicken McNuggets.
Meanwhile, AI music generator Suno has been hacked - and the stolen data appears to show exactly how much copyrighted music they hoovered up to train their models.
All this and more in episode 477 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest James Ball.
An app has appeared in India that lets anyone with a smartphone stop a passing e-rickshaw dead in its tracks - no login, no passwords, no permissions needed.
Meanwhile, Geoff - swimming in money and Lamborghinis, as all published authors are - has been on the receiving end of a slew of AI-generated scam pitches from fake book marketing experts. Rather than ignore them, he's been playing them at their own game...
All this and more in this episode of the "Smashing Security" podcast with cyb
An app has appeared in India that lets anyone with a smartphone stop a passing e-rickshaw dead in its tracks - no login, no passwords, no permissions needed.
Meanwhile, Geoff - swimming in money and Lamborghinis, as all published authors are - has been on the receiving end of a slew of AI-generated scam pitches from fake book marketing experts. Rather than ignore them, he's been playing them at their own game...
All this and more in this episode of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Geoff White.
A 15-year-old boy asked a chatbot for help - and cancelled nearly 47,000 anime streaming subscriptions in under four hours. Meanwhile, researchers have documented the first fully autonomous, agentic AI-driven ransomware attack, "JadePuffer". What does this tell us about the future of cybersecurity?
Also, Apple's "Hide My Email" feature turns out to hide rather less than it promises - despite Apple knowing it has a problem for over a year.
All this and more in this episode of the "Smashing
A 15-year-old boy asked a chatbot for help - and cancelled nearly 47,000 anime streaming subscriptions in under four hours. Meanwhile, researchers have documented the first fully autonomous, agentic AI-driven ransomware attack, "JadePuffer". What does this tell us about the future of cybersecurity?
Also, Apple's "Hide My Email" feature turns out to hide rather less than it promises - despite Apple knowing it has a problem for over a year.
All this and more in this episode of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Zoë Rose.
Polymarket has built an entire business on predicting the future. So how did it manage to spectacularly fail to predict its own hack? Plus, the Google engineer with a million-dollar secret, and the curious case of the airport hairdryer.
Meanwhile, "FortiBleed" sees 75,000 Fortinet firewalls thrown wide open - and the real damage is going to roll on for years.
All this and more in episode 474 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and
Polymarket has built an entire business on predicting the future. So how did it manage to spectacularly fail to predict its own hack? Plus, the Google engineer with a million-dollar secret, and the curious case of the airport hairdryer.
Meanwhile, "FortiBleed" sees 75,000 Fortinet firewalls thrown wide open - and the real damage is going to roll on for years.
All this and more in episode 474 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Quentyn Taylor.

 Entrar