❌

Visualização normal

Ontem — 7 de Novembro de 2026Cybersecurity News
  • ✇Security | CIO
  • OpenAI buys tiny software developer to improve Codex
    OpenAI is buying Pierre Computer Company in order to incorporate the San Francisco-based software developer’s Code.Storage infrastructure layer for Git into its Codex AI-powered programming tool. Pierre Computer, whose employees number just barely in the double digits, has got plenty of clout for its small size. It’s well-known for Code.Storage offering, as well as for its open-source software libraries, Trees and Diffs, which OpenAI already uses in Codex. OpenAI has
     

OpenAI buys tiny software developer to improve Codex

6 de Novembro de 2026, 10:42

OpenAI is buying Pierre Computer Company in order to incorporate the San Francisco-based software developer’s Code.Storage infrastructure layer for Git into its Codex AI-powered programming tool.

Pierre Computer, whose employees number just barely in the double digits, has got plenty of clout for its small size. It’s well-known for Code.Storage offering, as well as for its open-source software libraries, Trees and Diffs, which OpenAI already uses in Codex.

OpenAI has experienced some of the limitations of Git itself, and its in-house engineering teams are already working to improve its support for human coders and AI agents working in parallel. Earlier this week the company described how it built a new back end for Git repositories, Pando, to enable concurrent working at scale.

The AI developer has been pushing Codex more aggressively this year: offering it to Mac users and expanding it to Windows. It cited Pierre Computer’s ability to help developers review code as one of the reasons for the acquisition. OpenAI highlighted the Diffs’ Edit mode and the recently released Highlights as components that were particularly helpful to development teams.

Announcing the deal on its news page, OpenAI set out how it would integrate the company into its existing offerings. “With the Pierre team, we wish to set the standard for modern software development: from the first branch an agent creates to that magic moment when code is deployed to the world. We want to make Codex the place where developers and agents take on their most ambitious projects.”

Neither company disclosed details of the acquisition price. OpenAI said that Code.Storage customers will be able to continue using the product until it brings the features into Codex, while Pierre Computer’s open-source projects will remain open, and OpenAI will continue to contribute to them.

This article first appeared on InfoWorld.

Antes de ontemCybersecurity News
  • ✇Cybersecurity News
  • Postman AI Plugin Hijacking Sparks Developer Outcry Do Son
    Postman AI plugin hijacking sparks controversy after the desktop app silently modifies Codex and Claude Code configs to favor its own tools. Related Posts: Apple AI Budget Cuts Target Internal Model Usage OpenAI Unveils ChatGPT Images 2.6 with Animated GIF Support ChatGPT Search Volume Reaches 20 Percent of Google The post Postman AI Plugin Hijacking Sparks Developer Outcry appeared first on Daily CyberSecurity.
     
  • ✇Security | CIO
  • How CIOs can retain control as AI writes more code
    AI is writing more code than ever. Software specialist Sonar’s 2026 State of Code Developer Survey, based on more than 1,100 professional developers, found that 72% of those who’ve tried AI coding tools now use them every day, and that today, AI now accounts for 42% of committed code, a number that’s expected to reach 65% by next year. But while developers embrace AI-enabled coding services, many professionals are uncertain about how their businesses will cope with this
     

How CIOs can retain control as AI writes more code

4 de Novembro de 2026, 07:00

AI is writing more code than ever. Software specialist Sonar’s 2026 State of Code Developer Survey, based on more than 1,100 professional developers, found that 72% of those who’ve tried AI coding tools now use them every day, and that today, AI now accounts for 42% of committed code, a number that’s expected to reach 65% by next year.

But while developers embrace AI-enabled coding services, many professionals are uncertain about how their businesses will cope with this influx of AI-generated code. Sonar’s research additionally discovered that 96% of developers don’t fully trust it, and only 48% always verify it before committing.

In fact, 38% of developers told the researchers that reviewing AI code requires more effort than analyzing code written by human colleagues. That’s a pattern recognized by Tim Chilton, a managing geospatial consultant at UK mapping agency Ordnance Survey (OS). “There’s truth in the headlines that AI can get carried away, and developers spend more time fixing the code that’s been created than not,” he says.

While that’s not a pattern he sees at the OS, Chilton says his organization is cautious about how developers use AI coding tools, and conversations with other digital leaders suggest a similar approach. AI-enabled coding is indeed almost ubiquitous, and it can allow developers to reach new, higher levels of productivity, but more doesn’t necessarily mean better code.

To ensure that such coding services produce business benefits, CIOs must take control of the development process. They should exploit agents carefully, set professional responsibilities, and establish guidelines, policies, and organization-wide training.

Exploiting the agents

Snowflake co-founder and president Benoît Dageville suggests there are two ways to view AI-powered coding. One is the scary way, where AI takes over your tasks without human input. The second is the efficient way, where AI helps you do the same things as before, but at a fraction of the cost. He’s a big believer in the latter, both for himself and his teams.

“The route depends on the organization; their application of AI coding depends on their priorities,” he says. “However, I hope that overall, AI will have a positive effect on humans. I’m using AI every day to code, and if I compare myself to one or two years ago versus now, I’m more efficient and productive, but I’m also writing five times more code.”

Steve Lucas, CEO of integration technology specialist Boomi, also notes the increase in output. He quotes research that suggests 4% of GitHub public commits are already being authored by Claude Code. That proportion is expected to rise to 20% of all daily commits by the end of this year. Staff at Boomi already use AI tools to produce more code.

“We’re writing 10 times the amount today than we did two years ago,” says Lucas. The increase in AI-enabled coding is so significant that he’s spoken with Boomi chief product and technology officer Ed Macosky about goals for the proportion of self-modifying code.

“I believe AI should recursively modify 80% of a software organization’s code,” Macosky says. “Infinite improvement is demanded. If AI is extraordinarily good at breaking security protocols, the only way to keep up isn’t the kind of accordion model of human code design. AI use must be linear in scale and continuous.”

Crucially, Lucas suggests using AI to check and modify that AI doesn’t mean coders go away. “In fact, I think we’ll need more engineers, not fewer,” he says. “We need these professional experts to ensure the quality of the code that’s written.”

At OS, Chilton uses Coco, Snowflake’s coding agent. The tool does as much as 90% of a development task that he would otherwise complete from scratch. “It’s taken an hour to finish, instead of weeks or never,” he says, reflecting on the power of AI coding services.

However, the tool’s influence is carefully constrained. The agent doesn’t work in isolation, and Chilton checks its output in detail. He says all organizations need a similar process and should value experienced professionals who can use AI coding tools effectively.

“If you’re giving a tool to someone who isn’t capable of checking an agent’s work, as a digital leader, you run the risk of putting too much faith in AI just running with its output,” he says. “I think that’s a big risk, so there’s still a need for experienced developers.” 

Setting clear responsibilities

While placing humans in the loop can help ensure AI-enabled code is safe and effective, developers shouldn’t be weighed down by their new management responsibilities.

Gill Haus, CIO at Chase, the consumer banking arm of JPMorgan Chase & Co, says AI coding benefits can only be realized when agents are introduced with a strong focus on automating supporting technology and processes, which reduces the need for too much human input.

“If you have 12,000 engineers, they can write 12,000 engineers’ worth of code in a day,” he says. “If those 12,000 engineers have agentic technology, they can write much more. But if you don’t have automation left to right with confidence, you create more manual processes. You can’t move as quickly since there are only so many humans you can put in the middle.”

Haus says Chase never releases services in production that don’t pass its high bar for quality and security. Strong engineering practices, pipelines, and architecture, plus a tried-and-tested approach to automation, can help ensure AI coding produces solid outputs without a burdensome amount of human intervention.

“We’re focused on effective automation so we’re able to unleash this technology safely and effectively,” he says. “This is something many other companies should be focused on if they aren’t already, because otherwise you can’t keep up with the pace of change.”

François-Xavier Pierrel, group chief data and ad tech officer at French TV network TF1, is another digital leader who says maintaining control as AI writes more code means keeping the human in the loop in a clearly defined manner. His team documents agentic processes using Atlassian project management and collaboration tools, such as Confluence.

Pierrel says policy management is crucial as the agentic transformation gathers pace.  One key step is ensuring professionals who use agents conform to internal standards. Smart businesses set policies that state clearly when staff can explore an agent, delegate work to it, or release it in production.

“We don’t have hundreds of agents deployed yet,” he says. “But the moment you reach a certain level of volume, if you don’t have compliance and policies in place, AI becomes a critical mess, and then it can be disruptive in a negative way.”

Building strong foundations

Kirsty Roth, chief operating officer at content and technology specialist Thomson Reuters, agrees digital leaders must be proactive. Her firm’s explorations with models and agents suggest that AI can help with time-intensive coding processes, such as writing. This capability means her organization carefully considers the roles people fulfil.

“In the last 12 months, we’ve put lots of thought into where we’re seeing benefits,” she says. “It’s great AI can do some of the coding work, but what does that mean for people’s jobs? We used to have thousands of engineers. Do we now need more architects or product people?”

Roth refers to security. While cyber is always a priority for Thomson Reuters, the firm dedicates significant resources to controlling threats in the AI age. Developing high-level development and security skills requires a concerted effort. Yet Roth says ensuring people have the right skills to manage AI is in many ways a familiar IT trend.

“All this effort is no different than digital, cloud, mobile, social, or other big tech trends,” she says. “They all take several years to have an impact as the initial hype comes, and then you’ve got to work through the reality and think about how you upskill people for the new world.”

Crucially, coding is no longer the sole preserve of the software developer. AI coding tools make it much easier for non-IT professionals to vibe code applications. Tal Carmi, CIO at technology specialist WalkMe, says non-developers can create useful tools. However, effective outputs rely on a careful balance between enablement and guidance.

He adds that most of these employees don’t need in-depth capabilities, such as a database or a content delivery network. Instead, non-IT staff require a dedicated place to upload their products. WalkMe’s engineering specialists ask key questions to ensure their outputs are safe, considering credentials and potentially problematic packages.

“You need to add guardrails,” he says. “A lot of the work for in-house engineers is shifting from building to testing. The people who aren’t coders don’t necessarily have security in mind.”

The key takeaway, suggests Emmanuel Frenehard, chief digital officer at biopharmaceutical giant Sanofi, is that digital leaders must help professionals feel comfortable. Successful digital leaders ensure the business generates value from agents, and his firm is helping its staff, particularly its developers, to embrace these tools.

“I genuinely worry for professionals who don’t use AI to code, because in five years, they may not have jobs,” he says. “So we’re guiding, coaching, and training them, but people must take the journey. The train has left the station. You can decide to be on it, or just look at it.”

  • ✇Cybersecurity News
  • Stack Overflow Question Decline Accelerates in AI Era Do Son
    The dramatic Stack Overflow question decline dropped monthly posts below 1,000 as developers embrace autonomous AI coding agents. Related Posts: Trezor Hardware Wallet Implant Found in Reseller Units Microsoft 365 Storage Changes Reduce Family Cloud Quotas Claude CarPlay Update Adds Hands-Free AI Voice The post Stack Overflow Question Decline Accelerates in AI Era appeared first on Daily CyberSecurity.
     

EMBRACE Flaws in 5 AI Coding Tools Enable Code Execution and File Theft

EMBRACE affects AI coding tools Cursor, GitHub Copilot, Codex, VS Code and Claude Desktop, enabling code execution, file theft and browser address-bar spoofing.

Security Teams and AI Tools: Why Executives Won’t Adopt What They Can’t Control

Executives need visibility into workplace AI, clear data controls and limits on agent access before approving wider adoption. Here’s what businesses need in place.

Inside the Phishing Marketplace Microsoft Just Took Down: 2,300 Fake Templates Exposed

15 de Outubro de 2026, 05:22

Microsoft cybercrime crackdown

A text alert about an undelivered package or an unpaid toll may look like a one-off scam. A new Microsoft cybercrime crackdown shows it is often the visible end of a much larger operation. Microsoft and Health-ISAC, a global non-profit that helps health sector organizations share cyber threat information and improve operational resilience, have moved to dismantle three services, YAM Store, CoGUI and Iron Man, that supplied criminals worldwide with accounts, hosting and tools to build fake websites and online identities. Since January 2026, the three services have collectively enabled more than one billion malicious messages targeting over 75,000 organizations worldwide. More than 750 million of those messages were aimed at Microsoft customers alone. Consumers, healthcare organizations, financial institutions and other businesses in more than 150 countries were targeted, generating tens of millions of dollars for the operators.

How the Microsoft Cybercrime Crackdown Began

The investigation started in late 2025 after Japan's National Police Agency (NPA) alerted Microsoft to malicious messaging campaigns targeting people in Japan. The NPA continued providing intelligence and investigative support throughout the probe as partners traced those campaigns back to the businesses supplying criminals around the world. Investigators expected to find individual campaigns. Instead, they traced the activity to a sprawling Chinese-language marketplace that was difficult for non-native-speaking investigators to penetrate. The probe widened to include the Japan Cybercrime Control Center (JC3), Resecurity, Cloudflare, Oracle, Proofpoint and TRM Labs. Drawing on its network of more than 130 member organizations, JC3 linked what appeared to be separate incidents into a broader pattern of scams against Japanese companies and financial institutions. Health-ISAC provided insight into the impact on healthcare organizations.

What the Microsoft Cybercrime Crackdown Uncovered

YAM Store operated much like an online shop. Customers could browse products, compare prices and buy fraudulent Microsoft and Google accounts along with ready-made scam tools, including those used for credential theft. Controlled purchases by Microsoft helped confirm how it worked. In some cases, operators bought internet domains that legitimate organizations had allowed to expire, often in sectors such as non-profits and education, with specialized product offerings for those sectors. They rebuilt the websites to make those organizations appear active, then used them to fraudulently obtain Microsoft 365 accounts for resale. The infrastructure sold through YAM Store was frequently paired with CoGUI. This service supplied ready-made websites and messages impersonating companies, banks, government agencies and other trusted organizations. Rather than build fraudulent sites themselves, criminals could quickly deploy pages designed to steal passwords, payment details and personal data. CoGUI became one of the most widely used offerings in the ecosystem, particularly targeting victims in Japan and the United States. [caption id="attachment_114817" align="aligncenter" width="600"]Microsoft cybercrime crackdown Image Source: https://blogs.microsoft.com/[/caption] By mid-2026, CoGUI was increasingly being replaced by Iron Man, which offered thousands of phishing templates tailored to specific brands, industries and countries. Criminals could use them to quickly deploy email, text and web content. Through test purchases and work with Resecurity, investigators identified more than 2,300 templates impersonating banks, retailers, healthcare providers, transportation authorities, police departments and government agencies across more than 150 countries. Others mimicked airlines, telecommunications companies and parcel delivery services. Some were built for government impersonation scams, using the look of official authority to pressure victims into paying or sharing sensitive information. Microsoft noted that an organization appearing in these templates does not mean its systems were compromised.

Court Order Backs Microsoft Cybercrime Crackdown

Acting on an order from the United States District Court for the Southern District of Florida, Microsoft and Health-ISAC seized and redirected domains that formed part of the infrastructure behind the three services. Microsoft has disabled more than 20,000 accounts linked to YAM Store and is blocking more than 100,000 domains used for impersonation and fraud, while removing infrastructure hosted on its services. Microsoft also shared intelligence with the U.S. Secret Service and international law enforcement partners. Investigators used AI tools to connect accounts, websites and infrastructure that initially appeared unrelated. The case reflects a trend highlighted in this year's Microsoft Digital Defense Report: modern fraud increasingly relies on businesses and services that help criminals reach more victims. No single organization saw the full picture of this transnational cybercrime network, and uncovering it required two-way information sharing across industries and borders. YAM Store, CoGUI and Iron Man are only part of a larger criminal ecosystem. Still, the Microsoft cybercrime crackdown makes it harder for criminals to obtain the accounts, tools and infrastructure that keep scam messages flowing. Microsoft Threat Intelligence has published a blog with further details on the network and steps customers can take to protect themselves.
  • ✇Firewall Daily – The Cyber Express
  • OLVX Marketplace Dismantled After Joint FBI-North Macedonia Probe Samiksha Jain
    The OLVX marketplace, an illicit online platform used to sell stolen personal data, login credentials and cybercrime tools, has been dismantled following a coordinated investigation by North Macedonia’s Ministry of Interior and the US Federal Bureau of Investigation (FBI). Authorities have filed criminal charges against a 20-year-old suspect from the Tetovo area, alleging involvement in computer fraud, misuse of personal data and the production and distribution of child sexual abuse material.
     

OLVX Marketplace Dismantled After Joint FBI-North Macedonia Probe

15 de Outubro de 2026, 02:31

OLVX marketplace

The OLVX marketplace, an illicit online platform used to sell stolen personal data, login credentials and cybercrime tools, has been dismantled following a coordinated investigation by North Macedonia’s Ministry of Interior and the US Federal Bureau of Investigation (FBI). Authorities have filed criminal charges against a 20-year-old suspect from the Tetovo area, alleging involvement in computer fraud, misuse of personal data and the production and distribution of child sexual abuse material. According to North Macedonia’s Ministry of Interior, the Cybercrime and Digital Forensics Sector submitted the charges against E.A., from the village of Golema Rečica, to the Basic Public Prosecutor’s Office in Tetovo. The investigation focused on the suspect’s alleged administration of the OLVX marketplace, which operated between 2023 and 2025. The operation began after the FBI provided intelligence that prompted a joint investigation into the platform and its associated criminal activities.

OLVX Marketplace Offered More Than 1,500 Stolen Login Credentials

Evidence gathered during the investigation indicated that the suspect administered domains and websites associated with OLVX between 2023 and 2025. The platform functioned as a cybercrime marketplace, where users could buy and sell stolen digital information, software tools and services intended to facilitate criminal activity. The marketplace primarily served cybercriminals seeking personal information and stolen login credentials that could provide access to victims’ online accounts and computer networks. During its operation, more than 1,500 sets of stolen login credentials were offered for sale, according to the authorities. The platform also used a cryptocurrency-based payment arrangement. Rather than operating an escrow service, as many underground marketplaces do, OLVX allowed users to load funds onto the site and use those funds to pay one another. The arrangement provided an alternative payment mechanism for transactions conducted through the platform.

Telegram Group Allegedly Offered Cybercrime Tools

The investigation also examined the suspect’s alleged activities on Telegram. Authorities said that between 2025 and 2026, the suspect administered an illicit online group called ONEMILI, which offered software tools and services designed to facilitate cybercrime. These included fraudulent refund schemes, according to the Ministry of Interior. Investigators also obtained evidence indicating that the suspect had acquired and possessed child sexual abuse material (CSAM) for personal use through Telegram. The allegations form part of the criminal charges filed with the prosecutor’s office. The available information does not specify whether the suspect has been arrested or whether court proceedings have begun.

FBI Investigation Highlights Cross-Border Cybercrime Enforcement

The operation marks the first jointly coordinated cybercrime operation between North Macedonia’s Ministry of Interior and the FBI, according to the ministry. The case demonstrates how intelligence sharing between law enforcement agencies can support investigations into online platforms operating across jurisdictions. Authorities have increasingly targeted illicit online marketplaces that facilitate the exchange of stolen information, cybercrime tools and tactics. Over the past five years, law enforcement agencies have taken down dozens of such marketplaces, which have become focal points for cybercriminals trading data and services. In a separate development, Microsoft announced the takedown of three popular Chinese phishing sites used by cybercriminals to send hundreds of millions of malicious messages impersonating more than 75,000 organizations worldwide. Although the cases involve different platforms and activities, both illustrate law enforcement and technology companies’ efforts to disrupt online infrastructure used for cybercrime. The North Macedonia investigation highlights the role of international cooperation in identifying platform administrators and disrupting services linked to the trade in stolen data. The Ministry of Interior said its Cybercrime and Digital Forensics Sector would continue working to combat cybercrime, protect personal data and improve digital safety.
  • ✇Cybersecurity News
  • Codex CLI Daemon Autostart Sparks Developer Backlash Do Son
    Discover why the new Codex CLI daemon autostart feature is causing frustration among developers. Learn how this background process impacts system updates. Related Posts: Google Play AI Apps Revolutionize Android Publishing Google Gemini 4 Argon Model Officially Launches Excel Copilot AI Gains Interactive Canvas Feature The post Codex CLI Daemon Autostart Sparks Developer Backlash appeared first on Daily CyberSecurity.
     

Codex CLI Daemon Autostart Sparks Developer Backlash

Por:Do Son
14 de Outubro de 2026, 04:20

Discover why the new Codex CLI daemon autostart feature is causing frustration among developers. Learn how this background process impacts system updates.

Related Posts:

The post Codex CLI Daemon Autostart Sparks Developer Backlash appeared first on Daily CyberSecurity.

  • ✇Firewall Daily – The Cyber Express
  • South Korea’s Shinhan Bank Hack Exposes Data of 25,000 Customers Samiksha Jain
    The Shinhan Bank cyberattack has exposed personal and financial information belonging to about 25,000 customers in South Korea, with investigators examining whether advanced artificial intelligence tools were used to carry out the intrusion. The leaked information reportedly includes customers’ names, phone numbers, loan borrowing details and annual income. South Korea’s Financial Supervisory Service has launched an emergency on-site inspection as authorities investigate how the breach occurr
     

South Korea’s Shinhan Bank Hack Exposes Data of 25,000 Customers

5 de Outubro de 2026, 03:55

Shinhan Bank cyberattack

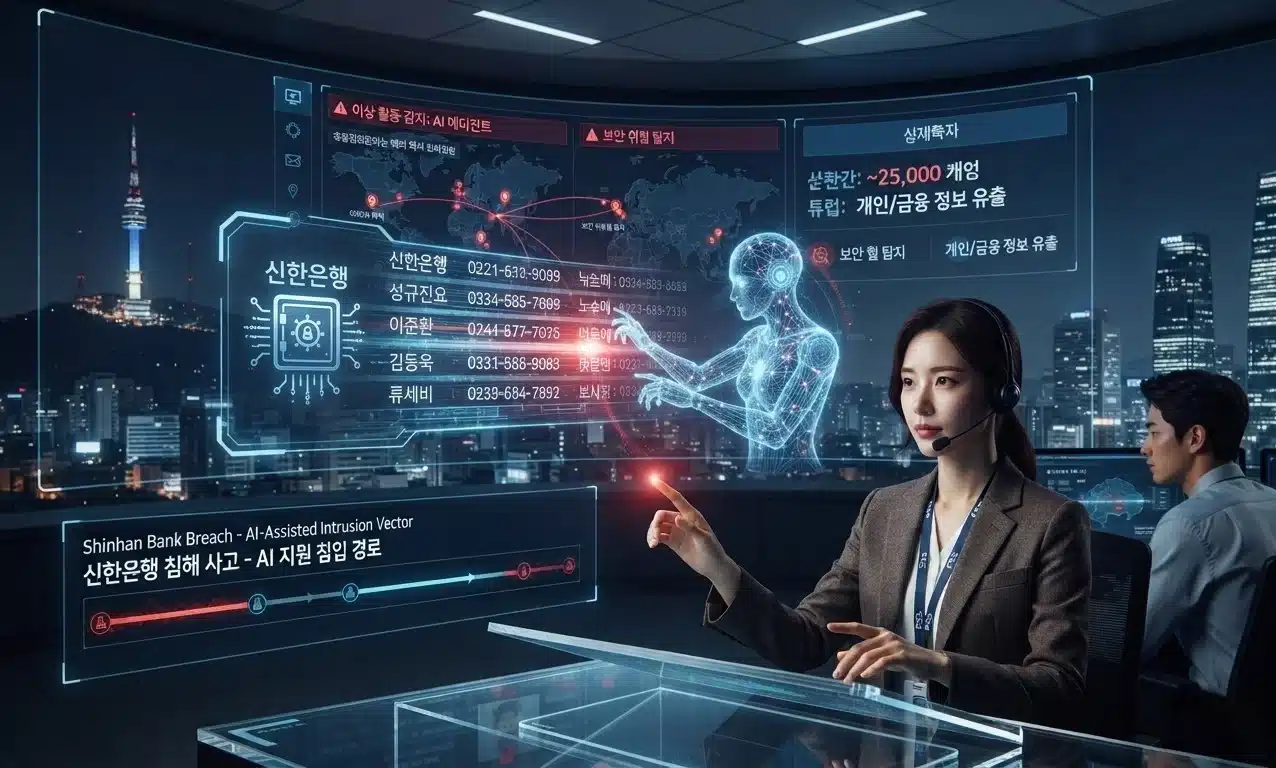
The Shinhan Bank cyberattack has exposed personal and financial information belonging to about 25,000 customers in South Korea, with investigators examining whether advanced artificial intelligence tools were used to carry out the intrusion. The leaked information reportedly includes customers’ names, phone numbers, loan borrowing details and annual income. South Korea’s Financial Supervisory Service has launched an emergency on-site inspection as authorities investigate how the breach occurred and whether the suspected use of AI points to a wider risk for financial institutions.

Shinhan Bank Cyberattack Under Investigation

Shinhan Bank said the information was leaked on Wednesday after hackers gained access to its systems. The bank immediately formed a response team and took measures aimed at limiting further damage. These measures included blocking access from external IP addresses and suspending the affected services. The bank said it had completed safety measures related to the incident. Sources cited in the reports said the attackers are suspected to be based overseas and may have used advanced AI tools during the attack. Experts said the bank may not have been specifically targeted, but could instead have been caught in attacks against vulnerable online platforms. The Financial Supervisory Service sent a team to the bank to examine the incident. Its investigation is expected to take months as officials determine the nature and extent of the data exposure.

AI Agent-Assisted Attacks Raise Concern

The suspected use of AI has added another concern to the Shinhan Bank breach. Cybersecurity experts said AI tools originally developed or shared for defensive purposes can also be adapted for malicious activity. Mun Chong-hyun, director at cybersecurity firm Genians, said several recent attacks in South Korea have involved such AI tools. He described the technology as a double-edged sword because capabilities created for cybersecurity can also be used to facilitate cybercrime. The concern is not limited to Shinhan Bank. An industry official said the wider financial sector could be exposed to AI agent-assisted attacks, and that financial institutions should conduct their own security checks to identify potential weaknesses and abnormal access attempts. The incident also highlights the type of information that can be exposed in attacks against banks. Unlike a breach involving only basic contact information, the Shinhan incident reportedly exposed both personal details and financial information.

South Korean Banks Face More Data Breaches

The Shinhan Bank cyberattack comes amid several recent incidents affecting South Korean lenders. KB Kookmin Bank said last Friday that personal information belonging to 119 customers had been leaked following an external intrusion. Hana Bank also reported a separate hack affecting 89 customers. South Korea’s Financial Services Commission has already held a meeting with local banks over the recent breaches and is expected to hold another meeting this week. The latest incidents have raised concerns about how AI-powered hacking could affect the financial sector, particularly if attackers can use automated tools to identify vulnerable systems or support attacks at greater scale. The Shinhan incident is relatively small compared with some of South Korea’s largest data breaches in terms of the number of affected people. However, the combination of personal and financial information makes the breach significant. Sungho Hwang, Korea country manager at NordVPN, said the exposed information could be used to create personalized scams. He also noted that generative AI has made such scams more convincing.

South Korea Faces Wider Cybersecurity Pressure

The banking incidents come as South Korea cyberattacks have increased across other sectors. Cyberattacks targeting South Korean military systems reached 18,951 cases in 2025, the highest annual figure in five years. The number was up 31 percent from 2024 and 108 percent from 2022. South Korea has also expanded its use of AI for defensive cybersecurity. The Ministry of Education and the Korea Education and Research Information Service operate an AI-based system designed to detect suspicious activity and issue automated alerts across 435 monitored institutions. In 2025, the system detected about 480 million potential cyber threat indicators, of which around 86,000 were confirmed as actual intrusions. As the investigation into the Shinhan Bank breach continues, the suspected role of AI is adding to concerns that financial institutions may need to account for increasingly automated forms of cyberattacks.
  • ✇Cybersecurity News
  • Phishing Abuses RMM Tools for Persistent Network Access Do Son
    A new campaign shows how phishing abuses RMM tools for access. See how phishing abuses RMM tools like MSP360 to install ScreenConnect clients. Related Posts: China-Aligned TA419 Credential Phishing Hits AI Experts Attackers Exploit Citrix NetScaler Zero-Day CVE-2026-88772 to Plant Hidden Web Shells Russia's Star Blizzard Scales Up Phishing With RedFlick to Deliver CosmicPulse Backdoor The post Phishing Abuses RMM Tools for Persistent Network Access appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Microsoft Details NeedyMantis Malware Used for Long-Term Access in Targeted Intrusions Do Son
    Microsoft details NeedyMantis malware, a modular backdoor that uses DLL sideloading to keep long-term access in telecom, academic, and government networks. Related Posts: UAT-11587 Targets Asian Governments With Antino Backdoor PaperCut Zero-Day Attack Hides AdaptixC2 Implant Inside Fake Microsoft Copilot New MacSync macOS Infostealer Targets Crypto Wallets The post Microsoft Details NeedyMantis Malware Used for Long-Term Access in Targeted Intrusions appeared first on Daily CyberSecurity.
     
  • ✇Security | CIO
  • OpenAI bets enterprises are ready to delegate real work to autonomous agents
    OpenAI says true agentic AI has finally arrived, pushing beyond the trivial capabilities of early-stage virtual assistants. This week at OpenAI Dev Day, the company introduced Dots, which CEO Sam Altman described as “remarkably capable, always-on” agents powered by GPT‑6 Astra. Dots have their own cloud computer, can be accessed in ChatGPT, Slack, or Teams, and plug into more than 4,000 apps based on human-set boundaries. In a keynote, Altman said using it will feel
     

OpenAI bets enterprises are ready to delegate real work to autonomous agents

30 de Setembro de 2026, 21:33

OpenAI says true agentic AI has finally arrived, pushing beyond the trivial capabilities of early-stage virtual assistants.

This week at OpenAI Dev Day, the company introduced Dots, which CEO Sam Altman described as “remarkably capable, always-on” agents powered by GPT‑6 Astra. Dots have their own cloud computer, can be accessed in ChatGPT, Slack, or Teams, and plug into more than 4,000 apps based on human-set boundaries.

In a keynote, Altman said using it will feel like “a whole new way to work with AI.”

“It can hugely magnify your ability and expand your potential, working 24/7 to take on things that you don’t want to do, so you can focus on higher-level work,” he said.

OpenAI also announced a slew of other new capabilities and tools, including GPT-6.1 Sol, a cheaper and faster sibling of GPT-6.1 Astra, which was shelved earlier this week due to safety concerns. Additionally, Codex is also now in the cloud, Codex CLI has voice control and can help developers inspect, edit, and run code locally, and a new Agents API supports computer use and provides components like harnesses, hosting, memory, and multi-agent controls.

Dots goes beyond ‘trivial’ tasks

Early virtual assistants have been useful for quick handoff tasks like booking reservations, but that is “trivial relative to what the technology can do,” Altman contended in his keynote.

Taking that to the next level, OpenAI’s new Dots can understand what’s happening in a user’s workflows and learns over time without requiring constant human instruction, he explained. Soon, users will be able to access Dots outside ChatGPT by interacting with it through text messages or even by calling the agents on the phone to discuss updates, changes, and weigh in on decision-making.

“You can delegate ambitious pieces of work the way you would to a high agency engineer or a chief of staff,” Altman said. Dots can monitor incoming bug reports and propose fixes, draft pull requests (PRs), or take on tasks like kicking off the next year’s budget planning cycle.

Altman provided the example of migrating an app off a legacy API. This can be difficult, because the API might be used all over a code base, he said, and it could break as developers start making changes. But Dots can trace dependencies and determine what needs to change, run tests, and suggest next steps.

“Think about how you would have done that the old way,” Altman noted. “How many people would have been involved? How much time would it have taken them? What could they have done instead?”

Dots is now available to all ChatGPT Pro, Business Premium, and Enterprise users. OpenAI is also now previewing specialist Dots for enterprises, and is working with Microsoft to integrate Dots into Agent 365. These will serve as virtual teammates to help scale more intensive work in accounting, marketing, or legal, Altman explained.

Carmi Levy, an independent technology analyst, said of everything announced at DevDay 2026, Dots might be the most impactful, as it represents OpenAI’s definitive move into AI agents.

While Meta has been grabbing headlines with its app store-topping Muse, OpenAI’s offering is potentially more relevant to enterprise decision makers who are still trying to figure out how agents can fit into their corporate AI development and deployment roadmap, he noted.

“It allows enterprise customers to build on their pre-existing investments in OpenAI’s stack, and represents a familiar adoption path for developers,” he said.

Cheaper and faster sibling of Astra

OpenAI launched GPT-6 Astra to a limited group of users earlier this month, calling it state-of-the-art in computer use, browsing, software engineering, cybersecurity, science, and professional work. But its generally availability was canceled this week after the model failed critical internal safety and alignment tests.

OpenAI learned from the experiment, Altman said, with early testers demanding: “make it cheaper and make it faster.” The answer to that is GPT 6.1 Sol, which provides near Astra level intelligence at one-fifth of the price. Cached inputs cost $0.10 (US) per million tokens, 95% less than standard input pricing. This makes it cheaper for agents to work through longer tasks, reuse context, and ruminate on solutions. Example uses include multi-step business workflows, code writing and debugging, and document analysis.

GPT 6.1 Sol is “smarter than Astra in some ways, and it will become your daily workhorse,” Altman said. It is now available to all Plus, Pro, Business, Enterprise, and Edu users of ChatGPT Work and Codex, and will soon be offered in an ‘Ultrafast’ plan, with up to 8X faster token generation.

Levy noted that GPT 6.1 Sol reduces the cost curve for enterprises looking to deploy AI agents at scale, all while “avoiding some of the privacy/safety/integrity baggage of the now-stillborn GPT 6.1 Astra.” It effectively shifts the economics of AI agents by dropping the price of resource-intensive development activities like querying repositories, running tests, and iterating code.

“It doesn’t have quite the power of Astra, but that was never what the average developer was looking for, anyway,” Levy noted. “Affordability still drives development decisions, and by leading with Sol, OpenAI removes one more barrier to broad-based adoption.”

New Codex capabilities, assurances around safety

In a much-anticipated move, OpenAI has introduced Codex Cloud, giving developers the ability to move coding tasks between devices without losing threads. “You don’t have to worry about closing your laptop in the middle of a run,” Altman said. “Your agents just keep working, wherever you are.”

Meanwhile, new Codex CLI capabilities allow developers to start, steer, delegate, and track tasks with voice commands, and a new Codex Security Cloud helps defenders identify vulnerabilities and prepare fixes.

Altman addressed the top-of-mind security and governance issue in his keynote. “The best version of AI is not about making people cogs in a giant machine,” he said, noting that there are some things that should not be automated.

“People often talk about AI as a new industrial revolution. I find that quite off-putting,” Altman said. “The future, if we get this right, can be much more like a new renaissance than a new industrial revolution.”

This article originally appeared on InfoWorld.

  • ✇Security | CIO
  • Microsoft’s new Copilot unifies enterprise context for chat and code
    Microsoft’s Copilot super-app has arrived, two months after CEO Satya Nadella confirmed it was in development. It combines conversational Chat, the autonomous Cowork agent, a redesigned coding environment named Code, and Autopilot, the persistent agent formerly known as Scout, into a single Copilot experience. The idea is to make those capabilities look less like separate tools and more like different ways of getting work done through a unified experience. The end goal is
     

Microsoft’s new Copilot unifies enterprise context for chat and code

25 de Setembro de 2026, 14:14

Microsoft’s Copilot super-app has arrived, two months after CEO Satya Nadella confirmed it was in development. It combines conversational Chat, the autonomous Cowork agent, a redesigned coding environment named Code, and Autopilot, the persistent agent formerly known as Scout, into a single Copilot experience.

The idea is to make those capabilities look less like separate tools and more like different ways of getting work done through a unified experience. The end goal is to enable users to describe what they want to accomplish without choosing a mode themselves, and with Copilot routing the task to Chat, Cowork, Code or another capability, Microsoft said.

The individual pieces of this experience are not entirely new, and build on  launches and consolidation moves that Microsoft has made over the past several months.

Nadella first described the unified Copilot architecture during an earnings call in July. He said it would bring chat, agents and business workflows into a single AI workspace while separating the orchestration layer, context and memory from any one AI model. Microsoft subsequently began unifying its consumer and Microsoft 365 Copilot apps ahead of the broader overhaul.

But Microsoft laid much of the groundwork in the period after its November 2025 Ignite conference, with the launch of Cowork for delegated multistep work, Scout for persistent agentic tasks, and natural-language app-building capabilities that have now evolved into Code.

The broader change goes beyond bringing those Copilot experiences together. With Friday’s updates, Microsoft is also adding components and infrastructure aimed at turning Copilot from an AI assistant embedded across Microsoft 365 into a broader orchestration layer for enterprise work.

These include Fabric IQ and Work IQ for enterprise context, Copilot Managed Runtime for running AI-built applications, a unified plugin registry for connecting capabilities, and usage-based billing and FinOps controls for managing agentic workloads and AI spending.

More enterprise context could boost productivity

The inclusion of Fabric IQ in Chat and Cowork, along with Work IQ’s access to data and workflows in Dynamics 365 and Power Platform, will make Copilot more effective for enterprise tasks by giving it a broader understanding of an organization’s data and workflows, potentially reducing hallucinations and improving productivity, said Abhishek Satapathy, principal analyst at Avasant.

“The practical shift is from AI that knows information to AI that can connect what happened, why it happened and what needs to happen next. For example, a business insight can increasingly become the starting point for analysis and follow-up action rather than requiring the user to manually move that context between reports, documents, conversations and business systems,” said Satapathy. “This is particularly relevant for analysts, managers and operations teams working across functions.”

Fabric IQ’s integration with Chat and Cowork is now generally available. Microsoft plans to integrate it with Code soon through its Frontier program. Work IQ will enter public preview over the next month, it said.

Redesigned Code expands the scope of software creation

Productivity is also the focus of Microsoft’s redesigned Code environment.

It “broadens the audience for software creation” by addressing the middle ground between traditional development and simple automation, bringing more use cases into the scope of what business users can build, including those that may be too narrow for a formal development project but too complex for basic automation, Satapathy said.

That means more internal applications, dashboards and workflow tools can potentially be built without going through a traditional development project, while developers can use the same environment to accelerate application creation and focus on more complex engineering and production requirements, he added.

Alongside Code, Microsoft is introducing Copilot Managed Runtime, a governed hosting environment for applications built with Code, Cowork and Copilot Studio. The runtime allows those applications to run within an organization’s Microsoft 365 environment while giving IT control over security, governance and access to live data, Microsoft said.

For enterprise developers and IT teams, the runtime could provide a common production layer for AI-created applications, helping enterprises move applications from experimentation and prototyping into production without having to create a separate operating model for each one, Satapathy said.

It could also help IT teams and CIOs curb shadow IT and application sprawl, said Manoj Chandra Jha, principal analyst at Nord-IQ Research. In its governed environment, IT departments can managed applications and agents created by employees consistently for security, identity, policies, lifecycle management, observability and deployment.

The new Copilot Managed Runtime is currently in public preview and will also be accessible inside the redesigned Code experience, Microsoft said. That experience will roll out to Microsoft’s Frontier program at the end of the month, with broad availability in the coming weeks, it added.

New FinOps tools could help CIOs judge business value

Beyond productivity, faster scaling of AI applications and curbing application sprawl, Microsoft is also giving enterprises more tools to manage the cost of agentic AI by expanding its cost-management capabilities in Agent 365 to include Code and Copilot Managed Runtime.

These capabilities will allow administrators to manage AI spending policies at scale, control access to model families and route credit requests through existing approval workflows, while giving visibility into the outcomes generated by agentic workloads to decide where to sustain, expand or optimize usage, the company said.

End users will also be able to view their credit usage, remaining balances and usage history directly in Copilot, helping them manage their AI usage, it added.

For Bhupendra Chopra, chief revenue officer at IT consulting firm Kanerika, the expanded FinOps capabilities will be critical for CIOs, particularly for understanding if agentic workloads and automation are delivering sufficient business value and if they need to be reworked.

“These capabilities can reveal correction rates for agents. If employees regularly have to undo an agent’s work, that can indicate stale context, poor business rules or an unreliable data foundation before it shows up as a larger operational problem,” Chopra said.

“These capabilities can reveal another insight: whether the time supposedly saved by automation actually translates into a measurable business outcome. Enterprises can automate 20 minutes of work but simply spend that time elsewhere, meaning the productivity gain only matters when it produces a measurable result,” he added.

Usage-based billing extended

Alongside these FinOps capabilities, Microsoft is also extending usage-based billing to more of the capabilities being brought together under Copilot. The model is not new to the platform, having been introduced for Cowork when the agent became generally available in June.

While Cowork, Code and Autopilot, along with new long-running agentic capabilities and frontier models, will use usage-based billing, Chat and Copilot across Microsoft 365 will remain covered by the user subscription license, the company said.

That distinction could require CIOs to think about AI spending differently from traditional productivity software, Satapathy said.

Instead of budgeting primarily around the number of users with Copilot licenses, CIOs may need to consider what work is being delegated to agents, how much that work consumes and what business value it produces, he added.

“Two employees with the same Copilot license, for instance, could generate very different AI costs depending on whether one uses Copilot for assistance while the other delegates longer-running work to agents,” he further said.

However, that might still be some way off, with several of the key capabilities still in preview or yet to roll out.

Home, the new starting point in Copilot where Chat and Cowork come together, will begin rolling out through Microsoft’s Frontier program in the coming weeks, while Autopilot is expanding to private preview at the end of the month, Microsoft said.

This article first appeared on Computerworld.

  • ✇Security | CIO
  • Cursor customers will lose access to OpenAI coding models in November
    OpenAI will stop AI coding platform Cursor from accessing its models from November 12, following the acquisition of Cursor parent Anysphere by Elon Musk‘s SpaceX. “Today, we notified SpaceX that we intend to wind down our contract providing OpenAI models to Cursor, with a proposed shutoff date of November 12, 2026,” the company wrote in a blog post. That shutoff, the company added, was based on its concerns that SpaceX will not use its technology in accordance with i
     

Cursor customers will lose access to OpenAI coding models in November

31 de Agosto de 2026, 12:48

OpenAI will stop AI coding platform Cursor from accessing its models from November 12, following the acquisition of Cursor parent Anysphere by Elon Musk‘s SpaceX.

“Today, we notified SpaceX that we intend to wind down our contract providing OpenAI models to Cursor, with a proposed shutoff date of November 12, 2026,” the company wrote in a blog post.

That shutoff, the company added, was based on its concerns that SpaceX will not use its technology in accordance with its terms of service, citing what it described as a history of Musk’s companies violating contracts: “After Musk acquired Twitter, now part of SpaceX, the company broke⁠ the terms of our contract (alongside many others). Under oath earlier this year, Musk admitted⁠ that xAI, now also part of SpaceX, had violated OpenAI’s terms of service (terms which are similar to xAI’s own),” the company wrote.

OpenAI and Musk remain locked in a broader legal dispute, with Musk having sued OpenAI over its transition from a nonprofit-controlled organization to a for-profit structure and OpenAI countering with allegations over Musk’s conduct and competing AI ventures.

Enterprises and developers using OpenAI models within Cursor now have about 10 weeks to transition to other AI models within Cursor, or choose a new coding platform.

Swapping problem

That may not be easy.

While the 10-week timeframe might be enough to assess the impact and decide a path forward, it will not be a trivial operation, said Abhishek Satapathy, principal analyst at Avasant.

Even for those just swapping models and staying with Cursor, there will be effort required to validate the replacement against development workflows currently running on OpenAI’s models, Satapathy said.

“This includes repository-level coding, debugging, refactoring, test case generation, multi-file changes and tasks where an agent has to inspect a codebase, make a sequence of changes, run tests and correct its own errors,” he said.

The need for validation stems from differences in how AI models handle coding, reasoning, tool use and instructions.

Developers may find that prompts or agent instructions that work well with OpenAI models produce different results with another model, requiring enterprises to retune prompts and evaluations, said Manoj Chandra Jha, principal analyst at Nord-IQ Research.

That recalibration could translate into a short-term productivity dip as development teams rework prompts and workflows and adjust to how the replacement model behaves, echoed Bhupendra Chopra, chief revenue officer at IT consulting firm Kanerika.

For enterprises considering a move away from Cursor, the transition becomes more complex, primarily because swapping coding platforms would require retraining developers, rebuilding integrations and agent configurations, and repeating security and governance reviews that not only require time but also adds costs, Satapathy said.

Broader risks of AI vendor dependence

The added complexity of changing platforms points to a broader issue for enterprises: their dependence on AI model providers and the commercial relationships that determine where those models can be used.

“Enterprises can no longer assume that a model available through an AI coding platform today will always remain available. Acquisitions, contracts, competition or regulation can change this,” said Pareekh Jain, principal analyst at Pareekh Consulting.

“Enterprises should therefore support multiple models, regularly test alternatives and avoid making important workflows too dependent on one model,” Jain added.

Similar principles should apply to the coding platforms as well, according to Satapathy.

“Enterprises should consider whether prompts, agent configurations, evaluation methods and tool integrations can be reused when the underlying model changes,” Satapathy said.

There are broader risks for the vendors too, especially OpenAI.

While Cursor appears better positioned to retain customers because enterprises can continue using the platform with other models, particularly with Anthropic’s pledged support, OpenAI risks losing developer usage as customers move to alternatives such as Claude without having to change their coding environment, Satapathy said.

This article first appeared on InfoWorld.

Black Hat USA 2026: One GitHub Issue Could Compromise Major AI Coding Workflows

At Black Hat USA 2026, Novee found GitHub workflow flaws in Claude Code, Gemini CLI and Codex that enabled RCE, credential theft and agent control in pipelines.

Top 8 Penetration Testing Tools to Enhance Your Security in 2026

13 de Outubro de 2026, 02:00

Compare the best penetration testing tools for 2026, including pricing, key features, use cases, and top picks for modern security teams today.

The post Top 8 Penetration Testing Tools to Enhance Your Security in 2026 appeared first on TechRepublic.

How to Make AI Tools Work Reliably for Growing Teams

Learn how growing teams make AI tools reliable with clear workflows, shared rules, secure systems, and repeatable processes that improve quality and speed daily
❌
❌