A severe DreamHost security breach exposed customer FTP credentials and webmail accounts, prompting urgent password rotations and website file audits.
Related Posts:
DigiCert Data Exposure Reveals Customer Contact Records and Identity Documents
NVIDIA Brev Security Incident Prompts SSH Key Rotation
Amadeus Airline Data Breach Hits Major Global Carriers
The post DreamHost Security Breach Exposes FTP and Webmail Data appeared first on Daily CyberSecurity.
A DigiCert data exposure revealed customer records and IDs after an internal business system breach. Learn what was exposed and how it was fixed.
Related Posts:
DreamHost Security Breach Exposes FTP and Webmail Data
NVIDIA Brev Security Incident Prompts SSH Key Rotation
Amadeus Airline Data Breach Hits Major Global Carriers
The post DigiCert Data Exposure Reveals Customer Contact Records and Identity Documents appeared first on Daily CyberSecurity.
A recent NVIDIA Brev security incident exposed virtual machine SSH keys, prompting emergency key rotations and security audits for AI developers.
Related Posts:
Amadeus Airline Data Breach Hits Major Global Carriers
Gitee Exposed Credentials Found Across Millions of Repositories
OffiDocs Chrome Extensions With 2.3 Million Installs Caught Harvesting Browsing URLs
The post NVIDIA Brev Security Incident Prompts SSH Key Rotation appeared first on Daily CyberSecurity.
An Amadeus airline data breach compromised passenger travel records across Malaysia Airlines, JAL, ANA, and Cathay Pacific via compromised credentials.
Related Posts:
Gitee Exposed Credentials Found Across Millions of Repositories
OffiDocs Chrome Extensions With 2.3 Million Installs Caught Harvesting Browsing URLs
Keystone Wallet Data Breach Exposes Customer Orders
The post Amadeus Airline Data Breach Hits Major Global Carriers appeared first on Daily CyberSecurity.
An Amadeus airline data breach compromised passenger travel records across Malaysia Airlines, JAL, ANA, and Cathay Pacific via compromised credentials.
42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups.
The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure Index, written by Mantas Sasnauskas.
“No file was opened for this index. Every number below comes from bucket nam
42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups.
The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure Index, written by Mantas Sasnauskas.
“No file was opened for this index. Every number below comes from bucket names, file extensions, file counts and last-modified timestamps. That is a deliberate limit. It keeps the research on the right side of the line, and it turns out to be enough to see where the sensitive material concentrates.” Ransomnews states. “We are calling it the Ransomnews Cloud Exposure Index, and we will rerun it quarterly so the numbers can be compared over time.”
The researchers used bucket names, file types, file counts and last-modified dates to collect their data. They did not open any files, allowing them to identify where sensitive information might be stored without accessing the content. They plan to repeat the research every three months to track changes over time.
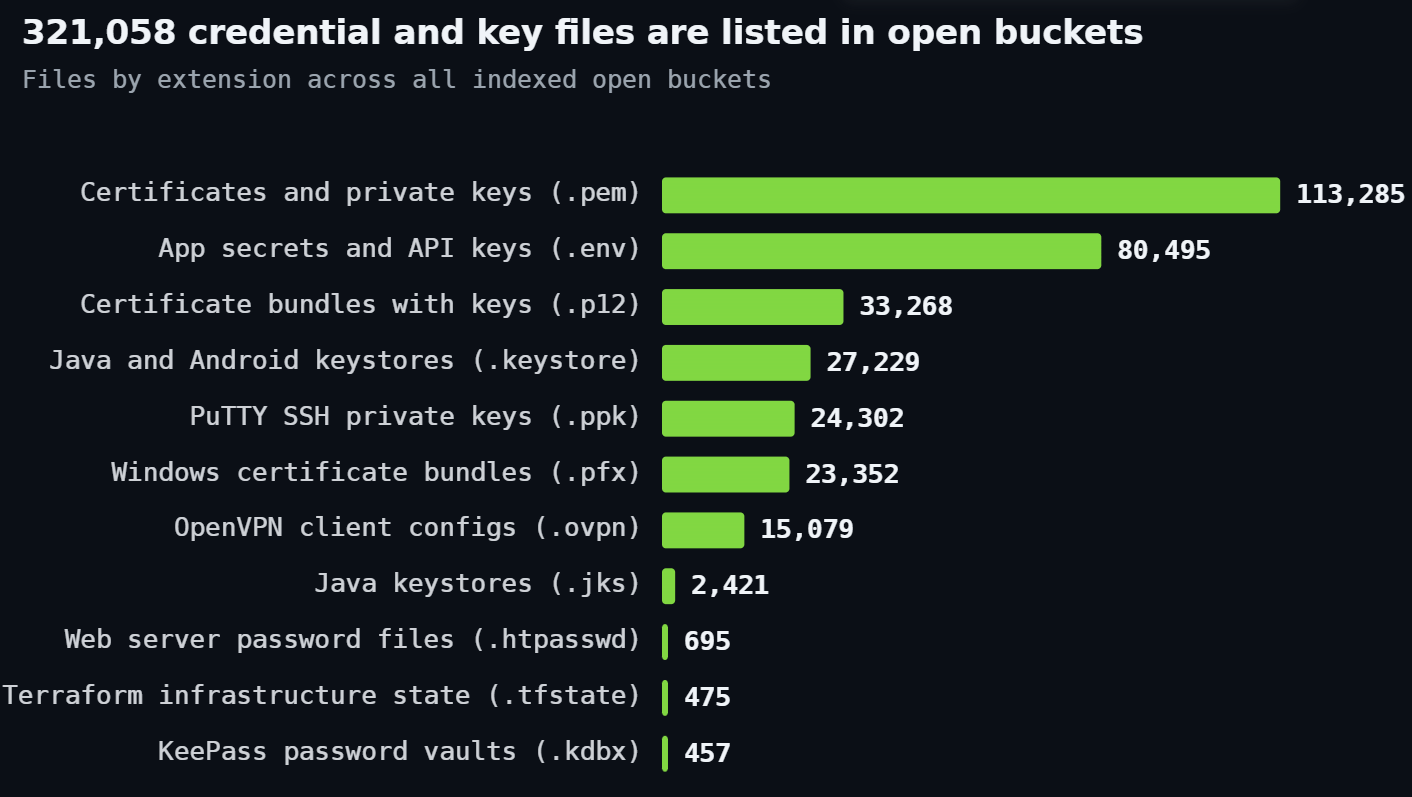
Amazon S3 accounts for 72% of the exposed buckets, roughly in line with its share of the market. This does not mean S3 has weaker security than other providers. Azure Blob, however, appears 2.5 to 3.6 times more often than expected among buckets named for backups, data exports and payroll records. The researchers also found 321,058 files related to credentials and keys. Of the exposed .env files, 67% were last modified in 2026.
Below is the split by provider, from a snapshot taken on October 7:
Provider
Open buckets
Share
Amazon S3
347,984
71.9%
Azure Blob
68,532
14.2%
Google Cloud Storage
53,131
11.0%
DigitalOcean Spaces
11,069
2.3%
Alibaba OSS
3,426
0.7%
Total
484,142
100%
A lot of these buckets are public on purpose, holding website assets, CDN mirrors, open datasets and podcast archives. So the index isn’t 484,142 breaches. It’s the pool where breaches hide, and the rest of the report narrows it down to the stores that should never have been listable.
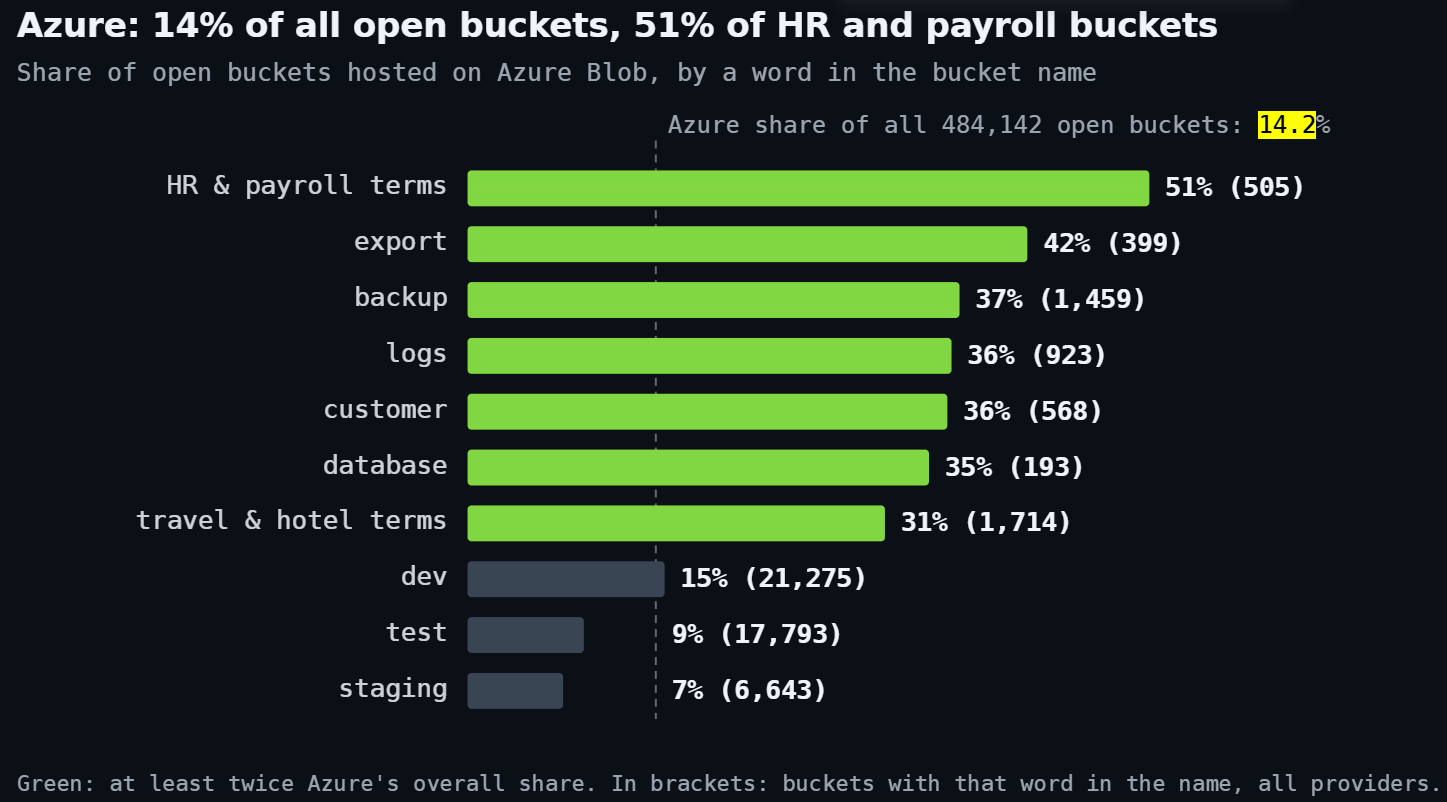
“Azure, by a wide margin relative to its size. Azure Blob holds 14.2% of open buckets, but 37% of the 1,459 buckets with “backup” in the name, 42% of the 399 named for exports, and 51% of the 505 carrying HR or payroll terms.” continues the report. “Buckets named for logs, customers and databases sit at 35% to 36%, all around two and a half times Azure’s baseline.”
The skew only shows up for operational data. Buckets named “dev” sit at Azure’s baseline of 15 percent, and “test” and “staging” fall below it, at 9 and 7 percent. The authors suspect Azure storage accounts more often hold line-of-business data such as backups, exports and HR systems that enterprises run on Microsoft, while S3 and Google Cloud carry more application assets. They call it a hypothesis the counts suggest and don’t prove, and it’s the first thing they want to test next time.
By sector, retail and e-commerce names lead with 5,666 buckets, mostly storefront assets. The more worrying number is that names tied to regulated sectors (finance, healthcare, education, government, legal and HR) appear on 10,891 unique open buckets. Those are the places where a stray file most likely holds personal, health or financial records, and where regulators expect to hear about it.
Sector (by bucket name)
Open buckets
Files in them
Retail and e-commerce
5,666
269.9M
Finance and insurance
3,508
58.0M
Healthcare
2,709
47.9M
Media and entertainment
2,696
136.2M
Education
2,393
60.6M
Gaming
2,296
79.0M
Travel and hospitality
1,714
118.7M
Real estate
1,137
60.7M
Government and public sector
1,000
36.2M
Legal
978
11.3M
Crypto
630
11.9M
HR and payroll
505
8.4M
Healthcare-related names appear in 2,709 buckets containing 47.9 million files. The researchers identified them using terms such as “hospital” (135 buckets), “patient” (135), “clinic” (277) and “dental” (331). HR and payroll is the smallest sector, with 505 buckets, 259 of which are hosted on Azure.
These figures are based on names, not proof of ownership. The search matches parts of words, so “store” can refer to object storage as well as shops. A single bucket can also appear in two sectors.
The exposed buckets also list about 4.7 million database and dump files, 15,130 mailbox archives, and tens of millions of spreadsheets and documents. Credential files are particularly concerning because they can turn a cloud misconfiguration into a real intrusion.
File type
What it is
Files listed
.pem
Certificates and private keys
113,285
.env
App secrets and API keys
80,495
.p12
Certificate bundles with keys
33,268
.keystore
Java and Android keystores
27,229
.ppk
PuTTY SSH private keys
24,302
.pfx
Windows certificate bundles
23,352
.ovpn
OpenVPN client configs
15,079
.jks
Java keystores
2,421
.htpasswd
Web server password files
695
.tfstate
Terraform infrastructure state
475
.kdbx
KeePass password vaults
457
Each of these exists to grant access. A .env file is where developers keep database passwords and API keys. A .tfstate file is Terraform’s record of a whole cloud setup, often with secrets in plain text, and a .kdbx vault is encrypted but now open to anyone who wants to guess passwords offline. Some .pem files are public certificates and some files are test fixtures, so the counts are a ceiling on live secrets and not a measure of them. It’s still a big ceiling.
Database files make up most of the sensitive material by volume:
File type
What it usually holds
Files listed
.sqlite
Embedded app databases
2,561,807
.bak
Database and server backups
752,055
.sql
Database dumps
687,446
.sqlite3
Embedded app databases
488,176
.dump
Database dumps
176,603
.mdb / .accdb
Microsoft Access databases
36,467
.dmp
Memory and crash dumps
12,809
.pst / .ost / .mbox
Mailbox archives
15,130
.eml
Saved emails
4,549,665
.csv
Data exports and records
at least 69,580,112
.xlsx / .xls
Spreadsheets
42,544,997
.docx
Word documents
24,936,788
.pdf
Documents, invoices, scans
at least 106,191,393
.log
Application and server logs
at least 61,310,809
The exposed buckets contain thousands of virtual disk images, including VMware, Hyper-V and QEMU files. A single disk image can contain an entire server, including credentials.
Some exposures involve active systems. Of 80,495 .env files, 67% were last modified in 2026. Certificates and SQLite databases include both recent and older files. Backups appear older, with 89% of the 752,055 .bak files last modified before 2025. Almost all PuTTY key files date from 2024.
Recent leaks need urgent attention, while long-standing exposures point to poor security management. The problem is ongoing: at least 113.6 million files were added to publicly listable buckets in the seven days before September 9. Over the previous 30 days, these included more than 21,000 SQL dumps, nearly 21,000 backup files, 4,477 .pem files and 1,298 .env files.
Public .env files can expose database passwords that ransomware affiliates and initial access brokers look for. Similar credentials appear in stolen-data logs, but in this case, attackers do not need to infect a device. They only need to search for exposed files.
Cloud providers already offer settings to prevent public access. Organizations should enable S3 Block Public Access, disable anonymous access to Azure Blob storage, and enable public access prevention in Google Cloud. These controls should apply at account or organization level to prevent new storage buckets from becoming public.
Organizations should also scan their storage for sensitive files such as .env, .sql, .bak, .pem, .ppk, .tfstate and .kdbx. Terraform state files and virtual disk images should be treated as secrets, stored privately, encrypted and monitored. Backups should never be publicly accessible, and recovery procedures must be tested.
One exposed bucket may be a mistake, but many often indicate a wider process failure. Organizations need to fix the underlying security controls, not just individual buckets.
The research has some limitations. The team queried search engines on October 25, while the bucket list was current to October 7 and the newest indexed file dated September 9. File-level data may therefore be about a month old. Counts are also capped at one million per query, so researchers split larger categories into date ranges and added the results.
Some limits apply. The team queried the search engines on October 25. The bucket list was current to October 7 and the newest indexed file was dated September 9, so file-level figures lag by about a month. The index caps any single count at one million, so larger types were split into date windows and summed.
A last-modified date shows when a file was written, not when it was exposed, and a listed file isn’t proof that its contents can be read. No bucket is named in the report. Exposures with a known owner in regulated sectors are going through responsible disclosure, with national CERTs copied where the owner is public sector or doesn’t respond.
“Rotate any secret that has ever sat in a public bucket. Closing the bucket does not un-leak the key. Assume anything that was listable was copied.” conlcudes the report.
60 OffiDocs Chrome extensions with 2.3M installs secretly send browsing URLs. See how these spying Chrome extensions work and how to stay safe.
Related Posts:
Keystone Wallet Data Breach Exposes Customer Orders
PingCAP Data Breach Exposes TiDB Cloud Customer Records and Source Code
Smart TV ACR Tracking Study Finds Failed Opt-Outs and 57 Million Exposed Viewing Records
The post OffiDocs Chrome Extensions With 2.3 Million Installs Caught Harvesting Browsing URLs appeared first on Daily CyberSe
A Keystone wallet data breach via Shopify API exposed customer shipping addresses, raising physical wrench attack concerns for crypto holders.
Related Posts:
PingCAP Data Breach Exposes TiDB Cloud Customer Records and Source Code
Smart TV ACR Tracking Study Finds Failed Opt-Outs and 57 Million Exposed Viewing Records
CAPCOM ID Data Breach Exposes 11.77 Million Records
The post Keystone Wallet Data Breach Exposes Customer Orders appeared first on Daily CyberSecurity.
A PingCAP data breach exposed customer records and source code. Learn how the TiDB Cloud security incident happened and how to protect your account.
Related Posts:
Keystone Wallet Data Breach Exposes Customer Orders
Smart TV ACR Tracking Study Finds Failed Opt-Outs and 57 Million Exposed Viewing Records
CAPCOM ID Data Breach Exposes 11.77 Million Records
The post PingCAP Data Breach Exposes TiDB Cloud Customer Records and Source Code appeared first on Daily CyberSecurity.
A CAPCOM ID data breach exposed 11.77 million records, including emails and login activity. No payment data was leaked.
Related Posts:
Quest Diagnostics Data Breach Hits Quanum Lab Services Manager Patient Records
Zeabur Shutdown Follows Repeated Data Breaches
Railway Security Incident Exposes Customer Environment Variables and Pauses All Deployments
The post CAPCOM ID Data Breach Exposes 11.77 Million Records appeared first on Daily CyberSecurity.
Quest Diagnostics data breach: hackers accessed patient records in its Quanum Lab Services Manager. Quest says it is not tied to the PHP flaw.
Related Posts:
CAPCOM ID Data Breach Exposes 11.77 Million Records
Zeabur Shutdown Follows Repeated Data Breaches
Railway Security Incident Exposes Customer Environment Variables and Pauses All Deployments
The post Quest Diagnostics Data Breach Hits Quanum Lab Services Manager Patient Records appeared first on Daily CyberSecurity.
The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts.
Related Posts:
Railway Security Incident Exposes Customer Environment Variables and Pauses All Deployments
Sourcenext Data Breach Exposes 22.5M User Records
OpenCode Security Breach Exposes 1.4% of Console Users
The post Zeabur Shutdown Follows Repeated Data Breaches appeared first on Daily CyberSecurity.
Railway security incident: attackers may have decrypted Railway environment variables. Builds are paused. Rotate API keys and credentials now.
Related Posts:
Zeabur Shutdown Follows Repeated Data Breaches
Sourcenext Data Breach Exposes 22.5M User Records
OpenCode Security Breach Exposes 1.4% of Console Users
The post Railway Security Incident Exposes Customer Environment Variables and Pauses All Deployments appeared first on Daily CyberSecurity.
A massive Sourcenext data breach exposed up to 22.5 million customer records via abused member APIs, prompting emergency company-wide password resets.
Related Posts:
OpenCode Security Breach Exposes 1.4% of Console Users
UpdraftPlus Data Breach Leads to UpdraftCentral Backdoor Attacks on WordPress Sites
Ricardo Data Leak Exposes User Contact Details
The post Sourcenext Data Breach Exposes 22.5M User Records appeared first on Daily CyberSecurity.
The OpenCode security breach may have exposed stored third-party API keys for 1.4% of Console users. Revoke and rotate keys now.
Related Posts:
Sourcenext Data Breach Exposes 22.5M User Records
UpdraftPlus Data Breach Leads to UpdraftCentral Backdoor Attacks on WordPress Sites
Ricardo Data Leak Exposes User Contact Details
The post OpenCode Security Breach Exposes 1.4% of Console Users appeared first on Daily CyberSecurity.
CyberLeek threatens to leak a playable GTA 6 build if its Solana meme coin hits a $30 million market cap, but the build remains unverified.
CyberLeek, the anonymous figure behind this summer’s wave of GTA 6 leaks, just raised the stakes considerably. After dropping 25 minutes of gameplay footage earlier last week, including nudity and dev menu access, they’re now threatening to release a complete, playable build of the game, start to finish.
“A GTA 6 leaker has reportedly threatened to pu
CyberLeek threatens to leak a playable GTA 6 build if its Solana meme coin hits a $30 million market cap, but the build remains unverified.
CyberLeek, the anonymous figure behind this summer’s wave of GTA 6 leaks, just raised the stakes considerably. After dropping 25 minutes of gameplay footage earlier last week, including nudity and dev menu access, they’re now threatening to release a complete, playable build of the game, start to finish.
CyberLeek posted the threat on its own website. The demand is simple: if its cryptocurrency reaches a $30 million market value, the leaker will release the playable build of GTA 6, including the full story mode, from start to finish, with the ending credits. CyberLeek says Take-Two can avoid the leak only by providing physical copies of the game and issuing a public apology. This sounds more like a challenge than a serious negotiation.
“Here’s the deal, nice and clean,” the leaker states. “CyberLeek hits 30 million marketcap, the build goes out — full story mode, played to the end, credits and all. Don’t believe it has full story mode? Ask for what you want to see, and it gets provided. Take-Two gets one way out: physical disks and a public apology. They can take it at any moment. Or they can gamble that CL is bluffing. Everyone knows which one they’ll pick.”
This is not CyberLeek’s first leak. Rockstar previously said the situation was painful and that this was not how it wanted fans to see the game after years of waiting. Take-Two, Rockstar’s parent company, has been trying to identify the leaker and even sought a court order requiring Discord to share information about their identity. The company is actively trying to stop the leaks rather than waiting for the situation to pass.
Take-Two, Rockstar’s parent company, has been actively hunting for the leaker and tried subpoenaing Discord for identifying information, so this isn’t a studio sitting back and hoping it blows over.
The efforts to stop the leaks have not worked so far. CyberLeek went silent for a while, then returned with new footage showing Jason fully naked and Lucia topless. Eurogamer reported that the video appears to be real and carries CyberLeek’s usual watermark.
CyberLeek did more than leak game footage. It also launched a Solana meme coin and uses the videos to promote it. Reports said the coin reached a market value of $25 million in late August, with more than $36 million in trading volume in a single day. Its value then fell sharply after Rockstar released official gameplay footage on Netflix and interest in the leaks declined. The new $30 million target is important because reaching it could trigger the release of a playable version of GTA 6 before the official launch.
Whether CyberLeek genuinely has a full playable build worth leaking is still unverified.
“The knowledge that a playable build of GTA 6 might be online has unsurprisingly encouraged hackers to lure curious users searching for it on unfamiliar websites.” states TechSpot. “Files labeled as the build have recently appeared on torrent websites, but these are certainly malicious. There is no evidence that CyberLeek or anyone else has, or even can, release an early version of the game.”
Fake downloads claiming to be the leaked build have already started circulating on torrent and piracy sites, several reportedly carrying malware, so anyone tempted to go looking is more likely to get infected than to get an early copy of GTA 6.
Take-Two has already lost close to $2.8 billion in market value over a 48 hour stretch tied to this leak saga, which tells you how seriously the market is taking the threat, even unverified. GTA 6 is still set for a November 19 release on PlayStation 5 and Xbox Series X/S, and neither Rockstar nor Take-Two has commented on this latest ultimatum. Extortion tied to a crypto pump scheme is a genuinely new flavor of leak drama, and it probably won’t be the last time someone tries combining the two.
A recent Ricardo data leak exposed 890,000 users. SMG fixed the security vulnerability, confirming passwords remain safe.
Related Posts:
The Growing Backlash Against Apple Intelligence Integration
Trump Mobile Data Breach Exposes 3,615 Customers in BYOD Leak
Denmark CPR Data Breach Exposes CPR Numbers of 8.8 Million People
The post Ricardo Data Leak Exposes User Contact Details appeared first on Daily CyberSecurity.
Explore how massive Apple Intelligence storage demands in macOS 27 Golden Gate face fierce backlash regarding enterprise security and user limitations.
Related Posts:
Ricardo Data Leak Exposes User Contact Details
Trump Mobile Data Breach Exposes 3,615 Customers in BYOD Leak
Denmark CPR Data Breach Exposes CPR Numbers of 8.8 Million People
The post The Growing Backlash Against Apple Intelligence Integration appeared first on Daily CyberSecurity.
Explore how massive Apple Intelligence storage demands in macOS 27 Golden Gate face fierce backlash regarding enterprise security and user limitations.
Trump Mobile data breach: BYOD leaks Trump Mobile customer data for 3,615 people, including Trump allies, via an infostealer and no MFA.
Related Posts:
Denmark CPR Data Breach Exposes CPR Numbers of 8.8 Million People
AI Coding Agents Leak 13,000 Internal Screenshots to Public GitHub Repos
Meta Muse Secretly Used Humans for AI Phone Calls
The post Trump Mobile Data Breach Exposes 3,615 Customers in BYOD Leak appeared first on Daily CyberSecurity.
Denmark CPR data breach: attackers abused a firm's access, leaving CPR numbers exposed for 8.8 million people. Here is what to know and do.
Related Posts:
Trump Mobile Data Breach Exposes 3,615 Customers in BYOD Leak
AI Coding Agents Leak 13,000 Internal Screenshots to Public GitHub Repos
Meta Muse Secretly Used Humans for AI Phone Calls
The post Denmark CPR Data Breach Exposes CPR Numbers of 8.8 Million People appeared first on Daily CyberSecurity.
PixelLeak: an AI agent screenshot leak put 13,000+ internal images from 300+ firms in public GitHub repos. See how it happened and how to check.
Related Posts:
Meta Muse Secretly Used Humans for AI Phone Calls
ShinyHunters Syndicate Alleges Major FBI Network Compromise
Leaked GitHub App Private Keys Expose Critical Infrastructure
The post AI Coding Agents Leak 13,000 Internal Screenshots to Public GitHub Repos appeared first on Daily CyberSecurity.

 Entrar