Visualização normal
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Fake ChatGPT and Claude Apps Use Signed Executables to Install Yoba Malware
Fake ChatGPT and Claude apps spread Yoba malware through GitHub, using signed executables to load a cryptominer on…
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Fake GTA VI Download Sites Push Malware Ahead of Launch
Fake GTA VI download sites lure gamers with leaked builds, malware, crypto payment demands and mobile versions ahead…
Fake GTA VI Download Sites Push Malware Ahead of Launch
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Cursor Distributed Claude Code Extensions With SSH Backdoor Code
Malicious Claude Code extensions targeted Windows and macOS developers through Cursor collecting device details and planting files for persistent remote access.
Cursor Distributed Claude Code Extensions With SSH Backdoor Code
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Hackers Pushing Remote Access Tool Through Fake Adobe Acrobat Pages
Fake Adobe Acrobat pages distribute signed ScreenConnect installers configured for attacker-controlled remote access to Windows PCs, CloudSEK’s researchers say.
Hackers Pushing Remote Access Tool Through Fake Adobe Acrobat Pages
-
Data and computer security | The Guardian

-
A gift to scammers: why you should probably keep your birthday a secret
Using a fake DOB or leaving the field blank when making an online account can offer protection from identity theftYou get a call from your bank saying there has been suspicious activity on your account. They read out your name, address and date of birth so you are happy it is a legitimate caller.But you are talking to criminals who have used your date of birth as part of a web of verifying information to convince you they are someone else. Continue reading...
A gift to scammers: why you should probably keep your birthday a secret
Using a fake DOB or leaving the field blank when making an online account can offer protection from identity theft
You get a call from your bank saying there has been suspicious activity on your account. They read out your name, address and date of birth so you are happy it is a legitimate caller.
But you are talking to criminals who have used your date of birth as part of a web of verifying information to convince you they are someone else.
Continue reading...
© Photograph: kmt_rf/Alamy

© Photograph: kmt_rf/Alamy

© Photograph: kmt_rf/Alamy
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
ADEX: AI Involved in 52% of Detected Ad Fraud Schemes – Shopping Agents Could be Next
New ADEX research shows how AI is making familiar scams cheaper and harder to detect, while fraudsters prepare to target AI shopping assistants.
ADEX: AI Involved in 52% of Detected Ad Fraud Schemes – Shopping Agents Could be Next
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
From Rules to AI and Back
Fraud prevention combines rules, AI and behavioral analytics to stop scams, reduce false declines and keep automated decisions explainable through human review.
From Rules to AI and Back
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Scanner Poses as 32 AI Bots to Find Credentials and Private Keys
A scanner impersonates 32 AI bots, including OpenAI and Claude crawlers, to search websites for exposed credentials, private keys and cloud configuration files.
Scanner Poses as 32 AI Bots to Find Credentials and Private Keys
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Hackers Abuse Microsoft Teams External Chats to Access Corporate PCs
Hackers impersonate IT support in Microsoft Teams external chats, tricking employees into granting remote access and installing malware on corporate computers.
Hackers Abuse Microsoft Teams External Chats to Access Corporate PCs
-
Security Affairs
-
AI-Generated Fake Bank Calls and NFC App Enabled €380,000 Fraud, Dutch Police Say
Dutch police arrest two men over AI-voiced bank fraud that allegedly used a fake app to steal card data from 170 victims, causing €380,000 in losses. Rotterdam police have arrested two men over a new type of bank fraud that used AI-generated phone calls, a fake banking app, and NFC technology to steal bank card data. In just three weeks, the scheme allegedly cost 170 victims around €380,000. “Rotterdam police arrested two suspects accused of a new form of bank-helpdesk fraud. The operati
AI-Generated Fake Bank Calls and NFC App Enabled €380,000 Fraud, Dutch Police Say
Dutch police arrest two men over AI-voiced bank fraud that allegedly used a fake app to steal card data from 170 victims, causing €380,000 in losses.
Rotterdam police have arrested two men over a new type of bank fraud that used AI-generated phone calls, a fake banking app, and NFC technology to steal bank card data. In just three weeks, the scheme allegedly cost 170 victims around €380,000.
“Rotterdam police arrested two suspects accused of a new form of bank-helpdesk fraud. The operation allegedly caused around €380,000 in losses for 170 victims in just three weeks.” NL Times reports. “The suspects allegedly used AI-generated phone calls and a fake banking app to copy victims’ bank cards remotely, allowing accomplices to withdraw thousands of euros. Victims came from across the Netherlands and ranged in age; dozens were in their twenties and thirties.”
The suspects allegedly used AI-generated calls to trick victims into believing their bank accounts were at risk. They then persuaded them to install a fake banking app and scan their bank cards with their phones. The app used NFC to capture card data, which accomplices could use to withdraw money. Victims came from across the Netherlands and included people of all ages, with dozens in their twenties and thirties.
A 23-year-old man from Vaassen, in Gelderland, is suspected of developing the technology and directing the group. A 25-year-old from Ede, also in Gelderland, is suspected of coordinating the operation. On Tuesday, a Rotterdam court ordered both men to remain in custody for at least another 90 days while the investigation continues.
The case started in mid-September, when Dutch banks reported the new fraud through the Electronic Crimes Task Force (ECTF). That’s a partnership of banks, police and prosecutors that shares information and expertise to fight financial and digital crime. Within days of consulting the task force, Rotterdam’s cybercrime team had identified the digital infrastructure used by the group.
Investigators monitored the servers to understand how the operation worked. They traced the people behind the technology, the phone calls made to victims, and the cash withdrawals.
The scam started with a recorded message warning victims about suspicious activity on their bank accounts.
“The callers used artificial intelligence (AI) to produce dozens of recordings featuring different voices, banks, companies, and scenarios. Victims were asked to press 1 if they did not recognize the alleged activity.” states the report. “They were then connected to someone posing as a bank employee.”
The message asked people to press 1 if they did not recognize the activity. They were then connected to someone pretending to be a bank employee. Following a prepared script, the caller pressured them to act quickly and take steps to block their bank cards.
The fake employee told victims to download an app and hold their bank card against the phone to scan it. The criminals presented this as a way to secure the accounts.
If a caller ever asks you to scan your card with an app, hang up and phone your bank on the number printed on the card.
According to police, the app sent data from the card’s near-field communication (NFC) chip, the technology behind contactless payments, to an app run by an accomplice. That person waited at a cash machine or payment terminal and could withdraw thousands of euros without the victim realizing what was happening.
“Police described this technical method as one they had not encountered before.” the report concludes.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, NFC)
-
Cybersecurity News
-
Apple Presto Return Scanner Targets In-Box Fraud
Apple deployed an in-box Apple Presto return scanner across retail stores to combat return fraud by running diagnostics on sealed iPhones. Related Posts: Come Back to Firefox Campaign Champions Web Privacy OpenSSL 4.1.0 Release Introduces Elbrus Support and DTLS 1.3 eMudhra Rogue Certificates Flood Certificate Transparency The post Apple Presto Return Scanner Targets In-Box Fraud appeared first on Daily CyberSecurity.
Apple Presto Return Scanner Targets In-Box Fraud
Apple deployed an in-box Apple Presto return scanner across retail stores to combat return fraud by running diagnostics on sealed iPhones.
Related Posts:
- Come Back to Firefox Campaign Champions Web Privacy
- OpenSSL 4.1.0 Release Introduces Elbrus Support and DTLS 1.3
- eMudhra Rogue Certificates Flood Certificate Transparency
The post Apple Presto Return Scanner Targets In-Box Fraud appeared first on Daily CyberSecurity.
-
Data and computer security | The Guardian

-
Cookie theft: how fraudsters get the digital key to your accounts
‘Session cookies’ are a primary target for hackers letting them hijack and use your accountsYou’ve had a busy morning of life admin, logging into various accounts to check balances and make payments. At the end of a productive few hours you close your laptop and move on to your next job.What you don’t know is that fraudsters have hijacked your session with the bank and are now able to access your account. You are the victim of cookie theft, which belongs to a type of fraud known as “session hija
Cookie theft: how fraudsters get the digital key to your accounts
‘Session cookies’ are a primary target for hackers letting them hijack and use your accounts
You’ve had a busy morning of life admin, logging into various accounts to check balances and make payments. At the end of a productive few hours you close your laptop and move on to your next job.
What you don’t know is that fraudsters have hijacked your session with the bank and are now able to access your account. You are the victim of cookie theft, which belongs to a type of fraud known as “session hijacking”.
Continue reading...
© Photograph: Rawf8/Alamy

© Photograph: Rawf8/Alamy

© Photograph: Rawf8/Alamy
-
Firewall Daily – The Cyber Express

-
Fake Reviews, Deceptive Ads: FTC Targets Alleged Passport Scam
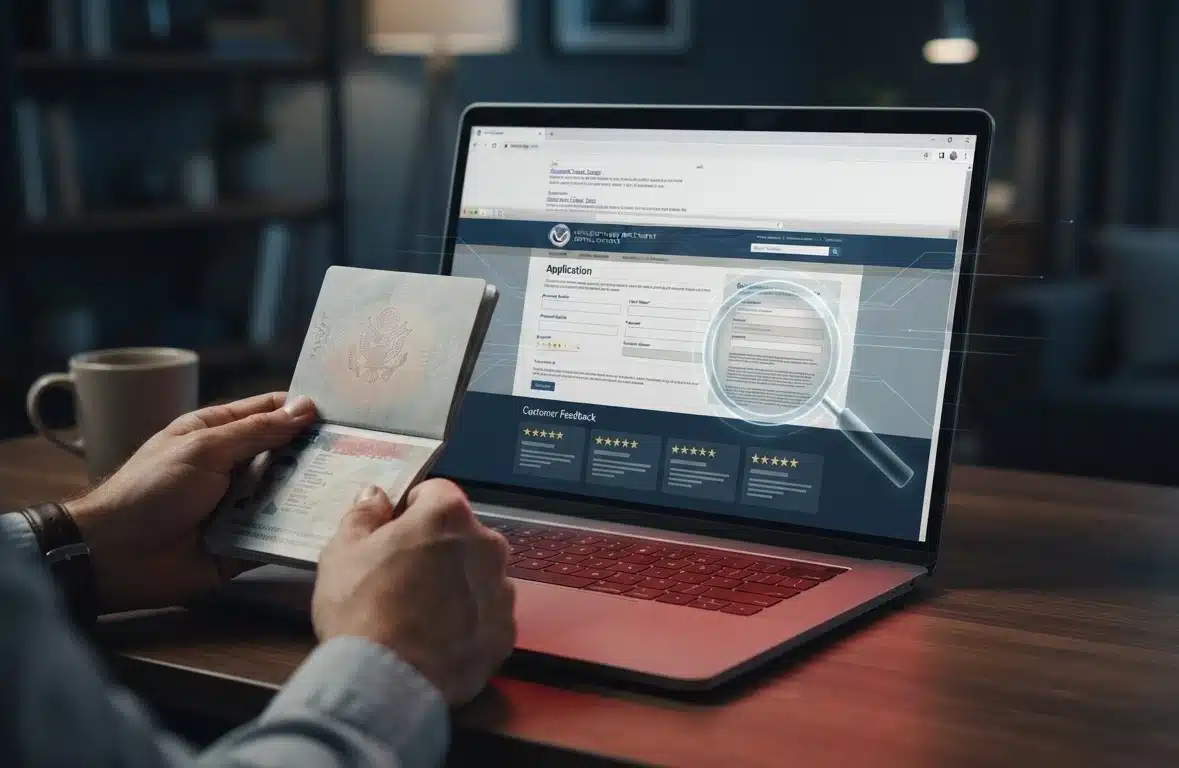
The Federal Trade Commission (FTC) has filed a complaint against GovAssist LLC, Entry LLC and Scott Zuckerman over an alleged government impersonation scheme targeting consumers seeking U.S. passport and travel-related services. The case highlights how paid search advertising, misleading service promises and allegedly fake customer reviews can be used to make commercial websites appear connected to official government services. According to the FTC, the defendants allegedly used websites and sp
Fake Reviews, Deceptive Ads: FTC Targets Alleged Passport Scam
![]()
According to the FTC, the defendants allegedly used websites and sponsored search results to attract travelers, collect personal and financial information, and mislead consumers about the services they would receive. The complaint was filed in the U.S. District Court for the District of Puerto Rico.
How the Government Impersonation Scheme Allegedly Worked?
The FTC alleges that, since at least October 2023, GovAssist, Entry and Zuckerman operated websites including GovAssist.com, Entry.com and IVS.us, offering passport applications, passport-related services, visa applications and visa renewals.
The complaint states that the websites presented themselves as affiliated with the U.S. State Department, although the defendants were neither the federal government nor authorized government-affiliated providers of passport-related services.
The alleged operation relied on paid search ads to reach people looking for official passport information. Searches such as “apply for a new passport,” “passport renewal,” and “passport renewal online” routinely returned IVS.us and Entry.com pages among Google’s top sponsored results, according to the FTC.
This approach allegedly placed commercial services in locations where users might expect to find official government resources. The distinction matters because consumers searching for essential documents may not recognize that a sponsored result belongs to a private company rather than a government agency.
Misleading Passport Service Claims and Hidden Costs
The FTC alleges that the defendants made false promises about what their services could deliver, including claims that they could directly issue U.S. passports. In many cases, consumers allegedly received only a completed passport application that was available for free through the State Department’s website.
The complaint also challenges the companies’ pricing disclosures. Although their advertisements or websites reportedly stated that services started at $89, the FTC alleges that the lowest available price was $119, plus a $29 shipping fee, bringing the total to $148.
Consumers also needed to pay the State Department when submitting their passport applications. According to the complaint, the defendants prominently displayed their own prices while omitting or downplaying the additional government fee, potentially leaving customers unaware that they would have to pay again.
Delivery claims are another part of the case. The FTC alleges that the defendants advertised expedited passport services promising delivery in as little as six to 10 business days or three to four business days. The agency contends these promises were false because the timelines were faster than the quickest expedited service available through the State Department, the only source of U.S. passports.
Fake Reviews and Consumer Trust
The complaint further alleges that the defendants used fake positive reviews to make their services appear legitimate. Their websites reportedly highlighted excellent ratings based on consumer feedback published on Trustpilot and other review platforms.
According to the FTC, those ratings relied on high numbers of fake positive reviews. If established, the allegations would show how misleading reviews can reinforce the credibility created by sponsored search placements, making it harder for consumers to distinguish legitimate services from deceptive offerings.
The alleged combination of deceptive ads and fake reviews is central to the case because consumers may rely on both search rankings and customer feedback when deciding which service to trust.
FTC Alleges Violations of Three Federal Laws
The FTC alleges that the defendants violated the FTC Act, the Impersonation Rule and the Gramm-Leach-Bliley Act. The complaint targets the alleged impersonation of government services, misleading representations about passport processing and pricing, and the use of false consumer reviews.
Zuckerman, identified as the owner and sole member of GovAssist and Entry, allegedly operated the scheme while subject to an FTC order in an earlier, unrelated case involving Support King LLC. That case concerned stalkerware and resulted in a final administrative order addressing data privacy.
The FTC said its staff received assistance from the U.S. Postal Inspection Service, the U.S. Attorney’s Office for the District of Puerto Rico and the U.S. Department of State. The Commission authorized the complaint in a 2-0 vote.
What the Case Reveals About Online Consumer Fraud
The allegations illustrate how consumer fraud can exploit the gap between what users expect from an online search and what a website actually provides. A sponsored result may appear prominently, but its placement does not establish that the service is government-operated or officially authorized.
The case also highlights the role of pricing transparency and review authenticity in online trust. Claims about faster processing, low starting prices, and positive customer experiences can influence purchasing decisions, particularly when consumers need time-sensitive travel documents.
The FTC has emphasized that filing a complaint does not establish that the defendants violated the law. The case will be decided by the court.
For consumers, the allegations underscore the importance of distinguishing official government services from third-party providers and checking fees, processing claims, and reviewing credibility before sharing personal or financial information. The FTC also states that it will never demand money, threaten consumers, instruct them to transfer money, or promise them a prize.
![]()
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare
site-verification-ok
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare
site-verification-ok
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Operation Serengeti III Nets 1,462 Arrests and $105M in Cybercrime Crackdown
INTERPOL’s Operation Serengeti III targeted cybercrime in 21 African countries, recovering over $105 million and identifying 65,929 victims…
Operation Serengeti III Nets 1,462 Arrests and $105M in Cybercrime Crackdown
-
Cybersecurity News
-
EU Opens Booking.com DSA Investigation Over Fake Listings and Phishing Scams
The EU's Booking.com DSA investigation targets fake listings, Booking.com phishing scams and hidden ads. Fines could hit 6% of global turnover. Related Posts: Claude Duet AI Agent Takes On OpenAI Dots and Muse Gemini in Apple CarPlay Arrives on Google Maps Chrome ClickFix Protection Scans Risky Clipboard Commands The post EU Opens Booking.com DSA Investigation Over Fake Listings and Phishing Scams appeared first on Daily CyberSecurity.
EU Opens Booking.com DSA Investigation Over Fake Listings and Phishing Scams
The EU's Booking.com DSA investigation targets fake listings, Booking.com phishing scams and hidden ads. Fines could hit 6% of global turnover.
Related Posts:
- Claude Duet AI Agent Takes On OpenAI Dots and Muse
- Gemini in Apple CarPlay Arrives on Google Maps
- Chrome ClickFix Protection Scans Risky Clipboard Commands
The post EU Opens Booking.com DSA Investigation Over Fake Listings and Phishing Scams appeared first on Daily CyberSecurity.
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Scammers Abuse Frame.io Notifications to Steal Microsoft 365 Credentials
Ocean Security found a phishing campaign, dubbed Phantom Preview, that abused legitimate Frame.io notifications and hidden PDF links…
Scammers Abuse Frame.io Notifications to Steal Microsoft 365 Credentials
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Nearly 480,000 Phishing Emails Traced to Computer Hidden Behind Hotel Fridge
Japanese police arrested a Chinese couple accused of hiding a computer in a Kobe hotel to send phishing emails and using stolen credit card details for purchases.
Nearly 480,000 Phishing Emails Traced to Computer Hidden Behind Hotel Fridge
-
Hackread – Latest Cybersecurity, Tech, Crypto & Hacking News
-
Microsoft Seizes YAM Store and Phishing Kit Domains Linked to 1B Malicious Messages
Microsoft and Health-ISAC seize domains linked to YAM Store, CoGUI and Iron Man, services that enabled over 1…
Microsoft Seizes YAM Store and Phishing Kit Domains Linked to 1B Malicious Messages
-
Cybersecurity News
-
Meta, Tech Firms and Police Hit West Africa Scam Centers in Joint Operation That Led to 28 Arrests
A scam crackdown on West Africa scam centers by Meta, tech firms and police removed 3.7M accounts, led to 28 arrests and freed 117 victims. Related Posts: DOJ Charges Engineer After OpenAI Recording Device Arrest DOJ Disrupts DPRK IT Worker Schemes Across More Than 70 US Companies Ivanti Connect Secure Zero-Day Chain CVE-2026-104935 Exploited by UTA0576 to Gain Root Access The post Meta, Tech Firms and Police Hit West Africa Scam Centers in Joint Operation That Led to 28 Arrests appeared firs
Meta, Tech Firms and Police Hit West Africa Scam Centers in Joint Operation That Led to 28 Arrests
A scam crackdown on West Africa scam centers by Meta, tech firms and police removed 3.7M accounts, led to 28 arrests and freed 117 victims.
Related Posts:
- DOJ Charges Engineer After OpenAI Recording Device Arrest
- DOJ Disrupts DPRK IT Worker Schemes Across More Than 70 US Companies
- Ivanti Connect Secure Zero-Day Chain CVE-2026-104935 Exploited by UTA0576 to Gain Root Access
The post Meta, Tech Firms and Police Hit West Africa Scam Centers in Joint Operation That Led to 28 Arrests appeared first on Daily CyberSecurity.
-
Firewall Daily – The Cyber Express

-
Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes
A new Kerala Police MoU will bring threat intelligence into cybercrime investigations in the state. Cyble, an AI-native cybersecurity company, has signed a three-year Memorandum of Understanding with Kerala Police that covers intelligence support, investigative assistance and capacity building. The agreement was signed through Cyble's Indian subsidiary, Cyble Infosec India Private Limited. It will support the Kerala Police Cyber Operations wing and Cyberdome in identifying and investigating e
Kerala Police Signs MoU With Cyble to Use Threat Intelligence in Cybercrime Probes
![]()
Why the Kerala Police MoU Focuses on Threat Intelligence
According to Cyble, cybercriminals increasingly use underground online forums and illicit marketplaces to trade stolen credentials, distribute leaked data, coordinate ransomware operations and facilitate fraud. Identifying these activities before they cause harm requires timely intelligence and effective collaboration between technology providers and law enforcement agencies. [caption id="attachment_114716" align="aligncenter" width="600"]What MoU Covers
Under the MoU, Cyble will support Kerala Police with intelligence relevant to cybercrime investigations. This includes compromised credentials, ransomware activity, data leaks, phishing and fraud infrastructure, and the impersonation of government and police brands. The collaboration has three other parts:- No-cost evaluation access to select Cyble platforms.
- Training for police officers in open-source intelligence (OSINT) and dark web investigations.
- Joint research into emerging threats such as AI-enabled fraud, deepfakes, mule account networks and investment scams.