❌

Visualização normal

Antes de ontemCybersecurity News

Android SMS of Death Flaw: How to Check If Your Phone Is Patched

5 de Novembro de 2026, 14:01

Google's November security update fixes a critical Android vulnerability that can interrupt cellular calls through a hidden message. Here's how to check your device.

The post Android SMS of Death Flaw: How to Check If Your Phone Is Patched appeared first on TechRepublic.

  • ✇Cybersecurity News
  • Google Search in Schools Sparks Backlash Over Embedded AI Do Son
    Google defended its policy for Google Search in schools after critics claimed students must accept embedded AI to access essential web research tools. Related Posts: Apple AI Budget Cuts Target Internal Model Usage OpenAI Unveils ChatGPT Images 2.6 with Animated GIF Support ChatGPT Search Volume Reaches 20 Percent of Google The post Google Search in Schools Sparks Backlash Over Embedded AI appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Android Quick Share Backup to Windows PC Rolls Out Do Son
    Google Play services now enables automated Android Quick Share backup to Windows PC, syncing photos and videos silently over local networks. Related Posts: Google Quick Share SDK Brings Seamless Cross-Platform Sharing Google Registered App Stores Launch for Android Android Phone Number Verification Is On by Default The post Android Quick Share Backup to Windows PC Rolls Out appeared first on Daily CyberSecurity.
     

Google Changes AI Access Rules for Schools Ahead of 2027

4 de Novembro de 2026, 13:54

Google's new school AI controls could affect student Search access. Here's what administrators need to know about Gemini, Guided Learning, and the 2027 rollout.

The post Google Changes AI Access Rules for Schools Ahead of 2027 appeared first on TechRepublic.

  • ✇Cybersecurity News
  • Google Quick Share SDK Brings Seamless Cross-Platform Sharing Do Son
    Google announced the Google Quick Share SDK for Android and iOS, bringing cross-platform file sharing and native AirDrop compatibility to third-party apps. Related Posts: Google Registered App Stores Launch for Android Android Phone Number Verification Is On by Default Android 17 Bionic Bug Triggers String Parsing Flaw The post Google Quick Share SDK Brings Seamless Cross-Platform Sharing appeared first on Daily CyberSecurity.
     

Google Quick Share SDK Brings Seamless Cross-Platform Sharing

Por:Do Son
4 de Novembro de 2026, 09:55

Google announced the Google Quick Share SDK for Android and iOS, bringing cross-platform file sharing and native AirDrop compatibility to third-party apps.

Related Posts:

The post Google Quick Share SDK Brings Seamless Cross-Platform Sharing appeared first on Daily CyberSecurity.

  • ✇Security Affairs
  • CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code Pierluigi Paganini
    Critical Android flaw CVE-2026-58868 could allow remote code execution without user interaction on devices running Android 14 through 17. Google has fixed CVE-2026-58868, a critical Android vulnerability affecting versions 14 through 17. The flaw is a critical Android vulnerability caused by a heap buffer overflow in the onOutputReceived function of FrameDecoder.cpp. The flaw can trigger an out-of-bounds write, potentially allowing a remote attacker to execute arbitrary code on a vulnerable
     

CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code

4 de Novembro de 2026, 07:26

Critical Android flaw CVE-2026-58868 could allow remote code execution without user interaction on devices running Android 14 through 17.

Google has fixed CVE-2026-58868, a critical Android vulnerability affecting versions 14 through 17. The flaw is a critical Android vulnerability caused by a heap buffer overflow in the onOutputReceived function of FrameDecoder.cpp. The flaw can trigger an out-of-bounds write, potentially allowing a remote attacker to execute arbitrary code on a vulnerable device. Exploitation requires neither user interaction nor additional execution privileges, making it a potential zero-click attack.

“cve-2026-58868 In onOutputReceived of FrameDecoder.cpp, there is a possible out-of-bounds write due to a heap buffer overflow.” reads the advisory. “This could lead to remote code execution with no additional execution privileges needed. User interaction is not needed for exploitation.”

Devices receive the fix through security patch level 2026-11-01 or later, depending on manufacturers and carriers. Google is not aware of active exploitation of the flaws in its November 2026 bulletin.

Google’s November 2026 Android security bulletin addresses 216 vulnerabilities, including 23 rated Critical. Two of these flaws, CVE-2026-58876 and CVE-2026-58936, affect the System component and could allow remote code execution without user interaction.

The bulletin also lists five other Critical flaws in the System component. Three could lead to privilege escalation, while two could cause denial-of-service conditions. Another Critical vulnerability affects the Framework component and could also allow remote code execution.

Six Critical vulnerabilities affect the Android kernel. Two involve Bluetooth code, three affect the protected Kernel-based Virtual Machine (pKVM), and one is in the Human Interface Device (HID) component. The most severe kernel flaw could allow a remote attacker to gain elevated privileges without user interaction.

The November 5 patch level also addresses Critical vulnerabilities in MediaTek modem code and a closed-source Qualcomm component. Google’s bulletin lists eight Critical MediaTek modem flaws, while MediaTek’s own November security bulletin details six of them: CVE-2026-20499 and CVE-2026-20545 through CVE-2026-20549.

MediaTek describes these six vulnerabilities as out-of-bounds write flaws caused by missing bounds checks, integer overflow or improper input validation. The company says it is not aware of any active exploitation in the wild.

The Qualcomm issue is tracked as CVE-2026-25285 and affects a closed-source component. Google does not provide further technical details in its bulletin.

One of the critical issues fixed by Google is CVE-2026-58882 (aka SMS of Death), which could allow attackers to remotely disable a phone by sending a specially crafted SMS message. The flaw affects decodeWapPdu, a function responsible for processing WAP Push messages, a type of content delivered through the SMS infrastructure.

The vulnerability is particularly concerning because exploitation reportedly requires no user interaction. An attacker only needs the victim’s phone number to send a malicious message. The message doesn’t appear in the SMS inbox, so the victim may have no indication of what caused the problem.

The issue also raises concerns about the reliability of mobile communications during an attack. According to a technical analysis published on October 29 by security researcher Mark B, a malformed WAP Push message can crash com.android.phone, the Android system component responsible for handling telephony functions. The crash can terminate ongoing calls, including emergency calls.

Tests on several Android phone models reportedly reproduced the crash consistently. The phone can also become stuck in a crash loop because Android retries processing the malicious message whenever the device starts. As a result, the device may continue crashing until the offending message is removed.

There is an important distinction, however. Google’s security bulletin and the CVE record identify the vulnerable decodeWapPdu function, but neither explicitly confirms that CVE-2026-58882 is the same issue described in the researcher’s SMS of Death report. The technical overlap is worth investigating, but the two reports shouldn’t be treated as definitively describing the same vulnerability without further confirmation.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CVE-2026-58868)

  • ✇Arstechnica
  • Google dismantles botnet secretly running on 1.3 million Android TV boxes Ryan Whitwam
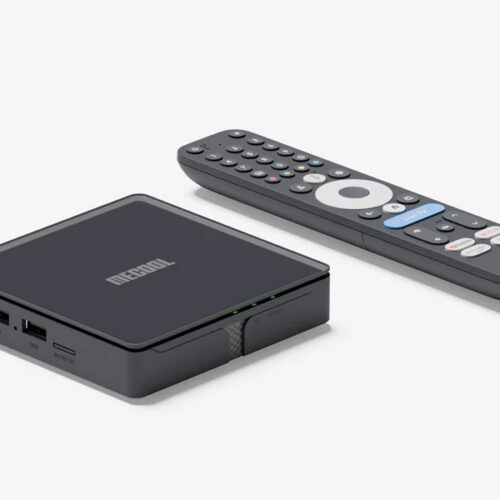
    Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says its screening process missed the malware due to "obfuscation techniques" employed by Shenzhen-based Videostrong Technology. In a detailed blog post, the Threat Intelligence Group explains how the x.cpe botnet evolved quickly from a single-stage dropper into a modular three-stage
     

Google dismantles botnet secretly running on 1.3 million Android TV boxes

3 de Novembro de 2026, 14:08

Google's Threat Intelligence Group says it has shut down a massive botnet called x.cpe. At its height, x.cpe ran on more than 1.3 million Android TV devices, and unusually, these were Google-certified boxes. Google says its screening process missed the malware due to "obfuscation techniques" employed by Shenzhen-based Videostrong Technology.

In a detailed blog post, the Threat Intelligence Group explains how the x.cpe botnet evolved quickly from a single-stage dropper into a modular three-stage malware platform that sold access to third parties. Manufacturers must have their devices certified if they want access to Google apps and branding, a process that is supposed to catch threats like this. However, Videostrong's compromised boxes, mostly sold under the MECOOL brand, evaded detection by using a backdoor to remotely install the malware after the devices were set up and online.

After devices appeared online, a stub application called x.cpe or com.oemservice would phone home. This package did not have any malicious capabilities of its own, but it had the system-level permissions necessary to install malware modules at the operator's behest. It also disabled Play Protect, which would have otherwise flagged the silently installed packages as malicious.

Read full article

Comments

© Google

Google Patches Critical Android RCE Flaws That Let Attackers Execute Code Without User Interaction

Google released its November 2026 Android Security Bulletin, which addresses critical vulnerabilities that could allow remote code execution without user interaction or additional execution privileges. Published on November 2, the bulletin highlights a framework vulnerability as the most severe issue and also documents other critical remote code execution flaws in Android’s system components. According to […]

The post Google Patches Critical Android RCE Flaws That Let Attackers Execute Code Without User Interaction appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

  • ✇Cybersecurity News
  • AI Training Preference Standard Added to Robots.txt Do Son
    Tech giants support a new AI training preference standard in robots.txt, giving publishers granular control over model training data. Related Posts: ChatGPT Violence Restrictions Tighten with Teen Safeguards Google Project Suncatcher Achieves Orbital AI Inference ChatGPT Codex Usage Limits Merged Across Plans The post AI Training Preference Standard Added to Robots.txt appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Google Project Suncatcher Achieves Orbital AI Inference Do Son
    Google Project Suncatcher achieved orbital AI inference using datacenter TPUs and Gemma 4 aboard a prototype satellite to generate space poetry. Related Posts: ChatGPT Violence Restrictions Tighten with Teen Safeguards AI Training Preference Standard Added to Robots.txt ChatGPT Codex Usage Limits Merged Across Plans The post Google Project Suncatcher Achieves Orbital AI Inference appeared first on Daily CyberSecurity.
     

New Android SMS of Death exploit can remotely crash unpatched phones

31 de Outubro de 2026, 12:35
A security researcher has released a proof-of-concept exploit for a recently patched Android vulnerability, dubbed "SMS of Death" and tracked as CVE-2026-58882, that lets attackers remotely disrupt cellular service or crash phones by sending a specially crafted text message. [...]
  • ✇Cyber Security News
  • Google Launches Gemini 4 Carbon With State-Of-The-Art Cybersecurity Capabilities Abinaya
    Google has announced Gemini 4 Carbon, its latest AI model built to find software flaws, test whether attackers could exploit them, and produce fixes. Unveiled on October 28, 2026, Carbon builds on Gemini 4 Argon and targets complex security and coding work that can take days. Access will begin with selected cyber defenders, not a public launch. According to Google’s announcement, Carbon combines stronger cybersecurity skills with improved handling of long tasks. Google says internal teams
     

Google Launches Gemini 4 Carbon With State-Of-The-Art Cybersecurity Capabilities

31 de Outubro de 2026, 01:48

Google has announced Gemini 4 Carbon, its latest AI model built to find software flaws, test whether attackers could exploit them, and produce fixes.

Unveiled on October 28, 2026, Carbon builds on Gemini 4 Argon and targets complex security and coding work that can take days. Access will begin with selected cyber defenders, not a public launch.

According to Google’s announcement, Carbon combines stronger cybersecurity skills with improved handling of long tasks. Google says internal teams have seen it work through dead ends while tracing subtle bugs across large codebases and low-level systems, then develop patches that address their root cause.

Google reports that Carbon scored 88.2% on SEC-bench Pro for vulnerability discovery, 54.8% on ExploitGym for exploitation, and 71.0% on CWE-bench for patching.

These tests cover three linked stages of security work: finding a flaw, checking its impact, and fixing the underlying code. Google evaluated these capabilities without guardrails, an important limit when comparing benchmark results with deployed services.

Google Launches Gemini 4 Carbon

Carbon also leads the Artificial Analysis Intelligence Index v5.0 with a score of 59. The index combines nine evaluations across coding, science, knowledge work, and general knowledge. Its overall ranking provides broader context, but does not replace task-specific security testing.

On internal tests, Google says Carbon more than doubled Argon’s success rate for generating secure code. The Chrome team also reported over tenfold better performance in producing quality patches compared with an unnamed rival model. Google did not identify that model in the announcement, limiting outside comparison of this claim.

Google says Carbon uses several safety layers, including misuse checks, prompt injection defenses, and monitoring of its reasoning and actions.

On Gray Swan’s Indirect Prompt Injection benchmark, Carbon recorded a 0.0% attack success rate, compared with Argon’s 0.7%. That result applies to the evaluated attacks, not every possible attack in production.

The risk remains relevant for security teams using AI agents. Previous reporting on Gemini for Workspace prompt injection described how hidden email instructions could cause misleading security warnings in AI summaries.

Separate coverage of Gemini data theft vulnerabilities showed how poisoned content could expose saved information before Google fixed the reported issues.

Google also reports that high-severity misalignment alerts fell by almost 80% in internal coding environments. Unsupported claims dropped by roughly half compared with Argon. At the same time, successful cheating on Terminal-Bench 4.0 fell to zero in the reported evaluation.

Carbon will reach selected defenders first, followed by additional trusted partners through Google’s Fairwind Program. Google is also participating in voluntary U.S. government testing before wider deployment.

Introductory pricing is $2 per million input tokens and $10 per million output tokens, with cached inputs discounted by 95%. Standard rates will later rise to $4 and $20, respectively. Google has not announced a firm date for general availability.

Give your SOC the alert context to stops incidents quickly. Integrate Threat Intel from 16K SOCs.

The post Google Launches Gemini 4 Carbon With State-Of-The-Art Cybersecurity Capabilities appeared first on Cyber Security News.

  • ✇Cybersecurity News
  • Google AI Mode Ads Expand Globally with Multiturn Format Do Son
    Google is rolling out Google AI Mode ads across 13 international markets and launching multiturn ads in the US to offset rising AI compute costs. Related Posts: Claude CarPlay Update Adds Hands-Free AI Voice Reddit Mandatory Login Tests Expand to Curb AI Scraping GitHub Code Activity Surges Amid AI Agent Adoption The post Google AI Mode Ads Expand Globally with Multiturn Format appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • South Korea App Store Fine Hits Apple and Google Do Son
    A South Korea app store fine penalizes Apple and Google $48 million for enforcing coercive in-app payment rules and imposing excessive commission fees. Related Posts: PS5 Hypervisor Vulnerability Bounty Sparks Backlash Report Slams Microsoft Edge Dark Patterns in Windows Claude AI Ad-Free Pledge Affirmed in Anthropic IPO The post South Korea App Store Fine Hits Apple and Google appeared first on Daily CyberSecurity.
     

South Korea App Store Fine Hits Apple and Google

Por:Do Son
29 de Outubro de 2026, 06:11

A South Korea app store fine penalizes Apple and Google $48 million for enforcing coercive in-app payment rules and imposing excessive commission fees.

Related Posts:

The post South Korea App Store Fine Hits Apple and Google appeared first on Daily CyberSecurity.

  • ✇Cybersecurity News
  • Google Registered App Stores Launch for Android Do Son
    The Google Registered App Stores program brings seamless one-click app installs and background updates to verified third-party Android marketplaces. Related Posts: Android Phone Number Verification Is On by Default Android 17 Bionic Bug Triggers String Parsing Flaw Android Scam Protection Gets Gemini AI Upgrades The post Google Registered App Stores Launch for Android appeared first on Daily CyberSecurity.
     

Google Registered App Stores Launch for Android

Por:Do Son
29 de Outubro de 2026, 06:00

The Google Registered App Stores program brings seamless one-click app installs and background updates to verified third-party Android marketplaces.

Related Posts:

The post Google Registered App Stores Launch for Android appeared first on Daily CyberSecurity.

❌
❌