❌

Visualização normal

Antes de ontemCybersecurity News
  • ✇Security | CIO
  • OpenAI buys tiny software developer to improve Codex
    OpenAI is buying Pierre Computer Company in order to incorporate the San Francisco-based software developer’s Code.Storage infrastructure layer for Git into its Codex AI-powered programming tool. Pierre Computer, whose employees number just barely in the double digits, has got plenty of clout for its small size. It’s well-known for Code.Storage offering, as well as for its open-source software libraries, Trees and Diffs, which OpenAI already uses in Codex. OpenAI has
     

OpenAI buys tiny software developer to improve Codex

6 de Novembro de 2026, 10:42

OpenAI is buying Pierre Computer Company in order to incorporate the San Francisco-based software developer’s Code.Storage infrastructure layer for Git into its Codex AI-powered programming tool.

Pierre Computer, whose employees number just barely in the double digits, has got plenty of clout for its small size. It’s well-known for Code.Storage offering, as well as for its open-source software libraries, Trees and Diffs, which OpenAI already uses in Codex.

OpenAI has experienced some of the limitations of Git itself, and its in-house engineering teams are already working to improve its support for human coders and AI agents working in parallel. Earlier this week the company described how it built a new back end for Git repositories, Pando, to enable concurrent working at scale.

The AI developer has been pushing Codex more aggressively this year: offering it to Mac users and expanding it to Windows. It cited Pierre Computer’s ability to help developers review code as one of the reasons for the acquisition. OpenAI highlighted the Diffs’ Edit mode and the recently released Highlights as components that were particularly helpful to development teams.

Announcing the deal on its news page, OpenAI set out how it would integrate the company into its existing offerings. “With the Pierre team, we wish to set the standard for modern software development: from the first branch an agent creates to that magic moment when code is deployed to the world. We want to make Codex the place where developers and agents take on their most ambitious projects.”

Neither company disclosed details of the acquisition price. OpenAI said that Code.Storage customers will be able to continue using the product until it brings the features into Codex, while Pierre Computer’s open-source projects will remain open, and OpenAI will continue to contribute to them.

This article first appeared on InfoWorld.

  • ✇Cybersecurity News
  • Windows Paint RCE CVE-2026-83844 Affects Hundreds of Millions Do Son
    Microsoft patched Windows Paint RCE vulnerability CVE-2026-83844 with an 8.1 CVSS score. Update now to block potential remote code execution attacks. Related Posts: Penpot File Takeover Flaw Details and PoC Exploit Publicly Disclosed Attackers Exploit SonicWall SonicOS SSLVPN Flaw CVE-2026-19868 in the Wild Veeam Releases Kernel Updates to Fix Critical CVE-2026-98432 Flaw Across Backup Appliances The post Windows Paint RCE CVE-2026-83844 Affects Hundreds of Millions appeared first on Daily Cy
     
  • ✇Cybersecurity News
  • SnappyMail Remote Code Execution Chain Disclosed With Public PoC Exploit Code Do Son
    SnappyMail RCE chain disclosed with a public proof-of-concept exploit. The auth bypass hit dev builds only; avoid master builds from Oct 22-Nov 4. Related Posts: Rails 8.0.5.2 and 8.1.4.1 Fix 21 Security Flaws, Including Critical Active Storage File Write Bug Airbyte Vulnerability Exploited in the Wild Lets Attackers Run Code in Connector Builder PoC Exploit and Technical Details Published for Puppet Server RCE Flaw CVE-2026-115731 (CVSS 9.4) The post SnappyMail Remote Code Execution Chain Di
     
  • ✇Cybersecurity News
  • PoC Exploit and Technical Details Published for Puppet Server RCE Flaw CVE-2026-115731 (CVSS 9.4) Do Son
    Puppet Server RCE CVE-2026-115731 (CVSS 9.4) now has a public proof-of-concept exploit. Update OpenVox and Puppet Enterprise to patched versions. Related Posts: Rails 8.0.5.2 and 8.1.4.1 Fix 21 Security Flaws, Including Critical Active Storage File Write Bug SnappyMail Remote Code Execution Chain Disclosed With Public PoC Exploit Code Airbyte Vulnerability Exploited in the Wild Lets Attackers Run Code in Connector Builder The post PoC Exploit and Technical Details Published for Puppet Server
     
  • ✇Cybersecurity News
  • INFINITT PACS Vulnerabilities: 2 Critical Flaws Do Son
    Patch two critical INFINITT PACS vulnerabilities today. Learn how CVE-2026-16305 and CVE-2026-16306 expose medical systems and secure your network now. Related Posts: Rails 8.0.5.2 and 8.1.4.1 Fix 21 Security Flaws, Including Critical Active Storage File Write Bug SnappyMail Remote Code Execution Chain Disclosed With Public PoC Exploit Code Airbyte Vulnerability Exploited in the Wild Lets Attackers Run Code in Connector Builder The post INFINITT PACS Vulnerabilities: 2 Critical Flaws appeared
     
  • ✇Cybersecurity News
  • Linux 7.4 Merge Window Sets Record with AI Patches Do Son
    The Linux 7.4 merge window reached a record 19,671 commits as Linus Torvalds highlighted early AI patches and major hardware support. Related Posts: OpenBSD 8.0 Release Introduces Kernel Hardening and Day-One Errata GNOME OS Preview Brings GNOME 51.1 to the Public Linux Assisted-by Tag Dropped for AI Patches The post Linux 7.4 Merge Window Sets Record with AI Patches appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • PSK Agent RAT Hits Magento Stores Through StyleSmuggler Exploitation Do Son
    StyleSmuggler exploitation of CVE-2026-75650 drops the PSK Agent RAT and a PHP webshell on Magento stores. See how to detect and respond. Related Posts: Hugging Face Malware Campaign Infects AI GPU Servers Google Disrupts Videostrong XCPE Botnet on Android TV NIK C2 Framework Integrates OpenAI API to Analyze Stolen Data in Live Attacks The post PSK Agent RAT Hits Magento Stores Through StyleSmuggler Exploitation appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Arista Security Vulnerabilities Risk Remote Code Execution Do Son
    Arista fixed critical Arista security vulnerabilities CVE-2026-111497 and CVE-2026-98432 that allow unauthenticated remote code execution. Update now. Related Posts: Ubuntu Kernel Fixes for CVE-2026-98432 (CVSS 9.8) Land in Proposed Pocket cPGuard Supply Chain Attack Pushes Backdoor Through Update Channel TeamViewer Client Vulnerability Enables Remote Code Execution The post Arista Security Vulnerabilities Risk Remote Code Execution appeared first on Daily CyberSecurity.
     
  • ✇Security | CIO
  • Salesforce acquires Rune Technologies to add offline capabilities to Missionforce
    Salesforce is in the process of acquiring US-based defense-tech startup Rune Technologies to add offline capabilities to Missionforce, its Agentforce avatar for national security, defense, aerospace, and government agencies. The startup’s TyrOS platform will be used to extend Missionforce into frontline military logistics, enabling deployed units to forecast supply requirements, optimize resource allocation, and make operational decisions even when network connectivity
     

Salesforce acquires Rune Technologies to add offline capabilities to Missionforce

2 de Novembro de 2026, 09:58

Salesforce is in the process of acquiring US-based defense-tech startup Rune Technologies to add offline capabilities to Missionforce, its Agentforce avatar for national security, defense, aerospace, and government agencies.

The startup’s TyrOS platform will be used to extend Missionforce into frontline military logistics, enabling deployed units to forecast supply requirements, optimize resource allocation, and make operational decisions even when network connectivity is unavailable, the CRM software provider said in a statement.

That is possible due to TyrOS’s offline-first architecture that caches last-known information about inventory, vehicles, and transportation routes using NFC-based hardware, allowing deployed units to access operational data without a continuous connection to centralized systems, according to the company’s website.

The platform can also exchange prioritized information between distributed nodes through a mesh network when connectivity becomes available, the website showed.

Currently, Missionforce acts as a system of record for personnel, equipment, and supplies across defense organizations, while providing tools for strategic planning.

For CIOs of defense organizations, the acquisition could mean improved operational continuity and better utilization of available resources, said Premal Shah, principal analyst at Avasant.

This would be helpful because frontline units could now continue to access critical logistics information and coordinate resource requirements during connectivity disruptions, rather than relying on manual records or waiting for centralized systems to become available, Shah added.

Once connectivity is restored, information can be synchronized across distributed nodes, helping headquarters regain visibility into frontline requirements and make more informed decisions about resource allocation and resupply, he further added.

However, implementing technologies such as TyrOS comes with its own set of risks, according to Pareekh Jain, principal analyst at Pareekh Consulting.

CIOs need to ensure that information updated by different military units while offline does not result in conflicting records when their systems reconnect, while also maintaining data security across distributed locations, Jain said.

TyrOS, though, is not an untested technology in military environments. Its platform is already deployed with the US Army and US Marine Corps, giving Rune an established presence in the defense sector, Salesforce said.

It plans to use the acquisition to build the foundation for a recent 10-year contract it won with the US Army, which has a $5.6 billion ceiling and focuses on modernizing military operations. The transaction is expected to close by April 2027.

South Korea President Eyes Cybersecurity Task Force After North Korea-Linked Crypto Heist

3 de Novembro de 2026, 05:10

cybersecurity task force

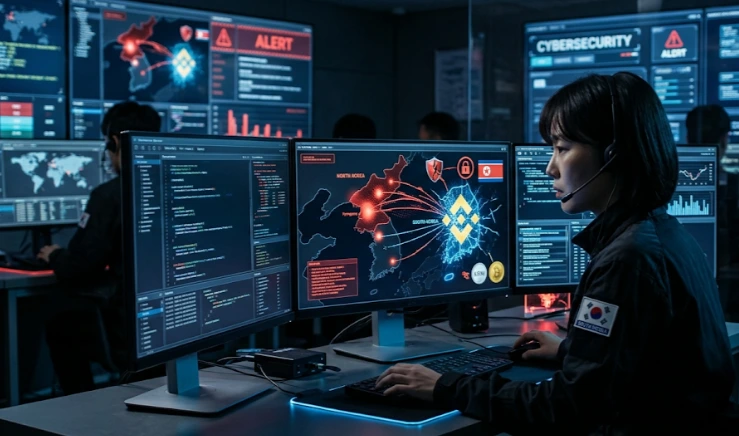
South Korean President Lee Jae-myung has directed officials to look into creating a cybersecurity task force. A wave of hacking incidents at financial firms and a massive cryptocurrency theft linked to North Korea have raised alarm over the country's digital defenses.  Lee instructed on Tuesday, Nov. 3, 2026, during a Cabinet meeting at Cheong Wa Dae in Seoul. The proposed task force would focus solely on strengthening online security. 

Cybersecurity Task Force and North Korea's Binance Heist 

The directive follows a string of attacks on domestic financial companies that exposed customer data. The most recent targets were Mirae Asset Global Investments, cryptocurrency exchange Bithumb, and Daishin Securities. It also comes after the hacking of Binance, the world's largest crypto exchange, in which more than US$6 billion in cryptocurrency was stolen. The U.S. Federal Bureau of Investigation (FBI) has since attributed the theft to North Korea, which gives the incident a national security dimension beyond financial crime. Lee said cyber threats have grown severe enough to endanger the national economy, national security and the daily lives of ordinary citizens. He called for "a comprehensive prevention system" to address them. According to the president, hacking methods are becoming more sophisticated and widespread, driven partly by advances in artificial intelligence (AI). He said this trend is exposing clear limits in the systems currently used to maintain security.

A Possible "Czar Agency" Amid North Korea Threats 

Lee's plans go further than a single task force. He stressed the need for talks on setting up a pan-government agency responsible for cybersecurity across both the public and private sectors.  He specifically told officials to "proactively consider the formation of a cybersecurity czar agency" that could act as a strong and effective control tower for security management.  The president also ordered officials to thoroughly fix security weaknesses at major state institutions and key national infrastructure, naming information communications, energy, and finance. Because hackers tied to North Korea have repeatedly targeted financial assets, the finance sector is a particularly pressing concern. 

Social Media Limits for Teens Also on the Agenda 

Cybersecurity was not the only digital issue raised at the meeting. Lee also called for quick discussions on the government's plan to restrict adolescents' use of social media.  "The harmful effects (of social media on teenagers) appear to be greater than what we think," Lee said.  The government is pursuing measures to limit social media sign-ups by young teens and to restrict their use of certain services, including algorithm-based ones. The goal is to shield adolescents from the harms of social media.  Lee told Kim Jong-cheol, chairman of the Korea Media and Communications Commission, to "conduct relevant discussions thoroughly and promptly." He pointed to similar efforts already under way in Europe, Australia and Canada.  Kim replied that the plan should be pursued on the basis of social consensus. He said the commission intends to gather public input and finalize the measures in the first half of next year.  Officials will now weigh whether to form a cybersecurity task force and a broader czar agency. Their decisions will shape how South Korea responds to escalating digital threats, including attacks attributed to North Korea. 
  • ✇Cybersecurity News
  • 15 Critical pgAdmin 4 Vulnerabilities Fixed in Version 9.19 Do Son
    The PostgreSQL project resolved 15 critical pgAdmin 4 vulnerabilities in version 9.19, fixing command injection flaw CVE-2026-116241 and credential leaks. Related Posts: Critical MediaTek Vulnerabilities Patched in Chipsets Public PoC Exploit Disclosed for Linux Kernel Bonding Vulnerability Critical FreePBX Vulnerabilities Patched in User Manager The post 15 Critical pgAdmin 4 Vulnerabilities Fixed in Version 9.19 appeared first on Daily CyberSecurity.
     

A gift to scammers: why you should probably keep your birthday a secret

Using a fake DOB or leaving the field blank when making an online account can offer protection from identity theft

You get a call from your bank saying there has been suspicious activity on your account. They read out your name, address and date of birth so you are happy it is a legitimate caller.

But you are talking to criminals who have used your date of birth as part of a web of verifying information to convince you they are someone else.

Continue reading...

© Photograph: kmt_rf/Alamy

© Photograph: kmt_rf/Alamy

© Photograph: kmt_rf/Alamy

  • ✇Cybersecurity News
  • Progress Patches 10.0 CVSS WS_FTP Server Flaw CVE-2026-84295 and 14 Other Bugs Do Son
    Patch 15 WS_FTP Server vulnerabilities now, including 10.0 CVSS flaw CVE-2026-84295 and 9.9 CVSS command injection bug CVE-2026-90868. Related Posts: Android SMS of Death Bug Triggers Remote Reboots JetBrains Patches Critical Flaws in IDEs and Background Services After Certificate Breach CERT/CC Warns of Xerj Authentication Bypass Flaw CVE-2026-97406 The post Progress Patches 10.0 CVSS WS_FTP Server Flaw CVE-2026-84295 and 14 Other Bugs appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • WordPress Core Vulnerability Exploited in the Wild Do Son
    A critical WordPress Core vulnerability is exploited in the wild. Update to WordPress 7.1.4 immediately to fix the unauthenticated race condition RCE. Related Posts: Android SMS of Death Bug Triggers Remote Reboots JetBrains Patches Critical Flaws in IDEs and Background Services After Certificate Breach CERT/CC Warns of Xerj Authentication Bypass Flaw CVE-2026-97406 The post WordPress Core Vulnerability Exploited in the Wild appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Critical EDK II PXE Vulnerability Allows Pre-Boot Remote Code Execution Do Son
    Patch CVE-2026-97631 now. This critical 9.5 CVSS EDK II PXE vulnerability allows unauthenticated pre-boot RCE via crafted ICMP error packets. Related Posts: Kerio Connect Vulnerability CVE-2026-112353 Exploited in the Wild to Steal Mailboxes Apache Kafka Fixes 12 Vulnerabilities, Including a JWT Bypass That Grants Full Cluster Access FreeSWITCH Vulnerability CVE-2026-116779 Exploited in the Wild to Run Commands The post Critical EDK II PXE Vulnerability Allows Pre-Boot Remote Code Execution a
     
  • ✇Cybersecurity News
  • Details and PoC Exploits Released for Two Unpatched free5GC Vulnerabilities Do Son
    Details and PoC are public for two unpatched free5GC vulnerabilities in the 5G core: BSF auth bypass CVE-2026-115926 and an exposed root CA key. Related Posts: Kerio Connect Vulnerability CVE-2026-112353 Exploited in the Wild to Steal Mailboxes Apache Kafka Fixes 12 Vulnerabilities, Including a JWT Bypass That Grants Full Cluster Access FreeSWITCH Vulnerability CVE-2026-116779 Exploited in the Wild to Run Commands The post Details and PoC Exploits Released for Two Unpatched free5GC Vulnerabil
     
  • ✇Cybersecurity News
  • TeamViewer Patches Three High-Severity Vulnerabilities in Client Software Do Son
    Update to TeamViewer 15.83 to patch three high-severity TeamViewer vulnerabilities: CVE-2026-92372, CVE-2026-111585, and CVE-2026-92374. Related Posts: Intelbras Camera Vulnerability Lets Attackers Knock Mibo Cameras Offline Body-Parser Flaw CVE-2026-111181 Lets One Request Crash Express Servers, PoC Public Unauthenticated File Read Leaks Master Key in LiteLLM Enterprise Proxy, CVSS 10.0 The post TeamViewer Patches Three High-Severity Vulnerabilities in Client Software appeared first on Daily
     
  • ✇Cybersecurity News
  • Public PoC Exploit Disclosed for Critical libheif RCE Vulnerabilities Do Son
    Details and PoC exploit code are out for critical libheif vulnerabilities GHSA-x8r2-mggj-j6wr and GHSA-2jg2-4ch7-h545. Upgrade to 1.23.3 now. Related Posts: Intelbras Camera Vulnerability Lets Attackers Knock Mibo Cameras Offline Body-Parser Flaw CVE-2026-111181 Lets One Request Crash Express Servers, PoC Public Unauthenticated File Read Leaks Master Key in LiteLLM Enterprise Proxy, CVSS 10.0 The post Public PoC Exploit Disclosed for Critical libheif RCE Vulnerabilities appeared first on Dail
     
  • ✇Cybersecurity News
  • CISA Adds Adobe Magento and Google Brotli Flaws to KEV Catalog Do Son
    CISA KEV catalog adds actively exploited Magento flaw CVE-2026-48356 and Brotli vulnerability CVE-2026-111497. Patch before November 10. Related Posts: Intelbras Camera Vulnerability Lets Attackers Knock Mibo Cameras Offline Body-Parser Flaw CVE-2026-111181 Lets One Request Crash Express Servers, PoC Public Unauthenticated File Read Leaks Master Key in LiteLLM Enterprise Proxy, CVSS 10.0 The post CISA Adds Adobe Magento and Google Brotli Flaws to KEV Catalog appeared first on Daily CyberSecur
     
  • ✇Cybersecurity News
  • Denmark Ends Collabora Pilot in Blow to Open Source Do Son
    Denmark ends Collabora pilot testing across its public sector after formatting errors disrupted case workflows, securing a quiet victory for Microsoft. Related Posts: Microsoft Voluntary Buyout Program Targets 60,000 Staff Apple Blocks eMudhra Certificates Over Weak Key Flaw Anthropic S-1 IPO Filing Targets Historic $2T Valuation The post Denmark Ends Collabora Pilot in Blow to Open Source appeared first on Daily CyberSecurity.
     
❌
❌