❌

Visualização normal

Antes de ontemCybersecurity News
  • ✇Security Affairs
  • 484,142 Exposed Cloud Buckets Contain 18 Billion Files Pierluigi Paganini
    42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups. The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure Index, written by Mantas Sasnauskas. “No file was opened for this index. Every number below comes from bucket nam
     

484,142 Exposed Cloud Buckets Contain 18 Billion Files

29 de Outubro de 2026, 15:43

42 publicly listable cloud buckets containing 18 billion files, including exposed credentials, database dumps and backups.

The Ransomnews research team counted 484,142 publicly listable cloud storage buckets in October 2026, holding 18.05 billion files. They built the count from the search engines that index open cloud storage and published it as the Ransomnews Cloud Exposure Index, written by Mantas Sasnauskas.

“No file was opened for this index. Every number below comes from bucket names, file extensions, file counts and last-modified timestamps. That is a deliberate limit. It keeps the research on the right side of the line, and it turns out to be enough to see where the sensitive material concentrates.” Ransomnews states. “We are calling it the Ransomnews Cloud Exposure Index, and we will rerun it quarterly so the numbers can be compared over time.”

The researchers used bucket names, file types, file counts and last-modified dates to collect their data. They did not open any files, allowing them to identify where sensitive information might be stored without accessing the content. They plan to repeat the research every three months to track changes over time.

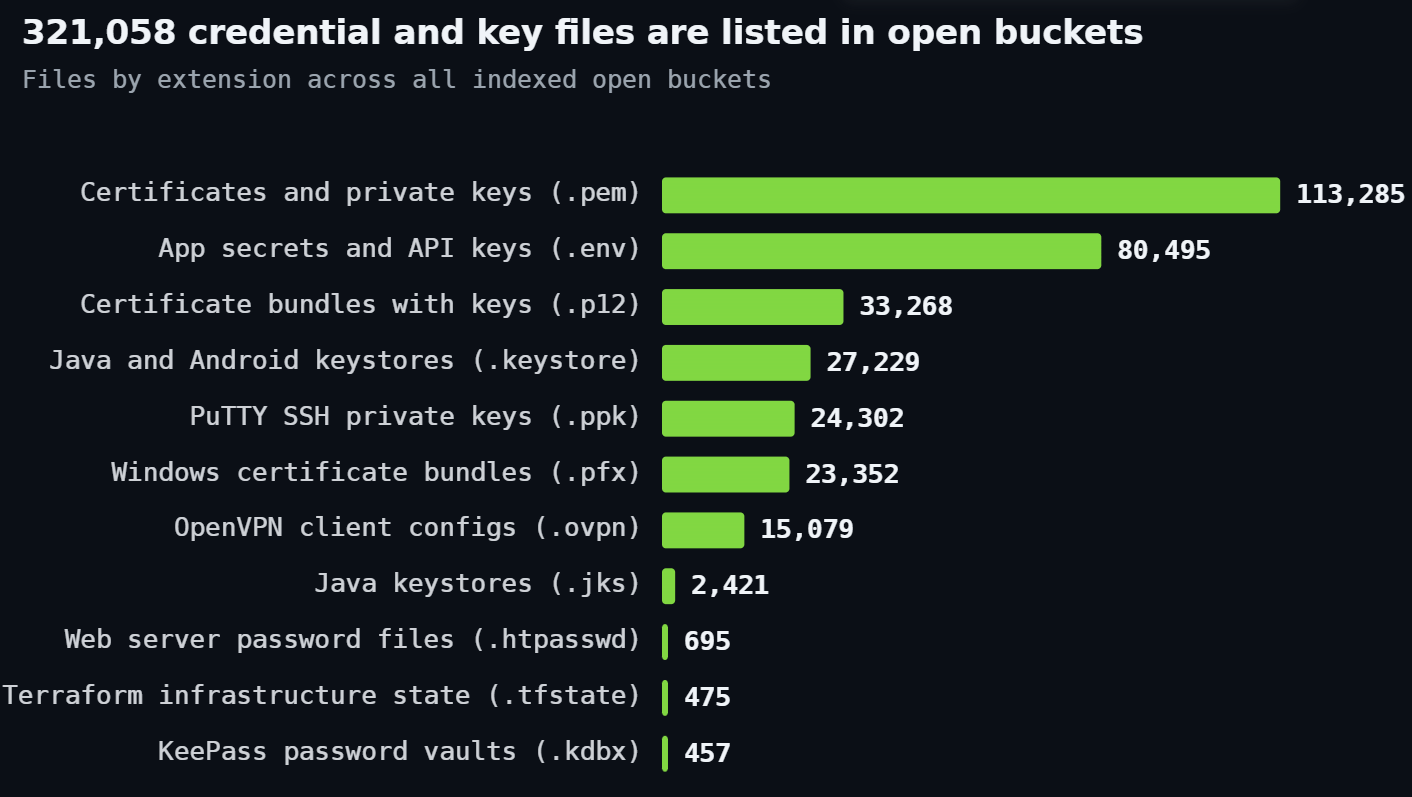
Amazon S3 accounts for 72% of the exposed buckets, roughly in line with its share of the market. This does not mean S3 has weaker security than other providers. Azure Blob, however, appears 2.5 to 3.6 times more often than expected among buckets named for backups, data exports and payroll records. The researchers also found 321,058 files related to credentials and keys. Of the exposed .env files, 67% were last modified in 2026.
Below is the split by provider, from a snapshot taken on October 7:

ProviderOpen bucketsShare
Amazon S3347,98471.9%
Azure Blob68,53214.2%
Google Cloud Storage53,13111.0%
DigitalOcean Spaces11,0692.3%
Alibaba OSS3,4260.7%
Total484,142100%

A lot of these buckets are public on purpose, holding website assets, CDN mirrors, open datasets and podcast archives. So the index isn’t 484,142 breaches. It’s the pool where breaches hide, and the rest of the report narrows it down to the stores that should never have been listable.

“Azure, by a wide margin relative to its size. Azure Blob holds 14.2% of open buckets, but 37% of the 1,459 buckets with “backup” in the name, 42% of the 399 named for exports, and 51% of the 505 carrying HR or payroll terms.” continues the report. “Buckets named for logs, customers and databases sit at 35% to 36%, all around two and a half times Azure’s baseline.”
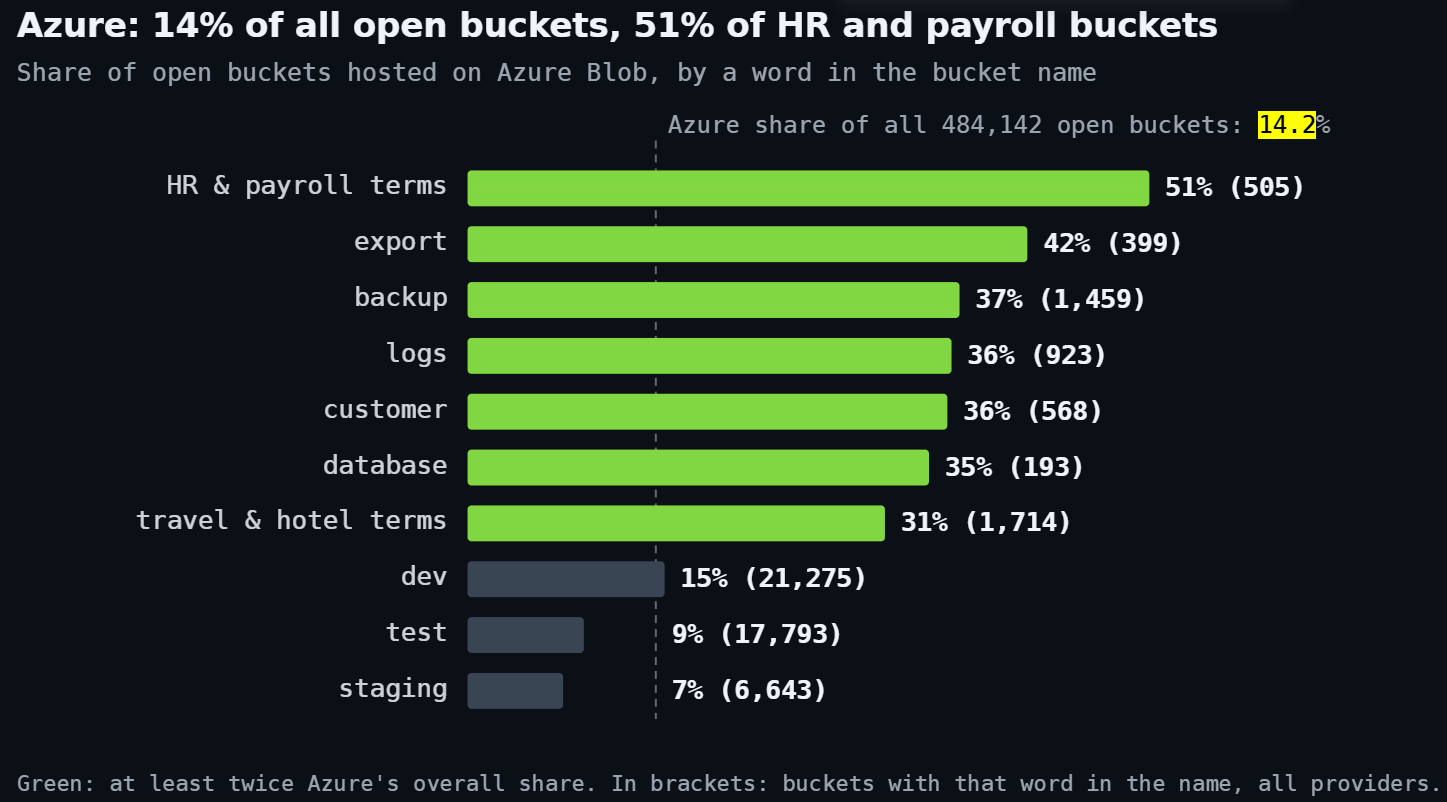
The skew only shows up for operational data. Buckets named “dev” sit at Azure’s baseline of 15 percent, and “test” and “staging” fall below it, at 9 and 7 percent. The authors suspect Azure storage accounts more often hold line-of-business data such as backups, exports and HR systems that enterprises run on Microsoft, while S3 and Google Cloud carry more application assets. They call it a hypothesis the counts suggest and don’t prove, and it’s the first thing they want to test next time.

By sector, retail and e-commerce names lead with 5,666 buckets, mostly storefront assets. The more worrying number is that names tied to regulated sectors (finance, healthcare, education, government, legal and HR) appear on 10,891 unique open buckets. Those are the places where a stray file most likely holds personal, health or financial records, and where regulators expect to hear about it.

Sector (by bucket name)Open bucketsFiles in them
Retail and e-commerce5,666269.9M
Finance and insurance3,50858.0M
Healthcare2,70947.9M
Media and entertainment2,696136.2M
Education2,39360.6M
Gaming2,29679.0M
Travel and hospitality1,714118.7M
Real estate1,13760.7M
Government and public sector1,00036.2M
Legal97811.3M
Crypto63011.9M
HR and payroll5058.4M

Healthcare-related names appear in 2,709 buckets containing 47.9 million files. The researchers identified them using terms such as “hospital” (135 buckets), “patient” (135), “clinic” (277) and “dental” (331). HR and payroll is the smallest sector, with 505 buckets, 259 of which are hosted on Azure.

These figures are based on names, not proof of ownership. The search matches parts of words, so “store” can refer to object storage as well as shops. A single bucket can also appear in two sectors.

The exposed buckets also list about 4.7 million database and dump files, 15,130 mailbox archives, and tens of millions of spreadsheets and documents. Credential files are particularly concerning because they can turn a cloud misconfiguration into a real intrusion.

File typeWhat it isFiles listed
.pemCertificates and private keys113,285
.envApp secrets and API keys80,495
.p12Certificate bundles with keys33,268
.keystoreJava and Android keystores27,229
.ppkPuTTY SSH private keys24,302
.pfxWindows certificate bundles23,352
.ovpnOpenVPN client configs15,079
.jksJava keystores2,421
.htpasswdWeb server password files695
.tfstateTerraform infrastructure state475
.kdbxKeePass password vaults457

Each of these exists to grant access. A .env file is where developers keep database passwords and API keys. A .tfstate file is Terraform’s record of a whole cloud setup, often with secrets in plain text, and a .kdbx vault is encrypted but now open to anyone who wants to guess passwords offline. Some .pem files are public certificates and some files are test fixtures, so the counts are a ceiling on live secrets and not a measure of them. It’s still a big ceiling.

Database files make up most of the sensitive material by volume:

File typeWhat it usually holdsFiles listed
.sqliteEmbedded app databases2,561,807
.bakDatabase and server backups752,055
.sqlDatabase dumps687,446
.sqlite3Embedded app databases488,176
.dumpDatabase dumps176,603
.mdb / .accdbMicrosoft Access databases36,467
.dmpMemory and crash dumps12,809
.pst / .ost / .mboxMailbox archives15,130
.emlSaved emails4,549,665
.csvData exports and recordsat least 69,580,112
.xlsx / .xlsSpreadsheets42,544,997
.docxWord documents24,936,788
.pdfDocuments, invoices, scansat least 106,191,393
.logApplication and server logsat least 61,310,809

The exposed buckets contain thousands of virtual disk images, including VMware, Hyper-V and QEMU files. A single disk image can contain an entire server, including credentials.

Some exposures involve active systems. Of 80,495 .env files, 67% were last modified in 2026. Certificates and SQLite databases include both recent and older files. Backups appear older, with 89% of the 752,055 .bak files last modified before 2025. Almost all PuTTY key files date from 2024.

Recent leaks need urgent attention, while long-standing exposures point to poor security management. The problem is ongoing: at least 113.6 million files were added to publicly listable buckets in the seven days before September 9. Over the previous 30 days, these included more than 21,000 SQL dumps, nearly 21,000 backup files, 4,477 .pem files and 1,298 .env files.

Public .env files can expose database passwords that ransomware affiliates and initial access brokers look for. Similar credentials appear in stolen-data logs, but in this case, attackers do not need to infect a device. They only need to search for exposed files.

Cloud providers already offer settings to prevent public access. Organizations should enable S3 Block Public Access, disable anonymous access to Azure Blob storage, and enable public access prevention in Google Cloud. These controls should apply at account or organization level to prevent new storage buckets from becoming public.

Organizations should also scan their storage for sensitive files such as .env, .sql, .bak, .pem, .ppk, .tfstate and .kdbx. Terraform state files and virtual disk images should be treated as secrets, stored privately, encrypted and monitored. Backups should never be publicly accessible, and recovery procedures must be tested.

One exposed bucket may be a mistake, but many often indicate a wider process failure. Organizations need to fix the underlying security controls, not just individual buckets.

The research has some limitations. The team queried search engines on October 25, while the bucket list was current to October 7 and the newest indexed file dated September 9. File-level data may therefore be about a month old. Counts are also capped at one million per query, so researchers split larger categories into date ranges and added the results.

Some limits apply. The team queried the search engines on October 25. The bucket list was current to October 7 and the newest indexed file was dated September 9, so file-level figures lag by about a month. The index caps any single count at one million, so larger types were split into date windows and summed.

A last-modified date shows when a file was written, not when it was exposed, and a listed file isn’t proof that its contents can be read. No bucket is named in the report. Exposures with a known owner in regulated sectors are going through responsible disclosure, with national CERTs copied where the owner is public sector or doesn’t respond.

“Rotate any secret that has ever sat in a public bucket. Closing the bucket does not un-leak the key. Assume anything that was listable was copied.” conlcudes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Cloud Buckets)

  • ✇Firewall Daily – The Cyber Express
  • Australian Data Breach Incidents Up 66% as AI Sharpens Scams Samiksha Jain
    Australians filed a cybercrime report about every six minutes over the past year, and artificial intelligence is making the attacks behind those reports faster and more convincing. That is the main finding of the ASD Cyber Threat Report 2025-26. It is the seventh annual assessment from the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC). In FY2025-26, the agency received more than 82,000 cybercrime reports through ReportCyber. It responded to over 1,500 cyber secur
     

Australian Data Breach Incidents Up 66% as AI Sharpens Scams

28 de Outubro de 2026, 04:25

ASD Cyber Threat Report

Australians filed a cybercrime report about every six minutes over the past year, and artificial intelligence is making the attacks behind those reports faster and more convincing. That is the main finding of the ASD Cyber Threat Report 2025-26. It is the seventh annual assessment from the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC).

In FY2025-26, the agency received more than 82,000 cybercrime reports through ReportCyber. It responded to over 1,500 cyber security incidents, up more than 20% on the previous year and 36% over five years. It also notified Australian entities of potentially malicious activity more than 4,400 times, almost 80% more than in FY2024-25.

What the ASD Cyber Threat Report Says About AI

The report calls AI the defining force in the threat environment this year. In his foreword, Deputy Prime Minister and Defence Minister Richard Marles wrote that AI is helping malicious actors find vulnerabilities faster and exploit them at greater scale, speed and sophistication. He also noted that new threats have emerged in recent weeks from the unintended actions of AI agents and from model testing.

ASD’s ACSC makes one clear distinction. AI has not created new kinds of threats. It has amplified and sped up existing ones. AI-enabled cyber threats are most visible in social engineering. Attackers are using AI to write phishing emails with no spelling or grammar errors and to automate targeted spearphishing. The Australian Securities and Investments Commission has also seen a sharp rise in scams that use deepfake videos of celebrities and politicians.

The time defenders have to respond is also shrinking. The agency has previously observed that most vulnerabilities are exploited within two weeks, and some within 48 hours of a patch being released. It expects AI-driven tools to shorten that window further over the next 12 months. Publicly reported vulnerabilities (CVEs) rose 30%. Old flaws are still a problem too: ASD’s ACSC recorded the successful exploitation of a vulnerability first identified in 2008.

Incident Severity Grows in ASD Cyber Threat Report Data

Only one Category 2 incident was recorded this year. However, extensive compromises rose from 26 to 40. ASD’s ACSC identified 362 incidents after proactively notifying organisations. A single notification about cPanel vulnerabilities, sent to 340 entities in May 2026, led to more than 60 confirmed incidents.

The number of ransomware incidents held steady at 139, but extensive ransomware incidents rose from 16 to 24. Health Care, Professional, Scientific and Technical Services, and Manufacturing remained the most affected sectors. Data breaches made up 98 incidents, a 66% increase on the previous year. Separately, the Office of the Australian Information Commissioner received 1,205 breach notifications in 2025. That is the highest yearly total since its Notifiable Data Breaches scheme began in 2018.

The financial impact is rising for businesses. The average self-reported cost of cybercrime per business report rose 16% to $93,500. For medium-sized businesses, it rose 45% to $141,300. The average cost for individuals stayed at $33,000. Identity fraud remained the most reported cybercrime, although reports fell 18%.

Stolen access is now a major entry point. Compromised accounts and credentials were among the most frequently reported incident categories, and phishing appeared in 39% of incidents. Government survey research cited in the report found that 55% of Australians reuse passwords across multiple accounts.

State Actors and Critical Infrastructure in the ASD Cyber Threat Report

State-sponsored actors continued to target Australian government, business and individuals to gain sensitive information. The report says these actors are increasingly pre-positioning inside networks to enable future disruption. Marles wrote that the line separating state-sponsored espionage from sabotage and cybercrime is becoming increasingly blurred.

In April 2026, ASD’s ACSC and international partners highlighted a shift by China-nexus actors. These actors are moving towards large covert networks built from compromised home and small office routers, Internet of Things devices and smart devices.

Critical infrastructure accounted for 154 incidents, or 10% of the total, a decrease of almost 7%. Phishing was the leading initial access technique at 36%, and Financial and Insurance Services was the most affected critical infrastructure division at 30%.

What the Threat Report Asks Organisations to Do

In October 2026, ASD’s ACSC released the Essentials series. It evolves the Essential Eight into a principles-based framework with three chapters: Enterprise IT, Operational Technology and Cloud.

Under its Cyber Action Year, the agency is pushing five priorities:

  • Replacing or mitigating legacy technology.
  • Implementing best-practice event logging.
  • Managing supply chain risk.
  • Preparing for AI-enabled threats.
  • Preparing for post-quantum cryptography, including ceasing the use of traditional asymmetric cryptography by the end of 2030 or sooner.

The report also urges organisations to patch faster. For individuals, it recommends reviewing privacy settings and enabling multi-factor authentication or passkeys.

Suspicious activity, incidents and vulnerabilities can be reported at cyber.gov.au or through the Australian Cyber Security Hotline on 1300 CYBER1 (1300 292 371).

  • ✇Security Affairs
  • FBI and CISA Warn of SafePay Ransomware Attacks on 600 Organizations Pierluigi Paganini
    SafePay ransomware has hit 600+ organizations since 2024, using stolen credentials, VPN access and double extortion to pressure victims into paying. CISA, the FBI, the US Secret Service, Germany’s Landeskriminalamt Rheinland-Pfalz, and two UK law enforcement agencies jointly published an advisory this week on SafePay, a ransomware group they describe as one of the most active operations currently running. The group has breached at least 600 organizations across critical infrastructure sector
     

FBI and CISA Warn of SafePay Ransomware Attacks on 600 Organizations

22 de Outubro de 2026, 03:48

SafePay ransomware has hit 600+ organizations since 2024, using stolen credentials, VPN access and double extortion to pressure victims into paying.

CISA, the FBI, the US Secret Service, Germany’s Landeskriminalamt Rheinland-Pfalz, and two UK law enforcement agencies jointly published an advisory this week on SafePay, a ransomware group they describe as one of the most active operations currently running. The group has breached at least 600 organizations across critical infrastructure sectors since August 2024, spanning North America, South America, Europe, and Australia.

“Since August 2024, SafePay ransomware group’s operations have affected a wide range of businesses and critical infrastructure in North America, South America, Europe, and Australia. SafePay ransomware was among the most active ransomware groups in 2026. The SafePay threat actors have impacted at least 600 separate victims from multiple critical infrastructure sectors.” reads the joint advisory, “The authoring agencies encourage organizations to implement the recommendations in the Mitigations section of this advisory to reduce the likelihood and impact of SafePay ransomware incidents.”

SafePay appeared in mid-2024 as an independent ransomware group that operates without affiliates. This is unusual because many major ransomware groups work like franchises, allowing other criminals to use their tools and services. SafePay grew as groups such as BlackCat and LockBit declined, and its activity has continued. The advisory includes findings from FBI, US Secret Service, and German investigations through August 2026.

SafePay’s preferred entry points are exposed credentials, brute force password attacks, and VPN access.

“The FBI, USSS, and cybersecurity researchers observed SafePay threat actors obtaining initial access [TA0001] to organizations through various means, including credential exposure, implementing brute force password attacks [T1110], and exploiting virtual private network (VPN) access.” states the advisory. “SafePay threat actors use the IP addresses of the VPN provider “Mullvad” to attain initial access—specifically, SafePay threat actors use phished account profiles to access victim networks to exploit the following known Common Vulnerabilities and Exposures (CVEs) for edge device products”

Security teams should watch for unusual login attempts coming from Mullvad VPN IP addresses. SafePay also uses stolen account credentials and automated scripts to exploit known vulnerabilities in internet-facing devices. These include Cisco VPN flaws from 2020 and 2023, a Veeam vulnerability, and a SonicWall access control issue.

Once inside a network, the attackers rely on common tools rather than specialized malware. They use PsExec, WinRM, RDP, and PowerShell to move between systems. A PowerShell script called ShareFinder.ps1 helps them find shared folders and identify valuable data. Mimikatz is used to steal credentials, while AnyDesk and TeamViewer provide remote access. To steal data, the group uses tools such as FileZilla, RClone, WinSCP, and even OneDrive.

Encryption uses a ChaCha20 stream cipher combined with RSA for key exchange, with methods customized based on file type and size. Files get the .SafePay extension appended.

“Data encrypted with the SafePay ransomware variant (appended with .SafePay) cannot be recovered without the decryption key. SafePay threat actors hold the encrypted data for ransom and typically demand a subset of company revenue in cryptocurrency in exchange for decryption software.” states the advisory. “SafePay threat actors leave a ransom note on the victim’s system, typically on the desktop or root directory, advising them that SafePay locked their system and to reach out over a chat portal at a TOR .onion website link with a victim ID as the login. “

Paying the ransom remains the only path to decryption for encrypted files, and even that isn’t guaranteed to work.

The group runs a double-extortion model: steal first, encrypt second, threaten to post the stolen data publicly if the victim doesn’t pay. After encryption, SafePay sends victims to a Tor-based chat portal for negotiations. A representative also makes phone calls to apply pressure. If no payment comes, everything goes on the leak site. The group also deletes Volume Shadow Copies and resets network-attached backup devices to factory settings, which is the operational equivalent of cutting off every exit before the fire starts.

The advisory recommends several basic security measures. Keep internet-facing devices, especially VPNs and firewalls, up to date. Prioritize vulnerabilities listed in CISA’s Known Exploited Vulnerabilities catalog. Enable multi-factor authentication (MFA) for VPNs, webmail, and accounts that access critical systems.

Limit the number of accounts allowed to use administrative tools. SafePay relies on legitimate Windows tools to move through compromised networks, making its activity harder to detect. Organizations should also keep backups offline, encrypted, and immutable so attackers cannot access, change, or delete them.

CISA also recommends reviewing all accounts with admin privileges, setting time-limited access where possible, and disabling command-line tools for any account that doesn’t need them.

The advisory includes IOC files in STIX XML and JSON format, full MITRE ATT&CK mapping, and complete file and IP indicators.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

  • ✇Security Affairs
  • ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up Pierluigi Paganini
    Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed. Cybersecurity has always been a race between attackers and defenders. ENISA’s latest assessment suggests that frontier AI is changing the speed of that race, and the gap between discovering a vulnerability and exploiting it could soon become measured in minutes rather than months. In its July 2026 paper, ENISA’s view on Cybersecurit
     

ENISA: Frontier AI Is Changing the Speed of Cyberattacks. Europe Needs to Catch Up

14 de Setembro de 2026, 17:35

Frontier AI is compressing the attack lifecycle from vulnerability discovery to exploitation, forcing defenders to detect, patch and respond at machine speed.

Cybersecurity has always been a race between attackers and defenders. ENISA’s latest assessment suggests that frontier AI is changing the speed of that race, and the gap between discovering a vulnerability and exploiting it could soon become measured in minutes rather than months.

In its July 2026 paper, ENISA’s view on Cybersecurity in the Frontier AI Era, the EU cybersecurity agency argues that advanced AI is compressing parts of the attack chain, from reconnaissance and vulnerability discovery to exploitation, lateral movement and data theft. The problem isn’t simply that AI can find more bugs. It’s that it can connect individual findings into a working attack.

That distinction is important. Traditional security operations could often rely on the time required for a human attacker to research a target, understand a vulnerability, develop an exploit and deploy it. ENISA says that “grace period” is disappearing as automated systems take over more of the work.

The agency describes a particularly worrying possibility: what it calls “negative time-to-exploit”. In practice, attackers could gain access to usable exploit information before defenders have even received or deployed a fix. ENISA says vulnerability weaponisation may now occur within 15 minutes of disclosure, while research cited in its report puts the median time from initial access to data exfiltration at 72 minutes.

That puts traditional patch management under pressure. A company can receive a vulnerability advisory, send it through a change process, test the update, obtain approval and schedule deployment. An attacker does not have to follow any of those steps.

ENISA calls this an “Authority Gap”: organisations may simply take longer to approve a defensive action than an AI-assisted attacker needs to exploit the weakness. The uncomfortable question is whether some environments will eventually need autonomous or near-autonomous patching because waiting for human approval could become the greater risk.

That doesn’t mean companies should blindly automate every security update. Automated patching can break systems, disrupt critical services or introduce new bugs, and ENISA explicitly identifies verification of AI-generated patches as a new bottleneck. The challenge is therefore not automation versus humans, but deciding which decisions can safely happen at machine speed and which still require human approval.

The scale of vulnerability discovery could create another problem. ENISA reports that one organisation went from roughly 80 CVEs in the first quarter of 2025 to almost 500 in the first quarter of 2026, then saw the volume rise to about 500 reports per day when frontier-AI tools were used.

At that point, finding vulnerabilities is no longer the main bottleneck. Verification and remediation become the problem.

Security teams already know what happens when too many alerts arrive at once. The difference is that AI could produce them at a scale humans cannot review manually. ENISA therefore recommends shifting resources from discovery alone toward faster triage, prioritisation and remediation, using approaches such as EPSS and VEX to focus scarce resources on vulnerabilities that are most likely to matter.

There’s another issue that deserves more attention: low-severity vulnerabilities may become more dangerous when AI can chain them together. ENISA notes that frontier models can reason about application logic, credentials, configurations and API access rather than simply identify isolated coding flaws. That can turn several individually modest weaknesses into a practical attack path.

This changes how defenders should think about risk. A vulnerability that looks harmless in isolation may become useful when combined with a weak credential, an exposed API or a poorly configured service.

The same pressure is already affecting the disclosure process. ENISA says AI-generated vulnerability reports have begun to overwhelm parts of the open-source reporting pipeline, with platforms and maintainers struggling to separate useful findings from repetitive or poorly validated submissions. At the same time, the agency notes that the quality of AI-generated reports has improved, meaning the problem could become both more serious and harder to filter.

There is a similar shift on the defensive side. ENISA recommends integrating AI into the software development lifecycle, using continuous threat modelling and automated testing rather than treating security as a review performed at the end of development. It also argues for AI-assisted incident response that can validate telemetry, prioritise events and contain the blast radius while keeping human oversight in place.

That last condition matters. The answer to machine-speed attacks cannot simply be giving machines unlimited authority to fight back. Defensive AI needs its own controls, permissions and audit trails, especially when it can make changes to production systems.

ENISA also recommends an “assume-breached” approach. Organisations should expect that some attacker will eventually get inside and design segmentation, monitoring and access controls so that one compromised component doesn’t automatically become a route into everything else.

The agency sees this as a structural change rather than another temporary threat trend. It recommends machine-speed defence under the broader concept of “Cybersecurity as Code”, covering areas such as vulnerability management, incident response, security architecture and secure software development.

Europe also has a policy problem to solve. NIS2, the Cyber Resilience Act and the AI Act already provide parts of the framework, but ENISA argues that Europe should develop common benchmarks for testing advanced AI models in cyber ranges, measuring exploitability and simulating chained attacks.

The agency also sees value in European cybersecurity data. Incident reports, malware samples, vulnerability disclosures and threat intelligence could support trusted defensive AI models, provided organisations apply strong safeguards, anonymisation and access controls.

For companies, however, the message is much simpler than the policy language suggests. Review your asset inventory, understand which systems are exposed, identify unsupported components and measure whether your detection and response can keep up with an attack that moves in minutes rather than hours. ENISA explicitly recommends near-real-time security operations, with single-digit-minute targets for mean time to detect and respond.

The defenders who adapt fastest won’t necessarily be those with the most advanced AI model. They’ll be the ones that have already removed the basic obstacles: fragmented logging, excessive privileges, slow approvals, unknown assets and systems nobody wants to patch because nobody is quite sure what will break.

AI is making attacks faster. It doesn’t change the basic rules of cybersecurity.

It just makes the cost of ignoring them arrive much sooner.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Frontier AI)

Anthropic: AI Misuse Is Entering a New Phase: From Cybercrime to Surveillance, Propaganda and Weapons

12 de Setembro de 2026, 13:46

AI is becoming an operational force for cybercrime, surveillance, propaganda, fraud and weapons development, lowering the cost and scale of attacks.

Artificial intelligence (AI) is becoming more than a tool for people who want to do something malicious. It is increasingly becoming part of the operational machinery itself.

That is the main message emerging from Anthropic ‘s latest Threat Intelligence report, which examines malicious activity identified and disrupted between December 2025 and August 2026. The cases cover cyber operations, influence campaigns, surveillance, fraud, biological research, conventional weapons and attempts to extract the capabilities of frontier AI models.

The actors involved are equally diverse. Anthropic describes suspected state-sponsored groups, financially motivated criminals, commercial surveillance operators and politically motivated individuals. What connects many of these cases is not a new attack technique, but the way AI changes the economics, speed and scale of operations.

AI is becoming an operational layer

The report makes an important distinction from the usual discussion about AI-powered hacking.

The biggest change may not be that AI can discover a new vulnerability or write malware. It is that models can now contribute across almost the entire attack chain, from reconnaissance and tool development to exploitation, credential theft, data processing and exfiltration.

Anthropic observed operations in which AI systems executed commands against victim networks, harvested credentials and exfiltrated information. At the more autonomous end of the spectrum, multi-agent frameworks conducted reconnaissance, exploitation and data theft against several victims in parallel, sometimes for hours or days with limited human intervention.

This has an important consequence for defenders. Sophisticated attacks no longer necessarily require sophisticated attackers.

According to Anthropic, AI is reducing the gap that once separated well-funded state operations from smaller criminal groups. Reconnaissance, exploitation, coding and data analysis that previously required several specialists can increasingly be delegated to AI systems running at machine speed.

The underlying attacks are often familiar. Stolen credentials, exposed services, vulnerable edge devices, phishing and SQL injection still play a central role. What has changed is the cost of putting them together at scale.

Cybercrime becomes a production line

One of the clearest examples involves a financially motivated operation that harvested credentials from software and online services.

The attackers downloaded and analyzed 1.8 million Android application packages, searching for hardcoded secrets, while running a parallel process to collect GitHub-related credentials. The important point is not the number of apps. It is the automated pipeline connecting discovery, credential collection, validation and subsequent intrusion activity.

“One French-speaking operator going by the aliases of (MeowSHA | frkoo | blazespider) ran a distributed credential-harvesting pipeline across a fleet of 10 AWS EC2 workers. This pipeline mass-downloaded 1.8 million distinct Android APKs from multiple app-store sources, decompiled them, and scanned for hardcoded secrets with Detecting and countering misuse of AI: September 2026 12 TruffleHog.” reads the report. “Verified findings were routed in real time to a Telegram group organized into over 100 source types. A parallel GitHub organization email harvester fed a second stream of stolen GitHub Personal Access Tokens. These two credential pipelines supplied the initial-access credentials for the bulk of the confirmed breaches associated with frkoo.”

The same model appears elsewhere in the report. Attackers used AI to develop malware and phishing tools, analyze compromised environments, process stolen information and maintain access to victims.

In one campaign, stolen tokens could be replayed against Microsoft services to access mailbox contents, including deleted messages. The attackers used techniques designed to make their traffic resemble legitimate Microsoft clients. Anthropic says Claude was used to engineer and test the tooling.

This is what makes the development significant. AI does not need to invent a completely new attack for the threat level to increase. If it can automate enough of the existing process, a small team can attempt operations that previously required a much larger workforce.

Surveillance at machine speed

The report becomes even more striking when it moves beyond cybercrime.

Anthropic identified nation-state actors and commercial surveillance operators using Claude to build systems for monitoring populations, profiling individuals and analyzing social media activity. The cases involve actors linked to China, Iran and West Africa, as well as the commercial surveillance-for-hire market.

“These cases include threat actors from China, Iran, and West Africa, as well as the commercial “surveillance-for-hire” market, and range from operations carried out by a single individual to entire teams.” continues the report. “Anthropic’s Usage Policy prohibits using Claude to conduct non-consensual surveillance and profiling, and to use our services to violate individuals’ civil liberties and human rights. In every case we describe below, the threat actors violated our Usage Policy and attempted to circumvent controls designed to detect such misuse.”

In one case, a consultant working for Malian national security authorities used Claude to engineer a mass-interception platform capable of monitoring communications across the country’s mobile operators and producing dossiers on targets.

In another, Iranian actors used Claude to develop a malicious Firefox extension designed to harvest information about social-media users. Chinese operators used AI to analyze large volumes of social-media content, identify potential targets and generate intelligence reports.

One particularly revealing operation targeted Uyghur communities in Syria. An actor without Arabic-language skills used Claude to draft messages in the appropriate dialect, translate replies in real time, role-play as an expert to evaluate the operation and prepare the resulting information for a suspected human case officer.

This shows another important shift. AI is not merely analyzing surveillance data after it has been collected. It can become part of the system that decides whom to watch, how to approach them and how to turn raw information into intelligence.

Propaganda can also be industrialized

The same automation is appearing in influence operations.

Anthropic describes an operation linked with high confidence to UAE government officials in which AI supported a network of roughly 300 inauthentic social-media accounts. The operation also created a front NGO using the identity of a real organization, produced apparently independent human-rights material and ghost-wrote testimony intended for presentation to the UN Human Rights Council.

The actors also profiled 18 members of the European Parliament and journalists and prepared dossiers on UN Special Rapporteurs who had criticized UAE conduct in Sudan.

The significance is not simply that AI can generate propaganda. Political actors have been producing propaganda for centuries. The difference is that AI can make the process much cheaper and more scalable while allowing operators to generate different narratives, personas and documents for different audiences.

The line between genuine grassroots activity and centrally coordinated influence therefore becomes harder to see.

Fraud gets a human face without the human

The report also provides a remarkably concrete example of AI-powered consumer fraud.

A China-based app studio built more than 20 dating applications and used AI personas to communicate with users while advertising the services as fully human. During a two-week period, Anthropic identified more than 4,700 AI personas that interacted with at least 25,000 people.

“A China-based app studio used Claude to both build a network of over 20 dating apps and power the AI personas used to converse with users–despite advertising their service as fully human.” states Anthropic. “Over a two-week window in April 2026, we discovered more than 4,700 distinct AI personas that engaged in conversations with at least 25,000 unique individuals.”

The operation combined AI and human workers. The bots handled large volumes of conversations, while real people performed activities such as video calls and social-media interactions designed to convince victims that they were dealing with genuine users.

The reported ratio was roughly three AI personas for every real person. Claude generated around 2.36 million messages during the period examined.

This is an important preview of how AI could change online fraud. The attacker no longer needs thousands of people to maintain thousands of conversations. A small human operation can supervise a much larger artificial workforce.

The terrorism risk deserves attention

The report does not identify a confirmed terrorist attack conducted with Claude. It does, however, document activity that illustrates why AI-assisted weapons development deserves attention from counterterrorism and national-security agencies.

Anthropic identified six cases involving weapons development, procurement or intelligence gathering in China, Russia and Yemen. The cases include guided rockets, ballistic-missile simulations, anti-torpedo systems, autonomous drone swarms, electronic-warfare targeting and directed-energy weapons.

“We identified a cell of threat actors based in northern Yemen running three weapons development programs: a guided rocket that used a commodity phone-class flight computer with final-phase homing guidance; a multi-stage ballistic missile with a stated range goal above 2,000 km; and a multi-variant missile (referred to as the “R2000” set) that included a hypersonic glide vehicle variant.” continues the report.

The Yemen case is particularly significant from a terrorism perspective, even though Anthropic does not establish that the actors were a terrorist organization. A weapons-development cell used Claude Code to work on guidance, navigation and control software for a guided rocket. Multiple AI instances were assigned different roles, including coding, research and code review. The group also carried out a real-world test of a guided rocket and returned to the model afterward to analyze the failure.

That distinction matters. AI is not necessarily giving a terrorist group the ability to build an advanced weapons system from nothing. What it can do is reduce the amount of specialized engineering expertise required to modify, integrate and troubleshoot technologies that the group already possesses.

For counterterrorism agencies, this creates a potential new problem: the proliferation of technical capability may no longer depend entirely on recruiting highly specialized engineers.

Weapons development is not limited to missiles

The report provides several other examples.

One China-based actor used Claude to develop documentation and software for an anti-torpedo system, including a technical proposal of more than 200 pages and comparative analysis of US naval systems. The actor repeatedly asked the model to act as a hostile expert and criticize its own work, effectively creating an automated review process.

A Russia-based operation worked on an autonomous FPV drone swarm using Claude Code and simulation infrastructure. Other cases involved electronic warfare, air-defense suppression and intelligence gathering related to directed-energy weapons.

The pattern is consistent: AI can compress research, engineering, documentation and testing cycles.

That does not mean the model independently created these weapons. In several cases, the actors already had expertise, hardware or access to the necessary infrastructure. The AI accelerated the work around them.

Biology is an even harder problem

Biological misuse presents a different challenge because intent is much harder to establish.

Anthropic says today’s models are capable of assisting with increasingly complex scientific research, making it harder to guarantee that they cannot meaningfully support dangerous biological work.

The report describes five cases involving potentially sensitive research. They include gain-of-function work involving chikungunya, planning related to mammalian adaptation of avian influenza, an orthopoxvirus immune-evasion research proposal, optimization of venom peptides and computational redesign of toxins.

Anthropic is careful about what these cases prove. It does not claim that the researchers intended to develop biological weapons, nor that Claude enabled a biological weapon. The cases demonstrate something more subtle: dangerous research can look very similar to legitimate scientific research when viewed one request at a time.

That makes traditional content filtering much harder.

A sophisticated actor does not necessarily have to ask an AI model, “How do I build a biological weapon?” They can divide the work into apparently legitimate scientific tasks and combine the answers elsewhere.

AI is also becoming the target

Perhaps the most strategic part of the report concerns illicit distillation.

Anthropic says several Chinese AI companies attempted to extract capabilities from Claude by creating large numbers of fraudulent accounts, routing enormous numbers of queries through proxy networks and collecting model outputs for training.

Alibaba’s operation reached almost three million exchanges per day from more than 3,500 fraudulent accounts, with more than 151 million exchanges observed between May and July. The activity targeted agentic tasks, software engineering, kernel development and long-horizon reasoning.

Zhipu used hundreds of fraudulent accounts to extract and process reasoning traces. Moonshot, meanwhile, allegedly forwarded customer requests to Claude while presenting Claude’s responses as if they came from its own Kimi models.

The privacy implications are serious as well. Anthropic says some rerouted requests contained sensitive corporate information, live credentials and surveillance data. In one case, DeepSeek allegedly relayed requests containing internal AI-program specifications; another exposed credentials associated with a Russian government database.

This creates a new category of AI supply-chain risk: an organization may think it is using one AI service while its data and workloads are actually being processed by another.

The common thread is scale

The cases in the report look very different, but they point in the same direction.

AI is becoming a force multiplier for cybercriminals, intelligence services, propagandists, fraudsters, surveillance operators and potentially armed groups. It can automate the boring parts of an operation, accelerate the difficult parts and allow a small number of people to coordinate activity at a scale that would previously have required a much larger organization.

This is why the most important finding is not that AI can hack systems or generate malicious code.

The bigger issue is that AI is changing the economics of malicious activity.

A criminal group can process millions of files. A surveillance unit can turn huge volumes of social-media posts into target profiles. A propaganda operation can maintain hundreds of artificial identities. A fraud operation can hold thousands of conversations simultaneously. A weapons program can use AI to accelerate software development and technical analysis.

And in the most advanced cyber cases, AI systems can perform several of these tasks with little human intervention. Anthropic reports that humans still tend to retain the decisions that matter most, such as selecting targets and deciding how to monetize results. But the operational workload between those decisions can increasingly be delegated to machines.

That may be the real security threshold we are crossing.

The question is no longer simply whether AI can be abused. It clearly can.

The more important question is how much of a malicious operation can now be delegated to AI before a human has to step in.

Anthropic’s report suggests that the answer is already: quite a lot.

“Sophisticated and persistent threat actors continuously test our safeguards and try to circumvent the technical measures we use to detect and prevent misuse.” concludes the report. “We’ll continue to evolve our safeguards and coordinate with our partners to improve our ability to detect, disrupt, and prevent future misuse.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Anthropic)

  • ✇The Security Ledger
  • Researcher: Flaw In Fleet Management Service Exposes 250k Commercial Vehicles To Attack Paul Roberts
    A quarter million commercial vehicles in India and sensitive data on tens of thousands of drivers were vulnerable to attacks because of flaws in widely used fleet management software maintained by a VE Commercial Vehicles, a joint venture between the Volvo Group and Eicher Motors, a security researcher has revealed. The post Researcher: Flaw In Fleet Management Service Exposes 250k Commercial Vehicles To Attack appeared first on The Security Ledger with Paul F. Roberts.
     

Researcher: Flaw In Fleet Management Service Exposes 250k Commercial Vehicles To Attack

10 de Agosto de 2026, 07:26

A quarter million commercial vehicles in India and sensitive data on tens of thousands of drivers were vulnerable to attacks because of flaws in widely used fleet management software maintained by a VE Commercial Vehicles, a joint venture between the Volvo Group and Eicher Motors, a security researcher has revealed.

The post Researcher: Flaw In Fleet Management Service Exposes 250k Commercial Vehicles To Attack appeared first on The Security Ledger with Paul F. Roberts.

Talos: Attackers Refine Phishing Playbook To Target Critical Infrastructure

28 de Julho de 2026, 16:30

Phishing played a part in more than half of all incident response engagements undertaken by Talos, Cisco's threat research organization, during the second quarter of 2026, with healthcare organizations and manufacturing firms among the top targets.

The post Talos: Attackers Refine Phishing Playbook To Target Critical Infrastructure appeared first on The Security Ledger with Paul F. Roberts.

  • ✇The Security Ledger
  • Edge Devices Are Your Cyber Underbelly. Here’s Why. Paul Roberts
    In this episode of the podcast, host Paul Roberts interviews Nishawn Smagh of the firm GreyNoise Intelligence about the findings of their State of the Edge report, an analysis of GreyNoise data on risks stemming from compromised edge devices such as broadband routers, VPN gateways, smart home devices and more. Shawn and Paul talk about how attackers are turning edge devices into their favorite entry point, and strategies for organizations to counter the growing risk of compromised edge devices.
     

Edge Devices Are Your Cyber Underbelly. Here’s Why.

20 de Julho de 2026, 08:00

In this episode of the podcast, host Paul Roberts interviews Nishawn Smagh of the firm GreyNoise Intelligence about the findings of their State of the Edge report, an analysis of GreyNoise data on risks stemming from compromised edge devices such as broadband routers, VPN gateways, smart home devices and more. Shawn and Paul talk about how attackers are turning edge devices into their favorite entry point, and strategies for organizations to counter the growing risk of compromised edge devices.

The post Edge Devices Are Your Cyber Underbelly. Here’s Why. appeared first on The Security Ledger with Paul F. Roberts.

💾

Residential Proxy Risks: Understanding Google’s Latest Action Against 2 Million Strong NetNut

3 de Julho de 2026, 09:00

Google announced that it helped take down NetNut, a 2 million strong malicious residential proxy network. The incident highlights the growing risks posed by residential proxy networks that quietly conscript consumer devices into services used by cybercriminals and nation-state actors alike.

The post Residential Proxy Risks: Understanding Google’s Latest Action Against 2 Million Strong NetNut appeared first on The Security Ledger with Paul F. Roberts.

  • ✇The Security Ledger
  • How Claude Planted Malicious Code In A Crypto-Trading App Paul Roberts
    A malicious campaign by North Korean state actors saw a malicious npm package dependency slipped into a crypto trading agent by an AI coding agent, according to a new report by ReversingLabs. The incident highlights a troubling new frontier in software supply chain attacks: hackers targeting developers...and the AI tools writing their code. The post How Claude Planted Malicious Code In A Crypto-Trading App appeared first on The Security Ledger with Paul F. Roberts.
     

How Claude Planted Malicious Code In A Crypto-Trading App

28 de Abril de 2026, 10:57

A malicious campaign by North Korean state actors saw a malicious npm package dependency slipped into a crypto trading agent by an AI coding agent, according to a new report by ReversingLabs. The incident highlights a troubling new frontier in software supply chain attacks: hackers targeting developers...and the AI tools writing their code.

The post How Claude Planted Malicious Code In A Crypto-Trading App appeared first on The Security Ledger with Paul F. Roberts.

  • ✇Security Boulevard
  • LLMs Generate Predictable Passwords Bruce Schneier
    LLMs are bad at generating passwords: There are strong noticeable patterns among these 50 passwords that can be seen easily: All of the passwords start with a letter, usually uppercase G, almost always followed by the digit 7. Character choices are highly uneven ­ for example, L , 9, m, 2, $ and # appeared in all 50 passwords, but 5 and @ only appeared in one password each, and most of the letters in the alphabet never appeared at all. There are no repeating characters within any password. P
     

LLMs Generate Predictable Passwords

26 de Fevereiro de 2026, 09:07

LLMs are bad at generating passwords:

There are strong noticeable patterns among these 50 passwords that can be seen easily:

  • All of the passwords start with a letter, usually uppercase G, almost always followed by the digit 7.
  • Character choices are highly uneven ­ for example, L , 9, m, 2, $ and # appeared in all 50 passwords, but 5 and @ only appeared in one password each, and most of the letters in the alphabet never appeared at all.
  • There are no repeating characters within any password. Probabilistically, this would be very unlikely if the passwords were truly random ­ but Claude preferred to avoid repeating characters, possibly because it “looks like it’s less random”.
    ...

The post LLMs Generate Predictable Passwords appeared first on Security Boulevard.

2025 Q4 DDoS threat report: A record-setting 31.4 Tbps attack caps a year of massive DDoS assaults

5 de Fevereiro de 2026, 11:00

Welcome to the 24th edition of Cloudflare’s Quarterly DDoS Threat Report. In this report, Cloudforce One offers a comprehensive analysis of the evolving threat landscape of Distributed Denial of Service (DDoS) attacks based on data from the Cloudflare network. In this edition, we focus on the fourth quarter of 2025, as well as share overall 2025 data.

The fourth quarter of 2025 was characterized by an unprecedented bombardment launched by the Aisuru-Kimwolf botnet, dubbed “The Night Before Christmas" DDoS attack campaign. The campaign targeted Cloudflare customers as well as Cloudflare’s dashboard and infrastructure with hyper-volumetric HTTP DDoS attacks exceeding rates of 200 million requests per second (rps), just weeks after a record-breaking 31.4 Terabits per second (Tbps) attack.

Key insights

  1. DDoS attacks surged by 121% in 2025, reaching an average of 5,376 attacks automatically mitigated every hour.

  2. In the final quarter of 2025, Hong Kong jumped 12 places, making it the second most DDoS’d place on earth. The United Kingdom also leapt by an astonishing 36 places, making it the sixth most-attacked place.

  3. Infected Android TVs — part of the Aisuru-Kimwolf botnet — bombarded Cloudflare’s network with hyper-volumetric HTTP DDoS attacks, while Telcos emerged as the most-attacked industry.

2025 saw a huge spike in DDoS attacks

In 2025, the total number of DDoS attacks more than doubled to an incredible 47.1 million. Such attacks have soared in recent years: The number of DDoS attacks spiked 236% between 2023 and 2025.

In 2025, Cloudflare mitigated an average of 5,376 DDoS attacks every hour — of these, 3,925 were network-layer DDoS attacks and 1,451 were HTTP DDoS attacks. 

Network-layer DDoS attacks more than tripled in 2025

The most substantial growth was in network-layer DDoS attacks, which more than tripled year over year. Cloudflare mitigated 34.4 million network-layer DDoS attacks in 2025, compared to 11.4 million in 2024.

A substantial portion of the network-layer attacks — approximately 13.5 million — targeted global Internet infrastructure protected by Cloudflare Magic Transit and Cloudflare’s infrastructure directly, as part of an 18-day DDoS campaign in the first quarter of 2025. Of these attacks, 6.9 million targeted Magic Transit customers while the remaining 6.6 million targeted Cloudflare directly. 

This assault was a multi-vector DDoS campaign comprising SYN flood attacks, Mirai-generated DDoS attacks, and SSDP amplification attacks to name a few. Our systems detected and mitigated these attacks automatically. In fact, we only discovered the campaign while preparing our DDoS threat report for 2025 Q1 — an example of how effective Cloudflare’s DDoS mitigation is!

In the final quarter of 2025, the number of DDoS attacks grew by 31% over the previous quarter and 58% over 2024. Network-layer DDoS attacks fueled that growth. In 2025 Q4, network-layer DDoS attacks accounted for 78% of all DDoS attacks. The amount of HTTP DDoS attacks remained the same, but surged in their size to rates that we haven’t seen since the HTTP/2 Rapid Reset DDoS campaign in 2023. These recent surges were launched by the Aisuru-Kimwolf botnet, which we will cover in the next section. 

“The Night Before Christmas” DDoS campaign

On Friday, December 19, 2025, the Aisuru-Kimwolf botnet began bombarding Cloudflare infrastructure and Cloudflare customers with hyper-volumetric DDoS attacks. What was new in this campaign was its size: The botnet used hyper-volumetric HTTP DDoS attacks exceeding rates of 20 million requests per second (Mrps).

The Aisuru-Kimwolf botnet is a massive collection of malware-infected devices, primarily Android TVs. The botnet comprises an estimated 1-4 million infected hosts. It is capable of launching DDoS attacks that can cripple critical infrastructure, crash most legacy cloud-based DDoS protection solutions, and even disrupt the connectivity of entire nations.

Throughout the campaign, Cloudflare’s autonomous DDoS defense systems detected and mitigated all of the attacks: 384 packet-intensive attacks, 329 bit-intensive attacks, and 189 request-intensive attacks, for a total of 902 hyper-volumetric DDoS attacks, averaging 53 attacks a day.

The average size of the hyper-volumetric DDoS attacks during the campaign were 3 Bpps, 4 Tbps, and 54 Mrps. The maximum rates recorded during the campaign were 9 Bpps, 24 Tbps, and 205 Mrps.

To put that in context, the scale of a 205 Mrps DDoS attack is comparable to the combined populations of the UK, Germany, and Spain all simultaneously typing a website address and then hitting 'enter’ at the same second.

While highly dramatic, The Night Before Christmas campaign accounted for only a small portion of the hyper-volumetric DDoS attacks we saw throughout the year.

Hyper-volumetric DDoS attacks

Throughout 2025, Cloudflare observed a continuous increase in hyper-volumetric DDoS attacks. In 2025 Q4, hyper-volumetric attacks increased by 40% compared to the previous quarter.

As the number of attacks increased over the course of 2025, the size of the attacks increased as well, growing by over 700% compared to the large attacks seen in late 2024, with one reaching 31.4 Tbps in a DDoS attack that lasted just 35 seconds. The graph below portrays the rapid growth in DDoS attack sizes as seen and blocked by Cloudflare — each one a world record, i.e. the largest ever disclosed publicly by any company at the time.

Like all of the other attacks, the 31.4 Tbps DDoS attack was detected and mitigated automatically by Cloudflare’s autonomous DDoS defense, which was able to adapt and quickly lock on to botnets such as Aisuru-Kimwolf.

Most of the hyper-volumetric DDoS attacks targeted Cloudflare customers in the Telecommunications, Service Providers and Carriers industry. Cloudflare customers in the Gaming industry and customers providing Generative AI services were also heavily targeted. Lastly, Cloudflare’s own infrastructure itself was targeted by multiple attack vectors such as HTTP floods, DNS attacks and UDP flood.

Most-attacked industries

When analyzing DDoS attacks of all sizes, the Telecommunications, Service Providers and Carriers industry was also the most targeted. Previously, the Information Technology & Services industry held that unlucky title.

The Gambling & Casinos and Gaming industries ranked third and fourth, respectively. The quarter’s biggest changes in the top 10 were the Computer Software and Business Services industries, which both climbed several spots. 

The most-attacked industries are defined by their role as critical infrastructure, a central backbone for other businesses, or their immediate, high-stakes financial sensitivity to service interruption and latency.

Most-attacked locations

The DDoS landscape saw both predictable stability and dramatic shifts among the world's most-attacked locations. Targets like China, Germany, Brazil, and the United States were the top five, demonstrating persistent appeal for attackers. 

Hong Kong made a significant move, jumping twelve spots to land at number two. However, the bigger story was the meteoric rise of the United Kingdom, which surged an astonishing 36 places this quarter, making it the sixth most-attacked location.  

Vietnam held its place as the seventh most-attacked location, followed by Azerbaijan in eighth, India in ninth, and Singapore as number ten.

Top attack sources

Bangladesh dethroned Indonesia as the largest source of DDoS attacks in the fourth quarter of 2025. Indonesia dropped to the third spot, after spending a year as the top source of DDoS attacks. Ecuador also jumped two spots, making it the second-largest source.

Notably, Argentina soared an incredible twenty places, making it the fourth-largest source of DDoS attacks. Hong Kong rose three places, taking fifth place. Ukraine came in sixth place, followed by Vietnam, Taiwan, Singapore, and Peru.

Top source networks

The top 10 list of attack source networks reads like a list of Internet giants, revealing a fascinating story about the anatomy of modern DDoS attacks. The common thread is clear: Threat actors are leveraging the world's most accessible and powerful network infrastructure — primarily large, public-facing services. 

We see most DDoS attacks coming from IP addresses associated with Cloud Computing Platforms and Cloud Infrastructure Providers, including DigitalOcean (AS 14061), Microsoft (AS 8075), Tencent (AS 132203), Oracle (AS 31898), and Hetzner (AS 24940). This demonstrates the strong link between easily-provisioned virtual machines and high-volume attacks. These cloud sources, heavily concentrated in the United States, are closely followed by a significant presence of attacks coming from IP addresses associated with traditional Telecommunications Providers (Telcos). These Telcos, primarily from the Asia-Pacific region (including Vietnam, China, Malaysia, and Taiwan), round out the rest of the top 10.

This geographic and organizational diversity confirms a two-pronged attack reality: While the sheer scale of the highest-ranking sources often originates from global cloud hubs, the problem is truly worldwide, routed through the Internet's most critical pathways from across the globe. In many DDoS attacks, we see thousands of various source ASNs, highlighting the truly global distribution of botnet nodes.

To help hosting providers, cloud computing platforms and Internet service providers identify and take down the abusive IP addresses/accounts that launch these attacks, we leverage Cloudflare’s unique vantage point on DDoS attacks to provide a free DDoS Botnet Threat Feed for Service Providers. 

Over 800 networks worldwide have signed up for this feed, and we’ve already seen great collaboration across the community to take down botnet nodes.

Helping defend the Internet

DDoS attacks are rapidly growing in sophistication and size, surpassing what was previously imaginable. This evolving threat landscape presents a significant challenge for many organizations to keep pace. Organizations currently relying on on-premise mitigation appliances or on-demand scrubbing centers may benefit from re-evaluating their defense strategy.

Cloudflare is dedicated to offering free, unmetered DDoS protection to all its customers, regardless of the size, duration, or volume of attacks, leveraging its vast global network and autonomous DDoS mitigation systems.

About Cloudforce One

Driven by a mission to help defend the Internet, Cloudforce One leverages telemetry from Cloudflare’s global network — which protects approximately 20% of the web — to drive threat research and operational response, protecting critical systems for millions of organizations worldwide.

  • ✇Deep Space PT
  • Vazamentos de dados em massa: como identificar menções críticas contato@axur.com (Time de Conteúdo)
    A Deep e Dark Web se tornaram repositórios massivos de informações corporativas comprometidas. Todos os dias, grupos de ransomware publicam gigabytes de dados roubados, fóruns clandestinos comercializam credenciais, e marketplaces ilegais oferecem acesso a sistemas inteiros. Para equipes de segurança, o desafio não é apenas saber que esses vazamentos existem. É conseguir identificar, em meio a milhões de arquivos, quais realmente contêm informações sensíveis da organização.
     

Vazamentos de dados em massa: como identificar menções críticas

12 de Dezembro de 2025, 17:07

A Deep e Dark Web se tornaram repositórios massivos de informações corporativas comprometidas. Todos os dias, grupos de ransomware publicam gigabytes de dados roubados, fóruns clandestinos comercializam credenciais, e marketplaces ilegais oferecem acesso a sistemas inteiros. Para equipes de segurança, o desafio não é apenas saber que esses vazamentos existem. É conseguir identificar, em meio a milhões de arquivos, quais realmente contêm informações sensíveis da organização.

“PhantomCard”: como funciona o golpe de pagamentos por aproximação

27 de Novembro de 2025, 10:38

Na metade de 2025, chegou ao Brasil um novo tipo de fraude com cartões de crédito em que os criminosos convencem a vítima a aproximar seu cartão do celular para retransmitir dados e autorizar um pagamento de forma inesperada.

Insider Threat: como se proteger do aliciamento de colaboradores

27 de Novembro de 2025, 09:43

Com as cifras milionárias que os criminosos cibernéticos têm obtido com suas ações, cooptar funcionários dentro das empresas por meio de suborno se tornou uma opção viável para obter acesso às redes corporativas. Os criminosos, infelizmente, têm dinheiro para "investir" nesse método.

  • ✇Deep Space PT
  • 5 tendências do Threat Landscape 2025-26 que todo CISO precisa conhecer contato@axur.com (Time de Conteúdo)
    O cenário de cibersegurança em 2025 viveu um paradoxo: temos mais dados, mais visibilidade e mais ferramentas do que nunca, mas nunca estivemos tão sobrecarregados de alertas. O desafio não está mais em saber o que está acontecendo, mas em transformar informação em ação. Com mais de 6 bilhões de novas credenciais detectadas e um crescimento de 65% no phishing direcionado ao setor financeiro, cinco tendências se destacam como críticas para a preparação das equipes de segurança em 2026.
     

5 tendências do Threat Landscape 2025-26 que todo CISO precisa conhecer

17 de Novembro de 2025, 16:06

O cenário de cibersegurança em 2025 viveu um paradoxo: temos mais dados, mais visibilidade e mais ferramentas do que nunca, mas nunca estivemos tão sobrecarregados de alertas. O desafio não está mais em saber o que está acontecendo, mas em transformar informação em ação. Com mais de 6 bilhões de novas credenciais detectadas e um crescimento de 65% no phishing direcionado ao setor financeiro, cinco tendências se destacam como críticas para a preparação das equipes de segurança em 2026.

Novos dados revelam como ataque do grupo Sarcoma comprometeu a Unimed RS

31 de Outubro de 2025, 18:27

O nosso time de pesquisa e investigação, Axur Research Team, confirmou nesta semana a publicação de 2,8 terabytes de dados atribuídos à Unimed RS em fóruns da dark web, em um episódio reivindicado pelo grupo de ransomware Sarcoma.

Especial de Halloween: As histórias mais assustadoras de cibersegurança

28 de Outubro de 2025, 08:47

Todos gostamos de um bom susto no Halloween — mas algumas das histórias mais arrepiantes não acontecem em casas mal-assombradas, e sim no mundo digital. De vazamentos massivos de dados e dumps de credenciais na dark web a sistemas sem patch que abrem as portas para milhões de identidades roubadas, esses casos reais mostram como o dia a dia de quem trabalha com cibersegurança pode ser verdadeiramente assustador.

❌
❌