❌

Visualização normal

Antes de ontemCyber Threat Intel
  • ✇Malwarebytes
  • Update Chrome: Google fixes 37 security flaws, including seven critical bugs
    On October 13 and 14, Google issued several Chrome updates.Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 155.0.8059.79/.80 for Windows and Mac and 155.0.8059.79 for Linux. The update includes 37 security fixes, including seven rated Critical.On the same day, Google released version 155.0.8059.79 for Android. It may not be available on Google Play for everyone yet but keep an eye out for it. Google says it also includes stability and performance improveme
     

Update Chrome: Google fixes 37 security flaws, including seven critical bugs

15 de Outubro de 2026, 11:15

On October 13 and 14, Google issued several Chrome updates.

Most users are on Chrome’s Stable channel. The desktop update brings Chrome to versions 155.0.8059.79/.80 for Windows and Mac and 155.0.8059.79 for Linux. The update includes 37 security fixes, including seven rated Critical.

On the same day, Google released version 155.0.8059.79 for Android. It may not be available on Google Play for everyone yet but keep an eye out for it. Google says it also includes stability and performance improvements.

Updates will roll out over the coming days and weeks.

How to update Chrome

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind on updates if you never close your browser or if something goes wrong, such as an extension preventing the update.

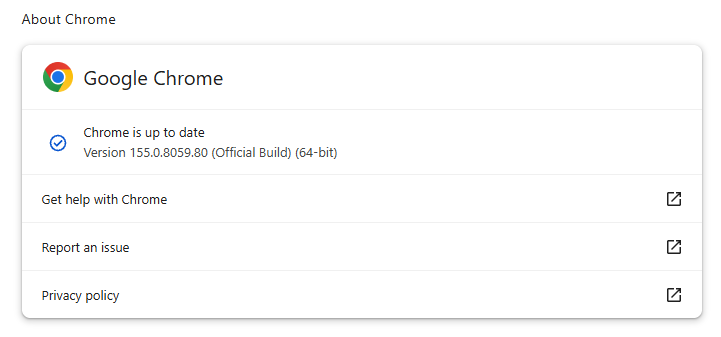
If you don’t want to wait for the rollout to reach you, manually updating is easy. Open About Google Chrome from Chrome’s settings or Help menu. Chrome will check for updates. If one is available, click Relaunch to apply it.

Chrome 155.0.8059.80 is up to date

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

Technical details

Some of the security fixes deserve a closer look.


Mobile protection, anywhere, anytime.

.wp-block-kadence-advancedbtn.kb-btns400740_ab89fd-c4{gap:var(--global-kb-gap-xs, 0.5rem );justify-content:center;align-items:center;}.kt-btns400740_ab89fd-c4 .kt-button{font-weight:normal;font-style:normal;}.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0{margin-right:5px;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button{color:#555555;border-color:#555555;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:focus{color:#ffffff;border-color:#444444;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button::before{display:none;}.wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns400740_ab89fd-c4 .kt-btn-wrap-0 .kt-button:focus{background:#444444;}
ul.menu .wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button{width:initial;}.wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button{color:var(--color-neutral-10);background:var(--color-brand-blue-60);border-top-left-radius:40px;border-top-right-radius:40px;border-bottom-right-radius:40px;border-bottom-left-radius:40px;padding:var(--kb-btn-padding);margin:var(--kb-btn-margin);box-shadow:1px 1px 2px 0px rgba(0, 0, 0, 0.2);}.wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button:hover, .wp-block-kadence-advancedbtn .kb-btn400740_68fb6a-2d.kb-button:focus{box-shadow:0px 4px 0px 0px var(--color-brand-blue-90);}Try it now

The first is tracked as CVE-2026-110152, a buffer overflow in ANGLE in Google Chrome on Android. It could allow a remote attacker to execute arbitrary code outside the sandbox via a crafted HTML page.

ANGLE is Chrome’s graphics-translation layer. A buffer overflow occurs when a program puts more data into an area of memory than it can hold, overwriting data in adjoining memory. An attacker can exploit this to make the vulnerable process run malicious code.

Chrome vulnerabilities that enable remote code execution outside the browser sandbox are particularly valuable to attackers because they can turn a visit to a malicious or compromised website into direct code running on the underlying operating system, often without requiring additional exploitation steps.

Then I spotted two use-after-free vulnerabilities in the PDF component. CVE-2026-110136, rated Critical, could allow a remote attacker to execute arbitrary code outside the sandbox via a crafted HTML page. CVE-2026-110147, rated High, could allow an attacker to execute arbitrary code inside the sandbox via a crafted HTML page.

A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.

Inside the sandbox means the malicious code would run in a restricted, sealed-off environment designed to limit access to the rest of your device. That limits what the attacker can do as it constrains them to the browser, lowering the impact compared with code running outside the sandbox. However, attackers often chain multiple vulnerabilities together to escape the sandbox and achieve a more serious compromise. So, the phrase describes an important security limitation, but it does not mean the vulnerability is harmless.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →
  • ✇Malwarebytes
  • Update Windows: Record Patch Tuesday fixes flaw already under attack
    Microsoft’s October Patch Tuesday release addresses a record-breaking 1,413 vulnerabilities, including an actively exploited Windows Shell zero-day and two other publicly disclosed flaws. Just when you thought a previous record would stand for a while, Microsoft comes out again with the largest monthly Patch Tuesday release. Microsoft has said its growing use of AI to find and fix security vulnerabilities means users should expect more fixes in its monthly updates. How to apply patches and check
     

Update Windows: Record Patch Tuesday fixes flaw already under attack

14 de Outubro de 2026, 08:26

Microsoft’s October Patch Tuesday release addresses a record-breaking 1,413 vulnerabilities, including an actively exploited Windows Shell zero-day and two other publicly disclosed flaws.

Just when you thought a previous record would stand for a while, Microsoft comes out again with the largest monthly Patch Tuesday release. Microsoft has said its growing use of AI to find and fix security vulnerabilities means users should expect more fixes in its monthly updates.

How to apply patches and check if you’re protected

These updates fix security problems and help keep your Windows PC protected. Here’s how to make sure you’re up to date:

  • Click the Start button, then open Settings.
  • Select Windows Update (usually at the bottom of the menu on the left).
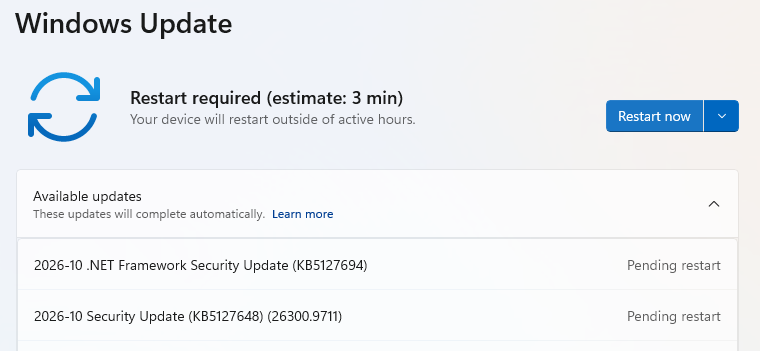
  • Click Check for updates. Windows will search for the latest security updates. If you’ve enabled Get the latest updates as soon as they’re available under More options, you may be prompted to restart immediately to complete the update.
    restart to update
  • Otherwise, continue to the next step.
  • If updates are available, they’ll start downloading automatically. When they’re ready, click Install or Restart now if prompted. Your computer may need a restart to finish the update.
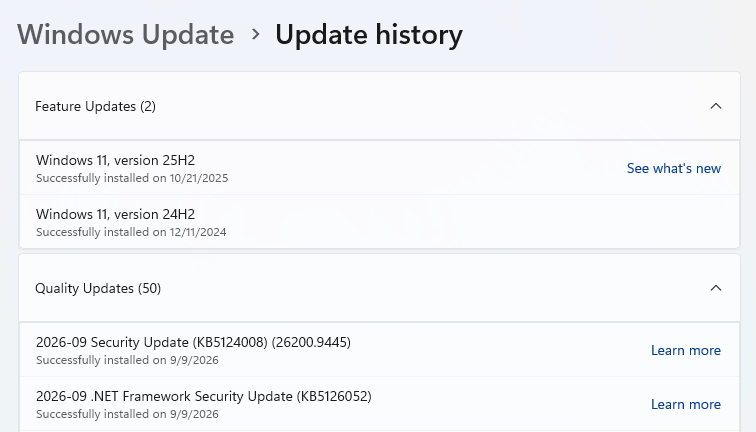
  • After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set.
Windows update

Technical details

As usual, we’ve selected a few vulnerabilities to highlight for readers interested in the technical details.

We’ll start with the actively exploited vulnerability tracked as CVE-2026-96951 (CVSS score 8.8 out of 10), a Windows Shell security feature bypass vulnerability.

The security feature it can bypass is the Mark of the Web (MOTW) defense, which can warn users about potentially unsafe downloaded files.

Successful exploitation requires user interaction. For example, in an email or instant message attack, the attacker could send the targeted user a specially crafted file designed to exploit the vulnerability, but the user would have to click a link or open an attachment.

Another one to keep an eye on is CVE-2026-108398 (CVSS score 8.8 out of 10), where an untrusted search path in .NET Framework allows an authorized attacker to bypass a security feature locally. The bypassed feature is Windows Defender Application Control (WDAC), which could lead to the ability to run unauthorized applications on target systems. This vulnerability was publicly disclosed before the patch.

Another publicly disclosed vulnerability is CVE-2026-92707 (CVSS score 5.3 out of 10). The flaw can let an unauthenticated remote attacker exhaust memory in affected applications that process specially crafted MessagePack data. MessagePack-CSharp is a software component that helps applications pack and unpack data in a compact format, making it efficient to store or exchange information. Exposure depends on how a service uses the library to pack and unpack the information.


From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

  • ✇Malwarebytes
  • Microsoft fixes record 964 flaws, including 2 exploited zero-days
    Microsoft’s September 2026 Patch Tuesday addresses 964 CVEs, including 104 rated Critical and 860 rated Important, making it the company’s largest Patch Tuesday release on record. Microsoft lists 974 CVEs in its full September security release. However, 10 of those affect cloud services or involve fixes that Microsoft applies itself, leaving 964 vulnerabilities that customers need to patch. The release includes fixes for two actively exploited Windows zero-days. Both are local elevation-o
     

Microsoft fixes record 964 flaws, including 2 exploited zero-days

9 de Setembro de 2026, 07:01

Microsoft’s September 2026 Patch Tuesday addresses 964 CVEs, including 104 rated Critical and 860 rated Important, making it the company’s largest Patch Tuesday release on record.

Microsoft lists 974 CVEs in its full September security release. However, 10 of those affect cloud services or involve fixes that Microsoft applies itself, leaving 964 vulnerabilities that customers need to patch.

The release includes fixes for two actively exploited Windows zero-days. Both are local elevation-of-privilege vulnerabilities that could allow an attacker who already has access to a device to gain SYSTEM privileges. Neither provides remote access by itself, but SYSTEM-level access is valuable to malware operators after they gain an initial foothold through phishing, stolen credentials, or another method.

How to apply patches and check if you’re protected

These updates fix security problems and help keep your Windows PC protected. Here’s how to make sure you’re up to date:

  • Click the Start button, then open Settings.
  • Select Windows Update (usually at the bottom of the menu on the left).
  • Click Check for updates. Windows will search for the latest security updates. If you’ve enabled Get the latest updates as soon as they’re available under More options, you may be prompted to restart immediately to complete the update. Otherwise, continue to the next step.
Windows 11 up to date
  • If updates are available, they’ll start downloading automatically. When they’re ready, click Install or Restart now if prompted. Your computer may need a restart to finish the update.
  • After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set.
    Windows up to date

Technical details

The unusually large batch also includes high-severity remote-code-execution vulnerabilities in Windows DNS Server and Remote Desktop Services, as well as fixes affecting Exchange Server, SharePoint, SQL Server, Office, and core Windows components.

Let’s take a closer look at the two zero-day vulnerabilities. Microsoft classifies a vulnerability as a zero-day if it was publicly disclosed or actively exploited before an official fix became available.

The first is a Windows Update Stack elevation-of-privilege (EoP) vulnerability with a CVSS score of 7.8 out of 10, tracked as CVE-2026-81963. The description says:

“Improper link resolution before file access (‘link following’) in Windows Update Stack allows an authorized attacker to elevate privileges locally.”

This means Windows can be persuaded to open or modify the wrong file because it follows a shortcut-like pointer without properly checking where that pointer leads. Microsoft says attackers exploited the bug before a patch was available.

The second zero-day, tracked as CVE-2026-85880, also has a CVSS score of 7.8 out of 10. Microsoft describes it as:

“heap-based buffer overflow in Windows ALPC allows an authorized attacker to elevate privileges locally.”

Microsoft says an attacker who can execute code in a low-privilege AppContainer could exploit the vulnerability locally to escape the sandbox and elevate their privileges on the affected system. No additional user interaction is required.

Windows ALPC is an internal messaging system in the Windows operating system that allows different programs on the same computer to communicate with each other quickly.

A buffer overflow occurs when an area of memory within a software application reaches its boundary and data spills into an adjacent memory region. The heap is a region of memory used for dynamic memory allocation.

These are not the kinds of bugs a typical victim triggers merely by opening a malicious document or visiting a website. But local privilege escalation is a critical part of many attack chains: After malware runs with limited rights, a SYSTEM-level exploit can help an intruder disable defenses, access protected data, establish persistence, or move through a network.


From reporting threats to removing them.

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

  • ✇Malwarebytes
  • Two critical Chrome flaws put users at risk on malicious websites
    Update September 4, 2026 Shortly after this article was published, Google released another Chrome update that patches an actively exploited flaw in the V8 JavaScript engine, tracked as CVE-2026-85046. Google rates the vulnerability as high severity and says an exploit already exists in the wild. An attacker could use a crafted HTML page to execute arbitrary code inside the Chrome sandbox. Because it is already being exploited, HKCERT rates the overall risk as extremely high. After ins
     

Two critical Chrome flaws put users at risk on malicious websites

2 de Setembro de 2026, 08:15

Update September 4, 2026

Shortly after this article was published, Google released another Chrome update that patches an actively exploited flaw in the V8 JavaScript engine, tracked as CVE-2026-85046.

Google rates the vulnerability as high severity and says an exploit already exists in the wild. An attacker could use a crafted HTML page to execute arbitrary code inside the Chrome sandbox. Because it is already being exploited, HKCERT rates the overall risk as extremely high.

After installing the latest update, Chrome should be at version 152.0.7977.82/.83 on Windows and Mac, or 152.0.7977.82 on Linux.

Chrome is rolling out an update for its desktop browser. The update includes 26 security fixes, two of which Google rates as critical use-after-free vulnerabilities.

How to update Chrome

If you don’t want to wait for the rollout to reach you, manually updating is easy.

The easiest option is to allow Chrome to update automatically. But you can end up lagging behind if you never close your browser or if something goes wrong with the update.

To update manually, click the More menu (three dots), then go to Settings > About Chrome. If an update is available, Chrome will start downloading it automatically. Restart Chrome to complete the update, and you’ll be protected against these vulnerabilities.

You can find an explanation of the version numbering system and step-by-step instructions in our guide: How to update Chrome on every operating system.

Technical details

Let’s look at the two critical vulnerabilities. Both are use-after-free (UAF) vulnerabilities. A use-after-free vulnerability occurs when a program attempts to access a memory location after it has been freed. That can cause crashes or, in some cases, allow an attacker to run their own code.

The first, tracked as CVE-2026-84353, was found in Shared Tab Groups and could allow a remote attacker using social engineering to execute arbitrary code outside the browser sandbox via a crafted HTML page. Here, social engineering likely means an attacker would have to lure you to a malicious website or open an email in HTML format.

The other critical vulnerability, tracked as CVE-2026-84352, was found in WebGL. WebGL, short for Web Graphics Library, is a browser technology that lets websites display interactive 2D and 3D graphics. The vulnerability could allow a remote attacker to execute arbitrary code outside the sandbox via a crafted HTML page.

Chrome vulnerabilities that enable remote code execution outside the browser sandbox are particularly valuable to attackers because they can turn a visit to a malicious or compromised website into direct code running on the underlying operating system, often without requiring additional exploitation steps.


Stop threats before they can do any harm.

Malwarebytes Browser Guard blocks phishing pages and malicious sites automatically. Free, one click to install. Add it to your browser →
  • ✇Malwarebytes
  • Patch Tuesday: Update now to fix 421 flaws, including three zero-days
    Microsoft’s August 2026 Patch Tuesday addresses 421 Microsoft vulnerabilities, including 62 rated Critical. One Windows vulnerability has been exploited in the wild by the Lazarus group to gain SYSTEM privileges. The August update is smaller than July’s record-breaking release, but it’s still among Microsoft’s largest Patch Tuesday batches. More importantly, it includes several flaws likely to attract attacker interest: a publicly disclosed Windows privilege escalation flaw with a proof-of-co
     

Patch Tuesday: Update now to fix 421 flaws, including three zero-days

12 de Agosto de 2026, 10:48

Microsoft’s August 2026 Patch Tuesday addresses 421 Microsoft vulnerabilities, including 62 rated Critical. One Windows vulnerability has been exploited in the wild by the Lazarus group to gain SYSTEM privileges.

The August update is smaller than July’s record-breaking release, but it’s still among Microsoft’s largest Patch Tuesday batches. More importantly, it includes several flaws likely to attract attacker interest: a publicly disclosed Windows privilege escalation flaw with a proof-of-concept (PoC), a newly completed unauthenticated SharePoint remote code execution (RCE) chain, and a potentially wormable Windows DNS Server flaw.

How to apply patches and check if you’re protected

These updates fix security problems and help keep your Windows PC protected. Here’s how to make sure you’re up to date:

  • Click the Start button, then open Settings.
  • Select Windows Update (usually at the bottom of the menu on the left).
  • Click Check for updates. Windows will search for the latest security updates. If you’ve enabled Get the latest updates as soon as they’re available under More options, you may be prompted to restart immediately to complete the update. Otherwise, continue to the next step.
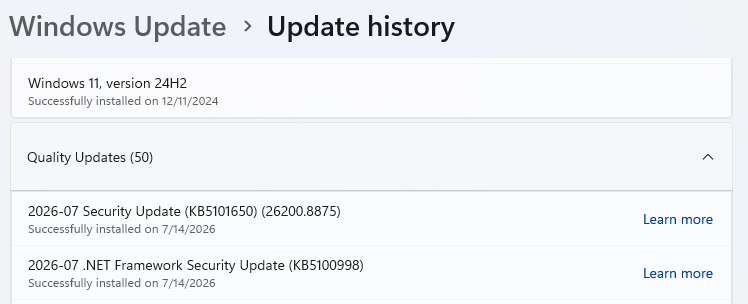
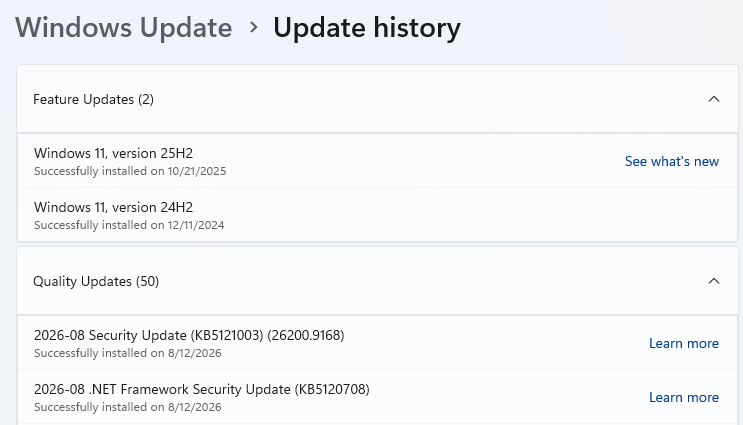
Windows update history - August 12, 2026
  • If updates are available, they’ll start downloading automatically. When they’re ready, click Install or Restart now if prompted. Your computer may need a restart to finish the update.
  • After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set.
Windows up to date

Technical details

Windows Deployment Services (WDS) users should prioritize CVE-2026-62893 (CVSS score 9.8 out of 10), an unauthenticated RCE flaw in the TFTP (Trivial File Transfer Protocol) server. TFTP normally runs on UDP port 69 and has no built-in authentication. It is primarily an enterprise and school network issue, but it could enable lateral movement where WDS is deployed.

Microsoft also fixed CVE-2026-62832, a publicly disclosed elevation of privilege (EoP) vulnerability in the Windows User Profile Service. It maps to the issue researchers called LegacyHive, for which a limited public proof of concept was released in July.

The PoC demonstrates how a local authenticated attacker could abuse the service’s registry hive handling to load another user’s hive, potentially including an administrator’s. The released demonstration is deliberately constrained and requires credentials for another user, but the availability of code and the broad Windows footprint make this one a strong candidate for exploitation attempts.

Another good reason to promptly update is the number (I counted 48) of remote code execution (RCE) fixes for Office applications and components, including Excel, Word, Outlook, PowerPoint, and the Office graphics component. Document-borne vulnerabilities are attractive to phishing operators because email attachments and shared documents provide delivery mechanisms that people are likely to open.


CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review →


  • ✇Malwarebytes
  • July 2026 Patch Tuesday fixes 622 Microsoft CVEs, including three zero-days
    Just one month ago, June 2026 Patch Tuesday broke Microsoft’s previous record with 206 CVEs and three zero‑days. July now triples that count, reinforcing that the era of “small” Patch Tuesdays may be over as AI‑driven vulnerability discovery ramps up. The update includes 59 critical vulnerabilities, as well as three publicly disclosed zero-days. Microsoft classifies these as zero-days because information about the vulnerabilities became public before patches were available. Two are known to b
     

July 2026 Patch Tuesday fixes 622 Microsoft CVEs, including three zero-days

15 de Julho de 2026, 09:21

Just one month ago, June 2026 Patch Tuesday broke Microsoft’s previous record with 206 CVEs and three zero‑days. July now triples that count, reinforcing that the era of “small” Patch Tuesdays may be over as AI‑driven vulnerability discovery ramps up.

The update includes 59 critical vulnerabilities, as well as three publicly disclosed zero-days. Microsoft classifies these as zero-days because information about the vulnerabilities became public before patches were available. Two are known to be actively exploited by attackers.

How to apply patches and check if you’re protected

These updates fix security problems and keep your Windows PC protected. Here’s how to make sure you’re up to date:

1. Open Settings

  • Click the Start button, then open Settings.

2. Go to Windows Update

  • Select Windows Update (usually at the bottom of the menu on the left).

3. Check for updates

  • Click Check for updates. Windows will search for the latest security updates.
  • If you’ve enabled Get the latest updates as soon as they’re available under More options, you may be prompted to restart immediately. If so, restart your computer to complete the update. Otherwise, continue to the next step.
    Windows Update History for July 2026

4. Download and install

  • If updates are available, they’ll start downloading automatically. When they’re ready, click Install or Restart now if prompted. Your computer may need a restart to finish the update.

5. Double-check you’re up to date

  • After restarting, go back to Windows Update and check again. If it says You’re up to date, you’re all set.
Windows is up to date

Technical details

Let’s look at the three zero-days.

First is a Windows BitLocker security feature bypass vulnerability, tracked as CVE-2026-50661. It is not known to be actively exploited. Microsoft describes it as:

“Protection mechanism failure in Windows BitLocker allows an unauthorized attacker to bypass a security feature with a physical attack.”

In other words, even if you’ve encrypted your machine with BitLocker, an attacker could exploit this vulnerability to access your data if they have physical access to your computer.

Next is the actively exploited CVE-2026-56155, an Active Directory Federation Services (ADFS) elevation of privilege (EoP) vulnerability. ADFS is a Microsoft software component that provides single sign-on (SSO) and federated access. It acts as a trust broker between an organization’s Active Directory and applications. An attacker who successfully exploited this vulnerability could gain administrator privileges. Reportedly, Microsoft discovered the vulnerability while investigating active attacks.

Last but not least is CVE-2026-56164, a Microsoft SharePoint Server elevation of privilege vulnerability. SharePoint Server is the on-premises version of Microsoft’s web-based collaboration and document management platform. A missing authentication check in Microsoft Office SharePoint could allow an attacker to elevate privileges over a network.

Both actively exploited vulnerabilities have been added to the Cybersecurity and Infrastructure Security Agency (CISA) Known Exploited Vulnerabilities (KEV) Catalog, which sets patch deadlines for Federal Civilian Executive Branch (FCEB) agencies. CISA has also urged organizations using SharePoint Server to implement hardening measures after the latest exploitations.


CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review →


  • ✇ASEC BLOG
  • June 2026 Threat Trend Report on APT Groups ATCP
    Purpose and Scope The June 2026 Threat Trend Report on APT Groups summarizes the trend of state-sponsored threat groups actively incorporating generative AI, cloud services, OAuth tokens, and commercial MaaS (Malware-as-a-Service) platforms into their attack operations. A key finding is that the scope of attacks has expanded beyond traditional Malware infections to include account and […]
     

June 2026 Threat Trend Report on APT Groups

Por:ATCP
13 de Julho de 2026, 12:00
Purpose and Scope The June 2026 Threat Trend Report on APT Groups summarizes the trend of state-sponsored threat groups actively incorporating generative AI, cloud services, OAuth tokens, and commercial MaaS (Malware-as-a-Service) platforms into their attack operations. A key finding is that the scope of attacks has expanded beyond traditional Malware infections to include account and […]
  • ✇ASEC BLOG
  • May 2026 Threat Trend Report on APT Groups ATCP
    Purpose and Scope The May 2026 APT Trends report identified supply chain attacks, developer environment attacks, automated Initial Breach, and exploitation of runtime environments as key developments. Lazarus, Famous Chollima, Gamaredon, MuddyWater, and Nimbus Manticore are of particular concern. Status of Major APT Groups by Region North Korea The Lazarus group exploited Git Hooks (Git […]
     

May 2026 Threat Trend Report on APT Groups

Por:ATCP
15 de Junho de 2026, 12:00
Purpose and Scope The May 2026 APT Trends report identified supply chain attacks, developer environment attacks, automated Initial Breach, and exploitation of runtime environments as key developments. Lazarus, Famous Chollima, Gamaredon, MuddyWater, and Nimbus Manticore are of particular concern. Status of Major APT Groups by Region North Korea The Lazarus group exploited Git Hooks (Git […]
  • ✇ASEC BLOG
  • April 2026 Threat Trend Report on APT Groups ATCP
    Purpose and Scope this report covers cyber espionage and covert sabotage activities by Region-led threat groups believed to be supported by the Region. it excludes cybercrime groups that operate for financial gain. based on publicly available analysis over the past month, we categorized threat actors according to the names of their representatives in the ATIP. […]
     

April 2026 Threat Trend Report on APT Groups

Por:ATCP
17 de Maio de 2026, 12:00
Purpose and Scope this report covers cyber espionage and covert sabotage activities by Region-led threat groups believed to be supported by the Region. it excludes cybercrime groups that operate for financial gain. based on publicly available analysis over the past month, we categorized threat actors according to the names of their representatives in the ATIP. […]
❌
❌