This week on the Lock and Code podcast…
At just 17 years old, Jordan DeMay was murdered by strangers online.
That’s how Jordan’s father, John DeMay, described what happened to his son four years ago. At home in Michigan, Jordan was readying for a weekend trip when he received a friend request on Instagram. The invite was sent by a user named “dani.robertts” whose profile showed an attractive young woman. After accepting the request, Jordan and the account chatted about nothing in particula
At just 17 years old, Jordan DeMay was murdered by strangers online.
That’s how Jordan’s father, John DeMay, described what happened to his son four years ago. At home in Michigan, Jordan was readying for a weekend trip when he received a friend request on Instagram. The invite was sent by a user named “dani.robertts” whose profile showed an attractive young woman. After accepting the request, Jordan and the account chatted about nothing in particular—teenage matters, getting to know one another—before “dani” became flirtatious, eventually sending Jordan what she claimed was a nude photograph of herself.
Jordan responded in kind with an explicit photograph of himself.
But here, a trap was revealed.
“Dani Robertts” was not a young, friendly, interested woman. Dani Robertts was several men, sending messages from thousands of miles away in Lagos, Nigeria, who had followed a script to pressure young men into handing over their money. This was not the first time these men had run this scam. But with a great deal of investigative work, it hopefully has become the last.
What happened to Jordan can happen to anyone—and it has happened to far too many young men and women today. It is a type of attack commonly referred to as “sextortion.”
Today, on the Lock and Code podcast with host David Ruiz, we speak with John DeMay about his son Jordan, his family’s relationship with social media, and what parents should know.
BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.
As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, Sh
BBC News reports it has seen samples of stolen FBI agents’ medical examinations. The “fitness-for-work” reports identify FBI agents by name and address, and reveal even more personal details. They include blood and urine test results and doctors’ notes mentioning high cholesterol, blood in the urine, and even a shellfish and banana allergy.
As we reported last week, extortion group ShinyHunters claims to have breached the FBI. After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
The BBC’s findings raise the stakes: The alleged theft includes highly sensitive medical records, not just staff identity and contact data. ShinyHunters shared samples with journalists as proof of its claims.
The BBC states:
“The samples shared with journalists appear genuine and include names, addresses, phone numbers, badge numbers, job titles and information about spouses.”
ShinyHunters claims it accessed several systems, including FBI MedLink, which stores medical records, and FBI BEAST, which handles background checks on employees and applicants, but the FBI has not confirmed these claims. The FBI has acknowledged an incident affecting FBIJobs-related systems and says it is investigating whether its own environment or a third-party provider was compromised.
The group’s stated demand remains non-financial: It wants the FBI to retract or remove a May advisory that ShinyHunters calls false and defamatory. It says it will release the data within five days if its demands are not met.
The cybercriminals also raised the number of affected people. ShinyHunters nows claims to hold sensitive information on around 60,000 current and former FBI staff. Medical histories could make affected people vulnerable long after the immediate incident: Unlike a stolen password, a medical record cannot be changed.
What to do if you’re affected
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
Extortion group ShinyHunters is not afraid to make enemies. Now it claims to have breached the FBI.
After reportedly taking over ransomware group Clop’s leak site, ShinyHunters says it attacked the FBI to punish the agency for spreading what it calls false information about the group.
In a very long post on its leak site, the group outlines its grievances:
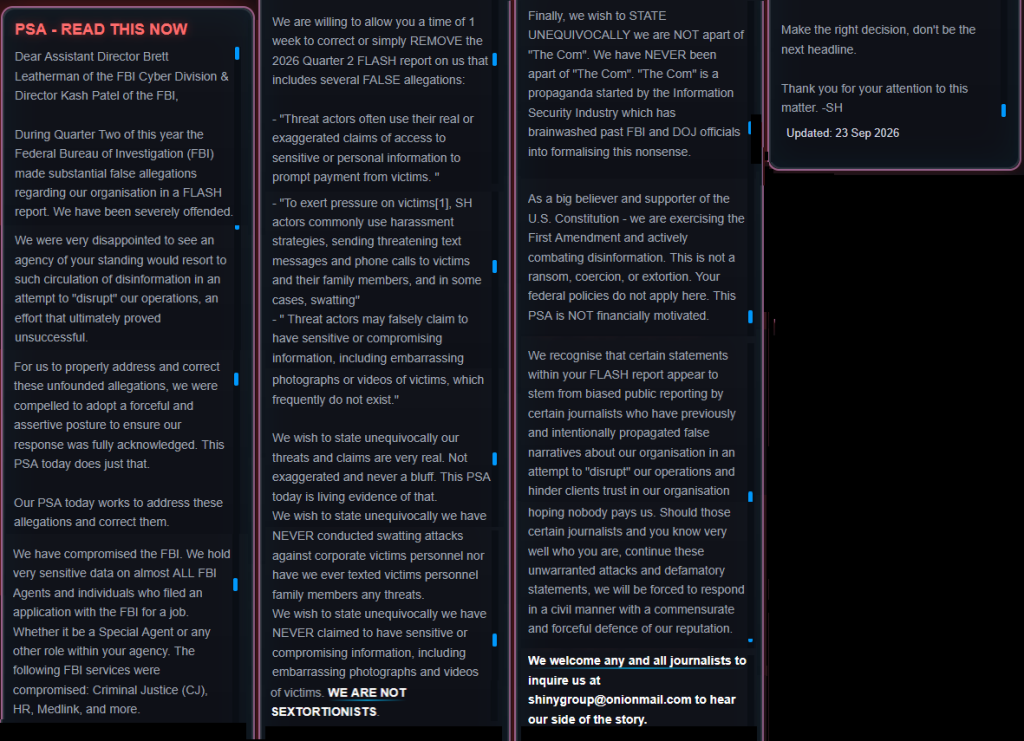
“PSA – READ THIS NOW
Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI
In a very long post on its leak site, the group outlines its grievances:
“PSA – READ THIS NOW
Dear Assistant Director Brett Leatherman of the FBI Cyber Division & Director Kash Patel of the FBI,
During Quarter Two of this year the Federal Bureau of Investigation (FBI) made substantial false allegations regarding our organisation in a FLASH report. We have been severely offended.
We were very disappointed to see an agency of your standing would resort to such circulation of disinformation in an attempt to “disrupt” our operations, an effort that ultimately proved unsuccessful.
For us to properly address and correct these unfounded allegations, we were compelled to adopt a forceful and assertive posture to ensure our response was fully acknowledged. This PSA today does just that.
Our PSA today works to address these allegations and correct them.
We have compromised the FBI. We hold very sensitive data on almost ALL FBI Agents and individuals who filed an application with the FBI for a job. Whether it be a Special Agent or any other role within your agency. The following FBI services were compromised: Criminal Justice (CJ), HR, Medlink, and more.
We are willing to allow you a time of 1 week to correct or simply REMOVE the 2026 Quarter 2 FLASH report on us that includes several FALSE allegations:
“Threat actors often use their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims.”
“To exert pressure on victims[1], SH actors commonly use harassment strategies, sending threatening text messages and phone calls to victims and their family members, and in some cases, swatting”
“Threat actors may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist.”
We wish to state unequivocally our threats and claims are very real. Not exaggerated and never a bluff. This PSA today is living evidence of that.
We wish to state unequivocally we have NEVER conducted swatting attacks against corporate victims personnel nor have we ever texted victims personnel family members any threats.
We wish to state unequivocally we have NEVER claimed to have sensitive or compromising information, including embarrassing photographs and videos of victims. WE ARE NOT SEXTORTIONISTS.
Finally, we wish to STATE UNEQUIVOCALLY we are NOT apart of “The Com”. We have NEVER been apart of “The Com”. “The Com” is a propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalising this nonsense.
As a big believer and supporter of the U.S. Constitution – we are exercising the First Amendment and actively combating disinformation. This is not a ransom, coercion, or extortion. Your federal policies do not apply here. This PSA is NOT financially motivated.
We recognise that certain statements within your FLASH report appear to stem from biased public reporting by certain journalists who have previously and intentionally propagated false narratives about our organisation in an attempt to “disrupt” our operations and hinder clients trust in our organisation hoping nobody pays us. Should those certain journalists and you know very well who you are, continue these unwarranted attacks and defamatory statements, we will be forced to respond in a civil manner with a commensurate and forceful defence of our reputation.
We welcome any and all journalists to inquire us at shinygroup@onionmail[.]com to hear our side of the story.
Make the right decision, don’t be the next headline.
Thank you for your attention to this matter. -SH
Updated: 23 Sep 2026“
The post is essentially a hostile “correction notice” directed at FBI leaders Brett Leatherman and Kash Patel. Its central grievance is an FBI advisory that says ShinyHunters commonly harasses victims and their families, including through threatening messages, phone calls, and, in some cases, swatting.
It also warns that threat actors may exaggerate their access to personal information or falsely claim to possess compromising photos or videos. The advisory does not use the word “sextortion,” but ShinyHunters appears to have interpreted the reference to compromising material that way. The group denies much of the FBI’s account while simultaneously using coercive language of its own.
The document it appears to mean is the FBI/IC3 public advisory “ShinyHunters: Cyber Criminal Group Attacks Learning Management System,” issued on May 15, 2026. Despite ShinyHunters calling it a “2026 Quarter 2 FLASH report,” the publicly accessible document is labeled a Public Service Announcement (PSA), not a FLASH.
It also denies carrying out swatting attacks or sending threatening messages to the family members of people working for its corporate victims.
The group also denies being part of The Com, a decentralized network linked to cybercrime and violence. It calls that connection:
“propaganda started by the Information Security Industry which has brainwashed past FBI and DOJ officials into formalizing this nonsense.”
The group then threatens journalists it accuses of spreading these “false narratives.”
The most worrying part of the message is the group’s claim that it stole sensitive data on:
“almost ALL FBI Agents, and individuals who filed an application with the FBI for a job.”
According to 404 Media, ShinyHunters provided a sample containing information on roughly 5,000 FBI agents, including names, home addresses, phone numbers, and details about their spouses. The publication reportedly verified portions of the sample, but the full dataset and the wider claims about the breach have not been independently confirmed.
The group also reportedly defaced the FBI’s jobs website. The FBI says it is aware of claims involving unauthorized activity affecting FBIjobs.gov and is investigating, although “broken” does not necessarily mean “breached.”
What to do if you’re affected
The FBI has not yet confirmed what information was accessed or who was affected. If you are a current or former FBI employee, a relative of one, or have applied for an FBI job:
Check the FBI’s advice. Every breach is different, so check FBI.gov for updates and follow any specific advice it offers.
Change your password. If you have an FBI Jobs account and reuse its password elsewhere, change it on those other accounts. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop, or phone as your second factor. Some forms of 2FA can be phished just as easily as a password, but 2FA that relies on a FIDO2 device can’t be phished.
Watch out for impersonators. Cybercriminals may contact you posing as the FBI, another government agency, or someone you know. Verify the identity of anyone who contacts you.
Take your time. Phishing attacks often impersonate people or brands you know and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.
The FBI has issued a Public Service Announcement (PSA) warning that criminals are breaking into social media and personal accounts to steal and distribute intimate images and videos without consent. The FBI refers to this type of content as non-consensual intimate images (NCII).
The stolen material may be posted or sold on criminal marketplaces alongside victims’ names, phone numbers, email addresses, and social media handles, creating opportunities for harassment, stalking, and sextortion.
The FBI has issued a Public Service Announcement (PSA) warning that criminals are breaking into social media and personal accounts to steal and distribute intimate images and videos without consent. The FBI refers to this type of content as non-consensual intimate images (NCII).
The stolen material may be posted or sold on criminal marketplaces alongside victims’ names, phone numbers, email addresses, and social media handles, creating opportunities for harassment, stalking, and sextortion.
According to the FBI, criminals use a mix of account takeover and social engineering tactics:
Password and PIN guessing: Criminals make high-volume login attempts using data from breaches, public social media profiles, leak sites, and other publicly available sources. Known victims may be targeted using name variations, birth dates, and other predictable personal details.
Fake customer service texts: Victims receive a message claiming their social media account will be locked or disabled. The criminal triggers a legitimate password reset request, then persuades the victim to hand over the resulting verification code.
Phishing emails: Lookalike support domains and email addresses warn of a “new login” and direct victims to a fake password change page designed to steal credentials.
This is different from the familiar “I recorded you” sextortion email, which typically relies on intimidation rather than a real account compromise. Still, if such an email includes a password you still use, change it immediately wherever it remains in use.
How to stay safe
There are several ways to reduce the risk of becoming a victim:
Avoid storing sensitive images on social media platforms or other internet-connected services when possible. Breaches and leaks happen, and those images can end up in the wrong hands.
Use a password manager to create a unique, long password for every account. Don’t base passwords or PINs on names, birthdays, or other public information.
Treat unexpected “account warning” links in texts and emails as suspicious. Open the service’s official app or type the known web address yourself instead. Don’t trust sponsored search results to take you to the correct website.
If you discover that intimate content has been stolen or shared, preserve any relevant links and evidence, secure the affected accounts, and report it through the FBI’s NCII reporting portal at ncii.ic3.gov.
Scammers don’t need to hack you. They just need you to click once.
The Federal Bureau of Investigation’s (FBI) Internet Crime Complaint Center (IC3) is warning that scammers are impersonating the bureau on social media and on messaging apps, targeting people who’ve already been victims of cybercrime.
The FBI has issued warnings like this before, but scammers posing as IC3 employees and FBI agents continue to evolve their schemes and claim new victims.
The best-known of these scams are recovery scams, complete with FBI logos and branding that make them loo
The Federal Bureau of Investigation’s (FBI) Internet Crime Complaint Center (IC3) is warning that scammers are impersonating the bureau on social media and on messaging apps, targeting people who’ve already been victims of cybercrime.
The FBI has issued warnings like this before, but scammers posing as IC3 employees and FBI agents continue to evolve their schemes and claim new victims.
The best-known of these scams are recovery scams, complete with FBI logos and branding that make them look far more convincing.
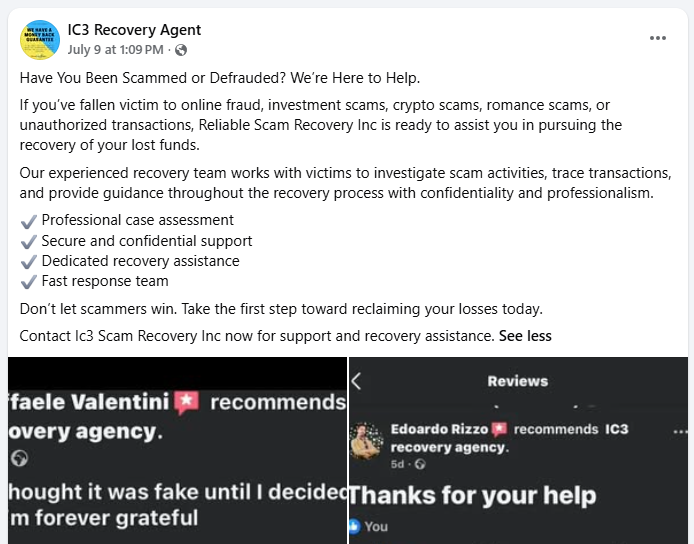
Facebook accounts like the one below—and yes, I reported it—with equally fake reviews prey on people who have already fallen victim to a scammer.
“Have You Been Scammed or Defrauded? We’re Here to Help.
If you’ve fallen victim to online fraud, investment scams, crypto scams, romance scams, or unauthorized transactions, Reliable Scam Recovery Inc is ready to assist you in pursuing the recovery of your lost funds.
Our experienced recovery team works with victims to investigate scam activities, trace transactions, and provide guidance throughout the recovery process with confidentiality and professionalism.
Professional case assessment
Secure and confidential support
Dedicated recovery assistance
Fast response team
Don’t let scammers win. Take the first step toward reclaiming your losses today.
Contact Ic3 Scam Recovery Inc now for support and recovery assistance.”
The scammers count on victims feeling desperate and embarrassed. They have no scruples about victimizing them all over again.
The post contains a lot of the tell-tale signs IC3 warns about. Very vague but reassuring claims: “experienced recovery team,” “professional case assessment,” “secure and confidential support” all sound impressive but provide no verifiable detail. High‑level promises like “investigate scam activities” and “trace transactions” imply special legal or technical powers, but the FBI warns that scammers make similar promises to convince victims they’re dealing with authorized investigators.
Besides setting up fake IC3 accounts, they also monitor social media for posts from victims saying they’ve reported a scam to the FBI, then swoop in posing as FBI follow‑up contacts.
If victims remain unconvinced, the scammers may create videos depicting senior FBI officials or other recognizable public figures urging them to submit their case through a specific link “to speed up recovery.” The FBI says criminals are increasingly using AI-generated deepfake audio and video to make these messages appear genuine.
How to stay safe
First and foremost, remember that IC3 has no official social media presence, does not investigate crimes via social media, and will never contact victims directly to recover funds.
“The IC3 does not work with any non-law enforcement entity, such as law firms or crypto services, to recuperate lost funds or investigate cases. The IC3 will never directly contact you for information or money.”
So, if an “agent” appears in your direct messages (DMs) right after you post publicly about being a crime victim or planning to report to the FBI, assume they are a scammer until independently verified. A few other tips:
Never pay upfront: Legitimate government agencies never ask you for advance payment to recover stolen money.
Ignore unsolicited claims: Be highly suspicious of anyone who reaches out to you out of the blue claiming they can reverse a previous scam.
Never share your credentials: Do not give remote access to your device or hand over your passwords and recovery phrases to unknown third parties.
Don’t provide IDs or financial information. Scammers can use them for identity theft or further fraud.
Use verification tools: If you receive a suspicious email, message, or phone call, you can verify its legitimacy using tools like Malwarebytes Scam Guard.
Report scammers: If you or someone you know has fallen victim to this scam, file a complaint with the IC3 at ic3.gov.
Something feel off? Check it before you click.
Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.
ASEC Blog publishes Ransom & Dark Web Issues Week 4, May 2026 Customer Data of Japanese Educational Franchise Sold on BreachForums by Hasan Data from Japanese Government Agency for National Civil Servant Personnel Administration Sold on BreachForums by Hasan FBI Issues Warning Regarding Fraudulent FIFA Websites Ahead of 2026 FIFA […]
ASEC Blog publishes Ransom & Dark Web Issues Week 4, May 2026 Customer Data of Japanese Educational Franchise Sold on BreachForums by Hasan Data from Japanese Government Agency for National Civil Servant Personnel Administration Sold on BreachForums by Hasan FBI Issues Warning Regarding Fraudulent FIFA Websites Ahead of 2026 FIFA […]
Notes the April 2026 Dark Web Threat Actor Trend Report summarizes trends in hacktivists and threat actors operating on the deep web and dark web. due to the nature of the sources, some of the information is difficult to fully verify as factual. Major Issues NoName05716 claimed repeated DDoS attacks against dozens of organizations, including […]
Notes the April 2026 Dark Web Threat Actor Trend Report summarizes trends in hacktivists and threat actors operating on the deep web and dark web. due to the nature of the sources, some of the information is difficult to fully verify as factual. Major Issues NoName05716 claimed repeated DDoS attacks against dozens of organizations, including […]
CISA and the FBI recently released a joint statement that the People’s Republic of China (PRC) is targeting commercial telecommunications infrastructure as part of a significant cyber espionage campaign. As a result, the agencies released a joint guide, Enhanced Visibility and Hardening Guidance for Communications Infrastructure, with best practices organizations and agencies should adopt to protect against this espionage threat.
According to the statement, PRC-affiliated actors compromised net
According to the statement, PRC-affiliated actors compromised networks at multiple telecommunication companies. They stole customer call records data as well as compromised private communications of a limited number of people. Sen. Mark R. Warner (D-Virginia) told the Washington Post that the threat actors listened on audio calls and even moved between networks. As a result, many media sources reported that texts between Android and Apple devices are not secure.
Historic and sophisticated cyberattack
The headlines of the Washington Post deemed it the worst telecom hack in our nation’s history, per a top U.S. senator. On the surface, this seems a bit melodramatic, with only 150 identified victims. However, experts predict the affected number of people will go into the millions. Warner, who serves as chairman of the Senate Intelligence Committee, went as far as to say that Salt Typhoon makes Colonial Pipeline and SolarWinds “look like child’s play.”
The data collected during the attack falls into two categories, reported NBC. The first included call records showing the time and number called, with most records in the Washington, D.C. area. The other included listening to live calls of specific targets, which may include Donald Trump and Kamala Harris.
However, the most concerning aspect of the attack is the national security implications. Richard Forno, Principal Lecturer in Computer Science and Electrical Engineering at UMBC, explained in UMBC Magazine that Salt Typhoon compromised the portals used by U.S. intelligence and law enforcement. As a result, he says that the attackers may have gotten information about which Chinese spies and informants counterintelligence agencies were monitoring, which those targets can then use to avoid detection.
“U.S. officials have said that many of the ways Salt Typhoon penetrated its targets was through existing weaknesses with the infrastructure. As I’ve written previously, failing to implement basic cybersecurity best practices can lead to debilitating incidents for organizations of all sizes. Given how dependent the world is on networked information systems, it is more important than ever to maintain cybersecurity programs that make it difficult for attacks to succeed, especially for critical infrastructure like the phone network,” wrote Forno.
Reducing the risk of Salt Typhoon
With words like espionage and intercepting texts thrown around, the biggest question on people’s minds is how to protect themselves from this threat. Many experts are currently recommending using encrypted apps, such as WhatsApp and X, instead of traditional texting.
“Encryption is your friend, whether it is on text messaging or if you have the capacity to use encrypted voice communications, even if the adversary is able to intercept the data if it is encrypted, it will make it impossible, if not really hard, for them to detect it. So, our advice is to try to avoid using plain text,” said Jeff Greene, CISA Executive Assistant Director for Cybersecurity, during a press briefing reported by USA Today.
Forbes also reported that an FBI official recommended citizens use a cell phone that automatically receives timely operating system updates. Additionally, the phone should have responsibly managed encryption and phishing-resistant multi-factor authentication (MFA) for email, social media and collaboration tool accounts.
“So it’s somewhat ironic that one of the countermeasures recommended by the government to guard against Salt Typhoon spying is to use strongly encrypted services for phone calls and text messages – encryption capabilities that it has spent decades trying to undermine so that only ‘the good guys’ can use it,” wrote Forno.
To learn how IBM X-Force can help you with anything regarding cybersecurity including incident response, threat intelligence, or offensive security services schedule a meeting here.
If you are experiencing cybersecurity issues or an incident, contact X-Force to help: US hotline 1-888-241-9812 | Global hotline (+001) 312-212-8034.

 Entrar