The Indian CA eMudhra Limited has eight TLS certificates with laughably weak private keys:
The compromised eMudhra keys were defective at a level that’s challenging the imagination of many of the engineers studying the incident. A normal size for a NIST P-384 elliptic curve cryptography private key contains roughly 384 bits of entropy, a size allowing almost 2384, or a number with 116 digits, different possibilities. The private key sizes of the compromised keys ranged from 3 to 8 bits. Astonish
The compromised eMudhra keys were defective at a level that’s challenging the imagination of many of the engineers studying the incident. A normal size for a NIST P-384 elliptic curve cryptography private key contains roughly 384 bits of entropy, a size allowing almost 2384, or a number with 116 digits, different possibilities. The private key sizes of the compromised keys ranged from 3 to 8 bits. Astonishingly, the private keys were 4, 56, 66, 115, 155, 156, 230, 237.
“That is extremely in the ‘this should not be possible’ category,” Valdorda said. “Maybe some horribly dangerous key generation interface has a ‘size’ parameter and they set it to 1 by mistake???”
Ben Cartwright-Cox, director of BGP.tools, said: “My guess is that it’s example code that accidentally leaked to production, but hard to know. But it’s bonkers that no one noticed.”
At this early stage, the most immediate threat appears to be for those using VPNs, especially in countries with governments likely to maliciously intercept traffic. There are likely many other cases for concern. End users largely have no recourse other than to hold off using many non-browser forms of TLS communication until they receive assurances updates are in place.
The whole certificate regime has long been a mess:
The incident is the latest to expose a fatal flaw in the TLS regimen. It’s only as strong as its weakest link, which in this case was eMudhra. Fortunately, transparency logs account for much of that failure, but this measure requires parties to actively monitor massive feeds and works only after unauthorized certificates have been issued. eMudhra representatives weren’t immediately available to answer questions.
One caveat: exploiting compromised certificates requires an active adversary-in-the-middle attack, meaning the attacker must act as a proxy between two TLS parties and receive encrypted traffic, decrypt it, reencrypt it, and send it to the other party. Such capabilities, in some cases, are usually limited to only the most well-resourced attackers. People with control of a local networkat a coffee shop, university, or other organizationface much less of a challenge.
Cleanup of this is going to be another mess—and it’s right on top of the PHP vulnerabilities.
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published.
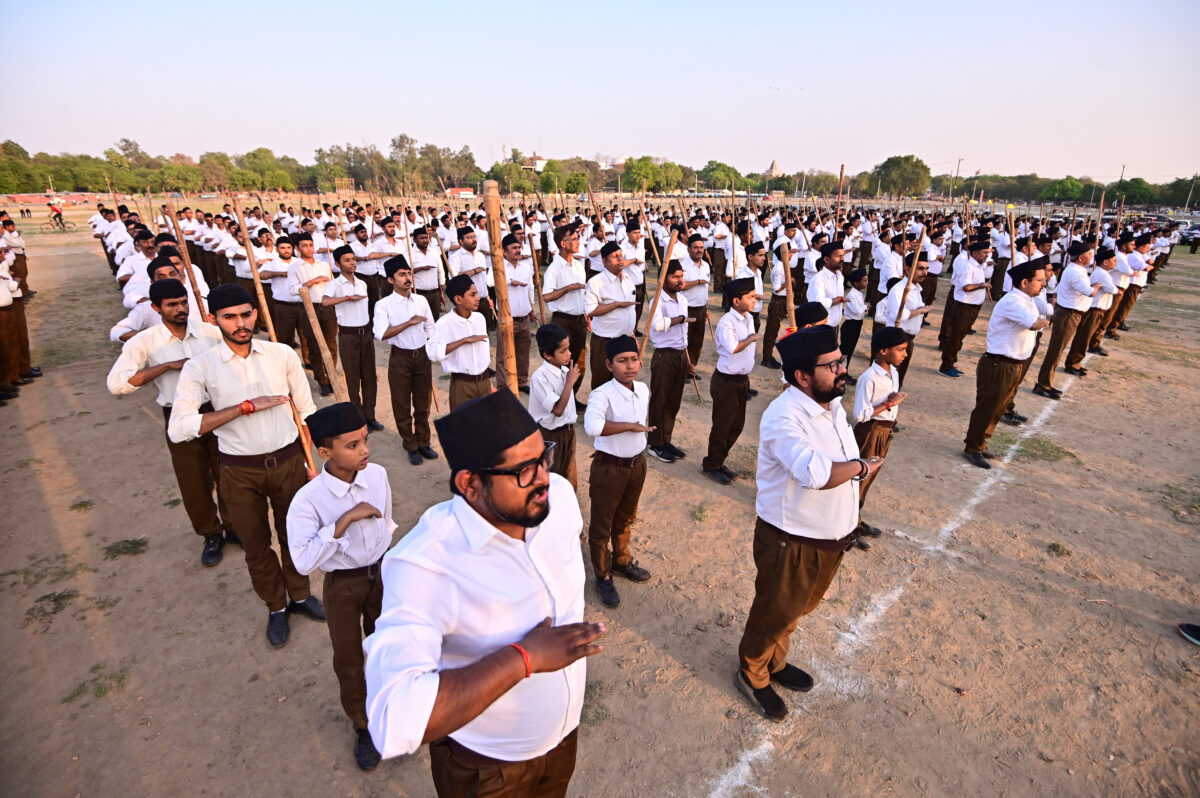
US non-profits whose founding leaders or organisations have been associated with India’s controversial Rashtriya Swayamsevak Sangh (RSS) – or initiatives the Hindu nationalist group has endorsed – received millions of dollars over recent years through grants that allow donors to remain anonymous, a Bellingcat analysis has found.
The right-wing and Hindu nationalist volunteer organisation is
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published.
US non-profits whose founding leaders or organisations have been associated with India’s controversial Rashtriya Swayamsevak Sangh (RSS) – or initiatives the Hindu nationalist group has endorsed – received millions of dollars over recent years through grants that allow donors to remain anonymous, a Bellingcat analysis has found.
The right-wing and Hindu nationalist volunteer organisation is widely considered the ideological parent of India’s ruling Bharatiya Janata Party (BJP). Prime Minister Narendra Modi, a former RSS worker, is one of its most famous supporters.
But the RSS’ vision of India as a Hindu nation is controversial both at home and abroad: it was previously banned in India three times, and a bipartisan US commission on religious freedom recently called for the US government to sanction the group “for their responsibility and tolerance of severe violations of religious freedom”. Almost a hundred US politicians, both Democratic and Republican, recently pledged not to take funding from RSS-linked entities.
India’s far-right Hindu nationalist volunteer group RSS remains an unregistered entity in India. Source: Prabhat Kumar Verma/ZUMA Press Wire via Reuters Connect
“The RSS functions without independent oversight of its resources, finances, influence, and activities,” said Dr Angana P Chatterji, an anthropologist and scholar of South Asia studies at the University of California, Berkeley. “This is not proportional to the vast power, reach, and influence it possesses. Its leadership and cadre are protected from accountability and scrutiny,” she added.
The RSS had not responded to multiple requests for comment, as of publication.
Bellingcat identified two US-registered non-profits that appeared to have past and present ties to the RSS, or organisations associated with them, based on the non-profits’ or RSS websites and publications, as well as statements by the non-profits’ founders and spokespeople. The non-profits were the Ekal Vidyalaya Foundation of USA Inc (Ekal USA) and Sewa International Inc (referred to as Sewa USA).
We looked at all Form 990s – tax returns that US non-profit organisations are required to file annually – listing Ekal USA and Sewa USA as grant recipients, as well as the Form 990s of the charities themselves, from 2020 to 2024. As of September, the latest available Form 990s for Sewa USA were for the fiscal year ending December 2024, while Ekal USA also filed a form for the fiscal year ending December 2025, which was excluded for consistency, although the same pattern was observed during this period.
This analysis showed that the charities received at least US$24.4 million from 34 organisations that manage donor-advised funds (DAFs), or 20.7 percent of the total $117.8 million they reported receiving in contributions and grants during this period.
The actual amount from DAFs may be higher, as we excluded filings that covered partial years outside of this period – for example, June 2019 to June 2020. The filings from the two charities we identified were based on the calendar year.
The Form 990s also revealed that the vast majority of the money spent by these two charities on grants to other organisations or individuals was in India or the South Asia region rather than in the US: Ekal USA donated $33.7 million in foreign grants – all of which went towards the Ekal Vidyalaya project in India according to its filings – and none in domestic grants in the five years from 2020 to 2024, while Sewa USA reported $29.7 million in foreign grants and $622,613 in domestic grants during the same period.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
DAFs are common vehicles for people in the US who want to make donations to charitable causes while receiving tax relief or benefits. Donors do not control the money once they donate it but can advise on which charities the money eventually ends up at.
These funds are legally maintained and operated by non-profit sponsoring organisations. As public charities, DAF sponsor organisations detail the amounts and recipients of grants that they make on behalf of their donors in their Form 990s. However, they do not disclose who their donors are, and donors can choose to remain anonymous. (Note: Bellingcat USreceives grants from donor-advised funds, and some grants do not disclose the name of the grant recommender. However, many of our donors are listed on our funding page.)
There are many more organisations reportedly linked to the RSS that are not included in this analysis, but we focused on these two because of the large amounts of grants they received through DAFs, with the original sources of the funds untraceable from public information, as well as evidence pointing to both historical and current connections between them and the RSS or organisations associated with the RSS.
It is worth noting that some of the evidence we found pointing towards a connection between the two charities and the RSS or organisations associated with the RSS was from before or after the period we analysed (2020 to 2024). There is no evidence that DAF grants funded the RSS, only that they went to organisations that appear to have connections with the RSS. Experts told us that DAF grants undergo less regulatory scrutiny than other charitable donations and that DAF sponsor organisations have discretion over whether to restrict or permit donations to certain recipients.
Ekal USA
Houston, Texas-based Ekal USA is a non-profit that describes its mission in its Form 990s as “to provide free elementary education and free primary healthcare to children in remote and rural India”. The USA branch of Ekal Vidyalaya, according to its website, was founded in 2001 as part of efforts to “reach out to the global diaspora” in order to achieve a goal to “expand the reach of Ekal to 100,000 villages”.
RSS chief Mohan Bhagwat has appeared at multiple Ekal Vidyalaya events in India promoting the initiative over the years, as far back as 2014 and most recently in May.
Ekal USA was started in the late 1990s as a programme of the Vishwa Hindu Parishad of America (VHPA), or World Hindu Council of America, VHPA spokesperson Shyam Tiwari told Bellingcat in an email response. He added that it was set up as an independent organisation in early 2000. According to VHPA’s website, Ekal USA was established in 2002.
VHPA is based in the US, while the similarly named Vishwa Hindu Parishad (VHP) is in India. VHP lists VHPA in the “Hindus Abroad” section of its website. A 2017 article from VHPA’s magazine states that late founder Mahesh Mehta was trained by the RSS since he was 10 years old, and that the VHPA was born after Mehta was advised by the former supreme leader of the RSS to “build VHP in USA”. The national spokesperson of VHP in India, Vinod Bansal, said that it is an independent organisation that “sometimes shares ideology” with VHPA.
RSS’ website states that VHP was launched to organise Hindus and “reconvert all those who had been knowingly or unknowingly proselytised to alien faiths and are now desirous of coming back to the Hindu fold”. Bansal referred to VHP as an “independent part of the RSS” and an “ideological brother”.
Ekal USA Chairman-Advisor Subhash Gupta wrote in an Ekal USA publication this year that in the ‘80s and ‘90s, he was “president of the VHP’s Houston chapter” and “often received many high-profile guests from RSS and VHP”.
Gupta did not respond to requests for comment as of publication.
From 2020 to 2024, Ekal USA reported receiving more than $48.4 million in contributions and grants. Of this amount, at least $8.3 million was from DAF grants, based on Form 990s that listed Ekal USA as a grantee.
According to Ekal USA’s Form 990s, it transferred $33.7 million in foreign grants during this period and none in domestic grants for organisations or individuals. The forms also show that all the foreign grant money went towards building Ekal Vidyalaya schools in India. The rest of its expenses involved operational costs such as staff salaries.
The Ekal Vidyalaya movement has been criticised over reports that allege the schools are used to indoctrinate millions of India’s poorest and most vulnerable children and women with Hindu nationalist ideology, including that Muslims and Christians are “enemies of Hinduism”. Ekal Vidyalaya in India did not respond to multiple requests for comment.
Ekal USA did not respond to Bellingcat’s questions about these reports or any relationship it may have with the RSS. However, on its FAQ page, the group states that it does not teach religion in its schools and “does not discriminate based on caste, religious affiliation or linguistic affiliations”.
Sewa USA
Sewa USA, also based in Houston, describes itself as a “Hindu faith-based, humanitarian, nonprofit service organisation” and is listed under the heading of “Sewa Movement” on the website of India-based charity group Sewa International.
Sewa USA Vice President of Public Affairs Rakhi Israni told Bellingcat over email that the organisation “does not operate as a branch or affiliate of the RSS” or participate in political activity.
But multiple pages on the organisation’s website appear to indicate a connection between the non-profit and the RSS. In 2022, Sewa USA reposted an article on its website referring to Sewa International as “the US-based charitable non-profit organisation with links to the Rashtriya Swayamsevak Sangh (RSS)”. In a press release about the death of its founding member Ved Prakash Nanda in 2023, it noted that Nanda was “immersed in the ideals of the [RSS]”. And two different blog posts from 2021 and 2024 on Sewa USA’s website had volunteers citing RSS-led activities as the starting point for their involvement.
In addition, Sewa USA has also posted multiple times on social media and its website about an India-based organisation – Sewa Bharati – that appears to have the support of the RSS.
Sewa USA referred to Sewa Bharati as a “sister organisation” in an X post in 2014, and its regional chapter in Purvanchal as a “partner organisation” in a Facebook post in 2022.
On its website, Sewa USA said in a post that volunteers from its “partner organisations in India” had participated in rescue operations related to the 2023 train accident in Odisha, and listed several initiatives by Sewa Bharati in India. It also launched a fundraiser for families affected by floods in Maharashtra in September 2025, which mentioned that over 100 Sewa Bharati volunteers were already on the ground clearing debris and assisting communities.
“Foreign grants awarded to partner agencies in India, including service-oriented NGOs like Sewa Bharati, are strictly project-based, fully audited, and evaluated based on measurable humanitarian impact in education, health, and disaster relief,” Israni told Bellingcat.
Subscribe to the Bellingcat newsletter
Subscribe to our newsletter for first access to our published content and events that our staff and contributors are involved with, including interviews and training workshops.
RSS’ website links directly to the main website of Sewa Bharati through a tab on its main navigation bar labelled “Sewa”, and Sewa Bharati is mentioned in RSS’ 2016 annual report under the heading “Seva Vibhag”, a Sanskrit term for “service department”.
A blog post on Sewa Bharati’s website from December 2024 about an event the group organised described Indian Defence Minister Rajnath Singh as highlighting the role of RSS leaders in establishing Sewa Bharati in his address and noting that “RSS not only builds the nation but also the individual”. RSS Joint General Secretary Alok Kumar also spoke at the Sewa Bharati event, according to the blog post.
In response to Bellingcat’s queries, Israni said that Sewa USA had “no role in Sewa Bharati’s governance or operations”. Sewa Bharati did not respond to multiple requests for comment as of publication.
Sewa USA received almost $69.4 million in contributions and grants from 2020 to 2024, according to its Form 990s. Filings listing Sewa USA as a grantee show that at least $16 million was from DAFs. In its expenditure statements, Sewa USA reported giving $29.7 million in foreign grants to groups in South Asia during this period and about $622,613 in grants domestically in the US, while the rest of its expenditures included operational costs such as salaries and travel. It is not specified in the forms how much funding, if any, Sewa USA transferred to Sewa Bharati during this period, and Sewa USA did not respond to questions about any amounts transferred as of publication.
‘Cause-Neutral’ Funding
Experts told Bellingcat that there was less regulatory scrutiny of grants distributed through DAFs than some other types of charitable donations.
“For donor-advised funds, there’s actually less oversight by the IRS because donor-advised funds are considered public charities rather than private foundations,” said Samuel Brunson, a law professor at Loyola University Chicago.
“If a private foundation were giving money to organisations in India, that would be a little bit trickier. But if it’s a public charity … there’s not really a ton of oversight on that as long as the money that the US tax-exempt organisation is giving meets its charitable purpose.”
Lloyd Hitoshi Mayer, a law professor at the University of Notre Dame who specialises in non-profits, said that it was “irrebuttably presumed” that funds granted to US organisations with the non-profit 501(c)(3) tax status were being used for good charitable purposes.
“The existing federal tax laws related to donor-advised funds put some restrictions on what grants donor-advised fund sponsor organisations, which actually control the funds, can make. But the big exception is that Congress said, ‘If you make a grant to a Section 501(c)(3) charity, you’re good.’ You don’t have to do any additional oversight.”
Some DAF sponsor organisations have previously faced criticism for granting money to charities that have promoted homophobic, anti-immigrant or anti-Muslim views. Several were also criticised for pausing funding to the Southern Poverty Law Centre earlier this year, although this case demonstrated how DAFs can prevent funds from going to some groups recommended by donors, if the DAFs deem them unsuitable.
Brunson told Bellingcat that DAF sponsor organisations “absolutely have the right and ability” to halt processing donations to certain organisations. “Whether we want them to do that or not is a separate question,” he said.
Bellingcat reached out to the top three DAF sponsor organisations that donated to the two non-profits we identified – Fidelity Investments Charitable Gift Fund (Fidelity Charitable), American Online Giving Foundation (AOGF) and Charles Schwab-affiliated Donor Advised Charitable Giving (DAFgiving360; known before 2024 as Schwab Charitable) – to ask about their internal policies on assessing charities receiving donations through their funds. In total, the three DAFs accounted for almost $20 million, or 81.7 percent, of the DAF grants to Ekal USA and Sewa International for full reporting years between 2020 and 2024.
Fidelity Charitable, AOGF and DAFgiving360 all told Bellingcat that they had due diligence processes in place when evaluating non-profits.
Fidelity Charitable’s website states that it is a “cause-neutral” charity, but it ensures grants are used solely for charitable purposes. AOGF said non-profits must comply with eligibility requirements regarding hate speech, discrimination and the use of funds.
Meanwhile, DAFgiving360 said that a grant recipient may be subject to monitoring or placed under temporary suspension “due to circumstances that DAFgiving360 deems appropriate”, such as if there is a public interest consideration or if the recipient does not further DAFgiving360’s mission.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters. In the days immediately following the suspect’s arrest, remaining ShinyHunters members dramatically escalated their attacks, stealing highly sensitive data from the FBI and extorting the Russian ransomware group Cl0p.
According to three sources familiar with the matter, the Dutch man arrested by authorities this month i
Authorities in the Netherlands have arrested a 24-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group ShinyHunters. In the days immediately following the suspect’s arrest, remaining ShinyHunters members dramatically escalated their attacks, stealing highly sensitive data from the FBI and extorting the Russian ransomware group Cl0p.
According to three sources familiar with the matter, the Dutch man arrested by authorities this month is Pepijn van der Stap, a convicted cybercriminal from Almere and Lelystad in the Netherlands. Van der Stap was previously convicted in 2023 in connection with a string of data thefts and extortions that prosecutors said earned between €1.5 million and €2.7 million.
At his trial in late 2023, van der Stap admitted that he lived a Dr. Jekyll and Mr. Hyde existence, secretly using the hacker handle “Umbreon” to extort victims and post their data on English language hacking communities like the now-defunct RaidForums and Breached. By day, however, van der Stap was working as a software engineer at the Amsterdam-based cybersecurity startup Hadrian, while volunteering at the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit security research group.
Pepijn van der Stap’s alter ego “Umbreon” selling a database on RaidForums, offering information on 2.3 million people from The Netherlands in September 2021. This user’s avatar is a depiction of the Pokemon character Umbreon. Image: KELA.
Van der Stap confessed to his data theft and extortion activity, and was sentenced to four years in prison (one of which was suspended). During his trial, van der Stap opted to remain in custody for a time rather than at home, saying he could not find better treatment on the outside for his ongoing psychological issues, which he claimed included PTSD related to childhood trauma. He was released from prison in December 2025.
In an interview with KrebsOnSecurity on September 9, 2026, Van der Stap cast himself as a reformed hacker who was trying to turn his life around and make a positive contribution to society. Van der Stap is currently employed as offensive security lead at the Dutch company Neo Security, which did not respond to requests for comment.
Van der Stap said he was still dealing with civil lawsuits and restitution related to his previous cybercrime victims, and that he was trying his best to make amends. But not long after that interview, the Dutch hacker abruptly stopped replying to messages. Efforts by others close to him also repeatedly failed to elicit a response for the past two weeks.
The LinkedIn profile for Pepijn van der Stap.
According to two sources with knowledge of the matter, Van der Stap was arrested by Dutch authorities on or around September 16, and has been held in custody for questioning since. One source said a colleague of theirs personally witnessed Dutch authorities carting items out of Van der Stap’s residence.
Authorities in the Netherlands have been asking the public for help in identifying the voice in a recorded telephone call from February 2026 in which a native Dutch-speaking ShinyHunters member social engineered their way into Odido, the nation’s largest mobile telecommunications provider. In that intrusion, ShinyHunters tricked an Odido employee into logging in at a spoofed website, and then used that access to steal data on more than 6.2 million Dutch people.
Responding to Dutch news media, ShinyHunters confirmed that the suspect in the audio clip is indeed a member of the hacker collective.
“Our team member has our full support – emotionally, mentally, and financially,” the hackers said. “Everything has been arranged, including a criminal defense lawyer. We do not look down on our staff and members; we take excellent care of them,” reads a statement ShinyHunters shared with NL Times. It remains unclear if the Dutch police have matched the Odido caller to a confirmed real-life identity. The Dutch police unit handling the Odido incident did not respond to requests for comment.
The group also lashed out at the authorities in the Netherlands. “The Dutch police will need all the luck in the world – and everyone’s prayers – if they want to catch him before we carry out another large-scale data theft in the Netherlands,” the ShinyHunters statement said. “Frankly, the Dutch police are a big joke; they are incapable of doing anything. Incompetent. Irrelevant. Unimportant. Useless.”
FBI, CL0P HACKS
Just days after sources say Van der Stap was detained by Dutch authorities, ShinyHunters claimed credit for an unusually brazen breach at the FBI’s job application site apply.fbijobs.gov. According to reporting from 404 Media, the data stolen from the FBI site includes Social Security numbers and personal information on more than 5,000 officials.
404 Media and Reuters reported the FBI data included each person’s job title or team, such as special agent, threat intake examiner, major cybercrimes unit, and those investigating cyber threats from foreign state-backed actors. Reuters examined documents shared by ShinyHunters and found they included sensitive psychiatric and medical files of FBI staff. The FBI issued a brief statement confirming the hack.
ShinyHunters said it gained access to the FBI site and other victims by exploiting a recently patched vulnerability (CVE-2026-35273) in PeopleSoft, a software-as-a-service platform from the software giant Oracle that is broadly used by companies to manage hiring and human resources, benefits and payroll. Oracle quickly issued a fix for the Peoplesoft vulnerability that ShinyHunters reportedly began exploiting as a zero-day in June, and at the time Mandiant released web application firewall rules intended for organizations who couldn’t apply the security update quickly enough.
But on Friday, BleepingComputer reported that ShinyHunters used a URL-encoding trick to bypass Mandiant’s suggested web application firewall rules designed to mitigate the threat from the PeopleSoft flaw. In a report released Sept. 25, security experts at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that ShinyHunters had mass-exploited the PeopleSoft vulnerability to steal data from dozens of systems across a range of industries, including higher education, technology, healthcare, agriculture, transportation and government.
Van der Stap’s former hacker alias Umbreon was hidden in plain sight throughout the imagery ShinyHunters used to spread news about the FBI hack: The defacement image that ShinyHunters left behind on the hacked FBI jobs site included an ASCII art design featuring the Pokemon character Umbreon. The message at the top read, “This site has been seized by ShinyHunters. rooting your systems since ’19 ;)” The image appears identical to a defacement message ShinyHunters used in their 2020 hack of the English-language cybercrime community Hackforums.
The defacement message left by ShinyHunters on the FBI jobs site included an ASCII art rendition of the Pokemon character Umbreon. Image: Bleeping Computer.
Multiple sources close to the ShinyHunters investigation said the group’s recent risky attacks against the FBI and one of Russia’s most venerated ransomware groups amounted to a major pivot away from the more measured tenor of the hacking gang’s operations. Those sources said the sudden shift came about after ShinyHunters was taken over by a teenage cybercriminal from Amman, Jordan who goes by the nickname Rey and operates as part of a cybercrime group called ScatteredLapsussHunters (SLSH), which experts say is an amalgamation of three hacking groups — Scattered Spider, LAPSUS$ and ShinyHunters.
Those sources said Rey had an ongoing beef with the Dutch hacker over control of the ShinyHunters brand and data, and that the inclusion of the oversized Umbreon Pokemon image in the FBI jobs site defacement was likely an attempt by Rey to pin the hack on the Dutchman.
Rey was first publicly identified by the cybersecurity firm KELA in March 2025. In advance of our November 2025 profile of Rey, KrebsOnSecurity messaged Rey’s father and asked for permission to interview his teenage son. Rey’s dad merely forwarded the message to his son, who admitted to participating in ransomware attacks and said he was trying to extricate himself from the SLSH hacker group.
BLAMING UMBREON
Immediately after news of the FBI jobs site hack was picked up in the media, Rey’s main account on Twitter/X (Ryan Moran/@rmoskovy) was taunting the Cl0p ransomware group and the FBI, crudely depicting them as the twin towers in New York being struck by planes labeled “cl0p drama” and “fbi breach claim.” In the foreground of the city is the giant Pokemon figure of Umbreon.
A taunting meme uploaded to Twitter/X by Rey’s now-defunct account on Sept. 22. A giant float-sized version of the Pokemon character Umbreon can be seen in the bottom left.
On Sept. 24, KrebsOnSecurity again contacted Rey’s dad, asking to interview him and his son for a story on Rey’s apparent ascendency as the head of ShinyHunters. Just hours after that request, Rey deleted his longtime Twitter/X account. Meanwhile, Rey’s dad, who works for the Royal Jordanian Airlines, has failed to respond to a half-dozen emailed requests for comment about his son’s alleged activities.
Where does the bad blood between SLSH and ShinyHunters come from? According to a story in Wired this month, ShinyHunters and SLSH members briefly partnered earlier this year to help better monetize important stolen credentials collected by TeamPCP, an upstart group that was having great success compromising global code supply chains with malicious software but hadn’t been able to profit much from their stolen data (two alleged leaders of TeamPCP were arrested last month in Australia, and in an interview the TeamPCP leader claimed they made just $20,000).
The Wired story noted how Mandiant had infiltrated TeamPCP and was secretly responsible for having the crime group’s stolen credentials burned so quickly: Mandiant was secretly feeding those credentials to the major cloud providers like Amazon and Microsoft, who quickly invalidated the stolen keys. Meanwhile, the formerly cooperating hacker groups began to blame one another for causing the credentials to become worthless.
Wired’s Andy Greenberg reported that a few weeks after partnering with TeamPCP, “ShinyHunters went rogue, carrying out its own extortions with TeamPCP’s credentials but without giving the supply-chain hackers their cut.”
Mandiant researcher Austin Larsen told KrebsOnSecurity earlier this month that ShinyHunters has been enjoying a successful extortion spree so far this year, and is on track to pull in nearly $100 million in extortion payments from cybercrime victims in 2026.
Van der Stap claims he was never motivated by money and that his earlier hacker activity was driven by a desire to have the world’s most complete collection of stolen databases. Speaking with reporters from Bloomberg in 2024, Van der Stap said that singular focus in turn fueled his desire to carry out cyberattacks.
“The hacking was very easy for me, and it wasn’t a compulsion,” he told Bloomberg. “My habit was collecting. Collecting data, organizing data, downloading data, creating folders.”
DIVD, the nonprofit security research group where Van der Stap previously served as a volunteer, disclosed on LinkedIn last week that the organization was dealing with an internal cybersecurity incident that appears to have involved the malicious use of artificial intelligence. DIVD has released few details about that incident, but a spokesperson for the nonprofit told KrebsOnSecurity it does not appear related to ShinyHunters, nor are there any signs the matter involves the work of a previous volunteer.
Update: 3:44 p.m. ET: Corrected Van der Stap’s age, which is 24 (not 23).
Update, 4:54 p.m. ET: The Dutch police have confirmed the arrest of a 24-year-old in connection with the ShinyHunters investigation. In a statement on Twitter/X, the Dutch police said the man will appear on Tuesday, September 29 before the chambers of the Rotterdam District Court, and that it will provide more information tomorrow.
Sept. 29, 9:42 a.m. ET: The Dutch news outlet RTLreports that investigators suspect Van der Stap tried to orchestrate at least two murders. RTL reported the two murders were allegedly to be committed abroad, and that there are indications the suspect gave the order for this.
The FBI released a short video message on the ShinyHunters investigation from Brett Leatherman, assistant director of the FBI’s cyber division, who thanked Dutch law enforcement partners for their assistance and urged remaining ShinyHunters members to turn themselves in.
“Arrests have a way of changing who is willing to talk, and seized infrastructure has a way of showing us who’s left,” Leatherman said. “The longer you stay in this, the more we learn about you. You know how to find us, and we know how to find you. I suggest you reach out to us while the choice is still yours.”
“In the age of misinformation, the line between fact and fiction is blurrier than ever.”
“For those of us working in video news, verification isn’t a nice-to-have. It’s a necessity. It is how we protect the stories we help shape and how we earn and maintain trust in an increasingly chaotic information ecosystem,” Abu Dhabi-registered video news agency Viory posted on LinkedIn on April 9, 2026, offering training to help newsrooms and journalists sort fact from fiction.
The self-described “
“In the age of misinformation, the line between fact and fiction is blurrier than ever.”
“For those of us working in video news, verification isn’t a nice-to-have. It’s a necessity. It is how we protect the stories we help shape and how we earn and maintain trust in an increasingly chaotic information ecosystem,” Abu Dhabi-registered video news agency Viory posted on LinkedIn on April 9, 2026, offering training to help newsrooms and journalists sort fact from fiction.
The self-described “video news agency of the Global South” has delivered journalism training to multiple national press agencies across Africa, Asia and the Middle East.
However, when it comes to Viory itself, the line between fact and fiction is very blurry indeed.
Bellingcat has found multiple links between the digital infrastructure of Viory and Ruptly news agency, a branch of sanctioned Russian propaganda outlet Russia Today, including shared IP addresses, a Viory-linked site using a digital security certificate registered to Ruptly, and Ruptly sending site performance data to Viory. While there have been previousreports on suspected links between the two outlets, our investigation adds new evidence about Viory’s ties to Ruptly media.
When contacted for comment, both Viory and Ruptly denied any connection with each other.
Composite Image created by Bellingcat.
‘Video News Agency of the Global South’
Viory’s main offering is raw video footage of news events provided via subscription. According to Viory, its clients include “major international news outlets, local media organisations, and independent creatives in more than 170 countries”.
If its own figures are to be believed, Viory was strikingly well established at its launch in November 2023, by which time it claimed to have a “pre-assembled team of over 150 full-time staff, and an established network of over 3,000 video journalists across the world”.
The name “Viory” is a trade name. The company’s legal name is Darpo Vision FZ LLC, according to its website, which also states that it is registered in Abu Dhabi. In August 2024, Darpo Vision FZ LLC filed for a trademark in the US for the name Viory, which was approved in December of 2025.
As of May 2026, Bellingcat found press releases and news reports referencing at least 30 agreements between Viory and partners in more than 22 countries, as well as cooperation agreements with government agencies, training agreements with universities and regional journalism bodies.
Ruptly is a video news agency formerly based in Berlin and ultimately controlled by Russia Today (RT), which is owned by Russian state media company ANO TV-Novosti. ANO TV-Novosti has been on the EU sanctions list since December 2022 for spreading “pro-Kremlin propaganda and disinformation” and supporting Russia’s war against Ukraine.
RT launched Ruptly, which operated in Berlin via a German-registered subsidiary in 2013, with the goal of “becom[ing] the go-to alternative resource in a highly concentrated market of professional news video footage, and to deliver coverage of stories that other agencies miss.”
Sanctions imposed on RT following Russia’s 2022 invasion of Ukraine choked off Ruptly’s source of funds in Germany, leading the German company to begin insolvency proceedings in October 2024. Ruptly continues to operate from Moscow as of 2026.
As with Viory, Ruptly’s main offering is providing raw news footage to subscribers around the world. It relies on a large network of international freelancers and stringers. In 2016 RT claimed that Ruptly had “surpassed” newswire services AFP and Reuters on YouTube, and was serving more than 600 media organisations in 45 countries.
Felix Huesmann of the German outlet RedaktionsNetzwerk Deutschland (RND),was the first to outline links between Ruptly and Viory while covering the insolvency proceedings of Ruptly. He found that Darpo Vision’s original details on the Abu Dhabi Creative Media Authority’s site included an email address d.toktosunova@gmail.com. It has not been confirmed who this email address belongs to; however, the username matches the first name initial and surname of Dinara Toktosunova, the managing director of Ruptly. When asked about this email address by Huesmann in 2024, Ruptly “explained that Toktosunova is focused on securing the future of the Ruptly team [in Moscow] and is not working anywhere else as a managing director.”The activist group, OSINT For Ukraine, also outlined links between Ruptly and Viory, including the movement of multiple key staff between the two organisations and strong similarities between the two organisations’ platforms and content.
Darpo Vision’s Security Certificate
The legal entity behind Viory, Darpo Vision, was set up in one of Abu Dhabi’s free zones – special economic areas that have business-friendly incentives such as tax exemptions and that allow 100 percent foreign ownership. The free zones also offer what some describe as high levels of “corporate privacy,” which others assert has created a haven for shell companies and opaque corporate structures.
Darpo Vision initially had its own web domain, darpo.vision. The site has since been removed. Whois records show that the domain was registered by Darpo Vision FZ LLC in December 2022 to a PO Box in Abu Dhabi, using a Russian domain name registrar and a Moscow phone number.
Initially, Darpo.vision had its own Secure Sockets Layer (SSL) certificate – a digital certificate that authenticates a website’s identity, allowing it to secure and encrypt data. However, VirusTotal data shows that as of at least June 2024, darpo.vision was using a wildcard SSL certificate registered to ruptly.video. A Wildcard SSL certificate is a single certificate with a wildcard character (*) in the domain name field. This allows the certificate to secure a single domain and multiple subdomains. You can see historical SSL certificates for darpo.vision.
James Wilson, a software and networking engineer with 20 years of experience and currently Enterprise Technology editor at Risky Business Media, told Bellingcat that to prevent unauthorised use or forgery of SSL certificates, a private key is needed to create and use a wildcard certificate across multiple domains.
“The fact that darpo.vision was using a wildcard SSL certificate for ruptly.video indicates that whoever was running darpo.vision also had access to the private key for ruptly.video’s SSL certificate. Normally, only the people operating Ruptly’s web hosting infrastructure would be likely to have access to that,” Wilson explained.
When asked by Bellingcat about whether there were alternative possible explanations, Wilson suggested that it was theoretically possible that someone may have hacked Ruptly and stolen their private SSL key.
“However, using that wildcard SSL certificate on a domain that didn’t match the wildcard in the certificate defies explanation as the browser would alert the user to the certificate error,” he added.
Shared IP Addresses
Bellingcat also identified multiple shared IP addresses which appeared to be concurrently in use by both Ruptly and Viory between May 2025 and May 2026.
From 2025 onwards, the Russian IP address 158.160.132.25 has been used concurrently by viory.video, ruptly.video, ruptly.agency and ruptly.tv, according to VirusTotal. Similarly, since the beginning of 2026, IP address 84.252.135.88 has been used concurrently by viory.video, viory.team, ruptly.video, ruptly.agency and ruptly.tv, according to VirusTotal.
VirusTotal data shows that from 2025 onwards, IP address 158.160.166.22 has been used by ruptly.video and viory.video while from 2026 onwards, IP address 158.160.226.68 has been used by viory.video and ruptly.tv. The VirusTotal data appearsto show these IP addresses being used exclusively by Ruptly and Viory as of 2025 and 2026. However, VirusTotal does not necessarily capture all domains which resolve to an IP, and other domains may also have resolved to these IP addresses, which were not observed by VirusTotal’s passive DNS replication service. It is also important to note that in some cases, unrelated domains use the same IP addresses.
Ruptly Sends Site Performance Data to Viory
Viory’s and Ruptly’s site infrastructure was also linked through data sent via Sentry, an internal error tracking and performance monitoring platform.
An API scan of Ruptly’s main client login page, ruptly.agency, on March 26, 2026, shows that the page was sending data to a subdomain of viory.team. This domain appears to be used by Viory primarily for backend purposes, based on subdomains which appear to refer to common developer and site management tools such as Traefik and ArgoCD, in addition to Sentry.io. Notably, two subdomains also appear to refer to Ruptly.
The purpose of one domain sending data to another domain’s Sentry project is generally to consolidate all of the relevant performance and error data in one place for in-house developers to monitor.
The ruptly.agency page’s request to viory.team also includes an authentication key for Viory’s Sentry project. Ruptly.agency is not the only Ruptly domain sending Sentry data to viory.team. As of May 9, 2026 the login page for ruptly.video’s own Sentry project, sentry.ops.ruptly.video, automatically redirects to sentry.ops.ruptly.video/auth/login/viory/. Ruptly Video’s Sentry login page also features “Viory” as the title.
The ruptly.video Sentry login page is also sending data to the viory.team Sentry project, the ruptly.agency homepage and using a favicon hosted on viory.team.
A third Ruptly domain, ruptly.tv, also sends performance data to viory.team’s Sentry project via cms.dev.ruptly.tv.
James Wilson noted that in each case, the Ruptly domains sending data to Viory appeared to be using a different Sentry key.
“If you look at each of these snippets sending telemetry data [from the Ruptly domains], the specific Sentry keys for sentry.ops.viory.team are different for each. I presume that someone with access to Viory’s Sentry keys has generated and included fresh Sentry keys in each of these instances in order to differentiate between the telemetry from this site versus others using the same Sentry instance,” Wilson said.
“This cuts against the idea that this is, for example, a case of someone just lazily copy-pasting code on Ruptly’s domains. It suggests that each of these snippets was likely to have been deliberately included. The alternative explanation of changing these API keys to some arbitrary value seems much less plausible given the lack of diligence in ensuring other aspects of the content didn’t cross-reference the domains.”
‘Ruptly’ Page Title on Viory Test Page
Finally, Bellingcat found a page at frontend.dev.viory.video/en that appears likely to be a developer test page for the front page of Viory’s main domain viory.video.
Notably, however, the page title reads “Stream trending news | Ruptly.” The page description included in the source code also refers to Ruptly:
“Follow breaking world news in real-time and stream the latest developments in politics, sports, finance, science, tech, and more from one of the top online news sites. Download and share international news today with award-winning news agency Ruptl” [sic].
Screenshot of frontend.dev.viory.video/en page, captured May 10th 2026. Archived source.
Wilson said that the use of the Ruply page title and text on the Viory test page “looks like a case of lazy copy and pasting”.
“That could potentially be done by someone outside of Ruptly, although it would be strange.”
While this particular piece lies on the lower end of the spectrum of proof, Wilson said that together with the other stronger pieces of evidence, including multiple Ruptly domains appearing to send data to Viory using different API keys, and Ruptly’s wildcard SSL certificate on Darpo Vision’s site, the weight of evidence for a connection between Ruptly and Viory adds up.
“None of the pieces of evidence are watertight on their own, but when you add them together it’s difficult to think of other plausible explanations for all of them being true at the same time,” he added.
“None of the pieces of evidence are watertight on their own, but when you add them together it’s difficult to think of other plausible explanations for all of them being true at the same time,”
-James Wilson
Bellingcat also found that Ruptly appears to have connections to a company in Hong Kong. Company records from July 2022 indicate that this company was originally named Ruptly Limited, but in September of that year, the company’s name was changed to Lotus Production Limited.
The Hong Kong company remains registered as active and filed annual reports in September 2025.
Russian Slant in the ‘Global South’
Anna Hiller, a Bangkok-based Consultant Research Analyst for the Institute for Strategic Dialogue told Bellingcat that the resources provided by Viory can be an attractive pool of source material for smaller media outlets, governments and academic institutions with small budgets.
She told Bellingcat that Viory’s editorial choices are clear when looking at the site’s videos.
“When accessing Viory, the prominence of pro-Russian and pro-China content is immediately noticeable, including numerous articles focused on Vladimir Putin, Russia-China cooperation, and broader China-related narratives.”
Bellingcat contacted Viory, Darpo Vision and Lotus Production Limited to ask about the connections we found between the Viory website and Ruptly and between Lotus Production Limited and Ruptly.
Viory said that it had no connection with Ruptly. “Viory has no connection with Ruptly; any suggestion otherwise based on ordinary use of similar digital platforms, tools or cloud providers is poorly founded and inaccurate; Viory is a UAE-based, privately held, self-funded and 100% privately owned organisation, and receives no funding, direction or instructions from any state media,” the company said in an email response.
Ruptly also said it was not connected to Viory. It declined to respond to Bellingcat’s questions, including about specific findings such as Ruptly’s domains sending technical performance and error data to Viory, calling these questions “irrelevant”.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
The challenges of conducting open-source research in China are well-documented. Consistently named one of the most digitally oppressive countries in the world, China blocks some of the world’s largest social media platforms, such as Facebook, Google, and YouTube. Those that are still accessible are mostly Chinese-owned, strictly regulated and monitored in real time by AI systems as well as tens of thousands of “internet police”.
But despite these strict controls, Chinese apps – which boast m
But despite these strict controls, Chinese apps – which boast more than a billion estimated users – remain an information goldmine for investigative journalists covering stories both within and outside China.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
Since most foreign sites are banned, Chinese platforms are the largest resource available to journalists and researchers interested in what’s going on in the world’s second-most populous country. Even when a topic is being censored, patterns in the censorship can themselves serve as investigative leads: a 2020 BuzzFeed News investigation, for example, mapped out detention camps in Xinjiang by examining areas that had been blanked out on China’s Baidu Maps.
With millions of Chinese people living overseas, social media activity by members of the diaspora can also turn into global stories.
Serial rapist Zou Zhenhao, a Chinese PhD student, was jailed in London last year after one of his victims posted a warning on Xiaohongshu, also known as Little Red Book or Rednote, an app popular with young Chinese women living abroad. Another woman Zou had raped reached out to the original poster, who put her in touch with the police – leading to the conviction of a man described by police as possibly one of the worst sexual predators in British history.
Founded in 2013 as a Hong Kong shopping guide, Xiaohongshu has evolved into a lifestyle and e-commerce platform that has been compared with Instagram, Pinterest and Amazon. Last year, it reported about 300 million monthly active users, rivalling some of China’s largest social media platforms.
Xiaohongshu saw a surge in international users in January 2025 amid a threatened ban on short video app TikTok. Photo: VCG via Reuters Connect
The app’s 600 million daily searches by the end of 2024 also accounted for half of market leader Baidu’s search volume, demonstrating that it is emerging as a critical search and discovery engine, not just a social platform.
Although primarily a Chinese-language app, Xiaohongshu gained attention in the English-speaking world last year, when millions of American TikTok users flocked to the platform in anticipation of a TikTok ban under US President Donald Trump.
Responding to the surge of international users – sparked by the #TikTokRefugees trend – Xiaohongshu rolled out an AI-powered translation feature, making the app more accessible to non-Chinese audiences. This also meant that journalists without Chinese language skills can more easily communicate on and navigate the platform.
Despite its growing popularity both within and outside China, the app is relatively new and underexplored compared to more well-established platforms such as Weibo.
This guide aims to provide a starting point for those looking to explore Xiaohongshu for open-source investigations, including an overview of its main user demographics, potential topics to explore and strategic search methods specific to the app.
User Demographics and Topics
According to Xiaohongshu’s official data, the platform’s demographic profile is mainly young, female and urban. As of 2024, 70 percent of its users were women, with half of all users belonging to Gen Z and living in China’s largest cities.
As previously mentioned, the app has also gained popularity with the Chinese diaspora. Many Chinese nationals living abroad use it as a search engine for local information, posting and searching for content related to their daily lives, from restaurant recommendations and apartment hunting to navigating foreign bureaucracies and finding community resources.
This demographic profile makes Xiaohongshu particularly well-suited for investigating stories about consumer fraud and urban livability issues. For example, Chinese outlets like Jiemian have used Xiaohongshu posts to expose the grey-market ecosystem of paid reviews and fake endorsements tied to the platform’s e-commerce model, while in 2022, International Financial News traced a mother-and-baby store scam that defrauded over 400 parents back to product recommendation posts on the platform.
Given its predominantly female user base, Xiaohongshu has also evolved into one of China’s most important spaces for feminist discourse and women’s issues. Academic researchers have used content on the platform to analyse local discussions on menstrual shaming, sexual harassment, and the controversial “divorce cooling-off period” introduced in 2021. As Rest of World reported, women have increasingly congregated on Xiaohongshu, where they outnumber male users and have found ways to trick the app’s recommendation algorithm so their posts are shown mostly to other women.
The Relevance of Censorship
Political content and current affairs about China are largely absent from the app – a result of both active censorship and platform design.
All Chinese social media platforms, including Xiaohongshu, operate under strict content moderation requirements from the Cyberspace Administration of China. A leaked 143-page internal document published by China Digital Times in 2022 revealed how Xiaohongshu censors respond to government directives in “real-time”, blocking content related to politically sensitive topics such as criticism of the Chinese Communist Party, labour strikes and student suicides. Xiaohongshu’s commercial focus also makes it less likely that these topics would be discussed on the platform: as Rest of World reported, the platform functions less like Weibo – a public square for current events – and more like “a giant mall, where shoppers tell each other what to buy”.
Coverage of international affairs is also tightly controlled: only state-owned or state-controlled news organisations can obtain licences to publish original news content. However, content about life abroad, particularly stories about the cost of living, healthcare, or social problems in Western countries, circulates more freely on platforms including Xiaohongshu, and provide journalists with insight into how Chinese diaspora communities engage with local political systems.
For example, when the 2025 Miss Finland was accused of making anti-Asian gestures, searching for “芬兰小姐” (Miss Finland) and “投诉” (complaint) on Xiaohongshu revealed a trove of collective action: users shared different complaint pathways, posted templates for filing reports, and documented various outcomes from their complaints.
For such large-scale public events, Xiaohongshu can be both an organising platform and a rich source for tracking how diaspora communities coordinate responses to discrimination, providing journalists with insight into grassroots activism and transnational advocacy networks.
Getting Started
Xiaohongshu is available for download on both Apple’s App Store and Google Play worldwide, or can be accessed via a web browser. In international app stores, the app appears under the name “RedNote,” but this is the same application as Xiaohongshu – content and accounts are shared across both. The key difference is that RedNote users who register with overseas phone numbers are automatically tagged as international users, which affects the content the algorithm surfaces to them.
For users who download the app outside mainland China, Xiaohongshu automatically detects the device language and location. Upon first login, international users are prompted with an option to automatically translate all content into English (or their device language). If enabled, posts and comments will display with translations by default, and the algorithm will prioritise English-language content and posts created by or for international users, such as expat influencers.
For researchers and journalists seeking to observe the platform as Chinese users experience it, consider disabling automatic translation. This allows you to see content as it natively appears and helps you distinguish between posts created for international audiences versus those created for domestic users – a distinction that matters when assessing how representative your sample is for the relevant topic.
The default home feed, or the “Explore” tab, is where the algorithm surfaces content based on your engagement history, location and user profile. The feed uses a grid layout displaying post thumbnails with titles and like counts.
On the top right corner of the screen, the search bar also allows keyword searches across posts, users and topics. Results can be filtered by content type (e.g. notes, videos, users or products) and sorted by relevance or recency.
The search bar on the top right and the Explore page are some of the most relevant features for journalists and researchers on Xiaohongshu. Source: Xiaohongshu
Using the Search Bar
Xiaohongshu’s search function is relatively basic. You can search by keywords and filter by time and location, but the options are general: time filters include “past day,” “past week,” or “past six months,” while location filters offer “same city” or “nearby”.
For example, searching “Canada” returns posts tagged with that keyword, which you can then sort by recency or proximity.
Search results for “Canada” in English (left) show mainly travel and tourism-related content, while a search in Chinese (right) shows more content posted in Chinese by Chinese people about living in Canada. Source: Xiaohongshu
For breaking news events, try searching location names or names of individuals involved in the incident, filtering for the most recent posts to capture real-time reactions and on-the-ground accounts before they’re censored or deleted.
Xiaohongshu primarily uses algorithms to curate and push content through personalised feeds. For journalists using Xiaohongshu for investigative purposes, it can be useful to actively search for topics of interest to train your algorithm – the more you search and engage with specific content, the more relevant posts the algorithm will surface to you.
However, if you are researching the platform itself – studying what content Xiaohongshu promotes, how censorship operates, or what narratives dominate – you may want to start from a clean slate. In that case, consider periodically turning off personalised recommendations (Settings → Privacy Settings → Personalisation Options), clearing your browsing history, clearing cached data, or using a fresh account to observe what the platform shows to a “neutral” user.
Language and Lingo
During the influx of “TikTok refugees” in January 2025, Xiaohongshu launched a translation feature for users outside mainland China, enabling the automatic translation of comments and posts.
However, this does not translate search queries. The platform’s search engine is still optimised for Chinese, though there is a “prioritise English” filter for overseas users, and searching in English will return some results.
Searching for “Canada” in English, with “EN preferred” selected, will mainly return posts in English. Source: Xiaohongshu
But the language you search in shapes far more than just your results – it determines which version of the platform you see. When you search in English or use an international account, the algorithm treats you as a foreign user and surfaces content accordingly: influencers explaining why they love living in China, comparisons showing Chinese life favourably against the West.
This isn’t a neutral cross-section of the platform – it is a curated bubble. To access what Chinese users actually discuss among themselves, it would be more effective to search in simplified Chinese and, ideally, use a China-registered account if you have access to one. If you don’t read Chinese, you can also consider using a translation tool (Google Translate, DeepL, or an AI assistant) to convert your search terms into simplified Chinese before entering them.
Despite such tools and the in-app translation feature, it is always useful when researching using Chinese platforms to work with a native speaker familiar with the local context. They can flag when an innocuous-seeming term actually carries hidden meaning, and help identify coded conversations about a censored topic.
On Xiaohongshu specifically, this coded language extends beyond political topics to include anything the platform’s algorithm might flag as “vulgar” or promotional. For example, users substitute fruits and neutral terms for body parts or sexual content to avoid being flagged as inappropriate – the peach emoji for buttocks, or 炒菜 (“cooking”) for explicit material. They may also use abbreviations and emojis for commercial terms to evade anti-marketing filters, such as “vx” (the abbreviation of how WeChat is pronounced in Chinese) or “绿” (“plus green”, apparently referring to WeChat’s green logo) for WeChat, or “米” (rice) or the moneybag emoji for money.
Advanced Search Strategies
For more sophisticated searching, consider using third-party marketing analytics tools like Xinhong and Qiangu, which can show trending topics, popular posts and engagement metrics, as well as identify key content creators posting about specific subjects.
For example, on Xinhong, when you search for “Canada” in Chinese, it also shows show trending related searches such as “加拿大总理” (Canadian Prime Minister). Clicking through these suggestions leads to recent posts—for example, posts about Mark Carney’s latest statements at Davos, along with user comments and reactions.
A search on the Xinhong platform for “Canada” in Chinese also suggests related trending topics (in green box) such as “in Canada”, “living in Canada” and “Canadian Prime Minister”. Source: Xinhong, annotation by Bellingcat
While these tools are designed for marketers, they provide journalists with valuable capabilities: tracking how topics evolve, identifying influential voices in specific communities, and discovering related hashtags or discussions that might not surface through basic platform search. These tools often require paid subscriptions but can significantly enhance research efficiency for long-term investigations.
Another valuable feature is Xiaohongshu’s group chat function, where users gather around shared keywords and topics—from city-specific communities to niche interests. These groups are often highly active and provide access to candid community discussions that don’t appear in public posts. To find relevant groups, go to Messages → Group Square, where you can browse categories or search by keyword and request to join.
Monitoring active group chats related to relevant topics, whether that’s a specific city, industry, or issue, can help journalists and researchers stay updated on emerging issues and detect potential story leads before they become widely visible on public feeds.
Preserving the Evidence
Chinese social media content can disappear quickly and without warning due to censorship, making immediate preservation critical.
Always take two preservation steps immediately upon discovering relevant content:
First, screenshot the entire post, including the URL, timestamp, username, like/comment counts, and location tags. These metrics establish context and authenticity. Use tools that capture full-page screenshots rather than just visible portions, as posts can be long and comments extensive. Second, archive the web page using services like archive.today or Wayback Machine. Note that these services capture only static content – comments and engagement metrics may not be fully preserved and should be screenshotted separately.
For Xiaohongshu specifically, always preserve the user’s unique ID found in their profile URL when viewed on a browser, which follows the format “user/profile/[unique ID]”. Users can change their display names, but this unique identifier remains constant, allowing you to track accounts over time even after name changes. This is critical for long-term investigations or when monitoring specific sources.
The unique ID of a user can be found in the profile URL on a browser. Source: Xiaohongshu
Xiaohongshu operates under the same legal and censorship constraints as all Chinese social media platforms, and researchers should approach it with appropriate caution. Content moderation is extensive: users who post about sensitive subjects risk having their content removed or their accounts suspended, and the platform is required to comply with government data requests. For researchers, this means the information you find represents only what has survived the censorship process.
That said, Xiaohongshu remains a remarkably rich resource for open-source research. Its strength lies precisely in its apolitical, lifestyle-oriented identity: while political discussion is suppressed, candid conversations about everyday life flourish. For journalists willing to invest in learning the platform’s rhythms, building Chinese-language search skills, and understanding its coded vocabularies, Xiaohongshu offers a window into how ordinary Chinese people talk among themselves – an area that remains largely untapped by international media.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
This article is the result of a collaboration with Indian media outlet Newslaundry. You can find Newslaundry’s editorially independent coverage here.
Collage illustration by Klawe Rzeczy. Elements from Unsplash.
Indian companies have shipped more than 320 million synthetic opioid pills to West Africa – where they have not been approved by regulators – over the past three years, a Bellingcat investigation has found.
Export records from trade data provider 52wmb show that more than 1,400
This article is the result of a collaboration with Indian media outlet Newslaundry. You can find Newslaundry’s editorially independent coverage here.
Collage illustration by Klawe Rzeczy. Elements from Unsplash.
Indian companies have shipped more than 320 million synthetic opioid pills to West Africa – where they have not been approved by regulators – over the past three years, a Bellingcat investigation has found.
Export records from trade data provider 52wmb show that more than 1,400 consignments of tapentadol worth almost USD $130 million were sent from India to West Africa between January 2023 and December 2025.
Tapentadol, a painkiller two to three times more potent than tramadol, has not been approved for use in most West African countries, where some nations are grappling with an escalating opioid abuse epidemic.
However, this investigation shows that dozens of Indian suppliers have flooded the region with tapentadol over the past three years. Where dosages were listed, more than half the pills were in powerful strengths of 200mg or more – dosages that are not even approved in India.
The exports, cross-checked against records provided by trade data aggregator ImportGenius, show most tapentadol pills sent between 2023 and 2025 had the coastal nations of Sierra Leone and Ghana listed as their declared destinations.
The two West African countries were collectively marked as the destination for more than 80 per cent of the total value of tapentadol sent to the region.
Experts have documented how drug traffickers adapt quickly to international regulations and law enforcement efforts. In 2018, India tightened export controls around the opioid tramadol, one of the most trafficked synthetic drugs to West Africa.
In 2021, the International Narcotics Control Board (INCB) said large-scale tapentadol trafficking had been identified, particularly in consignments destined for Africa. It had previously noted that India’s strengthened tramadol controls could lead traffickers to substitute the drug with other potent synthetic opioids.
A BBC investigation last year revealed that Indian company Aveo Pharmaceuticals was illegally exporting tablets containing a mix of tapentadol and the muscle relaxant carisoprodol to West Africa. This led India’s drug regulator, the Central Drugs Standard Control Organisation (CDSCO), to ban the manufacture and export of all combinations of the two drugs.
Bellingcat’s investigation, in collaboration with Indian publishing partner Newslaundry, reveals that the supply of tapentadol pills from India to West Africa has surged in recent years.
Export data from 52wmb shows the value of tapentadol sent to the region has risen from about USD $27 million in the three year period from 2020 to 2022, to almost USD $130 million from 2023 to 2025.
Julius Maada Bio, Sierra Leone’s president, in 2024 declared a national emergency over rampant drug abuse and branded kush – a toxic blend of psychoactive substances including cannabis and synthetic opioids – a “death trap”.
Authorities in Sierra Leone have intercepted illegal tapentadol, including last July when the National Revenue Authority (NRA) said it thwarted a smuggling operation near its north-west border with Guinea.
The NRA and other agencies including the Transnational Organised Crime Unit, National Drug Law Enforcement Agency, and the Pharmacy Board of Sierra Leone did not respond to Bellingcat’s requests for comment.
Sierra Leone’s NRA said customs officers seized tapentadol near a border crossing in July. Source: National Revenue Authority
Ghana’s Narcotics Control Commission (NACOC) said the illegal importation of tapentadol was first recorded in 2022 after international efforts to curb the tramadol crisis resulted in criminal networks shifting production to other pharmaceutical opioids including tapentadol, tafrodol and carisoprodol.
The agency has recorded a “steady rise” in tapentadol trafficking over the past three years, with authorities seizing more than 3.7 million tablets (250mg strength). Most were traced back to India, it said.
“NACOC investigations confirm that the bulk of tapentadol is trafficked into Ghana through seaports and by air, via express courier services,” a spokesperson said. “At the ports, the drug is concealed in containerized cargo falsely declared as pharmaceuticals, electrical materials or household goods. Express courier services are used for smaller, high-value quantities, often packed alongside legitimate consignments to avoid detection.”
NACOC said Ghana had emerged as both a destination and transit hub for tapentadol, with the majority of intercepted consignments bound for Niger, Mali, Burkina Faso and Nigeria. When sold domestically, it said the street drug was promoted as a tramadol substitute.
Ghana’s Food and Drugs Authority (FDA) said last year that the abuse of pharmaceutical opioids such as tapentadol — commonly known on the street as “Red” — was on the rise.
The FDA told Bellingcat it had “never issued any permit” for the manufacture or importation of tapentadol, in any strength, to any importer or to any country. It said any tapentadol shipments to Ghana were for “trans-shipment to neighbouring country”.
Import data for Ghana shows that no tapentadol entered the country between 2023 and 2025, which supports NACOC’s position that the drugs are being concealed and falsely declared. Import data for Sierra Leone was not available through 52wmb.
Ghana’s FDA destroyed 230 cartons of the illegally imported tapentadol last April and seized 7,700 tapentadol tablets at a border crossing last August. NACOC said it was combatting opioid importation through regulation, enforcement and cooperation with its counterparts in other countries. Source: FDA
India’s drug and pharmaceutical exports have grown to more than $30 billion a year, according to the Pharmaceuticals Export Promotion Council of India (Pharmexcil), a division of the ministry of commerce and industry.
While tapentadol is available in India on prescription in strengths of up to 100mg (immediate release) and 200mg (extended release), authorities are aware of its risk of misuse. Last year, the Indian drug regulator’s Technical Advisory Board said the Department of Revenue may be requested to schedule the painkiller under the Narcotic Drugs and Psychotropic Substances Act, which would tighten rules around its export.
To export pharmaceutical products at strengths that are not approved in India, exporters are required to obtain an export “no objection certificate” (NOC) from the CDSCO, for which they have to submit proof of the drug’s approval in the importing country. Publicly available information shows tapentadol is not approved for use in any of the West African nations identified as part of this investigation.
The CDSCO did not respond to questions from Bellingcat or our publishing partner, Newslaundry.
In response to “Right to Information” requests submitted by Newslaundry, the CDSCO said only two companies had been granted authorisation to manufacture tapentadol for export between 2019 and 2024. However, the trade data analysed by Bellingcat did not list either company as an exporter of tapentadol to West Africa.
The CDSCO also said it had issued export NOCs for tapentadol to 51 companies since 2024, but that these were not for export to West African countries.
Meanwhile, Bellingcat’s analysis of trade data shows that more than 60 Indian suppliers have exported tapentadol to West Africa since 2023. The exporters are mostly pharmaceutical companies but also include smaller operations, such as one company owned by a Nigerian man who sent more than US $4 million of tapentadol to Niger and Ghana.
In the BBC’s investigation, journalist Surabhi Tandon reported on the increase in cross-border smuggling of tramadol, “a catch-all name to describe the range of opioids used as street drugs”, from Ghana to Nigeria. Source: BBC News
Dinesh Thakur, co-author of the book Truth Pill, told Newslaundry there were gaps in India’s drug regulatory framework that made it possible for potentially unsafe medicines to be manufactured and exported without proper oversight.
“There is no regulatory framework which checks a genuine importer and counterfeit importer between countries,” said Thakur, a former pharmaceutical executive who now works as a public health activist.
Mohammed Adinoyi Usman, a consultant anaesthetist at Rasheed Shekoni Federal University Teaching Hospital in Nigeria, said tackling Africa’s opioid crisis was complicated by a lack of resources across the region, weak government responses, and inaction by law enforcement agencies.
He said more collaboration and intelligence sharing was needed, especially across West African countries, to combat the problem. “We see so many opioids coming into our region because of a range of factors including under-funded institutions like customs and drug agencies, weak border controls and corruption,” he said.
“Africa is different. Even southern Africa is different from western Africa – each region has its peculiarities. In Nigeria, we don’t have well-functioning institutions to help control it. But our government is trying.”
Dr Usman said access to prescription opioids in Africa was inadequate, and pointed to research showing the disparity in distribution of legal opioids to low-income countries compared to high-income nations that consume the bulk of the world’s pain relief medication. He said opioid abuse was linked to crime and negative health outcomes.
“Sadly, access to prescription opioids is very limited in Africa,” Dr Usman said, “but the costs of illegal use are high.”
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
The video posted by a state branch of India’s ruling Bharatiya Janata Party (BJP) showed Assam chief minister Himanta Biswa Sarma shooting an image of two men in Muslim skull caps. “Foreigner-free Assam”, read one caption across the video. “Why did you not go to Pakistan?” said another.
Screenshots of the now-deleted video shared by BJP on Feb. 7 showing Assam Chief Minister Himanta Biswa Sarma shooting an AI-generated version of INC leader Gaurav Gogoi (in a white skull cap) and another uni
The video posted by a state branch of India’s ruling Bharatiya Janata Party (BJP) showed Assam chief minister Himanta Biswa Sarma shooting an image of two men in Muslim skull caps. “Foreigner-free Assam”, read one caption across the video. “Why did you not go to Pakistan?” said another.
Screenshots of the now-deleted video shared by BJP on Feb. 7 showing Assam Chief Minister Himanta Biswa Sarma shooting an AI-generated version of INC leader Gaurav Gogoi (in a white skull cap) and another unidentified, bearded man. Source: BJP4Assam/X
One of the men in the photo that Sarma was portrayed as shooting was Gaurav Gogoi, a leader of the Indian National Congress (INC), the BJP’s main competitor in Assam for the state’s upcoming legislative elections next month.
Gogoi has stated that he is Hindu but enjoys visiting different religious sites and observing their norms. He has been photographed wearing traditional Muslim attire during religious occasions such as Eid.
But the image of him in the video shared by BJP Assam, wearing a casual singlet with a skull cap, was not one of those occasions.
Bellingcat has seen several dozen videos posted by the BJP that use generative artificial intelligence (AI) alongside anti-Muslim and anti-Bangladeshi messaging in the border states of Assam and West Bengal in December last year, ahead of legislative elections scheduled in both states for April.
Left: Original photo shared by Gogoi on Jun. 17, 2025. Right: An image shared by BJP Assam that was edited with AI to show Gogoi with a skull cap, beard and Quran. Source: gauravgogoiasm/Facebook, BJP4Bengal/Facebook
Bellingcat analysed 499 social media posts containing photos and videos shared on Facebook, Instagram and X by the BJP’s official accounts in the two states for this time period, finding 194 posts that appeared to meet the United Nations’ definition of hate speech: discriminating against persons or communities based on inherent characteristics such as religion and national origin. Of these, 31 (about one in six of the hateful posts) contained the obvious use of AI-generated imagery.
Chart: Galen Reich
These appear to be part of a larger pattern of politicians and parties globally using generative AI to amplify hateful or divisive content, particularly ahead of major political events such as elections.
Ahead of the New York City mayoral race last year, Andrew Cuomo’s official X account shared, then deleted, an AI-generated video depicting Mamdani eating rice with his hands and a Black man in a keffiyeh shoplifting. In Italy, several opposition parties complained to a communications watchdog after deputy prime minister Matteo Salvini’s League party published a series of AI-generated images depicting men of colour attacking women or police officers. And in the UK, videos by an AI-generated rapper funded by the far-right Advance UK party, with lyrics targeting Muslims, were viewed millions of times.
A Campaign of Hate
Both Assam and West Bengal share a border with Bangladesh. BJP, the world’s largest political party, is currently in power in Assam, where legislative elections are scheduled on Apr. 9. West Bengal, which goes to the polls on Apr. 23, is governed by the Trinamool Congress (TMC).
Map: Pooja Chaudhuri. Source: Goran tek-en, CC BY-SA 4.0, via Wikimedia Commons
US-based international affairs expert Mohammed Zeeshan told Bellingcat that the “dehumanising and debasing” terminology used in India to refer to alleged illegal Bangladeshi immigrants, including by senior ministers, has caused resentment towards India in Bangladesh.
“The situation, in fact, was so bad that Hasina herself had subtly warned the Modi government in public statements that Indian domestic rhetoric was endangering Bangladeshi Hindus, who bore the brunt of that resentment,” Zeeshan said.
Zobaida Nasreen, a professor of anthropology at Dhaka University, said that anti-Muslim rhetoric intensified by BJP leaders reinforces the belief in Bangladesh that Muslims and Bengalis are being collectively targeted in India.
“Viral videos containing this message tend to spread quickly across Bangladeshi media and social platforms especially on Facebook, enhancing perceptions of hostility and triggering anti-India sentiment or nationalist backlash,” she added.
In December, the month our dataset was collected, Dipu Das, a Hindu garment worker, was beaten to death at an anti-India protest in Bangladesh over allegations that he had made derogatory remarks about Islam.
And while the administration led by Bangladesh’s newly elected leader Tarique Rahman has sought to reset strained ties, most of the hateful social media posts we saw posted by the BJP in December attacked Bangladeshi Muslims and/or Bengali-origin Muslims in India, showing how tensions between the two countries continue to influence political messaging in India’s border states.
Bellingcat’s analysis included a total of 202 posts by BJP Assam and 297 by BJP’s West Bengal branch on their official accounts. We also looked at posts shared by BJP’s main opponent parties – 194 from INC in Assam and 357 from the TMC in West Bengal – during the same time period in December.
This included all visual social media posts (containing photos or videos) by each party in December, except those that did not appear to contain any overt political messaging, such as those simply commemorating public holidays. We only counted each photo or video once, regardless of how many platforms it was shared across.
Although all of the major parties contesting in the Assam and West Bengal state elections appeared to use AI-generated imagery in some of their posts, there appeared to be a particularly high concentration of hateful messaging in the ones posted by the BJP’s accounts.
In Assam, we identified 28 posts by BJP using apparently AI-generated imagery, of which 24 carried hateful messaging. Of the 194 INC posts we looked at from December, 41 appeared to feature AI-generated imagery, but none of these appeared to carry hateful messaging.
In West Bengal, we found 14 BJP posts that contained clear indicators of AI-generated imagery, seven of which were hateful. We also identified 15 posts by the incumbent TMC that appeared to feature AI imagery, but none of these appeared to meet the definition of hate speech.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
When contacted for comment, BJP Assam spokesperson Rupam Goswami did not directly respond to questions on the party’s general use of AI but said they did not post any AI-generated photos of Gogoi. “BJP does not stoop so low,” he told Bellingcat.
As for the “point blank” shooting video, Goswami initially said the person responsible had been punished and removed from the party. However, when asked about Sarma saying that he would re-post the video with those he was depicted shooting labelled as “Bangladeshis”, Goswami said, “[Bangladeshis] need to be completely suppressed.”
BJP West Bengal did not respond to multiple requests for comment by Bellingcat via phone and email.
It is important to note that as generative AI technology improves, it can be increasingly difficult to detect AI-generated imagery. Our manual count of AI-generated imagery only included posts that had obvious signs of generative AI such as unnaturally smooth textures and multiple people with the same faces. It is therefore possible that there were other images in our dataset where generative AI was used more subtly.
However, Joyojeet Pal, Professor of Information at the University of Michigan, told Bellingcat that the quality of these visuals, or whether they looked real, was not the priority.
“What politicians in India have understood is that the sociocultural drivers of misinformation are most important for elections, so they harp on about things to the extent that they have started to not care about form over substance. It looks bad? It doesn’t matter,” he said.
More important to voters, according to Pal, was whether they already believed in the narrative contained in the videos, which generative AI could help create more quickly: “AI is helping cement polarised opinions by giving you the kind of content you have already decided you want to engage with.”
When asked about INC’s use of AI, party spokesperson Aman Wadud said that it was obvious that some of the videos they posted were made with AI and that there was no intention to mislead.
“AI can be both destructive and creative. We are using it in a creative manner, we are not using it in a destructive manner. We don’t violate people’s dignity, we don’t falsely accuse people,” he said.
TMC did not respond to Bellingcat’s multiple requests for comment via phone and email by publication time.
Portraying Bengali Muslims as ‘Foreigners’
The largest category of hateful messaging Bellingcat observed in the BJP’s posts targeted Bangladeshi or Bengali-origin Muslims, referring to them as “infiltrators” or “foreigners”. We counted 66 such posts by the BJP’s Assam and West Bengal branches from December, of which eight appeared to contain obvious AI-generated imagery.
One video referencing this theme shows AI-generated visuals of protests against “illegal infiltration” in Assam, with the caption urging people to “wake up” or the country would “turn into Bangladesh”.
A different one uses real footage from past violence in Assam mixed in with images of Muslim men. A song playing in the background accuses them of taking over “Assamese land” and shows AI images of “Assamese” people, i.e. those not in stereotypical Muslim clothing, crying.
An AI-generated image of a crying man in non-Muslim clothing and a traditional Assamese scarf on his shoulders. Source: BJP4Assam/X
Both videos use religious markers to draw a distinction between “infiltrators” – men in skull caps or lungis associated with Bengal-origin Muslims – and “citizens” in non-Muslim attire.
Clothing is often used by the Hindu far-right as a visual shorthand for identity and a deepening religious divide. In 2019, Prime Minister Narendra Modi said of protests against a controversial citizenship law that those responsible for violence could be “identified by their clothes”.
In the hateful posts seen by Bellingcat, both real and AI-generated images of opposition figures – particularly Gogoi – were shown alongside messaging that suggested that they supported “foreigners” or “infiltrators”.
The Center for the Study of Organized Hate (CSOH) also noted, in a 2025 report on AI-generated imagery and Islomophobia in India, that Hindu far-right politicians and media outlets have invoked and reinforced the trope of Muslims as “infiltrators” for years.
“AI-generated images on these themes reinforce associations between Muslim identity and illegality, reinforcing xenophobic and Islamophobic stereotypes. In doing so, they play a powerful role in justifying exclusionary policies and normalising discrimination against Muslims,” the report said.
‘Save Hindus’
Zenith Khan, a data analyst who worked on the CSOH report, noted that AI-generated propaganda was often tightly knit with current political moments, and its impact depended on “timing it right” especially when “people are emotionally charged”.
The violence against the minority Hindu community in Bangladesh has been used by the BJP to raise concerns over the safety of Hindus in India.
Days after Das’ lynching, the Assam state branch of BJP posted a video with an image of his face – except that it was manipulated with AI to show tears streaming from his eyes. “Save Hindus”, said the text accompanying the video.
Posts by BJP’s West Bengal unit also seemed to frame Muslims as criminals or threats. A video, styled after the TV show “Stranger Things”, raised alarms over an “upside down” version of the state under the current government.
A man is depicted being chased by men in skull caps. Arrows label them as “Ralib,” “Galib,” and “Chalib” – a play on Muslim names ending in “-lib” – in case the skull caps left any ambiguity about their Muslim portrayal.
“Stranger Things” themed post that depicts Hindus under threat from Muslims in West Bengal. Source: BJP4Bengal/X
INC filed a police complaint in September last year against the BJP for sharing AI videos targeting Gogoi and the Muslim community, as well as another complaint in relation to the video of Sarma portrayed as shooting two men “point blank” in February.
INC Assam spokesperson Wadud said that no action had been taken on the party’s police complaints as far as he knew.
Disinformation researcher Bharat Nayak told Bellingcat that it has always been tech platforms’ responsibility to control new types of content.
“The goal post can’t shift. This has always been a tech problem,” he said.
When this responsibility is shrugged off, Nayak added, the result is a lack of accountability. “If you’re using old videos from other countries as new, you will have people countering you. But AI-generated videos can be shared without context just to spread hate – like showing people in skull caps – and the ‘when, where, how’ questions vanish.”
Both Meta – which owns Facebook and Instagram – and X have policies against hateful conduct.
Meta also announced in 2024 that it would start adding “AI info” labels to more content detected as AI-generated, while some X users spotted a similar feature introduced on the platform last month. Only five of INC’s AI visuals that we identified – and none of those by TMC or the BJP – had a disclaimer that said “AI-generated”.
Bellingcat reached out to Meta and X for comment on whether the posts we identified breached their terms of use regarding hateful conduct or labelling AI-generated posts. A Meta spokesperson said they were reviewing the flagged content and “will take appropriate action on any violations of our policies”. As of publication, X had not responded.
Kalim Ahmed from Bellingcat’s Discord Community contributed research to this piece.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.

 Entrar