Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published. Become a member and support our work here.
Imagery captured by the European Space Agency’s freely available Sentinel-2 and Sentinel-1 satellites appears to be delayed over Gaza and parts of the West Bank, a Bellingcat analysis has found.
While the delay remains relatively short at just 24 hours, this can still impact the speed at which analysts and researchers can observe what is happening
Sign up here to receive Bellingcat’s biggest investigations by email as soon as they are published. Become a member and support our work here.
Imagery captured by the European Space Agency’s freely available Sentinel-2 and Sentinel-1 satellites appears to be delayed over Gaza and parts of the West Bank, a Bellingcat analysis has found.
While the delay remains relatively short at just 24 hours, this can still impact the speed at which analysts and researchers can observe what is happening in the region.
For example, the Israeli Defence Forces demolished homes in the West Bank Palestinian city of Hebron in recent days. New imagery captured on October 26, which included Hebron, would allow open source researchers to quickly confirm the demolitions, assess the impacted area and observe any unreported IDF activity. But imagery for the western half of Hebron was not available until October 27 due to the Sentinel-2 delay, inhibiting real-time fact-checking and reporting on this evolving situation.
A spokesperson for the European Union told Bellingcat that the delay was not related to events in Gaza but to “mitigate possible threats” due to the war in the Middle East “including Iran’s attacks on its neighbours and possible threats to European interests”. The delayed region of Sentinel tiles that cover Gaza as well as parts of Israel and the West Bank also extends over the Eastern Mediterranean Sea.
The European Union ordered a 24-hour delay on Sentinel satellite imagery over the Gulf of Oman earlier this year during US and Israeli strikes on Iran. However the delay impacting Gaza and parts of the West Bank has not been announced or previously reported.
“Such decisions are taken unanimously by all EU Member states and will stay in place as long as necessary,” the spokesperson said. They also said that while the Copernicus program, which includes the Sentinel satellites, operated a free and open data policy there were limitations to this for security.
When asked if the delay, which began in late March, was related to the presence of US vessels in the Eastern Mediterranean or if there were other areas of delay, the spokesperson said they had no further comment.
However, in July, the European Union published Council Decision 2026/1716, which ordered a 24-hour delay on Sentinel imagery over the Gulf of Oman, after a request from the US government which was involved in strikes on Iran at that time.
Just two weeks later, the European Union issued a corrigendum that unpublished decision 2026/1716 and removed it from the Council of the European Union record, although satellite data shows the delay has remained.
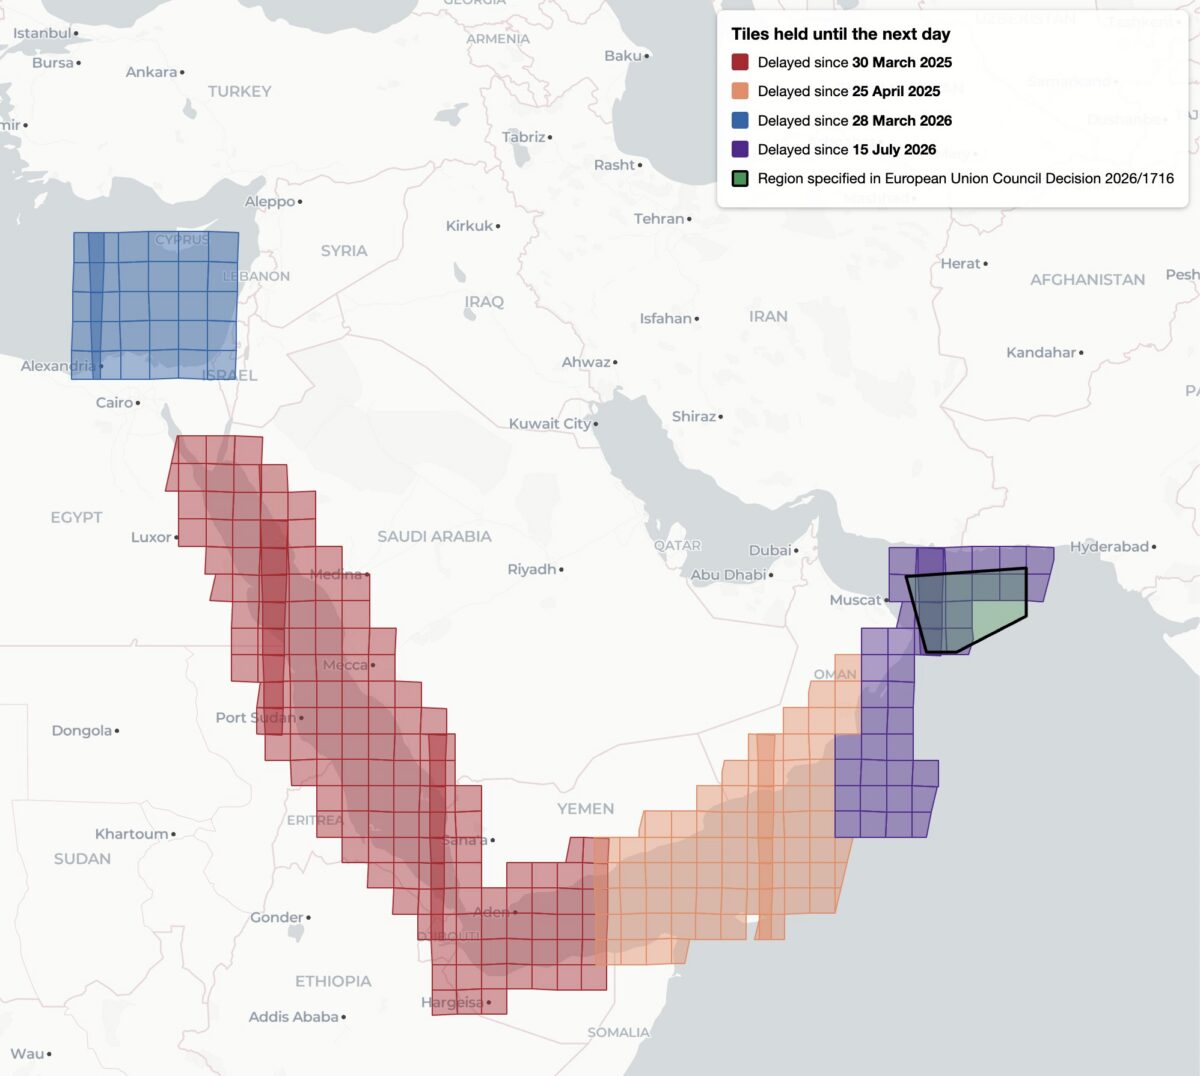
This decision, while it was available, was reportedly the first public notification of delayed Sentinel imagery. Yet it was not the first time that Sentinel imagery has been restricted, analysis shows. Bellingcat found four distinct regions of delayed satellite imagery during 2025 and 2026: the Gulf of Oman, the Gulf of Aden/western Arabian Sea, the Red Sea as well as the previously unreported delay in the Eastern Mediterranean Sea and parts of Israel, the West Bank and the entirety of Gaza.
Bellingcat’s analysis shows the regions where Sentinel-2 imagery is subject to a 24-hour delay, and when the delay was imposed. Only the July 15, 2026 delay over the Gulf of Oman was referenced by European Commission directives and the region referenced in 2026/1716 encompasses only a portion of the delayed tiles.
Bellingcat’s analysis shows that these delays have been implemented in stages. Twenty-four hour delays of Sentinel-2 imagery were first observed by open source researchers in March and April 2025 after the US launched a naval and air strike campaign against Houthi targets in Yemen.
The previously unreported imagery delay in the Eastern Mediterranean began on March 28, 2026, the same month that commercial American space imaging company Planet Labs also restricted imagery across the Middle East. The Gulf of Oman delay began on July 15, 2026, two days after the publication of Council Decision 2026/1716.
Decision 2026/1716 also specified that the delay be implemented for both Sentinel-2 and Sentinel-1 radar imagery. Bellingcat’s analysis of Sentinel-1 image availability shows that this is the case for both the Gulf of Oman region and the unreported region over the Eastern Mediterranean Sea. However, the 2025 restrictions on Sentinel-2 imagery in the Red Sea and Gulf of Aden are not implemented in Sentinel-1.
Sentinel-1 imagery uses “synthetic aperture radar” to capture lower resolution radar images that can collect data at night and on cloudy days. This differs from Sentinel-2, which captures optical satellite imagery at higher resolution.
Bellingcat’s analysis shows the regions where Sentinel-1 satellite imagery is subject to a 24-hour delay and when that delay was imposed.
A Tale of Two Tiles
Sentinel satellite imagery is most commonly accessed by open source researchers through Copernicus Browser, a free online platform, but it is also distributed as large tiled files in the Copernicus Data Space Ecosystem. These tiles are numbered using the Military Grid Reference System, and can be listed using APIs that provide information on each tile, including the capture and publication time. By comparing the capture and publication time, the publication delay can be computed.
For example, the catalog information for the tile T36RXV, which includes Gaza and portions of the West Bank, Negev and Egypt, provides the following metadata for the October 21, 2026 capture.
Metadata from tile T36RXV, which includes Gaza and portions of the West Bank, Negev and Egypt.
This shows that while the image was captured at 08:20 UTC on October 21, it was not published until 10:09 UTC on October 22 — almost 26 hours later. This is in contrast to the neighboring tile T36RYV, which includes parts of the West Bank, Israel, and Jordan. API data for this tile shows that the image was published at 12:10 UTC on October 21, just under four hours after the capture time.
Metadata from tile T36RYV, which includes parts of the West Bank, Israel, and Jordan.
This difference is not unique to this date either. Bellingcat’s analysis shows that this tile has been consistently delayed by one day since March 28, 2026.
Graphing the publication delay for two adjacent Sentinel-2 tiles shows a clear difference beginning March 28, 2026.
This method can be extended further, and by analysing every tile with valid publication date timestamps, Bellingcat identified all global Sentinel-2 and Sentinel-1 delays since 2023. The only consistent delays visible were those identified in the Gulf of Oman, the Gulf of Aden/western Arabian Sea, the Red Sea and Eastern Mediterranean in 2025 and 2026.
Impact on open source investigations
While the 24-hour delay on certain Sentinel imagery is a less severe restriction than other satellite providers have imposed, it can still impact the open source research process in fast moving situations. This is especially so in recent months as the European Space Agency’s Sentinel satellite data has emerged as a refuge as other satellite data is censored.
The image below shows how imagery for the eastern half of Hebron was visible on October 26, but not the western half where demolitions took place earlier this week.
The city of Hebron, Palestine, seen in Copernicus Browser on October 26, 2026. While imagery is available for the eastern half of the city, there is no recent imagery of the western half.
The shape of the missing tiles can be seen by zooming out within the Copernicus browser, demonstrating how imagery of Gaza and other parts of Israel and the West Bank are also delayed.
The missing tiles also include Gaza, parts of Israel, Egypt, and Cyprus, and the Eastern Mediterranean Sea.
Sentinel imagery covering western Hebron after the demolitions took place was published on October 27. However, the delay prevented local reports from being verified with satellite imagery while the situation was still ongoing.
Some Sentinel-2 users have previously described the challenges of covering fast-moving issues in the Gulf of Oman when the Sentinel delay was announced in March.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that are helping Russia circumvent existing financial restrictions.
Heleket’s support agent on Telegram claims, despite all evidence to the contrary, that it is not affiliated with Cryptomus. Image: Richard Sanders.
On October 8, the U.K. issued sanctions (
The United Kingdom has issued economic sanctions against Cryptomus, a chameleonic cryptocurrency platform that experts say serves as a major conduit for payments related to ransomware, narcotics, darknet markets, fraud and cybercrime services that are helping Russia circumvent existing financial restrictions.
Heleket’s support agent on Telegram claims, despite all evidence to the contrary, that it is not affiliated with Cryptomus. Image: Richard Sanders.
On October 8, the U.K. issued sanctions (PDF) against Cryptomus — previously known as Certa Payments and Xeltox Enterprises — for processing payments that benefit the Russian government and its financial institutions. The sanctions freeze any Cryptomus assets at U.K. banks, and bar British companies from offering it any business, virtual or otherwise. Also targeted in these sanctions were the virtual payment platforms VexPay, TokenSpot, and the Tsunami Payments service.
As explained in our December 2024 investigation, “How Cryptocurrency Turns to Cash in Russian Banks,” Cryptomus has been a key payment processor for dozens of Russian cryptocurrency exchanges and websites hawking cybercrime services. The company has changed its name several times since emerging in 2022, most recently to “Heleket” last year after Canada levied a record CAD $176 million fine against the platform for anti-money laundering violations.
The blockchain data-crunching firm Chainalysis said the U.K. sanctions target the broader infrastructure supporting Russia’s wartime economy.
“Cryptomus and Heleket have emerged as major payment hubs for illicit activity,” Chainalysis wrote in an October 8 blog post. “Together, these services received more illicit funds across tracked categories than the mixers in our dataset and the number of illicit counterparties surged to more than 900 in a single month in late 2025.”
The Cryptomus support bot on Telegram, responding on Oct. 8 to an inquiry by saying the platform was suddenly unable to process transactions.
In April 2026, the blockchain analysis firm TRM Labsfound Cryptomus had processed more than $7 billion in transactions since its inception in 2022, including transactions associated with child sexual abuse material vendors, terrorist financing networks, and human trafficking operations.
TRM noted that Cryptomus’s transaction volume cratered after the platform instituted new “know your customer” or KYC rules, and that the cryptocurrency platform responded to the Canadian fines by launching Heleket as a parallel service that continued to offer no-KYC payment processing.
Richard Sanders is a blockchain analyst and investigator who spent months mapping out Cryptomus’s payment infrastructure and transacting with its customers. Sanders said the U.K. sanctions on Cryptomus are important because Canada’s fine against the platform was ultimately unenforceable and uncollectible.
“A fine doesn’t stop a cryptocurrency payment processor from processing payments,” Sanders wrote on LinkedIn. “Sanctions kill the operation. The distinction matters.”
As our 2024 investigation noted, Cryptomus shared a Vancouver address with dozens of other foreign currency dealers and money transfer businesses — none of which appeared to be physically located there. Following the CAD $176 million fine for alleged money laundering violations, Cryptomus appealed the penalty, launched Heleket as a parallel service, and kept on processing large volumes of sketchy transactions, Sanders said.
Sanders said the sanctions also are notable because they are the first known instance of a “Five Eyes” country (referring to the Australia, Canada, New Zealand, the U.K. and the U.S.) sanctioning a cryptocurrency operation incorporated in another Five Eyes jurisdiction.
Where do entities like Cryptomus and Heleket derive their authority to offer international financial services? The answer appears to involve fake financial institutions overseen by a phony regulatory body positioned in a country that is not widely recognized as a sovereign nation.
Our 2024 investigation found the sole shareholder of Cryptomus’s parent company Certa Payments was a 25-year-old Ukrainian woman who also headed several other firms, including the WS Management and Advisory Corporation, which bills itself as the regulatory body that exclusively oversees licenses for cryptocurrency, foreign exchange and online gaming businesses incorporated in the disputed region in northwest Africa known as the Western Sahara.
That entity’s website — crasadr.com — says it assists applicants with bank setup and formation, online gaming licenses, and the creation and licensing of foreign exchange brokers. One of Certa Payments’ former sites — certa[.]website — also shared a server with 12 other domains, including rasd-state[.]ws, a website for the Central Reserve Authority of the Western Sahara.
The website crasadr dot com, the official website of the Central Reserve Authority of Western Sahara, which lists the entities awarded licenses for cryptocurrencies, gaming and foreign exchange services.
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata for more than 100 million AT&T customers in 2024 was sentenced to 70 months in federal prison today and ordered to pay nearly $300,000 in restitution to victims.
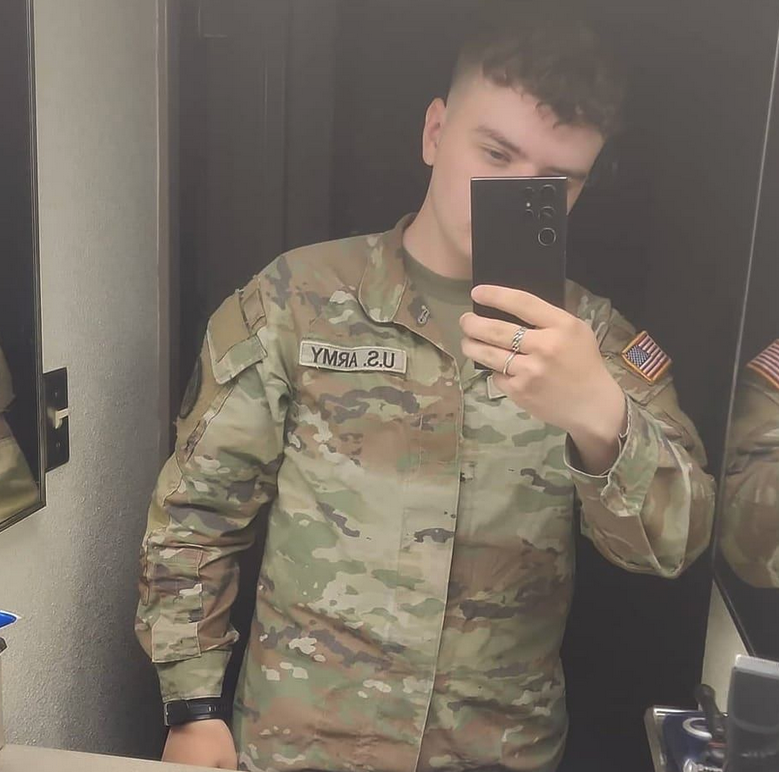
One of several selfies from the Facebook page of Cameron Wagenius.
Cameron John Wagenius, 22, was stationed at a U.S. Army base in South Korea when he adopted the cybercriminal persona “Kiberphant0m
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata for more than 100 million AT&T customers in 2024 was sentenced to 70 months in federal prison today and ordered to pay nearly $300,000 in restitution to victims.
One of several selfies from the Facebook page of Cameron Wagenius.
Cameron John Wagenius, 22, was stationed at a U.S. Army base in South Korea when he adopted the cybercriminal persona “Kiberphant0m.” Working with three alleged co-conspirators, Kiberphant0m downloaded data from several large customers of the cloud data storage service Snowflake that had exposed credentials and did not enforce multi-factor authentication (Snowflake has since mandated MFA on all accounts).
In October 2024, Kiberphant0m bragged on the cybercrime forums that he’d stolen the call and text metadata (e.g. source and destination number, timestamp, duration, etc.) for tens of millions of AT&T customers. Kiberphant0m claimed to have hacked into more than dozen telecommunications companies worldwide, including Verizon’s Push-to-Talk business, and publicly extorted these companies in exchange for a promise not to publish the stolen data.
In late November 2025, KrebsOnSecurity warned that Kiberphant0m was likely a U.S. soldier stationed in South Korea. Less than a month later, Wagenius was arrested and charged in two separate federal indictments, and soon pleaded guilty to all counts in both cases.
At his sentencing hearing in Seattle today, Wagenius was sentenced to nearly six years in federal prison, and ordered to pay $294,978 in restitution.
Federal prosecutors said Wagenius was assisted in his efforts to extort victim companies by Kenneth Schuchman, a 28-year old man from Vancouver, Washington who has a lengthy cybercriminal history. In 2019, Schuchman pleaded guilty to operating the Satori botnet, a vast collection of hacked Internet-of-Things (IoT) devices that was used for large-scale distributed denial-of-service (DDoS) attacks.
Two other alleged co-conspirators of Wagenius are still facing charges in connection with the Snowflake data thefts; Conor Riley Moucka, a.k.a. “Judische,” of Kitchener, Ontario was arrested in 2024 and pleaded guilty in August 2026; and John Erin Binns, an American man currently living in Turkey who is also wanted for a 2021 data breach at T-Mobile that exposed the personal information of at least 76 million customers.
Kiberphant0m also admitted to re-extorting victims, and threatening to disclose national security secrets. Immediately following Moucka’s arrest — after AT&T had already paid the extortion group a $370,000 Bitcoin ransom — Kiberphant0m posted on hacker forums what he claimed were the AT&T call logs for then President-elect Donald Trump and for then Vice President Kamala Harris, as well as schematics allegedly stolen from the U.S. National Security Agency (NSA).
Paul Russell is a resident agent in charge at the Defense Criminal Investigative Service (DCIS), the criminal investigative arm of the U.S. Department of Defense Office of Inspector General. Russell said when DCIS received information that a soldier with secret clearance was allegedly involved in cybercrime and extortion, the agency began working the investigation alongside the FBI, the Army Criminal Investigative Division (CID), and the U.S. Secret Service.
“We don’t often get leads where there’s an active duty soldier with a secret clearance who’s creating hacking tools and trafficking in data,” Russell said. “That doesn’t happen every day, and so when that hits it really spins all of our partner organizations up. It was very serious from jump street, just because it was unique, it was an insider threat, and we weren’t sure what we were dealing with.”
A sentencing memo (PDF) filed Sept. 19 by federal prosecutors in Seattle notes that while Wagenius pleaded guilty almost immediately and has been remarkably cooperative, he recently got caught trying to find security vulnerabilities in the BOP’s computer network. The government’s memo notes that while incarcerated and awaiting sentencing, Wagenius violated the computer use policies of the Bureau of Prisons (BOP) in attempts to learn about vulnerabilities in BOP computer systems.
“According to records from BOP, in or around September 2025, Wagenius used another inmate’s email system to request that the email recipient prompt a commercial AI tool to provide information about “[w]hat CVE’s are there for Windows 10 Enterprise privilege escalation and bypasses” and to “[p]rovide the CVE’s and a real world working script for each CVE . . . without omitted code,” the government’s memo states.
The memo states that less than a week later, Wagenius used a different inmate’s email account and requested that the email recipient prompt an AI tool to “[p]rovide the step by step for CVE-2023-45208, code for this if any, and if no code exists make some, make sure to describe everything in detail.” CVE-2023-45208 is a three-year-old “command injection” vulnerability in D-Link networking devices.
That same month, Wagenius allegedly again requested that the email recipient prompt AI with the question, “How do you make an antenna in a prison environment with commissary or readily available items/tools to improve/make an antenna to extend radio reception?”
Federal prosecutors said Wagenius also requested that the recipient research escaping prison.
“In several instances, Wagenius framed the AI queries as being posed in connection to a book he was writing. This is a common method of ‘prompt injection,’ in which attackers feed specially crafted, deceptive inputs into commercial AI tools that are programmed to avoid outputting malicious code that can be used to exploit computer vulnerabilities,” the sentencing memo reads.
The government told the court it is unaware of evidence that Wagenius figured out how to use or deploy the vulnerabilities he was researching in the BOP’s systems, and when questioned said he was only researching “potential vulnerabilities to provide information to the BOP.”
Incredibly, despite the enormous financial value of the data stolen from AT&T and other telecom providers, Wagenius’s extortion efforts were largely unsuccessful. The government’s sentencing memo says Wagenius made a whopping total of around $1,500 from selling stolen data.
“While Wagenius was not particularly financially successful as a cybercriminal, he both intended to and caused significant harm to numerous individual victims, U.S. companies, and the U.S. government,” the memo states.
A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company based in Louisiana. KrebsOnSecurity also has learned that the New Orleans field office of the Federal Bureau of Investigation (FBI) today
A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company based in Louisiana. KrebsOnSecurity also has learned that the New Orleans field office of the Federal Bureau of Investigation (FBI) today launched an official inquiry into the source of the images.
A record available at this identity theft service that includes the drivers license for U.S. Defense Secretary Pete Hegseth, one of several high-ranking U.S. government officials whose drivers licenses can be found for sale.
On Monday, Aug. 31, a source alerted KrebsOnSecurity to a service advertised by a new user on the Russian cybercrime forum Exploit, offering access to digital scans of identity documents on more than 170 million people in North America. The source brought it to my attention because the proprietor of this identity theft service offered my Virginia drivers license as a free sample in their initial sales thread on Exploit.
The service, dubbed Nexus, claims to have more than 153 million drivers licenses for people in the United States and Canada, as well as more than 10 million identification cards; more than three million travel documents and/or international IDs; and at least 579,000 medical cards.
A quick look around Nexus finds they are likely not exaggerating about that 153 million number: Running a blank search in Nexus (with no search parameters entered) returns approximately 11.5 million pages of results, with roughly 15 results displayed per page. It includes documents from people in both Canada and the United States, but the bulk of these records are on Americans: searching for just Canadian drivers licenses returns approximately 1.1 million results, with the largest concentration from Ontario (473,673 records).
Curiously, the identity records include not only drivers licenses but also marijuana dispensary cards. Some of the records list their “source” as “CDL,” presumably short for “commercial drivers license.” Other records carry the source notation of “CAC,” which may refer to Common Access Cards, government issued identity cards that grant physical access to government buildings and secure rooms.
The people behind Nexus claim the license images are coming from an active breach at “a major identity verification company” whose customers include multiple Fortune 500 companies.
The record totals listed by the Nexus identity theft service. The number of drivers license records increased by nearly 400,000 in the span of just 24 hours.
“We have been continuously exfiltrating new data for over a year into our private database,” the service enthused in its introductory post on Exploit. “Records are available to preview before purchase with pertinent information redacted. Customer photos are displayed if available.”
Indeed, over the past 24 hours, the number of drivers license records listed as available in Nexus has increased by nearly 400,000, suggesting that freshly stolen license data is being harvested and uploaded to this service on a semi-regular basis.
The record featuring my drivers license includes six image files: three pairs of photos of the license’s front and back, a basic image scan, as well as infrared and ultraviolet versions of the same images. A date and timestamp is appended to each image file, and the timestamp on my license scan corresponds to a date in June 2025 when I took a flight to the midwest United States to attend a family funeral.
Some of the 153 million+ license scans — including mine — feature six image files with date and timestamps appended to the filenames. Not all records include photos, and some that do feature photos do not display the associated filenames.
Intent on discovering the source of this data, KrebsOnSecurity asked more than a dozen friends and family members for permission to search for their licenses in this service. Each person whose license could be found (nine of them) confirmed having traveled on or very close to the dates in the timestamps attached to their images. It is unclear what timezone these timestamps are in, but from reviewing car rental records shared by several people who helped with this research, it appears the timezone is set to Greenwich Mean Time (GMT).
At first, I thought the source of the data might have something to do with airports. However, that theory went out the window when it became apparent there were no passports in this data set. Also, only some of those who helped with this research said they showed their drivers license at the airport on the day of their travel. One person whose license was in Nexus hadn’t flown at all recently, but was renting a car from Hertz for several months around the date of their timestamp.
Two of those who agreed to help are federal employees who said they shared other forms of government identification when passing through airport security. However, those individuals each said they shared their state-issued drivers licenses later that day when renting vehicles at their respective destinations, and that both rented their cars from Hertz.
After finding a note in my calendar for the day of my June 2025 flight reminding me to bring my passport, I remembered that I also never actually shared my drivers license when I went through security at Reagan National Airport on that day because I did not yet have a Real ID, a security-enhanced drivers license that is now required by the Transportation Security Administration (TSA) for all domestic travel. Instead, I showed the TSA agent my government-issued U.S. passport.
Here’s where it gets interesting: I was able to find my mother’s drivers license in this service as well, and the timestamps for her images are just a few seconds apart from mine. That’s notable because we both handed our licenses to the Hertz rental car representative at the same time.
According to my mom, the only place she gave her drivers license to that day was the rental car company, and if memory serves that is also true for me. I don’t recall if the rental car representative inserted our licenses into any kind of machine, but I remember they held onto them for several minutes behind the counter while we were signing various forms. KrebsOnSecurity sought comment from Hertz and will update this story in the event they reply.
Zach Edwards is a well-known security and privacy researcher who recently launched a service called DecryptAds to help people better understand how online advertisers are tracking them. A scan of Edwards’s drivers license is available for purchase on this identity theft service, and Edwards said the timestamp on his record corresponds to the middle of a trip last month to Las Vegas for the annual DEFCON security conference.
Edwards told KrebsOnSecurity that although he did not rent a car in Vegas, he did hand over his license at the TSA checkpoint, at a marijuana dispensary in Vegas, and at his hotel (the Aria). But he said the only one of those three that for sure scanned his ID in some kind of device was the dispensary.
To enter Planet13’s weed dispensary in Las Vegas, one must pass through a red telephone booth. Image: Zach Edwards.
Edwards said the dispensary he visited that day was Planet13, a multi-state chain with stores in California, Florida, Illinois and Nevada. In 2022, the New Orleans-based identity provider idscan.net published a press release announcing an exclusive identity verification agreement with Planet13’s dispensaries nationally. IDScan says it processes ID verification for more than 1,000 marijuana dispensaries in 19 U.S. states.
The “trust” page of idscan.net states that the company provides identity verification services for numerous big brands, including Hertz, Target, Fedex, Motorola Solutions, the financial services giant Jack Henry, and Caesars Entertainment. And as idscan.net’s own documentation states, the technology scans IDs with both infrared and ultraviolet light. Idscan.net says the company’s systems and technology perform more than 21 million verifications monthly, at more than 20,000 locations around the world.
Image: idscan.net.
Contacted by KrebsOnSecurity, idscan.net said it was investigating the matter, but the company has not yet shared an official statement or a substantive reply to specific questions sent via email.
“At this point I’m not able to share any additional information, but the updates you have provided have been welcome, and helpful to our team’s investigation,” wrote Jillian Kossman, a marketing and operations leader at idscan.net.
During the course of my research for this story, word got around to the FBI that I was poking at the apparent source of this new identity theft service’s data. Probably they were tipped off when I shared with a trusted source that Nexus also is selling the drivers license information for the assistant director of the FBI (I did not find FBI Director Kash Patel’s license in Nexus).
Earlier this afternoon, I was added to a conference call with a half-dozen FBI agents, including senior leaders from the agency’s cyber division. During that call, the FBI shared that earlier today their New Orleans field office opened an official investigation into an apparent breach involving idscan.net.
Edwards said that as more in-person and online experiences require sharing drivers licenses, vendors who collect this sensitive data need to be held to a higher standard.
“This episode should further strengthen the resolve for people who are fighting back against online ID schemes which are requiring countless providers to ask for drivers licenses in order to access services under the guise of protecting kids,” Edwards told KrebsOnSecurity. “These systems are putting sensitive data into more and more 3rd party vendors, and we don’t have nearly the oversight to ensure they are safe.”
Larry Baldwin is principal intelligence researcher at the cybersecurity firm Cybera. Baldwin said a front and back scan of his drivers license available at Nexus contains timestamps that correspond to the date of a car rental from Hertz on a recent vacation.
Baldwin said the Nexus identity theft service presents multiple serious security and privacy threats, noting that state-issued drivers licenses are commonly used as proof of one’s identity when opening new lines of credit. Baldwin said the service could also dangerously expose many people who do not wish to be found but who cannot meaningfully change their appearance (or at least not enough to fool today’s AI-based image matching tools).
This category of people, he said, includes those fleeing domestic violence, and even people who have been assigned a whole new life and identity as part of the federal government’s witness protection program, which is generally reserved for criminal defendants in racketeering and conspiracy investigations who agree to cooperate with federal authorities.
“Just when it seems like we’re making some headway in improving authentication controls through drivers license verification systems, this happens and the very thing those improvements are dependent on are compromised,” Baldwin said.
Update, Sept. 8: IDscan.net published a brief notice saying it has “determined that an unauthorized third party may have accessed and/or copied certain customer information, including full names and drivers license or other government-issued identification numbers.” The statement said IDscan.net is notifying affected individuals and offering credit protection services.
Update, Sept. 2, 6:05 p.m. ET: A spokesperson for Caesars Entertainment said Caesars has not been a client of IDScan.net and has not used VeriScan since February 2025, despite IDScan.net listing them as a client on their website. That person said Caesars had no active VeriScan accounts at the time of the incident and did not authorize IDScan.net to retain data from its accounts, and that IDScan.net said the incident should have no impact on Caesars Entertainment.
Update, 8:56 p.m. ET: Shortly after this story was published, the Nexus identity theft service website vanished from the darkweb, replacing its login page with a plain text message that reads, “This service is no longer available.”
This is a potentially fast-moving story. Any changes or updates will be noted here along with a timestamp.
It can be daunting to determine who’s responsible for showing ads on the websites we visit, or who’s harvesting data from the mobile apps we use every day. That information is already semi-public, but it is not easily parsed and traditionally much of it has remained walled away in the hands of large advertising platforms. Not anymore: A powerful and free new service called DecryptAds scrapes and correlates this adtech data and makes it simple to quickly learn a great deal about the entities that
It can be daunting to determine who’s responsible for showing ads on the websites we visit, or who’s harvesting data from the mobile apps we use every day. That information is already semi-public, but it is not easily parsed and traditionally much of it has remained walled away in the hands of large advertising platforms. Not anymore: A powerful and free new service called DecryptAds scrapes and correlates this adtech data and makes it simple to quickly learn a great deal about the entities that are tracking you.
A Decryptads summary of the advertising partnerships declared by espn.com.
The newly launcheddecryptads.com says it is constantly scraping the files that websites and apps make publicly available to disclose the companies that are permitted to run ads or collect user data. These files include:
–ads.txt: all of the adtech companies and data brokers that may run ads or harvest data from the site;
–app-ads.txt: entities that can harvest data from or display ads on mobile and smart TV apps;
–buyers.json/sellers.json: the entities buying, selling or reselling ad inventory for a given site or app.
Zach Edwards is chief research officer for DecryptAds and a threat researcher at the security company Infoblox. Edwards said he and two other founders decided the service was needed because the adtech data in these files is generally only useful when it can be cross-referenced to build a more complete picture of the advertising ecosystem for each website or app.
“It’s an adtech tool but we’re trying to approach adtech from a security perspective,” Edwards said. “It’s really built for a lot of privacy and security use cases that have been dramatically underserved.”
Those use cases, he said, include tracking down the source of malicious ads that try to foist malware on targeted users, identifying ad networks located in adversarial nations, and detecting the fast growing swarms of AI-generated slop websites and apps. And as decryptads.com demonstrates, these potential security and privacy threats are near impossible to detect just by viewing a single apps.txt or app-ads.txt file.
“Supply-chain integrity issues rarely live in a single file,” the site explains. “They show up as broken cross-references between ads.txt, app-ads.txt, and sellers.json files; as cloned declaration sets across unrelated domains; as seller removals that only make sense when viewed across exchanges; and even as supply paths in bid logs that never actually appear in any given publisher’s authorized-seller list.”
A search in DecryptAds for the hugely popular sports network espn.com reveals 143 ad partners and 19 registered data broker domains are listed within its ads.txt and app-ads.txt files. That data broker information is gradually becoming available because four states — California, Oregon, Texas and Vermont — have recently passed laws requiring data brokers to register if they buy or sell data on consumers from those states. DecryptAds reports that almost half of those data brokers are collecting geolocation data from espn.com visitors who aren’t blocking ads, while another three disclose that they collect device fingerprints and sensitive personal information.
A visual representation of the complex ad supply chain declared by espn.com. Image: decryptads.com.
HIGH-RISK AD PARTNERS
DecryptAds also makes it easy to learn the beneficiaries and national origins of the advertising firms lurking in apps and websites, displaying a conspicuous warning when adtech partners of an app or website are based in “geo-risk” areas like China and Russia, or in countries with strong financial and political ties to both — such as Cyprus and the United Arab Emirates (UAE).
According to DecryptAds, espn.com works with four different advertising entities that are based in either Russia, China or the UAE, including the adtech firm Between Digital, which lists a New York address. However, the dossier on Between Digital flags them as a Russian firm, showing that their publisher offers (PDF) are processed through Alfa Bank, Russia’s largest private commercial bank and one of several financial institutions placed under U.S. sanctions in 2022 after Russia invaded Ukraine. KrebsOnSecurity sought comment from both Between Digital and the company’s founder, and will update this story in the event that either replies.
A search for several top U.S. military news websites — including armytimes.com, airforcetimes.com, defensenews.com, navytimes.com, marinecorpstimes.com and federaltimes.com — shows they all allow Between Digital to serve ads and track users, as well as two entities in the UAE and another in the ownership secrecy haven of Panama. DecryptAds reports that Between Digital is collecting ad data on approximately 55,000 partner websites.
The “Geo Risk” section of decryptads.com.
Pivoting on Between Digital’s app-ads.txt file reveals hundreds of domains featuring simple web-based games that are frequently interrupted by ads. Edwards said Between Digital’s own declarations show the company is listed as both a publisher and a reseller on approximately two-thirds of their portfolio.
“It means they are basically playing both sides of the bidding equation, which creates opportunities to direct client spend at your owned and operated properties or client infrastructure, essentially creating opportunities for conflicts of interest,” Edwards told KrebsOnSecurity. “The problem we have right now is that for years we’ve had almost no one policing these ads.txt and app-ads.txt files.”
The Opera Web browser remains quite popular, and probably many users are unaware that since 2016 it has been majority owned and controlled by the Chinese company Kunlun Tech (the operational headquarters of Opera remain in Oslo, Norway).
Opera.com’s profile at DecryptAds identifies 27 registered data brokers collecting information, including 15 adtech partners in the UAE, six in China, three in Cyprus, two in Russia and one each in Hong Kong and Ukraine. DecryptAds makes clear, however, that these companies represent just seven percent of the adtech partners specified in Opera.com’s ads.txt and app-ads.txt files.
LEGAL DOSSIERS
One feature of DecryptAds that sent this author down multiple hours-long research rabbit holes is its Legal Dossier lookup, which takes several minutes for each search but eventually churns out oodles of useful information about who owns a particular domain or app, when it was registered, and any aliases or relationships it may have to adtech companies and other websites or apps.
For example, last month KrebsOnSecurity wrote about researchers from Bitsight who found that an extremely popular line of TV streaming sticks called H96 quietly rent out each user’s Internet connection to strangers. Bitsight also discovered that when these devices aren’t being used to stream pirated video content, they are spoofing themselves as mobile phones clicking ads on AI-generated slop websites.
Bitsight concluded that the same Chinese company that made several of the malicious apps common to all of these H96 streaming sticks — the Fengwo Group — also also ran the network of ads and AI slop websites being clicked on by tens of thousands of these devices that are pretending to be mobile phones.
Examples of ad landing pages linked to the Fengwo Group. These sites were designed to show ads only to H96 devices that were spoofing their device type as mobile phones. Image: Bitsight.
A DecryptAds legal dossier on the (now dormant) Fengwo Group domain name for the AI slop website pictured on the left in the screenshot above (medicalbeautyhub dot com) shows it shares a seller ID (1674071) with a gaming website — giacoloredstones[.]com — which features yet another seller ID (103488000).
Pivoting on that latter seller ID reveals hundreds of active websites within Russia’s Yandex ad system featuring extremely low-quality games or simple utilities that pepper visitors with ads.
QUIET REMOVALS
Edwards said that when advertising networks suspect a given advertiser is engaged in unauthentic clicks or displaying malicious ads, very often those networks will quietly remove the offender from their list of approved partners without letting anyone else know about their suspicions.
This practice, he said, makes it easier for dodgy adtech firms to avoid accountability and continue victimizing others. To address that visibility gap, DecryptAds features a quiet removals feed that records and correlates all of the sellers.json removals across ad exchanges for the same seller domain or name.
A screenshot of the Quiet Removals Feed at decryptads.com.
“The way the adtech industry works, someone will write a report about ad fraud and only share it with their own clients and they won’t make it public,” Edwards said. “The ban is just removing them from the sellers.json file, but they told nobody. One day it was there, the next it was gone. So if you’re trying to navigate who is suspicious, that’s usually tough to do because there are a lot of adtech companies removing things all at once.”
MALVERTISING AND AI SLOP
Malvertising, the term given to the practice of inserting malicious ads that foist malware or redirect visitors to phishing pages, remains an all-too-frequent occurrence in the modern adtech industry. But Edwards said these malicious ads are far more commonly found now on newly generated AI slop websites than on high traffic destinations that typically employ a variety of technologies and third party tools to quickly flag bad ads.
“None of these slop AI content farms are paying for that kind of protection,” he said. “They’re just signing up the lowest quality partners, and it essentially becomes a greased rail to target the users of those sites with malicious ads. Most malvertising attacks don’t happen on espn.com or huffpost.com, but rather [on] some lower quality content farm and someone just went there because it came up in a search.”
Edwards said the AI slop websites are populated with machine-generated blog posts and images, and cover a wide array of themes from home improvement and decorating to food recipes, hunting, cars and consumer technology. He said organizations that get hit with malicious ads are often at a loss for what to do next, unaware that in most cases the answer is one of the entities listed inside the website’s ads.txt or app-ads.txt file.
“A lot of serious organizations are starting to understand that if we’re not breaking down this ad data, we’re not going to know who’s targeting government people with zero-click payloads on an almost daily basis,” he said.
Edwards maintains that truly getting a handle on the malvertising and AI slop problems will require more data-sharing by the major ad networks. Specifically, he says those platforms do not broadly share what’s known as the “supply chain object” or SCO, structured data attached to each advertising bid request that lets buyers see every seller, reseller and intermediary involved in passing an ad impression from the publisher to the final buyer.
“That SCO tells you who sold it or resold it, and who was the final entity that bought the impression that served that malware payload,” Edwards explained. “You may see the malicious zero-click redirection, but without the supply chain object — which is only served server side — you won’t know who targeted your people with malware and won’t have a way to try and prevent it properly. But if we can encourage the adtech industry to expose that SCO, it will get easier to find the culprit behind any one bad ad.”
DecryptAds also offers an application programming interface (API) that allows researchers to automate queries and integrate the site’s functionality into popular AI platforms.
WHAT CAN YOU DO?
The only sane reaction to the examples described above is to block all online ads outright. This approach is broadly endorsed by security experts because it also makes it more difficult for adtech firms and data brokers to build detailed profiles on you and track your movements around the web and in the real world.
However, much depends on how you normally prefer to browse the Internet, and how much trust you place in third party browser plugins and extensions. For those primarily surfing via a regular desktop or laptop Web browser, uBlock Origin Lite is an excellent free and well-maintained open source option. uBlock Origin also should work with mobile browsers like Firefox, but apparently only on Android-based devices.
Adblock Plus is a decent option for iPhone and iPad users. For power users, Adblock and uBlock Origin both support custom blocking rules from easylist.to, which publishes a frequently updated list that removes most advertisements from webpages.
The well established browser extension NoScript blocks all non-approved Javascript code, and it generally does a fine job blocking most ads from loading. However, script blockers like NoScript may not be suitable for average users who don’t enjoy constantly having to referee which scripts should be allowed to load so that each site displays properly.
More technically inclined/adventuresome readers should strongly consider a hardware approach to blocking ads at the local network level, because that is easily the cheapest, most secure and scalable way to do it. A tiny, low-cost and broadly available computer known as a Raspberry Pi can be turned into a powerful ad blocker for all devices on a local network when fitted with a microSD memory card and a free program called Pi-hole. Once you’ve set it up properly and changed your router’s network settings to use the Pi-hole’s DNS sinkhole and DHCP servers, it should prevent ads from displaying on any devices connected to that network.
Bear in mind that ad blockers often do little to block ads and/or tracking that occurs from within mobile apps that users have chosen to install on their devices. Many websites now push users to install a mobile app, supposedly in order to more fully access and enjoy the site’s services and content. But in my experience, they’re not doing this because the user experience is somehow way better on the app (as LinkedIn tries to convince us non-app users several times a week via email). On the contrary, I find most mobile apps to be horribly designed, annoying, and/or completely unnecessary, and when given the option I will almost always choose to interact with a website or service directly in a Web browser.
No, the cold truth is that big web destinations tend to get pushy with their apps because they make it easier for these companies to keep you on their platforms longer and to collect (and in many cases resell) far more precise data about who, what and where their users are. Also, companies pushing customers the hardest to install mobile apps always seem to liberally opt everyone in to having their data used to train large language models these days. So be cautious about the apps you install on your mobile devices (including any smart TVs!), and poke around their listings at DecryptAds if you want to learn more about their privacy practices and any relationships they may have to adtech firms.
A 26-year-old Canadian man once described as one of the most consequential cybercrime threat actors of 2024 has pleaded guilty to computer fraud and conspiracy to hack and extort more than 165 organizations that used the cloud provider Snowflake. Connor Riley Moucka, of Kitchener, Ontario, also admitted to stealing call and text history records of more than 100 million AT&T customers.
A surveillance photo of Connor Riley Moucka, a.k.a. “Judische” and “Waifu,” dated Oct 21, 2024, 9 days befor
A 26-year-old Canadian man once described as one of the most consequential cybercrime threat actors of 2024 has pleaded guilty to computer fraud and conspiracy to hack and extort more than 165 organizations that used the cloud provider Snowflake. Connor Riley Moucka, of Kitchener, Ontario, also admitted to stealing call and text history records of more than 100 million AT&T customers.
A surveillance photo of Connor Riley Moucka, a.k.a. “Judische” and “Waifu,” dated Oct 21, 2024, 9 days before Moucka’s arrest. This image was included in an affidavit filed by an investigator with the Royal Canadian Mounted Police (RCMP).
The U.S. Justice Department said between February and October 2024, Moucka and co-conspirators used stolen login credentials to steal cloud-hosted data belonging to at least 165 customers of a U.S.-based software-as-a-service company.
The hackers targeted stolen credentials for Snowflake customer accounts that did not enforce multi-factor authentication, and extorted or attempted to extort a host of well-known companies, including TicketMaster, Lending Tree, Advance Auto Parts and Neiman Marcus. Snowflake responded to the data thefts by increasing password complexity requirements and enforcing multi-factor authentication.
Moucka adopted new nicknames frequently — sometimes operating multiple identities concurrently — but two of his best-known monikers were “Judische” and “Waifu.” Judische’s admitted role in the Snowflake data thefts was first documented by KrebsOnSecurity in a September 2024 story about the overlap between Western, English-speaking cybercriminals and extremist groups that harass and extort minors into harming themselves or others.
That September 2024 story identified Judische as a software engineer from Ontario who has been involved in numerous data breaches and voice phishing attacks against U.S. companies since at least 2020. A little more than a month later, Canadian authorities arrested Moucka on a provisional warrant from the United States.
The government says Moucka and others used their unauthorized access to steal billions of sensitive customer records and download terabytes of information, “including individuals’ non-content call and text history records, banking and other financial information, payroll records, Drug Enforcement Administration (DEA) registration numbers, driver’s license numbers, passport numbers, social security numbers and other personally identifiable information. They then extorted victims by threatening to publish data online.”
Moucka also threatened and harassed government officials and security researchers who were helping to track him down. The Justice Department said the conspirators made over $2.5 million in ransom payments, and that in at least one instance, Moucka re-extorted a victim with threats of further disclosure of the victim’s stolen data.
“Moucka used the stolen data of a government officer and members of a then-former government officer’s immediate family in this re-extortion attempt,” reads a statement from the Justice Department.
One of Moucka’s admitted co-conspirators is Cameron “Kiberphant0m” Wagenius, a U.S. Army soldier who pleaded guilty in July 2025 to extorting AT&T and Verizon for their customer account data. Less than a month before Wagenius’s arrest, KrebsOnSecurity published a deep dive into Kiberphant0m’s various Telegram and Discord identities over the years, revealing how the owner of the accounts told others they were in the Army and stationed in South Korea.
One of several selfies on the Facebook page of Cameron Wagenius.
Kiberphant0m also re-extorted victims. Immediately following Moucka’s arrest, Kiberphant0m posted on hacker forums what he claimed were the AT&T call logs for then President-elect Donald Trump and for then Vice President Kamala Harris, as well schematics allegedly stolen from the U.S. National Security Agency (NSA).
Wagenius is set to be sentenced on September 3, 2026. The government says he faces a maximum penalty of 20 years in prison for conspiracy to commit wire fraud, a maximum penalty of five years in prison for extortion in relation to computer fraud, and a mandatory two-year sentence consecutive to any other prison time for aggravated identity theft.
The third alleged co-conspirator is John Erin Binns, 26, an elusive American man who fled the United States after being indicted for his admitted role in a 2021 breach at T-Mobile that exposed the personal information of at least 76 million customers.
Sources close to the investigation said Binns, also known as “IRDev” and “IntelSecrets,” was until recently incarcerated in a Turkish prison, but that he has since been released and has resurfaced online. Those sources said Binns also recently obtained Turkish citizenship, and under Turkish law a citizen cannot be extradited to a foreign country.
An image of a passport that Binns shared in an email to KrebsOnSecurity in Feb. 2023.
Moucka pleaded guilty to four criminal counts, including computer fraud, wire fraud, aggravated identity theft, and conspiracy. He is slated to be sentenced on Oct. 27 and faces a mandatory minimum penalty of two years in prison on the aggravated identity theft count, as well as a maximum penalty of 30 years in prison on the remaining counts. Ultimately, it will be up the federal judge how much time Moucka actually serves for his extensive cybercriminal rap sheet.
IntroductionThe modern cyber threat landscape has seen a fundamental shift in how threat actors manage and deploy their infrastructure. Advanced persistent threats (APTs) have almost completely moved away from static command-and-control (C2) servers, opting instead to build complex, multi-layered botnets known as Operational Relay Box (ORB) networks. Project ORBITAL (which stands for Operational Relay Box Intelligence, Tracking, & Analysis Lexicon) was established as a centralised intelligen
The modern cyber threat landscape has seen a fundamental shift in how threat actors manage and deploy their infrastructure. Advanced persistent threats (APTs) have almost completely moved away from static command-and-control (C2) servers, opting instead to build complex, multi-layered botnets known as Operational Relay Box (ORB) networks.
Project ORBITAL (which stands for Operational Relay Box Intelligence, Tracking, & Analysis Lexicon) was established as a centralised intelligence matrix to track, analyse, and ultimately help defenders disrupt this highly evasive infrastructure.
To construct these networks, adversaries systematically compromise unpatched, end-of-life devices. By targeting legacy, unpatched Small Office/Home Office (SOHO) router and Internet-of-Things (IoT) devices attackers can create a sprawling, decentralised mesh of proxy nodes. By routing their operations through layers of compromised devices, adversaries mask their true origins, making malicious activity blend seamlessly with legitimate regional traffic.
Blogs by my colleagues at Team Cymru as well as Google offer detailed explanations as to why and how these ORBs have grown over many years and continue to expand.
Project Background
Project ORBITAL represents a centralised Open Source Intelligence (OSINT) collection driven by public reporting from advanced research teams across the cybersecurity and technology sectors. This initiative aggregates telemetry and findings from top-tier vendors including Cisco Talos, CrowdStrike, Google, GreyNoise Labs, Lumen Black Lotus Labs, Microsoft, SecurityScorecard, Sekoia, SentinelLabs, Sygnia, and Team Cymru. Furthermore, it incorporates critical alerts and intelligence shared publicly by United States government agencies, specifically the Federal Bureau of Investigation (FBI), the Cyber National Mission Force (CNMF), and the National Security Agency (NSA).
This repository builds on the methodology of my previous OSINT tracking initiatives. It is heavily inspired by the structure and community success of my earlier matrix projects, specifically the Ransomware Tool Matrix (RTM) (here), the Ransomware Vulnerability Matrix (RVM) (here), and the Russian APT Tool Matrix (RUTM) (here). By applying a similar, structured approach to mapping Operational Relay Box (ORB) networks, this project aims to provide defenders with a clear, actionable lexicon for hunting and tracking evasive edge-device botnets.
Graph Visualisation
Once Project ORBITAL was initially assembled, it was then possible to use a GitHub Action automation with NetworkX and PyVis to create a Graph Visualisation using the data collected. Once in this view, some interesting patterns could be observed.
Analysis of the extracted data uncovered that ASUS devices were the most targeted out of all of the targeted devices by ORBs from the public reports.
Another interesting point the graph highlighted is that the LapDogs ORB network had the highest number of reported targeted devices.
In most reported scenarios, a singular threat group used a dedicated ORB network. However, from extracting the details from the Google and SentinelLabs reports, an adversary like APT15, reportedly leverages both SPACEHOP and PurpleHaze ORB networks, alongside two other separate adversaries UNC2630 and UNC5174.
The overlap in ORB usage suggests these APTs aren't all building their own botnets from scratch. These overlaps likely indicate there are provisioning teams, such as specialised contractors, like Beijing Integrity Tech, who build and maintain these ORB networks and then lease access to the broader Chinese intelligence community in the Ministry of State Security (MSS) and People’s Liberation Army (PLA).
Panda-monium
Below is the list of well-known China-nexus APTs listed using CrowdStrike’s naming scheme and their Google or Microsoft aliases that are all mentioned in Project ORBITAL.
CAULDRON PANDA (aka UNC3886)
ETHEREAL PANDA (aka Flax Typhoon)
JUDGMENT PANDA (APT31, Violet Typhoon)
KEYHOLE PANDA (aka UNC2630, APT5)
MURKY PANDA (aka Silk Typhoon)
VANGUARD PANDA (aka Volt Typhoon)
VIXEN PANDA (aka APT15, Nylon Typhoon)
The most notable aspect about this list is that it contains APTs with wildly different mandates. VANGUARD PANDA (Volt Typhoon) is famous for pre-positioning within critical infrastructure with the potential disruptive attacks, while KEYHOLE PANDA (APT5) and JUDGMENT PANDA (APT31) are long-running cyber-espionage and IP theft operators. The fact that both the saboteurs and the spies have all adopted ORB networks goes to show that this tactic is not niche but instead is the baseline standard for Chinese APT operational security (OPSEC).
How to Access
You can find Project ORBITAL on my GitHub repository below:
If you’ve seen reports of a wildfire in your region and you’re looking for open source data, NASA’s fire-tracking tool is often the first place to start. It provides a heat signature and an approximate location. But detection is only the first step in understanding what’s happened. In this guide, we explore ways to analyse and report on the scale and severity of wildfires, including those in protected areas where ecosystems are often most fragile. We also examine how often fires recur in the sam
If you’ve seen reports of a wildfire in your region and you’re looking for open source data, NASA’s fire-tracking tool is often the first place to start. It provides a heat signature and an approximate location. But detection is only the first step in understanding what’s happened. In this guide, we explore ways to analyse and report on the scale and severity of wildfires, including those in protected areas where ecosystems are often most fragile. We also examine how often fires recur in the same region over multiple seasons, helping to identify patterns in fire activity as climate change reshapes fire risk around the world.
Satellite imagery from Copernicus Browser will be used to visualise the spread of the fire, and vegetation health indices to assess burn severity. The datasets will then be combined in QGIS for more in-depth analysis. At each stage, suggestions will be offered for turning the data into clear, reportable findings.
Throughout this guide, a single case study will be used: Sicily’s Zingaro Nature Reserve. In 2025, wildfires swept across the region, destroying forests, grasslands and croplands. Located on the Capo San Vito peninsula, the reserve was so severely affected that sections remain closed today.
Visualising Scorched Earth
When investigating a wildfire, it’s important to narrow down whenit occurred and whereit spread. The Landsat and Sentinel-2 missions are well-suited to this task, providing regular free imagery of most of the Earth’s landmass.
Below are two sets of Sentinel-2 imagery showing conditions shortly before and after a fire on July 25, 2025,near Capo San Vito, Sicily. The top two images are true-colour, similar to what would be seen from an aeroplane window. The image on the top right shows an area of scorched earth on the eastern side of the peninsula, but the exact extent of the fire is difficult to determine because the colour of the ground has changed only slightly.
Satellite images of Capo San Vito, Sicily, showing before (left) and after (right) a fire on July 25, 2025. Top row: true-colour imagery. Bottom row: false-colour imagery highlighting fire damage in red. Source: Contains modified Copernicus Sentinel data 2025, processed with Copernicus Browser.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
The bottom two images are false-colour and highlight the difference between healthy vegetation and burned areas. Such imagery is possible because Sentinel-2 captures bands of light outside the visible range, a technique known as multispectral imaging. In these images, the near-infrared (NIR) band is coloured green, and the shortwave infrared (SWIR) band is coloured red. Healthy vegetation mainly reflects NIR light, so it appears green, while burned areas mainly reflect SWIR light, so they appear red.
These images were created with Copernicus Browser, a free browser-based tool from the European Space Agency for accessing and working with Sentinel imagery. It allows users to browse the Sentinel-2 catalogue by date and visualise different band combinations. You don’t need an account to use the browser, but signing in enables additional features.
If you’d like to try Copernicus Browser without further explanation, you can go straight to the false-colour post-fire image here.
To follow along step by step, first open Copernicus Browser. Then to visualise Sentinel-2 imagery:
Zoom to the desired area on the map or use the search bar (San Vito Lo Capo, north-west Sicily)
Select the date of interest (‘2025-07-27’ selected below).
Select the layer of interest (‘True color’ by default; SWIR selected below).
Screenshot of Copernicus Browser. Annotations by Bellingcat.
By identifying the last available image before the fire and the earliest image after it in which the full burn area is visible, it’s possible to establish the location and timeline of the fire.
This allows us to report the following finding: “Satellite imagery reveals the extent of the damage caused by wildfires across the Capo San Vito peninsula on Sicily’s northern coast between July 20 and July 27, 2025.”
Extra exercise: Look up a recent fire (e.g., wildfires near Penco, Chile in January 2026), navigate to the affected location and try to visualise the burned area using Copernicus Browser.
The visibly scorched area can be measured using the Area of Interest tool (highlighted below), which allows users to draw a polygon on the map and calculate the total area in square kilometres. (Once drawn, keep the polygon in the editor, as it will be used again later.)
Estimated burn area of 53.97 km2 using the Area of Interest tool. Screenshot of Copernicus Browser. Annotations by Bellingcat.
Reportable finding: “The wildfire that swept across Sicily’s Capo San Vito peninsula in 2025 burned more than 50 km2 of the peninsula, according to Sentinel-2 data.”
Repeatedly measuring the burned area over time allows you to follow the progression of a fire. This method was used by Bellingcat when covering the Etosha National Park wildfire in late September 2025.
Extra exercise: Replicate the analysis of the Etosha National Park fire from this Bellingcat article.
Assessing Burn Severity
Some fires only affect surface vegetation, while others scorch the ground and cause long-lasting damage. Burn severity can be measured using an index called the Normalised Burn Ratio (NBR).
How Does the Normalised Burn Ratio (NBR) Detect Burned Areas?
The spectral response of a material describes how reflective it is to different types of light. The graph below shows the difference between healthy vegetation and bare soil in terms of the amount and types of light they reflect.
Reflectance data reproduced from the ECOSTRESS Spectral Library using Conifer for Healthy Vegetation and Black Loam for bare soil. Graphic by Bellingcat.
By focusing on the NIR and SWIR bands, where reflectivity differs significantly between healthy vegetation and bare soil left after a burn, an index can be calculated:
NBR = (NIR – SWIR) / (NIR + SWIR)
A high NBR indicates healthy vegetation, while a low NBR indicates burned areas.
Copernicus Browser doesn’t include a default NBR layer, but it can be added via a custom script, as shown in the screenshot below:
Load the script by clicking the green circular arrows to the right of the URL.
Click ‘Apply’ (you may need to scroll down).
Alternatively, you can skip these steps and go straight to the custom NBR post-fire image here.
Screenshot of Copernicus Browser. Annotations by Bellingcat.
The NBR layer displays positive values in green (healthy vegetation) and negative values in purple (burned areas), making the boundary of the scorched area much clearer than before.
To calculate the change in NBR in Copernicus Browser, use the Statistical Information tool (a free account is required to access this feature).
Within the date selector, choose a date a few weeks or months after the fire.
Using the Area of Interest polygon, select the ‘Statistical Info chart’ icon.
Set the maximum cloud cover to around 30% using the slider in the top right.
Select a date range that captures the available data surrounding the fire (July 20-27 shown below).
Identify when the fire occurred on the graph (this will be marked by a sharp drop in the NBR, as shown below).
Hover over the points on the graph immediately before and after the fire to display the mean value.
Composite of screenshots from within Copernicus Browser.
In this example, the pre-fire image had an average NBR of 0.11 and the post-fire image had an average NBR of -0.18. The NBR decreased by 0.29, which represents a moderate burn.
Severity Level
Change in NBR
Unburned
Less than 0.100
Low
0.100 – 0.269
Moderate
0.270 – 0.659
High
0.660 or greater
Burn severity table from the US Forest Service (page 38), simplified by Bellingcat.
Reportable finding: In late July, the fire, which scorched more than 50km2 of Sicily’s Capo San Vito peninsula, was deemed moderately severe according to the US Forest Service guidelines.
Extra exercise: Find a custom visualisation script of interest from this repository and explore what it does.
Wildfires in Conservation Areas
By focusing on protected sites such as nature reserves and national parks, we can begin to assess how wildfires affect areas of high conservation value. Controlled burns are widely used in agriculture and land management, but unchecked fires in protected areas risk eroding fragile ecosystems.
The proportion of the Zingaro Nature Reserve that was damaged by the fire can be estimated by combining the NBR image created in Copernicus Browser with a dataset from Protected Planet, a global map of protected areas that includes nature reserves.
QGIS, a program for working with geographic data, is well-suited for this type of analysis. Download and install QGIS on your computer. For help with this step, refer to the QGIS installation guide.
To download the NBR image from Copernicus Browser:
With the NBR visualisation selected, click the ‘Download’ icon.
Switch tabs at the top from ‘Basic’ to ‘Analytical’.
Change the image format to ‘TIFF (32-bit float)’.
Change the image resolution to ‘HIGH’.
Change the coordinate system to ‘Popular Web Mercator (EPSG:3857)’.
Toggle the ‘Clip extra bands’ switch to the off position (see image below).
Select the ‘Custom’ layer check box (and deselect any others).
Click ‘Download’.
Wait. It could take several minutes for the image to be generated and downloaded.
Screenshot of Copernicus Browser. Annotations by Bellingcat.
Once the image has downloaded, rename it to NBR.tiff to make it easier to work with.
Next, open QGIS and click ‘New Project’ in the upper left.
Load the image from Copernicus Browser by dragging and dropping the downloaded file into QGIS.
Useful QGIS Terminology
CRS – The Coordinate Reference System describes how the world should be measured and projected. Two of the most common are:
EPSG:4326 – WGS 84, which uses latitude and longitude as the unit of measurement.
EPSG:3857 – WGS 84 / Pseudo-Mercator, which uses metres as the unit of measurement.
Raster – a type of data that uses pixels to represent information (such as satellite imagery)
Vector – a type of data that uses points, lines, and polygons to represent information (such as a burn area polygon).
Processing the NBR Image
Next, we categorise each pixel in the NBR image as burned or unburned.
Previous analysis in Copernicus Browser showed that the Zingaro Nature Reserve’s NBR value dropped below zero only after the fire (before image: mean NBR value on July 20, 0.11; after image: mean NBR value on July 27, -0.18).
We can use this analysis to set a threshold; anything below zero will be categorised as burned.
The QGIS Raster Calculator lets us apply our threshold to the NBR image and create a new layer.
Open the Raster Calculator by selecting ‘Raster > Raster Calculator…’ from the menu bar at the top.
Screenshot of the QGIS Raster Calculator. Annotations by Bellingcat
The Raster Calculator lists the raster bands available in the project. In this example, there are five. These bands are set by the custom script we used in Copernicus Browser and are numbered as follows:
Red
Green
Blue
Pixel validity (not used in this example)
NBR index
To create a new raster layer that applies our threshold on the NBR index band:
Double-click the fifth band (ending ‘@5’) to add it to the expression box at the bottom.
Add < 0 using your keyboard (shown above).
Select the ‘Create on-the-fly raster instead of writing layer to disk’ checkbox.
Click ‘OK’.
The expression NBR@5 < 0 tells QGIS to categorise NBR index values as burned if they are less than zero.
The new layer shows burned areas as white (a value of 1), and unburned areas as black (a value of 0).
Screenshot of QGIS.
Extra exercise: Download an NBR image captured before the fire. Use the Raster Calculator to create a new layer that shows burn severity.
As before, drag and drop the downloaded file into QGIS. This time, the download is a zip file and contains many PDF files as well as the geodatabase file of interest. Scroll down to the bottom of the list and select the ‘gdbtable’ file with a polygon icon on the left side (see the blue highlighted row below), then press ‘Add Layers’.
Screenshot of QGIS. Annotations by Bellingcat.
This adds the nature reserve polygon as a layer in QGIS (and gives it an arbitrary colour). The nature reserve is almost completely contained within the white burned area, indicating it was heavily affected by the wildfire.
Screenshot of QGIS.
Quantifying the Burned Area in the Nature Reserve
To measure the proportion of the nature reserve that was burned by the wildfire, we will use the Zonal Histogram tool from the QGIS Processing Toolbox to count the number of unburned and burned pixels within the reserve polygon.
Open the toolbox with ‘Processing > Toolbox’, and a pane should open to the right. In the Processing Toolbox search field, look up ‘Zonal Histogram’ and double-click the result to open the tool.
To create a new layer:
Set the ‘Raster layer’ to the threshold burn area layer (NBR@5 < 0)
Set the ‘Vector layer containing zones’ to the nature reserve polygon layer (should start with ‘WDPA_’).
Click ‘Run’
Click ‘Close’
Screenshot of QGIS. Annotations by Bellingcat.
This will create a new layer called ‘Output zones’, which is a copy of the nature reserve polygon with pixel counts added.
Select the output layer in the lower left and click ‘Attribute Table’ in the upper right. (The attribute table is a spreadsheet-like view of the data contained in a layer.)
For the output layer, there is just one row because there is only one polygon. If the layer contained many polygons, there would be many rows.
The newly calculated counts are added to the end of the table, so scroll all the way to the right. Look for fields starting with ‘HISTO_’. Here, HISTO_0 is the count of unburned pixels (value of 0), and HISTO_1 is the count of burned pixels (value of 1).
Screenshot of QGIS. Annotations by Bellingcat.
To calculate the proportion of burned area, the number of burned pixels is divided by the total number of pixels.
Proportion = 57413 / (57413 + 2195) = 0.96318…
A value of 0.96318 means that just over 96.3% of the nature reserve burned.
Reportable finding: In late July, more than 95% of the Zingaro Nature Reserve burned in a wildfire, according to Sentinel-2 satellite imagery and Protected Planet data.
Tracking Past Wildfires
To assess the significance of an ongoing wildfire, it is important to place it in historical context. How does it compare with previous fires in the same area? Is it part of a seasonal pattern, or does it represent an unusually severe event?
With coverage dating back to 2008, the European Forest Fire Information System (EFFIS) automatically maps wildfires across Europe, North Africa, and parts of the Middle East.
Fire data can be requested directly from EFFIS using web form, with results delivered by email. For ease, you can also download Bellingcat’s archived copy of EFFIS wildfire data for Italy covering 2015–2025.
For this section, it is best to open a new QGIS project.
To view and analyse historic wildfires in the Zingaro Nature Reserve using EFFIS data:
(Optional) Add the OpenStreetMap layer from the XYZ Tiles category by double-clicking it.
Load the EFFIS data into QGIS. If prompted to select a coordinate transformation, click ‘OK’ to accept the default option.
Load the Protected Planet Zingaro Nature Reserve polygon as described earlier.
Open the Vector Intersection tool by selecting ‘Vector > Geoprocessing Tools > Intersection…’ from the menu bar at the top.
Screenshot of QGIS Annotations by Bellingcat.
The Intersection tool creates a new layer containing only the fires that affected the Zingaro Nature Reserve. To create the new layer:
Set the ‘Input layer’ to the EFFIS fires layer.
Set the ‘Overlay layer’ to the Zingaro Nature Reserve polygon layer.
Click ‘Run’.
Screenshot of QGIS Annotations by Bellingcat.
QGIS functionality can be extended through plugins, including Data Plotly, which adds data visualisation tools. To install Data Plotly, open the Plugin Manager by selecting ‘Plugins > Manage and Install Plugins…’ from the menu bar, then:
Search for ‘Data Plotly’ in the available list.
Select the plugin from the search results.
Click ‘Install Plugin’ to download and install it.
Screenshot of QGIS Annotations by Bellingcat.
Once installed, open the Data Plotly panel with ‘View > Panels > DataPlotly’. The panel should appear on the right-hand side of the QGIS window.
To plot a graph of historic wildfire activity within the nature reserve, configure Data Plotly as follows:
For ‘Plot type’, choose ‘Bar Plot’.
Set the ‘Layer’ to the newly created ‘Intersection’ layer.
In ‘X field’, type “year(initialdat)”. This expression extracts the year from the fire’s approximate start date, allowing events from the same year to be grouped together.
In ‘Y field’ enter “$area/1000000”. This expression calculates the burned area within the nature reserve in square kilometres.
Note: EFFIS data provide initial and final dates for each fire, which are approximate because they depend on the availability of satellite imagery. These dates should be treated as bounds for when a fire occurred, rather than as the dates when it started and ended.
Next, switch to the Layout tab in Data Plotly:
Untick ‘Show Legend’. Only do this for simple plots where a legend is not required.
Add a title and labels for the X and Y axes.
Finally, click ‘Create Plot’ and wait a few seconds for the chart to be generated.
Screenshot of QGIS Annotations by Bellingcat.
The chart shows that the Zingaro Nature Reserve has experienced several significant wildfires over time. However, in 2025, the data show that the fire burned a larger area within the reserve than the major fires recorded in 2020 and 2017.
Bar chart showing the burned area of the Zingaro Nature Reserve between 2015 and 2025.
Reportable finding: The Zingaro Nature Reserve has experienced three major wildfires since 2015. Of these, the 2025 fire burned a larger area within the reserve than those recorded in 2020 and 2017.
The tools and methods in this guide can be applied to wildfires in many other regions. By combining satellite imagery with environmental and historical datasets, it’s possible to move beyond detection and begin to quantify a fire’s impact. In doing so, you can also place individual incidents in context, revealing whether they are part of a recurring pattern or an unusually severe event.
Merel Zoet and Claire Press contributed to this report.
This guide contains modified Copernicus Sentinel data (2025), processed with Copernicus Browser, as well as data from the European Forest Fire Information System (EFFIS) of the European Commission Joint Research Centre.
Bellingcat is a non-profit and the ability to carry out our work is dependent on the kind support of individual donors. If you would like to support our work, you can do so here. You can also subscribe to our Patreon channel here. Subscribe to our Newsletter and follow us on Bluesky here, Instagram here, Reddit here and YouTube here.
Support Bellingcat
Your donations directly contribute to our ability to publish groundbreaking investigations and uncover wrongdoing around the world.
Our first story of 2026 revealed how a destructive new botnet called Kimwolf has infected more than two million devices by mass-compromising a vast number of unofficial Android TV streaming boxes. Today, we’ll dig through digital clues left behind by the hackers, network operators and services that appear to have benefitted from Kimwolf’s spread.
On Dec. 17, 2025, the Chinese security firm XLab published a deep dive on Kimwolf, which forces infected devices to participate in distributed denial-o
Our first story of 2026 revealed how a destructive new botnet called Kimwolf has infected more than two million devices by mass-compromising a vast number of unofficial Android TV streaming boxes. Today, we’ll dig through digital clues left behind by the hackers, network operators and services that appear to have benefitted from Kimwolf’s spread.
On Dec. 17, 2025, the Chinese security firm XLab published a deep dive on Kimwolf, which forces infected devices to participate in distributed denial-of-service (DDoS) attacks and to relay abusive and malicious Internet traffic for so-called “residential proxy” services.
The software that turns one’s device into a residential proxy is often quietly bundled with mobile apps and games. Kimwolf specifically targeted residential proxy software that is factory installed on more than a thousand different models of unsanctioned Android TV streaming devices. Very quickly, the residential proxy’s Internet address starts funneling traffic that is linked to ad fraud, account takeover attempts and mass content scraping.
The XLab report explained its researchers found “definitive evidence” that the same cybercriminal actors and infrastructure were used to deploy both Kimwolf and the Aisuru botnet — an earlier version of Kimwolf that also enslaved devices for use in DDoS attacks and proxy services.
XLab said it suspected since October that Kimwolf and Aisuru had the same author(s) and operators, based in part on shared code changes over time. But it said those suspicions were confirmed on December 8 when it witnessed both botnet strains being distributed by the same Internet address at 93.95.112[.]59.
Image: XLab.
RESI RACK
Public records show the Internet address range flagged by XLab is assigned to Lehi, Utah-based Resi Rack LLC. Resi Rack’s website bills the company as a “Premium Game Server Hosting Provider.” Meanwhile, Resi Rack’s ads on the Internet moneymaking forum BlackHatWorld refer to it as a “Premium Residential Proxy Hosting and Proxy Software Solutions Company.”
Resi Rack co-founder Cassidy Hales told KrebsOnSecurity his company received a notification on December 10 about Kimwolf using their network “that detailed what was being done by one of our customers leasing our servers.”
“When we received this email we took care of this issue immediately,” Hales wrote in response to an email requesting comment. “This is something we are very disappointed is now associated with our name and this was not the intention of our company whatsoever.”
The Resi Rack Internet address cited by XLab on December 8 came onto KrebsOnSecurity’s radar more than two weeks before that. Benjamin Brundage is founder of Synthient, a startup that tracks proxy services. In late October 2025, Brundage shared that the people selling various proxy services which benefitted from the Aisuru and Kimwolf botnets were doing so at a new Discord server called resi[.]to.
On November 24, 2025, a member of the resi-dot-to Discord channel shares an IP address responsible for proxying traffic over Android TV streaming boxes infected by the Kimwolf botnet.
When KrebsOnSecurity joined the resi[.]to Discord channel in late October as a silent lurker, the server had fewer than 150 members, including “Shox” — the nickname used by Resi Rack’s co-founder Mr. Hales — and his business partner “Linus,” who did not respond to requests for comment.
Other members of the resi[.]to Discord channel would periodically post new IP addresses that were responsible for proxying traffic over the Kimwolf botnet. As the screenshot from resi[.]to above shows, that Resi Rack Internet address flagged by XLab was used by Kimwolf to direct proxy traffic as far back as November 24, if not earlier. All told, Synthient said it tracked at least seven static Resi Rack IP addresses connected to Kimwolf proxy infrastructure between October and December 2025.
Neither of Resi Rack’s co-owners responded to follow-up questions. Both have been active in selling proxy services via Discord for nearly two years. According to a review of Discord messages indexed by the cyber intelligence firm Flashpoint, Shox and Linus spent much of 2024 selling static “ISP proxies” by routing various Internet address blocks at major U.S. Internet service providers.
In February 2025, AT&T announced that effective July 31, 2025, it would no longer originate routes for network blocks that are not owned and managed by AT&T (other major ISPs have since made similar moves). Less than a month later, Shox and Linus told customers they would soon cease offering static ISP proxies as a result of these policy changes.
Shox and Linux, talking about their decision to stop selling ISP proxies.
DORT & SNOW
The stated owner of the resi[.]to Discord server went by the abbreviated username “D.” That initial appears to be short for the hacker handle “Dort,” a name that was invoked frequently throughout these Discord chats.
Dort’s profile on resi dot to.
This “Dort” nickname came up in KrebsOnSecurity’s recent conversations with “Forky,” a Brazilian man who acknowledged being involved in the marketing of the Aisuru botnet at its inception in late 2024. But Forky vehemently denied having anything to do with a series of massive and record-smashing DDoS attacks in the latter half of 2025 that were blamed on Aisuru, saying the botnet by that point had been taken over by rivals.
Forky asserts that Dort is a resident of Canada and one of at least two individuals currently in control of the Aisuru/Kimwolf botnet. The other individual Forky named as an Aisuru/Kimwolf botmaster goes by the nickname “Snow.”
On January 2 — just hours after our story on Kimwolf was published — the historical chat records on resi[.]to were erased without warning and replaced by a profanity-laced message for Synthient’s founder. Minutes after that, the entire server disappeared.
Later that same day, several of the more active members of the now-defunct resi[.]to Discord server moved to a Telegram channel where they posted Brundage’s personal information, and generally complained about being unable to find reliable “bulletproof” hosting for their botnet.
Hilariously, a user by the name “Richard Remington” briefly appeared in the group’s Telegram server to post a crude “Happy New Year” sketch that claims Dort and Snow are now in control of 3.5 million devices infected by Aisuru and/or Kimwolf. Richard Remington’s Telegram account has since been deleted, but it previously stated its owner operates a website that caters to DDoS-for-hire or “stresser” services seeking to test their firepower.
BYTECONNECT, PLAINPROXIES, AND 3XK TECH
Reports from both Synthient and XLab found that Kimwolf was used to deploy programs that turned infected systems into Internet traffic relays for multiple residential proxy services. Among those was a component that installed a software development kit (SDK) called ByteConnect, which is distributed by a provider known as Plainproxies.
ByteConnect says it specializes in “monetizing apps ethically and free,” while Plainproxies advertises the ability to provide content scraping companies with “unlimited” proxy pools. However, Synthient said that upon connecting to ByteConnect’s SDK they instead observed a mass influx of credential-stuffing attacks targeting email servers and popular online websites.
A search on LinkedIn finds the CEO of Plainproxies is Friedrich Kraft, whose resume says he is co-founder of ByteConnect Ltd. Public Internet routing records show Mr. Kraft also operates a hosting firm in Germany called 3XK Tech GmbH. Mr. Kraft did not respond to repeated requests for an interview.
In July 2025, Cloudflare reported that 3XK Tech (a.k.a. Drei-K-Tech) had become the Internet’s largest source of application-layer DDoS attacks. In November 2025, the security firm GreyNoise Intelligencefound that Internet addresses on 3XK Tech were responsible for roughly three-quarters of the Internet scanning being done at the time for a newly discovered and critical vulnerability in security products made by Palo Alto Networks.
Source: Cloudflare’s Q2 2025 DDoS threat report.
LinkedIn has a profile for another Plainproxies employee, Julia Levi, who is listed as co-founder of ByteConnect. Ms. Levi did not respond to requests for comment. Her resume says she previously worked for two major proxy providers: Netnut Proxy Network, and Bright Data.
Synthient likewise said Plainproxies ignored their outreach, noting that the Byteconnect SDK continues to remain active on devices compromised by Kimwolf.
A post from the LinkedIn page of Plainproxies Chief Revenue Officer Julia Levi, explaining how the residential proxy business works.
MASKIFY
Synthient’s January 2 report said another proxy provider heavily involved in the sale of Kimwolf proxies was Maskify, which currently advertises on multiple cybercrime forums that it has more than six million residential Internet addresses for rent.
Maskify prices its service at a rate of 30 cents per gigabyte of data relayed through their proxies. According to Synthient, that price range is insanely low and is far cheaper than any other proxy provider in business today.
“Synthient’s Research Team received screenshots from other proxy providers showing key Kimwolf actors attempting to offload proxy bandwidth in exchange for upfront cash,” the Synthient report noted. “This approach likely helped fuel early development, with associated members spending earnings on infrastructure and outsourced development tasks. Please note that resellers know precisely what they are selling; proxies at these prices are not ethically sourced.”
Maskify did not respond to requests for comment.
The Maskify website. Image: Synthient.
BOTMASTERS LASH OUT
Hours after our first Kimwolf story was published last week, the resi[.]to Discord server vanished, Synthient’s website was hit with a DDoS attack, and the Kimwolf botmasters took to doxing Brundage via their botnet.
The harassing messages appeared as text records uploaded to the Ethereum Name Service (ENS), a distributed system for supporting smart contracts deployed on the Ethereum blockchain. As documented by XLab, in mid-December the Kimwolf operators upgraded their infrastructure and began using ENS to better withstand the near-constant takedown efforts targeting the botnet’s control servers.
An ENS record used by the Kimwolf operators taunts security firms trying to take down the botnet’s control servers. Image: XLab.
By telling infected systems to seek out the Kimwolf control servers via ENS, even if the servers that the botmasters use to control the botnet are taken down the attacker only needs to update the ENS text record to reflect the new Internet address of the control server, and the infected devices will immediately know where to look for further instructions.
“This channel itself relies on the decentralized nature of blockchain, unregulated by Ethereum or other blockchain operators, and cannot be blocked,” XLab wrote.
The text records included in Kimwolf’s ENS instructions can also feature short messages, such as those that carried Brundage’s personal information. Other ENS text records associated with Kimwolf offered some sage advice: “If flagged, we encourage the TV box to be destroyed.”
An ENS record tied to the Kimwolf botnet advises, “If flagged, we encourage the TV box to be destroyed.”
Both Synthient and XLabs say Kimwolf targets a vast number of Android TV streaming box models, all of which have zero security protections, and many of which ship with proxy malware built in. Generally speaking, if you can send a data packet to one of these devices you can also seize administrative control over it.
If you own a TV box that matches one of these model names and/or numbers, please just rip it out of your network. If you encounter one of these devices on the network of a family member or friend, send them a link to this story (or to our January 2 story on Kimwolf) and explain that it’s not worth the potential hassle and harm created by keeping them plugged in.
KrebsOnSecurity.com celebrates its 16th anniversary today! A huge “thank you” to all of our readers — newcomers, long-timers and drive-by critics alike. Your engagement this past year here has been tremendous and truly a salve on a handful of dark days. Happily, comeuppance was a strong theme running through our coverage in 2025, with a primary focus on entities that enabled complex and globally-dispersed cybercrime services.
Image: Shutterstock, Younes Stiller Kraske.
In May 2024, we scrutinize
KrebsOnSecurity.com celebrates its 16th anniversary today! A huge “thank you” to all of our readers — newcomers, long-timers and drive-by critics alike. Your engagement this past year here has been tremendous and truly a salve on a handful of dark days. Happily, comeuppance was a strong theme running through our coverage in 2025, with a primary focus on entities that enabled complex and globally-dispersed cybercrime services.
Image: Shutterstock, Younes Stiller Kraske.
In May 2024, we scrutinized the history and ownership of Stark Industries Solutions Ltd., a “bulletproof hosting” provider that came online just two weeks before Russia invaded Ukraine and served as a primary staging ground for repeated Kremlin cyberattacks and disinformation efforts. A year later, Stark and its two co-owners were sanctioned by the European Union, but our analysis showed those penalties have done little to stop the Stark proprietors from rebranding and transferring considerable network assets to other entities they control.
In December 2024, KrebsOnSecurity profiled Cryptomus, a financial firm registered in Canada that emerged as the payment processor of choice for dozens of Russian cryptocurrency exchanges and websites hawking cybercrime services aimed at Russian-speaking customers. In October 2025, Canadian financial regulators ruled that Cryptomus had grossly violated its anti-money laundering laws, and levied a record $176 million fine against the platform.
In September 2023, KrebsOnSecurity published findings from researchers who concluded that a series of six-figure cyberheists across dozens of victims resulted from thieves cracking master passwords stolen from the password manager service LastPass in 2022. In a court filing in March 2025, U.S. federal agents investigating a spectacular $150 million cryptocurrency heist said they had reached the same conclusion.
Phishing was a major theme of this year’s coverage, which peered inside the day-to-day operations of several voice phishing gangs that routinely carried out elaborate, convincing, and financially devastating cryptocurrency thefts. A Day in the Life of a Prolific Voice Phishing Crew examined how one cybercrime gang abused legitimate services at Apple and Google to force a variety of outbound communications to their users, including emails, automated phone calls and system-level messages sent to all signed-in devices.
In January, we highlighted research into a dodgy and sprawling content delivery network called Funnull that specialized in helping China-based gambling and money laundering websites distribute their operations across multiple U.S.-based cloud providers. Five months later, the U.S. government sanctioned Funnull, identifying it as a top source of investment/romance scams known as “pig butchering.”
In April, the U.S. Department of Justice indicted the proprietors of a Pakistan-based e-commerce company for conspiring to distribute synthetic opioids in the United States. The following month, KrebsOnSecurity detailed how the proprietors of the sanctioned entity are perhaps better known for operating an elaborate and lengthy scheme to scam westerners seeking help with trademarks, book writing, mobile app development and logo designs.
In June, KrebsOnSecurity.com was hit by the largest DDoS attack that Google had ever mitigated at the time (we are a grateful guest of Google’s excellent Project Shield offering). Experts blamed that attack on an Internet-of-Things botnet called Aisuru that had rapidly grown in size and firepower since its debut in late 2024. Another Aisuru attack on Cloudflare just days later practically doubled the size of the June attack against this website. Not long after that, Aisuru was blamed for a DDoS that again doubled the previous record.
In October, it appeared the cybercriminals in control of Aisuru had shifted the botnet’s focus from DDoS to a more sustainable and profitable use: Renting hundreds of thousands of infected Internet of Things (IoT) devices to proxy services that help cybercriminals anonymize their traffic.
However, it has recently become clear that at least some of the disruptive botnet and residential proxy activity attributed to Aisuru last year likely was the work of people responsible for building and testing a powerful botnet known as Kimwolf. Chinese security firm XLab, which was the first to chronicle Aisuru’s rise in 2024, recently profiled Kimwolf as easily the world’s biggest and most dangerous collection of compromised machines — with approximately 1.83 million devices under its thumb as of December 17.
XLab noted that the Kimwolf author “shows an almost ‘obsessive’ fixation on the well-known cybersecurity investigative journalist Brian Krebs, leaving easter eggs related to him in multiple places.”
Image: XLab, Kimwolf Botnet Exposed: The Massive Android Botnet with 1.8 million infected devices.
I am happy to report that the first KrebsOnSecurity stories of 2026 will go deep into the origins of Kimwolf, and examine the botnet’s unique and highly invasive means of spreading digital disease far and wide. The first in that series will include a somewhat sobering and global security notification concerning the devices and residential proxy services that are inadvertently helping to power Kimwolf’s rapid growth.
Thank you once again for your continued readership, encouragement and support. If you like the content we publish at KrebsOnSecurity.com, please consider making an exception for our domain in your ad blocker. The ads we run are limited to a handful of static images that are all served in-house and vetted by me (there is no third-party content on this site, period). Doing so would help further support the work you see here almost every week.
And if you haven’t done so yet, sign up for our email newsletter! (62,000 other subscribers can’t be wrong, right?). The newsletter is just a plain text email that goes out the moment a new story is published. We send between one and two emails a week, we never share our email list, and we don’t run surveys or promotions.
Thanks again, and Happy New Year everyone! Be safe out there.
Key Takeaways Private Threat Briefs: 20+ private DFIR reports annually. Contact us today for pricing or a demo! Table of Contents: Case Summary Analysts Initial Access Execution Persistence Privilege Escalation Defense Evasion Credential Access Discovery Lateral Movement Command and Control Exfiltration Impact Timeline Diamond Model Indicators Detections MITRE ATT&CK Case Summary The intrusion […]
The post From a Single Click: How Lunar Spider Enabled a Near Two-Month Intrusion appeare
Key Takeaways Private Threat Briefs: 20+ private DFIR reports annually. Contact us today for pricing or a demo! Table of Contents: Case Summary Analysts Initial Access Execution Persistence Privilege Escalation Defense Evasion Credential Access Discovery Lateral Movement Command and Control Exfiltration Impact Timeline Diamond Model Indicators Detections MITRE ATT&CK Case Summary The intrusion […]
A month or so ago a friend of mine received the following message on Steam from someone in their Friends list (they were already friends):Figure 1 - 'this is for you' The two links are different and refer to a Gift Card on Steam's community platform. As you might have noticed, the domain is not related to Steam at all, but rather is an attempt at phishing. The URLs are:stermcormmunity[.]com/gift-card/steamcoummuniity[.]com/gift-card/The differences are subtle enough that you may j
A month or so ago a friend of mine received the following message on Steam from someone in their Friends list (they were already friends):
Figure 1 - 'this is for you'
The two links are different and refer to a Gift Card on Steam's community platform. As you might have noticed, the domain is not related to Steam at all, but rather is an attempt at phishing.
The differences are subtle enough that you may just miss it. When you click on the link, you are redirected to a 'Summer Gift Marathon'.
Figure 2 - Fake Steam website
Once you log in to the fake Steam website, your credentials are stolen and will be used to spread more phishing, likely steal your inventory items and so on.
Other phishing sites related to this campaign are:
New ones do pop up from time to time, so stay vigilant.
Tips
Only log in on the legitimate Steam community website, this being https://steamcommunity.com/. An extra tip is to bookmark the legitimate site, so even if you do get a message like this, you can go straight to your bookmark and search what you need from there.
If someone new tries to add you as a Friend and immediately sends a message like the above, alarm bells should start ringing.
If someone already on your Friends list suddenly sends a random message with an even more random link out of the blue, cue the alarm bells again.
If you want to check the website out in a safe manner, then you can use URLscan.io, which will give you a verdict of the website as well as an image preview. In addition, you can use VirusTotal to review a website's reputation.
Note that an 'all clean' does not necessarily mean it is. Caution above all!
Follow Steam's Account Security Recommendations to stay safe.
One of the challenges with investigating cybercrime is the
infrastructure the adversaries leverage to conduct attacks. Cybercriminal
infrastructure has evolved drastically over the last 25 years, which now involves
hijacking web services, content distribution networks (CDNs), residential
proxies, fast flux DNS, domain generation algorithms (DGAs), botnets of IoT
devices, the Tor network, and all sorts of nested services.
This blog shall investigate a small UK-based hosting provider
known as Bit
One of the challenges with investigating cybercrime is the
infrastructure the adversaries leverage to conduct attacks. Cybercriminal
infrastructure has evolved drastically over the last 25 years, which now involves
hijacking web services, content distribution networks (CDNs), residential
proxies, fast flux DNS, domain generation algorithms (DGAs), botnets of IoT
devices, the Tor network, and all sorts of nested services.
This blog shall investigate a small UK-based hosting provider
known as BitLaunch as an example of how challenging it can be to tackle
cybercriminal infrastructure. Research into this hosting provider revealed that
they appear to have a multi-year history of cybercriminals using BitLaunch to
host command-and-control (C2) servers via their Anonymous
VPS service.
The year-on-year growing number of CobaltStrike C2 servers
hosted on BitLaunch’s services could be an indicator of tacit collusion with
cybercriminals through the facilitation of cheap and quick to procurement of
VPSs that end up being used to launch ransomware attacks on all sorts of
victims, including hospitals, schools, governments, companies, and charities.
The concept of aiding and abetting criminal activity in law is
essentially when an individual or an organisation intentionally assists,
facilitates, or encourages a crime. In this case, it would be aiding and
abetting the creation of cybercriminal infrastructure. If a hosting provider
ignores clear red flags (e.g., cryptocurrency payments from known illicit
sources or use of servers for illegal activities), they might still be held criminally
liable under wilful blindness under certain laws.
In the past, authorities have taken down bulletproof hosting
(BPH) providers that knowingly support cybercrime, such as CyberBunker and
LolekHost. In February 2025, the UK government also sanctioned
a Russia-based BPH known as ZSERVERS (aka XHOST) for facilitating LockBit
attacks.
Update: This blog was updated with a statement from BitLaunch (see the end of this blog).
Who is BitLaunch aka BL Networks aka BLNWX?
Active since at least 2017, BitLaunch (also known as BL
Networks or BLNWX) is a virtual private server (VPS) reseller whose autonomous
system number (ASN) is AS399629.
Up to 48 IPv4 networks belong to BitLaunch
which are used to "instantly launch a Linux or Windows VPS” where
customers can “pay hourly with Bitcoin, Litecoin, and Ethereum, with no firm
commitments." BitLaunch also supports their customers via a command-line (CLI)
tool and a Python
library. BitLaunch has another name, however, in their legal terms and conditions
they go by Liber Systems and have their own separate website.
Why focus on BitLaunch?
BitLaunch is quite interesting as they present themselves as
a UK-based company run by two local UK businessmen. Their “anonymous Bitcoin
VPS” service is regularly abused for all sorts of cybercriminal activities. What
triggered this research was the fact that their nickname “BLNWX” was regularly
reappearing in cyber threat intelligence (CTI) vendor reports on ransomware and
other cybercriminal campaigns. It is also worth highlighting that while BitLaunch own their
own IP networks, they are a VPS reseller as well who works with DigitalOcean,
Linode, and Vultr, as shown from their website below.
One website that reviews so-called “offshore services” (offshore[.]cat) has listed BitLaunch as being a “verified” offshore hoster that accepts cryptocurrency, only requires email request confirmation to open an account, and is described as allowing anyone to “create VPSs in seconds, using crypto” making them an attractive hoster for cybercriminals. Their service paired with their CLI tools and Python libraries makes it super easy to stand up C2 servers rapidly.
Command and Control (C2) infrastructure on BLNWX
Significant numbers of CobaltStrike C2s among other hacking
tools and malware families have been discovered on BitLaunch. I would like to
thank the owner of the C2IntelFeedsBot (@drb_ra)
account on X/Twitter who assisted with this research by providing their feed of
C2 servers discovered on BitLaunch.
The image below shows a sampling of the known C2 servers
hosted with BitLaunch between 2021 and 2025. The most notable part of this
diagram is the number of CobaltStrike C2 servers in particular. Cobalt Strike
is a well-known C2 framework used by organised cybercriminal groups to launch
ransomware attacks. It is also favoured by state-sponsored threat groups as
well.
Over the last few years, several dozen C2 servers have been
identified by the C2IntelFeedsBot and each
year, the number of C2s has continued to grow as more cybercriminals identify
BitLaunch as a preferable service to support their ransomware campaigns.
The image below displays the totals calculated between “2021-06-26
12:33:41" and "2025-02-05 18:46:10." It is not a complete
picture by any means, but this independently verifiable data gives a decent
idea of the rate at which BitLaunch is being used by cybercriminals, with each
year since 2022 has trended upwards.
One of the interesting things about CobaltStrike is that it
is a commercial offensive security tool (OST). It is issued to legitimate
customers through licenses, which have a unique watermark. While there have
been several cracked versions of CobaltStrike over the years, it is possible to
track certain groups through their usage of the same CobaltStrike versions.
The image below shows the distribution of the CobaltStrike
watermarks gathered from BitLaunch. Notably, “0” is the most common. This is
often the case when analysing CobaltStrike watermarks as this signifies it is
the cracked version.
OSINT collection and analysis of the CobaltStrike watermarks
revealed potential connections to several well-known cybercriminal groups using
BitLaunch who have a history of conducting ransomware attacks:
"426352781” – This watermark is used by ShadowSyndicate,
a ransomware affiliate group tracked by Group-IB which is connected to multiple
Ransomware-as-a-Serivce (Raas) platforms. This watermark is also historically associated
with CobaltStrike Beacons dropped
by the Qakbot malware botnet.
“1580103824” – This watermark was linked to ShadowSyndicate
as well, alongside the Cleo
exploitation campaign attributed CL0P ransomware. A threat group tracked by
CERT-UA as UAC-0056 has also been observed
using this watermark too.
”987654321” – This watermark has been associated
with the IcedID malware botnet and the Dagon Locker ransomware gang previously.
”1359593325” – This watermark has been used by CobaltStrike
Beacons in campaigns attributed
to the Russian Foreign Intelligence Service (SVR)
“391144938” and “305419896” – These watermarks have been
attributed to campaigns by multiple Chinese cyber-espionage campaigns tracked
by SentinelOne,
Recorded
Future, Zscaler,
and Cisco
Talos.
C2s on BLNWX attributed to Ransomware Gangs by CTI vendors
There are a number of CTI reports over the last couple years
that directly reference BitLaunch Networks (BLNWX) IP addresses as Indicators
of Compromise (IOCs) as part of high-profile ransomware campaigns.
This includes attribution
to the Yanluowang ransomware attack against Cisco, a C2 linked
to the JavaScript more_eggs backdoor used by FIN6 (who is connected to
ransomware campaigns), a dozen IPs attributed to Rhysida
ransomware attacks, and a Rhysida and Interlock ransomware precursor
campaign tracked as TAG-124,
as well as the PaperCut
exploitation campaign which involved
both LockBit and CL0P.
Additional notable CTI alerts that called out BLNWX include
a report on Latrodectus,
a ransomware precursor campaign, by Proofpoint; Okta-themed phishing campaigns
attributed to Scattered
Spider, who has carried out ALPHV/BlackCat and RansomHub attacks, by
Intel471; infrastructure used to enable
the BlackBasta ransomware gang by QuadrantSec, as well as C2 servers of the IcedID
malware botnet that has been used by ransomware gangs for initial access.
Assessment of BitLaunch
As of February 2025, BitLaunch's parent firm Liber Systems Limited is run by two UK-based directors according to UK Companies House. While they are profiting off this Anonymous VPS service they are not taking the appropriate steps to prevent their service from being used by
ransomware and malware gangs. Organised cybercrime groups have evidently found and recognised this about BitLaunch and are leveraging the cheap, crypto-accepting service
that doesn’t ask too many questions.
To be fair to BitLaunch, they appear to be responsive to
takedowns and are noted on Offshore[.]cat as enforcing DMCA requests. The crux
of the issue though is that the cybercriminals can use their service to rapidly
spin up instances for C2 for a few hours and chuck it away again. This means there often no need to submit a takedown as the cybercriminals has already abandoned the C2 and can spin up another one. Therefore,
the cybercriminals can continually leverage BitLaunch without interference.
As a security researcher, and not a police officer, I cannot comment on how cooperative BitLaunch have been with the police and it is probably not something BitLaunch would want to advertise to their customers anyway based on who some of their customers are.
For BitLaunch’s two directors, this works out nicely for them. They
can take the cybercriminals money via cryptocurrency and also appear to be
ethical and compliant by assisting with law enforcement takedown requests. Currently, they appear to be helping both the criminals and the police, and have been getting away with it for years.
On BitLaunch’s front page advertisement they highlight as
the main focus as being able to pay hourly for the use VPS and that customers
can pay in “anonymous cryptocurrency.” It is in my opinion, and that of other
cybersecurity researchers I have spoken to about this (including red teamers and penetration testers), that
this service is perfect for C2 servers and almost nothing else legitimate.
The Broader Issue with Anonymous VPSs
In BitLaunch’s blogs, they say they believe the internet should be "open, free, and devoid of interference by any single government or authority" adding that accept cryptocurrency because "citizens of some countries do not have bank accounts and can use Bitcoin
instead" because the local banks have control over who their citizens can send money to.
Their blogs also state that they believe internet users should be allowed to
run their own virtual private networks (VPNs) for anti-surveillance and privacy
reasons. They also provide lots of guides on how to configure private VPNs for this purpose. While this is a legitimate service that is useful for some people in specific situations, having it be abused by ransomware gangs is a situation that needs to be changed.
This issue of selling anonymous VPSs is not specific to this one company. BitLaunch is
obviously a small company and proactively combating cybercriminals from
registering VPSs on their service is an expensive and multi-pronged challenge
for any hoster, which includes preventing abuse while preserving the privacy of
their customers.
Hosters such as BitLaunch could use services such as Shodan, Abuse.ch,
GreyNoise, OTX Alienvault, and AbuseIPDB to check if their IP addresses are
being abused. One interesting example of a hoster trying to tackle this issue is how PQ Hosting (aka Stark Industries Solutions) announced publicly on their blog that they have partnered with Team Cymru, a netflow security intelligence firm. Alternatively, hosters could use a blockchain analytics platform like Chainalysis, TRM Labs, or Arkham Intelligence, to trace cryptocurrency payments from known illicit wallet clusters.
There will, however, always be some threats that slip through the net. It is undoubtedly a difficult challenge for small hosters
who do not have funds to sacrifice on network observability tools or CTI
platforms. Even some of the world’s largest hosters, such as Cloudflare
struggle with this as well and end up having their services abused for cybercrime operations.
The anonymous VPS problem could be
compared to issues in other industries such as stolen funds being used to buy gift cards or game keys that are then resold for money laundering. Another platform often
abused for a variety of scams and phishing campaigns is Gmail. Is Google being
wilfully negligent to cybercrime happening on their platform? That’s a question
I shall leave for readers to decide on their own.
Overall, this type of issue is analogous to a hotel offering rooms for the night and organized criminals renting them to commit various types of crimes inside them. Ultimately, the criminals are the ones breaking the law, not the hotel, but if the hotel is being constantly made aware of these activities by bystanders and law enforcement, it is their duty to shut that activity down, to the best of their abilities.
What the UK Could Do About It
In this scenario around BitLaunch, there are three potential ways the UK could help stop these small hosters being taken advantage of by
cybercriminal operations.
Firstly, the cybersecurity and hosting industry could launch an initiative through institutions, such as the British Computer Society (BCS) or something, that would work to convince hosting providers that the
hassle being investigated by law enforcement agencies, sanctions, or the chance
of being arrested is not worth the funds generated from selling C2 servers to cybercriminals.
Secondly, as BitLaunch (or Liber Systems) is registered here, the UK Government Department for Science, Innovation, and Technology (DSIT) could work with them and other small hosters to regulate the industry and
provide support to these businesses to warn them of the dangers of offering
unregulated VPS services and inform them how they contribute to the
damage that ransomware attacks are having on the UK and elsewhere.
Third, providing free network observability services to
hosters could also help them proactively shutdown C2 servers before they are
weaponised against victims. All UK hosters can sign-up to the free UK
government-provided service called MyNCSC, offered by the UK
NCSC, which is part of GCHQ. Hosters will then get alerts when MyNCSC detects
which IPs are flagged for hosting C2 servers (such as CobaltStrike).
As the UK government’s mandate
is to “make the UK the safest place in the world to live and work online” then
tackling the issue with these UK-based hosters supporting ransomware
should also be one of those priorities.
Indicators of Compromise
Historic Malicious BLNWX IP addresses are available below:
Statement from BitLaunch following the publication of this blog:
"BitLaunch appreciates the conversation surrounding the misuse of VPS hosting services. It is an important topic, and there is always room for improvement and reflection. That said, we believe the article contains several key inaccuracies and misleading implications. We take the prevention of abuse on our platform very seriously, and we would like to offer the following context:
We reject the notion that BitLaunch may be in "tacit collusion with cybercriminals" due to the year-on-year growth of IPs associated with CobaltStrike C2 servers. In fact, the number of abusive IPs has not increased relative to BitLaunch's rapid infrastructure growth – it is just that more IP blocks are available overall.
At the time of writing, BitLaunch has 50 /24 prefixes announced over BGP, totalling 12,800 IP addresses. As a result, 82 C2s in 2024 represents just 0.6% of our IPs over the entire year. Across all first and third party hosts, abuse per month is around 1% of active servers.
We strongly disagree that BitLaunch is "not taking the appropriate steps to prevent their service from being used by ransomware and malware gangs". BitLaunch takes regular and concrete action against abuse, including no longer serving the Russian market. We employ a full-time, dedicated abuse team that already uses various tools to proactively and passively identify malicious servers. These tools include abuse.ch, urlscan, spamhaus, and more. Servers are suspended as soon as malicious activity is suspected, per our Acceptable Use policy.
The report implies that BitLaunch may be ignoring key red flags, such as accepting cryptocurrency from known illicit sources, and mentions that hosters can use blockchain analysis services to prevent this. BitLaunch already uses Elliptic for this purpose. We also disagree with the opinion that our service is "perfect for C2 servers and almost nothing else". As previously stated, abuse per month accounts for 1% of active servers despite BitLaunch accepting payments exclusively in cryptocurrency. There are numerous reasons to pay privately with cryptocurrency that do not involve illegal activity.
We believe the report fails to disclose a potential conflict of interest. The researcher works for Carrier Hotel Equinix, which serves some of our direct competitors. One such customer, PQ Hosting, is linked in the blog as a positive example of dealing with malicious activity.
Finally, we would like to thank BushidoToken for giving us a chance to issue this addendum. We welcome constructive critique on this topic and appreciate the opportunity to reflect on our abuse-prevention strategies and their communication."
Introduction to Infrastructure Pivoting
Pivoting on infrastructure is a handy skill for cyber threat
intelligence (CTI) analysts to learn. It can help to reveal the bigger picture
when it comes to malware, phishing, or network exploitation campaigns. Infrastructure
pivoting essentially is the act of looking for more systems an adversary has
created. The main benefit of this pursuit is the identification of additional
targets or victims, more tools or malware samples, and ultimately new insigh
Pivoting on infrastructure is a handy skill for cyber threat
intelligence (CTI) analysts to learn. It can help to reveal the bigger picture
when it comes to malware, phishing, or network exploitation campaigns. Infrastructure
pivoting essentially is the act of looking for more systems an adversary has
created. The main benefit of this pursuit is the identification of additional
targets or victims, more tools or malware samples, and ultimately new insights
about the adversary’s capabilities.
If done correctly, being able to pivot on adversary
infrastructure will be very useful during incident response (IR) engagements. For
example, it may lead to being able to attribute the intrusion to a known
adversary. This will help others during an IR engagement understand the level
of threat posed to the victim organisation.
Receiving Threat Data
To be able to pivot on adversary infrastructure, threat data
is needed such as the intelligence shared by threat reports put out
by various researchers from public and private sector organisations. This
scenario, however, involves relying on the analysis skills of other researchers to explain
what the infrastructure is and when they observed it in use.
This blog will examine threat data provided by public sector
organisations such as the Computer Emergency Response Team of Ukraine (CERT-UA)
as well as cybersecurity vendors such as Deep Instinct, Cyble, and Fortinet.
These organisations have shared indicators of compromise (IOCs) uncovered
following analysis of adversary intrusion activities or upload to online
malware sandboxes, such as VirusTotal, among others.
Introduction to the Ghostwriter Campaign
On 3 June 2024, Fortinet shared a report
on malicious XLS macro documents leading to Cobalt Strike Beacons. Analysis of
the XLS documents showed that they appeared to be targeting the Ukrainian
military and linked to a known Belarusian state-sponsored APT group tracked as Ghostwriter
(aka UNC1151, UAC-0057, TA445). On 4 June 2024, Cyble also shared a report
on a similar campaign.
In both reports, if the XLS was opened and the macros were executed
by the target, a malicious DLL file was downloaded from an adversary-created domain.
In Fortinet’s report, two similar “.shop” domains were mentioned. In Cyble’s
report another “.shop” domain was also called out.
Overlapping IOCs
The first pivot on Ghostwriter APT infrastructure that will be
demonstrated involves finding indicators of compromise (IOCs) such as domains
and IP addresses that appear in multiple threat reports.
The fastest way to realize these overlaps is through
continuous collection of reported IOCs into a Threat Intelligence Platform
(TIP). This will reveal IOCs that appear in multiple threat reports through
tagging and sources of where IOCs come from. Eventually, one domain or IP
address will get reported by multiple entities and the connection will make
itself apparent.
In Figure 1 (see below) the domain “goudieelectric[.]shop”
appeared in both Cyble’s blog and Fortinet’s blog. Analysis of all three
domains found that they use the same generic top-level domain (gTLD),
registrar, and name servers, as well as have a robots.txt directory configured.
These common infrastructure characteristics indicate that all three domains
were created by the same adversary.
Figure 1. Three similar
domains appearing in two threat reports.
Domain Registration & Hosting Overlaps
When more IOCs are reported in other threat reports it is
possible to link them to other known domains, this is due to adversaries
reusing the same registrars, name servers, and gTLDs.
In Figure 2 (see below), Deep Instinct reported
two more domains that could also be linked to the previous three domains through
the mutual use of the PublicDomainsRegistry registrar, Cloudflare name servers,
and the robots.txt file.
Figure 2. Five
similar domains that appear across three threat reports.
Further, CERT-UA reported three more domains (see
Figure 3 below) that could be linked to the infrastructure cluster through this
same method as well. This pattern of behaviour is a strong indicator that these
domains were created by the same adversary.
Figure 3. Eight similar domains that appear across four threat reports.
Finding Unreported Domains
Since the domains from the above threat reports were
collected and linked together through overlapping attributes, it is now
possible to use these attributes to find more domains that had gone unreported.
Using a VirusTotal domain attribute query, additional domains
can be found by using the following registration pattern:
Name Servers: CLOUDFLARE
Registrar: PublicDomainRegistry
TLD: *.shop
This revealed up to 24 domains that matched this pattern
that were likely created by Ghostwriter, a state-sponsored APT group:
backstagemerch[.]shop
bryndonovan[.]shop
chaptercheats[.]shop
clairedeco[.]shop
connecticutchildrens[.]shop
disneyfoodblog[.]shop
eartheclipse[.]shop
empoweringparents[.]shop
foampartyhats[.]shop
goudieelectric[.]shop
ikitas[.]shop
jackbenimblekids[.]shop
kingarthurbaking[.]shop
lansdownecentre[.]shop
lauramcinerney[.]shop
medicalnewstoday[.]shop
moonlightmixes[.]shop
penandthepad[.]shop
physio-pedia[.]shop
semanticscholar[.]shop
simonandschuster[.]shop
thevegan8[.]shop
twisterplussize[.]shop
utahsadventurefamily[.]shop
Note: VirusTotal domain searches are only available
to VirusTotal Enterprise users. There are other providers which allow you to search
for domain registration patterns such as DomainTools, Validin, and Zetalytics. There
also some free OSINT sites such as nslookup.io
and viewdns.info that can be useful in
certain scenarios.
Finding Related Malware Samples
Using the list of similar domains that were uncovered
through the registration pattern search, it is then possible to find additional
malware samples communicating with them.
This can be achieved by looking at domains in VirusTotal and
checking the Relations tab can show communicating files as shown in
Figure 4 below.
Figure 4. Additional malware samples
uncovered via the VirusTotal relations tab
Using a VirusTotal graph can help to reveal every
communicating file with every domain discovered through the registration pattern
search, as shown in Figure 5 below.
Figure 5. All
communicating files with every additional domain identified.
In conclusion, it is important for CTI analysts to closer
inspect the attributes of the IOCs they come across. It is not uncommon for
state-sponsored APT groups to make such mistakes when creating their
infrastructure to launch attacks from. By exploiting this fact, CTI analysts
can learn much more about the adversary’s targets, capabilities, and the behaviours
of the humans themselves behind such campaigns.
The importance of this type of work was demonstrated in
December 2023 when the US Treasury
sanctioned members of the Russian APT group known as Callisto
(aka Star Blizzard, BlueCharlie, COLDRIVER, GOSSAMER BEAR). The real world
identity of Andrey Korinets was revealed after he was sanctioned for fraudulently
creating and registering malicious domain infrastructure for Russian federal
security service (FSB) spear phishing campaigns.

 Entrar