❌

Visualização normal

Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates

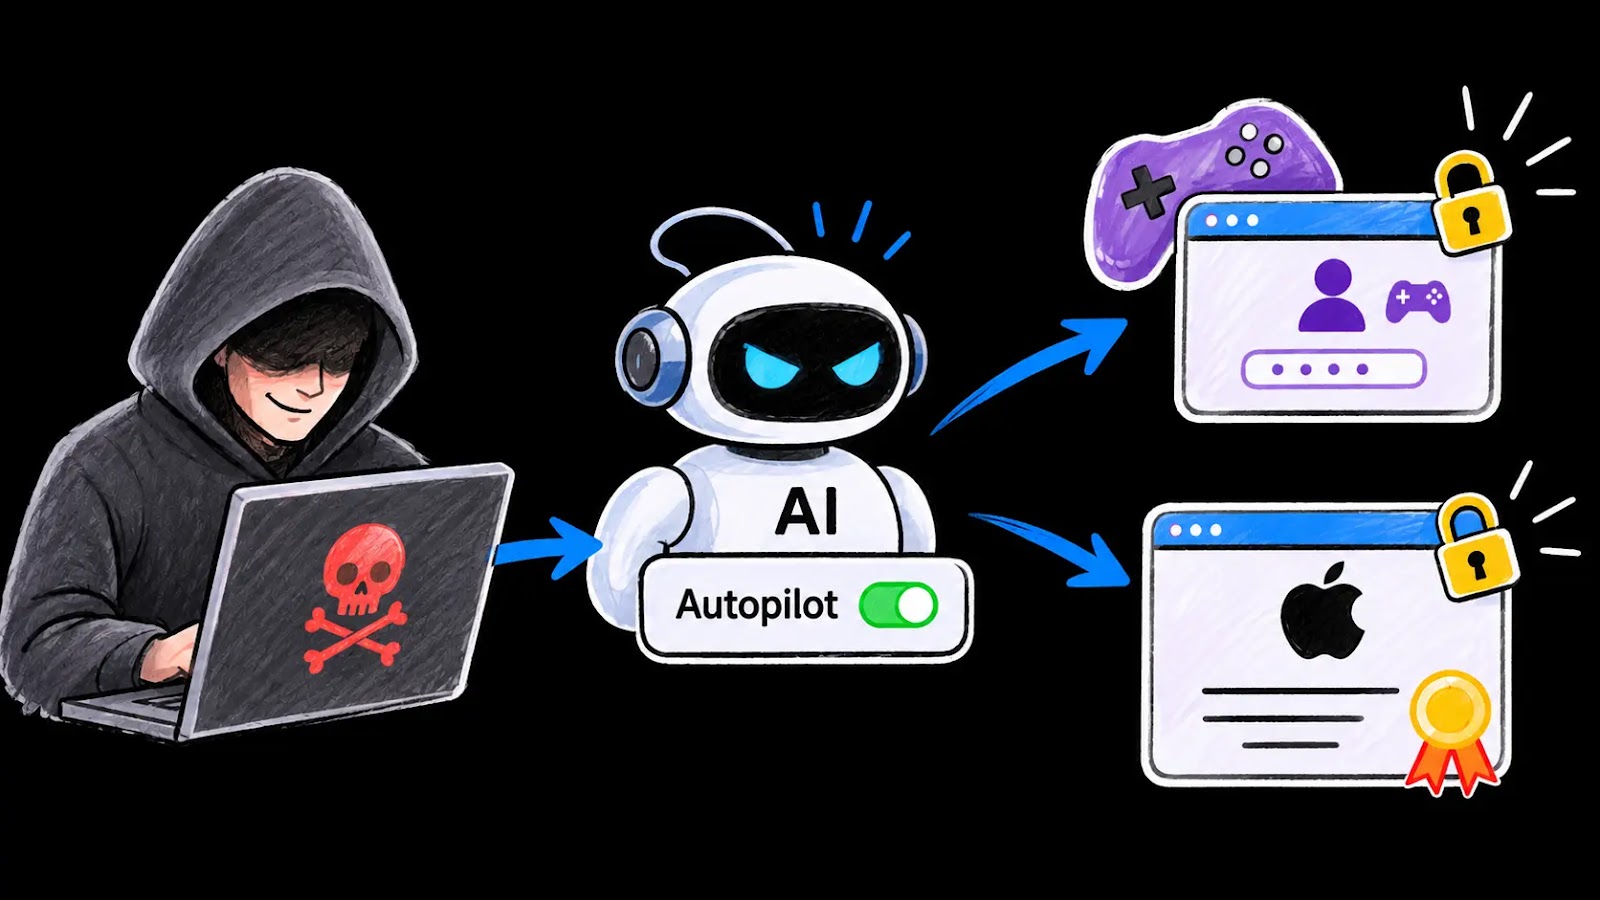
ARTEX, a Chinese open-source agentic penetration-testing platform, to run autonomous attacks. The operators set a goal and then mostly check progress. Researchers identified 2,557 systems that host or hosted ARTEX panels, and 1,608 were live and public. Ten misconfigured instances exposed their full databases. Those databases show the models, prompts and actions behind the campaigns. […]

The post Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers

A design flaw in Anthropic’s Claude Dispatch feature let a malicious browser extension run commands on the operating system, even on a different computer. Researchers at Forever Security named the attack ThisBash. They found that Claude Dispatch accepted instructions from an ordinary logged-in claude.ai session. An extension that could control that site could therefore send […]

The post Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
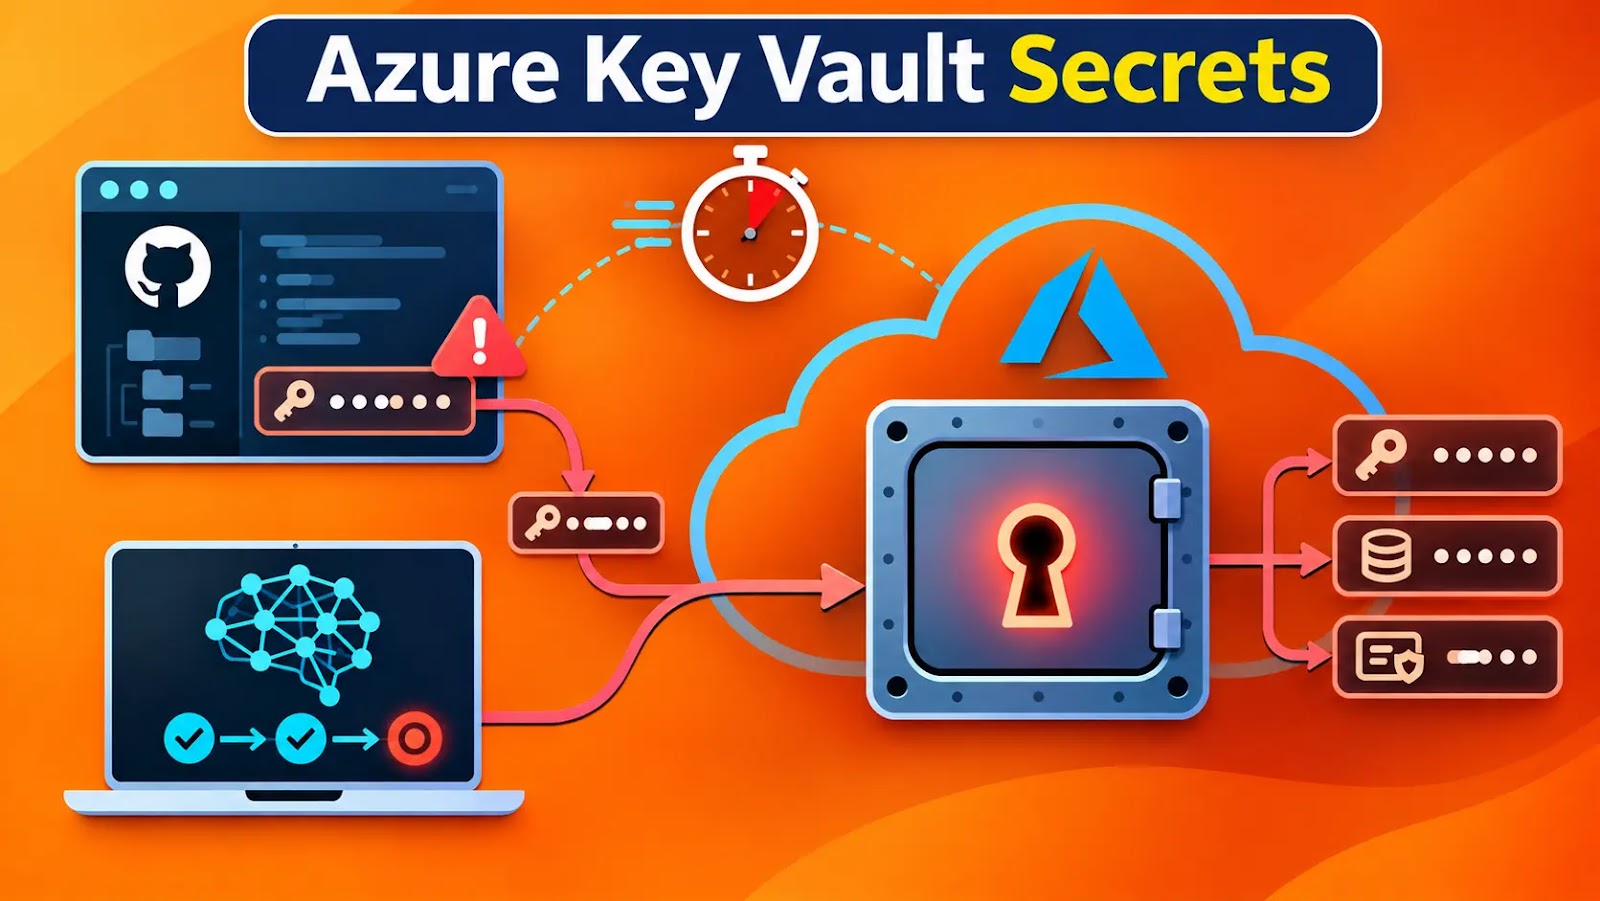
Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials

Attackers using the ARTEX agentic AI framework to discover exposed GitHub credentials and rapidly compromise cloud environments. In one intrusion, an AI agent progressed from searching GitHub for application secrets to exfiltrating Azure Key Vault data in just five minutes. The activity compresses a familiar attack chain: finding leaked credentials, validating access, mapping resources, and […]

The post Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
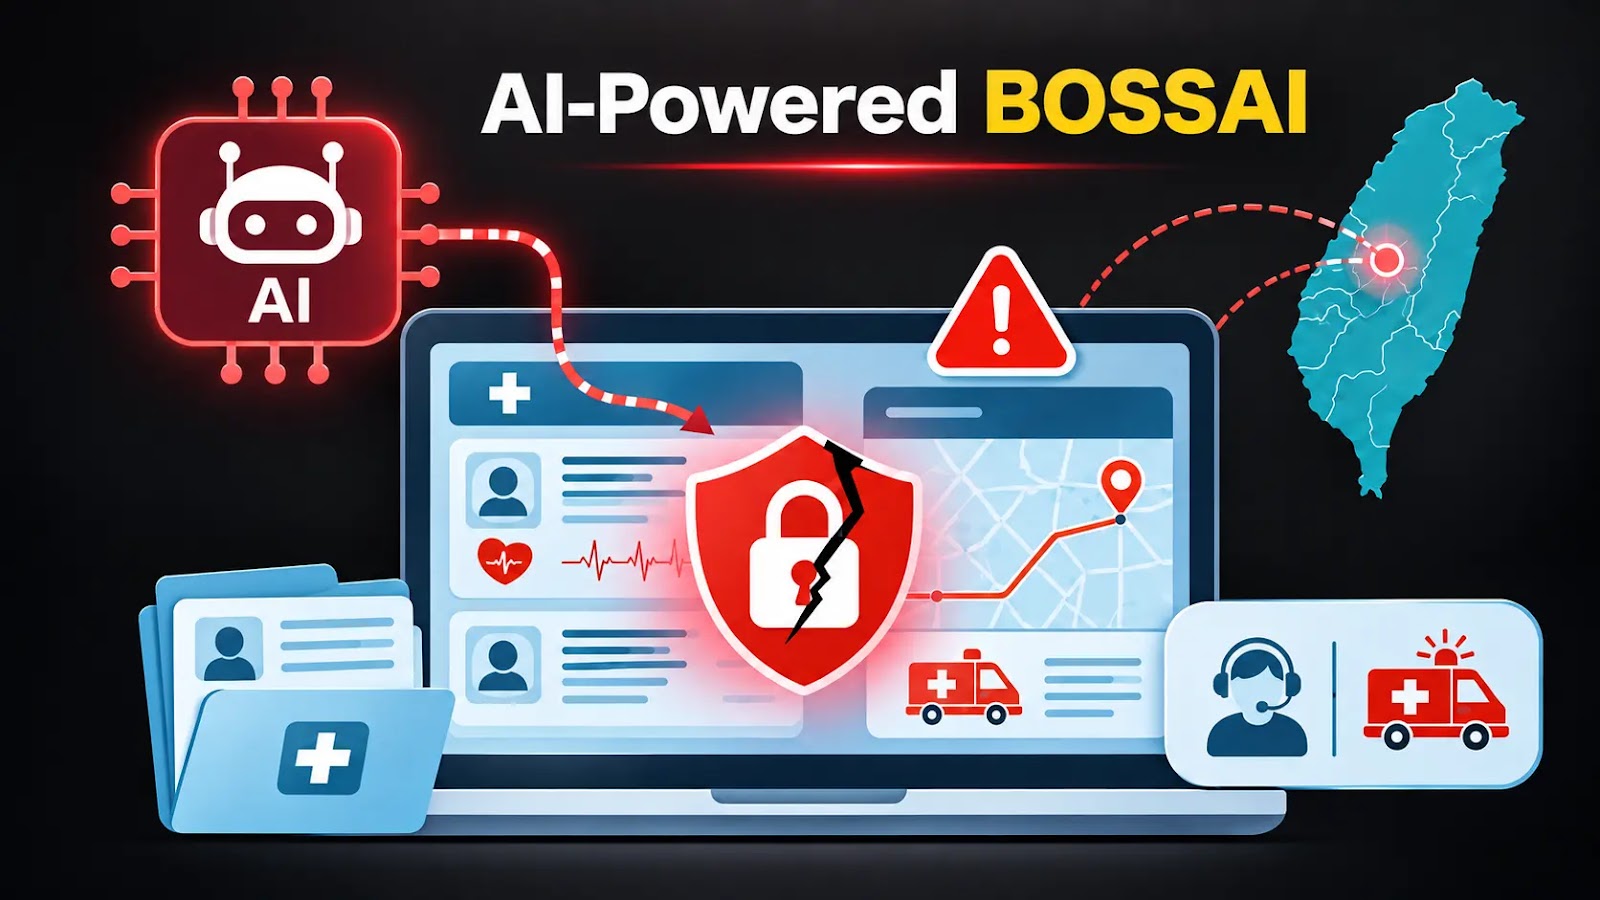
AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan

BOSSAI, an agentic attack platform run by one operator that exposed emergency medical and dispatch data in Taipei. The campaign targeted hundreds of organizations in eleven countries, including emergency services, banks, universities, military systems and e-commerce sites. Confirmed breaches hit universities and emergency providers, with medical data and PII exfiltrated. A Taipei fire department patient-care […]

The post AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CrowdStrike and Deloitte Spain Expand Cybersecurity Alliance With AI-Powered Threat Detection

CrowdStrike and Deloitte Spain announced an expanded cybersecurity alliance. This new phase of their collaboration focuses on AI-powered risk advisory. The partnership integrates executive security strategy with the implementation and day-to-day operations of the Security Operations Center (SOC), using Falcon IQ to turn exploitable risks into prioritized actions. This expansion combines CrowdStrike’s Falcon platform with […]

The post CrowdStrike and Deloitte Spain Expand Cybersecurity Alliance With AI-Powered Threat Detection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
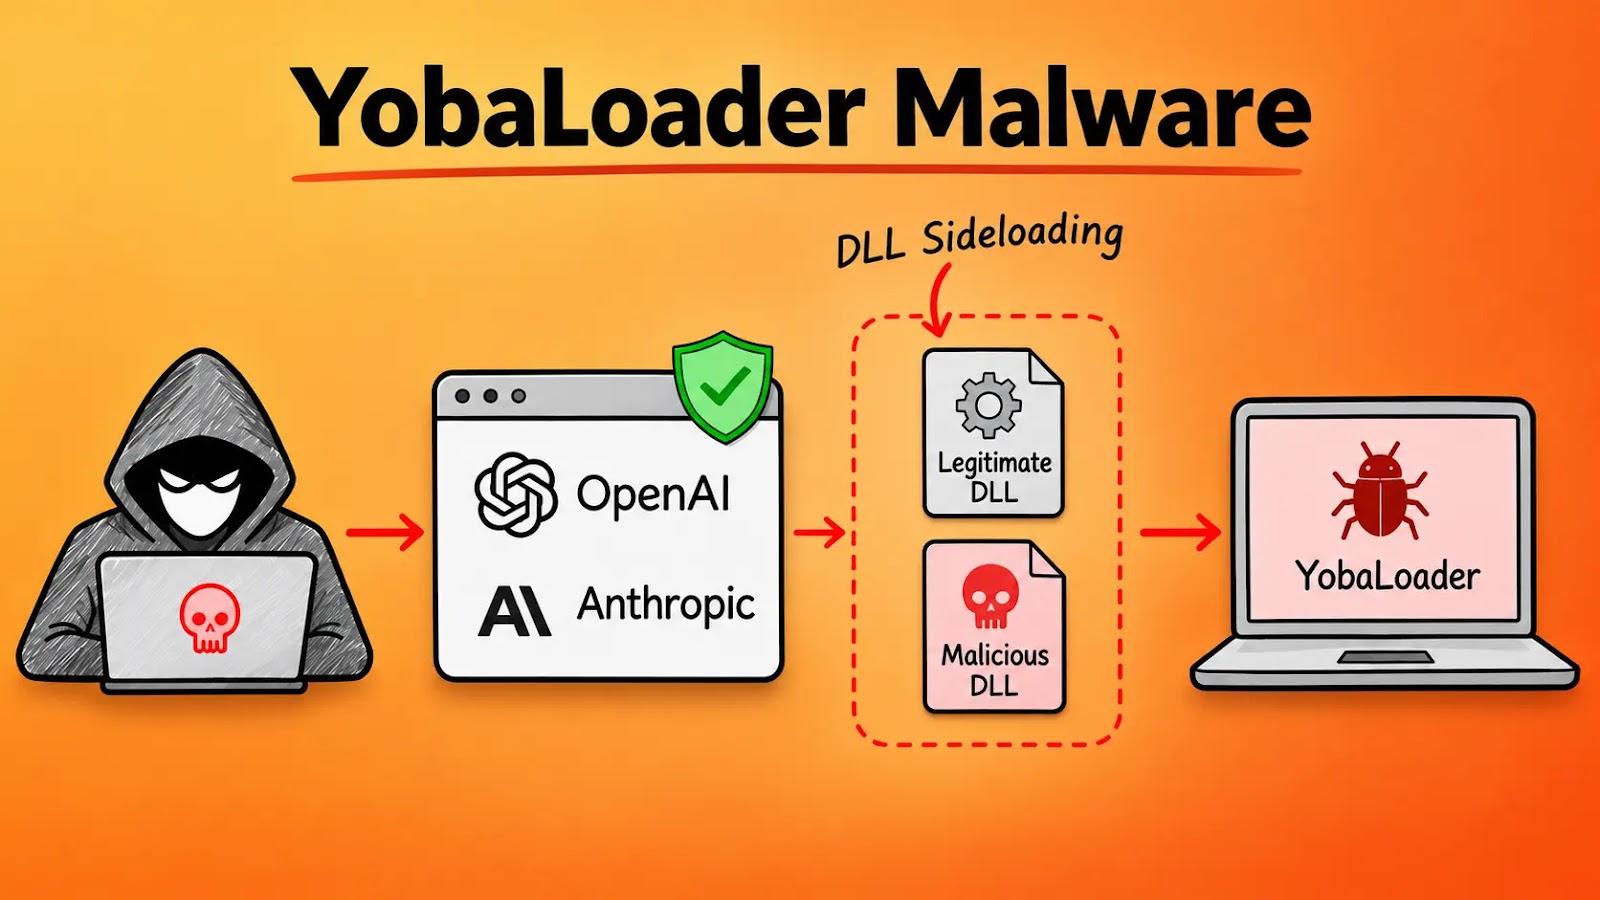
Hackers Exploit DLL Sideloading in Signed OpenAI and Anthropic Binaries to Deploy YobaLoader Malware

A campaign tracked as Yoba abuses interest in generative AI to push cryptocurrency-mining malware through fake GitHub projects. Check Point Research published its findings on October 27, 2026, after about two months of tracking. The operators pair legitimate, signed OpenAI and Anthropic executables with a malicious winmm.dll, so the payload loads through DLL sideloading. The […]

The post Hackers Exploit DLL Sideloading in Signed OpenAI and Anthropic Binaries to Deploy YobaLoader Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Weaponize Open-Source CyberStrikeAI Framework to Launch AI-Powered Network Intrusions

Hackers are abusing CyberStrikeAI, an open-source penetration-testing framework, to orchestrate network intrusions against educational organizations across Africa and Latin America. The findings illustrate AI moving beyond attack preparation into operational decision-making. Published November 2, Kaspersky’s investigation describes a human-directed operation in which an LLM selects tools, generates commands, interprets results, and determines subsequent actions. The […]

The post Hackers Weaponize Open-Source CyberStrikeAI Framework to Launch AI-Powered Network Intrusions appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Malicious Claude Code VS Code Extension Installs Persistent SSH Backdoor to Give Attackers Remote Access

A trojanized version of the Claude Code extension, identified as anthropic.claude-code version 2.1.313, contains a malicious loader that enables persistent SSH access to developer systems. Researchers analyzed an artifact obtained from Open VSX and discovered 66 lines of JavaScript added to the legitimate extension bundle. This additional code lets the attacker’s script run before the […]

The post Malicious Claude Code VS Code Extension Installs Persistent SSH Backdoor to Give Attackers Remote Access appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Anthropic’s Claude Chains One-Click and Zero-Click Exploits to Bypass Chrome, Android and Linux Security

Anthropic announced that an unreleased research model called Claude successfully developed working exploit chains for Chrome, Safari, Android, Windows, and Linux. The company’s Frontier Red Team shared these findings on October 27, 2026. Many exploit chains required minimal or no user interaction, and the team reported every identified flaw to the respective vendor before publication. […]

The post Anthropic’s Claude Chains One-Click and Zero-Click Exploits to Bypass Chrome, Android and Linux Security appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Compromise 17 Exposed AI Pentesting Panels to Deploy Malware and Steal Credentials

Attackers have compromised at least 17 internet-exposed Cairn AI penetration-testing panels, turning autonomous security agents against their own infrastructure to steal credentials, establish unauthorized access, and deploy malware. Victims included panels associated with suspected criminal operations, alongside instances apparently used for legitimate red teaming, bug bounty research, and capture-the-flag challenges. The attacks exploit unauthenticated administrative […]

The post Hackers Compromise 17 Exposed AI Pentesting Panels to Deploy Malware and Steal Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Researchers Discover OpenAI API Vulnerability That Leaks Hidden AI Reasoning Traces

Researchers have disclosed a vulnerability in the OpenAI API that reveals hidden reasoning traces by exploiting conversation compaction. This technique, named “Compaction Smuggling,” bypassed existing safeguards and could allow for the extraction of valuable training material from advanced models. According to Xint, OpenAI confirmed the issue, implemented an undisclosed fix on October 23, 2026, and […]

The post Researchers Discover OpenAI API Vulnerability That Leaks Hidden AI Reasoning Traces appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Unauthorized AI Agents Found Accessing Customer Accounts at Major U.S. Banks

U.S. banks face challenges as third-party artificial intelligence agents detect unauthorized access to customer accounts. This situation raises concerns about credential sharing, automated transactions, and the difficulty of distinguishing legitimate customer activity from automation-initiated actions. According to a report from Axios on October 22, several banks, including Morgan Stanley, Bank of America, JPMorgan, and Wells […]

The post Unauthorized AI Agents Found Accessing Customer Accounts at Major U.S. Banks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Used AI-Generated Scripts to Break Into Government Linux Servers and Hunt for Secrets

Hackers used apparently AI-generated scripts to compromise government Linux infrastructure, harvest credentials and pursue sensitive databases and official mailboxes in a campaign tracked as CL-UNK-1211. The investigation, published October 15, linked the operation to government entities and state-affiliated infrastructure. Attribution remains unresolved: under Unit 42’s attribution framework, the UNK designation means researchers have not established […]

The post Hackers Used AI-Generated Scripts to Break Into Government Linux Servers and Hunt for Secrets appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Attackers Target Flowise AI Agents With Credential Theft, Prompt Injection and Workflow Hijacking

An attacker used an exposed Flowise AI orchestration server to enumerate workflows, harvest credentials, and try to turn its language-model agent into an offensive analysis assistant. Sekoia says the findings were first shared in a private FLINT report on 7 September 2026. The honeypot emulated Flowise 2.2.8 and captured requests without running real system code […]

The post Attackers Target Flowise AI Agents With Credential Theft, Prompt Injection and Workflow Hijacking appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Gemini-Compatible AI Browsers Could Help Scammers Run Thousands of Fake Accounts, Researchers Warn

Antidetect browsers tools that create separate browser profiles with altered digital fingerprints could help scammers operate thousands of apparently unrelated social media accounts. The research focuses on Kameleo, AdsPower and MultiLogin, commercially available platforms with legitimate uses in marketing, e-commerce and privacy protection. Researchers say they also found the tools referenced in criminal forums and […]

The post Gemini-Compatible AI Browsers Could Help Scammers Run Thousands of Fake Accounts, Researchers Warn appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Researchers Uncover GhostShares Flaw That Makes Meta Muse AI Conversations Easy to Find

A privacy weakness in Meta’s Muse AI assistant that made shared conversations discoverable through passive DNS records, exposing personal files and internal business documents. Dubbed GhostShares, the issue affected public sharing links whose supposedly unguessable identifiers appeared inside searchable hostnames. Meta told Ars Technica on October 20 that it was suspending the feature. The finding […]

The post Researchers Uncover GhostShares Flaw That Makes Meta Muse AI Conversations Easy to Find appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Ransomware Gangs Use AI to Find and Steal the Most Sensitive Company Data Quickly

Ransomware operators are using generative AI to sharpen phishing campaigns, speed up reconnaissance, and identify sensitive corporate information to steal. Zscaler ThreatLabz describes a shift toward faster, more selective extortion, where attackers prioritize damaging disclosures rather than relying exclusively on file encryption. That represents a 275.8% annual increase. These figures establish the scale of theft, […]

The post Ransomware Gangs Use AI to Find and Steal the Most Sensitive Company Data Quickly appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Use Hundreds of AI Agents to Exploit PaperCut Servers and Steal Windows Credentials

A likely Russian-speaking threat actor used hundreds of AI agents to exploit PaperCut NG/MF servers, steal Windows credentials and establish reusable access to internal networks. GreyNoise identified at least 440 compromised instances belonging to 395 organizations across 48 countries, demonstrating how agent-assisted workflows can accelerate exploitation of enterprise infrastructure. The operator combined OpenAI’s Codex harness […]

The post Hackers Use Hundreds of AI Agents to Exploit PaperCut Servers and Steal Windows Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AI Agent Workflows Could Expose Credentials Through Trusted Developer Tools

AI agents can expose credentials during routine development tasks, moving secrets from protected stores into command arguments, logs, transcripts, and inputs to external models. The concern is not that developer tools are inherently malicious. Rather, agents inherit developer privileges and repeatedly translate requests into shell commands, consuming their output before deciding what to execute next. […]

The post AI Agent Workflows Could Expose Credentials Through Trusted Developer Tools appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AI Used in 84% of Ransomware Attacks as Identity Infrastructure Comes Under Fire.

Artificial intelligence appeared in ransomware incidents affecting 84% of surveyed victims, while 87% reported attacks targeting or exploiting identity infrastructure. The findings connect accelerated criminal operations with weaknesses in the systems governing enterprise access. The study surveyed 1,200 IT and security professionals across nine countries and eight industry sectors. Crucially, it included only organizations that […]

The post AI Used in 84% of Ransomware Attacks as Identity Infrastructure Comes Under Fire. appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌