❌

Visualização normal

Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts

Hackers are using streaming app lures to distribute Mirax. This Android banking trojan lets operators remotely control victims’ phones and initiate fraudulent transfers. Estimated losses reach millions of dollars, although confirmed cases capture only part of the campaign’s impact. The operation remained active when Group-IB published its November 5 investigation. Researchers linked the infections through […]

The post Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Google Patches Critical Android RCE Flaws That Let Attackers Execute Code Without User Interaction

Google released its November 2026 Android Security Bulletin, which addresses critical vulnerabilities that could allow remote code execution without user interaction or additional execution privileges. Published on November 2, the bulletin highlights a framework vulnerability as the most severe issue and also documents other critical remote code execution flaws in Android’s system components. According to […]

The post Google Patches Critical Android RCE Flaws That Let Attackers Execute Code Without User Interaction appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Turn Low-Cost Android Phones Into Hidden Proxy Botnets Through Preinstalled Malware

Midnight Mimosa, a widespread Android malware campaign, is turning inexpensive smartphones into advertising fraud engines and potential residential proxy nodes by embedding malicious apps in device firmware before purchase. Bitdefender observed thousands of infected devices across more than 150 countries over approximately two years, exposing a persistent compromise that ordinary application removal cannot resolve. The […]

The post Hackers Turn Low-Cost Android Phones Into Hidden Proxy Botnets Through Preinstalled Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial application packages used in India, combining accessibility-based PIN capture with a transparent overlay that intercepts interactions inside legitimate Google Pay and MobiKwik interfaces. The findings extend Cyble’s October 2025 investigation, which documented GhostBat spreading through fraudulent mParivahan applications, harvesting banking messages, and stealing UPI PINs through […]

The post New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Android Malware Exposes Its Own Operators While Hijacking Phones and Stealing Sensitive Data

An Android remote-access Trojan, YuanKong, whose weakly protected dropper reveals more than its hidden payload: it exposes the operator account identifiers embedded in each build. Analysis of 110 droppers uncovered 57 distinct child payloads, 42 operator accounts and 44 rotating build brands, all tied together by a shared signing certificate and command-and-control (C2) infrastructure. Its […]

The post Android Malware Exposes Its Own Operators While Hijacking Phones and Stealing Sensitive Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Android Firmware Malware Uses Ad Fraud and Proxy Botnets to Generate Revenue

Midnight Mimosa, an Android malware campaign embedded in firmware that monetizes compromised smartphones through advertising fraud and residential proxy services. Disclosed on October 8, the operation affected thousands of devices across more than 150 countries over roughly two years, predominantly inexpensive phones built on MediaTek platforms. Unlike malware requiring a malicious download, Midnight Mimosa arrives […]

The post Android Firmware Malware Uses Ad Fraud and Proxy Botnets to Generate Revenue appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Android 17 Advanced Protection Adds Intrusion Logging, USB Security and Brute-Force Defense

Google has expanded Android Advanced Protection with six security enhancements targeting spyware investigations, malicious USB connections, accessibility abuse, browser exploits, and repeated authentication failures. Announced on October 1, 2026, the update strengthens Android 17 defenses for journalists, officials, public figures, and security-conscious users. The changes build on Android 16’s device-level Advanced Protection, introduced in May […]

The post Android 17 Advanced Protection Adds Intrusion Logging, USB Security and Brute-Force Defense appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
GitHub AI Agent Uncovers 24 Android App Vulnerabilities

GitHub Security Lab has disclosed 24 vulnerabilities in Android applications discovered through its open-source AI security agent and specialized audit taskflows. The findings highlight issues that could enable covert location tracking in the OsmAnd navigation app and account takeover attacks against Wikipedia users on Android. Kevin Stubbings, a researcher at GitHub Security Lab, developed targeted […]

The post GitHub AI Agent Uncovers 24 Android App Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
RemControl Android Malware Targets 30+ Banking Apps to Steal PINs and Credentials

A newly uncovered Android banking trojan dubbed RemControl is targeting customers of more than 30 financial institutions across Europe, the Middle East, and Canada. The malware combines fake Google Play pages, Android Accessibility Service abuse, credential-stealing overlays, real-time screen streaming, and remote-control functions to compromise mobile banking sessions. The company tracks the operator behind the […]

The post RemControl Android Malware Targets 30+ Banking Apps to Steal PINs and Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
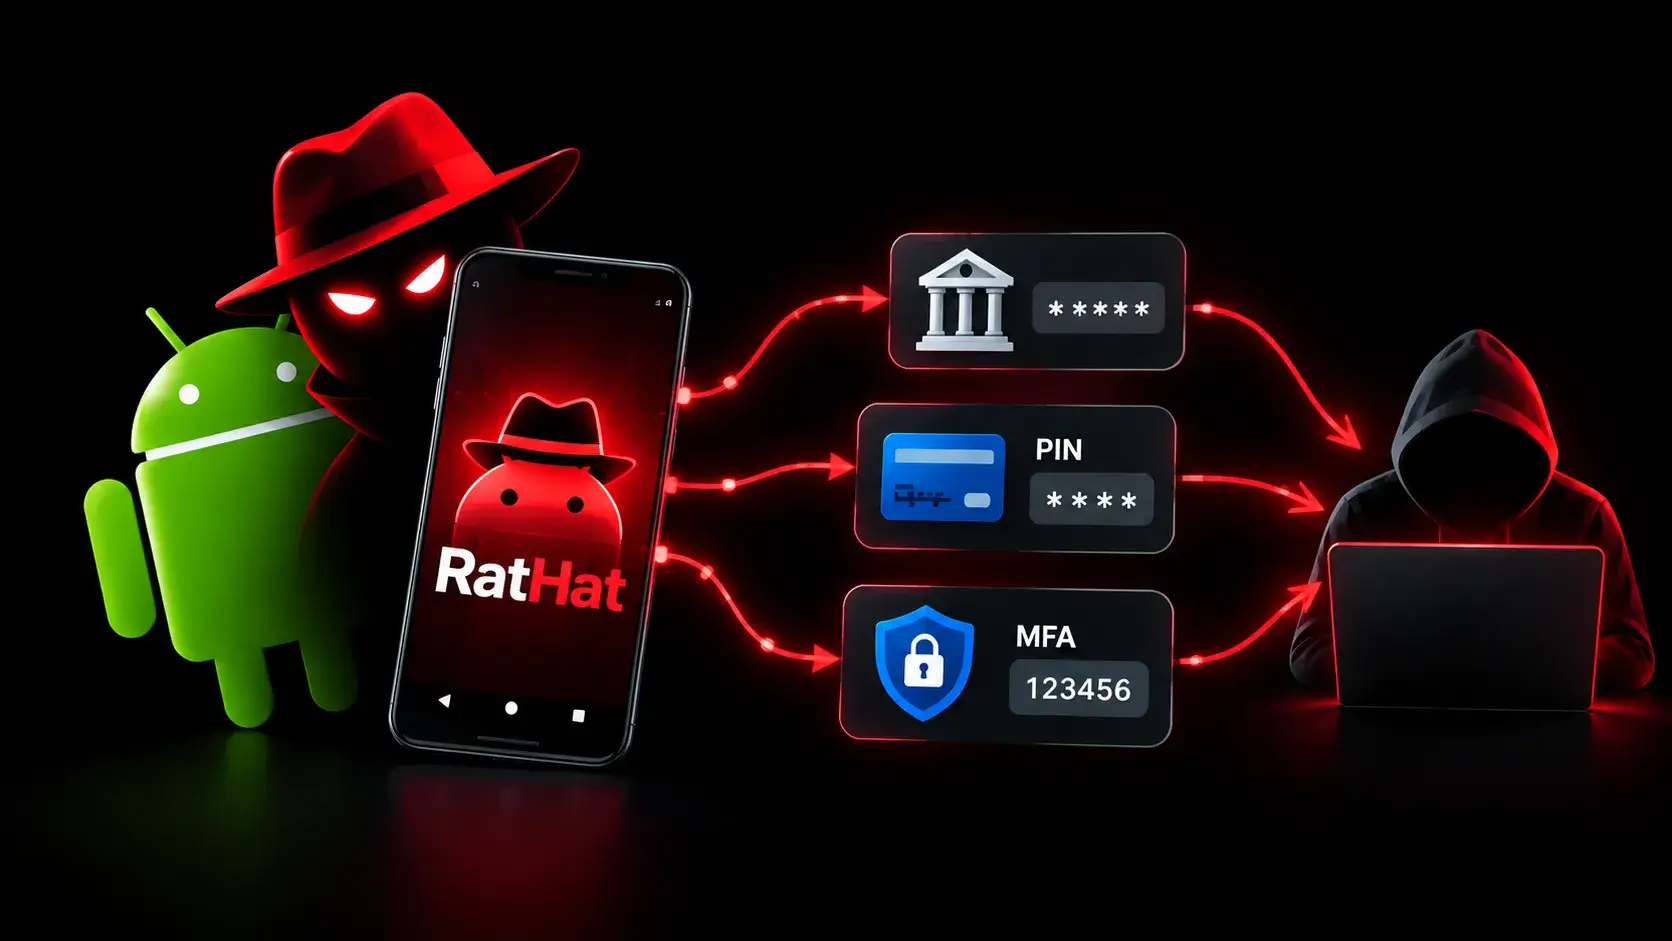
AI-Powered RatHat Android Trojan Steals Bank Credentials, PINs and MFA Codes

Researchers have identified a new Android banking Trojan called RatHat that utilizes artificial intelligence to automate device compromise and steal financial credentials, PINs, and one-time passcodes. Zimperium’s zLabs researchers analyzed this malware, which represents a significant evolution in Android threats. AI-Powered RatHat Android Trojan Unlike traditional malware that relies on fixed scripts, RatHat offers a […]

The post AI-Powered RatHat Android Trojan Steals Bank Credentials, PINs and MFA Codes appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌