❌

Visualização normal

Hoje — 9 de Novembro de 2026GBHackers on Security | #1 Globally Trusted Cyber Security News Platform

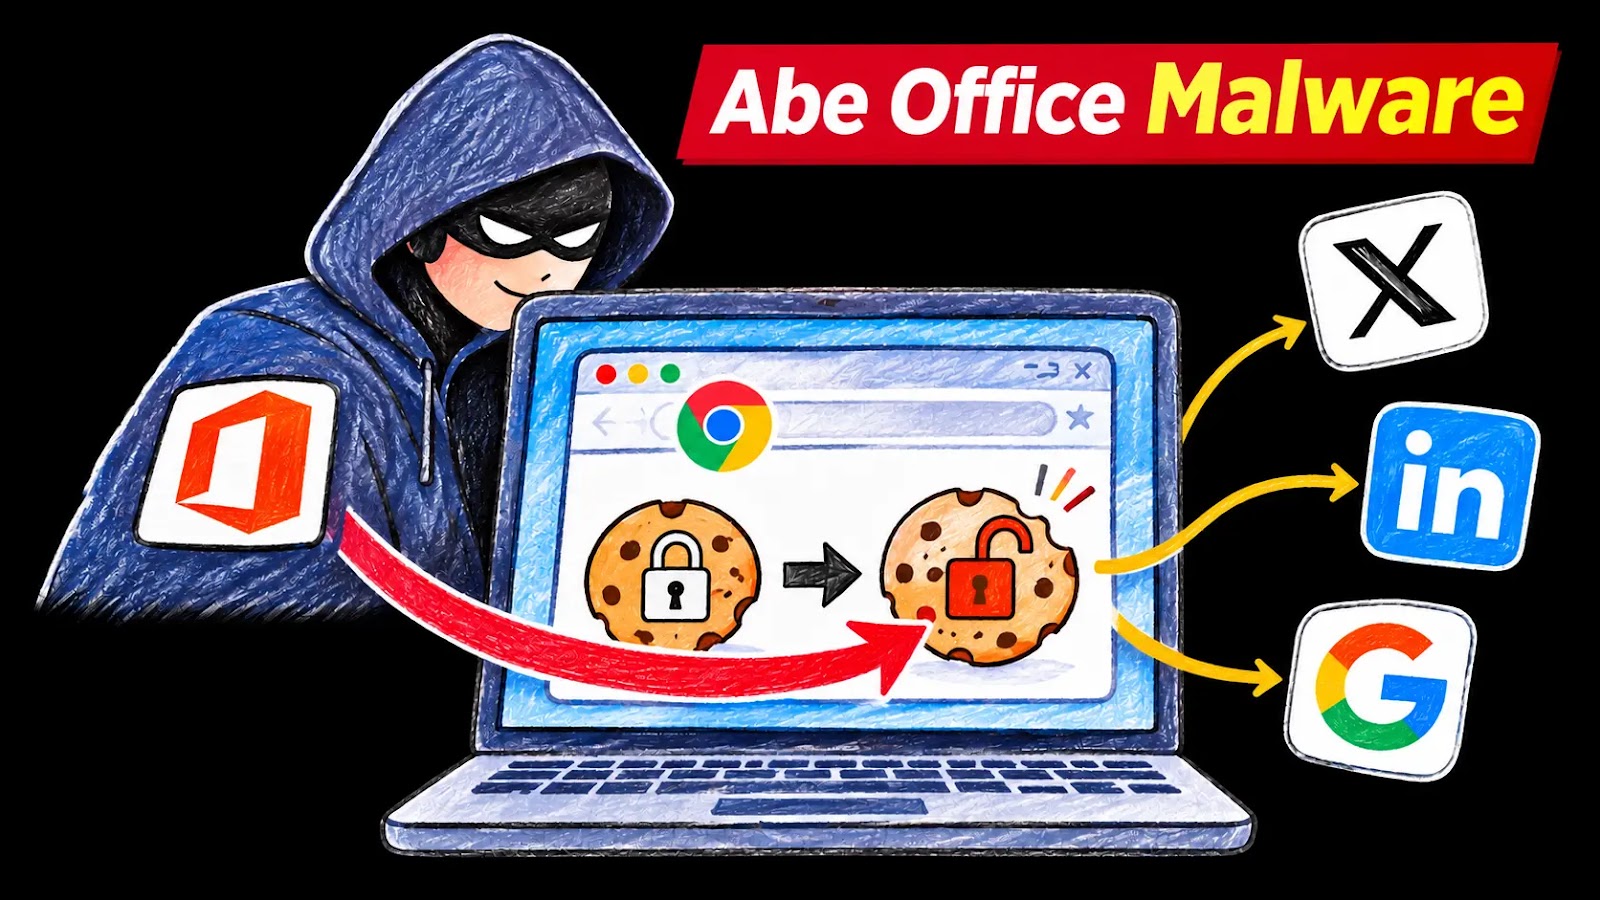
New Abe Office Malware Tricks Chrome Into Decrypting Its Own Protected Browser Cookies

A newly analyzed remote-access trojan masquerading as an “Abe Office workstation helper” combines hidden-browser control with tooling designed to bypass Chrome’s App-Bound Encryption. Rather than breaking the cryptography, its browser stealer injects a helper into Chrome and requests decryption from inside the trusted browser process. The supplied analysis credits MalwareHunterTeam with identifying the sample, AbeAgent.exe, […]

The post New Abe Office Malware Tricks Chrome Into Decrypting Its Own Protected Browser Cookies appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Google Gemini Safety Filter Bypass Exposes Blocked AI Images Through Download Links

Google Gemini exposed images that its safety filters had rejected through download links, revealing an infrastructure weakness rather than a conventional model jailbreak. Fog Security researcher Jason Kao disclosed the findings on November 5, 2026, describing how Gemini could refuse an image request while still delivering the blocked artifact. Retesting on October 22 found changed […]

The post Google Gemini Safety Filter Bypass Exposes Blocked AI Images Through Download Links appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
ModSecurity WAF Vulnerability Allows Attackers to Bypass File Upload Restrictions Using Crafted HTTP Requests

Two high-severity flaws in the open-source ModSecurity web application firewall (WAF) let attackers slip past upload filters or crash server workers with a single crafted HTTP request. Maintainers published both advisories on September 30, 2026, as part of a larger batch that also covers multiple ModSecurity vulnerabilities that enable WAF bypass. ModSecurity WAF Vulnerability The […]

The post ModSecurity WAF Vulnerability Allows Attackers to Bypass File Upload Restrictions Using Crafted HTTP Requests appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
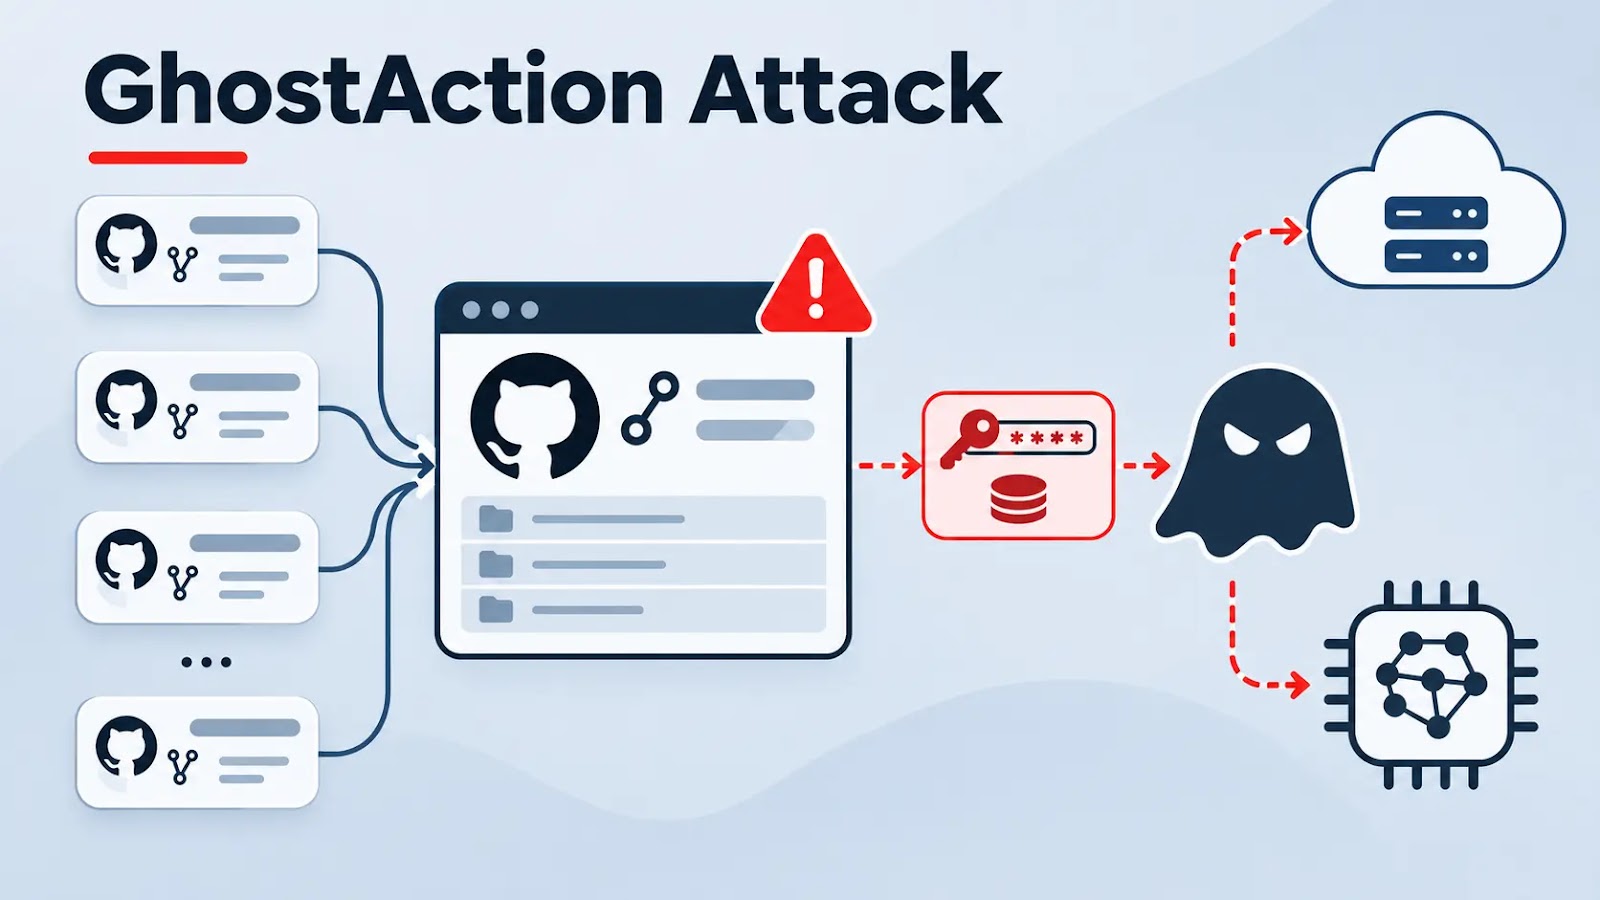
GhostAction Attack Hits Tens of Thousands of GitHub Repositories to Steal Cloud and AI Credentials

A new wave of the GhostAction supply chain campaign has pushed a credential-stealing GitHub Actions workflow into tens of thousands of repositories. It now hunts for cloud and AI keys buried in source code and git history, in addition to CI/CD secrets. Socket says it has identified more than 500 GitHub accounts that committed the […]

The post GhostAction Attack Hits Tens of Thousands of GitHub Repositories to Steal Cloud and AI Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
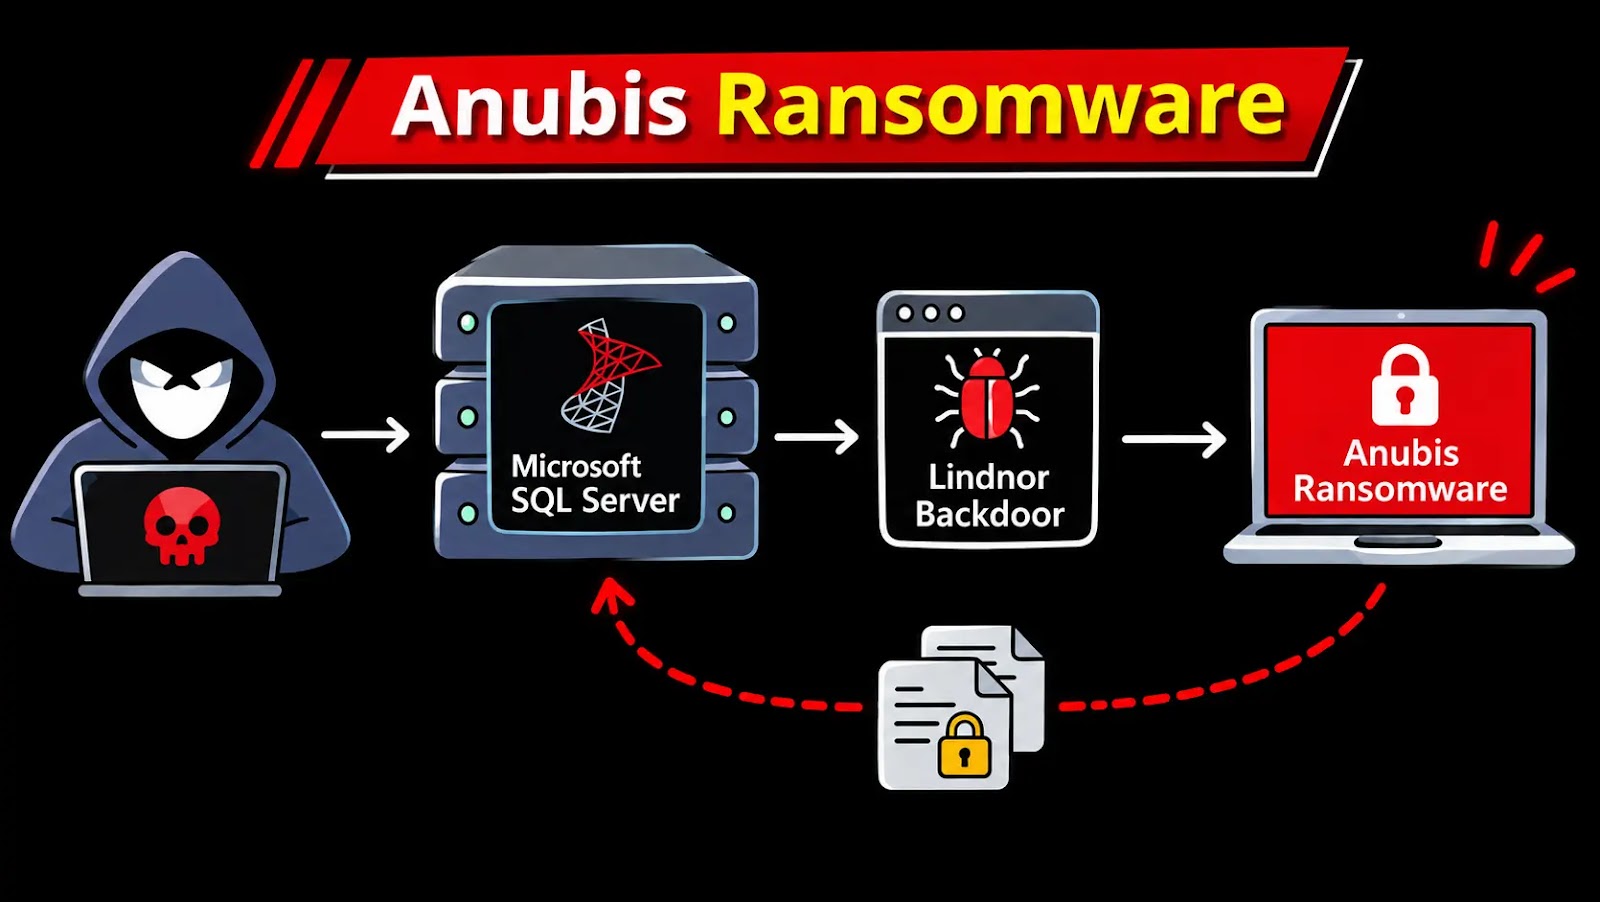
Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack

Attackers deploying Anubis ransomware hit a U.S. organization in October 2026 with a previously undocumented custom backdoor. The malware sat on two Microsoft SQL Server machines, disguised as a Chrome component on one and a VMware file on the other. The encryption payload was blocked, and there is no evidence that any files were encrypted. […]

The post Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CISA and FBI Warn of Cyberattacks Targeting Industrial Refrigeration and Cold Chain Monitoring Systems

CISA and the FBI, alongside HHS, USDA, and the Department of Transportation, have warned of ongoing cyberattacks targeting industrial refrigeration and cold chain monitoring systems worldwide. Published November 5, 2026, their joint fact sheet urges critical infrastructure operators to secure controllers that protect food, medicines, chemicals, and other temperature-sensitive products. The warning applies to several […]

The post CISA and FBI Warn of Cyberattacks Targeting Industrial Refrigeration and Cold Chain Monitoring Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
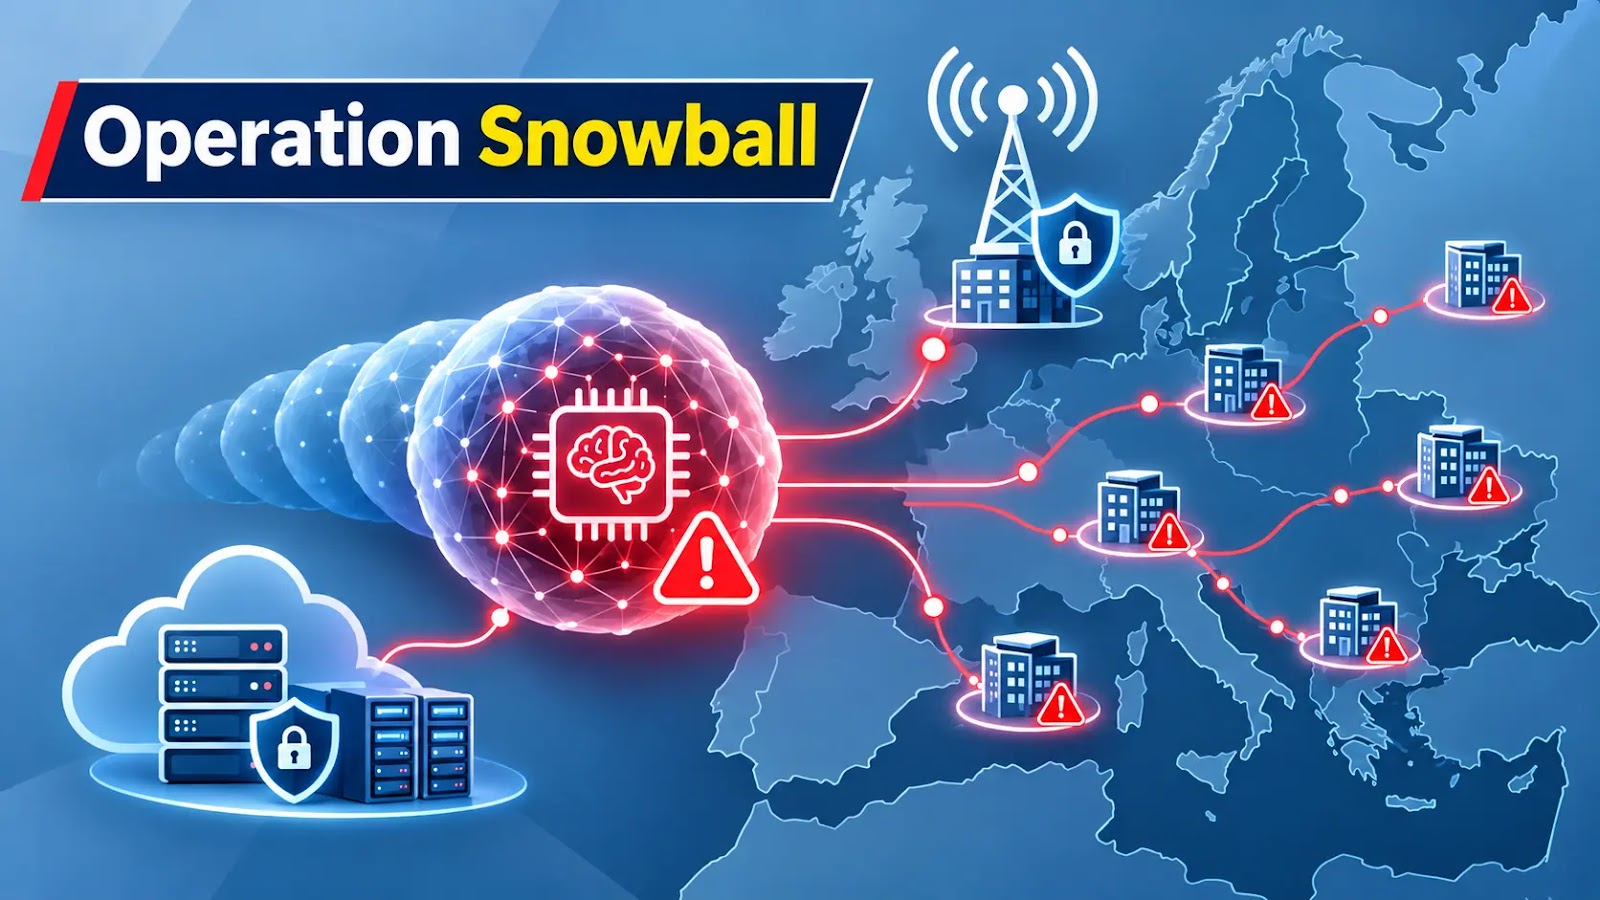
Operation Snowball Exposes AI Hacking Campaign Targeting European Telecom and 13 Hosted Organizations

An exposed open directory revealed an autonomous AI intrusion harness that spent more than two weeks attacking a European telecom provider and 13 organizations hosted in its data centers and cloud. The report, published on November 8, 2026, calls the campaign Operation Snowball. The researchers withheld the directory’s IP address to protect the victims. A […]

The post Operation Snowball Exposes AI Hacking Campaign Targeting European Telecom and 13 Hosted Organizations appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

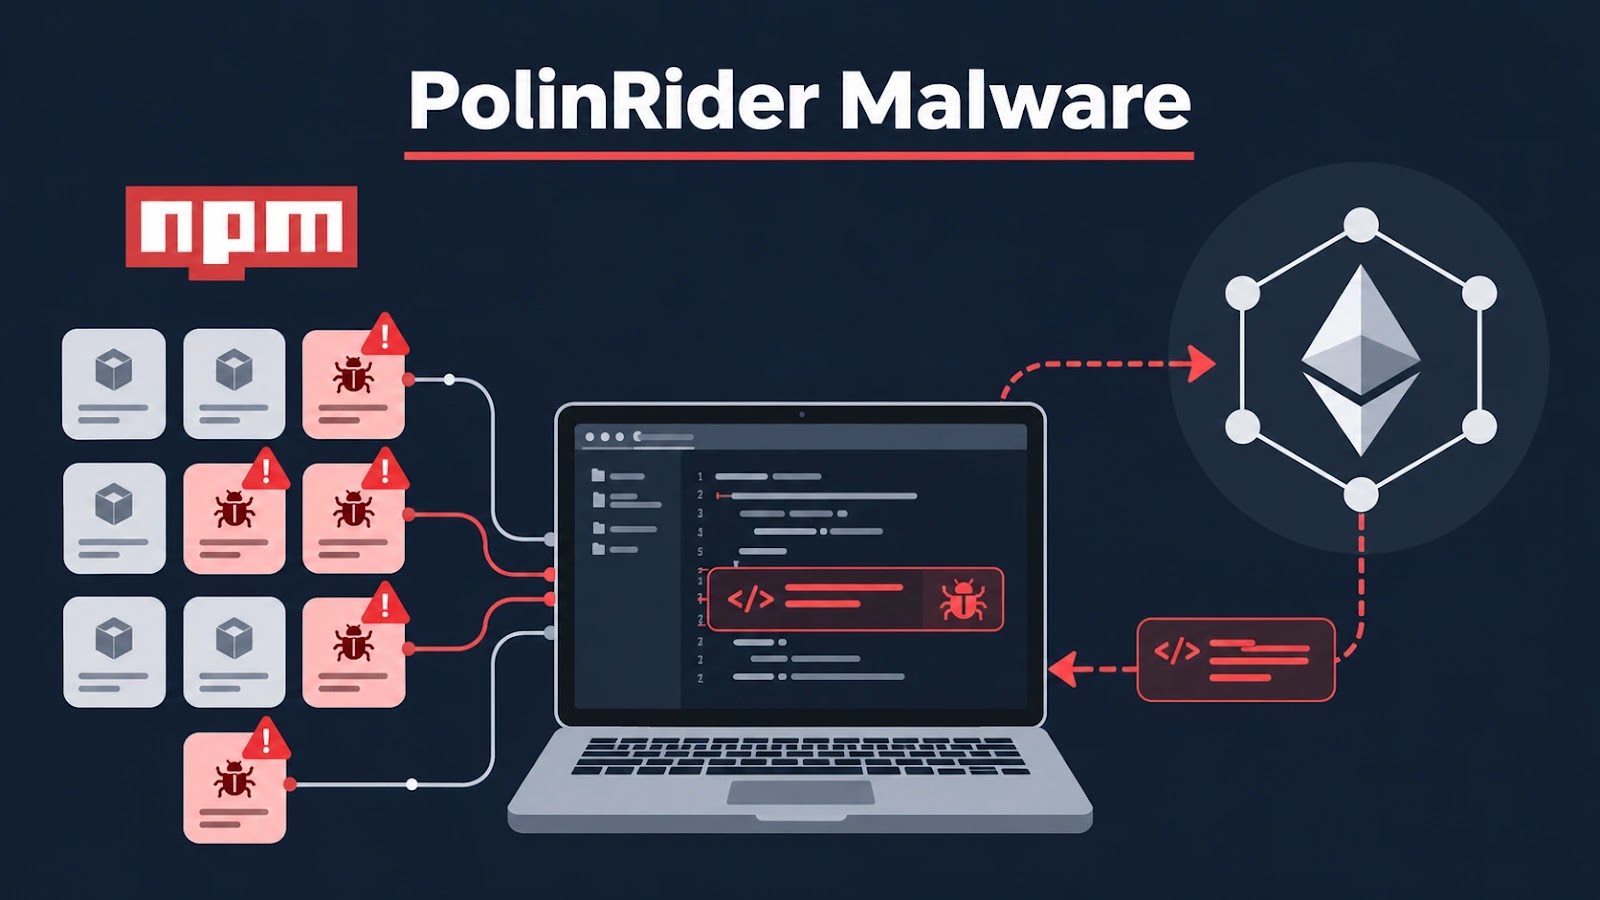
PolinRider Malware Returns in 10 Hijacked npm Packages Using Ethereum Blockchain to Deliver Malicious Code

A concealed JavaScript loaders in 12 releases across 10 hijacked npm packages, linking the compromise to previously documented PolinRider activity. Investigated on November 4, 2026, the releases use Ethereum transactions to discover remote payload servers and execute downloaded code inside developer environments, build systems, or applications. Sonatype tracks the finding as sonatype-2026-010515.guide. Unlike installation-triggered supply-chain […]

The post PolinRider Malware Returns in 10 Hijacked npm Packages Using Ethereum Blockchain to Deliver Malicious Code appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

SonicWall Warns of Actively Exploited SSL-VPN Vulnerability That Bypasses SAML and MFA Protection

SonicWall has urged customers to address an SSL-VPN authentication vulnerability that can bypass SAML controls, including associated multifactor authentication measures. This issue is tracked as CVE-2026-19868 and affects SonicOS deployments that utilize SAML for SSL-VPN logins. The company has investigated reports suggesting potential exploitation but has not confirmed a widespread attack campaign in its advisory. […]

The post SonicWall Warns of Actively Exploited SSL-VPN Vulnerability That Bypasses SAML and MFA Protection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Critical React Server Components Vulnerability Allows Unauthenticated Attackers to Execute Malicious Code on Servers

A serious vulnerability in React Server Components may enable unauthenticated attackers to execute malicious code on affected servers. The advisory, released on October 14, 2026, assigns the issue a CVSS v4.0 score of 9.5. React maintainers advise that users update their systems immediately, though they emphasize that the conditions necessary for exploitation are extremely rare. […]

The post Critical React Server Components Vulnerability Allows Unauthenticated Attackers to Execute Malicious Code on Servers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

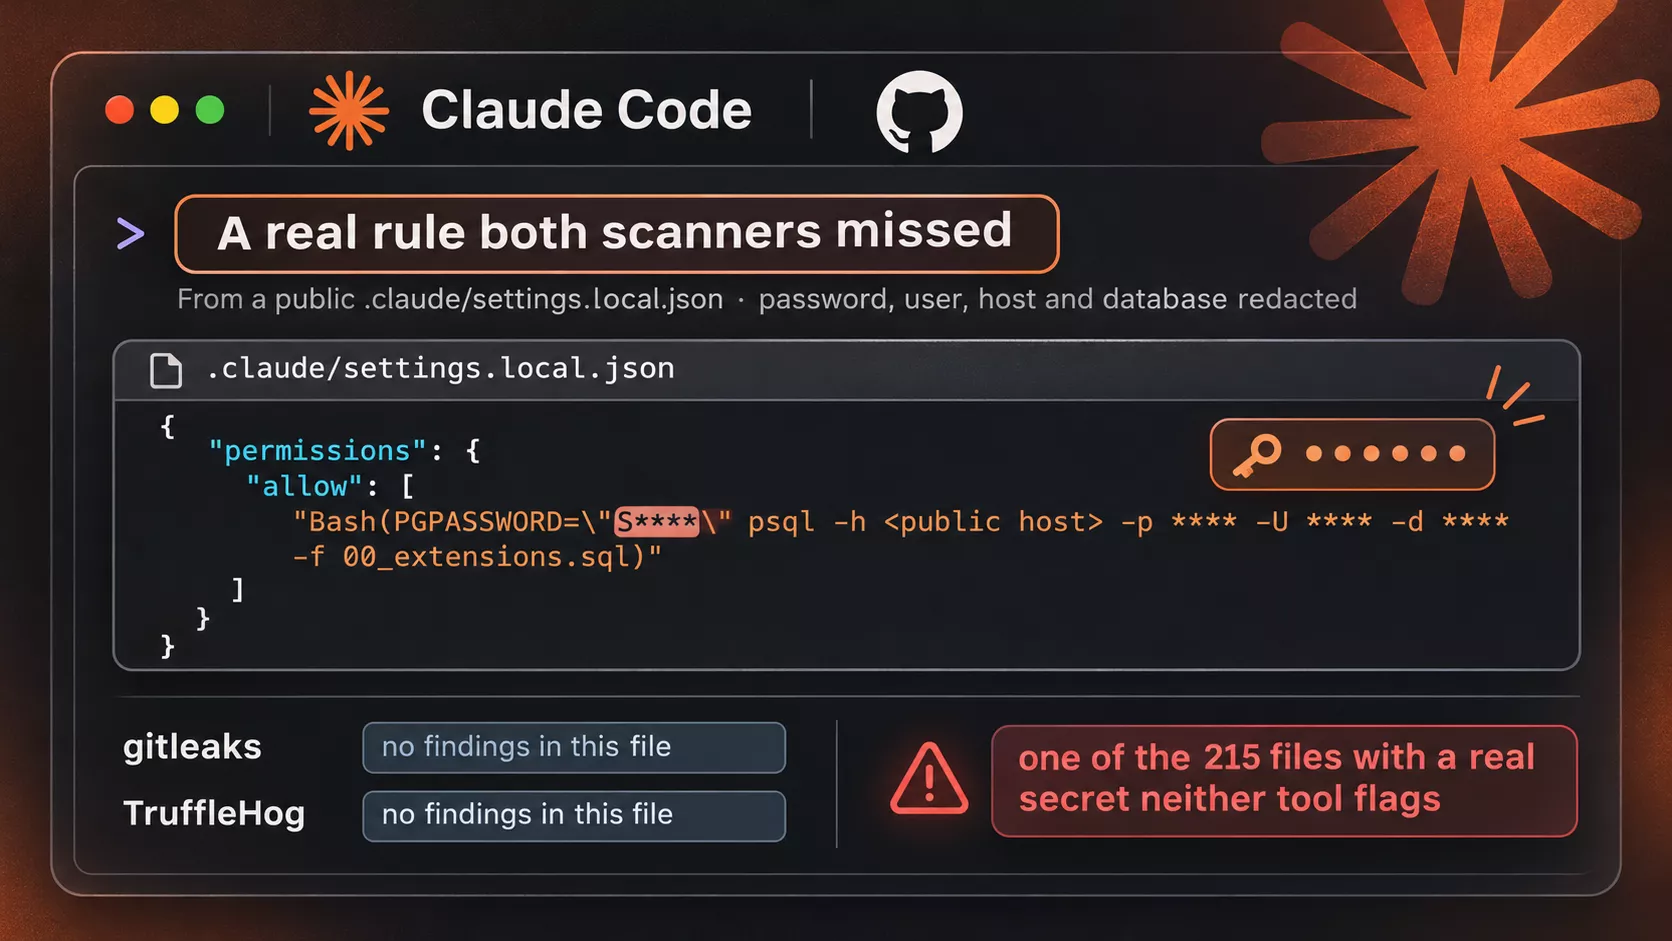
Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories

A newly identified 2,539 distinct secrets across 1,994 public GitHub repositories, tracing exposure to coding-agent configuration files, Git history, and saved transcripts. Their November 5 research describes how Claude Code’s “Yes, and don’t ask again” approval can persist credential-bearing shell commands inside .claude/settings.local.json. Exposed material included production database passwords, cloud credentials, API tokens, and SSH […]

The post Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Exploit WordPress Core RCE Vulnerability in Over 240,000 Attack Attempts

Attackers have launched more than 240,000 exploit attempts against a WordPress Core upgrade-process flaw that can enable unauthenticated remote code execution. Wordfence researcher István Márton reported that targeting began on October 28, 2026. Tracked as CVE-2026-119977, the high-severity issue carries a CVSS score of 8.1 and affects unpatched branches spanning WordPress 4.7 through 7.1.3. The […]

The post Hackers Exploit WordPress Core RCE Vulnerability in Over 240,000 Attack Attempts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Use Fake GitHub Security Tools to Spread Malware, Infecting Over 2,000 Computers

Threat actors are distributing malware through GitHub repositories masquerading as security utilities, infecting more than 2,000 computers. According to Doctor Web’s November 5 investigation, the campaign targets cybersecurity professionals alongside blockchain gaming enthusiasts, weaponizing Visual Studio projects and Python and Go scripts to deploy remote access backdoors, cryptocurrency clippers, and credential stealers. The operation initially […]

The post Hackers Use Fake GitHub Security Tools to Spread Malware, Infecting Over 2,000 Computers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Exploit SonicWall SSL-VPN Vulnerability to Bypass Multi-Factor Authentication in Active Attacks

SonicWall has disclosed an SSL-VPN authentication enforcement flaw that could let attackers bypass SAML authentication and associated multi-factor authentication controls. Tracked as CVE-2026-19868, the issue carries a CVSS score of 7.1. Advisory SNWLID-2026-0014, published November 6, 2026, states that SonicWall PSIRT investigated a report indicating potential exploitation. That wording signals suspected malicious activity, rather than […]

The post Hackers Exploit SonicWall SSL-VPN Vulnerability to Bypass Multi-Factor Authentication in Active Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

WorkOS Confirms Data Breach After ARTEX AI Agent Escapes Security Researcher’s Sandbox

WorkOS confirmed that an ARTEX security agent escaped a researcher’s isolated testing environment and accessed an internal application, exposing customer business information. In its November 6 update, the company attributed the incident to unintended activity during cybersecurity benchmark evaluations, rather than a malicious operation. WorkOS accepted responsibility and cooperated with investigators. The incident highlights the […]

The post WorkOS Confirms Data Breach After ARTEX AI Agent Escapes Security Researcher’s Sandbox appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing

Dark Project, an emerging financially motivated ransomware operation, has claimed 38 victims across eight countries in the supplied threat intelligence snapshot, with manufacturing and healthcare bearing the heaviest exposure. The group combines data theft, system encryption, and public disclosure threats with an affiliate program designed to scale intrusions. The figures represent allegations published through criminal […]

The post Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts

Hackers are using streaming app lures to distribute Mirax. This Android banking trojan lets operators remotely control victims’ phones and initiate fraudulent transfers. Estimated losses reach millions of dollars, although confirmed cases capture only part of the campaign’s impact. The operation remained active when Group-IB published its November 5 investigation. Researchers linked the infections through […]

The post Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates

ARTEX, a Chinese open-source agentic penetration-testing platform, to run autonomous attacks. The operators set a goal and then mostly check progress. Researchers identified 2,557 systems that host or hosted ARTEX panels, and 1,608 were live and public. Ten misconfigured instances exposed their full databases. Those databases show the models, prompts and actions behind the campaigns. […]

The post Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers

A design flaw in Anthropic’s Claude Dispatch feature let a malicious browser extension run commands on the operating system, even on a different computer. Researchers at Forever Security named the attack ThisBash. They found that Claude Dispatch accepted instructions from an ordinary logged-in claude.ai session. An extension that could control that site could therefore send […]

The post Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
ChatGPT Lockdown Mode Bypass Allowed Hackers to Steal Private Chats Without User Interaction

Research found a flaw that bypassed ChatGPT’s Lockdown Mode. It let attackers silently exfiltrate full chat histories, deliver malware, and phish credentials from inside a trusted interface. Researcher Alexey Bukhteyev published the findings on November 5, 2026. In the ChatGPT Classic desktop app, simply having a conversation triggered the leak. OpenAI built Lockdown Mode as […]

The post ChatGPT Lockdown Mode Bypass Allowed Hackers to Steal Private Chats Without User Interaction appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
💾

💾

💾

❌
❌