❌

Visualização normal

Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing

Dark Project, an emerging financially motivated ransomware operation, has claimed 38 victims across eight countries in the supplied threat intelligence snapshot, with manufacturing and healthcare bearing the heaviest exposure. The group combines data theft, system encryption, and public disclosure threats with an affiliate program designed to scale intrusions. The figures represent allegations published through criminal […]

The post Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery

HYFLOCK ransomware operators have developed successive Windows encryptors that lock files, access network shares, and attempt to obstruct recovery, while implementation flaws create sharply different outcomes for victims. The investigation distinguishes demonstrated functionality from promotional claims. Although researchers confirmed encryption and scheduled-task registration, they did not establish successful domain-wide propagation or reliable execution after remote […]

The post Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
3AM Ransomware Hackers Use AI-Assisted Attacks to Breach UK Schools and Spread Across Windows Domains

A ransomware affiliate known as 3AM compromised a UK school network using a mix of traditional intrusion techniques and patterns suggesting the involvement of artificial intelligence. According to Bitdefender’s investigation on November 3, this operation appears to follow a suspected hybrid workflow: a human operator selects the targets while a language model may handle repetitive […]

The post 3AM Ransomware Hackers Use AI-Assisted Attacks to Breach UK Schools and Spread Across Windows Domains appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
NIST Releases New Cybersecurity Guidelines to Protect Small Businesses From Phishing and Ransomware Attacks

The National Institute of Standards and Technology (NIST) released new cybersecurity guidance to help solo business owners protect themselves against threats like phishing, ransomware, and account compromise. Published on November 2, 2026, NIST Cybersecurity White Paper 50 simplifies the Cybersecurity Framework 2.0 and offers practical actions for businesses with limited IT infrastructure. The publication, Small […]

The post NIST Releases New Cybersecurity Guidelines to Protect Small Businesses From Phishing and Ransomware Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Japan’s GMO Internet Warns Customers to Unplug PCs as Hackers Threaten Ransomware

Japan’s GMO Internet Group urged Onamae.com Desktop Cloud customers to back up their data, disconnect computers from networks, shut them down, and unplug connected cables after suspected attackers threatened to publish customer information and launch ransomware at noon on October 27. The emergency instructions followed unauthorized access to the company’s cloud desktop service and an […]

The post Japan’s GMO Internet Warns Customers to Unplug PCs as Hackers Threaten Ransomware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Gentlemen Ransomware Hackers Hijack Legitimate Lenovo Drivers to Disable Security Software

The Gentlemen ransomware operation is abusing legitimate Lenovo and Safetica kernel drivers to terminate security software, weakening endpoint defenses before encryption. Acronis Threat Research Unit researchers identified two custom dropper samples during a recent incident, exposing how the group weaponizes vulnerable drivers rather than relying exclusively on conventional process termination commands The technique, known as […]

The post Gentlemen Ransomware Hackers Hijack Legitimate Lenovo Drivers to Disable Security Software appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Ransomware Gangs Use AI to Find and Steal the Most Sensitive Company Data Quickly

Ransomware operators are using generative AI to sharpen phishing campaigns, speed up reconnaissance, and identify sensitive corporate information to steal. Zscaler ThreatLabz describes a shift toward faster, more selective extortion, where attackers prioritize damaging disclosures rather than relying exclusively on file encryption. That represents a 275.8% annual increase. These figures establish the scale of theft, […]

The post Ransomware Gangs Use AI to Find and Steal the Most Sensitive Company Data Quickly appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AI Used in 84% of Ransomware Attacks as Identity Infrastructure Comes Under Fire.

Artificial intelligence appeared in ransomware incidents affecting 84% of surveyed victims, while 87% reported attacks targeting or exploiting identity infrastructure. The findings connect accelerated criminal operations with weaknesses in the systems governing enterprise access. The study surveyed 1,200 IT and security professionals across nine countries and eight industry sectors. Crucially, it included only organizations that […]

The post AI Used in 84% of Ransomware Attacks as Identity Infrastructure Comes Under Fire. appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Kimsuky Uses Quasar RAT to Deploy Funhouse Ransomware Through Multi-Stage Scripts

A Kimsuky campaign that delivers Funhouse ransomware through a malicious Hangul document disguised as a resume. The operation combines embedded OLE objects, sequential scripts, a Python backdoor, and Quasar RAT, linking the September 2026 activity to earlier Endpoint ransomware deployments attributed to the group. The findings indicate continuity rather than an entirely new ransomware operation. […]

The post Kimsuky Uses Quasar RAT to Deploy Funhouse Ransomware Through Multi-Stage Scripts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Gentlemen Ransomware Affiliate Uses MCP as C2 Channel in Live Cyberattacks

A Russian-speaking Gentlemen ransomware affiliate used the Model Context Protocol (MCP) to execute commands during live intrusions, turning an AI coding assistant’s tool interface into an operational command-and-control channel. CloudSEK identified the activity while investigating exposed infrastructure belonging to an operator calling himself Azazel. Azazel also operated LEAKNED, an independent leak site that allegedly diverted […]

The post Gentlemen Ransomware Affiliate Uses MCP as C2 Channel in Live Cyberattacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

New Galago Ransomware Operation Emerges With Links to Panzer Extortion Group

A newly identified ransomware operation tracked as Galago has emerged with apparent operational links to the Panzer ransomware group, raising concerns of an expanding double-extortion ecosystem targeting organizations worldwide. Researchers began directly monitoring Galago’s dark leak site (DLS) on 15 September 2026. At the time of observation, the group’s Tor-based leak portal was inactive and […]

The post New Galago Ransomware Operation Emerges With Links to Panzer Extortion Group appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
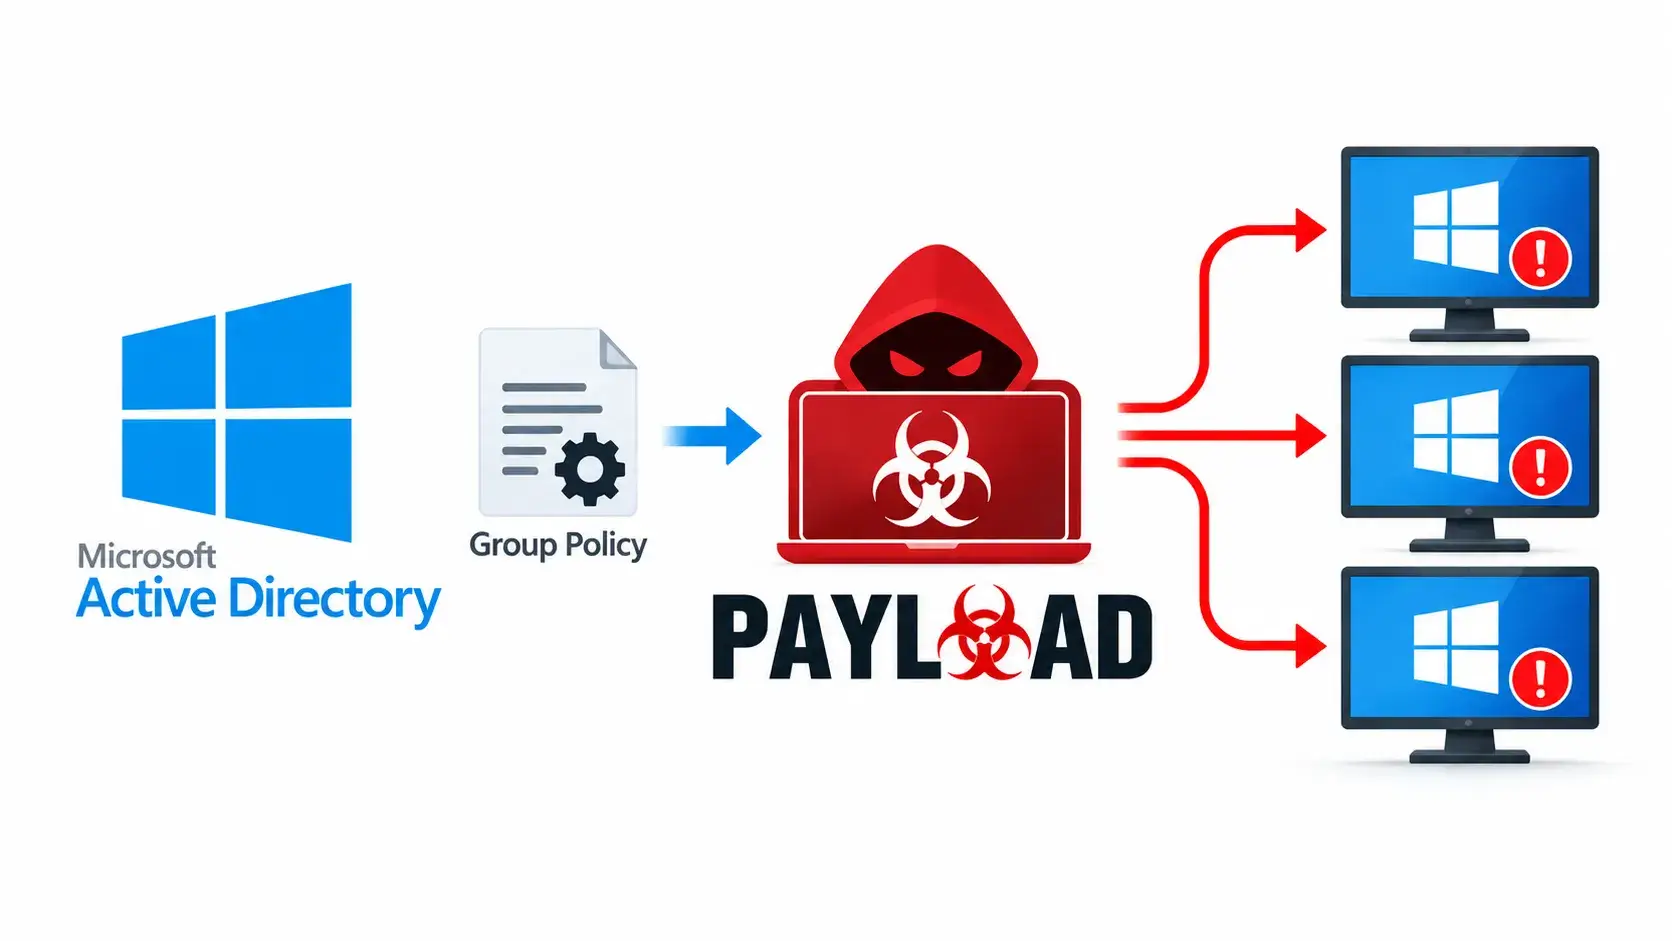
PAYLOAD Ransomware Abuses Active Directory Group Policy to Disrupt Entire Windows Domain

A ransomware incident in which attackers used Active Directory Group Policy to disrupt operations without deploying a Windows encryptor or leaving malware running on endpoints. In April 2026, the attackers accessed a FortiGate SSL VPN using compromised domain credentials, then gained domain-admin-equivalent rights. PAYLOAD Ransomware On April 13, Kaspersky’s Global Emergency Response Team (GERT) created […]

The post PAYLOAD Ransomware Abuses Active Directory Group Policy to Disrupt Entire Windows Domain appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Feral Wolf Hackers Exploit Confluence and 1C to Deploy GenieLocker Ransomware

Feral Wolf has expanded its ransomware tradecraft by abusing exposed Atlassian Confluence servers and insecure 1C:Enterprise deployments to gain access to Russian corporate networks before deploying GenieLocker ransomware. The campaign, tracked from May through August 2026, targeted organizations in the retail, construction, manufacturing, and IT sectors. BI.ZONE DFIR investigators found that the threat actor combined […]

The post Feral Wolf Hackers Exploit Confluence and 1C to Deploy GenieLocker Ransomware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems

A newly observed ransomware operation dubbed SETTRA is abusing the legitimate MeshAgent remote monitoring and management platform for persistence while using recovery-inhibition and defense-evasion techniques to maximize the impact of Windows encryption attacks. Huntress investigated two SETTRA incidents in July and September 2026, uncovering a repeatable operational pattern involving victim-specific ransomware binaries, Windows log clearing, […]

The post New SETTRA Ransomware Uses MeshAgent RMM and BYOVD to Encrypt Windows Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
JADEPUFFER Evolves Agentic Ransomware to Target AI Models and Training Data

JADEPUFFER, the agentic threat actor first linked to an autonomous ransomware operation against exposed Langflow infrastructure, has evolved its tooling to target artificial intelligence models, training datasets, and vector data. Its latest payload, ENCFORGE, marks a shift from conventional database extortion toward destruction-focused attacks on high-value AI and machine-learning assets. The group’s ENCFORGE locker targets […]

The post JADEPUFFER Evolves Agentic Ransomware to Target AI Models and Training Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌