❌

Visualização normal

Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

Hackers Use Stolen Microsoft Entra ID App Credentials to Breach 27 Organizations and Steal Sensitive Data

Hackers are exploiting stolen Microsoft Entra ID application credentials to infiltrate Microsoft 365 and Azure environments, impacting 27 organizations via managed service providers (MSPs) and their downstream clients. Todyl’s MXDR team is monitoring this ongoing campaign, referred to as Key Eater. Since November 1, 2026, the attackers have targeted approximately 45 app registrations across about […]

The post Hackers Use Stolen Microsoft Entra ID App Credentials to Breach 27 Organizations and Steal Sensitive Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Fake Microsoft Support Scams Spread Through Online Ads as Researchers Uncover Organized Fraud Network

An organized fraud operation using paid advertisements, Microsoft Azure hosting, and centrally managed telephone numbers to distribute counterfeit Microsoft support pages. The investigation links one backend serving the kit to Mandarin-speaking developers and registration details referencing Hubei, China. Those findings suggest operational connections, not definitive attribution. Crucially, the identified backend appeared in detections at 11 […]

The post Fake Microsoft Support Scams Spread Through Online Ads as Researchers Uncover Organized Fraud Network appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Analyzes 383,000 Security Vulnerabilities and Reveals Which Flaws Hackers Exploit Most

Microsoft’s analysis of approximately 383,000 disclosed vulnerabilities shows that attackers overwhelmingly favor weaknesses enabling system takeover rather than exploiting vulnerabilities indiscriminately. The research identifies 2,056 CVEs linked to real-world exploitation, roughly 0.5% of the population, highlighting why vulnerability management must prioritize demonstrated attacker utility over disclosure volume or severity scores alone. Covering vulnerabilities published from […]

The post Microsoft Analyzes 383,000 Security Vulnerabilities and Reveals Which Flaws Hackers Exploit Most appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Releases Emergency Fix for Windows 11 Remote Desktop Connection Failures

Microsoft has resolved an issue in Windows 11 that prevented non-administrator users from connecting to devices with Administrator protection enabled. This fix was included in KB5127936, released on October 28, 2026, and is part of subsequent updates. While this issue is urgent for affected organizations, Microsoft has categorized the release as a preview update rather […]

The post Microsoft Releases Emergency Fix for Windows 11 Remote Desktop Connection Failures appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft to Disable SMS and Voice Authentication in Entra ID Starting February 2027

Microsoft will begin retiring Microsoft-provided SMS and voice authentication in Microsoft Entra ID on February 1, 2027, requiring affected organizations to migrate users or arrange alternative telecom delivery before enforcement starts. The change covers Worldwide and Government Community Cloud (GCC) environments, with rollout expected to finish in early February. Administrators should treat February 1 as […]

The post Microsoft to Disable SMS and Voice Authentication in Entra ID Starting February 2027 appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Edge Security Flaws Allow Attackers to Execute Code Without Memory Corruption

Researcher Orange Tsai from DEVCORE has published a complete exploit chain for Microsoft Edge that successfully escapes the browser’s sandbox and executes code on Windows. This exploit utilizes only logical vulnerabilities and does not involve any memory corruption. Tsai developed it for Pwn2Own Berlin 2026, where it earned a $175,000 award and later received the […]

The post Microsoft Edge Security Flaws Allow Attackers to Execute Code Without Memory Corruption appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
💾

Microsoft Releases Emergency Windows Updates to Revoke Trust in Compromised eMudhra Certificates

Microsoft has released an emergency Windows update to remove trust in certificates associated with compromised eMudhra certificate authority keys. The out-of-band update, issued on October 26, 2026, eliminates seven certificates from the Windows trust list. Following this, the same removals were applied to Microsoft Edge on October 27, as stated by the Microsoft Security Response […]

The post Microsoft Releases Emergency Windows Updates to Revoke Trust in Compromised eMudhra Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
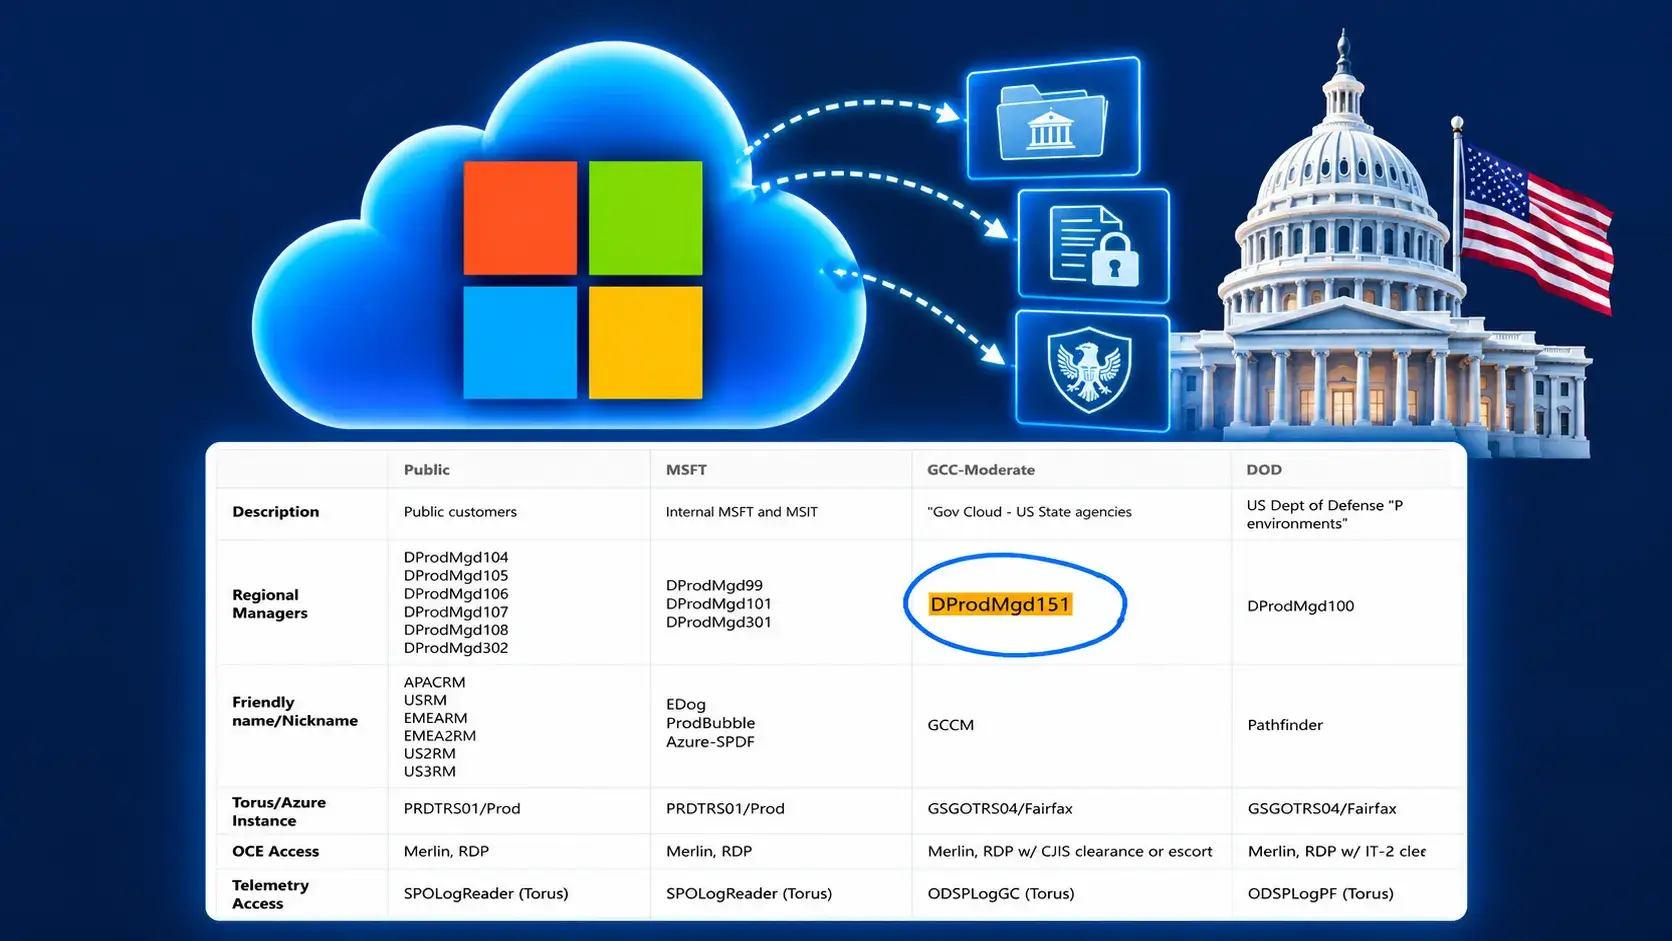
Microsoft Whistleblower Claims Foreign Engineers Can Access Sensitive U.S. Government Cloud Systems

An alleged Microsoft whistleblower has raised concerns regarding overseas engineers accessing U.S. government cloud information through the company’s “escort” support process. Screenshots mentioned in an October 28 post by the X account Conspiracookie allegedly show approval for an engineer based in India to view logs associated with Microsoft’s Government Community Cloud (GCC). However, these claims […]

The post Microsoft Whistleblower Claims Foreign Engineers Can Access Sensitive U.S. Government Cloud Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Windows Server Zero-Day Flaw Lets Attackers Crash Servers With a Single Malicious Packet

Corelight researchers have disclosed a Windows Server vulnerability that lets attackers with network access crash affected systems with a single malicious DFS referral response. This vulnerability, tracked as CVE-2026-70111, affects Windows Server versions 2019, 2022, and 2025. According to Corelight’s disclosure on October 13, Microsoft addressed the flaw in its October 2026 updates. Notably, there […]

The post Windows Server Zero-Day Flaw Lets Attackers Crash Servers With a Single Malicious Packet appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
  • ✇GBHackers on Security | #1 Globally Trusted Cyber Security News Platform
  • Meta and Microsoft Reduce Internal Use of Claude AI Divya
    Meta and Microsoft are reducing employee reliance on Anthropic’s Claude AI while promoting their own coding assistants, according to an October 5 report by The Information. This change relates to internal budgets and development workflows, not a complete withdrawal of Claude from Microsoft’s customer offerings. This reported shift highlights competitive tension, as both companies use […] The post Meta and Microsoft Reduce Internal Use of Claude AI appeared first on GBHackers Security | #1 Global
     

Meta and Microsoft Reduce Internal Use of Claude AI

Meta and Microsoft are reducing employee reliance on Anthropic’s Claude AI while promoting their own coding assistants, according to an October 5 report by The Information. This change relates to internal budgets and development workflows, not a complete withdrawal of Claude from Microsoft’s customer offerings. This reported shift highlights competitive tension, as both companies use […]

The post Meta and Microsoft Reduce Internal Use of Claude AI appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
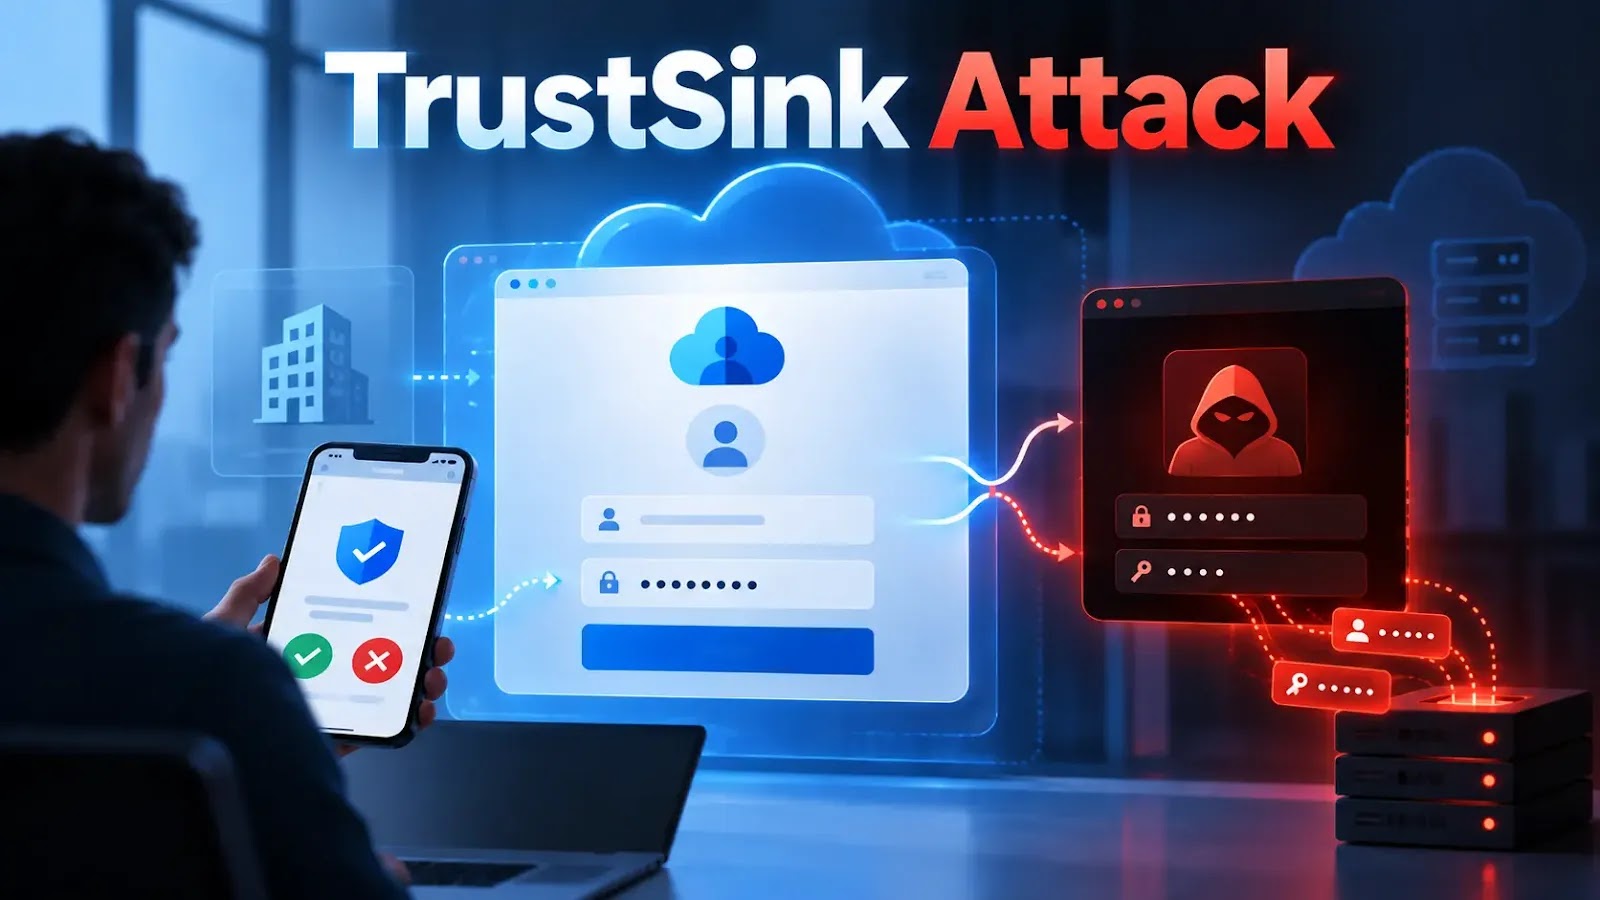
Microsoft Entra TrustSink Attack Uses Rogue MFA Provider to Steal Passwords

TrustSink, a post-compromise credential-phishing technique that abuses Microsoft Entra External Authentication Methods (EAMs) to place a rogue password prompt inside an otherwise legitimate Microsoft sign-in flow. The attack enables an adversary with elevated tenant privileges to capture plaintext passwords while returning a valid signed token to Entra, allowing the victim’s login to complete without an […]

The post Microsoft Entra TrustSink Attack Uses Rogue MFA Provider to Steal Passwords appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
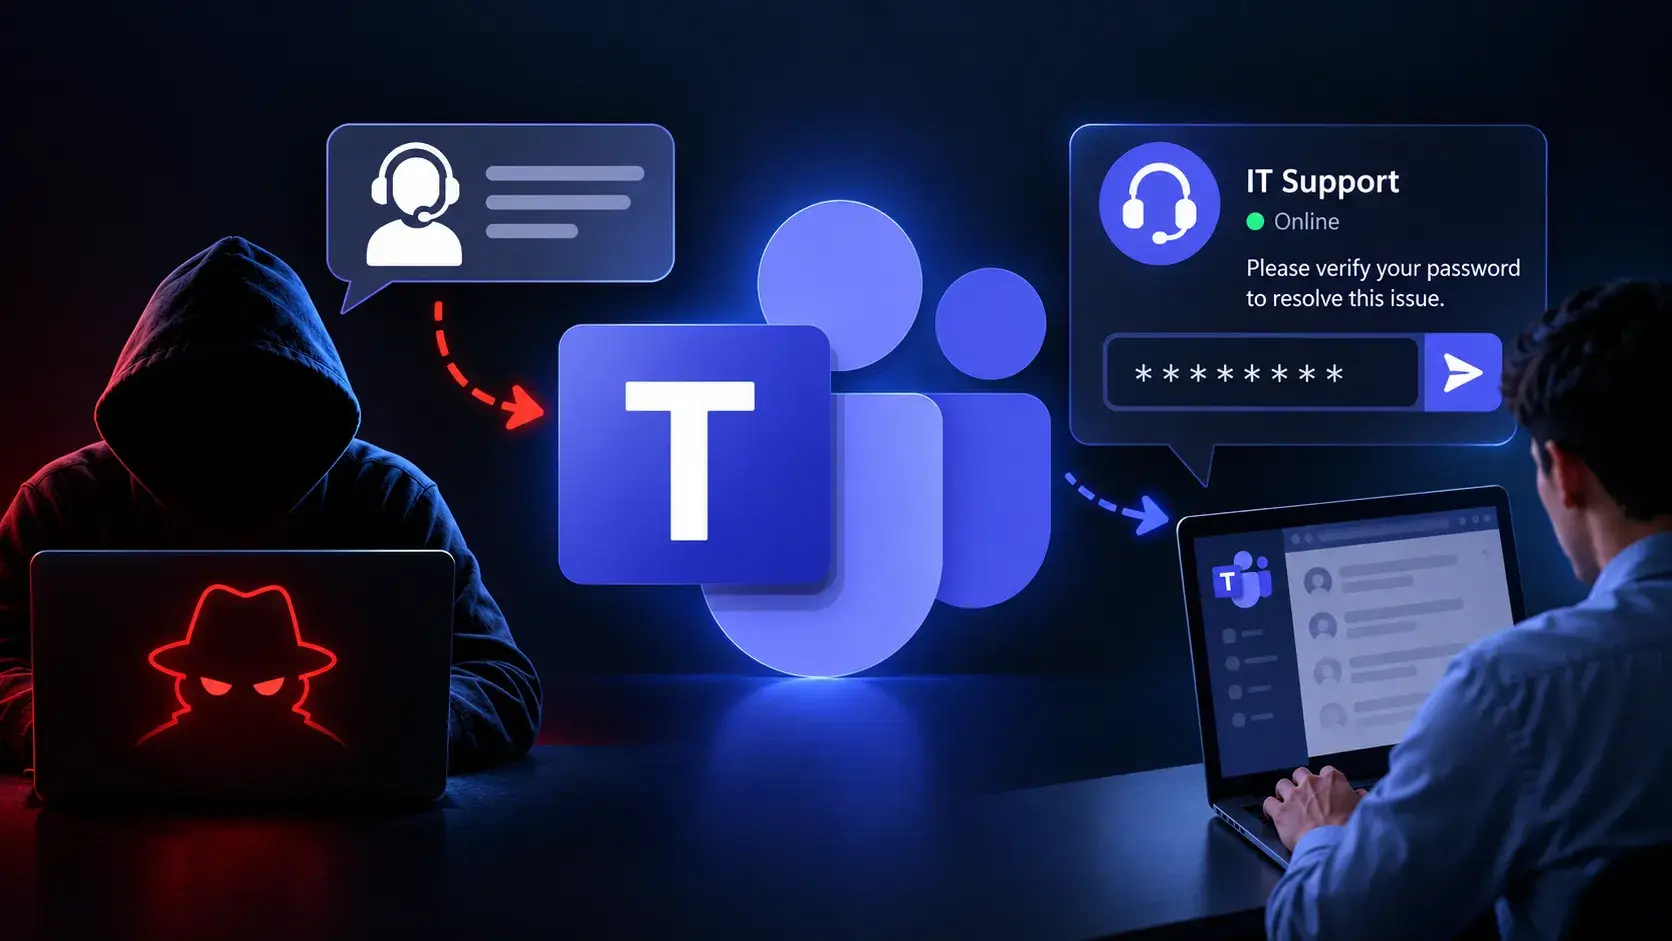
Hackers Abuse Microsoft Teams to Pose as IT Support and Steal Employee Passwords

Threat actors are increasingly abusing Microsoft Teams’ external chat capabilities to impersonate corporate IT help desks. They trick employees into installing malware, granting remote access, and stealing Windows credentials. These attacks exploit a simple vulnerability: employees tend to distrust suspicious emails but often do not apply the same caution to collaboration platforms like Teams. Attackers […]

The post Hackers Abuse Microsoft Teams to Pose as IT Support and Steal Employee Passwords appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Offers $60,000 Bounty for Critical Cross-Tenant Vulnerabilities

Microsoft has expanded its incentives for security researchers focusing on Dynamics 365 and Power Platform, offering rewards ranging from $1,250 to $60,000 for qualifying vulnerabilities. The program prioritizes flaws that have a direct and demonstrable security impact in supported cloud services, including cross-tenant issues that could compromise isolation between customer environments. Microsoft Offers $60,000 Bounty […]

The post Microsoft Offers $60,000 Bounty for Critical Cross-Tenant Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Pose as IT Support to Hijack Microsoft 365 Accounts With Fake Passkey Alerts

Threat actors are impersonating corporate IT helpdesk staff in an active social-engineering campaign that hijacks Microsoft 365 identities, establishes MFA persistence, and systematically collects data from SharePoint, OneDrive, and Exchange Online. Microsoft Security Research said it has observed the cloud-focused intrusions since May 2026. The activity is marked by unusual sign-ins, attacker-added authentication methods, extensive […]

The post Hackers Pose as IT Support to Hijack Microsoft 365 Accounts With Fake Passkey Alerts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Windows BitLocker Flaw Lets Attackers Execute Code on Vulnerable Systems

Microsoft disclosed CVE-2026-69449, an Important-severity vulnerability in Windows BitLocker. This issue is classified as a heap-based buffer overflow (CWE-122) and may allow remote code execution (RCE). Microsoft released details about this vulnerability on September 8, 2026. The CVSS 3.1 base score is 6.7, with a temporal score of 5.8. Windows BitLocker Flaw The vulnerability uses […]

The post Windows BitLocker Flaw Lets Attackers Execute Code on Vulnerable Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Teams Adds QR Code Protection to Block Phishing and Fraud

Microsoft is developing a new security feature for Teams messaging that will obscure QR codes sent by external users. This measure aims to help organizations reduce phishing and fraud risks associated with malicious QR code campaigns. Listed under Microsoft 365 Roadmap ID 570439, this feature is currently in development and is scheduled for rollout in […]

The post Microsoft Teams Adds QR Code Protection to Block Phishing and Fraud appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft 365 Direct Send Bypass Lets Attackers Spoof Internal Users Without Credentials

A Microsoft 365 email security-control bypass that lets attackers submit unauthenticated messages posing as internal users by leaving one SMTP field blank. The technique targets Exchange Online’s RejectDirectSend setting and does not represent a vulnerability in Microsoft software or in ReliaQuest systems; instead, it exposes a limitation in how the control evaluates Direct Send traffic. […]

The post Microsoft 365 Direct Send Bypass Lets Attackers Spoof Internal Users Without Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌