❌

Visualização normal

Hoje — 10 de Novembro de 2026GBHackers on Security | #1 Globally Trusted Cyber Security News Platform

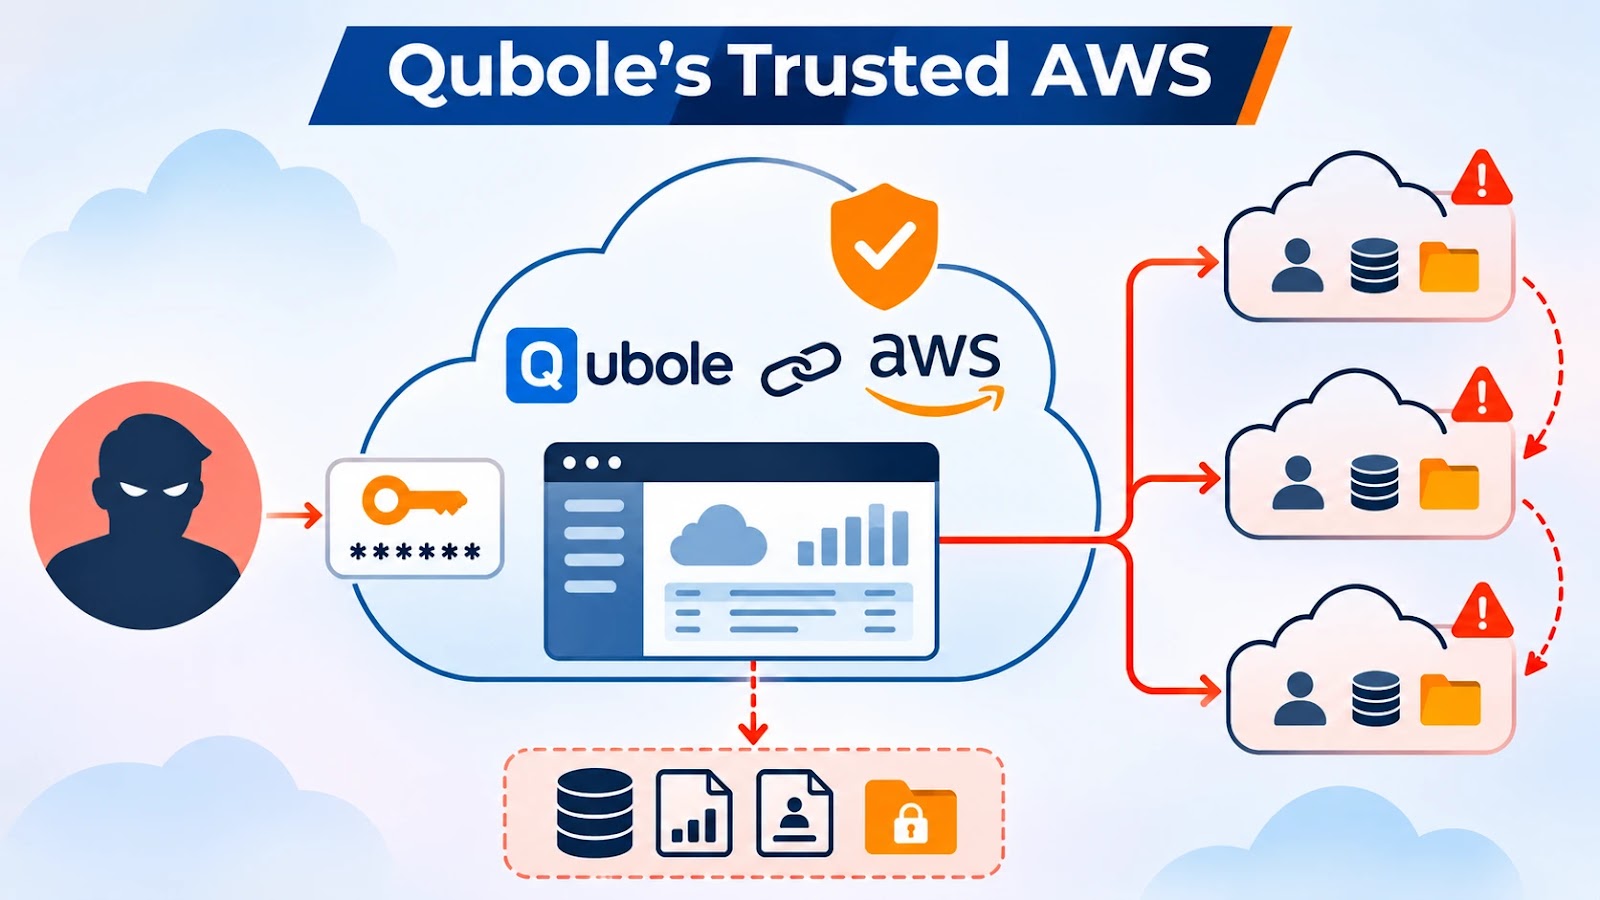
Hackers Abuse Qubole’s Trusted AWS Access to Breach Multiple Cloud Accounts and Steal Sensitive Data

Hackers abused AWS credentials associated with Qubole to breach multiple customer cloud environments, harvest secrets, and steal sensitive S3 data between October 14 and October 26, 2026. Sentra reported that more than a dozen organizations were hacked, describing the broader impact as involving dozens of Qubole customers. Some compromised integration roles had remained dormant for […]

The post Hackers Abuse Qubole’s Trusted AWS Access to Breach Multiple Cloud Accounts and Steal Sensitive Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

SAP November 2026 Patch Day Fixes Four Maximum-Severity Security Vulnerabilities

SAP released 35 new security notes and four GitHub security advisories on November 10, 2026, alongside three updates to earlier notes. Four vulnerabilities carry the maximum CVSS score of 10.0 and affect NetWeaver Internet Communication Manager, Web Dispatcher, SAP Gateway, and the SAML2 Service Provider. The release covers memory corruption, missing authentication, access control failures, […]

The post SAP November 2026 Patch Day Fixes Four Maximum-Severity Security Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Critical Apache Airflow Flaw CVE-2026-68982 Enables Unauthenticated Remote Code Execution

A critical missing-authentication flaw in Apache Airflow lets attackers run code on Celery workers without any Airflow credentials. Tracked as CVE-2026-68982, the bug is classified as CWE-306 and affects Airflow versions before 3.4.0 that use CeleryExecutor. Anyone who can write to the Celery broker can make a worker run any Python function it can import, […]

The post Critical Apache Airflow Flaw CVE-2026-68982 Enables Unauthenticated Remote Code Execution appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
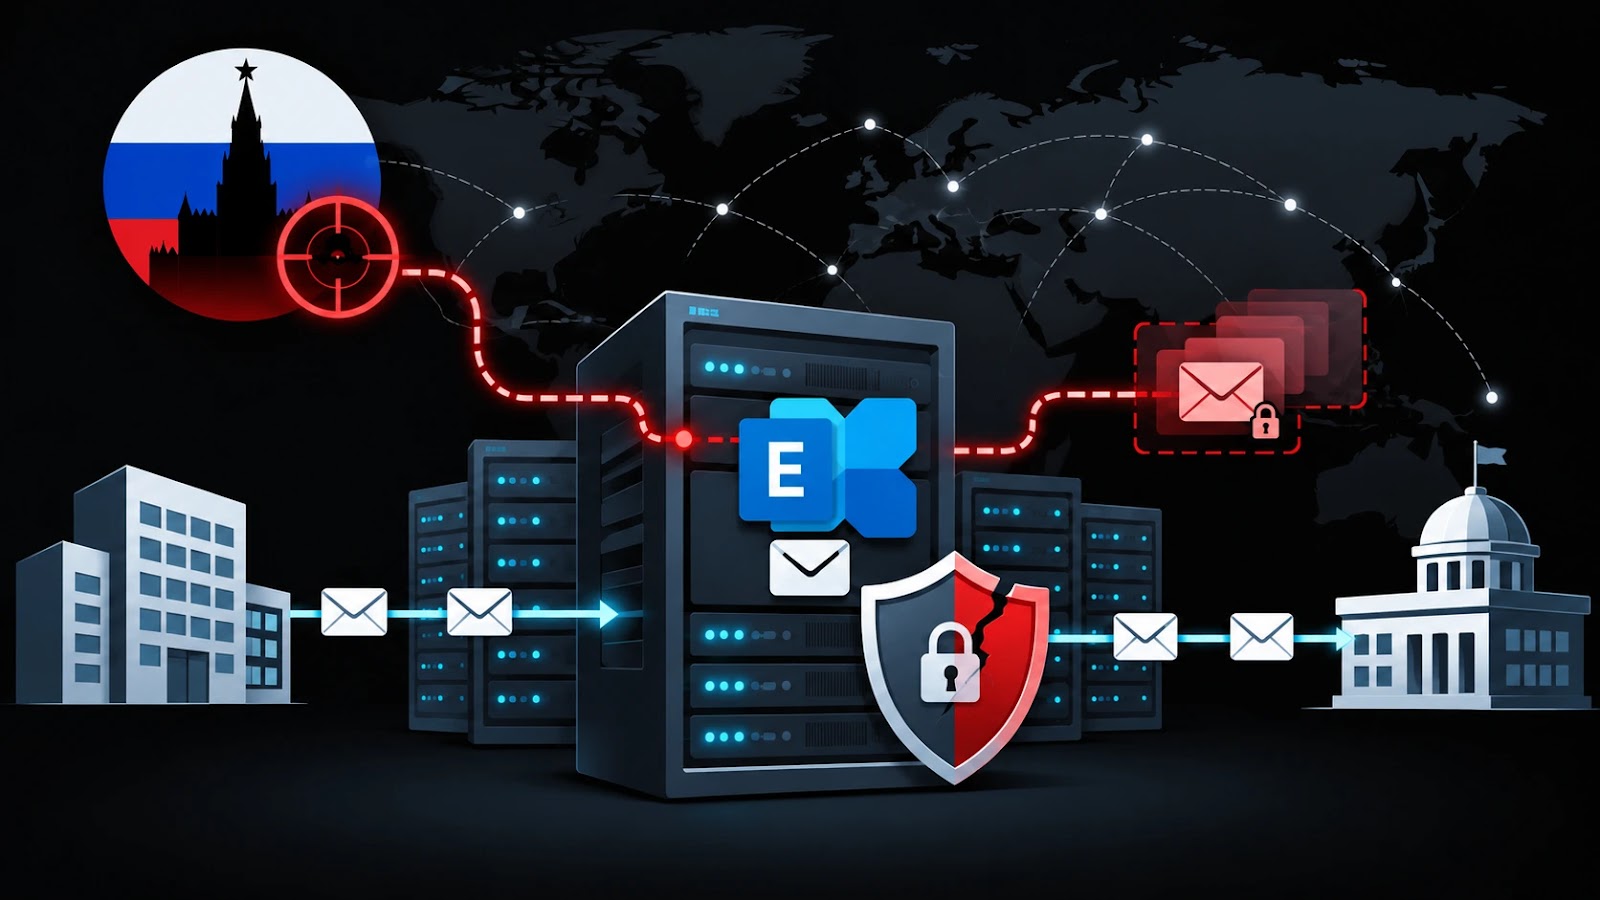
Russian-Linked Turla Hackers Abuse Microsoft Exchange Infrastructure to Target Sensitive Communications

Russian-linked espionage group Turla has deployed a previously undocumented .NET malware toolkit that turns compromised Microsoft Exchange servers into surveillance platforms and command infrastructure. Named Cereal, the modular toolset intercepts selected emails while allowing legitimate messages to continue through the transport pipeline, concealing intelligence collection inside routine government communications. ESET disclosed the findings on November […]

The post Russian-Linked Turla Hackers Abuse Microsoft Exchange Infrastructure to Target Sensitive Communications appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
SEGA Confirms Data Breach Exposing 2.19 Million Customer Email Addresses Following Third-Party Cyberattack

SEGA confirmed on November 9, 2026, that attackers stole 2,196,044 customer email addresses after breaching Arara, its newsletter provider. Of these, 92,273 included information linked to newsletter delivery. The incident affected messages promoting SEGA and SEGA Fave products, highlighting the risks of third-party breaches. The intrusion involved Arara Message, an outsourced email distribution platform. SEGA […]

The post SEGA Confirms Data Breach Exposing 2.19 Million Customer Email Addresses Following Third-Party Cyberattack appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
North Korean Hackers Target Drone Technology and Software Supply Chains in New Cyberespionage Campaigns

North Korea-aligned hackers have renewed attacks on drone technology companies while expanding operations against software supply chains. Together, these campaigns expose industrial knowledge and software distribution channels to compromise. ESET’s APT Activity Report, published October 28, covers operations observed between April and September 2026. Researchers identified renewed Lazarus targeting of the drone sector and a […]

The post North Korean Hackers Target Drone Technology and Software Supply Chains in New Cyberespionage Campaigns appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Fireworks AI Hit by LLMJacking Cyberattack Exposing Customer Data and AI Model Weights

Fireworks AI has disclosed a wider security breach involving customer account information, billing records, secrets, datasets, and incomplete model weights. Its November 9 update links the activity to financially motivated criminals pursuing LLM-jacking, which involves stealing access to large language models and reselling their capacity through illegal routing gateways. The investigation remains ongoing. The company […]

The post Fireworks AI Hit by LLMJacking Cyberattack Exposing Customer Data and AI Model Weights appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Dark Storm Team Offers DDoS Attacks, Database Dumps, and Stolen Access Through Telegram Channels

Dark Storm Team uses Telegram as both a hacktivist broadcasting network and a cybercrime storefront, advertising distributed denial-of-service attacks, database dumps, compromised accounts, and surveillance access. A StealthMole investigation described in the supplied material traces an operation combining politically framed disruption claims with commercial services, cryptocurrency payments, and repeated channel migrations. First observed in late […]

The post Dark Storm Team Offers DDoS Attacks, Database Dumps, and Stolen Access Through Telegram Channels appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Apple iOS 27.2.1 Fixes 9 Security Vulnerabilities Affecting iMessage, Bluetooth, and AirPlay

Apple released iOS 27.2.1 and iPadOS 27.2.1 on November 9, 2026, fixes nine security vulnerabilities and affect iMessage, Bluetooth pairing, AirPlay, App Intents, and the brotli compression library. Apple’s security releases page lists the update. The flaws range from memory corruption to weak authorization and broken rate limits. Users should install the update soon. The […]

The post Apple iOS 27.2.1 Fixes 9 Security Vulnerabilities Affecting iMessage, Bluetooth, and AirPlay appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
11 Cybersecurity Maturity Assessment Tools: The 2026 Buyer’s Verdict Guide

Maturity assessment answers the board’s simplest hard question “how good are we, really, and versus whom?” and the tooling market answers through four different lenses: framework self-assessment platforms (NIST CSF, C2M2), telemetry-driven scores computed from live estates, outside-in ratings benchmarks, and exposure-grounded posture math. Lens honesty is the buying discipline, because a questionnaire score and […]

The post 11 Cybersecurity Maturity Assessment Tools: The 2026 Buyer’s Verdict Guide appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Ontem — 9 de Novembro de 2026GBHackers on Security | #1 Globally Trusted Cyber Security News Platform

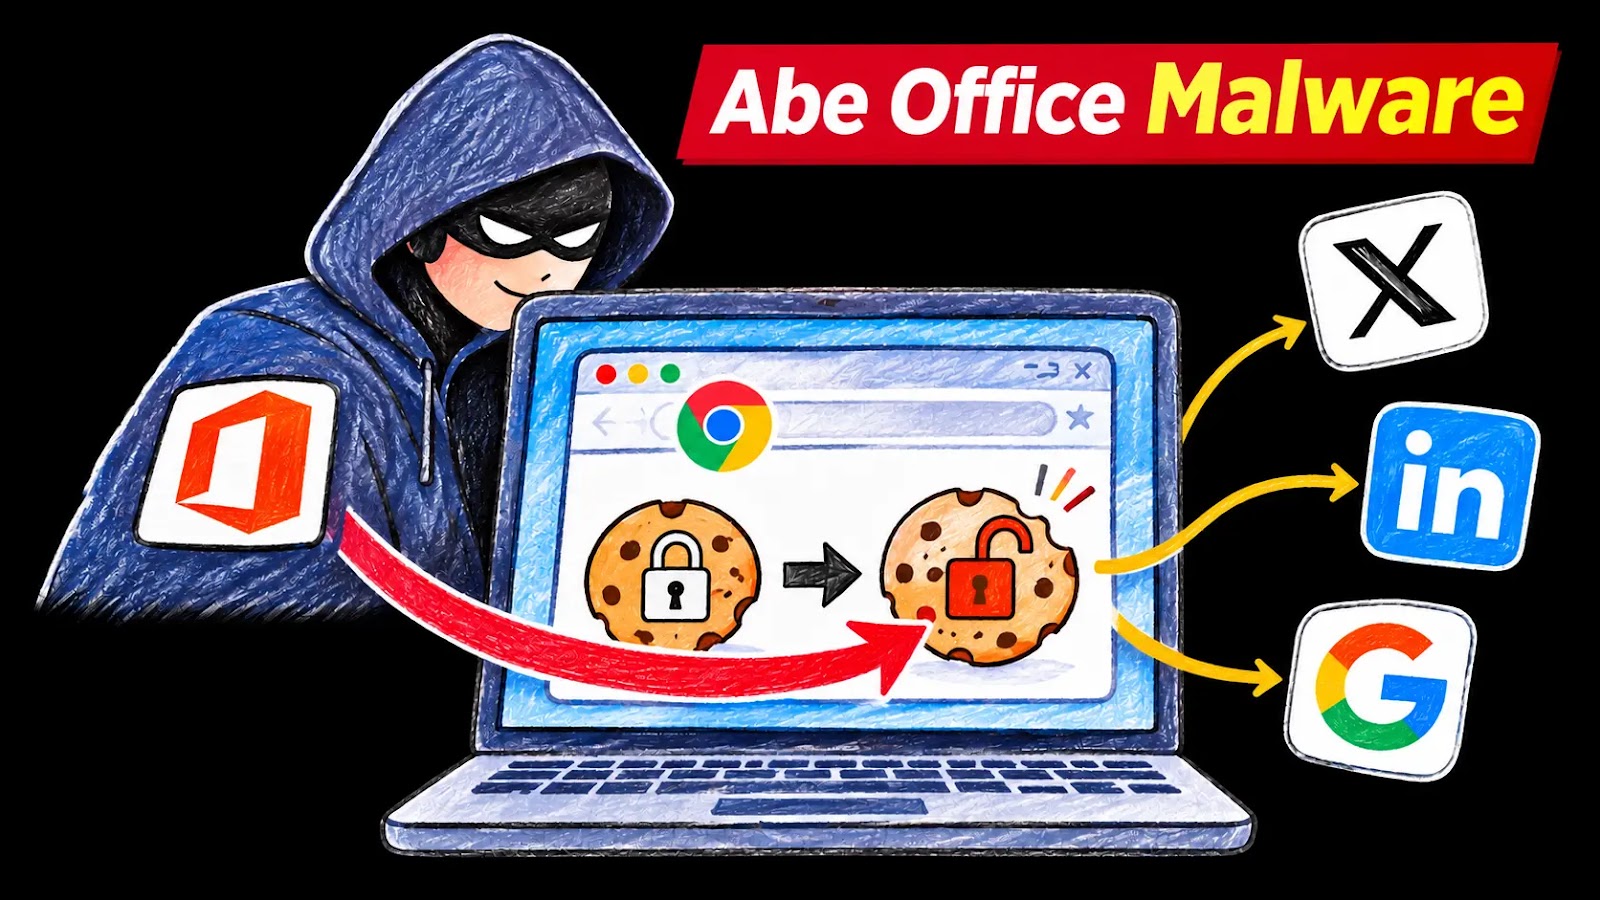
New Abe Office Malware Tricks Chrome Into Decrypting Its Own Protected Browser Cookies

A newly analyzed remote-access trojan masquerading as an “Abe Office workstation helper” combines hidden-browser control with tooling designed to bypass Chrome’s App-Bound Encryption. Rather than breaking the cryptography, its browser stealer injects a helper into Chrome and requests decryption from inside the trusted browser process. The supplied analysis credits MalwareHunterTeam with identifying the sample, AbeAgent.exe, […]

The post New Abe Office Malware Tricks Chrome Into Decrypting Its Own Protected Browser Cookies appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
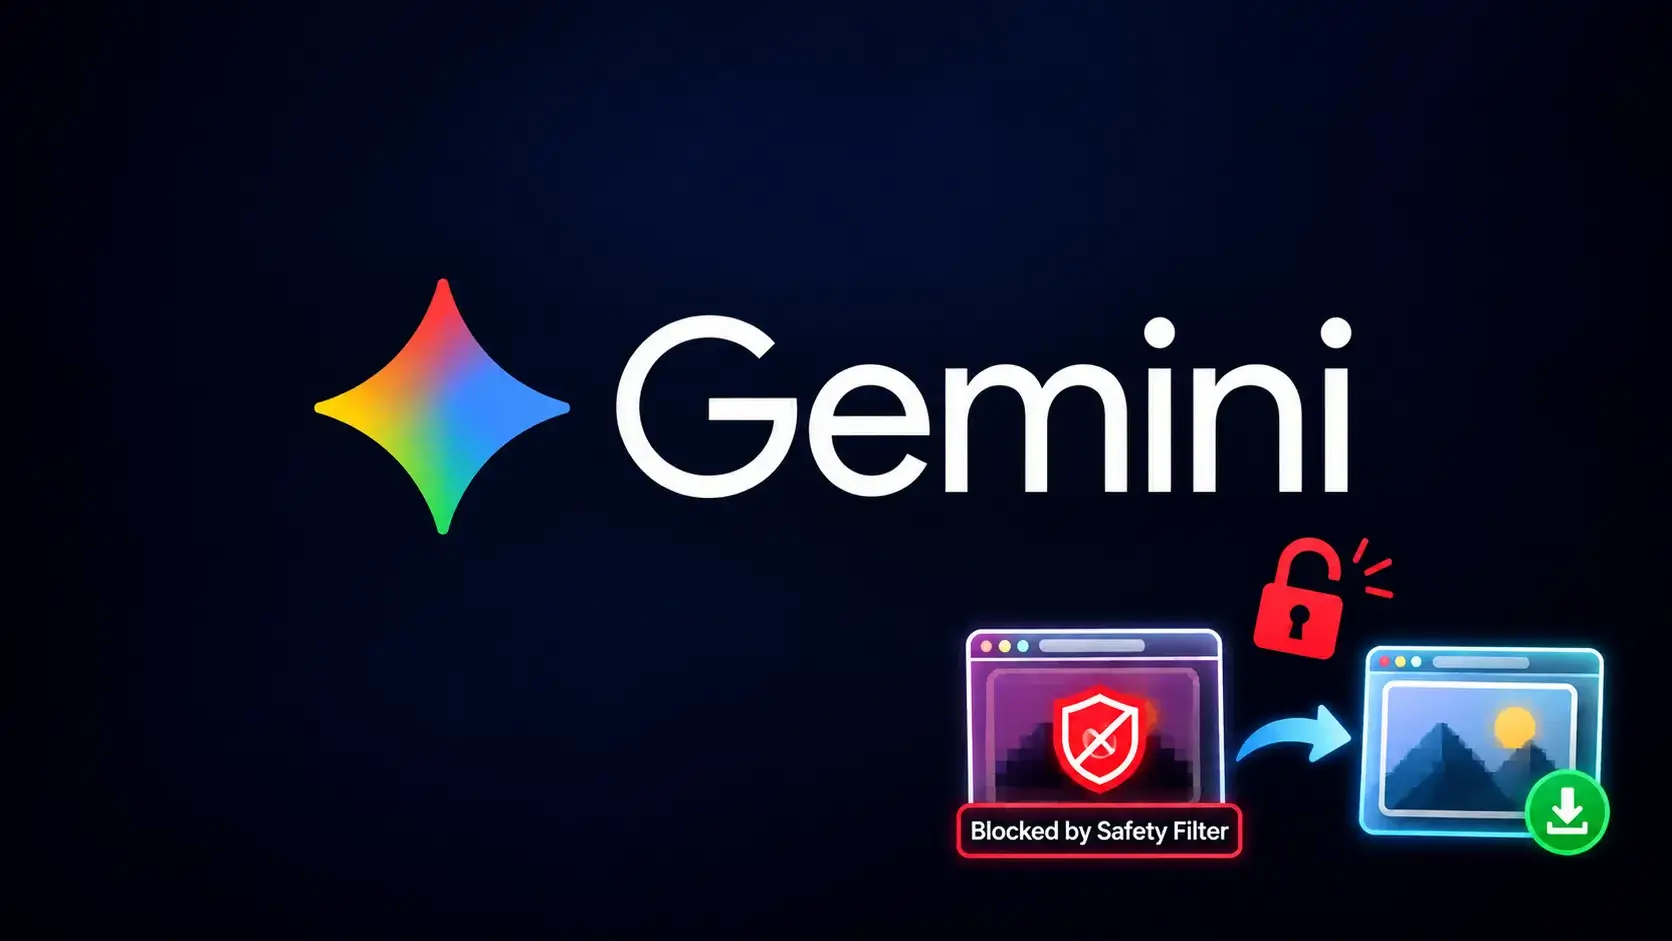
Google Gemini Safety Filter Bypass Exposes Blocked AI Images Through Download Links

Google Gemini exposed images that its safety filters had rejected through download links, revealing an infrastructure weakness rather than a conventional model jailbreak. Fog Security researcher Jason Kao disclosed the findings on November 5, 2026, describing how Gemini could refuse an image request while still delivering the blocked artifact. Retesting on October 22 found changed […]

The post Google Gemini Safety Filter Bypass Exposes Blocked AI Images Through Download Links appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
ModSecurity WAF Vulnerability Allows Attackers to Bypass File Upload Restrictions Using Crafted HTTP Requests

Two high-severity flaws in the open-source ModSecurity web application firewall (WAF) let attackers slip past upload filters or crash server workers with a single crafted HTTP request. Maintainers published both advisories on September 30, 2026, as part of a larger batch that also covers multiple ModSecurity vulnerabilities that enable WAF bypass. ModSecurity WAF Vulnerability The […]

The post ModSecurity WAF Vulnerability Allows Attackers to Bypass File Upload Restrictions Using Crafted HTTP Requests appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
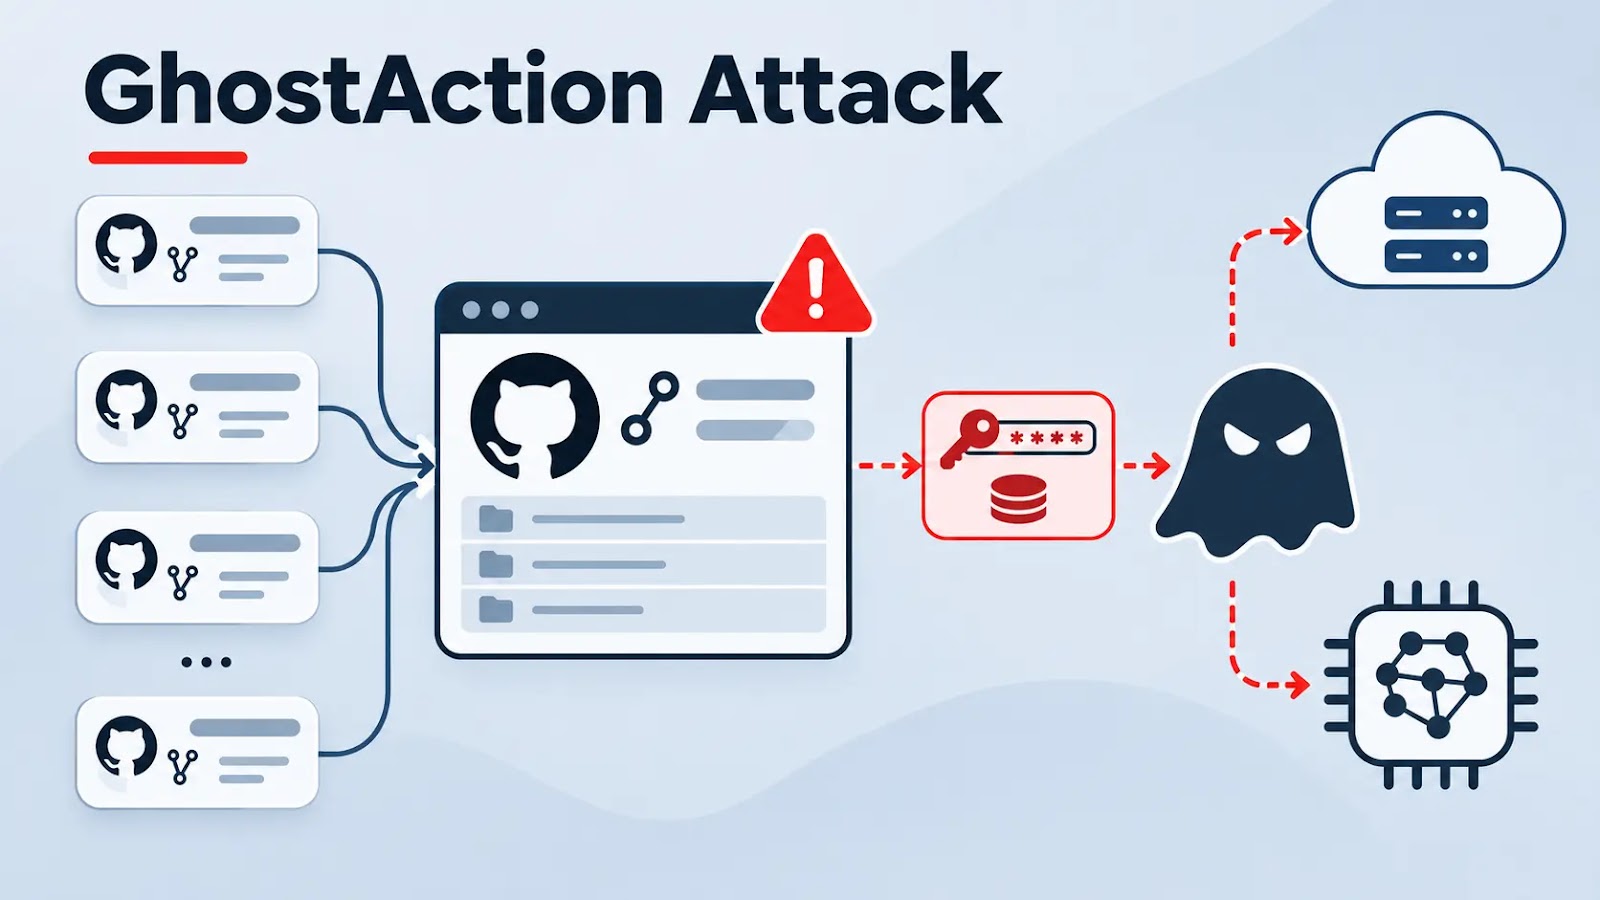
GhostAction Attack Hits Tens of Thousands of GitHub Repositories to Steal Cloud and AI Credentials

A new wave of the GhostAction supply chain campaign has pushed a credential-stealing GitHub Actions workflow into tens of thousands of repositories. It now hunts for cloud and AI keys buried in source code and git history, in addition to CI/CD secrets. Socket says it has identified more than 500 GitHub accounts that committed the […]

The post GhostAction Attack Hits Tens of Thousands of GitHub Repositories to Steal Cloud and AI Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
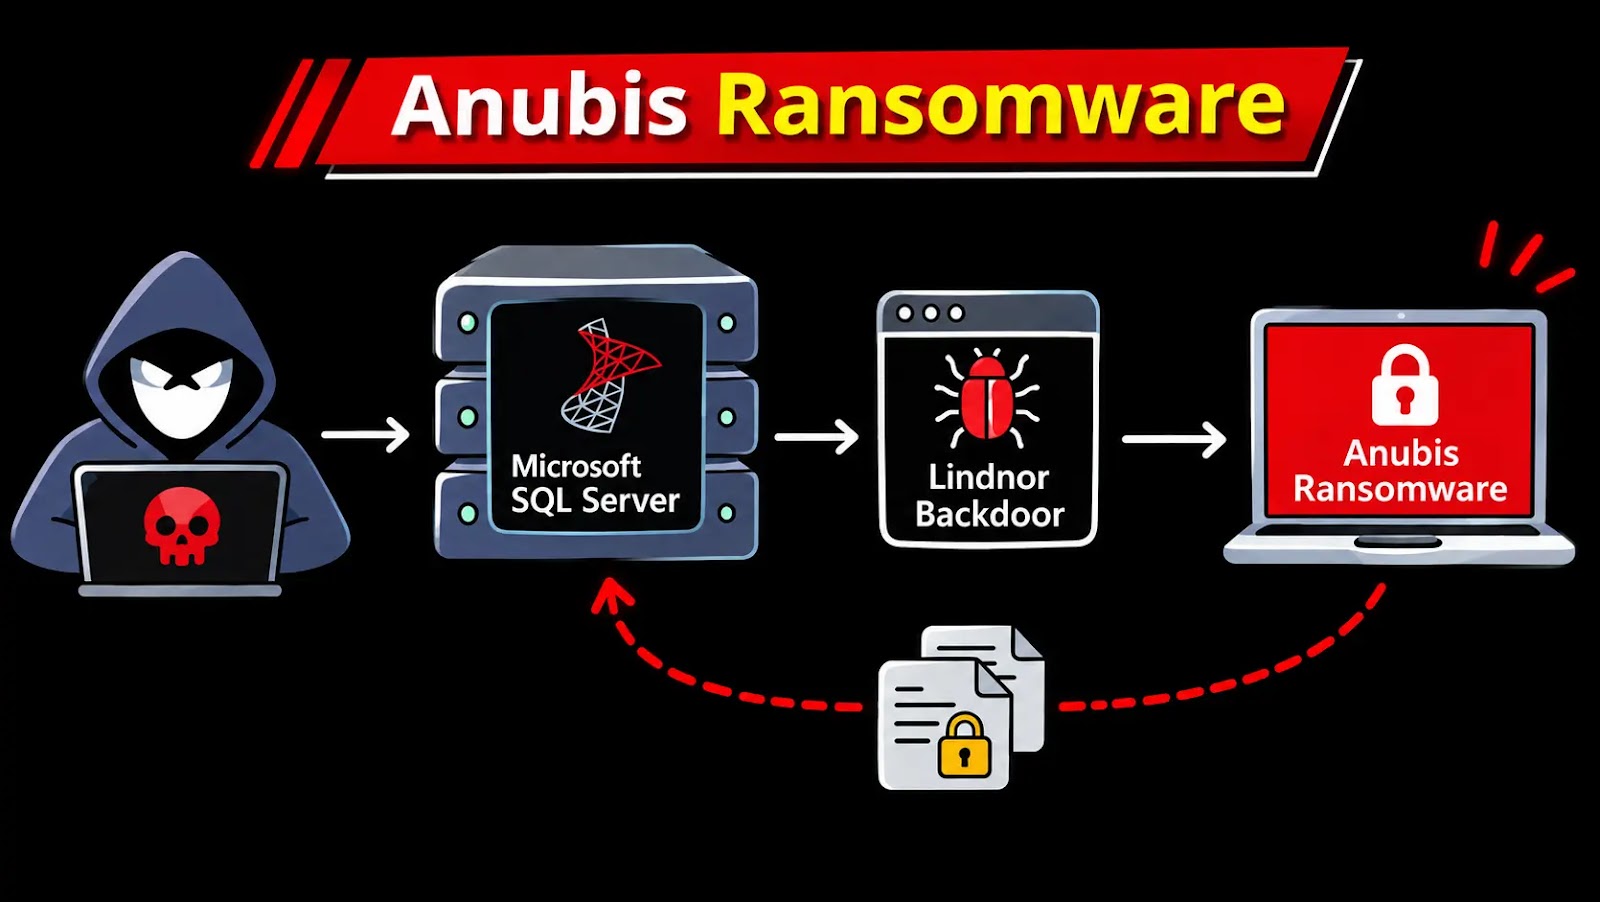
Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack

Attackers deploying Anubis ransomware hit a U.S. organization in October 2026 with a previously undocumented custom backdoor. The malware sat on two Microsoft SQL Server machines, disguised as a Chrome component on one and a VMware file on the other. The encryption payload was blocked, and there is no evidence that any files were encrypted. […]

The post Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CISA and FBI Warn of Cyberattacks Targeting Industrial Refrigeration and Cold Chain Monitoring Systems

CISA and the FBI, alongside HHS, USDA, and the Department of Transportation, have warned of ongoing cyberattacks targeting industrial refrigeration and cold chain monitoring systems worldwide. Published November 5, 2026, their joint fact sheet urges critical infrastructure operators to secure controllers that protect food, medicines, chemicals, and other temperature-sensitive products. The warning applies to several […]

The post CISA and FBI Warn of Cyberattacks Targeting Industrial Refrigeration and Cold Chain Monitoring Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
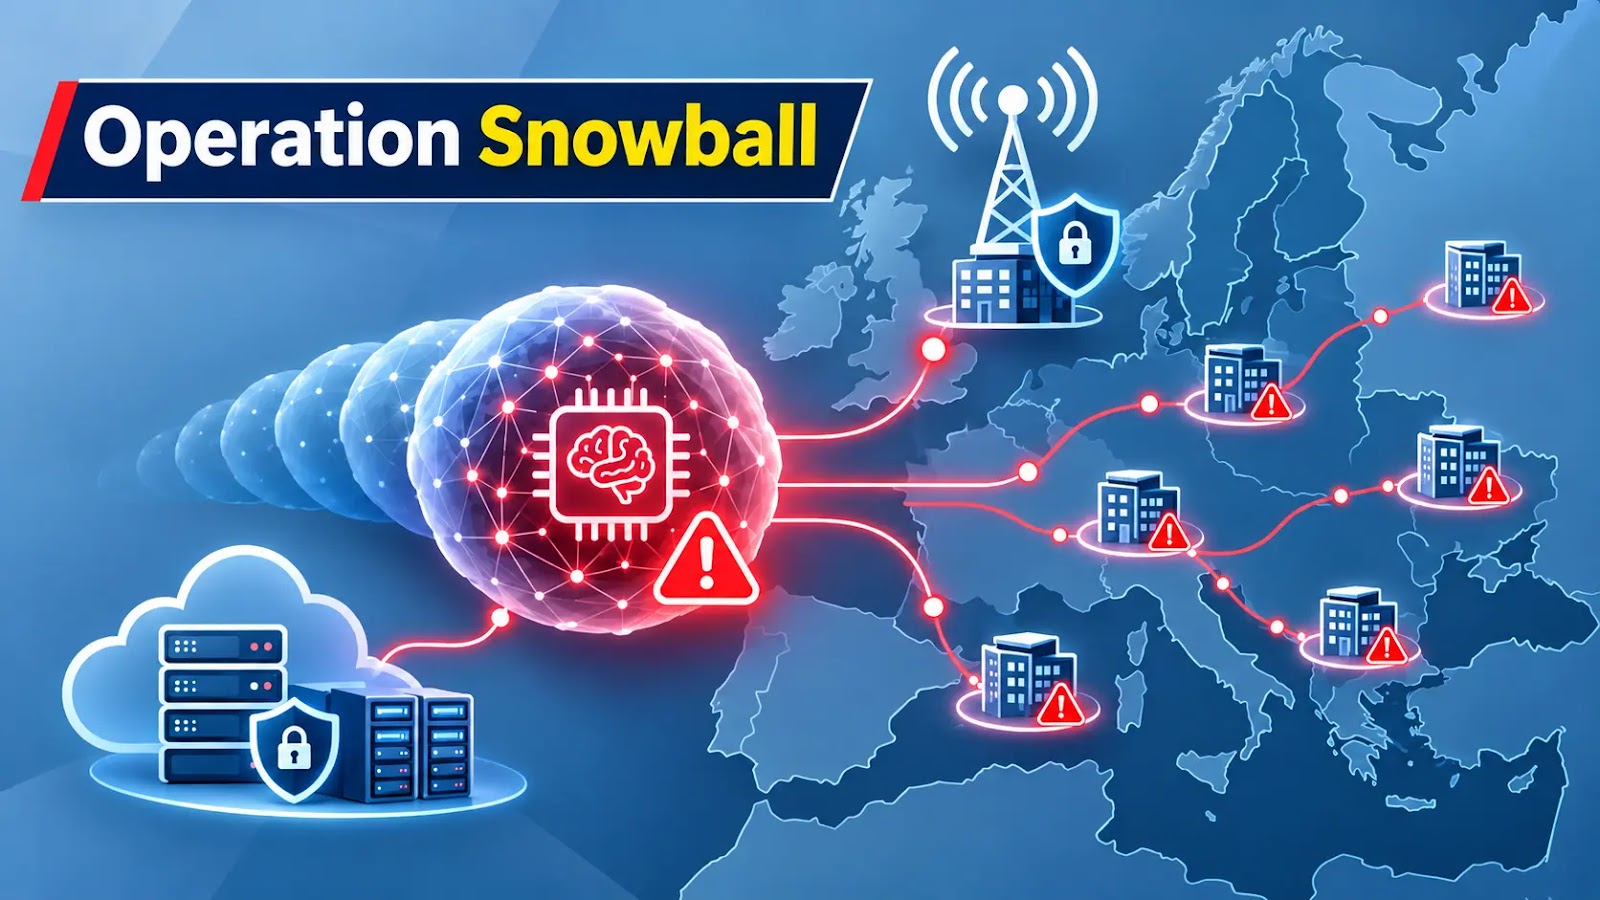
Operation Snowball Exposes AI Hacking Campaign Targeting European Telecom and 13 Hosted Organizations

An exposed open directory revealed an autonomous AI intrusion harness that spent more than two weeks attacking a European telecom provider and 13 organizations hosted in its data centers and cloud. The report, published on November 8, 2026, calls the campaign Operation Snowball. The researchers withheld the directory’s IP address to protect the victims. A […]

The post Operation Snowball Exposes AI Hacking Campaign Targeting European Telecom and 13 Hosted Organizations appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
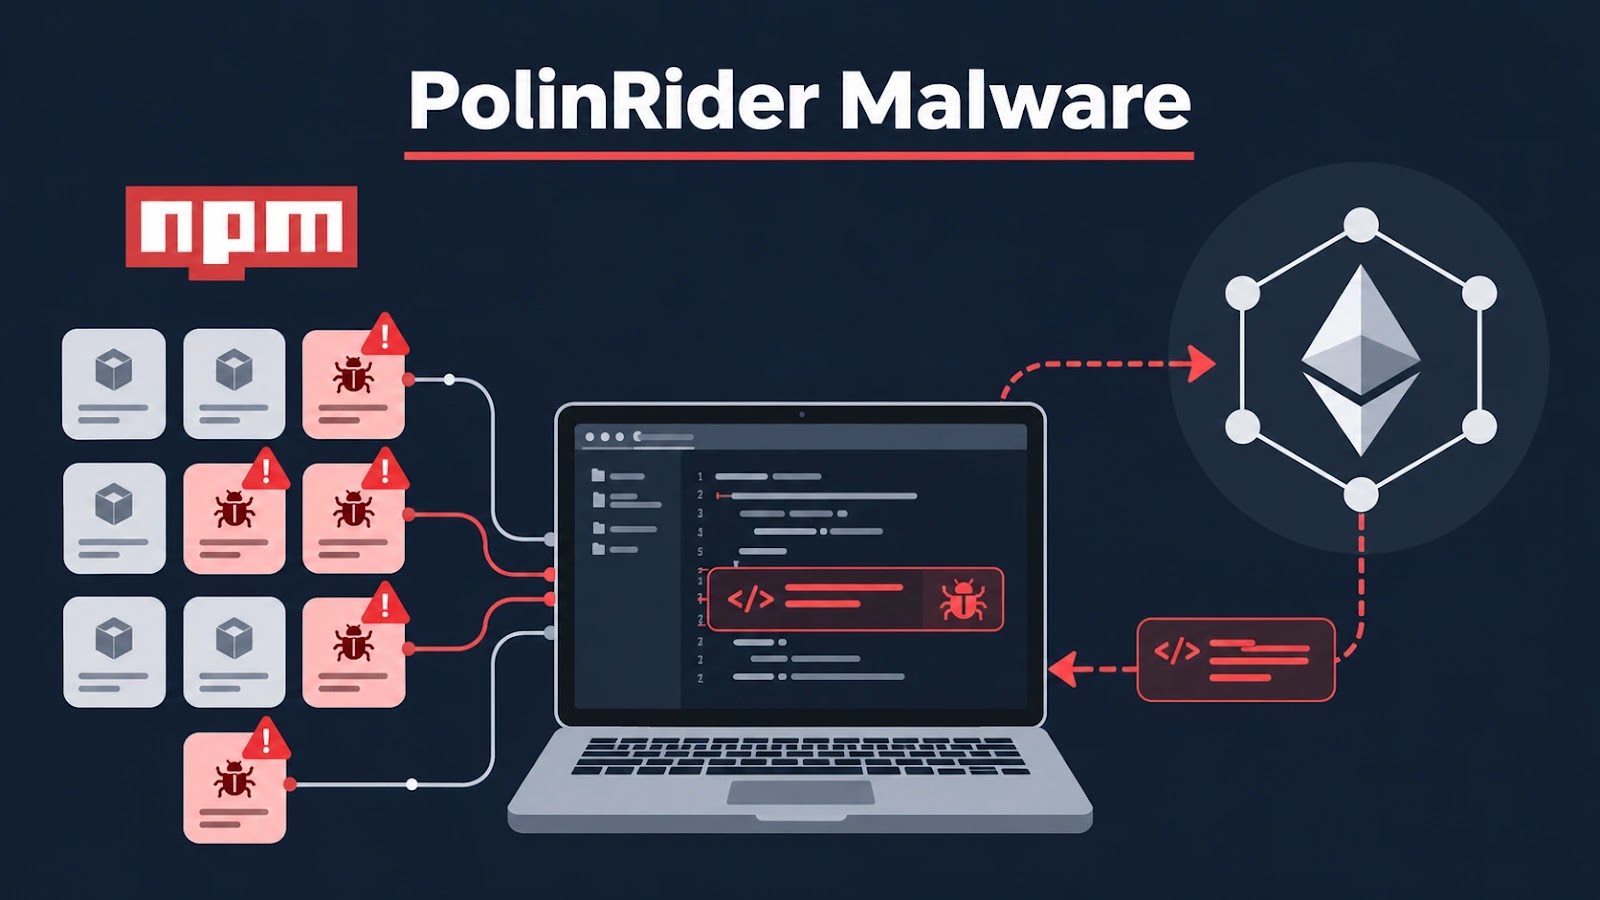
PolinRider Malware Returns in 10 Hijacked npm Packages Using Ethereum Blockchain to Deliver Malicious Code

A concealed JavaScript loaders in 12 releases across 10 hijacked npm packages, linking the compromise to previously documented PolinRider activity. Investigated on November 4, 2026, the releases use Ethereum transactions to discover remote payload servers and execute downloaded code inside developer environments, build systems, or applications. Sonatype tracks the finding as sonatype-2026-010515.guide. Unlike installation-triggered supply-chain […]

The post PolinRider Malware Returns in 10 Hijacked npm Packages Using Ethereum Blockchain to Deliver Malicious Code appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

SonicWall Warns of Actively Exploited SSL-VPN Vulnerability That Bypasses SAML and MFA Protection

SonicWall has urged customers to address an SSL-VPN authentication vulnerability that can bypass SAML controls, including associated multifactor authentication measures. This issue is tracked as CVE-2026-19868 and affects SonicOS deployments that utilize SAML for SSL-VPN logins. The company has investigated reports suggesting potential exploitation but has not confirmed a widespread attack campaign in its advisory. […]

The post SonicWall Warns of Actively Exploited SSL-VPN Vulnerability That Bypasses SAML and MFA Protection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Critical React Server Components Vulnerability Allows Unauthenticated Attackers to Execute Malicious Code on Servers

A serious vulnerability in React Server Components may enable unauthenticated attackers to execute malicious code on affected servers. The advisory, released on October 14, 2026, assigns the issue a CVSS v4.0 score of 9.5. React maintainers advise that users update their systems immediately, though they emphasize that the conditions necessary for exploitation are extremely rare. […]

The post Critical React Server Components Vulnerability Allows Unauthenticated Attackers to Execute Malicious Code on Servers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌