❌

Visualização normal

Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

NIST Releases New Cybersecurity Guidelines to Protect Small Businesses From Phishing and Ransomware Attacks

The National Institute of Standards and Technology (NIST) released new cybersecurity guidance to help solo business owners protect themselves against threats like phishing, ransomware, and account compromise. Published on November 2, 2026, NIST Cybersecurity White Paper 50 simplifies the Cybersecurity Framework 2.0 and offers practical actions for businesses with limited IT infrastructure. The publication, Small […]

The post NIST Releases New Cybersecurity Guidelines to Protect Small Businesses From Phishing and Ransomware Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

New ChatGPT Phishing Kit Uses Rotating WordPress Websites to Steal Payment Details and OTPs

A phishing campaign impersonating OpenAI is using disposable WordPress websites and live attacker oversight to steal payment card details and potentially capture one-time passwords. Fraudulent ChatGPT Plus billing emails warn that subscription payments have failed, directing recipients to counterfeit checkout pages where operators control the victim’s next step. The operation combines infrastructure churn with interactive […]

The post New ChatGPT Phishing Kit Uses Rotating WordPress Websites to Steal Payment Details and OTPs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK

A judicial-themed phishing campaign targeting Colombian organizations that delivers XWorm through obfuscated scripts, encrypted PowerShell, and a reusable .NET loader. The recovered loader is binary-identical to one documented in a September 10, 2026, UK-linked case, connecting otherwise differently packaged delivery chains. The overlap establishes loader reuse, not common attribution. Different payload hashes, execution targets, and […]

The post Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Scammers Exploit Dell and Staples Order Emails to Bypass Traditional Phishing Detection

Scammers are abusing legitimate Dell and Staples order notifications to deliver callback phishing lures, embedding fraudulent helpline numbers inside transactional emails that pass authentication checks. Cisco Talos observed roughly 1,400 messages across two campaigns, highlighting how trusted retail infrastructure can carry attacker-controlled instructions without relying on spoofed senders or malicious links. The activity extends a […]

The post Scammers Exploit Dell and Staples Order Emails to Bypass Traditional Phishing Detection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Scammers Turn Legitimate Fintech Platforms Into Phishing Tools to Steal Banking Details

Scammers have weaponized a legitimate spend-management platform to send phishing messages and validate stolen financial credentials, turning trusted payment infrastructure into an operational part of fraud instead of attacking it directly. Group-IB documented the activity within a client environment after the platform reported suspicious payment notifications in late April 2026. According to the supplied research, […]

The post Scammers Turn Legitimate Fintech Platforms Into Phishing Tools to Steal Banking Details appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Disrupts CoGUI Phishing Kit Linked to Over 100 Million Malicious Emails a Month

Microsoft and international partners have disrupted infrastructure supporting CoGUI. This phishing kit Proofpoint says generates more than 100 million malicious emails monthly. The coordinated action targeted a Chinese-speaking fraud ecosystem encompassing related phishing kits, infrastructure providers, and services enabling credential theft and financial fraud. Microsoft and Health-ISAC filed a civil lawsuit in the U.S. District […]

The post Microsoft Disrupts CoGUI Phishing Kit Linked to Over 100 Million Malicious Emails a Month appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Iron Man Phishing-as-a-Service Kit Impersonates Banks, Couriers and Government Agencies Worldwide

Iron Man System, a commercial phishing-as-a-service platform supplying criminals with ready-made websites impersonating banks, couriers, tax agencies, traffic authorities, and other trusted organizations worldwide. Researchers purchased a license through human intelligence operations and deployed the kit inside an isolated laboratory. Packet captures and configuration analysis connected the working deployment to vendor-controlled infrastructure, providing evidence beyond […]

The post Iron Man Phishing-as-a-Service Kit Impersonates Banks, Couriers and Government Agencies Worldwide appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
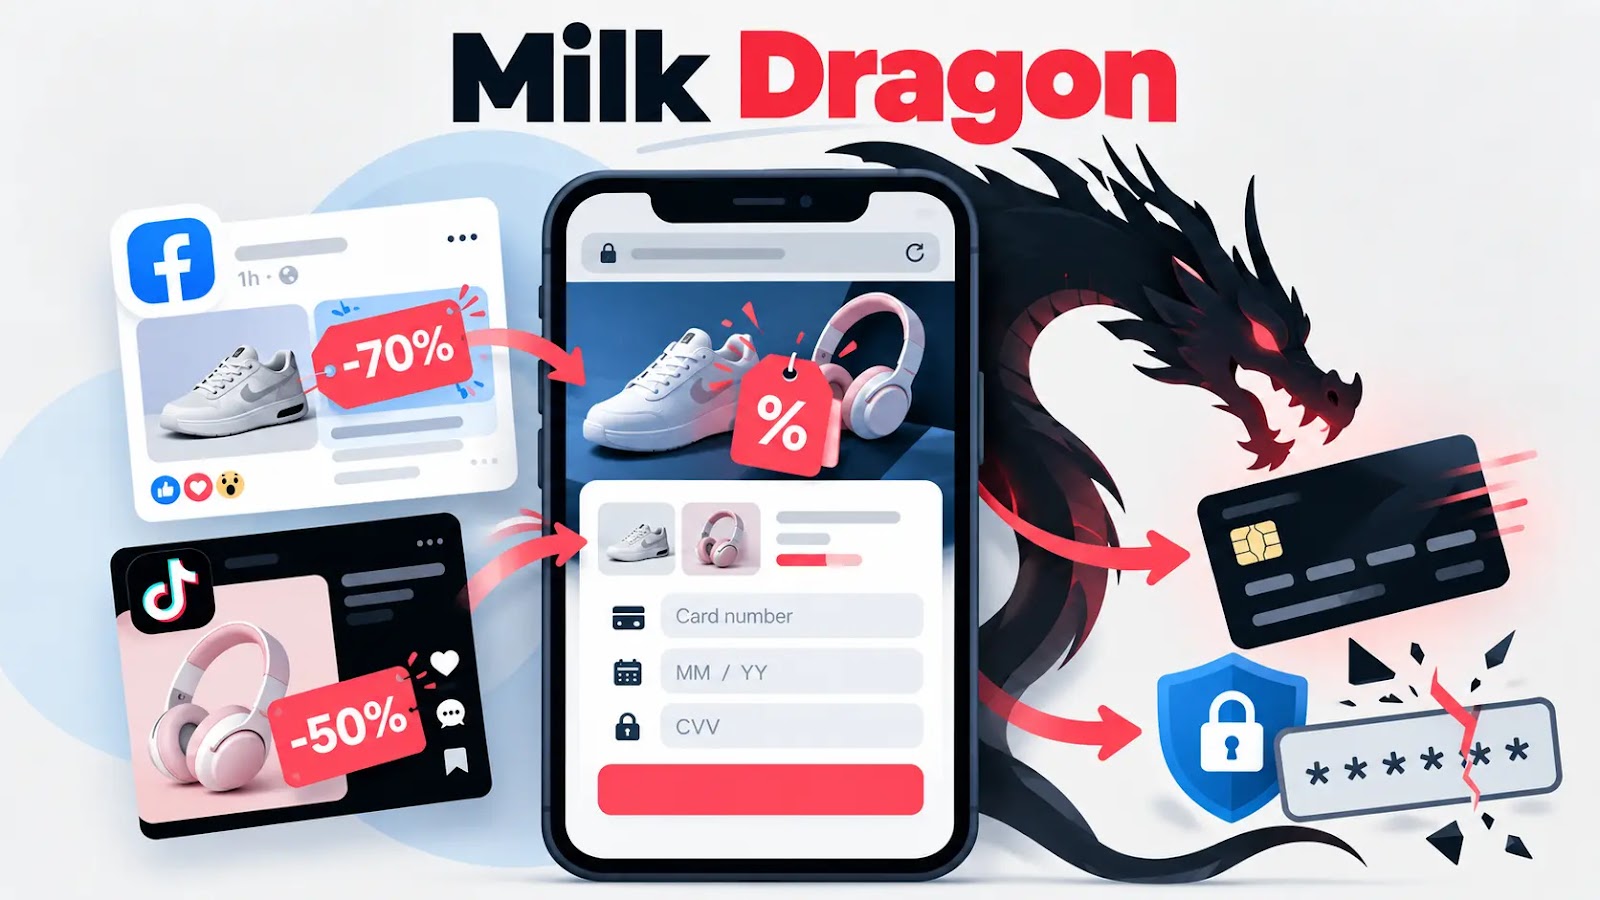
Milk Dragon Phishing Kit Uses Facebook and TikTok Discounts to Steal Cards and Bypass MFA

A phishing-as-a-service operation dubbed Milk Dragon, also known as NaiLong, is abusing discount-themed Facebook and TikTok posts to steal payment-card data and intercept multi-factor authentication (MFA) challenges. Group-IB identified 258 phishing pages linked to the kit since October 2025, with victims across 66 countries. Rather than relying on classic delivery-failure notices, bank alerts, or account-lockout […]

The post Milk Dragon Phishing Kit Uses Facebook and TikTok Discounts to Steal Cards and Bypass MFA appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Warns of EvilTokens AI Phishing Service Hijacking Thousands of Accounts

Microsoft has warned that the EvilTokens phishing-as-a-service platform has become a major driver of AI-enabled device-code phishing, compromising more than 12,000 email inboxes across over 10,000 organizations worldwide since emerging in February 2026. The operation, linked to the threat actor Microsoft tracks as Storm-2992, industrializes token theft, mailbox reconnaissance, and business email compromise at scale […]

The post Microsoft Warns of EvilTokens AI Phishing Service Hijacking Thousands of Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
ChatGPT Phishing Campaign Targets Both Work and Personal OpenAI Accounts

Threat actors are increasingly impersonating OpenAI’s ChatGPT service in credential-phishing campaigns, exploiting the growing use of generative AI across both enterprise and personal environments. A recently observed campaign uses a fraudulent subscription-payment notice to lure victims into disclosing OpenAI account credentials and potentially payment details through a convincing fake ChatGPT login page. The lure claims […]

The post ChatGPT Phishing Campaign Targets Both Work and Personal OpenAI Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
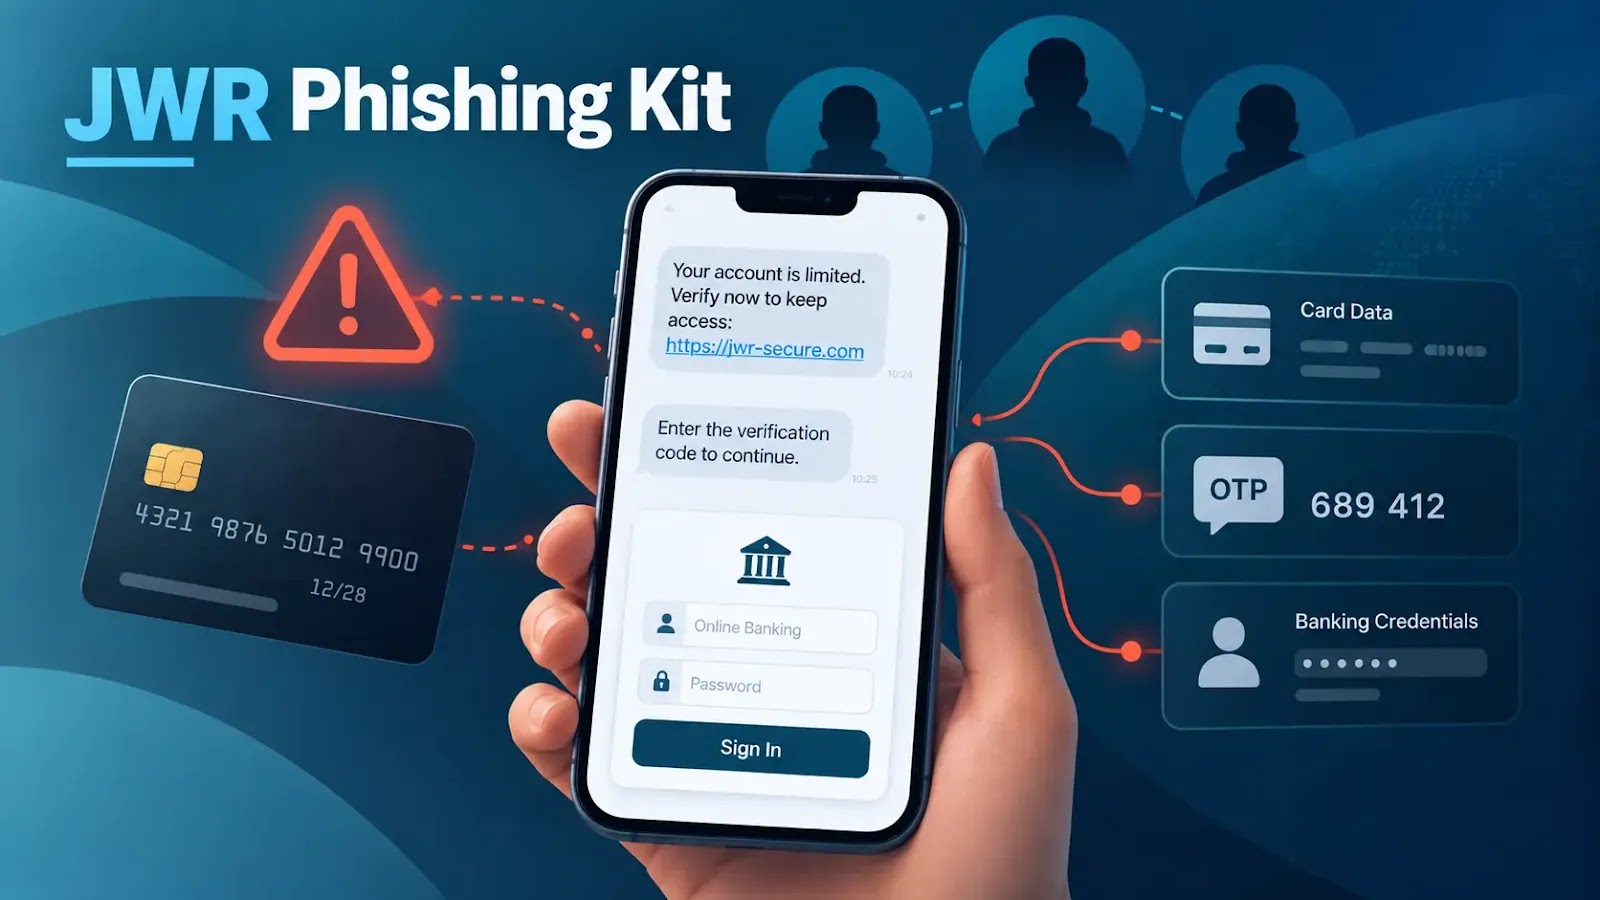
Smishing Triad Hackers Use JWR Phishing Kit to Steal Cards, OTPs and Bank Credentials

A large-scale SMS phishing campaign linked to the Smishing Triad is using a sophisticated phishing kit dubbed JWR to harvest payment-card data, one-time passwords, online-banking credentials, identity information, and digital-wallet logins. Group-IB attributed the activity to an operator sub-cluster tracked as Outsider, which appears to operate as a customer within the wider phishing-as-a-service ecosystem rather […]

The post Smishing Triad Hackers Use JWR Phishing Kit to Steal Cards, OTPs and Bank Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Phishing Attacks Abuse Trusted Email Infrastructure and URL Cloaking to Evade Security Filters

Phishing operators are increasingly shifting away from malware-laden attachments and toward trusted delivery services, authenticated domains, and multi-stage URL cloaking designed to defeat conventional email inspection. The continuously running VBSpam comparative test evaluated ten public full email-security products and one open-source solution against wanted, unwanted, and malicious mail streams. The assessment was conducted under the […]

The post Phishing Attacks Abuse Trusted Email Infrastructure and URL Cloaking to Evade Security Filters appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New Phishing Attack Uses Blob URLs to Hide Malicious Pages From Security Scanners

A phishing campaign that moves the credential-harvesting page out of attacker-controlled web infrastructure and into the victim’s browser. Unlike ordinary phishing kits, which host cloned login portals on domains that can eventually be detected and disrupted, this campaign delivers malicious content assembled only after a user follows the attack chain. A blob URL is a […]

The post New Phishing Attack Uses Blob URLs to Hide Malicious Pages From Security Scanners appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Global Phishing Campaign Abuses Google Infrastructure to Evade Security and Steal Credentials

A large-scale phishing operation is abusing trusted Google services as a multi-stage redirect network to bypass email security controls, deliver highly personalized credential-harvesting pages, and, in some cases, install ScreenConnect remote-access software. The campaign’s central advantage is that it presents trusted Google-owned domains at nearly every point a gateway, proxy, or analyst is likely to […]

The post Global Phishing Campaign Abuses Google Infrastructure to Evade Security and Steal Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Teams Adds QR Code Protection to Block Phishing and Fraud

Microsoft is developing a new security feature for Teams messaging that will obscure QR codes sent by external users. This measure aims to help organizations reduce phishing and fraud risks associated with malicious QR code campaigns. Listed under Microsoft 365 Roadmap ID 570439, this feature is currently in development and is scheduled for rollout in […]

The post Microsoft Teams Adds QR Code Protection to Block Phishing and Fraud appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌