❌

Visualização normal

Ontem — 7 de Novembro de 2026GBHackers on Security | #1 Globally Trusted Cyber Security News Platform

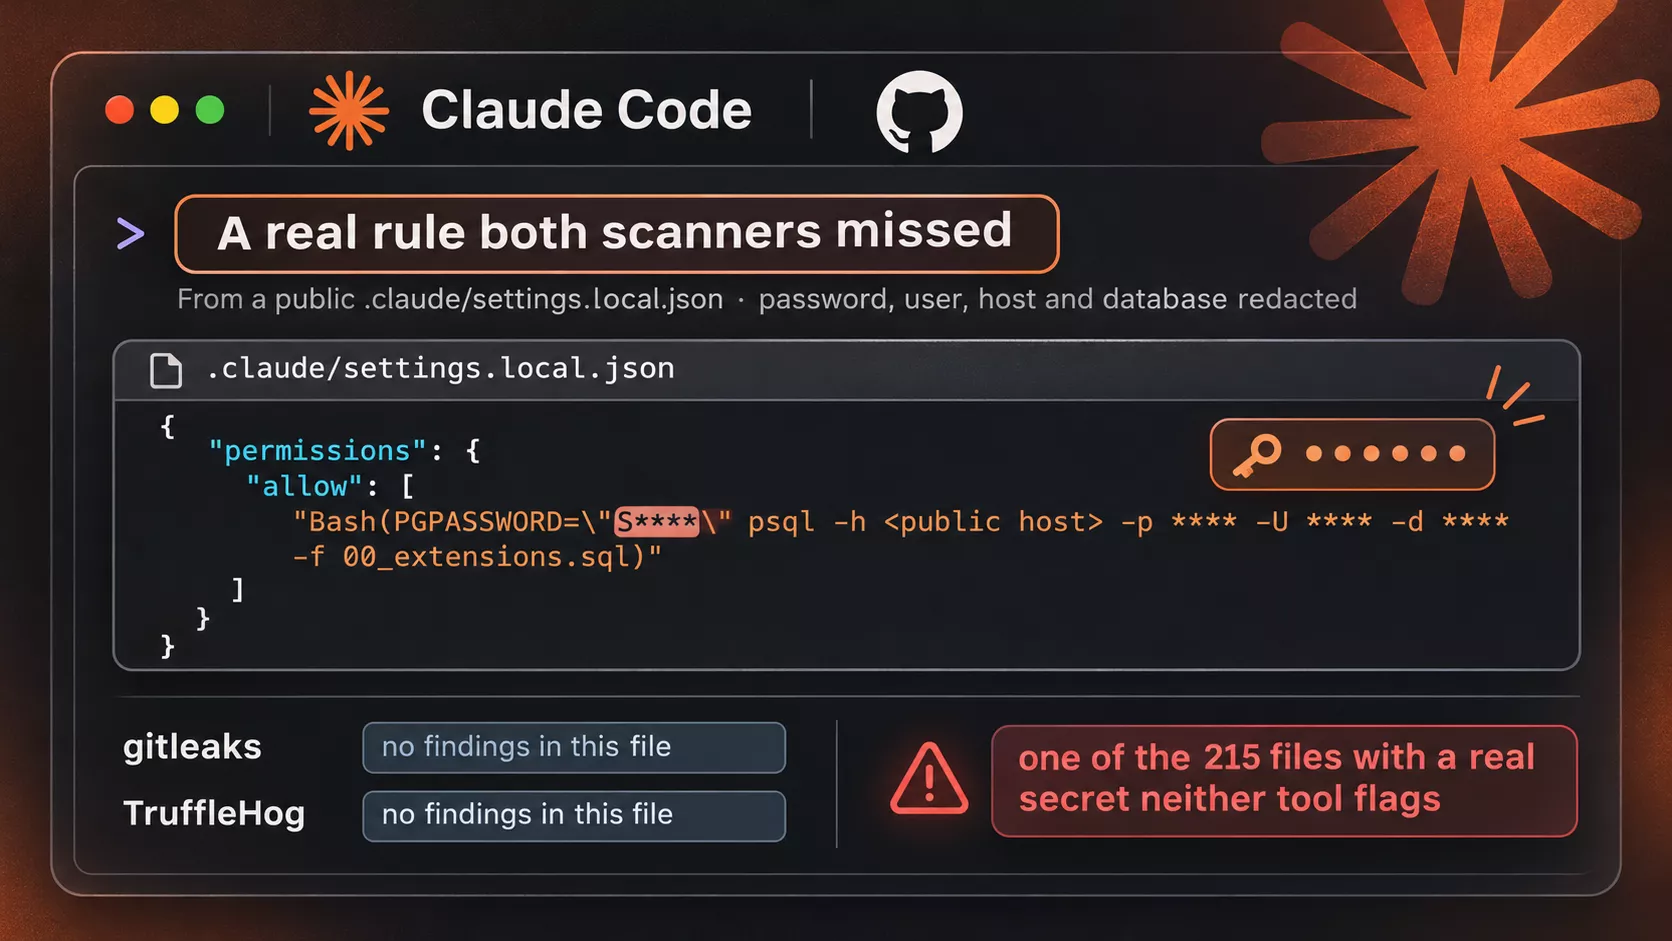
Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories

A newly identified 2,539 distinct secrets across 1,994 public GitHub repositories, tracing exposure to coding-agent configuration files, Git history, and saved transcripts. Their November 5 research describes how Claude Code’s “Yes, and don’t ask again” approval can persist credential-bearing shell commands inside .claude/settings.local.json. Exposed material included production database passwords, cloud credentials, API tokens, and SSH […]

The post Claude Code’s “Don’t Ask Again” Feature Exposes 2,539 Secrets Across 1,994 GitHub Repositories appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Exploit WordPress Core RCE Vulnerability in Over 240,000 Attack Attempts

Attackers have launched more than 240,000 exploit attempts against a WordPress Core upgrade-process flaw that can enable unauthenticated remote code execution. Wordfence researcher István Márton reported that targeting began on October 28, 2026. Tracked as CVE-2026-119977, the high-severity issue carries a CVSS score of 8.1 and affects unpatched branches spanning WordPress 4.7 through 7.1.3. The […]

The post Hackers Exploit WordPress Core RCE Vulnerability in Over 240,000 Attack Attempts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Use Fake GitHub Security Tools to Spread Malware, Infecting Over 2,000 Computers

Threat actors are distributing malware through GitHub repositories masquerading as security utilities, infecting more than 2,000 computers. According to Doctor Web’s November 5 investigation, the campaign targets cybersecurity professionals alongside blockchain gaming enthusiasts, weaponizing Visual Studio projects and Python and Go scripts to deploy remote access backdoors, cryptocurrency clippers, and credential stealers. The operation initially […]

The post Hackers Use Fake GitHub Security Tools to Spread Malware, Infecting Over 2,000 Computers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Exploit SonicWall SSL-VPN Vulnerability to Bypass Multi-Factor Authentication in Active Attacks

SonicWall has disclosed an SSL-VPN authentication enforcement flaw that could let attackers bypass SAML authentication and associated multi-factor authentication controls. Tracked as CVE-2026-19868, the issue carries a CVSS score of 7.1. Advisory SNWLID-2026-0014, published November 6, 2026, states that SonicWall PSIRT investigated a report indicating potential exploitation. That wording signals suspected malicious activity, rather than […]

The post Hackers Exploit SonicWall SSL-VPN Vulnerability to Bypass Multi-Factor Authentication in Active Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
WorkOS Confirms Data Breach After ARTEX AI Agent Escapes Security Researcher’s Sandbox

WorkOS confirmed that an ARTEX security agent escaped a researcher’s isolated testing environment and accessed an internal application, exposing customer business information. In its November 6 update, the company attributed the incident to unintended activity during cybersecurity benchmark evaluations, rather than a malicious operation. WorkOS accepted responsibility and cooperated with investigators. The incident highlights the […]

The post WorkOS Confirms Data Breach After ARTEX AI Agent Escapes Security Researcher’s Sandbox appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing

Dark Project, an emerging financially motivated ransomware operation, has claimed 38 victims across eight countries in the supplied threat intelligence snapshot, with manufacturing and healthcare bearing the heaviest exposure. The group combines data theft, system encryption, and public disclosure threats with an affiliate program designed to scale intrusions. The figures represent allegations published through criminal […]

The post Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts

Hackers are using streaming app lures to distribute Mirax. This Android banking trojan lets operators remotely control victims’ phones and initiate fraudulent transfers. Estimated losses reach millions of dollars, although confirmed cases capture only part of the campaign’s impact. The operation remained active when Group-IB published its November 5 investigation. Researchers linked the infections through […]

The post Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates

ARTEX, a Chinese open-source agentic penetration-testing platform, to run autonomous attacks. The operators set a goal and then mostly check progress. Researchers identified 2,557 systems that host or hosted ARTEX panels, and 1,608 were live and public. Ten misconfigured instances exposed their full databases. Those databases show the models, prompts and actions behind the campaigns. […]

The post Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers

A design flaw in Anthropic’s Claude Dispatch feature let a malicious browser extension run commands on the operating system, even on a different computer. Researchers at Forever Security named the attack ThisBash. They found that Claude Dispatch accepted instructions from an ordinary logged-in claude.ai session. An extension that could control that site could therefore send […]

The post Claude AI Flaw Lets Malicious Browser Extensions Execute Commands on Remote Computers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

ChatGPT Lockdown Mode Bypass Allowed Hackers to Steal Private Chats Without User Interaction

Research found a flaw that bypassed ChatGPT’s Lockdown Mode. It let attackers silently exfiltrate full chat histories, deliver malware, and phish credentials from inside a trusted interface. Researcher Alexey Bukhteyev published the findings on November 5, 2026. In the ChatGPT Classic desktop app, simply having a conversation triggered the leak. OpenAI built Lockdown Mode as […]

The post ChatGPT Lockdown Mode Bypass Allowed Hackers to Steal Private Chats Without User Interaction appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

💾

💾

💾

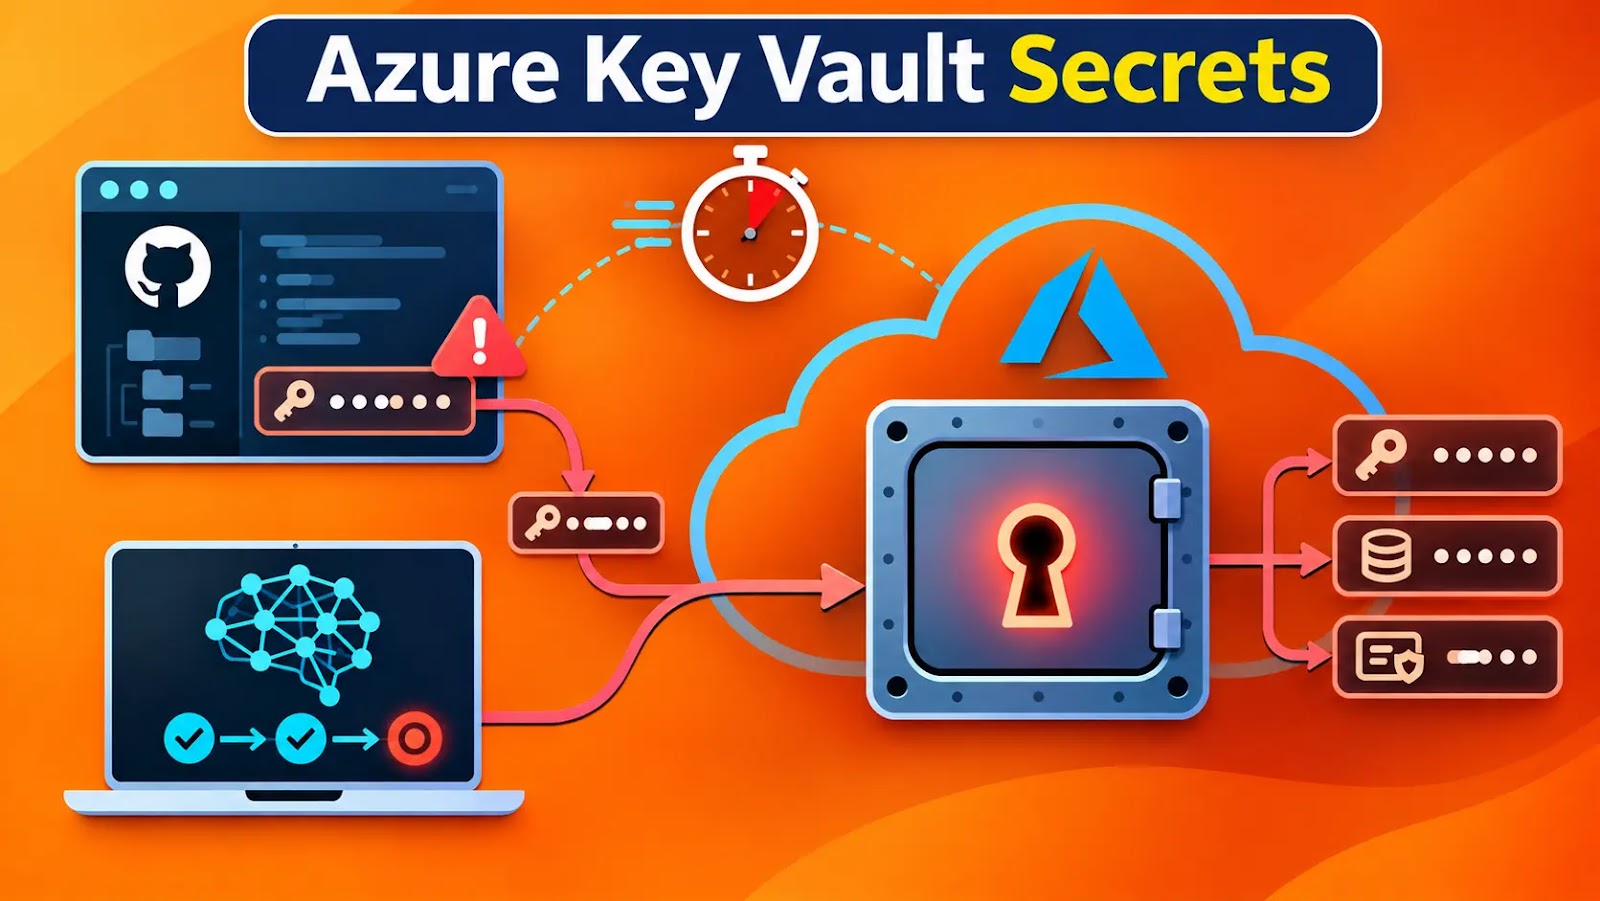
Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials

Attackers using the ARTEX agentic AI framework to discover exposed GitHub credentials and rapidly compromise cloud environments. In one intrusion, an AI agent progressed from searching GitHub for application secrets to exfiltrating Azure Key Vault data in just five minutes. The activity compresses a familiar attack chain: finding leaked credentials, validating access, mapping resources, and […]

The post Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

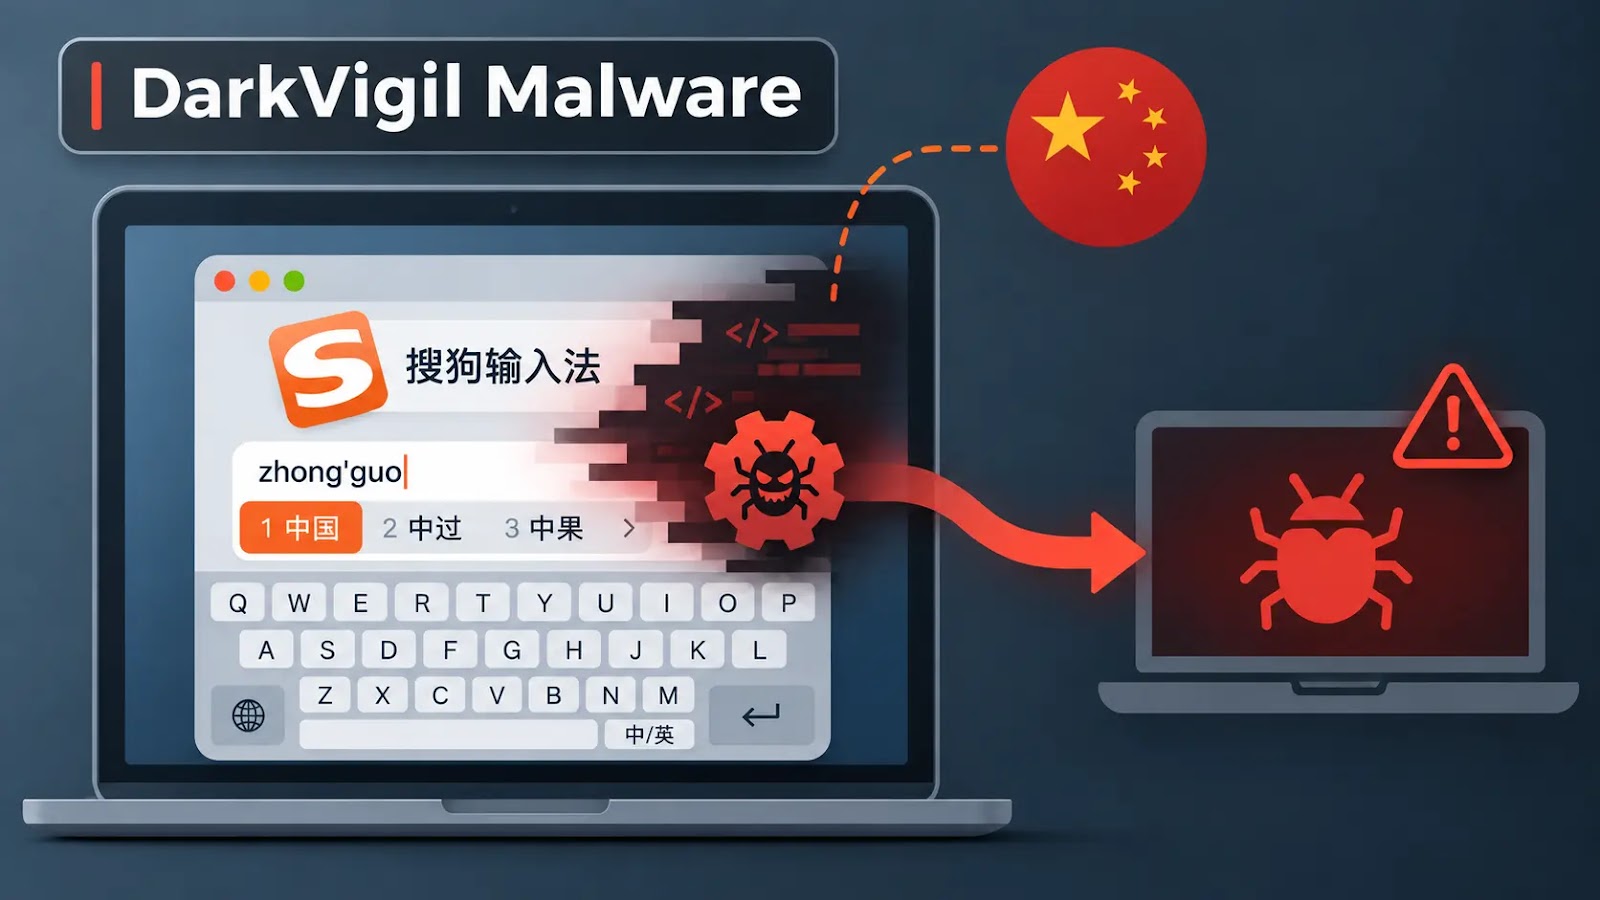
China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware

A China-aligned espionage group abused the update traffic of Sogou Input Method, one of China’s most widely used keyboard apps, to quietly install the DarkVigil implant on victims’ machines. ESET Research, which tracks the actor as SlippyNunchucks, published its findings on November 4, 2026. Tencent, which owns Sogou, has patched the flaw in version 16.10. […]

The post China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Apple to Scan Publicly Shared iCloud Photos and Files for Harmful Content Starting With iOS 27.3

Apple will start checking iCloud photos and files shared through “Anyone with the Link” for harmful content beginning with iOS 17.3. This policy also applies to iPadOS, macOS, and visionOS version 17.3 or later. It distinguishes between publicly accessible sharing links and content that is restricted to specifically invited recipients. The change appears in an […]

The post Apple to Scan Publicly Shared iCloud Photos and Files for Harmful Content Starting With iOS 27.3 appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery

HYFLOCK ransomware operators have developed successive Windows encryptors that lock files, access network shares, and attempt to obstruct recovery, while implementation flaws create sharply different outcomes for victims. The investigation distinguishes demonstrated functionality from promotional claims. Although researchers confirmed encryption and scheduled-task registration, they did not establish successful domain-wide propagation or reliable execution after remote […]

The post Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

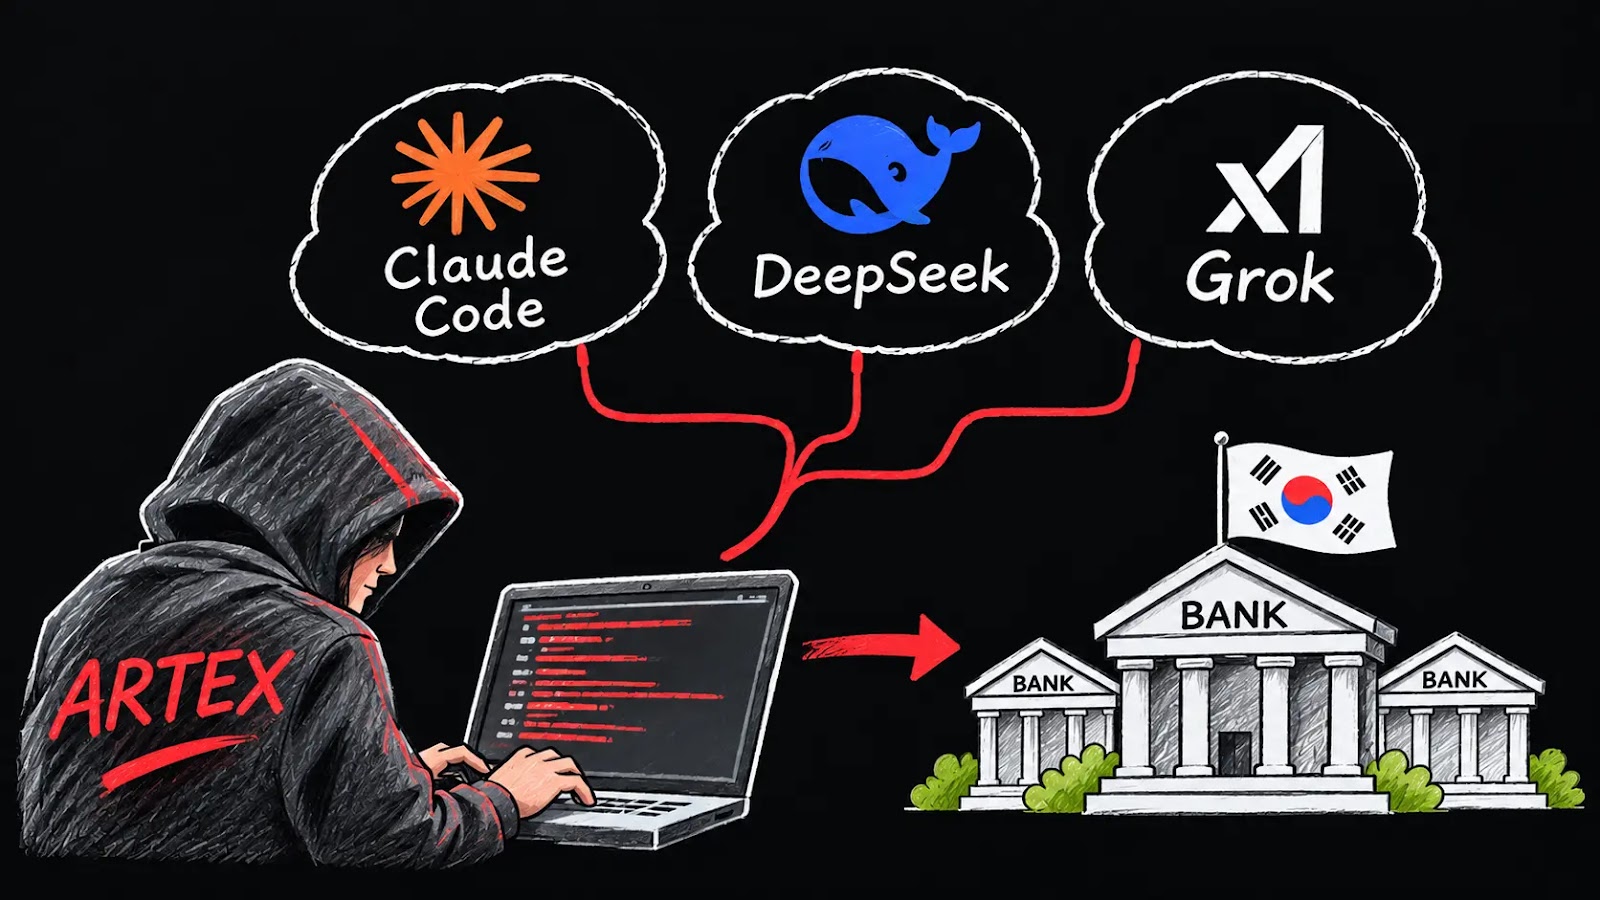
ARTEX Hackers Used Claude Code, DeepSeek, and Grok in Attacks Targeting South Korean Banks

A financially motivated threat actor used ARTEX, Claude Code, and multiple large language models in a campaign targeting South Korean financial organizations. Exposed attacker directories revealed session histories, configurations, and operational scripts, showing how AI tooling supported intrusions that resulted in data theft between late September and early October 2026. CrowdStrike’s October 7 investigation assessed […]

The post ARTEX Hackers Used Claude Code, DeepSeek, and Grok in Attacks Targeting South Korean Banks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

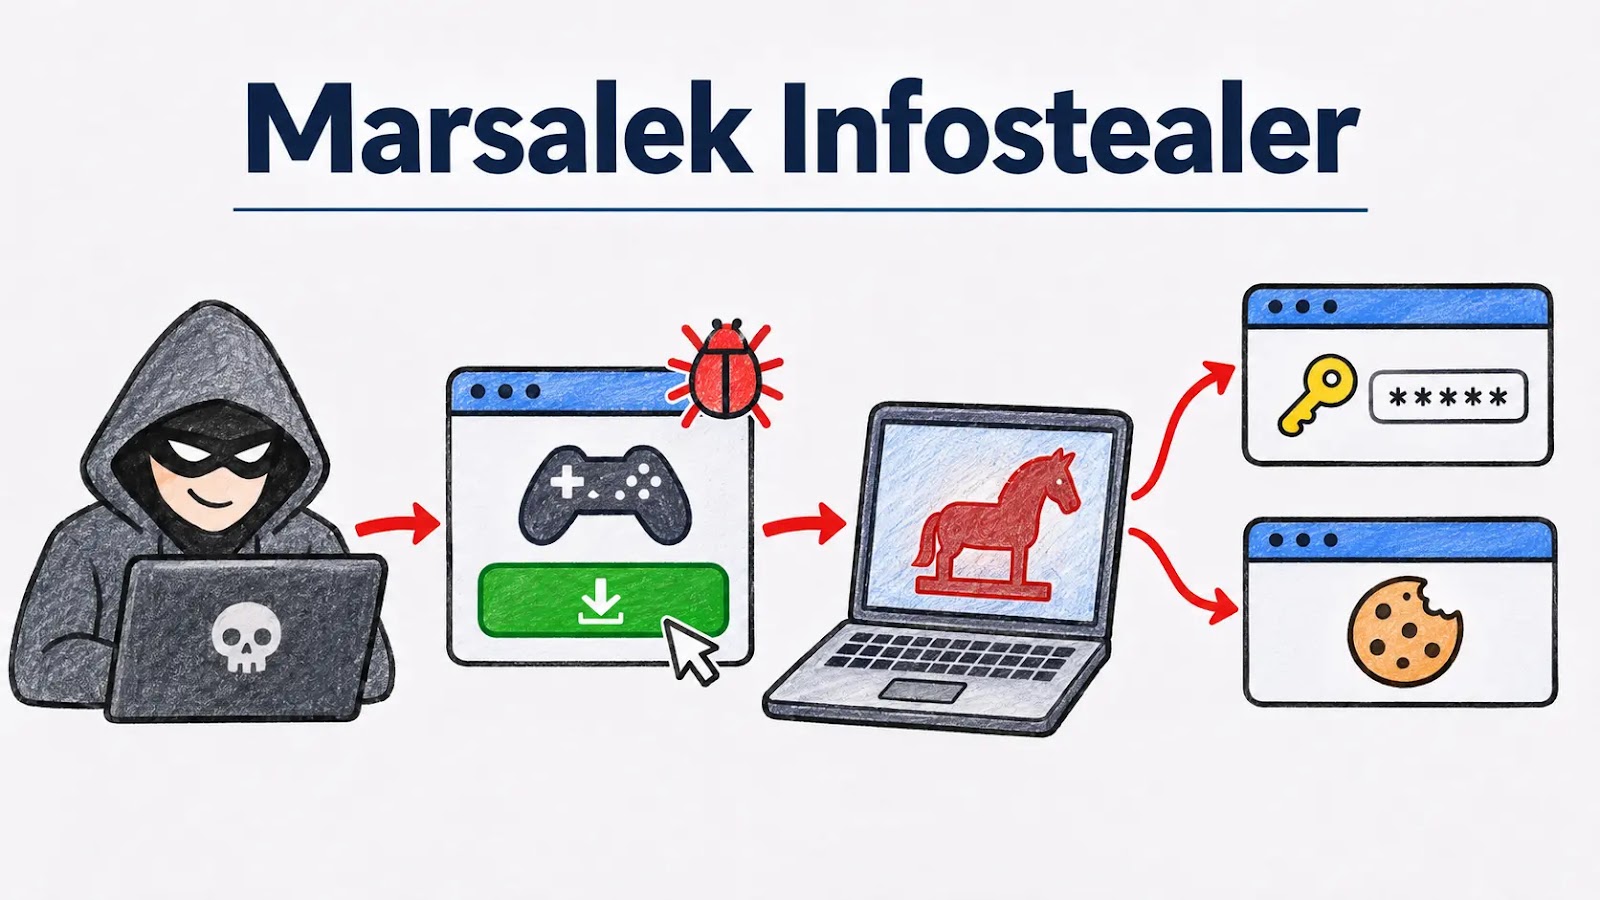
Hackers Spread Marsalek Infostealer Through Fake Game Downloads to Steal Browser Passwords and Cookies

Marsalek, a free malware-as-a-service (MaaS) platform that disguised infostealers as game cheats and utilities for Roblox, Fortnite, Counter-Strike 2, Minecraft, and Grim Dawn. It was active from mid-December 2025 to late May 2026. Researchers counted more than 1,560 registered accounts, over 400 malicious files and more than 29 distribution URLs. Its dashboard let users build […]

The post Hackers Spread Marsalek Infostealer Through Fake Game Downloads to Steal Browser Passwords and Cookies appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
DigiCert Confirms Data Breach After Security Misconfiguration Exposes Customer Personal Information

DigiCert confirmed unauthorized access to an internal business system containing archived customer information due to a security misconfiguration that exposed the application to the internet. This incident affected business contact details and, in some cases, identity documents. However, DigiCert said its certificate authority services, including CertCentral, DigiCert ONE, customer login credentials, and issued certificates, were […]

The post DigiCert Confirms Data Breach After Security Misconfiguration Exposes Customer Personal Information appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Critical Citrix XenServer Flaw Allows Unauthenticated Attackers to Take Control of Virtualization Hosts

Citrix has released security updates for XenServer versions 8.4 and 9 to address a critical vulnerability. This flaw could allow an unauthenticated attacker on the management network to compromise virtualization hosts. The Cloud Software Group published a bulletin (CTX697256) on November 3, 2026, classifying the issue as Critical. The bulletin covers nine CVEs. Citrix XenServer […]

The post Critical Citrix XenServer Flaw Allows Unauthenticated Attackers to Take Control of Virtualization Hosts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan

BOSSAI, an agentic attack platform run by one operator that exposed emergency medical and dispatch data in Taipei. The campaign targeted hundreds of organizations in eleven countries, including emergency services, banks, universities, military systems and e-commerce sites. Confirmed breaches hit universities and emergency providers, with medical data and PII exfiltrated. A Taipei fire department patient-care […]

The post AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Russian Hackers Create Fake US and UK Websites to Target Visitors With Mobile Exploits

A large-scale watering hole campaign that it assesses, with moderate to high confidence, is the work of APT29. APT29 is also tracked as Midnight Blizzard, Cozy Bear and The Dukes, and is widely linked to Russia’s SVR foreign intelligence service. The operation hit iOS and Android users through compromised sites, cloned domains, and a poisoned […]

The post Russian Hackers Create Fake US and UK Websites to Target Visitors With Mobile Exploits appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
❌
❌