❌

Visualização normal

Ontem — 6 de Novembro de 2026GBHackers on Security | #1 Globally Trusted Cyber Security News Platform

Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing

Dark Project, an emerging financially motivated ransomware operation, has claimed 38 victims across eight countries in the supplied threat intelligence snapshot, with manufacturing and healthcare bearing the heaviest exposure. The group combines data theft, system encryption, and public disclosure threats with an affiliate program designed to scale intrusions. The figures represent allegations published through criminal […]

The post Dark Project Ransomware Gang Claims 38 Victims Across 8 Countries, Targeting Healthcare and Manufacturing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts

Hackers are using streaming app lures to distribute Mirax. This Android banking trojan lets operators remotely control victims’ phones and initiate fraudulent transfers. Estimated losses reach millions of dollars, although confirmed cases capture only part of the campaign’s impact. The operation remained active when Group-IB published its November 5 investigation. Researchers linked the infections through […]

The post Hackers Use Fake Streaming Apps to Spread Mirax Android Malware and Steal Bank Accounts appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates

ARTEX, a Chinese open-source agentic penetration-testing platform, to run autonomous attacks. The operators set a goal and then mostly check progress. Researchers identified 2,557 systems that host or hosted ARTEX panels, and 1,608 were live and public. Ten misconfigured instances exposed their full databases. Those databases show the models, prompts and actions behind the campaigns. […]

The post Hackers Put AI Agents on Autopilot to Steal Gaming Accounts and Apple Signing Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
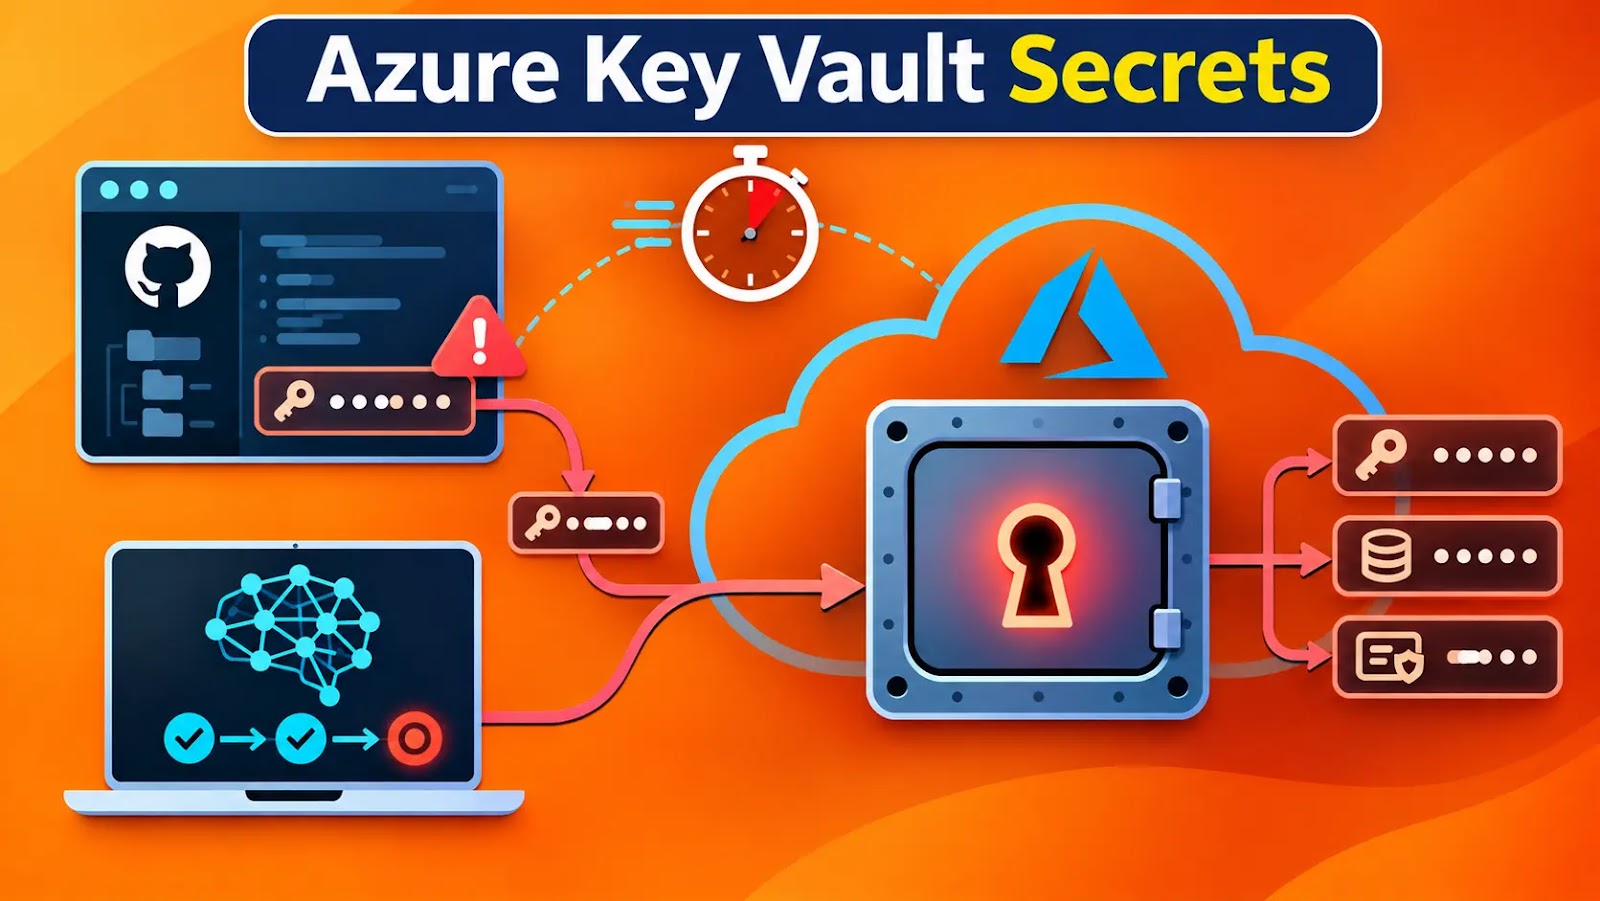
Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials

Attackers using the ARTEX agentic AI framework to discover exposed GitHub credentials and rapidly compromise cloud environments. In one intrusion, an AI agent progressed from searching GitHub for application secrets to exfiltrating Azure Key Vault data in just five minutes. The activity compresses a familiar attack chain: finding leaked credentials, validating access, mapping resources, and […]

The post Hackers Use ARTEX AI to Steal Azure Key Vault Secrets Just 5 Minutes After Finding Exposed GitHub Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Antes de ontemGBHackers on Security | #1 Globally Trusted Cyber Security News Platform

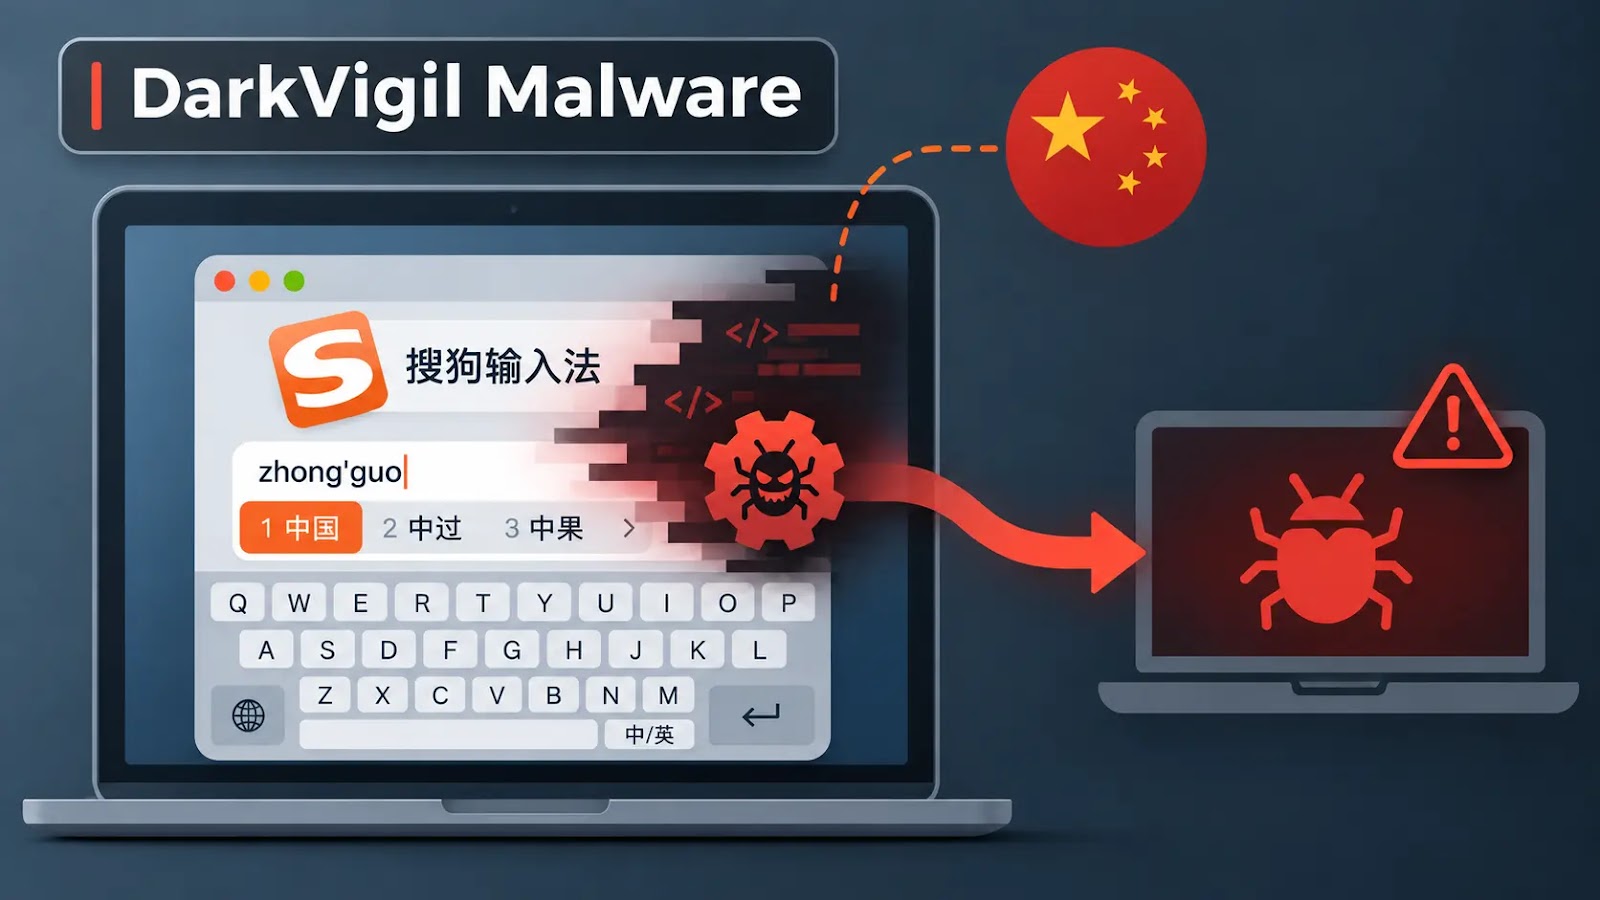
China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware

A China-aligned espionage group abused the update traffic of Sogou Input Method, one of China’s most widely used keyboard apps, to quietly install the DarkVigil implant on victims’ machines. ESET Research, which tracks the actor as SlippyNunchucks, published its findings on November 4, 2026. Tencent, which owns Sogou, has patched the flaw in version 16.10. […]

The post China-Aligned Hackers Hijack Popular Sogou Keyboard Software to Secretly Install DarkVigil Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery

HYFLOCK ransomware operators have developed successive Windows encryptors that lock files, access network shares, and attempt to obstruct recovery, while implementation flaws create sharply different outcomes for victims. The investigation distinguishes demonstrated functionality from promotional claims. Although researchers confirmed encryption and scheduled-task registration, they did not establish successful domain-wide propagation or reliable execution after remote […]

The post Hackers Develop New HYFLOCK Ransomware That Encrypts Files and Attempts to Block Recovery appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
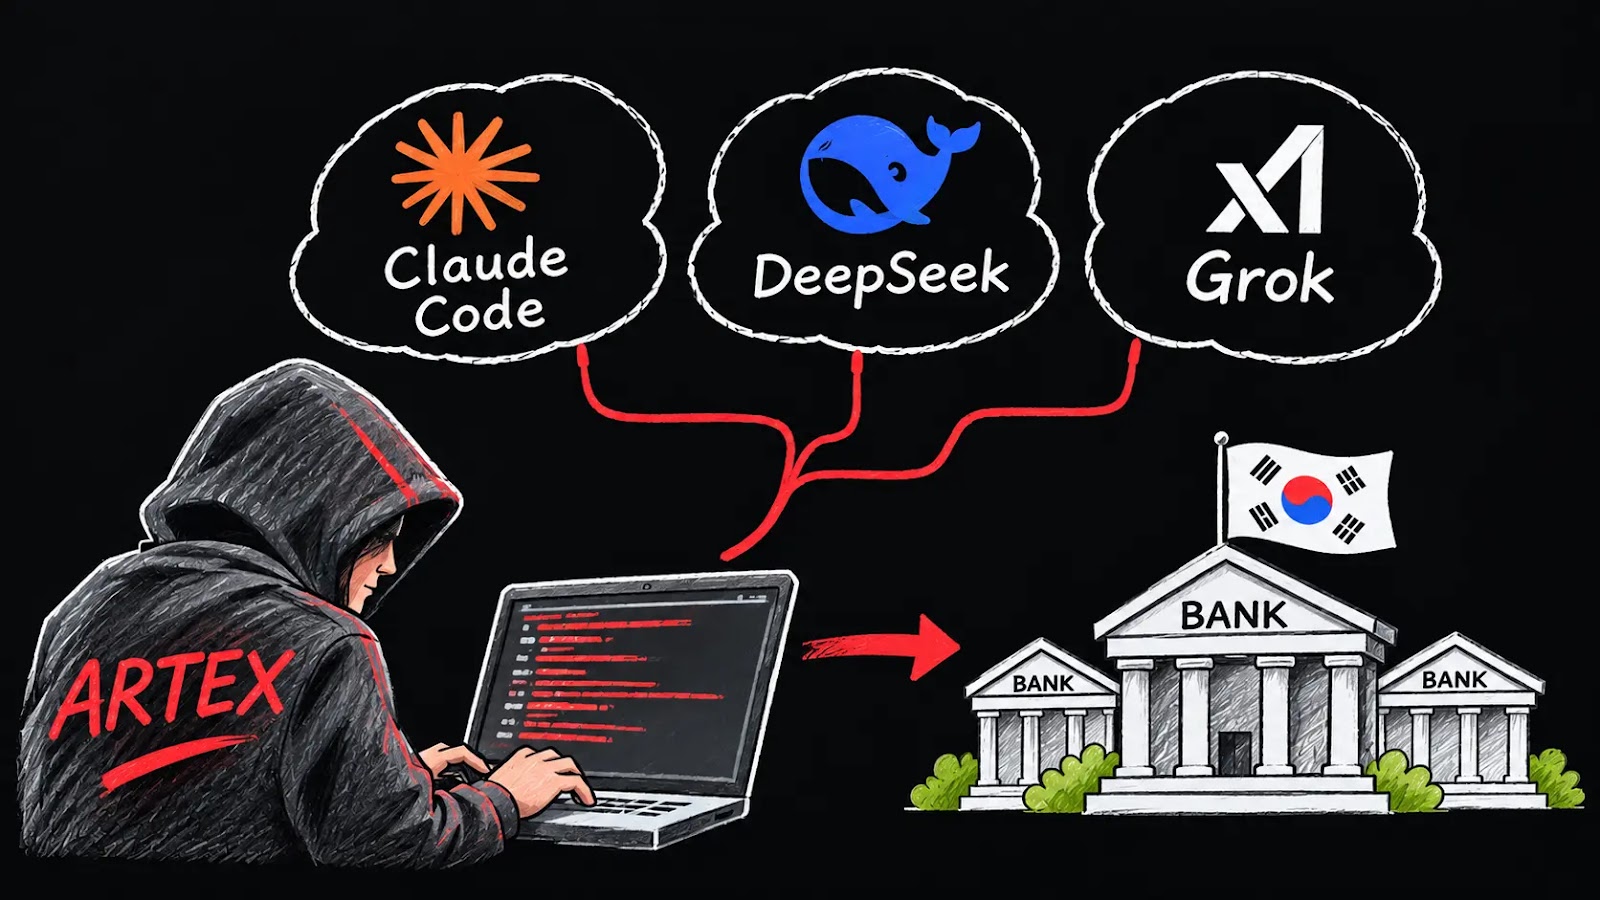
ARTEX Hackers Used Claude Code, DeepSeek, and Grok in Attacks Targeting South Korean Banks

A financially motivated threat actor used ARTEX, Claude Code, and multiple large language models in a campaign targeting South Korean financial organizations. Exposed attacker directories revealed session histories, configurations, and operational scripts, showing how AI tooling supported intrusions that resulted in data theft between late September and early October 2026. CrowdStrike’s October 7 investigation assessed […]

The post ARTEX Hackers Used Claude Code, DeepSeek, and Grok in Attacks Targeting South Korean Banks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
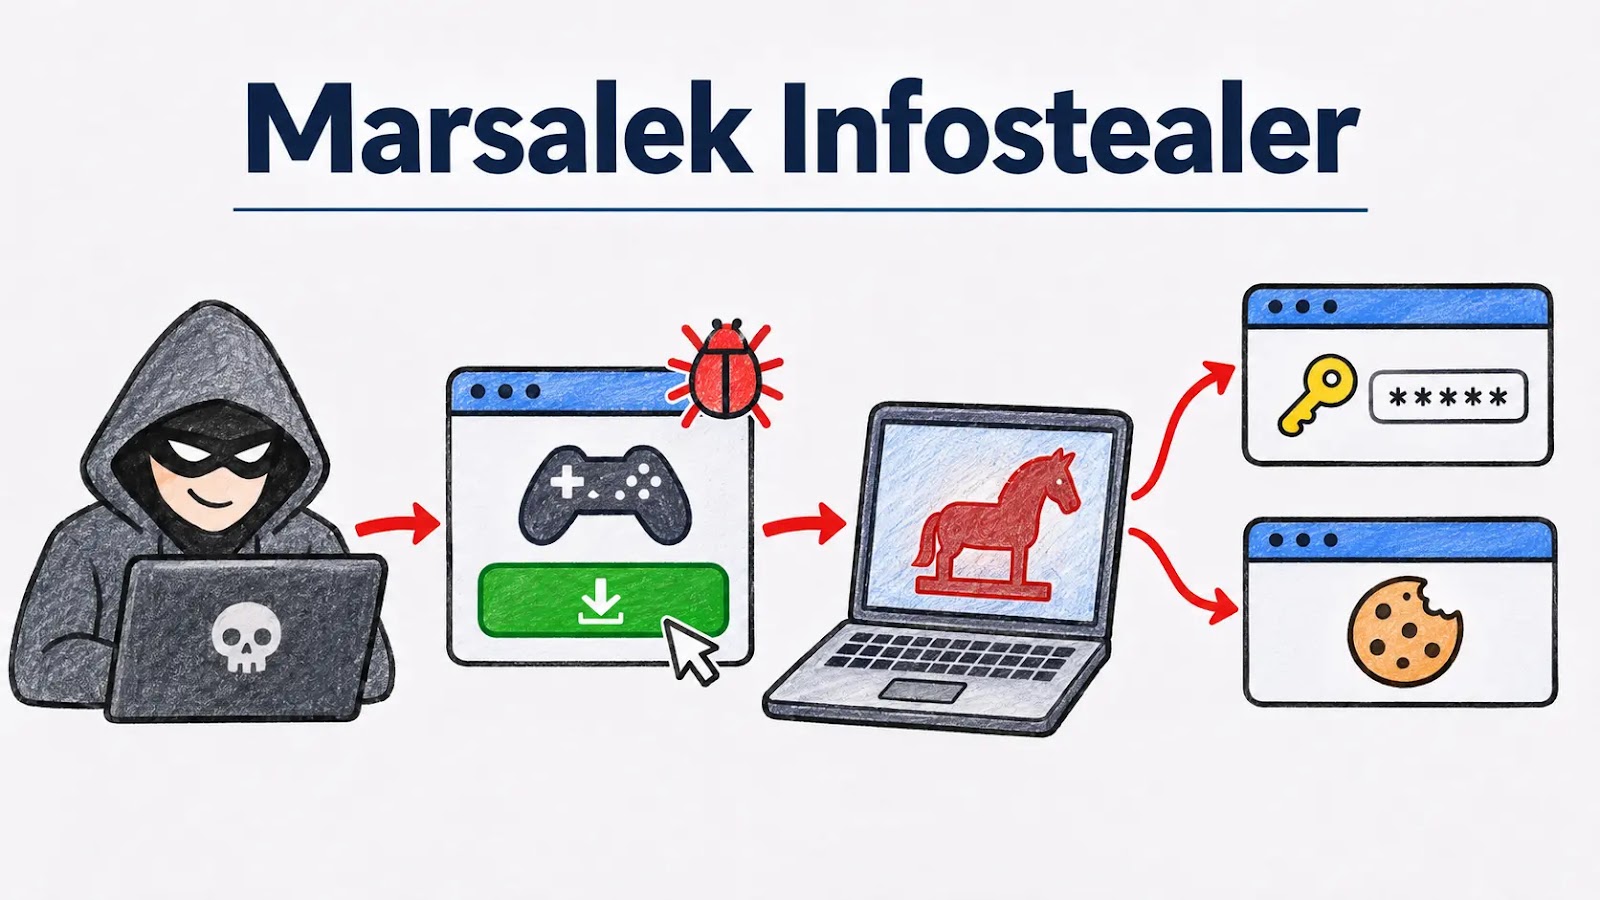
Hackers Spread Marsalek Infostealer Through Fake Game Downloads to Steal Browser Passwords and Cookies

Marsalek, a free malware-as-a-service (MaaS) platform that disguised infostealers as game cheats and utilities for Roblox, Fortnite, Counter-Strike 2, Minecraft, and Grim Dawn. It was active from mid-December 2025 to late May 2026. Researchers counted more than 1,560 registered accounts, over 400 malicious files and more than 29 distribution URLs. Its dashboard let users build […]

The post Hackers Spread Marsalek Infostealer Through Fake Game Downloads to Steal Browser Passwords and Cookies appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan

BOSSAI, an agentic attack platform run by one operator that exposed emergency medical and dispatch data in Taipei. The campaign targeted hundreds of organizations in eleven countries, including emergency services, banks, universities, military systems and e-commerce sites. Confirmed breaches hit universities and emergency providers, with medical data and PII exfiltrated. A Taipei fire department patient-care […]

The post AI-Powered BOSSAI Attacks Expose Patient Records and Emergency Dispatch Data in Taiwan appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Russian Hackers Create Fake US and UK Websites to Target Visitors With Mobile Exploits

A large-scale watering hole campaign that it assesses, with moderate to high confidence, is the work of APT29. APT29 is also tracked as Midnight Blizzard, Cozy Bear and The Dukes, and is widely linked to Russia’s SVR foreign intelligence service. The operation hit iOS and Android users through compromised sites, cloned domains, and a poisoned […]

The post Russian Hackers Create Fake US and UK Websites to Target Visitors With Mobile Exploits appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Fake Microsoft Support Scams Spread Through Online Ads as Researchers Uncover Organized Fraud Network

An organized fraud operation using paid advertisements, Microsoft Azure hosting, and centrally managed telephone numbers to distribute counterfeit Microsoft support pages. The investigation links one backend serving the kit to Mandarin-speaking developers and registration details referencing Hubei, China. Those findings suggest operational connections, not definitive attribution. Crucially, the identified backend appeared in detections at 11 […]

The post Fake Microsoft Support Scams Spread Through Online Ads as Researchers Uncover Organized Fraud Network appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
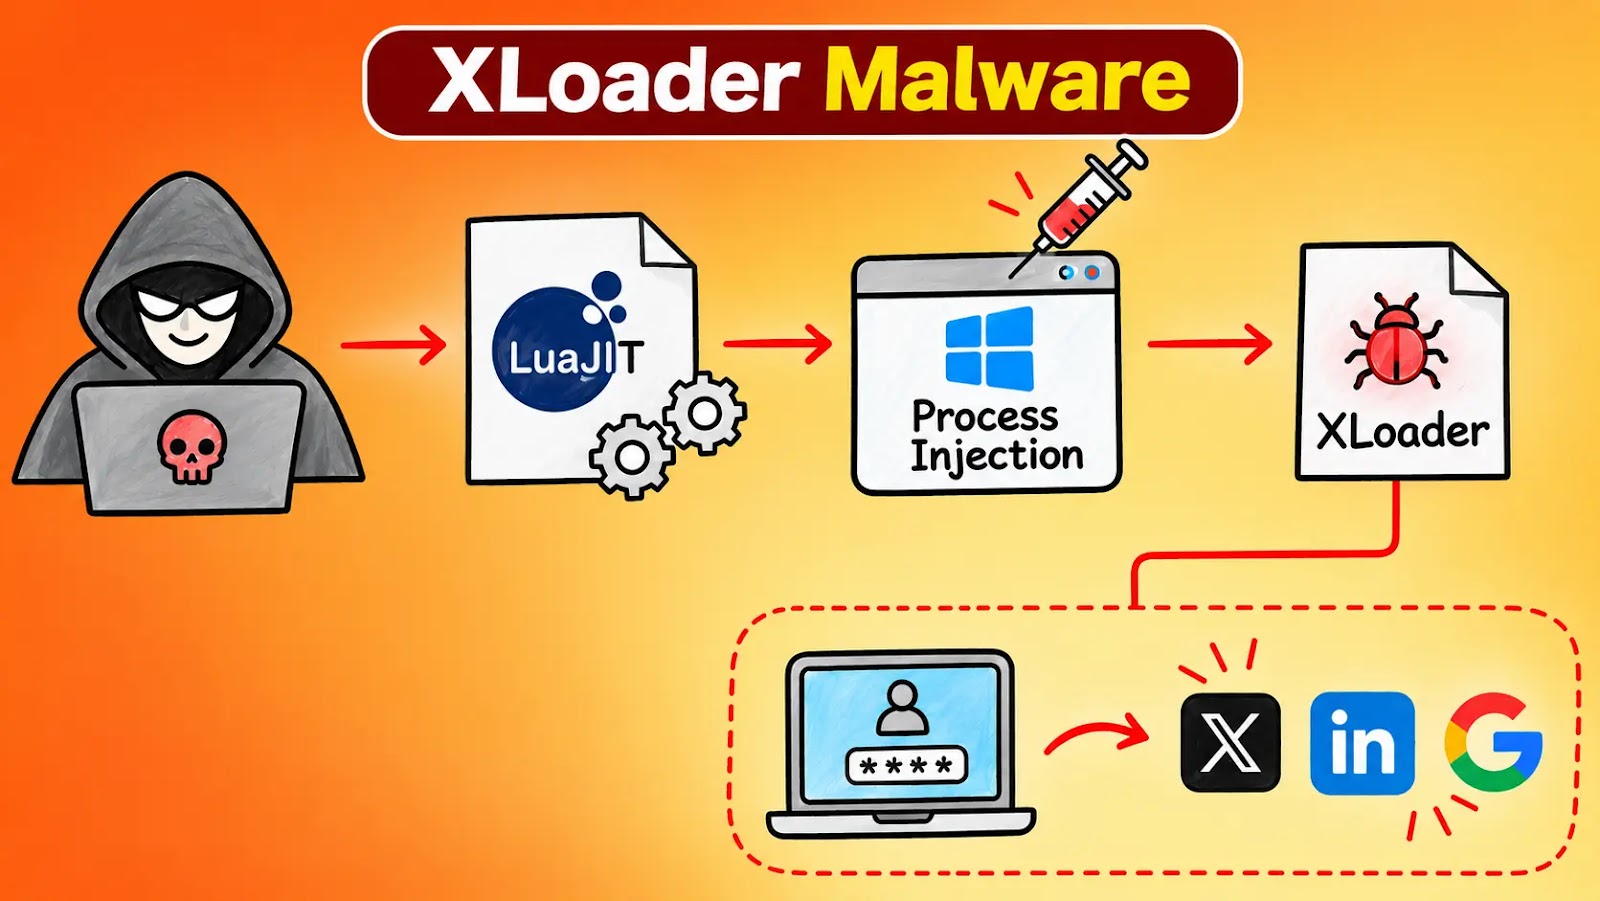
Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware

A new XLoader infection chain. It hides the credential stealer inside an embedded LuaJIT interpreter. It moves it into another Windows process through shared-section injection. The campaign uses business-themed email lures. It also delivered Agent Tesla, Remcos and XWorm . The chain starts with order and payment emails. One Greek-language message has a subject starting […]

The post Hackers Abuse LuaJIT and Windows Process Injection to Hide XLoader Credential-Stealing Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
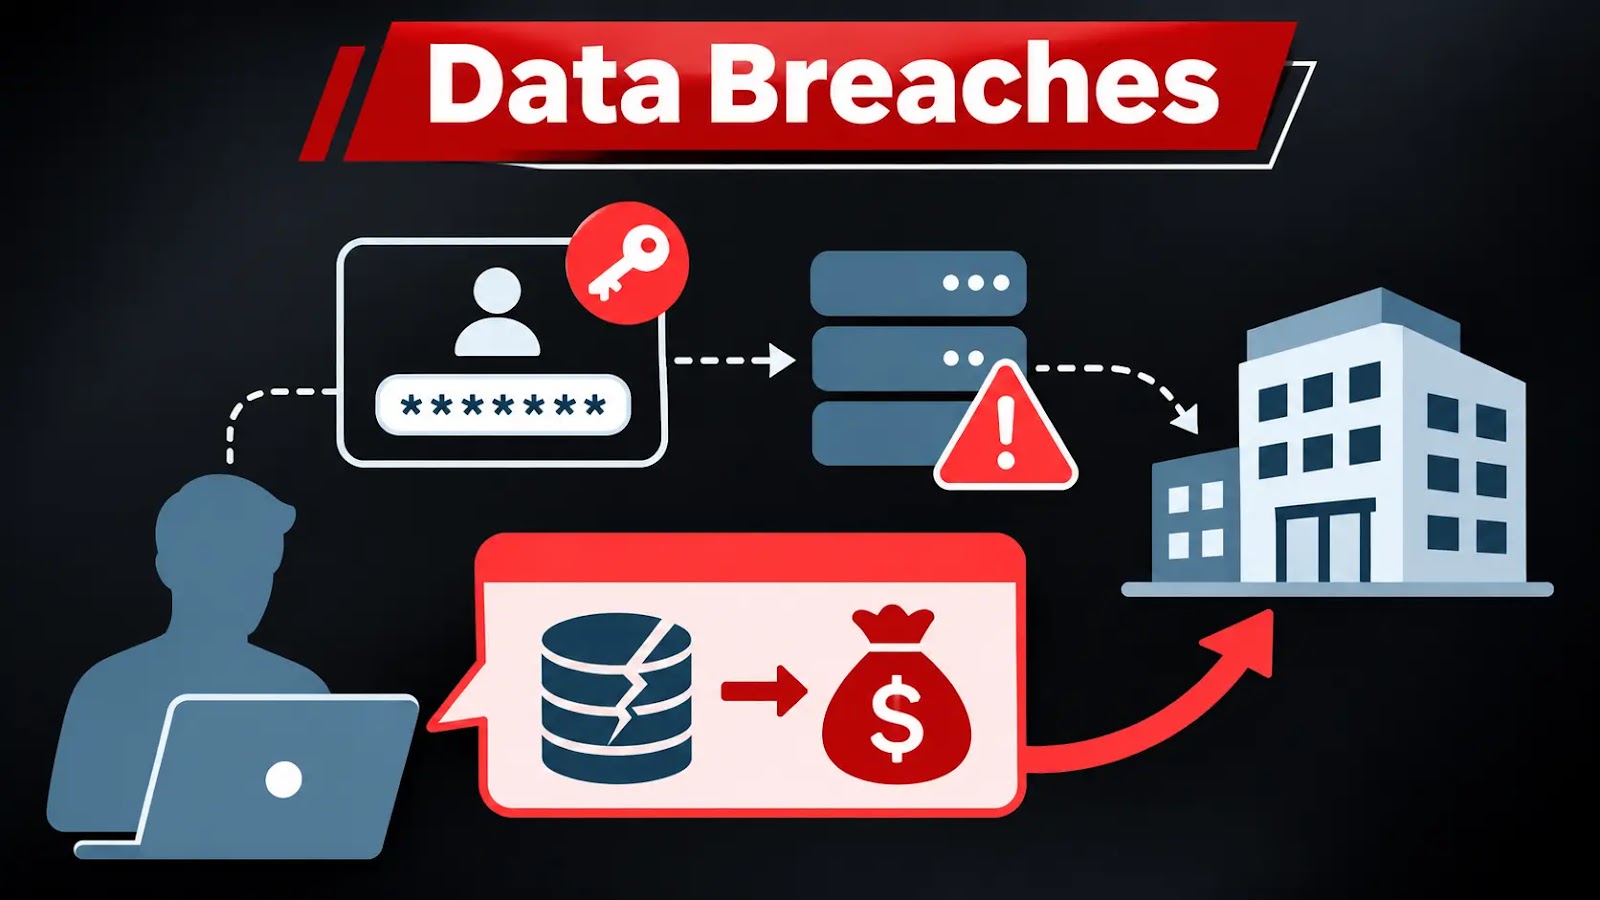
Hackers Use Stolen Credentials to Fake Major Data Breaches and Pressure Companies for Money

Hackers are using exposed credentials to access limited corporate data, then presenting that access as evidence of major breaches to pressure companies into paying. The findings concern external attacker activity affecting third parties, not a compromise of ReliaQuest’s environment. They highlight a distinction: authentic leaked records do not automatically prove the extensive network intrusion an […]

The post Hackers Use Stolen Credentials to Fake Major Data Breaches and Pressure Companies for Money appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
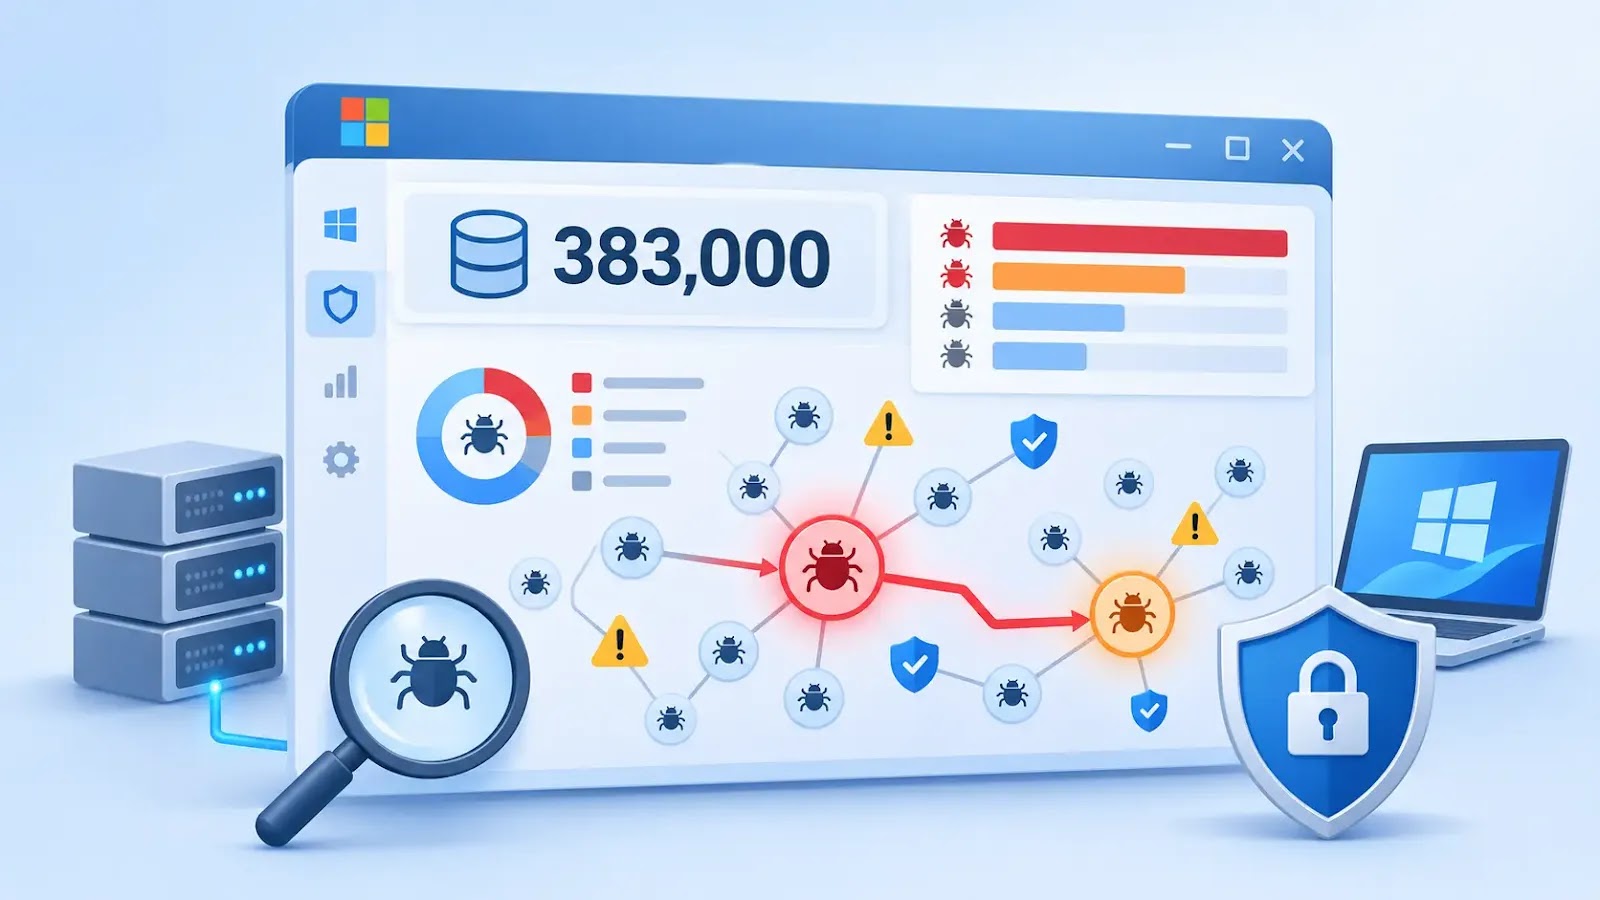
Microsoft Analyzes 383,000 Security Vulnerabilities and Reveals Which Flaws Hackers Exploit Most

Microsoft’s analysis of approximately 383,000 disclosed vulnerabilities shows that attackers overwhelmingly favor weaknesses enabling system takeover rather than exploiting vulnerabilities indiscriminately. The research identifies 2,056 CVEs linked to real-world exploitation, roughly 0.5% of the population, highlighting why vulnerability management must prioritize demonstrated attacker utility over disclosure volume or severity scores alone. Covering vulnerabilities published from […]

The post Microsoft Analyzes 383,000 Security Vulnerabilities and Reveals Which Flaws Hackers Exploit Most appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
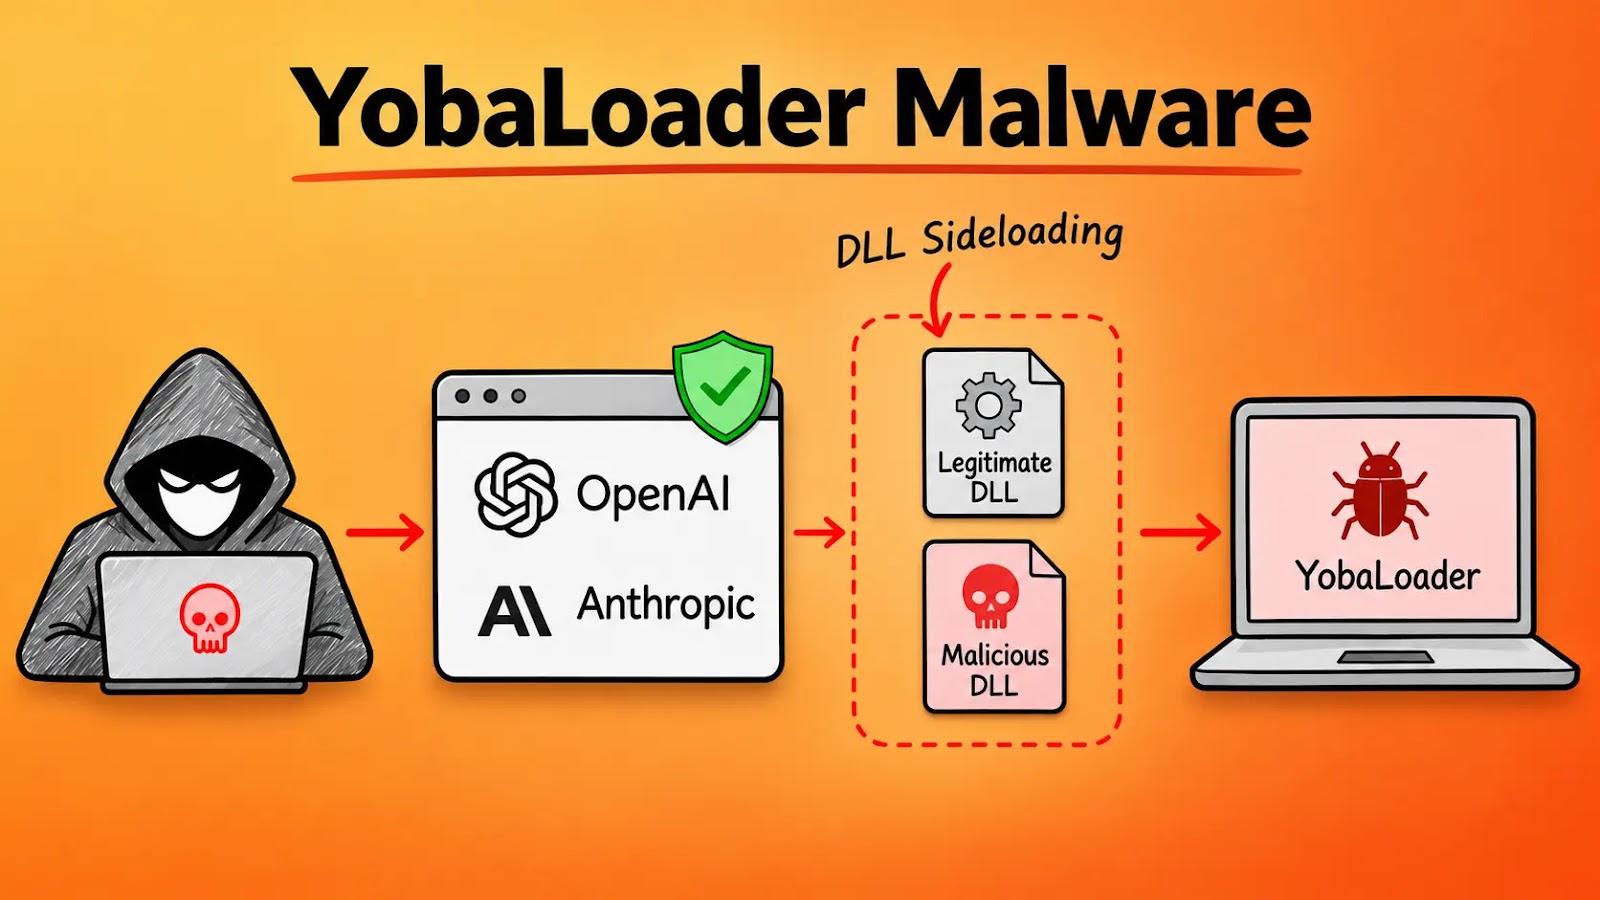
Hackers Exploit DLL Sideloading in Signed OpenAI and Anthropic Binaries to Deploy YobaLoader Malware

A campaign tracked as Yoba abuses interest in generative AI to push cryptocurrency-mining malware through fake GitHub projects. Check Point Research published its findings on October 27, 2026, after about two months of tracking. The operators pair legitimate, signed OpenAI and Anthropic executables with a malicious winmm.dll, so the payload loads through DLL sideloading. The […]

The post Hackers Exploit DLL Sideloading in Signed OpenAI and Anthropic Binaries to Deploy YobaLoader Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
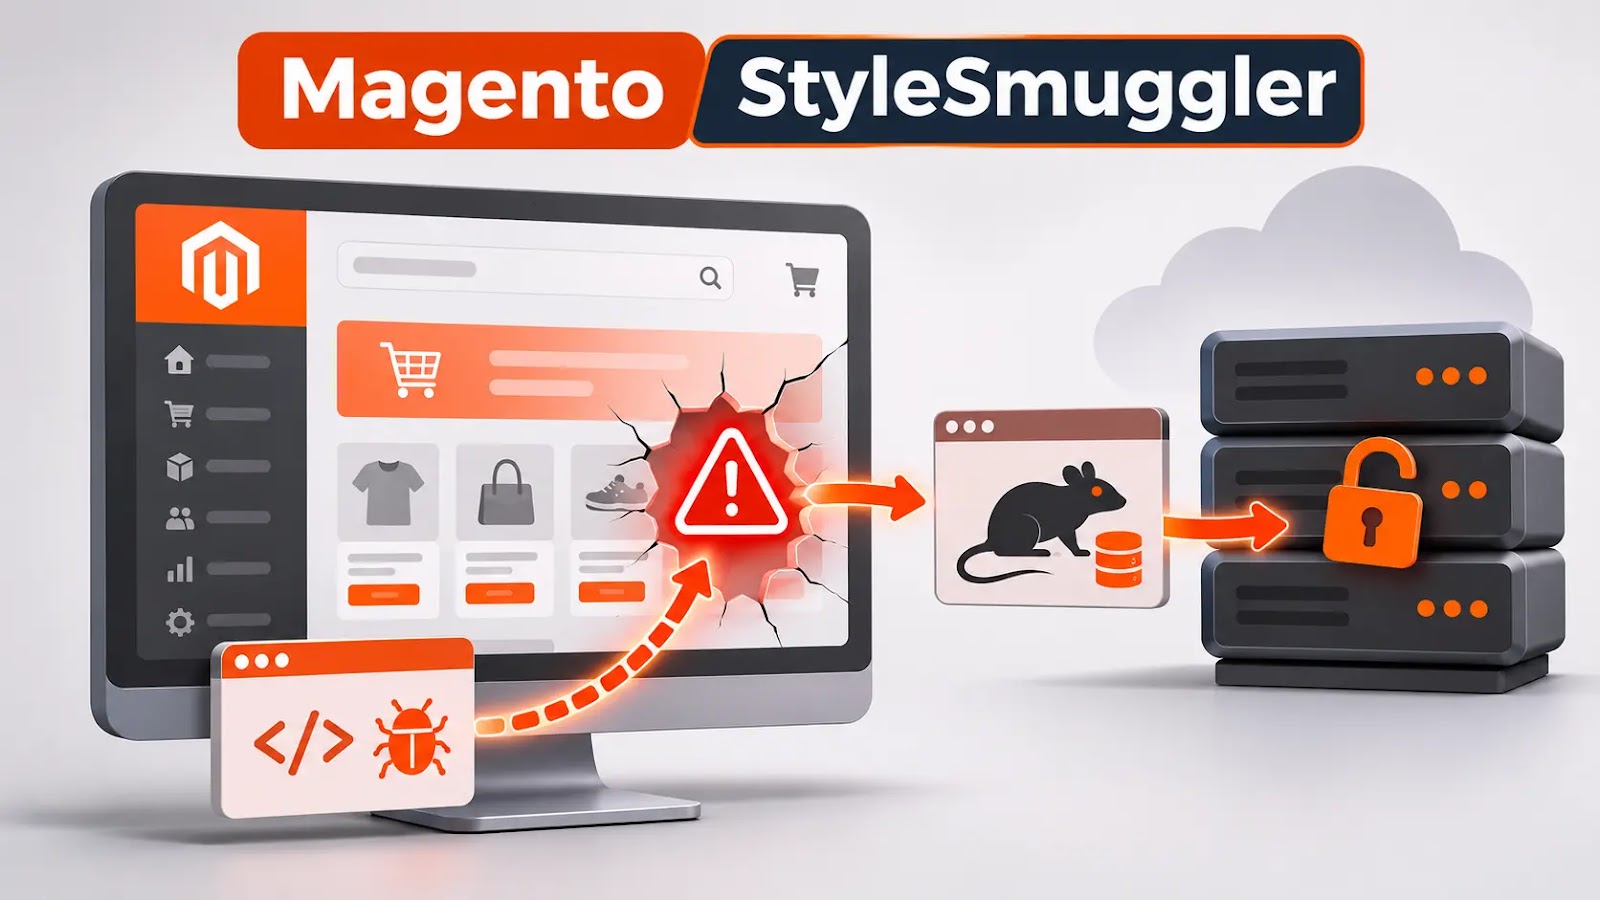
Hackers Exploit Critical Magento StyleSmuggler Vulnerability to Deploy PSK Agent RAT and Hijack Servers

Attackers exploited the critical StyleSmuggler vulnerability in Magento and Adobe Commerce to deploy PSK Agent, a remote access trojan enabling command execution, traffic proxying, and persistent server access. The campaign ran September 9–13, 2026, targeting stores across Western Europe, North America, and Asia-Pacific. Imperva’s earlier analysis reports a CVSS score of 10.0 and exploitation preceding […]

The post Hackers Exploit Critical Magento StyleSmuggler Vulnerability to Deploy PSK Agent RAT and Hijack Servers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
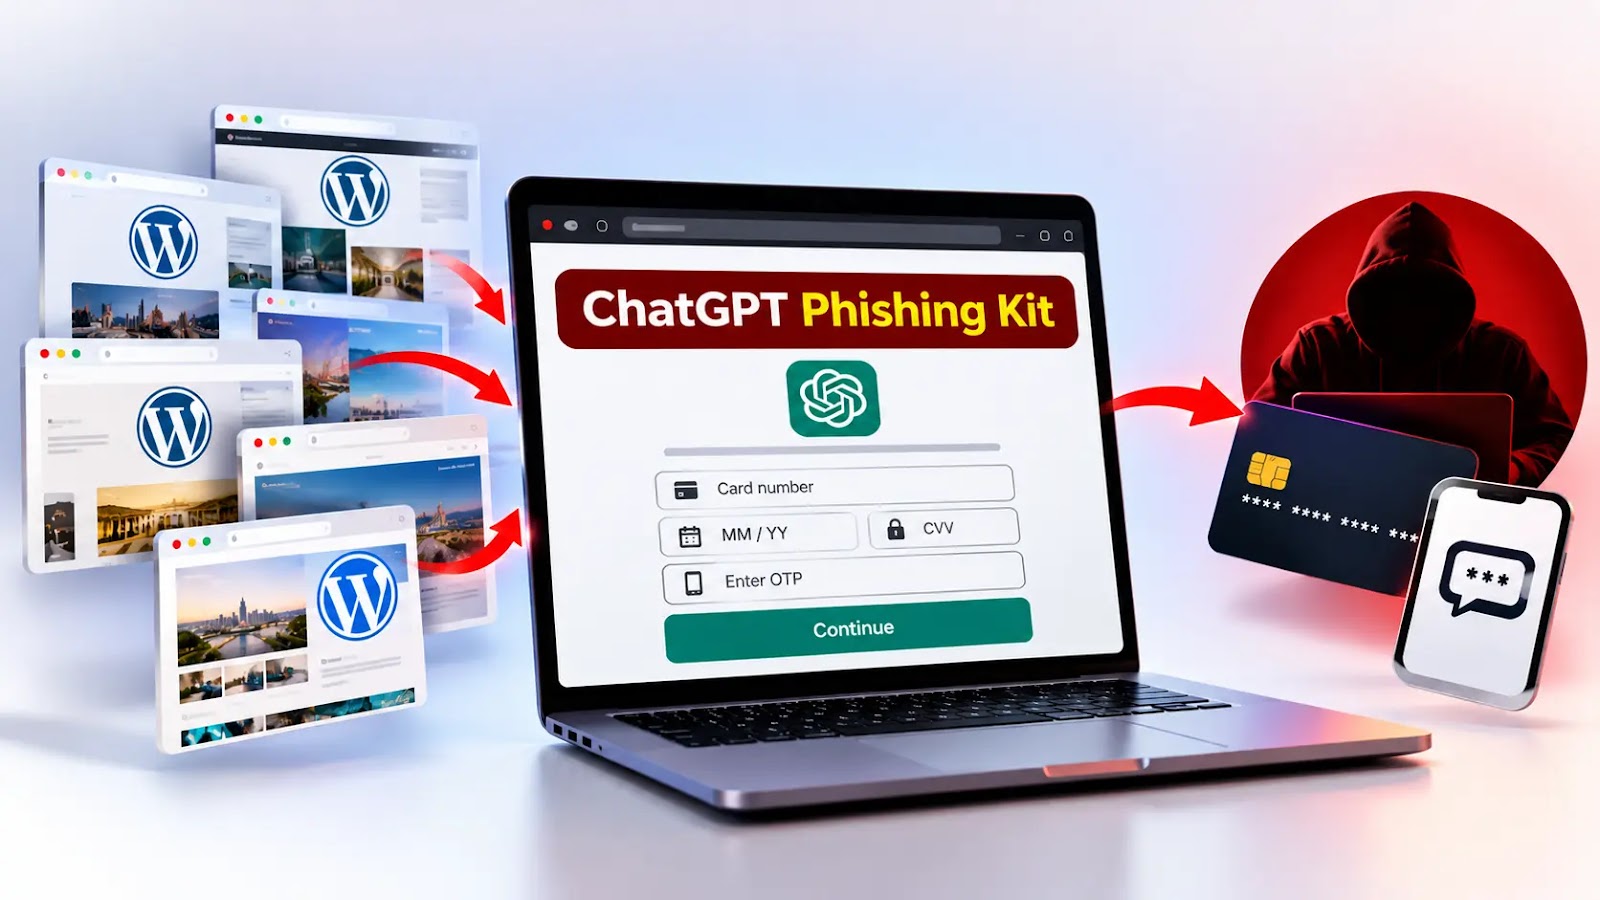
New ChatGPT Phishing Kit Uses Rotating WordPress Websites to Steal Payment Details and OTPs

A phishing campaign impersonating OpenAI is using disposable WordPress websites and live attacker oversight to steal payment card details and potentially capture one-time passwords. Fraudulent ChatGPT Plus billing emails warn that subscription payments have failed, directing recipients to counterfeit checkout pages where operators control the victim’s next step. The operation combines infrastructure churn with interactive […]

The post New ChatGPT Phishing Kit Uses Rotating WordPress Websites to Steal Payment Details and OTPs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
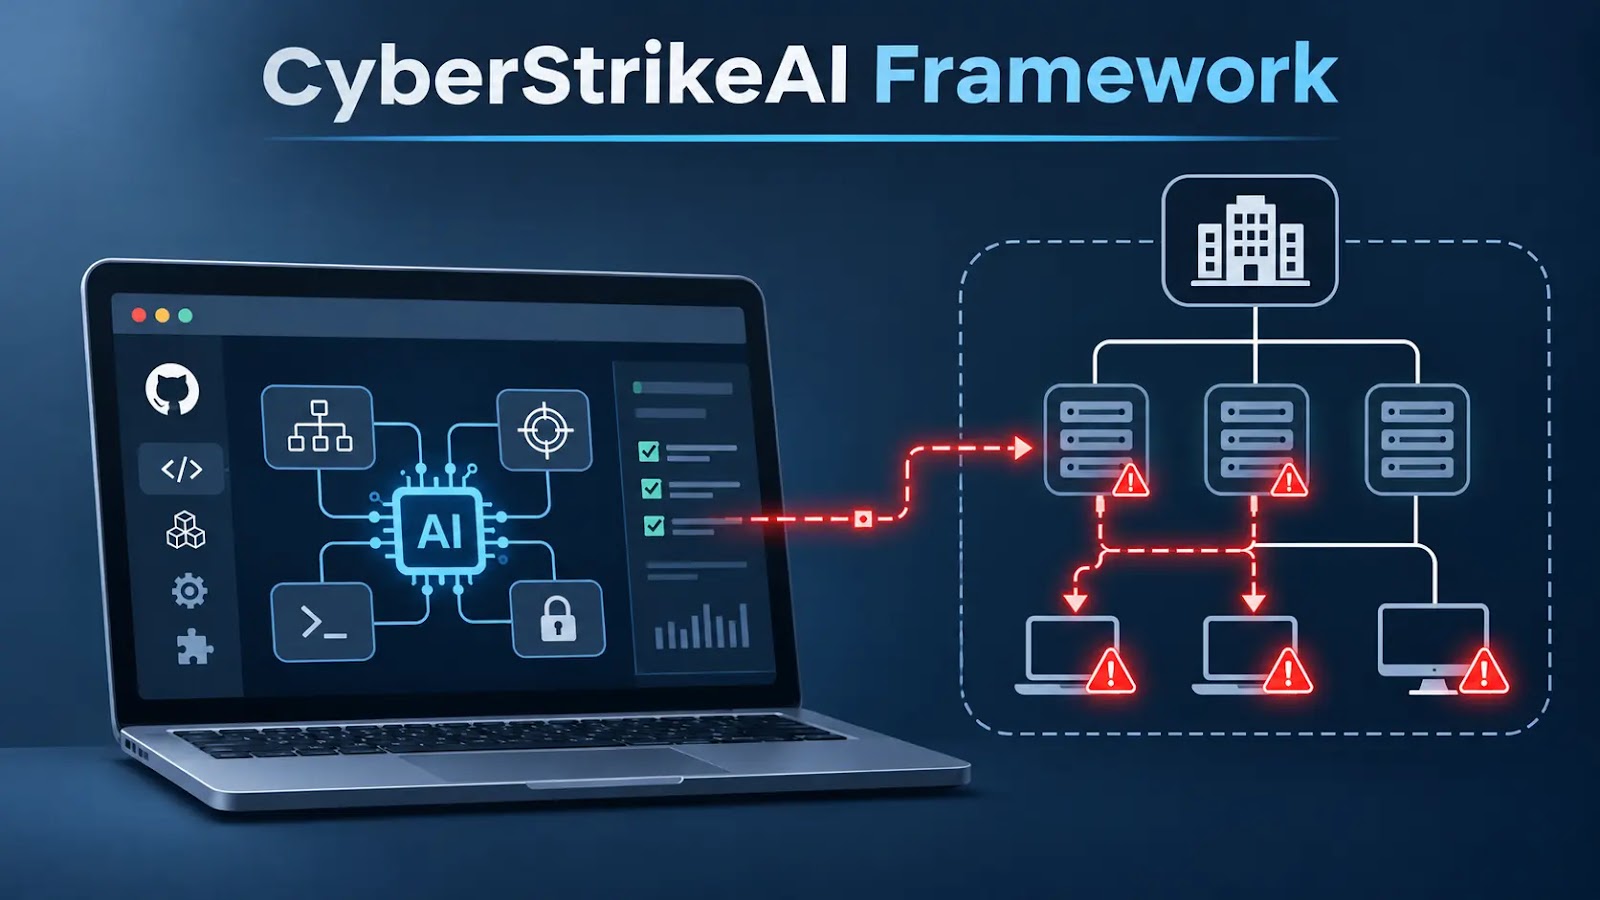
Hackers Weaponize Open-Source CyberStrikeAI Framework to Launch AI-Powered Network Intrusions

Hackers are abusing CyberStrikeAI, an open-source penetration-testing framework, to orchestrate network intrusions against educational organizations across Africa and Latin America. The findings illustrate AI moving beyond attack preparation into operational decision-making. Published November 2, Kaspersky’s investigation describes a human-directed operation in which an LLM selects tools, generates commands, interprets results, and determines subsequent actions. The […]

The post Hackers Weaponize Open-Source CyberStrikeAI Framework to Launch AI-Powered Network Intrusions appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
319 Suspicious Chrome Extensions Hijack Default Search Settings Without Sensitive Permissions

An investigation into browser extensions identified 319 suspicious extensions linked to about 13.4 million reported users, exposing a search-hijacking ecosystem operating since 2016. Marketed as manual finders, PDF converters, safe search utilities, and AI search tools, the extensions funnel queries through operator-controlled infrastructure before delivering Yahoo or Bing results. The Searchjacked investigation expands earlier research […]

The post 319 Suspicious Chrome Extensions Hijack Default Search Settings Without Sensitive Permissions appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
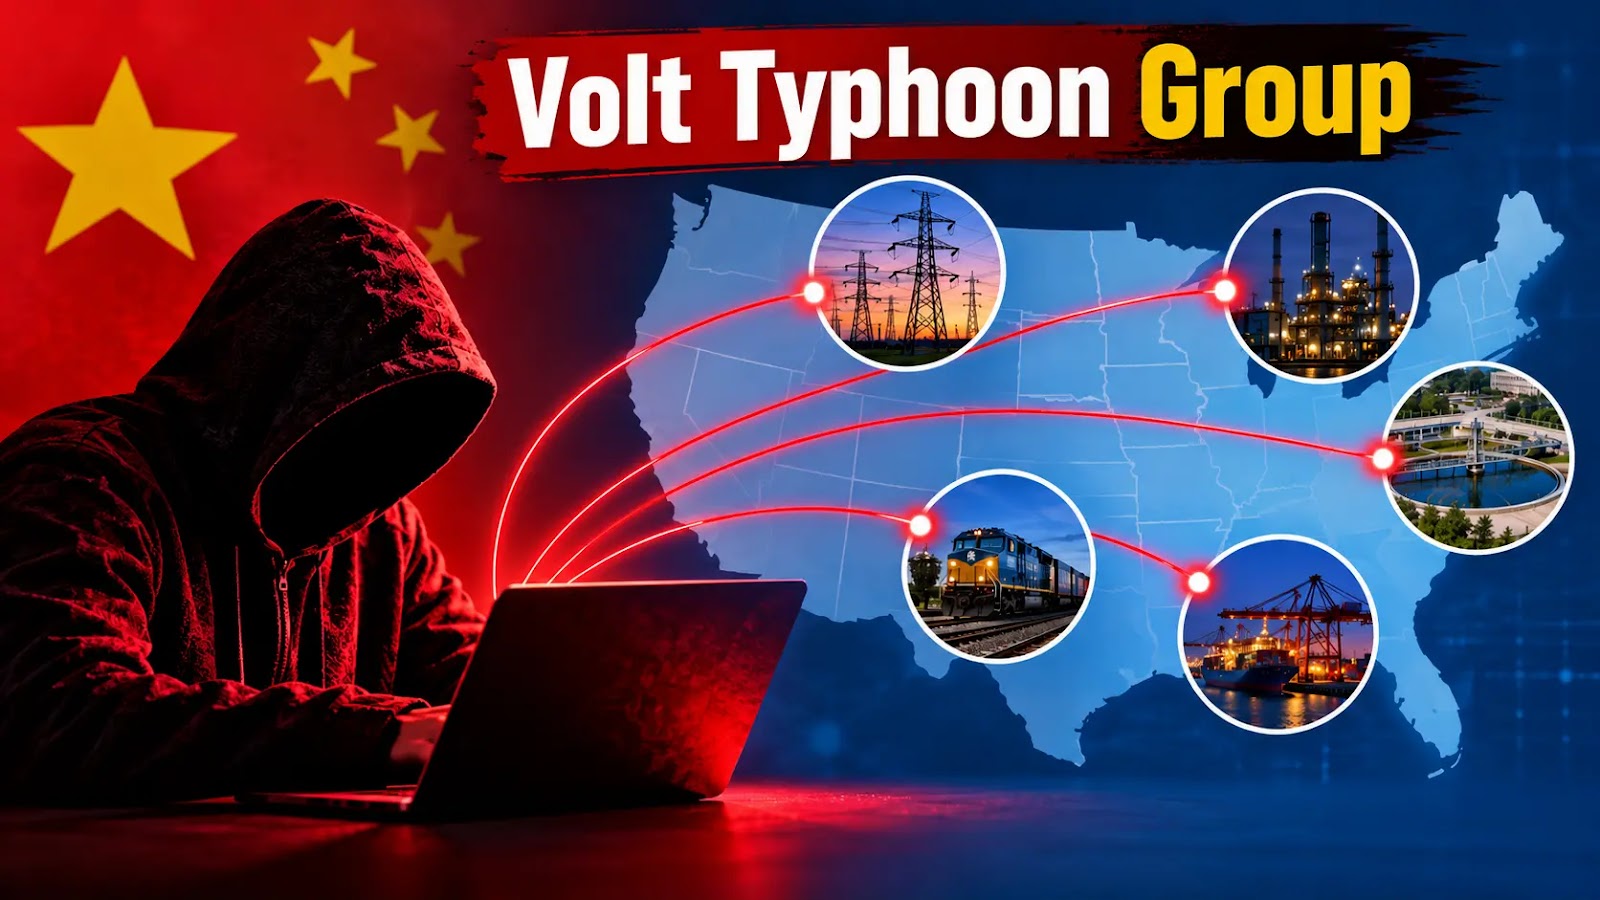
Volt Typhoon Hackers Exploit Multiple Zero-Days to Breach U.S. Critical Infrastructure Networks

Chinese state-sponsored hacking group Volt Typhoon has exploited multiple previously unknown vulnerabilities in enterprise management platforms to penetrate strategically significant organizations. Its investigation exposed Silent Train, a covert access framework built from rapidly rotating chains of compromised devices. Over three years, Black Lotus Labs issued hundreds of victim notifications, helping investigations uncover four confirmed zero-day […]

The post Volt Typhoon Hackers Exploit Multiple Zero-Days to Breach U.S. Critical Infrastructure Networks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌
❌