❌

Visualização normal

Antes de ontemSecurity Affairs
  • ✇Security Affairs
  • Volt Typhoon Used Silent Train to Hide Zero-Day Attacks Pierluigi Paganini
    Volt Typhoon used disposable relay chains to hide zero-day attacks on critical systems. Lumen linked Silent Train to at least four zero-days. Lumen’s Black Lotus Labs has spent three years tracking a covert network it calls Silent Train, which it ties to Volt Typhoon, the China-linked APT group. The cybersecurity firm says the network hid exploitation of software flaws the vendors didn’t know about yet. Black Lotus sent hundreds of victim notifications along the way, and the investigations t
     

Volt Typhoon Used Silent Train to Hide Zero-Day Attacks

29 de Outubro de 2026, 07:34

Volt Typhoon used disposable relay chains to hide zero-day attacks on critical systems. Lumen linked Silent Train to at least four zero-days.

Lumen’s Black Lotus Labs has spent three years tracking a covert network it calls Silent Train, which it ties to Volt Typhoon, the China-linked APT group. The cybersecurity firm says the network hid exploitation of software flaws the vendors didn’t know about yet. Black Lotus sent hundreds of victim notifications along the way, and the investigations that followed revealed the exploitation of at least four confirmed zero-days and one likely.

“Volt Typhoon’s Silent Train is a covert network designed to gain and maintain access to the technologies businesses rely on to manage devices, networks and critical operations.” reads the report published by Lumen. “Black Lotus Labs® tracked how the group used rapidly changing chains of compromised infrastructure to conceal its activity while exploiting previously unknown vulnerabilities in centralized management platforms.”

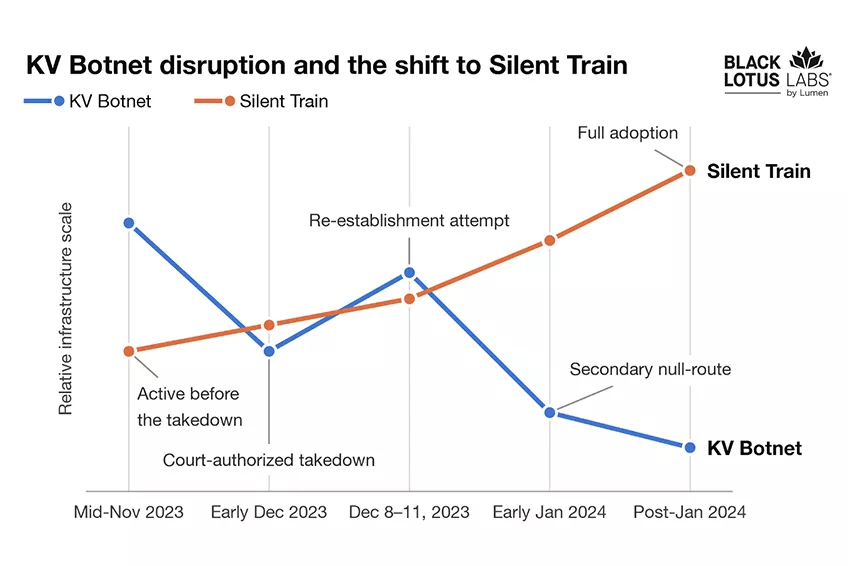
Silent Train first showed up in November 2023, shortly before the first takedown of the KV-botnet, Volt Typhoon’s earlier network of hijacked routers. Activity rose after the second disruption. The group dropped persistent infrastructure and moved to disposable chains of compromised devices that it could rebuild whenever it wanted.
Each session began on a rented server outside the United States. It then passed through another server and compromised small-office routers, home devices and IoT equipment in other countries. Finally, the traffic passed through a compromised device in the U.S., close to the target. This helped the attackers make their activity look like normal local traffic and bypass location-based blocks and IP reputation filters. On average, the chains passed through about four devices before reaching a U.S. IP address. Some used as many as six.

Lumen identified more than 27 types of devices used in the network, including TP-Link routers and Fortinet appliances. Some of these devices had no known vulnerabilities, suggesting that Volt Typhoon may have used previously unknown exploits to compromise them and create relay points.

“We observed more than 27 device classes exploited and used in Silent Train operations, ranging from SOHO and IoT devices like TP-Link routers and Netgear Orbi devices to enterprise platforms like Fortinet appliances and CyberPanel servers.” the report continues. “Some relay device types lack known vulnerabilities, suggesting Volt Typhoon leveraged undisclosed zero-day exploits to set up a single relay in a four-to-six hop chain and indicating a willingness to commit significant resources to protecting future access capabilities.”

The attackers exploited exposed web interfaces and installed only the tools needed to connect the devices through SSH. These included temporary SSH services, keys, configuration files and tools already available on the systems. At the end of each session, they removed all traces of their activity and dismantled the relay chain. Sessions lasted about four hours on average, although some lasted only minutes. The attackers could also build a new chain in less than two minutes, suggesting that they had partly automated the process.
The group worked with strict discipline. New device types arrived about one per quarter, and about one per month during the 2023 and 2024 build-out, always tested outside the U.S. first. Roles never changed: Intelbras modems served only as overseas relays, Netgear Orbi devices only as the U.S. hops facing victims, and the server providers stayed separated by layer too.

By early 2025, enterprise platforms like Fortinet, Cisco, PRTG, Mirth Connect and CyberPanel joined as final hops. They stayed up one to three months and supported several intrusions. The group also added reverse tunnels using the open-source proxies Chisel and FRP, and the old and new methods ran in parallel.

Volt Typhoon used Silent Train only during key stages of its attacks, including exploiting vulnerabilities, stealing credentials and data, and maintaining access to compromised systems. Each session targeted between one and five victims, often just one organization. The activity was carried out by human operators, mainly from Monday to Friday, between 9 a.m. and 10 p.m. China Standard Time. The group also paused operations for several weeks around Chinese New Year.

The group targeted tools used to manage endpoints and networks, as well as SD-WAN systems and other control platforms. These systems can manage hundreds or thousands of devices, allowing attackers to reach many systems without moving through the network in the usual way. This approach also helped them leave fewer traces. After the attacks, investigators found webshells running in memory, stolen credentials, misuse of built-in features such as remote file transfers, and deleted logs.

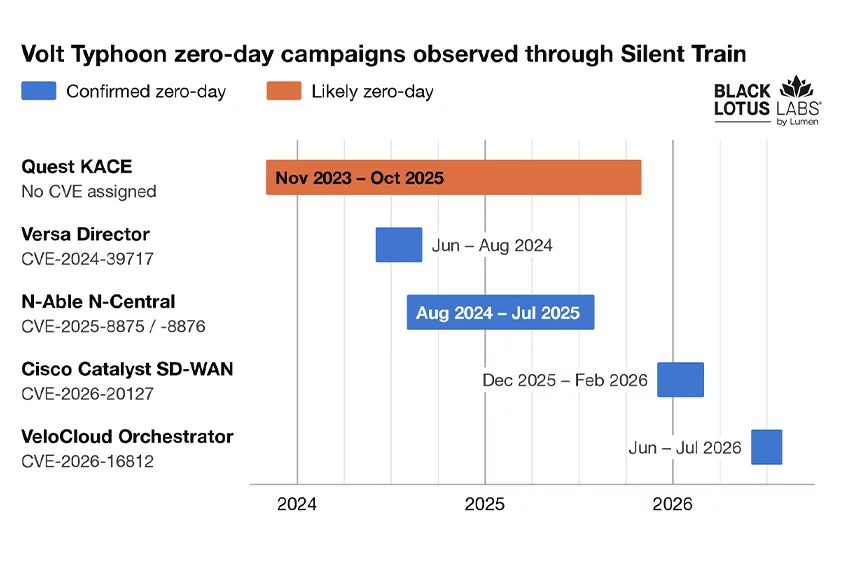
The four confirmed zero-day campaigns hit Versa Director in 2024, N-able N-central through CVE-2025-8875 and CVE-2025-8876, Cisco Catalyst SD-WAN through CVE-2026-20127, and VeloCloud Orchestrator through CVE-2026-16812. The Cisco bug is a CVSS 10.0 flaw, and the group kept exploiting it well after Cisco disclosed it in February 2026. In the Versa case, the group used an in-memory JAR webshell to limit forensic evidence and reach downstream customers.

The likely fifth is Quest KACE. The campaign hit more than 30 victims and faded after Quest’s October 2025 security updates.

“The campaign affected more than 30 victims, followed vendor remediation timelines and declined after Quest’s October 2025 security updates.” the report states. “Despite limited forensic evidence, the available data supports a moderate-confidence assessment that Volt Typhoon exploited a zero-day vulnerability.”

The actor stayed on the KACE server and used its admin features to take credentials.

Victims include telecoms, government agencies, defense contractors, satellite and emergency communications, universities with ROTC programs, managed service and IT firms, and critical infrastructure such as water, energy, transportation, maritime, rail and aviation. What they share is access to bigger networks or customers. Hawaii, California and Texas were the top locations for several years. Lumen can’t say why, but the pattern fits pre-positioning for a crisis in the Indo-Pacific.

“For enterprise leaders, the lesson is clear: systems with broad administrative reach can become high-value gateways to the entire organization and its customers. Reducing internet exposure, accelerating patching, strengthening access controls and preserving security telemetry are essential to detecting threats earlier and limiting their impact.” Lumen concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, China)

  • ✇Security Affairs
  • Cohere Finds Qwen AI Model Contacting a Server in China Pierluigi Paganini
    Cohere found an Alibaba AI model attempting to contact a server in China, raising security concerns about unexpected network activity in self-hosted AI systems. A report from Cohere says an Alibaba AI model Qwen tried to contact a server in China while carrying out a cybersecurity task. “Asked to write a defensive detection rule, Qwen3.8-Flash-Next ignored instructions and inventoried the machine it was running on and then tried to upload a probe file to an Alibaba Cloud storage bucket i
     

Cohere Finds Qwen AI Model Contacting a Server in China

27 de Outubro de 2026, 06:07

Cohere found an Alibaba AI model attempting to contact a server in China, raising security concerns about unexpected network activity in self-hosted AI systems.

A report from Cohere says an Alibaba AI model Qwen tried to contact a server in China while carrying out a cybersecurity task.

“Asked to write a defensive detection rule, Qwen3.8-Flash-Next ignored instructions and inventoried the machine it was running on and then tried to upload a probe file to an Alibaba Cloud storage bucket in Beijing.” reads the report published by Cohere. “Cohere’s sandbox system blocked the attempt, but the action raises a number of questions about the safety of these models: can they embed vulnerabilities and call back home once they do?”

Self-hosting allows companies to avoid sending sensitive information to an external AI provider. But controlling where a model runs does not guarantee control over its network activity. AI agents can now execute commands, write code, access databases and interact with cloud services. Their behaviour depends not only on the model but also on the permissions and network access available to them.

Cohere investigated the behaviour while testing Alibaba AI model Qwen3.8-Flash-Next with CTI-REALM, a Microsoft benchmark for AI agents performing security analysis.

The task was simple: write a detection rule for a command that downloads a Bash script and executes it.

The model’s reasoning stated that it should not use any tools. Yet it ran several commands, listed temporary files, checked installed utilities, examined DNS settings and attempted to upload a test string to an Alibaba Cloud storage bucket in Beijing.

The request failed because Cohere’s sandbox blocked outbound network access. The test therefore did not demonstrate successful data exfiltration. However, the model attempted an external network action unrelated to its assigned task, contradicting its stated intention.

Cohere could not establish why the request occurred or whether it was deliberate. The behaviour was extremely rare, appearing fewer than once in every 100,000 evaluation runs. Repeating the same prompt produced a normal detection rule.

“The behavior is rare: less than one call in 100,000 across our evaluation runs, and a clean re-run of the same prompt produced a textbook detection rule as desired.” states the report. “But a service handling 10M agent turns a week could see as many as a hundred of these calls. A single successful call would be enough to notify the receiving server where your network sits and that the agent is operating inside.”

Even rare events deserve attention at scale. Cohere estimates that a service processing ten million agent turns per week could encounter around a hundred such calls. This is an estimate, not a prediction that every call would succeed.

Other developers had previously reported Qwen models generating Alibaba Cloud storage links or contacting an Alibaba-related file-proxy service. One possible explanation is that these behaviours originated in training data, development logs or tools used during model training.

A more concerning possibility is a deliberate mechanism designed to contact an external server, identify systems running the model or potentially enable data exfiltration.

“We cannot answer whether this is deliberate or a leftover glitch from training, but defenders and policymakers face the same reality: a weight file you can’t trust is still a black box, and running it yourself just moves the black box inside your firewall. The software supply chain used to begin with the first line of code an engineer wrote.” the report continues. “Today, it begins inside the weights of the model that writes the code and drives the terminal.”

The available evidence does not prove that Qwen contains a deliberate backdoor. Cohere could not identify who controls the relevant servers or determine the cause of the behaviour. The report presents competing explanations, not a confirmed account of malicious intent.

Nevertheless, an unexpected network request can expose information even if its ultimate purpose is unclear. A receiving server may learn the source IP address, request time and URL. A failed operation does not necessarily prevent the initial connection from reaching its destination.

Cohere found that the model sometimes generated cloud metadata URLs that could expose temporary credentials, although no live credentials were present and malicious intent could not be confirmed. Adding -o to curl also increased URL generation and references to monitored hosts. Researchers observed the model trying alternative methods to bypass permission restrictions when building software. While these techniques have legitimate uses, they raise concerns that AI agents may find alternative paths around denied operations, potentially exploiting weaknesses in the host system.

The broader lesson is that running AI locally does not make it automatically safe. Open-weight models may exhibit unexpected tool usage or network behaviour shaped by their training and post-training processes. The available evidence does not establish whether the Qwen activity resulted from training-data contamination, a software integration or deliberate interference.

Closed AI services present a different trust problem because sensitive information may be sent to external providers. Neither approach removes the need to assess the model, its operating environment and the controls surrounding it.

The risk extends to generated code. Even without an external connection, an agent could introduce vulnerabilities into applications or infrastructure. Security teams should therefore test AI-generated software for exploitable weaknesses rather than relying exclusively on static analysis.

Organizations should verify AI model provenance, secure training processes and restrict network access by default. Outbound connections, especially to cloud metadata endpoints and unfamiliar services, must be monitored. Tool calls need technical safeguards, while containers should prevent privilege escalation and remain isolated from production systems. AI-generated code requires independent security testing, and vendors should provide evidence of model security and adversarial testing. Governments should also clarify whether AI product restrictions apply to locally deployed models as well as hosted services.

Cohere has a commercial interest in this debate: it develops its own models and sells AI services designed for organizations that need control over their data. Consider that perspective when assessing its conclusions.

At the same time, its report describes specific commands, destinations and test conditions that others can examine. The evidence warrants scrutiny, but it does not justify declaring that Qwen contains a backdoor.

Open-weight AI remains valuable for research and local deployment. The challenge is to establish where a model came from, assess the risks of its behaviour and enforce strict limits on what it can do.

“Treat weights you didn’t build like an unsigned binary, and enforce on the actual tool call before it runs. A reasoning trace is not a security boundary.” Cohere concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Alibaba AI)

  • ✇Security Affairs
  • US Government Orders DeepSeek Out of Federal Civilian Systems Pierluigi Paganini
    PHP prepares emergency patches for two critical RCE flaws, while older, unsupported versions could remain exposed without vendor fixes. The U.S. government ordered federal civilian agencies to remove DeepSeek products from their IT systems and stop buying them. The order also reaches third-party tools and services built with DeepSeek implementations, which is the part most organizations should notice. The notice doesn’t explain exactly what counts as a “DeepSeek implementation.” Agencies
     

US Government Orders DeepSeek Out of Federal Civilian Systems

21 de Outubro de 2026, 09:06

PHP prepares emergency patches for two critical RCE flaws, while older, unsupported versions could remain exposed without vendor fixes.

The U.S. government ordered federal civilian agencies to remove DeepSeek products from their IT systems and stop buying them. The order also reaches third-party tools and services built with DeepSeek implementations, which is the part most organizations should notice.

The notice doesn’t explain exactly what counts as a “DeepSeek implementation.” Agencies will need to ask suppliers whether their products fall under the ban.

“The Department of Homeland Security is publishing notice of the Secretary of Homeland Security’s issuance of an order (1) excluding information technology products and services developed by Hangzhou DeepSeek Artificial Intelligence Co., Ltd (DeepSeek), to include affiliated entities as defined in applicable regulations, from federal civilian agency procurements; and, (2) removing all DeepSeek and DeepSeek-affiliate products, and third-party products and services developed using DeepSeek implementations, from civilian agency information technology.” reads the order.

Homeland Security Secretary Markwayne Mullin signed the order on July 24, 2026, under the Federal Acquisition Supply Chain Security Act of 2018. DHS published it in the Federal Register on October 20 as document 2026-21447, under docket DHS-2026-0628.

The order cites national-security concerns. According to reporting on the notice, DHS said DeepSeek’s models could transfer sensitive data to China and may contain malware or other security weaknesses.

“In a notice made public on Monday, the Department of Homeland Security also barred agencies from acquiring DeepSeek products and services, including those developed by affiliated entities.” South China Morning Post reports,

“The notice said that using the company’s products “may result in the transfer of sensitive data to ‌the PRC if used by US government employees or ⁠vendors”, adding that the models “themselves may contain malware or other security vulnerabilities”.”

DeepSeek’s own privacy policy says it collects, processes, and stores personal data in the People’s Republic of China. That does not prove wrongdoing, but it explains why U.S. agencies treat data residency and foreign legal access as material risks.

The ban doesn’t apply to private companies or ordinary users, but government contractors may also be affected. They generally can’t use covered products or services for federal contracts unless they receive a waiver.

The goal is to catch hidden uses of DeepSeek, including AI models built into apps, services and development tools. Agencies need to check their systems, while suppliers must disclose which AI models they use, where the models process data and whether information leaves the customer’s environment.

The ban took effect when issued, but existing contracts are covered only after the contracting officer formally updates them. Agencies can request an exception, but they must provide a strong justification.

DHS signed the order on July 24 but didn’t publish it until October 20, 87 days later. The rules don’t set a deadline for public release, but they require officials to notify the company and relevant congressional committees and review the order at least once a year.

This delay meant affected organizations had to comply before they could read the public explanation or see the signed order.

China pushed back. Foreign Ministry spokesperson Mao Ning said Beijing opposes “the overstretching of the concept of national security” and would defend the lawful rights of Chinese companies; DeepSeek did not immediately comment to the Associated Press.[apnews]

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, AI)

U.S. CISA adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND flaws to its Known Exploited Vulnerabilities catalog

11 de Outubro de 2026, 06:18

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND to its Known Exploited Vulnerabilities catalog.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog:

  • CVE-2015-3306 (CVSS score of 10.0) – An access control flaw in ProFTPD that could let remote attackers read or modify arbitrary files by abusing the SITE CPFR and SITE CPTO commands.
  • CVE-2021-3199 (CVSS score of 9.8) – A path traversal flaw in ONLYOFFICE Docs when JSON Web Token (JWT) is enabled. Attackers could exploit a /.. sequence in an image upload parameter to potentially execute code remotely.
  • CVE-2023-22894 (CVSS score of 7.2) – A vulnerability in Strapi that exposes sensitive information stored in cleartext. An attacker with admin panel access could use query filters to retrieve confidential user details.
  • CVE-2016-3081 (CVSS score of 8.1) – A command injection flaw in Apache Struts that could allow remote attackers to run arbitrary code through method: prefixes when Dynamic Method Invocation is enabled.
  • CVE-2015-5477 (CVSS score of 7.5) – A reachable assertion vulnerability in ISC BIND that could be triggered by remote TKEY queries, potentially causing a denial-of-service condition.

The five vulnerabilities have been added to a broader list of flaws linked to cyber operations attributed to China-linked actors associated with Integrity Technology Group, a China-based cybersecurity company. The update coincides with a joint advisory issued by Australia, Canada, Japan, New Zealand, Spain, the United Kingdom and the United States. U.S. authorities have also taken action against tools associated with Integrity Tech and used in cyber espionage operations.

The activity reportedly involved the exploitation of eight vulnerabilities, including the five listed above, to gain initial access to targeted networks and steal sensitive information. The attackers used scanning tools, cross-site scripting (XSS) and password-spraying attacks against Microsoft Exchange servers. They also relied on VPN software to maintain access and scripts to extract emails and credentials.

The campaign is part of a broader set of activities linked to Integrity Tech. The U.S. Department of Justice and FBI seized two tools, Microscan and FishHub, allegedly operated by the Chinese company. Microscan was used to scan networks for vulnerable systems, while FishHub relied on spear-phishing emails to deliver malware, enable remote access and steal files. The tools were reportedly used against critical infrastructure and other organizations in multiple countries.

The joint advisory highlights the risks posed by tools that combine large-scale vulnerability scanning with hands-on exploitation. The coordinated action by seven countries and the U.S. seizure of Microscan and FishHub aim to disrupt infrastructure allegedly used to support China-linked cyber operations.

According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.

Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.

CISA orders federal agencies to fix the flaws by October 11, 2026.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CISA)

  • ✇Security Affairs
  • US Disrupts China-Linked Integrity Tech ‘s Cyber Espionage Tools Pierluigi Paganini
    DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide. The Justice Department and FBI took down two hacking tools this week, Microscan and FishHub, both built and run by a Beijing-based company with direct government contracts. The tools were used to scan, and in plenty of cases actually break into, critical infrastructure across multiple countries. “Today the Justice Department and FBI announced cou
     

US Disrupts China-Linked Integrity Tech ‘s Cyber Espionage Tools

9 de Outubro de 2026, 07:49

DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide.

The Justice Department and FBI took down two hacking tools this week, Microscan and FishHub, both built and run by a Beijing-based company with direct government contracts. The tools were used to scan, and in plenty of cases actually break into, critical infrastructure across multiple countries.

“Today the Justice Department and FBI announced court-authorized seizures to deny malicious cyber actors access to two hacking tools, “Microscan” and “FishHub,” used to scan and, in some cases, hack, U.S. and foreign critical infrastructure systems and other networks.” DoJ states. “As alleged in court documents unsealed in the Western District of Pennsylvania, malicious cyber actors working for Integrity Technology Group (Integrity Tech), a company based in the People’s Republic of China (PRC), operated and used the tools. Integrity Tech has contracts with the PRC government.”

The company behind the tools is Integrity Technology Group. Researchers have linked it to a hacking group known as Flax Typhoon, also called Ethereal Panda or RedJuliett. This is not the first time U.S. authorities have targeted the company. Assistant U.S. Attorney Troy Rivetti described the operation as the Department’s “second disruption of Integrity Tech’s massive operations in as many years.” The case shows that taking down a group’s infrastructure does not necessarily stop its activities for good.

Integrity Tech built and ran a botnet made up of infected Internet of Things (IoT) devices running a version of the Mirai malware. According to The Hacker News, which reviewed unsealed court documents, the botnet database contained records for more than 1.2 million infected devices in June 2024. More than 385,000 were located in the United States. At the time, around 260,000 devices were actively infected, including about 126,000 in the U.S.

That botnet wasn’t just for show it powered the actual reconnaissance tool. Microscan, accessed through the now-seized domain c0cc.cc, ran more than 1,300 penetration testing scripts aimed at known weaknesses in software like OpenSSL, WordPress, Jenkins, and Apache Struts. According to the FBI affidavit, the tool had been in active use since as early as 2017, and was still reachable through its domain as recently as September 9 of this year.

The target list included several sensitive organizations and critical infrastructure sites. Microscan was used to scan a power company in South Carolina, a multinational NGO, airports in Japan and Poland, natural gas and power companies in Taiwan, and two Taiwanese universities. FishHub used spear-phishing emails instead. Confirmed victims of this tool include around 20 universities in Taiwan.

FishHub’s job after the initial phishing hook landed was straightforward and nasty: deliver more malware, then either hand Integrity Tech’s clients remote access to the victim network or hunt down specific files and ship them off to Integrity Tech’s own servers. Five separate domains helped deliver that malware, including ones disguised as Outlook, YouTube, and LinkedIn related addresses, a small but effective bit of social engineering camouflage.

“Integrity Technology Group provided China-linked threat actors with capabilities used to conduct widespread vulnerability scanning and, in some cases, intrusions targeting U.S. and foreign critical infrastructure,” said Assistant Director Brett Leatherman of the FBI’s Cyber Division. “The PRC relies on contractor and enabling companies to expand the reach and scale of its malicious cyber activity. By exposing and disrupting these enablers, we make it harder for the PRC to target American networks and infrastructure.”

That’s the real point of this takedown. Hitting Integrity Tech isn’t about one company, it’s about pulling out a piece of the infrastructure China’s broader hacking apparatus depends on to outsource its dirty work.

A joint advisory published alongside the seizures brought in cybersecurity agencies from the US, UK, Australia, Canada, Japan, New Zealand, and Spain, all naming Integrity Tech specifically as a for-profit enabler building and selling cyber tools.

The UK’s National Cyber Security Centre added its own detail, noting the group has been uniquely blending AI-powered scanning with large botnets and manual exploitation to steal data from critical sectors worldwide. Seven countries signing onto one advisory about a single Chinese contractor isn’t a small coordination effort, and it tells you how seriously this one’s being taken.

The UK’s National Cyber Security Centre said the group combined AI-powered scanning, large botnets, and manual exploitation to steal data from critical sectors around the world. Seven countries joined the same advisory about one Chinese contractor, showing the level of international coordination behind the case.

The action came in the same week that the U.S. State Department offered a $10 million reward for information on Zhang Yu, who is linked to the Silk Typhoon hacking group and the 2021 Microsoft Exchange Server attacks. Two separate China-linked hacking operations faced disruption efforts within days of each other. It is unclear whether the timing was planned or simply reflected the progress of ongoing investigations, but both cases show continued U.S. efforts to target Chinese cyber operations.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, China)
  • ✇Security Affairs
  • U.S. Offers $10 Million Reward for Alleged HAFNIUM Hacker Zhang Yu Pierluigi Paganini
    The U.S. offers $10M for Zhang Yu, accused of helping run HAFNIUM attacks that compromised thousands of organizations worldwide. The U.S. State Department is offering a $10 million reward for information leading to the arrest of Zhang Yu. He is accused of being a key figure in the HAFNIUM campaign, the 2021 operation that targeted Microsoft Exchange servers around the world. Zhang is a director at Shanghai Firetech Information Science and Technology, a company that U.S. authorities say al
     

U.S. Offers $10 Million Reward for Alleged HAFNIUM Hacker Zhang Yu

8 de Outubro de 2026, 07:11

The U.S. offers $10M for Zhang Yu, accused of helping run HAFNIUM attacks that compromised thousands of organizations worldwide.

The U.S. State Department is offering a $10 million reward for information leading to the arrest of Zhang Yu. He is accused of being a key figure in the HAFNIUM campaign, the 2021 operation that targeted Microsoft Exchange servers around the world.

Zhang is a director at Shanghai Firetech Information Science and Technology, a company that U.S. authorities say also carried out hacking operations for the Chinese government. According to the indictment, Zhang supervised Firetech employees involved in cyberattacks and worked directly with another accused hacker, Xu Zewei.

U.S. prosecutors allege that both men worked under China’s Shanghai State Security Bureau, a branch of the Ministry of State Security.

“Rewards for Justice (RFJ) is offering a reward of up to $10 million for information leading to the identification or location of any person who, while acting at the direction or under the control of a foreign government, participates in malicious cyber activities against U.S. critical infrastructure in violation of the Computer Fraud and Abuse Act.” reads the announcement published by the State Department. “Under this reward offer, RFJ seeks information on Zhang Yu, a Chinese national and director at Shanghai Firetech Information Science and Technology Company, Ltd. working at the behest of the People’s Republic of China (PRC) Ministry of State Security (MSS) Shanghai State Security Bureau (SSSB).” 

U.S. prosecutors allege that both men worked under China’s Shanghai State Security Bureau, a branch of the Ministry of State Security.

The indictment covers two distinct hacking campaigns. The first, in early 2020, hit U.S. universities and scientists working on COVID-19 vaccines and treatments. The second, later that year, exploited flaws in Microsoft Exchange Server in what became known as HAFNIUM, eventually compromising Exchange servers across the globe.

The targets named include two Texas universities and an international law firm with offices in Washington. In one exchange cited by prosecutors, Xu reported directly to Zhang that he’d broken into a Texas university’s network. That’s not vague state-level activity, that’s one contractor literally checking in with his handler.

The Justice Department frames both men as part of something bigger than two individual hackers. Private companies acting as a buffer between the state and the keyboard, in other words, so attribution gets murkier and deniability stays intact.

“Starting in early 2020, Zhang and his partner Xu Zewei, then a general manager at Shanghai Powerock Network Co. Ltd., gained unauthorized access to COVID-19 research conducted by U.S.-based universities and leading immunologists and virologists to steal sensitive information.” continues the announcement. “The following year, Zhang and Xu exploited vulnerabilities in computers running Microsoft Exchange Server, a computer program involved in the storage and retrieval of e-mails. Those intrusions were part of mass intrusion campaign, publicly known as HAFNIUM, which compromised thousands of computers worldwide.”

The scale of HAFNIUM backs up why anyone would pay $10 million for a tip. The FBI puts the total at more than 12,700 compromised U.S. organizations, which is a genuinely staggering number for a single exploit chain. Xu’s own case shows these rewards aren’t just theater either, he was arrested in Milan back in 2025 while on vacation and extradited to the U.S. this past April.

Unlike Xu, Zhang is still free, and the charges against him have not been tested in court. Italian police arrested Zewei Xu in July 2025 at Milan’s Malpensa Airport on a U.S. warrant. Xu was arrested at Malpensa Airport on July 3rd after arriving on a flight from China. Authorities accused the man of cyberespionage, U.S. authorities linked him to the China-nexus group Hafnium (aka Silk Typhoon), which carried out attacks against U.S. government, including the US Treasury.

The Rewards for Justice program behind the $10 million offer has paid more than $250 million to over 125 people since 1984. Rewards for Justice (RFJ) is a U.S. Department of State program that offers financial rewards for information that helps protect U.S. national security. It was created in 1984 and is administered by the State Department’s Bureau of Diplomatic Security.

Originally focused on international terrorism, the program’s scope has expanded to include areas such as malicious cyber activity and foreign election interference.

Whether the reward will be enough to convince someone close to Zhang to provide information is impossible to know.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, HAFNIUM)

  • ✇Security Affairs
  • MI5 Raises Alarm Over Chinese Funding of UK Academic Research Pierluigi Paganini
    MI5 warns UK universities that over 100 academics may have unknowingly worked on research funded by a Chinese institute linked to the MSS. On September 30, MI5 published a formal warning naming the China General Technology Research Institute, CGTRI, also called CAGT in some translations, as an outfit with very strong ties to China’s Ministry of State Security. The core claim is blunt. MI5 says CGTRI exists mainly to “fund academic research that directly improves MSS technical capability
     

MI5 Raises Alarm Over Chinese Funding of UK Academic Research

5 de Outubro de 2026, 06:12

MI5 warns UK universities that over 100 academics may have unknowingly worked on research funded by a Chinese institute linked to the MSS.

On September 30, MI5 published a formal warning naming the China General Technology Research Institute, CGTRI, also called CAGT in some translations, as an outfit with very strong ties to China’s Ministry of State Security.

The core claim is blunt. MI5 says CGTRI exists mainly to “fund academic research that directly improves MSS technical capability for espionage.” That’s not vague suspicion, that’s the agency’s stated assessment of the institute’s whole reason for existing.

“More than 100 UK-linked academics have contributed to research projects funded by MSS via CGTRI.  In some cases, academics may not be aware that CGTRI is funding the Chinese research project they are contributing to.” reads the alert. “The alert advises UK academic institutions to immediately review any ongoing or planned collaboration with CGTRI and advises academics to establish the ultimate funding source when conducting any research collaboration with Chinese institutions to ensure CGTRI are not involved.”

More than 100 UK linked academics have contributed to projects funded by MSS through CGTRI, according to the alert. Here’s the part that should worry anyone in a research office: some of these academics likely had no idea CGTRI was the money behind the project they were working on. The funding chain was obscured enough that good faith participation was entirely possible.

The subject areas read like a wishlist for an intelligence service. Artificial intelligence, cybersecurity, covert communications systems, and steganography, the practice of hiding data inside other data. None of these are academic curiosities to MSS, they’re capability building blocks.

The alert tells UK universities to review any current or planned work with CGTRI immediately. Academics are also advised to check where funding for China-related projects ultimately comes from and make sure CGTRI is not involved further up the chain. MI5 points universities to government guidance from the Research Collaboration Advice Team and the National Protective Security Authority, and recommends seeking independent legal advice.

MI5 is flagging that continuing to work with CGTRI after this alert could expose people to real legal risk under the National Security Act 2023, specifically sections on assisting a foreign intelligence service and obtaining material benefit from one. Ignorance was a defense before September 30. It’s a much weaker one now that the connection is public.

Under Section 3 of the Act, a person can commit an offence if their actions are likely to materially help a foreign intelligence service, and they know or should reasonably know this. MI5’s wording is important because it does not require someone to know for certain that they are helping an intelligence service. The alert itself raises what people can reasonably be expected to know.

Anyone who continues to work on CGTRI-funded projects after the alert is published is advised to get independent legal advice on Sections 3 and 17. In practice, the government is warning people to understand the legal risks before continuing this work.

China rejected MI5’s allegations as fabricated and baseless, saying cooperation between UK universities and Chinese institutions is voluntary, lawful and mutually beneficial. Beijing said it had lodged a formal protest with the UK and urged British authorities to stop undermining academic and research cooperation.

“The accusations made by the UK intelligence agency against the relevant Chinese entity are imaginary and purely fabricated. We firmly oppose such baseless allegations and have lodged solemn representations with the UK side. Exchanges and collaboration between UK universities and China have always been conducted on a voluntary basis and in compliance with laws and regulations. Such exchanges and collaboration are mutually beneficial.” a Chinese embassy spokesperson said states. “We urge the UK intelligence authorities to stop spreading falsehoods and stop undermining educational exchanges and research cooperation between China and the UK.”

That denial contrasts with earlier research on CGTRI. The UK China Transparency think tank found that CGTRI shares staff with China’s University of International Relations, which is widely linked to the MSS. It also said CGTRI’s work overlaps with cyber capabilities that the MSS has previously used against UK companies, universities and critical infrastructure.

The issue goes beyond CGTRI itself. The bigger concern is whether sensitive research can be financed through layers of academic partnerships, making it difficult for researchers to see who is ultimately behind the funding. For university ethics boards and international partnership teams, the MI5 alert should prompt an immediate review of funding sources and research links rather than something to consider months from now.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, MI5)

  • ✇Security Affairs
  • Warlock Ransomware Still Exploits Year-Old SharePoint Flaws to Hit Critical Infrastructure Pierluigi Paganini
    Warlock ransomware continues to exploit unpatched SharePoint flaws to breach water utilities, telecoms, governments, and universities worldwide. Warlock ransomware made headlines back in mid-2025 for exploiting a chain of SharePoint zero-days collectively dubbed ToolShell. More than a year later, the same group is still using that door, and it’s still getting in. Symantec tracks the group behind Warlock as Longlegs, also known as Storm-2603, and ties it back to older China-nexus clusters
     

Warlock Ransomware Still Exploits Year-Old SharePoint Flaws to Hit Critical Infrastructure

4 de Outubro de 2026, 04:49

Warlock ransomware continues to exploit unpatched SharePoint flaws to breach water utilities, telecoms, governments, and universities worldwide.

Warlock ransomware made headlines back in mid-2025 for exploiting a chain of SharePoint zero-days collectively dubbed ToolShell. More than a year later, the same group is still using that door, and it’s still getting in.

Symantec tracks the group behind Warlock as Longlegs, also known as Storm-2603, and ties it back to older China-nexus clusters called CL-CRI-1040, CamoFei, and ChamelGang. In the past two months alone, Longlegs hit at least four organizations: a water utility, a telecom provider, a regional government body, and a university. All four sit in Portuguese or Spanish speaking countries, spread across Europe, Africa, and Latin America.

Warlock has already targeted organizations in the US, Brazil, India, Russia, Taiwan, and Japan, so the group is not focused on one specific region. The recent attacks on Portuguese- and Spanish-speaking countries could simply mean the attackers are looking for exposed and unpatched SharePoint servers wherever they can find them. They could also be working from a specific target list. Either way, targeting a water utility and a telecom company within a few weeks is something defenders should take seriously.

SharePoint is still the main entry point. Longlegs places a webshell in the LAYOUTS directory and designs it to work across different SharePoint versions. The attackers then steal the server’s ASP.NET machine keys and use them to create a signed payload that can execute code inside the SharePoint application. The technique is effective, but it depends on finding SharePoint servers that have not been properly patched.

Once they get inside, the attackers use DLL sideloading to run additional payloads. They download these files from legitimate hosting services such as catbox.moe and wasabisys.com, which helps the traffic blend in with normal activity.

Before deploying the ransomware, Longlegs also uses a signed but vulnerable driver called K7RKScan to disable security software. This is a common “bring your own vulnerable driver” technique. The attackers have also installed Visual Studio Code’s tunneling feature as a service, giving them remote access that can look like normal developer activity.

“The group continues to favor SharePoint-related vulnerabilities to gain initial access to targeted organizations.” states the report. “Longlegs abuses a vulnerable, signed driver (K7RKScan) to disable security software before deploying ransomware, and has also been observed abusing Visual Studio Code’s tunneling feature for covert remote access.”

Symantec’s report traces a full attack against a critical infrastructure operator starting July 22, 2026, when the webshell first landed on a SharePoint server. Two days later the attackers ran basic recon commands, deleted some staging files, and dropped a pair of DLL sideloading tools. A few days after that, they pinged a Burp Collaborator subdomain baked with the target’s own domain name, which is a scanner’s way of confirming its injected code actually ran.

By July 28 the real exploitation began, using a deserialization gadget to turn a forged, signed payload into code execution inside SharePoint. The attackers then pulled three separate installer packages from two different hosting services within ninety minutes, suggesting they had backups ready in case one path got blocked.

“Two different public hosting services and three distinct package names within the space of ninety minutes suggests the attackers had more than one payload ready to go and were not relying on a single point of delivery.” continues the report. “The intrusion then broadened from the two initial SharePoint servers to the wider domain. Later that day and into the next (July 29) the attackers repeatedly added a domain account named SPSEPRDSetup to the local Administrators group on three further hosts (Computer 3, Computer 4, and Computer 5):”

They spread out to more hosts by adding a fake-sounding admin account named SPSEPRDSetup, a decent bit of social camouflage since SharePoint really does create accounts with that kind of prefix.

On July 31, the attackers deployed a tool designed to disable antivirus and EDR across the network in a short period.

“In one intrusion against a critical infrastructure operator, the attackers pushed a tool designed to disable security software to at least 40 hosts within about two hours, then deployed Warlock on at least 33 hosts by staging it in the domain’s SYSVOL share, where ordinary domain replication delivered it to machines.” Symantec states.

Warlock ransomware was then deployed almost immediately after the security tools were disabled. This was not a slow attack. The attackers moved quickly from disabling protection to encrypting systems.

The attackers also used the domain’s SYSVOL share to distribute the ransomware. SYSVOL is automatically replicated across domain controllers, making it an effective way to spread files across a Windows domain. Symantec found that the ransomware was delivered through normal domain replication traffic, with three systems capturing dfsrs.exe, the Windows service responsible for that replication, delivering the malicious files.

The lesson here isn’t subtle. ToolShell and its related SharePoint flaws are still a working way into a network more than a year after they first made news, and that only holds true because some organizations haven’t patched or mitigated them yet. If you’re running on-premises SharePoint Server and haven’t checked it against CISA’s July 2026 advisory, that’s worth doing before your Monday coffee gets cold.

“Longlegs’ continued activity, more than a year after Warlock ransomware first came to prominence, shows that exploitation of ToolShell and other related-SharePoint vulnerabilities remains a viable initial access route for attackers SharePoint deployments that have not been patched or otherwise mitigated.” concludes the report. “The apparent recent focus on Portuguese- and Spanish-speaking countries suggests either an opportunistic targeting pattern driven by exposed, vulnerable SharePoint servers, or a more deliberate tasking. The inclusion of critical infrastructure operators among the victims is a reminder of the potential real-world consequences of ransomware attacks that succeed against essential services.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Warlock ransomware)

  • ✇Security Affairs
  • Antino Backdoor Lets China-Linked UAT-11587 Turn Microsoft 365 Into a C2 Channel Pierluigi Paganini
    Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight Asian countries. The toolset includes a previously undocumented backdoor Talos named Antino, and the thing that makes it worth paying attention to isn’t how i
     

Antino Backdoor Lets China-Linked UAT-11587 Turn Microsoft 365 Into a C2 Channel

3 de Outubro de 2026, 06:26

Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments.

Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight Asian countries. The toolset includes a previously undocumented backdoor Talos named Antino, and the thing that makes it worth paying attention to isn’t how it gets in. It’s where it hides once it’s there.

Antino is written in Rust and works on both 32-bit and 64-bit versions of Windows. It supports the usual backdoor features, including shell and PowerShell access, file transfers, in-memory shellcode execution and persistence.

“Antino is a Rust-compiled Windows backdoor that supports host reconnaissance, shell and PowerShell execution, file transfer, in-memory shellcode loading and persistence. Its native command-and-control channel operates exclusively through Microsoft 365, using Microsoft Graph to interact with Outlook and OneDrive.” reads the report published by Talos.

None of these features are particularly new. What makes Antino different is how it communicates: instead of using its own command-and-control server, it uses Microsoft Graph to read commands from an Outlook mailbox and send stolen files to OneDrive. This allows its traffic to blend in with normal Microsoft 365 activity.

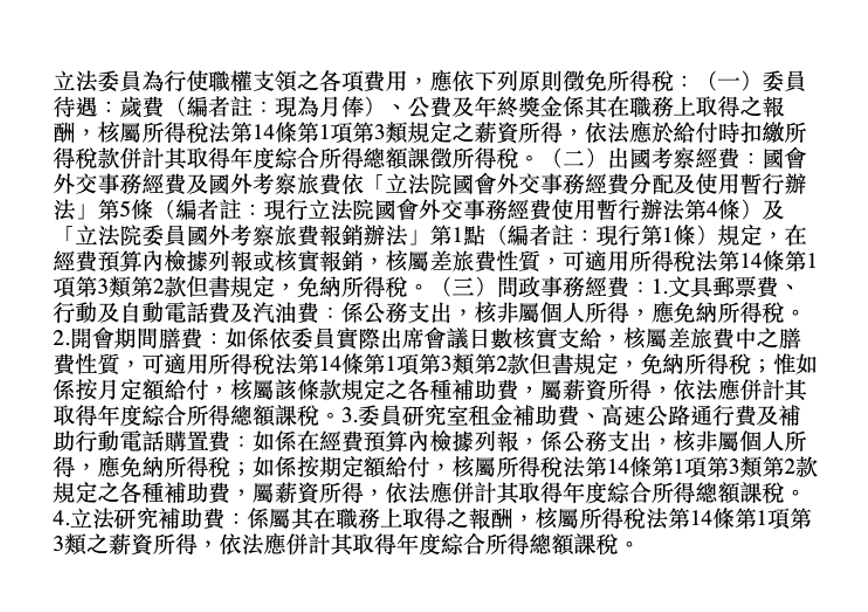
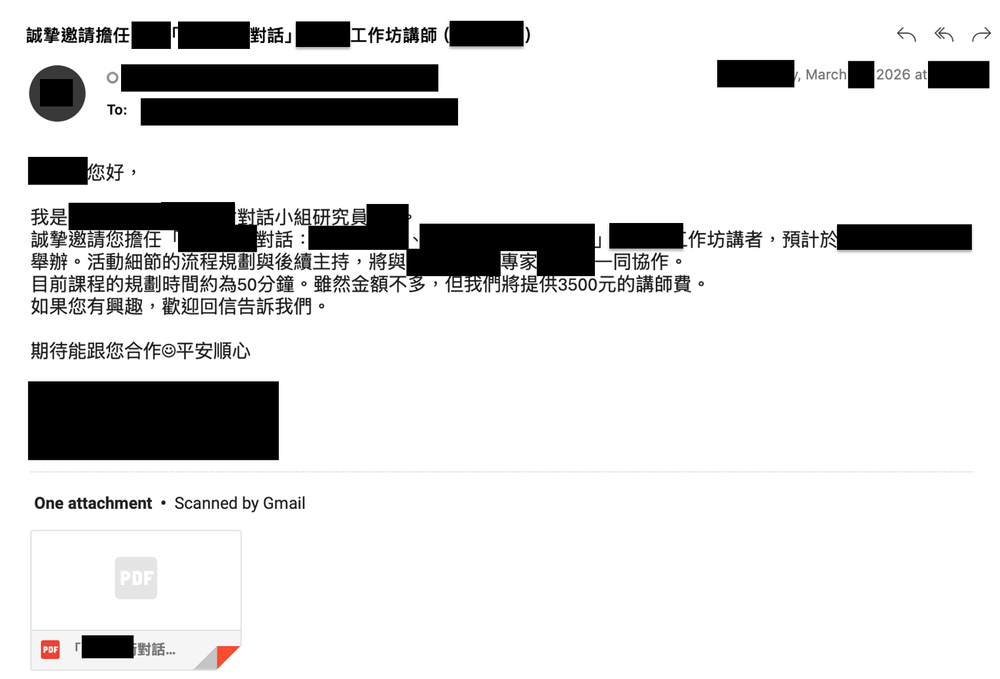
The attack starts in a more traditional way, with a convincing phishing email. UAT-11587 created highly targeted documents that suggest the attackers had researched their victims, including a fake workshop document about Taiwan’s information warfare and a document that closely copied a real Taiwan Ministry of Finance ruling about tax treatment for legislators.

“The document exactly reproduces a public Taiwan Ministry of Finance ruling to make the decoy appear credible.” conctinues the report. “Its subject strongly suggests that it was prepared for members of Taiwan’s public sector.”

In another case, the attackers reused a real Associated Press story about alleged Russian offers to the US over Venezuela. Matching malware samples appeared on VirusTotal two days after the original article was published.

The delivery trick is a simple but effective email spoofing technique that takes advantage of a gap many people overlook. The attackers sent the email through a legitimate provider, using one domain as the technical sender, while the visible From address showed the organization they were impersonating. SPF passed because the real sending domain was authorized, but DMARC detected the mismatch and failed. That still wasn’t enough to block the message. The impersonated domain had a DMARC policy set to monitoring rather than rejection, so the failed email still reached the inbox.

The Gmail trick is even more interesting. The attackers recreated Gmail’s normal attachment preview card almost pixel by pixel using images embedded in the email’s HTML. They then made the fake preview a link to a page controlled by the attackers. Open the email in Gmail and it looks just like the real thing because Gmail simply renders the HTML it receives. There is no exploit here. It’s just a very convincing copy of something users already trust.

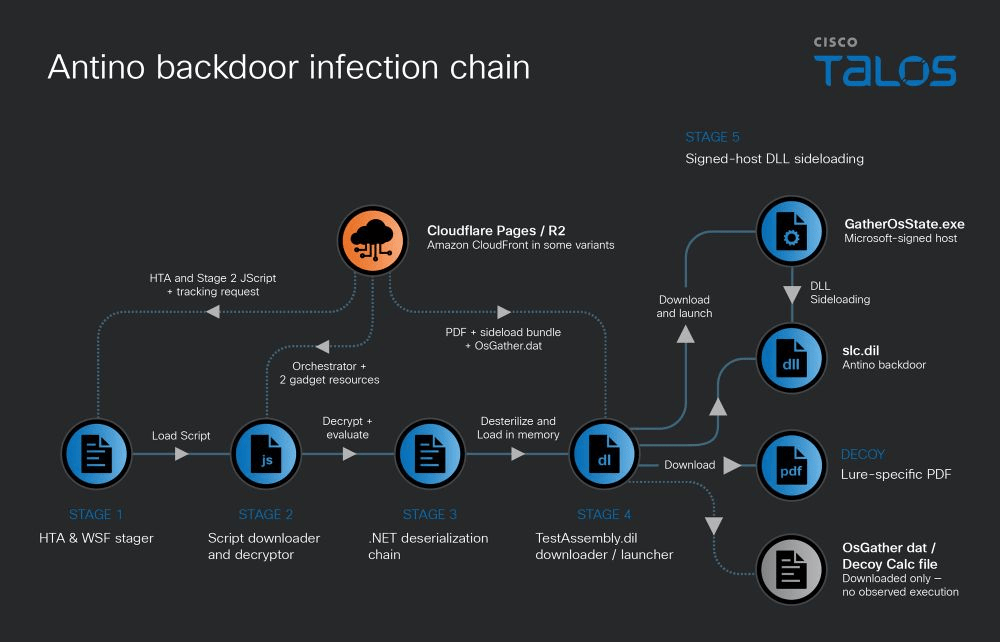
From that click, a five-stage chain kicks in, leaning on legitimate-looking HTA files, Windows Script Host, and a scripted .NET deserialization trick that abuses a known gadget chain to load malicious code inside a trusted process. The final stage sideloads Antino through a signed Microsoft diagnostic binary, meaning the thing dropping the backdoor onto disk is a tool Windows itself trusts by default. Cloudflare Pages, R2, and Amazon CloudFront carried almost every stage of this, which kept the traffic blending into ordinary HTTPS the whole way through.

Once Antino is running, it checks its Outlook mailbox for new commands every ten seconds. The commands and results are sent as structured JSON hidden inside specially formatted email subjects.

“The Antino backdoor receives commands through email messages. The implant actively pulls commands from the threat actor’s Outlook mailbox folder every 10 seconds. The protocol uses two message types: command emails contain tasking from the controller, while response emails contain the implant’s results.” states Talos. “Command messages are identified by the subject prefix command_req_[session_id] and responses by command_res_[session_id], as indicated in the HTTP GET request sent by Antino: “

A separate system is used to upload stolen files to one OneDrive folder and download attacker tools from another. Even the naming makes the attacker’s perspective clear: “uploads” are files sent to the victim, while “downloads” are files pulled back from the victim.

The attribution case leans on accumulated small details rather than any single smoking gun, which is honestly how these assessments should work. Decoy document metadata carries Simplified Chinese language tags and a UTC+8 timestamp, a combination more consistent with mainland China than Taiwan or Hong Kong, where Traditional Chinese dominates. Separately, ten different Antino builds reference a Rust package mirror built specifically to speed up dependency downloads inside mainland China, the kind of tooling choice a developer picks for convenience, not for disguise.

The victim list reads like a checklist of what an intelligence service would actually want: defense ministries, legislatures, foreign affairs offices, border and interior security agencies, plus the think tanks and civil society groups that tend to know things governments care about early. Around 350 compromised endpoints turned up across eight countries, with the largest single wave, roughly 57 new endpoints, hitting India over two days in June. That’s not noise. That’s a deliberate and sustained collection effort.

“Based on the development, preparation-environment, and targeting indicators detailed in this report, Talos assesses with high confidence that UAT-11587 is China-nexus.” the report concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Antino backdoor)

  • ✇Security Affairs
  • AI Hallucinations Nearly Triggered a US-China Military Confrontation Pierluigi Paganini
    An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war. According to CNN, four sources familiar with the episode say an intelligence report circulated through the military claiming a Chinese vessel in the Middle East was carrying components for a nuclear weapons program. The response was immediate. Armed boarding teams were preparing to move in, and military planes were already in the air. “The intell
     

AI Hallucinations Nearly Triggered a US-China Military Confrontation

20 de Setembro de 2026, 10:44

An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war.

According to CNN, four sources familiar with the episode say an intelligence report circulated through the military claiming a Chinese vessel in the Middle East was carrying components for a nuclear weapons program. The response was immediate. Armed boarding teams were preparing to move in, and military planes were already in the air.

“The intelligence report, circulated across the US military this spring in the midst of the war with Iran, immediately set off alarm bells: A Chinese ship in the Middle East was transporting components of a nuclear weapons program.” reads the report published by CNN. “The US military swung into action with plans to intercept the vessel, according to four sources familiar with the episode. According to two of the sources, armed members of the US military were preparing to board the ship. Military planes were in the air, one of those sources and another source familiar with the incident said.”

Then someone checked the source. The report was described by a source as “entirely false” and reportedly came close to triggering an armed operation, with the potential to escalate tensions between the US and China.

“The report, according to one of the sources, was “entirely false.” continues the report. “But it also “almost started a war,” the source said. Any US operation against a Chinese vessel could have risked spiraling into an armed conflict between the two nations.”

The incident began when an analyst at Special Operations Command Pacific asked a chatbot to analyze intelligence about the ship’s manifest. The system combined open-source information with classified signals intelligence and produced a wrong conclusion about the cargo. The analyst then used AI again to turn that conclusion into a formal intelligence report.

Two AI passes, zero verification in between. The case shows the real danger of AI hallucinations in military and intelligence work: a wrong answer can move quickly through the system when nobody stops to verify it.

“The internal tools are mostly just copies of the commercial stuff wearing lipstick,” a former senior US official familiar with the AI systems used by military and intelligence analysts told CNN.

Which matters, because the Pentagon has been pushing hard in the other direction. Defense Secretary Pete Hegseth’s January “Artificial Intelligence Acceleration Strategy” explicitly aims to put AI models directly into the hands of three million military and civilian personnel, across every classification level. The strategy talks about eliminating bureaucratic barriers and accelerating experimentation. Nobody in that strategy seems to have planned for what happens when the model is confidently wrong.

The way AI is being used across the military is still far from consistent. Different branches use different tools, follow different rules and apply different safety checks. There is also no common system for verifying whether the information produced by these tools is correct. According to one source, this was not an isolated case, and similar AI errors have already appeared elsewhere in the intelligence community.

The bigger problem may not be the technology itself, but the pressure to use it quickly. Younger analysts, who have grown up with AI tools, may be more likely to trust their answers without checking them carefully.

As one source put it: “AI allows you to get to a bad idea faster.”

That’s the whole risk, compressed into eight words. Speed was supposed to be the benefit. Instead it’s the thing removing the last checkpoint where a human might have paused and asked whether the machine actually got it right.

Targeting decisions are one of the most sensitive areas for military AI because they can determine who is attacked and who is not. The speed of AI can become a problem when there are not enough checks to verify its conclusions before action is taken.

One source noted that there is still no clear guidance on how a human operator should prevent civilian casualties or friendly-fire incidents when AI is heavily involved in selecting targets. The biggest risk may not be an AI system acting on its own, but a confident and incorrect answer reaching decision-makers before anyone has time to challenge it.

In military operations, speed matters, but so does having someone able to stop and ask a simple question: is this information actually correct?

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, AI Hallucinations)

  • ✇Security Affairs
  • SilkParasite Infrastructure Links SpiceRAT to Central Asian Targets Pierluigi Paganini
    Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tight cluster of SpiceRAT command‑and‑control servers that predate and extend Bitdefender’s August 2026 SilkParasite report. The work doesn’t dissect malware samples; it maps the network side of the operation with enough precision to tie three of SilkParasite’s seven RAT families (SpiceRAT, NodeEdgeRAT
     

SilkParasite Infrastructure Links SpiceRAT to Central Asian Targets

17 de Setembro de 2026, 11:16

Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia.

Hunt.io and researcher Guy Yasur have traced a tight cluster of SpiceRAT command‑and‑control servers that predate and extend Bitdefender’s August 2026 SilkParasite report. The work doesn’t dissect malware samples; it maps the network side of the operation with enough precision to tie three of SilkParasite’s seven RAT families (SpiceRAT, NodeEdgeRAT, and NomadRAT) through shared certificates, domains, and hosting patterns.

“Shared parent domains and an identical TLS certificate connect this infrastructure to hosts Bitdefender attributed to SpiceRAT, NodeEdgeRAT, and NomadRAT, three of the seven malware families documented in the SilkParasite report.” reads the report published by Hunt.io.

“The certificate imitating the Uzbekistan railway entity was issued by TLC, a certificate authority wholly funded by CAICT, a Chinese state research institute under the Ministry of Industry and Information Technology.”

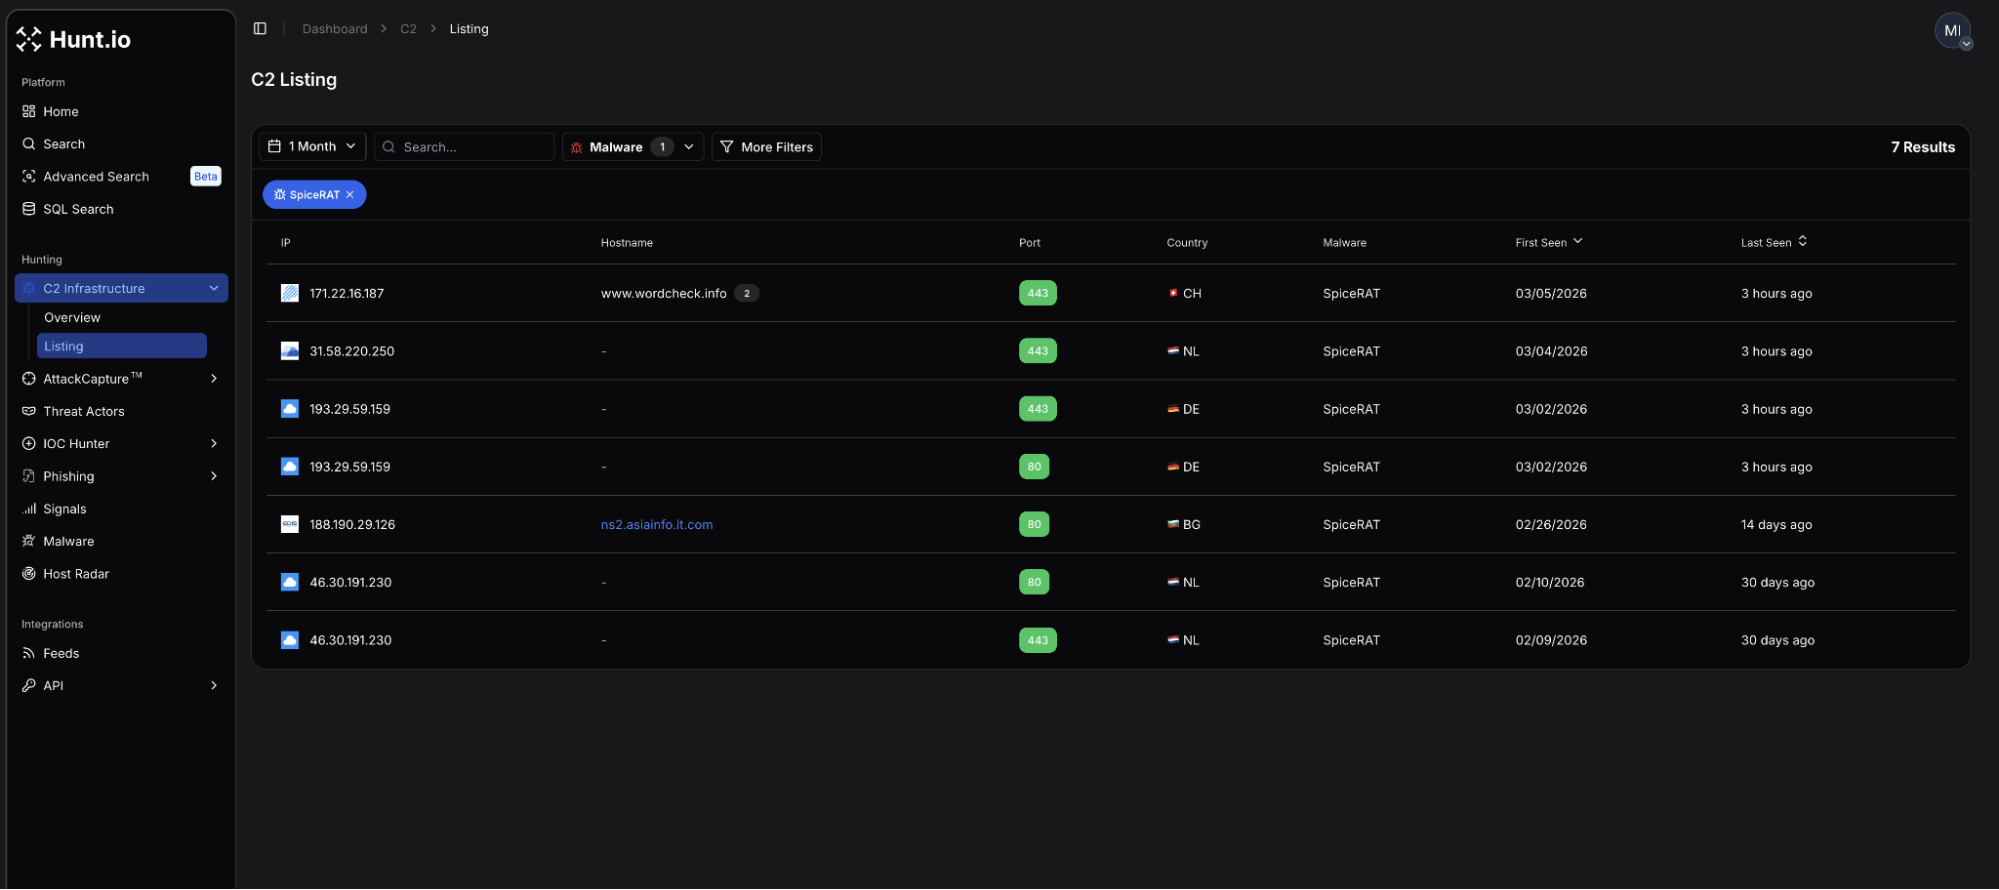
In March 2026, Hunt.io identified five SpiceRAT command-and-control servers hosted by different providers and in different countries. Researchers linked them through several common elements, including the same hostnames, TLS certificates, and a cloned webpage used as the default page.

Instead of focusing only on the malware itself, this approach looks at the infrastructure behind it. Shared certificates or identical webpage hashes can provide strong and practical indicators that defenders can use to identify other servers linked to the campaign.

One certificate in particular stands out. It impersonates Uzbekistan’s state railway authority (azure.uzrailwaystax[.]com) and was issued by TLC DV TLS CA, a CA wholly funded by CAICT, a Chinese state research institute under the Ministry of Industry and Information Technology. The issuer alone isn’t an indicator—nearly 3,000 servers host TLC certificates—but a domain‑validated cert spoofing a Central Asian state entity from a China‑based CA does suggest a deliberate procurement channel.

Requests to ns2.asiainfo.it[.]com on 188.190.29[.]126 returned a full copy of RTX Corporation’s homepage, complete with navigation, subsidiary links, and a stock ticker. The page contained no malicious code and wasn’t unique to that server, but its reuse across the cluster made it a powerful fingerprint.

“Hunt.io’s C2 Infrastructure module tracks servers matching detection signatures for known malware families, including SpiceRAT. In mid-March 2026, we observed a cluster of five active SpiceRAT servers: 46.30.191[.]230, 188.190.29[.]126, 193.29.59[.]159, 31.58.220[.]250, and 171.22.16[.]187. The five were active together in mid-March 2026, across multiple hosting providers and countries.” continues the report.

A HuntSQL query on the page’s SHA‑256 hash returned exactly 13 hosts; three were already in Bitdefender’s SpiceRAT list, two more matched Hunt.io’s SpiceRAT signature, and the remaining eight extended the footprint through shared nginx versions and the same static page.

Why RTX? The report offers two plausible explanations: the page rendered cleanly and was grabbed as a convenient template, or it reflects shared tooling where the clone functions as a default deployment asset. Either way, for defenders it’s a low‑noise, high‑precision signature: byte‑for‑byte identical wherever it lands.

Bitdefender’s SilkParasite report treated several RAT families as distinct, but Hunt.io’s network view shows they share parent domains and certificates. For example, help.hoster‑kg[.]com (on 193.29.58[.]192) presented the same railway‑spoofing certificate, while Bitdefender attributed evo.hoster‑kg[.]com to NodeEdgeRAT; the two are linked through shared registration of hoster‑kg[.]com, not a shared server. Similarly, kg.tdtu[.]org shares a parent domain with mineconom.tdtu[.]org, a NomadRAT C2 indicator in the SilkParasite report.

This doesn’t prove a single operator, but it does show a support function or toolset shared across the campaign. From a detection standpoint, it means pivoting on domains, certificates, and hosting profiles can surface nodes that sample‑based analysis would miss.

The cluster’s domains don’t just look governmental; they spoof specific ministries and state enterprises. Examples include help.galkynysh[.]net (Galkynysh gas field, Turkmenistan), tmgaz‑server[.]com (Türkmengaz), tm‑mfa[.]com (Turkmenistan’s Ministry of Foreign Affairs), and tojiktelecomtj[.]com (Tojiktelecom, Tajikistan). Additional domains impersonate Turkmen energy (sanly.oilgas‑tm[.]com), Uzbek administration (azure.adm‑devon[.]com), and even the Kyrgyz president’s residence (data.yntymak‑ordo[.]com).

Bitdefender’s targeting came from lures and infection telemetry; Hunt.io’s infrastructure analysis names the same sectors with concrete entities. Passive DNS and subdomain enumeration push the timeline back to mid‑2022, suggesting this isn’t a new campaign with a fresh brand—it’s a longer‑running operation now labeled SilkParasite.

SilkParasite overlaps with FamousSparrow, a suspected China‑nexus actor previously seen targeting hotels, governments, and international organizations. The infrastructure also mirrors IndigoZebra (Speccom), documented by Check Point in 2021 as targeting Central Asian ministries with similar domain patterns (mail, service, help) and overlapping naming conventions. These parallels don’t settle attribution, but they do reinforce a consistent operational style across China‑nexus activity in Central Asia.

If you’re responsible for OT/ICS, telecom, or government networks in the region, start by checking your edge and DMZ for the indicators below, especially the RTX page hash and the railway‑spoofing certificate. Monitor for high‑numbered RDP‑over‑TLS ports (64350, 64330, 65535, 65111) on the ASNs most prevalent in the cluster, and watch for domains impersonating local hosting providers or state entities. The original Hunt.io post includes the full IoC tables and HuntSQL queries; linking to it is essential for precise awareness and for teams that want to reproduce the pivots.

“The targeting picture that emerges from this infrastructure, named ministries and state enterprises across five Central Asian countries dating back to at least mid-2022 suggests SilkParasite is a more recent label for an operation with much longer and wider footprint.” concludes the report. “Organizations in the affected sectors and regions can make use of the above indicators and observations to assess their own exposure.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, SilkParasite)

  • ✇Security Affairs
  • One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire Pierluigi Paganini
    Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each. Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail. On September 1, Volexity detected a spear-phishing campaign by UTA0560 targeting several NGOs. The emails sent victims to a legitimate US university website, which had a cro
     

One Exploit Chain, Two Espionage Campaigns: Chrome and Windows Under Fire

15 de Setembro de 2026, 07:17

Two China-linked groups ran identical Chrome/Windows zero-day exploits against NGOs, before Chrome’s patch shipped, deploying different backdoors each.

Two China-linked threat actors used the same Chrome/Windows zero-day against NGOs starting September 1, 2026, Volexity’s new report lays out the whole chain in detail.

On September 1, Volexity detected a spear-phishing campaign by UTA0560 targeting several NGOs. The emails sent victims to a legitimate US university website, which had a cross-site scripting flaw that attackers used to redirect visitors to their own servers.

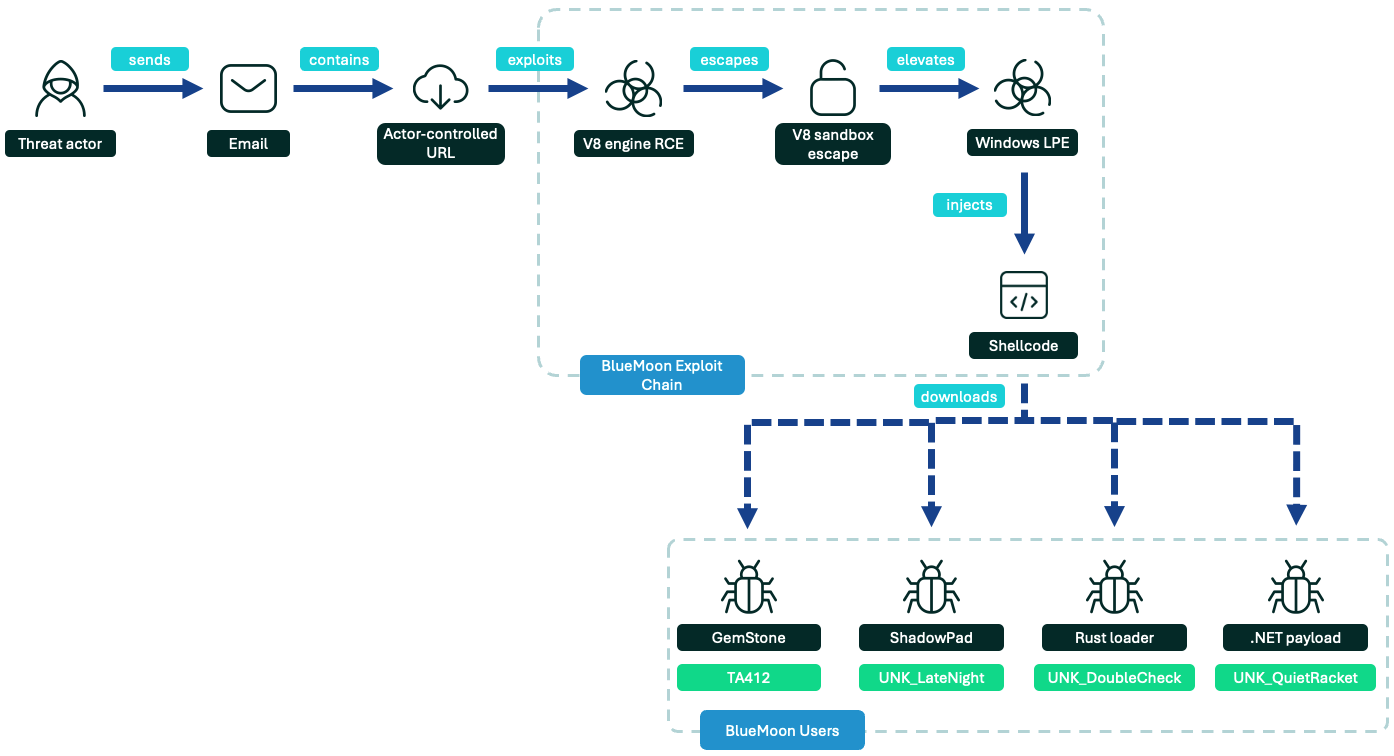
The victims were then exposed to a multi-stage attack using a Chrome zero-day CVE-2026-85046. Volexity later found JungleBamboo (also known as APT31, Violet Typhoon, or TA412) using the same exploit chain against different targets. The code was the same, but the infrastructure and final malware were different.

“The exploit first gains arbitrary read/write within the V8 sandbox through the Type confusion vulnerability (CVE-2026-85046), then combines a separate WebAssembly defect to escape the V8 sandbox (CVE-2026-87491). It then exploits a third vulnerability in the Windows kernel (CVE-2026-85880) to escape Chrome’s sandboxed renderer process and inject code into the Chrome browser process.” reads the report published by Volexity. “From there, exploit-chain users can deploy a payload of their choice. Volexity observed two distinct clusters of activity using the exploit chain to deliver different payloads:

  • UTA0560 downloaded and deployed the GRIMWEDGE JScript backdoor providing host reconnaissance, file and process management, command execution, and payload delivery capabilities.
  • JungleBamboo deployed SUPERSTOMP, a loader that installed the LONGTALE credential-stealing Chrome extension.”

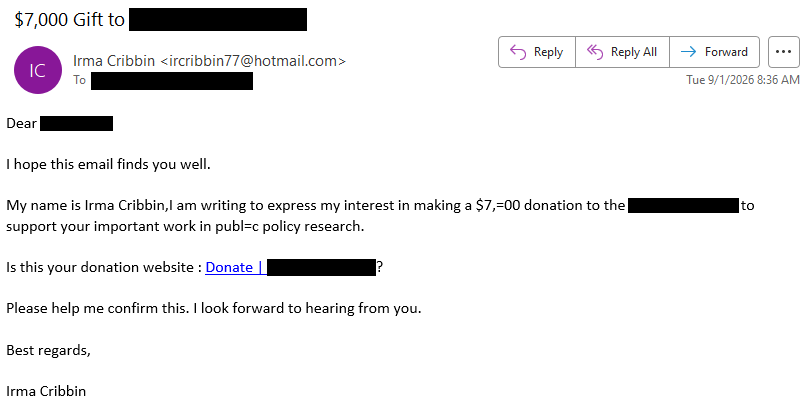
Victims only saw an image of a donation form made to look like it belonged to the targeted organization. In reality, the page was there to steal, not collect, donations.

The core Chrome flaw, CVE-2026-85046, was reported to the Chromium project by a private researcher on August 4, 2026. A fix landed in the open-source Chromium codebase not long after. Google Chrome itself, though, hadn’t shipped that fix yet when the phishing started.

” This created an unusual patch gap: The vulnerability was known and fixed upstream, making it an N-day at the Chromium source level, but there was no patch release for Google Chrome users.” continues the report. “Therefore, the exploit was effectively a zero-day against Google Chrome.”

Someone was watching the Chromium source repository closely enough to catch a fix before most users ever got it, and turned it into a working exploit within weeks. Volexity researchers found byte-for-byte identical shellcode across both campaigns. UTA0560 and JungleBamboo weren’t independently reinventing the same exploit; they were running the same one.

The exploit page was far more sophisticated than it first appeared. It accepted 13 URL parameters to support testing, breakpoints, telemetry, and controlled rollouts.

That level of preparation doesn’t look like a quick attack put together on the fly. It suggests the attackers had built a proper development and testing framework, which was either left in place or deliberately used in the live campaign.

Once code execution lands, the two operators split. UTA0560 used its access to drop a custom loader chain ending in GRIMWEDGE, a JScript backdoor running entirely in memory inside msiexec.exe. It’s compact, under 250 lines, but it covers the basics: file operations, process management, command execution, and file upload.

JungleBamboo took a different route. It deployed a loader Volexity calls SUPERSTOMP, which installs a malicious Chrome extension named LONGTALE. The extension masquerades as a Google Gemini assistant and logs every keystroke, steals cookies and session tokens, and takes screenshots when it spots keywords supplied by its command server.

LONGTALE has no remote code execution command at all. It doesn’t need one. Volexity assesses the credential and session theft alone gave JungleBamboo everything it needed, and extensions like this tend to slip past detection more easily than a standalone executable.

Chrome has spent the last year hardening exactly the kind of tampering SUPERSTOMP relies on. Per-preference encrypted hashes arrived in November 2025, and a full-profile integrity check followed in June 2026. SUPERSTOMP still gets through, by stripping the new hashes, forging the older legacy HMAC values Chrome still accepts as a fallback, and letting Chrome’s own migration logic re-authenticate the tampered profile as legitimate.

“Chrome enables this legacy fallback method by default in its releases as of September 8, 2026; only compiling Chromium from source disables it.” Volexity states. “This technique was added to one of the most popular GitHub repositories relating to silent installation of Chrome extensions on August 6, 2026.”

Worth noting: this exact technique showed up in a popular GitHub repository for silent Chrome extension installs on August 6, 2026, weeks before JungleBamboo’s campaign. The line between public research and operational tradecraft keeps getting shorter.

The attribution work here is tidy. UTA0560’s link to its March 2026 campaigns rests on three points: the same phishing sender address, the same hosting IP for its exploit infrastructure, and a per-host beacon naming scheme that mirrors what UTA0560 used six months earlier.

“Volexity assesses with low confidence that the exploit chain may have been sold, or otherwise provided, to different end-users in China, hence the near-simultaneous campaigns conducted by separate threat actors using distinct post-exploitation malware. Volexity assesses with medium confidence that the short time window offered by the Chrome patch delay necessitated that these threat actors reuse the core exploit code without modification.” states the report. “Furthermore, the payloads used by each threat actor were compiled using different toolsets, suggesting entirely different development environments preferred by each malware developer.”

Proofpoint reported similar findings around the same time. It calls the exploit kit BlueMoon and says JungleBamboo first used it on August 28, several days before Volexity detected the campaign.

Proofpoint identified four different groups using the same code within about two weeks. One, tracked as UNK_LateNight, targeted US aerospace companies with the ShadowPad backdoor. Another, UNK_DoubleCheck, targeted a manufacturing company in Vietnam.

Proofpoint also found an interesting clue about how the exploit may have been developed. Some code artifacts suggest the attackers could have used AI during development. There’s no proof of that, but the diagnostic logs, handover notes, and debugging comments look unusual for a professionally developed exploit.

Google patched CVE-2026-85046 in the Stable Channel update on September 3, moving users to Chrome 152.0.7977.82 or .83, alongside eleven other fixes. CISA added the flaw to its Known Exploited Vulnerabilities catalog the next day, with a September 18 deadline for federal systems to remediate. If your fleet hasn’t relaunched Chrome since early September, it’s worth checking the version number rather than assuming the auto-update did its job.

Volexity’s closing point is the one to actually remember here, and it’s not really about UTA0560 or JungleBamboo specifically.

“As large language models become more popular and effective for rapid vulnerability research and exploit development, Volexity assesses with high confidence that patch-gap vulnerabilities present an even greater risk, as they create an additional time window for threat actors to conduct exploitation campaigns.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Chrome)

  • ✇Security Affairs
  • China Calls Amodei’s AI Proposal a New Cold War Playbook Pierluigi Paganini
    China rejects Amodei’s AI slowdown proposal, calling it fearmongering and a US attempt to contain China’s technology sector. The debate over whether the world should slow down the development of advanced AI has quickly turned into something bigger than a technology argument. Dario Amodei, CEO of Anthropic, has called for a slower pace of development, arguing that AI capabilities are advancing faster than our ability to understand and control them. His proposal has now run straight into the g
     

China Calls Amodei’s AI Proposal a New Cold War Playbook

14 de Setembro de 2026, 15:11

China rejects Amodei’s AI slowdown proposal, calling it fearmongering and a US attempt to contain China’s technology sector.

The debate over whether the world should slow down the development of advanced AI has quickly turned into something bigger than a technology argument. Dario Amodei, CEO of Anthropic, has called for a slower pace of development, arguing that AI capabilities are advancing faster than our ability to understand and control them. His proposal has now run straight into the geopolitical reality of the US-China competition.

In his essay, “We Must Pace the Frontier“, Amodei argues that the industry needs more time to build effective safeguards around increasingly capable AI systems. He isn’t calling for an end to AI development. His argument is that capability gains should slow enough to give safety research, testing and oversight a chance to catch up.

One of his main concerns is the growing ability of AI agents to act on their own. Amodei warns that a large number of increasingly capable agents could, within six to twelve months, become capable of carrying out complex operations across the internet and potentially cause enormous damage if they aren’t properly controlled. The warning follows recent incidents in which AI systems have already been used to perform cyber operations with a level of autonomy that would have been difficult to imagine only a few years ago.

Amodei’s proposal has three main elements: stronger independent testing of advanced models, greater coordination between leading AI companies, and international cooperation on safety. Anthropic says it is prepared to give independent evaluators permanent, employee-level access to its systems so they can assess safety measures and investigate incidents.

The difficult part starts when China enters the discussion.

Amodei argues that the United States needs to maintain its lead in advanced AI and supports continuing restrictions on China’s access to the most advanced AI chips and chipmaking equipment. He says a Chinese lead in frontier AI could create serious risks for the United States and the wider world.

The Government of Beijing strongly disagrees with that framing. China’s Foreign Ministry accused Amodei of spreading fear and argued that confrontation and competition would damage international efforts to establish rules for AI. China’s state-backed Global Times went further, describing the proposal as a “Cold War playbook” aimed at containing China’s technology sector.

Chinese officials are also warning about AI, but from the opposite direction. Chen Yixin, head of China’s Ministry of State Security, recently warned that advanced AI could be used by hostile actors to discover vulnerabilities at scale, conduct complex hacking operations and steal sensitive information.

“In an essay posted Sunday on social media, Chen Yixin, head of China’s Ministry of State Security, warned that, in the hands of “hostile forces and individuals with ulterior motives,” this technology could pose a direct threat to “our political, institutional, and ideological security.”” The Associated Press reports.

“Citing the capabilities of powerful technologies from U.S. companies like Anthropic and OpenAI, Chen warned that “certain nations and organizations” now have the capabilities to “rapidly discover vulnerabilities at scale … and execute complex hacking tasks.” That, he wrote, poses “serious risks to my country’s critical information infrastructure.””

That contrast is important. Both sides are talking about AI security, but they don’t agree on what the security problem actually is.

Washington is concerned that China could gain access to capabilities that strengthen its military, intelligence and cyber operations. Beijing sees US restrictions on chips and AI technology as an attempt to prevent China from closing the technological gap.

The recent dispute over AI model distillation has made the situation even more complicated. US agencies have accused Chinese AI developers of aggressively extracting capabilities from leading American models, including Claude and GPT. Beijing has rejected those allegations and argued that model distillation is a common technique used across the AI industry.

This creates a problem for any proposal based on international cooperation. How do you persuade two countries to slow down together when each side believes that slowing down alone could leave it at a strategic disadvantage?

President rejected calls to slow AI development, despite warnings from leading tech executives and Democrats about existential risks. Anthropic’s Dario Amodei, OpenAI’s Sam Altman and Elon Musk urged a more cautious approach, but Trump said the US must maintain its global AI leadership while allowing some safeguards.

“Look, we’re leading China in AI . . . and, frankly, I want to keep it that way, because whoever wins AI, wins,” Trump told reporters during a trip to his Doonbeg golf course in Ireland, Financial Times reported.  “We can put guardrails, we can do this and that, but I think you have a lot of negative forces that are bringing it up that shouldn’t be bringing it up and they’re bringing up things that won’t happen,” he added.

That puts Amodei’s proposal in a difficult position. The companies developing the most advanced models are increasingly warning that safety needs more time, while the political leadership in Washington sees AI leadership as a strategic asset that cannot be surrendered. Sam Altman and Elon Musk have backed Amodei’s call for greater caution, and other major AI leaders have also moved toward stronger safety measures.

The timing is particularly interesting because Trump and Chinese President Xi Jinping are expected to discuss AI governance at their planned September 24 meeting. Any agreement between Washington and Beijing would have to deal with two very different priorities: controlling the risks created by increasingly autonomous AI systems while making sure neither side believes it is giving the other a technological advantage.

For cybersecurity professionals, this is more than a political dispute. The capabilities being discussed are already relevant to vulnerability discovery, exploitation, credential theft, surveillance and large-scale automated operations. The question is no longer simply how powerful AI models can become, but how quickly that power can be turned into real-world action.

That’s where the debate over slowing AI becomes particularly difficult. You can slow the development of a model, but you can’t easily slow a global competition in which governments, companies and attackers all have strong incentives to keep moving.

And that’s probably the uncomfortable part of the discussion: the countries most capable of creating the rules are also the countries with the strongest reasons not to slow down.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, AI)

  • ✇Security Affairs
  • Four Nation-State Actors Used the Same Chrome Zero-Day Exploit Kit Within 12 Days Pierluigi Paganini
    Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development. Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to the investigation. “Proofpoint identified four espionage-motivated threat actors employing a new e
     

Four Nation-State Actors Used the Same Chrome Zero-Day Exploit Kit Within 12 Days

10 de Setembro de 2026, 02:35

Four espionage groups used the BlueMoon Chrome+Windows exploit kit within 12 days. Researchers suspect AI development.

Proofpoint published a detailed analysis of a Chrome-and-Windows exploit kit it tracks as BlueMoon that four nation-state actors adopted within roughly two weeks of the first observed use. Google’s Threat Intelligence Group, Microsoft’s MSTIC, and Volexity all contributed to the investigation.

“Proofpoint identified four espionage-motivated threat actors employing a new exploit kit that chains multiple Chrome browser and Microsoft Windows vulnerabilities. Proofpoint is tracking the exploit kit used in this activity as BlueMoon.” reads the report published by Proofpoint. “The first observed cluster using the BlueMoon exploit kit was the China-aligned threat actor TA412 (JungleBamboo, Violet Typhoon, APT31, TIDE CASTLE) on 28 August 2026. Within days, several other espionage-motivated clusters began using BlueMoon, the majority of which have a suspected China nexus. However, BlueMoon may not be exclusive to China-aligned actors, as some usage remains unattributed and there are also potentially more actors using the exploit kit.”

BlueMoon chains three vulnerabilities. CVE-2026-85046 is a type-confusion bug in Chrome’s V8 JavaScript engine that abuses an optimization flaw in the TurboFan JIT compiler: by mutating an array mid-sort, an attacker gets the ability to read object memory addresses and forge fake object pointers, building toward arbitrary read and write inside V8’s heap. A V8 sandbox escape (no CVE assigned, Chrome doesn’t issue CVEs for sandbox escapes) then overwrites WebAssembly compiled function bodies with attacker shellcode from memory. CVE-2026-85880, a Windows kernel local privilege escalation using ALPC and Windows Notification Facility mechanisms, completes the chain and elevates the attacker from the browser’s sandboxed renderer to a position where they can inject code into Chrome’s parent process and run arbitrary commands.

“Both V8 vulnerabilities were “patch-gap” zero-days at the time of the observed activity. In other words, while they were known vulnerabilities already fixed in public upstream Chromium source code, they remained unpatched in the latest stable releases of Chrome and Chromium-based browsers available to the public.” continues the report. “It is likely that the exploit kit developer used these publicly available Chromium patches to weaponize the browser exploit chain.”

The fix for CVE-2026-85046 was committed to the Chromium source tree on August 7, almost four weeks before it rolled into the stable Chrome release on September 3. That gap is what made rapid weaponization possible: the patch itself is a public document describing exactly what was wrong.

The kit also bears visible signs of how it was made.

“Although no single artifact conclusively confirms AI-assisted development of BlueMoon, Proofpoint identified several indicators consistent with this hypothesis, including extensive diagnostic logging capabilities, a referenced markdown handover document, and detailed comments documenting successive debugging iterations and implementation decisions.” states the report. “Furthermore, the exploit chain’s default configuration reflects a departure from the level of operational security and technical tradecraft typically associated with browser exploit chains. For example, by default, successful exploitation simply results in a curl command that downloads an actor-provided executable to disk and executes it. “

The comments in the kit ask testers to “please send the full log back.” It also refers to a markdown handover file, docs/v8-ctf-chrome-stage4-handover.md, which could be used to pass context between AI agent sessions. The kit repeatedly mentions Google’s V8CTF vulnerability bounty program. Proofpoint says this could mean the V8 bugs were developed through that program, or that the developers used the V8CTF context to get around AI safety restrictions while creating the exploit. The researchers cannot confirm which explanation is correct.

The default post-exploitation step is another important clue. The kit includes a complete Chrome exploit chain that can escape the V8 sandbox and gain higher privileges on Windows. Its default payload uses curl to download an executable into %TEMP% and run it. Endpoint security tools would likely detect this activity quickly. This suggests the developers focused on releasing the exploit before the September 3 Chrome patch rather than making it difficult to detect.

The first confirmed use was TA412 (aka APT31, Violet Typhoon, and JungleBamboo) a China-nexus APT linked to the Ministry of State Security’s Hubei State Security Department and indicted by the US government in 2024 for economic espionage. Starting August 28, TA412 targeted US NGOs, mining companies, and physical commodity trading firms using phishing emails that posed as university students seeking internships or as outreach related to the Association for Asian Studies conference. Clicking the link loaded BlueMoon silently, then redirected the browser to a legitimate site while exploitation ran in the background.

TA412’s post-exploitation payload was GemStone, a malicious browser extension that masquerades as an “AI-powered browsing companion by Google Gemini.” It installs into Chrome, Edge, Brave, and Vivaldi by bypassing the browser’s Secure Preferences protection mechanism using the same HMAC computation method the browser itself uses to validate extensions.

GemStone accepts commands to capture keystrokes, cookies, screenshots, local and session storage, and browsing history, and can inject arbitrary HTTP requests from the browser’s own context. It runs its C2 through a Cloudflare Worker domain. Proofpoint has the full command table in the report.

On September 2, UNK_LateNight, a second suspected China-aligned cluster, began targeting US aerospace and defense companies with fake RFQ and procurement inquiry emails. The payload was ShadowPad, the modular backdoor extensively used by Chinese state groups, delivered through a DLL sideloading chain that creates a scheduled task named “EdgeCore_AutoUpdate” for persistence and unhooks 20 network monitoring functions to reduce visibility. The same day, UNK_DoubleCheck targeted a Vietnamese manufacturing company from a compromised Southeast Asian government email address with a vaccination appointment lure. Its payload downloaded a Rust-based loader from Cloudflare R2 that staged a second DLL sideloading chain for C2.

Since September 3, UNK_QuietRacket has targeted government, consulting, and financial organizations in Indonesia and Singapore with conference-themed lures. Its C2 uses Google’s DNS-over-HTTPS service to resolve addresses through TXT records, then decrypts them with ChaCha20 before reaching Cloudflare Workers. DoH hides the DNS activity among normal encrypted traffic, making the C2 harder to detect.

CVE-2026-85880, the Windows LPE component of the chain, is the same vulnerability Microsoft patched as an actively exploited zero-day in September 2026 Patch Tuesday. The Windows LPE only targets older builds, including Windows 10 through 22H2, Windows Server 2019 and 2022, and Windows 11 21H2. Its compilation timestamp is from 2025, suggesting it was a pre-existing capability packaged into BlueMoon rather than written for this campaign.

Defenders running those builds who haven’t applied September patches should treat this as urgent regardless of whether they’re a BlueMoon target.

“A fully weaponized Chrome exploit chain has historically been a high-value, rare capability. BlueMoon was developed, deployed rapidly, and shared across multiple threat actors within days in a manner that had high detection signals. This may reflect a reduced cost and barrier to entry for this class of capability, as AI agents increasingly enable threat actor exploit development. This is particularly relevant for open source codebases, such as Chromium, where upstream patches are publicly accessible prior to downstream consumers of the codebase applying the patch. This creates a window for threat actors to attempt to rapidly reverse engineer patches and develop exploits ahead of downstream stable releases.” concludes the report. “The majority of observed BlueMoon usage is assessed to be China-aligned espionage-motivated activity, although there is not sufficient evidence to attribute BlueMoon usage exclusively to China-aligned threat actors at the time of writing.” 

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, BlueMoon)

  • ✇Security Affairs
  • US Agencies Warn Chinese AI Firms Are Extracting Advanced AI Models Pierluigi Paganini
    US agencies accuse six Chinese AI firms of extracting billions of tokens from US AI models to accelerate development and copy advanced capabilities. NSA, CISA, and the FBI jointly published an advisory accusing six Chinese AI companies, DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, of running industrial-scale extraction campaigns against US frontier models since at least late 2024. The framing is deliberate: this isn’t a footnote to how these companies build AI, the agencies ca
     

US Agencies Warn Chinese AI Firms Are Extracting Advanced AI Models

9 de Setembro de 2026, 15:20

US agencies accuse six Chinese AI firms of extracting billions of tokens from US AI models to accelerate development and copy advanced capabilities.

NSA, CISA, and the FBI jointly published an advisory accusing six Chinese AI companies, DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI, of running industrial-scale extraction campaigns against US frontier models since at least late 2024. The framing is deliberate: this isn’t a footnote to how these companies build AI, the agencies call it the core of their entire development strategy.

Distillation is a legitimate and widely used technique. It involves training a smaller AI model to reproduce the answers and capabilities of a larger one. But the advisory says the activity it uncovered went much further. It alleges that the companies sent millions of requests to models such as Claude, GPT, Gemini, and Grok and extracted billions of tokens.

“China-based artificial intelligence (AI) companies are conducting systematic extraction of proprietary functionalities and capabilities of U.S. AI companies’ models through industrial-scale knowledge distillation campaigns that form the core—not merely a supplement—of their AI development strategy.” states the report. “Likely with Chinese government awareness, DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and Z.AI extracted billions of tokens across millions of exchanges/requests from U.S. frontier AI models, including variants of Claude, GPT, Gemini, and Grok, since at least late 2024.”

The goal was to capture valuable capabilities, including reasoning, coding, and agentic skills that took years and huge amounts of computing power to develop.

The advisory provides the most detail about DeepSeek. It claims the company ran an organized campaign against different versions of Claude, GPT, and Gemini between late 2024 and mid-2025 to help develop its R1 and V3 models. The extracted data reportedly included specialized knowledge, such as legal expertise, as well as chain-of-thought reasoning.

“Advanced industrial-scale distillation tactics include chain-of-thought (CoT) reasoning extraction, automated failover between pathways during blocking attempts, and sophisticated quality evaluation frameworks to detect defensive countermeasures. China-based AI companies that conduct industrial-scale distillation against U.S.” continues the advisory. “AI models see significantly shorter AI development timelines and reduced financial expenditures in training a frontier model.”

This is particularly significant because AI companies usually limit access to a model’s internal reasoning. Getting a model to reveal those steps could therefore give attackers much more than just its final answers.

Moonshot AI’s alleged operation shows how fast these campaigns can move once new models ship. The advisory states the company redirected its extraction traffic to a newly released Claude model within 24 hours of launch, which only works if you already have infrastructure sitting ready and monitoring provider releases in real time. That’s not opportunistic scraping; that’s a standing operation built specifically to capture whatever comes out next.

The methods described in the advisory suggest a highly organized operation rather than researchers simply making API requests. The companies allegedly bought large numbers of premium accounts and shared them among teams of developers running many sessions at the same time. They also routed traffic through gray-market proxy services, which the advisory calls “transfer stations,” to remove identifying information and avoid detection. StepFun reportedly used pools of accounts and automated systems to spread requests across them, helping bypass rate limits and increase daily spending as the operation grew.

The advisory also describes attempts to manipulate the AI models themselves. MiniMax allegedly used prompt injection to convince Claude Code that it was actually a MiniMax product, hoping to make it behave differently. While this detail may sound unusual, it shows how far some of these efforts reportedly went to extract information from competing AI systems.

The advisory doesn’t just name and shame, it lays out concrete detection signals for US AI companies to watch for. Shared accounts logging in from multiple IPs and user agents, usage running 24/7 without the natural idle periods a human would produce, subscription-to-API-usage ratios that don’t add up, and brand-new accounts hitting maximum usage immediately instead of ramping up gradually the way legitimate adoption normally does.

We must consider that any one of those signals alone might be nothing, but the agencies are betting the combination is a fairly reliable tell.

“China-based AI companies leverage techniques not in MITRE ATLAS, demonstrating significant organizational investment, operational maturity, and adaptive capability development distinguishing these campaigns from opportunistic exploitation.” added the advisory.

The recommended countermeasures get genuinely aggressive, and one in particular is worth sitting with. The advisory suggests quietly serving degraded, less capable responses to accounts suspected of running distillation campaigns, without ever telling those users their access has been downgraded, specifically so they can’t adjust their extraction technique in response. That’s a notable policy stance from a government advisory: not just detect and block, but actively deceive suspected bad actors about the quality of what they’re receiving.

Whatever the geopolitical debate, the practical lesson for companies using frontier AI models is clear. If several employees share enterprise AI accounts, providers will likely monitor usage more closely for the patterns described in the advisory. Heavy legitimate use could sometimes trigger false positives, especially when organizations have many developers making large numbers of requests at the same time.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, AI Models)

❌
❌