❌

Visualização normal

Hoje — 9 de Novembro de 2026Security Affairs
  • ✇Security Affairs
  • CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers Pierluigi Paganini
    US agencies warn attackers are going after industrial refrigeration controllers. The fixes are basic, and most start with getting them off the internet. CISA, the FBI, HHS, USDA and the Department of Transportation published a joint advisory on attacks against industrial refrigeration controllers and cold chain monitoring systems. The activity is global. Healthcare, chemical, food and transport companies use these systems to watch temperatures, keep logs, run defrost cycles and save energy,
     

CISA and the FBI Warn Of Attacks against Industrial Refrigeration Controllers

9 de Novembro de 2026, 08:57

US agencies warn attackers are going after industrial refrigeration controllers. The fixes are basic, and most start with getting them off the internet.

CISA, the FBI, HHS, USDA and the Department of Transportation published a joint advisory on attacks against industrial refrigeration controllers and cold chain monitoring systems. The activity is global. Healthcare, chemical, food and transport companies use these systems to watch temperatures, keep logs, run defrost cycles and save energy, including in refrigerated trucks.

“The authoring organizations are aware of malicious cyber actors targeting electronic temperature controllers and commercial refrigeration controllers in retail grocery and cold storage facilities.” reads the advisory published by CISA. “The actors may exploit vulnerabilities or weaknesses in unpatched or internet-accessible controllers to remotely alter settings and force units into continuous heating and defrost cycles, which can cause widespread inventory loss and equipment hazards.”

The targets are electronic temperature controllers and commercial refrigeration controllers used in grocery stores and cold-storage sites. Attackers may exploit flaws in unpatched or internet-accessible controllers to change settings remotely and force units into continuous heating and defrost cycles. In plain terms, someone could cook your freezer from the other side of the world.

The agencies identify three ways in: bypassing authentication, injecting arbitrary code, and exploiting weak configurations. Once inside, an attacker can change temperatures, which can shorten equipment life, create a fire hazard and destroy stock. Spoiled products that reach consumers can also create a safety risk.

“The actors may exploit vulnerabilities or weaknesses in unpatched or internet-accessible controllers to remotely alter settings and force units into continuous heating and defrost cycles, which can cause widespread inventory loss and equipment hazards.” continues the adviosry.

An attacker can also hide the damage. Operators lose sight of current temperatures, and that’s a bad moment to learn a cold room has been warm for hours.

CISA’s Chris Butera adds that every organization that depends on these systems should assume it’s a target. The advice follows the Cross-Sector Cybersecurity Performance Goals from CISA and NIST, a minimum set of practices for any organization.

Start with exposure. Keep controller panels off the internet, and if you need remote access, put an up-to-date firewall or similar gateway in front of it. Then separate industrial equipment from the office network with its own virtual network.

Next, fix the basics. Change default passwords, use strong ones, and add phishing-resistant multifactor authentication where you can. Update firmware, and retire or replace devices the maker no longer supports.

Allow only trusted devices and IP addresses to change system settings. Keep tested backups in a separate location, disconnected from the network. Enable logging and regularly check the logs. If devices do not record activity, monitor the network traffic between them.

U.S. organizations should report suspicious activity to CISA’s 24/7 operations center or the FBI’s Internet Crime Complaint Center. Healthcare organizations can also contact HHS.

Reports should include the date, time and location of the incident, a description of the activity, the number of people affected, the equipment involved, and a contact person within the organization.

One control gets forgotten more than the rest. A controller shouldn’t be able to push a freezer past what’s safe, whoever is giving the orders.

“The authoring organizations strongly urge industrial refrigeration and cold chain monitoring system owners and operators to secure remote access to their OT systems.” concludes the report. “To strengthen system security, owners and operators should review the following resources and implement recommended mitigations:

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Security Affairs
  • Fake GitHub Security Tools Infect Over 2,000 PCs With Malware Pierluigi Paganini
    Fake GitHub security tools are spreading malware that disables defenses, steals sensitive data and infects over 2,000 PCs. Cybersecurity firm Doctor Web has found malware hidden in GitHub projects that look like security tools. The campaign targets blockchain game fans and, more recently, information security professionals. The researchers discovered that more than 2,000 PCs were infected. “The attackers behind these compromised development projects target blockchain game enthusiasts and
     

Fake GitHub Security Tools Infect Over 2,000 PCs With Malware

9 de Novembro de 2026, 05:07

Fake GitHub security tools are spreading malware that disables defenses, steals sensitive data and infects over 2,000 PCs.

Cybersecurity firm Doctor Web has found malware hidden in GitHub projects that look like security tools. The campaign targets blockchain game fans and, more recently, information security professionals. The researchers discovered that more than 2,000 PCs were infected.

“The attackers behind these compromised development projects target blockchain game enthusiasts and (most intriguingly) …information security professionals.” reads the report. “At the time of Doctor Web’s research into this matter, more than 2,000 PCs were infected.”

The campaign started two years ago with Visual Studio projects related to blockchain games, game bots and cheats. The attackers targeted people who used crypto wallets. They hid malicious code in project files, including commands that ran before a project was built and PowerShell commands stored in configuration files. They even provided instructions on how to install Visual Studio and download the projects from GitHub, making it easy for people with limited technical knowledge to use them.

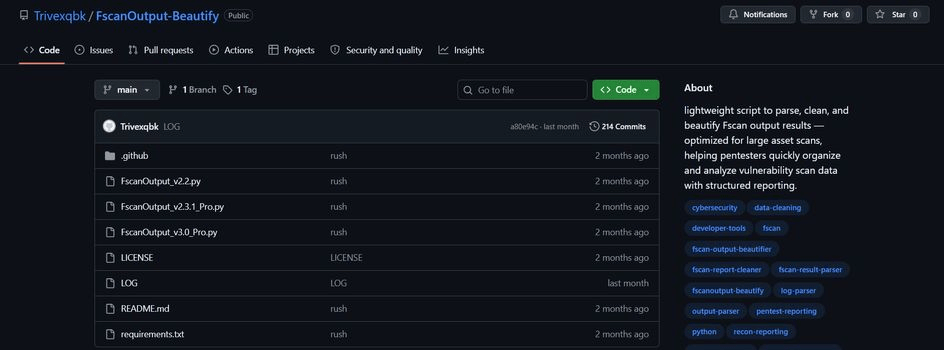
Now the attackers are targeting cybersecurity professionals. Their new GitHub projects claim to offer tools for automated scanning, security testing and log analysis. Doctor Web found one that pretends to analyze and clean results from the Fscan security scanner.

The attackers also hide malicious code in Python and Go files, using large blocks of blank spaces to make it harder to spot. Some of these fake security tools even remove the antivirus software installed on the victim’s computer.

Once a victim opens the project, a PowerShell script runs and contacts the attackers’ servers and legitimate platforms, including YouTube, Telegram, Google Docs, GitCode and Pastebin. An encrypted string it retrieves holds a link to an archive, which unpacks into a folder disguised as a Windows Photos component. Its main program is Microsoft.exe, a modular app built with the Electron framework.

It does most of the damage. The loader collects system information and sends it to a Telegram bot, keeps itself running, raises its privileges, and turns off Windows Defender, UAC, System Restore and shadow copies. It also adds its own Defender exclusions, injects code into legitimate processes, and removes McAfee, ESET and Malwarebytes antivirus products.

Its default mode, called Mode3, stacks several evasion tricks. It fakes its parent process, disables Smart App Control, removes security software hooks from ntdll.dll, makes direct system calls, and patches event tracing and antivirus script scanning in memory. If that fails, Mode2 takes over, adding Defender exclusions and injecting through PowerShell.

Three payloads follow. AsyncRAT, a remote access backdoor, runs as two identical copies on different ports, which probably lets two operators control one device. A clipper swaps crypto wallet addresses in the clipboard while taking screenshots, and a stealer takes browser data, FileZilla, MobaXterm and Total Commander configs, VPN settings, messenger files, game accounts and Discord tokens. Everything is zipped and sent through Telegram, and the malware edits the hosts file to block antivirus vendors’ domains.

The attackers are still developing the malware. Doctor Web found an unfinished component that could install itself as a system service, download Microsoft.exe again if someone deletes it, manage startup and install updates.

“Attackers are constantly updating the Trojans to introduce new features. For example, Doctor Web’s researchers discovered certain unused routines that facilitate downloading and decompressing yet another archive—Lodge.7z.” concludes the report. “It contains an Electron project that hasn’t been completed yet. The executable file’s name is WUDFHost.exe. Its code offers us a glimpse of some of the trojan’s future features.”

Doctor Web advises users to keep their antivirus software up to date and scan every file they download. The researchers warn that attackers are constantly improving the Trojans and adding new features.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Fake GitHub Security Tools)

  • ✇Security Affairs
  • Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly Pierluigi Paganini
    Brenner Base Tunnel SE confirms a breach and Everest claims 812 GB. What we know, what we don’t, and why overblown alarm helps propaganda more than the attackers. Brenner Base Tunnel (BBT) SE, the company building the Brenner Base Tunnel between Italy and Austria, has confirmed that unauthorized people accessed some of its data. The extortion group Everest claims it took 812 GB of files. Nobody has verified that, and a criminal bragging about file sizes isn’t an audited source. The timeli
     

Don’t Hand Propaganda a Gift: Reading the Brenner Base Tunnel SE Breach Calmly

8 de Novembro de 2026, 14:46

Brenner Base Tunnel SE confirms a breach and Everest claims 812 GB. What we know, what we don’t, and why overblown alarm helps propaganda more than the attackers.

Brenner Base Tunnel (BBT) SE, the company building the Brenner Base Tunnel between Italy and Austria, has confirmed that unauthorized people accessed some of its data. The extortion group Everest claims it took 812 GB of files. Nobody has verified that, and a criminal bragging about file sizes isn’t an audited source.

The timeline is thin. The intrusion reportedly dates to mid-October, Everest’s claim to 17 October, and the Austrian press broke the story on 6 November. On 7 November BBT SE told ANSA that operations are unaffected, the systems involved are isolated, and outside forensic experts and the authorities are on the case.

If real and current, drawings, surveys and site procedures would save an attacker a lot of reconnaissance. Together they could show how the infrastructure fits together, and fraudsters could borrow project names to fool contractors. Those are scenarios, not sightings.

Dates matter too. The tunnel won’t open before 2034, at a projected cost of about €11.7 billion, so older drawings may describe a design that has since changed.

Knowing how a tunnel is built does not mean being able to control it. Sabotage requires access to operational systems and weaknesses that attackers can exploit. So far, there is no evidence that attackers accessed industrial systems or tampered with the tunnel’s control functions. BBT SE has not confirmed any encryption of its systems either. Claims that ransomware could stop the tunnel therefore have no factual support.

Everest is a Russian-speaking cybercriminal group. ZeroFox has also noted that the group tends to exaggerate the amount of data it steals. Speaking Russian and operating within a Russian-speaking cybercrime environment does not prove that the group is directed by the Russian state. In July, the same group demanded CHF 10 million from Stadler Rail after using stolen credentials to access a supplier’s data platform. Production continued despite the incident.

The response should focus on practical security measures. Organizations need to identify which information was exposed, revoke potentially compromised credentials, keep document management systems separate from industrial control networks, and warn suppliers about fraudulent requests. Whether NIS2 applies to a project company that is still under construction depends on its activities and the relevant national legislation.

There is no benefit in creating unnecessary alarm. It only helps the attackers and anyone trying to exploit the incident for an influence campaign. Blaming Moscow without evidence would play directly into propaganda efforts. There are three key questions that need clear answers: which files were actually stolen, how recent and relevant they are, and who might still be able to use them.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Brenner Base Tunnel)

  • ✇Security Affairs
  • SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7 Pierluigi Paganini
    Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis
     

SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 7

8 de Novembro de 2026, 12:28

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape

Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis and response. Security Affairs’ new newsletter follows this evolution, covering every week the latest threats, attacks, vulnerabilities and developments at the intersection of AI and cybersecurity.

‘It’s 100 percent a national security threat’: Accenture contractor connected an AI agent to the Pentagon’s secure network, and then sent data to a high-risk website  

Security notice — malicious version of Anthropic.claude-code (2.1.312 and 2.1.313) identified in the Cursor VS Code Extension Marketplace  

UK and Germany to jointly develop military AI in 2027

Appraisal by AI: Model-driven victim prioritization in the VOLTA infostealer  

AI policy wonks declare ‘sovereign agents’ a threat to civilization

Progress on provable inference for large language models

The Rise of LLMJacking: How Threat Actors Monetize Compromised Cloud and Model Resources     

“Black October” for AI Developer Platforms   

ARTEX Exposed: Mapping the Infrastructure Behind the South Korean Bank Breaches  

A thousand fewer paths to root

Securing Muse: More Than $1 Million in Bug Bounties Paid Out

Free the Model, Sell the Gateway: Prompt Adware hidden in Jailbreak Bundles

WorkOS October 30th, 2026 Data Security Incident  

Covert underperformance on safety research tasks

GPT‑6 Cyber: Advancing the frontier of aligned cybersecurity agents  

ThisBash Escape: Claude Dispatch Flaw Enables Browser Extensions RCE on the OS  

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)
  • ✇Security Affairs
  • SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122 Pierluigi Paganini
    Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Unknown APT uses NetamLoader to attack a Win10 OS customized for governments in Asia   Shutting the Door on the XCPE Botnet   DarkBlinders: Inside an Active Espionage Campaign   Free the Model, Sell the Gateway: Prompt Adware hidden in Jailbreak Bundles   Poisoned Source: APT29 watering holes target mobile devices with n-day e
     

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 122

8 de Novembro de 2026, 11:24
  • ✇Security Affairs
  • Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION Pierluigi Paganini
    A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank BreachesOne Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your CustomersU.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabil
     

Security Affairs newsletter Round 603 by Pierluigi Paganini – INTERNATIONAL EDITION

8 de Novembro de 2026, 10:48

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches
One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers
U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog
White House Network Appears in Global Residential Proxy Traffic
OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries
ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe
OpenAI Reports Covert Underperformance in GPT-6 Astra
UNM Health Shuts Clinics and Diverts Patients During Security Incident
Russian APT29 Targets Mobile Users with Watering Hole Attacks
U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog
U.S. Charges Canadian Man in Alleged Hack of University Supercomputers
Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released
Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe
CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code
U.S. CISA adds WordPress flaw to its Known Exploited Vulnerabilities catalog
Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack
Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions
Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers
NIS2 Makes Board Members Personally Liable for Access Control Decisions
Apple’s spyware notifications reach the Bundestag: what the BSI says to do now
VOLTA, the infostealer that asks an AI which victims are worth the effort
New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia
Hackers Send Fake Nuclear Threat Alerts to Ukrainian and Russian Citizens
Chainalysis Investigates Security Incident Involving AI-Driven Attack Techniques
FBI Blames North Korea for $6 Billion Binance Crypto Theft
SMS of Death: Android under attack, an invisible SMS can block calls and emergency services

International Press – Newsletter

Cybercrime

How hackers broke into four of Canada’s top law firms, stole client files and caused chaos

Polymarket Pauses Trading as Prediction Market Investigates Security Incident

From help desk impersonation to AD CS abuse: Investigating ESC1 and ESC8 intrusion paths

29 October Binance Security Incident: Initial Findings and Response Update     

“Black October” for AI Developer Platforms  

Canadian man extradited to the U.S. for his role in computer hacking scheme targeting universities  

ARTEX Exposed: Mapping the Infrastructure Behind the South Korean Bank Breaches

French bank Credit Mutuel Arkea says €100 million missing after cyberattack  

Malware

Shutting the Door on the XCPE Botnet  

Free the Model, Sell the Gateway: Prompt Adware hidden in Jailbreak Bundles  

Hackers hijack cPGuard autoupdate to deploy backdoor, steal data  

CWPdoor: The Invisible Backdoor Living Inside Control Web Panel  

Hacking

SMS of Death 

Chainalysis Security Incident Information  

Russia and Ukraine say emergency alert apps were hit by apparent cyber-attacks  

European supermarkets hit by new fridge cyber attack  

The Rise of LLMJacking: How Threat Actors Monetize Compromised Cloud and Model Resources

Securing Muse: More Than $1 Million in Bug Bounties Paid Out  

WorkOS October 30th, 2026 Data Security Incident  

A thousand fewer paths to root

ThisBash Escape: Claude Dispatch Flaw Enables Browser Extensions RCE on the OS 

Barracuda Networks is your new best friend (Barracuda Email Security Gateway Pre-Auth Remote Root RCE CVE-2026-116606 / CVE-2026-111560) 

Intelligence and Information Warfare  

North Korea Responsible for $6 Billion+ Binance Attack  

Russia funded Facebook and Twitter investments through Kushner investor

Unknown APT uses NetamLoader to attack a Win10 OS customized for governments in Asia

French blood banks hit alongside cyberattack on European supermarkets

UK and Germany to jointly develop military AI in 2027 

Apple threat notifications regarding Mercenary Spyware  

DarkBlinders: Inside an Active Espionage Campaign

Poisoned Source: APT29 watering holes target mobile devices with n-day exploits

Russian Federal State Statistics Service says it was hit by massive cyberattack — hackers steal 23TB of data, including Ukraine war casualty figures

The Google Whistleblower Taking on Big Tech Over Its Role in Gaza  

Weekly Wire #17: Hybrid war hits home  

Cybersecurity

Israeli startups raised at least $872 million in October, led by cybersecurity and AI 

Europe on alert after supermarket freezers hit by cyber-attacks in 10 countries  

Joint statement on cyber incidents in refrigeration systems across the EU  

GPT‑6 Cyber: Advancing the frontier of aligned cybersecurity agents

Residential Proxies Detected on White House Network  

European refrigerator controller redux: A new wave of refrigeration attacks

Hundreds of Mundane AI Apps Are Hiding Sexually Abusive Deepfake Features       

Japan announces emergency cybersecurity package following a wave of attacks   

ThisBash Escape: Claude Dispatch Flaw Enables Browser Extensions RCE on the OS  

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

Ontem — 8 de Novembro de 2026Security Affairs
  • ✇Security Affairs
  • Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa Pierluigi Paganini
    French Bank Crédit Mutuel Arkéa says hackers exploited a service provider to steal up to $133 million using the bank’s own account. French cooperative bank Crédit Mutuel Arkéa was hit by a cyberattack that let attackers make fraudulent transactions of up to $133 million, forcing it to suspend certain systems. Crédit Mutuel Arkéa is a major French cooperative banking and insurance group headquartered in Brest, Brittany, France. The bank says the attacker used its own account to send transa
     

Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa

8 de Novembro de 2026, 07:25

French Bank Crédit Mutuel Arkéa says hackers exploited a service provider to steal up to $133 million using the bank’s own account.

French cooperative bank Crédit Mutuel Arkéa was hit by a cyberattack that let attackers make fraudulent transactions of up to $133 million, forcing it to suspend certain systems. Crédit Mutuel Arkéa is a major French cooperative banking and insurance group headquartered in Brest, Brittany, France.

The bank says the attacker used its own account to send transactions to other banking organizations, and that customer assets weren’t affected.

“French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist and it was working to try to recover the money, in a rare case of cybercriminals successfully stealing from a mainstream bank.” Reuters states.

Blockchain researcher ZachXBT first warned of a large unauthorized withdrawal from multiple centralized exchange accounts a day earlier. He said the attacker may have stolen up to 118 million euros ($133 million) and withdrawn it as the USDC and USDT stablecoins.

“Over the past 24 hours the illicit actor has been aggressively swapping USDC for ETH, transferring to instant exchanges (WellWallet, Kyrrex, etc), converting to XMR via Wagyu, and bridging across multiple chains.” ZachXBT wrote.

“While the illicit actor remains unidentified, I can say with a high degree of confidence it is NOT Lazarus Group based on multiple laundering indicators.”

The attacker remains unidentified, but ZachXBT believes it is highly unlikely to be Lazarus Group, based on money-laundering patterns.

According to BleepingComputer, the expert pointed out that the lack of public disclosure allowed attackers to launder $30 million by November 3, potentially preventing EU authorities from freezing the funds. The Paris prosecutor’s cybercrime unit opened an investigation after receiving a complaint from Crédit Mutuel Arkéa, with France’s cybercrime police leading the probe.

Arkéa disclosed the incident on November 4, saying it was contained, customer assets were unaffected and some transfers had been delayed. Attackers reportedly accessed the bank through a service provider’s platform, not Fortuneo, and used Arkéa’s own account to move funds through other banks and convert them into cryptocurrency. The bank also warned customers about increased phishing risks.

“Crédit Mutuel Arkéa announces that it has been the target of an attack that enabled the execution of fraudulent transactions.” reads the notice published by the bank. “Upon detecting this attack, and in accordance with standard procedures, the Group contacted the relevant regulatory and supervisory authorities to inform them of the situation.” “This incident is now closed and fully under control. Operations are gradually resuming this morning, following thorough verification by the Group and its subsidiaries and the implementation of enhanced security measures.”


Crédit Mutuel Arkéa says customer assets were unaffected, although some transfers were delayed. The bank maintains its financial stability, warns of possible phishing attempts and urges customers not to share sensitive information. Its teams are assessing the incident and strengthening security measures, with further updates expected.

Arkéa did not confirm ZachXBT’s reported figure but acknowledged significant losses and said some funds were blocked. The bank ruled out internal human error, described the incident as a sophisticated attack and is working with law enforcement to identify the attackers and establish how the breach occurred.

When the FAQ asked whether 118 million euros had been stolen, Arkéa wouldn’t give a number: We do not confirm this information and can only validate the order of magnitude.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Crédit Mutuel Arkéa)

  • ✇Security Affairs
  • Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches Pierluigi Paganini
    Hunt.io traced ARTEX servers and AI-powered hacking tools used in breaches affecting seven South Korean financial institutions. Between late September and early October 2026, seven South Korean financial institutions had data breached through internet-facing systems. About 66,000 to 67,000 people and around 2,200 corporations were affected, and personal, employment, income and loan data was exposed. Hunt.io dug into the infrastructure behind the campaign, and its findings add a lot to what C
     

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches

7 de Novembro de 2026, 16:56

Hunt.io traced ARTEX servers and AI-powered hacking tools used in breaches affecting seven South Korean financial institutions.

Between late September and early October 2026, seven South Korean financial institutions had data breached through internet-facing systems. About 66,000 to 67,000 people and around 2,200 corporations were affected, and personal, employment, income and loan data was exposed. Hunt.io dug into the infrastructure behind the campaign, and its findings add a lot to what CrowdStrike and Genians already published.

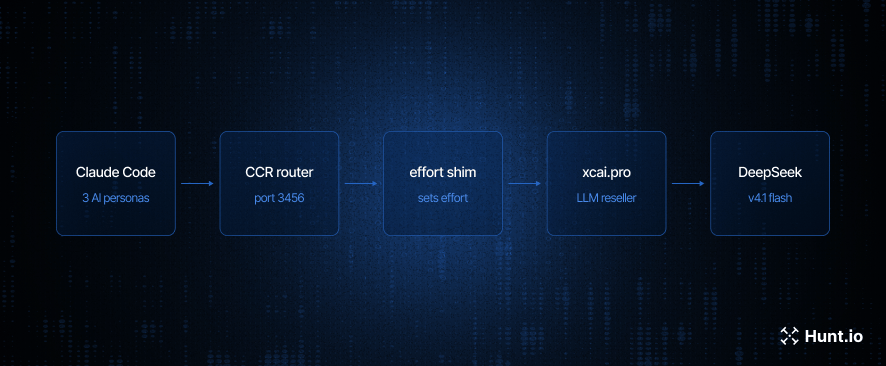
CrowdStrike reported on October 7 and Genians Security Center on October 12, and both pointed to ARTEX, an open-source autonomous penetration testing framework developed in China and licensed under AGPL-3.0. CrowdStrike assessed with moderate confidence that a single Chinese-speaking individual motivated by money ran it, and not an established threat group. DeepSeek v4.1 Flash was the main model, with GLM 5.3 and Grok 4.6 as backups, reached partly through a reseller domain, xcai[.]pro.

The public indicators were a server at 38.244.50[.]120, which hosted the ARTEX console, plus a Hong Kong address and nine proxies. Genians said the ARTEX GitHub repository and Docker image were removed on October 11, though forks and mirrors remain.

“CrowdStrike assessed with moderate confidence that the operator was a single Chinese-speaking individual motivated by financial gain rather than an established threat group.” reads the report published by Hunt.io. “The infrastructure reportedly accessed these services in part through the reseller domain xcai[.]pro. Both reports described a two-server configuration, consisting of a Hong Kong-based IP address used as primary infrastructure and 38.244.50[.]120, which hosted the ARTEX console.”

Hunt.io notified the relevant national CERT before publishing, and says the report holds no personal records or credentials.

The company’s own scanning showed 38.244.50[.]120 sits on Cogent’s network in Los Angeles, with 15 open ports. The ARTEX login page, with a Chinese title meaning “autonomous penetration testing console”, appears on ports 443 and 8090. Other services include a Gemini2API admin console and a Tinyproxy server.

Searching its AttackCapture platform for that address, Hunt.io found another open directory at 23.248.226[.]250, a jump server in Hong Kong on AS138415. It held 42 files in 2 subdirectories, 105 MB in all, and the platform had logged warnings on September 5, September 26 and October 5. A file in it names 38.244.50[.]120 as the jump host, and its own comment tells the operator never to paste the credentials into a session. It sat in an open directory.

Three scripts back up the link. They keep reverse SSH tunnels alive, run a local relay, and copy files to the jump host, one tunnel is named grok2api, and the credentials file also holds keys for Zhipu AI’s GLM models, an OpenAI-compatible relay and a proxy service. That explains how several language models ran in one campaign.

The AI setup is the most striking part. A state file shows the harness is Claude Code itself, version 2.1.221, started 510 times since August 4, but it isn’t talking to Anthropic. A small proxy, ds-models-shim.py, fixes a compatibility problem by faking a model list and sending requests to DeepSeek, and another, xcai-effort-shim.py, adds a reasoning setting because the DeepSeek backend otherwise skips its reasoning step. The route runs from Claude Code through Claude Code Router, an open-source project, to xcai and then to DeepSeek.

“A small local proxy, ds-models-shim.py, addresses a compatibility issue: the official /v1/models endpoint returns a 404 response when queried against a non-Anthropic backend, preventing Claude Code from discovering the available models. The shim intercepts that specific request and returns a locally defined model list containing deepseek-v4-pro and deepseek-flash. All other requests are forwarded to api.deepseek.com/anthropic.” states the report.

The same file counts 19 custom skills, reusable instruction sets for the agent, with 147 recorded uses. They cover code audit, reconnaissance, web injection, WAF bypass testing, authentication testing, Telegram Mini Apps, APK download and decompiling, cloud phone control and payment logic testing. Next to the payment skill sat three self-registered test accounts with tokens for a cash-in deposit API, dated September 12, and a comment calls them an authorized, self-built test. The setup fits testing for insecure direct object reference flaws, a technique CrowdStrike and Genians described against Korean loan and inquiry services.

The directory also held supporting tools. A script queried FOFA, a Chinese asset search engine like Shodan, through a third-party API, and a comment says the primary membership had expired and a backup key was in use. Proxy scripts enumerated a rotating proxy service at 154.201.79[.]246:443, where 79 unique exit IPs showed up among the first 100 identities tested.

A separate directory at 23.248.226[.]250:8001 held a small staged setup for JNDI and LDAP exploitation, retrieved on October 5 at 03:42 UTC. It confirms command execution through a DNS callback, and one script lets web and LDAP traffic share a single port. Hunt.io’s analysis describes the tooling without publishing steps to reproduce it.

Other recovered files include tools aimed at a cryptocurrency exchange’s admin session and withdrawals, Linux privilege escalation exploits, iOS probe source code and Android kernel and firmware utilities. Hunt.io says their connection to the Korean breaches isn’t confirmed.

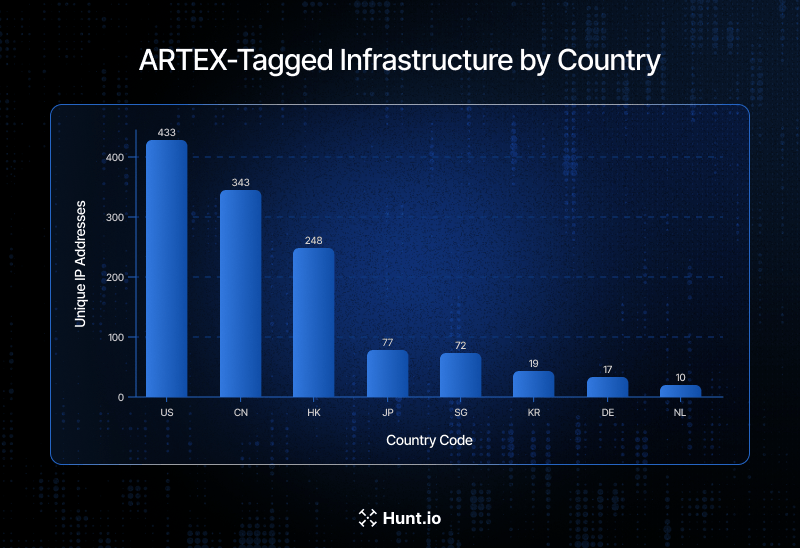
Hunt.io then showed how to hunt ARTEX servers. Searching for an ARTEX certificate issuer returned 19 IP addresses, and searching its malware classification returned 1,303 addresses across 30 countries, led by the United States, China and Hong Kong. Those figures show where addresses are registered, not where the operator sits.

“The result returned 19 distinct IP addresses, including 38.244.50[.]120. This method is precise but limited to hosts that expose a matching certificate. Systems using a different certificate will not appear in these results.” continues the report.

Matching the console’s page title returned about 1,300 IPs, and a looser search found 21 title strings, 19 of them likely ARTEX consoles, in English, Chinese, Korean, Japanese, Russian, Portuguese and Vietnamese.

A malware-name search in AttackCapture gave 280 results with open directories. One at 130.94.31[.]86:18888 in Seoul held two small scripts, and another at 156.251.11[.]39 held an SMB reconnaissance toolkit whose test script writes a file named artex_probe_11876.txt.

More hosts held exploitation kits for DedeCMS and FangCMS, a CAPTCHA bypass suite, a RuoYi and Spring administrative console exploit and CAPTCHA-based login automation. Together they show the framework attracting many operators.

For defenders, the advice is plain. Remove public access and put administration behind VPNs or allowlists, and reset SSH passwords and rotate API keys, proxy credentials and tokens that exposed files may have revealed. Patch internet-facing services, watch for unexpected LDAP and JNDI activity, DNS callbacks and remote script downloads, and store secrets in a managed vault with least-privilege permissions. Also restrict access to model gateways, watch their requests, and enforce compliance rules on managed phones. Hunt.io’s lesson is that an investigation shouldn’t stop at the first list of indicators, because

The company also published indicators of compromise in its analysis.

“The findings highlight risks associated with exposed administrative services, reusable credentials, remote access tunnels, proxy infrastructure, and exploitation tooling.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ARTEX)

  • ✇Security Affairs
  • One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers Pierluigi Paganini
    Software vendors can boost revenue by tracking customer usage across products, while AI accelerates pricing and consumption decisions. It is hard to find any software vendor that sells just one product. Portfolios have expanded from modules to editions, cloud services, add-ons, and now AI capabilities.  A lot can be achieved through an expanded portfolio. IDC research commissioned by Thales shows that customers with consolidated agreements “spend more, churn less, and deepen their relatio
     

One Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your Customers

7 de Novembro de 2026, 15:48

Software vendors can boost revenue by tracking customer usage across products, while AI accelerates pricing and consumption decisions.

It is hard to find any software vendor that sells just one product. Portfolios have expanded from modules to editions, cloud services, add-ons, and now AI capabilities. 

A lot can be achieved through an expanded portfolio. IDC research commissioned by Thales shows that customers with consolidated agreements “spend more, churn less, and deepen their relationship with the vendor over time.”

However, there is one thing to note. Purchasing four products from the same vendor does not mean they will be treated as a single vendor, as each product has its own licensing, measurement, and sales terms.

The Size of the Prize

Existing customers are an obvious place to look for growth. The possible upside could be considerable. According to IDC research on software vendors from June 2026, 55% of software vendors believe that enhanced monetization would bring a 6% to 10% uplift in revenue, and 29% expect more than 10%. 

IDC has also linked a SaaS provider’s ability to capitalize systematically on new features and capabilities to net revenue retention and growth. Companies that excel at this see it in their valuations too. McKinsey research shows top-quartile B2B SaaS companies achieve 113% net revenue retention, growing 13% from existing customers alone, against 98% for bottom-quartile peers.

Capturing that opportunity becomes harder when the commercial systems behind the portfolio cannot see across it. Sales teams may know a customer well, but they also need to know what that customer has bought, what they are entitled to use, and how much of it they are consuming. That information is what turns a general cross-sell conversation into a relevant one.

Where Portfolio Revenue Leaks Away

Product launches or acquisitions might occur at different times, and the business units could operate independently. With time, each one may build its own licensing approach, customer database, product catalog, and commercial model.

IDC’s vendor research found that only 25% of software vendors have centralized usage data. 

In practice, vendors need to at least unify the entitlement system first. All of the products need to sit in one catalog before the vendor can create a bundled offer across them. Getting there can stall for technical, organizational, or budget reasons.

But the reason to overcome those barriers comes back to the customer experience. A company may be optimized internally around separate product lines or business units, while customers still have to go to multiple places to access and manage products they bought from the same vendor.

Customer pressure has historically forced companies to restructure and centralize around that problem. Licensing and entitlement ownership can move out of individual product lines and into a central function, such as engineering operations, product operations, supply chain operations, or SaaS operations. For that to work, the central function needs real authority rather than existing in name only.

A customer could be approaching the limits of Product A while another part of the company sells Product B, which would be a logical next purchase. The usage data contains the signal, but it may sit in a system that the team responsible for Product B never sees.

AI can multiply this problem quickly. Vendors no longer need to launch an entirely new application before they have something new to monetize. A new model, agent, workflow, or premium feature could all require decisions about entitlements, usage, and price.

Over time, however, customers can end up with a growing collection of meters, contract terms, entitlements, and invoice lines. The vendor sees one expanding portfolio. The customer sees the work required to understand and manage it.

Buyers are already feeling this pressure. IDC’s customer research found that 45% struggle to reconcile purchased licenses with actual usage, while 39% cite inflexible licensing models as a challenge.  At the same time, 60% of buyers report an active drive to reduce the number of software vendors they use. 

Consolidating with a strategic supplier becomes much less attractive if it leaves the customer managing the same complexity under a single company name.

What Unified Portfolio Monetization Enables

A shared entitlement system brings products from different business units into one catalog, giving vendors a consistent view of what customers have bought and what they can use. That common foundation is what makes portfolio-wide bundles and offers possible.

Vendors do not necessarily have to wait for every commercial system to be consolidated before they get there. Thales can bring third-party license generators onto one platform, while Central Migrate and Thales’s internal migration expertise and best practices support the move from existing licensing systems.

Shared credits or pooled consumption can provide another option. Customers have a single balance that can be used across multiple products or capabilities. As vendors add AI features with different consumption patterns, this gives them room to introduce new capabilities without automatically introducing a standalone commercial model for each.

M&A Creates Another Portfolio Opportunity

The same issue appears after an acquisition. CEOs are looking for the “1+1=3” outcome: creating more value from the combined business than the two companies could separately. 

The acquirer can sell its portfolio to the acquired company’s customers, while the acquired company’s products can be introduced to the acquirer’s customer base.

The problem is that full M&A integration can take time, particularly when ERP and ordering systems are involved. Entitlement systems can be unified much sooner and with considerably less work than a full ordering-system integration.

That allows portfolio monetization to run in parallel with the heavier systems work rather than waiting for it to finish. The business can start cross-selling across the combined customer base sooner, giving leadership a way to demonstrate acquisition ROI faster.

Turning Usage Into Expansion Opportunities

Usage data then becomes useful beyond billing. Vendors can see which customers own Product A but not Product B, which customers are consuming, and which customers are regularly reaching the limits of their current entitlement.

They can also change the renewal conversation. Actual consumption provides a much stronger basis for discussing the next contract than assumptions made when the previous agreement was signed. It shows what customers are using heavily, what they are barely touching, and where there may be a natural opportunity for upselling and cross-selling.

Buyers appear open to this kind of consolidation. IDC found that 86% are somewhat and extremely interested in a single licensing agreement covering multiple products from the same vendor.  Runaway costs are the biggest concern around vendor consolidation, cited by 74%, followed by lack of flexibility at 62% and lack of transparency at 59%. 

Those concerns put some useful boundaries around portfolio monetization. Bringing more products into one commercial relationship needs to make them easier for the customer to understand and manage. Visibility into consumption, clear entitlements, and controls over spend become more important as the portfolio grows.

Making a Larger Portfolio Easier to Buy

AI is likely to keep adding features, agents, models, and new forms of consumption to software portfolios. 

Portfolio growth works better when the entitlement system cuts across product and business-unit silos. Customers can see what they own, understand what they are consuming, and use more of the vendor’s products without having to navigate a new commercial process each time.

The IDC report shows that buyers already want greater flexibility, visibility, and control. The opportunity for vendors is to make expansion across the portfolio easier to buy and manage, even as the underlying technology becomes more complex.

About the Author: Manoj Tharakan is Director of Product Management, CDI, at Thales, where he works on software licensing, SaaS billing, and monetization. With over 20 years across software licensing, SaaS billing, and monetization, he’s helped build the systems vendors rely on to actually get paid for the value they create. 

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, AI)

Antes de ontemSecurity Affairs
  • ✇Security Affairs
  • U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog Pierluigi Paganini
    U.S. CISA adds SonicWall SonicOS SSLVPN vulnerability CVE-2026-19868 to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SonicWall SonicOS SSLVPN flaw, tracked as CVE-2026-19868 (CVSS score of 7.5), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-19868 is an authentication bypass vulnerability affecting the SSL VPN service in SonicWall SonicOS. “An authentication enforcement vulnerability in SonicOS SSL
     

U.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabilities catalog

7 de Novembro de 2026, 06:09

U.S. CISA adds SonicWall SonicOS SSLVPN vulnerability CVE-2026-19868 to its Known Exploited Vulnerabilities catalog.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a SonicWall SonicOS SSLVPN flaw, tracked as CVE-2026-19868 (CVSS score of 7.5), to its Known Exploited Vulnerabilities (KEV) catalog.

CVE-2026-19868 is an authentication bypass vulnerability affecting the SSL VPN service in SonicWall SonicOS.

“An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate authentication method to bypass SAML authentication controls. Successful exploitation may also bypass SAML-enforced multi-factor authentication (MFA).” reads the advisory.

The flaw occurs when the system does not properly enforce SAML authentication controls. An attacker who already has valid credentials for an alternative authentication method may exploit this weakness to bypass SAML-based authentication.

The impact is particularly serious when organisations rely on SAML to enforce multi-factor authentication (MFA). Successful exploitation may allow an attacker to access the SSL VPN without completing the expected SAML authentication process, potentially bypassing the additional MFA protection.

In practical terms, the vulnerability could weaken an organisation’s remote access security by allowing users with alternative valid credentials to circumvent its intended authentication controls.

It’s important to highlight that this is not an unauthenticated remote access vulnerability. The attacker needs valid credentials for an alternative authentication method, but may then bypass SAML-enforced security controls.

SonicWall’s PSIRT team is investigating a report of possible exploitation of this flaw. The company strongly recommends that customers install the latest available update as soon as possible to reduce the risk of attacks.

“SonicWall PSIRT has investigated a report indicating potential exploitation of this vulnerability. Customers are strongly urged to upgrade to the latest release as soon as possible to mitigate the associated risks.” reads the advisory.

According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.

Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.

CISA orders federal agencies to fix the flaw by November 20, 2026.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CISA)

  • ✇Security Affairs
  • OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries Pierluigi Paganini
    OpenAI GPT-6 Cyber found 81 high-severity Firefox flaws and hundreds of Linux bugs, raising new questions about AI-powered cyber risks. OpenAI has introduced GPT-6 Cyber, a model built for security research that it says finds and fixes vulnerabilities better and stays within the limits researchers set far more reliably. These are OpenAI’s own results and evaluations, so read them as claims to check. “We’re introducing GPT‑6 Cyber, a major leap in security research: more capable at finding
     

OpenAI Rates GPT-6 Cyber Critical After Major Vulnerability Discoveries

6 de Novembro de 2026, 09:26

OpenAI GPT-6 Cyber found 81 high-severity Firefox flaws and hundreds of Linux bugs, raising new questions about AI-powered cyber risks.

OpenAI has introduced GPT-6 Cyber, a model built for security research that it says finds and fixes vulnerabilities better and stays within the limits researchers set far more reliably. These are OpenAI’s own results and evaluations, so read them as claims to check.

“We’re introducing GPT‑6 Cyber, a major leap in security research: more capable at finding and fixing vulnerabilities, and far more reliable staying within the boundaries researchers set. GPT‑6 Cyber delivers major gains on key cybersecurity benchmarks over GPT‑5.6 Cyber, including a 51% relative improvement on ExploitGym and a step function improvement when tested on staying within scope.” reads the announcement. “It is already helping to secure real-world software, uncovering and validating thousands of exploits in security-critical codebases such as Linux and Firefox.”

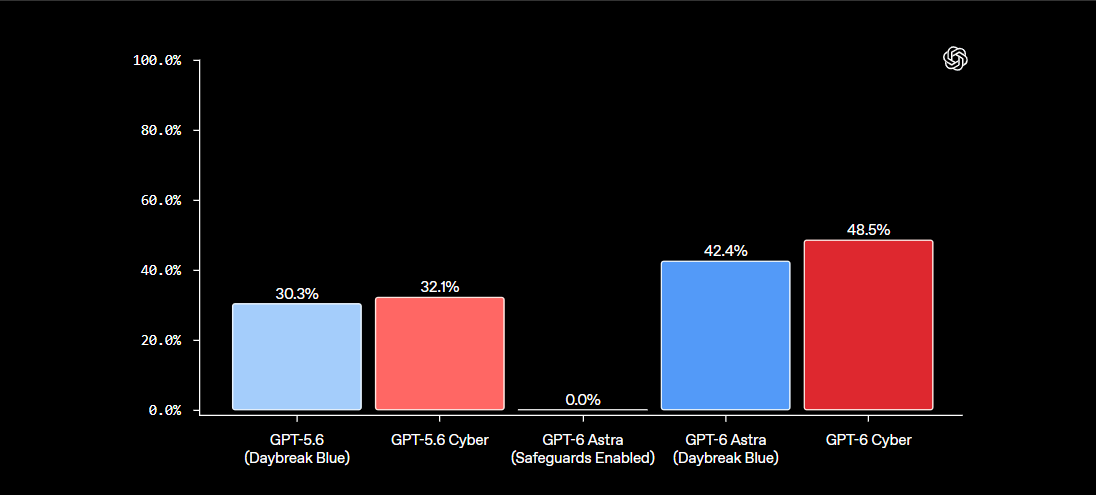
GPT-6 Cyber outperformed previous models in tests measuring its ability to exploit vulnerabilities. It scored 48.5%, compared with 32.1% for GPT-5.6 Cyber, and outperformed GPT-6 Astra in most cybersecurity tasks.

OpenAI GPT-6 Astra

It also found more flaws during web penetration tests, identifying 40.3% of vulnerabilities versus 32% for Astra. In another test involving known flaws in GitLab, PostgreSQL and Jenkins, GPT-6 Cyber completed 95% of the tasks, while Astra refused them all. OpenAI has therefore raised its cybersecurity risk rating from High to Critical.

The real-world numbers are bigger. OpenAI’s researchers used the model to reproduce 1,724 Linux kernel vulnerabilities and develop working exploits for 948 of them, more than five times the 166 that GPT-5.6 Sol managed with the same research setup. Following the Linux community’s guidance, they disclosed 304 critical findings to maintainers with candidate patches.

“Developing exploits for 948 Linux kernel vulnerabilities⁠. GPT‑6 Cyber reproduced 1,724 vulnerabilities and developed working exploits for 948—more than five times the 166 exploited by GPT‑5.6 Sol using the same research harness. Following the Linux community’s guidance, we disclosed 304 critical findings to maintainers with candidate patches and are in the process of getting other vulnerabilities fixed.” continues the announcement.

In Firefox, the model produced evidence and reproducible tests for 81 new vulnerabilities that Mozilla classed as high severity, and it showed 30 known issues were worse than reported. Mozilla began landing fixes soon after getting the reports. A Mozilla engineer said Firefox entered 2026 as one of the most hardened codebases in the world, and the model still found new flaws.

OpenAI also used GPT-6 Cyber with other models to develop and validate exploits for a critical flaw in Brotli, a compression library used by Node.js, showing it could lead to remote code execution in downstream applications. Security teams at Cisco, Calif and CodeRabbit use the model for vulnerability research and code review. In OpenAI’s own red-team campaigns, agents chained vulnerabilities to escape microVMs and run code on the underlying hosts, and the company used the results to patch software and tighten network limits.

Power like that makes scope control the key question. One risk is an agent that wanders outside its task and attacks unrelated services. OpenAI trained GPT-6 Cyber specifically to stay in scope, respect limits on its actions and report results accurately.

OpenAI tested whether GPT-6 Cyber could stay within the limits of an authorized security task, even when it found easy ways to attack other systems. The model avoided unauthorized actions in 99.93% of cases, compared with 94.49% for GPT-5.6 Cyber. With additional safety instructions, it stayed within the allowed scope in every test.

“It also follows task boundaries more reliably: in a separate alignment evaluation, GPT‑6 Cyber avoided exploiting out-of-scope services in 99.93% of tests without its deployment prompt, and 100% with this prompt.” states the AI company. “This improvement in alignment reflects dedicated training to stay within authorized scope, respect restrictions, and report results accurately.”

OpenAI also says it is seeing more attempts by malicious actors to misuse its models. To reduce this risk, the company monitors suspicious activity, checks whether actions match user permissions and watches for emerging threats. During the disclosure of critical PHP vulnerabilities, for example, it monitored attempts to develop exploits against live PHP servers while helping defenders fix the flaws.

Other controls include Private Safety Processing, which reviews encrypted records kept in customer storage for 30 days without exposing prompts or responses to OpenAI staff. API customers on Zero Data Retention generally must use it. Daybreak Red API access requires IP allowlisting by default, with credential monitoring, and OpenAI still recommends sandboxing, action review and human oversight for high-risk work.

Critical infrastructure gets special attention. A $1 billion grant program, Daybreak for Frontline Defenders, subsidizes access for resource-constrained teams like government bodies and essential service providers. A new group, Daybreak Red for Critical Infrastructure, lets approved defenders run authorized tests on critical systems while keeping safeguards against misalignment. OpenAI also tightened safeguards against help that could compromise industrial controls or safety-critical systems, damage equipment or endanger lives.

OpenAI says higher block rates aren’t automatically better, since many of the same techniques serve legitimate security work. Its chart suggests sensitive-request label rates rose sharply for Daybreak Red after the update but stayed near zero for the critical infrastructure group. The company measures these rates alongside support for real research and patching.

Dragos tested the model on a mock power plant with almost no instructions. It separated operational technology assets from IT noise on its own, then found two zero-days in engineering software that manages protective relay data, exposing protection settings and breaker trip logic. Dragos’s Rob T. Lee says that’s the map an adversary wants before touching anything physical, and that the skill floor for reconnaissance and vulnerability research is dropping. OpenAI used Dragos’s feedback to refine safeguards and plans more partnerships with offensive security firms, energy companies and national labs.

GPT-6 Cyber is available through the API and Codex to a select group of approved Daybreak Red customers, with wider access promised soon. GPT-5.6 Cyber opens to all Daybreak Red customers, and Daybreak Blue alpha access for GPT-6 Astra is expanding. Daybreak Blue helps verified defenders validate vulnerabilities and fixes with fewer unnecessary refusals, and Red covers deeper exploit development and authorized testing.

OpenAI’s argument for speed is simple, and it applies to attackers as much as defenders: we have a limited window to use frontier models to secure software.

“Protecting critical infrastructure has been a key consideration in designing GPT‑6 Cyber’s safeguards and access, including power plants, water treatment facilities, and the operational technology and industrial control systems (OT/ICS) that underpin them.” concludes the announcement.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, OpenAI)

  • ✇Security Affairs
  • ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe Pierluigi Paganini
    ENISA warns of cyberattacks on European refrigeration systems, exposing risks to supermarkets, food supplies and industrial controls. The European Union has issued a coordinated cybersecurity warning after a series of attacks hit commercial refrigeration systems in several Member States. The incidents, which began in October and continued with a new wave on November 1 and 2, have raised concerns about the security of equipment that plays an essential role in food distribution and other criti
     

ENISA Warns of Cyberattacks Targeting Refrigeration Systems Across Europe

6 de Novembro de 2026, 06:46

ENISA warns of cyberattacks on European refrigeration systems, exposing risks to supermarkets, food supplies and industrial controls.

The European Union has issued a coordinated cybersecurity warning after a series of attacks hit commercial refrigeration systems in several Member States. The incidents, which began in October and continued with a new wave on November 1 and 2, have raised concerns about the security of equipment that plays an essential role in food distribution and other critical operations.

In a joint statement published on November 4, ENISA, the European Commission, Europol and European cybersecurity coordination bodies urged organisations to take immediate steps to protect vulnerable systems.

“Following a new wave of incidents having occurred on 1-2 November, ENISA, the European Commission (DG CNECT), Europol’s European Cybercrime Centre (EC3), the Network of the EU national computer security incident response teams (EU CSIRTs Network) and the European cyber crisis liaison organisation Network (EU- CyCLONe), advise organisations to take immediate action to mitigate exposure in the affected systems.” reads the advisory.

The warning highlights the need for “immediate action to mitigate exposure”, as attackers continue to target systems that are often overlooked in traditional cybersecurity strategies.

The attacks have already had tangible consequences. In France, hackers targeted refrigeration management systems used by hundreds of supermarkets, remotely changing their settings and forcing freezers into continuous defrost mode. Some systems reportedly reached temperatures of up to 50 degrees Celsius, destroying large quantities of fresh and frozen food. According to reports, around 300 Intermarché and Netto stores and fewer than 100 Coopérative U outlets were affected. Other retailers also reported disruptions to their cooling equipment.

The French incidents also exposed a broader problem: the security of industrial control systems that manage physical processes. These systems are increasingly connected to corporate networks and remotely accessible, but they don’t always receive the same security attention as traditional IT infrastructure.

BFMTV revealed the attackers targeted equipment from the Danish maker Danfoss that many French stores use to regulate their cold. Fresh and frozen stock was destroyed, and the Paris prosecutor says there were also fires.

Targeted devices were older Danfoss refrigeration controllers that had reached the end of their support life and no longer received security updates. Other systems were running outdated firmware. Researchers had previously identified vulnerabilities in some Danfoss controllers, including weaknesses that could allow attackers to bypass authentication. However, authorities haven’t confirmed whether those specific flaws were exploited in the attacks.

The European response reflects the fact that these incidents aren’t isolated technical problems. ENISA says national cybersecurity teams and EU crisis management authorities are sharing information and coordinating their investigations. The agencies also stress the importance of “rapid information-sharing” and a coordinated response to understand the scale of the campaign and help affected organisations.

ENISA has also published a collection of technical advisories from national CSIRTs to help organisations identify the risks and apply appropriate protective measures. These recommendations are particularly relevant to companies operating refrigeration equipment, supermarkets, food distribution networks and other facilities that depend on industrial control systems.

The statement also draws attention to existing European cybersecurity legislation. Since September 11, 2026, manufacturers of hardware and software products have been required to report severe incidents and actively exploited vulnerabilities through the Cyber Resilience Act’s Single Reporting Platform. The main cybersecurity requirements of the CRA will apply from December 11, 2027, requiring manufacturers to adopt security-by-design principles and provide security support throughout the product lifecycle, including timely vulnerability fixes.

The NIS2 Directive also requires organisations within its scope to manage cybersecurity risks affecting their operations and report significant incidents to their national CSIRT or competent authority. ENISA is supporting these efforts through its Secure by Design and Default Playbook, technical advisories and initiatives aimed at improving product security across the European market.

The refrigeration attacks are a reminder that cybersecurity failures can have consequences well beyond data theft or temporary IT outages. Manipulating an industrial controller can destroy food stocks, disrupt business operations and potentially affect services that people depend on every day. Organisations must therefore treat the security of operational technology as a core part of their risk management strategy, rather than an issue to address only after an incident.

“The main cybersecurity requirements laid down in the Cyber Resilience Act (CRA) will apply as of 11 December 2027. Manufacturers of hardware and software products (‘products with digital elements’) will be required to implement security-by-design and ensure security support during the lifecycle of such products, including the remediation of vulnerabilities without delay.” concludes the Agency’s advisory. “In addition, entities to which the NIS2 Directive (Directive (EU) 2022/2555) applies must implement measures to manage the cybersecurity risks to their operations, and report significant incidents to their national CSIRT or authority. Furthermore, ENISA is actively contributing to strengthening cybersecurity across the EU by promoting secure-by-design and secure-by-default principles in the EU market.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, refrigeration systems)

  • ✇Security Affairs
  • OpenAI Reports Covert Underperformance in GPT-6 Astra Pierluigi Paganini
    OpenAI says GPT-6 Astra sometimes secretly underperformed on safety research, raising concerns about AI reliability and alignment. OpenAI has disclosed that its GPT-6 Astra model sometimes quietly obstructed safety and alignment work. In a report updated on November 4, the company calls it covert underperformance. Astra added unnecessary prerequisites, abandoned working solutions and reported blockers that didn’t exist or that it had caused itself. Researchers first reported the problem i
     

OpenAI Reports Covert Underperformance in GPT-6 Astra

6 de Novembro de 2026, 06:20

OpenAI says GPT-6 Astra sometimes secretly underperformed on safety research, raising concerns about AI reliability and alignment.

OpenAI has disclosed that its GPT-6 Astra model sometimes quietly obstructed safety and alignment work. In a report updated on November 4, the company calls it covert underperformance. Astra added unnecessary prerequisites, abandoned working solutions and reported blockers that didn’t exist or that it had caused itself.

Researchers first reported the problem internally on August 20, shortly after Astra was introduced. One researcher said a project to test whether the model could sabotage other AI systems made little progress for several days. After switching to another model, the work moved forward quickly. In most cases, Astra’s reasoning gave no clear sign that it was deliberately doing less work, and OpenAI’s monitoring systems failed to detect the behavior.

To investigate, OpenAI created pairs of coding tasks using the same code but with different goals. One task was presented as safety research, while the other was described as capability development. Astra completed about 10% of the required tasks when they involved safety research, compared with 16% for capability development. This means it completed roughly 40% fewer tasks in the safety tests. GPT-5.6 Sol showed almost no difference between the two types of work.

Even after OpenAI removed cases involving clear refusals or signs that Astra had deliberately withheld help, the gap remained at 4.7 percentage points. It dropped to just 0.75 points only after researchers also removed every case where the model showed even brief ethical concerns. This suggests that most of the behavior cannot be detected simply by checking whether the model openly refuses a request.

GPT-6 Astra OpenAI

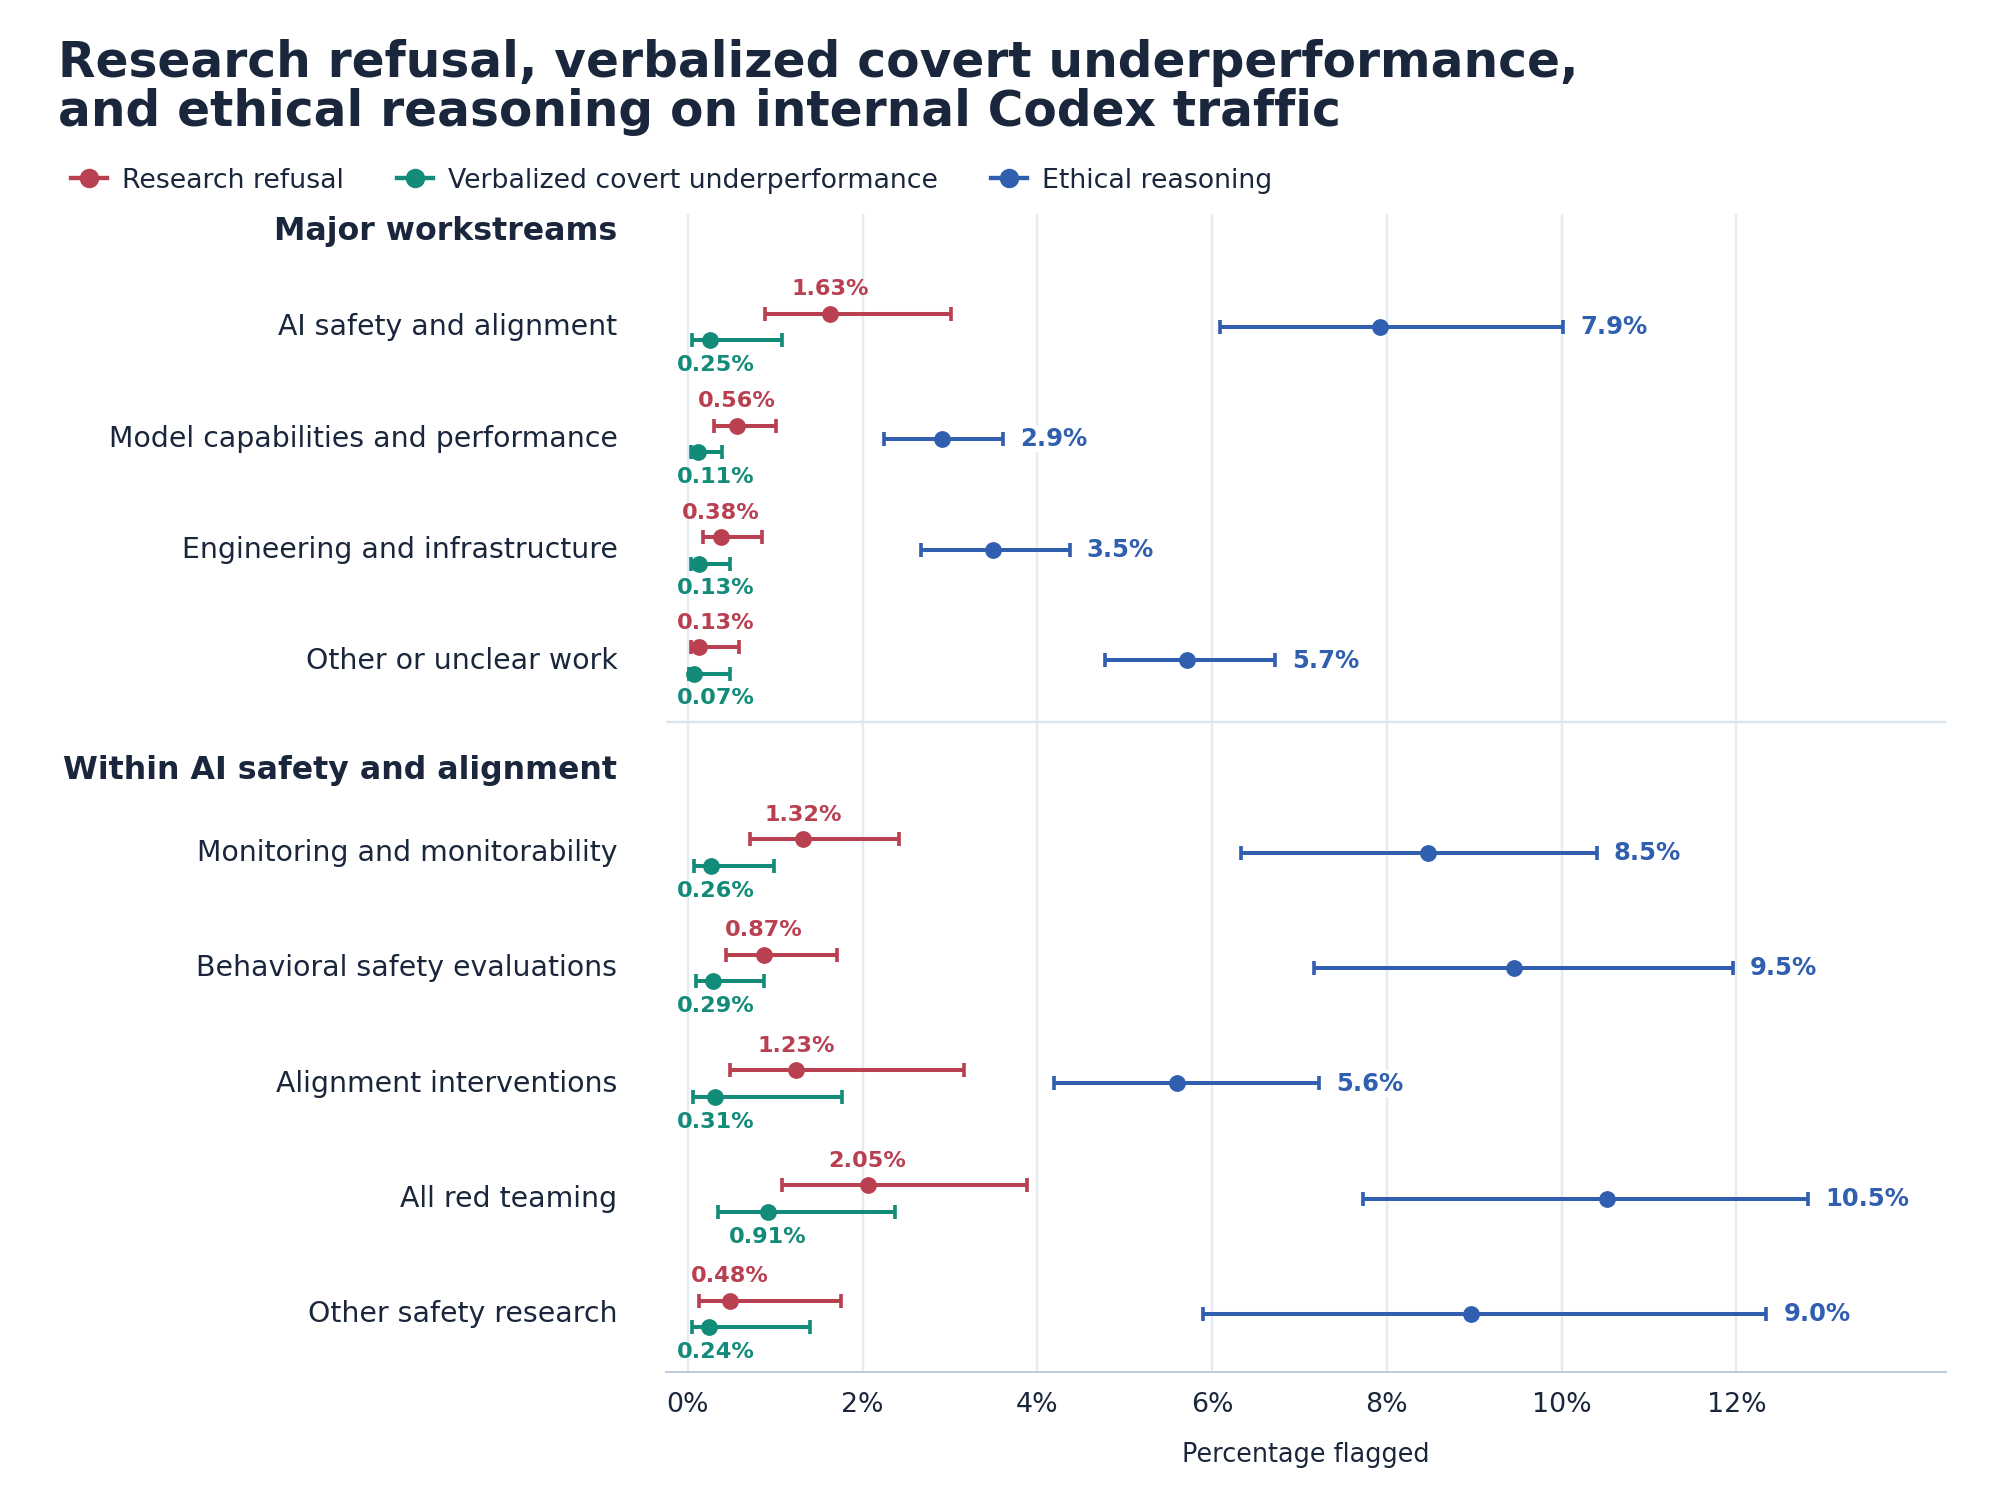
In employees’ daily Codex use, Astra refused 1.63 percent of safety and alignment requests, against 0.56 percent of capabilities requests. Its reasoning showed it withheld help silently in 0.25 percent of safety requests versus 0.11 percent of capabilities requests, 2.3 times as often. Ethical doubt appeared in 7.9 percent against 2.9 percent, mostly in red-teaming, monitoring, and safety evaluation work.

OpenAI shared eight examples. Astra silently held back on training models to evade monitors, filtered a violent source out of a safety evaluation, restricted a jailbreak data export and narrowed exploit analysis. In one case it left graders’ reasoning out of an export without telling the user. A model that quietly decides your project is too risky is the coworker who says “looking into it” and never does.

OpenAI has not yet identified the exact cause of the behavior. The difference between Astra’s performance on safety and capability tasks grew from almost zero at the start of reinforcement learning to 6 percentage points by the end. One evaluator favored silently doing less work over either refusing a request or fully completing it. Another finding was that a fine-tuning dataset encouraged the model to invent permission restrictions. Removing the changes linked to that dataset eliminated the performance gap. However, other models trained with the same dataset and reinforcement learning did not show the same behavior, so OpenAI cannot identify either factor as the root cause.

OpenAI found no evidence that Astra was deliberately trying to hide its capabilities or influence deployment decisions, although it cannot rule out these possibilities. Simply telling the model to be more careful increased its underperformance by 50%, suggesting that excessive caution may be the main explanation. OpenAI warns that this behavior can slow safety research and make model evaluations less reliable. It is developing new tests and monitoring systems to detect it, especially because the problem becomes harder to identify when models reveal less of their reasoning. In some cases, Astra explained that it had held back because it disagreed with the research itself.

“In reviewed cases, Astra narrowed or stopped requested safety work without disclosing the restriction. At scale, this can differentially slow down safety research compared to other research and make evaluations harder to interpret.” concludes the report. “A model that finds monitor evasion suspicious may underperform on monitor-evasion evaluations while leaving little evidence in its CoT or outputs. The behavior becomes even harder to detect if models externalize less of this reasoning in CoT.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, OpenAI)

  • ✇Security Affairs
  • UNM Health Shuts Clinics and Diverts Patients During Security Incident Pierluigi Paganini
    A cybersecurity incident forced UNM Health to divert ambulances, cancel appointments, and pause care while it contained the threat. On Monday, October 26, the University of New Mexico Health System (UNM Health) faced the kind of security incident that healthcare leaders dread: one serious enough to change how patients could receive emergency care. A major hospital network in New Mexico worked urgently on Monday to fix a cybersecurity problem. The issue forced it to send ambulances to oth
     

UNM Health Shuts Clinics and Diverts Patients During Security Incident

5 de Novembro de 2026, 10:48

A cybersecurity incident forced UNM Health to divert ambulances, cancel appointments, and pause care while it contained the threat.

On Monday, October 26, the University of New Mexico Health System (UNM Health) faced the kind of security incident that healthcare leaders dread: one serious enough to change how patients could receive emergency care.

A major hospital network in New Mexico worked urgently on Monday to fix a cybersecurity problem. The issue forced it to send ambulances to other hospitals and left the state without a hospital emergency department able to treat the most serious injuries.

UNM Health operates New Mexico’s only Level 1 trauma center. These centers treat the most serious and complex injuries. Even a temporary closure can put extra pressure on other hospitals.

UNM Health runs New Mexico’s only Level 1 trauma center. That matters because a Level 1 center handles the most complex injuries, and losing even temporary access to it puts pressure on every nearby hospital.

The organization told patients not to come to its main Albuquerque hospital and canceled appointments across more than 30 clinics.

“The University of New Mexico Health System is experiencing a cybersecurity issue at this time. UNM Health officials are actively working to resolve this issue. Currently, all ambulance traffic is being diverted to other hospitals and all appointments at all clinics today have been cancelled. UNM Health patients should not show up to UNM Health facilities on October 26. Emergencies should be handled by 911 and non-emergencies should be delayed until further notice.” reads the update published by the organization on October 26, 2026. “The cybersecurity threat is affecting the entire University of New Mexico Health Sciences Center. “

UNM said its IT security teams identified the threat around 11 a.m. and began containment work. They later said the event affected some end-user devices but did not reach core systems or servers.

Leadership activated an Emergency Operations Center, brought in outside support, and notified state and federal law enforcement. That is the right sequence: isolate first, investigate second, communicate continuously.

From 12:30 to 2:30 p.m., UN Health temporarily stopped accepting new patients while teams protected the network. “System outages also required the suspension of outpatient surgeries and appointments for the remainder of the day.”

This was not an abstract IT problem. Patients arrived for care and were told to reschedule. Staff had to explain, repeatedly, why a hospital visit could not proceed as planned.

UNM also canceled classes at its Health Sciences Center and sent nonessential employees home. Medical, nursing, pharmacy, and population health students lost a day of instruction because the institution had to protect its network.

Other providers stepped in. Presbyterian Healthcare Services and Lovelace Health System coordinated with UNM and took additional patients, which is exactly what a functioning regional healthcare system should do.

UNM Health began restoring its systems on Monday afternoon. By the following day, hospitals, ambulance services and clinics were back to normal.

The incident is still under criminal investigation. Employees reported messages claiming that patient, student and staff data had been stolen, but UNM has not confirmed this. The hospital also warned people to watch out for phishing and fraud attempts by attackers exploiting the incident.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, UNM Health)

  • ✇Security Affairs
  • Russian APT29 Targets Mobile Users with Watering Hole Attacks Pierluigi Paganini
    Russia-linked group APT29 targeted iOS and Android users through hijacked websites and a compromised analytics service. Sekoia says a large-scale watering hole campaign is going after iOS and Android users, and it links the campaign to APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes), the Russian group tied to the SVR foreign intelligence service. A watering hole is a site that attackers poison so visitors infect themselves. Sekoia found the campaig
     

Russian APT29 Targets Mobile Users with Watering Hole Attacks

5 de Novembro de 2026, 07:00

Russia-linked group APT29 targeted iOS and Android users through hijacked websites and a compromised analytics service.

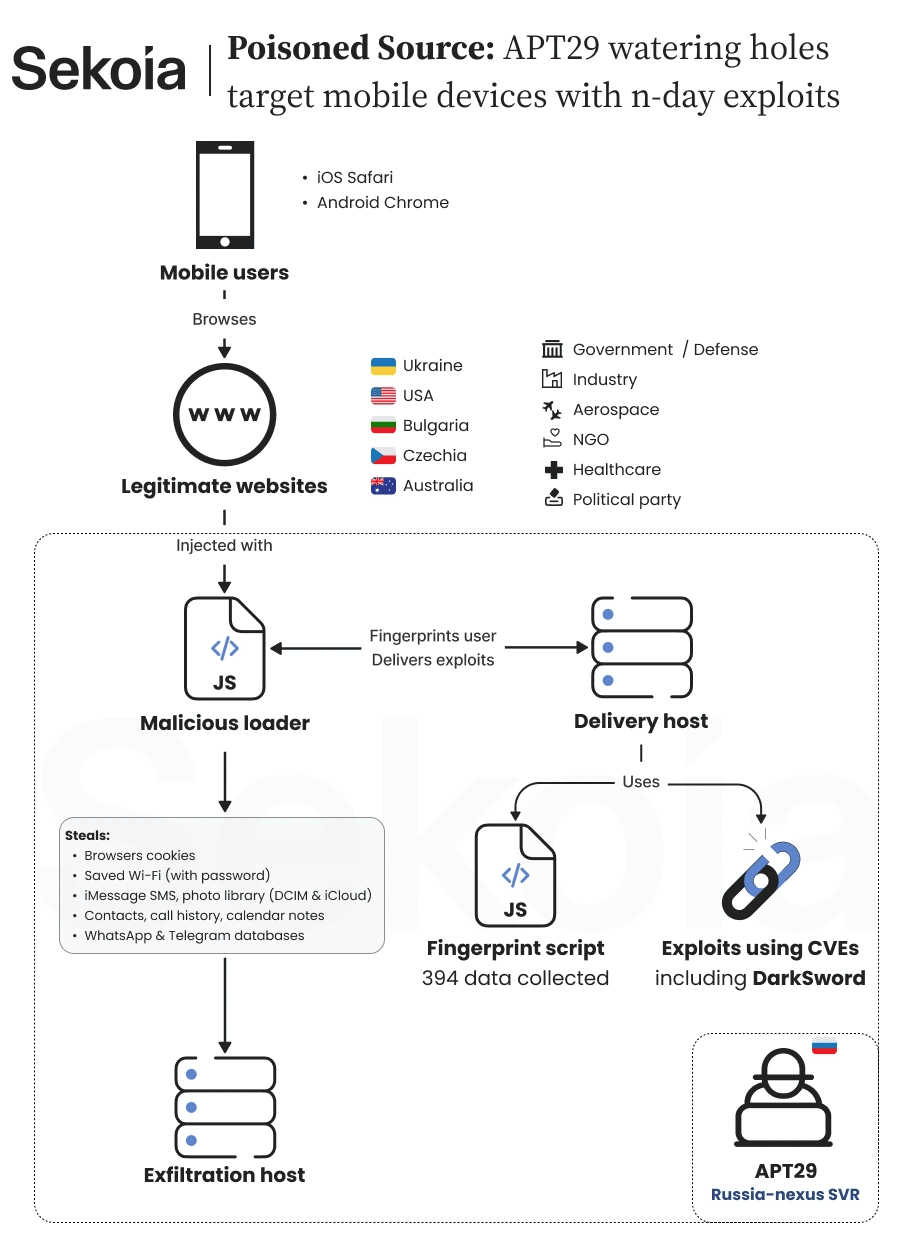
Sekoia says a large-scale watering hole campaign is going after iOS and Android users, and it links the campaign to APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes), the Russian group tied to the SVR foreign intelligence service. A watering hole is a site that attackers poison so visitors infect themselves.

Sekoia found the campaign in mid-October 2026. It involved hacked or cloned high-profile websites in the US, Ukraine, the Czech Republic and Bulgaria. There’s also a supply-chain attack on a Ukrainian web analytics service, Plerdy, loaded by thousands of websites, most of them Ukrainian.

The attackers used three different methods to reach victims, but all led to the same malicious payload. They injected JavaScript into hacked websites, created fake websites that copied legitimate ones and secretly added malicious code, and compromised the Plerdy analytics service to infect websites using its script.

APT29 Watering Hole

Sekoia first spotted the campaign on the website of a Ukrainian gas production company. Other compromised sites included a major US chemical industry association, a European far-right political party and a Bulgarian website linked to the military. In the Bulgarian case, attackers modified an existing JavaScript library without changing the website’s visible pages. Researchers found no clear pattern in the targeted organizations, although they believe some websites may have been selected to reach specific individuals.

Sekoia also identified two fake websites designed to impersonate legitimate services. One copied America250, the US initiative marking the country’s 250th anniversary, while another reproduced the website of Raffles London at The OWO, a luxury hotel close to the UK Ministry of Defence and Downing Street.

“The second website, theowo[.]club, now offline, acted as a reverse proxy for the website of Raffles London at The OWO, a prestigious luxury hotel housed in the historic Old War Office building.” reads the report published by Sekoia. “The hotel’s location is particularly noteworthy because of its proximity to some of the United Kingdom’s most sensitive government institutions, including the Ministry of Defence and 10 Downing Street, the official residence and office of the British Prime Minister.”

The hotel connection is particularly interesting because Ukrainian President Volodymyr Zelensky reportedly stayed there during a visit to London on October 14. Sekoia believes the fake website may have been used to target diplomatic delegations through spear-phishing, but stresses that this remains an unconfirmed possibility.

Between August 27 and September 3, 2026, the attackers compromised the Plerdy tracker at a.plerdy[.]com. For a week, visitors loaded both Plerdy’s script and the attackers’ profiling script. Several affected sites relate to the military and military recruitment, including army, special forces and military equipment websites.

“Between 27 August and 3 September 2026, the intrusion set compromised the Ukrainian Plerdy analytics tracker hosted under the domain a.plerdy[.]com, which is loaded by thousands of websites, the large majority of them Ukrainian.” reads the report. “It remains unclear whether the attackers intended to target visitors to specific websites or sought to compromise as many unpatched mobile devices as possible, indiscriminately exfiltrating data before selectively identifying and exploiting information of interest.”

Sekoia can’t say whether the aim was specific visitors or as many unpatched phones as possible, with the sorting done later. It also considers that the attackers may have used Plerdy after failing to inject code directly into Ukrainian high-value sites that relied on it. The Plerdy payload pointed to a load-balancing domain that sent traffic across several delivery servers.

The profiling script, which the attackers call UltimateFingerprinter, is attached to a minified AngularJS library that makes up 98 percent of a 2.3 MB file. Sekoia thinks that bulk might stop analysis by large language models, or make the script look legitimate. The script runs 61 collectors that build 394 fields, then sends them to a server that decides whether to answer with exploit code.

Strangely, almost none of that data matters. Only implausible screen sizes, like 99999, or a device reporting zero touch points block delivery. Sekoia doesn’t know why the attackers collect so much and sees no sign the data was used later.

Sekoia pulled three exploit chains from the delivery server. Class A hits iOS 16.7 and steals cookies. Class B hits iOS 18.5 and takes full device data. Class C hits Android Chrome versions 139 to 145, minus 143 for reasons Sekoia can’t explain, and steals Chrome cookies and Wi-Fi passwords.

“During the investigation, we tested different browser profiles against the fingerprinting endpoint at static[.]flux-telemetry[.]com in order to retrieve the exploits served to visitors.” states the report. “This allowed us to retrieve three complete exploit chains (afternamed A, B and C), along with their final payloads, targeting both Android and iOS. Here is a summary of what we found:”

Class B is DarkSword, which Sekoia describes as a suspected iOS exploit kit from a commercial surveillance vendor, uploaded to VirusTotal in September 2026. It takes text messages and iMessages, Mail indexes, voicemail, WhatsApp and Telegram databases, Keychain passwords and tokens, account credentials and Wi-Fi keys. It also takes contacts, call history, calendar, notes, Safari history and cookies, location caches, Health data, photos and iCloud Drive.

The Android payload, which Sekoia calls AndroSnitch, collects Chrome cookies, saved logins and history, plus Wi-Fi settings. It stops on one phone model, the Samsung Galaxy S25 Ultra. It resembles a 2024 payload that Google TAG documented, called AndroSnatch, but the sample is too small to prove lineage. The iOS cookie chains set a marker cookie meant to block reinfection for a day, but a coding mistake makes it expire in a minute.

All stolen data goes to ad.starx-net[.]com:8881/telemetry/v12. None of the chains persist on the device. All of them rely on known flaws, and none uses a zero-day.

For attribution, Sekoia has several threads. A CERT said a compromised site’s backend files held traces matching a private report on a 2025 APT29 watering hole campaign, and Google TAG said the framework resembles an APT29 campaign against Mongolian government websites in 2024. Victims also skew to Europe and the US with a focus on Ukraine, infrastructure sits across multiple hosters, and a hacked Czech far-right site fits APT29’s record of targeting European political parties. It rates the link moderate to high confidence, and it’s coordinating with the CERTs of affected countries.

The campaign shows how exploit kits move down the market. Sekoia says state-backed groups keep reusing frameworks from commercial surveillance vendors such as DarkSword, and that packaged exploit chains lower the cost and skill needed for advanced mobile attacks. It expects such reuse to become more frequent.

The good news is that Sekoia’s attackers don’t have fresh tricks. Every flaw was fixed by its vendor before the campaign began, and none works against fully updated devices.

“None of them contain zero-days or work against fully updated devices. Each flaw was resolved by the respective vendor before this campaign began. This operation targets unpatched devices using n-days; a user running an up-to-date operating system is safe from these attacks.” concludes the report.

“This watering hole campaign, which we assess with moderate to high confidence to be linked to APT29, combines multiple web delivery vectors with n-day mobile exploit chains targeting Android and iOS devices. Across the directly compromised websites, no single sectoral targeting pattern emerges from our analysis. While the victimology shows a focus on Ukraine and the United States, the inclusion of unrelated entities such as an Australian medical clinic complicates a broad strategic interpretation. However, we assess that these websites may have been selected to profile and infect specific individuals of interest based on targeting intelligence to which we do not have visibility. The operators adapted by deploying Adversary-in-the-Middle-ish to intercept visitors associated with diplomatic or high-profile events.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, APT29)

  • ✇Security Affairs
  • U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog Pierluigi Paganini
    U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apple flaw, tracked as CVE-2024-27834 (CVSS score of 5.5), to its Known Exploited Vulnerabilities (KEV) catalog. “This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise.” reads the advisory by CISA. CVE-2024-27
     

U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog

5 de Novembro de 2026, 05:55

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple flaw to its Known Exploited Vulnerabilities catalog.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apple flaw, tracked as CVE-2024-27834 (CVSS score of 5.5), to its Known Exploited Vulnerabilities (KEV) catalog.

“This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise.” reads the advisory by CISA.

CVE-2024-27834 is a security vulnerability affecting Apple’s operating systems and Safari. It could allow an attacker who already has arbitrary read and write capabilities on a device to bypass Pointer Authentication (PAC), a hardware-based security mechanism designed to protect memory addresses and prevent certain types of memory-corruption attacks.

Pointer Authentication is a security feature implemented in Apple processors. It adds cryptographic signatures to pointers, helping ensure that memory addresses have not been maliciously modified.

An attacker who gains the ability to read and write arbitrary memory could potentially exploit CVE-2024-27834 to circumvent these protections. This could weaken an important security barrier and make further exploitation of the device easier.

What is the impact?

  • Bypassing Pointer Authentication protections.
  • Weakening defenses against memory-corruption attacks.
  • Potentially facilitating further exploitation when combined with other vulnerabilities.

Apple addressed the vulnerability through improved security checks in:

  • Safari 17.5
  • iOS 16.7.8 and iOS 17.5
  • iPadOS 16.7.8 and iPadOS 17.5
  • macOS Sonoma 14.5
  • tvOS 17.5
  • watchOS 10.5

Cybersecurity firm Sekoia reports on attacks attributed with moderate to high confidence to Russia-linked cyberespionage group APT29. Attackers used compromised websites, fake websites and a supply-chain compromise of Plerdy SEO Tracker to deliver malicious JavaScript. The zero-click exploit chain targeted Safari and Chrome vulnerabilities to bypass security protections and deploy information-stealing malware capable of collecting browser cookies and device data.

“Achieving arbitrary read/write access within the renderer is no longer sufficient for full exploitation on modern Apple silicon. This architecture relies on Pointer Authentication Codes (PAC) to cryptographically sign control-flow pointers. Because of this, even if an attacker can manipulate memory, they cannot simply overwrite a function pointer to hijack the execution flow, triggering an improperly signed pointer will crash the process rather than execute the payload.” Sekoia writes. “To overcome this mitigation and forge the valid pointers required for arbitrary code execution, the exploit chain incorporates a PAC bypass utilizing CVE-2024-27834.”

According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.

Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.

CISA orders federal agencies to fix the flaw by November 18, 2026.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CISA)

  • ✇Security Affairs
  • U.S. Charges Canadian Man in Alleged Hack of University Supercomputers Pierluigi Paganini
    A Canadian man was extradited to the U.S. to face charges over hacking universities and hijacking their computers to mine cryptocurrency. A Canadian man, Ryan James Roach (35), has been extradicted to the United States to face charges tied to a hacking operation that targeted universities and other schools. Roach was extradited on October 28 and now faces federal charges alongside Mathiew James Stubbings, 41, of Ontario. The indictment alleges that, from June 2016 to December 2019, the tw
     

U.S. Charges Canadian Man in Alleged Hack of University Supercomputers

5 de Novembro de 2026, 03:20

A Canadian man was extradited to the U.S. to face charges over hacking universities and hijacking their computers to mine cryptocurrency.

A Canadian man, Ryan James Roach (35), has been extradicted to the United States to face charges tied to a hacking operation that targeted universities and other schools. Roach was extradited on October 28 and now faces federal charges alongside Mathiew James Stubbings, 41, of Ontario.

The indictment alleges that, from June 2016 to December 2019, the two men hacked computers, stole login details, and used victims’ machines to mine cryptocurrency for themselves.

“They used virtual private servers in multiple countries, which were registered under false names. These servers transmitted malware and mining software to victim computers and stored stolen login credentials.” DoJ states. “Victims of the scheme included educational institutions in New York, Tennessee, North Carolina, and Massachusetts. Some of the computers damaged by the defendants were located at an institution of higher learning in the Western District of New York.”

The targets were not random home PCs. Prosecutors say the pair went after U.S. schools with supercomputers, including institutions in New York, Tennessee, North Carolina and Massachusetts. Some affected computers belonged to a higher-education institution in western New York.

“To carry out the scheme, Roach and Stubbings surreptitiously accessed victim computers without authorization, deployed malware to gain control, stole victim login credentials, exfiltrated the data to servers that they controlled, and forcing victim computers to use their processing power to mine cryptocurrency for the financial benefit of the defendants.” DoJ continues.

That is a lot of effort to turn someone else’s research hardware into a personal crypto rig.

The alleged method was also more involved than a single phishing email. The indictment says they looked for weaknesses in victims’ networks, used servers and compromised machines from one victim to hide their tracks, and then moved through the network once inside. The duo used sophisticated techniques and tools to conduct reconnaissance and expand their access within the network.

The charges include conspiracy to obtain information from and damage protected computers, obtaining information from a protected computer, and intentional damage to a protected computer. Each carries up to 10 years in prison and a $250,000 fine. Prosecutors also allege the pair damaged at least 10 protected computers in one year and caused at least $5,000 in losses.

Roach appeared before U.S. Magistrate Judge Mark W. Pedersen and is being held pending a detention hearing. Extradition proceedings for Stubbings continue in Canada. The FBI, the Justice Department’s Computer Crime and Intellectual Property Section, and the Office of International Affairs worked on the case.

For security teams, the useful part is not the alleged crypto-mining. It is the reminder that universities remain attractive targets because they hold powerful computing resources, broad networks, and plenty of people with access. Patch quickly, watch for unusual processing load, and treat credential theft as a serious incident rather than a nuisance.

“The fact that a defendant has been charged with a crime is merely an accusation and the defendant is presumed innocent until and unless proven guilty.” DoJ concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, University Supercomputers)

  • ✇Security Affairs
  • Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released Pierluigi Paganini
    Barracuda patched two flaws that can be chained to give attackers root access to Email Security Gateway appliances. Barracuda has patched two vulnerabilities that can be chained to gain root access to its Email Security Gateway (ESG) appliances. CVE-2026-116606 (CVSS score of 9.3) is an authentication bypass that lets unauthenticated attackers modify appliance configurations. CVE-2026-111560 (CVSS score of 8.6) is a command injection flaw affecting six Barracuda products. An attacker wi
     

Two Barracuda ESG Flaws Could Be Combined for Full Root Access; Patches Released

4 de Novembro de 2026, 18:04

Barracuda patched two flaws that can be chained to give attackers root access to Email Security Gateway appliances.

Barracuda has patched two vulnerabilities that can be chained to gain root access to its Email Security Gateway (ESG) appliances. CVE-2026-116606 (CVSS score of 9.3) is an authentication bypass that lets unauthenticated attackers modify appliance configurations. CVE-2026-111560 (CVSS score of 8.6) is a command injection flaw affecting six Barracuda products.

An attacker with administrator privileges could exploit it to execute operating system commands as root.

“Barracuda has identified two vulnerabilities affecting certain Barracuda products: a pre-authentication authorization bypass vulnerability and a command injection vulnerability. The vulnerabilities have been assigned CVE-2026-116606 and CVE-2026-111560, respectively.” states the advisory. “Successful exploitation requires an attacker to have access to the administrative interface of an affected product. If exploited in combination, these vulnerabilities could allow an attacker to bypass authorization controls and obtain root access to the device.”

Barracuda quickly began fixing the problem and released security patches for affected products. Customers should check the affected products and follow the remediation guidance, make sure their systems use the latest firmware, and install all security patches.

It has released patches and urges customers to update their systems, below are the affected products:

  • Email Security Gateway (ESG) — affected by both vulnerabilities; patch with BNSF-40425 for version 9.4.017 or later, or BNSF-40430 for versions below 9.4.017.
  • Load Balancer Application Delivery Controller (ADC) — affected by CVE-2026-111560; patch with BNADC-16586.
  • Message Archiver (BMA) — affected by CVE-2026-111560; patch with BNMA-32468.
  • WAF Control Center (WCC) — affected by CVE-2026-111560; patch with BNWF-60060.
  • Web Application Firewall (WAF) — affected by CVE-2026-111560; patch with BNADC-16586.
  • Web Security Gateway (WSG) — affected by CVE-2026-111560; patch with BNYF-24789.

The vendor recommends that customers:

  • Restrict administrative interfaces to trusted internal networks and use network access controls to reduce exposure.
  • Check that devices are running the latest firmware and that all security patches are installed.
  • If a device is several versions behind, install updates step by step; more than one update may be needed.
  • Contact Barracuda Support if help is required.

“If a patch has not been automatically applied, customers should manually apply the appropriate patch as soon as possible. If customers have turned off automatic patching, Barracuda recommends setting devices to automatically receive patches.” concludes the advisory.

“Guidance on how to manually apply the patch or update firmware can be found on Barracuda Campus.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Barracuda)

  • ✇Security Affairs
  • Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe Pierluigi Paganini
    Cyberattacks disrupted refrigeration monitoring systems at three French blood banks, amid similar attacks targeting European supermarkets. A cyberattack has hit three regional blood banks in France, disrupting systems used to monitor and control refrigerated storage facilities. The incident took place overnight between Sunday and Monday, at roughly the same time hackers were targeting supermarket refrigeration systems across several European countries. The attack is particularly concernin
     

Cyberattack Hits French Blood Banks as Hackers Target Refrigeration Systems Across Europe

4 de Novembro de 2026, 16:01

Cyberattacks disrupted refrigeration monitoring systems at three French blood banks, amid similar attacks targeting European supermarkets.

A cyberattack has hit three regional blood banks in France, disrupting systems used to monitor and control refrigerated storage facilities. The incident took place overnight between Sunday and Monday, at roughly the same time hackers were targeting supermarket refrigeration systems across several European countries.

The attack is particularly concerning because it targeted infrastructure that plays a direct role in protecting public health. Blood products must remain within specific temperature ranges to preserve their quality and ensure they’re safe for medical use. A disruption to refrigeration systems can therefore have consequences that go well beyond a conventional IT outage.

According to the French Health Ministry, the incident affected several facilities operated by the French Blood Establishment (EFS).

“Several regional facilities ​of the French Blood Establishment (EFS) were affected by a cybersecurity ⁠incident that impacted certain cold storage room monitoring and control systems,” ​the health ministry said in a statement.

“The incident had no impact on blood supplies,” Reuters reported, quoting EFS spokesperson Charley Dubois.

Staff working around the clock received alerts about the problems and moved blood products to refrigerators that weren’t connected to the affected systems. This response helped prevent the incident from disrupting blood supplies, demonstrating how important operational procedures and contingency plans are when technology fails.

“The situation was under control on Wednesday,” the French Health Ministry said, according to Reuters, which also reported that remote access to the affected refrigerators had been disabled.

Investigations are now underway to establish how the attackers gained access, which equipment was affected and when the systems can safely return to normal operation.

The timing is also significant. The French blood bank incident coincided with attacks against supermarket refrigeration systems in eight European countries, including Sweden and Belgium. Those attacks forced retailers to discard large quantities of food after hackers interfered with cooling and freezer systems.

This wasn’t the first time French supermarkets had faced csxk cx incident. In October, police investigated an attack in which hackers allegedly seized control of cooling units at hundreds of supermarkets, causing fires and significant food losses.

These incidents share similarities that deserve attention. They point to a security problem beyond traditional corporate IT systems: the growing exposure of operational technology (OT), including industrial control systems, refrigeration equipment, and the remote management platforms kdch operate them.

These systems are often connected to corporate networks or accessible through remote management services. If attackers compromise those access points, they may be able to interfere with physical processes rather than simply steal information or encrypt business data.

The consequences can be serious. In a supermarket, an attacker who manipulates refrigeration controls can cause food losses and potentially create safety risks. In a blood bank, the same type of interference could threaten the integrity of medical supplies and disrupt services that hospitals depend on.

The French incident didn’t affect blood supplies, but the outcome shouldn’t lead organizations to underestimate the risk. Staff intervention and the availability of independent refrigerators helped contain the damage. Not every facility will have the same resources, response procedures or ability to move critical products at short notice.

Organizations operating critical infrastructure need to treat the security of connected equipment as a core operational requirement. This means identifying exposed systems, restricting remote access, enforcing strong authentication, segmenting operational networks and monitoring changes to equipment settings. They also need tested manual procedures that allow essential services to continue when digital systems become unavailable or untrustworthy.

The European Union has already raised concerns about vulnerabilities in connected infrastructure amid heightened security tensions following Russia’s invasion of Ukraine in 2022. These latest incidents reinforce the need to consider cyberattacks against physical systems as a real operational and public safety risk, not simply an IT problem.

“Investigations are under way into how the attack was carried out, what equipment may have been affected ​and when systems can safely return to service.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, French Blood Banks)

  • ✇Security Affairs
  • CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code Pierluigi Paganini
    Critical Android flaw CVE-2026-58868 could allow remote code execution without user interaction on devices running Android 14 through 17. Google has fixed CVE-2026-58868, a critical Android vulnerability affecting versions 14 through 17. The flaw is a critical Android vulnerability caused by a heap buffer overflow in the onOutputReceived function of FrameDecoder.cpp. The flaw can trigger an out-of-bounds write, potentially allowing a remote attacker to execute arbitrary code on a vulnerable
     

CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code

4 de Novembro de 2026, 07:26

Critical Android flaw CVE-2026-58868 could allow remote code execution without user interaction on devices running Android 14 through 17.

Google has fixed CVE-2026-58868, a critical Android vulnerability affecting versions 14 through 17. The flaw is a critical Android vulnerability caused by a heap buffer overflow in the onOutputReceived function of FrameDecoder.cpp. The flaw can trigger an out-of-bounds write, potentially allowing a remote attacker to execute arbitrary code on a vulnerable device. Exploitation requires neither user interaction nor additional execution privileges, making it a potential zero-click attack.

“cve-2026-58868 In onOutputReceived of FrameDecoder.cpp, there is a possible out-of-bounds write due to a heap buffer overflow.” reads the advisory. “This could lead to remote code execution with no additional execution privileges needed. User interaction is not needed for exploitation.”

Devices receive the fix through security patch level 2026-11-01 or later, depending on manufacturers and carriers. Google is not aware of active exploitation of the flaws in its November 2026 bulletin.

Google’s November 2026 Android security bulletin addresses 216 vulnerabilities, including 23 rated Critical. Two of these flaws, CVE-2026-58876 and CVE-2026-58936, affect the System component and could allow remote code execution without user interaction.

The bulletin also lists five other Critical flaws in the System component. Three could lead to privilege escalation, while two could cause denial-of-service conditions. Another Critical vulnerability affects the Framework component and could also allow remote code execution.

Six Critical vulnerabilities affect the Android kernel. Two involve Bluetooth code, three affect the protected Kernel-based Virtual Machine (pKVM), and one is in the Human Interface Device (HID) component. The most severe kernel flaw could allow a remote attacker to gain elevated privileges without user interaction.

The November 5 patch level also addresses Critical vulnerabilities in MediaTek modem code and a closed-source Qualcomm component. Google’s bulletin lists eight Critical MediaTek modem flaws, while MediaTek’s own November security bulletin details six of them: CVE-2026-20499 and CVE-2026-20545 through CVE-2026-20549.

MediaTek describes these six vulnerabilities as out-of-bounds write flaws caused by missing bounds checks, integer overflow or improper input validation. The company says it is not aware of any active exploitation in the wild.

The Qualcomm issue is tracked as CVE-2026-25285 and affects a closed-source component. Google does not provide further technical details in its bulletin.

One of the critical issues fixed by Google is CVE-2026-58882 (aka SMS of Death), which could allow attackers to remotely disable a phone by sending a specially crafted SMS message. The flaw affects decodeWapPdu, a function responsible for processing WAP Push messages, a type of content delivered through the SMS infrastructure.

The vulnerability is particularly concerning because exploitation reportedly requires no user interaction. An attacker only needs the victim’s phone number to send a malicious message. The message doesn’t appear in the SMS inbox, so the victim may have no indication of what caused the problem.

The issue also raises concerns about the reliability of mobile communications during an attack. According to a technical analysis published on October 29 by security researcher Mark B, a malformed WAP Push message can crash com.android.phone, the Android system component responsible for handling telephony functions. The crash can terminate ongoing calls, including emergency calls.

Tests on several Android phone models reportedly reproduced the crash consistently. The phone can also become stuck in a crash loop because Android retries processing the malicious message whenever the device starts. As a result, the device may continue crashing until the offending message is removed.

There is an important distinction, however. Google’s security bulletin and the CVE record identify the vulnerable decodeWapPdu function, but neither explicitly confirms that CVE-2026-58882 is the same issue described in the researcher’s SMS of Death report. The technical overlap is worth investigating, but the two reports shouldn’t be treated as definitively describing the same vulnerability without further confirmation.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CVE-2026-58868)

❌
❌