❌

Visualização normal

Antes de ontemSecurity Affairs

U.S. CISA adds Linux Kernel and Broadcom VMWare ESX  flaws to its Known Exploited Vulnerabilities catalog

29 de Outubro de 2026, 13:05

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Linux Kernel and Broadcom VMWare ESX flaws to its Known Exploited Vulnerabilities catalog.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Linux Kernel and Broadcom VMWare ESX vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog:

Below are the flaws added to the catalog:

  • CVE-2026-41709 (CVSS score of 7.6) Broadcom VMWare ESX Insufficient Logging Vulnerability
  • CVE-2026-46300 (CVSS score of 2.7) Linux Kernel Missing Initialization of a Variable Vulnerability

In July, Broadcom released patches to address five vulnerabilities affecting VMware ESXi, vCenter, Workstation, and Fusion, including CVE-2026-41709. The vulnerability in VMware ESX is caused by insufficient logging. A malicious user with administrator privileges could perform certain operations on the affected system without those actions being recorded in the logs.

This could allow an attacker to hide specific activities and make it harder for security teams to detect suspicious behavior, investigate incidents, and determine what happened. The flaw does not itself grant administrator privileges; the attacker must already have them.

According to CrowdStrike’s 2026 Legal Threat Landscape Report, which said the China-linked threat actor Warp Panda (aka Armory Castle, UNC5221, Clay Typhoon and VerdantBamboo) exploited CVE-2026-41709 as a zero-day in early 2026 to reduce the visibility of its activities in audit logs.

Warp Panda targets internet-facing edge devices by exploiting zero-day vulnerabilities and deploying custom malware to maintain persistent, covert access. The group also attempts to evade detection by bypassing audit logging, stealing cloud session tokens and registering unauthorized multi-factor authentication (MFA) devices.

The second flaw added to the catalog is CVE-2026-46300, also known as Fragnesia, could let local attackers gain root access through page cache corruption.

The flaw affects the XFRM ESP-in-TCP subsystem and could allow local attackers to gain full root access by corrupting the kernel page cache.

Security experts warn that the issue is dangerous because attackers with low privileges can modify read-only files in memory and take complete control of vulnerable systems. The vulnerability was discovered by William Bowling of the V12 security team, while Wiz published a detailed technical analysis.

“The vulnerability allows unprivileged local attackers to modify read-only file contents in the kernel page cache.” reads the report published by Wiz. “Attackers can then achieve root privileges through deterministic page-cache corruption.”

Fragnesia shares similarities with earlier Linux privilege escalation flaws, such as Dirty Frag and Copy Fail. According to researchers, the bug can reliably provide root access on major Linux distributions without requiring race conditions or complicated timing attacks.

According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.

Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.

CISA orders federal agencies to fix CVE-2026-41709 by November 11, 2026, while CVE-2026-46300, must be fixed by October 31, 2026.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CISA)

CVE-2026-41709

  • ✇Security Affairs
  • North Korea-linked Hackers Hide a Backdoor Inside HAProxy Pierluigi Paganini
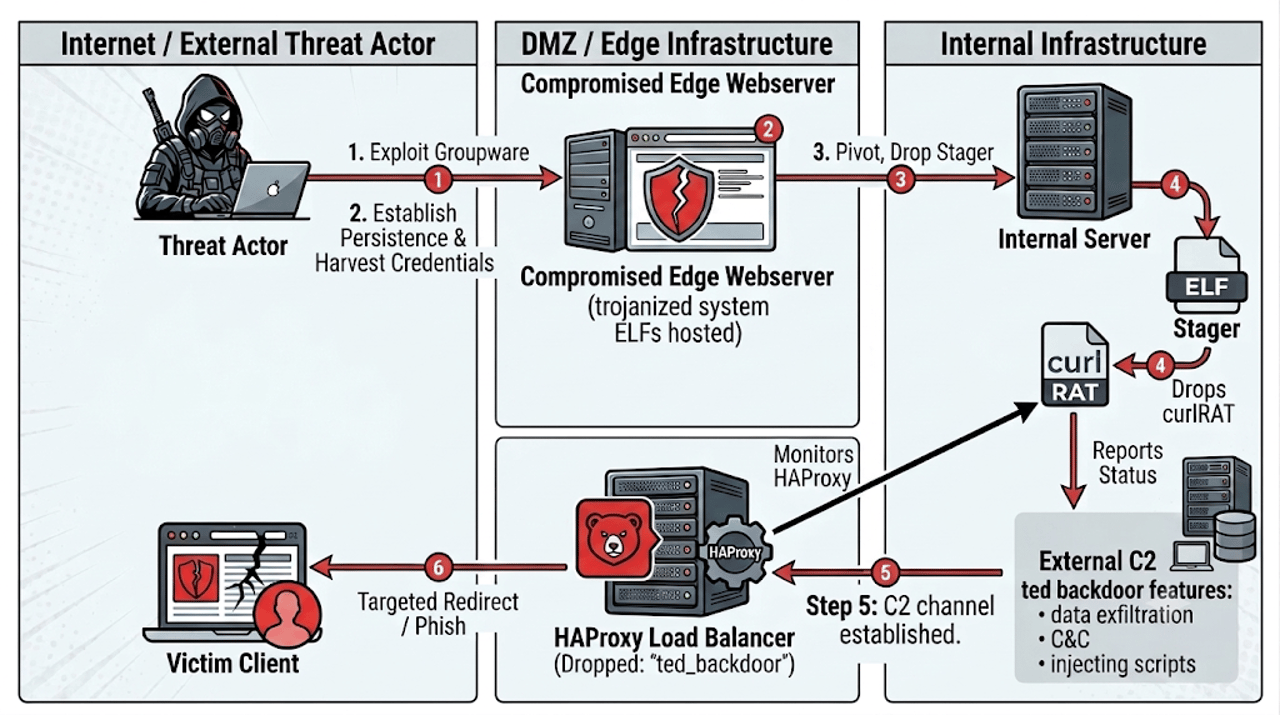
    North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally. North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s research documents a previously undocumented Linux toolkit hitting South Korea’s automotive and media sectors, and the depth of
     

North Korea-linked Hackers Hide a Backdoor Inside HAProxy

8 de Setembro de 2026, 06:11

North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally.

North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s research documents a previously undocumented Linux toolkit hitting South Korea’s automotive and media sectors, and the depth of integration here goes well beyond a typical backdoor bolted onto a system.

“A new Linux toolkit, identified by Rapid7 Labs, has been targeting organizations across South Korea’s automotive and media industries with minimal detection. The campaign made use of a HAProxy instance named “ted backdoor”, alongside trojanized versions of crond, agetty, atd, sshd, and polkitd.” reads the report published by Rapid7. “This previously undocumented framework enabled threat actors to execute remote commands on compromised servers, inject malicious scripts into web traffic, perform credential harvesting, and engage in long-term surveillance.”

The implant, which Rapid7 calls the “ted backdoor” based on debug strings the attackers left behind, isn’t a separate process running alongside HAProxy. It’s compiled directly into HAProxy’s own source code as a custom plugin, using the software’s native filter API, internal memory management, and event scheduler to intercept HTTP traffic while completely legitimate load balancing keeps running normally on top of it.

“The standout feature of this toolkit is its depth of integration with the target environment. The ted backdoor is compiled as part of the victim’s existing HAProxy version 2.8.12.” continues the report. “It uses its native filter API, internal memory pools, event scheduler, and process management infrastructure to intercept traffic and hide from monitoring, while genuine load balancing traffic operates as expected.”

Rapid7 explains, which is really the whole thesis of why this backdoor is so hard to spot: it’s not an addition to the software, it’s woven into it.

The backdoor receives commands through a surprisingly simple trick. The attackers send a request for a fake image at /favorite_list_2x_m500_ico.jpg. This switches the HAProxy filter into command-and-control mode.

The malware then saves the command in a named pipe and removes traces of the request from HAProxy’s internal counters. It also clears the forwarding buffers, so the request never reaches the backend server. The command ends at the load balancer, leaving nothing in the application logs to show that it happened.

This ability to erase its own traces makes the backdoor very different from a normal web shell. The C2 requests never reach the backend server and are also removed from HAProxy’s statistics.

As a result, neither the application logs nor HAProxy’s connection logs show that the attack happened. A security team checking the logs could find nothing suspicious because the backdoor has already erased the evidence.

Beyond remote command execution, the backdoor can quietly inject malicious scripts or entirely swap out page content for specific victims matched by IP address, browser fingerprint, or even a hidden authentication credential smuggled inside the Accept-Language header, effectively turning a company’s own load balancer into a watering hole against its own visitors. It also hooks response bodies carefully enough to hide the size difference caused by injected content, stripping the header that would let a browser notice the byte-range mismatch. That’s a level of protocol-level care that suggests real HAProxy internals expertise, not a quick copy-paste job.

The main backdoor also comes with a separate toolkit that modifies common Linux system daemons such as crond, agetty, atd, and sshd. These programs continue to work normally but also carry malicious features.

One component acts as an SSH keylogger. It captures passwords that administrators enter in plain text and quietly records them. Another tool, called curlRAT, contacts a remote server every 12 hours by default, or every 30 seconds when the attacker enables its fast-poll mode.

curlRAT also checks whether the system runs inside a virtual machine. If it does not find the expected signs, it refuses to run. This behavior suggests the attackers designed the malware to avoid sandboxes and other analysis environments.

Attribution here sits at medium confidence, and Rapid7 is upfront about the limits of what the evidence actually shows. The targeting pattern, simple XOR-based encryption, a custom substitution cipher, and command-server infrastructure already linked to APT37 by other threat intelligence feeds all point toward North Korean state involvement, with some technical overlap also drawing comparisons to a concurrent Lazarus Group campaign against South Korean media sites.

“Further evidence is necessary to make a more definitive assessment. Moreover, the presence of ngx_* prefixed routines within the ted backdoor suggest code reused from an nginx backdoor. The ngx_* prefixed routines were observed during the latest Funnull campaign, where (similar to our case) a custom nginx filter was registered to hook HTTP traffic, and simple XOR encryption was applied to the configuration file.” Rapid7 states. “However, other than a similar naming convention, no significant code-level overlaps exist to support a stronger linkage.”

If your organization runs HAProxy, or really any edge component handling SSL termination and traffic routing, the practical lesson here is uncomfortable but simple: that software deserves the same scrutiny as your actual application servers, not less. The Hacker News confirmed in early September that the specific command domains used in this campaign have already gone dark, returning no DNS records at all, which is useful for reviewing historical logs but does nothing to stop whatever comes next from the same operators. Checking a load balancer’s own logs isn’t enough anymore when the backdoor’s entire design goal is making sure those logs never see it in the first place.

“ted backdoor and curlRAT were designed to persist during long-term espionage operations with the ability to steal cookie sessions, credentials, redirect selected users, conduct drive-by download attacks, and hide evidence of the tampered page to a specific range of IPs to evade detection.” concludes the report. “Defenders should treat any edge component managing user traffic, SSL, or runtime modules with the same strict security standards as their main application servers. Relying on the component’s own logs is not enough; securing these systems requires independent network correlation, memory behavioral analysis, and binary integrity checks.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, North Korea)

❌
❌