❌

Visualização normal

Antes de ontemSecurity Affairs

New wave of fridge cyberattacks hits European supermarkets, this time in Belgium, Luxembourg, Sweden and Estonia

2 de Novembro de 2026, 09:09

A new wave of fridge cyberattacks hit supermarket refrigeration systems across five European countries, raising temperatures and causing food losses.


A new wave of fridge cyberattacks has affected supermarket refrigeration systems in several European countries. Fridges and freezers suddenly rose in temperature overnight, with some incidents suspected to be caused by hackers. On Monday, November 2, Ahold Delhaize and Colruyt reported an IT incident affecting dozens of stores in Belgium and Luxembourg. Swedish supermarket chains ICA and Coop also reported similar problems.

“Ahold Delhaize and Colruyt said on Monday that an IT ​incident overnight hit fridges and freezers in dozens of stores in Belgium and Luxembourg, while Swedish grocers ‌ICA and Coop reported similar temperature spikes, with one store blaming a cyberattack.” Reuters states.

BREAKING: 🇸🇪 Swedish grocery giant ICA, one of Sweden's largest supermarket chains, says several of its stores have been hit by a cyberattack overnight, causing refrigerators and freezers to be remotely set to 50°C.

The incident has likely resulted in large quantities of food… pic.twitter.com/wrcmGHw1qV

— GeoInsider (@InsiderGeo) November 2, 2026

“Problems were discovered at several grocery stores in Sweden overnight Monday.” reported Sweden Herald.

“We are aware that a limited number of stores were affected by an incident overnight that affected their refrigeration and freezer systems. Ica is providing support in handling the incident, Ica Group press officer Gustaf Nilsson tells TT.”

The latest incidents follow a similar wave of fridge cyberattacks in France last month. In mid-October, a large cyberattack hit the refrigeration systems of hundreds of French supermarkets, BFMTV revealed. The attackers targeted equipment from the Danish maker Danfoss that many French stores use to regulate their cold. Fresh and frozen stock was destroyed, and the Paris prosecutor says there were also fires.

The method is simple and nasty. Refrigeration systems have a forced defrost function that clears ice buildup, and the attackers appear to have triggered it remotely in a continuous mode, with a temperature setting of 50 degrees. The equipment heated for several hours instead of keeping goods cold, and when staff opened the fridges and freezers in the morning, a sector source told BFM, “a wave of heat” came out.

The attack caused fires and food losses. However, cybersecurity consultant Emil Olofsson of Integrity 360 told Swedish news agency TT that temperatures reached 80°C in some cases and several units caught fire. This figure differs from the one reported by police.

ICA Kvantum in Sjöbo said on Facebook that a cyberattack caused the refrigeration problems. ICA Hägerstensåsen in Stockholm was also reportedly affected. According to the Sjöbo store, the temperature inside its fridges and freezers rose to 50°C.

In Belgium, Delhaize detected unusual temperature increases in its refrigeration systems on Monday. Spokesperson Sarah De Meester said the company is investigating the incident.

Stephan Moelans, CEO of Sabcobel, the company that manages Delhaize’s refrigeration systems, told news agency Belga that hackers had switched the units’ evaporators to defrost mode. His office declined to comment to Reuters. Colruyt Group, which operates Spar stores in Belgium through a franchise system, said five stores had suffered attacks on their refrigeration systems. Meanwhile, Belgian newspaper Le Soir reported that dozens of Delhaize and Carrefour stores were affected.

🇧🇪🇸🇪 UPDATE: REFRIGERATION DISRUPTIONS SPREAD ACROSS EUROPE – SWEDEN AND BELGIUM AFFECTED

IN SWEDEN:
• At least 6 ICA supermarkets affected by suspected refrigeration system hacks.
• Coop has now CONFIRMED that 6 of its stores in central Sweden are also affected.
• Freezer… https://t.co/a3oGMrGdmz pic.twitter.com/8Q3CFDDLhT

— Coffe Report (@CoffeReport) November 2, 2026

It follows a similar attack in France last month. Police said hackers seized control of the cooling units at hundreds of supermarkets and raised temperatures as high as 50 degrees Celsius (122 Fahrenheit), which caused fires and food losses. Cybersecurity consultant Emil Olofsson of Integrity 360 told TT, Sweden’s news agency, that temperatures there reached 80 degrees and some units caught fire, a figure that differs from the police number.

In Belgium, Delhaize noticed temperature increases in its cooling systems on Monday, spokesperson Sarah De Meester said, and the company is investigating. Stephan Moelans, CEO of the refrigeration firm Sabcobel, which runs Delhaize’s systems, told the news agency Belga it was a cyberattack that switched the units’ evaporators to defrost mode. His office declined to comment to Reuters. Colruyt Group, which runs Spar stores in Belgium under a franchise system, said five shops had their fridge systems attacked, and Le Soir reported that dozens of Delhaize and Carrefour stores were affected.

Ahold also reported a cybersecurity incident to Dutch police last month, after it detected suspicious activity in its infrastructure. Nothing in the reporting ties that report to Monday’s incident.

🇧🇪🧊🇸🇪 Fridges and freezers at dozens of supermarkets in Belgium and Sweden overheated overnight in a suspected cyberattack, similar to the one that hit French stores three weeks ago. Delhaize calls it an "IT incident."

Delhaize said about 40 of its Belgian stores were affected… pic.twitter.com/qzw6uDybWb

— 🔥🗞The Informant (@theinformant_x) November 2, 2026

In Sweden, John Billow, head of the national cybersecurity centre, told Reuters his team was working on several incidents involving refrigeration systems in grocery stores around the country. An ICA Kvantum store in Sjöbo said on Facebook that a cyberattack caused its problems, and an ICA store told its followers that its temperatures had been “hacked” overnight and set to 50 degrees. Fifty degrees is fine for a beach and poor for ice cream. That store later said it had opened.

At ICA Baronen in Stockholm, a notice said all the freezers were broken because of a cyberattack. The sales manager said the attack came at 2 a.m. and staff noticed it at 5:30 a.m. ICA Hägerstensåsen in Stockholm was reportedly hit too.

ICA said only a limited number of stores were affected and that it is helping them deal with the incident. However, press officer Gustaf Nilsson did not say how many stores were involved.

Coop told Swedish news agencies Aftonbladet and TT that six stores in central Sweden had similar problems. Press manager Carlos Cancino said it was still unclear whether any food would need to be thrown away or whether the refrigeration units had simply stopped working or had switched to heating mode. He also did not rule out further incidents affecting other stores.

An Estonian supermarket chain was also affected. Its refrigeration systems were reportedly set to 50°C, technology provider Kitman Coldtech told public broadcaster ERR. CEO Jann Mutso did not reveal the name of the supermarket chain, saying: “This is very recent. It happened this morning.”

How did the attackers get in? In France, Olofsson says they obtained login details for the control systems, which were exposed directly to the internet. He says the attack targeted a product that controls the cooling systems and that the hack isn’t very complicated, so amateurs may have carried it out.

Billow says Swedish authorities have noticed in recent weeks that quite a lot of exposed operational technology devices exist in Sweden, and they’ve been clear that these must be updated or patched.

Refrigerators and heating systems, security cameras and alarm networks were once largely mechanical, and now they can be monitored and controlled remotely. That gives cybercriminals new openings. Authorities haven’t said who was behind last month’s incidents, and nobody has claimed responsibility.


The Sweden Herald reported that the cause of the attacks on Swedish supermarkets remains unknown.

Update 20:00 Rome Time

The company at the center of the European supermarket refrigeration cyberattacks is Danfoss the same company whose refrigeration systems were targeted during the cyberattacks in France a few weeks ago.

Danfoss says the incidents are primarily exploiting vulnerabilities in… pic.twitter.com/3tDNVMOyhn

— GeoInsider (@InsiderGeo) November 2, 2026

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, fridge cyberattacks)

  • ✇Security Affairs
  • Attackers Take Control of Dahua Cameras and Video Recorders Via Easy4IP Pierluigi Paganini
    Ukraine warns that attackers can remotely access Dahua cameras and recorders via Easy4IP, viewing video and changing settings. Ukraine’s cyber incident response team CERT-UA has warned about attackers taking over video surveillance systems made by Dahua. In its alert dated October 23, 2026, it reports unauthorized remote access to IP cameras and video recorders. The attackers have watched the live video, changed device settings and created accounts of their own. The alert doesn’t say who was
     

Attackers Take Control of Dahua Cameras and Video Recorders Via Easy4IP

27 de Outubro de 2026, 06:56

Ukraine warns that attackers can remotely access Dahua cameras and recorders via Easy4IP, viewing video and changing settings.

Ukraine’s cyber incident response team CERT-UA has warned about attackers taking over video surveillance systems made by Dahua. In its alert dated October 23, 2026, it reports unauthorized remote access to IP cameras and video recorders. The attackers have watched the live video, changed device settings and created accounts of their own. The alert doesn’t say who was targeted or how many devices are affected.

The attackers abused Easy4IP, Dahua’s cloud feature that lets users access devices remotely. When this feature is enabled, the camera or recorder connects to Dahua’s cloud and registers using its serial number. Anyone who knows the serial number may be able to access the device through the cloud, without needing an open port or a public IP address. This means the connection can bypass the protection normally provided by a router’s firewall.

As a result, a camera that isn’t directly exposed to the internet may still be at risk. CERT-UA warns that devices with Easy4IP enabled may be vulnerable even when they cannot be accessed directly from the internet.

“The main vector is the P2P/cloud access function (Easy4IP). The device independently initiates an outgoing connection to the manufacturer’s cloud infrastructure and registers in it by serial number. Access to the device is then established via the cloud by serial number, bypassing NAT and firewall, without published ports and a “white” IP address.” reads the report published by CERT-UA. “Thus, the lack of direct access from the Internet does not guarantee the security of the device with the active P2P function.”

Serial numbers follow predictable patterns, so attackers may be able to guess them automatically and check which devices are registered in the cloud. Simply keeping a serial number private isn’t enough to ensure security.

Once attackers connect to a device, they need to get past its login. They may try common or weak passwords or exploit security flaws in outdated firmware, especially CVE-2021-33044 and CVE-2021-33045. These two vulnerabilities allow attackers to bypass authentication without a password, so even a strong password won’t protect a device running vulnerable firmware.

There are three signs that a device may have been compromised. First, look for accounts you don’t recognize. Second, check for changed settings, including text added over the video image. However, the absence of these labels does not mean the device is safe. Third, check the audit logs for logins using Dahua’s DVRIP protocol from the local address 127.0.0.1, which can indicate access through the cloud service.

CERT-UA recommends four steps:

  1. Turn off P2P and cloud access if you don’t use it.
  2. Keep cameras off the internet. For remote access, use a VPN and allow only authorized IP addresses.
  3. Check the account list for ones you didn’t create, and check which cloud accounts are linked to the device and disconnect unknown ones.
  4. Update the software by hand to the latest version, and set up a regular update routine.


CERT-UA advises organizations that detect signs of unauthorized access to report them to cert@cert.gov.ua and check all Dahua devices on their networks, including those that may have been forgotten. The agency warns that all devices with active P2P functionality are at risk.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, IP cameras)

  • ✇Security Affairs
  • Rust-Based CikaBika Bot Turns Discord into a Command Center Pierluigi Paganini
    CikaBika Bot uses fake documents to infect Windows systems, then abuses Discord and Ngrok to execute commands, spy on victims, and steal files. Darktrace researchers have documented a new campaign distributing a remote access trojan called CikaBika Bot, written in Rust and controlled entirely through Discord. The infection chain starts with a disk image that looks like a business proposal, and ends with an attacker who can run arbitrary commands, steal files, and capture your screen, all thr
     

Rust-Based CikaBika Bot Turns Discord into a Command Center

18 de Outubro de 2026, 08:33

CikaBika Bot uses fake documents to infect Windows systems, then abuses Discord and Ngrok to execute commands, spy on victims, and steal files.

Darktrace researchers have documented a new campaign distributing a remote access trojan called CikaBika Bot, written in Rust and controlled entirely through Discord. The infection chain starts with a disk image that looks like a business proposal, and ends with an attacker who can run arbitrary commands, steal files, and capture your screen, all through messages in a chat platform.

“The infection chain begins with a disk image and a malicious Windows shortcut. A Nim loader extracts the final payload and attempts to plant it in Microsoft Edge’s installation directory using a PowerShell UAC bypass.” reads the analysis published by Darktrace. “Once running, the RAT collects host information, registers the device with Discord, and accepts commands through a dedicated channel.”

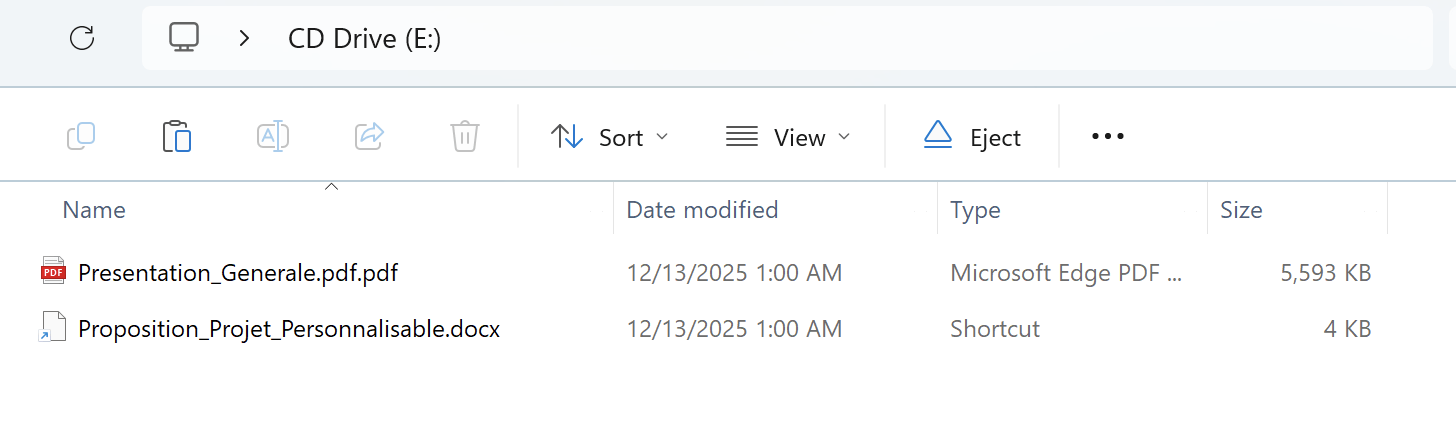
The attackers use a disk image named Proposition_Projet.img as a lure; it contains two files, a PDF that appears to be a legitimate French-language document about writing summaries, and a Windows shortcut disguised as a Word document.

Open the shortcut and a hidden PowerShell process starts running in the background while the PDF displays on screen to keep the victim occupied.

The shortcut starts PowerShell, which reads the fake PDF as raw data. It uses a value hidden inside the file as a key to decrypt and extract a program, then saves it to a temporary folder. This program is a loader written in Nim, a programming language that is less common in malware than C. Attackers may use Nim because security tools are less familiar with it. The loader contains two more components: a Rust DLL and a PowerShell script.

The PowerShell script then tries to copy the DLL into Microsoft Edge’s installation folder and name it dbghelp.dll. This is the name of a legitimate debugging library that Edge normally loads. To access the protected folder without triggering a User Account Control (UAC) prompt, the script changes a Windows registry setting and misuses computerdefaults.exe to bypass the security check. Darktrace describes the technique as DLL search-order hijacking.

“The attacker appears to be exploiting this dependency through DLL search-order hijacking. However, it does not export every function in Edge’s delay-import table, meaning its compatibility with the host is incomplete.” the analysis continues.”The observed code establishes the intended sideloading route, rather than proving that Edge successfully loaded the planted DLL.”

However, the researchers note that the malicious DLL does not provide all the functions Edge expects, so this technique may not work on every system.

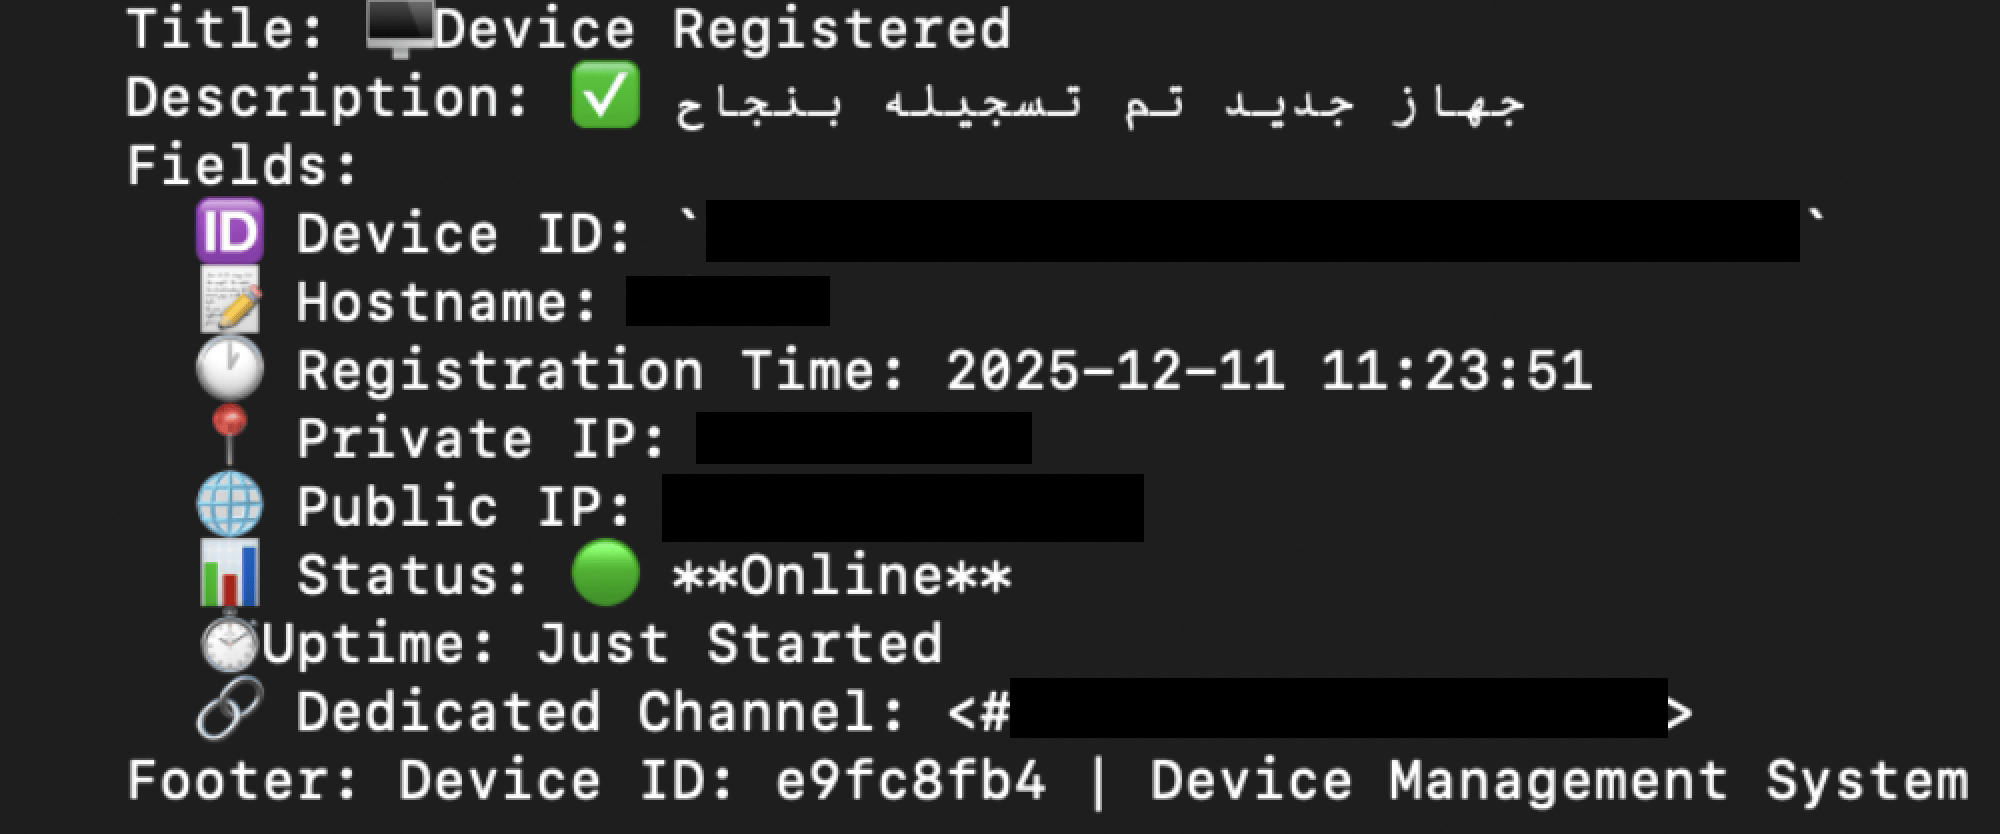
Assuming the implant lands and runs, it immediately registers the infected machine with Discord, creating a dedicated channel for that specific device. It then collects system information, runs tasklist and ipconfig, takes a screenshot, and sends everything back to the operator through that channel. The attacker gets a full picture of the machine within the first few seconds of infection.

The command set from there covers most of what an attacker would need. Remote shell access, process listing and termination, file upload and download, and surveillance functions including screenshot capture, camera access, and screen streaming.

“Once installed, CikaBika Bot uses Discord as its C2 platform, allowing the attacker to manage compromised devices, execute commands, and retrieve files without maintaining dedicated C2 infrastructure.” the cybersecurity firm states. “The observed use of Discord channels for individual victims, alongside additional data exfiltration through ngrok, shows how legitimate services can be repurposed to support malicious operations.”

Discord is a legitimate service used by millions of people and organizations every day. Traffic to Discord doesn’t look unusual on most networks, it’s not blocked by default, and standard endpoint security tools aren’t designed to treat Discord messages as potential command-and-control traffic. The attacker never has to spin up a dedicated server, register a suspicious domain, or deal with infrastructure that can get taken down. They just need a Discord account.


One drawback for attackers is that Discord can detect abuse and shut down the accounts and servers they use. However, creating new accounts is easy and costs very little. The attackers also use Ngrok to transfer files instead of sending large amounts of data through Discord. This reduces their reliance on Discord and limits the impact if the platform shuts down their accounts.

“CikaBika Bot demonstrates how attackers continue to rely on social engineering techniques to deliver malware.” concludes the report. “Although the initial distribution method has not been confirmed, the use of a disk image containing a shortcut disguised as a Word document, alongside a legitimate-looking PDF, suggests the campaign was designed for phishing.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, malware)

  • ✇Security Affairs
  • ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure Pierluigi Paganini
    Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT. FortiGuard Labs researchers spotted a Linux malware family they call ClingSTUN, and the name gives away its trick immediately. Instead of relying on a dedicated command server, the malicious code leans on STUN, the protocol that helps devices behind a router figure out their real public IP address. Video calling apps use it constantly, which means ClingSTUN
     

ClingSTUN Linux Backdoor Abuses Public STUN Infrastructure

6 de Outubro de 2026, 03:31

Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT.

FortiGuard Labs researchers spotted a Linux malware family they call ClingSTUN, and the name gives away its trick immediately. Instead of relying on a dedicated command server, the malicious code leans on STUN, the protocol that helps devices behind a router figure out their real public IP address. Video calling apps use it constantly, which means ClingSTUN’s network traffic hides inside something that already looks completely normal.

“ClingSTUN functions as a back-connect proxy backdoor, turning infected systems into remotely controlled proxy nodes. It abuses public STUN (Session Traversal Utilities for NAT) infrastructure to discover externally mapped IP addresses and ports, maintain NAT bindings, and improve connectivity between compromised hosts and remote operators.” reads the report published by Fortinet. “Because many of the STUN servers it contacts are legitimate public services, the resulting traffic easily blends with normal VoIP and WebRTC communications.”

The attack starts with a familiar problem: old, unpatched devices exposed to the internet. Fortinet first spotted the campaign exploiting a known command injection flaw in Hytec Inter routers. As the campaign evolved, the attackers changed their download infrastructure and expanded the list of vulnerabilities they were exploiting.

In the latest wave, they were targeting devices from more than a dozen vendors, including D-Link, TP-Link, Realtek and Linksys, as well as several DVR and IoT cloud platforms. Many of these devices are easy targets because they are rarely updated or closely monitored.

Once the attackers find a vulnerable device, a small downloader script installs the right malware version for its hardware. It supports common architectures such as ARM, MIPS, PowerPC and Intel.

The latest version also checks the device for other malware before installing itself. It scans mounted filesystems and kills suspicious processes running from temporary directories. In other words, ClingSTUN is not just trying to infect the device. It also tries to remove competing malware and take full control.

The persistence mechanism is almost old-fashioned in its simplicity. The malware copies itself into two separate locations, then appends itself to three different boot scripts so it survives a reboot no matter which startup path the device actually uses. It also walks through every running process, checks whether the command line matches what the process claims to be, and kills anything that doesn’t line up, which is both a defense mechanism and a fairly blunt way of eliminating rival malware fighting for the same compromised box.

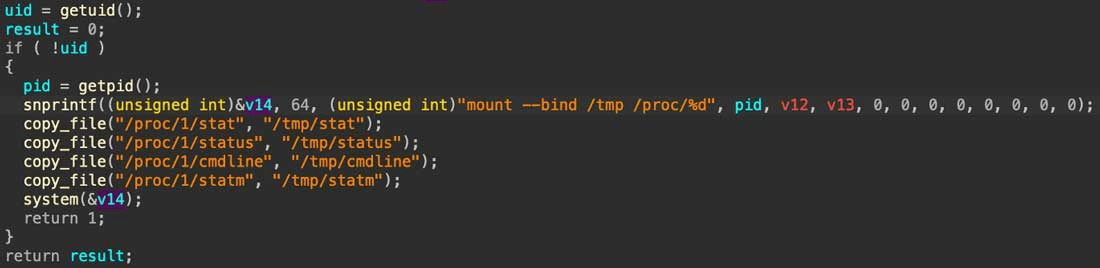
Two details stand out as genuinely well thought through rather than copy-pasted from some other botnet’s source code. First, it opens the device’s watchdog timer and quietly disables it, so the device never auto-reboots itself out of the infection the way embedded hardware is designed to if something goes wrong. Second, once it’s running as root, it swaps its own process metadata for a copy of PID 1’s, the very first process the kernel starts, which makes a basic process listing show what looks like the init system instead of malware.

“After setting up persistence, ClingSTUN clears its original command-line arguments so that its command line appears empty in tools such as “ps.” It then checks whether it is running as root (UID 0).” reads the report. “If so, it copies selected process information files from “/proc/1/” to “/tmp” and bind-mounts “/tmp” over its own “/proc/” directory, concealing its process information behind metadata copied from PID 1.”

The STUN part is especially interesting because it helps ClingSTUN hide in normal network traffic. The malware sends standard requests to public STUN servers to find out its external IP address and port. These are the same services commonly used by VoIP and WebRTC applications.

Later versions reduced the number of STUN servers and required all connections to work, which suggests the attackers were improving reliability. Because the traffic goes to legitimate third-party services, it can be difficult for defenders to tell the difference between ClingSTUN activity and normal traffic from apps such as Zoom.

Command delivery itself still needs a human on the other end willing to send a 20-byte packet the right way.

“ClingSTUN establishes a UDP socket, binds to a random local port, and sends standard 20-byte STUN binding requests. It sends these to 24 public endpoints and ensures at least half succeed.” Fortinet states. “The third evolution reduced this to 13 endpoints and ensures every endpoint connection succeeds.”

A single control datagram can trigger ClingSTUN to open a fresh outbound TCP connection to an address the operator specifies, pull down a command over that connection, and execute it, which keeps the heavy lifting off the STUN channel and limits what shows up in any one place. The malware also carries hardcoded exploits for seven more vulnerabilities purely for spreading itself further, meaning every infected device doubles as a scanner looking for its next host.

Fortinet stresses that the STUN servers are not compromised or malicious. They are simply working as intended. These third-party services should not automatically be treated as attacker-controlled infrastructure.

“ClingSTUN’s exploitation of known, unpatched vulnerabilities reinforces the importance of consistent cyber hygiene.” concludes the report. “Organizations should inventory Internet-facing devices, track their firmware and support status, and promptly apply available security updates, prioritizing vulnerabilities known to be actively exploited.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ClingSTUN)

  • ✇Security Affairs
  • WHIPSHOT and SLAPSHOT: the tools behind an active Citrix NetScaler campaign Pierluigi Paganini
    Mandiant and GTIG detail active exploitation of a Citrix NetScaler zero-day, deploying custom web shells WHIPSHOT and SLAPSHOT for root access. Mandiant and Google Threat Intelligence Group caught active exploitation of a zero-day in Citrix NetScaler ADC and Gateway appliances in late September 2026. The bug, tracked as CVE-2026-88772 (CVSS score of 9.5), has been exploited in attacks in the wild since at least early September, hitting government, financial services, education, and legal ser
     

WHIPSHOT and SLAPSHOT: the tools behind an active Citrix NetScaler campaign

30 de Setembro de 2026, 04:25

Mandiant and GTIG detail active exploitation of a Citrix NetScaler zero-day, deploying custom web shells WHIPSHOT and SLAPSHOT for root access.

Mandiant and Google Threat Intelligence Group caught active exploitation of a zero-day in Citrix NetScaler ADC and Gateway appliances in late September 2026. The bug, tracked as CVE-2026-88772 (CVSS score of 9.5), has been exploited in attacks in the wild since at least early September, hitting government, financial services, education, and legal services organizations across North America and Europe. Citrix disclosed a second zero-day being exploited alongside it, CVE-2026-88771.

CVE-2026-88772 is a memory overflow that can lead to remote code execution or denial of service, and it affects appliances with DTLS enabled. That’s particularly relevant for NetScaler Gateway because DTLS is enabled by default for VPN virtual servers unless an administrator has explicitly disabled it.

The bug is triggered during the appliance’s first handshake, before any login is required. NetScaler’s packet engine processes incoming DTLS traffic to set up the encrypted connection. A specially crafted or fragmented header can corrupt its memory, allowing an attacker to run arbitrary code with root privileges on the underlying FreeBSD system, without needing any credentials.

There are also signs of a successful attack in the logs. You may see an SSL handshake failure using DTLSv1.0 with the message “Handshake failure-Internal Error.” At the same time, the packet engine process crashes and the appliance’s watchdog fails to restart it. If these events happen close together, they could indicate that the exploit was successfully triggered.

“While Google Threat Intelligence Group does not possess exploit code, analysis of frontline telemetry suggests that transmitting specially malformed or fragmented record headers induces heap memory boundary corruption within the packet engine, diverting control flow to execute arbitrary shellcode with root-level operating system privileges on the underlying FreeBSD platform.” reads Google’s report. “Successful exploitation attempts generated two log artifacts:

0-PPE-0 : default SSLLOG SSL_HANDSHAKE_FAILURE 0 : SPCBId - ClientIP - ClientPort - VserverServiceIP - VserverServicePort 443 - ClientVersion DTLSv1.0 - CipherSuite "TLS1-AES-256-CBC-SHA" - Session New - Reason "Handshake failure-Internal Error""

Once inside, the attacker’s first move is installing a web shell, and the installation trick itself is worth appreciating for its pettiness. In some intrusions, the attacker edited the appliance’s Apache config to treat .deb files as executable PHP scripts, then dropped a web shell wearing that fake extension. Nobody expects a Debian package to run code, which is exactly the point.

A stealthier version does the same trick with .sig files instead, and adds a redirect so that a request for a harmless looking .ico icon file actually gets served by the hidden PHP shell. Someone requesting /vpn/media/e6ee7c85.ico unknowingly triggers e6ee7c85.sig. Mandiant even noticed some of these requests returning a normal-looking 404 error while taking unusually long to process, which is the kind of detail that only stands out once you know to look for it.

Getting root access the first time is easy because the exploit already runs with root privileges. To keep that access for future web requests, the installer makes /bin/sh setuid, so commands run through the shell continue to run as root.

It then forces a full reboot of the appliance to make sure the changes stay in place. Simple, effective, and a pretty clever way to make the compromised system keep giving the attacker root access.

The two custom tools doing the real work are called WHIPSHOT and SLAPSHOT, and Mandiant hadn’t seen either before.

“Following successful exploitation, the initial web shell payload self-installs by modifying target httpd.conf files, configuring the system to treat specified non-script file types as executable PHP scripts, setting the stage for the deployment of additional custom malware including WHIPSHOT (a PHP web shell) and SLAPSHOT (a Python proxy/tunneler).” states the report.

WHIPSHOT is the PHP web shell, disguised as a Debian package, that reads commands hidden inside sequential HTTP header fields, decodes them from Base64, and forwards them over a local loopback connection. It also quietly kills its own error reporting and always answers with a 404, so a scan of the web server logs shows nothing unusual on the surface.

SLAPSHOT is what lets the attacker move beyond the compromised appliance. It creates a simple Python proxy that opens a local port and forwards TCP traffic into the internal network.

In one confirmed attack, the attacker used it to explore the network and look for credentials. The connection started from an internet-facing gateway, giving the attacker a tunnel into the internal network.

SLAPSHOT even cleans up after itself if nobody’s using it, closing idle sessions after 15 minutes and shutting itself down entirely after 10 minutes with no activity, deleting its own port and lock files on the way out. That’s not laziness, that’s someone who’s thought about what a forensic analyst would go looking for and decided not to leave it lying around.

This is not a new problem. Edge devices such as VPN gateways, load balancers and firewalls are often targeted because they are exposed to the internet, are usually outside standard endpoint security tools, and may contain credentials that provide access to the internal network.

Mandiant recommends patching to the fixed versions first. Isolating a remote-access gateway can cause major disruption. If patching is not immediately possible, disabling DTLS and blocking inbound UDP/443 can stop this specific attack path, but it does not protect against the second zero-day.

If an appliance may have been compromised, assume that all credentials it handled are exposed. This includes admin accounts, SSH keys, TLS certificates, LDAP and RADIUS credentials, and other secrets used to access internal systems. Rotate them after the appliance has been patched, not before.

“This campaign underscores the continued targeting of edge devices to gain initial access to victim networks, a trend that GTIG has tracked across a range of threat actors. Notably, these vulnerabilities made up about half of the enterprise-related zero-days in 2025.” contludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Citrix NetScaler)

  • ✇Security Affairs
  • Foreign Hackers Target Two Colorado Water Utilities Pierluigi Paganini
    Hackers targeted two Colorado water utilities, changing OT settings and disabling alarms, but causing no impact on water services or safety. Foreign hackers targeted the operational technology (OT) systems of two small private water utilities in Colorado in late August, apparently trying to disrupt operations. Local authorities haven’t identified the affected utilities or the attackers. Attackers reportedly changed equipment settings, disabled remote access and alarms, and modified pumpin
     

Foreign Hackers Target Two Colorado Water Utilities

21 de Setembro de 2026, 15:09

Hackers targeted two Colorado water utilities, changing OT settings and disabling alarms, but causing no impact on water services or safety.

Foreign hackers targeted the operational technology (OT) systems of two small private water utilities in Colorado in late August, apparently trying to disrupt operations. Local authorities haven’t identified the affected utilities or the attackers.

Attackers reportedly changed equipment settings, disabled remote access and alarms, and modified pumping cycles. The incidents were brief and did not affect water services or public safety. The utilities serve fewer than 200 people, and few technical details are available.

The Colorado governor added the attack was carried out by ‘foreign actors’.

“The intrusions did not affect drinking water quality or treatment processes, according to Colorado Gov. Jared Polis’ office. But the incidents add Colorado to a widening series of breaches in U.S. water and wastewater infrastructure.” reported Fox News.

“These two incidents consisted of individuals changing equipment settings, disabling remote access and alarms, and altering pumping cycles,” Polis spokeswoman Ally Sullivan said in a statement. “These were brief incidents, and the risks were quickly addressed by the providers themselves, who subsequently alerted the state.”

“We cannot confirm what foreign actors may have been involved, but we are aware of ongoing efforts across the nation by an Iranian-backed group to access drinking water and wastewater systems, as per the Cybersecurity and Infrastructure Security Agency,” Sullivan wrote in a separate statement.

Despite references to Iran-linked attacks, there is no confirmation that the two Colorado utilities were part of the same campaign that targeted water facilities in at least a dozen US states in July.

Federal authorities have not published a complete list of affected utilities. However, confirmed targets include facilities in Minnesota, Michigan, Alabama, Georgia, New Jersey, South Dakota,and Wisconsin. The available evidence does not currently establish a direct link between those attacks and the Colorado incidents.

The recent attacks have renewed concerns about cybersecurity weaknesses in U.S. water infrastructure, especially at small and rural utilities that often have limited security staff and resources.

In August, CISA urged water utilities to find and secure internet-exposed PLCs after July attacks showed how easily exposed industrial systems can be compromised.

Over 100 internet-exposed systems in the US water and wastewater sector got hit by cyberattacks in July 2026, and CISA’s response wasn’t just an incident report, it was a how-to guide for making sure it doesn’t happen to you next. The agency’s exposure reduction guidance, published August 21, walks through exactly how organizations can find their own internet-facing weak points before an attacker does.

The pattern behind the July attacks was surprisingly simple. Most of the affected systems were programmable logic controllers (PLCs), small industrial computers that control pumps and valves. Many connected directly to cellular modems and had no firewall or gateway between them and the internet. CISA warns that this type of setup can expose PLCs to serious security risks.

“Directly connecting PLCs to the internet through cellular modems can create significant security risks. However, internet exposure reduction does not mean disabling necessary remote access; organizations should remove remote access when it is unnecessary and secure it when it is necessary.” states CISA.

Hackers remotely accessed exposed PLCs, changed device IP addresses and passwords, and in some cases disabled shutdown processes and alarms, creating what CISA called unsafe conditions without notifying the operators running the actual equipment. Iran is the suspected actor behind much of this activity, likely tied to the ongoing war involving the US and Israel, though officials have stopped short of a formal attribution.

Since fiscal year 2025, the EPA has identified more than 900 vulnerabilities across over 650 water systems and helped address about 700 of them at more than 500 utilities. The agency has also carried out more than 710 cybersecurity risk assessments and provided technical support to around 15,900 utilities.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, water utilities)

❌
❌