❌

Visualização normal

Antes de ontemSecurity Affairs
  • ✇Security Affairs
  • ShinyHunters arrest number three: a Canadian ransomware negotiator Pierluigi Paganini
    A Canadian ransomware negotiator faces extortion charges in the FBI’s ShinyHunters crackdown. Here’s what is known, and what isn’t. ShinyHunters is the focus of a global FBI investigation, and the crackdown has led to the October 8 arrest of a Canadian ransomware negotiator who now faces extortion charges. Reuters reported the arrest, citing court documents, prison records and a person familiar with the case. The group has also stolen information about FBI employees. Court documents file
     

ShinyHunters arrest number three: a Canadian ransomware negotiator

12 de Outubro de 2026, 18:26

A Canadian ransomware negotiator faces extortion charges in the FBI’s ShinyHunters crackdown. Here’s what is known, and what isn’t.

ShinyHunters is the focus of a global FBI investigation, and the crackdown has led to the October 8 arrest of a Canadian ransomware negotiator who now faces extortion charges. Reuters reported the arrest, citing court documents, prison records and a person familiar with the case. The group has also stolen information about FBI employees.

Court documents filed in the Eastern District of Pennsylvania, which includes Philadelphia, accuse the defendant of conspiring to threaten the confidentiality of information to extort money and of interfering with commerce.

“A Canadian ransomware negotiator was arrested Thursday and faces unspecified extortion charges, according to court documents, prison records and ​a person familiar with the matter, as the FBI cracks down ‌on a hacking group that stole information about its employees.” Reuters states. “Edward Dubrovsky faces charges of conspiracy to “threaten to impair the confidentiality of information with intent to extort money” and “interference with commerce,” according ​to court documents, opens new tab filed with the Eastern District of Pennsylvania, which covers Philadelphia.”

Krebs on Security reports that the second charge involves threats. The main criminal complaint remains sealed, so the details of the defendant’s alleged role are not yet public.

The records spell the last name two ways, Dobrovsky or Dobrosky, and they don’t list an age, a profession or an employer. A person briefed on the matter told Reuters the defendant is Edward Dubrovsky, a Canadian cybersecurity executive. Reuters couldn’t even settle the spelling, which tells you how early this is.

“Federal court records show that on October 8, an Edward Dobrovsky (note the slight misspelling of the last name) was arrested in Pennsylvania on cyber extortion and conspiracy charges.” states the report. “Several of those documents — including the core complaint — are now sealed. But a handful of them were indexed at Courtlistener.com, including a summary of the complaint, which charges the defendant with “conspiracy to threaten to impair the confidentiality of information with the intent to extort money,” and “interference with commerce by threats.””

Federal prosecutors in Philadelphia didn’t return repeated messages about the discrepancies. Reuters also couldn’t reach Dubrovsky, his lawyers, or CyberSteward, the company named on his LinkedIn profile. According to Krebs, the available records showed no attorney yet.

“An online search reveals the Cyber Risk Summit was held at the Loews Philadelphia Hotel between Oct. 5 and Oct. 7. The conference had several sponsors, but according to the summit’s website its biggest sponsor was a Canadian security company called Cypfer.” states Krebs. “According to LinkedIn, one of Cypfer’s “ex-founders” was Edward Dubrovsky, who is now associated with another Canadian security firm and sponsor called CyberSteward. In a post to LinkedIn approximately one month ago, Dubrovsky said he had plans to attend the Cyber Risk Summit with the rest of the CyberSteward team.”

CyberSteward advertises itself as a specialist in threat actor engagement, cyber extortions, complex negotiations and settlement facilitation. On LinkedIn, Dubrovsky presents himself as an expert in negotiating ransom payments with cybercriminals. SecurityWeek notes he’s also the author of a book on responding to cyber extortion.
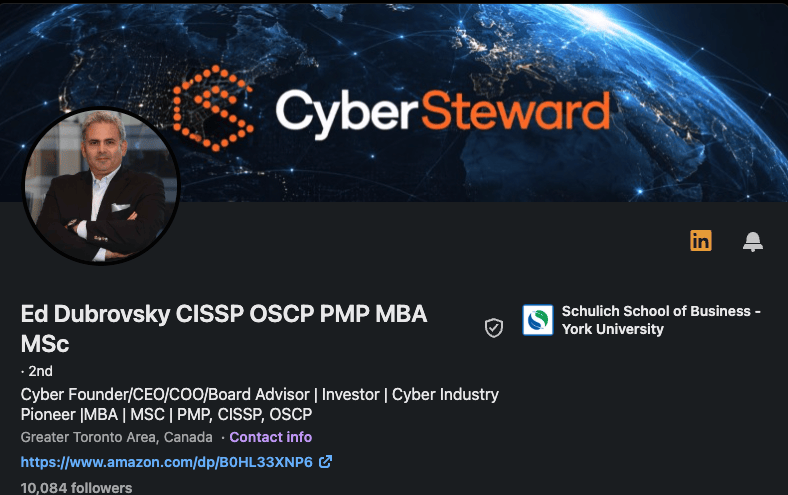
Politico and Krebs reported the arrest first. Krebs says he was in Philadelphia for a cyber insurance conference. Federal prison records show a man with his name detained at a federal detention center in the city.

ShinyHunters is the backdrop. Last month the group claimed it had stolen information on nearly every FBI employee, and it said it got into the bureau’s jobs website and other systems in response to an FBI report earlier this year warning about its activity. FBI blamed the intrusion on a contractor’s failure to patch vulnerable Oracle PeopleSoft software.

When Reuters asked about the arrest, the FBI pointed to a statement from Director Kash Patel and declined further comment.

🚨 Our agents in the field have arrested another suspected co-conspirator of the ShinyHunters group – the group believed to be responsible for the recent https://t.co/RG0D4I5KFS incident, which occurred on a platform managed by a third-party vendor.

This is the latest arrest…

— FBI Director Kash Patel (@FBIDirectorKash) October 9, 2026

Patel described the arrest as the latest in a series of actions against ShinyHunters over just a few days. According to SecurityWeek, he said the FBI will continue working to disrupt the remaining network. This is the third suspected arrest linked to ShinyHunters in recent weeks, following one in the Netherlands on September 15 and another in Jordan on September 28.

The case has also moved to another court. A notice filed on October 9 transferred it to the Eastern District of Texas, where sources told Krebs on Security the FBI’s ShinyHunters investigation is focused.

However, authorities have not publicly explained what the defendant allegedly did. Reuters reports that the charges have not been specified, and the main complaint remains sealed. Krebs on Security also reports, citing sources, that executives at other ransomware negotiation firms could face charges. The FBI says ShinyHunters has extorted more than $70 million this year.

The latest arrest brings the number of suspected ShinyHunters members detained in recent weeks to three. On September 15, authorities arrested a suspected member in the Netherlands. A second alleged key member was reportedly arrested in Jordan on September 28 and is said to be cooperating with the FBI.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ShinyHunters)

  • ✇Security Affairs
  • FBI Drops Accenture Contractor After Sensitive Data Breach Pierluigi Paganini
    Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security. The FBI pulled an Accenture contractor off its account on Monday, and the reason is almost mundane compared to the damage it caused. One update didn’t get installed on time. “The ‌Federal Bureau of Investigation removed an Accenture contractor on Monday over their role in a damaging data breach that exposed sensitive personal details of thousand
     

FBI Drops Accenture Contractor After Sensitive Data Breach

6 de Outubro de 2026, 06:27

Accenture lost an FBI contract after a missed security patch exposed sensitive employee data, raising serious concerns over operational security.

The FBI pulled an Accenture contractor off its account on Monday, and the reason is almost mundane compared to the damage it caused. One update didn’t get installed on time.

“The ‌Federal Bureau of Investigation removed an Accenture contractor on Monday over their role in a damaging data breach that exposed sensitive personal details of thousands of bureau employees, two sources familiar with the matter told Reuters.” Reuters reports. “The development comes as the FBI is still trying to ascertain the ramifications of the breach, ​which some former bureau officials have described as a major blow to the organization’s operational security.”

Two sources told Reuters the bureau cut ties with the contractor over their role in a breach that exposed sensitive personal data on thousands of FBI employees. Former bureau officials are calling it a serious hit to the organization’s operational security, not just an embarrassing headline. That’s a strong statement coming from people who used to run the place.

“To date, our review has determined that the incident occurred as the result of a security failure ​of a platform managed by a third-party organization — after a contractor failed to implement a security patch explicitly issued to secure the ​platform,” FBI cyber chief Brett Leatherman said in the statement to Reuters. “As such, the FBI has removed the contractor and taken all necessary steps to both mitigate any further risk and protect our workforce.”

FBI cyber chief Brett Leatherman laid out exactly what went wrong in a statement to Reuters. The incident traces back to a platform managed by a third party, where a contractor “failed to implement a security patch explicitly issued to secure the platform.” Not an unknown flaw, not a zero day, a fix that already existed and just didn’t get installed.

Reuters’ sources identified the platform as Oracle PeopleSoft, the human resources software running the FBI’s job site, and named Accenture as the third party managing it. Oracle hasn’t responded to requests for comment. Accenture, for its part, said only that it’s proud to support the FBI’s mission and plans to keep doing so, dodging every question about the contractor or the missed patch.

In June, Google warned about a ShinyHunters-linked campaign targeting PeopleSoft users. On the same day, Oracle issued a security alert about the vulnerability and released a fix. Both companies told PeopleSoft customers to install all critical patches and security updates as soon as possible.

ShinyHunters later said they used this same PeopleSoft vulnerability to access the FBI’s job site. Patching large enterprise systems can be difficult, but this wasn’t an unknown or obscure flaw. It had already been publicly identified, attackers were exploiting it, and a fix was available.

In September, the popular cybercrime group ShinyHunters claimed that it breached the U.S. Federal Bureau of Investigation (FBI) and stole sensitive information belonging to FBI employees and job applicants. The group says the operation was not financially motivated and was instead carried out in response to an FBI warning published earlier this year.

The claim surfaced on September 22 and quickly drew attention after ShinyHunters said it obtained data on a large number of current and former FBI personnel. The group reportedly offered a sample of around 5,000 records as evidence and claimed that the stolen information could include names, addresses, phone numbers, Social Security numbers, assignments and, in some cases, family details.

Reuters was able to partially match some of the sample information with other records, including data associated with FBI Director Kash Patel.

“Reuters was able to partially verify the authenticity of the information by running the details, including the Social Security numbers, ​against credit bureau records and previously breached data preserved by the dark-web intelligence firm District 4 Labs.” reads the report published by Reuters. “In at least 10 instances — including in the case ‌of FBI ⁠Director Kash Patel — Reuters found details that appeared to match. A person familiar with the matter said that the job descriptions in the data also matched in at least some cases.”

The FBI acknowledged that it is aware of claims involving unauthorized activity affecting FBIjobs.gov and said it is investigating. The agency has not confirmed that its internal systems were compromised or that ShinyHunters obtained the data it claims to possess.

ShinyHunters provided a possible technical explanation for the alleged intrusion. The group claims the exploitation of an Oracle PeopleSoft zero-day, reportedly using it to gain remote code execution through infrastructure connected to the FBI’s recruitment services.

The attackers also reportedly claimed access to several FBI-related services, including human resources systems and a system they referred to as Medlink. They allegedly said that between 2 TB and 3 TB of data had been taken and that the FBI jobs infrastructure had been compromised.

There is also a clear motive behind the operation claimed by ShinyHunters. The group says it targeted the FBI after a May 2026 public advisory describing its tactics and warning victims against paying. ShinyHunters disputes the FBI’s characterization of its activities and is reportedly demanding that the Bureau retract or correct the warning.

This makes the alleged attack unusual. Instead of immediately demanding a conventional ransom, the group appears to be using the stolen data as leverage in a dispute with U.S. law enforcement.

The timing is also significant. ShinyHunters has recently claimed responsibility for several major breaches and has been involved in a public dispute with the Clop cybercrime operation. The group recently claimed to have compromised Clop’s data leak site, highlighting the increasingly aggressive behavior surrounding the group.

The stolen data is much more sensitive than the usual names and email addresses seen in data breaches. It includes details about named employees’ counterintelligence roles, home addresses of human intelligence operatives, and medical and psychiatric records of FBI staff.

For an agency where some employees depend on keeping their identities, jobs and home addresses private, this goes beyond a normal data breach. It creates a serious operational security risk.

Last week a key ShinyHunters suspect got picked up in Jordan and reportedly started cooperating with investigators, which might help the bureau understand just how bad the damage really is. Removing one contractor doesn’t undo an exposure like this, it just closes the door after the fact.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Accenture)

  • ✇Security Affairs
  • ShinyHunters Suspect Detained in Jordan Helps FBI Track Down the Group Pierluigi Paganini
    A suspected ShinyHunters member arrested in Jordan is reportedly cooperating with the FBI, helping investigators track down the group. A suspected member of ShinyHunters, the group that claims to have stolen data on every FBI employee, was picked up in Jordan this week. The man is Saif al-Din Khader, detained by Jordanian authorities, with two sources placing the arrest on Tuesday. Reuters couldn’t confirm the exact circumstances or where he’s being held. “A suspected member of the S
     

ShinyHunters Suspect Detained in Jordan Helps FBI Track Down the Group

4 de Outubro de 2026, 10:41

A suspected ShinyHunters member arrested in Jordan is reportedly cooperating with the FBI, helping investigators track down the group.

A suspected member of ShinyHunters, the group that claims to have stolen data on every FBI employee, was picked up in Jordan this week.

The man is Saif al-Din Khader, detained by Jordanian authorities, with two sources placing the arrest on Tuesday. Reuters couldn’t confirm the exact circumstances or where he’s being held.

“A suspected member of the ShinyHunters hacking group, which ​says it stole data on every FBI employee, was detained in Jordan this week and is cooperating with the FBI, three people familiar with the matter told Reuters.” the Reuters states.

Two sources said he’s now helping the FBI and international law enforcement track down the rest of the group.

One source told Reuters that Khader is showing investigators his own devices and digital communications to help identify former associates. That gives investigators real access to potential evidence, not just a general promise to cooperate.

“The FBI declined to comment on any specific arrest or activity abroad but said that the bureau “continues to aggressively investigate ​the recent cyber incident allegedly involving ShinyHunters, having already worked with partners to arrest multiple subjects — and we will spare no resource in bringing each of the responsible individuals to justice.”” Reuters continues.

The case matters beyond Khader’s arrest. ShinyHunters claims to have stolen personal data on FBI employees, and Reuters’ earlier analysis found that the leaked sample included detailed personal information, sensitive job-related data, and psychiatric and medical records. Some have compared the incident to the 2015 OPM breach, in which a China-linked attack exposed security clearance data belonging to millions of Americans. If the ShinyHunters claims are even partly confirmed, that comparison would be justified.

Dutch police confirmed this week that the 24-year-old man from Amsterdam was arrested earlier this month as part of an investigation into the cybercrime group ShinyHunters. The suspect appears before Rotterdam District Court today, September 29. Multiple sources, including KrebsOnSecurity, have identified him as Pepijn van der Stap, a Dutch hacker previously known online as “Umbreon.”

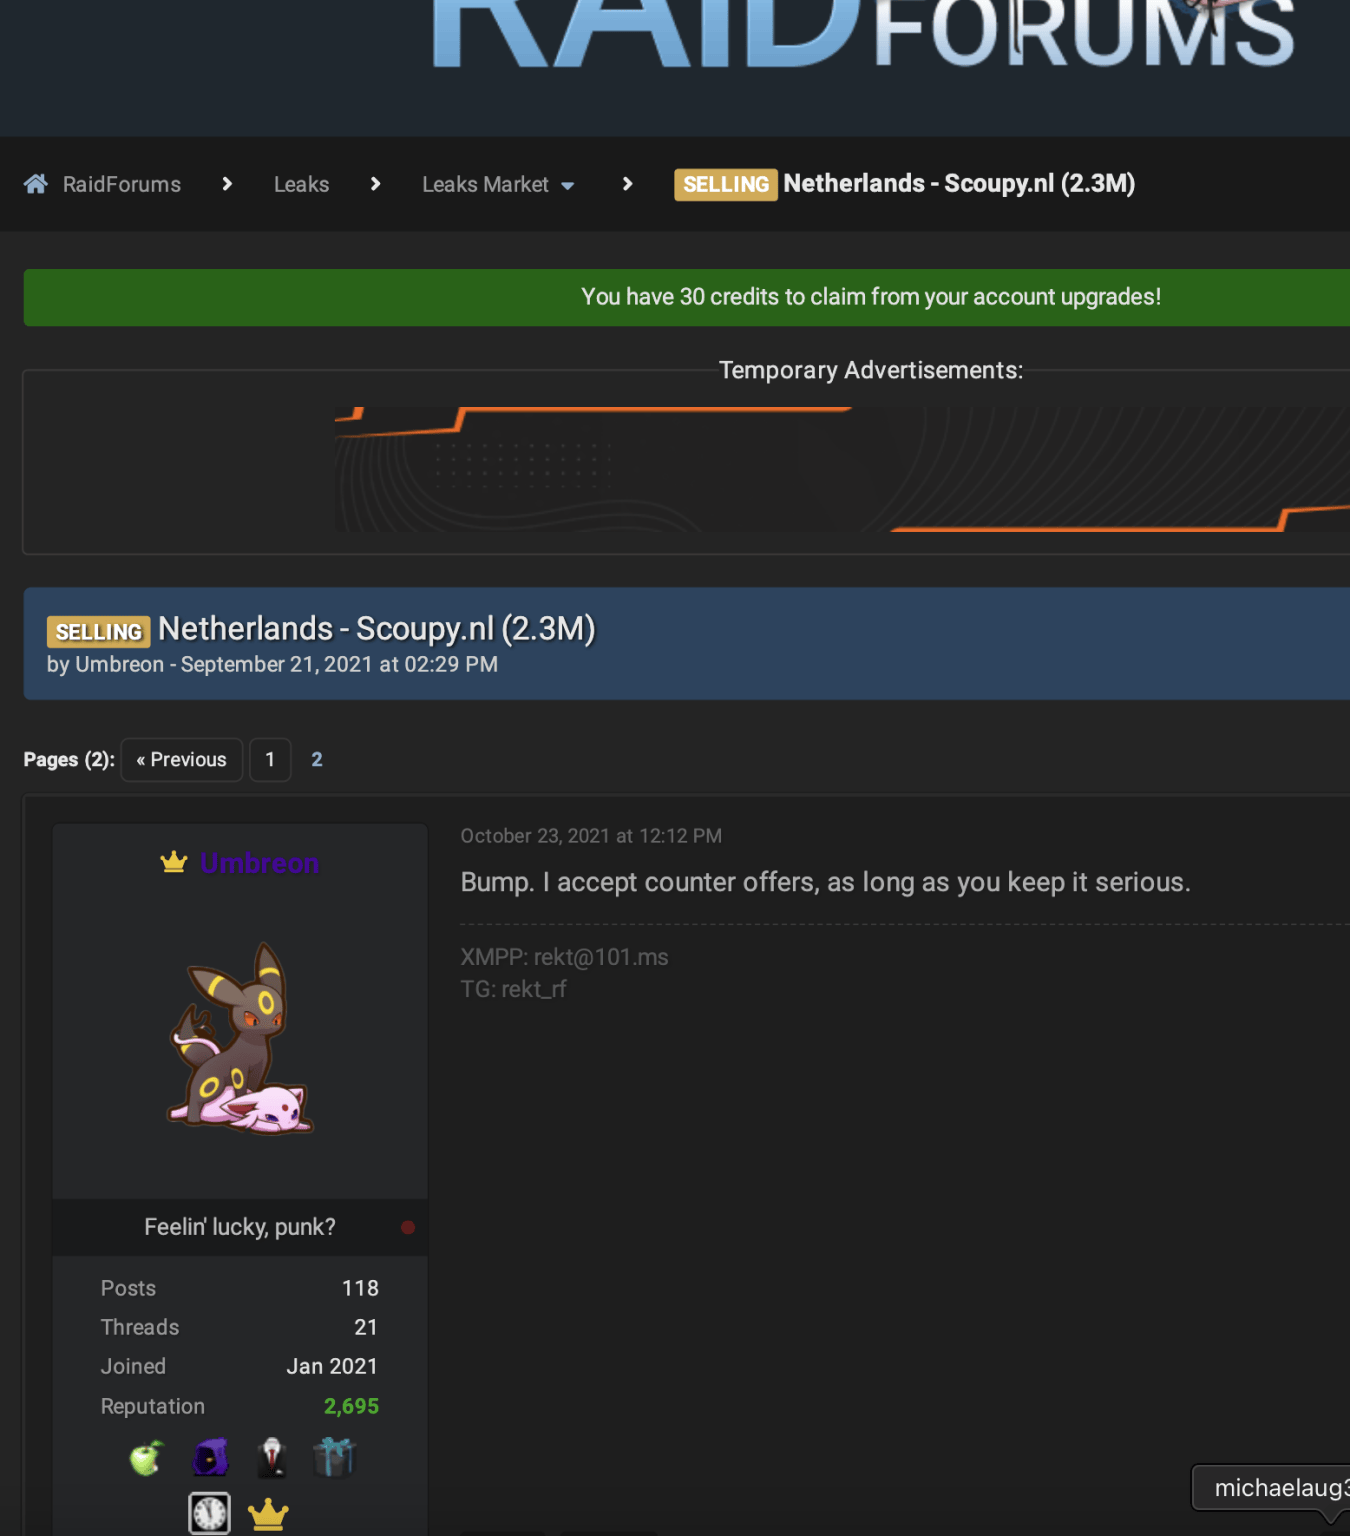
The connection to ShinyHunters runs through the “Umbreon” alias. Van der Stap used that handle and Pokémon imagery on BreachForums as early as 2021.

ShinyHunters
Source KrebsOnSecurity

Then the FBI jobs site defacement that ShinyHunters left after the FBIjobs.gov breach prominently featured an ASCII art version of the same Pokémon character, and the image appears identical to one used in a 2020 HackForums defacement attributed to ShinyHunters, a year before Van der Stap created his Umbreon account. That last detail cuts both ways: either the alias predates him in this context, or the timing coincidence is genuinely awkward. KrebsOnSecurity adds a more pointed interpretation: sources familiar with the investigation say the Umbreon imagery in the FBI defacement may have been a deliberate attempt by ShinyHunters’ current leader, a teenager from Amman, Jordan known as Rey, to pin the hack on Van der Stap. The two reportedly had ongoing bad blood over control of the ShinyHunters brand and data.

FBI Director Kash Patel had already hinted that more arrests were coming.

“FBI teams are working new leads RIGHT NOW. More arrests are on the table.” Patel wrote on X.

NO SAFE HAVEN.

Working with our Dutch National Police partners, the FBI helped put an alleged leader of ShinyHunters—a global cybercrime threat actor—behind bars.

And we’re not done.

FBI teams are working new leads RIGHT NOW. More arrests are on the table.

If you attack… pic.twitter.com/T7CK4KIKl9

— FBI Director Kash Patel (@FBIDirectorKash) September 30, 2026

ShinyHunters’ own infrastructure has been wobbling since this week started. Reuters lost contact with the group’s usual communication account on Tuesday, the same day Khader was reportedly detained, and by Wednesday the group’s dark web leak site had gone offline entirely. The alleged leader of the group, Rey, told journalist Brian Krebs in November 2025 that he’d been quietly cooperating with law enforcement since June, well before any of this became public.

In November 2025, security journalist Brian Krebs reported that Rey was Saif Al-Din Khader after analyzing information obtained from infostealer logs and speaking directly with Khader over Signal.

What is new is what cooperation can look like when someone is in custody. An FBI Cyber Division official explained the situation last week: arrests can make people more willing to talk, while seized servers can reveal information about those who are still outside. Once someone’s laptop becomes evidence, loyalty can disappear very quickly.

A new ShinyHunters leak site reportedly came back online on Thursday, so the group itself isn’t dead, just missing one more member.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ShinyHunters )

  • ✇Security Affairs
  • 24-Year-Old Arrested in Dutch Investigation Into ShinyHunters Pierluigi Paganini
    Dutch police confirm the arrest of a 24-year-old Amsterdam man as part of an investigation into the ShinyHunters hacking group. Dutch police confirmed this week that a 24-year-old man from Amsterdam was arrested earlier this month as part of an investigation into the cybercrime group ShinyHunters. The suspect appears before Rotterdam District Court today, September 29. Multiple sources, including KrebsOnSecurity, have identified him as Pepijn van der Stap, a Dutch hacker previously known onl
     

24-Year-Old Arrested in Dutch Investigation Into ShinyHunters

29 de Setembro de 2026, 04:30

Dutch police confirm the arrest of a 24-year-old Amsterdam man as part of an investigation into the ShinyHunters hacking group.

Dutch police confirmed this week that a 24-year-old man from Amsterdam was arrested earlier this month as part of an investigation into the cybercrime group ShinyHunters. The suspect appears before Rotterdam District Court today, September 29. Multiple sources, including KrebsOnSecurity, have identified him as Pepijn van der Stap, a Dutch hacker previously known online as “Umbreon.”

“According to three sources familiar with the matter, the Dutch man arrested by authorities this month is Pepijn van der Stap, a convicted cybercriminal from Almere and Lelystad in the Netherlands. Van der Stap was previously convicted in 2023 in connection with a string of data thefts and extortions that prosecutors said earned between €1.5 million and €2.7 million.” states KrebsOnSecurity. “At his trial in late 2023, van der Stap admitted that he lived a Dr. Jekyll and Mr. Hyde existence, secretly using the hacker handle “Umbreon” to extort victims and post their data on English language hacking communities like the now-defunct RaidForums and Breached. By day, however, van der Stap was working as a software engineer at the Amsterdam-based cybersecurity startup Hadrian, while volunteering at the Dutch Institute for Vulnerability Disclosure (DIVD), a nonprofit security research group.”

Het klopt dat er deze maand een 24-jarige man uit Amsterdam is aangehouden in een onderzoek naar de hackersgroep ShinyHunters. Op dinsdag 29 september staat de man voor de raadkamer van de rechtbank Rotterdam. Morgen komen wij met meer info.

— Politie Landelijke Opsporing en Interventies (@Pol_Ops_Int) September 28, 2026

This isn’t Van der Stap’s first time facing charges for hacking. He was arrested in January 2023 and accused of hacking and blackmailing more than a dozen companies in the Netherlands and abroad. He later pleaded guilty and was sentenced to four years in prison, with one year suspended, followed by three years of probation.

He was released in December 2025 and later worked as an offensive security lead at Dutch company Neo Security. At the same time, he was still facing civil lawsuits from some of his previous victims.

KrebsOnSecurity spoke with him on September 9, 2026. He described himself as a reformed hacker trying to make amends. He stopped responding to messages soon after. On September 15, Dutch police searched the Amsterdam home he shared with his mother and seized several electronic devices.

The connection to ShinyHunters runs through the “Umbreon” alias. Van der Stap used that handle and Pokémon imagery on BreachForums as early as 2021.

ShinyHunters
Source KrebsOnSecurity

Then the FBI jobs site defacement that ShinyHunters left after the FBIjobs.gov breach prominently featured an ASCII art version of the same Pokémon character, and the image appears identical to one used in a 2020 HackForums defacement attributed to ShinyHunters, a year before Van der Stap created his Umbreon account. That last detail cuts both ways: either the alias predates him in this context, or the timing coincidence is genuinely awkward. KrebsOnSecurity adds a more pointed interpretation: sources familiar with the investigation say the Umbreon imagery in the FBI defacement may have been a deliberate attempt by ShinyHunters’ current leader, a teenager from Amman, Jordan known as Rey, to pin the hack on Van der Stap. The two reportedly had ongoing bad blood over control of the ShinyHunters brand and data.

“Multiple sources close to the ShinyHunters investigation said the group’s recent risky attacks against the FBI and one of Russia’s most venerated ransomware groups amounted to a major pivot away from the more measured tenor of the hacking gang’s operations.” continues Krebs. “Those sources said the sudden shift came about after ShinyHunters was taken over by a teenage cybercriminal from Amman, Jordan who goes by the nickname Rey and operates as part of a cybercrime group called ScatteredLapsussHunters (SLSH), which experts say is an amalgamation of three hacking groups — Scattered Spider, LAPSUS$ and ShinyHunters.”

The ShinyHunters picture has gotten considerably more complicated. According to Krebs, the group was effectively taken over by Rey, who operates as part of a hybrid crew called ScatteredLapsussHunters, combining elements of Scattered Spider, LAPSUS$, and ShinyHunters. The FBI breach, the extortion attempt against Russian ransomware group Cl0p, and the overall escalation in aggressive behavior all followed Van der Stap’s arrest, which sources described as a major pivot from how the group had been operating. Mandiant told Krebs that ShinyHunters is on track to collect nearly $100 million in extortion payments in 2026 alone.

Dutch police were already investigating a separate incident linked to the ShinyHunters group. The group had breached Odido, the Netherlands’ largest mobile carrier, by tricking an employee into entering their credentials on a fake login page during a phone call. The attack exposed data relating to more than 6.2 million Dutch people.

Police later released a recording of the caller and asked the public to help identify the voice. ShinyHunters confirmed that the voice belonged to one of its members and said it would provide full support, including a criminal defense lawyer.

However, DataBreaches, which had spoken with Van der Stap several times, said the voice did not sound like him. A close friend reportedly reached the same conclusion.

“The one audio clip the police revealed following the Odido hack by ShinyHunters did not sound like van der Stap, whom we have spoken with on the phone numerous times. A close friend of his also said the audio clip of the Odido hacker connected to ShinyHunters was not van der Stap’s voice.” states DataBreaches. “There is no doubt ShinyHunters is linked to the Odido hack, but no evidence has been presented (or even charges at this point) linking van der Stap to that incident.”

Whether that’s true or a calculated deflection is exactly what the Rotterdam District Court is now beginning to work out.

One thread worth following separately: DIVD, the Dutch nonprofit security research group where Van der Stap had previously volunteered, disclosed last week that it was dealing with an internal security incident involving apparent malicious use of AI. The organization said it doesn’t appear related to ShinyHunters and shows no signs of involving a former volunteer, but the timing, arriving alongside Van der Stap’s arrest and the group’s escalating activity, means nobody’s treating that as a coincidence until the facts say otherwise.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, cybercrime)

  • ✇Security Affairs
  • ShinyHunters claims FBI breach after alleged PeopleSoft zero-day attack Pierluigi Paganini
    ShinyHunters claims FBI breach via PeopleSoft zero-day, steals staff data; FBI investigating, no confirmation yet. The popular cybercrime group ShinyHunters is claiming that it breached the U.S. Federal Bureau of Investigation (FBI) and stole sensitive information belonging to FBI employees and job applicants. The group says the operation was not financially motivated and was instead carried out in response to an FBI warning published earlier this year. The claim surfaced on September 22
     

ShinyHunters claims FBI breach after alleged PeopleSoft zero-day attack

23 de Setembro de 2026, 10:56

ShinyHunters claims FBI breach via PeopleSoft zero-day, steals staff data; FBI investigating, no confirmation yet.

The popular cybercrime group ShinyHunters is claiming that it breached the U.S. Federal Bureau of Investigation (FBI) and stole sensitive information belonging to FBI employees and job applicants. The group says the operation was not financially motivated and was instead carried out in response to an FBI warning published earlier this year.

The claim surfaced on September 22 and quickly drew attention after ShinyHunters said it had obtained data on a large number of current and former FBI personnel. The group reportedly offered a sample of around 5,000 records as evidence and claimed that the stolen information could include names, addresses, phone numbers, Social Security numbers, assignments and, in some cases, family details.

Reuters was able to partially match some of the sample information with other records, including data associated with FBI Director Kash Patel. However, the news agency could not determine where the information originally came from or independently confirm that it had been stolen from FBI systems.

“Reuters was able to partially verify the authenticity of the information by running the details, including the Social Security numbers, ​against credit bureau records and previously breached data preserved by the dark-web intelligence firm District 4 Labs.” reads the report published by Reuters. “In at least 10 instances — including in the case ‌of FBI ⁠Director Kash Patel — Reuters found details that appeared to match. A person familiar with the matter said that the job descriptions in the data also matched in at least some cases.”

The FBI has acknowledged that it is aware of claims involving unauthorized activity affecting FBIjobs.gov and said it is investigating. The agency has not confirmed that its internal systems were compromised or that ShinyHunters obtained the data it claims to possess.

ShinyHunters has provided a possible technical explanation for the alleged intrusion. The group claims the exploitation of an Oracle PeopleSoft zero-day, reportedly using it to gain remote code execution through infrastructure connected to the FBI’s recruitment services.

The claim is notable because ShinyHunters has already been linked to attacks exploiting a real PeopleSoft zero-day earlier this year. In June, Oracle addressed CVE-2026-35273, a critical unauthenticated remote code execution vulnerability in PeopleSoft PeopleTools. Google and Mandiant later linked exploitation of that flaw to ShinyHunters activity targeting organizations, particularly in the education sector.

That history makes the latest claim technically plausible, but it does not prove that the same group used another PeopleSoft zero-day against the FBI. No public CVE or vendor confirmation currently exists for the alleged new vulnerability.

The attackers also reportedly claimed access to several FBI-related services, including human resources systems and a system they referred to as Medlink. They allegedly said that between 2 TB and 3 TB of data had been taken and that the FBI jobs infrastructure had been compromised.

Reuters and other media outlets confirmed the recruitment website did experience disruption around the time of the claim. A page that had reportedly been defaced by the attackers later displayed a scheduled-maintenance message. That disruption could be consistent with an intrusion, but it is not by itself proof that the wider FBI systems were breached.

There is also a clear motive behind the operation claimed by ShinyHunters. The group says it targeted the FBI after a May 2026 public advisory describing its tactics and warning victims against paying. ShinyHunters disputes the FBI’s characterization of its activities and is reportedly demanding that the Bureau retract or correct the warning.

This makes the alleged attack unusual. Instead of immediately demanding a conventional ransom, the group appears to be using the stolen data as leverage in a dispute with U.S. law enforcement.

The timing is also significant. ShinyHunters has recently claimed responsibility for several major breaches and has been involved in a public dispute with the Clop cybercrime operation. The group recently claimed to have compromised Clop’s data leak site, highlighting the increasingly aggressive behavior surrounding the group.

For now, however, the FBI investigation remains the missing piece. Until investigators confirm the intrusion, the extent of access and the origin of the leaked records, the ShinyHunters account should remain a claim rather than an established FBI breach.

What is already clear is that the incident would be serious if confirmed. Personal information belonging to law enforcement personnel could expose agents and their families to targeted harassment, social engineering and other forms of abuse. But the available evidence does not yet allow those consequences to be attributed to a confirmed compromise of FBI internal systems.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, FBI)

❌
❌