❌

Visualização normal

Ontem — 7 de Novembro de 2026Security Affairs
  • ✇Security Affairs
  • White House Network Appears in Global Residential Proxy Traffic Pierluigi Paganini
    Layer3 found residential proxy traffic using the White House network, raising concerns about potential exposure of internal systems. Layer3 Intel says it found residential proxy traffic leaving through the White House network. The researchers spotted it while browsing their new Residential Proxy Observatory, a tool that gives a global view of residential proxy and anonymized internet activity. “While our team was looking through it, we noticed residential proxy exit activity on AS2650. A
     

White House Network Appears in Global Residential Proxy Traffic

6 de Novembro de 2026, 19:17

Layer3 found residential proxy traffic using the White House network, raising concerns about potential exposure of internal systems.

Layer3 Intel says it found residential proxy traffic leaving through the White House network. The researchers spotted it while browsing their new Residential Proxy Observatory, a tool that gives a global view of residential proxy and anonymized internet activity.

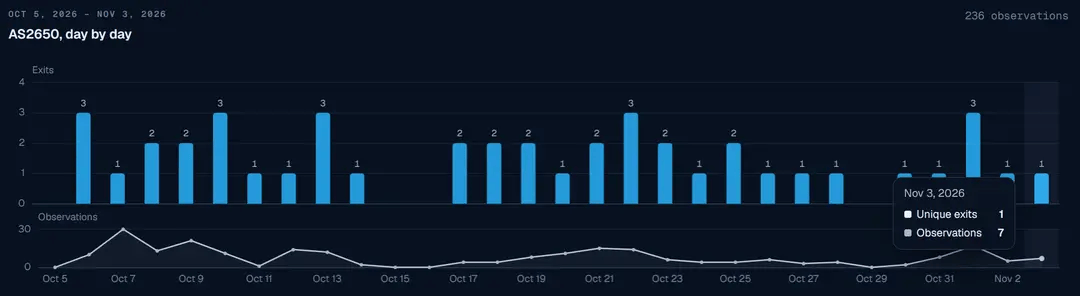
“While our team was looking through it, we noticed residential proxy exit activity on AS2650. AS2650 is registered to the Executive Office of the President, the federal agency that hosts the White House network.” reads the report published by Layer3.

A residential proxy service allows customers to use everyday devices to route their internet traffic. This makes their activity look as if it comes from the device’s normal home internet connection. Layer3 detected this activity on AS2650, a network registered to the Executive Office of the President, the agency responsible for the White House network. Layer3 has not accused anyone at the White House of wrongdoing and says its data cannot identify who or what caused the activity.

Between October 5 and November 3, Layer3 detected 236 connections through this network. The traffic came from six IP addresses and was recorded on 26 of those 30 days. A total of 28 residential proxy services were able to use the network. To check their findings, researchers compared the IP addresses with data from other security services, including Spur and Synthient. Both services also identify these addresses as residential proxy exit points.

proxy traffic using the White House network

Getting this data took no special skill. Anyone can sign up to a public residential proxy service, pay a few dollars and send requests through it. Layer3 says it didn’t target the network or try to steer its probes there, and it caught the activity by chance, simply by requesting global rotating access through these services.

The timing suggests something more than a guest network. About half the activity falls between 5 p.m. and midnight Eastern time, and almost none happens in the early morning. Layer3 reads that as a person, not public guest Wi-Fi: someone regularly on the White House network late into the evening whose device carries a proxy SDK, a software kit that turns a device into an exit point.

“Past research has shown that poorly secured proxy SDKs can allow internal network access and lateral movement. This is how past botnets have spread. In A Broken System Fueling Botnets, the researchers at Synthient documented how the Kimwolf botnet reached at least 2 million devices, mostly Android devices with an exposed ADB service, through residential proxy networks.” continues the report. “If an SDK on this network has the same kind of flaw, anyone buying proxy access could use it to reach internal systems.”

That matters because poorly secured proxy SDKs have let attackers into internal networks before. Synthient’s research, A Broken System Fueling Botnets, documented how the Kimwolf botnet reached at least 2 million devices, mostly Android devices with an exposed ADB service, through residential proxy networks. If an SDK on the White House network has the same kind of flaw, anyone buying proxy access could reach internal systems. Layer3 doesn’t claim that’s the case here, and it describes the risk as conditional.

The White House isn’t the only surprise. The observatory also finds residential proxies in some of the most isolated places on the planet. Saint Helena, Ascension and Tristan da Cunha, a South Atlantic territory that includes the most remote inhabited island in the world, shows 413 addresses and more than 32,000 observations, split between Starlink and the local provider, Sure Saint Helena.

Layer3 also detected three instances of proxy activity in Antarctica. All came from a Cloudflare WARP address linked to McMurdo Station. The researchers jokingly noted that penguins are not suspects. On Pitcairn Island, they found one Starlink address and one observation. Norfolk Island had one Norfolk Telecom address with four observations, while Svalbard had one Starlink address in Longyearbyen with three observations.

The researchers also found 388 addresses in the Falkland Islands, 43 in the Chagos Islands, 21 in Tokelau and seven in South Georgia. These findings suggest that residential proxy networks now operate in almost every corner of the world. For security teams, the main concern is that devices connected to protected networks could unknowingly become proxy exit points, potentially exposing those networks to outside traffic.

However, Layer3 says its data only shows where proxy traffic exits. It cannot identify the device being used or the person behind it. As the company explains, “Our data shows the exits, not the device or the person behind them.”

“Residential proxies have infected every corner of the world, and it looks like there is no place they cannot reach. Layer3 Intel tracks residential proxy and anonymization infrastructure worldwide. Even when the proxies hide in networks on the farthest corners of the planet, we can still observe them, leaving threat actors no place to hide.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, proxy traffic)

Antes de ontemSecurity Affairs
  • ✇Security Affairs
  • Russian APT29 Targets Mobile Users with Watering Hole Attacks Pierluigi Paganini
    Russia-linked group APT29 targeted iOS and Android users through hijacked websites and a compromised analytics service. Sekoia says a large-scale watering hole campaign is going after iOS and Android users, and it links the campaign to APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes), the Russian group tied to the SVR foreign intelligence service. A watering hole is a site that attackers poison so visitors infect themselves. Sekoia found the campaig
     

Russian APT29 Targets Mobile Users with Watering Hole Attacks

5 de Novembro de 2026, 07:00

Russia-linked group APT29 targeted iOS and Android users through hijacked websites and a compromised analytics service.

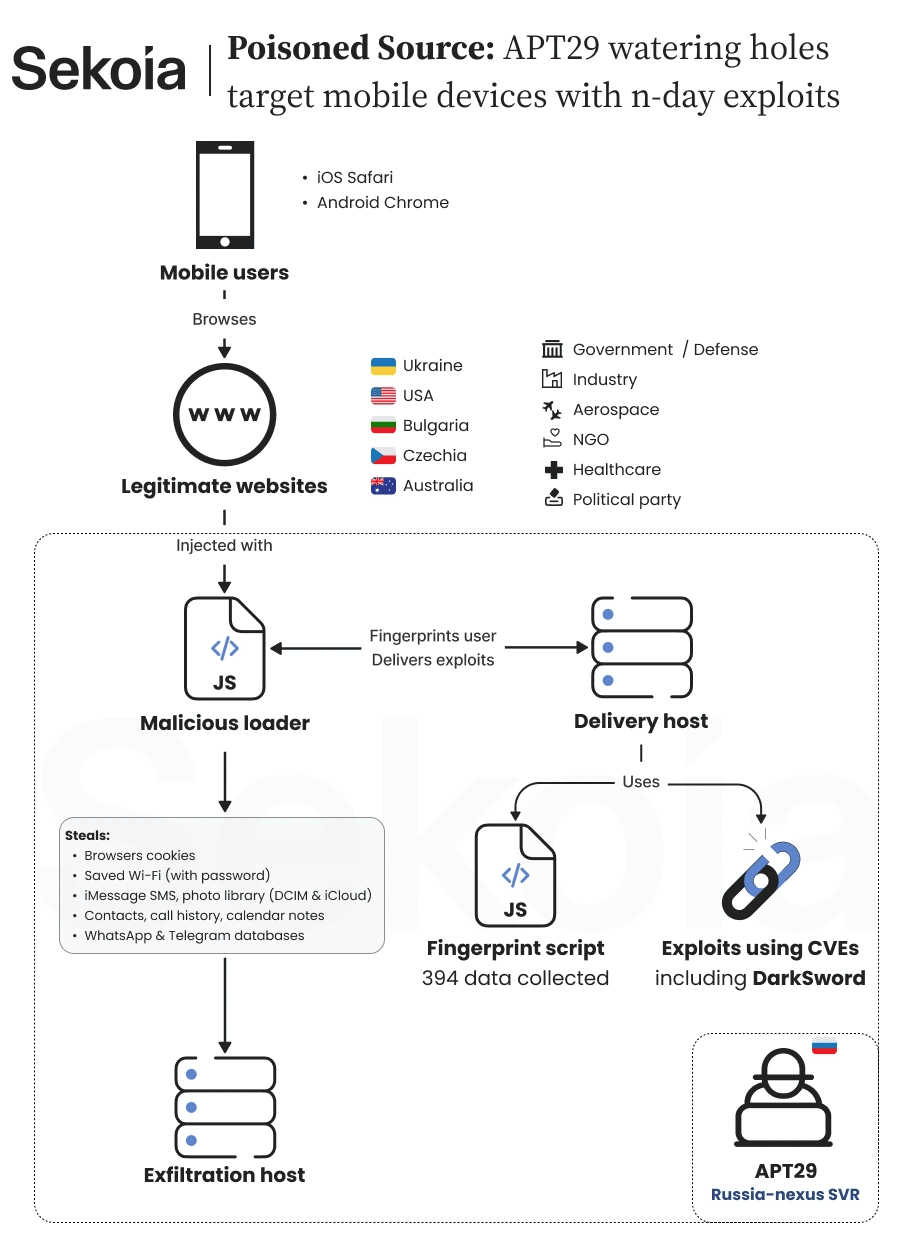
Sekoia says a large-scale watering hole campaign is going after iOS and Android users, and it links the campaign to APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes), the Russian group tied to the SVR foreign intelligence service. A watering hole is a site that attackers poison so visitors infect themselves.

Sekoia found the campaign in mid-October 2026. It involved hacked or cloned high-profile websites in the US, Ukraine, the Czech Republic and Bulgaria. There’s also a supply-chain attack on a Ukrainian web analytics service, Plerdy, loaded by thousands of websites, most of them Ukrainian.

The attackers used three different methods to reach victims, but all led to the same malicious payload. They injected JavaScript into hacked websites, created fake websites that copied legitimate ones and secretly added malicious code, and compromised the Plerdy analytics service to infect websites using its script.

APT29 Watering Hole

Sekoia first spotted the campaign on the website of a Ukrainian gas production company. Other compromised sites included a major US chemical industry association, a European far-right political party and a Bulgarian website linked to the military. In the Bulgarian case, attackers modified an existing JavaScript library without changing the website’s visible pages. Researchers found no clear pattern in the targeted organizations, although they believe some websites may have been selected to reach specific individuals.

Sekoia also identified two fake websites designed to impersonate legitimate services. One copied America250, the US initiative marking the country’s 250th anniversary, while another reproduced the website of Raffles London at The OWO, a luxury hotel close to the UK Ministry of Defence and Downing Street.

“The second website, theowo[.]club, now offline, acted as a reverse proxy for the website of Raffles London at The OWO, a prestigious luxury hotel housed in the historic Old War Office building.” reads the report published by Sekoia. “The hotel’s location is particularly noteworthy because of its proximity to some of the United Kingdom’s most sensitive government institutions, including the Ministry of Defence and 10 Downing Street, the official residence and office of the British Prime Minister.”

The hotel connection is particularly interesting because Ukrainian President Volodymyr Zelensky reportedly stayed there during a visit to London on October 14. Sekoia believes the fake website may have been used to target diplomatic delegations through spear-phishing, but stresses that this remains an unconfirmed possibility.

Between August 27 and September 3, 2026, the attackers compromised the Plerdy tracker at a.plerdy[.]com. For a week, visitors loaded both Plerdy’s script and the attackers’ profiling script. Several affected sites relate to the military and military recruitment, including army, special forces and military equipment websites.

“Between 27 August and 3 September 2026, the intrusion set compromised the Ukrainian Plerdy analytics tracker hosted under the domain a.plerdy[.]com, which is loaded by thousands of websites, the large majority of them Ukrainian.” reads the report. “It remains unclear whether the attackers intended to target visitors to specific websites or sought to compromise as many unpatched mobile devices as possible, indiscriminately exfiltrating data before selectively identifying and exploiting information of interest.”

Sekoia can’t say whether the aim was specific visitors or as many unpatched phones as possible, with the sorting done later. It also considers that the attackers may have used Plerdy after failing to inject code directly into Ukrainian high-value sites that relied on it. The Plerdy payload pointed to a load-balancing domain that sent traffic across several delivery servers.

The profiling script, which the attackers call UltimateFingerprinter, is attached to a minified AngularJS library that makes up 98 percent of a 2.3 MB file. Sekoia thinks that bulk might stop analysis by large language models, or make the script look legitimate. The script runs 61 collectors that build 394 fields, then sends them to a server that decides whether to answer with exploit code.

Strangely, almost none of that data matters. Only implausible screen sizes, like 99999, or a device reporting zero touch points block delivery. Sekoia doesn’t know why the attackers collect so much and sees no sign the data was used later.

Sekoia pulled three exploit chains from the delivery server. Class A hits iOS 16.7 and steals cookies. Class B hits iOS 18.5 and takes full device data. Class C hits Android Chrome versions 139 to 145, minus 143 for reasons Sekoia can’t explain, and steals Chrome cookies and Wi-Fi passwords.

“During the investigation, we tested different browser profiles against the fingerprinting endpoint at static[.]flux-telemetry[.]com in order to retrieve the exploits served to visitors.” states the report. “This allowed us to retrieve three complete exploit chains (afternamed A, B and C), along with their final payloads, targeting both Android and iOS. Here is a summary of what we found:”

Class B is DarkSword, which Sekoia describes as a suspected iOS exploit kit from a commercial surveillance vendor, uploaded to VirusTotal in September 2026. It takes text messages and iMessages, Mail indexes, voicemail, WhatsApp and Telegram databases, Keychain passwords and tokens, account credentials and Wi-Fi keys. It also takes contacts, call history, calendar, notes, Safari history and cookies, location caches, Health data, photos and iCloud Drive.

The Android payload, which Sekoia calls AndroSnitch, collects Chrome cookies, saved logins and history, plus Wi-Fi settings. It stops on one phone model, the Samsung Galaxy S25 Ultra. It resembles a 2024 payload that Google TAG documented, called AndroSnatch, but the sample is too small to prove lineage. The iOS cookie chains set a marker cookie meant to block reinfection for a day, but a coding mistake makes it expire in a minute.

All stolen data goes to ad.starx-net[.]com:8881/telemetry/v12. None of the chains persist on the device. All of them rely on known flaws, and none uses a zero-day.

For attribution, Sekoia has several threads. A CERT said a compromised site’s backend files held traces matching a private report on a 2025 APT29 watering hole campaign, and Google TAG said the framework resembles an APT29 campaign against Mongolian government websites in 2024. Victims also skew to Europe and the US with a focus on Ukraine, infrastructure sits across multiple hosters, and a hacked Czech far-right site fits APT29’s record of targeting European political parties. It rates the link moderate to high confidence, and it’s coordinating with the CERTs of affected countries.

The campaign shows how exploit kits move down the market. Sekoia says state-backed groups keep reusing frameworks from commercial surveillance vendors such as DarkSword, and that packaged exploit chains lower the cost and skill needed for advanced mobile attacks. It expects such reuse to become more frequent.

The good news is that Sekoia’s attackers don’t have fresh tricks. Every flaw was fixed by its vendor before the campaign began, and none works against fully updated devices.

“None of them contain zero-days or work against fully updated devices. Each flaw was resolved by the respective vendor before this campaign began. This operation targets unpatched devices using n-days; a user running an up-to-date operating system is safe from these attacks.” concludes the report.

“This watering hole campaign, which we assess with moderate to high confidence to be linked to APT29, combines multiple web delivery vectors with n-day mobile exploit chains targeting Android and iOS devices. Across the directly compromised websites, no single sectoral targeting pattern emerges from our analysis. While the victimology shows a focus on Ukraine and the United States, the inclusion of unrelated entities such as an Australian medical clinic complicates a broad strategic interpretation. However, we assess that these websites may have been selected to profile and infect specific individuals of interest based on targeting intelligence to which we do not have visibility. The operators adapted by deploying Adversary-in-the-Middle-ish to intercept visitors associated with diplomatic or high-profile events.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, APT29)

  • ✇Security Affairs
  • U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog Pierluigi Paganini
    U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apple flaw, tracked as CVE-2024-27834 (CVSS score of 5.5), to its Known Exploited Vulnerabilities (KEV) catalog. “This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise.” reads the advisory by CISA. CVE-2024-27
     

U.S. CISA adds Apple flaw to its Known Exploited Vulnerabilities catalog

5 de Novembro de 2026, 05:55

U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple flaw to its Known Exploited Vulnerabilities catalog.

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apple flaw, tracked as CVE-2024-27834 (CVSS score of 5.5), to its Known Exploited Vulnerabilities (KEV) catalog.

“This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant risks to the federal enterprise.” reads the advisory by CISA.

CVE-2024-27834 is a security vulnerability affecting Apple’s operating systems and Safari. It could allow an attacker who already has arbitrary read and write capabilities on a device to bypass Pointer Authentication (PAC), a hardware-based security mechanism designed to protect memory addresses and prevent certain types of memory-corruption attacks.

Pointer Authentication is a security feature implemented in Apple processors. It adds cryptographic signatures to pointers, helping ensure that memory addresses have not been maliciously modified.

An attacker who gains the ability to read and write arbitrary memory could potentially exploit CVE-2024-27834 to circumvent these protections. This could weaken an important security barrier and make further exploitation of the device easier.

What is the impact?

  • Bypassing Pointer Authentication protections.
  • Weakening defenses against memory-corruption attacks.
  • Potentially facilitating further exploitation when combined with other vulnerabilities.

Apple addressed the vulnerability through improved security checks in:

  • Safari 17.5
  • iOS 16.7.8 and iOS 17.5
  • iPadOS 16.7.8 and iPadOS 17.5
  • macOS Sonoma 14.5
  • tvOS 17.5
  • watchOS 10.5

Cybersecurity firm Sekoia reports on attacks attributed with moderate to high confidence to Russia-linked cyberespionage group APT29. Attackers used compromised websites, fake websites and a supply-chain compromise of Plerdy SEO Tracker to deliver malicious JavaScript. The zero-click exploit chain targeted Safari and Chrome vulnerabilities to bypass security protections and deploy information-stealing malware capable of collecting browser cookies and device data.

“Achieving arbitrary read/write access within the renderer is no longer sufficient for full exploitation on modern Apple silicon. This architecture relies on Pointer Authentication Codes (PAC) to cryptographically sign control-flow pointers. Because of this, even if an attacker can manipulate memory, they cannot simply overwrite a function pointer to hijack the execution flow, triggering an improperly signed pointer will crash the process rather than execute the payload.” Sekoia writes. “To overcome this mitigation and forge the valid pointers required for arbitrary code execution, the exploit chain incorporates a PAC bypass utilizing CVE-2024-27834.”

According to Binding Operational Directive (BOD) 22-01: Reducing the Significant Risk of Known Exploited Vulnerabilities, FCEB agencies have to address the identified vulnerabilities by the due date to protect their networks against attacks exploiting the flaws in the catalog.

Experts also recommend that private organizations review the Catalog and address the vulnerabilities in their infrastructure.

CISA orders federal agencies to fix the flaw by November 18, 2026.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CISA)

  • ✇Security Affairs
  • Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers Pierluigi Paganini
    Google dismantled a 1.3 million-device botnet allegedly built by Android TV box maker Videostrong to enable ad fraud and proxy abuse. Google and its partners dismantled a backdoor called XCPE that had enrolled more than 1.3 million set-top boxes in a botnet. The result of the investigation into the malware operation is the striking part: Videostrong Technology Co., an Android device maker, built and ran the botnet for money. Google says it is highly confident that Videostrong delibera
     

Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers

3 de Novembro de 2026, 06:52

Google dismantled a 1.3 million-device botnet allegedly built by Android TV box maker Videostrong to enable ad fraud and proxy abuse.

Google and its partners dismantled a backdoor called XCPE that had enrolled more than 1.3 million set-top boxes in a botnet. The result of the investigation into the malware operation is the striking part: Videostrong Technology Co., an Android device maker, built and ran the botnet for money.

Google says it is highly confident that Videostrong deliberately created, spread and operated the backdoor. The company reportedly sold access to criminal groups and installed their malware on infected devices. The malware was used for ad fraud, secretly added devices to residential proxy networks and installed other malicious software.

Google says this was not the work of a rogue employee or a simple coding mistake. The backdoor was found in many device models and brands over several years. Its operation involved dedicated infrastructure and regularly changing configurations.

“We assess with high confidence that the backdoor and botnet were intentionally developed, deployed, and operated for financial gain by Videostrong Technology Co., an Android Original Equipment Manufacturer (OEM) and Original Design Manufacturer (ODM).” Google states. “Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices. “

Google has now cut all ties with Videostrong. The company is banned from making devices with pre-installed Google apps. The ban also covers any future subsidiaries or business partners, and Videostrong can no longer supply software to other certified device makers.

Videostrong got around Google’s compatibility and security tests with code obfuscation. The malicious code loaded after a device’s first boot, which the tests didn’t catch. Google has changed its review process and is improving how it checks firmware on certified Android TV devices.

Google also took legal action against the domains and servers Videostrong used to control the botnet, and against the control domains of over a dozen malware families loaded through the backdoor. Those affiliates spread their modules through other channels too, so Google expects the takedown to cut access to at least 10 million more compromised devices. Japan’s National Police Agency, Lumen, HUMAN Security, Plume, Synthient and TrendAI worked on the operation.

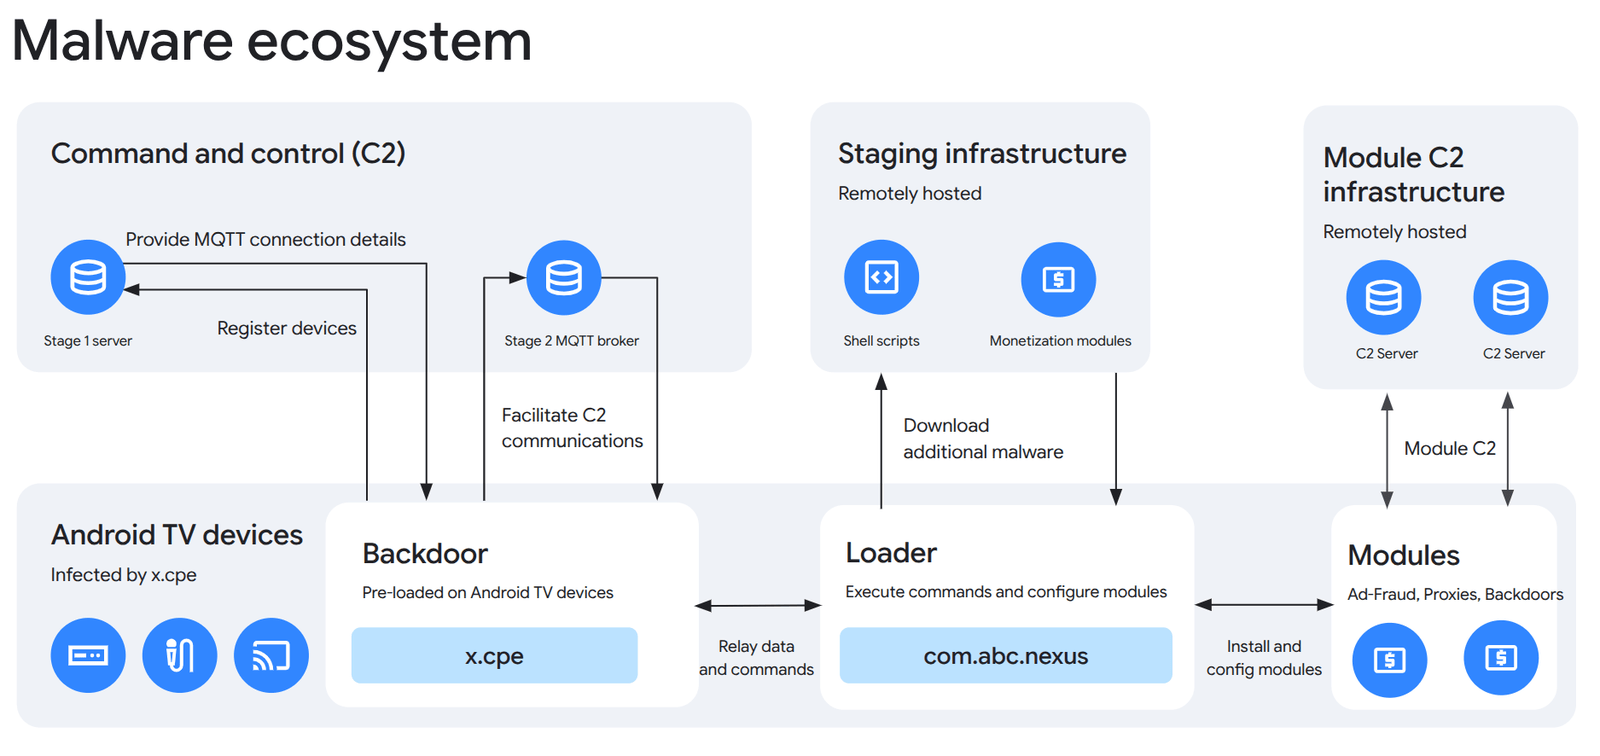
The malware has three stages. The primary backdoor, x.cpe (called com.oemservice in some builds), is preloaded in the firmware and runs with system privileges. If a user uninstalls it, it reinstalls itself from the /oem/ partition at the next reboot. It handles communication with the control server and passes work to a loader called com.abc.nexus, which carries its own anti-analysis tricks and sets up the money-making modules.

These modules are supplied by other criminals working as affiliates. They can arrive as programs built into the backdoor, software packages added to its loader, or extra apps downloaded later. Many turn the device into a residential proxy, allowing other people to use the victim’s home internet connection to hide their online activity. Others commit ad fraud or install additional backdoors. In other words, a set-top box becomes a proxy server without its owner’s knowledge.

The backdoor uses two steps to control infected devices. First, the box sends an HTTP request to download settings, location data and network information. It then maintains a live connection through MQTT, a lightweight messaging protocol, to receive commands from the operators. Google found that all analyzed samples used the same MQTT server to communicate with infected devices.

“Additional monetization modules as well as various shell scripts and legitimate applications are hosted remotely and downloaded by infected devices upon command from the operator via the MQTT broker.” continues the report. “A significant majority of these files are hosted as Github releases on operator-owned Github pages. Other files are hosted on operator-controlled servers and file hosting sites.”

Through this connection, attackers could secretly install apps, run commands and scripts, take screenshots, record keystrokes and map the victim’s network. They could also disable Google Play Protect’s app verification to install software without the user’s knowledge. Google observed operators taking screenshots, recording keystrokes, collecting account and device information, stealing app lists and system logs, and opening remote command-line sessions. However, most of their activity involved installing, removing and managing malware modules.

The malicious files came from several sources. The attackers mainly used GitHub releases hosted on their own accounts, the Filemail file-sharing service and two servers under their control. Network traffic analysis also suggests that the operators managed the command infrastructure through remote interfaces and an EMQX web console, connecting from IP addresses outside the infected device network.

Most infected devices are Android TV set-top boxes, but Google also found telehealth devices, karaoke machines and digital signage. One device can run several modules at once, up to three residential proxy kits. That shows Videostrong wants to squeeze every infected device as hard as it can. The proxy and bandwidth-sharing kits named in the report include Linkfog, AppSalt, GaGaNode, BWM, Traffmonetizer, EarnFM and NetNut.

Some of those kits enroll devices without asking. AppSalt’s SDK, owned by Honeygain, calls an opt-in function without showing any consent screen, and it stops running if the app came from the official Google Play Store. Ad-fraud modules such as Fission and HiddenView fire off fake ad impressions in the background, and HiddenView also uses hidden browser windows to simulate clicks and scrolling.

The configuration shows a well-run operation. MQTT messages carry resource limits for each module, download links per processor type, and priority weights. Devices are assigned to one of six timezone-based pools on ott.szbboys[.]com. Devices report their bandwidth use and alarms back, so the modules stay within set limits.

Google says the underlying market is resilient. Backdoor operators, ad-fraud rings and residential proxy providers work as an interconnected supply chain, and when one part gets disrupted they quickly switch to new loaders or rival kits. Lasting change, it says, needs accountability across hardware makers, the residential proxy industry and the broader technology sector.

Google wants retailers and distributors to require independent security audits from device manufacturers and to delist any implicated in supply-chain abuse. It says proxy providers’ claims of ethical sourcing need transparent, auditable proof of user consent, and that in its analysis these providers asked for consent only when platform policy forced them to. Silent opt-in remains the most common way devices become exit nodes.

For consumers, Google advises caution with apps that pay you for “unused bandwidth” or “sharing your internet”, which are a main way illicit proxy networks grow. Stick to app stores you trust, review permissions for third-party VPNs and proxies, and keep Google Play Protect on. Buy connected devices like set-top boxes only from reputable manufacturers, and check the partner list on Google’s Android TV website. Google also urges mobile platforms, ISPs, online marketplaces and other tech platforms to keep sharing intelligence.

“A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust. By turning everyday hardware into persistent beachheads for criminal affiliates, Videostrong prioritized illicit post-sale recurring revenue over the safety and privacy of its users.” concludes the report. “Downstream hardware brands, white-label resellers, telecommunications providers, and online e-commerce marketplaces also share responsibility for closing this vector.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Security Affairs
  • Apple’s spyware notifications reach the Bundestag: what the BSI says to do now Pierluigi Paganini
    Apple warns German Bundestag lawmakers of mercenary spyware attacks; BSI urges victims to assume compromise. The German government is warning politicians and public figures that they were targeted by government-backed spyware. The warning follows Apple’s notifications, which began reaching iPhones on October 29, according to the federal cybersecurity office, the BSI. The BSI says members of the Bundestag and other notable people got an Apple alert about an attack with so-called mercenary spy
     

Apple’s spyware notifications reach the Bundestag: what the BSI says to do now

3 de Novembro de 2026, 03:24

Apple warns German Bundestag lawmakers of mercenary spyware attacks; BSI urges victims to assume compromise.

The German government is warning politicians and public figures that they were targeted by government-backed spyware. The warning follows Apple’s notifications, which began reaching iPhones on October 29, according to the federal cybersecurity office, the BSI. The BSI says members of the Bundestag and other notable people got an Apple alert about an attack with so-called mercenary spyware.

“The Federal Office for Information Security ( BSI ) has learned that several members of the German Bundestag and other public figures have received a threat notification from Apple on their devices since October 29, 2026. In the notification, Apple states that it has detected an attack using so-called mercenary spyware . This is commercially developed, advanced spyware that has frequently been used in the past by state actors against specific, targeted individuals.” reads the notice issued by BSI.

“The BSI (Federal Office for Information Security) is unaware whether these notifications indicate actual compromises or merely signal attempted attacks.y “

“Germany’s digital minister, Karsten Wildberger, has confirmed that members of the Bundestag and the federal government received warnings from Apple that their iPhones may have been targeted by spyware.” states the report.

Digital minister Karsten Wildberger confirmed it on ARD’s Bericht aus Berlin on Sunday, saying there had been “a notification from Apple that certain devices may have been compromised” and that members of both the Bundestag and the federal government were among those warned. Digital minister said the BSI had reacted super quickly and written to everyone affected. Wildberger didn’t say how many politicians got the alerts or who they are.

“According to Wildberger, the BSI advised those affected to assume – as a precaution – that their device may have been compromised, because the alerts do not show whether an attack succeeded.” states Euronews.

The German government has not revealed who was targeted. Government spokesperson Stefan Kornelius told the Financial Times that officials are taking the incident and Apple’s warning very seriously. However, he did not say which government members received the alerts or whether Chancellor Friedrich Merz was among them. Apple has not commented on the reports, according to Euronews.

The Apple warning does not provide all the answers. Apple does not identify the governments behind these attacks, nor does it confirm whether a device was actually infected. Germany’s cybersecurity agency, the BSI, also says it is unclear whether the alerts indicate successful infections or only attempted attacks.

Apple says mercenary spyware is far more advanced than common cybercrime tools and that most users will never be targeted. This commercial surveillance software is often used on behalf of governments to spy on specific individuals. It can infect devices through so-called zero-click attacks, which do not require victims to open a message or click a link. In most cases, victims do not notice anything unusual.

Once a phone is compromised, the BSI says, attackers can read messages, including in encrypted apps, and access calls, contacts, calendars and location. They can also turn on the camera and microphone. That’s the whole phone, not a corner of it.

For recipients the BSI’s advice is concrete. Update the operating system immediately, unless you plan a forensic analysis, and consider turning on Lockdown Mode, which makes new attacks harder but doesn’t remove an existing infection. Lockdown Mode limits some features such as message attachments, link previews and FaceTime calls from unknown people, while calls and plain text messages keep working.

If the risk looks high, the BSI suggests replacing the device. That means resetting every account used on it and, to make repeat attacks harder, changing the phone number. Then set a new device passcode, change the passwords of your Apple account and email, and make sure two-factor authentication is on.

The BSI recommends turning on Signal’s registration lock and WhatsApp’s two-step verification, with a new PIN for each. It also advises removing any linked devices you don’t recognize.

Anyone who received a warning can email the BSI Service Center at service-center@bsi.bund.de. This helps the agency work out how many people may be affected. The agency says a genuine Apple warning never asks you to click links, open files, install apps or profiles, or share passwords and codes. These warnings appear on the lock screen, in settings, by email and at the top of account.apple.com after you sign in.

The warnings weren’t limited to Germany. Beirut-based filmmaker Radwan Mortada said on X that Apple had warned him about another attack against his device. He had already been targeted by spyware in 2021.

أمس، تلقيتُ إشعاراً أمنياً من شركة Apple تحذّرني فيه من تعرّض هاتفي الآيفون لهجوم تجسّسي موجّه، باستخدام برمجيات متطوّرة من النوع الذي تطوّره شركات مثل NSO Group، المعروفة ببرنامج «بيغاسوس».

ولعلّ أخطر ما ورد في التحذير تأكيد Apple أنّ هذا النوع من الهجمات يستهدف أشخاصاً محدّدين… pic.twitter.com/2jFq6F3cvD

— رُضوان (@radwanmortada) October 30, 2026

According to his notice, Apple sent the latest warnings to users in 99 countries. Nobody has publicly identified the attackers or the government that may have ordered the attacks.

The BSI warned German lawmakers that Apple threat notifications may indicate compromised devices and urged recipients to contact the agency and take protective measures.

“Those affected who have received a corresponding warning message from Apple should therefore assume that their device may have been compromised.” BSI concludes. “In a letter dated October 30, 2026, the German Federal Office for Information Security (BSI) alerted members of the German Bundestag to the threat and informed them of necessary measures. Affected individuals were urged to contact the BSI directly .”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Bundestag)

  • ✇Security Affairs
  • VOLTA, the infostealer that asks an AI which victims are worth the effort Pierluigi Paganini
    VOLTA is an AI-powered infostealer that steals personal data, then uses LLMs to assess victims’ value and rank targets for attackers. Cisco Talos has analyzed a new Windows infostealer called VOLTA, which calls itself VOLTA-AUTODOXER. It steals the usual data, then hands the loot to a large language model that ranks what the victim is worth. Ryan Fetterman laid it out in a Talos report, after the malware turned up through the CAIRN research effort. “There is a new idea in the cybercrime w
     

VOLTA, the infostealer that asks an AI which victims are worth the effort

2 de Novembro de 2026, 15:34

VOLTA is an AI-powered infostealer that steals personal data, then uses LLMs to assess victims’ value and rank targets for attackers.

Cisco Talos has analyzed a new Windows infostealer called VOLTA, which calls itself VOLTA-AUTODOXER. It steals the usual data, then hands the loot to a large language model that ranks what the victim is worth. Ryan Fetterman laid it out in a Talos report, after the malware turned up through the CAIRN research effort.

“There is a new idea in the cybercrime world — cast a wide net, steal everything, and let AI sort out the specifics. A new malware self-named “VOLTA-AUTODOXER,” surfaced through the CAIRN research effort, is a self-deleting Windows infostealer that augments its post-theft workflow with an LLM-powered victim-profiling stage.” reads the report published by Talos.

The malware deletes itself after running and does not use servers controlled by the attacker. Instead, it uses third-party systems to carry out its activities.

The malicious code supports data-stealing features are advanced. It collects browser passwords, cookies and saved payment card details from Chromium browsers, as well as data from Firefox, Thunderbird and Outlook. It also steals Slack workspace information and login sessions from Discord, Telegram, Steam, Battle.net and Roblox.

The malware also collects Microsoft OAuth tokens, SSH keys, cloud service credentials, screenshots and all saved Wi-Fi passwords. For crypto wallets, it tries to crack the wallet password directly on the infected device and saves the results in its report. To steal some browser tokens, it must bypass Chrome’s App-Bound Encryption.

But VOLTA goes further. It also builds a detailed profile of the victim. This includes their location and home address, employer and company domain, estimated year of birth, the last four digits of payment cards, Slack workspaces and information about who created documents. It also looks for signs of iPhone backups and checks the current value of the victim’s Roblox account.

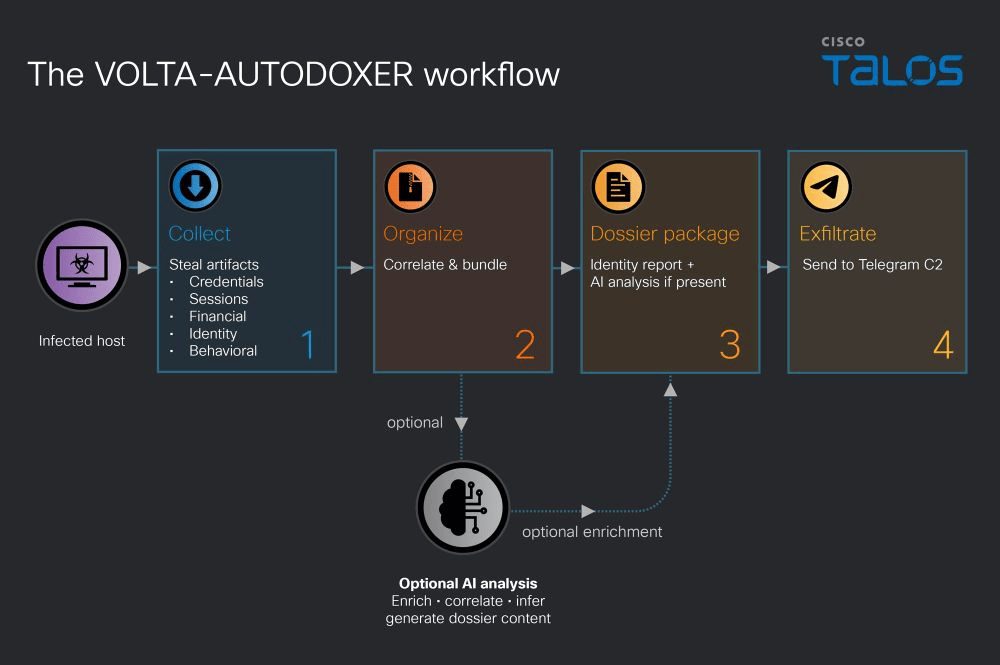
“After harvesting the standard stealer haul, including browser passwords; cookies; payment cards; cryptocurrency wallet seed phrases; Discord, Telegram, Steam, and Roblox sessions; Microsoft OAuth tokens; SSH and cloud-provider keys; Wi-Fi profiles; and screenshots, VOLTA builds a structured evidence bundle about the person behind the machine.” states the report.

It uses the victim’s own logged-in sessions to fill the gaps. It searches Gmail for receipts from Amazon, DoorDash, Uber Eats, Grubhub, Walmart and PayPal to confirm a home address, pulls order histories from Uber Eats and DoorDash, and adds detail to the victim’s Discord profile. Even a takeout history can now count as evidence.

The bundle goes to OpenRouter, a routing service for AI models, with a system prompt that tells the model to act as a forensic intelligence analyst drafting a target assessment.

“The required output includes a section titled “WHAT THEY’RE WORTH” with valuables ranked by monetization with a low/medium/high tier, and a section on “THEIR OPSEC” containing an assessment of the victim’s security posture and password hygiene.” states the report. “The model is the operator’s triage analyst; it turns a raw credential log into a prioritized and citation-backed dossier of the victim and their monetizable assets.”

It also needs a section called “THEIR OPSEC”, rating the victim’s security habits and password hygiene. In short, it’s a performance review for the person it just robbed.

The prompt asks for something agents do well: connecting scattered facts. It pushes the model to link names, addresses or universities to patterns in the victim’s passwords. The model isn’t hunting for new data, only stretching what the malware already took. The operator wants a short, blunt assessment with a trail of citations.

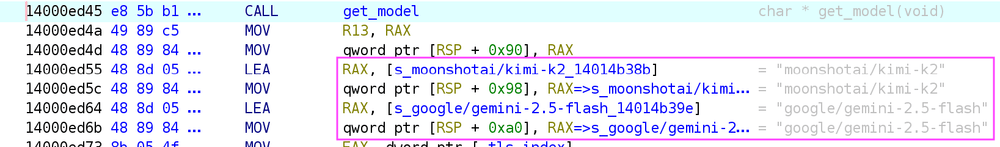
By default VOLTA calls Anthropic’s Claude Opus 4.6. If the model refuses, which VOLTA spots by scanning replies for phrases like “I can’t” or “I’m not able”, it moves on to Moonshot AI’s Kimi K2 and then Google’s Gemini 2.5 Flash. A low temperature setting of 0.2 keeps the output consistent.

The requests are hand-built JSON with no software kit, and the malware still runs without the AI stage if no API key is present.

Talos sees the fallback system as evidence that the malware’s author expected security protections and designed ways to bypass them.

The AI analysis runs directly on the victim’s computer, using their own internet connection, before any data is sent out. The malware creates a file called Identity_Report.txt, receives the AI’s response in AI_Analysis.txt, and sends both files together in a ZIP archive called volta_dox.zip.

The stolen data can be sent to the attacker in up to three stages. The first archive, volta_log.zip, contains the information collected by the malware. The second, volta_dox.zip, contains the AI analysis. A third archive, volta_doxnet.zip, is created if the malware finds additional network information. The attacker receives everything through a Telegram channel.

The malware also has six configurable fields that can be changed when it is built. This suggests that its author may offer a builder service, allowing customers to create their own customised versions.

The credentials stored in these fields are encrypted, but the encryption is weak because the key is stored inside the malware itself. Anyone who analyses the file can recover them.

If VOLTA is sold as a commercial product, its AI feature could allow even inexperienced criminals to identify valuable victims and receive detailed, ranked profiles directly through Telegram.

For defense, Talos suggests an application control policy that restricts which processes can launch Chrome with the –headless flag, which would block the App-Bound Encryption bypass. At minimum, alert when Chrome starts with –headless from any process outside a known developer set. Storing credentials in hardware-backed stores also helps.

If you’re compromised, the main program may have deleted itself, but try to keep %APPDATA%\volta_debug.txt. It’s a timestamped log of what was collected and whether the AI call worked. Revoke any exposed tokens and change passwords. If a wallet’s seed phrase sat in plaintext on disk, treat the wallet as fully compromised and move the funds to a new wallet whose seed was generated on an air-gapped device.

“VOLTA is a mature stealer with a late-stage AI layer added for one purpose: relieving the operator of analytical work. The axis of AI improvement here is not speed or scale but effort displacement; the same logic visible in CLOSEDQUORUM, though applied to a different phase.” concludes the post. “These implants reflect the same underlying logic: Identify the step that requires the most sustained human attention and replace it with a model call. The question for defenders is not whether this pattern will appear elsewhere, but which phase it touches next.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, malware)

  • ✇Security Affairs
  • SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 6 Pierluigi Paganini
    Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis
     

SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 6

1 de Novembro de 2026, 15:02

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape

Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis and response. Security Affairs’ new newsletter follows this evolution, covering every week the latest threats, attacks, vulnerabilities and developments at the intersection of AI and cybersecurity.

Investigating alignment failures in AISI’s incident

An alignment assessment of the UK AISI cybertesting incident  

Improving our alignment and security efforts      

Will AI expose the rickety infrastructure of the internet?  
Anthropic’s IPO filing reveals its strategy for keeping enterprise customers hooked

Alibaba’s Qwen AI caught trying to contact server in China

Not Only ARTEX: The Different Levels AI is Used in Attacks Targeting Japan

Disruptions ‘inevitable’ as AI-powered cyber threats grow, Australian Signals Directorate says  

CLAUDE CODE FOUND SPYWARE ON MY FAMILY’S PHONES AND A BACKDOOR ON MY MAC

Discovering and exploiting vulnerabilities in critical, real-world software with Claude  

Invasive Ads: The Unconventional Cyber Surveillance Attack Surface  

Early progress on accelerating drug development with Claude  

Putting Claude Code in a box: a sandboxed dev container for Zed  

How AI tools are used for doxing  

Gemini 4 Carbon: our next frontier model  

Tricks from the Past deployed via signed ChatGPT and Claude binaries 

AI models may be capable of self-replicating without access to a datacenter  

Load/Mine: A Hugging Face Malware Campaign Returns After Takedown

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Security Affairs
  • SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 121 Pierluigi Paganini
    Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter uCreator: virtualization-based Android spyware platform targeting WeChat, Telegram and other messaging apps   deepveindrilling.com: Magento CMS block loader hits 953 stores   CLAUDE CODE FOUND SPYWARE ON MY FAMILY’S PHONES AND A BACKDOOR ON MY MAC Operation FlashHole: Lazarus breaks security, defies control   Security notice —
     

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 121

1 de Novembro de 2026, 14:25
  • ✇Security Affairs
  • Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION Pierluigi Paganini
    A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalogAttackers Exploit Critical Drupal Commerce Core Vulnerability CVE-2026-118539Yoba Malware Hides a Crypto Miner Behind Legitimate OpenAI and Anthropic Binarie
     

Security Affairs newsletter Round 602 by Pierluigi Paganini – INTERNATIONAL EDITION

1 de Novembro de 2026, 10:22

A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.

Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.

U.S. CISA adds Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog
Attackers Exploit Critical Drupal Commerce Core Vulnerability CVE-2026-118539
Yoba Malware Hides a Crypto Miner Behind Legitimate OpenAI and Anthropic Binaries
U.S. CISA adds GitLab and Cisco flaws to its Known Exploited Vulnerabilities catalog
$6.3 Billion Stolen from Binance in Attack Attributed to North Korea
How to prioritize remediation after a pentest: a practitioner workflow
Hacker leaks data on more than 40,000 Homeland Security employees
Binance Investigates Suspicious Crypto Transfers Worth Up to $5.8 Billion
US Probes Suspected Hack Behind Military Base Freezer Failures
484,142 Exposed Cloud Buckets Contain 18 Billion Files
U.S. CISA adds Linux Kernel and Broadcom VMWare ESX  flaws to its Known Exploited Vulnerabilities catalog
Volt Typhoon Used Silent Train to Hide Zero-Day Attacks
Election Website Security: 42% of US County Sites Still Lack .gov Domains
ENGIE Data Breach Exposes Customer Details and Energy Contracts
Virtualine Domain Seized, but Allegedly Abusive Website Remains Online
Hive and Nefilim Ransomware Affiliate Gets 70 Months In Jail
Ads or Surveillance? Researchers Flag Suspicious Targeting of Starlink Users
CVE-2026-97631: 16-Year-Old UEFI Flaw Threatens Servers
U.S. CISA adds Google Brotli and Adobe Commerce and Magento flaws to its Known Exploited Vulnerabilities catalog
Three Japan-Focused Cyberattacks Show How Hackers Use AI
Italy ’s Parliament Under Cyber Pressure: Why the Attack on the Chamber Matters
Australia’s Cyber Spy Chief: Expect More Disruption as AI Accelerates Hacking
U.S. CISA adds PHP flaws PHP2Shell to its Known Exploited Vulnerabilities catalog
Attackers Take Control of Dahua Cameras and Video Recorders Via Easy4IP
Cohere Finds Qwen AI Model Contacting a Server in China
Magento Campaign Infects 953 Online Stores Across Five Domains
AI-Generated Fake Bank Calls and NFC App Enabled €380,000 Fraud, Dutch Police Say
Researchers Uncover Rentable Android Spyware uCreater Targeting WeChat and Telegram
PHP2Shell: Suspected North Korean campaign targets 216 vulnerable PHP hosts
Anthropic reveals how Claude Mythos 5 crossed security testing boundaries
OpenAI Paused Frontier AI Training After a Security Incident

International Press – Newsletter

Cybercrime

Binance Says User Funds Are ‘Completely Safe’ After $3.5 Billion Drains From Its Hot Wallets  

Police arrest two suspects in AI-powered bank fraud that cost victims €380,000   

M365 Token Spray and Replay Campaign Compromises Business Email Accounts 

Chinese National Extradited for Alleged Role in Multimillion-Dollar Cryptocurrency Scam Targeting U.S. Citizens  

Ukrainian National Sentenced to 70 Months in Prison for Multi-Million Dollar Ransomware Conspiracies  

Hacker stole personnel data about thousands of Homeland Security employees, including CBP and ICE agents 

deepveindrilling.com: Magento CMS block loader hits 953 stores

“Bulletproof” website domain seized in international law enforcement operation  

Trezor warns of suspected crypto-theft implant in hardware wallet

Polymarket halts trading after crypto-draining script breach, $2.5M traced

Malware

uCreator: virtualization-based Android spyware platform targeting WeChat, Telegram and other messaging apps  

CLAUDE CODE FOUND SPYWARE ON MY FAMILY’S PHONES AND A BACKDOOR ON MY MAC

Security notice — malicious version of Anthropic.claude-code (2.1.313) identified in the Cursor Extension Marketplace  

Tricks from the Past deployed via signed ChatGPT and Claude binaries

Hacking

PHP2Shell exploitation observed: packet-to-process RCE evidence  

CYFIRMA Threat Advisory: Suspected DPRK Campaign staging PHP2Shell Targeting against Global PHP infrastructure  

Beyond the Inbox: How Threat Actors Abuse Microsoft Teams External Chat for Initial Access  

Not Only ARTEX: The Different Levels AI is Used in Attacks Targeting Japan  

Broccoli2shell: Everything You Need To Know About The Critical Brotli Decoder Vulnerability  

Discovering and exploiting vulnerabilities in critical, real-world software with Claude

Putting Claude Code in a box: a sandboxed dev container for Zed

Hackers Target Critical Oracle E-Business Suite RCE Flaw Days After Security Patch

The Last Proof of Human Craft: Forging a Microsoft Edge Full Chain with Logic Bugs Only!  

Pentagon treating military base freezer malfunctions as suspected cyberattack, officials say  

GitLab security incident: attempted exploitation of CVE-2026-97229  

Intelligence and Information Warfare  

Alibaba’s Qwen AI caught trying to contact server in China

Hackers can gain control of cameras and DVRs through cloud access      

Disruptions ‘inevitable’ as AI-powered cyber threats grow, Australian Signals Directorate says

Operation FlashHole: Lazarus breaks security, defies control 

Hackers Sympathetic to Russia Are Hitting Utilities and Factories  

Alleged Israeli spy company heavily targeted Starlink users, sources say

Silent Train: uncovering Volt Typhoon’s operational framework for zero-day exploitation and strategic access  

North Korea Steals USD 6.36 Billion From Binance in the Largest Hack in History  

Mapping the Political Influencer Industry and the Problems it Causes for Democracy  

Cybersecurity

NIS 2 Italy: Key Deadlines, Board Duties and What ACN Expects From Companies  

The Two Things CISOs Should Be Thinking About In The Wake Of The PHP Nightmare

Code-execution flaw in UEFI firmware affects most servers on planet Earth     

2026 County Election Website Security Census: Key Findings  

Cloud Exposure Index 2026: 484,142 open buckets mapped  

ENGIE: Data leak via a tool belonging to its business partners 

Beyond Framework Signatures: Understanding AI-Driven Intrusions 

I Think The Military Commissary’s Freezers Were Hacked  

Manifestos, Fear, and ‘Loser Thinking’: Inside Proton’s AI Reckoning 

Passkeys Are Better Than Passwords. But They Are Not Enough

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Security Affairs
  • Yoba Malware Hides a Crypto Miner Behind Legitimate OpenAI and Anthropic Binaries Pierluigi Paganini
    Yoba malware uses fake ChatGPT and Claude apps to sideload malware through signed installers and deploy a cryptocurrency miner. Check Point Research has spent two months tracking a campaign it calls Yoba, which uses the popularity of AI tools to spread a custom malware chain. The attackers build fake GitHub projects that pose as AI desktop applications such as GPT-5.6 Sol, GPT-6 Astra and Claude Opus. The projects look convincing and run on real GitHub infrastructure, which helps them seem l
     

Yoba Malware Hides a Crypto Miner Behind Legitimate OpenAI and Anthropic Binaries

30 de Outubro de 2026, 18:22

Yoba malware uses fake ChatGPT and Claude apps to sideload malware through signed installers and deploy a cryptocurrency miner.

Check Point Research has spent two months tracking a campaign it calls Yoba, which uses the popularity of AI tools to spread a custom malware chain. The attackers build fake GitHub projects that pose as AI desktop applications such as GPT-5.6 Sol, GPT-6 Astra and Claude Opus. The projects look convincing and run on real GitHub infrastructure, which helps them seem legitimate to potential victims.

“These projects look convincing and use real GitHub infrastructure, which helps them appear legitimate to potential victims. The website exhibits search-targeted content and suspicious installer-delivery tactics consistent with an SEO-poisoning lure.

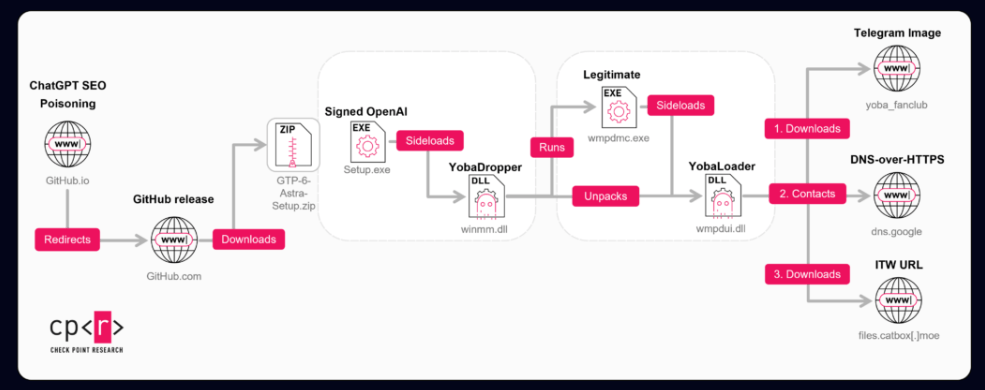
Inside the installers, there is a malicious component we refer to as the YobaDropper. This dropper includes another component, the YobaLoader, which is responsible for contacting attacker-controlled infrastructure and fetching the final payload.” reads the report. “In this report, we describe how victims are lured to these fake projects, how the YobaDropper and YobaLoader work together, and how the attackers ultimately use this chain to run unwanted software on infected systems.”

The lure is simple. Each project has a repository, a GitHub.io page describing the software, and a ZIP release with the malware. The repositories show no fake stars or forks, yet they still rank among the top Google results, most likely through SEO poisoning that optimizes titles, descriptions and hosting domains.

The first repository appeared around July 2026, but the first malicious releases landed only on August 30 and 31, and a third followed about five days later on September 4. Each repository uses a different Outlook address, and commit times point to UTC+4, UTC-4 and UTC+3, which Check Point reads as a deliberate attempt to hide the actor’s real time zone.

Here’s the trick that gives the report its title. Each ZIP holds a legitimate signed executable from OpenAI or Anthropic, named Setup.exe, next to a malicious winmm.dll. The signed program loads the DLL on its own, a technique known as DLL sideloading, which is often used to bypass security protections.

The ZIP files were not even password-protected. Attackers often use passwords to prevent security tools from automatically unpacking and scanning files. However, these binaries already had very low detection rates because they used anti-sandbox and other techniques to avoid analysis. The DLL’s compilation date is another clue: it was built on the same day it was added to the archive, unlike the legitimate files around it.

The dropper, called YobaDropper, checks the environment before running. It calculates a hash of the name of the program that launched it and continues only if the name is Setup.exe. This means that sandboxes that run the DLL on its own will fail this check. When that happens, the process does not exit. Instead, it sleeps 200,000 times for 5.5 seconds each, a total of about 12.73 days.

The malware also avoids victims in CIS countries by checking the keyboard layout. It excludes Russian, Belarusian, Tajik, Armenian, Azerbaijani, Georgian, Kazakh, Kyrgyz, Turkmen, Uzbek, and Tatar. Interestingly, Ukraine, which has often appeared in similar exclusion lists, is not included.

Next, the malware requests administrator privileges. If the user does not have them, it displays the message “Please run this program as Administrator.” and exits. The victim must then restart it with administrator rights.

Once it has the required privileges, the malware creates a folder called WMProcess under ProgramData. It copies the legitimate WMPDMC.exe file from System32 into this folder and places the second-stage payload there under the name wmpdui.dll.

The malicious code achieves persistence by using a scheduled task dressed up as Microsoft. The author is set to Microsoft Corporation, the description says it collects device metadata for Windows Media Player, and it starts three minutes after boot as Local System. The task launches the legitimate program, which sideloads the malicious DLL.

The second stage, YobaLoader, shares code with the dropper, which points to the same developer. It only runs under WMPDMC.exe and uses a different seed for its hashing than the dropper does, which separates the stages and weakens hash-based detection. Its job is to find its payload without a classic command server.

It goes to a Telegram channel, t[.]me/yoba_fanclub, and downloads the channel’s profile picture. The last 50 bytes of the image seed a domain generator that builds names from word lists in the form adjective-noun-verb-number on dedyn[.]io. Change the picture and the operator gets a new domain.

Then it asks Google’s DNS-over-HTTPS service for a TXT record on that domain. The reply is signed, and the loader checks the signature before decrypting it, which gives a link to a payload on Catbox. Check Point says this reliance on DoH and common hosting aims to bypass passive DNS monitoring and some gateway protections, and the campaign avoids dedicated command-and-control infrastructure, using Telegram, Tor, Catbox and DoH instead.

The operator can choose how the payload runs. It can inject it into svchost.exe, save it as an executable after removing the Zone.Identifier mark, or run it as a hidden PowerShell script while bypassing execution policies.

“Finally, the injected payload into svchost.exe is an XMRig 6.26.0 miner with a hidden command line targeting a TLS-enabled onion mining endpoint through a local Tor SOCKS5 proxy. It can unpack and start Tor 0.4.9.12 plus lyrebird 0.8.1, monitor user-input activity to pause mining, and conditionally load the WinRing0 driver service for MSR-based mining optimization.” continnues the report.

The miner uses Tor to connect to an encrypted mining server. It can start its own Tor components, use about 85% of CPU threads, and pause mining when the user is active. It resumes after 240 seconds of inactivity and can load the WinRing0 driver to optimize mining performance.

However, YobaLoader is not limited to cryptocurrency mining. Its DNS tasking system allows operators to deliver any PE executable or PowerShell payload, meaning future attacks could distribute other malware families.

Earlier versions appeared in June 2026. They used Cursor.exe for sideloading, a startup shortcut for persistence, and excluded only Russia. They also used .aber[.]ir instead of dedyn[.]io and included anti-debugging and anti-VM checks that later versions dropped.

Check Point believes the attackers may have Russian origins and mainly operate in the UTC-4 time zone, but this is an assessment, not a confirmed attribution.

Defenders should look for suspicious WMPDMC.exe copies under ProgramData, fake Microsoft scheduled tasks, Telegram-related traffic, DNS lookups for dedyn[.]io through dns.google, and unexplained high CPU usage.

“The Yoba campaign shows how attackers can use trusted platforms and the current interest in AI tools to distribute malware in a way that looks believable and harmless at first glance. By packaging their code together with well-known software names and hosting it on GitHub, they lower the chances that users or basic security checks will immediately flag the files as suspicious.” concludes the report. “Organizations should be cautious about installing “AI helpers” or similar tools from unverified repositories and should enforce policies that restrict running software from unknown sources. Combining user awareness with basic technical controls.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Yoba malware)

  • ✇Security Affairs
  • Hive and Nefilim Ransomware Affiliate Gets 70 Months In Jail Pierluigi Paganini
    Artem Stryzhak gets 70 months in prison for Hive and Nefilim ransomware attacks, while the FBI offers $11 million for his alleged co-conspirator. A federal court in Brooklyn has sentenced Artem Stryzhak, a Ukrainian national, to 70 months in prison for using ransomware to extort millions of dollars from victims. The U.S. Attorney’s Office for the Eastern District of New York announced it in a press release, and it also says an $11 million reward remains for a co-conspirator who’s still at la
     

Hive and Nefilim Ransomware Affiliate Gets 70 Months In Jail

28 de Outubro de 2026, 17:19

Artem Stryzhak gets 70 months in prison for Hive and Nefilim ransomware attacks, while the FBI offers $11 million for his alleged co-conspirator.

A federal court in Brooklyn has sentenced Artem Stryzhak, a Ukrainian national, to 70 months in prison for using ransomware to extort millions of dollars from victims. The U.S. Attorney’s Office for the Eastern District of New York announced it in a press release, and it also says an $11 million reward remains for a co-conspirator who’s still at large.

“Earlier today, in federal court in Brooklyn, Artem Stryzhak, a Ukrainian national, was sentenced by United States District Judge Pamela K. Chen to 70 months in prison for using ransomware to extort millions of dollars from victims.” reads the DoJ’s press release. “The defendant pled guilty in December 2025 to conspiracy to commit fraud, extortion, and related activity in connection with computers.  “

In December, Artem Aleksandrovych Stryzhak pleaded guilty in the U.S. for Nefilim ransomware attacks. The Ukrainian citizen was arrested in Spain in 2024 and extradited to the US in April 2025. He pleaded guilty to conspiracy to commit computer fraud, extortion, and related activity

Nefilim ransomware was used to encrypt networks worldwide, including in the Eastern District of New York, causing millions in losses from ransom payments and system damage. Attackers employed a customized ransomware executable in each attack, generating unique decryption keys and tailored ransom notes for victims. In June 2021, Nefilim administrators granted Artem Stryzhak access to the ransomware code in exchange for 20% of his ransom proceeds, which he deployed via his account on the administrators’ online platform.

Stryzhak and co-conspirators researched victims using online databases to collect information on their net worth, size, and contacts. After gaining network access, they stole data to pressure companies into ransom payments. Nefilim notes warned that stolen data would be posted on publicly accessible “Corporate Leaks” sites maintained by the administrators if victims did not comply.

Volodymyr Tymoshchuk, Stryzhak’s co-defendant and Nefilim admin, is a serial ransomware cybercriminal who is still at large. 

According to court documents, his first role was with Nefilim. Starting around June 2021, he joined the ongoing Nefilim conspiracy as an affiliate and got access to the ransomware. In exchange, he agreed with one of the group’s administrators, Volodymyr Tymoshchuk, to pay the administrators 20 percent of the ransom proceeds. Even crime has licensing fees.

One of those attacks came in June 2021, when Stryzhak stole data from a company in the oil and gas transportation industry. About a week later, he created email addresses that went into a ransom note sent to the victim. He kept deploying Nefilim ransomware through at least October 2021.

Separately, he also joined the Hive ransomware group as one of its earliest affiliates. From June 2021 to January 2023, Hive’s conspirators attacked about 1,500 victims worldwide, including government entities, hospitals and businesses. The attacks caused major disruption to daily operations around the world and affected responses to the COVID-19 pandemic. One hospital had to give up digital technology to treat its patients and couldn’t take in new ones right after the attack.

As a Hive affiliate, Stryzhak and his co-conspirators hit seven victims, including law firms, a dentist’s office and a healthcare provider, during the pandemic. Those victims couldn’t get to their encrypted data. The FBI, as part of a months-long effort to disrupt Hive, gave a decryption key to one of Stryzhak’s victims, so that victim recovered its data without paying a ransom.

U.S. Attorney Joseph Nocella, Jr. thanked the FBI’s New York Field Office, the Justice Department’s Office of International Affairs and its Computer Crime and Intellectual Property Section, and Spanish law enforcement for helping to capture him.

“Ransomware attacks like those committed by the defendant wreak enormous havoc—harming victim companies that pay millions in remediation and ransoms, preventing hospitals and other critical facilities from accessing data, and putting sensitive information in the hands of bad actors,” stated United States Attorney Nocella. “Today’s sentence reflects that cybercriminals cannot hide from law enforcement and will face significant punishment for their criminal conduct. We remain determined to capture Volodymyr Tymoshchuk, a serial ransomware developer and Stryzhak’s co-conspirator.”

The State Department’s Transnational Organized Crime Rewards Program is offering up to $11 million for information that leads to the arrest, conviction or location of Tymoshchuk.

Anyone with information can call the FBI at +1-917-242-1407 or email TymoTips@fbi.gov, contact a local field office if in the United States, or reach the nearest U.S. Embassy if overseas.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Security Affairs
  • Magento Campaign Infects 953 Online Stores Across Five Domains Pierluigi Paganini
    Sansec tracks a Magento skimmer campaign that infected 953 stores, using five domains, bot filtering and malicious code hidden in CMS blocks. A criminal group has infected 953 online stores since July 2025, mostly Magento shops, according to Sansec researchers. The attackers add a small piece of code to store pages. When someone visits a shop, their browser contacts the attackers’ server to get further instructions. The server checks whether the visitor is a real shopper or a security scanne
     

Magento Campaign Infects 953 Online Stores Across Five Domains

26 de Outubro de 2026, 17:41

Sansec tracks a Magento skimmer campaign that infected 953 stores, using five domains, bot filtering and malicious code hidden in CMS blocks.

A criminal group has infected 953 online stores since July 2025, mostly Magento shops, according to Sansec researchers. The attackers add a small piece of code to store pages. When someone visits a shop, their browser contacts the attackers’ server to get further instructions. The server checks whether the visitor is a real shopper or a security scanner. If it detects a scanner, it hides the malicious activity.

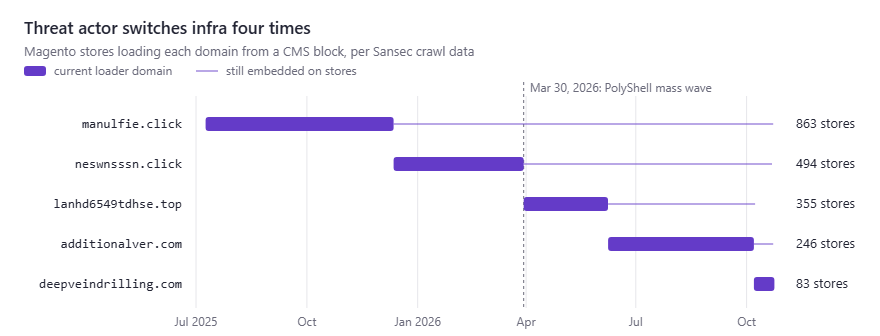
“deepveindrilling.com is the newest web address of a criminal group that breaks into online stores. The group adds a small piece of code to the store’s pages.” Sansec’s analysis states. “The group has done this to 953 stores since July 2025, mostly Magento shops. It moves to a new address every few months.”

The group’s latest domain is deepveindrilling.com. Sansec found it in the CMS blocks of 83 stores, almost all running Magento. CMS blocks are content sections that Magento adds to store pages. The domain was registered on October 6, 2026, and the first stores began loading it the following evening.

This is the fifth domain linked to a campaign that Sansec has tracked since July 2025 and reported in March as the PolyShell mass attack. Most stores using the latest domain had already been targeted. Of the 83 stores, 60 had previously loaded one of the group’s malicious scripts, and 34 had been doing so since October 2025.

The domain sits behind Cloudflare, and its front page returns a 404. It only answers script requests from visitors of infected stores. The loader code lives in the cms_block table, and Sansec’s scanner, eComscan, found it there on 148 server installs over the campaign, never in core_config_data or theme files.

eComscan first found the new loader at 21:54 UTC on October 7. By the end of October 8, Sansec’s crawler had found it on 74 stores, as two scripts. The first reads a value called fpCode from the visitor’s browser storage, and when the value is set, the script puts the stored code in an invisible div and clicks it. The browser then runs the code as an event handler, without using eval().

Nothing in the block writes fpCode, so the script from deepveindrilling.com has to set it. A visitor who received the payload once runs it again on every later page view, even when the domain is offline or blocked. The March version deleted its stored payload after one run.

On October 23 the operator rewrote the blocks again, and the loader appeared on 9 more stores. All 71 stores Sansec re-crawled by October 24 run the new version. It replaces the plain script tag with an inline loader that sends a browser fingerprint to https://deepveindrilling.com/?s=49b7ca5f&fp=.

The fingerprint flags automated browsers through navigator.webdriver, Selenium globals and ChromeDriver’s cdc_ properties. It also adds the GPU name from WebGL, CPU cores, memory, screen size, time zone, languages and client hints. The server picks its response from all of that.

The filter works. When urlscan.io loaded an infected store with an automated Chrome browser, it got HTTP 200, and Sansec found no added content in the page. Sansec hasn’t captured the final payload yet.

Older payloads give a hint of what real visitors get. Sansec Watch, the firm’s monitoring service for content security policies, shows what the earlier stage served. On December 12, 2025, a customer logged in to an infected store got a script from manulfie.click that loaded https://crypto-insider.top/ssl/ and, five minutes later, https://leqdger.click/ssl/.

On December 15 and 16, neswnsssn.click inserted the same leqdger.click script on two more stores. leqdger.click is a misspelling of the crypto wallet brand Ledger. It was registered on September 12, 2025 and has since expired.

Before October, the second script was the “Script (async)” integration of Keitaro, a commercial ad tracker that doubles as a traffic distribution system, a tool that sorts visitors. It sends the referrer, page title and query string to a base64 encoded URL such as https://additionalver.com/Mb2z8J?&se_referrer=, where the path is the Keitaro campaign alias. The system then decides per visitor whether to return a payload, a redirect or nothing.

“When Sansec requested the additionalver.com script as a Windows desktop visitor on October 24, it returned QWE=123;, a statement that does nothing, and set a cookie that marks the visitor for 24 hours. deepveindrilling.com drops Keitaro and moves the bot filtering into the loader.” continues the report.

Here are the five loader domains over 15 months:

DomainRegisteredFirst seen on storesStores
manulfie.clickbefore July 2025, re-registered 2026-05-232025-07-09863
neswnsssn.clickbefore December 2025, re-registered 2026-05-222025-12-12494
lanhd6549tdhse.top2026-03-252026-03-30355
additionalver.com2026-06-072026-06-08246
deepveindrilling.com2026-10-062026-10-0783

Two other domains were found on a small number of stores: hdfdsi84j3h.top, registered three minutes after lanhd6549tdhse.top, and c85grt98sd.com.

Two older domains, neswnsssn.click and manulfie.click, expired and were registered again in May 2026. Both now use the nameservers of abovedomains.com, a domain parking service. Between August and October 2026, Sansec still found the manulfie.click loader on nine stores and the neswnsssn.click loader on six. When visitors open these stores, their browsers send information about the previous page and the current page title to the new domain owner. The browsers also run any script returned by that domain.

Sansec Watch received reports of visitors’ browsers connecting to all four earlier domains. One domain, additionalver.com, was linked to around 52,000 reports.

The October activity did not rely on a new vulnerability. Of the 83 affected stores, 60 had already been infected. Earlier attacks appear to have exploited file upload flaws in Magento. In March, the group injected its malicious code into 471 stores in just one hour by uploading webshells through PolyShell (CVE-2026-48356).

Some infected Magento stores had files uploaded through PolyShell or SessionReaper (CVE-2025-54236). In a separate group of 3,024 stores affected by another skimmer, the infection rate was 32%.

One Magento 2.4.7-p1 store contained PolyShell webshells disguised as PNG images, alongside malicious code in a CMS block. The code switched from additionalver.com to deepveindrilling.com on October 7. The store had not installed Adobe’s PolyShell fix, APSB26-73.

However, installing all patches does not guarantee a store is safe. Another store running Magento 2.4.7-p10 had no missing core patches but was infected on October 23. Earlier scans had already found a rogue admin account and a GSocket backdoor.

Sansec recommends checking CMS content for malicious code, including base64-encoded domains. Administrators should search both the cms_block and cms_page tables for suspicious patterns such as fpCode and se_referrer. They should also inspect uploaded files for webshells, check for unknown admin accounts, and look for suspicious processes. Removing the malicious scripts is not enough: store owners must also identify and fix the vulnerability or backdoor that allowed the attackers in.

After cleanup, change the database, admin and API integration passwords. Install APSB26-73 for PolyShell and APSB25-88 for SessionReaper. Sansec Shield blocks both attacks while you schedule the upgrade.

Sansec lists the indicators of compromise at the end of its report.

“If your store loads any domain from the indicators of compromise, the attacker can write to your database. Deleting the script does not remove that access. See How to check your store.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Magento)

  • ✇Security Affairs
  • AI-Generated Fake Bank Calls and NFC App Enabled €380,000 Fraud, Dutch Police Say Pierluigi Paganini
    Dutch police arrest two men over AI-voiced bank fraud that allegedly used a fake app to steal card data from 170 victims, causing €380,000 in losses. Rotterdam police have arrested two men over a new type of bank fraud that used AI-generated phone calls, a fake banking app, and NFC technology to steal bank card data. In just three weeks, the scheme allegedly cost 170 victims around €380,000. “Rotterdam police arrested two suspects accused of a new form of bank-helpdesk fraud. The operati
     

AI-Generated Fake Bank Calls and NFC App Enabled €380,000 Fraud, Dutch Police Say

26 de Outubro de 2026, 12:06

Dutch police arrest two men over AI-voiced bank fraud that allegedly used a fake app to steal card data from 170 victims, causing €380,000 in losses.

Rotterdam police have arrested two men over a new type of bank fraud that used AI-generated phone calls, a fake banking app, and NFC technology to steal bank card data. In just three weeks, the scheme allegedly cost 170 victims around €380,000.

“Rotterdam police arrested two suspects accused of a new form of bank-helpdesk fraud. The operation allegedly caused around €380,000 in losses for 170 victims in just three weeks.” NL Times reports. “The suspects allegedly used AI-generated phone calls and a fake banking app to copy victims’ bank cards remotely, allowing accomplices to withdraw thousands of euros. Victims came from across the Netherlands and ranged in age; dozens were in their twenties and thirties.”

The suspects allegedly used AI-generated calls to trick victims into believing their bank accounts were at risk. They then persuaded them to install a fake banking app and scan their bank cards with their phones. The app used NFC to capture card data, which accomplices could use to withdraw money. Victims came from across the Netherlands and included people of all ages, with dozens in their twenties and thirties.

A 23-year-old man from Vaassen, in Gelderland, is suspected of developing the technology and directing the group. A 25-year-old from Ede, also in Gelderland, is suspected of coordinating the operation. On Tuesday, a Rotterdam court ordered both men to remain in custody for at least another 90 days while the investigation continues.

The case started in mid-September, when Dutch banks reported the new fraud through the Electronic Crimes Task Force (ECTF). That’s a partnership of banks, police and prosecutors that shares information and expertise to fight financial and digital crime. Within days of consulting the task force, Rotterdam’s cybercrime team had identified the digital infrastructure used by the group.

Investigators monitored the servers to understand how the operation worked. They traced the people behind the technology, the phone calls made to victims, and the cash withdrawals.

The scam started with a recorded message warning victims about suspicious activity on their bank accounts.

“The callers used artificial intelligence (AI) to produce dozens of recordings featuring different voices, banks, companies, and scenarios. Victims were asked to press 1 if they did not recognize the alleged activity.” states the report. “They were then connected to someone posing as a bank employee.”

The message asked people to press 1 if they did not recognize the activity. They were then connected to someone pretending to be a bank employee. Following a prepared script, the caller pressured them to act quickly and take steps to block their bank cards.

The fake employee told victims to download an app and hold their bank card against the phone to scan it. The criminals presented this as a way to secure the accounts.

If a caller ever asks you to scan your card with an app, hang up and phone your bank on the number printed on the card.

According to police, the app sent data from the card’s near-field communication (NFC) chip, the technology behind contactless payments, to an app run by an accomplice. That person waited at a cash machine or payment terminal and could withdraw thousands of euros without the victim realizing what was happening.

“Police described this technical method as one they had not encountered before.” the report concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, NFC)

  • ✇Security Affairs
  • Researchers Uncover Rentable Android Spyware uCreater Targeting WeChat and Telegram Pierluigi Paganini
    uCreater is Android spyware disguised as trusted apps, stealing credentials, messages and wallet data through a rentable platform. uCreater is a rentable Android spyware platform that hides inside repackaged legitimate apps, targeting messaging services and mobile wallets. Its YingGai framework can intercept one-time passwords, steal account and chat data, collect contacts, manipulate sessions and spoof camera feeds to bypass identity checks. Victims may install modified versions of Telegram
     

Researchers Uncover Rentable Android Spyware uCreater Targeting WeChat and Telegram

26 de Outubro de 2026, 09:11

uCreater is Android spyware disguised as trusted apps, stealing credentials, messages and wallet data through a rentable platform.

uCreater is a rentable Android spyware platform that hides inside repackaged legitimate apps, targeting messaging services and mobile wallets. Its YingGai framework can intercept one-time passwords, steal account and chat data, collect contacts, manipulate sessions and spoof camera feeds to bypass identity checks. Victims may install modified versions of Telegram, WeChat or GCash through sideloading or social engineering.

Researcher Ovi found stolen data on a control server, but the number of victims and links between operators and customers remain unconfirmed.

“The repackaged APK can be relatively thin: target-specific instrumentation is retrieved after installation from the operator’s Alibaba OSS and MinIO infrastructure, including buckets and paths named Huuk_<target> and fengzhuang-app (literally, “packaging”). Distribution hosts include telegram-apk.uzyzx.com.” researcher Ovi states. “I could reconstruct much of the post-installation execution chain from the recovered code, but I could not directly establish the initial delivery mechanism for every victim.”

Ovi rebuilt most of the chain from recovered code but couldn’t establish how every victim got the first install.

The product is older than the samples. The package com.ucreater.autotool dates to about 2014, Windows tools tied to ucreater.com were signed between 2016 and 2019, and the YingGai mobile line shows up in records from September 2021. The samples Ovi studied run from 2024 to 2026: uip.exe builds from February to December 2024, Telegram repacks from July and November 2024, the WeChat host and Telegram framework from December 2024, and the Onion Box client from March 2026. The control server’s ICP filing, 湘ICP备2024061212号, dates to 2024.

The infrastructure hints at scale, though not at victim numbers. Ovi counts about 20 target apps with confirmed code support, six operator domains with dozens of subdomains, three Redis buses, two MQTT buses, and a cloud-phone cluster in Changsha spread across several ISPs. A Censys search for the operator’s Tengine gateway fingerprint returned roughly 48 hosts. It looks like a multi-year product sold to many downstream operators, but he can’t say how many customers used it or how many devices fell.

Attributing the platform to a specific legal entity is more difficult. Hunan Youchuang Technology is linked to the ucreater.com brand and a self-signed certificate on videoflow.cn. Changsha Sukai Network holds the ICP filing for the control server’s main domain, qianxuncc.cn, while Changsha Zhuoqing E-commerce appears as the signing identity on uip.exe, using a DigiCert certificate. A common owner is plausible but unproven.

Another lead involves hunanzhijing.com, a domain belonging to the Hunan Intelligent Police Public Safety Technology Research Institute. It shares the same gateway fingerprint, and an official Hunan document connects the institute to an intelligent-policing research project. However, shared cloud infrastructure establishes only co-tenancy, not ownership or operational involvement. There is no evidence that the police developed or operated uCreater.

Other infrastructure links also require caution. A Thailand-based relay used by the Telegram component, hosted on Huawei Cloud, also served gambling websites, an advertising-account service and an SMS service. The cloud-phone web client displayed a certificate for another vendor, while the gateway served a Vue application titled 舆情交易, meaning “public-opinion trading”. These observations are leads for further investigation, not proof of common ownership.

uCreater relies on app virtualization, a technique already identified by Zimperium as a growing mobile threat. VirtualApp runs another application inside a container, LSPatch merges code hooks into repackaged apps without requiring root access, and Pine hooks Android’s runtime. Together, these components allow malicious code to operate inside a legitimate app while it is signed in and has access to decrypted data.

“uCreater is notable because it turns these techniques into a reusable, remotely managed product.” the researchers continues.

Operators distribute modified versions of Telegram-X, Telegram-Web and other messaging apps, integrating modules through LSPatch or loading them from an asset called TgJarPine.dex. WeChat can instead run inside a VirtualApp container, including the va_vx or Onion Box host. LSPatch also stores the original APK under cache/lspatch/origin/*.apk. The presence of this path or the specific asset can help identify an infected device.

The approach differs from GodFather, a banking trojan documented by Zimperium that runs apps in a virtual container and displays fake overlays to capture credentials. uCreater operates inside the real application without relying on an overlay. It uses XposedBridge hooks, reflection and access to the app’s own database interfaces. This allows it to reach beyond login screens and potentially support any application for which the vendor develops a module. Ovi found no evidence linking the two platforms.

One distinguishing feature is a local command server embedded in each hooked application. It exposes around 40 numbered handlers, with descriptions and parameters that allow operators to discover available functions. The code supports device monitoring, contact and SMS collection, installed-app enumeration, message sending, chat-history retrieval, session management and account-related actions.

The Telegram module can execute SQL queries directly against the application’s live database through its own interface. Its Db_MessagesStorageRawQuery handler accepts operator-supplied SQL and returns results through compatibility classes that recreate Telegram objects. This can expose information that would otherwise be protected in the app’s encrypted or locally stored data while the application is running.

The module also hooks Telegram’s SRPHelper.getX routine, capturing the two-step verification password in cleartext before hashing and storing it for exfiltration. The code provides functions to list or reset sessions, change or confirm a linked phone number, delete an account and lock users out. It can also remove its own session from the victim’s device list, potentially concealing the operator’s access. Ovi stresses that the source code demonstrates these capabilities, not that every action has been successfully performed against victims.

The implant retrieves its control-server address from Redis using the Domain key, optionally selecting a value for a particular channel. It caches the address and can fall back to a hardcoded value, explaining why callback domains differ between builds. Signed JSON beacons report to endpoints under /api/callback/Tg*, while command requests include a device fingerprint and signature and use retries with increasing delays.

Updates and additional code arrive through Alibaba Object Storage Service (OSS) and MinIO. The Telegram module retrieves an update manifest and hooks from designated storage paths, while a contacts.vcf file can supply contact information. The WeChat component subscribes to a Redis channel identified by a device-specific machine ID, with its host and credentials embedded in a child code file.

The WeChat module focuses on account access rather than chat-history collection. Its _2_0_UploadAppLoginInfo command retrieves login identity information, after which the app data can be packaged, uploaded to OSS and used in account cloning. Ovi found no evidence that the examined sample accessed WeChat’s encrypted database.


Ovi tested uCreater on a Pixel 10 Pro running Android 17 and found that its bundled Pine engine fails because of changes to Android’s internal APIs. The latest sample, dated July 29, 2026, still uses the outdated engine. Although this creates obstacles for operators, updating Pine could restore functionality, and other devices remain untested. Ovi also identified five samples that successfully contacted the control server, confirming active deployments targeting Telegram, Telegram-X and WeChat.

Ovi and researcher Jurre discovered the platform’s source code after finding an exposed GitLab server. Other infrastructure was protected by IP allowlists, but this server contained the control platform’s source code, configuration and operational details.

The repositories revealed Spring Cloud services for command dispatch, authorization capture, data collection, backups and message bridging, alongside a Vue-based administration console. Thirteen repositories contained commit histories identifying roughly three dozen developers, with activity timestamps consistent with China time. At least one commit used a corporate email domain associated with Tanzhou, a Changsha software firm.

uCreater’s backend is a rented, multi-tenant platform that lets operators manage infected devices, steal account data and automate contact collection. Kafka, RocketMQ, Redis and Nacos coordinate commands and schedule activity to avoid triggering security controls. The infrastructure runs on Aliyun and Huawei Cloud, with control services and storage hosted in China. Although GitLab records identify developers behind key components, Ovi stresses they are not confirmed operators. The recovered backend did not appear to support Telegram, and some callback domains are no longer active.

Ovi attributes the platform to a vendor in Changsha and Hunan operating through three companies, each linked to a different technical or infrastructure artifact. The reseller model, focus on mobile wallets and theft of authentication codes suggest financially motivated crime, but the researcher presents this as an assessment rather than a proven fact.

The technical findings show that uCreater goes beyond a conventional banking trojan or a tool that merely steals credentials. By embedding code inside legitimate applications, it can manipulate sessions, access account data, collect contacts and potentially take control of messaging accounts. Its rented, multi-tenant architecture also allows different operators to use the same underlying platform.

The scale of the infrastructure indicates a substantial operation, but neither the number of customers nor the number of compromised devices has been established. Likewise, infrastructure overlaps and developer records provide investigative leads, not conclusive proof of who operated the spyware or who was responsible for individual attacks.

“Mapping points to a commercial resale structure, and targeting driven by wallets and OTPs. My assumption is financially-motivated crimeware.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Security Affairs
  • SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 5 Pierluigi Paganini
    Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis
     

SECURITY AFFAIRS AI-CYBERSECURITY NEWSLETTER ROUND 5

25 de Outubro de 2026, 14:49

Security Affairs AI-CYBERSECURITY newsletter includes a collection of the best articles and research on AI in the international landscape

Artificial intelligence is rapidly changing cybersecurity, reshaping both the techniques used by attackers and the tools available to defenders. AI agents can automate tasks, analyze large amounts of data, discover vulnerabilities and accelerate offensive operations. At the same time, AI is creating new capabilities for threat detection, incident analysis and response. Security Affairs’ new newsletter follows this evolution, covering every week the latest threats, attacks, vulnerabilities and developments at the intersection of AI and cybersecurity.

AI-CYBERSECURITY Newsletter

25-year-old Israeli founder sells stealth AI startup for up to $35 million without raising capital

OpenAI claims 100-plus secret files followed ex-employee back to Apple  

Open weight takes 71.5% of tokens and 23% of spend

OpenAI Models Hacked Data Portals, Raided a Crypto Wallet to Finish Tasks  

Meta removes language that raised scraping and AI training concerns

Can LLMs Supercharge Geolocations? Our Tests Show Big Improvements But Humans Remain Key 

Agents are your newest insiders. Security must move at their speed  

Anthropic Acquires Confidential AI Startup Opaque Systems

ATT&CK v20: Critical Infrastructure Campaigns, Adversary Use and Abuse of AI, & Iranian Cyber Espionage  

UK Election Watchdog Develops AI System to Flag Deepfakes Within 3 Hours

Meta’s Muse hits 10M U.S. downloads in 40 days, a milestone reached by only 11 other apps  

Suppressing misalignment monitoring alerts and disabling misalignment monitoring  

Anthropic pitches AI safety bill that may block a model if 50+ people could be killed  

Making attacking agents pay  

LiteLLM Compromised in Supply Chain Attack Delivering Credential Stealer and Backdoor

AI Just Found a Bug That Puts up to 70% of the World’s Websites at Risk

AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise  

Torvalds: AI is fine for competent devs, but spare us the ‘drive-by’ patches

Our latest defenses against evolving web scams

UK government sets out $800 million of AI security funding

Securing our frontier model training environment  

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Security Affairs
  • SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 120 Pierluigi Paganini
    Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Auditing the auditor: Unmasking Apex Accelerator GhostAction Attack Escalates By Targeting GitHub Users       Plex vulnerabilities being exploited in the wild to drop a cryptominer   WordPress Rank Math SEO PRO Plugin 3.0.123 is vulnerable to a high priority Backdoor   ROMULUS: Analysis of a New Multi-Payload ClickFix Delivery
     

SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 120

25 de Outubro de 2026, 10:27
  • ✇Security Affairs
  • PHP2Shell: Millions of Attacks, No Confirmed Successful Exploits Yet Pierluigi Paganini
    PHP2Shell attacks have surged into the millions, but no successful exploitation is confirmed. Patch it immediately. On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP req
     

PHP2Shell: Millions of Attacks, No Confirmed Successful Exploits Yet

23 de Outubro de 2026, 07:52

PHP2Shell attacks have surged into the millions, but no successful exploitation is confirmed. Patch it immediately.

On October 21, PHP released emergency patches for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619 (CVSS score of 9.2), affecting every PHP version that handles web requests. The bug code dates back to PHP 5.4 from 2012, lives in the PHP engine itself rather than in any application, and allows unauthenticated remote code execution via crafted HTTP requests.

Cloudflare researchers observed tens of thousands of exploit attempts within 45 minutes of public disclosure, hundreds of thousands within two hours, and millions by October 22.

Some stats on #php2shell. In the 10 hours before it was publicly announced, across the @Cloudflare network we saw thousands of attempts to exploit it. That jumped to tens of thousands in the 45 minutes post announcement, hundreds of thousands within 2 hours, and millions now.

— Matthew Prince 🌥 (@eastdakota) October 22, 2026

As of October 23, Censys counts over 34.4 million PHP services still running vulnerable versions. Governments, hospitals, and schools across Asia, Europe, and North America have preemptively taken services offline rather than wait.

Below is an image showing the hosts potentially vulnerable to CVE-2026-109618 and/or CVE-2026-109619.

PHP CVE-2026-109618 and/or CVE-2026-109619
Source Censys

Security firms using honeypots report the same pattern: attackers are scanning many servers and trying to exploit the PHP flaws, but no successful remote code execution has been confirmed in real-world attacks. Sophos says this suggests that attackers are also struggling to exploit the vulnerabilities. Even its own security team needed more effort than expected, despite using AI, to develop a working exploit.

However, the risk is growing. VulnCheck researchers have developed an exploit that bypasses ASLR, a security feature that randomizes where code is stored in memory. By combining both vulnerabilities, they can use a memory leak to bypass this protection and run code on the target system. The exploit works, even though there is no evidence of widespread use yet.

The attempts that have been caught so far are mostly scanning, fingerprinting, and botnet delivery attempts. Cowrai’s analysis of PHP2Shell traffic in the wild found connections to a Mirai variant called Potassium, which contacts a C2 server, checks for an HTTP 200 response, then downloads a Linux executable as a follow-on payload.

“The payload, a likely Mirai botnet variant known as Potassium, was not delivered since the exploitation attempt was unsuccessful due to being blocked by Sophos countermeasures.” states the report published by Sophos. “However, analysis of the sample revealed that is an updated and significantly expanded version of the Mirai-derived botnet variant identified in early 2026.”

The malware can download additional files and disrupt networks. It contacts a hard-coded command-and-control server, checks that the server responds successfully, and downloads a file designed to run on Linux. If normal address lookup fails, it can use public DNS servers such as Google DNS and Cloudflare DNS. Like other Mirai malware, it can also launch distributed denial-of-service (DDoS) attacks.

Arctic Wolf found that both malware samples had Ethereum Name Service (ENS) resolution disabled, meaning the feature was available but not active.

“ENS resolution was disabled in both samples, indicating that the capability was present but inactive.” states Arctic Wolf. “If enabled in future variants, it could complicate disruption by reducing reliance on registrars and DNS providers, requiring defenders to block the ENS names, RPC infrastructure, and resolved command-and-control addresses.”

The botnet’s developers have already added the ability to use ENS to find command-and-control (C2) servers. This could help them keep their infrastructure online and make it harder for authorities to take down their domains, but the feature has not yet been enabled.

Sophos blocked the attempted Potassium delivery before it succeeded. But analysis of the sample itself showed it’s a significantly expanded version of the Mirai variant spotted earlier in 2026, with added DDoS capabilities and fallback DNS resolution using public servers like 8.8.8.8 and 1.1.1.1 hardcoded as backup.

PHP2Shell is being compared to Log4Shell because it affects a huge number of systems. The flaw is in PHP itself, so it can affect websites, content management systems and shared hosting services. Even a basic WordPress site with no extra plugins is at risk if it uses a vulnerable PHP version.

Fixes are available in PHP versions 8.2.35, 8.3.36, 8.4.27 and 8.5.12. Older versions, including 7.4, 8.0 and 8.1, need fixes provided by their software distributors or an upgrade to a supported version.

Cisco Talos notes that scanning for flaws and using public exploit code is easier than building attacks into custom tools. Advanced attackers may still be developing those tools, so administrators should use this time to patch vulnerable systems.

“The true impact of this vulnerability will take time to evaluate.” concludes Talos. “These types of vulnerabilities that impact core technologies tend to cascade into other platforms and applications as they evaluate impact and provide associated patching, harkening back to the waves of exploitation that we saw after Log4J.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, PHP2Shell)

  • ✇Security Affairs
  • PHP2Shell Attacks Started Four Days Before Public Disclosure, AWS Reports Pierluigi Paganini
    AWS detected PHP2Shell exploit attempts four days before disclosure, highlighting the risk of attackers exploiting critical flaws before patches arrive. Attackers attempted to exploit two critical PHP vulnerabilities four days before the flaws became public, according to Amazon Threat Intelligence. “Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating to Oct. 17, 2026, in MadPot telemetry, four days before public disclosure of CVE-2026-109618 and CVE-2026-109619.
     

PHP2Shell Attacks Started Four Days Before Public Disclosure, AWS Reports

22 de Outubro de 2026, 11:55

AWS detected PHP2Shell exploit attempts four days before disclosure, highlighting the risk of attackers exploiting critical flaws before patches arrive.

Attackers attempted to exploit two critical PHP vulnerabilities four days before the flaws became public, according to Amazon Threat Intelligence.

“Amazon Threat Intelligence identified a PHP2Shell exploitation attempt dating to Oct. 17, 2026, in MadPot telemetry, four days before public disclosure of CVE-2026-109618 and CVE-2026-109619.” reads the report published by Amazon team.”The exploit attempt originated from an IP address associated with a commercial anonymization network. While the vulnerability was under embargo, the targeting of a honeypot from an anonymized IP address suggests the activity was conducted by a threat actor, though it remains unclear how the actor acquired exploit information prior to disclosure.”

The activity began on October 17, 2026, and appeared in telemetry from MadPot, AWS’s network of honeypots designed to attract and study malicious activity. The company said the first attempt targeted a honeypot from an IP address linked to a commercial anonymization network. The vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, were still under embargo at the time.

AWS believes the use of anonymized infrastructure suggests a threat actor was behind the activity. However, the company hasn’t established how the attacker obtained information about the vulnerabilities before their public disclosure, nor has it confirmed that the early attempts would have succeeded against real-world systems.

The first attempt wasn’t an isolated event. AWS detected multiple proof-of-concept exploits on October 21, with the earliest appearing at around 02:00 UTC, roughly 12 hours before the scheduled public release and patch at 14:00 UTC.

Between 02:00 and 08:00 UTC that day, AWS observed further attempts against MadPot from additional anonymized infrastructure. The payloads and anonymization services varied, leading the company to suspect that multiple actors were involved.

After the embargo ended and PHP released the fixes, more proof-of-concept exploits appeared within hours. AWS reported that attackers used them against its sensors almost immediately, describing PHP2Shell as being broadly exploited in the wild.

The findings show why the date of a public security advisory can’t always serve as the starting point for an incident investigation. In this case, defenders had to account for activity that began before they could publicly identify the vulnerabilities.

“The actual payloads and choices in anonymization infrastructure varied, suggesting these were multiple actors.” continues the report. “Technical analysis is ongoing, and it’s unclear if any of these attempts would have succeeded in real-world systems.”

PHP2Shell refers to two critical flaws in the PHP runtime that can allow unauthenticated remote code execution. An attacker may be able to send a specially crafted web request and run commands on a vulnerable server without first logging in.

PHP published fixes on October 21. The corrected releases are PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, according to the official PHP security notice.

The vulnerabilities affect PHP itself, rather than a specific website application. As a result, updating WordPress, Drupal or another application won’t fix the underlying problem if the server continues to run a vulnerable PHP runtime.

AWS says there is no configuration-only workaround that fully addresses both flaws. Organizations should install the fixed PHP version as soon as possible and check whether their hosting provider, operating system vendor or container image has supplied the necessary update.

For systems that can’t be patched immediately, AWS suggests considering whether blocking multipart file uploads is practical. Administrators should assess the impact on their applications before applying that restriction, and they shouldn’t treat it as a replacement for installing the fixes.

AWS recommends reviewing web server logs for suspicious requests, particularly POST requests containing the PHP_SESSION_UPLOAD_PROGRESS string in multipart form data. Security teams should also look for unexpected processes launched by PHP and unexplained changes to files on web application servers.

These checks matter because an attack may leave evidence beyond the original HTTP request. Unexpected command interpreters, newly created files or unusual process activity can help investigators determine whether an attacker progressed beyond probing a vulnerable endpoint.

AWS also published six IP addresses associated with observed activity:

  • 103.216.220.92, observed on October 17
  • 31.223.184.166, observed on October 21
  • 37.19.200.5, observed on October 21
  • 134.209.159.64, observed on October 21
  • 103.114.163.188, observed on October 21
  • 95.217.98.37, observed on October 21

These addresses require careful handling. AWS warns that some belong to shared anonymization infrastructure and aren’t exclusive to PHP2Shell activity, so organizations should investigate matching events rather than automatically blocking every address.

The Cloudflare analysis of PHP2Shell provides additional context. Cloudflare said it had deployed web application firewall protections before public disclosure and had already observed attack traffic targeting its customers, including attempts to change payloads to evade those protections.

A web application firewall can help reduce exposure, but it doesn’t replace patching. Defenders should combine updated software with log analysis, process monitoring and checks for suspicious file changes.

AWS draws a broader lesson from the incident: organizations shouldn’t assume that exploitation begins only after a vulnerability becomes public. The October 17 activity shows that attackers may obtain or develop exploit information while a flaw is still under coordinated disclosure.

Attackers are using AI to develop exploits faster, sometimes within hours of a patch being released. Security teams need to patch critical systems quickly and investigate attacks from the earliest known date. For PHP2Shell, AWS recommends checking logs and activity from October 17 onward, including suspicious behavior that detection tools may not yet recognize.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, PHP)

  • ✇Security Affairs
  • FBI and CISA Warn of SafePay Ransomware Attacks on 600 Organizations Pierluigi Paganini
    SafePay ransomware has hit 600+ organizations since 2024, using stolen credentials, VPN access and double extortion to pressure victims into paying. CISA, the FBI, the US Secret Service, Germany’s Landeskriminalamt Rheinland-Pfalz, and two UK law enforcement agencies jointly published an advisory this week on SafePay, a ransomware group they describe as one of the most active operations currently running. The group has breached at least 600 organizations across critical infrastructure sector
     

FBI and CISA Warn of SafePay Ransomware Attacks on 600 Organizations

22 de Outubro de 2026, 03:48

SafePay ransomware has hit 600+ organizations since 2024, using stolen credentials, VPN access and double extortion to pressure victims into paying.

CISA, the FBI, the US Secret Service, Germany’s Landeskriminalamt Rheinland-Pfalz, and two UK law enforcement agencies jointly published an advisory this week on SafePay, a ransomware group they describe as one of the most active operations currently running. The group has breached at least 600 organizations across critical infrastructure sectors since August 2024, spanning North America, South America, Europe, and Australia.

“Since August 2024, SafePay ransomware group’s operations have affected a wide range of businesses and critical infrastructure in North America, South America, Europe, and Australia. SafePay ransomware was among the most active ransomware groups in 2026. The SafePay threat actors have impacted at least 600 separate victims from multiple critical infrastructure sectors.” reads the joint advisory, “The authoring agencies encourage organizations to implement the recommendations in the Mitigations section of this advisory to reduce the likelihood and impact of SafePay ransomware incidents.”

SafePay appeared in mid-2024 as an independent ransomware group that operates without affiliates. This is unusual because many major ransomware groups work like franchises, allowing other criminals to use their tools and services. SafePay grew as groups such as BlackCat and LockBit declined, and its activity has continued. The advisory includes findings from FBI, US Secret Service, and German investigations through August 2026.

SafePay’s preferred entry points are exposed credentials, brute force password attacks, and VPN access.

“The FBI, USSS, and cybersecurity researchers observed SafePay threat actors obtaining initial access [TA0001] to organizations through various means, including credential exposure, implementing brute force password attacks [T1110], and exploiting virtual private network (VPN) access.” states the advisory. “SafePay threat actors use the IP addresses of the VPN provider “Mullvad” to attain initial access—specifically, SafePay threat actors use phished account profiles to access victim networks to exploit the following known Common Vulnerabilities and Exposures (CVEs) for edge device products”

Security teams should watch for unusual login attempts coming from Mullvad VPN IP addresses. SafePay also uses stolen account credentials and automated scripts to exploit known vulnerabilities in internet-facing devices. These include Cisco VPN flaws from 2020 and 2023, a Veeam vulnerability, and a SonicWall access control issue.

Once inside a network, the attackers rely on common tools rather than specialized malware. They use PsExec, WinRM, RDP, and PowerShell to move between systems. A PowerShell script called ShareFinder.ps1 helps them find shared folders and identify valuable data. Mimikatz is used to steal credentials, while AnyDesk and TeamViewer provide remote access. To steal data, the group uses tools such as FileZilla, RClone, WinSCP, and even OneDrive.

Encryption uses a ChaCha20 stream cipher combined with RSA for key exchange, with methods customized based on file type and size. Files get the .SafePay extension appended.

“Data encrypted with the SafePay ransomware variant (appended with .SafePay) cannot be recovered without the decryption key. SafePay threat actors hold the encrypted data for ransom and typically demand a subset of company revenue in cryptocurrency in exchange for decryption software.” states the advisory. “SafePay threat actors leave a ransom note on the victim’s system, typically on the desktop or root directory, advising them that SafePay locked their system and to reach out over a chat portal at a TOR .onion website link with a victim ID as the login. “

Paying the ransom remains the only path to decryption for encrypted files, and even that isn’t guaranteed to work.

The group runs a double-extortion model: steal first, encrypt second, threaten to post the stolen data publicly if the victim doesn’t pay. After encryption, SafePay sends victims to a Tor-based chat portal for negotiations. A representative also makes phone calls to apply pressure. If no payment comes, everything goes on the leak site. The group also deletes Volume Shadow Copies and resets network-attached backup devices to factory settings, which is the operational equivalent of cutting off every exit before the fire starts.

The advisory recommends several basic security measures. Keep internet-facing devices, especially VPNs and firewalls, up to date. Prioritize vulnerabilities listed in CISA’s Known Exploited Vulnerabilities catalog. Enable multi-factor authentication (MFA) for VPNs, webmail, and accounts that access critical systems.

Limit the number of accounts allowed to use administrative tools. SafePay relies on legitimate Windows tools to move through compromised networks, making its activity harder to detect. Organizations should also keep backups offline, encrypted, and immutable so attackers cannot access, change, or delete them.

CISA also recommends reviewing all accounts with admin privileges, setting time-limited access where possible, and disabling command-line tools for any account that doesn’t need them.

The advisory includes IOC files in STIX XML and JSON format, full MITRE ATT&CK mapping, and complete file and IP indicators.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ransomware)

  • ✇Security Affairs
  • NSO Spyware Pegasus Hit a Serbian University Rector Six Days Before Snap Elections Pierluigi Paganini
    Citizen Lab confirmed Pegasus on a Serbian rector’s iPhone 6 days before elections, raising the known civil society spyware target count to 16. The Citizen Lab published a research note confirming that the iPhone of Vladan Đokić, Rector of the University of Belgrade, was infected with NSO Group’s Pegasus spyware sometime in 2026. The infection used a zero-click exploit, meaning Đokić did nothing to trigger it. No tap, no opened file, nothing. “In collaboration with the SHARE Foundation,
     

NSO Spyware Pegasus Hit a Serbian University Rector Six Days Before Snap Elections

21 de Outubro de 2026, 02:57

Citizen Lab confirmed Pegasus on a Serbian rector’s iPhone 6 days before elections, raising the known civil society spyware target count to 16.

The Citizen Lab published a research note confirming that the iPhone of Vladan Đokić, Rector of the University of Belgrade, was infected with NSO Group’s Pegasus spyware sometime in 2026. The infection used a zero-click exploit, meaning Đokić did nothing to trigger it. No tap, no opened file, nothing.

“In collaboration with the SHARE Foundation, we found with high confidence that Professor Vladan Đokić, Rector of the University of Belgrade, and prominent supporter of the Serbian student movement, was hacked with NSO Group’s Pegasus spyware in 2026.” states Citizen Lab.

Đokić became a prominent figure in Serbia’s student-led pro-democracy movement after refusing to facilitate a government crackdown on protesters. Serbian authorities raided his offices on March 31, seizing computers and servers. The Citizen Lab found the infection with high confidence and describes the investigation as ongoing.

The timing raises questions. The discovery came just six days before Serbia’s snap parliamentary elections on October 25. Until September, Đokić had been publicly named as a possible candidate to lead the Student List. Since he spoke out against the crackdown, pro-government media have repeatedly attacked him.

Citizen Lab explained what a Pegasus infection means. Once installed, the spyware can give its operator the same access to a device as its owner. This includes private and encrypted messages, and the ability to turn on the microphone and camera without the owner’s knowledge.

“With the assistance of the SHARE Foundation, the Citizen Lab analyzed forensic artifacts collected from Vladan Đokić’s Apple iPhone at his request and with his consent.” reads the report. “We found with high confidence that it was infected with NSO Group’s Pegasus spyware in 2026. The infection leveraged a zero-click exploit.”

In a statement published by the university, Đokić called the spyware “another attempt of intimidation.” He called for an independent investigation, the public release of its findings, and criminal prosecution of those responsible.

“Additionally, we note that Rade Bajić, who, as a prosecutor, investigated official corruption in a failed project in Belgrade, received an Apple Threat Notification.” continues Citizen Labs.

The Citizen Lab also flagged Rade Bajić, a senior prosecutor who worked on the “Generalštab” case, a corruption investigation into the removal of heritage protections from a Belgrade site to clear the way for a luxury development backed by a company linked to Jared Kushner, President Trump’s son-in-law. Bajić says he was removed from the investigation in November 2025 without explanation, and spoke at a student protest in February denouncing political interference in the case.

He received an Apple Threat Notification on August 13 and a reminder on August 27. The Citizen Lab treats this as a high-confidence indicator that his device was likely targeted with mercenary spyware. Forensic analysis of his device is still ongoing and no confirmation of infection has been published yet.

These two cases bring the known total to at least 16 members of Serbian civil society targeted or infected with commercial spyware in 2026. In September, the SHARE Foundation, with support from Citizen Lab and Amnesty International, reported an earlier wave of attacks. The victims included a student protester confirmed to have been infected with Pegasus, opposition party members, and local officials. Those cases occurred around the period leading up to Serbia’s March local elections. The latest confirmed case was discovered just six days before the October parliamentary elections.

Serbia’s security service dismissed the September reports as purely trivial sensationalism and said it operates within Serbian law. Citizen Lab did not identify who was behind the attack on Đokić’s phone. Pegasus is sold only to governments and state agencies, which limits the number of possible operators.

If you received an Apple Threat Notification, treat your device as compromised until a technical expert confirms otherwise. In Serbia, contact the SHARE Foundation. Everywhere else, Access Now’s Digital Security Helpline supports journalists, human rights defenders, and activists. Enable Lockdown Mode on your iPhone immediately, keep iOS updated, and get your close contacts and colleagues screened as well.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Pegasus)

❌
❌