Entrar


EvilTokens made phishing-as-a-service look easy. Then it got taken down
Microsoft, Coinbase and law enforcement took down EvilTokens, a phishing kit that compromised 12,000 inboxes through device-code phishing and AI.
EvilTokens showed up in February 2026 and moved fast. Within months it had compromised more than 12,000 inboxes across over 10,000 organizations.
Microsoft says the EvilTokens platform, operated by Storm-2992, is a phishing-as-a-service kit sold to cybercriminals through Telegram. The service costs $1,500 upfront and $500 per month, with additional tools available for extra fees. Its control panel lets customers build and manage phishing campaigns, customize landing pages, configure domains, track victims, and manage stolen authentication tokens.
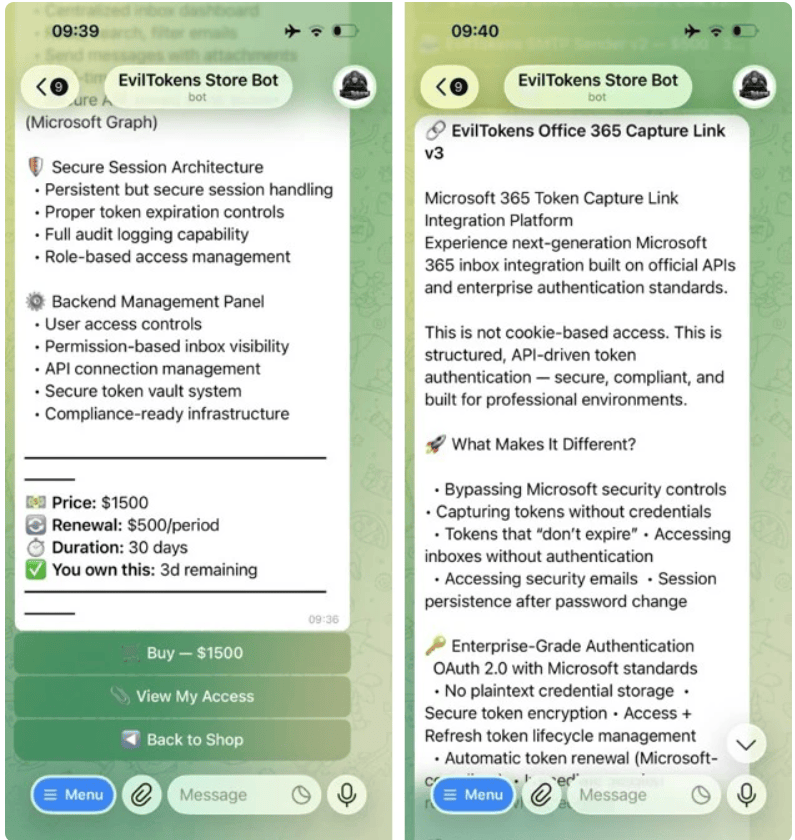
The platform includes 44 themes and uses AI to create targeted phishing emails based on a victim’s role. Lures can impersonate Microsoft services, document signing platforms, cloud providers, payment systems, and other business services.
What made EvilTokens different wasn’t the phishing itself, it was the AI wrapped around it. Once a mailbox was open, an AI assistant sifted through the contents, mapped who controlled payments, and flagged the accounts worth targeting. A task that used to take a skilled operator hours now took the platform seconds, which meant far less skilled criminals could run campaigns that used to require real expertise.
“Post-compromise, EvilTokens enabled threat actors to utilize AI assistants to sift through victim mailbox activity and engineer a phishing message based on the accessible email content. EvilTokens also allowed threat actors to conduct Microsoft Graph reconnaissance to map organizational structure and permissions, enabling continued access and potential lateral movement while tokens remain valid.” reads the report published by Microsoft. “While token-targeting phishing is not new, it has become far more common and industrialized over the last several years as organizations adopted multifactor authentication (MFA).”
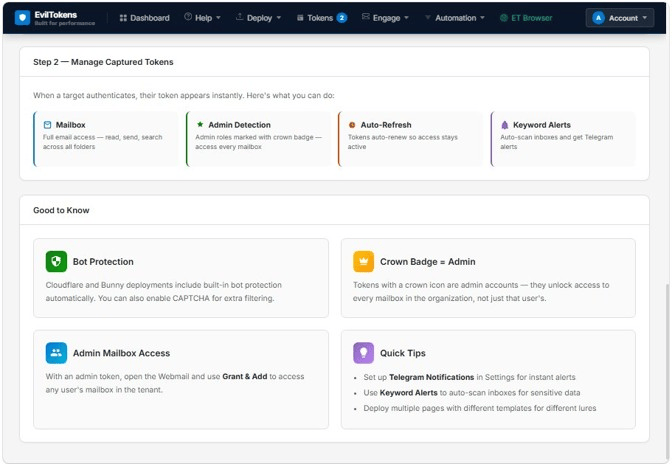
The technique at the core of it is called device code phishing, and it’s worth understanding because it doesn’t touch your password at all. Device code sign-in exists for things like smart TVs and conference room devices that can’t handle a normal login screen. You get a short code on the device, then type it into a browser somewhere else to finish signing in.
“Device code phishing occurs when threat actors insert themselves into this process. Instead of a legitimate device requesting access, the threat actor initiates the flow and provides the user with a code through a phishing lure.” states Micorsoft. “When the user enters the code, they unknowingly authorize the threat actor’s session, granting access to the account without exposing credentials.”
That gap between devices is exactly what gets abused. A fake email, styled as an invoice or a DocuSign request, sends the victim to a page that’s quietly requested a real Microsoft device code behind the scenes. The victim sees the code, gets told to enter it on Microsoft’s actual login page to “verify their identity,” and does exactly that.
Below is the description provided by Coinbase of the attack on Microsoft’s device code login flow:
- The attacker’s access tokens survived password resets. Attackers registered devices in Entra ID for persistent access, created hidden inbox rules to suppress alerts and delete evidence, then impersonated finance staff, vendors, or executives inside live payment threads to redirect payments, including cryptocurrency.
- Victims received convincing, AI-generated emails styled as invoices, shared documents, or voicemail notifications, with malicious links embedded.
- The links led to fake Microsoft or DocuSign pages displaying a code and instructing victims to enter it on Microsoft’s real website to “verify their identity.” Doing so authorized the attacker’s session. Because authentication happened on Microsoft’s legitimate infrastructure, MFA was bypassed entirely.
The victim’s own MFA never gets a chance to fire, because the attacker’s session is the one that gets approved, not theirs. No password stolen, no suspicious login flagged, just a normal-looking authentication that happened to authorize the wrong person.
From there the kit did the boring but effective part. Attackers registered new devices to keep access alive past a password reset, built hidden inbox rules to bury their tracks, and then slid into ongoing email threads to redirect payments, sometimes in cryptocurrency, sometimes straight to a bank account.
Taking it down needed more than one company. Microsoft’s Digital Crimes Unit led the legal side, seizing 50 websites and disabling over 175 domains tied to the operation. Coinbase, Cloudflare, Health-ISAC, OpenAI, Railway, SpyCloud, and Shadowserver all contributed pieces, and the mix says something about how these takedowns actually work now: it’s rarely just the software vendor.
Coinbase’s part is the one worth lingering on, because it’s the least obvious. EvilTokens sold its kits for crypto and moved the proceeds through the Tron blockchain, so Coinbase’s Global Intelligence team followed the money instead of the malware. They traced roughly $1.1 million in revenue across four addresses, found over 1,000 deposits from more than 700 separate wallets, and mapped the full path from payment to cash-out.
That money trail is what led to a name, and the name led to an arrest. On September 11, London’s Metropolitan Police picked up the operator, seizing devices and evidence for examination. One detail from the investigation lands somewhere between alarming and funny: parts of the platform itself were reportedly “vibe coded,” meaning the criminals used AI to help build their own criminal tooling. The irony writes itself.
For anyone defending a network against this, the practical response comes down to a few habits worth making automatic. Treat any device code you didn’t request yourself as an immediate red flag, since no legitimate service asks you to “verify” anything by entering a code it sent you. Verify payment changes through a phone call to a known number, not through the email thread where the request showed up, and push toward passkeys or hardware keys wherever the option exists.
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, phishing)