An exploration of the shift from reactive "assume breach" mentalities to AI-driven prevention, highlighting how Domain-Specific Language Models (DSLMs) empower security architects to eliminate configuration drift and tool sprawl.
The post AI for Security Infrastructure: Rebalancing Cybersecurity for the Decade Ahead appeared first on Security Boulevard.
An exploration of the shift from reactive "assume breach" mentalities to AI-driven prevention, highlighting how Domain-Specific Language Models (DSLMs) empower security architects to eliminate configuration drift and tool sprawl.
NIST Cybersecurity Framework for UK SMEs: A Practical Guide to Identify, Protect, Detect, Respond, and Recover The NIST Cybersecurity Framework is a useful way to organise cybersecurity work around business risk. For UK SMEs, that matters because most teams do not have the time or budget to do everything at once. A framework gives you […]
The post NIST Cybersecurity Framework for UK SMEs: A Practical Guide to Identify, Protect, Detect, Respond, and Recover appeared first on Clear Path Security L
NIST Cybersecurity Framework for UK SMEs: A Practical Guide to Identify, Protect, Detect, Respond, and Recover The NIST Cybersecurity Framework is a useful way to organise cybersecurity work around business risk. For UK SMEs, that matters because most teams do not have the time or budget to do everything at once. A framework gives you […]
Threat modelling using STRIDE for system architects Threat modelling is one of the most useful habits a system architect can build. Done well, it helps you spot design weaknesses before they become expensive problems to fix. Done badly, it turns into a long list of theoretical threats that nobody uses. STRIDE is a simple way […]
The post Threat modelling using STRIDE for system architects appeared first on Clear Path Security Ltd.
The post Threat modelling using STRIDE for system architects appe
Threat modelling using STRIDE for system architects Threat modelling is one of the most useful habits a system architect can build. Done well, it helps you spot design weaknesses before they become expensive problems to fix. Done badly, it turns into a long list of theoretical threats that nobody uses. STRIDE is a simple way […]
Protective security is one of those topics that can sound broader and more complex than it needs to be. For UK SMEs, the practical question is simple: what do you need to protect, how much protection is enough, and how do you make it work without creating unnecessary overhead? Within the NCSC Cyber Assessment Framework, […]
The post Protective Security in the NCSC CAF: A Practical Guide for UK SMEs appeared first on Clear Path Security Ltd.
The post Protective Security in the NCSC CAF: A Practic
Protective security is one of those topics that can sound broader and more complex than it needs to be. For UK SMEs, the practical question is simple: what do you need to protect, how much protection is enough, and how do you make it work without creating unnecessary overhead? Within the NCSC Cyber Assessment Framework, […]
Cyber risk used to be the kind of problem you could delegate. Something for the CISO, the IT team, and maybe an external auditor to worry about once a year. That comfort zone is gone. In the last decade, a new reality has set in: a single cyber incident can erase hundreds of millions of […]
The post The $700 million question: How cyber risk became a market cap problem first appeared on TrustCloud.
The post The $700 million question: How cyber risk became a market cap problem appeared first on Se
Cyber risk used to be the kind of problem you could delegate. Something for the CISO, the IT team, and maybe an external auditor to worry about once a year. That comfort zone is gone. In the last decade, a new reality has set in: a single cyber incident can erase hundreds of millions of […]
Safe vulnerability disclosure for UK SMEs: a practical guide For many UK SMEs, the idea of someone reporting a security weakness can feel unsettling at first. It may sound technical, formal, or even a little confrontational. In practice, safe vulnerability disclosure is simply a controlled way for people to tell you about a security issue […]
The post Safe vulnerability disclosure for UK SMEs: a practical guide appeared first on Clear Path Security Ltd.
The post Safe vulnerability disclosure for
Safe vulnerability disclosure for UK SMEs: a practical guide For many UK SMEs, the idea of someone reporting a security weakness can feel unsettling at first. It may sound technical, formal, or even a little confrontational. In practice, safe vulnerability disclosure is simply a controlled way for people to tell you about a security issue […]
Supplier assurance for UK SMEs: a practical guide to checking third parties without overcomplicating it Most UK SMEs rely on suppliers in some way. That might be payroll software, a managed IT provider, a marketing agency, a logistics partner, or a cloud service that holds customer data. The more your business depends on third parties, […]
The post Supplier assurance for UK SMEs: a practical guide to checking third parties without overcomplicating it appeared first on Clear Path Security Ltd.
Th
Supplier assurance for UK SMEs: a practical guide to checking third parties without overcomplicating it Most UK SMEs rely on suppliers in some way. That might be payroll software, a managed IT provider, a marketing agency, a logistics partner, or a cloud service that holds customer data. The more your business depends on third parties, […]
For many UK SMEs, supply chain resilience is not a specialist security project. It is a business continuity issue. If a key supplier cannot deliver, a software provider has an outage, or a partner mishandles data, the impact can show up quickly in customer service, cash flow, and reputation. The good news is that you […]
The post Supply Chain Resilience for UK SMEs: Practical Steps to Reduce Third-Party Risk appeared first on Clear Path Security Ltd.
The post Supply Chain Resilience for UK SMEs:
For many UK SMEs, supply chain resilience is not a specialist security project. It is a business continuity issue. If a key supplier cannot deliver, a software provider has an outage, or a partner mishandles data, the impact can show up quickly in customer service, cash flow, and reputation. The good news is that you […]
From cybersecurity breaches to natural disasters, disruptive events can occur suddenly and without warning. As a result, it is crucial for organizations to develop resilient plans that not only respond to incidents in real time but also ensure long-term operational survivability. This article examines the concepts of incident response and business continuity, exploring their differences […]
The post Proven incident response and business continuity strategy first appeared on TrustCloud.
The post
From cybersecurity breaches to natural disasters, disruptive events can occur suddenly and without warning. As a result, it is crucial for organizations to develop resilient plans that not only respond to incidents in real time but also ensure long-term operational survivability. This article examines the concepts of incident response and business continuity, exploring their differences […]
Cybersecurity Can Learn from the Artemis Launch
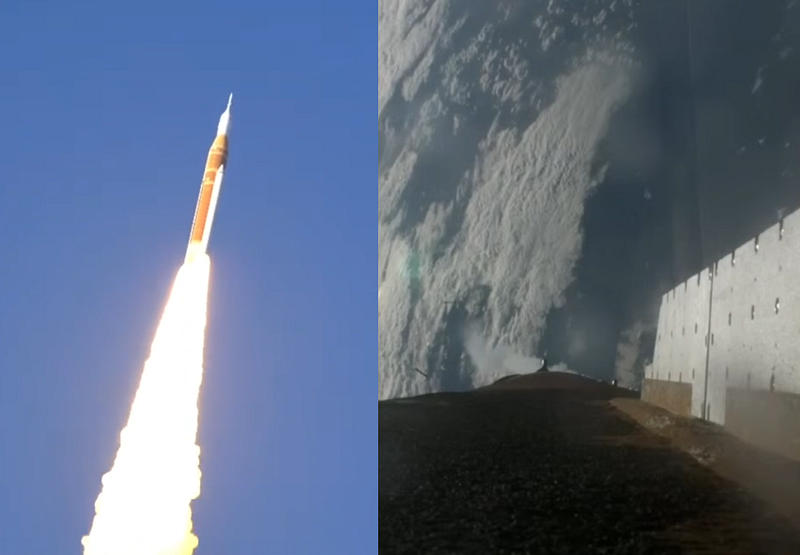
The Artemis II mission, bringing humans back to the Moon, had a successful launch today! An amazing cumulation of efforts to manage the mindboggling combination of risks to push a massive rocket into space, in preparation for a trip to orbit the Moon.
Such endeavors come with tremendous risks, which a world-class team works to minimize, but some residual aspects remain and are accepted.
Congratulations to the entire NASA team!
Cybersecurity C
The Artemis II mission, bringing humans back to the Moon, had a successful launch today! An amazing cumulation of efforts to manage the mindboggling combination of risks to push a massive rocket into space, in preparation for a trip to orbit the Moon.
Such endeavors come with tremendous risks, which a world-class team works to minimize, but some residual aspects remain and are accepted.
Congratulations to the entire NASA team!
Cybersecurity Can Learn
The cybersecurity industry can learn many lessons from today’s Artemis II achievement.
Having strategic capabilities with clear objectives, resources, and accountability is key:
1. Prediction: Understanding the broad scope of risks, which are likely, and how best to manage them.
2. Prevention: Essential to mitigate the greatest risks that could lead to catastrophe.
3. Detection: Constant monitoring to identify problems as they arise and give the best opportunities to react in a timely manner.
4. Response: Well-rehearsed actions that intercept problems to minimize overall impact.
Lessons from each area create a feedback loop into the process, to make it stronger and more adaptive over time.
Establish and maintain an enduring cybersecurity strategy. Don’t rely on disconnected tactical efforts, as they will underperform over time.
If you need advisement, assistance is out there, reach out to industry leaders.
Overview As cybersecurity threats continue to evolve and become more sophisticated, the need for comprehensive preparedness has never been more critical. Tabletop exercises are essential for testing and refining incident response plans, enhancing coordination between departments, and staying ahead of malicious actors. In this article, we outline seven tabletop exercise scenarios that cybersecurity teams should […]
The post 7 tabletop exercise scenarios every cybersecurity team should practice in
Overview As cybersecurity threats continue to evolve and become more sophisticated, the need for comprehensive preparedness has never been more critical. Tabletop exercises are essential for testing and refining incident response plans, enhancing coordination between departments, and staying ahead of malicious actors. In this article, we outline seven tabletop exercise scenarios that cybersecurity teams should […]
In the evolving digital economy, adopting a prevention-first strategy for cloud workflows is essential. This article explores the importance of preemptive security measures to protect sensitive operations from breaches, detailing steps for organizations to enhance their security posture.
The post Prevention is the Only Cloud Security Strategy That Works appeared first on Security Boulevard.
In the evolving digital economy, adopting a prevention-first strategy for cloud workflows is essential. This article explores the importance of preemptive security measures to protect sensitive operations from breaches, detailing steps for organizations to enhance their security posture.
AI can now scan codebases and generate hundreds of potential vulnerabilities in minutes. But when 112 bug reports collapse into 22 confirmed flaws and only two exploitable issues, the real disruption is how AI is reshaping the entire vulnerability lifecycle.
The post 112 or 22 to 2: Who Moved the Vulnerability Cheese? appeared first on Security Boulevard.
AI can now scan codebases and generate hundreds of potential vulnerabilities in minutes. But when 112 bug reports collapse into 22 confirmed flaws and only two exploitable issues, the real disruption is how AI is reshaping the entire vulnerability lifecycle.
The CDK Global breach exposed how niche vendors can cripple entire industries. Move beyond questionnaires to continuous, AI-driven monitoring of third-, fourth- and nth‑party dependencies, dynamic prioritization, and threat‑informed supply‑chain risk management.
The post The Silent Supply Chain: Why Your Fourth-Party Vendor is Your Biggest Blindspot appeared first on Security Boulevard.
The CDK Global breach exposed how niche vendors can cripple entire industries. Move beyond questionnaires to continuous, AI-driven monitoring of third-, fourth- and nth‑party dependencies, dynamic prioritization, and threat‑informed supply‑chain risk management.
As AI adoption accelerates, organizations must evolve their security strategies from prompt filtering to comprehensive behavioral monitoring. This shift is critical to safeguarding against adaptive threats and ensuring safe AI deployment in production environments.
The post The Attack Chain Your AI System is Already Missing appeared first on Security Boulevard.
As AI adoption accelerates, organizations must evolve their security strategies from prompt filtering to comprehensive behavioral monitoring. This shift is critical to safeguarding against adaptive threats and ensuring safe AI deployment in production environments.
Today’s CISO is a strategic leader responsible for risk communication, security culture, education, and executive alignment. Technical expertise remains essential, but influence, clarity, and leadership now define success.
The post How the CISO’s Role is Evolving From Technologist to Chief Educator appeared first on Security Boulevard.
Today’s CISO is a strategic leader responsible for risk communication, security culture, education, and executive alignment. Technical expertise remains essential, but influence, clarity, and leadership now define success.
For today’s CISOs, enterprise cyber risk management is no longer a technical exercise. It’s a leadership mandate that sits at the intersection of security, business risk, regulation, and executive accountability. Aligning proactive cybersecurity risk management strategies with the business's overall risk posture is an ongoing, necessary process. A lack of alignment between cybersecurity and enterprise risk management can expose organizations to financial and reputational losses, and cybers
For today’s CISOs, enterprise cyber risk management is no longer a technical exercise. It’s a leadership mandate that sits at the intersection of security, business risk, regulation, and executive accountability. Aligning proactive cybersecurity risk management strategies with the business's overall risk posture is an ongoing, necessary process. A lack of alignment between cybersecurity and enterprise risk management can expose organizations to financial and reputational losses, and cybersecurity represents an entire risk profile that businesses must continuously address. Cyber threatsare persistent and pervasive, especially with new risks emerging from AI adoption in recent years.
AI agents have moved from novelty to operational reality, acting autonomously across business systems in ways traditional AI security posture management (AISPM) and IAM can’t fully govern. Learn why risk now emerges at runtime, where existing posture tools fall short, and how Agentic SPM enables continuous discovery, runtime decision control, and auditability for autonomous agents.
The post Why AISPM Isn’t Enough for the Agentic Era appeared first on Security Boulevard.
AI agents have moved from novelty to operational reality, acting autonomously across business systems in ways traditional AI security posture management (AISPM) and IAM can’t fully govern. Learn why risk now emerges at runtime, where existing posture tools fall short, and how Agentic SPM enables continuous discovery, runtime decision control, and auditability for autonomous agents.
Explore how organizations can prepare for the quantum age by developing quantum security intelligence, establishing governance plans, and prioritizing system updates. Learn strategies for building resilience without exorbitant investments as quantum computing technology advances
The post Will Your Organization Take the Quantum Leap in 2026? Read This First appeared first on Security Boulevard.
Explore how organizations can prepare for the quantum age by developing quantum security intelligence, establishing governance plans, and prioritizing system updates. Learn strategies for building resilience without exorbitant investments as quantum computing technology advances

 Entrar