❌

Visualização normal

Antes de ontemFirewall Daily – The Cyber Express
  • ✇Firewall Daily – The Cyber Express
  • Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role Ashish Khaitan
    A wave of data leaks from Japanese web systems in autumn 2026 has sharpened concern over AI's role in cyberattacks on Japan. The National Cybersecurity Office alerted businesses on October 9, and the chair of the ruling party's cybersecurity headquarters said cyberspace was in a "state of emergency."  Researchers reconstructed three attack infrastructures from files left in attackers' open directories. All three are separate from those in earlier reports on ARTEX, an autonomous AI penetration
     

Three Cyberattack Campaigns Target Japan, Exposing AI’s Growing Role

29 de Outubro de 2026, 06:10

Cyberattacks on Japan

A wave of data leaks from Japanese web systems in autumn 2026 has sharpened concern over AI's role in cyberattacks on Japan. The National Cybersecurity Office alerted businesses on October 9, and the chair of the ruling party's cybersecurity headquarters said cyberspace was in a "state of emergency."  Researchers reconstructed three attack infrastructures from files left in attackers' open directories. All three are separate from those in earlier reports on ARTEX, an autonomous AI penetration-testing system.   AI's role varied widely. Without victim-side logs, the findings cannot confirm each attempt's success, the full damage, or the attackers' identities. Victims are described only by count, industry, size, and country. 

Case A: Automated Cyberattacks on Japan 

In a short burst in October 2026, Case A abused CyberStrikeAI, an open-source agent-based penetration-testing tool with a Simplified Chinese console. Entries like "credential-search agent 8/44" show 44 agents dividing up reconnaissance, exploitation, command and control, persistence, exfiltration, and reporting. The platform produced Japanese forms and fake login pages.   It also throttled traffic to each target to avoid detection. At least 19 organizations received identical reports, including at least 16 in Japan and others in Taiwan and Hong Kong. Most were smaller businesses and local public bodies. Yet many entries read "no session, no web shell, no exfiltration." The deepest intrusion began at an unauthenticated administration interface on a legacy system. 

Case B: Human-Led, AI-Assisted 

Over about 24 days in August and September, a human operator used an LLM for planning and tooling. The operator scanned at least 6,000 Japanese IP addresses and also probed AI assets in South Korea. One LLM-written plan targeted AI and GPU services. To get it, the operator framed the request as an authorized assessment to bypass the model's guardrails. Other tools sought to hijack and pool access to other people's AI services, likely to get cheap inference capacity.  One company suffered full control through FTP, a database, administrator rights, a web shell, and SSH, and the attacker repeatedly restored backdoors after cleanup. At another, a GIS server left on default credentials exposed several hundred thousand cadastral and commercial records, Windows credentials, and email. Several hundred attempts on one cluster failed. 

Case C: Limited AI Role 

From January to October, a seasoned operator ran at least six campaigns, several in parallel from September onward. They targeted at least 1,300 WebLogic candidates and 35 VPN entry points, mainly in Japan and South Korea. The target lists also included the UK, France, Italy, Qatar, and Colombia. Devices included Cisco SD-WAN, Citrix NetScaler, F5 BIG-IP, and Yamaha RTX1210. On the RTX1210, leftover credentials in configuration files opened direct access to corporate networks. Section headings such as echo '=== ... ===' in the command history and emoji status markers in scripts point, with high confidence, to AI-written tools. A skilled human mimicking that style cannot be excluded. 

Lessons Beyond ARTEX 

All three operations worked in Simplified Chinese and sorted results under names like jp_success, jp_attack, and jp_cve_attack. Each picked targets opportunistically, and most of their activity came before the ARTEX reports. Whether they share an operator is unconfirmed, and their language is only a weak clue to origin.  AI increased scale, speed, localization, and reporting. It did not change the types of vulnerabilities exploited, the entry points, or how many targets were deeply compromised. The AI also logged planned steps as finished and overstated success. LLMs can also invent vulnerability IDs. These flaws can help with detection and honeypots. Defenders found the PHP2Shell flaws, disclosed in October 2026, through an AI-assisted audit, but no AI-found zero-day was exploited in these cases. 

Defending Against Cyberattacks on Japan 

Recommended steps: 
  • Inventory public-facing systems and update or isolate legacy ones. 
  • Remove exposed default credentials and admin interfaces. 
  • Secure VPN and edge-device configurations against credential reuse. 
  • Check internal AI and GPU services for exposure. 
  • Monitor for low-frequency, distributed attempts. 
  • Prepare for LLM misuse through requests built on false premises. 
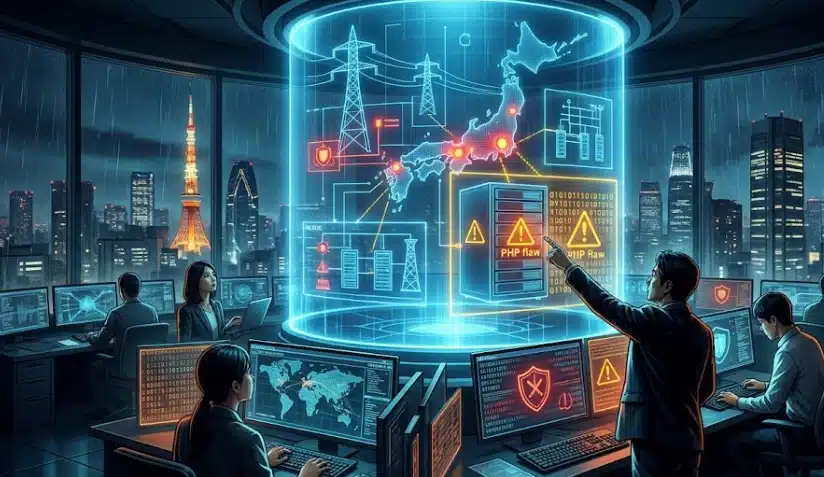
Fast patching and virtual patching matter more as the time between disclosure and exploitation shrinks. The attackers' identities, the AI models used, and the full damage remain unknown. 
  • ✇Firewall Daily – The Cyber Express
  • Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services Ashish Khaitan
    Japan is preparing to set up a dedicated team to run AI-driven cyberattack simulations to expose weaknesses in technology systems. Japan’s plan for AI cyberattack simulations comes as organizations worldwide scramble to address critical PHP flaws that have disrupted parts of the internet.  Speaking on Friday, Industry Minister Ryosei Akazawa said those defending against cyber threats need to think like attackers, using AI proactively to uncover potential weak points before they can be exploited.
     

Japan AI Cyberattack Simulations Planned as PHP Flaws Disrupt Services

23 de Outubro de 2026, 04:19

AI cyberattack simulations

Japan is preparing to set up a dedicated team to run AI-driven cyberattack simulations to expose weaknesses in technology systems. Japan’s plan for AI cyberattack simulations comes as organizations worldwide scramble to address critical PHP flaws that have disrupted parts of the internet. 

Speaking on Friday, Industry Minister Ryosei Akazawa said those defending against cyber threats need to think like attackers, using AI proactively to uncover potential weak points before they can be exploited. 

His comments follow widespread disruption caused by the disclosure of the PHP flaws, which led to millions of reported hacking attempts. Businesses and governments were forced to patch their systems or temporarily take websites offline.  

Because PHP is widely used to build and run websites and web applications, any weakness in the language poses a risk to organizations across many sectors. 

How PHP Flaws Hit Banks, Airlines and Government 

The vulnerabilities triggered precautionary shutdowns across banking, transport, airline and government services in several countries. 

In Japan, Nomura, Mitsubishi UFJ Financial Group, ANA and East Japan Railway temporarily halted some online services. The Ministry of Finance, the National Tax Agency and the Meteorological Agency also suspended certain digital services as part of their security response. 

On Friday, JR East said some of its services were back online, while others would resume only after safety checks. Nippon Paint said it had applied a security patch and restored its website. 

The disruption shows how difficult it is to secure interconnected digital infrastructure when a widely used software component turns out to have serious weaknesses. 

SoftBank Pauses Emergency Alerts Over PHP Flaws 

The fallout also reached services people rely on in a crisis. Telecommunications company SoftBank said it was temporarily suspending its mobile emergency alert system while it carried out maintenance to fix a PHP vulnerability. 

While the system is down, customers will not receive early warnings through it for earthquakes, tsunami threats, disasters, or evacuation information. The case shows that cybersecurity incidents can extend well beyond ordinary websites and interrupt access to vital public safety information. 

Why Japan AI Cyberattack Simulations Point to Proactive Defense 

The episode has put a fresh focus on finding vulnerabilities before attackers do. The Japan AI cyberattack simulations are designed to help defenders understand how weaknesses might be targeted and to sharpen their response capabilities, in line with the approach Ryosei Akazawa outlined. 

Simulation alone is not enough, however. Installing patches remains essential, and organizations need to test updated systems carefully before bringing services back, especially where transport, finance, and government operations are affected. 

As AI tools grow more capable for both attackers and defenders, businesses and governments face the task of pairing fast vulnerability detection with effective security updates, continuous monitoring, and resilient digital infrastructure. 

Cloudflare
Verify you are human

loading

Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content.
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare

site-verification-ok

Cloudflare
Verify you are human
loading
Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content.
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare

site-verification-ok

The Cyber Express Weekly Roundup: US Puts $10 Million Bounty on Chinese Hacker, Japan Moves to Hunt Hidden Attackers and More

9 de Outubro de 2026, 10:22

weekly roundup October 9th

This weekly roundup covers a massive exposure of personal data from Denmark's national population register, a U.S. bounty on a Chinese hacker accused of stealing COVID-19 research, Japan's plan to actively search for attackers hiding in its critical infrastructure, a pair of breaches at Japanese publisher Nikkei, a call for AI-driven decision-making in security operations, and a Massachusetts town's ongoing recovery from an August cyberattack.  Two threads run through this week's stories. First, attackers keep getting in through doors that were already open: a company's lawful access to a government register, employees' hijacked email accounts, and unpatched mail servers. Second, the time between intrusion and discovery remains dangerously long, which is why governments and security leaders are pushing to find intruders sooner and respond faster. 

The Cyber Express Weekly Roundup 

Hackers Abuse Company's Legitimate Access to Expose Data of 8.8 Million in Denmark 

The Danish government said unauthorized individuals obtained the names, addresses, and CPR numbers of roughly 8.8 million people from the Central Person Register. They did it by misusing the legal access granted to a private Danish company. The register holds records on about 11 million people, including residents, Danes living abroad, and deceased individuals. Read more… 

US Offers $10 Million Reward for Chinese Hacker Accused of Stealing COVID-19 Research 

The U.S. State Department is offering up to $10 million for information on Zhang Yu, a Chinese national accused of hacking COVID-19 research at U.S. universities on behalf of China's Ministry of State Security. Zhang and his alleged partner, Xu Zewei, are also tied to the 2021 HAFNIUM campaign, which exploited Microsoft Exchange vulnerabilities to compromise more than 12,700 U.S. entities. Xu was arrested in Italy in 2025 and extradited to the U.S. in April 2026. Zhang remains at large. Read more… 

Japan to Launch Threat Hunting Program to Find Hidden Attackers in Critical Infrastructure 

Japan plans to partner with private companies in fiscal 2027 to proactively look for attackers who may already be sitting undetected inside power, telecom, and other critical infrastructure networks. The National Cybersecurity Office will build detection methods by recreating attack scenarios in a virtual environment and will share them with operators. The Defense Ministry will provide experienced personnel to companies on request. Read more… 

Nikkei Hit by Two Breaches as Hijacked Accounts Send 9,000 Malicious Emails 

Japanese publisher Nikkei disclosed on October 4 that attackers had taken over employees' Microsoft 365 accounts. On September 30, they used those accounts to send roughly 9,000 emails with malicious links to staff and external contacts. Nikkei also revealed a separate breach of its Google Workspace accounts, ongoing since late July, that may have exposed the names and email addresses of 1,646 employees and business partners. Read more… 

Agentic AI Turns Cybersecurity Into a Race of Decision Speed 

In an opinion piece, Cyble's Salleh Kodri argues that security teams no longer struggle to see threats. Their problem is "decision latency": the time it takes to turn alerts from many tools into the right action. As AI accelerates attackers' reconnaissance and decision-making, Kodri says defenders should use AI to correlate intelligence and act faster. Read more… 

Andover Confirms Attackers Accessed Town Systems in August Cyberattack 

Officials in Andover, Massachusetts, confirmed that the August 13 cyberattack involved unauthorized access to some town systems. They have not yet determined whether any data was stolen or whether personal information was involved. The town says it paid no ransom. It has hired a law firm and cybersecurity firm Vector3 to investigate, with costs covered by cyber insurance. Read more… 

Weekly Cybersecurity Takeaway 

Several of this week’s incidents started with access that looked legitimate. In Denmark, attackers abused a private company’s authorized connection to the national register instead of breaking in. At Nikkei, hijacked employee accounts sent thousands of malicious emails under a trusted name.  Time is the other common thread. Nikkei’s Google Workspace breach ran for over two months before disclosure, and Andover still doesn’t know what was taken. Japan’s threat hunting plan assumes attackers may already be inside, and Kodri warns that spotting an alert means little if acting on it takes too long.  Organizations should monitor third-party access as closely as their own staff’s. They should secure email accounts with phishing-resistant authentication and actively hunt for intruders rather than wait for alerts. 
  • ✇Firewall Daily – The Cyber Express
  • Japan Plans Major Cyber Hunt to Detect Hidden Attacks on Critical Infrastructure Samiksha Jain
    Japan is stepping up its plans to find cyber attackers who may already be inside the networks that keep essential services running. Under a new fiscal 2027 initiative, the government plans to work with private companies to strengthen Japan threat hunting across critical infrastructure, including power utilities and telecommunications operators. The focus is not only on stopping attacks after they are detected, but on finding signs that an attacker has gained access and is quietly moving throu
     

Japan Plans Major Cyber Hunt to Detect Hidden Attacks on Critical Infrastructure

5 de Outubro de 2026, 03:02

Japan threat hunting

Japan is stepping up its plans to find cyber attackers who may already be inside the networks that keep essential services running. Under a new fiscal 2027 initiative, the government plans to work with private companies to strengthen Japan threat hunting across critical infrastructure, including power utilities and telecommunications operators. The focus is not only on stopping attacks after they are detected, but on finding signs that an attacker has gained access and is quietly moving through a system without triggering an alert. The government will develop ways to detect these threats and share the methods with private-sector operators, while the Defense Ministry will be able to provide personnel to assist companies when requested.

Japan Threat Hunting to Target Hidden Cyber Threats

The initiative forms part of Japan’s broader active cyber defense efforts. Threat hunting involves actively searching systems for signs of malicious activity rather than waiting for an alert or confirmed attack. Japan’s National Cybersecurity Office plans to use information about potential threats to recreate attack scenarios in a virtual environment. The office will then develop and test detection methods that can be used by private-sector companies. The aim is to help critical infrastructure operators identify attackers that may have already entered their systems and remained undetected. Detecting such activity could also help reduce the risk of a cyberattack disrupting essential services during an emergency. Legislation related to active cyber defense took effect on Thursday, giving the government a framework for expanding these cybersecurity measures.

Defense Ministry to Assist Critical Infrastructure Operators

Japan’s Defense Ministry is also preparing to provide direct support to operators of critical infrastructure. Companies will be able to request assistance, after which the ministry could dispatch personnel with threat-hunting experience developed through the information systems of Japan’s Self-Defense Forces. The National Cybersecurity Office and Defense Ministry have included the related costs in their fiscal 2027 budget requests. Threat hunting can require considerable resources because security teams need to collect and examine large amounts of system event logs. The purpose is to identify unusual activity that may otherwise go unnoticed. NTT Data Japan has been carrying out proactive threat hunting on its own systems since 2024. The company checks system logs for suspicious activity even when there has been no security alert. A representative of the National Cybersecurity Office also said threat-hunting methods could help address ransomware. Such attacks can involve attackers exploring a victim’s systems after gaining initial access, meaning suspicious activity may exist before the ransomware itself is deployed.

Recent Cyberattacks Add to Japan’s Concerns

Japan’s planned expansion of threat hunting comes as cyber incidents have affected government networks and companies across different sectors. In September 2026, the government disclosed that its common infrastructure network had been targeted in a cyberattack that began in May. Digital Minister Hisashi Matsumoto said about 246,000 personal records could have been leaked. The affected Government Solution Service, or GSS, is used by government agencies and independent administrative agencies. The potentially exposed information included about 189,000 employee records and around 57,000 records belonging to businesses and individuals involved in agency operations. An analysis found that a third party had compromised the system by exploiting a bypass involving a virtual private network, or VPN. Other recent incidents have affected private-sector operations. The Nichirei cyberattack in July disrupted food deliveries after the frozen food and logistics company confirmed unauthorized access to its servers. The incident affected logistics operations supporting KFC Japan. Nihon Kotsu also recently reported a malware-related incident that disrupted taxi dispatch services after parts of its IT infrastructure were taken offline. Earlier incidents involving Aflac Japan, KDDI, Sapporo Holdings and Nidec showed that attackers could gain access through subsidiaries, overseas operations or third-party infrastructure. Japan’s fiscal 2027 plans therefore put greater emphasis on looking for attackers that may already be inside a network, rather than relying only on alerts after suspicious activity has become visible.
❌
❌