
❌

Visualização normal

Antes de ontemFirewall Daily – The Cyber Express
  • ✇Firewall Daily – The Cyber Express
  • Australian Data Breach Incidents Up 66% as AI Sharpens Scams Samiksha Jain
    Australians filed a cybercrime report about every six minutes over the past year, and artificial intelligence is making the attacks behind those reports faster and more convincing. That is the main finding of the ASD Cyber Threat Report 2025-26. It is the seventh annual assessment from the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC). In FY2025-26, the agency received more than 82,000 cybercrime reports through ReportCyber. It responded to over 1,500 cyber secur
     

Australian Data Breach Incidents Up 66% as AI Sharpens Scams

28 de Outubro de 2026, 04:25

ASD Cyber Threat Report

Australians filed a cybercrime report about every six minutes over the past year, and artificial intelligence is making the attacks behind those reports faster and more convincing. That is the main finding of the ASD Cyber Threat Report 2025-26. It is the seventh annual assessment from the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC).

In FY2025-26, the agency received more than 82,000 cybercrime reports through ReportCyber. It responded to over 1,500 cyber security incidents, up more than 20% on the previous year and 36% over five years. It also notified Australian entities of potentially malicious activity more than 4,400 times, almost 80% more than in FY2024-25.

What the ASD Cyber Threat Report Says About AI

The report calls AI the defining force in the threat environment this year. In his foreword, Deputy Prime Minister and Defence Minister Richard Marles wrote that AI is helping malicious actors find vulnerabilities faster and exploit them at greater scale, speed and sophistication. He also noted that new threats have emerged in recent weeks from the unintended actions of AI agents and from model testing.

ASD’s ACSC makes one clear distinction. AI has not created new kinds of threats. It has amplified and sped up existing ones. AI-enabled cyber threats are most visible in social engineering. Attackers are using AI to write phishing emails with no spelling or grammar errors and to automate targeted spearphishing. The Australian Securities and Investments Commission has also seen a sharp rise in scams that use deepfake videos of celebrities and politicians.

The time defenders have to respond is also shrinking. The agency has previously observed that most vulnerabilities are exploited within two weeks, and some within 48 hours of a patch being released. It expects AI-driven tools to shorten that window further over the next 12 months. Publicly reported vulnerabilities (CVEs) rose 30%. Old flaws are still a problem too: ASD’s ACSC recorded the successful exploitation of a vulnerability first identified in 2008.

Incident Severity Grows in ASD Cyber Threat Report Data

Only one Category 2 incident was recorded this year. However, extensive compromises rose from 26 to 40. ASD’s ACSC identified 362 incidents after proactively notifying organisations. A single notification about cPanel vulnerabilities, sent to 340 entities in May 2026, led to more than 60 confirmed incidents.

The number of ransomware incidents held steady at 139, but extensive ransomware incidents rose from 16 to 24. Health Care, Professional, Scientific and Technical Services, and Manufacturing remained the most affected sectors. Data breaches made up 98 incidents, a 66% increase on the previous year. Separately, the Office of the Australian Information Commissioner received 1,205 breach notifications in 2025. That is the highest yearly total since its Notifiable Data Breaches scheme began in 2018.

The financial impact is rising for businesses. The average self-reported cost of cybercrime per business report rose 16% to $93,500. For medium-sized businesses, it rose 45% to $141,300. The average cost for individuals stayed at $33,000. Identity fraud remained the most reported cybercrime, although reports fell 18%.

Stolen access is now a major entry point. Compromised accounts and credentials were among the most frequently reported incident categories, and phishing appeared in 39% of incidents. Government survey research cited in the report found that 55% of Australians reuse passwords across multiple accounts.

State Actors and Critical Infrastructure in the ASD Cyber Threat Report

State-sponsored actors continued to target Australian government, business and individuals to gain sensitive information. The report says these actors are increasingly pre-positioning inside networks to enable future disruption. Marles wrote that the line separating state-sponsored espionage from sabotage and cybercrime is becoming increasingly blurred.

In April 2026, ASD’s ACSC and international partners highlighted a shift by China-nexus actors. These actors are moving towards large covert networks built from compromised home and small office routers, Internet of Things devices and smart devices.

Critical infrastructure accounted for 154 incidents, or 10% of the total, a decrease of almost 7%. Phishing was the leading initial access technique at 36%, and Financial and Insurance Services was the most affected critical infrastructure division at 30%.

What the Threat Report Asks Organisations to Do

In October 2026, ASD’s ACSC released the Essentials series. It evolves the Essential Eight into a principles-based framework with three chapters: Enterprise IT, Operational Technology and Cloud.

Under its Cyber Action Year, the agency is pushing five priorities:

  • Replacing or mitigating legacy technology.
  • Implementing best-practice event logging.
  • Managing supply chain risk.
  • Preparing for AI-enabled threats.
  • Preparing for post-quantum cryptography, including ceasing the use of traditional asymmetric cryptography by the end of 2030 or sooner.

The report also urges organisations to patch faster. For individuals, it recommends reviewing privacy settings and enabling multi-factor authentication or passkeys.

Suspicious activity, incidents and vulnerabilities can be reported at cyber.gov.au or through the Australian Cyber Security Hotline on 1300 CYBER1 (1300 292 371).
  • ✇Firewall Daily – The Cyber Express
  • G7, CISA Urge Urgent Shift to Post-Quantum Cryptography Samiksha Jain
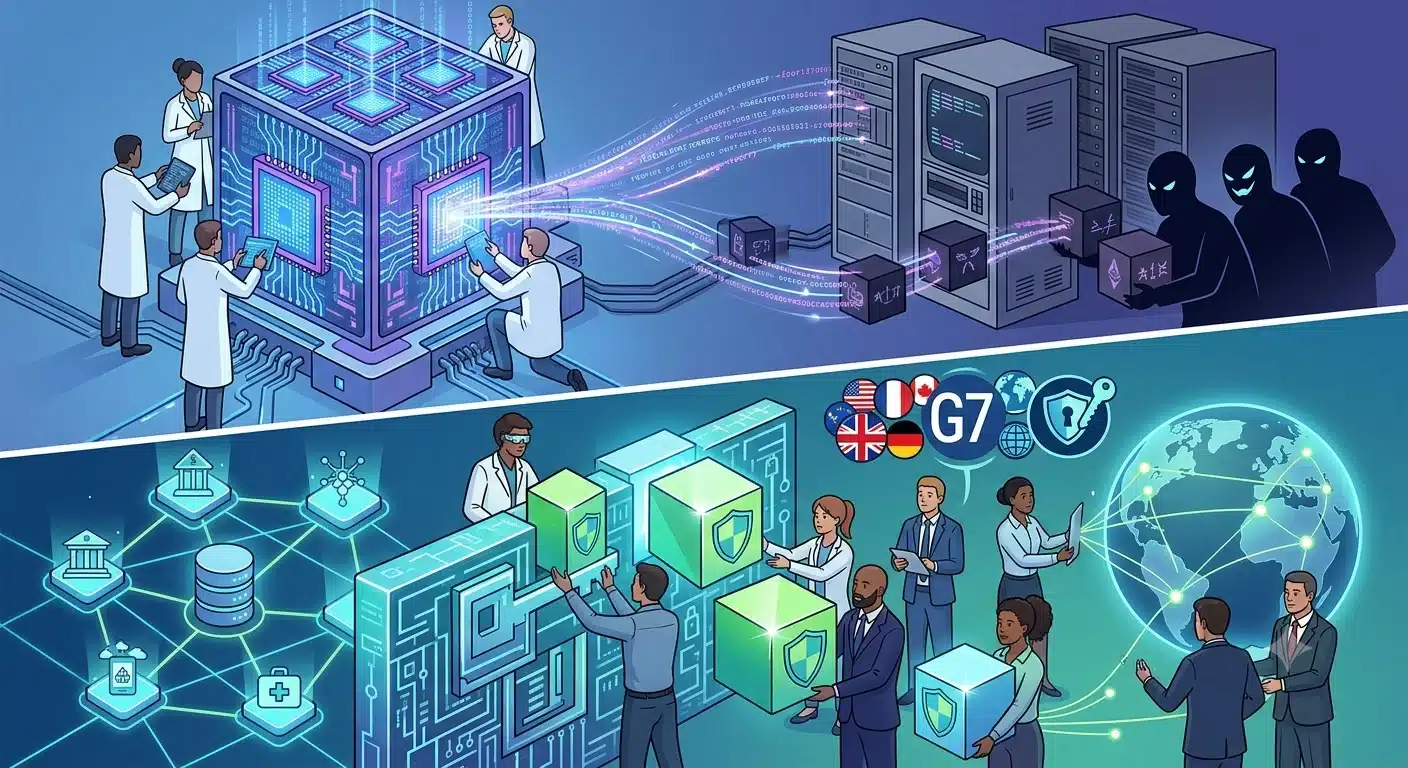
    Some of the world's leading democracies are pushing governments and companies to start preparing for post-quantum cryptography before quantum computers become powerful enough to break the encryption systems that protect global digital infrastructure today. In a joint advisory released Thursday, the G7 Cybersecurity Working Group and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) said organizations should begin their transition to post-quantum cryptography now, rather than wait
     

G7, CISA Urge Urgent Shift to Post-Quantum Cryptography

7 de Setembro de 2026, 03:51

post-quantum cryptography

Some of the world's leading democracies are pushing governments and companies to start preparing for post-quantum cryptography before quantum computers become powerful enough to break the encryption systems that protect global digital infrastructure today.

In a joint advisory released Thursday, the G7 Cybersecurity Working Group and the U.S. Cybersecurity and Infrastructure Security Agency (CISA) said organizations should begin their transition to post-quantum cryptography now, rather than waiting until cryptographically relevant quantum computers (CRQCs) are available to threat actors.

Why the Post-Quantum Cryptography Shift Cannot Wait

The publication, titled "Preparing for the Post-Quantum Era: A Call to Action," warns that the quantum computing threat is no longer a distant concern. While the exact timeline for CRQC development remains uncertain, the working group said recent technological advances suggest such machines could emerge sooner than expected, putting widely used public-key cryptography mechanisms at risk.

One of the most immediate dangers is a tactic known as "harvest now, decrypt later," where malicious actors intercept and store encrypted data today with the intention of decrypting it once a CRQC becomes available. This poses a serious risk to governmental records, sensitive personal data, and trade or business secrets that require long-term confidentiality.

The advisory also cautions that CRQCs could eventually be used to target authentication mechanisms, allowing bad actors to impersonate trusted entities, forge data, or compromise equipment. Because supply chain vulnerabilities can cascade, a single organization's delay in adopting post-quantum cryptography could expose entire sectors to compromise.

According to the report, organizations that fail to act may also face business consequences beyond security risk, including exclusion from public procurement contracts and loss of competitive advantage.

Five Priorities for the PQC Transition

The G7 Cybersecurity Working Group outlined five priority areas to guide the global shift toward post-quantum cryptography:

  1. Raising awareness — Many organizations still view the quantum threat as a distant or purely technical issue. The group called for awareness campaigns, technical guidance, and workforce upskilling to reframe it as an economic and business risk.
  2. Developing national strategies — Countries are encouraged to build strategies that ensure an adequate supply of quantum-safe hardware and software while encouraging adoption, integrating the effort into broader digital privacy and security policies.
  3. Advancing research and development — Governments should fund research programs and support pilot projects and testbeds to help organizations test and refine their transition to post-quantum cryptography.
  4. Building public-private partnerships — Collaboration between government, industry, and academia is seen as key to developing domestic expertise, lowering transition costs, and sharing playbooks and case studies across sectors.
  5. Integrating PQC into cybersecurity requirements — The group recommends treating post-quantum cryptography adoption as a natural evolution of cryptographic best practice, and embedding requirements into public procurement to push both vendors and organizations toward quantum-safe systems.

The advisory emphasizes that the shift to post-quantum cryptography cannot be solved by individual organizations in isolation. Instead, it calls for early engagement, coordinated planning, and informed decision-making across public and private sectors worldwide.

Tackling the risks that the impending quantum computing era poses to current cryptographic systems... requires a coordinated global effort to transition to PQC," the report states, adding that public and private organizations must act now to safeguard confidential data, supply chains, and critical systems.

The document was jointly published by cybersecurity authorities from Canada, Germany, Italy, Japan, the United Kingdom, the United States, and France's ANSSI, with participation from the European Commission and support from the EU Agency for Cybersecurity (ENISA).

❌
❌