Apple will begin checking publicly shared iCloud content in version 27.3. Here's what the change means for file sharing, encryption, and account restrictions.
The post Apple to Check Public iCloud Links Starting With iOS 27.3 appeared first on TechRepublic.
Apple will begin checking publicly shared iCloud content in version 27.3. Here's what the change means for file sharing, encryption, and account restrictions.
Problem in language that underpins 70% of sites has led governments and companies to pull sites offline to patch faultTell us: have you been affected by the PHP code flaw?What is PHP, and how bad is the computer language flaw causing website shutdowns globally?Websites around the world have been hit by millions of attempts to exploit a recently discovered vulnerability in their code, cybersecurity companies have said, as the US warned the flaw could allow attackers to take control of web servers
Websites around the world have been hit by millions of attempts to exploit a recently discovered vulnerability in their code, cybersecurity companies have said, as the US warned the flaw could allow attackers to take control of web servers, steal data and disrupt services.
The problem in the PHP programming language, which underpins about 70% of the world’s websites, emerged on Wednesday causing governments and companies to pull their websites off the internet before they could be attacked and so they could patch the fault.
Westminster appears to be waking up to warnings over AI safety, with concerns over its use by extremist groups and bad actors“I have this sense that, within a few months, AI is going to be all anyone is talking about,” said one cabinet minister, with an ominous stare.It was Labour conference, with everyone from ministers to activists jubilant at Andy Burnham’s takeover and a bounce in the polls after the change of leader. Continue reading...
Westminster appears to be waking up to warnings over AI safety, with concerns over its use by extremist groups and bad actors
“I have this sense that, within a few months, AI is going to be all anyone is talking about,” said one cabinet minister, with an ominous stare.
It was Labour conference, with everyone from ministers to activists jubilant at Andy Burnham’s takeover and a bounce in the polls after the change of leader.
A Ahold Delhaize cyber incident has disrupted parts of the grocery retailer's IT infrastructure, prompting the company to take some systems offline while its teams investigate and mitigate the issue. Although stores remain open, reports from the Netherlands and Belgium indicate that the incident is affecting distribution operations, customer service and some delivery-related activities.
Ahold Delhaize confirmed the security issue in a statement but did not disclose its nature or explain w
A Ahold Delhaize cyber incident has disrupted parts of the grocery retailer's IT infrastructure, prompting the company to take some systems offline while its teams investigate and mitigate the issue. Although stores remain open, reports from the Netherlands and Belgium indicate that the incident is affecting distribution operations, customer service and some delivery-related activities.
Ahold Delhaize confirmed the security issue in a statement but did not disclose its nature or explain whether customer or employee information had been compromised. The company said its teams were working to assess and contain the problem, adding that protecting its infrastructure was a priority.
"Protecting our infrastructure in the best interest of our customers, associates and partners is a top priority. We apologize for any inconvenience this issue may have caused customers and partners," reads the release.
The retailer also apologized for any inconvenience caused due to Ahold Delhaize cyber incident to customers and business partners. It has not provided a timeline for restoring all affected systems.
Ahold Delhaize Cyber Incident Affects IT Systems
Ahold Delhaize operates across nine countries, including the United States and several European markets, and employs more than 384,000 people. Its American grocery brands include Food Lion and Stop & Shop.
The company has not confirmed whether the Ahold Delhaize cyber incident involves ransomware, a data breach or another form of cyberattack. It also has not provided details about the systems affected or the extent of the disruption across its operations.
Reports from employees and customers suggest that the effects of Ahold Delhaize cyber incident are extending beyond internal IT systems. Food Lion employees in the United States have discussed the incident on social media, with managers reportedly describing it as an IT outage.
[caption id="attachment_114748" align="aligncenter" width="600"] Image Source: Reddit[/caption]
A Stop & Shop customer also reported delivery-related concerns on social media, complaining about a lack of information and an estimated delivery time for an order scheduled for Thursday.
These reports indicate operational difficulties, although the company has not publicly confirmed the specific causes of the individual disruptions.
Albert Heijn IT Outage Disrupts Distribution Centers
In the Netherlands, several Albert Heijn distribution centers have reportedly come to a standstill following the digital security incident. The disruption could affect product availability in stores if deliveries are delayed.
According to VRT News, customers are temporarily unable to place orders for the current week. Customer service has also been temporarily unavailable, although the retailer's app and website remain accessible.
The situation has raised concerns about the potential impact on grocery supply chains, particularly where distribution centers support stores across national borders.
Albert Heijn's distribution center in Tilburg, which supplies stores in Belgium, is also affected by the incident. However, Albert Heijn Belgium said the impact on its operations remains limited for now.
The Belgian business said it handles smaller volumes and can temporarily use other distribution centers to maintain supplies. Nevertheless, some products could become temporarily unavailable at certain stores.
Stores Remain Open as Investigation Continues
Despite the reported IT and distribution problems, Ahold Delhaize has said its stores remain open and continue serving customers.
Delhaize also confirmed that its stores in Belgium and Luxembourg remain open, allowing customers to shop as usual. The company said it had taken immediate measures to protect its IT systems and that its teams were working to restore operations.
Data security remains a central concern as the investigation continues. In its statement, the company emphasized that protecting customer, employee and partner data was its highest priority.
However, the available information does not establish whether any data was accessed, stolen or exposed during the incident.
The absence of a confirmed recovery timeline also leaves uncertainty around when all affected systems and services will return to normal.
Customer Data Protection Remains a Key Concern
The Ahold Delhaize cyber incident highlights the operational consequences that a security issue can have across a large grocery retail network, particularly when IT systems and distribution infrastructure are affected simultaneously.
For now, the company has confirmed the security issue and the steps being taken to mitigate it, but several important questions remain unanswered. These include the cause of the incident, the full scope of the disruption, whether sensitive information was affected and when normal operations will resume.
Until further details emerge, the extent of the incident's impact on customers, employees and supply chains remains unclear.
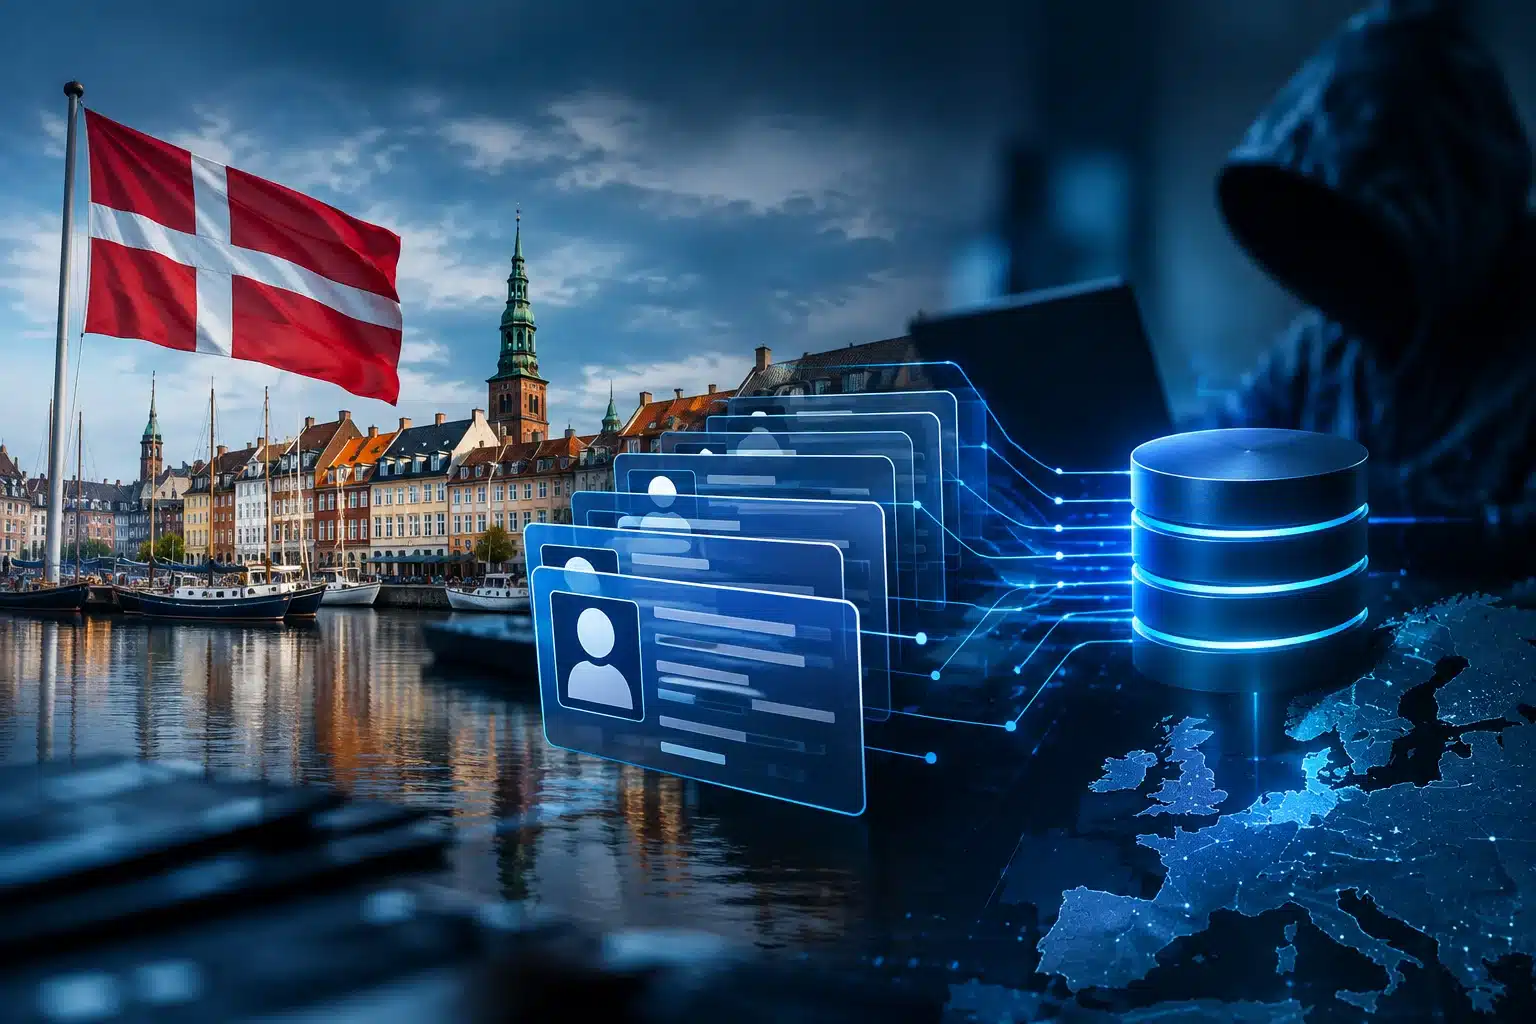
The Denmark data breach has exposed the names, addresses and CPR numbers of approximately 8.8 million people after unauthorized users exploited a Danish company's legitimate access to the country's Central Person Register (CPR), according to the Danish government.
The CPR administration became aware of irregular behavior in the system on October 2, after identifying activity that had occurred during September. An investigation found that unauthorized individuals had used a private Danish comp
The Denmark data breach has exposed the names, addresses and CPR numbers of approximately 8.8 million people after unauthorized users exploited a Danish company's legitimate access to the country's Central Person Register (CPR), according to the Danish government.
The CPR administration became aware of irregular behavior in the system on October 2, after identifying activity that had occurred during September. An investigation found that unauthorized individuals had used a private Danish company's legal access to search the CPR system and obtain information on millions of registered people.
The CPR currently contains information on approximately 11 million registered people, including those who are living in Denmark, people who have moved abroad and deceased individuals.
Denmark Data Breach Involved Legitimate CPR Access
The Denmark data breach did not result from unauthorized access being granted directly to the attackers. Instead, unauthorized users abused a private company's legitimate access to the CPR system.
Under Section 38 of Denmark's Civil Registration Act, private companies with a legitimate interest can receive information from the CPR about specific groups of people they have individually identified in advance. Companies must also be entitled to receive the information under the General Data Protection Regulation and Denmark's Data Protection Act.
The investigation found that unauthorized individuals used this legitimate access to retrieve information from the register.
The exposed information includes names, addresses and CPR numbers, which serve as personal identification numbers in Denmark. The CPR administration said the unauthorized access did not include the names and addresses of people who had registered for name and address protection.
Investigation Into CPR Data Breach Continues
The CPR administration has stopped the company's access to the system and is working with specialists and relevant authorities to establish how the incident occurred.
The case has been reported to the Danish Data Protection Authority, while police are investigating in cooperation with other relevant authorities.
Authorities said the investigation remains in its early stages, and it is not yet possible to identify who was responsible for the unauthorized access. The CPR administration also warned that further investigation could lead to changes or clarification of the information currently available about the incident.
Denmark's Minister of Research, Education and Digitalisation Christina Egelund described the incident as serious and said a thorough security review of the CPR system would be conducted. Additional measures have also been launched to prevent similar incidents.
What the Denmark Data Breach Means for Citizens
Authorities have reminded citizens not to provide passwords or other confidential information during phone calls or email exchanges, even when the person making contact appears to know their name, address or CPR number.
Guidance is available through Denmark's Sikker Digital service, while the Cyberhotline for digital security has extended its opening hours from 8 a.m. to midnight in the coming days.
The incident also highlights the risks associated with legitimate access to sensitive databases. In this case, the access used to obtain the information was originally available to a private company under Denmark's existing rules for accessing CPR data.
Cybersecurity Awareness Month Puts Data Protection in Focus
The Denmark data breach comes during October's Cybersecurity Awareness Month, a period focused on improving awareness of digital security risks. The incident highlights why protecting access to sensitive personal information remains an important part of cybersecurity.
For organizations handling large volumes of personal data, the case also shows the importance of monitoring legitimate access and identifying unusual activity. However, Danish authorities have stressed that the investigation is still underway and that the full circumstances of the incident have yet to be established.
Multiple critical IBM Guardium vulnerabilities expose servers to remote attacks. Update to fix these IBM Guardium vulnerabilities and secure your data.
Related Posts:
FomoPeek App Hides an iOS Kernel Exploit to Steal Crypto
Critical MongoDB Driver Vulnerabilities Require Immediate Patching
Plugin4Shell: Zero-Click RCE Hits Four AI Coding Agents
The post Critical IBM Guardium Vulnerabilities Need Immediate Patching appeared first on Daily CyberSecurity.
Multiple critical IBM Guardium vulnerabilities expose servers to remote attacks. Update to fix these IBM Guardium vulnerabilities and secure your data.
Exclusive: Official UK security assessment found Microsoft cloud platform storing files was at potential risk from hostile hackersVast troves of highly sensitive police data are lying on Microsoft cloud platforms which an official UK security assessment deemed to be vulnerable to “compromise” by foreign actors and the US government, a Guardian investigation can reveal.The files include criminal records, victim statements, internal emails and sensitive information held by more than 40 police forces
Exclusive: Official UK security assessment found Microsoft cloud platform storing files was at potential risk from hostile hackers
Vast troves of highly sensitive police data are lying on Microsoft cloud platforms which an official UK security assessment deemed to be vulnerable to “compromise” by foreign actors and the US government, a Guardian investigation can reveal.
The files include criminal records, victim statements, internal emails and sensitive information held by more than 40 police forces across the UK.
Apple is challenging a UK order reportedly requiring access to encrypted iCloud data, reviving a wider dispute over privacy, security, and lawful access.
The post Apple Challenges UK Demand For Access To Encrypted iCloud Data appeared first on TechRepublic.
Apple is challenging a UK order reportedly requiring access to encrypted iCloud data, reviving a wider dispute over privacy, security, and lawful access.
Details of parents and staff, including email addresses and phone numbers, are among data taken by cybercriminalsThe Department for Education and a police database have been targeted by a cyber-attack, exposing more than 740,000 pieces of data.Details of government officials, senior school leaders, university staff, police officers and members of the public have been taken by hackers. Continue reading...
Introduction
Mexico is one of the host countries for the 2026 FIFA World Cup, with matches to be played in three major cities: Mexico City, Monterrey, and Guadalajara. These locations are expected to see a large influx of international visitors, increasing the potential security risks. Many of those risks arise from users connecting to public wireless networks.
To better understand the wireless environments that visitors may encounter, we at Kaspersky GReAT conducted a wardriving assessment in t
Mexico is one of the host countries for the 2026 FIFA World Cup, with matches to be played in three major cities: Mexico City, Monterrey, and Guadalajara. These locations are expected to see a large influx of international visitors, increasing the potential security risks. Many of those risks arise from users connecting to public wireless networks.
To better understand the wireless environments that visitors may encounter, we at Kaspersky GReAT conducted a wardriving assessment in the three host cities. The aim of the study was to analyze characteristics, deployment patterns, security configurations and potential exposure risks of public Wi-Fi infrastructure in urban wireless environments.
The information collected during the assessment was used exclusively for passive observation and infrastructure analysis. No attempts were made to authenticate, intercept communications, exploit systems or interact with the detected wireless networks beyond the publicly broadcast management information.
During processing of the collected data, one step involved filtering out networks belonging to cars or cell phones categorized as mobile hotspots because they do not represent networks that can be considered part of the assessment.
Research scope
The cities included in the study have high population density and extensive wireless infrastructure deployments. We chose areas with the most prominent wireless network activity and highly concentrated public access points. We carried out wardriving research in Monterrey back in 2008, but the city’s hotspot landscape has changed since then.
We chose the following analysis areas for each of the cities:
Mexico City: México City Stadium, Mexico City International Airport, Zócalo, Paseo de la Reforma, Colonia Roma, La Condesa, Polanco, and Coyoacán.
Guadalajara: Guadalajara Stadium, Guadalajara International Airport, the city center, Zapopan, Providencia, Avenida Chapultepec, Colonia Americana, Tlaquepaque, and the area around Andares.
Monterrey: Monterrey Stadium, Monterrey International Airport, Fundidora Park, Cintermex Monterrey, the downtown area, Barrio Antiguo, MacroPlaza, and the San Pedro financial district.
The wireless information was collected using passive wireless reconnaissance techniques. The collected information included:
SSID analysis and information exposure, including BSSID-derived SSIDs
Default router configurations and ISP deployments
Frequency and signal characteristics
Channel congestion and spectrum usage
Wireless security configurations, including:
Open and insecure wireless networks
WPS-enabled networks
Secure networks (WPA2/WPA3) with WPS enabled
We performed a wireless infrastructure analysis in Mexico City, Guadalajara, and Monterrey. We drove through the areas surrounding the World Cup stadiums, tourist zones, and other places where fan concentrations are likely to be largest. Our goal was to evaluate the security status, deployment characteristics and operational exposure of detected wireless networks.
In total, we recorded 84,588 signals with 69,473 unique Service Set Identifiers (SSIDs) in busy locations and World Cup zones across the three cities. Mexico City accounted for 61.4% of the signals, Guadalajara for 23.6%, and Monterrey for 14.8%. Approximately 82% of the signals had a single SSID (81.9%, 81.34%, and 84% respectively). Notably, they all operate under the IEEE 802.11 standard protocol.
Particular attention was given to identifying standard deployment patterns, legacy configurations, default vendor settings and information disclosure through publicly broadcast wireless identifiers.
The following sections present the results that were obtained by analyzing wireless infrastructure across the three locations.
Our findings
SSID analysis and information exposure
SSID analysis was conducted to evaluate naming conventions, deployment standardization and potential information exposure.
Only a few networks (0.0047%) have an invisible SSID, meaning the names of these networks are not broadcast. Some users prefer to hide the SSID for various reasons, such as the network’s purpose, the profile of its users, internal policies, etc. In contrast, the rest of the networks maintained active SSID broadcasting.
SSID structures may unintentionally disclose operational details about internet service providers (ISPs), device manufacturers, deployment practices, organizational ownership or user identity. The repeated presence of default SSID naming patterns across the analyzed locations indicates a significant degree of infrastructure homogeneity and reuse of default wireless configurations. It may also facilitate passive infrastructure profiling by revealing standard characteristics in use.
Approximately 34% of the detected networks retained the default SSID naming conventions provided by the manufacturer or ISP, while 66% used customized identifiers.
Distribution of SSID naming conventions (download)
Several recurring SSID naming conventions associated with ISP-provided deployments were identified in the three cities. The most frequently observed patterns include identifiers such as “Club_Totalplay_WiFi”, “izzi WiFi”, and “Megacable WiFi”, which suggests extensive standardization of wireless infrastructure deployment. Additionally, we observed distinctive location-specific SSIDs in each area of analysis, such as “XXXX-Internet para Todos-CDMX” or “RED JALISCO”.
Sequential SSID naming structures were also identified during the analysis. Patterns such as “INFINITUMXX” and “IZZI-XX” suggest automated ISP deployment and large-scale deployment strategies.
We identified 33 unique sequential naming structures among the 137 sequential SSIDs in total, representing approximately 0.16% of the detected wireless networks.
The following graph shows the top five sequential SSID patterns found in the largest number of networks:
Five most frequently observed sequential patterns (download)
Several customized SSIDs contained personal or organizational identifiers, including family names, professions, addresses or internal department references. Although personalized SSIDs may simplify local network identification for users, they may also expose sensitive information that could be useful for social engineering, physical targeting, or organizational profiling.
BSSID-derived SSID
During the analysis, multiple networks were identified that used the physical MAC address of a Wi-Fi access point (BSSID) as the visible SSID. This practice exposes hardware-level information that could facilitate vendor fingerprinting and targeted reconnaissance activities.
The organizationally unique identifier (OUI) contained in the first bytes of the BSSID identifies the equipment manufacturer. Threat actors can correlate exposed manufacturers with device-specific vulnerabilities.
Notably, we found that more than 30% of networks in all three cities reuse the MAC address as the SSID.
Default router configurations and ISP deployments
We performed wireless infrastructure profiling to identify the most common wireless equipment manufacturers and ISP deployments across the three locations.
Large-scale ISP deployments frequently use standardized wireless configurations and vendor-specific hardware platforms. Identifying dominant manufacturers and ISP naming conventions can provide insight into infrastructure and deployment practices facilitating the mapping of standardized attack surfaces.
The following figure shows the distribution of the most commonly used manufacturers.
Most frequently observed wireless equipment manufacturers (download)
The manufacturer analysis revealed a strong concentration of wireless infrastructure among a limited number of vendors. Across the three locations, Huawei Technologies, MediaTek-based devices, and other manufacturers’ equipment that is distributed through ISP channels represented a significant portion of the detected deployments. Mexico City had the most diverse infrastructure, while Monterrey and Guadalajara had a greater concentration of wireless equipment known as SOHO (small office/home office) or residential-grade hardware. The widespread presence of standard vendor platforms may facilitate infrastructure fingerprinting and large-scale targeting of known device-specific vulnerabilities.
Most frequently observed wireless equipment manufacturers across the three cities (download)
ISP deployments frequently exhibited standardized configuration patterns and recurring manufacturer identifiers. Our ISP deployment analysis revealed a high concentration of access points associated with major residential internet providers. Deployments associated with Infinitum, Totalplay and Izzi represented a substantial portion of the detected wireless infrastructure across all locations. These findings suggest a high degree of deployment standardization across networks associated with major residential internet providers. This observation was supported by the repeated presence of ISP-associated SSIDs such as “Infinitum”, “Totalplay”, and “Izzi”, combined with manufacturer identifiers frequently associated with consumer equipment, including Huawei, ZTE and other residential wireless equipment vendors.
It is important to note that, for this analysis, ISPs were primarily inferred from SSID naming conventions and manufacturer fingerprint data. A significant portion of the detected wireless networks fell into the “UNKNOWN/CUSTOM” category. This classification includes custom hotspots and networks whose naming conventions did not expose identifiable ISP-associated patterns. The findings suggest that many users and organizations (as we saw previously, approximately 66%) use custom network names, limiting direct provider attribution.
The following figure illustrates the distribution of ISP-associated wireless deployments in general.
To better understand this distribution, we took the most frequently observed ISPs by city.
Most frequently observed ISPs across the three cities (download)
Frequency and signal characteristics
We also analyzed wireless signal characteristics to evaluate coverage quality, signal strength, and frequency band utilization in the three cities. In dense urban environments, signal quality and frequency spectrum distribution can affect wireless reliability, client connectivity, roaming performance, and overall network efficiency.
Signal quality analysis revealed that a substantial portion of the detected access points operated under weak or very weak signal conditions. Monterrey had the highest percentage of very weak signals, with approximately 50% of detected deployments. Similar patterns were observed in Guadalajara and Mexico City, suggesting high-density wireless environments with overlapping coverage areas. Only a limited percentage of networks were classified within the very good or excellent signal categories across the three locations.
Signal stability analysis revealed that most detected wireless deployments exhibited stable beacon transmission behavior. More than 96% of the detected access points across all locations were classified as stable, while only a small percentage exhibited unstable or indeterminate signal behavior.
These findings imply that the majority of the wireless infrastructure observed during the assessment corresponded to permanently deployed access points rather than transient or intermittent wireless devices.
Frequency band analysis revealed the strong prevalence of 2.4 GHz wireless deployments across the three locations. More than 95% of the detected wireless networks operated within the 2.4 GHz spectrum, while only a small percentage of deployments were classified under the unknown or non-standard frequency categories. This uneven distribution reflects the continued prevalence of legacy-compatible wireless infrastructure and SOHO deployments.
These findings are consistent with dense urban wireless environments with large numbers of access points in restricted spectrum allocations.
Channel congestion and spectrum usage
Next, we analyzed wireless channel utilization to evaluate frequency spectrum congestion and channel allocation patterns across the three cities. Our analysis focused on the 2.4 GHz spectrum, where channel overlap and high access point density commonly produce interference and degraded wireless performance. In densely populated wireless environments, an excessive concentration of access points on a limited number of channels can lead to co-channel interference, packet collisions, reduced throughput, and degraded network stability.
Spectrum congestion analysis revealed that the 2.4 GHz band consistently experienced elevated congestion levels across the three cities. The detailed results showed a strong concentration of deployments on channels 11, 6 and 1, which are traditionally recommended as non-overlapping channels within the 2.4 GHz spectrum. Channel 11 was the most utilized channel, accounting for 25.2% of the detected access points, followed by channel 6 with 22.5% and channel 1 with 19.5%. This distribution indicates that most wireless deployments adhere to standard channel allocation practices for 2.4 GHz Wi-Fi environments.
The following figure illustrates the overall distribution of the most frequently utilized wireless channels.
To further assess wireless spectrum saturation, the detected access points were grouped according to channel congestion levels: VERY_HIGH, HIGH, UNKNOWN, MEDIUM, LOW and NONE.
Mexico City had the highest proportion of heavily congested wireless channels, with approximately 7% of detected access points operating under HIGH congestion conditions. Guadalajara followed with nearly 5% of deployments categorized as HIGH congestion, while Monterrey had the lowest percentage at approximately 3.29%.
These findings suggest that wireless spectrum saturation increases proportionally with urban infrastructure density and access point concentration. Despite the presence of congested deployments, most detected access points were categorized as LOW or MEDIUM congestion, suggesting severe spectrum saturation was localized rather than uniformly distributed.
A thorough analysis of individual channel utilization revealed that channels 11, 6 and 1 consistently experienced the highest congestion levels across the three cities, which correlates with our previous findings. These channels accounted for the majority of VERY_HIGH congestion classifications, particularly within the 2.4 GHz band.
In Mexico City, channel 11 alone accounted for more than 25% of detected deployments and consistently exhibited VERY_HIGH congestion levels.
This behavior reflects the limited availability of non-overlapping channels within the 2.4 GHz spectrum and the widespread reliance on default wireless configurations.
Overall, the channel utilization analysis showed that wireless deployments are concentrated heavily within the traditional, non-overlapping 2.4 GHz channels. While this strategy reduces adjacent-channel interference, excessive access point density on the same channels can still produce significant co-channel contention and poor wireless performance in high-density urban environments.
Wireless security configurations
The next thing we evaluated was the security posture of the detected wireless networks. We analyzed the wireless security configurations advertised by access points in each of the locations.
Overall security configuration distribution
The analysis revealed that WPA2 was the dominant wireless authentication mechanism across the three cities. Mexico City had the highest WPA2 adoption rate at 81.19%, followed by Monterrey at 79.19% and Guadalajara at 77.59%.
The study found that every 6th open access point (17%) was unsafe, namely 16.5% in Mexico City, 18.5% in Guadalajara, and 17.2% in Monterrey. Open wireless deployments were consistently present across all locations, ranging between 10% and 12% of detected access points. These findings show that despite the widespread deployment of modern wireless security standards, encryption adoption remains incomplete.
Distribution of wireless authentication mechanisms across the three locations (download)
To simplify the interpretation of wireless security posture, we grouped detected networks into four categories:
Secure (WPA2/WPA3)
Insecure (Open/WEP)
Weak (WPA)
Unknown
Across the three locations, secure networks comprised most of detected deployments, accounting for approximately 82% of all access points. However, insecure open networks still account for between 10% and 12% of detected wireless infrastructure, consistent with our previous findings. It is important to mention that networks within the unknown category are not considered secure.
Mexico City had the highest percentage of secure deployments at 83.54%, while Guadalajara had the highest percentage of insecure open networks at 12.46%. Although Monterrey had the lowest percentage of insecure networks, open deployments still accounted for more than 10% of the detected access points.
Wireless security posture grouping across the three locations (download)
Although modern WPA2/WPA3 encryption standards dominate current wireless deployments, the continued presence of open and legacy WPA deployments indicates that insecure wireless configurations remain relevant from an operational standpoint. These networks may expose users to passive traffic interception, unauthorized monitoring, rogue access point attacks, and credential harvesting techniques.
WPS-enabled networks
We also analyzed Wi-Fi Protected Setup (WPS) in all the locations to evaluate additional attack surfaces. WPS is a standard feature on wireless routers that enables devices such as printers, repeaters or mobile phones to connect to a secure Wi-Fi network without manually entering a long password, typically through a PIN-based enrolled mechanism. Although WPA2 and WPA3 provide strong encryption mechanisms, the presence of WPS can introduce security weaknesses due to inherently vulnerable PIN-based enrollment methods.
By combining detections from the three locations, we found that 55% of all detected access points did not advertise WPS capabilities, leaving 45% of deployments vulnerable to WPS-based abuse. These results suggest that, despite the adoption of modern encryption standards, a significant portion of wireless infrastructure continues to expose legacy convenience features.
During the analysis, we found that Mexico City had the highest proportion of WPS-enabled networks, with 46.61% of the detected access points advertising WPS capabilities. Guadalajara was second with 43.45%, while Monterrey had the lowest proportion at 40.93%.
The percentage of detected access points advertising WPS capabilities across the three locations (download)
Almost half of the detected wireless networks in each city continued to advertise WPS, indicating that WPS prevalence is consistently high across the three cities.
Secure networks with WPS enabled
In many cases, networks classified as secure because of WPA2/WPA3 encryption still had WPS functionality enabled, which effectively increased the available attack surface.
To further assess the relationship between encryption strength and WPS exposure, we conducted a secondary analysis of secure networks (WPA2/WPA3) only. The results showed that around half of all secure deployments still exposed WPS, with the following breakdown for each city:
Mexico City: 53.7%
Guadalajara: 50.9%
Monterrey: 47.5%
The proportion of secure networks with WPS enabled across the three locations (download)
These findings indicate that encryption strength alone is not enough to evaluate wireless security posture because additional protocol features, such as WPS, may still expose exploitable attack vectors.
Additional security considerations
Overall, travelers operating within dense public environments are exposed not only to insecure wireless infrastructure but also to various risks associated with digital interactions. These risks include many threats, from public USB charging systems and phishing QR codes to proximity-based protocols and exposure to shared public devices, such as interactive totems or kiosks. One particular point that should be taken into account in light of our research is the issue of rogue wireless deployments.
Rogue access points are not necessarily malicious; they may be set up accidentally by misconfiguring router settings. An entry point for potential compromise might be caused by various misconfigurations, from a weak password to an insecure protocol. However, attackers deploy such unauthorized hotspots with malicious intent to infiltrate a network. Threat actors may deploy rogue access points posing as legitimate public wireless networks in airports, hotels, cafés and tourist areas. These deployments are called “evil twins” and can trick users into connecting to attacker-controlled infrastructure capable of intercepting traffic, harvesting credentials, or performing man-in-the-middle attacks. Further risk lies in the potential compromise of local network devices or even malware distribution. Such threats complement our findings, underscoring the importance of implementing traffic encryption, using a security solution and exercising extreme caution while browsing via public networks.
Conclusion
The wardriving assessment conducted in Mexico City, Guadalajara, and Monterrey revealed that modern wireless infrastructure continues to present multiple forms of operational exposure despite the widespread adoption of WPA2 and WPA3 security standards. The analysis demonstrated that wireless environments are highly standardized in all the locations, with recurring ISP deployments, default SSID naming conventions, homogeneous manufacturer distribution, and predictable channel allocation practices observed in all three cities.
Although most of the detected networks were classified as secure under WPA2/WPA3 authentication mechanisms, a significant proportion were exposing additional attack surfaces through enabled WPS functionality, default configurations, sequential SSID structures, and infrastructure metadata disclosure. This demonstrates that encryption strength alone is insufficient for evaluating the overall security posture of wireless infrastructure. Additionally, the prevalence of open networks and legacy wireless configurations indicates that insecure deployments are still operationally relevant in all the locations.
The results also showed that wireless infrastructure is heavily concentrated within the 2.4 GHz spectrum, particularly around channels 11, 6, and 1. This leads to elevated congestion and increased co-channel interference in densely populated urban environments.
SSID analysis further revealed that publicly broadcast wireless identifiers frequently expose valuable operational information about ISPs, equipment manufacturers, deployment templates, organizational ownership, and user-defined naming practices. The identification of default ISP naming conventions, sequential SSID structures, and BSSID-derived SSIDs demonstrated that many deployments prioritize operational convenience and simplicity over exposure minimization and privacy.
The scope of the threats stemming from vulnerable wireless configurations poses serious digital exposure risks for users. The widespread presence of standard deployments, predictable SSID naming and publicly exposed infrastructure identifiers can facilitate passive reconnaissance, infrastructure fingerprinting and opportunistic targeting.
Recommendations
To minimize the risks of wireless-based exposure and the attack surface related to hotspot infrastructure, we recommend taking the following measures:
Disable WPS functionality on wireless routers whenever possible, particularly within WPA2/WPA3 deployments.
Avoid using default SSID naming conventions that disclose ISP providers, router manufacturers, or deployment templates.
Refrain from using personal, organizational, or location-based identifiers in wireless network names.
Avoid configuring SSID using BSSID or naming conventions derived from MAC addresses, as these may expose hardware fingerprinting information.
Promote migration toward modern WPA3-capable infrastructure while removing legacy wireless protocols when operationally feasible.
Reduce wireless congestion by optimizing channel allocation strategies and minimizing excessive dependence on the 2.4 GHz spectrum.
Encourage adoption of 5 GHz and newer wireless technologies to reduce interference and improve spectrum efficiency.
The findings presented in this assessment emphasize the importance of combining strong wireless encryption standards, secure deployment practices, exposure minimization strategies, and user awareness to enhance the overall security posture of wireless environments.
Health service has given US tech firm ‘unlimited access’ to certain data to build integrated platform, according to reportsUK politics live – latest updatesMPs have warned that an NHS decision to grant Palantir access to identifiable patient information in its plan to use AI to improve the health service is “dangerous” and will fuel public fears that data privacy is not being prioritised.NHS England has allowed staff from the US tech firm and other contractors to access patient data before it ha
MPs have warned that an NHS decision to grant Palantir access to identifiable patient information in its plan to use AI to improve the health service is “dangerous” and will fuel public fears that data privacy is not being prioritised.
NHS England has allowed staff from the US tech firm and other contractors to access patient data before it has been pseudonymised, despite internal fears of a “risk of loss of public confidence”, the Financial Times reported.
Banks, governments and tech providers urged to upgrade security because current systems will soon be obsolete Banks, governments and technology providers need to be prepared for quantum computer hackers capable of breaking most existing encryption systems by 2029, Google has warned.The tech company said in a blogpost that quantum computers would pose a “significant threat to current cryptographic standards” before the end of the decade and urged other companies to follow its lead. Continue read
Banks, governments and tech providers urged to upgrade security because current systems will soon be obsolete
Banks, governments and technology providers need to be prepared for quantum computer hackers capable of breaking most existing encryption systems by 2029, Google has warned.
The tech company said in a blogpost that quantum computers would pose a “significant threat to current cryptographic standards” before the end of the decade and urged other companies to follow its lead.
In a move that bucks the entire industry trend, TikTok has confirmed it will not implement end-to-end encryption (E2EE) for direct messages on its platform — arguing that E2EE would make users less safe. We break down what’s really going on: the child safety argument, the privacy counterargument, the geopolitical questions surrounding ByteDance, and what […]
The post TikTok Says No to End-to-End Encryption: Here’s Why That’s a Big Deal appeared first on Shared Security Podcast.
The post TikTok S
In a move that bucks the entire industry trend, TikTok has confirmed it will not implement end-to-end encryption (E2EE) for direct messages on its platform — arguing that E2EE would make users less safe. We break down what’s really going on: the child safety argument, the privacy counterargument, the geopolitical questions surrounding ByteDance, and what […]
Millions installed 'productivity' Chrome extensions that became malware after acquisition. Here's how browser extensions became enterprise security's weakest link.
The post The Chrome Extension Backdoor: How ‘Productivity Tools’ Became Enterprise Attack Vectors appeared first on Security Boulevard.
Millions installed 'productivity' Chrome extensions that became malware after acquisition. Here's how browser extensions became enterprise security's weakest link.
Shadow AI leaks data to uncontrolled external systems and spreads virally across organizations, requiring user training and compliant alternatives rather than prohibition.
The post Shadow AI: When Everyone Becomes a Data Leak Waiting to Happen appeared first on Security Boulevard.
Shadow AI leaks data to uncontrolled external systems and spreads virally across organizations, requiring user training and compliant alternatives rather than prohibition.
TikTok has shifted to a majority-American entity, TikTok USDS Joint Venture, LLC, to comply with U.S. national security requirements and avoid a ban. This week we discuss why a recent privacy policy update went viral—especially language about sensitive data like immigration status and precise location—and argue much of it reflects longstanding practices and required California […]
The post TikTok’s New U.S. Deal and Privacy Policy: What Users Don’t Understand appeared first on Shared Security Po
TikTok has shifted to a majority-American entity, TikTok USDS Joint Venture, LLC, to comply with U.S. national security requirements and avoid a ban. This week we discuss why a recent privacy policy update went viral—especially language about sensitive data like immigration status and precise location—and argue much of it reflects longstanding practices and required California […]
Explore the evolving landscape of privacy and security in the age of AI. This article examines the cultural and regulatory differences between the U.S. and Europe, the limitations of current policies, and the imperative for architectural solutions to ensure that autonomous systems can uphold privacy standards.
The post Why the US–EU Privacy Divide Still Matters in the Age of AI appeared first on Security Boulevard.
Explore the evolving landscape of privacy and security in the age of AI. This article examines the cultural and regulatory differences between the U.S. and Europe, the limitations of current policies, and the imperative for architectural solutions to ensure that autonomous systems can uphold privacy standards.
Russian state has tolerated parallel probiv market for its convenience but now Ukrainian spies are exploiting itRussia is scrambling to rein in the country’s sprawling illicit market for leaked personal data, a shadowy ecosystem long exploited by investigative journalists, police and criminal groups.For more than a decade, Russia’s so-called probiv market – a term derived from the verb “to pierce” or “to punch into a search bar” – has operated as a parallel information economy built on a network
Russian state has tolerated parallel probiv market for its convenience but now Ukrainian spies are exploiting it
Russia is scrambling to rein in the country’s sprawling illicit market for leaked personal data, a shadowy ecosystem long exploited by investigative journalists, police and criminal groups.
For more than a decade, Russia’s so-called probiv market – a term derived from the verb “to pierce” or “to punch into a search bar” – has operated as a parallel information economy built on a network of corrupt officials, traffic police, bank employees and low-level security staff willing to sell access to restricted government or corporate databases.
Sensitive information relates to more than 100 individuals and their refereesPersonal details submitted by applicants for a job at Tate art galleries have been leaked online, exposing their addresses, salaries and the phone numbers of their referees, the Guardian has learned.The records, running to hundreds of pages, appeared on a website unrelated to the government-sponsored organisation, which operates the Tate Modern and Tate Britain galleries in London, Tate St Ives in Cornwall and Tate Live
Sensitive information relates to more than 100 individuals and their referees
Personal details submitted by applicants for a job at Tate art galleries have been leaked online, exposing their addresses, salaries and the phone numbers of their referees, the Guardian has learned.
The records, running to hundreds of pages, appeared on a website unrelated to the government-sponsored organisation, which operates the Tate Modern and Tate Britain galleries in London, Tate St Ives in Cornwall and Tate Liverpool.
When courts ban people from accessing leaked data – as happened after the airline’s data breach – only hackers and scammers winFollow our Australia news live blog for latest updatesGet our breaking news email, free app or daily news podcastIt’s become the playbook for big Australian companies that have customer data stolen in a cyber-attack: call in the lawyers and get a court to block anyone from accessing it.Qantas ran it after suffering a major cybersecurity attack that accessed the frequent
It’s become the playbook for big Australian companies that have customer data stolen in a cyber-attack: call in the lawyers and get a court to block anyone from accessing it.

 Entrar