❌

Visualização normal

Antes de ontemStream principal

3AM Ransomware Hits 37 UK School Systems in Suspected AI-Assisted Attack

Bitdefender details a 3AM ransomware attack on a UK school estate that encrypted 37 systems, with command timing suggesting possible AI-assisted troubleshooting.

Midnight Mimosa Malware Found Preinstalled on Low-Cost Android Phones

Low-cost Android phones can arrive already compromised, with malware embedded in their firmware before buyers switch them on.
  • ✇Security Affairs
  • Chaotic Eclipse Released BigDiskBuster, A PoC For Windows Defender Update DoS Zero-Day Pierluigi Paganini
    The researcher Chaotic Eclipse released BigDiskBuster, a PoC exploit for a Windows Defender Update DoS Zero-Day vulnerability. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit BigDiskBuster, it triggers a Denial of Service Vulnerability in Windows Defender Update. The security researcher claims to have developed BigDiskBuster, a proof-of-c
     

Chaotic Eclipse Released BigDiskBuster, A PoC For Windows Defender Update DoS Zero-Day

22 de Setembro de 2026, 11:04

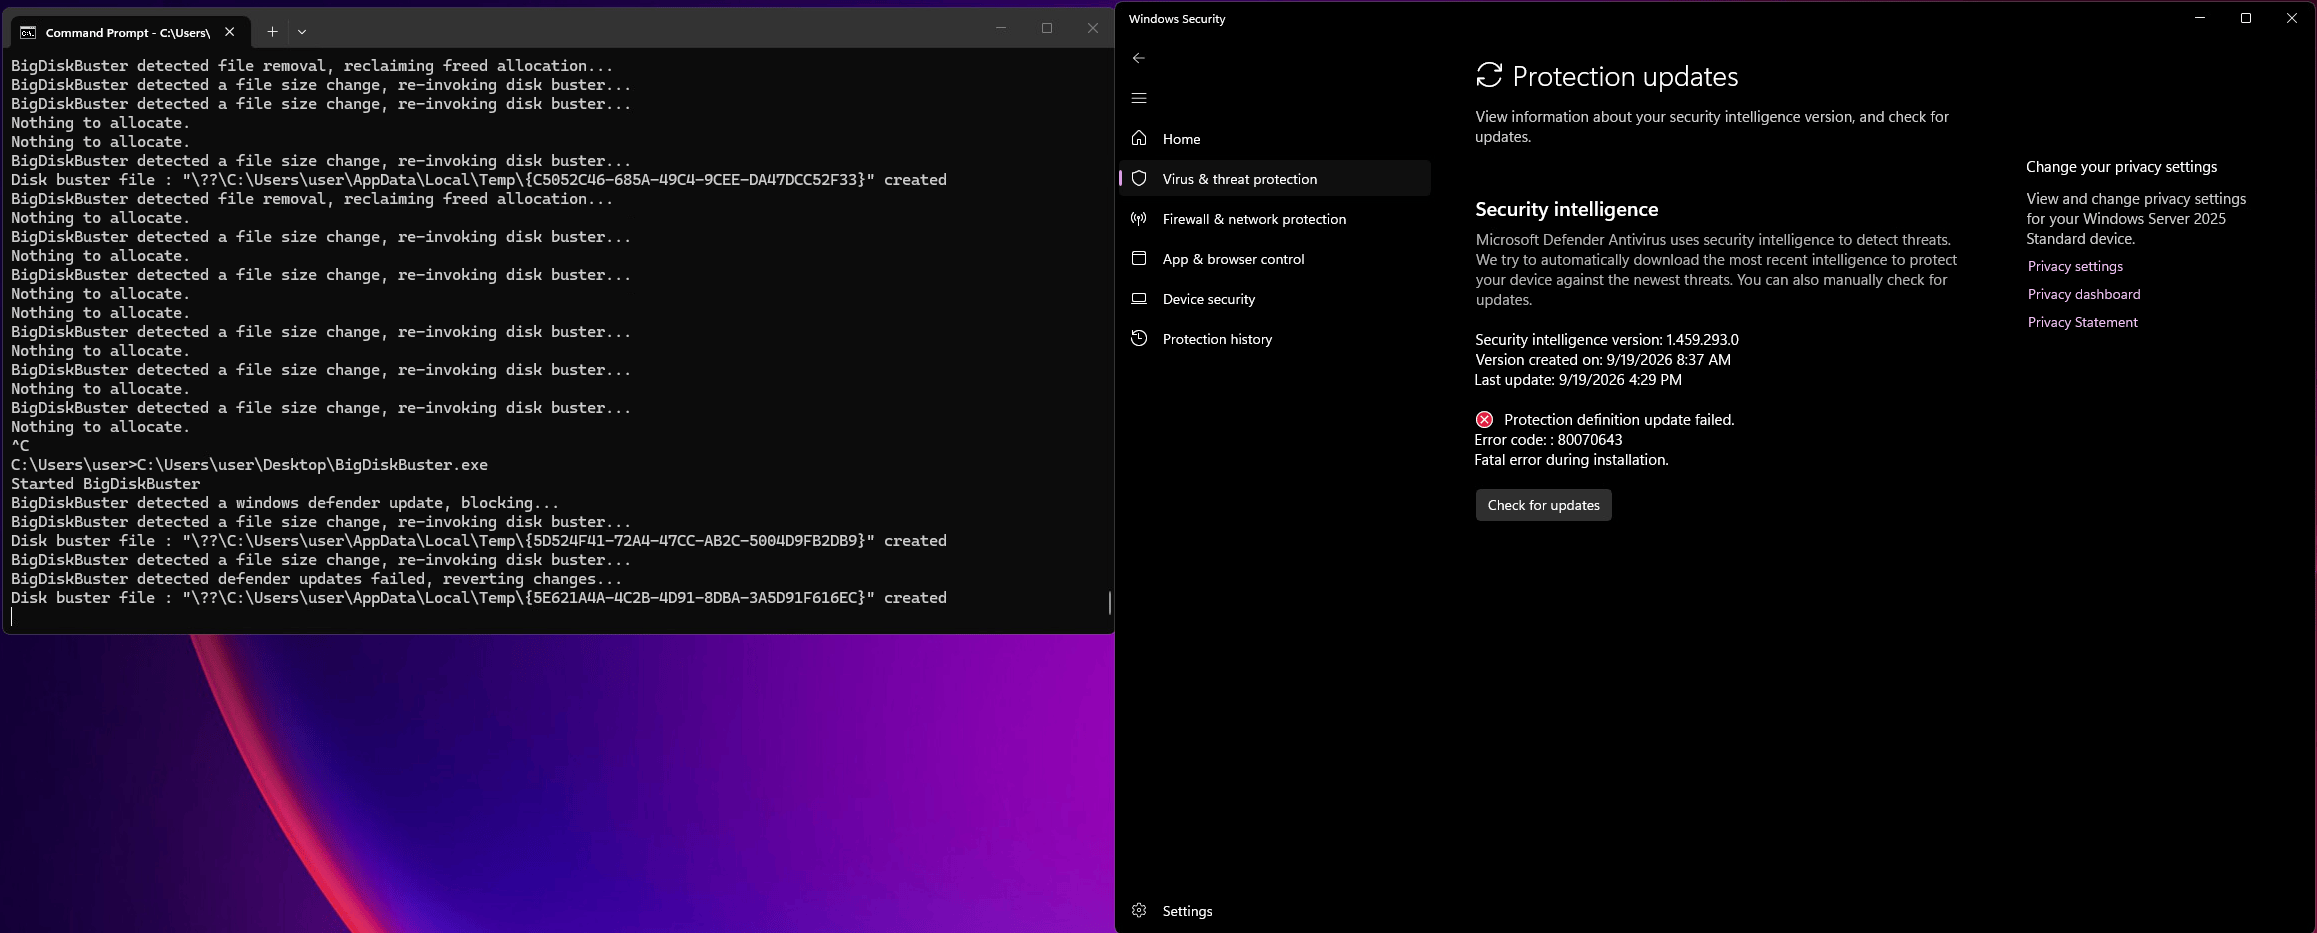
The researcher Chaotic Eclipse released BigDiskBuster, a PoC exploit for a Windows Defender Update DoS Zero-Day vulnerability.

Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit BigDiskBuster, it triggers a Denial of Service Vulnerability in Windows Defender Update.

The security researcher claims to have developed BigDiskBuster, a proof-of-concept that can block Microsoft Defender from receiving platform and signature updates.

“This proof of concept is similar to UnDefend, it prevents windows defender from performing platform/signature updates.” wrote the expert. “Seems to work on all supported windows versions but PoC is a bit buggy and needs some rewritting but you get the idea.”

Chaotic Eclipse says the technique works across supported Windows versions, although the current PoC is still buggy and needs further development.

In September, Chaotic Eclipse released multiple zero-day exploits targeting Nvidia (GreenSection) and Microsoft Defender (ShieldCrash).

Recently, Chaotic Eclipse also released exploits targeting other anti-malware and defense solutions. Chaotic Eclipse released a zero-day exploit targeting Kaspersky Endpoint Security he named HardBreacher, which triggers a privilege escalation flaw. The researcher pointed out that the PoC is unstable and may require repeated attempts, but when successful, it creates a DLL in System32 with full user permissions. The researcher also claims taking control of Kaspersky’s UI process can disrupt the antivirus and interfere with file-access controls, potentially leaving the system in an unstable state.

Nightmare Eclipse says the Kaspersky Endpoint Security zero-day allows privilege escalation on a fully patched Windows 11 25H2 system running Kaspersky Endpoint v14.0.0.504.

The researcher also released a zero-day exploit targeting GenDigital Avast Antivirus, named PrettyPrague. The exploit triggers a privilege escalation flaw.

The expert claims to have found another zero-day in an antimalware product, this time targeting Avast Antivirus. The PoC exploits a flaw in Avast Sandbox to dump the Windows SAM database and gain a SYSTEM-level shell. It reportedly works even on fully patched Avast Antivirus and Windows 11 25H2. The researcher also suspects the flaw may affect other Gen Digital products, including AVG and Norton.

Finally, Chaotic Eclipse released a new zero-day exploit targeting Crowdstrike Falcon cybersecurity platform. The researcher named the exploit FalconFlank, it triggers a privilege escalation flaw.

According to the researcher, FalconFlank abuses Falcon’s “Microsoft Office file malicious macro removal” feature. The function is part of Falcon’s remediation capabilities and operates with high privileges. The researcher claims that this behavior can be abused to escalate privileges from a low-privileged local user to a more powerful context.

Chaotic Eclipse is a researcher known for publicly releasing PoC exploits for zero-day vulnerabilities, often after criticizing vendors’ handling of vulnerability reports. His releases have mainly targeted Microsoft products, including Windows and Microsoft Defender, with some later exploited in the wild. Among the most notable are the Undefend and RedSun Defender zero-days.

His work has fueled debate over responsible disclosure and the risks of publishing working exploits.

Recently, Chaotic Eclipse revealed that he is Abdelhamid Naceri, a security researcher. Naceri previously worked with Microsoft in the UK and Germany. In a now-deleted X post, he described his departure from the company, claiming Microsoft terminated his employment without giving him a clear reason. He said Microsoft offered several financial settlements, but he rejected them because he wanted a formal explanation and help staying in Germany.

Naceri also said he challenged the dismissal in a German labor court. According to his account, Microsoft changed its arguments during the case, but the court ultimately upheld the termination. He said the long legal dispute left him with almost no compensation and caused serious financial and emotional problems, including treatment in a psychiatric hospital.

The researcher also admitted that an earlier claim that Microsoft had taken legal action against him was fabricated. The claim came during the controversy over Microsoft’s threats of legal action against security researchers who disclosed zero-day vulnerabilities.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, BigDiskBuster)

  • ✇Cybersecurity News
  • Microsoft Defender False Alarm: A Complete Resolution Do Son
    Discover how to permanently resolve the Microsoft Defender false alarm on Windows. Update your system now to stop inaccurate antivirus notifications. Related Posts: Master the Windows 11 Cloud Recovery Feature Resolve Microsoft Excel Copy Paste Issues Now Windows Server 2022 Mainstream Support Ends Soon The post Microsoft Defender False Alarm: A Complete Resolution appeared first on Daily CyberSecurity.
     

Microsoft Defender False Alarm: A Complete Resolution

Por:Do Son
20 de Setembro de 2026, 04:01

Discover how to permanently resolve the Microsoft Defender false alarm on Windows. Update your system now to stop inaccurate antivirus notifications.

Related Posts:

The post Microsoft Defender False Alarm: A Complete Resolution appeared first on Daily CyberSecurity.

  • ✇Security Affairs
  • Chaotic Eclipse Released ShieldCrash, A PoC For Microsoft Defender Zero-Day Pierluigi Paganini
    The researcher Chaotic Eclipse released ShieldCrash, a PoC exploit for a Microsoft Defender Zero-Day vulnerability. Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit ShieldCrash, it triggers an arbitrary file read as SYSTEM. The researcher claims that Microsoft has not fully fixed the ShieldBreak vulnerability (CVE-2026-69414). According to
     

Chaotic Eclipse Released ShieldCrash, A PoC For Microsoft Defender Zero-Day

9 de Setembro de 2026, 04:53

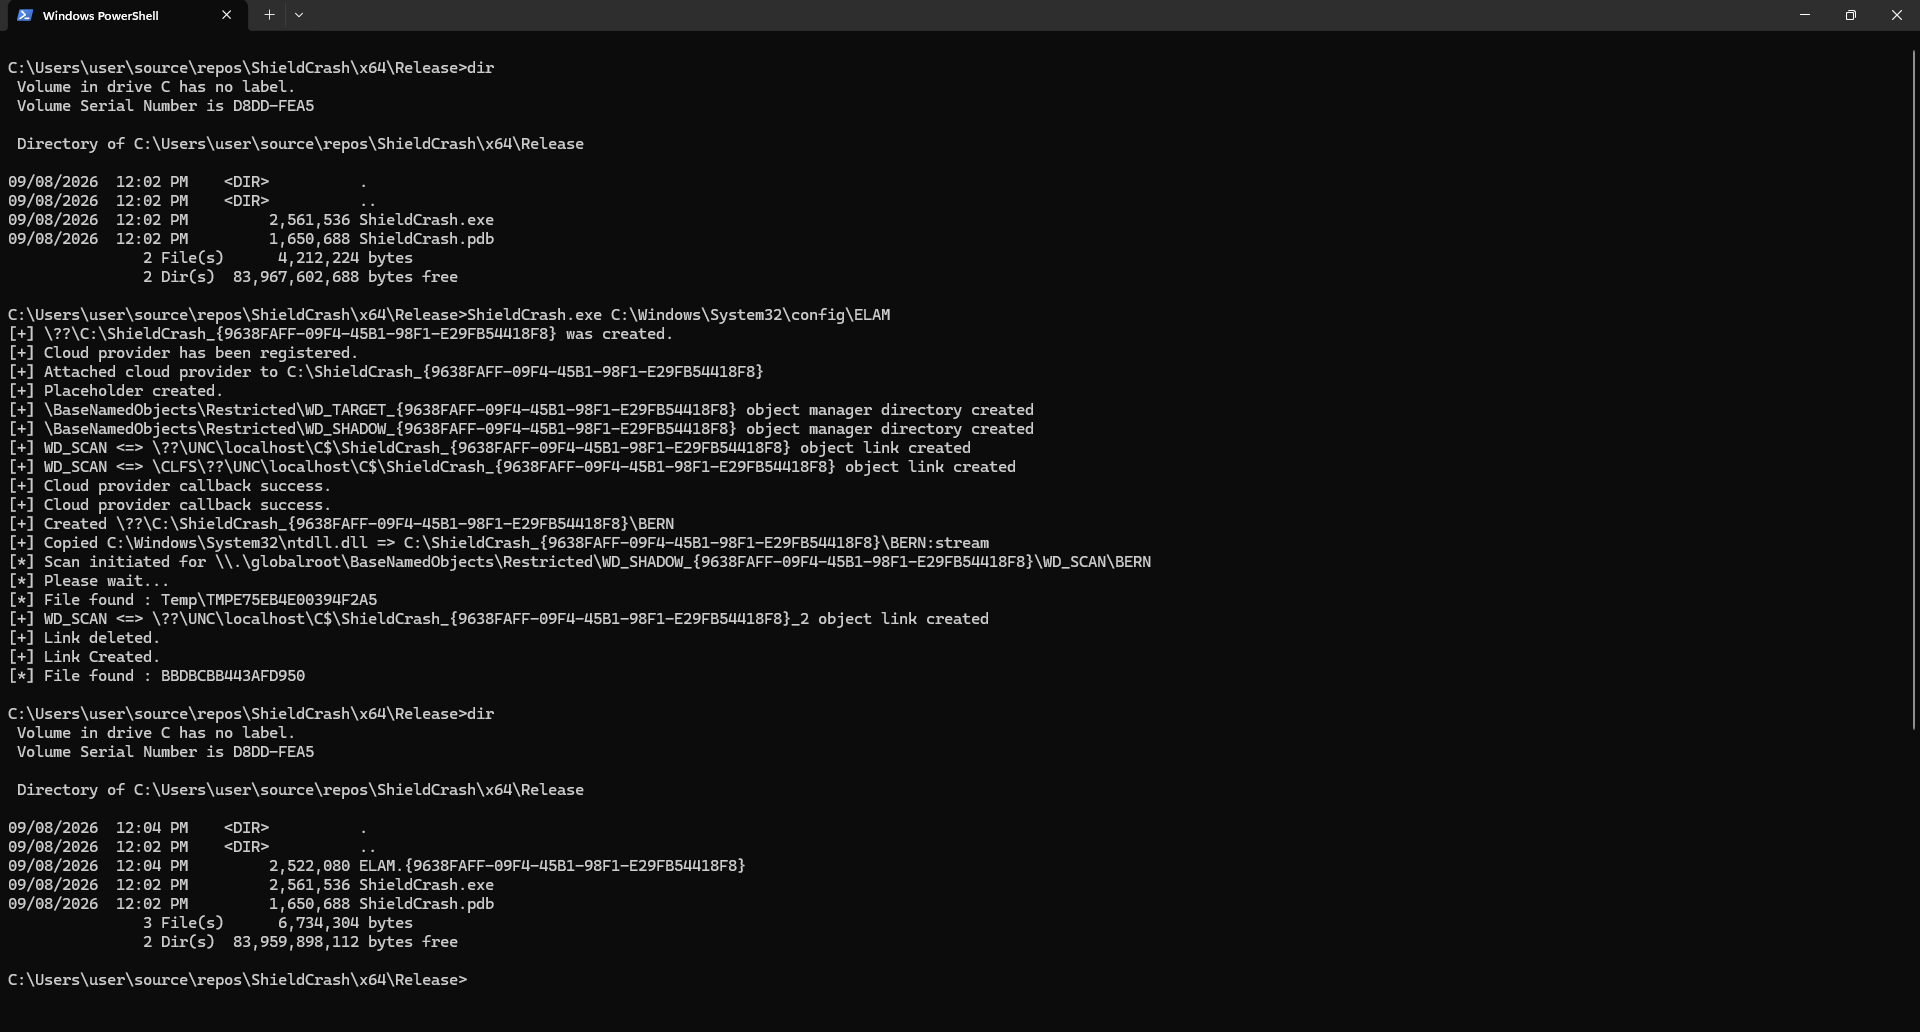
The researcher Chaotic Eclipse released ShieldCrash, a PoC exploit for a Microsoft Defender Zero-Day vulnerability.

Security researcher Chaotic Eclipse, also known as INFINITE NIGHTMARE, MSNightmare and Nightmare-Eclipse, released a new zero-day exploit targeting Microsoft Defender. The researcher named the exploit ShieldCrash, it triggers an arbitrary file read as SYSTEM.

The researcher claims that Microsoft has not fully fixed the ShieldBreak vulnerability (CVE-2026-69414). According to the researcher, Microsoft closed several ways to exploit the flaw but missed a specific condition that still allows the same attack.

The researcher published a proof of concept (PoC) that can read arbitrary files with SYSTEM privileges, the highest level of access on Windows. He says all supported Windows versions remain vulnerable, even after the September 2026 security updates.

“Microsoft has failed to properly patch ShieldBreak CVE-2026-69414, under specific conditions it is still possible to trigger the exact same problem that was caused by ShieldBreak. While Microsoft fixed several things to prevent re-exploiting the issue, they missed a spot where ShieldBreak can still be exploited.” Chaotic Eclipse wrote. “This PoC demonstrates an arbitrary file read as SYSTEM with September 2026, all supported windows versions are affected.”

The researcher described the PoC as a basic version for now. They may later develop it into a full SYSTEM-level exploit, but for now they published only enough code to show that Microsoft’s patch does not completely block ShieldBreak.

Microsoft recently updated the Malware Protection Engine to fix CVE-2026-69414. Version 1.1.26080.3 includes the fix, which requires no user action and does not affect systems with Microsoft Defender disabled. Microsoft recommends keeping malware definitions and the engine updated automatically.

“Microsoft is aware of an elevation of privilege in the Microsoft Malware Protection Engine in Microsoft Defender publicly referred to as “ShieldBreak ” reads Microsoft’s advisory. “In response to a constantly changing threat landscape, Microsoft frequently updates malware definitions and the Microsoft Malware Protection Engine. In order to be effective in helping protect against new and prevalent threats, antimalware software must be kept up to date with these updates in a timely manner. For enterprise deployments as well as end users, the default configuration in Microsoft antimalware software helps ensure that malware definitions and the Microsoft Malware Protection Engine are kept up to date automatically. Product documentation also recommends that products are configured for automatic updating.”

Last week, Chaotic Eclipse released a new zero-day exploit targeting Nvidia. The researcher named the exploit GreenSection, it triggers a Memory Corruption flaw.

Recently, Chaotic Eclipse released exploits targeting other anti-malware and defense solutions. Chaotic Eclipse released a zero-day exploit targeting Kaspersky Endpoint Security he named HardBreacher, which triggers a privilege escalation flaw. The researcher pointed out that the PoC is unstable and may require repeated attempts, but when successful, it creates a DLL in System32 with full user permissions. The researcher also claims taking control of Kaspersky’s UI process can disrupt the antivirus and interfere with file-access controls, potentially leaving the system in an unstable state.

Nightmare Eclipse says the Kaspersky Endpoint Security zero-day allows privilege escalation on a fully patched Windows 11 25H2 system running Kaspersky Endpoint v14.0.0.504.

The researcher also released a zero-day exploit targeting GenDigital Avast Antivirus, named PrettyPrague. The exploit triggers a privilege escalation flaw.

The researcher claims to have found another zero-day in an antimalware product, this time targeting Avast Antivirus. The PoC exploits a flaw in Avast Sandbox to dump the Windows SAM database and gain a SYSTEM-level shell. It reportedly works even on fully patched Avast Antivirus and Windows 11 25H2. The researcher also suspects the flaw may affect other Gen Digital products, including AVG and Norton.

Finally, Chaotic Eclipse released a new zero-day exploit targeting Crowdstrike Falcon cybersecurity platform. The researcher named the exploit FalconFlank, it triggers a privilege escalation flaw.

According to the researcher, FalconFlank abuses Falcon’s “Microsoft Office file malicious macro removal” feature. The function is part of Falcon’s remediation capabilities and operates with high privileges. The researcher claims that this behavior can be abused to escalate privileges from a low-privileged local user to a more powerful context.

Chaotic Eclipse, also known as Nightmare Eclipse, is a researcher known for publicly releasing PoC exploits for zero-day vulnerabilities, often after criticizing vendors’ handling of vulnerability reports. His releases have mainly targeted Microsoft products, including Windows and Microsoft Defender, with some later exploited in the wild. Among the most notable are the Undefend and RedSun Defender zero-days.

His work has fueled debate over responsible disclosure and the risks of publishing working exploits.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ShieldCrash)

  • ✇Malwarebytes
  • ShieldBreak bypasses Microsoft’s patch for earlier Defender flaw
    Microsoft Defender’s latest patch bypass shows a familiar problem. A newly disclosed Microsoft Defender flaw called ShieldBreak shows that fixing one attack path doesn’t always close every route to the same result. Microsoft has assigned ShieldBreak the identifier CVE-2026-69414 and confirmed it is an elevation of privilege (EoP) vulnerability in the Microsoft Malware Protection Engine. Microsoft says it is still working on a security update. If that sounds somehow familiar, you’re pro
     

ShieldBreak bypasses Microsoft’s patch for earlier Defender flaw

17 de Agosto de 2026, 10:34

Microsoft Defender’s latest patch bypass shows a familiar problem.

A newly disclosed Microsoft Defender flaw called ShieldBreak shows that fixing one attack path doesn’t always close every route to the same result.

Microsoft has assigned ShieldBreak the identifier CVE-2026-69414 and confirmed it is an elevation of privilege (EoP) vulnerability in the Microsoft Malware Protection Engine. Microsoft says it is still working on a security update.

If that sounds somehow familiar, you’re probably thinking of RoguePlanet, another vulnerability in Defender that Microsoft acknowledged on June 16 and patched on July 8.

A short timeline

At the time, the published exploit for RoguePlanet was described as depending on a race condition, meaning it was not guaranteed to work the same way on every machine. That was one reason the vulnerability was concerning but still somewhat limited from a practical point of view.

Microsoft’s July fix should have closed the door on that problem. But security fixes do not always eliminate a weakness at the root of the problem. Sometimes they block one known attack path, while a researcher later finds a different route to reach the same end result.

That appears to be what happened here. ShieldBreak has been described as a patch bypass because it reportedly sidesteps the earlier RoguePlanet fix, although it uses a different exploitation method rather than simply repeating the original attack.

In August, the same researcher disclosed ShieldBreak, and Microsoft responded by publishing a new advisory for CVE-2026-69414.

The advisory says the issue has been publicly disclosed, proof-of-concept (PoC) exploit code exists, exploitation is considered more likely, and no official fix is available yet. Microsoft says it is working on one.

How to stay safe

Until Microsoft releases a fix, the most important protection is preventing untrusted code from running on your computer in the first place. ShieldBreak is a local privilege escalation issue, so an attacker first needs some level of access to the machine.

Based on the best public reporting available right now, ShieldBreak appears to require Microsoft Defender to be enabled in order to work. Public testing indicates that the exploit does not succeed when Defender is off or when another product is registered as the active antivirus provider.

You're safe if Defender is turned off

So, narrowly speaking, disabling Defender appears to stop this specific ShieldBreak chain from working. However, that is not a good safety recommendation for most people. Turning off your antivirus removes an important layer of protection and could leave your computer exposed to other attacks.

For home users, all that means:

  • Install Microsoft’s security updates as soon as they become available.
  • Be very careful with downloads, email attachments, cracked software, and “fix” tools from random websites.
  • Keep backups of important files somewhere not directly connected to the PC.
  • Use an up-to-date, real-time anti-malware solution to alert you about and remove threats from your computer.

CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review →


Fake The Odyssey Downloads Are Hiding Password-Stealing Malware

10 de Agosto de 2026, 11:21

Fake downloads of The Odyssey are spreading Lumma Stealer malware capable of stealing passwords, cookies, payment data, and cryptocurrency information.

The post Fake The Odyssey Downloads Are Hiding Password-Stealing Malware appeared first on TechRepublic.

  • ✇Malwarebytes
  • Microsoft fixes RoguePlanet zero-day in Defender
    Microsoft issued a security update that fixes the zero-day vulnerability known as RoguePlanet in Microsoft Defender. RoguePlanet is tracked as CVE-2026-50656, a Microsoft Defender elevation of privilege (EoP) vulnerability. As we reported last month, if successfully exploited, RoguePlanet can allow an attacker to elevate privileges from a standard user account to NT AUTHORITY\SYSTEM, the highest privilege level on Windows. This means an attacker who gains access to a standard user account
     

Microsoft fixes RoguePlanet zero-day in Defender

9 de Julho de 2026, 08:38

Microsoft issued a security update that fixes the zero-day vulnerability known as RoguePlanet in Microsoft Defender.

RoguePlanet is tracked as CVE-2026-50656, a Microsoft Defender elevation of privilege (EoP) vulnerability. As we reported last month, if successfully exploited, RoguePlanet can allow an attacker to elevate privileges from a standard user account to NT AUTHORITY\SYSTEM, the highest privilege level on Windows.

This means an attacker who gains access to a standard user account on your computer could use the vulnerability to take complete control of the system. They don’t need advanced hacking skills or administrator permissions to do this.

Microsoft fixed the vulnerability by releasing Microsoft Malware Protection Engine version 1.1.26060.3008, an update to the core scanning engine that powers Microsoft Defender and other Microsoft security products.

How to protect your system

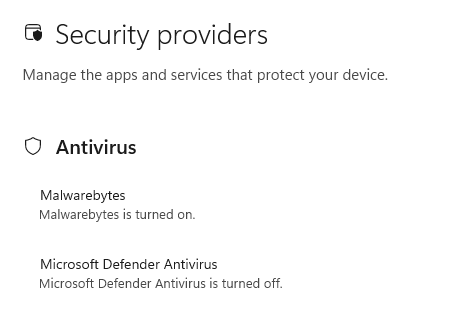
If Windows Security shows that another antivirus, such as Malwarebytes, is protecting your PC and Microsoft Defender Antivirus is turned off (as shown below), this particular vulnerability does not affect your system. Defender’s scanning engine isn’t running, so it can’t be exploited through this flaw.

Security providers
If you’re running another antivirus and Defender is turned off, there’s nothing to worry about

Most users are already protected

By default, Microsoft Defender automatically updates both its malware definitions and the Microsoft Malware Protection Engine.

But if you’re in any doubt, you can check the version of the Malware Protection Engine on your system. Here’s how:

  1. Click the Start button, type Security, and choose Windows Security from the results.
    Virus & threat protection
  2. Select Virus & threat protection, then under Virus & threat protection updates, click Check for updates.
  3. Click Settings (the cog icon) then select About.
  4. Look for a line called Engine Version. That number is the version of the Malware Protection Engine used by Microsoft Defender.
    • If your Engine Version is 1.1.26060.3008 or higher, your system has the patched (or newer) engine.
    • If your Engine Version is 1.1.26050.11 or lower, your system is still running a vulnerable engine. Run Windows Update and check for Defender updates again, or wait for the automatic update to complete.

Note: Version numbers are compared from left to right. For example, 1.1.26060.3008 is newer than 1.1.26050.11 because 26060 is higher than 26050.

If you use Windows Defender, leave automatic updates turned on. The Malware Protection Engine normally updates automatically, so most home users will receive the fix without doing anything. These steps are simply a way to double-check your system has the updated engine.


We don’t just report on threats—we remove them

Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.

1 Year of This Popular Antivirus is on Sale for $20

6 de Julho de 2026, 05:03

Bitdefender Antivirus Plus protects one PC for a full year with no monthly fees, and it even comes with a VPN.

The post 1 Year of This Popular Antivirus is on Sale for $20 appeared first on TechRepublic.

  • ✇Security Boulevard
  • Microsoft Defender Mistakenly Flags DigiCert Root Certificates as Malware Evan Rowe
    What happened A faulty Microsoft Defender antimalware signature update released around April 30, 2026, caused widespread false positive alerts by incorrectly flagging two legitimate DigiCert root certificates as high-severity malware. The detection, labeled Trojan:Win32/Cerdigent.A!dha, identified registry entries belonging to DigiCert Assured ID Root CA and DigiCert Trusted Root G4 as threats and automatically quarantined them […] The post Microsoft Defender Mistakenly Flags DigiCert Root Certi
     

Microsoft Defender Mistakenly Flags DigiCert Root Certificates as Malware

4 de Maio de 2026, 05:59

What happened A faulty Microsoft Defender antimalware signature update released around April 30, 2026, caused widespread false positive alerts by incorrectly flagging two legitimate DigiCert root certificates as high-severity malware. The detection, labeled Trojan:Win32/Cerdigent.A!dha, identified registry entries belonging to DigiCert Assured ID Root CA and DigiCert Trusted Root G4 as threats and automatically quarantined them […]

The post Microsoft Defender Mistakenly Flags DigiCert Root Certificates as Malware appeared first on CISO Whisperer.

The post Microsoft Defender Mistakenly Flags DigiCert Root Certificates as Malware appeared first on Security Boulevard.

Crush malware faster: Introducing Bitdefender sandbox integration with EclecticIQ

The challenge: Slow, fragmented malware analysis 

Cyber threats evolve rapidly, with advanced persistent threats (APTs) and zero-day malware bypassing traditional defences. SOC analysts need a faster, more integrated way to analyse suspicious files and URLs - without switching between multiple tools. 

❌
❌