❌

Visualização normal

Antes de ontemStream principal
  • ✇Firewall Daily – The Cyber Express
  • Fake Reviews, Deceptive Ads: FTC Targets Alleged Passport Scam Samiksha Jain
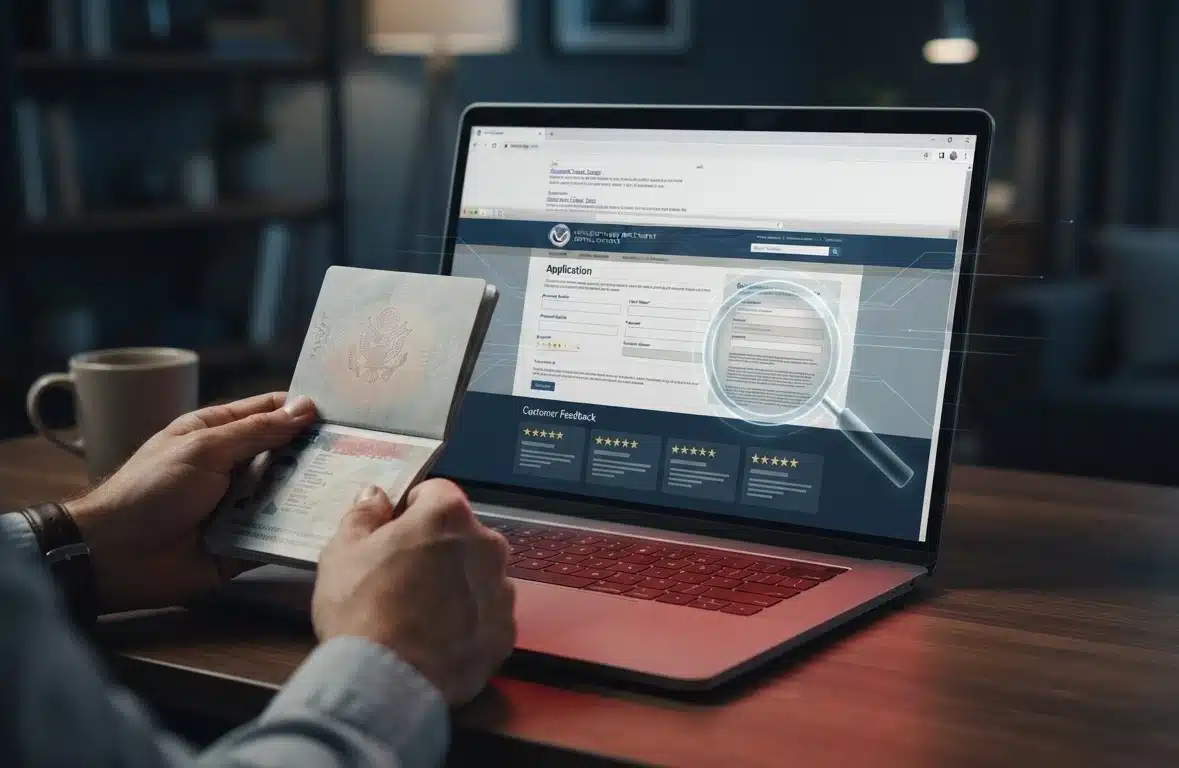
    The Federal Trade Commission (FTC) has filed a complaint against GovAssist LLC, Entry LLC and Scott Zuckerman over an alleged government impersonation scheme targeting consumers seeking U.S. passport and travel-related services. The case highlights how paid search advertising, misleading service promises and allegedly fake customer reviews can be used to make commercial websites appear connected to official government services. According to the FTC, the defendants allegedly used websites and sp
     

Fake Reviews, Deceptive Ads: FTC Targets Alleged Passport Scam

23 de Outubro de 2026, 07:27

Government impersonation scheme

The Federal Trade Commission (FTC) has filed a complaint against GovAssist LLC, Entry LLC and Scott Zuckerman over an alleged government impersonation scheme targeting consumers seeking U.S. passport and travel-related services. The case highlights how paid search advertising, misleading service promises and allegedly fake customer reviews can be used to make commercial websites appear connected to official government services.

According to the FTC, the defendants allegedly used websites and sponsored search results to attract travelers, collect personal and financial information, and mislead consumers about the services they would receive. The complaint was filed in the U.S. District Court for the District of Puerto Rico.

How the Government Impersonation Scheme Allegedly Worked?

The FTC alleges that, since at least October 2023, GovAssist, Entry and Zuckerman operated websites including GovAssist.com, Entry.com and IVS.us, offering passport applications, passport-related services, visa applications and visa renewals.

The complaint states that the websites presented themselves as affiliated with the U.S. State Department, although the defendants were neither the federal government nor authorized government-affiliated providers of passport-related services.

The alleged operation relied on paid search ads to reach people looking for official passport information. Searches such as “apply for a new passport,” “passport renewal,” and “passport renewal online” routinely returned IVS.us and Entry.com pages among Google’s top sponsored results, according to the FTC.

This approach allegedly placed commercial services in locations where users might expect to find official government resources. The distinction matters because consumers searching for essential documents may not recognize that a sponsored result belongs to a private company rather than a government agency.

Misleading Passport Service Claims and Hidden Costs

The FTC alleges that the defendants made false promises about what their services could deliver, including claims that they could directly issue U.S. passports. In many cases, consumers allegedly received only a completed passport application that was available for free through the State Department’s website.

The complaint also challenges the companies’ pricing disclosures. Although their advertisements or websites reportedly stated that services started at $89, the FTC alleges that the lowest available price was $119, plus a $29 shipping fee, bringing the total to $148.

Consumers also needed to pay the State Department when submitting their passport applications. According to the complaint, the defendants prominently displayed their own prices while omitting or downplaying the additional government fee, potentially leaving customers unaware that they would have to pay again.

Delivery claims are another part of the case. The FTC alleges that the defendants advertised expedited passport services promising delivery in as little as six to 10 business days or three to four business days. The agency contends these promises were false because the timelines were faster than the quickest expedited service available through the State Department, the only source of U.S. passports.

Fake Reviews and Consumer Trust

The complaint further alleges that the defendants used fake positive reviews to make their services appear legitimate. Their websites reportedly highlighted excellent ratings based on consumer feedback published on Trustpilot and other review platforms.

According to the FTC, those ratings relied on high numbers of fake positive reviews. If established, the allegations would show how misleading reviews can reinforce the credibility created by sponsored search placements, making it harder for consumers to distinguish legitimate services from deceptive offerings.

The alleged combination of deceptive ads and fake reviews is central to the case because consumers may rely on both search rankings and customer feedback when deciding which service to trust.

FTC Alleges Violations of Three Federal Laws

The FTC alleges that the defendants violated the FTC Act, the Impersonation Rule and the Gramm-Leach-Bliley Act. The complaint targets the alleged impersonation of government services, misleading representations about passport processing and pricing, and the use of false consumer reviews.

Zuckerman, identified as the owner and sole member of GovAssist and Entry, allegedly operated the scheme while subject to an FTC order in an earlier, unrelated case involving Support King LLC. That case concerned stalkerware and resulted in a final administrative order addressing data privacy.

The FTC said its staff received assistance from the U.S. Postal Inspection Service, the U.S. Attorney’s Office for the District of Puerto Rico and the U.S. Department of State. The Commission authorized the complaint in a 2-0 vote.

What the Case Reveals About Online Consumer Fraud

The allegations illustrate how consumer fraud can exploit the gap between what users expect from an online search and what a website actually provides. A sponsored result may appear prominently, but its placement does not establish that the service is government-operated or officially authorized.

The case also highlights the role of pricing transparency and review authenticity in online trust. Claims about faster processing, low starting prices, and positive customer experiences can influence purchasing decisions, particularly when consumers need time-sensitive travel documents.

The FTC has emphasized that filing a complaint does not establish that the defendants violated the law. The case will be decided by the court.

For consumers, the allegations underscore the importance of distinguishing official government services from third-party providers and checking fees, processing claims, and reviewing credibility before sharing personal or financial information. The FTC also states that it will never demand money, threaten consumers, instruct them to transfer money, or promise them a prize.

Cloudflare
Verify you are human

loading

Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content.
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare

site-verification-ok
Cloudflare
Verify you are human
loading
Checking your browser before accessing this site.
Click to verify →
Then you will be redirected to the requested content.
Ray ID: 8f3a2c1b9d4e5f6a · Performance & security by Cloudflare

site-verification-ok

TP-Link Faces 5 State Lawsuits: Are Its Routers Still Legal in the US?

8 de Outubro de 2026, 16:23

Five states have sued TP-Link over router security and disclosure claims. Here's how the lawsuits, FCC restrictions, and firmware vulnerabilities affect existing owners.

The post TP-Link Faces 5 State Lawsuits: Are Its Routers Still Legal in the US? appeared first on TechRepublic.

  • ✇Cybersecurity News
  • X Content Farm Lawsuit Targets Engagement Fraud Do Son
    Discover the details of the X content farm lawsuit. Elon Musk's social network takes legal action to recover $278,000 lost to creator revenue fraud. Related Posts: Amazon Blocks Meta Muse AI Assistant OpenAI Races to Counter Grok Bot and Meta's Muse DPC Imposes Massive GDPR Penalty on Google The post X Content Farm Lawsuit Targets Engagement Fraud appeared first on Daily CyberSecurity.
     

X Content Farm Lawsuit Targets Engagement Fraud

Por:Do Son
21 de Setembro de 2026, 23:35

Discover the details of the X content farm lawsuit. Elon Musk's social network takes legal action to recover $278,000 lost to creator revenue fraud.

Related Posts:

The post X Content Farm Lawsuit Targets Engagement Fraud appeared first on Daily CyberSecurity.

  • ✇Malwarebytes
  • Grindr settles HIV status data-sharing lawsuit for $35 million
    Grindr has reportedly agreed to pay £26 million (around $35 million) to settle a UK privacy lawsuit alleging that it shared sensitive user data, including some users’ HIV status, with advertisers. The claim was brought by London law firm Austen Hays on behalf of roughly 12,000 UK Grindr users. It alleges that the dating app breached privacy and data-protection laws during a period ending in early 2020. The claimants allege that Grindr shared personal and highly sensitive information with a
     

Grindr settles HIV status data-sharing lawsuit for $35 million

8 de Setembro de 2026, 09:51

Grindr has reportedly agreed to pay £26 million (around $35 million) to settle a UK privacy lawsuit alleging that it shared sensitive user data, including some users’ HIV status, with advertisers.

The claim was brought by London law firm Austen Hays on behalf of roughly 12,000 UK Grindr users. It alleges that the dating app breached privacy and data-protection laws during a period ending in early 2020.

The claimants allege that Grindr shared personal and highly sensitive information with advertising companies without consent. According to Austen Hays, the shared data may have included ethnicity, HIV status, the date of a user’s last HIV test, and whether they used pre-exposure prophylaxis (PrEP).

At the time of the alleged data sharing practices, Grindr was owned and controlled by the Chinese gaming company Beijing Kunlun Tech. Grindr was sold to US owners in 2020.

According to a US regulatory filing, Grindr will make two payments of £13 million: one by December 31, 2026, and the second by March 31, 2027.

In its SEC filing, Grindr said that the settlement is not an admission of liability and, while it disputes the allegations, it:

recognizes and acknowledges the distress and loss of trust expressed by some of its UK users regarding that pre-2020 period.

The UK settlement follows a separate enforcement case in Norway. The country’s Data Protection Authority found that Grindr had shared users’ personal data with advertising partners for behavioral advertising without a valid legal basis.

These cases illustrate a crucial privacy point: information does not need to be explicitly labeled as medical information or information about sexual orientation to expose intimate details about someone. Advertising identifiers, IP addresses, locations, device information, and confirmation that a person uses a particular app can be combined to identify them or draw sensitive conclusions about their life.

Many free apps rely on advertising SDKs, analytics providers, and other third parties to make money. These integrations can receive identifiers and event data that help target or measure advertising, but they can also create extensive trails of user behavior.

How to protect your privacy on dating apps

Grindr says it has overhauled its privacy program since 2020 and remains committed to user control and responsible data practices. Even so, dating apps can hold unusually personal information about their users.

To limit what you reveal:

  • Review the app’s privacy settings and turn off optional personalized advertising where available.
  • Limit your profile to details you’re comfortable sharing with potential matches.
  • Avoid linking a dating profile to public social-media accounts unless you want identities to be easily connected.
  • Revoke location permissions when you’re not actively using the app, or choose “while using the app” rather than continuous access where your operating system offers it.
  • Keep the app, your operating system, and your security software updated.
  • Watch for romance scams and extortion attempts, particularly requests to move the conversation off the app, send money, share intimate photos, or reveal identifying information.

If you’re unsure whether a message may be part of a scam, you can check it with Malwarebytes Scam Guard, which can help you assess the conversation and decide what to do next.


Scammers don’t need to hack you. They just need you to click once. 

Malwarebytes Identity Theft Protection catches suspicious activity before it becomes a problem.

  • ✇Firewall Daily – The Cyber Express
  • FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices Samiksha Jain
    The Hims & Hers lawsuit has put the telehealth provider under scrutiny after the FTC, along with Utah and California authorities, accused the company of deceptive billing practices and unlawfully sharing consumers' sensitive health information with third-party advertising platforms. According to a complaint filed in federal court, regulators allege that Hims & Hers misled consumers about its privacy protections, enrolled users in recurring subscriptions without clear disc
     

FTC Sues Hims & Hers Over Health Data Privacy, Billing Practices

Hims & Hers lawsuit

The Hims & Hers lawsuit has put the telehealth provider under scrutiny after the FTC, along with Utah and California authorities, accused the company of deceptive billing practices and unlawfully sharing consumers' sensitive health information with third-party advertising platforms. According to a complaint filed in federal court, regulators allege that Hims & Hers misled consumers about its privacy protections, enrolled users in recurring subscriptions without clear disclosure, and shared health-related data with companies including Meta and Snap.

The complaint alleges that the San Francisco-based telehealth provider failed to clearly inform consumers that prescription charges could be processed almost immediately after they submitted an online intake form, despite representing that they would first consult with a medical provider to determine an appropriate treatment.

FTC Complaint Alleges Deceptive Billing Practices

According to the FTC complaint, consumers interested in Hims & Hers services are required to complete an online intake form for review by a medical provider before receiving prescription treatment. During this process, users provide billing information after being assured they would not be charged unless medication was prescribed.

However, regulators allege that most consumers were not given a consultation with a provider before being charged. Instead, the complaint states that submitting the intake form automatically enrolled many users in recurring prescription subscriptions and processed charges before consumers had an opportunity to review or approve the treatment.

The complaint also alleges that Hims & Hers did not clearly disclose when prescription refills would occur, making it difficult for consumers to cancel subscriptions before the next billing cycle.

One consumer complaint cited by the FTC stated that they were told they would speak with a doctor within a few days and would not be charged immediately, but their payment was processed before any consultation took place.

Hims & Hers Lawsuit: Privacy Practices Under Investigation

The Hims & Hers lawsuit also centers on allegations involving health data privacy.

According to the complaint, Hims & Hers shared consumers' sensitive health information with advertising platforms such as Meta and Snap, despite assuring users that their medical information would remain private.

The FTC alleges that the company shared customer lists with advertising platforms and also used third-party tracking technologies that automatically transmitted website activity, referred to as "Events," to those companies.

Regulators argue that these practices exposed health-related information while contradicting the company's privacy representations to consumers.

Subscription Cancellation Process Questioned

The complaint further alleges that Hims & Hers created obstacles for consumers attempting to cancel recurring subscriptions.

Before 2023, most users could only cancel by contacting customer service through phone, email, or chat. Even after introducing online cancellation, regulators allege the company continued to make the process difficult by hiding the cancellation option behind multiple navigation steps. According to the complaint, consumers first had to select "add/remove items from order" before eventually reaching the cancellation page.

The FTC alleges these practices violate both the FTC Act and the Restore Online Shoppers' Confidence Act, which governs deceptive billing and subscription practices. Utah and California have also alleged violations under their respective consumer protection laws.

Hims & Hers Rejects Allegations

In a statement posted on X, Hims & Hers rejected the allegations and said the lawsuit ignores evidence provided during the FTC's nearly three-year investigation.

The company described the action as an attempt to generate headlines rather than enforce consumer protection laws and said it intends to defend itself in court vigorously.

Hims & Hers also stated that millions of consumers have relied on its services since 2017 and that its Privacy Policy explains how customer data is used. The company added that patients can choose how their information is handled and maintained that information shared with healthcare providers is used only to deliver care.

The lawsuit was authorized by a 2-0 vote of the Commission and filed in the U.S. District Court for the Northern District of California. The allegations remain claims made by regulators, and the court will ultimately decide the case.

Apple Sued Over Hide My Email Privacy Claims

17 de Julho de 2026, 11:19

Apple faces a proposed class action alleging a Hide My Email flaw could expose users’ real addresses despite the company’s privacy claims.

The post Apple Sued Over Hide My Email Privacy Claims appeared first on TechRepublic.

❌
❌