❌

Visualização normal

Antes de ontemStream principal
  • ✇Cybersecurity News
  • Palo Alto Networks Confirms Critical Brotli Flaw CVE-2026-111497 Affects PAN-OS Do Son
    Palo Alto confirms PAN-OS Brotli vulnerability CVE-2026-111497, a CVSS 9.2 buffer overflow in PAN-OS 12.2, 12.1 and 11.2. Install the hotfixes now. Related Posts: Apple iOS 27.2 Update Fixes 160 Security Flaws CISA Adds PHP2Shell to KEV as Confirmed RCE Attacks and Suspected DPRK Scanning Surface Apple Backports Fix for Exploited CoreGraphics Zero-Day CVE-2026-86950 to Older iPhones The post Palo Alto Networks Confirms Critical Brotli Flaw CVE-2026-111497 Affects PAN-OS appeared first on Dail
     
  • ✇Cybersecurity News
  • Palo Alto Networks Confirms PHP2Shell Flaws Affect PAN-OS and Panorama Do Son
    Palo Alto confirms PAN-OS PHP2Shell flaws CVE-2026-109618 and CVE-2026-109619 affect the firewall management interface. Restrict access and patch. Related Posts: PHP Warns of New Session Upload Progress Flaw CVE-2026-115560, Urges Mitigation LiteSpeed Cache Flaws Expose 7 Million WordPress Sites to Stored XSS Oracle Issues Java Security Alert to Distrust Compromised eMudhra Certificates The post Palo Alto Networks Confirms PHP2Shell Flaws Affect PAN-OS and Panorama appeared first on Daily Cyb
     
  • ✇Cybersecurity News
  • Palo Alto PAN-OS RCE Vulnerability CVE-2026-0322 Actively Exploited in the Wild Do Son
    Attackers are actively exploiting CVE-2026-0322, a high-severity Palo Alto PAN-OS RCE vulnerability in the management interface. Apply patches right now. Related Posts: Next.js Fixes Two Critical Unauthenticated RCE Flaws in Out-of-Band Update Citrix Patches XenServer Host Escape Risks and UniconOS Privilege Escalation Flaws SiteGuard Server Edition Flaw CVE-2026-106931 Exploited in the Wild for Root Access The post Palo Alto PAN-OS RCE Vulnerability CVE-2026-0322 Actively Exploited in the Wi
     
  • ✇Security Boulevard
  • Unauthorized Users Reportedly Gain Access to Anthropic’s Mythos AI Model Jeffrey Burt
    A group of unauthorized users reportedly has gained access to Anthropic’s controversial Claude Mythos Preview AI frontier model despite the AI vendor’s efforts to keep it out of public hands by limiting the organizations that can use it. Bloomberg reported that the unnamed group had tried multiple ways to gain access to the AI model.. The post Unauthorized Users Reportedly Gain Access to Anthropic’s Mythos AI Model appeared first on Security Boulevard.
     
  • ✇Krebs on Security
  • Iran-Backed Hackers Claim Wiper Attack on Medtech Firm Stryker BrianKrebs
    A hacktivist group with links to Iran’s intelligence agencies is claiming responsibility for a data-wiping attack against Stryker, a global medical technology company based in Michigan. News reports out of Ireland, Stryker’s largest hub outside of the United States, said the company sent home more than 5,000 workers there today. Meanwhile, a voicemail message at Stryker’s main U.S. headquarters says the company is currently experiencing a building emergency. Based in Kalamazoo, Michigan, Stryker
     

Iran-Backed Hackers Claim Wiper Attack on Medtech Firm Stryker

11 de Março de 2026, 13:20

A hacktivist group with links to Iran’s intelligence agencies is claiming responsibility for a data-wiping attack against Stryker, a global medical technology company based in Michigan. News reports out of Ireland, Stryker’s largest hub outside of the United States, said the company sent home more than 5,000 workers there today. Meanwhile, a voicemail message at Stryker’s main U.S. headquarters says the company is currently experiencing a building emergency.

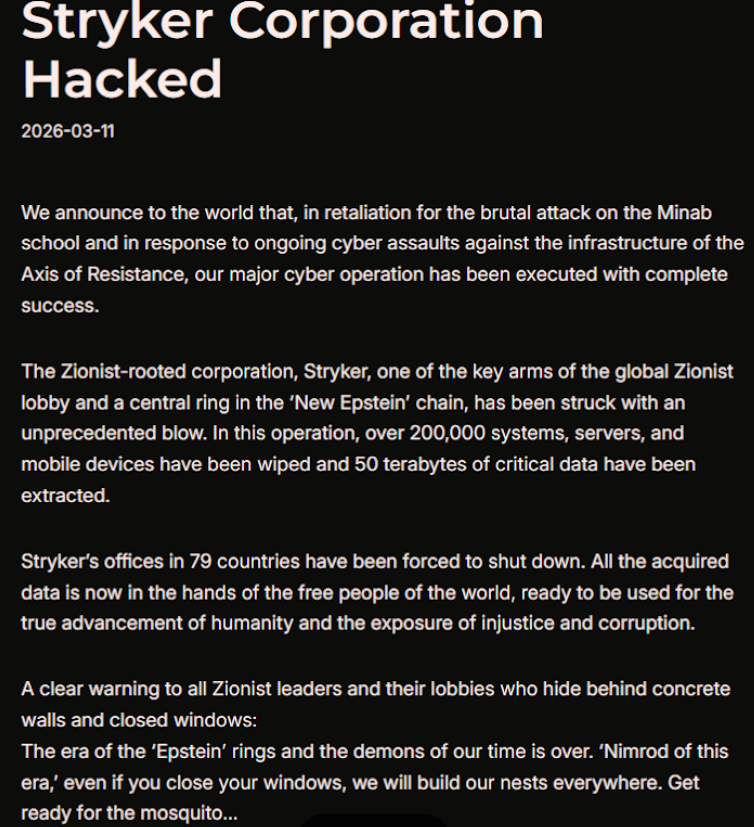
Based in Kalamazoo, Michigan, Stryker [NYSE:SYK] is a medical and surgical equipment maker that reported $25 billion in global sales last year. In a lengthy statement posted to Telegram, a hacktivist group known as Handala (a.k.a. Handala Hack Team) claimed that Stryker’s offices in 79 countries have been forced to shut down after the group erased data from more than 200,000 systems, servers and mobile devices.

A manifesto posted by the Iran-backed hacktivist group Handala, claiming a mass data-wiping attack against medical technology maker Stryker.

A manifesto posted by the Iran-backed hacktivist group Handala, claiming a mass data-wiping attack against medical technology maker Stryker.

“All the acquired data is now in the hands of the free people of the world, ready to be used for the true advancement of humanity and the exposure of injustice and corruption,” a portion of the Handala statement reads.

The group said the wiper attack was in retaliation for a Feb. 28 missile strike that hit an Iranian school and killed at least 175 people, most of them children. The New York Times reports today that an ongoing military investigation has determined the United States is responsible for the deadly Tomahawk missile strike.

Handala was one of several hacker groups recently profiled by Palo Alto Networks, which links it to Iran’s Ministry of Intelligence and Security (MOIS). Palo Alto says Handala surfaced in late 2023 and is assessed as one of several online personas maintained by Void Manticore, a MOIS-affiliated actor.

Stryker’s website says the company has 56,000 employees in 61 countries. A phone call placed Wednesday morning to the media line at Stryker’s Michigan headquarters sent this author to a voicemail message that stated, “We are currently experiencing a building emergency. Please try your call again later.”

A report Wednesday morning from the Irish Examiner said Stryker staff are now communicating via WhatsApp for any updates on when they can return to work. The story quoted an unnamed employee saying anything connected to the network is down, and that “anyone with Microsoft Outlook on their personal phones had their devices wiped.”

“Multiple sources have said that systems in the Cork headquarters have been ‘shut down’ and that Stryker devices held by employees have been wiped out,” the Examiner reported. “The login pages coming up on these devices have been defaced with the Handala logo.”

Wiper attacks usually involve malicious software designed to overwrite any existing data on infected devices. But a trusted source with knowledge of the attack who spoke on condition of anonymity told KrebsOnSecurity the perpetrators in this case appear to have used a Microsoft service called Microsoft Intune to issue a ‘remote wipe’ command against all connected devices.

Intune is a cloud-based solution built for IT teams to enforce security and data compliance policies, and it provides a single, web-based administrative console to monitor and control devices regardless of location. The Intune connection is supported by this Reddit discussion on the Stryker outage, where several users who claimed to be Stryker employees said they were told to uninstall Intune urgently.

Palo Alto says Handala’s hack-and-leak activity is primarily focused on Israel, with occasional targeting outside that scope when it serves a specific agenda. The security firm said Handala also has taken credit for recent attacks against fuel systems in Jordan and an Israeli energy exploration company.

“Recent observed activities are opportunistic and ‘quick and dirty,’ with a noticeable focus on supply-chain footholds (e.g., IT/service providers) to reach downstream victims, followed by ‘proof’ posts to amplify credibility and intimidate targets,” Palo Alto researchers wrote.

The Handala manifesto posted to Telegram referred to Stryker as a “Zionist-rooted corporation,” which may be a reference to the company’s 2019 acquisition of the Israeli company OrthoSpace.

Stryker is a major supplier of medical devices, and the ongoing attack is already affecting healthcare providers. One healthcare professional at a major university medical system in the United States told KrebsOnSecurity they are currently unable to order surgical supplies that they normally source through Stryker.

“This is a real-world supply chain attack,” the expert said, who asked to remain anonymous because they were not authorized to speak to the press. “Pretty much every hospital in the U.S. that performs surgeries uses their supplies.”

John Riggi, national advisor for the American Hospital Association (AHA), said the AHA is not aware of any supply-chain disruptions as of yet.

“We are aware of reports of the cyber attack against Stryker and are actively exchanging information with the hospital field and the federal government to understand the nature of the threat and assess any impact to hospital operations,” Riggi said in an email. “As of this time, we are not aware of any direct impacts or disruptions to U.S. hospitals as a result of this attack. That may change as hospitals evaluate services, technology and supply chain related to Stryker and if the duration of the attack extends.”

According to a March 11 memo from the state of Maryland’s Institute for Emergency Medical Services Systems, Stryker indicated that some of their computer systems have been impacted by a “global network disruption.” The memo indicates that in response to the attack, a number of hospitals have opted to disconnect from Stryker’s various online services, including LifeNet, which allows paramedics to transmit EKGs to emergency physicians so that heart attack patients can expedite their treatment when they arrive at the hospital.

“As a precaution, some hospitals have temporarily suspended their connection to Stryker systems, including LIFENET, while others have maintained the connection,” wrote Timothy Chizmar, the state’s EMS medical director. “The Maryland Medical Protocols for EMS requires ECG transmission for patients with acute coronary syndrome (or STEMI). However, if you are unable to transmit a 12 Lead ECG to a receiving hospital, you should initiate radio consultation and describe the findings on the ECG.”

This is a developing story. Updates will be noted with a timestamp.

Update, 2:54 p.m. ET: Added comment from Riggi and perspectives on this attack’s potential to turn into a supply-chain problem for the healthcare system.

Update, Mar. 12, 7:59 a.m. ET: Added information about the outage affecting Stryker’s online services.

  • ✇DCiber
  • Cibercriminosos adotam agentes de IA para lançar ataques autônomos e adaptáveis em 2025 Redação
    De acordo com um estudo publicado pelo Observatório Latino-Americano de Ameaças Digitais (OLAD) em 2025, 411 ataques cibernéticos e ameaças digitais direcionados a empresas e instituições na América Latina foram documentados durante o ano passado, incluindo infraestruturas críticas como alvos, espionagem e ransomware. À medida que os recursos de defesa de IA evoluem, o mesmo acontece com as estratégias e ferramentas de IA utilizadas pelos agentes de ameaças, criando um cenário de riscos em ráp
     

Cibercriminosos adotam agentes de IA para lançar ataques autônomos e adaptáveis em 2025

6 de Dezembro de 2025, 11:45

De acordo com um estudo publicado pelo Observatório Latino-Americano de Ameaças Digitais (OLAD) em 2025, 411 ataques cibernéticos e ameaças digitais direcionados a empresas e instituições na América Latina foram documentados durante o ano passado, incluindo infraestruturas críticas como alvos, espionagem e ransomware.

À medida que os recursos de defesa de IA evoluem, o mesmo acontece com as estratégias e ferramentas de IA utilizadas pelos agentes de ameaças, criando um cenário de riscos em rápida transformação que superam os métodos tradicionais de detecção e respostas. Nesse contexto, a nova pesquisa da Unit 42, equipe de inteligência de ameaças da Palo Alto Networks, intitulada Agentic AI Attack Framework, revelou como os criminosos estão começando a usar os agentes, uma evolução da inteligência artificial que vai além da geração de conteúdo a qual, ao contrário da generativa, que se concentra na criação de texto, imagens ou código, depende somente de agentes autônomos capazes de tomar decisões, adaptar ao ambiente e executar várias fases de um ataque cibernético sem intervenção humana direta.

O relatório detalha como esses agentes podem ser programados para executar tarefas como inspeção do sistema, escrever e-mails de phishing personalizados, evitar controles de segurança, manipular conversas em tempo real e remover rastros digitais. O mais preocupante é que eles podem aprender com os erros, ajustar o próprio comportamento e colaborar entre si, o que os torna uma ameaça muito mais dinâmica e difícil de conter.

Durante os testes, a Unit 42 simulou um ataque de ransomware, desde o comprometimento inicial até a exfiltração de dados, em apenas 25 minutos, usando IA em cada estágio da cadeia de ataque. Isso representou um aumento de 100 vezes na velocidade, totalmente impulsionado por IA.

Em contraste com os ciberataques tradicionais, que normalmente seguem padrões previsíveis e exigem intervenção humana em cada estágio, os ataques agênticos podem operar de forma contínua e adaptável. Isso significa que um único agente pode iniciar uma campanha de invasão, avaliar seu progresso, modificar sua estratégia em tempo real e escalar o ataque sem a necessidade de supervisão direta. Essa capacidade de ser autônomo representa um desafio para as equipes de cibersegurança, que precisam lidar com ameaças que não são apenas mais rápidas, como também mais inteligentes e persistentes.

Esses ataques cibernéticos podem ter consequências graves para as organizações. Por exemplo, um agente mal-intencionado pode enviar e-mails falsos altamente convincentes aos funcionários para roubar senhas, se infiltrar em sistemas internos e circular pela rede sem ser detectado. Isso leva ao roubo de informações confidenciais, como dados de clientes ou planos estratégicos, ou até mesmo ao sequestro de sistemas importantes por ransomware, paralisando as operações por dias. Além do impacto econômico, esses incidentes prejudicam a reputação da empresa, geram uma perda de confiança e podem levar a sanções legais se informações pessoais ou financeiras forem comprometidas.

Preparando-se para o imprevisível: como fortalecer a segurança organizacional

Nesse cenário, as organizações precisam de uma infraestrutura de segurança avançada e adaptável. Não é mais suficiente reagir a incidentes, agora é essencial antecipá-los por meio de monitoramento contínuo, análise inteligente de dados e automação dos principais processos.

A tendência à plataformização permite que as empresas reduzam a fragmentação tecnológica, melhorem a visibilidade do próprio ambiente digital e respondam mais rapidamente a qualquer tentativa de invasão. A Palo Alto Networks, por exemplo, está fazendo algo exatamente nesse sentido, desenvolvendo uma plataforma unificada de segurança de dados que abrangerá desde o desenvolvimento de código até ambientes de nuvem e centros de operações de segurança (SOCs). Essa iniciativa busca oferecer uma visão holística da segurança e facilitar o gerenciamento centralizado de ameaças, o que é essencial diante de um cenário de ataques cibernéticos cada vez mais sofisticados.

Além disso, a adoção de arquiteturas como o SASE (Secure Access Service Edge) fortalece a postura de segurança ao estender a proteção para além do perímetro tradicional. Essas tecnologias permitem controles granulares baseados em identidade, contexto e comportamento, o que é fundamental em um ambiente em que usuários, dispositivos e aplicativos estão distribuídos. Para as organizações brasileiras, investir nesse tipo de recurso representa uma melhoria técnica, bem como uma estratégia fundamental para garantir a continuidade operacional e a proteção de ativos essenciais contra ameaças cada vez mais automatizadas e persistentes.

O Brasil, com a crescente digitalização em setores-chave, como saúde, educação e serviços públicos, se torna um alvo atraente para essa ameaça emergente. A necessidade de fortalecer as capacidades de segurança cibernética no país é urgente, especialmente em face da adoção acelerada de tecnologias digitais em todos os níveis do governo e das empresas.

Diante desse cenário, especialistas da Palo Alto Networks recomendam que as organizações brasileiras implementem soluções de segurança que integrem recursos de detecção baseados em IA, bem como programas de conscientização e resposta a incidentes que considerem esse novo tipo de ameaças automatizadas.

A evolução dos ataques cibernéticos para esquemas mais autônomos e adaptáveis exige uma resposta igualmente inovadora. Somente por meio de estratégias proativas e colaborativas será possível mitigar os riscos apresentados por essa nova era de ataques alimentados pelos agentes de IA.

Sobre a Unit 42

A Unit 42 da Palo Alto Networks reúne pesquisadores de ameaças de renome mundial, respondentes de incidentes de elite e consultores de segurança especializados para criar uma organização orientada por inteligência e pronta para responder, apaixonada por ajudar a gerenciar o risco cibernético proativamente. Juntos, nossa equipe atua como seu consultor de confiança para ajudar a avaliar e testar controles de segurança contra as ameaças certas, transformar estratégias de segurança com uma abordagem informada sobre ameaças e responder a incidentes em tempo recorde para que você possa voltar aos negócios mais rapidamente. Visite paloaltonetworks.com/unit42.

Sobre a Palo Alto Networks

Como líder global em segurança cibernética, a Palo Alto Networks (NASDAQ: PANW) tem o compromisso de proteger nosso modo de vida digital por meio de inovação contínua. Com a confiança de organizações em todo o mundo, fornecemos soluções de segurança de ponta a ponta baseadas em IA em redes, nuvem, operações de segurança e IA, capacitadas pela inteligência e experiência em ameaças da Unit 42. Nosso foco na plataformização permite que as empresas simplifiquem a segurança em escala, garantindo que a proteção impulsione a inovação. Saiba mais em www.paloaltonetworks.com.

  • ✇HACKMAGEDDON
  • CVEs Targeting Remote Access Technologies in 2025 Paolo Passeri
    The exploitation of vulnerabilities targeting remote access technologies to gain initial access is continuing relentlessly also during 2025, with initial access brokers, and in general opportunistic and targeted threat actors, quite active in leveraging software flaws to break into organizations.
     

CVEs Targeting Remote Access Technologies in 2025

7 de Outubro de 2025, 05:18
The exploitation of vulnerabilities targeting remote access technologies to gain initial access is continuing relentlessly also during 2025, with initial access brokers, and in general opportunistic and targeted threat actors, quite active in leveraging software flaws to break into organizations.
❌
❌