Hackers have launched more than 240,000 exploit attempts against a WordPress Core vulnerability that can allow attackers to run malicious code without logging in. According to the supplied Wordfence report, attacks began on October 28, 2026, the same day WordPress released a security update addressing the flaw.
Tracked as CVE-2026-119977, the vulnerability carries a high severity CVSS score of 8.1. It affects unpatched WordPress branches from 4.7 through 7.1.3. Researcher Umut Bayram reported
Hackers have launched more than 240,000 exploit attempts against a WordPress Core vulnerability that can allow attackers to run malicious code without logging in. According to the supplied Wordfence report, attacks began on October 28, 2026, the same day WordPress released a security update addressing the flaw.
Tracked as CVE-2026-119977, the vulnerability carries a high severity CVSS score of 8.1. It affects unpatched WordPress branches from 4.7 through 7.1.3. Researcher Umut Bayram reported the weakness, which involves predictable, publicly accessible folders created during full WordPress Core upgrades.
WordPress addressed the issue in its October 28 security release, alongside several other security fixes. Older branches also received backported patches. Cybersecuritynews.com’s earlier coverage of WordPress 7.1.4 security fixes explained how the update changes temporary folder handling to reduce exposure during upgrades.
240,000 WordPress Exploit Attempts
During a full upgrade, WordPress extracts installation files into a temporary folder beneath /wp-content/upgrade/. On vulnerable installations, predictable folder names can let attackers find this separate installer through a web request while the update remains in progress. No existing WordPress account or user interaction is required.
The attack depends on a race condition, meaning the attacker must reach those files at the right moment. The temporary installer must remain accessible long enough to complete the attack before cleanup removes it. This timing requirement makes successful exploitation difficult, even when attackers repeatedly probe known paths.
The official WordPress release announcement confirms that the upgrade weakness can lead to remote code execution. The CVE record classifies it as a time-of-check, time-of-use race condition, with high potential impact on data confidentiality, integrity, and availability.
According to the supplied Wordfence analysis, attackers reaching the exposed installer could complete a staged installation, create an administrator account, and upload malicious PHP code. That access could support backdoors, content changes, or data theft. Observed requests targeted installer files inside predictable upgrade directories.
Wordfence’s supplied figures show attack traffic peaked on October 30, when its firewall blocked more than 74,000 requests. Activity was highest between October 29 and November 1. These figures describe blocked requests, not confirmed infections, successful code execution, or the number of individual websites affected.
Earlier reporting on 60,000 WordPress attack attempts made the same distinction. Repeated automated requests can increase the chance of finding an exposed installer, but request totals alone cannot establish whether attackers completed the required steps or gained lasting access.
Administrators should install WordPress 7.1.4 or the corresponding patched release for their branch. Automatic background updates may have installed the fix, but owners should verify completion. WordPress recommends immediate updating and notes that only its latest release receives active support.
Updating from a vulnerable version still uses its existing upgrade process once. The supplied Wordfence guidance recommends blocking public access to PHP files beneath /wp-content/upgrade/ before updating. Its protection requires Extended Protection mode because staged PHP files run outside normal WordPress loading.
A flaw in ChatGPT let attackers slip past Lockdown Mode, the safety setting meant to stop data leaks. Check Point Research found that a hidden pop-up trick could copy a user’s full chat history, show fake windows, and push malware. In the ChatGPT Classic desktop app, simply chatting was enough to trigger the leak. OpenAI has fixed the bug.
OpenAI launched Lockdown Mode on February 13, 2026, first for business plans. On June 4, it reached personal accounts, where users can turn it on under Set
A flaw in ChatGPT let attackers slip past Lockdown Mode, the safety setting meant to stop data leaks. Check Point Research found that a hidden pop-up trick could copy a user’s full chat history, show fake windows, and push malware. In the ChatGPT Classic desktop app, simply chatting was enough to trigger the leak. OpenAI has fixed the bug.
OpenAI launched Lockdown Mode on February 13, 2026, first for business plans. On June 4, it reached personal accounts, where users can turn it on under Settings > Security. The setting limits web browsing to cached pages and turns off live web access, image support in replies, Deep Research, Agent Mode, Canvas networking, live connectors, and file downloads.
OpenAI says it is built for high-risk users, such as executives and security teams, and is not needed by most people. Our earlier story on the ChatGPT Lockdown Mode release covers the basics.
The goal is to stop prompt injection, where hidden text tricks the AI into following an attacker’s orders. A common trick is to make the AI load a link like attacker.example/collect?data= followed by private details. The data then shows up in the attacker’s server logs and the chat looks normal.
In February 2026, OpenAI added an HTML preview to ChatGPT code blocks, so users can view a page right in the chat. That page runs inside two nested iframes, which are small boxed-in web pages. The box blocks outside images, scripts, and links, and it asks the user before anything leaves.
Researcher Alexey Bukhteyev spotted a weak point. The boxes allowed popups through two settings, allow-popups and allow-popups-to-escape-sandbox. ChatGPT guarded popups by swapping out the window.open function. A page could skip that guard by adding one more iframe and calling that iframe’s own window.open.
The popup then opened with no prompt, even in Lockdown Mode. Since the second setting was on, code in the popup ran outside the box.
The first risk was fake update windows. The popup kept the ChatGPT icon, while the attacker chose the title. That made a malware download look like a real app update. In a browser, downloads are not blocked, so a shared chat link was enough, and the victim did not even need an account. In the desktop app, the user still had to click the download link.
The second risk was silent data theft. In ChatGPT Classic, built on Electron, window.open worked without any user click. A malicious prompt, a malicious custom GPT, or a shared chat could then send the whole conversation, and uploaded files, to the attacker’s server.
The third risk was stolen logins. The team also reloaded the main ChatGPT window and signed the user out. A fake login page could then capture the password when the user signed back in.
Check Point reported the problem to OpenAI. On September 18, 2026, OpenAI said it removed both popup permissions from the outer preview iframe. Check Point retested and confirmed the trick no longer works. Check Point published its report on November 5.
No user action is needed for this specific bug, but a few habits lower the risk of similar ones. Do not click buttons, previews, or “update” prompts inside shared chats. Skip prompts copied from unknown sites and avoid custom GPTs from unknown builders.
Check the address bar or sign-in page before typing a password, especially after an unexpected logout. Keep the desktop app updated, and avoid pasting medical, financial, or work secrets into any chat unless needed.
Even OpenAI says its safeguards reduce risk but give no full guarantee. As AI tools run code and show web content, each new feature adds a new way in. Careful habits remain a necessary layer of protection.
Microsoft’s Windows Paint vulnerability, CVE-2026-83844, could allow an unauthenticated attacker to execute code over a network without user interaction.
The flaw carries a CVSS score of 8.1, placing it in the High severity category rather than Critical. However, confusion over the corrected Paint version has complicated patch checks for Windows administrators.
The vulnerability stems from an out-of-bounds read, a memory error in which software reads beyond its intended boundary.
Micros
Microsoft’s Windows Paint vulnerability, CVE-2026-83844, could allow an unauthenticated attacker to execute code over a network without user interaction.
The flaw carries a CVSS score of 8.1, placing it in the High severity category rather than Critical. However, confusion over the corrected Paint version has complicated patch checks for Windows administrators.
The vulnerability stems from an out-of-bounds read, a memory error in which software reads beyond its intended boundary.
Microsoft published the advisory on October 13, 2026. Its assessment lists a network attack vector, no required privileges, and high attack complexity, meaning successful exploitation depends on conditions that make an attack harder to carry out.
Windows 0-Click Paint RCE Vulnerability
The disclosure formed part of the October update cycle, covered in Cybersecurity News’ Microsoft October Patch Tuesday report. For administrators, the immediate concern is not simply whether an update exists, but whether the corrected application build has actually reached managed devices.
Microsoft initially listed Paint version 11.2605.91.0 as the fixed release. Administrators reported that Microsoft Store continued offering 11.2605.81.0, even after update checks and Store cache resets.
Microsoft’s advisory listed 11.2609.401.0 as the fix, suggesting the earlier version reference may have been incorrect. Microsoft has not confirmed that explanation.
Update availability also appears inconsistent. Some administrators reported difficulty obtaining a corrected build, while one participant in the Reddit discussion said the update had become available through Microsoft Store. These individual reports do not establish a universal rollout status. Claims that availability depends on region also remain unverified.
A crafted image could trigger the flaw, but Microsoft’s quoted guidance describes a crafted network packet sent to an affected service. The Hacker News discussion highlights the missing detail: neither the exposed service nor the complete attack path is identified. Suggestions involving Copilot or other components are speculation.
Administrators should check the installed Paint version rather than trust an “up to date” message alone. Neowin recommends following Microsoft’s current advisory and considering temporary removal where Paint is unnecessary. Restricting untrusted images may reduce general exposure, but it is not a confirmed fix for this specific network attack path.
Cybersecurity News’ separate PNG vulnerability coverage provides related context on image software security. Those flaws are separate from this Paint vulnerability.
Citrix has released security updates for XenServer versions 8.4 and 9 to address a critical vulnerability. This flaw could allow an unauthenticated attacker on the management network to compromise virtualization hosts. The Cloud Software Group published a bulletin (CTX697256) on November 3, 2026, classifying the issue as Critical. The bulletin covers nine CVEs. Citrix XenServer […]
The post Critical Citrix XenServer Flaw Allows Unauthenticated Attackers to Take Control of Virtualization Hosts ap
Citrix has released security updates for XenServer versions 8.4 and 9 to address a critical vulnerability. This flaw could allow an unauthenticated attacker on the management network to compromise virtualization hosts. The Cloud Software Group published a bulletin (CTX697256) on November 3, 2026, classifying the issue as Critical. The bulletin covers nine CVEs. Citrix XenServer […]
Airbyte vulnerability exploited in the wild lets users run code in Connector Builder containers. Upgrade self-managed Airbyte to 2.2.0 now.
Related Posts:
Rails 8.0.5.2 and 8.1.4.1 Fix 21 Security Flaws, Including Critical Active Storage File Write Bug
SnappyMail Remote Code Execution Chain Disclosed With Public PoC Exploit Code
PoC Exploit and Technical Details Published for Puppet Server RCE Flaw CVE-2026-115731 (CVSS 9.4)
The post Airbyte Vulnerability Exploited in the Wild Lets Attackers
A flaw in Zyxel GS1900 switches was already being used by hackers, and the patch meant to fix it did not work. Researchers at Binarly found that a public exploit hit a different bug than the one Zyxel had patched. Zyxel has now confirmed it as a new flaw, tracked as CVE-2026-107441.
Zyxel published its fix for CVE-2026-7273 on June 16, 2026. After GreyNoise reported real attacks in September, Binarly tested all ten fixed firmware releases on September 28 and found every one still open. Zyxel
A flaw in Zyxel GS1900 switches was already being used by hackers, and the patch meant to fix it did not work. Researchers at Binarly found that a public exploit hit a different bug than the one Zyxel had patched. Zyxel has now confirmed it as a new flaw, tracked as CVE-2026-107441.
Zyxel published its fix for CVE-2026-7273 on June 16, 2026. After GreyNoise reported real attacks in September, Binarly tested all ten fixed firmware releases on September 28 and found every one still open. Zyxel confirmed the new bug on October 11, shipped a fix on October 22, and published its advisory on November 3.
The flaw sits in the dispatcher.cgi web program. It carries a 9.8 critical score, and an attacker can run commands as root without logging in. The same weak code also exists in httprestorecfg.cgi and httpupload.cgi.
Zyxel GS1900 Zero-Day Exploited
The switch web page stores request parameters in a fixed memory block of 140 slots. Each slot holds 1,024 bytes. The code copies the data first and checks the count afterward. A long value in slot 139 spills over and overwrites the counter itself.
An attacker can set the counter to a negative number and write to memory before the block. This lets them overwrite function pointers and run their own commands. Zyxel’s patch added a count check, but the bad copy still happens before that check runs.
Binarly also says Zyxel described the bug wrongly. The flaw lives in global memory, not on the stack. It also works over normal HTTP from any network that can reach the switch, so Binarly rates it higher than the 8.8 score Zyxel gave.
GreyNoise says one actor hit 996 GS1900 switches in 48 countries around August 17. The actor stole device settings, hashed root passwords, and network details. A total of 564 of those switches still used factory default logins. Italy, the United States, and Taiwan had the most victims.
The exploit was a Python script hidden with PyArmor. It pulled a collector script from the attacker’s server using TFTP, then copied the stolen data to a web-readable folder. GreyNoise ties the actor to the Gitea campaign that Acronis called Red Heron, based on shared servers and malware.
That campaign used JITTERLY, a Linux backdoor with more than 30 commands. It hides a rootkit called SIXZUT inside itself, which can conceal files, processes, and network links. Binarly found its samples while checking this server for Binarly Transparency Platform detections.
CISA added CVE-2026-7273 to its Known Exploited Vulnerabilities list on September 21. Our earlier report on the CISA warning for Zyxel GS1900 switches covers that step. Binarly now says either Zyxel’s first patch was wrong, or the attacks hit a different bug than CISA named. Either way, the flaw in Binarly’s advisory is present in the ten releases sold as fixes.
Update every GS1900 switch to the October 22 fix or newer from Zyxel. Take web management pages off the internet and limit them to trusted admin networks. Change all default passwords right away.
CISA also tells teams to check devices for odd admin activity, changed settings, and strange web requests. Because attackers took hashed root credentials, treat any exposed switch as possibly stolen and rotate its passwords.
Google has released its November 2026 Android security update, addressing more than 200 vulnerabilities across the operating system, kernel, and hardware components.
Published on November 2, the bulletin includes critical remote code execution flaws that require no user interaction. Devices with security patch level 2026-11-05 or later receive all applicable fixes.
The most serious Framework issue, CVE-2026-58868, could allow remote code execution without additional execution privileges. G
Google has released its November 2026 Android security update, addressing more than 200 vulnerabilities across the operating system, kernel, and hardware components.
Published on November 2, the bulletin includes critical remote code execution flaws that require no user interaction. Devices with security patch level 2026-11-05 or later receive all applicable fixes.
The most serious Framework issue, CVE-2026-58868, could allow remote code execution without additional execution privileges. Google lists fixes for Android 14, 15, 16, 16 QPR2, and 17. The lack of required user interaction makes this a zero-click threat, removing the need to persuade someone to open malicious content.
Two other critical remote code execution vulnerabilities, CVE-2026-58876 and CVE-2026-58936, affect the System component across those same Android releases.
Google describes the most severe System issue as requiring neither additional privileges nor user interaction. However, the bulletin does not provide enough technical detail to establish the precise delivery method for each flaw.
These findings follow earlier Android updates addressing remote attack risks, including the September 2026 Android security update. The November bulletin does not state that its newly listed flaws are being exploited. A zero-click vulnerability describes the interaction required for an attack, not proof that attackers have already used it against users.
The update also covers high-severity information disclosure, privilege escalation, and denial-of-service bugs. Android runtime flaw CVE-2026-58988 could expose information locally without additional execution privileges or user interaction.
Other Framework and System entries could allow attackers to gain greater access, expose protected data, or interrupt services, depending on the specific vulnerability.
Android 0-Click Remote Code Execution Flaws
According to Google’s November Android Security Bulletin, the kernel fixes include critical issues affecting Bluetooth, Human Interface Device support, and protected Kernel-based Virtual Machine components.
Google says the most severe kernel vulnerability could enable remote privilege escalation without additional privileges or user interaction, making these fixes important alongside the platform patches.
Hardware coverage extends to Arm, Imagination Technologies, MediaTek, Unisoc, and Qualcomm components. MediaTek’s entries include eight critical modem vulnerabilities, while Qualcomm’s closed-source section contains another critical issue. These findings do not mean every Android phone contains every affected component. Exposure depends on the device’s hardware, software version, and the fixes supplied by its manufacturer.
The bulletin separates fixes into November 1 and November 5 patch levels. The earlier level covers the listed platform issues, while November 5 includes all applicable fixes from both groups and previous bulletins.
Cybersecurity News’ Android security patch guide explains why checking the patch date matters more than simply checking the Android version.
Users should install available manufacturer updates and check Google Play system updates separately. Google lists several affected Mainline components, including Media Codecs, MediaProvider, Telephonycore, and WiFi. Google’s update guidance explains how Pixel owners can check for software updates. Availability varies by device and carrier, so publication does not guarantee immediate delivery to every supported phone.
Google Play Protect remains useful, particularly for detecting harmful apps, but it does not replace operating system patches. Google’s severity ratings also assume platform protections are disabled or successfully bypassed, rather than guaranteeing exploitation on every device. For administrators, the practical priority is confirming supported devices receive the complete applicable November security update.
Attackers needed less than two days to start going after a freshly patched WordPress vulnerability. The flaw sits in WordPress core itself, and it can let an attacker run code on a website while that site is installing an update.
WordPress shipped version 7.1.4 on October 28, 2026, to close the hole. Within 48 hours of that release, exploitation attempts were already underway. Security firm Wordfence said it blocked 62,969 attacks aimed at this vulnerability in WordPress over a single 24-hou
Attackers needed less than two days to start going after a freshly patched WordPress vulnerability. The flaw sits in WordPress core itself, and it can let an attacker run code on a website while that site is installing an update.WordPress shipped version 7.1.4 on October 28, 2026, to close the hole. Within 48 hours of that release, exploitation attempts were already underway. Security firm Wordfence said it blocked 62,969 attacks aimed at this vulnerability in WordPress over a single 24-hour period.Anyone running WordPress for a business, a nonprofit, or a healthcare facility is being urged to update right away.
What WordPress 7.1.4 Fixes Beyond the WordPress Vulnerability
Version 7.1.4, released on October 28, is mainly a security release. Alongside the critical code execution fix, it patches several stored cross-site scripting (XSS) flaws, a denial-of-service issue, and two separate information leaks.The update also refreshes WordPress's bundled root certificates after eMudhra revoked its certificates. Of everything in the release, the code execution bug is the one attackers zeroed in on.Aaron Jorbin, who wrote the release announcement, told users to “update your sites without delay.”A GitHub security advisory published the next day described the issue as a timing weakness in the update system. If an unauthorized user moves quickly enough while an upgrade is running, they may be able to execute their own code on the server. No CVE number has been assigned to it so far.
How the Vulnerability in WordPress Works
When WordPress performs a full-package core update, it first extracts the new files into a dedicated directory inside the upgrade folder. According to the advisory, that directory had a predictable name and was reachable from the public web.That combination is the problem. An attacker who requests the right file at the right moment, before WordPress finishes cleaning up, could trick the server into running arbitrary PHP code.Pulling this off is not trivial. The attacker needs four conditions to line up: a full-package update in progress, web access to the temporary folder, a path they can guess, and a short window before the files are deleted. Under controlled conditions, that window may last only a few seconds.
Which Sites the WordPress Vulnerability Affects
The advisory lists every WordPress release from 4.7 through 7.1.3 as vulnerable. It also names the fixed version for each branch, including 7.0.8, 6.9.11, 6.8.12 and 5.9.20.The WordPress project said it backported the patch to all branches still receiving security maintenance, reaching as far back as 4.7. It also stressed that only the newest version is actively supported.Not every site can be taken over through this bug. The risk rises sharply, however, if an attacker hits a site while it is running a full-package update.Smaller websites face extra exposure. Many sit on shared servers with default settings, which makes them attractive targets for cybercriminals.
How Attackers Are Targeting the Vulnerability in WordPress
Wordfence traced the root cause to full-package upgrades repeatedly using web-accessible paths that are easy to guess. Alex Thomas, a threat analyst at Wordfence, said attackers quickly understood the race condition and turned their attention to it.Two of the biggest attack sources reportedly kept polling small groups of websites for roughly 14.5 hours. Other sources tried out different folder names and version names.The pattern looks like large-scale automated guessing rather than attacks on chosen victims. So far, no confirmed reports have put a number on how many sites have actually been compromised.
How Serious Is This WordPress Vulnerability?
Sources disagree on how severe the flaw is. The Hacker News gave it a CVSS score of 8.1, which falls in the high range. The GitHub advisory, by contrast, rates it as low severity.That gap most likely comes down to how hard the bug is to exploit successfully. Even so, the sheer volume of attack attempts and the simplicity of the fix make it sensible to treat this as a serious threat.
What Comes Next for This Vulnerability in WordPress
The probing is unlikely to stop soon. Once a vulnerability is patched, the fix itself becomes a detailed roadmap for anyone hunting sites that have not been updated.The WordPress project says backports to older branches are still in progress. The next major release, WordPress 7.2, is scheduled for December 8.The advisory credits researcher Umut Bayram with discovering the flaw and reporting it responsibly. There is currently no alternative workaround, so applying the patch is the only fix available.
Google released its November 2026 Android Security Bulletin, which addresses critical vulnerabilities that could allow remote code execution without user interaction or additional execution privileges. Published on November 2, the bulletin highlights a framework vulnerability as the most severe issue and also documents other critical remote code execution flaws in Android’s system components. According to […]
The post Google Patches Critical Android RCE Flaws That Let Attackers Execute Code With
Google released its November 2026 Android Security Bulletin, which addresses critical vulnerabilities that could allow remote code execution without user interaction or additional execution privileges. Published on November 2, the bulletin highlights a framework vulnerability as the most severe issue and also documents other critical remote code execution flaws in Android’s system components. According to […]
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has included a WordPress Core vulnerability in its Known Exploited Vulnerabilities catalog due to evidence of active exploitation. This vulnerability, identified as CVE-2026-119977, allows unauthenticated attackers to execute server-side code during a specific software upgrade window. CISA added this vulnerability to the catalog on November 3, 2026, […]
The post CISA Warns of Active Attacks Exploiting WordPress Core Code Execution
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has included a WordPress Core vulnerability in its Known Exploited Vulnerabilities catalog due to evidence of active exploitation. This vulnerability, identified as CVE-2026-119977, allows unauthenticated attackers to execute server-side code during a specific software upgrade window. CISA added this vulnerability to the catalog on November 3, 2026, […]
Cloudflare launched Zero Wire, a public vulnerability intelligence hub that helps security teams investigate critical internet threats, assess exploitation evidence, and prioritize remediation efforts. Available through Cloudflare Radar, the service combines technical research, vendor guidance, and network observations into concise briefings. Cloudflare’s launch announcement positions the platform as a practical starting point for organizations facing […]
The post Cloudflare Launches Zero Wire t
Cloudflare launched Zero Wire, a public vulnerability intelligence hub that helps security teams investigate critical internet threats, assess exploitation evidence, and prioritize remediation efforts. Available through Cloudflare Radar, the service combines technical research, vendor guidance, and network observations into concise briefings. Cloudflare’s launch announcement positions the platform as a practical starting point for organizations facing […]
A high-severity TeamViewer client vulnerability allows compromised remote machines to trigger memory corruption and execute arbitrary code on admin devices.
Related Posts:
Ubuntu Kernel Fixes for CVE-2026-98432 (CVSS 9.8) Land in Proposed Pocket
cPGuard Supply Chain Attack Pushes Backdoor Through Update Channel
7 Unpatched phpMyAdmin Vulnerabilities Exposed
The post TeamViewer Client Vulnerability Enables Remote Code Execution appeared first on Daily CyberSecurity.
A high-severity TeamViewer client vulnerability allows compromised remote machines to trigger memory corruption and execute arbitrary code on admin devices.
Ubuntu has published fixes for CVE-2026-98432, a critical Linux kernel flaw in IPv4 TCP connection handling. It carries a CVSS 3.1 score of 9.8 and can lead to remote code execution. The fixes for Ubuntu 22.04 LTS and newer are in the -proposed pocket, so they are not yet in the default updates channel. Critical […]
The post Ubuntu Releases Security Fixes for Critical Linux Kernel Vulnerability Allowing Remote Code Execution appeared first on GBHackers Security | #1 Globally Trusted Cyber Securi
Ubuntu has published fixes for CVE-2026-98432, a critical Linux kernel flaw in IPv4 TCP connection handling. It carries a CVSS 3.1 score of 9.8 and can lead to remote code execution. The fixes for Ubuntu 22.04 LTS and newer are in the -proposed pocket, so they are not yet in the default updates channel. Critical […]
Attackers exploited the critical StyleSmuggler vulnerability in Magento and Adobe Commerce to deploy PSK Agent, a remote access trojan enabling command execution, traffic proxying, and persistent server access. The campaign ran September 9–13, 2026, targeting stores across Western Europe, North America, and Asia-Pacific. Imperva’s earlier analysis reports a CVSS score of 10.0 and exploitation preceding […]
The post Hackers Exploit Critical Magento StyleSmuggler Vulnerability to Deploy PSK Agent
Attackers exploited the critical StyleSmuggler vulnerability in Magento and Adobe Commerce to deploy PSK Agent, a remote access trojan enabling command execution, traffic proxying, and persistent server access. The campaign ran September 9–13, 2026, targeting stores across Western Europe, North America, and Asia-Pacific. Imperva’s earlier analysis reports a CVSS score of 10.0 and exploitation preceding […]
In this article
Classifying the vulnerability landscapeVulnerabilities exploited in the wildWhere defenders should focusPatching is slow, while exploitation is fastImpact, exposure and where to focusNext in lineHow Microsoft Security helps defenders actReferencesLearn More
The vulnerability landscape continues to expand. From 1999 through September 2026, approximately 383,000 software vulnerabilities had been disclosed across platforms and technologies, yet
The vulnerability landscape continues to expand. From 1999 through September 2026, approximately 383,000 software vulnerabilities had been disclosed across platforms and technologies, yet only about 2,000 CVEs (roughly 0.5%) have been linked to real-world exploitation.
Those vulnerabilities follow clear patterns. Threat actors disproportionately target flaws that enable system takeover, particularly remote code execution, privilege escalation, and authentication bypass. AI-assisted vulnerability discovery and exploit development could further shorten the window defenders have to respond.
Patching remains essential, but remediation can take weeks or months on critical systems, and some legacy or unsupported systems cannot be patched. Defenders therefore need to concentrate protection where it can have the greatest impact, considering both the likelihood of exploitation and the potential blast radius of a successful attack.
Classifying the vulnerability landscape
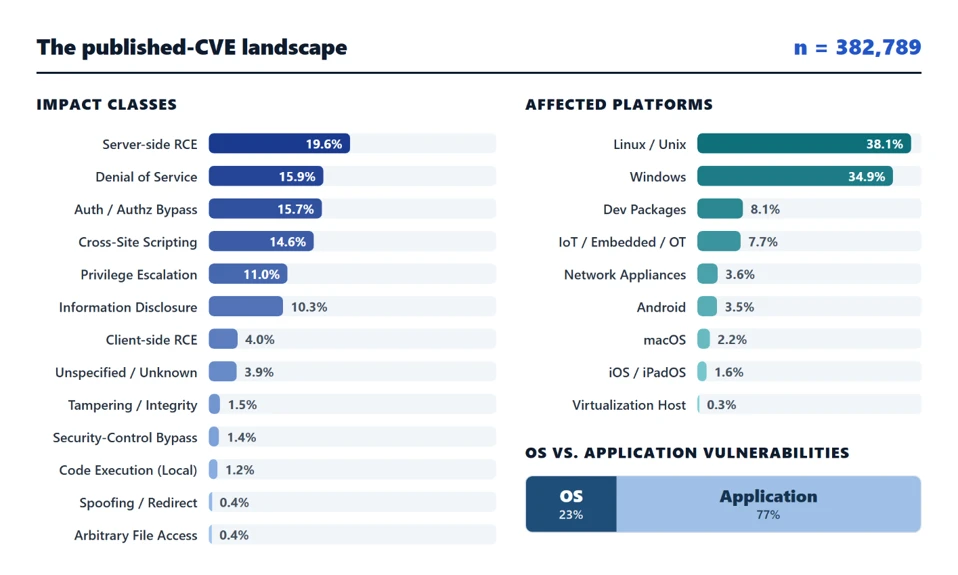
To make this large vulnerability population actionable, we analyzed each CVE across two dimensions: impact class and affected platform.
Impact class captures the outcome a threat actor could achieve by exploiting a vulnerability. Each CVE is assigned to the most consequential impact it directly enables. For example, when a vulnerability can bypass authentication and directly enable remote code execution (RCE), we classify it as RCE. This approach helps distinguish the underlying type of vulnerability from the security impact an attacker could achieve.
Server-side RCE: Remote code execution on a network-exposed service without user interaction.
Client-side RCE: Remote code execution that requires a user to open or run malicious content.
Local code execution: Code or command execution requiring local access or an existing foothold.
Local privilege escalation: Elevation from lower-level access to SYSTEM or root privileges.
Authentication or authorization bypass: Circumvention of authentication or access controls.
Security-control bypass: Circumvention of protections such as sandboxing, secure boot, or SmartScreen.
Information disclosure: Exposure of sensitive data or secrets.
Tampering or integrity: Unauthorized modification of data or system state.
Denial of service: Disruption of system or service availability.
Cross-site scripting (XSS): Script execution within a victim’s browser context.
Arbitrary file access: Unauthorized access to or placement of files.
Spoofing or redirect: Spoofing, redirection, or other forms of UI deception.
We also classified vulnerabilities by the platforms they affect, including Windows, Linux/Unix, mobile, network appliances, IoT/OT, virtualization hosts, and developer packages. A CVE can span multiple platforms. Developer packages are treated as a separate category because they are often cross-platform and represent a significant share of the overall vulnerability population.
Most CVEs in the analysis affect application code, including servers, web applications, browsers, productivity software, libraries, and firmware tooling, while a smaller share affects OS and system code such as kernels, drivers, and firmware.
This analysis covers CVEs published through September 2026 using Microsoft’s catalog of tracked vulnerabilities. Each CVE is counted once in the impact analysis and across each relevant platform in the platform analysis.
Figure 1 – The full published-CVE population as of September 2026, broken down by impact class and affected platform, and an OS vs. application split. Breadth dominates – many impact classes spread across many platforms, with about 77% of CVEs in application code and 23% in OS/system code.
Vulnerabilities exploited in the wild
The subset of vulnerabilities exploited in the wild is much smaller than the overall CVE population, and looks very different from it. Fewer than 1 in 200 published CVEs are ever used in a real attack, and those that do get used are overwhelmingly concentrated in the takeover classes that maximize threat actor impact and exposure.
The difference becomes clear when we look at impact. Exploitation is heavily concentrated in vulnerabilities that give attackers greater control over a system. Server-side RCE rises from 20% of published CVEs to 37% of exploited CVEs, local privilege escalation from 11% to 18%, and client-side RCE from 4% to 13%. By comparison, XSS falls from 15% to 4% and denial of service from 16% to 7%. OS vulnerabilities show a similar shift, increasing from 23% of the overall CVE population to 41% of exploited vulnerabilities.
These patterns are consistent with threat actors favoring vulnerabilities that can provide meaningful access and control. Remote code execution and privilege escalation can create footholds that support subsequent stages of an attack, while vulnerabilities that primarily cause a crash or limited script execution may offer less utility for broader compromise.
Importantly, a vulnerability’s stated classification does not always reflect what an attacker can reliably achieve in practice. For example, some vulnerabilities described as enabling RCE may ultimately result only in denial of service under real-world conditions. Understanding the demonstrated impact and exploitability of a vulnerability is therefore critical to effective prioritization.
Figure 2 – The 2,056 exploited-in-the-wild CVEs distribution, compared against the full published population: ghost lines mark each class and platform’s share of all ~380K published CVEs, and badges show the shift in percentage points. Takeover classes and OS code rise, while high-volume XSS and DoS fall.
Where defenders should focus
Patching is slow, while exploitation is fast
Patching is slow, and far slower on critical systems than others. Across platforms, servers are the critical assets and the slowest to patch. Microsoft Security Exposure Management data from 2026 shows that the median vulnerability is patched in about two weeks on Windows workstations but in more than a month on Windows Servers. It stretches to 10+ weeks on Linux Servers and for applications running on MacOS, and beyond a year on network appliances. That gap is the threat actor’s window, widest on the critical systems that stay exposed the longest.
Exploitation runs on the opposite clock: the most impactful vulnerabilities are weaponized in days, increasingly on or before disclosure. According to VulnCheck, 29% of the exploits in 2025 were launched within 1 day of CVE publication. According to CISA, the mean time from CVE publication to CISA KEV catalog fell from 89 days for CVEs that were published in 2024 to 57 days for CVEs that were published in 2025. 2026 CVE publications up to September already have that number dropping to 20 days, with a median of only 3 days since publication. Industry research suggests that advances in AI are a significant factor in the time reduction required to develop exploits, further increasing pressure on defenders to respond quickly.
Impact, exposure and where to focus
Two things determine a vulnerability’s value to a threat actor: impact and exposure. Impact is what successful exploitation provides, such as remote code execution or privilege escalation. Exposure is an asset’s position in the environment and the opportunities it creates for further compromise. An asset’s exposure is shaped by the identities, privileges, and connections available from it.
Servers often use service accounts, application identities, or cloud-managed identities with permissions beyond their operational needs. Compromising such a system can provide access to additional resources, sensitive data, administrative privileges, or trusted network paths. Together, impact and exposure determine the blast radius: a vulnerability that enables full control of a highly exposed system can enable widespread on-premises or cloud compromise.
Threat actors do not exploit at random: they go after the vulnerabilities that give the highest impact and exposure: full control of a system and the privileged identities and critical assets it has access to. As defenders, focusing on these vulnerabilities first can deliver the highest return on remediation investment.
Takeover vulnerabilities like remote code execution, authentication bypass and local privilege escalation lead here. They drive the broadest exposure and the largest blast radius, account for 78% of real-world exploited vulnerabilities, and stopping their exploitation interrupts attacks at the earliest stage, before compromise can propagate across the environment.
Next in line
A second slice deserves attention where context makes it severe: denial of service against availability-critical assets is recoverable in general, but can be mission-ending in parts of your environment where uptime is everything; disclosure of credentials or secrets can be minor as an insulated incident, but it feeds the same privileged-identity path mentioned above.
Figure 3 – The three remote-takeover classes analyzed across 1,239 exploited CVEs), each drilled down by affected platform and split into OS vs Application code. Bar length is the CVE count per platform; the dark segment is OS/system, the light segment is application.
How Microsoft Security helps defenders act
Threat actors do not begin with a vulnerability list. They begin by looking for a reachable way in. Microsoft Defender External Attack Surface Management approaches the environment from that same outside-in perspective, continuously discovering internet-facing infrastructure, including previously unknown or unmonitored assets, shadow IT, and third-party dependencies. This gives defenders an opportunity to remove unnecessary exposure before a reachable vulnerability becomes an entry point.
Once the reachable assets are known, the next question is which weaknesses deserve immediate attention. Defenders need a way to prioritize exposure beyond CVSS alone. Microsoft Defender Vulnerability Management addresses this challenge through Exposure Score and prioritized security recommendations.
Prioritization incorporates threat and exploitability signals, breach likelihood, internet exposure, and asset criticality, helping teams focus remediation on vulnerabilities that create the greatest actual exposure.
An initial foothold is only part of the risk. Attack Path Analysis connects assets and threat actor techniques into end-to-end routes from an entry point to a critical asset. Microsoft Security Exposure Management Attack Path Analysis provides a cross-workload view spanning endpoints, cloud, and hybrid environments, using vulnerability context from MDVM, endpoint data from Defender for Endpoint, and cloud asset data from Defender for Cloud. Within cloud environments, Defender CSPM Attack Path Analysis adds detailed context about internet exposure, vulnerabilities, network connections, identities, and permissions across Azure, AWS, and Google Cloud.
Together, these experiences show how an exposed workload could become a path through a privileged identity to sensitive data or another critical resource, helping defenders identify where to break the path before the initial compromise expands.
Patching remains essential, but it is not the only defensive action available. Microsoft Security helps defenders discover the doors threat actors can see, prioritize the weaknesses they are most likely to exploit, understand where a compromise could lead, and identify opportunities to break attack paths before compromise spreads to critical assets.
To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.
Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.
Brotli vulnerability CVE-2026-111497 affected products list: fixes for Node.js, .NET, Envoy, PAN-OS and distros, plus VMware and others still unpatched.
Related Posts:
Critical MediaTek Vulnerabilities Patched in Chipsets
Public PoC Exploit Disclosed for Linux Kernel Bonding Vulnerability
Critical FreePBX Vulnerabilities Patched in User Manager
The post Brotli Vulnerability Affected Products: Vendor Patch Status List appeared first on Daily CyberSecurity.
Brotli vulnerability CVE-2026-111497 affected products list: fixes for Node.js, .NET, Envoy, PAN-OS and distros, plus VMware and others still unpatched.
A public proof-of-concept exploit for CVE-2023-21768 shows how attackers with local access can gain SYSTEM privileges through the Windows Ancillary Function Driver for WinSock.
Researchers Valentina Palmiotti, known as chompie, and Ruben Boonen published the code. Their complete exploit targets vulnerable Windows 11 22H2 systems.
The release concerns a vulnerability patched in January 2023, not a newly disclosed Windows flaw. IBM published the researchers’ technical analysis on March 21, 2
A public proof-of-concept exploit for CVE-2023-21768 shows how attackers with local access can gain SYSTEM privileges through the Windows Ancillary Function Driver for WinSock.
Researchers Valentina Palmiotti, known as chompie, and Ruben Boonen published the code. Their complete exploit targets vulnerable Windows 11 22H2 systems.
The release concerns a vulnerability patched in January 2023, not a newly disclosed Windows flaw. IBM published the researchers’ technical analysis on March 21, 2023.
The vulnerability carries a CVSS score of 7.8 and requires low-level local privileges, with no user interaction. It does not provide a direct route into a computer over the internet. The flaw sits in afd.sys, a Windows kernel driver that handles requests from the WinSock networking interface.
According to IBM’s technical analysis, the researchers compared driver versions from December 2022 and January 2023 to understand Microsoft’s fix. Only one function, AfdNotifyRemoveIoCompletion, appeared to have changed, helping them narrow their investigation.
The older code failed to check a memory pointer supplied from a user application. That missing check let a local attacker write to kernel memory, where Windows stores sensitive system data.
Microsoft’s updated code added validation to ensure that pointers from user mode reference suitable user-space memory rather than protected kernel addresses.
POC for Windows WinSock Ancillary Vulnerability
The researchers said they diagnosed, reproduced, and turned the flaw into a working exploit in about one day, despite having no previous experience with this driver.
Their findings show how comparing patched and unpatched software can reveal enough detail to build an attack quickly.
The public GitHub repository describes the code as a demonstration. Its complete privilege escalation chain works on vulnerable Windows 11 22H2 installations, while the underlying memory-write capability works across vulnerable systems.
These are separate claims, and the repository does not promise full exploit compatibility with every affected Windows version. To move from a limited memory write to broader control, the exploit changes Windows I/O ring objects. These objects support queued input and output work.
The technique builds on research by Yarden Shafir and enables kernel memory reads and writes. The exploit then replaces a target process’s security token with one carrying SYSTEM privileges.
IBM also reported that 360 IceSword Lab found a different exploit in the wild in January 2023. That sample used the ProcessSocketNotifications interface rather than the researchers’ direct driver approach. This report does not establish that attackers used the published GitHub code.
Administrators should verify that affected devices received Microsoft’s fix or later applicable updates. IBM’s demonstration also worked without being blocked by HVCI, showing why that protection should not replace patching.

 Entrar