Discover how the North Korean WaterPlum cyber actor group uses fake job interviews to steal crypto and infiltrate networks globally.
Related Posts:
SideCopy APT Campaign Targets Academic Institutions
Microsoft Disrupts EvilTokens Cybercrime Platform
Operation RapidRust APT36 Campaign Targets Governments
The post The WaterPlum Cyber Actor Group Targets Global IT Professionals appeared first on Daily CyberSecurity.
North Korea-linked WaterPlum runs the Contagious Interview campaign, infecting over 30,000 devices using a fake job interview.
On September 18, Japan’s National Police Agency, the FBI, the US Department of Defense’s Cyber Crime Center, and intelligence agencies from Australia and Germany published a joint advisory about a group called WaterPlum, better known as Contagious Interview. The name says it all. The job interview is the infection vector.
The numbers in the advisory are hard to sh
North Korea-linked WaterPlum runs the Contagious Interview campaign, infecting over 30,000 devices using a fake job interview.
On September 18, Japan’s National Police Agency, the FBI, the US Department of Defense’s Cyber Crime Center, and intelligence agencies from Australia and Germany published a joint advisory about a group called WaterPlum, better known as Contagious Interview. The name says it all. The job interview is the infection vector.
The numbers in the advisory are hard to shrug off. At least 30,000 devices infected across more than 100 countries, funds or credentials stolen from over 7,000 cryptocurrency wallets, and a total of 1.7 billion yen, roughly $10.71 million, funneled back to North Korea. The victims are almost always the same type: freelance developers and specialists in blockchain and Web3 work.
Japan’s NPA and the FBI assess that both WaterPlum operators and some North Korean IT workers report to the same place, the 313 General Bureau of the Munitions Industry Department, under the Workers’ Party’s Central Committee. That’s not a loose affiliation. It’s an org chart.
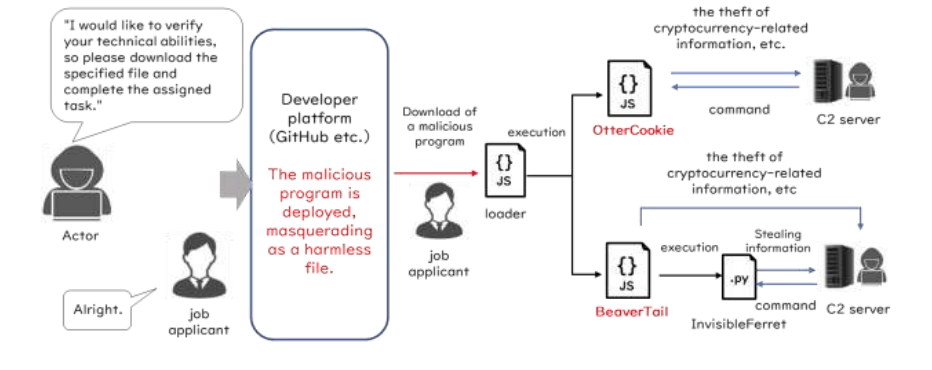
The trap itself is almost embarrassingly simple. WaterPlum actors pose as recruiters or hiring managers, often impersonating real AI, crypto, or NFT companies, and reach out on social media, job boards, and freelance platforms. Candidates get invited to a technical interview, then told to download a file to complete a coding test or fix a supposed bug on the video call.
“WaterPlum actors pose as prospective employers to target software developers and IT professionals worldwide under the pretext of attractive job opportunities. They often impersonate legitimate Artificial Intelligence (AI), cryptocurrency, or Non-Fungible Token (NFT) companies and have also used recruiting services.” reads the joint advisory. “WaterPlum actors have infected at least 30,000 devices in more than 100 countries and exfiltrated funds or account credentials from over 7,000 cryptocurrency wallets. WaterPlum actors have transferred 1.7 billion Japanese yen (JPY) (equivalent to 10.71 million USD) of cryptocurrency assets to the Democratic People’s Republic of Korea (DPRK).”
That file is never what it claims to be. The advisory names five malware families riding inside these downloads, BeaverTail, InvisibleFerret, OtterCookie, OtterCandy, and StoatWaffle, each doing its own piece of the job: one steals browser credentials, another opens a backdoor, another sets up a remote access trojan to move deeper into the machine. Once inside, the goal is straightforward: drain the wallet, then look for whatever else might be worth stealing.
What happens next goes beyond one stolen wallet. The report notes that a successful infection can give WaterPlum a way into the victim’s employer, opening the door to espionage, stolen source code, and further movement inside a company’s systems. Stolen ID photos get reused too, letting North Korean IT workers impersonate the victim to land more paying contracts elsewhere.
That last part connects to a separate but related scheme covered in the same advisory: North Korean IT workers using so-called “laptop farms.” These are physical locations, often just someone’s house, where a local facilitator plugs in company-issued laptops and lets a North Korean worker operate them remotely over VPN. The worker gets a Western-looking identity and a legitimate-sounding job. The facilitator gets a cut.
“Beyond immediate credential theft, successful infections provide WaterPlum actors opportunities to infiltrate organizations employing targeted developers, enabling espionage, intellectual property theft, and additional lateral movement in corporate environments. Stolen ID images can also be used by North Korean IT workers to impersonate victims and generate foreign currency.” continues the report. “Other sensitive data targeted for exfiltration includes:
Authentication data stored in web browsers (ID, password, etc.);
Cryptocurrency-wallet data (private key, seed phrase, etc.); and
Any files or data of interest to the actors on a PC or in shared folders (ID pictures of driver’s licenses, passports, etc.)”
Here’s a simpler and more natural version, while keeping the same details:
Japan says this is no longer just a theoretical threat. Authorities have already shut down the country’s first known “laptop farm,” run by a local facilitator who had moved several hundred million yen in cryptocurrency out of Japan. In the US, the FBI says it continues to prosecute people who help North Korean IT workers operate this way, across several states and under different charges.
The advisory also describes a case involving a Japanese crypto exchange that spotted one of these applicants in May 2025. His resume listed an unusually wide range of skills across more than a dozen technologies. He claimed to be Malaysian, raised in Finland, and fluent in Malay and Chinese, but struggled with basic English questions that did not fit his claimed background. The company rejected him, avoiding any damage.
Other red flags recruiters have picked up on read like a checklist for a bad Zoom call: the applicant glancing sideways as if reading a script, background voices that shouldn’t be there, video that keeps freezing at convenient moments, a firm preference for getting paid in crypto, sometimes to someone else’s account entirely.
Not every North Korean IT worker sticks to quiet fraud, either. One extorted a client over a payment dispute and leaked the company’s proprietary code online out of spite. Another, hired for basic website maintenance, defaced the site and knocked it offline instead. Petty, but the effect on the client was anything but.
The advisory draws one more thread together: WaterPlum’s cyberattack operators and North Korea’s IT worker network aren’t running in parallel. They’ve been caught using the same IP addresses to access laptop farms, register on freelance platforms, and apply for that same crypto exchange job. Same infrastructure, two revenue streams, one regime cashing the checks.
“The techniques described in this advisory are only examples; actors continuously evolve and refine their methods.” concludes the advisory. “Stay informed by monitoring alerts from domestic and international security agencies and by reviewing reports published by security vendors.”
Japan, the United States, Australia and Germany, today issued a joint cybersecurity advisory formally attributing the long-running "Contagious Interview" campaign to a North Korean state-sponsored group they are calling WaterPlum. The operation has infected more than 30,000 computers in more than 100 countries and stolen about 1.7 billion yen, or some $10.7 million, in cryptocurrency.
The advisory carries the seals of Japan's National Police Agency and National Cybersecurity Office, the FBI and
Japan, the United States, Australia and Germany, today issued a joint cybersecurity advisory formally attributing the long-running "Contagious Interview" campaign to a North Korean state-sponsored group they are calling WaterPlum. The operation has infected more than 30,000 computers in more than 100 countries and stolen about 1.7 billion yen, or some $10.7 million, in cryptocurrency.
The advisory carries the seals of Japan's National Police Agency and National Cybersecurity Office, the FBI and the U.S. Defense Department's Cyber Crime Center, the Australian Signals Directorate's Australian Cyber Security Centre and Germany's BND and BfV intelligence services. It places WaterPlum under the 313 General Bureau of North Korea's Munitions Industry Department, which oversees weapons production — framing the theft as state revenue generation rather than ordinary cybercrime.
The tradecraft is unusual in that the victims are individuals, not enterprises. Operators pose as recruiters for AI, cryptocurrency and NFT companies, approaching developers, web designers and blockchain specialists via social media, job boards and freelance marketplaces.
At the technical-interview stage, the candidate is asked to run a coding assignment or troubleshoot a video-conferencing problem. Either pretext delivers malware, typically via malicious Node Package Manager packages hosted on GitHub or Bitbucket. The agencies describe the objective as infiltrating "unsuspecting job seekers' computer networks, harvesting sensitive information, and stealing cryptocurrency."
Five malware families are named. BeaverTail, a JavaScript infostealer hidden in npm packages; InvisibleFerret, a Python backdoor; OtterCookie, a JavaScript remote access trojan with stealer functions; OtterCandy, which blends OtterCookie with a family called RATatouille; and StoatWaffle, a modular Node.js loader bundling credential harvesting and a RAT.
Together they siphon credentials, clipboard contents, keystrokes, screenshots, wallet keys and seed phrases, identity documents and source code. Japanese police put the most intense phase between December 2025 and July 2026, with roughly 7,000 cryptocurrency wallet cases recorded.
The advisory pairs the campaign with North Korea's remote IT worker scheme, treating it as the same revenue apparatus seen from the employer's side. Operatives use stolen identity documents and virtual private servers to obscure their locations, working from North Korea, China, Russia, Africa and Southeast Asia, while "laptop farms" in facilitators' homes supply plausible in-country IP addresses. Where placements sour, the agencies say the workers have turned to extortion over payment disputes, website defacement and publication of stolen source code. Japanese investigators dismantled one domestic laptop farm and traced several hundred million yen abroad.
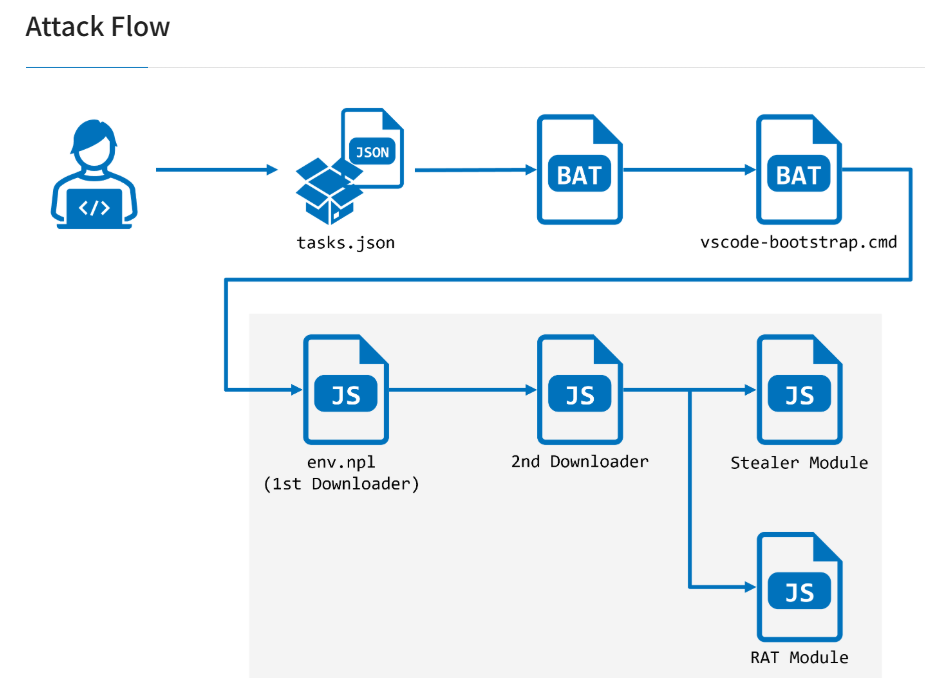
Guidance for practitioners is that run untrusted interview code only in a virtual machine; treat commands containing curl, base64, -enc, mshta or Invoke-WebRequest with suspicion; open unfamiliar projects in Visual Studio Code's Restricted Mode and inspect .vscode/tasks.json first; and after any infection, assume credentials are lost, rotate wallets from a clean device and reinstall the operating system. Employers are told to check applicant IP addresses against claimed locations and to watch for refusal to meet in person, frequent audio and video freezes, or use of face-swapping software.
The compliance exposure is significant. The U.S. State Department issued an alert to companies on North Korean IT workers in July, and the Justice Department has prosecuted facilitators and seized laptop farms. Firms that unknowingly pay a North Korean contractor risk sanctions liability, which is why the advisory pushes contractual controls and identity verification, not detection alone. Japan's Foreign Ministry said it would "strengthen its efforts with the ally and like-minded countries and the private sector."
What to watch: whether the attribution is followed by sanctions designations, how npm and code-hosting platforms respond to package delivery at this scale, and whether the ACSC issues Australia-specific guidance for contractor and Web3 employers.

 Entrar