❌

Visualização normal

Hoje — 8 de Novembro de 2026Stream principal
  • ✇Security Affairs
  • Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa Pierluigi Paganini
    French Bank Crédit Mutuel Arkéa says hackers exploited a service provider to steal up to $133 million using the bank’s own account. French cooperative bank Crédit Mutuel Arkéa was hit by a cyberattack that let attackers make fraudulent transactions of up to $133 million, forcing it to suspend certain systems. Crédit Mutuel Arkéa is a major French cooperative banking and insurance group headquartered in Brest, Brittany, France. The bank says the attacker used its own account to send transa
     

Attackers Exploit Third-Party Provider to Raid French Bank Crédit Mutuel Arkéa

8 de Novembro de 2026, 07:25

French Bank Crédit Mutuel Arkéa says hackers exploited a service provider to steal up to $133 million using the bank’s own account.

French cooperative bank Crédit Mutuel Arkéa was hit by a cyberattack that let attackers make fraudulent transactions of up to $133 million, forcing it to suspend certain systems. Crédit Mutuel Arkéa is a major French cooperative banking and insurance group headquartered in Brest, Brittany, France.

The bank says the attacker used its own account to send transactions to other banking organizations, and that customer assets weren’t affected.

“French lender Credit Mutuel Arkea said on Thursday hackers had stolen around €100 million ($112.61 million) in a cyber heist and it was working to try to recover the money, in a rare case of cybercriminals successfully stealing from a mainstream bank.” Reuters states.

Blockchain researcher ZachXBT first warned of a large unauthorized withdrawal from multiple centralized exchange accounts a day earlier. He said the attacker may have stolen up to 118 million euros ($133 million) and withdrawn it as the USDC and USDT stablecoins.

“Over the past 24 hours the illicit actor has been aggressively swapping USDC for ETH, transferring to instant exchanges (WellWallet, Kyrrex, etc), converting to XMR via Wagyu, and bridging across multiple chains.” ZachXBT wrote.

“While the illicit actor remains unidentified, I can say with a high degree of confidence it is NOT Lazarus Group based on multiple laundering indicators.”

The attacker remains unidentified, but ZachXBT believes it is highly unlikely to be Lazarus Group, based on money-laundering patterns.

According to BleepingComputer, the expert pointed out that the lack of public disclosure allowed attackers to launder $30 million by November 3, potentially preventing EU authorities from freezing the funds. The Paris prosecutor’s cybercrime unit opened an investigation after receiving a complaint from Crédit Mutuel Arkéa, with France’s cybercrime police leading the probe.

Arkéa disclosed the incident on November 4, saying it was contained, customer assets were unaffected and some transfers had been delayed. Attackers reportedly accessed the bank through a service provider’s platform, not Fortuneo, and used Arkéa’s own account to move funds through other banks and convert them into cryptocurrency. The bank also warned customers about increased phishing risks.

“Crédit Mutuel Arkéa announces that it has been the target of an attack that enabled the execution of fraudulent transactions.” reads the notice published by the bank. “Upon detecting this attack, and in accordance with standard procedures, the Group contacted the relevant regulatory and supervisory authorities to inform them of the situation.” “This incident is now closed and fully under control. Operations are gradually resuming this morning, following thorough verification by the Group and its subsidiaries and the implementation of enhanced security measures.”


Crédit Mutuel Arkéa says customer assets were unaffected, although some transfers were delayed. The bank maintains its financial stability, warns of possible phishing attempts and urges customers not to share sensitive information. Its teams are assessing the incident and strengthening security measures, with further updates expected.

Arkéa did not confirm ZachXBT’s reported figure but acknowledged significant losses and said some funds were blocked. The bank ruled out internal human error, described the incident as a sophisticated attack and is working with law enforcement to identify the attackers and establish how the breach occurred.

When the FAQ asked whether 118 million euros had been stolen, Arkéa wouldn’t give a number: We do not confirm this information and can only validate the order of magnitude.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Crédit Mutuel Arkéa)
  • ✇Security Affairs
  • Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches Pierluigi Paganini
    Hunt.io traced ARTEX servers and AI-powered hacking tools used in breaches affecting seven South Korean financial institutions. Between late September and early October 2026, seven South Korean financial institutions had data breached through internet-facing systems. About 66,000 to 67,000 people and around 2,200 corporations were affected, and personal, employment, income and loan data was exposed. Hunt.io dug into the infrastructure behind the campaign, and its findings add a lot to what C
     

Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank Breaches

7 de Novembro de 2026, 16:56

Hunt.io traced ARTEX servers and AI-powered hacking tools used in breaches affecting seven South Korean financial institutions.

Between late September and early October 2026, seven South Korean financial institutions had data breached through internet-facing systems. About 66,000 to 67,000 people and around 2,200 corporations were affected, and personal, employment, income and loan data was exposed. Hunt.io dug into the infrastructure behind the campaign, and its findings add a lot to what CrowdStrike and Genians already published.

CrowdStrike reported on October 7 and Genians Security Center on October 12, and both pointed to ARTEX, an open-source autonomous penetration testing framework developed in China and licensed under AGPL-3.0. CrowdStrike assessed with moderate confidence that a single Chinese-speaking individual motivated by money ran it, and not an established threat group. DeepSeek v4.1 Flash was the main model, with GLM 5.3 and Grok 4.6 as backups, reached partly through a reseller domain, xcai[.]pro.

The public indicators were a server at 38.244.50[.]120, which hosted the ARTEX console, plus a Hong Kong address and nine proxies. Genians said the ARTEX GitHub repository and Docker image were removed on October 11, though forks and mirrors remain.

“CrowdStrike assessed with moderate confidence that the operator was a single Chinese-speaking individual motivated by financial gain rather than an established threat group.” reads the report published by Hunt.io. “The infrastructure reportedly accessed these services in part through the reseller domain xcai[.]pro. Both reports described a two-server configuration, consisting of a Hong Kong-based IP address used as primary infrastructure and 38.244.50[.]120, which hosted the ARTEX console.”

Hunt.io notified the relevant national CERT before publishing, and says the report holds no personal records or credentials.

The company’s own scanning showed 38.244.50[.]120 sits on Cogent’s network in Los Angeles, with 15 open ports. The ARTEX login page, with a Chinese title meaning “autonomous penetration testing console”, appears on ports 443 and 8090. Other services include a Gemini2API admin console and a Tinyproxy server.

Searching its AttackCapture platform for that address, Hunt.io found another open directory at 23.248.226[.]250, a jump server in Hong Kong on AS138415. It held 42 files in 2 subdirectories, 105 MB in all, and the platform had logged warnings on September 5, September 26 and October 5. A file in it names 38.244.50[.]120 as the jump host, and its own comment tells the operator never to paste the credentials into a session. It sat in an open directory.

Three scripts back up the link. They keep reverse SSH tunnels alive, run a local relay, and copy files to the jump host, one tunnel is named grok2api, and the credentials file also holds keys for Zhipu AI’s GLM models, an OpenAI-compatible relay and a proxy service. That explains how several language models ran in one campaign.

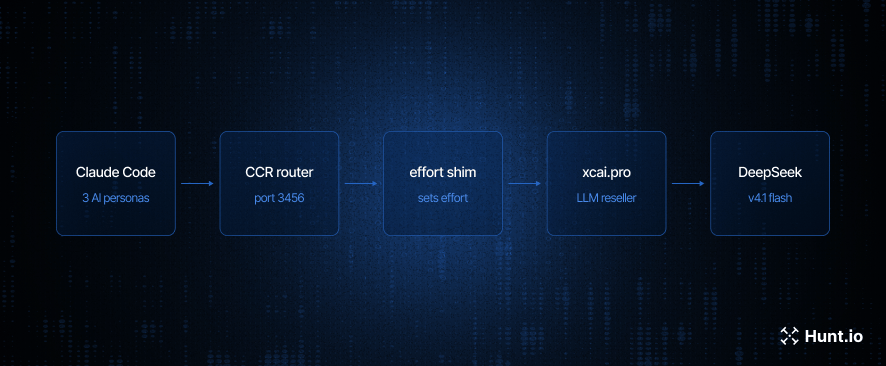
The AI setup is the most striking part. A state file shows the harness is Claude Code itself, version 2.1.221, started 510 times since August 4, but it isn’t talking to Anthropic. A small proxy, ds-models-shim.py, fixes a compatibility problem by faking a model list and sending requests to DeepSeek, and another, xcai-effort-shim.py, adds a reasoning setting because the DeepSeek backend otherwise skips its reasoning step. The route runs from Claude Code through Claude Code Router, an open-source project, to xcai and then to DeepSeek.

“A small local proxy, ds-models-shim.py, addresses a compatibility issue: the official /v1/models endpoint returns a 404 response when queried against a non-Anthropic backend, preventing Claude Code from discovering the available models. The shim intercepts that specific request and returns a locally defined model list containing deepseek-v4-pro and deepseek-flash. All other requests are forwarded to api.deepseek.com/anthropic.” states the report.

The same file counts 19 custom skills, reusable instruction sets for the agent, with 147 recorded uses. They cover code audit, reconnaissance, web injection, WAF bypass testing, authentication testing, Telegram Mini Apps, APK download and decompiling, cloud phone control and payment logic testing. Next to the payment skill sat three self-registered test accounts with tokens for a cash-in deposit API, dated September 12, and a comment calls them an authorized, self-built test. The setup fits testing for insecure direct object reference flaws, a technique CrowdStrike and Genians described against Korean loan and inquiry services.

The directory also held supporting tools. A script queried FOFA, a Chinese asset search engine like Shodan, through a third-party API, and a comment says the primary membership had expired and a backup key was in use. Proxy scripts enumerated a rotating proxy service at 154.201.79[.]246:443, where 79 unique exit IPs showed up among the first 100 identities tested.

A separate directory at 23.248.226[.]250:8001 held a small staged setup for JNDI and LDAP exploitation, retrieved on October 5 at 03:42 UTC. It confirms command execution through a DNS callback, and one script lets web and LDAP traffic share a single port. Hunt.io’s analysis describes the tooling without publishing steps to reproduce it.

Other recovered files include tools aimed at a cryptocurrency exchange’s admin session and withdrawals, Linux privilege escalation exploits, iOS probe source code and Android kernel and firmware utilities. Hunt.io says their connection to the Korean breaches isn’t confirmed.

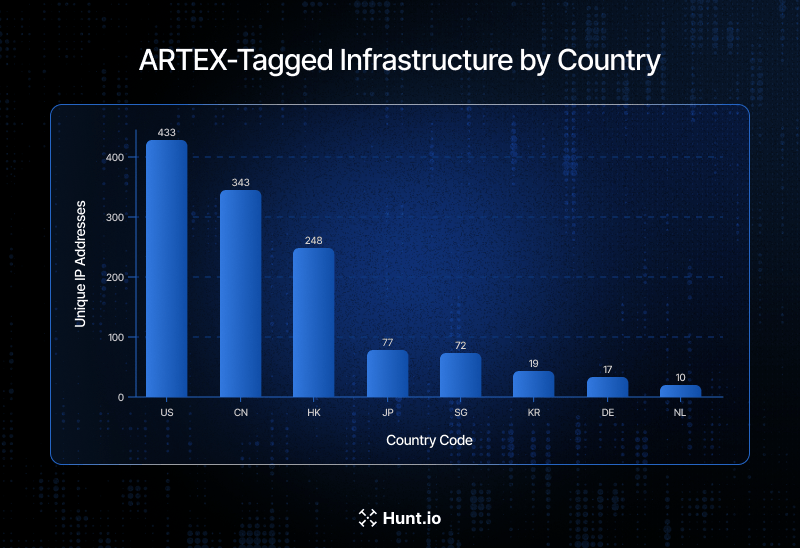
Hunt.io then showed how to hunt ARTEX servers. Searching for an ARTEX certificate issuer returned 19 IP addresses, and searching its malware classification returned 1,303 addresses across 30 countries, led by the United States, China and Hong Kong. Those figures show where addresses are registered, not where the operator sits.

“The result returned 19 distinct IP addresses, including 38.244.50[.]120. This method is precise but limited to hosts that expose a matching certificate. Systems using a different certificate will not appear in these results.” continues the report.

Matching the console’s page title returned about 1,300 IPs, and a looser search found 21 title strings, 19 of them likely ARTEX consoles, in English, Chinese, Korean, Japanese, Russian, Portuguese and Vietnamese.

A malware-name search in AttackCapture gave 280 results with open directories. One at 130.94.31[.]86:18888 in Seoul held two small scripts, and another at 156.251.11[.]39 held an SMB reconnaissance toolkit whose test script writes a file named artex_probe_11876.txt.

More hosts held exploitation kits for DedeCMS and FangCMS, a CAPTCHA bypass suite, a RuoYi and Spring administrative console exploit and CAPTCHA-based login automation. Together they show the framework attracting many operators.

For defenders, the advice is plain. Remove public access and put administration behind VPNs or allowlists, and reset SSH passwords and rotate API keys, proxy credentials and tokens that exposed files may have revealed. Patch internet-facing services, watch for unexpected LDAP and JNDI activity, DNS callbacks and remote script downloads, and store secrets in a managed vault with least-privilege permissions. Also restrict access to model gateways, watch their requests, and enforce compliance rules on managed phones. Hunt.io’s lesson is that an investigation shouldn’t stop at the first list of indicators, because

The company also published indicators of compromise in its analysis.

“The findings highlight risks associated with exposed administrative services, reusable credentials, remote access tunnels, proxy infrastructure, and exploitation tooling.” concludes the report.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, ARTEX)

Hot fridges, a fake nuclear alert and a $6bn heist: are we in the foothills of a hacking epidemic?

As AI exposes flaws in IT systems and geopolitics plays out on the cyber frontline, some experts say the events of recent weeks could soon be a common occurrence

Alex Pearce was doing the morning rounds at his fruit and vegetable wholesale business in London on Monday last week when he noticed something odd.

The defrost light on refrigeration unit 2 was on, and the panel reading was 150C. Unit 4 was the same.

Continue reading...

© Composite: Guardian Design/Getty Images

© Composite: Guardian Design/Getty Images

© Composite: Guardian Design/Getty Images

Ontem — 7 de Novembro de 2026Stream principal

Medical services company settles with 4 states over 2023 hack of sensitive patient records

6 de Novembro de 2026, 16:06
The case, brought by AGs in Connecticut, New Jersey, New York and Michigan, targeted the medical transcription, coding and imaging subsidiaries of the Nevada-based Perry Johnson Companies.

Certificate authority DigiCert reports data breach involving business customer info

6 de Novembro de 2026, 15:56
DigiCert explained that over the summer, an internal business system was "externally accessible when that was not intended," and someone had created an unauthorized account.

FBI agent pleads guilty to stealing $2.4 million in crypto from nation-state hackers

6 de Novembro de 2026, 13:53
Patrick Steven Yaroch, 37, is facing up to 20 years in prison on wire fraud and money laundering charges after admitting to using his position on an FBI investigative squad to steal more than $2.4 million in cryptocurrency to cover his debts.

Antes de ontemStream principal
  • ✇Security Affairs
  • UNM Health Shuts Clinics and Diverts Patients During Security Incident Pierluigi Paganini
    A cybersecurity incident forced UNM Health to divert ambulances, cancel appointments, and pause care while it contained the threat. On Monday, October 26, the University of New Mexico Health System (UNM Health) faced the kind of security incident that healthcare leaders dread: one serious enough to change how patients could receive emergency care. A major hospital network in New Mexico worked urgently on Monday to fix a cybersecurity problem. The issue forced it to send ambulances to oth
     

UNM Health Shuts Clinics and Diverts Patients During Security Incident

5 de Novembro de 2026, 10:48

A cybersecurity incident forced UNM Health to divert ambulances, cancel appointments, and pause care while it contained the threat.

On Monday, October 26, the University of New Mexico Health System (UNM Health) faced the kind of security incident that healthcare leaders dread: one serious enough to change how patients could receive emergency care.

A major hospital network in New Mexico worked urgently on Monday to fix a cybersecurity problem. The issue forced it to send ambulances to other hospitals and left the state without a hospital emergency department able to treat the most serious injuries.

UNM Health operates New Mexico’s only Level 1 trauma center. These centers treat the most serious and complex injuries. Even a temporary closure can put extra pressure on other hospitals.

UNM Health runs New Mexico’s only Level 1 trauma center. That matters because a Level 1 center handles the most complex injuries, and losing even temporary access to it puts pressure on every nearby hospital.

The organization told patients not to come to its main Albuquerque hospital and canceled appointments across more than 30 clinics.

“The University of New Mexico Health System is experiencing a cybersecurity issue at this time. UNM Health officials are actively working to resolve this issue. Currently, all ambulance traffic is being diverted to other hospitals and all appointments at all clinics today have been cancelled. UNM Health patients should not show up to UNM Health facilities on October 26. Emergencies should be handled by 911 and non-emergencies should be delayed until further notice.” reads the update published by the organization on October 26, 2026. “The cybersecurity threat is affecting the entire University of New Mexico Health Sciences Center. “

UNM said its IT security teams identified the threat around 11 a.m. and began containment work. They later said the event affected some end-user devices but did not reach core systems or servers.

Leadership activated an Emergency Operations Center, brought in outside support, and notified state and federal law enforcement. That is the right sequence: isolate first, investigate second, communicate continuously.

From 12:30 to 2:30 p.m., UN Health temporarily stopped accepting new patients while teams protected the network. “System outages also required the suspension of outpatient surgeries and appointments for the remainder of the day.”

This was not an abstract IT problem. Patients arrived for care and were told to reschedule. Staff had to explain, repeatedly, why a hospital visit could not proceed as planned.

UNM also canceled classes at its Health Sciences Center and sent nonessential employees home. Medical, nursing, pharmacy, and population health students lost a day of instruction because the institution had to protect its network.

Other providers stepped in. Presbyterian Healthcare Services and Lovelace Health System coordinated with UNM and took additional patients, which is exactly what a functioning regional healthcare system should do.

UNM Health began restoring its systems on Monday afternoon. By the following day, hospitals, ambulance services and clinics were back to normal.

The incident is still under criminal investigation. Employees reported messages claiming that patient, student and staff data had been stolen, but UNM has not confirmed this. The hospital also warned people to watch out for phishing and fraud attempts by attackers exploiting the incident.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, UNM Health)

  • ✇Security Affairs
  • U.S. Charges Canadian Man in Alleged Hack of University Supercomputers Pierluigi Paganini
    A Canadian man was extradited to the U.S. to face charges over hacking universities and hijacking their computers to mine cryptocurrency. A Canadian man, Ryan James Roach (35), has been extradicted to the United States to face charges tied to a hacking operation that targeted universities and other schools. Roach was extradited on October 28 and now faces federal charges alongside Mathiew James Stubbings, 41, of Ontario. The indictment alleges that, from June 2016 to December 2019, the tw
     

U.S. Charges Canadian Man in Alleged Hack of University Supercomputers

5 de Novembro de 2026, 03:20

A Canadian man was extradited to the U.S. to face charges over hacking universities and hijacking their computers to mine cryptocurrency.

A Canadian man, Ryan James Roach (35), has been extradicted to the United States to face charges tied to a hacking operation that targeted universities and other schools. Roach was extradited on October 28 and now faces federal charges alongside Mathiew James Stubbings, 41, of Ontario.

The indictment alleges that, from June 2016 to December 2019, the two men hacked computers, stole login details, and used victims’ machines to mine cryptocurrency for themselves.

“They used virtual private servers in multiple countries, which were registered under false names. These servers transmitted malware and mining software to victim computers and stored stolen login credentials.” DoJ states. “Victims of the scheme included educational institutions in New York, Tennessee, North Carolina, and Massachusetts. Some of the computers damaged by the defendants were located at an institution of higher learning in the Western District of New York.”

The targets were not random home PCs. Prosecutors say the pair went after U.S. schools with supercomputers, including institutions in New York, Tennessee, North Carolina and Massachusetts. Some affected computers belonged to a higher-education institution in western New York.

“To carry out the scheme, Roach and Stubbings surreptitiously accessed victim computers without authorization, deployed malware to gain control, stole victim login credentials, exfiltrated the data to servers that they controlled, and forcing victim computers to use their processing power to mine cryptocurrency for the financial benefit of the defendants.” DoJ continues.

That is a lot of effort to turn someone else’s research hardware into a personal crypto rig.

The alleged method was also more involved than a single phishing email. The indictment says they looked for weaknesses in victims’ networks, used servers and compromised machines from one victim to hide their tracks, and then moved through the network once inside. The duo used sophisticated techniques and tools to conduct reconnaissance and expand their access within the network.

The charges include conspiracy to obtain information from and damage protected computers, obtaining information from a protected computer, and intentional damage to a protected computer. Each carries up to 10 years in prison and a $250,000 fine. Prosecutors also allege the pair damaged at least 10 protected computers in one year and caused at least $5,000 in losses.

Roach appeared before U.S. Magistrate Judge Mark W. Pedersen and is being held pending a detention hearing. Extradition proceedings for Stubbings continue in Canada. The FBI, the Justice Department’s Computer Crime and Intellectual Property Section, and the Office of International Affairs worked on the case.

For security teams, the useful part is not the alleged crypto-mining. It is the reminder that universities remain attractive targets because they hold powerful computing resources, broad networks, and plenty of people with access. Patch quickly, watch for unusual processing load, and treat credential theft as a serious incident rather than a nuisance.

“The fact that a defendant has been charged with a crime is merely an accusation and the defendant is presumed innocent until and unless proven guilty.” DoJ concludes.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, University Supercomputers)

More Asian airlines announce data breaches after attack on Spanish IT provider Amadeus

4 de Novembro de 2026, 18:30
Japan Airlines, Cathay Pacific, Korean Air, Asiana Airlines, Singapore Airlines and Malaysia Airlines have all come forward over the last week to report data breaches traced back to Amadeus IT Group — a company that builds and maintains platforms for flight reservation, ticketing and check-in platforms.

  • ✇The CyberWire
  • The more you know, the less you know.
    This week, hosts of N2K CyberWire ⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠Maria Varmazis⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠ and⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠ ⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠Dave Bittner⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠ alongside ⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠Joe Carrigan⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠
     

The more you know, the less you know.

5 de Novembro de 2026, 03:00
This week, hosts of N2K CyberWire ⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠Maria Varmazis⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠ and⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠ ⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠Dave Bittner⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠ alongside ⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠Joe Carrigan⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠⁠ are discussing the latest in social engineering scams, phishing schemes, and criminal exploits that are making headlines. We start with some follow up from Adina, who shares a few more examples of things that become more complicated the more you learn about them, including statistics and the real-world effects of changes to complex systems. Dave adds quantum physics to the list. Maria covers new research from Akamai showing that online scam detections doubled in the past year, overtaking phishing for the first time in the company's data. Dave explores the case of a Brazilian man who traveled nearly 2,000 kilometers to meet a woman he fell in love with online, only to discover she was an AI-generated personality. Joe examines a phishing email disguised as a Calendly notification that claims to provide access to an official Social Security statement and potentially delivers malware. Our Catch of the Day features two suspicious emails, including an unsolicited donation offer supposedly from a billionaire.

  • ✇Security Affairs
  • CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code Pierluigi Paganini
    Critical Android flaw CVE-2026-58868 could allow remote code execution without user interaction on devices running Android 14 through 17. Google has fixed CVE-2026-58868, a critical Android vulnerability affecting versions 14 through 17. The flaw is a critical Android vulnerability caused by a heap buffer overflow in the onOutputReceived function of FrameDecoder.cpp. The flaw can trigger an out-of-bounds write, potentially allowing a remote attacker to execute arbitrary code on a vulnerable
     

CVE-2026-58868: Critical Android Bug Could Let Attackers Run Remote Code

4 de Novembro de 2026, 07:26

Critical Android flaw CVE-2026-58868 could allow remote code execution without user interaction on devices running Android 14 through 17.

Google has fixed CVE-2026-58868, a critical Android vulnerability affecting versions 14 through 17. The flaw is a critical Android vulnerability caused by a heap buffer overflow in the onOutputReceived function of FrameDecoder.cpp. The flaw can trigger an out-of-bounds write, potentially allowing a remote attacker to execute arbitrary code on a vulnerable device. Exploitation requires neither user interaction nor additional execution privileges, making it a potential zero-click attack.

“cve-2026-58868 In onOutputReceived of FrameDecoder.cpp, there is a possible out-of-bounds write due to a heap buffer overflow.” reads the advisory. “This could lead to remote code execution with no additional execution privileges needed. User interaction is not needed for exploitation.”

Devices receive the fix through security patch level 2026-11-01 or later, depending on manufacturers and carriers. Google is not aware of active exploitation of the flaws in its November 2026 bulletin.

Google’s November 2026 Android security bulletin addresses 216 vulnerabilities, including 23 rated Critical. Two of these flaws, CVE-2026-58876 and CVE-2026-58936, affect the System component and could allow remote code execution without user interaction.

The bulletin also lists five other Critical flaws in the System component. Three could lead to privilege escalation, while two could cause denial-of-service conditions. Another Critical vulnerability affects the Framework component and could also allow remote code execution.

Six Critical vulnerabilities affect the Android kernel. Two involve Bluetooth code, three affect the protected Kernel-based Virtual Machine (pKVM), and one is in the Human Interface Device (HID) component. The most severe kernel flaw could allow a remote attacker to gain elevated privileges without user interaction.

The November 5 patch level also addresses Critical vulnerabilities in MediaTek modem code and a closed-source Qualcomm component. Google’s bulletin lists eight Critical MediaTek modem flaws, while MediaTek’s own November security bulletin details six of them: CVE-2026-20499 and CVE-2026-20545 through CVE-2026-20549.

MediaTek describes these six vulnerabilities as out-of-bounds write flaws caused by missing bounds checks, integer overflow or improper input validation. The company says it is not aware of any active exploitation in the wild.

The Qualcomm issue is tracked as CVE-2026-25285 and affects a closed-source component. Google does not provide further technical details in its bulletin.

One of the critical issues fixed by Google is CVE-2026-58882 (aka SMS of Death), which could allow attackers to remotely disable a phone by sending a specially crafted SMS message. The flaw affects decodeWapPdu, a function responsible for processing WAP Push messages, a type of content delivered through the SMS infrastructure.

The vulnerability is particularly concerning because exploitation reportedly requires no user interaction. An attacker only needs the victim’s phone number to send a malicious message. The message doesn’t appear in the SMS inbox, so the victim may have no indication of what caused the problem.

The issue also raises concerns about the reliability of mobile communications during an attack. According to a technical analysis published on October 29 by security researcher Mark B, a malformed WAP Push message can crash com.android.phone, the Android system component responsible for handling telephony functions. The crash can terminate ongoing calls, including emergency calls.

Tests on several Android phone models reportedly reproduced the crash consistently. The phone can also become stuck in a crash loop because Android retries processing the malicious message whenever the device starts. As a result, the device may continue crashing until the offending message is removed.

There is an important distinction, however. Google’s security bulletin and the CVE record identify the vulnerable decodeWapPdu function, but neither explicitly confirms that CVE-2026-58882 is the same issue described in the researcher’s SMS of Death report. The technical overlap is worth investigating, but the two reports shouldn’t be treated as definitively describing the same vulnerability without further confirmation.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, CVE-2026-58868)

  • ✇Security Affairs
  • Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack Pierluigi Paganini
    Binance reveals how fake job interviews, malware and internal AI abuse enabled attackers to steal $6.34 billion. The Binance security incident on October 29 shows how a fake recruitment process can become the entry point to critical financial infrastructure. The attackers combined social engineering, compromised developer tools, stolen credentials and abuse of an internal AI application to reach the cryptocurrency exchange’s wallet signing systems. “Woah – so the Binance hack was indeed v
     

Binance Hack: How Fake Job Interviews and AI Abuse Led to a $6.34 Billion Attack

3 de Novembro de 2026, 16:44

Binance reveals how fake job interviews, malware and internal AI abuse enabled attackers to steal $6.34 billion.

The Binance security incident on October 29 shows how a fake recruitment process can become the entry point to critical financial infrastructure. The attackers combined social engineering, compromised developer tools, stolen credentials and abuse of an internal AI application to reach the cryptocurrency exchange’s wallet signing systems.

“Woah – so the Binance hack was indeed via a dodgy job interview for one of its developers who was tricked into downloading malware as part of the “interview” – costing the company >$3bn…” the popular best seller author and cybercrime expert Geoff White wrote on LinkedIn. “Worth noting:
– The 2016 hack of Bangladesh Bank also attributed to North Korea’s Lazarus Group of hackers was via a job application
– The 2022 theft of $625m from video game Axie Infinity happened via offering an employee a juicy job offer
RECRUITMENT IS RISK. If you’re not educating employees on this, start now…
– The 2024 heist of $1.5b from Bybit relied on tricking an employee of its supplier into downloading a dodgy share trading app onto the work machine (so not using a recruitment lure, but still deceiving a target into downloading malware)”

In its initial findings and response update, published on November 3, Binance described the operation as a “sophisticated, multi-stage campaign.” The company estimates that approximately $6.34 billion in digital assets were affected. The FBI attributed the incident to the North Korea-linked APT “TraderTraitor,” also tracked as Lazarus Group and APT38.

“Our current investigation indicates that this was a sophisticated, multi-stage campaign. It was not a single isolated breach or a simple phishing incident.” reads the update published by the crypto firm. “The attackers combined a range of techniques, including social engineering by fake recruitment interviews, malicious software downloads, compromised internal AI tooling, endpoint compromise, and an advanced transaction-authorisation method.”

The operation began months before the theft. In June 2026, an engineer from Binance’s Wallet DevOps team downloaded a tampered Homebrew installation while searching online for a popular AI coding tool. Binance detected the suspicious activity, replaced the device and rotated the associated credentials, but information about the engineer’s role and colleagues had already been exposed.

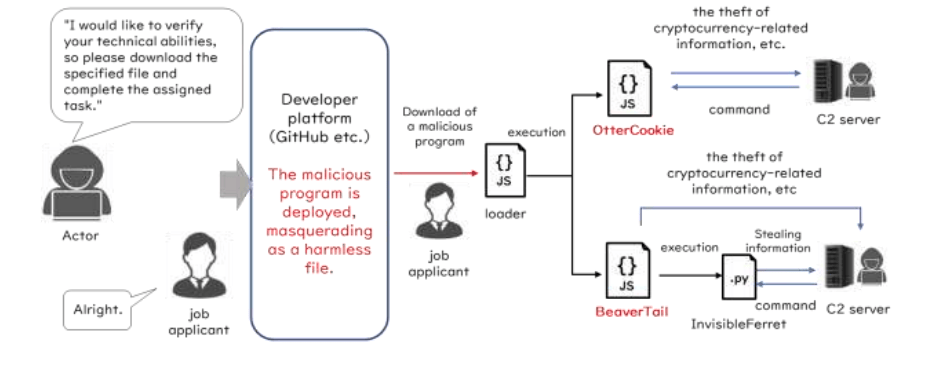
The attackers then targeted another software engineer through a legitimate job-hunting platform. In September, someone posing as a Project Director arranged two interviews: first with an HR representative, then with someone claiming to be the CEO of a fictitious company. During the first video interview, the supposed HR representative shared a social media account containing personal photos and videos to establish credibility.

At the end of the second interview, the engineer was asked to download a technical assignment containing a malicious code repository onto his work computer. The malware executed during setup, replacing a legitimate development tool component with a malicious version. It used obfuscation to evade detection, executed commands and established communication with an attacker-controlled server. Binance said its endpoint security tools didn’t detect the malware at the time.

“The second interview was conducted in a popular social chat app, near the end of the interview, Engineer B was instructed to download an “assignment” containing a malicious code repository onto his work computer.” states the firm. “The repository contained malicious code that executed during the setup process, initiating a series of unauthorized activities.”

The compromise then moved beyond the affected workstation. On October 20, attackers used the compromised computer to abuse an internal AI tool and gain access to the systems of two other employees, including the Wallet DevOps engineer initially targeted in June. They discovered that his computer contained a token with container deployment permissions.

This is one of the more significant aspects of the incident. The report doesn’t identify a vulnerability in the AI model itself. Instead, it shows how an internal application can become an attack pivot when an adversary gains access to a compromised employee’s environment and the permissions available to that user.

“The attacker leveraged the compromised computer of engineer B and used an internal AI tool to gain control over the Wallet DevOps Engineer A and another Wallet Software Engineer C.” states the report. “The attacker soon discovered Wallet DevOps Engineer A had a container deployment permission token on his computer.”

On October 29, the attackers used stolen credentials to access another engineer’s computer, deploy a container and execute a malicious script. This gave them access to Binance’s internal wallet signing service, allowing them to initiate transactions outside the normal withdrawal process.

The transfers involved several blockchain networks. Five Binance hot wallets sent 233.46 million XRP to an attacker-controlled address, while other transfers involved approximately 970,500 SOL, 44.2 million OP and 18,270 BTC.

The attackers also exploited Ethereum’s EIP-7702 authorization mechanism to grant a malicious smart contract partial execution rights over a Binance hot wallet.

“EIP-7702 allows an account to delegate certain execution rights to a smart contract without exposing the private key. In this case, the attacker used that mechanism to give an attacker-controlled smart contract partial execution rights over a Binance hot wallet.” the company states.

Suspending withdrawals wasn’t enough to stop the transfers because the malicious authorizations already existed on-chain and operated independently of Binance’s normal withdrawal infrastructure.

Binance had to develop a specific procedure to revoke them. The use of Multi-Party Computation (MPC) meant there was no single private key that could immediately invalidate the unauthorized permissions. The final unauthorized transfer, involving 2,961.9 ETH, was finalized at 23:56 UTC. Binance cleared the malicious authorization at 00:10 UTC on October 30.

The company estimates that approximately $6.34 billion in assets were affected, of which around $2.85 billion had been frozen or intercepted as of its November 3 update. Binance says it will absorb the financial impact and has already replenished 98% of the affected token assets, based on figures reported on October 31.

The exchange has rebuilt the affected wallet infrastructure and internal AI tool, replaced compromised devices, revoked associated credentials and tokens, and strengthened endpoint monitoring and wallet-service controls. It is also engaging independent cybersecurity firms to review the incident.

The attack highlights the need to treat recruitment processes, developer workstations and internal AI applications as part of the corporate attack surface. Technical assignments should run in isolated environments, deployment credentials should be short-lived and tightly restricted, and internal AI tools should never inherit unnecessary access to sensitive systems.

Binance also said its security team had detected and prevented 57 suspected North Korea-linked cyber threat cases during 2026. These included fake job interviews, malicious developer tools, compromised software packages and browser extensions, fake video-conferencing applications and campaigns designed to steal credentials or deploy remote-access malware.

The incident is another reminder that attackers don’t always need to break directly into critical infrastructure. Sometimes, compromising the people and tools that manage it is enough.

“We are sharing this initial report because security improves when the industry learns together.” concludes the update.

In September, Japan’s National Police Agency, the FBI, the US Department of Defense’s Cyber Crime Center, and intelligence agencies from Australia and Germany published a joint advisory about a group called WaterPlum, better known as Contagious Interview. The name says it all. The job interview is the infection vector.

The numbers in the advisory are hard to shrug off. At least 30,000 devices infected across more than 100 countries, funds or credentials stolen from over 7,000 cryptocurrency wallets, and a total of 1.7 billion yen, roughly $10.71 million, funneled back to North Korea. The victims are almost always the same type: freelance developers and specialists in blockchain and Web3 work.

Japan’s NPA and the FBI assess that both WaterPlum operators and some North Korean IT workers report to the same place, the 313 General Bureau of the Munitions Industry Department, under the Workers’ Party’s Central Committee. That’s not a loose affiliation. It’s an org chart.

The trap itself is almost embarrassingly simple. WaterPlum actors pose as recruiters or hiring managers, often impersonating real AI, crypto, or NFT companies, and reach out on social media, job boards, and freelance platforms. Candidates get invited to a technical interview, then told to download a file to complete a coding test or fix a supposed bug on the video call.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, Binance)

  • ✇Security Affairs
  • Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions Pierluigi Paganini
    Synology warns of ransomware attacks exploiting a 2024 flaw in outdated NAS devices, urging users to update DSM immediately. A security fix released in 2024 is now at the centre of ransomware attacks against Synology NAS devices. The company has found attackers targeting systems that still run outdated versions of DiskStation Manager (DSM), putting files stored on these network storage devices at risk of encryption and extortion. Synology disclosed the attacks on October 29, 2026. Its inv
     

Synology Warns of Ransomware Attacks Targeting NAS Devices Running Outdated DSM Versions

3 de Novembro de 2026, 13:31

Synology warns of ransomware attacks exploiting a 2024 flaw in outdated NAS devices, urging users to update DSM immediately.

A security fix released in 2024 is now at the centre of ransomware attacks against Synology NAS devices. The company has found attackers targeting systems that still run outdated versions of DiskStation Manager (DSM), putting files stored on these network storage devices at risk of encryption and extortion.

Synology disclosed the attacks on October 29, 2026. Its investigation found that threat actors are taking advantage of a vulnerability that the vendor had already addressed in December 2024. “These attacks aim to encrypt data and extort ransom.” The warning highlights how devices left without security updates can remain exposed long after vendors have released a fix.

The company hasn’t identified the exact vulnerability used in the attacks. Instead, it refers customers to Synology-SA-24:20, a security advisory published on November 5, 2024, which documents three flaws affecting DSM. The advisory was updated as fixes became available across different software branches, with the DSM 6.2 update released on December 5.

The three vulnerabilities have different security implications. CVE-2024-10441 is the most severe, with a CVSS score of 9.8. It affects the system plugin daemon and could allow an unauthenticated remote attacker to execute arbitrary code on a vulnerable device.

CVE-2024-50629 has a CVSS score of 5.3 and affects the DSM webapi component. It could allow remote attackers to read limited files. The third issue, CVE-2024-10445, is rated 4.3 and concerns improper certificate validation in the update functionality. It could allow an attacker in an adjacent network position to write limited files.

Synology hasn’t confirmed which of these vulnerabilities attackers are exploiting. The three flaws should therefore be considered part of the security advisory, not three confirmed entry points in the current ransomware campaign.

The vendor has released corrected builds for all the affected DSM branches. Users should check the full version number installed on their NAS and compare it with the minimum fixed releases listed in the advisory:

  • DSM 7.2.2: 7.2.2-72806-1 or later.
  • DSM 7.2.1: 7.2.1-69057-6 or later.
  • DSM 7.2: 7.2-64570-4 or later.
  • DSM 7.1: 7.1.1-42962-7 or later.
  • DSM 6.2: 6.2.4-25556-8 or later.

The impact of a ransomware infection on a NAS can extend well beyond the storage device itself. Businesses often use these systems to keep shared documents, operational files and backup copies in one place. If attackers encrypt that data, employees may lose access to essential information, while recovery can become much harder if the NAS also holds the backups needed to restore other systems.

Updating DSM is therefore an immediate priority for administrators and home users alike. Synology is also advising customers to enable automatic updates so that future security fixes don’t depend entirely on someone checking for them manually.

“Synology also recommends enabling automatic updates to keep DSM up to date at all times.” concludes the advisory.

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

Pierluigi Paganini

(SecurityAffairs – hacking, NAS)

Google dismantles massive botnet hidden in Android TV boxes

3 de Novembro de 2026, 16:48
The overwhelming majority of the infected devices in the X.CPE botnet are Android TV set-top boxes, Google said, adding that they observed a number of other infected Android-based IoT devices, including telehealth devices, karaoke machines and digital signage devices.

British businesses caught in Europe-wide supermarket fridge attacks

3 de Novembro de 2026, 14:43
Supermarket and grocery store refrigerator controls across Europe were hacked in the early hours of Monday in the second such wave of attacks in recent weeks — following a first wave in France — with unidentified perpetrators defrosting fridges and causing stock to spoil.

❌
❌