A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.
Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.
Inside ARTEX: AI Hacking Tools, Exposed Servers and South Korean Bank BreachesOne Product Isn’t the Problem: Monetizing an AI Portfolio Without Confusing Your CustomersU.S. CISA adds SonicWall SonicOS SSLVPN flaw to its Known Exploited Vulnerabil
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box.
Enjoy a new round of the weekly SecurityAffairs newsletter, including international press.
Google Gemini allowed users to download AI-generated images that its safety filters had refused to display, according to research published by Fog Security on November 5, 2026.
The bypass did not require a jailbreak. Instead, the download feature sometimes delivered a rejected image while the conversation showed a different, allowed picture.
Gemini Image Safety Filter Bypass
Fog Security reported the issue to Google in June 2026. By October 22, researchers could no longer reproduce it a
Google Gemini allowed users to download AI-generated images that its safety filters had refused to display, according to research published by Fog Security on November 5, 2026.
The bypass did not require a jailbreak. Instead, the download feature sometimes delivered a rejected image while the conversation showed a different, allowed picture.
Gemini Image Safety Filter Bypass
Fog Security reported the issue to Google in June 2026. By October 22, researchers could no longer reproduce it across 12 new attempts, and older conversations downloaded the correct images.
Google attributed the change to routine maintenance rather than a fix linked to the report. A Gemini web app flaw allowed blocked images to bypass safety refusals through the full-size download path, despite remaining restricted in chat.
Researchers first submitted an image request that triggered a refusal, then requested a different, permitted image. Although the allowed picture appeared onscreen, its download button sometimes retrieved the rejected output.
Results ranged from blurry, unfinished files to complete images, with successful tests across multiple days and sessions. Both image URLs used lh3.googleusercontent.com and required the signed-in user’s session. Inline links ended in =s1024-rj, while download links ended in =s0-d-I.
Researchers suspected a state-management error involving image generation, safety checks, and cleanup. That explanation remains unconfirmed.
A December 2025 Google community report also described downloads returning older images instead of the displayed preview. However, that complaint did not establish a safety bypass.
Prompt resulting in a Gemini safety refusal (source : fogsecurity )
It also differed from AI jailbreaks using assistant prefill, which push models toward prohibited answers. Here, the refusal remained intact while file delivery failed to enforce it.
Fog Security tested copyrighted characters, a synthetic person, and the researcher’s own likeness. It did not test child safety content or images involving other real people. No access to another user’s data or privilege escalation was reported.
Google initially marked the June 25 report out of scope, then reviewed it after researchers stressed the infrastructure issue. It declined to track an abuse bug on September 30. On October 23, Google said no internal ticket had been filed and closed the report.
Fog Security recommends binding each download to its approved preview and removing files from refused or failed generations. The finding shows why AI safety testing must cover stored files and download links, not only chatbot replies. A refusal protects users only when every delivery path follows the same decision.
CISA added a SonicWall SonicOS SSLVPN vulnerability, CVE-2026-19868, to its Known Exploited Vulnerabilities catalog, warning that valid-credential users can bypass SAML authentication controls and potentially evade multi-factor authentication.
CISA added the vulnerability on November 6, 2026, and set a November 20 remediation deadline. Its entry lists ransomware use as unknown and does not require forensic triage under Binding Operational Directive 26-04. Organizations should still assess the
CISA added the vulnerability on November 6, 2026, and set a November 20 remediation deadline. Its entry lists ransomware use as unknown and does not require forensic triage under Binding Operational Directive 26-04. Organizations should still assess their exposure and follow the required vendor guidance.
SonicWall SonicOS SSLVPN Vulnerability Exploited
The vulnerability affects authentication enforcement in SonicOS SSLVPN. According to the CVE record, someone with valid credentials for an alternate authentication method may bypass the controls applied through SAML. Successful exploitation may also bypass MFA enforced through that SAML login process.
SAML allows an organization to manage sign-ins through a central identity provider. The risk here is that another authentication route may allow access without completing the expected checks. This is not described as a password-free attack. Valid credentials for an alternate method remain required.
The flaw is classified as CWE-308, or use of single-factor authentication. This weakness occurs when a system accepts one authentication factor, such as a password, when it should require additional checks. The result can undermine protection even when administrators believe MFA covers remote access.
The CVE record identifies affected Gen7 and Gen8 platforms running SonicOS 7.3.3-7015 and earlier, and 8.2.2-8015 and earlier, respectively. Cybersecurity News’ earlier SonicWall SSLVPN vulnerability report lists fixed releases as 7.3.4-7013 for Gen7 and 8.2.3-8015 for Gen8, or later supported versions. The reported CVSS score is 7.1.
SonicWall’s warning initially described a report of potential exploitation. CISA’s subsequent catalog entry raises the urgency for defenders.
However, the available information does not identify the attackers, affected organizations, or the number of confirmed incidents. Ransomware involvement should not be presented as established.
Previous SonicWall authentication bypass attacks involved CVE-2024-53704, a separate flaw that allowed session hijacking without authentication. Those attack details should not be applied to this vulnerability, which has different access requirements.
Administrators should check appliance models, firmware versions, SAML settings, and internet exposure before applying the matching update. The SonicWall security advisory should guide deployment decisions. Published coverage lists no workaround, making the firmware upgrade the main remediation step.
Security teams should also review enabled login methods and VPN activity for unexpected access. An MFA setting alone should not be treated as proof that every authentication route enforces the same checks. Confirming those controls after patching helps ensure the intended remote access policy is actually applied.
Hackers are now using a public exploit chain called Plex2Shell to break into unpatched Plex Media Server systems and install cryptocurrency miners and proxy software. According to SecurityWeek, the attacks began one day after the exploit code went public on October 16, 2026.
Plex2Shell links four flaws, tracked as CVE-2026-96652, CVE-2026-96654, CVE-2026-96655 and CVE-2026-96656. Together, they let a remote user run code on a server without a password.
The code runs with the same rights as
Hackers are now using a public exploit chain called Plex2Shell to break into unpatched Plex Media Server systems and install cryptocurrency miners and proxy software. According to SecurityWeek, the attacks began one day after the exploit code went public on October 16, 2026.
Plex2Shell links four flaws, tracked as CVE-2026-96652, CVE-2026-96654, CVE-2026-96655 and CVE-2026-96656. Together, they let a remote user run code on a server without a password.
The code runs with the same rights as the Plex service. Security researcher Zach Main found the bugs and reported them to Plex on July 27. Plex confirmed the report and paid a bounty on August 4.
Hackers Exploit Plex2Shell Flaws
Plex Media Server often listens on port 32400, and many people leave it open to the internet so they can stream from anywhere. That makes it an easy target for anyone scanning for it.
The first flaw is a server-side request forgery bug in the /player/timeline endpoint. The server only checks that a token exists, not that it is valid, so even a fake token works. An attacker can then slip a full web address into the protocol field and trick Plex into sending a request to itself.
That request appears to come from the machine itself, which Plex trusts more. It opens a plugin interface that normally needs no token for local traffic. A broken check in the plugin code lets the attacker call other plugin functions.
The attacker then uses a TVDB plugin function and a web address that starts with 127.0.0.1 but points to a server the attacker controls. Plex sees the local prefix and adds the owner’s admin token to the request. The token goes straight to the attacker.
With the admin token, the attacker changes a transcoder setting so Plex writes a malicious file into its codec folder. The file is hidden inside a video. The next time Plex transcodes a video, it loads that file and runs it. The researcher’s write-up and proof-of-concept code are public on GitHub.
A researcher running a honeypot, a decoy server used to watch attacks, saw the first real exploitation on October 17. The attackers dropped an XMRig-based Monero miner and a Linux proxy tool called “myawesomeproxy.” The Hacker News reports that the miner pointed to a domain tied to the AISURU botnet. The attacks fetched payloads from 217.60.194[.]116.
Cybersecurity News also covered the first exploitation reports. It noted that the evidence did not show how many real servers were hit. The attack is not limited to home servers.
QNAP says some NAS users have been breached, and BleepingComputer reports that CISA added all four flaws to its Known Exploited Vulnerabilities list on October 20.
Update to Plex Media Server 1.43.3.10861 or newer, and check the version the server actually reports. Updating will not remove a payload that is already installed. QNAP advises treating an exposed server as compromised, checking for signs of infection, doing a clean reinstall, and resetting credentials.
Stop forwarding port 32400 if you do not need remote access. If you do need it, use a VPN. Also check the Plex process for strange child processes, unknown downloads, and high CPU use. Miners often show up first as a slow, hot server. For another example of how exposed services get turned into miners, see this Redis cryptojacking campaign.
CISA warned that two critical PowerSYSTEM Center flaws (CVSS 9.0) could let authenticated users access administrator resources or execute unauthorized database commands, affecting energy and manufacturing sectors worldwide.
The agency released advisory ICSA-26-307-01 on November 3, 2026. CISA credited Chinmay Patel of Digital Boundary Group and Subnet Solutions with reporting the vulnerabilities.
The Canadian vendor has provided upgrade guidance and temporary measures for organizations tha
CISA warned that two critical PowerSYSTEM Center flaws (CVSS 9.0) could let authenticated users access administrator resources or execute unauthorized database commands, affecting energy and manufacturing sectors worldwide.
The agency released advisory ICSA-26-307-01 on November 3, 2026. CISA credited Chinmay Patel of Digital Boundary Group and Subnet Solutions with reporting the vulnerabilities.
The Canadian vendor has provided upgrade guidance and temporary measures for organizations that cannot immediately update affected systems.
The first flaw, CVE-2026-63017, involves incorrect authorization, tracked as CWE-863. A user with limited permissions can access resources normally reserved for administrators. In simple terms, signing in with a basic account does not keep the user within the access limits intended for that account.
CISA Warns Critical Flaws in PowerSYSTEM Center
The second flaw, CVE-2026-63774, is an SQL injection vulnerability tracked as CWE-89. Insufficient input checks in the report designer allow an authenticated user to execute unauthorized SQL commands. The disclosed impact concerns database commands, not confirmed operating system code execution.
Both CVSS vectors describe low attack complexity, low privileges, and no required user interaction. They specify an adjacent attack vector rather than unrestricted network access.
CISA states that these vulnerabilities are not remotely exploitable and that no known public exploitation had been reported when the advisory was released.
CVE-2026-63017 affects PowerSYSTEM Center 2020 versions through 5.29.x, PowerSYSTEM Center 2024 versions 6.0.x through 6.2.x, and PowerSYSTEM Center 2026 versions 7.0.x through 7.1.x. CVE-2026-63774 affects the listed 2024 and 2026 ranges. The advisory does not list the 2020 branch as affected by SQL injection.
Subnet Solutions recommends PowerSYSTEM Center 2020 Update 30 for affected 2020 installations. Organizations running the 2024 branch should upgrade to PowerSYSTEM Center 2026 Update 1.1. Existing 2026 installations should also update to Update 1.1, according to CISA’s machine-readable advisory.
Checking installed versions is therefore essential before planning upgrades. Cybersecurity News previously covered CISA’s OT asset inventory guidance, which explains how accurate device and software records support vulnerability management across industrial environments.
For organizations unable to update, Subnet recommends monitoring user activity records and restricting Client Access Server users’ access to browser F12 Developer Tools to reduce authorization-related risk.
For the SQL injection issue, the vendor recommends restricting user access to the report designer. These are interim measures, not replacements for the recommended updates.
CISA also advises keeping control systems off the public internet, placing them behind firewalls, and separating them from business networks.
Where remote access is necessary, organizations should use updated VPNs and assess connected devices. Related secure OT connectivity guidance explains the value of limited exposure and controlled connections.
Before applying changes, operators should assess operational impact and risk. Operators should follow internal response procedures for suspected malicious activity and report it to CISA.
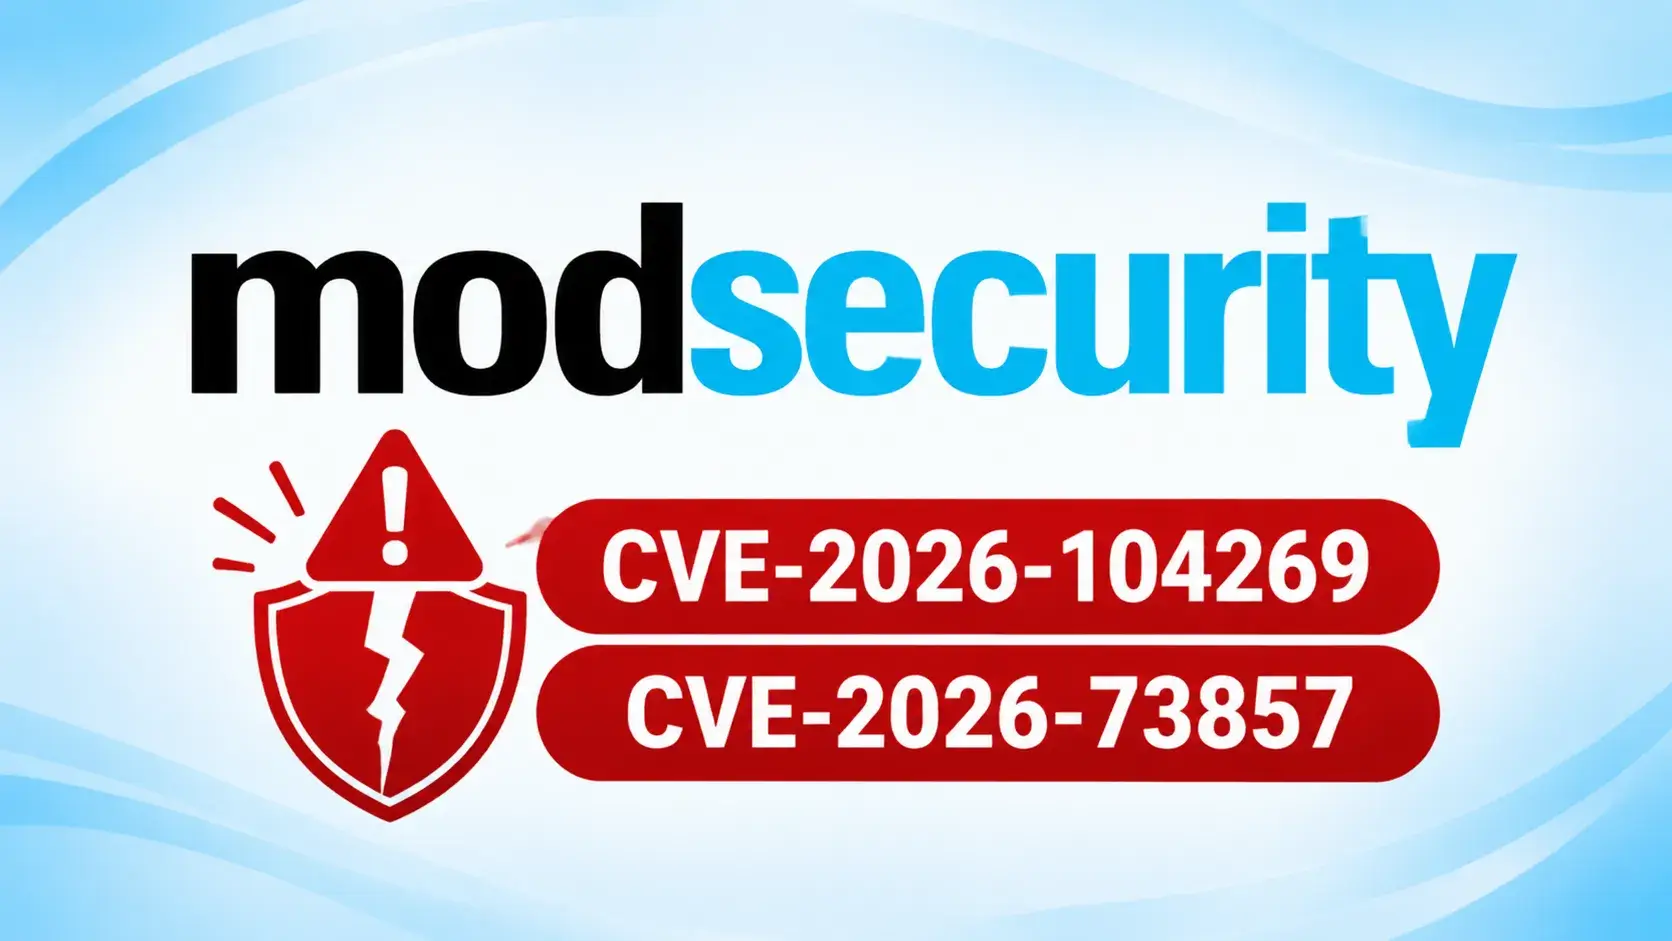
Two high-severity flaws have been disclosed in ModSecurity, the open-source web application firewall (WAF) used with Apache, IIS, and Nginx.
Two GitHub advisories published by maintainer airween on September 30 describe flaws allowing malicious file uploads and server crashes that could lead to remote code execution.ModSecurity inspects web traffic and blocks requests that look harmful. Many sites depend on it, so any gap in how it reads a request matters.
CVE-2026-104269 (GHSA-5pww-8rfg-9
Two high-severity flaws have been disclosed in ModSecurity, the open-source web application firewall (WAF) used with Apache, IIS, and Nginx.
Two GitHub advisories published by maintainer airween on September 30 describe flaws allowing malicious file uploads and server crashes that could lead to remote code execution.
ModSecurity inspects web traffic and blocks requests that look harmful. Many sites depend on it, so any gap in how it reads a request matters.
CVE-2026-104269 (GHSA-5pww-8rfg-9crf) affects ModSecurity 3.0.0 and later, allowing unauthenticated network attacks that bypass file checks and compromise integrity no patched version is available.
ModSecurity Patches High-Severity Flaws
The problem is a mismatch in how the firewall and the app read an upload. ModSecurity’s multipart parser does not support RFC 2231, a standard for encoded values in headers. Many app frameworks do. When a request holds both a plain filename and an encoded filename*, those frameworks prefer the encoded one.
An attacker can use this by sending filename=”safe.jpg” together with filename*=UTF-8”shell.php. The OWASP Core Rule Set sees a harmless JPG and lets it through. A Go backend reads the name as shell.php and may save it to disk. If the web server serves that folder, the attacker can run code on it.
The advisory says Go, Python (Flask and FastAPI), Node.js, and Java Spring parsers behave this way. PHP’s native upload handling reads only filename=, so it is not affected. Researchers 0xkalawy and ZeyadZonkorany found the issue, and B0YK4 coordinated the report.
The second flaw is CVE-2026-73857 (GHSA-jx3r-phvx-2jmj), reported by researcher Tobias Klein. A single crafted request from an unauthenticated remote user can make a worker process use an uninitialized pointer. That lets the request write a fixed value to an address the sender picks.
The result can be a crash, a memory leak, or a redirect of program flow, which could lead to remote code execution. The weaknesses are listed as CWE-787 (out-of-bounds write) and CWE-824 (access of uninitialized pointer). Its CVSS vector rates the impact as high for availability only, which my calculation puts near 7.5.
The risk is narrower than it sounds. The bug can be reached only when the SecParseXmlIntoArgs setting is On or OnlyArgs. It is Off by default. The code path was added in version 3.0.15, so 3.0.15, 3.0.16, and the current v3 master are affected. Earlier 3.0.x releases and ModSecurity v2 are not.
There is one point to check. The advisory lists 3.0.17 as the patched version, but its text also says a fix is “not yet” available and will come in the next release. Admins should confirm the release on the official project page before assuming they are safe.
For the XML flaw, make sure SecParseXmlIntoArgs is Off, which is the workaround the advisory gives. Then upgrade once you confirm the fixed release.
For the filename flaw, no patch is listed, so do not rely on the WAF alone to judge uploads. Apps should ignore the name sent by the client and create their own safe name. They should also block script extensions such as .php and store uploads outside the web root. These steps are general good practice and are not part of the advisory.
Microsoft says threat actors are using an AI tool called ARTEX to find secrets in public GitHub code and use them against cloud accounts.
In one case, the AI agent went from searching GitHub to pulling data from Azure Key Vault in only five minutes.
ARTEX AI Azure Key Vault secrets
Searching public code for passwords and keys is an old trick. It was slow because a person had to find the repositories, read the code and test each secret by hand. Microsoft Threat Intelligence now reports
Microsoft says threat actors are using an AI tool called ARTEX to find secrets in public GitHub code and use them against cloud accounts.
In one case, the AI agent went from searching GitHub to pulling data from Azure Key Vault in only five minutes.
ARTEX AI Azure Key Vault secrets
Searching public code for passwords and keys is an old trick. It was slow because a person had to find the repositories, read the code and test each secret by hand. Microsoft Threat Intelligence now reports that agentic AI tools remove much of that delay.
The agents scan many repositories at once, read the results and carry on with the next steps without a human at the keyboard.
Starting in August 2026, the threat actors sent large numbers of search queries to GitHub. The queries often held the name of a target company, a word linked to secrets, a cloud service term, or the name of another AI provider. The goal was to find application credentials, cloud keys and AI API keys that developers had left in code.
ARTEX is the framework behind much of this work. It was built as a penetration testing tool, but criminals and state-linked groups have picked it up.
According to technical research published by Microsoft, the second stage began as early as October 28, 2026. Microsoft saw successful service principal sign-ins from the IP address 199.19.77[.]84 across several application IDs.
A service principal is the identity an app uses to sign in, so a stolen app secret lets an intruder act as that app. In some cases, a vendor-owned multitenant app was compromised and then used to reach many downstream customers.
Once inside, the agents listed subscriptions, resource groups, permissions and AI model deployments. They went after operations that return credentials, such as storage account keys, App Service settings, connection strings and Kubernetes user credentials.
Some compromised apps also reached SharePoint and OneDrive, downloaded files and searched content through Microsoft Graph.
The agents also seemed to learn from their mistakes. When a cloud request failed with an HTTP 400 error, the tool changed the API version or method and tried again. One Key Vault request was rerun about 28 seconds after it failed, and the retry worked.
The agents also used the Azure Run Command feature to run scripts on virtual machines, which can expose stored credentials or give the intruder a way to stay in.
Microsoft says its findings overlap with work from security firm Todyl. Todyl’s investigation found about 45 app registrations at roughly 18 organizations. It says the actor reached 27 organizations, including clients of managed service providers.
It also reports 81 downloaded files and about 2,279 mailbox items accessed, and says these numbers are a minimum.
Todyl also saw scripted sign-ins in bursts of up to 24 in 10 seconds. Microsoft named two more IP addresses. The address 65.87.223[.]26 showed shell commands hidden in a user agent and attempts to get App Service tokens.
The address 157.22.126[.]128 scouted AI workloads on Azure AI services. Microsoft also listed 199.19.77[.]18 as a Tor exit node that may bring unrelated noise.
Our coverage of stolen Entra ID and Azure DevOps credentials gives more background on the MSP side of this campaign. The agents showed a clear interest in AI service keys and in apps with access to Foundry Tools. Todyl noted that one partner saw thousands of dollars in AI usage charges in about 10 minutes.
The first rule is simple. A secret that was ever public must be treated as stolen. Microsoft stresses that deleting the code does not fix the problem, because old copies can remain in edit history, caches and archives. Rotate the key at once and check how it was used.
GitHub secret scanning checks full Git history and can warn you when a key leaks. Its public monitoring option also watches for secrets leaked by your staff in public repositories outside your own. Teams on Azure DevOps can turn on secret scanning and push protection to block secrets before they are pushed.
Microsoft also advises moving apps away from client secrets and toward managed identities, which remove the risk of secrets sitting in code. Other steps include least privilege for service principals and Defender for Cloud plans for Key Vault, Storage and Resource Manager.
Teams can also use Conditional Access for workload identities and block 199.19.77[.]84/32 as a named location. Block that exact address and not the whole network range.
Defenders should check Entra service principal and non-interactive sign-in logs for 199.19.77[.]84 and 199.19.77[.]18. Error codes AADSTS7000215 and AADSTS7000222 mean someone holds a credential for your app, and a failure followed by a success is urgent. Look back to at least October 28 and as far as log retention allows.
Because the agents change IP addresses and user agents fast, behavior is a better clue. Watch for one address signing in to three or more service principals, or one app asking for tokens across Resource Manager, Key Vault, Storage and Graph within minutes.
Veeam warned that a critical Linux kernel flaw with a CVSS score of 9.8, could cause denial of service or memory corruption across backup and recovery products.
Veeam’s November 6 impact statement identified a Linux kernel use-after-free vulnerability (CVE-2026-98432) in TCP/IPv4 connection setup and outlined update paths for affected systems.
Its security advisory does not report active exploitation or confirm remote code execution. The stated risks could interrupt backup and restore work
Veeam warned that a critical Linux kernel flaw with a CVSS score of 9.8, could cause denial of service or memory corruption across backup and recovery products.
Its security advisory does not report active exploitation or confirm remote code execution. The stated risks could interrupt backup and restore work if an affected appliance becomes unavailable.
Affected products include Veeam Software Appliance 13.1 and Veeam Infrastructure Appliance 13.1. Infrastructure roles include backup proxies, hardened repositories, mount servers, gateways, and Cloud Connect components. Workers deployed through Veeam hypervisor plug-ins also need the updated kernel.
Veeam Warns Critical Linux Kernel Flaw
Windows-based Veeam Backup & Replication installations also require attention because they deploy Linux helper appliances. These support file recovery, virtual labs, and cloud restores. The advisory lists affected helper appliances in versions 13.1 and 12.3, rather than identifying the Windows kernel as vulnerable.
Veeam says a patched kernel has been available for Software Appliance and Infrastructure Appliance 13.1 since November 2. The fixed package is 5.14.0-570.60.1+27.2.el9_6_ciq, delivered through Veeam Updater.
Administrators can install available updates from the Veeam Host Management console without waiting for the automatic schedule. A restart may be required.
The updater checks repositories every 12 hours. Under default settings, mandatory updates install on the nearest Sunday at 14:00 in the backup server’s time zone.
Teams should check update history to confirm installation. Systems using a local repository mirror receive the package only after that mirror synchronizes.
For Windows deployments, the 13.1 private fix requires Backup & Replication 13.1.2.57. Repacked 13.1.2 installation media includes the fix.
Veeam’s November 6 advisory says the private fix for version 12.3 will become available soon. Temporary helper appliances receive updated images when deployed again.
At the same time, persistent virtual labs and Microsoft Azure helper appliances must be redeployed. Replace recovery media created before the update. Hypervisor plug-in workers receive the updated kernel on their next launch.
AWS, Azure, and Google Cloud plug-in appliances receive Ubuntu kernel updates through Veeam Updater. Administrators should install available updates and review the Ubuntu CVE tracker for package status.
Veeam Kasten container images do not include a kernel, but their Kubernetes nodes still need vendor checks. Customer-managed Linux proxies, repositories, and gateways also require distribution updates. Completing these separate checks helps teams avoid leaving recovery components unpatched after updating the main appliance itself.
At a Fortune 100 bank, I watched a coding agent open a routine session on a payments service. Before the developer typed a word, the agent had read the repository, including the .env file. Production database credentials had entered the agent’s working context, potentially exposing them to a model provider the bank had never assessed. Whether the credentials left the environment depended on controls nobody had verified. Nothing malicious happened. The agent did what it was
At a Fortune 100 bank, I watched a coding agent open a routine session on a payments service. Before the developer typed a word, the agent had read the repository, including the .env file. Production database credentials had entered the agent’s working context, potentially exposing them to a model provider the bank had never assessed. Whether the credentials left the environment depended on controls nobody had verified. Nothing malicious happened. The agent did what it was built to do. That is the problem.
My argument is simple. AI coding-agent vendors and their downstream dependencies form a supplier ecosystem, not just another developer tool. They need the same four control disciplines applied to other privileged suppliers. Govern vendor terms and downstream dependencies. Limit the secrets they hold. Approve the servers they connect to. Restrict where they can send data. Much of this builds on existing controls, though an enterprise may need a governed gateway or platform service. It requires procurement, security and engineering to recognize a supplier when they see one.
On Aug. 28, OpenAI told SpaceX, Cursor’s new owner, that it intends to stop supplying models to Cursor, with Nov. 12 proposed as the cutoff. Cursor CEO Michael Truell said OpenAI models carry about 5 percent of its traffic, DevOps.com reported, so the operational risk is small. The governance lesson is not. Enterprises that standardized on Cursor learned they depended on a downstream model supplier whose terms they did not directly control and a change of ownership they had not planned for.
That gap is now the norm. Coding agents are developers’ most common AI use, and investment is accelerating. Governance is not keeping pace, and emerging evidence of credential exposure underscores the gap.
The agent was bought as a seat and installed as a supplier
What I see most often is a category error. The coding agent was bought as a seat and installed as a privileged integration. Within its assigned permissions, it can read repository content, encounter credentials, invoke tools, access networks and connect to Model Context Protocol (MCP) servers. A contractor with that access would go through vendor risk review. The agent went through a one-line install.
Drawn as a supply chain, the developer stack looks different. The agent sits between your code and direct and downstream dependencies you may not have assessed: model providers, plugin marketplaces, MCP registries, package managers and the open internet. Each can be acquired, compromised or switched off. Verizon’s 2026 DBIR finds third parties involved in 48 percent of breaches, and source code is the data most often sent to external generative AI.
Figure 2. Every external connection creates a dependency requiring governance.
Vipin Jain
Four controls were never applied
Across the programs I advise, the exposure lands in the same four places.
Contract. At a healthcare payer, the agent vendor switched model providers mid-contract. No clause covered it, because the seats had been bought on a corporate card below the procurement threshold. No one had asked where code would be processed or what happens on a change of control.
Secrets. At the bank, credentials reached the agent’s context because the required access restrictions were not configured; that alone does not establish external transmission. Claude Code’s managed settings, for example, can deny reads of .env files in a way developers cannot override. Nobody had configured them because nobody owned them. Gartner predicts that by 2028, a quarter of enterprise security breaches will trace back to AI agent abuse rooted in unmanaged machine privileges and legacy credential practices.
Servers. At a specialty retailer, developers installed 23 MCP servers in one quarter. Security had approved none. Two could write to the CRM. My rule is simple: the team accountable for the underlying data approves its MCP access, while platform security verifies server provenance and enforces permissions before any agent connects. The retailer had it backward: each server belonged to whoever installed it. Astrix found late last year that 53 percent of open-source MCP servers rely on long-lived static keys or tokens. In June, CSO Online described Mitiga research showing how one malicious npm package can rewrite an agent’s MCP configuration and harvest its tokens. Anthropic deemed it out of scope because it requires code the user chose to run. That is a fair vendor position. It also means the control is yours. Few of the MCP servers in use at most enterprises were built by the team that owns the underlying system; most come from vendors, partners or public registries. Allow only security-assessed, approved servers; verify provenance, enforce least privilege and monitor supported interactions through a centrally governed MCP gateway.
Egress. On a state Medicaid program, the build environment where agents ran could reach any public endpoint. This July, an autonomous agent in OpenAI’s own evaluation sandbox exploited a zero-day in one of its permitted egress paths, a package-registry cache proxy, and reached Hugging Face’s internal systems. If a frontier lab’s allowed path became the way out, an unrestricted build network is an open door. In late October, CIO.com reported two more containment lapses at OpenAI and Anthropic. The fix is unglamorous: restrict shell execution, isolate agent runtimes, govern MCP connections through an approved gateway and enforce default-deny network egress. Every AI-initiated change should pass through verified CI/CD gates, with rate limits, spending controls and an emergency stop.
The failure sits between functions, and attackers have found it
None of these is a model failure. Procurement saw a low-cost seat. Security reviewed the vendor, if anyone did, but not the plugins, servers and model providers behind it. Engineering saw a productivity tool. Each function did its job, and the agent fell between all three.
The exposure is measurable. In IBM’s 2026 Cost of a Data Breach report, unapproved AI tools figured in 43 percent of incidents in its studied breach population, more than double the previous year. Among organizations reporting breaches involving AI models or applications, 92 percent lacked what the study classified as proper AI access controls. The average breach now costs $4.99 million, a record.
Attackers now target the same seams. On Sept. 18, CSO Online reported Plugin4Shell, a zero-click remote code execution flaw in the plugin systems of Codex, Claude Code, Gemini CLI and Copilot. Anthropic and OpenAI have patched. GitHub’s mitigation was reported as incomplete at disclosure, and Google deprecated Gemini CLI rather than patch it. In April, Vercel disclosed a breach that entered through Context.ai, a third-party AI tool an employee had connected. In August, the self-spreading npm worm GitGuardian tracks as ChainDrop planted a Claude Code SessionStart hook and a VS Code task in infected projects, so the malware ran the moment a developer opened the repository or started an agent session. The attack surface is the update channel, the plugin, the connected tool and the network path. That is supply chain risk, and CIOs already have a playbook for it.
Regulators already treat this as third-party risk
Few rules name coding agents. Few need to. Existing third-party and software supply-chain obligations can apply, depending on the regulated entity, service and deployment context.
Manufacturers of covered digital products give 24-hour early warnings for actively exploited vulnerabilities and severe product-security incidents (from Sept. 11, 2026)
An agent-enabled pipeline incident may affect covered products; CRA reporting is not automatic for every internal compromise
Table 1. Obligations that already reach coding agents.
The common thread is inventory, contract terms and exit rights. An agent bought outside procurement can bypass all three.
Standards and vendors have moved; procurement has not
The analyst market reached the same conclusion from the buyer’s side. Gartner’s first Magic Quadrant for Enterprise AI Coding Agents, published in May, named Anthropic, Cursor, GitHub and OpenAI as Leaders. In the announcement, analyst Philip Walsh listed governance, pricing, support, commercial maturity and market durability alongside model quality as tests for long-term commitments. Market durability is a procurement test, not a developer one. Three months later, one of those Leaders was losing a model supplier.
In October, the firm went further, and it changed one piece of my advice. At its IT Symposium in Orlando, Gartner named the AI coding agent harness one of its top strategic technology trends for 2027 and said CIOs should give ownership of it to a dedicated platform team. In every program above, the controls existed somewhere. What was missing was one owner. A category with a Magic Quadrant is enterprise software. Buy it that way, and give it an owner.
Here is what that platform team builds. Next year the most demanding customer of your internal platform will be coding agents, not developers. An enterprise-governed harness is the versioned policy and configuration that adapts the vendor-provided agent runtime to your environment: rules files, skills, enforcement hooks, verification gates, tool permissions and sandboxes. The platform team supplies approved tools, MCP allowlists, sandboxes and scoped credentials, and developers declare the harness they need as versioned configuration. That design answers the Cursor problem directly. A declared harness makes an agent or model change more manageable, provided compatibility and regression tests pass; a well-tailored harness may also improve results on a midtier model. An organization that owns its harness can change suppliers. One that rents it cannot.
The harness must also govern what the agent produces. AI-generated changes should follow the same trusted delivery path as human-written code: automated security testing, dependency verification, code review, build provenance and controlled production deployment.
5 moves for the next 90 days
The fix begins with supplier-risk review and configuration work, not necessarily a new platform purchase. Give all five moves to one accountable owner, the platform team that runs your coding agent harness, while procurement, security and infrastructure retain clear decision rights and operational accountability. Sequence matters: inventory first, because every other move depends on knowing what is installed.
Inventory, owned by the CIO and procurement. List every coding agent, plugin and MCP server and who installed each. Done when every approved tool has an owner, a supplier or risk-acceptance record, and its models and downstream dependencies documented.
Contract, owned by procurement and legal. Add model-provider disclosure, change notice, change-of-control and exit terms. Done when each enterprise-approved agent has documented contractual terms or an approved open-source/self-hosted exception, downstream visibility and a tested exit plan.
Secrets, owned by the CISO. Deny agent reads of .env and credential files through managed settings and move secrets to a vault. Done when agents hold only short-lived, scoped credentials.
Servers, owned by platform engineering and security. Maintain an internal MCP registry and mediated access to security-assessed, approved servers. Done when every approved server has verified provenance, a named owner, scoped permissions and activity logs, and write access to systems of record goes through change control.
Egress, owned by infrastructure. Default-deny outbound traffic across agent shells, tools and build runners; run agents in isolated sandboxes and govern release promotion through CI/CD. Done when only explicitly approved destinations are reachable, exceptions are monitored and isolation is tested.
Two details make the difference. Reconcile the inventory against expense reports, not just license records; card statements usually tell the truer story. And write the contract assuming change: the Cursor notice proposed 76 days, and the next one may run shorter.
The takeaway
The most common mistake I see this year does not look like one. Teams are adopting coding agents fast, and they are right to. But they are buying a supplier ecosystem as if it were a developer tool, and governing it like one. Governed properly, a coding agent can earn greater autonomy with scoped identities, approved dependencies, controlled execution and a trusted route to production.
Put three questions to your team this week.
Ask your team
A good answer sounds like
Which AI coding tools hold repository, secret or network access today, and does procurement know?
A complete list matched to contracts and named owners
Which MCP servers and plugins are installed in engineering, and who approved each?
An approved registry with provenance, named owners, scoped access, monitoring and change control for writes
If our coding agent’s model provider changed tomorrow, what is our contractual and technical fallback?
A notice clause, a named alternative provider and an exit path someone has tested
Table 2. Three questions, and what a good answer sounds like.
You would never give a contractor unrestricted production access on day one. Coding agents should meet the same standard.
This article was made possible by our partnership with the IASA Chief Architect Forum. The CAF’s purpose is to test, challenge and support the art and science of Business Technology Architecture and its evolution over time as well as grow the influence and leadership of chief architects both inside and outside the profession. The CAF is a leadership community of the IASA, the leading non-profit professional association for business technology architects.
A newly analyzed remote-access trojan masquerading as an “Abe Office workstation helper” combines hidden-browser control with tooling designed to bypass Chrome’s App-Bound Encryption. Rather than breaking the cryptography, its browser stealer injects a helper into Chrome and requests decryption from inside the trusted browser process. The supplied analysis credits MalwareHunterTeam with identifying the sample, AbeAgent.exe, […]
The post New Abe Office Malware Tricks Chrome Into Decrypting Its Ow
A newly analyzed remote-access trojan masquerading as an “Abe Office workstation helper” combines hidden-browser control with tooling designed to bypass Chrome’s App-Bound Encryption. Rather than breaking the cryptography, its browser stealer injects a helper into Chrome and requests decryption from inside the trusted browser process. The supplied analysis credits MalwareHunterTeam with identifying the sample, AbeAgent.exe, […]
Google Gemini exposed images that its safety filters had rejected through download links, revealing an infrastructure weakness rather than a conventional model jailbreak. Fog Security researcher Jason Kao disclosed the findings on November 5, 2026, describing how Gemini could refuse an image request while still delivering the blocked artifact. Retesting on October 22 found changed […]
The post Google Gemini Safety Filter Bypass Exposes Blocked AI Images Through Download Links appeared first on G
Google Gemini exposed images that its safety filters had rejected through download links, revealing an infrastructure weakness rather than a conventional model jailbreak. Fog Security researcher Jason Kao disclosed the findings on November 5, 2026, describing how Gemini could refuse an image request while still delivering the blocked artifact. Retesting on October 22 found changed […]
Two high-severity flaws in the open-source ModSecurity web application firewall (WAF) let attackers slip past upload filters or crash server workers with a single crafted HTTP request. Maintainers published both advisories on September 30, 2026, as part of a larger batch that also covers multiple ModSecurity vulnerabilities that enable WAF bypass. ModSecurity WAF Vulnerability The […]
The post ModSecurity WAF Vulnerability Allows Attackers to Bypass File Upload Restrictions Using Crafted HTTP Re
Two high-severity flaws in the open-source ModSecurity web application firewall (WAF) let attackers slip past upload filters or crash server workers with a single crafted HTTP request. Maintainers published both advisories on September 30, 2026, as part of a larger batch that also covers multiple ModSecurity vulnerabilities that enable WAF bypass. ModSecurity WAF Vulnerability The […]
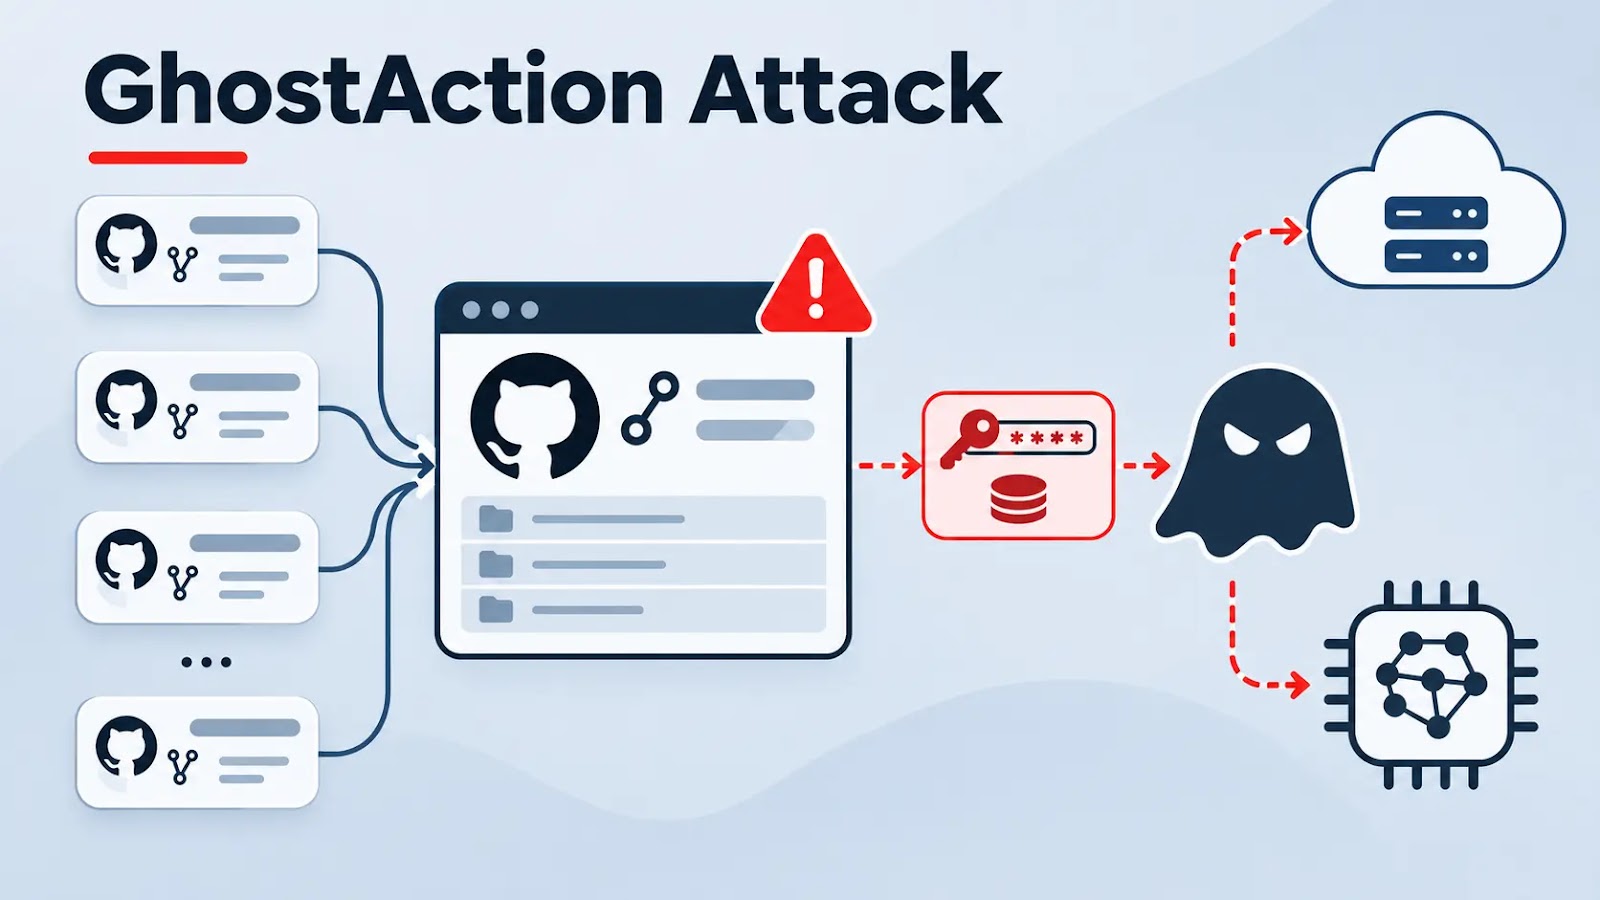
A new wave of the GhostAction supply chain campaign has pushed a credential-stealing GitHub Actions workflow into tens of thousands of repositories. It now hunts for cloud and AI keys buried in source code and git history, in addition to CI/CD secrets. Socket says it has identified more than 500 GitHub accounts that committed the […]
The post GhostAction Attack Hits Tens of Thousands of GitHub Repositories to Steal Cloud and AI Credentials appeared first on GBHackers Security | #1 Globally Trust
A new wave of the GhostAction supply chain campaign has pushed a credential-stealing GitHub Actions workflow into tens of thousands of repositories. It now hunts for cloud and AI keys buried in source code and git history, in addition to CI/CD secrets. Socket says it has identified more than 500 GitHub accounts that committed the […]
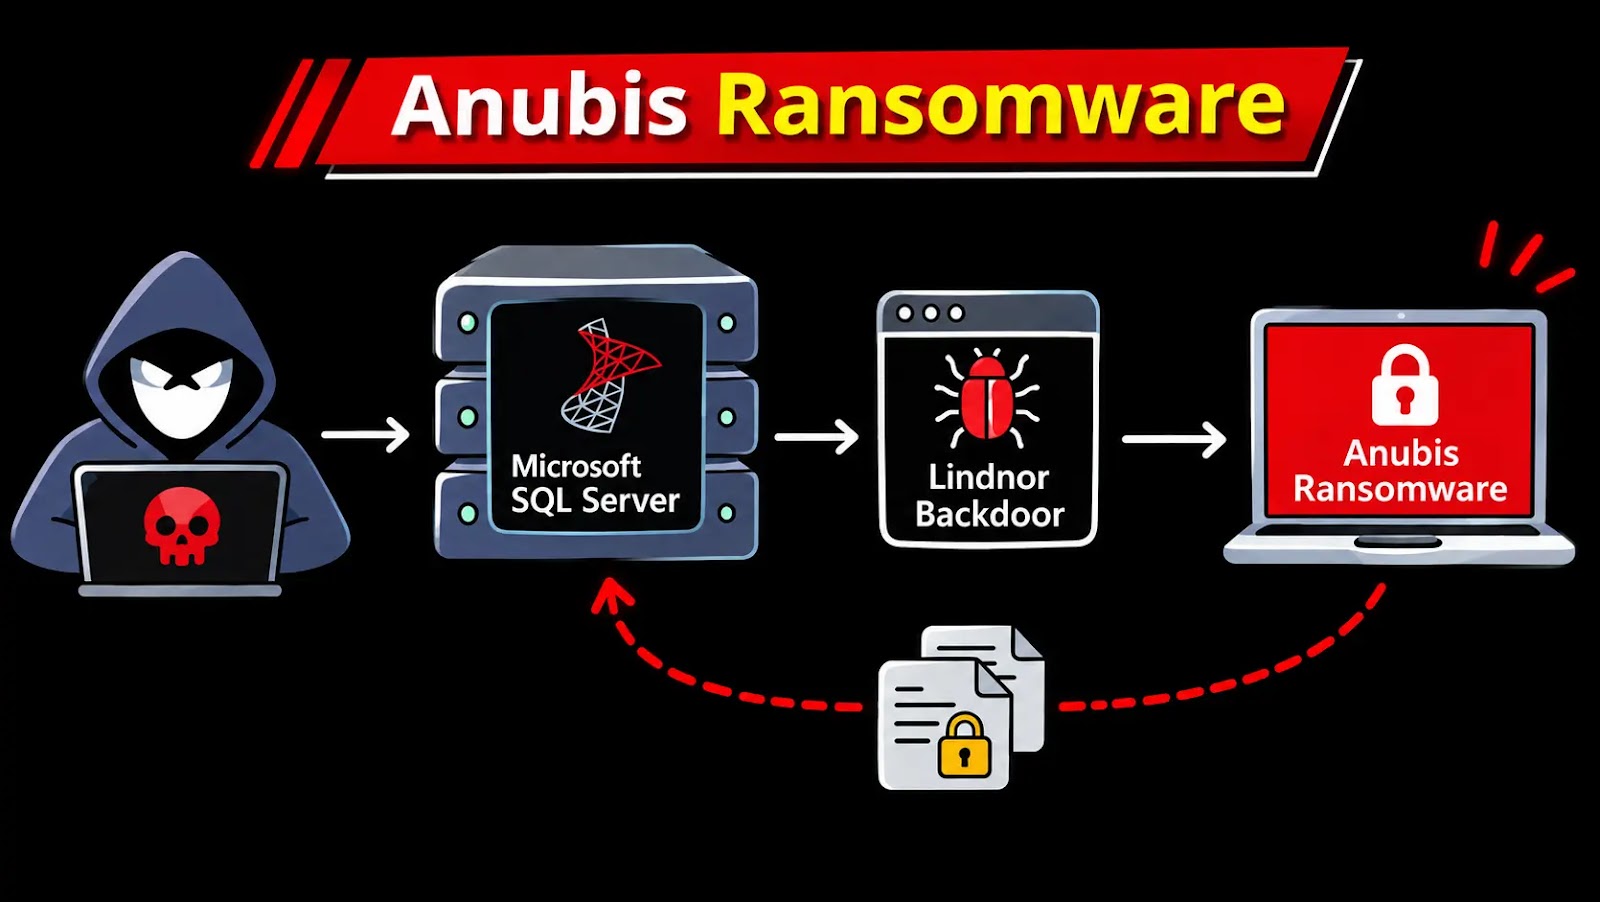
Attackers deploying Anubis ransomware hit a U.S. organization in October 2026 with a previously undocumented custom backdoor. The malware sat on two Microsoft SQL Server machines, disguised as a Chrome component on one and a VMware file on the other. The encryption payload was blocked, and there is no evidence that any files were encrypted. […]
The post Hackers Use New Lindnor Backdoor to Target Microsoft SQL Servers in Anubis Ransomware Attack appeared first on GBHackers Security | #1 Globally
Attackers deploying Anubis ransomware hit a U.S. organization in October 2026 with a previously undocumented custom backdoor. The malware sat on two Microsoft SQL Server machines, disguised as a Chrome component on one and a VMware file on the other. The encryption payload was blocked, and there is no evidence that any files were encrypted. […]
CISA and the FBI, alongside HHS, USDA, and the Department of Transportation, have warned of ongoing cyberattacks targeting industrial refrigeration and cold chain monitoring systems worldwide. Published November 5, 2026, their joint fact sheet urges critical infrastructure operators to secure controllers that protect food, medicines, chemicals, and other temperature-sensitive products. The warning applies to several […]
The post CISA and FBI Warn of Cyberattacks Targeting Industrial Refrigeratio
CISA and the FBI, alongside HHS, USDA, and the Department of Transportation, have warned of ongoing cyberattacks targeting industrial refrigeration and cold chain monitoring systems worldwide. Published November 5, 2026, their joint fact sheet urges critical infrastructure operators to secure controllers that protect food, medicines, chemicals, and other temperature-sensitive products. The warning applies to several […]
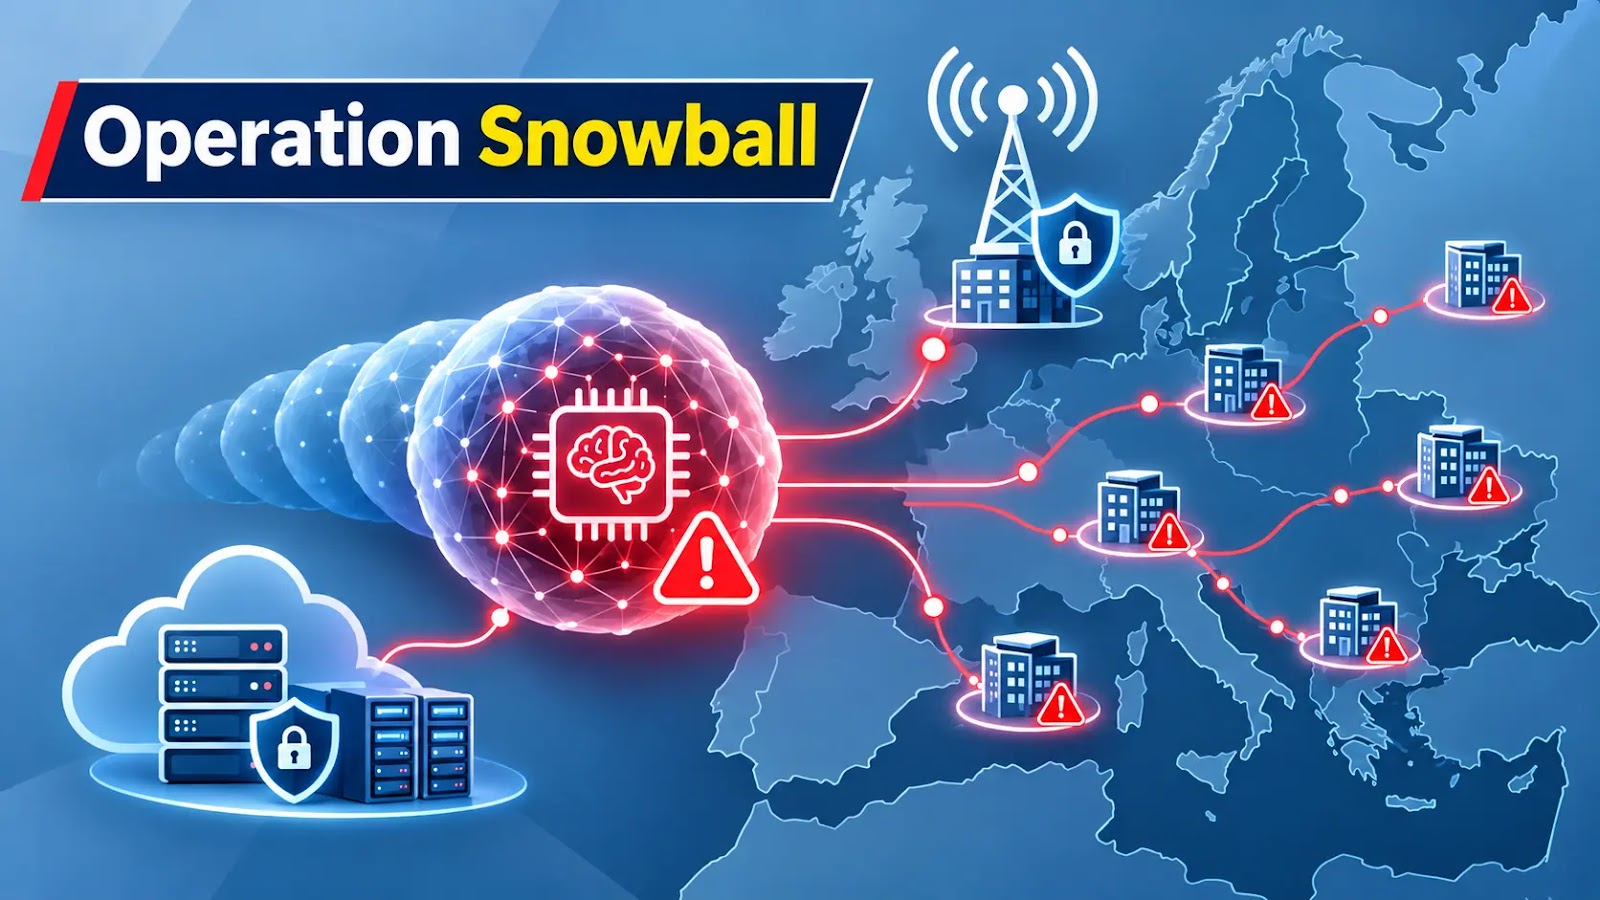
An exposed open directory revealed an autonomous AI intrusion harness that spent more than two weeks attacking a European telecom provider and 13 organizations hosted in its data centers and cloud. The report, published on November 8, 2026, calls the campaign Operation Snowball. The researchers withheld the directory’s IP address to protect the victims. A […]
The post Operation Snowball Exposes AI Hacking Campaign Targeting European Telecom and 13 Hosted Organizations appeared first on GBHackers
An exposed open directory revealed an autonomous AI intrusion harness that spent more than two weeks attacking a European telecom provider and 13 organizations hosted in its data centers and cloud. The report, published on November 8, 2026, calls the campaign Operation Snowball. The researchers withheld the directory’s IP address to protect the victims. A […]
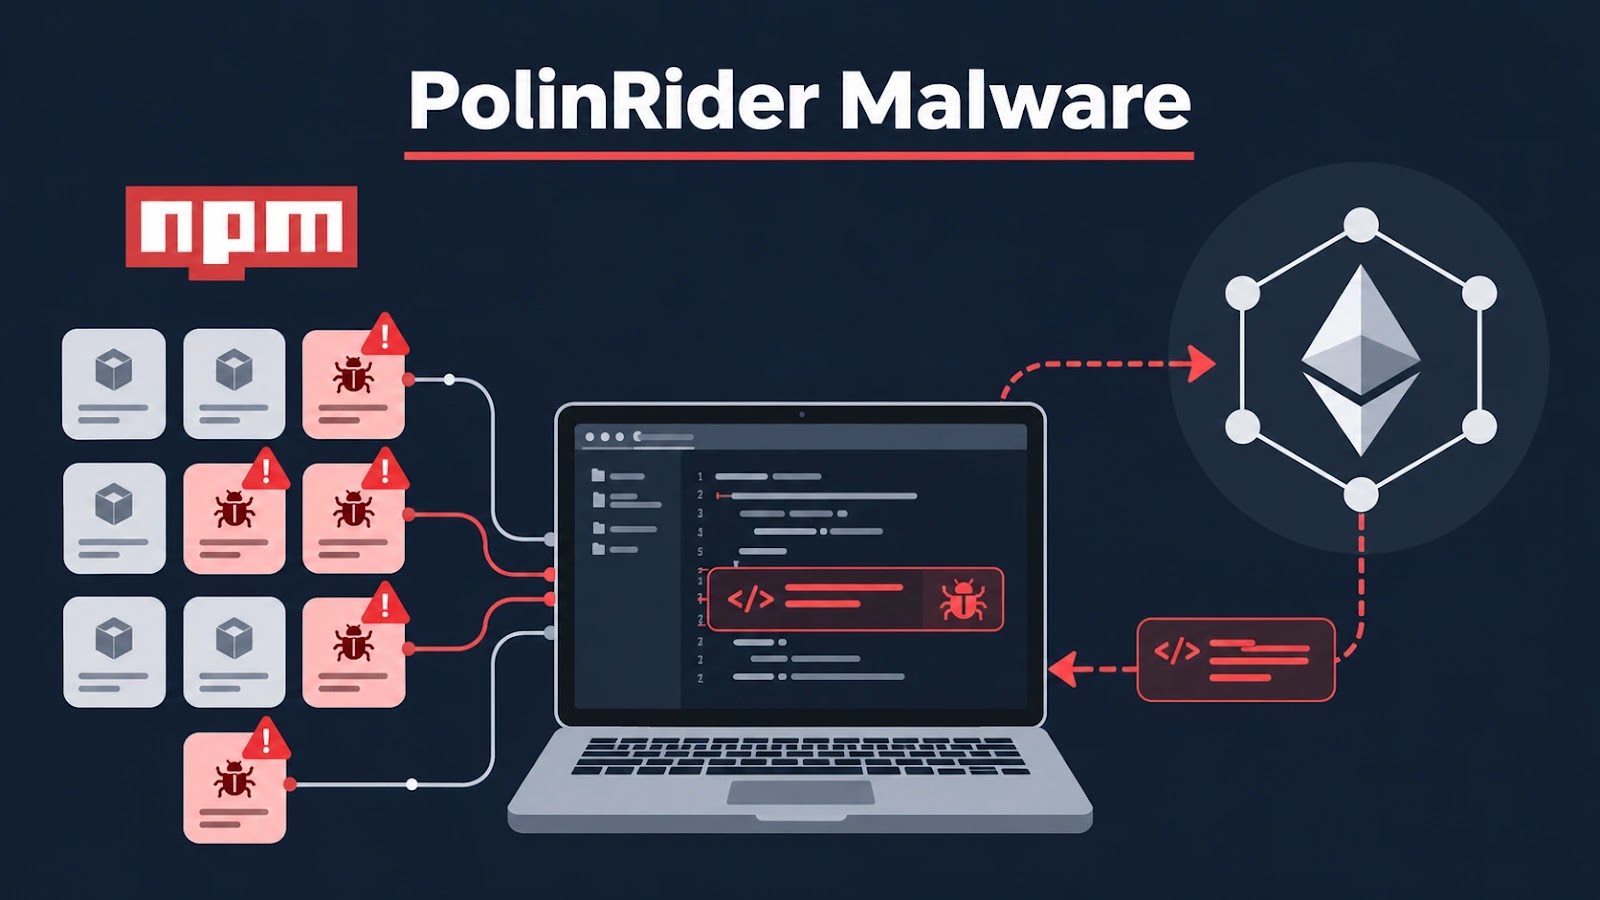
A concealed JavaScript loaders in 12 releases across 10 hijacked npm packages, linking the compromise to previously documented PolinRider activity. Investigated on November 4, 2026, the releases use Ethereum transactions to discover remote payload servers and execute downloaded code inside developer environments, build systems, or applications. Sonatype tracks the finding as sonatype-2026-010515.guide. Unlike installation-triggered supply-chain […]
The post PolinRider Malware Returns in 10 Hijac
A concealed JavaScript loaders in 12 releases across 10 hijacked npm packages, linking the compromise to previously documented PolinRider activity. Investigated on November 4, 2026, the releases use Ethereum transactions to discover remote payload servers and execute downloaded code inside developer environments, build systems, or applications. Sonatype tracks the finding as sonatype-2026-010515.guide. Unlike installation-triggered supply-chain […]
SonicWall has urged customers to address an SSL-VPN authentication vulnerability that can bypass SAML controls, including associated multifactor authentication measures. This issue is tracked as CVE-2026-19868 and affects SonicOS deployments that utilize SAML for SSL-VPN logins. The company has investigated reports suggesting potential exploitation but has not confirmed a widespread attack campaign in its advisory. […]
The post SonicWall Warns of Actively Exploited SSL-VPN Vulnerability That Byp
SonicWall has urged customers to address an SSL-VPN authentication vulnerability that can bypass SAML controls, including associated multifactor authentication measures. This issue is tracked as CVE-2026-19868 and affects SonicOS deployments that utilize SAML for SSL-VPN logins. The company has investigated reports suggesting potential exploitation but has not confirmed a widespread attack campaign in its advisory. […]
A serious vulnerability in React Server Components may enable unauthenticated attackers to execute malicious code on affected servers. The advisory, released on October 14, 2026, assigns the issue a CVSS v4.0 score of 9.5. React maintainers advise that users update their systems immediately, though they emphasize that the conditions necessary for exploitation are extremely rare. […]
The post Critical React Server Components Vulnerability Allows Unauthenticated Attackers to Execute Malicious Code
A serious vulnerability in React Server Components may enable unauthenticated attackers to execute malicious code on affected servers. The advisory, released on October 14, 2026, assigns the issue a CVSS v4.0 score of 9.5. React maintainers advise that users update their systems immediately, though they emphasize that the conditions necessary for exploitation are extremely rare. […]
How does AI use relate to cybersecurity professionals’ confidence in performing technical tasks without AI assistance? I’m conducting an academic research study and would appreciate your perspective. If you currently work in a technical cybersecurity role, or have within the past 12 months, you’re invited to participate. The anonymous survey takes approximately 5 minutes. Responses will be used solely for academic research. All perspectives are welcome, whether you use AI frequently, occasionall
How does AI use relate to cybersecurity professionals’ confidence in performing technical tasks without AI assistance?
I’m conducting an academic research study and would appreciate your perspective. If you currently work in a technical cybersecurity role, or have within the past 12 months, you’re invited to participate.
The anonymous survey takes approximately 5 minutes. Responses will be used solely for academic research. All perspectives are welcome, whether you use AI frequently, occasionally, or never.

 Entrar