❌

Visualização normal

Antes de ontemStream principal
  • ✇Securelist
  • Virtualization security: attack layers and misconfiguration impact Rauf Johari
    Introduction Incidents in virtual environments can begin with a software vulnerability, human error, a configuration weakness, or several of these factors at once. The investigation is rarely limited to the workload. Hypervisors, container runtimes, management consoles, monitoring platforms, identity systems, virtual networks, datastores, backups, and automation accounts all influence what an attacker can reach. Kaspersky GERT recently investigated two more ransomware cases on ESXi and Proxmox e
     

Virtualization security: attack layers and misconfiguration impact

6 de Novembro de 2026, 07:00

Introduction

Incidents in virtual environments can begin with a software vulnerability, human error, a configuration weakness, or several of these factors at once. The investigation is rarely limited to the workload. Hypervisors, container runtimes, management consoles, monitoring platforms, identity systems, virtual networks, datastores, backups, and automation accounts all influence what an attacker can reach.

Kaspersky GERT recently investigated two more ransomware cases on ESXi and Proxmox environments in which weak access controls, insufficient network separation, exposed administrative services, and poor management of privileged credentials contributed to the impact. A monitoring system that could reach the virtualization layer also exposed a reusable root credential. Once the attacker controlled that route, ordinary administrative access was enough to affect several hosts. No VM escape was required.

The incidents show why patching and secure configuration must be managed together. A fully patched hypervisor can still be compromised through a shared password, an overprivileged monitoring account, an open SSH path, or an administrator interface reachable from a general server network. NIST guidance places secure configuration baselines, restricted administrative access, current patches, and monitoring across all layers within the same set of sound security practices.

In this article, we’re going to describe both incidents with additional focus on common unsafe practices that were exploited, leading to compromise, as well as remediation tactics. We’ll also discuss the broader scope of threats targeting virtual environments for a better understanding of possible protection strategies.

The connected system defenders must protect

A business virtual environment is not just Hyper-V, VMware, or Docker but rather a connected stack. Management consoles, orchestration tools, monitoring platforms, and automation accounts sit above hypervisors and container engines. Registries, image stores, virtual switches, datastores, and backup systems connect the layers. Applications and business services run at the bottom, while much of the administrative power sits near the top.

The important boundaries extend beyond guest to host. They include workload to management plane, monitoring system to hypervisor, registry to deployment, administrator workstation to console, management plane to storage, and one virtual network segment to another. An attacker only needs one usable route. The possibility of compromise may lie in one stolen or insecurely placed administrator credential rather than in a complex escape exploit. In the GERT case, the compromise route passed through the monitoring platform and included a valid virtualization platform credential.

Case #1: From network monitoring to ESXi encryption

The investigation began with evidence of BlackNevas ransomware activity on a Windows system in a virtualized domain controller segment. UserAssist artifacts recorded execution of the AnyDesk RMM tool and GMER binaries. The environment also used PRTG Network Monitor to monitor its virtual infrastructure.
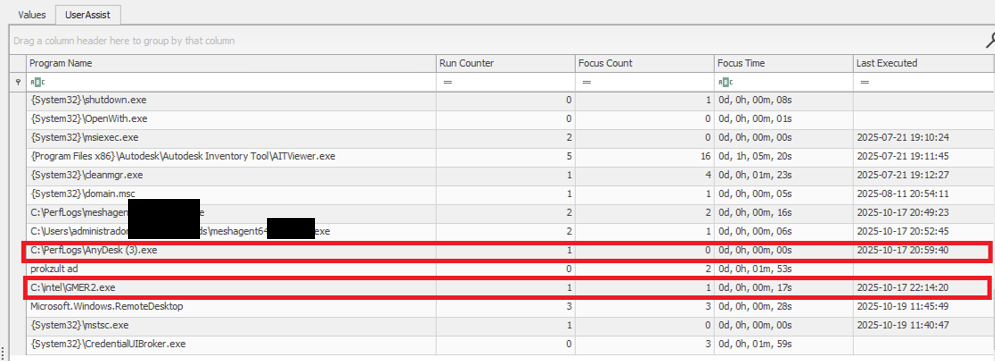
UserAssist artifacts

UserAssist artifacts

The available evidence showed that the PRTG deployment had broad access to the ESXi hosts and that the same root password was reused across several nodes. After obtaining access to the monitoring environment, the attacker used the ESXi credential to connect over SSH to the hosts that shared the same password. This design joined monitoring, credential storage, and direct administration into one attack path.

PRTG supports storing VMware credentials at the device or inherited group level. That feature is operationally useful, but a monitoring server becomes privileged infrastructure when it holds credentials that can administer the systems it observes. The security question is therefore not whether monitoring needs access, but whether the identity, privileges, storage method, and permitted network path are limited to the monitoring task.

The threat actor gained root access to the ESXi environment and used the esxcli command to bypass the system restriction by disabling the execInstalledOnly policy to execute the encryption binary and also perform anti-forensic log deletion. Let’s look closely at the timeline of the initial host compromise.

ESXi (192.168.*.*) timeline

2025-10-18 Connection attempts from IP address 192.168.*.*.
2025-10-19 During an SSH session by root from IP 192.168.*.*, the file esx is uploaded to the system.
2025-10-19 User "root" attempts to execute the binary esx with the error "Execution of non-installed file prevented".
	chmod 777 esx
	./esx /log
2025-10-19 User "root" deactivates the execInstalledOnly option.
	esxcli system settings advanced set -o 
	/User/execInstalledOnly -i 0
2025-10-19 User "root" executes the malware esx.
2025-10-19 New connection attempts from IP 192.168.*.*.

Now, at the same time, the following activities ensued on a different host with the same password for the root user:

ESXi (172.16.*.*) timeline

2025-10-19 SSH connection by user "root" from IP 172.16.*.*.
2025-10-19 User "root" executes the malware esx and clears the logs.
	chmod a+x esx && chmod 777 esx
	./esx /selftest
	nohup ./esx /p /vmfs/ /depth 5 /log /wipe
	./esx /depth 5 /log /wipe

Case #2: Credential notes impacting the whole Proxmox environment

GERT responded to a ransomware incident by The Gentlemen group, in which the threat actor gained access to Proxmox using information collected during the dwell time between initial access and visible impact. On a compromised system administrator workstation, the actor discovered administrative credentials and access details stored in notes in plain text. These records provided the information needed to log in to Proxmox using the root account.

The actor then activated the VNC web socket through the compromised root account, gaining extensive control over the Proxmox environment. This access was subsequently used to download and execute ransomware within the cluster, which resulted in the encryption of the entire virtual environment. Below are the log records showing the root account being used to access other hosts via a VNC web socket.

root@pam [01/08/2026:00:28:36 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:30:17 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:31:19 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:43:38 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****
root@pam [01/08/2026:00:44:49 -0400] "GET /api2/json/nodes/******/vncwebsocket?port=5900&vncticket=****

This incident is a clear example of the risks of storing privileged credentials in unsecured notes or other easily accessible files. Once the administrator workstation was compromised, the saved credentials allowed the actor to move from a single endpoint into the virtualization management layer. Because the credentials belonged to a highly privileged root account, one poor credential handling practice significantly increased the scope and impact of the attack. Privileged credentials should instead be stored in an approved password manager or privileged access management system, protected with multifactor authentication and rotated immediately if an administrator workstation is suspected of being compromised.

Why the misconfiguration caused broad impact

Both cases exhibited unsafe misconfiguration practices whose exploitation led to a bigger impact on the host system. Next, we will break down each misconfiguration to see how it enabled further compromise and what should be done to avoid it.

Monitoring inherited excessive privilege

In Case 1, the monitoring platform could do more than collect health and performance data. It held or could use credentials with enough privilege to reach ESXi directly. A compromise of the monitoring system therefore became a compromise of the management plane. Monitoring identities should be dedicated to the task and given only the permissions required by the deployed sensors.

Credential reuse

Password reuse converted one recovered secret into farm-wide access. System administration should use named identities through the central management plane. Each host should have unique credentials and proper password storage hygiene. Password strength alone does not limit the impact of theft, but where the credential can be used and where it is stored do.

Direct root access bypassed central control

Direct SSH access allowed the actor to authenticate as root, upload a binary, and change a security setting without first passing through vCenter role controls. Broadcom, the parent company of VMware, recommends managing vSphere through vCenter, disabling SSH during normal operation, and using Lockdown Mode where suitable. Required service accounts should be explicit exceptions rather than members of a broad administrator group.

Lack of enhanced security settings

The initial execution attempt was blocked by execInstalledOnly, but the attacker had enough privilege to disable this policy. Broadcom documents enforcement options that combine execInstalledOnly with UEFI Secure Boot and TPM-backed configuration protection. These controls must be enabled, tested, and monitored for change. A setting that can be silently disabled by the same credential used for daily administration provides limited resistance after account compromise.

Unsafe credential storage

Case 2 demonstrated the possibility of compromise lying in privileged credential exposure. The mitigation strategy involves not only securing the administrative credential storage but also general hardening practices of secret handling, such as privilege management and regular access audits.

How to close this attack path

In this section, we share remediation advice on how to mitigate such attacks, and detect and prevent them from going further. We recommend the following actions:

  • Separate monitoring from administration. Create a dedicated monitoring identity for each platform and restrict it to the smallest set of objects and actions that the monitoring sensors require. Do not use ESXi root or another emergency account for routine polling. Prevent monitoring servers from starting interactive administrator sessions unless a separately approved support workflow requires it. The same principle applies beyond VMware.
  • Replace stored root passwords. Locate every copy of hypervisor, management, storage, and backup credentials in monitoring tools, scripts, scheduled tasks, connection managers, and service configurations. Replace static passwords with vault retrieval, brokered identities, or limited API tokens where the platform supports them. Record every retrieval and rotate the secret after emergency use or compromise.
  • Restrict direct host access. Route normal ESXi administration through vCenter and enable an appropriate Lockdown Mode after testing monitoring, backup, and recovery dependencies. Keep ESXi Shell and SSH stopped by default. When support work requires SSH, enable it for a defined period, restrict the source, and alert on service activation, root login, and changes to the exception list of users who are allowed to connect via SSH.
  • Use a specialized security solution. In our portfolio, Kaspersky Cloud Workload Security (KCWS) is perfectly suited to address virtual environment risks, offering a powerful combination of two products: Kaspersky Hybrid Cloud Security (KHCS) and Kaspersky Container Security (KCS). Kaspersky Hybrid Cloud Security is specifically built to secure virtualized infrastructures, private data centers, and hybrid clouds. A patented Light Agent architecture minimizes resource impact without compromising performance, while comprehensive infrastructure visualization through a unified console gives administrators complete visibility and control over the entire hybrid network. Kaspersky Container Security covers every stage of a containerized app’s lifecycle, from development to operation. Among other capabilities, the solution allows for detecting misconfigurations using a dedicated scanner for images, file systems, and repositories that contain IaC files (such as Terraform, CloudFormation, Azure ARM templates, Helm charts, and Dockerfiles).
  • Treat configuration changes as security events. Alert when execInstalledOnly, Secure Boot enforcement, Lockdown Mode, SSH, local accounts, exception users, firewall rules, or remote logging settings change. Baseline the expected state and test whether the security team can detect an unauthorized change. A secure configuration set once does not mean that the control remains active on the host.
  • Isolate the management network. Place hypervisor, monitoring, backup, storage, and cluster administration on restricted management networks. Permit only the exact source and destination services required. Administrative workstations should enter through hardened jump hosts with named identities and multifactor authentication.
  • Protect logs, backups, and recovery. Forward ESXi, vCenter, Proxmox monitoring, identity, and network logs to protected storage that a compromised administrator cannot erase. Backup platforms should use separate identities, restricted management paths, and recovery copies outside ordinary administrative reach.

Configuration checks for monitored virtualization

Below are recommended checks to run when enabling virtualization monitoring. The safest state depends on the platform and monitoring method, but each control should be tested.

Control area Safer state Verification
Monitoring identity Dedicated service account or token with only required read and polling rights Review assigned roles and test every sensor without root or global administrator access
Credential storage No recoverable host root password on a monitoring or general-purpose server Review tool configurations, scripts, scheduled tasks, and connection stores for embedded credentials, access tokens, or other secrets
Network path Monitoring reaches only required polling services while administration uses a jump host Test management ports from monitoring server, user segments and untrusted network segments
Direct host access Lockdown Mode where suitable with SSH and ESXi Shell stopped by default Attempt direct client API and SSH access to host using a routine account
Configuration integrity Secure Boot and execInstalledOnly enforcement enabled where supported and tested Change a test setting through the approved process and confirm an alert is generated
Evidence Host, management, identity, monitoring, firewall, and PAM logs stored remotely Generate successful and failed logins and verify source, account, host, time, and action

The wider attack surface

Closing the monitoring and credential routes does not secure the environment by itself. Virtualization also relies on isolation boundaries, trusted images, management APIs, virtual networks, storage, and backups. Each layer requires a different control and leaves evidence in a different place.

VM and container escapes

In a VM escape, code inside a guest reaches past the VM boundary and affects the host or another guest. The weakness may be in a virtual device, an integration feature, a hypercall interface, or another component that translates guest requests for the host. If the escape works, control of one VM may lead to control of the physical server and every workload on it. VMware CVE-2025-22224 showed this risk: an attacker with administrator rights inside a VM could execute code as the VMX process on the host, and Broadcom reported exploitation in the wild.

A container escape can reach a similar result, but the starting point is different. Linux containers share the host kernel, so their isolation model differs from that of a VM. Namespaces limit what processes can see, cgroups control resource use, and capabilities split root privileges into smaller parts. A kernel or runtime bug can break this isolation. Copy Fail (CVE-2026-31431) is a good example of a kernel flaw. Code already running in a container could use a Linux AF_ALG crypto socket to change pages in the shared Linux kernel page cache. Because the host and other containers may read the same cached pages, the effect did not have to stay inside one container. The fix is a kernel update; Docker Engine 29.4.3 also tightened its default security profiles to reduce exposure on hosts that had not yet been patched.

Unsafe settings can also break the boundary. Privileged mode, excessive capabilities, writable host mounts, or access to the Docker socket may remove isolation without any software exploit. For instance, runc CVE-2024-21626 involved leaked file descriptors that could expose the host filesystem to a malicious image or container process.

This difference changes the investigation. A VM can often be treated like a separate computer with its own kernel, memory, and disk. A container is a group of host processes placed inside namespaces. If investigators collect only the container filesystem, they may leave the most useful process, socket, and control-plane evidence on the host.

Images and templates

A compromised golden VM image or container base image can spread through normal automation. Common weaknesses include unofficial public images, mutable tags, overprivileged build tokens, recoverable secrets in older layers, and stale templates that restore vulnerable software or forgotten accounts. Scanning might help, but it does not establish who built the artifact or whether the exact image tested and approved was the one ultimately deployed to production. Use controlled builders, provenance records, signature checks, and planned rebuilds from trusted sources.

Management tools and APIs

A stolen vCenter identity, exposed Docker API, overpowered Portainer role, or compromised backup console may give an attacker an easier route than an escape exploit. Portainer advisory GHSA-7fw3-x4r2-g7wc showed how a proxy validated one bind-mount representation but missed an equivalent API form, allowing an authenticated non-administrator with container creation privileges to reach host paths. The runtime performed a valid request after authorization had already failed in the management layer.

Administrative file-copy operations also deserve attention. Docker fixed archive and mount-handling flaws in CVE-2026-41567, CVE-2026-41568, and CVE-2026-42306. These cases required particular conditions and operator or API activity. They are a reminder to patch the daemon and record who initiated copy operations, which container was involved, the source and destination paths, and the result.

Virtual networks, storage, and backups

East-west traffic between virtual workloads may stay inside one host and bypass a physical sensor. Management, migration, storage, and workload traffic should use separate zones with filtering between them. Snapshot and memory files may contain credentials, while weak datastore permissions can expose whole virtual disks. Backup systems need broad access to recover services, which also makes them valuable to an attacker who wants to delete recovery points or reach several hosts.

Attack surface examples by layer

To sum up, the described attack vectors might be mitigated as follows:

Attack surface Initial access Possible impact Primary control
Credentials and configuration Password recovered from monitoring or an overprivileged account Direct control of several hypervisor nodes Unique vaulted credentials, segmented access, and configuration monitoring
VM escape Administrative access or code execution privileges inside a guest plus a hypervisor flaw Host process or neighboring workload compromise Patch the hypervisor and reduce risky virtual devices and guest privilege
Malicious container affecting kernel or runtime Code in a container or a malicious image Host filesystem, kernel, or shared cache impact Patch kernel and runtime, and remove privileged settings
Images and templates Compromised build input registry or golden image Repeated deployment of the compromise Immutable digests, controlled builds, provenance, and verification
Management API Stolen identity exposing endpoint or authorization gap Fleet-wide administrative actions MFA, least privilege, network restrictions, and complete API validation
Networks, storage, and backups Flat network or broad datastore and access through backups Lateral movement, data theft, encryption, and recovery loss Segmentation, least privilege, protected backups, and traffic monitoring

Conclusion

GERT cases that we presented in this article did not require an attacker to break the VM boundary. The attack path was created by an overprivileged monitoring relationship, an insecure password storage approach, a recoverable and reused root credential, broad management-network reachability, and direct SSH administration. Each element was legitimate on its own, but together they allowed one compromise to reach virtualization hosts and their workloads.

Misconfiguration should therefore receive the same operational attention as vulnerability management. Teams need to know where privileged credentials exist, which systems can use them, which network paths make them effective, and which logs will show their use. Escape flaws, unsafe images, API weaknesses, virtual network exposure, and attacks on storage or backups remain serious, but closing the known administrative route should come first.

  • ✇Cybersecurity News
  • Document Foundation Revisits the OOXML Standard Fight Do Son
    OOXML standardization history: The Document Foundation says Microsoft steered ISO approval in 2006-2008. Microsoft disputes such claims. Related Posts: Apple Presto Return Scanner Targets In-Box Fraud Come Back to Firefox Campaign Champions Web Privacy OpenSSL 4.1.0 Release Introduces Elbrus Support and DTLS 1.3 The post Document Foundation Revisits the OOXML Standard Fight appeared first on Daily CyberSecurity.
     
  • ✇Malwarebytes
  • Patient records exposed in Quest breach: What you need to know
    Quest Diagnostics has confirmed that an unauthorized party accessed a system healthcare providers use to order laboratory tests and view results, affecting personal information and patient records. Quest is a major US laboratory testing company whose services help healthcare professionals diagnose and monitor medical conditions. Those services range from routine laboratory testing to specialized testing in areas such as cancer, infectious diseases, and neurology.What happened and what was stolen
     

Patient records exposed in Quest breach: What you need to know

26 de Outubro de 2026, 08:34

Quest Diagnostics has confirmed that an unauthorized party accessed a system healthcare providers use to order laboratory tests and view results, affecting personal information and patient records.

Quest is a major US laboratory testing company whose services help healthcare professionals diagnose and monitor medical conditions. Those services range from routine laboratory testing to specialized testing in areas such as cancer, infectious diseases, and neurology.

What happened and what was stolen?

The company learned of unauthorized access to its Quanum Lab Services Manager, or LSM, on October 21. The compromised platform lets healthcare professionals order tests, access results, review historical trends, and order supplies. Quest paused access to the platform and began investigating. Quest says its core business operations remain up and running.

An investigation is ongoing. Quest has not yet published a count of affected patients or a complete list of the information accessed. It says it will notify affected patients, healthcare providers, and health plans.

The company said:

“personal information and patient records were affected.”

It confirms that health information and personally identifiable information were involved, but has not specified whether these included Social Security numbers, insurance identifiers, payment information, particular test results, or account passwords.

What patients can do now

Quest says it will send notification letters to affected patients once its investigation is complete. Those letters will describe available resources, including credit and identity monitoring. If you receive one, read it carefully and follow the instructions. You can also check the FAQs posted in Quest’s breach notice for updates.


Someone’s got their eye on your personal information. Make sure it’s us.


A breach does not automatically mean someone has misused your information, but you can take these precautions while you wait for more details:

  • Verify unexpected messages independently. Don’t let a message about the breach rush you into clicking a link, sharing sensitive information, or making a payment. Go to Quest’s official website yourself or use contact details you already trust.
  • Review medical bills and insurance statements. Look for appointments, tests, prescriptions, or services you did not receive. The Federal Trade Commission (FTC) identifies unfamiliar medical bills and unexpected items on an Explanation of Benefits statement, which explains how your insurer processed a claim, as warning signs of medical identity theft. Report discrepancies to your healthcare provider and your insurer.
  • Review your credit reports. Look for unfamiliar accounts or debts and dispute errors. Free reports are available through AnnualCreditReport.com.
  • Act if you find signs of identity theft. Visit IdentityTheft.gov for a recovery plan. If someone has received care in your name, ask the providers involved for copies of your medical records and request corrections in writing.

Medical identity theft is not just a financial problem; it can also affect your care. Someone using your identity to obtain treatment or submit insurance claims could introduce incorrect information into your health records. Checking medical statements and reporting anything unfamiliar can help you catch that misuse.


Let’s face it, an incognito window can only do so much. 
 
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance. 

Open-Source AI Agents Breach 27 Companies, Steal 600,000 Credit Card Records

Gambit Security found AI agents breached 27 companies, stole 600,000 credit card records and installed payment skimmers across compromised retail sites.
  • ✇Firewall Daily – The Cyber Express
  • India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering Samiksha Jain
    The Department of Telecommunications (DoT) Madhya Pradesh, India LSA has cautioned citizens against fraudulent SIM cards, misuse of telecom identifiers and tampering with IMEI numbers, warning that such violations can carry serious legal consequences under India’s Telecommunications Act, 2023. The advisory follows recent cybercrime investigations that uncovered instances of unauthorized SIM activation. In one case, a Point of Sale (PoS) agent in Chhattisgarh was found to have illegally
     

India’s DoT Warns Citizens Over SIM Fraud and IMEI Tampering

22 de Setembro de 2026, 03:56

Fraudulent SIM cards

The Department of Telecommunications (DoT) Madhya Pradesh, India LSA has cautioned citizens against fraudulent SIM cards, misuse of telecom identifiers and tampering with IMEI numbers, warning that such violations can carry serious legal consequences under India’s Telecommunications Act, 2023.

The advisory follows recent cybercrime investigations that uncovered instances of unauthorized SIM activation. In one case, a Point of Sale (PoS) agent in Chhattisgarh was found to have illegally activated 25 mobile connections using citizens’ identification documents without their knowledge or consent.

Following the discovery, the DoT and telecom service providers blacklisted the concerned PoS agent, preventing it from issuing mobile connections in the future.

DoT Investigates Fraudulent SIM Cards and Mobile Connections

The 25 mobile connections linked to the case were examined through the Digital Intelligence Platform, or DIP, operated by the DoT. Connections identified as suspicious were subjected to re-verification.

Numbers that failed the re-verification process were subsequently deactivated.

The action highlights concerns around SIM card fraud, particularly where mobile connections are obtained or activated using another person’s identity documents. The DoT has also cautioned citizens against transferring SIM cards registered in their names, as legal liability may extend to the original subscriber if the connection is later misused.

Telecommunications Act 2023 Sets Penalties

The DoT said fraudulent issuance of SIM cards, misuse of telecom identifiers and tampering with IMEI numbers are punishable offences under the Telecommunications Act 2023.

Such violations may attract imprisonment of up to three years and fines of up to ₹50 lakh.

The department has urged citizens to avoid obtaining SIM cards through fake documents, fraud, cheating or impersonation. It has also warned against procuring SIM cards in their own names and subsequently transferring, renting, loaning or otherwise providing them to others for misuse in cyber fraud or other unlawful activities.

Citizens have also been advised not to use devices such as modems, modules or SIM Boxes with configurable or tampered IMEI numbers.

IMEI Numbers and Telecom Identifiers Under Scrutiny

The DoT has highlighted the misuse of telecommunications identifiers, including the International Mobile Equipment Identity, or IMEI numbers, as a security concern.

Citizens have been cautioned against using mobile applications, websites or other methods to modify Calling Line Identity (CLI) or other telecommunications identifiers. The department has also warned against using devices with tampered IMEI numbers.

According to the advisory, misuse of SIMs and telecom identifiers can affect citizen safety and pose risks to the security and integrity of telecommunications networks.

Sanchar Saathi Enables SIM and Device Checks

The DoT has advised citizens to regularly use Sanchar Saathi to verify mobile connections issued in their names and block numbers that are unnecessary or not genuinely theirs.

The Sanchar Saathi platform also provides a facility called “Check Genuineness of Your Mobile handset,” which allows users to verify IMEI numbers and associated device information. The service can provide details including the handset’s brand name, model name and manufacturer information.

Citizens can access the Sanchar Saathi services through its portal or mobile application to check and secure their mobile connections and devices.

The DoT has urged citizens to remain vigilant and avoid sharing SIM cards registered in their names, particularly where the connection could later be used for cyber fraud or other unlawful activities.

  • ✇Malwarebytes
  • Loyalty points fraud is funding hacker holidays (Lock and Code S07E18)
    This week on the Lock and Code podcast… Crooks are taking a holiday. They’re counting on you to fund it. For decades, cybercriminals have stolen roughly the same types of data. Biographical and personal details—like Social Security numbers, birthdates, addresses, and phone numbers—can be stolen to commit identity fraud. Credit card numbers, expiration dates, and CVC codes can be stolen to make fraudulent purchases. Usernames and passwords can, in the wrong hands, let a cybercriminal impers
     

Loyalty points fraud is funding hacker holidays (Lock and Code S07E18)

7 de Setembro de 2026, 15:23

This week on the Lock and Code podcast…

Crooks are taking a holiday. They’re counting on you to fund it.

For decades, cybercriminals have stolen roughly the same types of data. Biographical and personal details—like Social Security numbers, birthdates, addresses, and phone numbers—can be stolen to commit identity fraud. Credit card numbers, expiration dates, and CVC codes can be stolen to make fraudulent purchases. Usernames and passwords can, in the wrong hands, let a cybercriminal impersonate someone, steal sensitive photographs to later use for extortion, or abuse a reputation.

All of these attack models seek to turn sensitive or important data into currency. But an emerging form of digital fraud is targeting data that, when used strategically, practically is currency: Loyalty points.

Loyalty points programs are run by nearly every type of consumer-facing business today, from hotels to airlines to grocery stores to donut shops. As repeat customers accrue these points, they can exchange them for discounted prices on future purchases, cutting the costs of hotel stays, flights, rental cars, and even entire vacations.

But the value stored within these loyalty points makes them a high target for cybercrime, said Kim Sutherland, Global Head of Fraud and Identity at LexisNexis® Risk Solutions.

“Most loyalty currency is worth about one cent per point, and then there are premium programs that can be worth more than that,” Sutherland said, explaining that 100,000 airlines points, for example, can be worth $1,000 in the US. “Why criminals care so much about this is because most of us are not paying attention to our loyalty programs the same way we would our bank account.”

But diligence is much needed here, Sutherland said, noting that one Chicago teacher only learned that 240,000 of his airlines points had been stolen because he received a basic confirmation email about their use. In another example, a man’s airline miles were stolen and fraudulently used to book rental cars in New York and Memphis.

Today, on the Lock and Code podcast with host David Ruiz, we speak with Sutherland about loyalty points theft— how it happens, what companies are doing to protect customers, and what people can do to stay safe.

“Some of us don’t even know how to access those points, right? Or we don’t even know we’re accumulating them, but the fraudsters do.”

Tune in today to listen to the full conversation.

Show notes and credits:

Intro Music: “Spellbound” by Kevin MacLeod (incompetech.com)
Licensed under Creative Commons: By Attribution 4.0 License
http://creativecommons.org/licenses/by/4.0/
Outro Music: “Good God” by Wowa (unminus.com)


Listen up—Malwarebytes doesn’t just talk cybersecurity, we provide it.

Protect yourself from online attacks that threaten your identity, your files, your system, and your financial well-being with our exclusive offer for Malwarebytes Premium for Lock and Code listeners.

  • ✇Firewall Daily – The Cyber Express
  • US Puts $10 Million Bounty on Alleged Iranian Cyber Chief Samiksha Jain
    The U.S. State Department has posted a $10 million reward for Amir Yaryab, a senior Iranian official accused of leading the Islamic Revolutionary Guard Corps Cyber-Electronic Command (IRGC-CEC) Cyber Operations Command and directing multiple hacking groups targeting critical infrastructure across the United States, Europe and the Middle East. According to the Rewards for Justice program, Yaryab allegedly oversees cyber operations conducted by IRGC-CEC-affiliated groups including CyberAv3ngers
     

US Puts $10 Million Bounty on Alleged Iranian Cyber Chief

7 de Setembro de 2026, 02:51

$10 Million Reward for Amir Yaryab

The U.S. State Department has posted a $10 million reward for Amir Yaryab, a senior Iranian official accused of leading the Islamic Revolutionary Guard Corps Cyber-Electronic Command (IRGC-CEC) Cyber Operations Command and directing multiple hacking groups targeting critical infrastructure across the United States, Europe and the Middle East. According to the Rewards for Justice program, Yaryab allegedly oversees cyber operations conducted by IRGC-CEC-affiliated groups including CyberAv3ngers, Dadeh Afzar Arman (DAA) and Mehrsam Andisheh Saz Nik (MASN). U.S. officials accuse these groups of using malware and conducting cyber and cyber-enabled information operations against civilian infrastructure worldwide.

$10 Million Reward for Amir Yaryab

The $10 million reward for Amir Yaryab seeks information leading to his identification or location. The offer applies to individuals acting at the direction or under the control of a foreign government who participate in malicious cyber activities against U.S. critical infrastructure in violation of the Computer Fraud and Abuse Act. [caption id="attachment_113961" align="aligncenter" width="600"]$10 million reward for Amir Yaryab Image Source: https://rewardsforjustice.net/[/caption] Yaryab is also accused of directing Shahid Hemmat and Shahid Shushtari, two groups linked to cyberattacks against U.S. organizations. The sectors allegedly targeted include defense, news, shipping, travel, energy, financial services and telecommunications. The six Iranian officials named in the advisory are linked to Iran's Islamic Revolutionary Guard Corps and its Cyber-Electronic Command.

Iranian Cyberattacks Target PLCs

The allegations also involve attacks against programmable logic controllers (PLCs), highlighting concerns around Iranian cyberattacks targeting industrial systems rather than focusing only on data theft. U.S. officials said Iranian-linked hackers compromised industrial control systems, specifically targeting the Vision series of PLCs manufactured by Israel-based Unitronics. These devices are used across water and wastewater, energy, food and beverage, manufacturing and healthcare sectors. The attackers exploited default credentials on the devices and left anti-Israel messages. Some of the compromises reportedly rendered the PLCs inoperative. The CyberAv3ngers group, which is linked to the IRGC-CEC, claimed responsibility for attacks against Unitronics Vision PLCs in October 2023. Beginning in November 2023, the group compromised default credentials in PLCs across the United States and left messages on the devices' digital screens.

CyberAv3ngers Attacks Critical Infrastructure

CyberAv3ngers has also claimed responsibility for attacks affecting other infrastructure. In October 2023, the group claimed it had breached ORPAK Systems, a provider of gas station solutions in Israel. The group said it had obtained the company's database and intended to publish it through its Telegram channel. The attack was reported to have disconnected 200 gasoline pumps from the system in the occupied Palestinian territories. In December 2023, CyberAv3ngers also claimed to possess and sell 1TB of data allegedly linked to Israel's electricity infrastructure. The group advertised the dataset for 5 Bitcoin, with an initial 100GB portion also offered at the same price.

U.S. Agencies Warn of PLC Cyberattacks

Concerns over critical infrastructure attacks involving PLCs continued into 2026. A joint advisory issued on April 7 by the FBI, CISA, NSA and other agencies warned that Iran-linked threat actors were actively exploiting internet-facing PLCs. The advisory said several organizations had experienced operational disruptions and financial losses after attackers interfered with industrial processes. The developments come amid broader U.S. actions against Iranian-linked cyber activity. The Justice Department accused Iran-connected hackers of breaching employee email accounts associated with the Department of Labor, the Federal Energy Regulatory Commission and multiple United Nations organizations. The Treasury Department also sanctioned Iranian nationals over cyberattacks targeting critical infrastructure. The State Department's reward offer places Amir Yaryab and the alleged activities of IRGC-CEC-linked groups at the center of the U.S. effort to identify individuals responsible for malicious cyber activity targeting critical infrastructure.
  • ✇Krebs on Security
  • FBI Probes Service Selling 153M+ Drivers Licenses BrianKrebs
    A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company based in Louisiana. KrebsOnSecurity also has learned that the New Orleans field office of the Federal Bureau of Investigation (FBI) today
     

FBI Probes Service Selling 153M+ Drivers Licenses

1 de Setembro de 2026, 19:40

A new identity theft service launched on the dark web this week is selling digital scans of more than 153 million drivers licenses from people in the United States and Canada. Based on interviews with individuals whose licenses are available for purchase on this service, it appears to be siphoning images collected by a widely-used identity verification company based in Louisiana. KrebsOnSecurity also has learned that the New Orleans field office of the Federal Bureau of Investigation (FBI) today launched an official inquiry into the source of the images.

A record available at this identity theft service that includes the drivers license for U.S. Defense Secretary Pete Hegseth, one of several high-ranking U.S. government officials whose drivers licenses can be found for sale.

On Monday, Aug. 31, a source alerted KrebsOnSecurity to a service advertised by a new user on the Russian cybercrime forum Exploit, offering access to digital scans of identity documents on more than 170 million people in North America. The source brought it to my attention because the proprietor of this identity theft service offered my Virginia drivers license as a free sample in their initial sales thread on Exploit.

The service, dubbed Nexus, claims to have more than 153 million drivers licenses for people in the United States and Canada, as well as more than 10 million identification cards; more than three million travel documents and/or international IDs; and at least 579,000 medical cards.

A quick look around Nexus finds they are likely not exaggerating about that 153 million number: Running a blank search in Nexus (with no search parameters entered) returns approximately 11.5 million pages of results, with roughly 15 results displayed per page. It includes documents from people in both Canada and the United States, but the bulk of these records are on Americans: searching for just Canadian drivers licenses returns approximately 1.1 million results, with the largest concentration from Ontario (473,673 records).

Curiously, the identity records include not only drivers licenses but also marijuana dispensary cards. Some of the records list their “source” as “CDL,” presumably short for “commercial drivers license.” Other records carry the source notation of “CAC,” which may refer to Common Access Cards, government issued identity cards that grant physical access to government buildings and secure rooms.

The people behind Nexus claim the license images are coming from an active breach at “a major identity verification company” whose customers include multiple Fortune 500 companies.

The record totals listed by the Nexus identity theft service. The number of drivers license records increased by nearly 400,000 in the span of just 24 hours.

“We have been continuously exfiltrating new data for over a year into our private database,” the service enthused in its introductory post on Exploit. “Records are available to preview before purchase with pertinent information redacted. Customer photos are displayed if available.”

Indeed, over the past 24 hours, the number of drivers license records listed as available in Nexus has increased by nearly 400,000, suggesting that freshly stolen license data is being harvested and uploaded to this service on a semi-regular basis.

The record featuring my drivers license includes six image files: three pairs of photos of the license’s front and back, a basic image scan, as well as infrared and ultraviolet versions of the same images. A date and timestamp is appended to each image file, and the timestamp on my license scan corresponds to a date in June 2025 when I took a flight to the midwest United States to attend a family funeral.

Some of the 153 million+ license scans — including mine — feature six image files with date and timestamps appended to the filenames. Not all records include photos, and some that do feature photos do not display the associated filenames.

Intent on discovering the source of this data, KrebsOnSecurity asked more than a dozen friends and family members for permission to search for their licenses in this service. Each person whose license could be found (nine of them) confirmed having traveled on or very close to the dates in the timestamps attached to their images. It is unclear what timezone these timestamps are in, but from reviewing car rental records shared by several people who helped with this research, it appears the timezone is set to Greenwich Mean Time (GMT).

At first, I thought the source of the data might have something to do with airports. However, that theory went out the window when it became apparent there were no passports in this data set. Also, only some of those who helped with this research said they showed their drivers license at the airport on the day of their travel. One person whose license was in Nexus hadn’t flown at all recently, but was renting a car from Hertz for several months around the date of their timestamp.

Two of those who agreed to help are federal employees who said they shared other forms of government identification when passing through airport security. However, those individuals each said they shared their state-issued drivers licenses later that day when renting vehicles at their respective destinations, and that both rented their cars from Hertz.

After finding a note in my calendar for the day of my June 2025 flight reminding me to bring my passport, I remembered that I also never actually shared my drivers license when I went through security at Reagan National Airport on that day because I did not yet have a Real ID, a security-enhanced drivers license that is now required by the Transportation Security Administration (TSA) for all domestic travel. Instead, I showed the TSA agent my government-issued U.S. passport.

Here’s where it gets interesting: I was able to find my mother’s drivers license in this service as well, and the timestamps for her images are just a few seconds apart from mine. That’s notable because we both handed our licenses to the Hertz rental car representative at the same time.

According to my mom, the only place she gave her drivers license to that day was the rental car company, and if memory serves that is also true for me. I don’t recall if the rental car representative inserted our licenses into any kind of machine, but I remember they held onto them for several minutes behind the counter while we were signing various forms. KrebsOnSecurity sought comment from Hertz and will update this story in the event they reply.

Zach Edwards is a well-known security and privacy researcher who recently launched a service called DecryptAds to help people better understand how online advertisers are tracking them. A scan of Edwards’s drivers license is available for purchase on this identity theft service, and Edwards said the timestamp on his record corresponds to the middle of a trip last month to Las Vegas for the annual DEFCON security conference.

Edwards told KrebsOnSecurity that although he did not rent a car in Vegas, he did hand over his license at the TSA checkpoint, at a marijuana dispensary in Vegas, and at his hotel (the Aria). But he said the only one of those three that for sure scanned his ID in some kind of device was the dispensary.

To enter Planet13’s weed dispensary in Las Vegas, one must pass through a red telephone booth. Image: Zach Edwards.

Edwards said the dispensary he visited that day was Planet13, a multi-state chain with stores in California, Florida, Illinois and Nevada. In 2022, the New Orleans-based identity provider idscan.net published a press release announcing an exclusive identity verification agreement with Planet13’s dispensaries nationally. IDScan says it processes ID verification for more than 1,000 marijuana dispensaries in 19 U.S. states.

The “trust” page of idscan.net states that the company provides identity verification services for numerous big brands, including Hertz, Target, Fedex, Motorola Solutions, the financial services giant Jack Henry, and Caesars Entertainment. And as idscan.net’s own documentation states, the technology scans IDs with both infrared and ultraviolet light. Idscan.net says the company’s systems and technology perform more than 21 million verifications monthly, at more than 20,000 locations around the world.

Image: idscan.net.

Contacted by KrebsOnSecurity, idscan.net said it was investigating the matter, but the company has not yet shared an official statement or a substantive reply to specific questions sent via email.

“At this point I’m not able to share any additional information, but the updates you have provided have been welcome, and helpful to our team’s investigation,” wrote Jillian Kossman, a marketing and operations leader at idscan.net.

During the course of my research for this story, word got around to the FBI that I was poking at the apparent source of this new identity theft service’s data. Probably they were tipped off when I shared with a trusted source that Nexus also is selling the drivers license information for the assistant director of the FBI (I did not find FBI Director Kash Patel’s license in Nexus).

Earlier this afternoon, I was added to a conference call with a half-dozen FBI agents, including senior leaders from the agency’s cyber division. During that call, the FBI shared that earlier today their New Orleans field office opened an official investigation into an apparent breach involving idscan.net.

Edwards said that as more in-person and online experiences require sharing drivers licenses, vendors who collect this sensitive data need to be held to a higher standard.

“This episode should further strengthen the resolve for people who are fighting back against online ID schemes which are requiring countless providers to ask for drivers licenses in order to access services under the guise of protecting kids,” Edwards told KrebsOnSecurity. “These systems are putting sensitive data into more and more 3rd party vendors, and we don’t have nearly the oversight to ensure they are safe.”

Larry Baldwin is principal intelligence researcher at the cybersecurity firm Cybera. Baldwin said a front and back scan of his drivers license available at Nexus contains timestamps that correspond to the date of a car rental from Hertz on a recent vacation.

Baldwin said the Nexus identity theft service presents multiple serious security and privacy threats, noting that state-issued drivers licenses are commonly used as proof of one’s identity when opening new lines of credit. Baldwin said the service could also dangerously expose many people who do not wish to be found but who cannot meaningfully change their appearance (or at least not enough to fool today’s AI-based image matching tools).

This category of people, he said, includes those fleeing domestic violence, and even people who have been assigned a whole new life and identity as part of the federal government’s witness protection program, which is generally reserved for criminal defendants in racketeering and conspiracy investigations who agree to cooperate with federal authorities.

“Just when it seems like we’re making some headway in improving authentication controls through drivers license verification systems, this happens and the very thing those improvements are dependent on are compromised,” Baldwin said.

Update, Sept. 8: IDscan.net published a brief notice saying it has “determined that an unauthorized third party may have accessed and/or copied certain customer information, including full names and drivers license or other government-issued identification numbers.” The statement said IDscan.net is notifying affected individuals and offering credit protection services.

Update, Sept. 2, 6:05 p.m. ET: A spokesperson for Caesars Entertainment said Caesars has not been a client of IDScan.net and has not used VeriScan since February 2025, despite IDScan.net listing them as a client on their website. That person said Caesars had no active VeriScan accounts at the time of the incident and did not authorize IDScan.net to retain data from its accounts, and that IDScan.net said the incident should have no impact on Caesars Entertainment.

Update, 8:56 p.m. ET: Shortly after this story was published, the Nexus identity theft service website vanished from the darkweb, replacing its login page with a plain text message that reads, “This service is no longer available.”

This is a potentially fast-moving story. Any changes or updates will be noted here along with a timestamp.

The Password Notebook Is Back — but Is It Actually Safer?

25 de Agosto de 2026, 15:18

Password notebooks are making an unexpected comeback as infostealers and browser attacks revive debate over the safest way to store credentials.

The post The Password Notebook Is Back — but Is It Actually Safer? appeared first on TechRepublic.

  • ✇Krebs on Security
  • Who’s Tracking You? Use This New Service to Find Out BrianKrebs
    It can be daunting to determine who’s responsible for showing ads on the websites we visit, or who’s harvesting data from the mobile apps we use every day. That information is already semi-public, but it is not easily parsed and traditionally much of it has remained walled away in the hands of large advertising platforms. Not anymore: A powerful and free new service called DecryptAds scrapes and correlates this adtech data and makes it simple to quickly learn a great deal about the entities that
     

Who’s Tracking You? Use This New Service to Find Out

14 de Agosto de 2026, 08:24

It can be daunting to determine who’s responsible for showing ads on the websites we visit, or who’s harvesting data from the mobile apps we use every day. That information is already semi-public, but it is not easily parsed and traditionally much of it has remained walled away in the hands of large advertising platforms. Not anymore: A powerful and free new service called DecryptAds scrapes and correlates this adtech data and makes it simple to quickly learn a great deal about the entities that are tracking you.

A Decryptads summary of the advertising partnerships declared by espn.com.

The newly launched decryptads.com says it is constantly scraping the files that websites and apps make publicly available to disclose the companies that are permitted to run ads or collect user data. These files include:

–ads.txt: all of the adtech companies and data brokers that may run ads or harvest data from the site;
–app-ads.txt: entities that can harvest data from or display ads on mobile and smart TV apps;
–buyers.json/sellers.json: the entities buying, selling or reselling ad inventory for a given site or app.

Zach Edwards is chief research officer for DecryptAds and a threat researcher at the security company Infoblox. Edwards said he and two other founders decided the service was needed because the adtech data in these files is generally only useful when it can be cross-referenced to build a more complete picture of the advertising ecosystem for each website or app.

“It’s an adtech tool but we’re trying to approach adtech from a security perspective,” Edwards said. “It’s really built for a lot of privacy and security use cases that have been dramatically underserved.”

Those use cases, he said, include tracking down the source of malicious ads that try to foist malware on targeted users, identifying ad networks located in adversarial nations, and detecting the fast growing swarms of AI-generated slop websites and apps. And as decryptads.com demonstrates, these potential security and privacy threats are near impossible to detect just by viewing a single apps.txt or app-ads.txt file.

“Supply-chain integrity issues rarely live in a single file,” the site explains. “They show up as broken cross-references between ads.txt, app-ads.txt, and sellers.json files; as cloned declaration sets across unrelated domains; as seller removals that only make sense when viewed across exchanges; and even as supply paths in bid logs that never actually appear in any given publisher’s authorized-seller list.”

A search in DecryptAds for the hugely popular sports network espn.com reveals 143 ad partners and 19 registered data broker domains are listed within its ads.txt and app-ads.txt files. That data broker information is gradually becoming available because four states — California, Oregon, Texas and Vermont — have recently passed laws requiring data brokers to register if they buy or sell data on consumers from those states. DecryptAds reports that almost half of those data brokers are collecting geolocation data from espn.com visitors who aren’t blocking ads, while another three disclose that they collect device fingerprints and sensitive personal information.

A visual representation of the complex ad supply chain declared by espn.com. Image: decryptads.com.

HIGH-RISK AD PARTNERS

DecryptAds also makes it easy to learn the beneficiaries and national origins of the advertising firms lurking in apps and websites, displaying a conspicuous warning when adtech partners of an app or website are based in “geo-risk” areas like China and Russia, or in countries with strong financial and political ties to both — such as Cyprus and the United Arab Emirates (UAE).

According to DecryptAds, espn.com works with four different advertising entities that are based in either Russia, China or the UAE, including the adtech firm Between Digital, which lists a New York address. However, the dossier on Between Digital flags them as a Russian firm, showing that their publisher offers (PDF) are processed through Alfa Bank, Russia’s largest private commercial bank and one of several financial institutions placed under U.S. sanctions in 2022 after Russia invaded Ukraine. KrebsOnSecurity sought comment from both Between Digital and the company’s founder, and will update this story in the event that either replies.

A search for several top U.S. military news websites — including armytimes.com, airforcetimes.com, defensenews.com, navytimes.com, marinecorpstimes.com and federaltimes.com — shows they all allow Between Digital to serve ads and track users, as well as two entities in the UAE and another in the ownership secrecy haven of Panama. DecryptAds reports that Between Digital is collecting ad data on approximately 55,000 partner websites.

The “Geo Risk” section of decryptads.com.

Pivoting on Between Digital’s app-ads.txt file reveals hundreds of domains featuring simple web-based games that are frequently interrupted by ads. Edwards said Between Digital’s own declarations show the company is listed as both a publisher and a reseller on approximately two-thirds of their portfolio.

“It means they are basically playing both sides of the bidding equation, which creates opportunities to direct client spend at your owned and operated properties or client infrastructure, essentially creating opportunities for conflicts of interest,” Edwards told KrebsOnSecurity. “The problem we have right now is that for years we’ve had almost no one policing these ads.txt and app-ads.txt files.”

The Opera Web browser remains quite popular, and probably many users are unaware that since 2016 it has been majority owned and controlled by the Chinese company Kunlun Tech (the operational headquarters of Opera remain in Oslo, Norway).

Opera.com’s profile at DecryptAds identifies 27 registered data brokers collecting information, including 15 adtech partners in the UAE, six in China, three in Cyprus, two in Russia and one each in Hong Kong and Ukraine. DecryptAds makes clear, however, that these companies represent just seven percent of the adtech partners specified in Opera.com’s ads.txt and app-ads.txt files.

LEGAL DOSSIERS

One feature of DecryptAds that sent this author down multiple hours-long research rabbit holes is its Legal Dossier lookup, which takes several minutes for each search but eventually churns out oodles of useful information about who owns a particular domain or app, when it was registered, and any aliases or relationships it may have to adtech companies and other websites or apps.

For example, last month KrebsOnSecurity wrote about researchers from Bitsight who found that an extremely popular line of TV streaming sticks called H96 quietly rent out each user’s Internet connection to strangers. Bitsight also discovered that when these devices aren’t being used to stream pirated video content, they are spoofing themselves as mobile phones clicking ads on AI-generated slop websites.

Bitsight concluded that the same Chinese company that made several of the malicious apps common to all of these H96 streaming sticks — the Fengwo Group — also also ran the network of ads and AI slop websites being clicked on by tens of thousands of these devices that are pretending to be mobile phones.

Examples of ad landing pages linked to the Fengwo Group. These sites were designed to show ads only to H96 devices that were spoofing their device type as mobile phones. Image: Bitsight.

A DecryptAds legal dossier on the (now dormant) Fengwo Group domain name for the AI slop website pictured on the left in the screenshot above (medicalbeautyhub dot com) shows it shares a seller ID (1674071) with a gaming website — giacoloredstones[.]com — which features yet another seller ID (103488000).

Pivoting on that latter seller ID reveals hundreds of active websites within Russia’s Yandex ad system featuring extremely low-quality games or simple utilities that pepper visitors with ads.

QUIET REMOVALS

Edwards said that when advertising networks suspect a given advertiser is engaged in unauthentic clicks or displaying malicious ads, very often those networks will quietly remove the offender from their list of approved partners without letting anyone else know about their suspicions.

This practice, he said, makes it easier for dodgy adtech firms to avoid accountability and continue victimizing others. To address that visibility gap, DecryptAds features a quiet removals feed that records and correlates all of the sellers.json removals across ad exchanges for the same seller domain or name.

A screenshot of the Quiet Removals Feed at decryptads.com.

“The way the adtech industry works, someone will write a report about ad fraud and only share it with their own clients and they won’t make it public,” Edwards said. “The ban is just removing them from the sellers.json file, but they told nobody. One day it was there, the next it was gone. So if you’re trying to navigate who is suspicious, that’s usually tough to do because there are a lot of adtech companies removing things all at once.”

MALVERTISING AND AI SLOP

Malvertising, the term given to the practice of inserting malicious ads that foist malware or redirect visitors to phishing pages, remains an all-too-frequent occurrence in the modern adtech industry. But Edwards said these malicious ads are far more commonly found now on newly generated AI slop websites than on high traffic destinations that typically employ a variety of technologies and third party tools to quickly flag bad ads.

“None of these slop AI content farms are paying for that kind of protection,” he said. “They’re just signing up the lowest quality partners, and it essentially becomes a greased rail to target the users of those sites with malicious ads. Most malvertising attacks don’t happen on espn.com or huffpost.com, but rather [on] some lower quality content farm and someone just went there because it came up in a search.”

Edwards said the AI slop websites are populated with machine-generated blog posts and images, and cover a wide array of themes from home improvement and decorating to food recipes, hunting, cars and consumer technology. He said organizations that get hit with malicious ads are often at a loss for what to do next, unaware that in most cases the answer is one of the entities listed inside the website’s ads.txt or app-ads.txt file.

“A lot of serious organizations are starting to understand that if we’re not breaking down this ad data, we’re not going to know who’s targeting government people with zero-click payloads on an almost daily basis,” he said.

Edwards maintains that truly getting a handle on the malvertising and AI slop problems will require more data-sharing by the major ad networks. Specifically, he says those platforms do not broadly share what’s known as the “supply chain object” or SCO, structured data attached to each advertising bid request that lets buyers see every seller, reseller and intermediary involved in passing an ad impression from the publisher to the final buyer.

“That SCO tells you who sold it or resold it, and who was the final entity that bought the impression that served that malware payload,” Edwards explained. “You may see the malicious zero-click redirection, but without the supply chain object — which is only served server side — you won’t know who targeted your people with malware and won’t have a way to try and prevent it properly. But if we can encourage the adtech industry to expose that SCO, it will get easier to find the culprit behind any one bad ad.”

DecryptAds also offers an application programming interface (API) that allows researchers to automate queries and integrate the site’s functionality into popular AI platforms.

WHAT CAN YOU DO?

The only sane reaction to the examples described above is to block all online ads outright. This approach is broadly endorsed by security experts because it also makes it more difficult for adtech firms and data brokers to build detailed profiles on you and track your movements around the web and in the real world.

However, much depends on how you normally prefer to browse the Internet, and how much trust you place in third party browser plugins and extensions. For those primarily surfing via a regular desktop or laptop Web browser, uBlock Origin Lite is an excellent free and well-maintained open source option. uBlock Origin also should work with mobile browsers like Firefox, but apparently only on Android-based devices.

Adblock Plus is a decent option for iPhone and iPad users. For power users, Adblock and uBlock Origin both support custom blocking rules from easylist.to, which publishes a frequently updated list that removes most advertisements from webpages.

The well established browser extension NoScript blocks all non-approved Javascript code, and it generally does a fine job blocking most ads from loading. However, script blockers like NoScript may not be suitable for average users who don’t enjoy constantly having to referee which scripts should be allowed to load so that each site displays properly.

More technically inclined/adventuresome readers should strongly consider a hardware approach to blocking ads at the local network level, because that is easily the cheapest, most secure and scalable way to do it. A tiny, low-cost and broadly available computer known as a Raspberry Pi can be turned into a powerful ad blocker for all devices on a local network when fitted with a microSD memory card and a free program called Pi-hole. Once you’ve set it up properly and changed your router’s network settings to use the Pi-hole’s DNS sinkhole and DHCP servers, it should prevent ads from displaying on any devices connected to that network.

Bear in mind that ad blockers often do little to block ads and/or tracking that occurs from within mobile apps that users have chosen to install on their devices. Many websites now push users to install a mobile app, supposedly in order to more fully access and enjoy the site’s services and content. But in my experience, they’re not doing this because the user experience is somehow way better on the app (as LinkedIn tries to convince us non-app users several times a week via email). On the contrary, I find most mobile apps to be horribly designed, annoying, and/or completely unnecessary, and when given the option I will almost always choose to interact with a website or service directly in a Web browser.

No, the cold truth is that big web destinations tend to get pushy with their apps because they make it easier for these companies to keep you on their platforms longer and to collect (and in many cases resell) far more precise data about who, what and where their users are. Also, companies pushing customers the hardest to install mobile apps always seem to liberally opt everyone in to having their data used to train large language models these days. So be cautious about the apps you install on your mobile devices (including any smart TVs!), and poke around their listings at DecryptAds if you want to learn more about their privacy practices and any relationships they may have to adtech firms.

  • ✇@BushidoToken Threat Intel
  • UK Cybercrime Journal: Evolution of Courier Fraud Campaigns BushidoToken
    What HappenedNew data published by the City of London Police in June 2026 reveals that courier fraud losses exceeded £21 million in 2025, with individuals aged over 70 being heavily targeted. The highest concentration of these offenses was recorded in London and the Home Counties.Cybercriminals and fraud syndicates are actively evolving their operational tactics, increasingly pivoting to messaging platforms like WhatsApp to contact their victims and remotely paying for third-party courier servic
     

UK Cybercrime Journal: Evolution of Courier Fraud Campaigns

12 de Agosto de 2026, 05:00

What Happened

  • New data published by the City of London Police in June 2026 reveals that courier fraud losses exceeded £21 million in 2025, with individuals aged over 70 being heavily targeted. The highest concentration of these offenses was recorded in London and the Home Counties.
  • Cybercriminals and fraud syndicates are actively evolving their operational tactics, increasingly pivoting to messaging platforms like WhatsApp to contact their victims and remotely paying for third-party courier services to facilitate physical collections.
  • UK law enforcement also highlighted a dangerous shift in 2025 toward high-value physical goods. Victims are being systematically manipulated into visiting multiple jewellers over an extended period to purchase gold and expensive jewellery, which they then hand directly to fraud couriers.

Recent operational crackdowns by UK Regional Organised Crime Units (ROCUs) showcase the nationwide scale of these networks:

  • North West ROCU Operations (July 2026): Police executed coordinated search warrants in Huddersfield and Manchester, arresting two men (aged 21 and 25) on suspicion of Conspiracy to Defraud and Money Laundering. In this specific series, the suspects impersonated bank fraud departments, convinced a victim her card was compromised, sent a courier to collect it, and immediately exploit the physical card to make numerous fraudulent transactions.
  • North East ROCU (NEROCU) Sentencing (June 2026): A complex, cross-country courier fraud operation spanning March to May 2022 concluded with a prison sentence for a primary operative. The network targeted 14 separate victims, convincing them to hand over physical bank cards and PIN numbers under the guise of an internal "investigation" by their bank's fraud department. The group scammed a total of £56,000, which was then rapidly laundered through the high street purchase of smartphones, designer clothing, and luxury jewellery.

Analyst Comment

Courier fraud is effectively a hybrid cyber-physical social engineering campaign. While the final phase relies on a physical courier arriving at a victim’s doorstep, the initial approach relies heavily on psychological manipulation and email, message, or phone call-based deception.

This type of fraud is notable as it follows a structured cybercriminal playbook that bypasses detection systems and takes advantage of the vulnerable in society. The victim is instructed to bypass normal banking security controls by withdrawing cash, disclosing sensitive credentials (like PINs), or purchasing high-value physical commodities like gold or luxury jewellery. This makes it difficult to proactively detect and prevent.

The other concerning factor is the couriers themselves. According to reports, they can be an unwitting third-party courier service that is paid to go to the victim's home to collect the assets. Online services enable cybercriminals to organise these pickups remotely, lowering their risk of being caught.

The £21 million sizeable loss metric from 2025 shows how profitable this low-tech, high manipulation vector remains. The recent shift to targeting gold and luxury jewellery is a deliberate evasion tactic against traditional anti-money laundering (AML) and banking fraud detection algorithms. While banks have grown adept at flagging unusual rapid bank transfers, they cannot easily stop an account holder from physically withdrawing funds or using a card over several days at different brick-and-mortar luxury retailers. This tactic serves as a highly liquid physical laundering pipeline for these syndicates that remains a challenge to prevent.

Defensive Takeaways

  • Implement Bank Transfer and Purchase Outlier Alerts: Financial institutions can focus on further behavioural monitoring for elderly demographics, looking specifically for sudden, consecutive high-value transactions at physical luxury retail or jewellery establishments and flag patterns on unusual activity for review.
  • Public Awareness on Cross-Media Scams: Security awareness campaigns must make it clear that legitimate institutions, specifically the Police and Banking Fraud teams, will never send a courier to a residential address to collect cash, PIN numbers, bank cards, or purchased items.
  • Vetting of Courier Logistics: Commercial courier services are increasingly being abused as infrastructure by these threat groups. Logistics firms must implement logging and analysis systems to detect unusual residential pickups booked via suspicious accounts and forged identities.

Relevant Sources

  1. https://www.cityoflondon.police.uk/news/city-of-london/news/2026/june/over-70s-targeted-as-courier-fraud-exceeds-21-million-in-2025-with-london-and-home-counties-hit-hardest/
  2. https://www.rocu.police.uk/news/2026/july/two-suspected-fraudsters-arrested-after-cross-border-strikes/
  3. https://www.rocu.police.uk/news/2026/june/a-courier-fraud-conman-has-been-jailed/

  • ✇Security | CIO
  • CIO 100 Award winners spotlight IT’s power to transform
    Each year the CIO 100 Awards showcase outstanding IT initiatives, and every year they illustrate the power and potential of technology to transform how people work, how organizations perform, and the value they offer to customers. The 2026 cohort of winners is no different. Each one demonstrates how IT executives and their teams successfully move from ideation to deployment to scaling a solution for the future, overcoming challenges and driving adoption along the way to en
     

CIO 100 Award winners spotlight IT’s power to transform

10 de Agosto de 2026, 07:01

Each year the CIO 100 Awards showcase outstanding IT initiatives, and every year they illustrate the power and potential of technology to transform how people work, how organizations perform, and the value they offer to customers.

The 2026 cohort of winners is no different. Each one demonstrates how IT executives and their teams successfully move from ideation to deployment to scaling a solution for the future, overcoming challenges and driving adoption along the way to ensure their organization gets a return on its investment.

[ Interested in meeting and learning from all CIO 100 winners? Join us next week at CIO 100 Awards & Conference in Frisco, TX. Limited seats remain! Register here ]

The winning initiatives come from a range of industries and utilize a host of technologies to achieve their goals, as is the case annually. A growing proportion of these stand-out projects leverage artificial intelligence, raising the bar on the art of the possible for all IT departments.

The following 10 award-winning projects serve as representatives for the outstanding work done by all the 2026 honorees.

ABB democratizes AI agent creation and deployment

Organization: ABB

Project: ABBY — AI Agentic Platform for Workforce Transformation

IT leader: Vikke Kandell, CIO

IT leaders at ABB, a manufacturer, had some big hurdles to clear when it came to building an AI strategy.

They had to overcome employee fears that AI would take away jobs, the potentially high cost of AI vendor licenses, and pressure from investors, customers, and executives to advance the use of AI in the enterprise.

“We looked at this and asked, ‘How do we address all this?’ and build something that the company is proud of,” says Babu Kuttala, vice president of data analytics and AI.

The answer is ABBY, an AI agentic platform that enables employees to create and deploy specialized AI agents for specific business tasks.

To build ABBY, Kuttala and his team used best-of-breed LLMs (about 25 in total). They built a centralized orchestration layer using generative AI that integrates internal knowledge bases with external ecosystems, creating a unified platform where agents can access enterprise data, understand required actions, and execute tasks across multiple systems. And they created preconfigured skills so that employees could build agents tailored to their workflows without having to code.

ABBY was rolled out in 2025 to 100 users but is now used by 63,000 (more than 75% of the company’s workforce, Kuttala notes) with an average of 10,000-plus workers using it daily. IT continues to add LLMs and capabilities to expand use of ABBY even further, Kuttala says.

Belcorp modernizes manufacturing with Smart Factory

Organization: Belcorp

Project: QPlant — Smart Factory

IT leader: Venkat Gopalan, Chief Digital, Data, and Technology Officer

Legacy processes were limiting Belcorp’s ability to scale and compete. Its manufacturing relied on ERP-driven processes with limited shop-floor automation and weak connectivity across production, packaging, quality, and maintenance. The company depended heavily on manual records and post-process reconciliation, resulting in fragmented data, limited real-time insight, inefficiencies, and higher risks for errors.

Smart Factory changed all that. The IT initiative reimagined how manufacturing teams work “by creating a connected, data-driven environment where production, quality, maintenance, and operations are aligned around real-time information and standardized execution,” says Venkat Gopalan, chief digital, data, and technology officer.

At Smart Factory’s core is a manufacturing execution system that orchestrates production workflows, quality processes, and operational execution, he explains. IoT-enabled equipment integration and a centralized SCADA platform provide real-time visibility into shop-floor operations, while electronic batch records digitize production execution, strengthen traceability, and reinforce compliance by design.

Integrating those operational technologies with the company’s enterprise platforms was another critical component of success, Gopalan says, creating a trusted flow of real-time data across manufacturing, quality, maintenance, and business systems. “This connected architecture transformed isolated data into actionable insights, enabling faster decision-making, greater operational visibility, and continuous improvement across the manufacturing lifecycle,” he adds.

The initiative generated more than $1 million in financial benefits in its first year alone.

“Most importantly, Smart Factory established the digital foundation for the future of manufacturing at Belcorp,” Gopalan says. “With real-time operational data and connected systems now in place, we’re well positioned to accelerate advanced analytics, AI-driven optimization, predictive maintenance, and other Industry 4.0 capabilities that will continue delivering value for years to come.”

Cohesity replatforms post-acquisition for commercial growth

Organization: Cohesity

Project: Lead to Cash Replatforming Program (Veritas Integration)

IT leader: Brian Spanswick, CIO

Cohesity set an ambitious objective: Complete an enterprise-scale lead-to-cash replatform in under six months.

That’s a tight timeline for any replatforming initiative, but Cohesity’s project had another layer of complexity. It followed Cohesity’s December 2024 acquisition of Veritas, a company twice its size in revenue, leaving Cohesity to integrate the majority of a global enterprise revenue engine into its own operating model without disrupting customers, partners, or sellers.

“We had to bring the two companies together, merge the workforces together, and create an overall harmonized organization and operating infrastructure platform,” says Eric Brown, who as CFO and COO led the project.

The program migrated heavily customized CRM, CPQ, PRM, ERP, and subscription platforms (some of which were “very brittle, very bespoke,” Brown says) to a unified SaaS CRM, CPQ, and ERP environment with uninterrupted selling, billing, and partner operations.

This was no lift-and shift, Brown stresses. “It was a business process optimization project as well. We want to run very efficiently, so we questioned everything and used the migration process to simplify and streamline the business in every possible respect.”

The initiative enabled continuity for 13,000-plus customers, protected revenue during integration, and established a scalable commercial foundation for future growth.

Brown cites several factors that contributed to success. First, leadership was upfront about what it would take to meet the deadline, a process that involved carefully prioritizing the capabilities that would appear in the first iteration. Leadership also streamlined decision-making, establishing office hours that “ran with military precision” to handle issues. And the company selected a specialized partner, requiring its top talent be assigned to Cohesity.

Dairyland Power goes agentic to protect field crews

Organization: Dairyland Power Cooperative

Project: ODIN — Organizational Effectiveness Agentic AI

IT leader: Nate Melby, VP and CIO

Dairyland Power Cooperative had amassed a large collection of field observations, incident reports, near-misses, safety rules, and work methods that could yield insights into processes and practices that could help protect its workers.

But the insights were essentially out of reach, trapped in siloes.

Dairyland’s organizational effectiveness team turned to CIO Nate Melby for help unlocking those insights. Melby then turned to agentic AI, recognizing that the technology could address the team’s need to make better use of its data.

“This was about finding insights on how to work more safely,” Melby says. “It’s about preventing incidents.”

The collaboration between the two teams created ODIN, the first agentic AI implementation of its kind in the electric utility industry.

Focused on worker safety, ODIN autonomously connects the collective safety knowledge of the organization and delivers actionable insights directly to field crews at the moment work is planned.

ODIN was developed through a hybrid approach that combined an agentic AI platform and Dairyland’s internal private generative AI platform called VoltWrite. ODIN leverages LLMs, retrieval-augmented generation, and a coordinated swarm of autonomous agents.

Agents work together to analyze internal safety data, performance history, work practices, and safety rules and then synthesize the information into clear guidance on the safest way to perform specific tasks.

ODIN has produced results, including a reduction in OSHA recordable injuries and improvements in the quality and consistency of pre-job safety briefings.

ODIN was deployed in early 2025 for use by Dairyland’s workers in transmission construction and electrical maintenance, which are the highest-risk work areas. Dairyland is looking to expand ODIN’s use to other teams.

Dow’s digital sustainability ledger drives low-carbon sales

Organization: Dow

Project: Carbon Footprint Ledger

IT leader: Deb Bauler, Chief Information and Digital Officer

Executives at Dow consider the Carbon Footprint Ledger (CFL) as more than a technology or innovative carbon accounting methodology. According to Senior Global IT Director Jeremy Preston, CFL is “a digital business capability that enables Dow to translate sustainability investments into customer value.”

CFL transformed how Dow uses greenhouse gas emissions data. It combines a methodology aligned to international standards with an enterprise-scale digital platform. It also integrates manufacturing, supply chain, commercial, and sustainability data to generate product carbon footprints under enterprise-level governance and management at scale.

In doing so, Preston says it creates “a trusted, traceable link between low-carbon processes and raw materials implemented across its manufacturing network and the lower-carbon products customers seek.”

The technology team worked closely with sustainability and business teams, collaboratively developing the capabilities needed to reconstruct product genealogy, maintain end-to-end data lineage, track low-carbon attributes across interconnected manufacturing processes, and generate product carbon footprints that can support customer offerings and commercial transactions.

CFL was built on Dow’s Integrated Data Hub and in partnership with Boston Consulting Group and Databricks.

The core CFL platform is fully deployed and supports commercial transactions today.

Preston says CFL “enables Dow to turn sustainability investments into customer value, commercial differentiation, and new growth opportunities.” Dow reports that it has driven hundreds of millions of dollars in low-carbon product sales in 2025 and 2026.

The company is now expanding its use. “We are extending adoption across additional products, manufacturing networks, business segments, and customer use cases while continuing to enhance automation, analytics, and integration with commercial processes,” Preston says.

J&J transforms quality management with AI

Organization: Johnson & Johnson

Project: Q&C Strategy

IT leader: Michael Comprelli, Vice President, Head of Technology, Technical Operations, and Risk; Joel O’Connor, Head of Technology, Medtech Quality, and Compliance

Johnson & Johnson is using AI to transform quality management through its Q&C Strategy.

QuIn is an AI-powered digital assistant that fuses human expertise with machine learning, automation, and data-driven insights to boost efficiency, reliability, and worker impact. By embedding gen AI into core quality management systems processes, QuIn proactively gathers actionable insights, increases operational efficiency, and allows teams to focus on high-value, patient-centric work.

Cora is an innovative generative AI platform that provides regulatory intelligence monitoring, impact analysis, and augmented content revision. Cora assists with document analysis, compliance comparison, stakeholder analysis, policy/standard creation, procedural/document updates, and document comparison. Cora is purpose-built for regulated environments, validating outputs against source material and offering a user experience that instills trust in the outcome.

QuIn and Cora, which automate time-intensive tasks and democratize information access, are on track to deliver significant value, with J&J reporting more than $62 million in documented true cost savings by 2028 from QuIn alone. Cora delivered $2 million in cost efficiency in 2025 and will deliver a documented cost savings of $25 million by 2028.

“Our teams proved responsible AI can be applied meaningfully in a highly regulated environment without compromising the rigor, accountability, or human judgment that quality requires,” says Michael Comprelli, vice president, head of technology, technical operations, and risk.

He continues, saying that J&J “moved these ideas beyond experimentation and into products that employees use in their daily work. We did that by bringing together Quality expertise, product management, data engineering, architecture, cybersecurity, user-experience design and AI engineering around a common purpose.”

JLL brings intelligent automation to business services

Organization: JLL

Project: Business Service Digitization

IT leader: Pinak Dash, Global Head of JLL Business Services and Legal Technologies

JLL launched its digitization initiative to drive process redesign as well as systematic AI and RPA deployment across JLL Business Services (JBS).

The initiative was designed to address inefficiencies that hampered scalability and competitive positioning. It was also designed to eliminate manual processes that consumed thousands of hours across finance, HR, legal, procurement, marketing, research, IT, and lease administration.

Pinak Dash, global head of JBS and legal technologies, says the digitization initiative had a dual-strategy combining traditional digitization with generative AI innovation to hundreds of processes.

JLL lists three innovations critical to the program’s success.

First is a hybrid platform that integrates RPA with JLL’s proprietary AI platform called Falcon, which created intelligent automation that adapts and learns. It enables real-time process automation, intelligent document processing with automated extraction/validation, and smart decision-making for continuously optimizing workflows.

The second innovation is its use of ProHance for real-time process monitoring and enabling of data-driven optimization. Sensors capture granular productivity metrics, identify bottlenecks, and provide actionable insights for continuous improvement across automated and manual processes.

Third is its custom AI assistants and transaction agents. Falcon-powered assistants provide intelligent knowledge search while specialized agents execute complex transactions across enterprise SaaS platforms. These handle multisystem workflows, reducing human touchpoints while maintaining accuracy and compliance.

Dash says the initiative has delivered quantifiable benefits through improved efficiency, accuracy, and quality of services provided to clients.

“The initiative delivers on our business goals, makes us more efficient, provides customers better service, and it opens up the capabilities and bandwidth of our people to do what they like to do and to find innovative ways to serve our business,” he adds.

Nationwide partnership platform delivers efficiencies, business growth

Organization: Nationwide

Project: Enterprise Digital Platform (EDP)

IT leader: Michael Carrel, EVP and CTO

Nationwide’s new Enterprise Digital Platform (EDP) gives the company “a scalable way to connect with external partners quickly, securely, and consistently across all areas of our business,” says company EVP and CTO Michael Carrel.

He explains that “instead of treating every integration as a custom effort, EDP creates a common front door for digital products, documentation, onboarding and governance.”

That innovation has produced better experiences for the company’s partners. It saves time for Nationwide teams, partners, and customers. And it supports faster launch times for new products and enables growth across the business.

“EDP changed the model from fragmented, point-to-point integrations into an enterprise platform built around reusable digital products. That shift lets us support a range of integration options in one governed environment, meet partners at different stages of technical maturity, and add new capabilities over time without redesigning every relationship from scratch,” Carrel explains.

EDP uses cloud-native microservices, role-based access control, and advanced analytics. Nationwide IT created modular microservices to make EDP more scalable, resilient, and adaptable. And IT decoupled it from infrastructure-specific dependencies so that it would be a platform-agnostic developer portal. That, Carrel says, reduced operational constraints across environments.

Additionally, IT shifted from a user-specific model to role-based access, which improved security, simplified administration, and better served the needs of different audiences.

Meanwhile, robust analytics delivers visibility into platform usage and performance, which Carrel says helps ensure Nationwide continuously evolves the platform based on measurable outcomes.

The core platform is fully deployed, with Nationwide planning to expand it.

“Our Enterprise Digital Platform is more than a piece of technology,” Carrel notes, “it represents a strategic enabler to support growth objectives across Nationwide’s businesses.”

PITT Ohio fast-tracks shipment requests with AI assist

Organization: PITT Ohio

Project: No Touch Email (N@TE AI)

IT leader: Scott Sullivan, President and CEO (formerly CIO)

As PITT Ohio started its AI journey in 2024, the mandate was clear: Use the technology to solve “real problems,” says Ryan Carner, director of enterprise IT solutions.

“We wanted to hit the ground running and find a problem that was solvable,” Carner says, noting that the company also wanted to use the experience to build in-house AI skills. “The idea was to find a business case for AI that would be our first but not the only one.”

PITT Ohio leaders decided to tackle what Carner describes as a “mundane but very important task for how our business operates”: handling emails to the customer service team.

The need was significant. Customer service representatives were manually processing hundreds of pickup request emails daily, each requiring five to 15 minutes to interpret and re-enter shipment details into the company’s transportation management system (TMS). The emails were complicated, containing a lot of information submitted in nonstandardized ways and varying formats. This repetitive task consumed valuable time, introduced errors, and delayed customer response.

N@TE uses generative AI and natural language processing to transform unstructured email content into structured pickup orders automatically and in real-time. N@TE scans incoming emails, extracts key shipment data, and creates orders directly in the TMS via API integration. It operates seamlessly within existing workflows, requiring no change in customer behavior or retraining of staff.

PITT Ohio deployed N@TE in 2025, and the company also secured a patent for the product that year. N@TE has produced a 30-60X increase in processing speed, 99% accuracy in extracting and populating order data, and a 70% reduction in handling costs per pickup order.

SMU builds AI adoption through grassroots ambassador program

Organization: Southern Methodist University

Project: Scaling AI Without Scaling AI: Organizational AI Scaling Through Willingness

IT leader: Jason Warner, Associate CIO

Like executives in most organizations, leaders at Southern Methodist University encountered mixed attitudes about AI. Some workers had little interest in using the tech, others were afraid it would take jobs, still others were curious about what it could do.

Associate CIO Jason Warner and other leaders decided to leverage that last group, believing the best way to get SMU faculty and staff to embrace AI was to use enthusiasts to help smooth the way.

So, instead of treating AI as a conventional technology rollout, Warner and his colleagues built opt-in communities of practice known as the AI Coalition of the Willing and Operation Copilot.

The goal, Warner says, was to build institutional capability, reduce risk, and generate momentum.

“We knew the fastest way to scale AI was to scale the willingness of people to use the technology, and not talking to people about cost savings and the like,” Warner says, adding that willing users as great ambassadors and evangelists who showcase in formal and informal ways the technology’s potential for hesitant or skeptical colleagues.

Participating faculty members have access to a licensed ChatGPT account as long as they use it. Staff members have access to Copilot accounts after taking a self-paced training course and likewise must use it to keep that access.

Warner says these willing workers are demonstrating the benefits of AI (significant time reclamation, reduced cognitive load, improved quality of outputs, expanded professional capacity).

SMU is now moving to a single solution and scaling AI, confident that its use will deliver returns following in the footsteps of the early adopters.

Interested in meeting and learning from all CIO 100 winners? Join us next week at CIO 100 Awards & Conference in Frisco, TX. Limited seats remain! Register here 

  • ✇Security | CIO
  • The gen AI helping Aetna review millions of medical records
    One of the biggest challenges companies like Aetna face every year is an annual HEDIS review of its records to identify gaps in care. For large national payors, the scale of the challenge is immense. So Aetna has deployed a gen AI-driven document intelligence platform that has reduced the need for manual review by 65%. “We have a large group of amazing trained medical coders who do this every day,” says Nathan Frank, chief digital and technology officer at Aetna. “This
     

The gen AI helping Aetna review millions of medical records

31 de Julho de 2026, 07:00

One of the biggest challenges companies like Aetna face every year is an annual HEDIS review of its records to identify gaps in care. For large national payors, the scale of the challenge is immense. So Aetna has deployed a gen AI-driven document intelligence platform that has reduced the need for manual review by 65%.

“We have a large group of amazing trained medical coders who do this every day,” says Nathan Frank, chief digital and technology officer at Aetna. “This is about making it easier for them by speeding up the process. Something that might have taken weeks or months we can now do in days.”

The Healthcare Effectiveness Data and Information Set (HEDIS) is a range of performance measures for the managed care industry. Developed and maintained by the nonprofit National Committee for Quality Assurance (NCQA), the first version of HEDIS was released in 1991.

Under the HEDIS measures, large managed care providers like Aetna review more than 10 million medical records annually to identify gaps in care. These gaps are missed or overdue preventative care or chronic disease management tests including missed cancer screenings, blood sugar tests for diabetics, eye exams, and immunizations. Closing these gaps improves patient outcomes, and health plans are measured in how well they perform. But processing medical records is no easy task.

“We’re talking about medical charts that have white space filled with handwritten notes,” Frank explains. It’s not just structured data, it’s lots of physical clinical documentation.”

Adding up the numbers

Frank says industry benchmarks for large providers indicate an annual review process that requires about 50,000 work weeks, equivalent to nearly 1,000 dedicated full-time employees. It would take a team of 50 reviewers more than 20 years to complete a single annual review using fully manual processes.

Enter AI Medical Chart Review, a platform developed by Aetna that leverages cloud services and gen AI to automatically extract clinically relevant data from records, and prioritize records based on the likelihood of measure closure and evidence strength.

“Large language models and gen AI give us the ability to train a model to decipher the charts, identify the high value codes, and build correlations,” Frank says.

In the space of about six months, Frank’s team ideated the platform, and designed and trained a PoC that was able to process millions of records in just two weeks. As a result, AI Medical Chart Review has earned Aetna a CIO 100 Award in IT innovation.

“Now we’ve gone through 14 million documents,” Franks says. “We’re seeing a reduction of manual effort, which is now being transitioned into other areas like quality control and making sure the automated chart review is working as expected.”

Behind the curtain

Using gen AI, the platform automatically ingests and analyzes unstructured medical records and clinical documents. And as part of that process, it identifies and extracts clinically relevant information for specific HEDIS measures like diagnosis codes, medication records, lab results, and visit documentation. With this data, the platform generates a prioritized set of records based on the likelihood of measure closure and strength of clinical evidence, which is then passed to human employees for review and validation.

Frank says the platform has increased gap closure rates (leading to improved Star Ratings and higher reimbursement), streamlined workflows, and enabled teams once dedicated to manual record review to shift focus to higher-value activities.

Frank says much of the speed and success in building the platform comes down to a shift in the way it approached the design and build process. Rather than exhaustively writing specifications and requirements, Aetna created a team that included engineers and subject matter experts who worked together to build out capabilities iteratively.

“It allowed us to move much faster, and having a business subject matter expert sitting in the same virtual or physical room with us got us a much better outcome,” Frank says. “The product model, our cloud compute model, and our AI governance model allow for quick reviews to make sure we’re using AI responsibly with the right guardrails. It’s increased the speed to get from product launch to go-live.”

He adds that small teams that don’t have to deal with a lot of bureaucracy are key to moving quickly.

“You need to design with security, compliance, and a responsible use of AI as core principles from day one,” he says. “Everything we do from a new build standpoint starts with thinking about how we make it cloud native, how we build with the right elasticity and speed, and how we optimize the cost.”

The most important element of all, he says, is a good relationship with your subject matter experts.

“You can have a great product manager and engineer, but you really need that business subject matter expert who’s excited about it, and who has a passion for transforming the process,” Frank says. “Once you put those three together, you’ll see amazing things like this happen all the time.”

  • ✇Malwarebytes
  • Chick-fil-A loyalty accounts hijacked using stolen passwords
    Fast-food chain Chick-fil-A is warning customers after attackers hijacked loyalty accounts using stolen passwords in a credential stuffing attack. Chick-fil-A says it detected suspicious login activity against some Chick-fil-A One accounts in June and launched an investigation. The company later concluded that unauthorized parties ran an automated credential stuffing attack against its website and mobile app between June 17 and June 19, 2026, using usernames and passwords obtained from previo
     

Chick-fil-A loyalty accounts hijacked using stolen passwords

22 de Julho de 2026, 09:46

Fast-food chain Chick-fil-A is warning customers after attackers hijacked loyalty accounts using stolen passwords in a credential stuffing attack.

Chick-fil-A says it detected suspicious login activity against some Chick-fil-A One accounts in June and launched an investigation. The company later concluded that unauthorized parties ran an automated credential stuffing attack against its website and mobile app between June 17 and June 19, 2026, using usernames and passwords obtained from previous data breaches or other third‑party sources. Chick-fil-A says it reset passwords and ended active sessions for affected accounts while investigating the incident.

Credential stuffing is an attack where criminals take username–password pairs stolen from one service and automatically try them on many other websites and apps to see where they still work. Because many people reuse passwords, attackers often gain access to accounts without ever breaking into the company’s systems in the traditional sense.

So, some may conclude that there are two sides to this. On the one hand, customers who reuse passwords across multiple sites make credential stuffing attacks much more likely to succeed. On the other, companies also have a responsibility to put protections in place to detect and block automated credential stuffing attacks before accounts are compromised.

How it works

To understand how it works, we’ve created a typical scenario:

  • Cybercriminals obtain large lists of breached credentials from previous data breaches, dark web markets, or public dumps.
  • They use automated tools to fire those credentials at login endpoints for popular services like retailers, banks, and loyalty programs.
  • They take over accounts where the credentials still work, then siphon off stored value, personal data, or loyalty rewards, or resell the access to other criminals.

To a victim, this may seem like a breach at the company, but technically speaking, the cybercriminals already had the credentials and were able to enrich their database with additional information about the victims.


What do cybercriminals know about you?

Use Malwarebytes’ free Digital Footprint scan to see whether your personal information has been exposed online.

According to Chick-fil-A’s breach notifications, the attackers may have accessed a combination of:

  • Name and email address.
  • Chick-fil-A One membership number and mobile pay number.
  • QR codes associated with the account.
  • The balance of any Chick-fil-A credit, such as gift cards or rewards on the account.
  • The last four digits of the stored credit or debit card number.

If you saved more details in your Chick-fil-A One account, attackers may also have seen:

  • Birthdate (month and day).
  • Phone number.
  • Physical address.

Advice for Chick-fil-A customers

The real problem is that, over the years, we’ve designed and adopted a system that no longer works well for most people: passwords. We tell people not to reuse them and to use a password manager to keep track of unique passwords for every account. But for many people, password managers still seem complicated or untrustworthy. I’m afraid the same may turn out to be true for passkeys.

If you have or suspect you had a Chick-fil-A One account, you should act even if you haven’t received a letter.

  • Set a new, unique password for your Chick-fil-A One account that you do not use anywhere else. And if you’ve used the same password elsewhere, change it on those accounts too.
  • If you cannot log in because your account was locked or reset, follow Chick-fil-A’s recovery process.
  • Turn on multi-factor authentication (MFA) if you haven’t already. Chick-fil-A supports MFA for Chick-fil-A One accounts using a verified mobile phone number.
  • Be aware that attackers can use the exposed data to craft more convincing phishing messages and scams.

Something feel off? Check it before you click.  

Malwarebytes Scam Guard helps you analyze suspicious links, texts, and screenshots instantly.  

Available with Malwarebytes Premium Security for all your devices, and in the Malwarebytes app for iOS and Android.  

Try it free → 

❌
❌